You need a Zoho account that can open the Zoho API Console. The client asks for read and write access to Vault users, user groups, passwords and folders.

Register a client in the Zoho API Console

The client is the Zoho app StackOne uses to ask each Vault administrator for access.

1

Choose the client type

Sign in to your Zoho API Console account, or the China API Console for a China account. The Applications page opens.

  • Click ADD CLIENT.
  • In Choose a Client Type, click CREATE NOW on the Server-based Applications card.
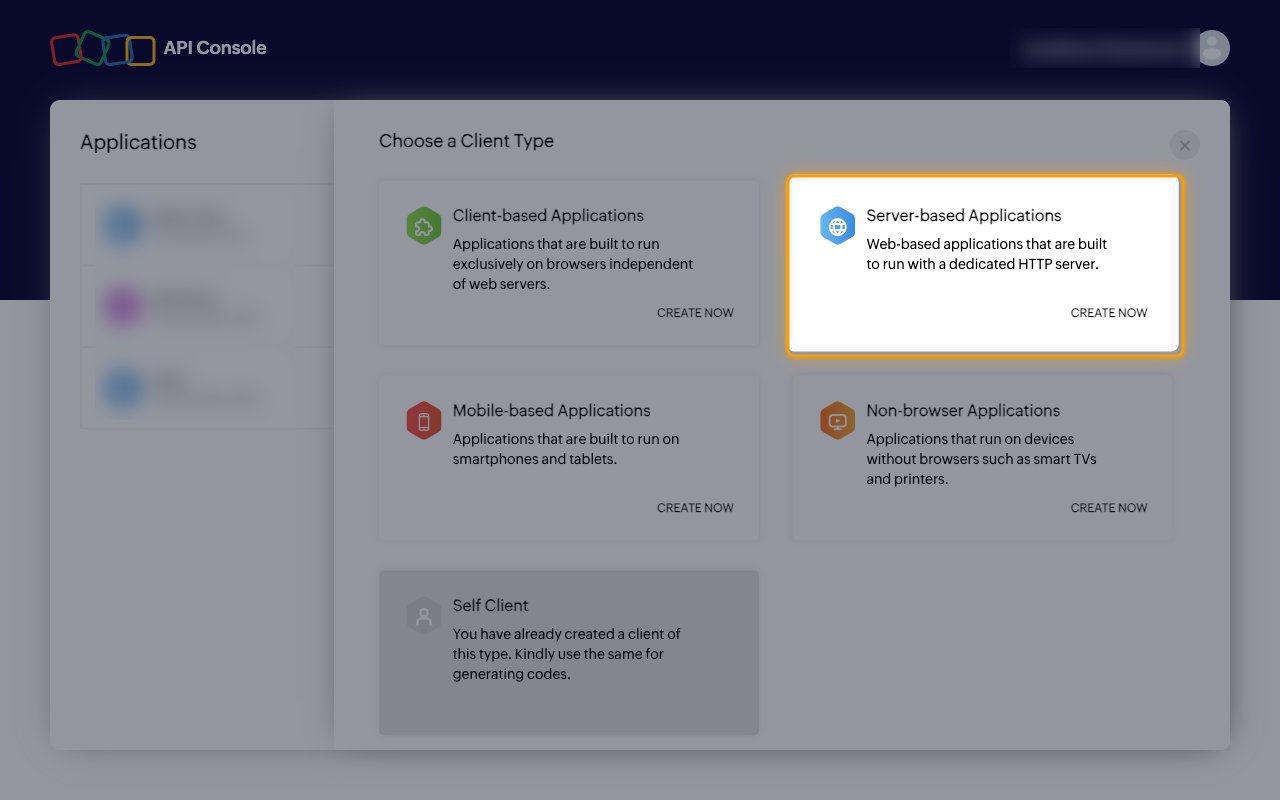
Choose a Client Type window with the Server-based Applications card highlighted
2

Enter the client details

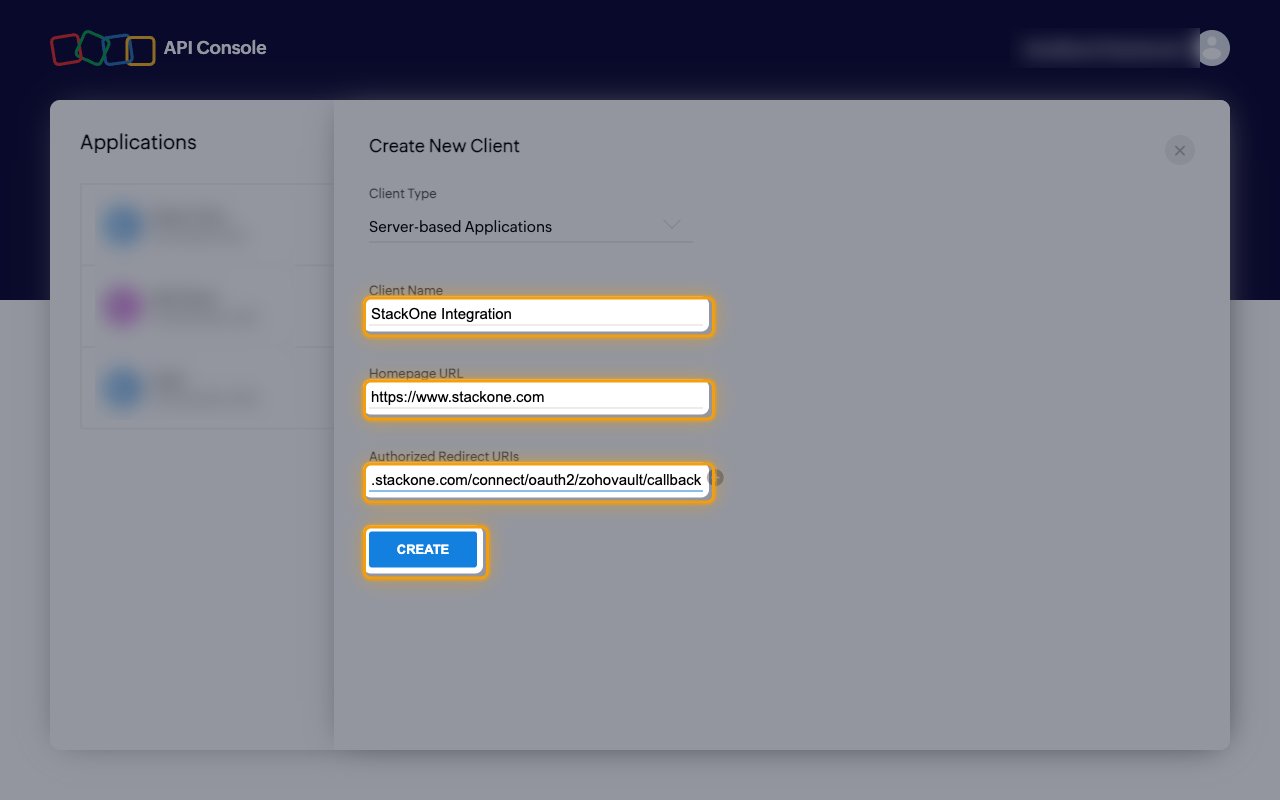
In Create New Client, fill in the fields.

  • Client Name: StackOne Integration
  • Homepage URL: your company website
  • Authorized Redirect URIs: the Callback URL from your Connector Profile
  • Click CREATE.
Create New Client form with Client Name, Homepage URL, Authorized Redirect URIs and CREATE highlighted
3

Copy the Client ID and Client Secret

The Client Secret tab of the new client shows your Client ID and Client Secret.

  • Click the copy icon next to each value.
  • Copy the Client ID and Client Secret into your Connector Profile.
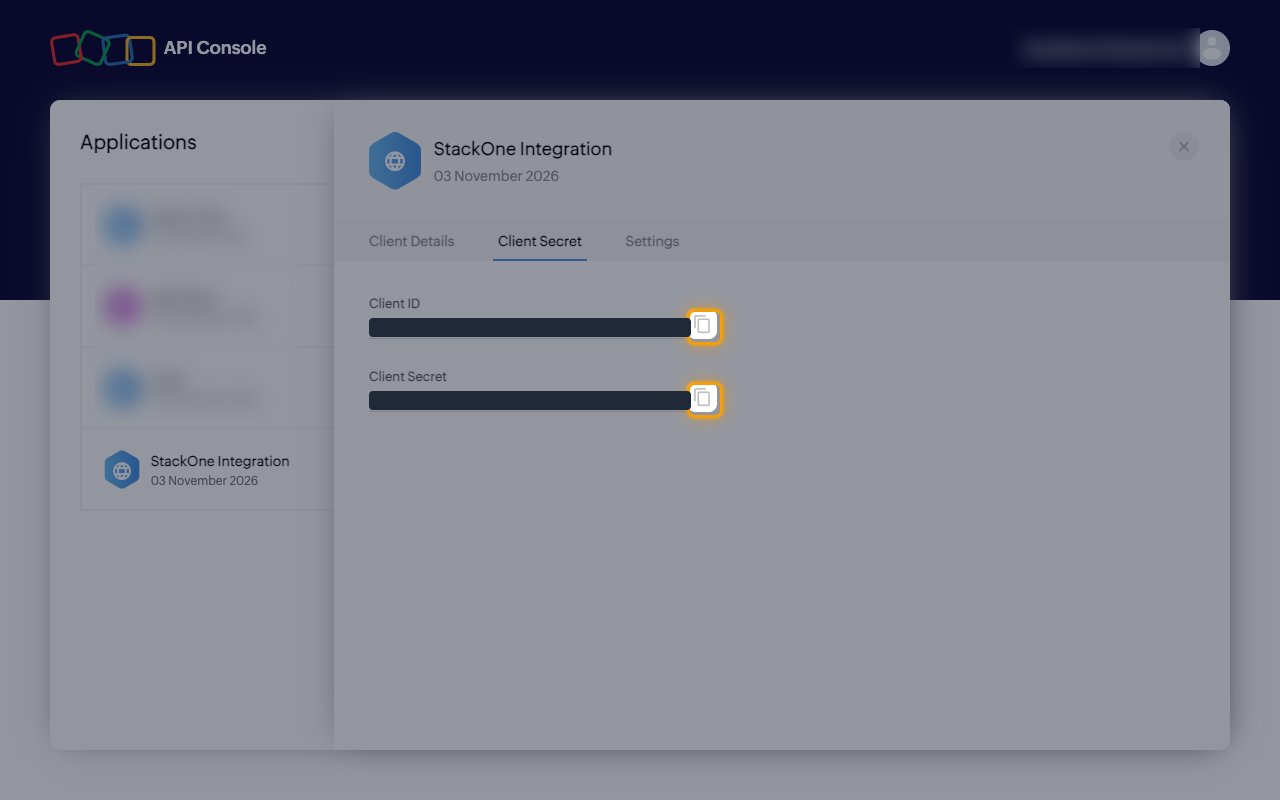
Client Secret tab with the copy icons next to Client ID and Client Secret highlighted and the values hidden
4

Enable other data centers

Customers whose Vault is in a data center other than the one your client is registered in need that data center enabled. Open the Settings tab of your client.

  • Under Multi-DC, switch on the toggle of each of those data centers, such as EU (zoho.eu).
  • Select Use the same OAuth credentials for all data centers. Zoho gives each enabled data center its own secret by default.
  • The Multi-DC list has no China data center. A customer on China (CN) needs a client registered in the China API Console.
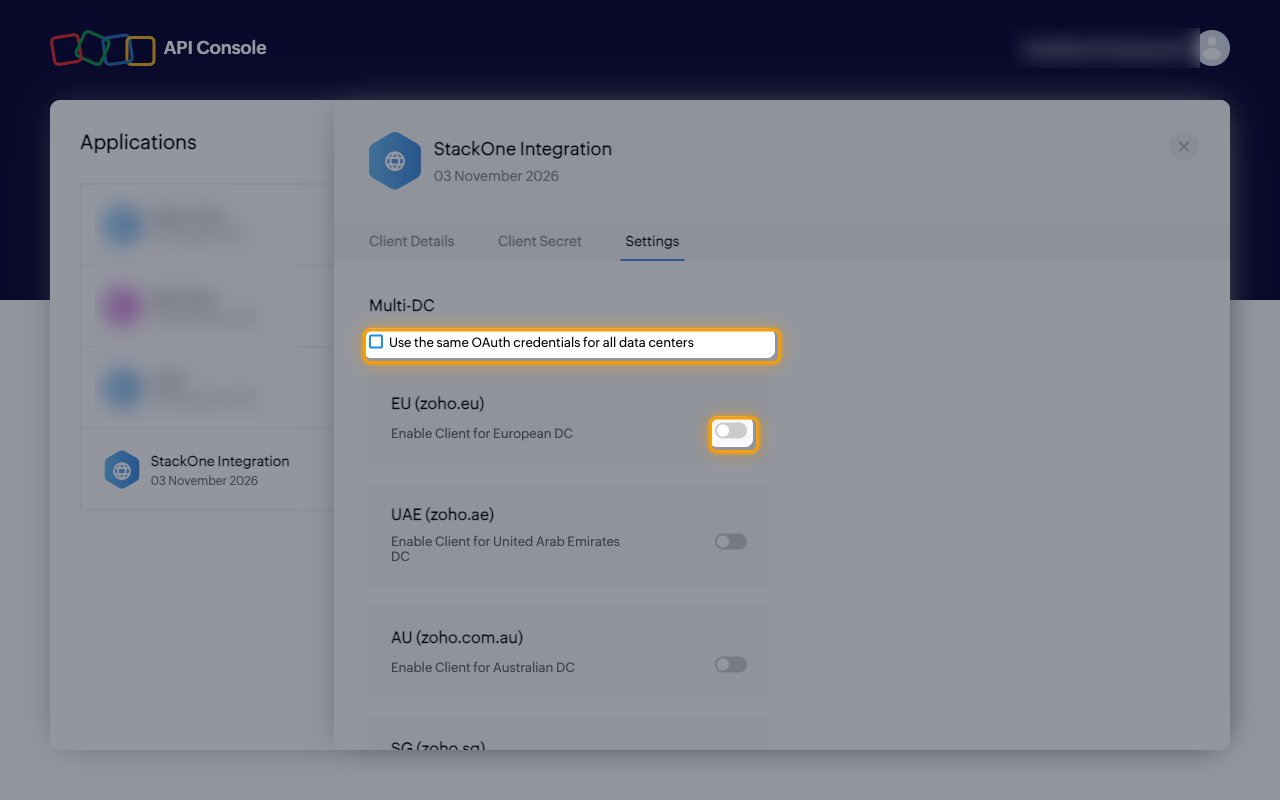
Settings tab with the Use the same OAuth credentials for all data centers checkbox and the EU toggle highlighted

Choose the OAuth Scopes

These are the Vault scopes StackOne asks each administrator to approve.

1

Review the scopes

Enables actions: Add User Group, Bulk Share Passwords With User Groups, Bulk Share Passwords With Users, Bulk Update Folder User Group Sharing, Check User Access, Create Folder, Create Password, Delete Folder, Delete Password, Get All User Groups, Get Folder User Group Sharing, Get Folder User Sharing, Get Login, Get Password, Get Password Files, Get Password User Group Sharing, Get Password User Sharing, Get Passwords, Get Unified Group, Get Unified Role, Get Unified User, Get User, Get User Group, Get Users, List Audit Activity, List Folder Audits, List Miscellaneous Audits, List Password Audits, List Passwords Shared To User, List Unified Groups, List Unified Roles, List Unified Users, List User Audits, Open Vault, Search Folders, Share Password With Outsider, Share Passwords With User, Update Folder, Update Folder User Group Sharing, Update Folder User Sharing, Update Password, Update Password File Data, Update Password User Group Sharing, Update Password User Sharing, Update User Group, View Folder

The secrets scopes give access to stored passwords and folders.

Create the StackOne Connector Profile

1

Create a Connector Profile

Enable the connector and create a Connector Profile in your project. See Setup Connector Profile.
2

Link an Account

Once the Connector Profile is created, continue to link an account.