

Generate the API access token
An API access token, sometimes called an API key, carries the permissions of the user who generates it.
Sign in to Tailscale
Sign in to your Tailscale admin console as an IT admin.
- IT admin is the smallest role that covers this connector. It reads users and the policy file and manages users, invitations and devices. It cannot change the policy file, DNS or billing.
- If your plan has no IT admin role, sign in as an Admin.
- Do not use a Network admin. Tailscale lets only an Owner, Admin or IT admin manage invitations, and the connection test lists pending invitations.
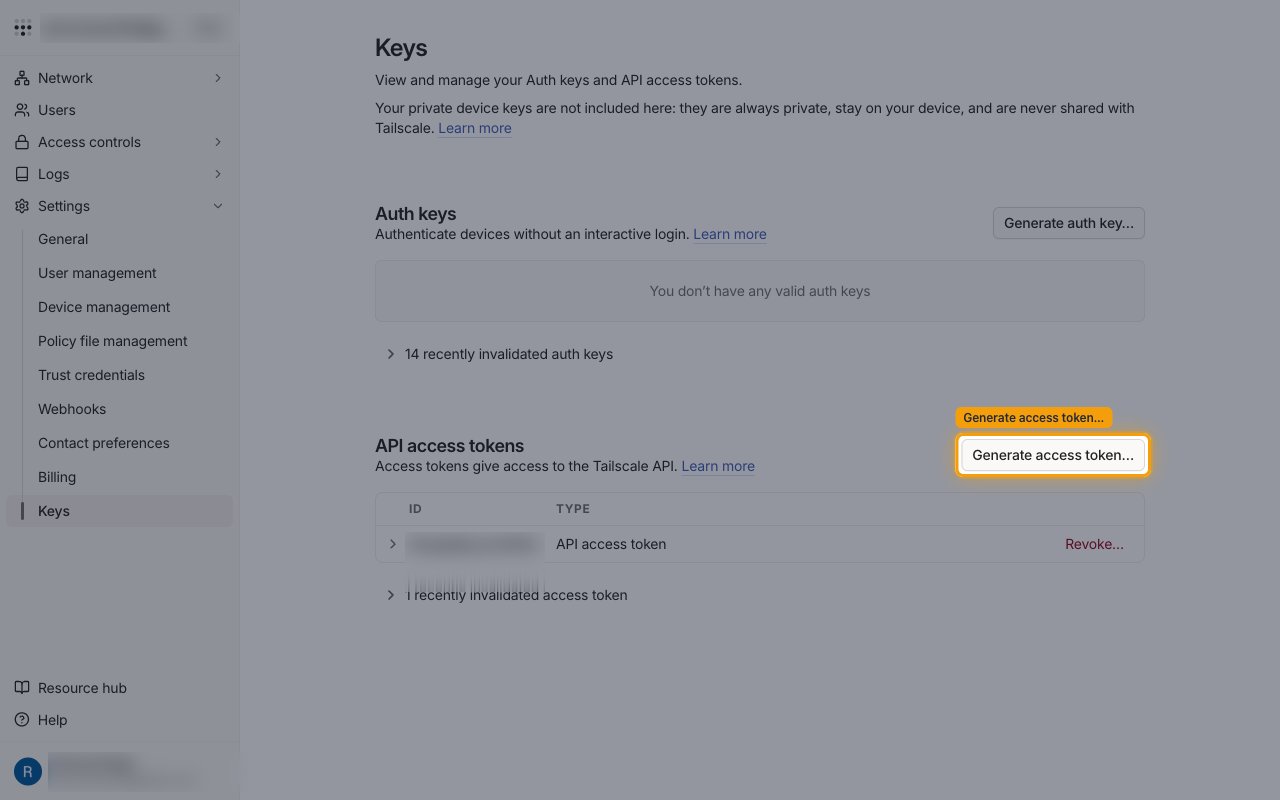
- Open the Keys page under Settings.
- In the API access tokens section, select Generate access token….
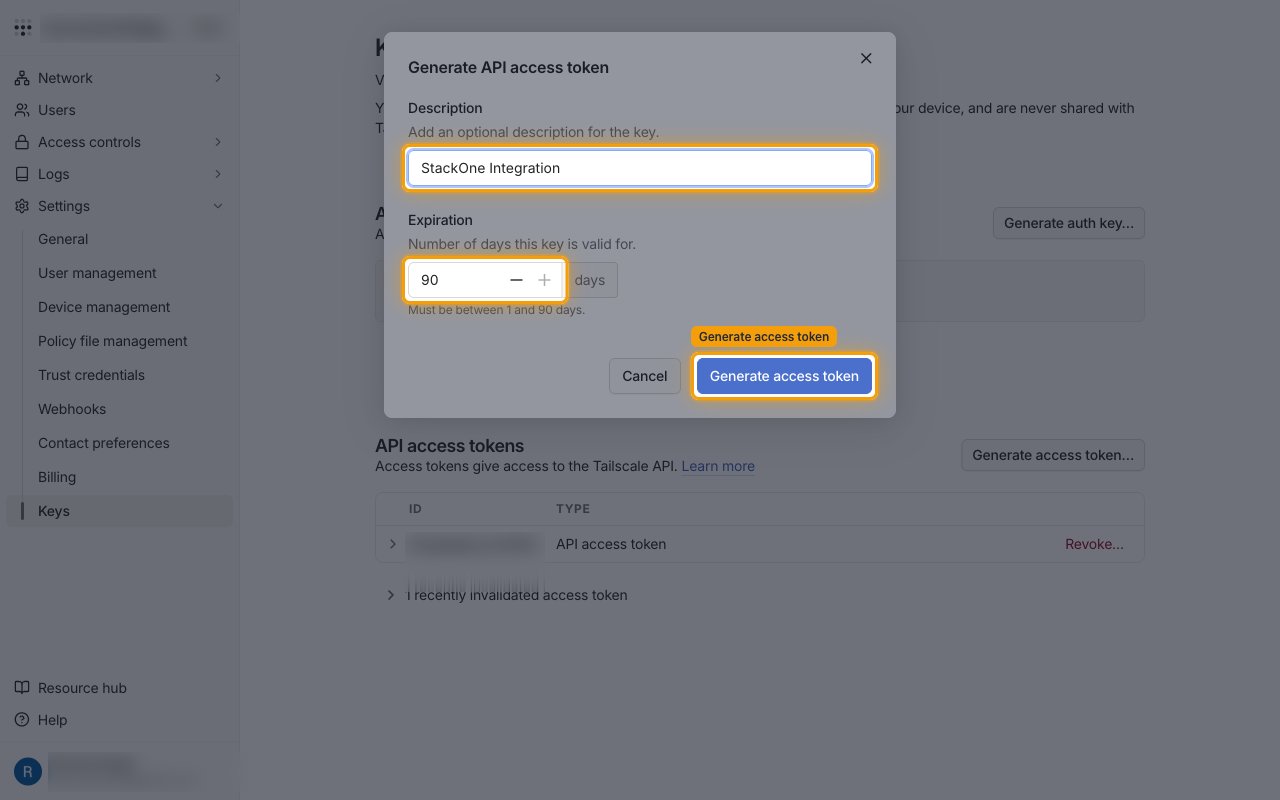
Set the description and expiration
In the Generate API access token dialog, enter a Description you will recognize, such as StackOne Integration. Set Expiration to the number of days the token stays valid, then select Generate access token.
- Tailscale accepts 1 to 90 days.
- When the token expires, the connection stops working until you paste a new token into StackOne Hub. Set a reminder to replace it before then.
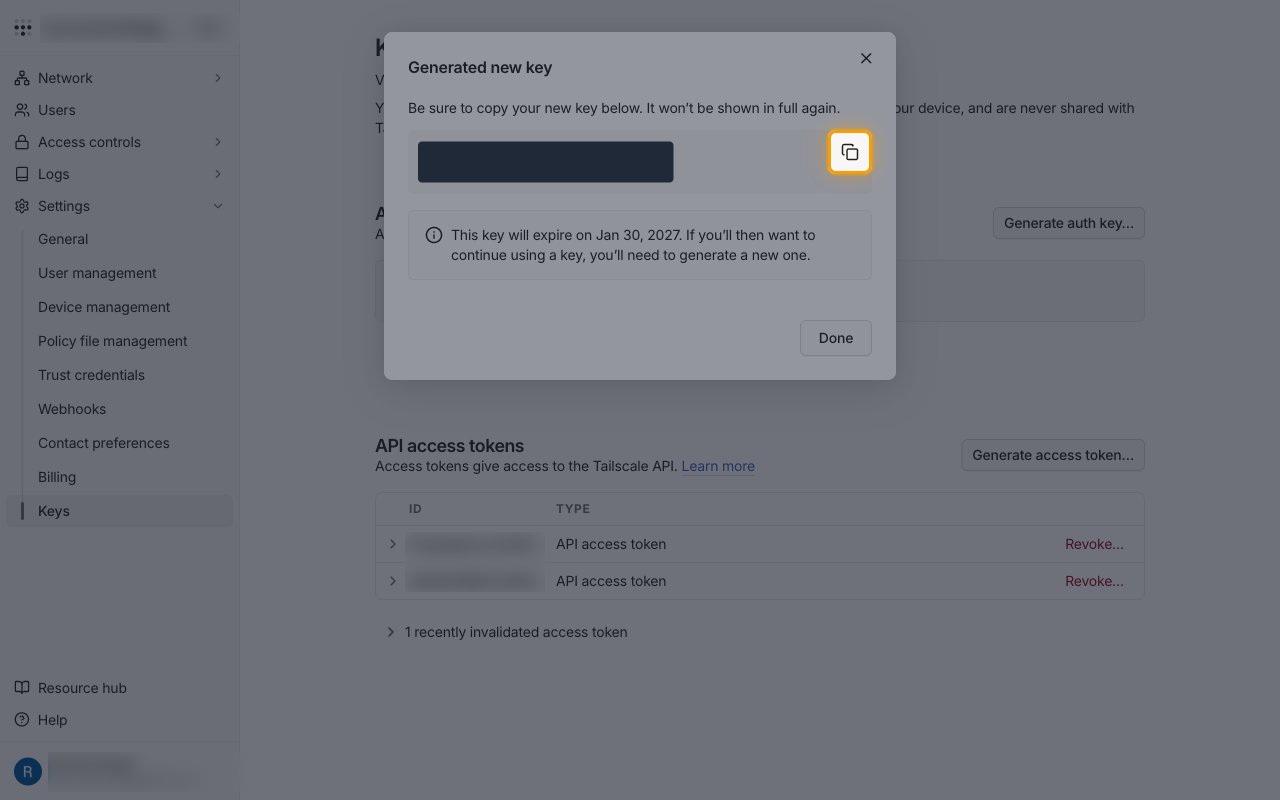
Copy the token
In the Generated new key dialog, copy the token with the copy button, store it securely for use later, then select Done.
- The token is only displayed once and cannot be retrieved later. If you do not copy it, generate a new token.
- The token starts with
tskey-apiand is case-sensitive. - Paste it into the API Access Token field in StackOne Hub.
Revoke the token
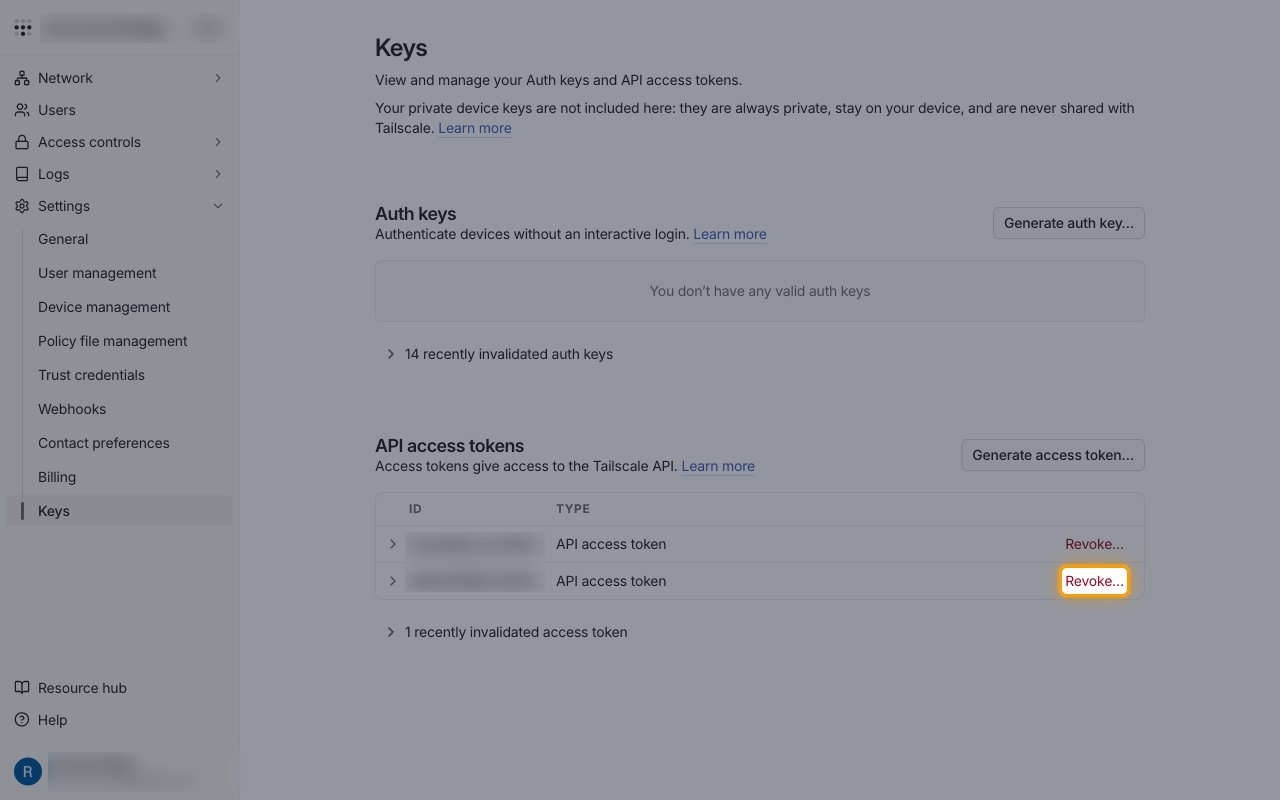
To stop StackOne from reading your tailnet before the token expires, revoke it.
Select Revoke
On the Keys page, in the API access tokens section, select Revoke… next to the token.
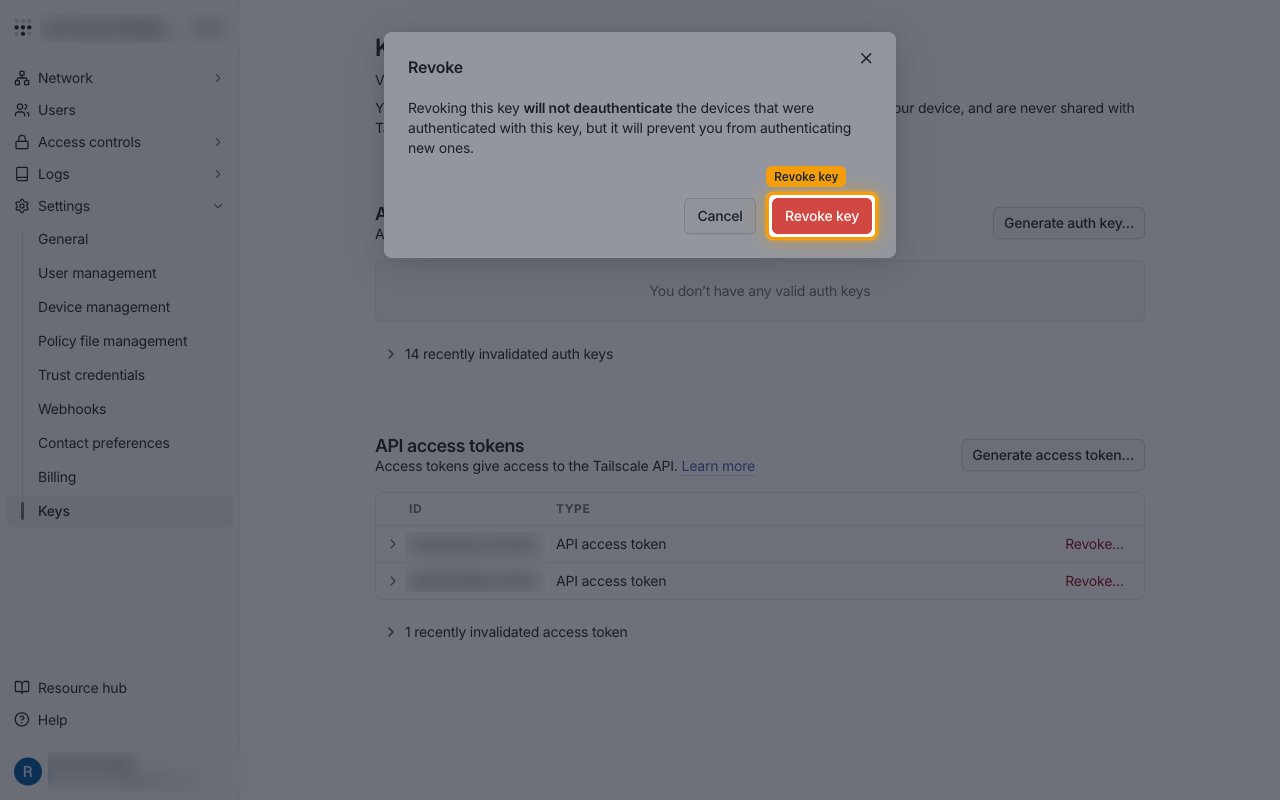
Confirm the revocation
Select Revoke key.
- Recently expired and revoked tokens stay listed on the Keys page.
Link the Account
Connect
- Click Connect.
- If applicable, the provider will redirect you to a sign-in or authorization page. Complete the provider’s authorization flow.
- Once authorization is successful, you will see a confirmation popup.
Use Actions
Next Steps
Webhooks setup
Configure receiving Events for Tailscale into StackOne.