

Find your Region
Your region determines which OVHcloud API endpoint StackOne calls for your account. It is set
by the OVHcloud subsidiary your account belongs to, and you select the matching option in
StackOne Hub.
- Europe serves the CZ, DE, ES, EU, FI, FR, GB, IE, IT, LT, MA, NL, PL, PT, SN and TN subsidiaries, so Morocco, Senegal and Tunisia use Europe too.
- Canada, Asia-Pacific and rest of world serves the ASIA, AU, CA, IN, QC, SG, WE and WS subsidiaries.
- United States serves the US subsidiary.
- Choose the region that matches the location of your account.
Create a local user for the connection
A Personal Access Token belongs to one local user and has only the rights that user’s group and
policies give it, so create a dedicated user for StackOne.
Sign in to OVHcloud
Sign in to the OVHcloud Control Panel for your region.
- Europe — OVHcloud Europe Control Panel
- Canada, Asia-Pacific and rest of world — OVHcloud Canada Control Panel
- United States — OVHcloud US Control Panel
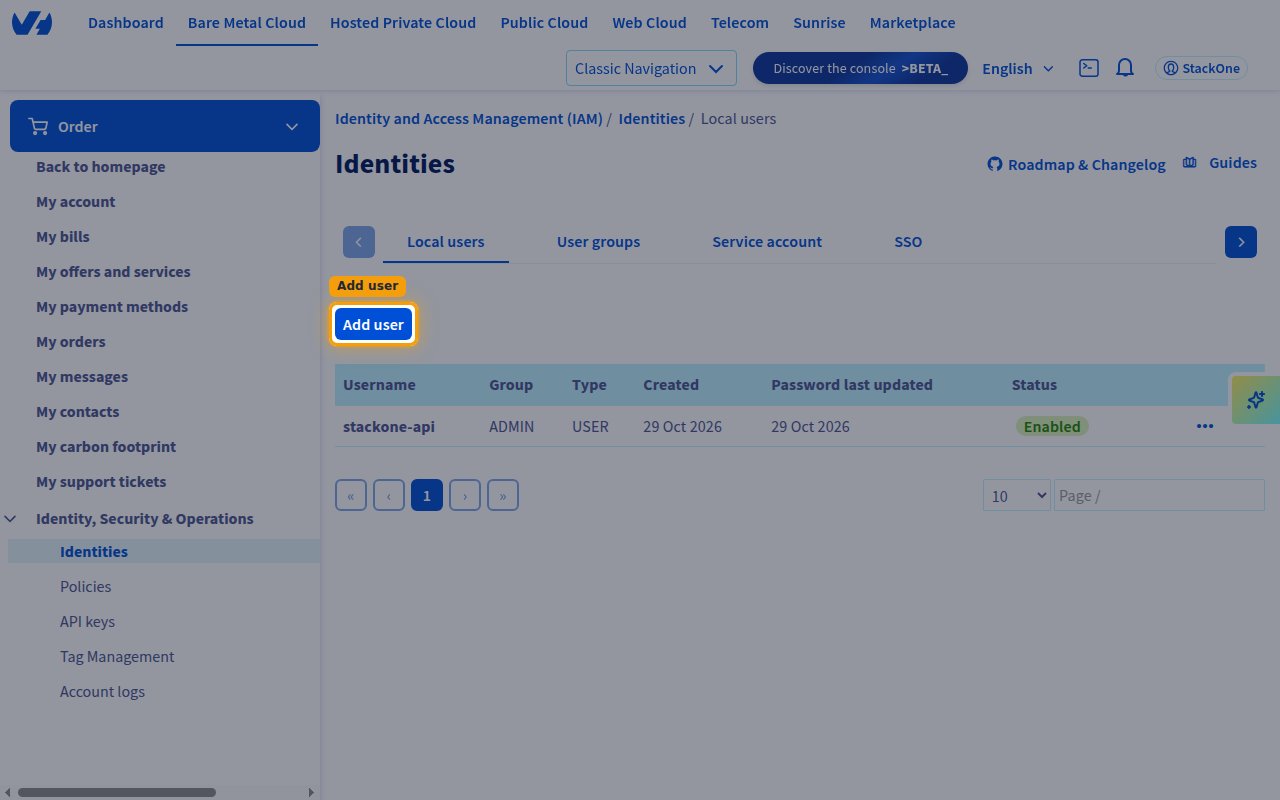
- Navigate to Identity, Security & Operations > Identities > Local users.
- Click Add user.
Add the user
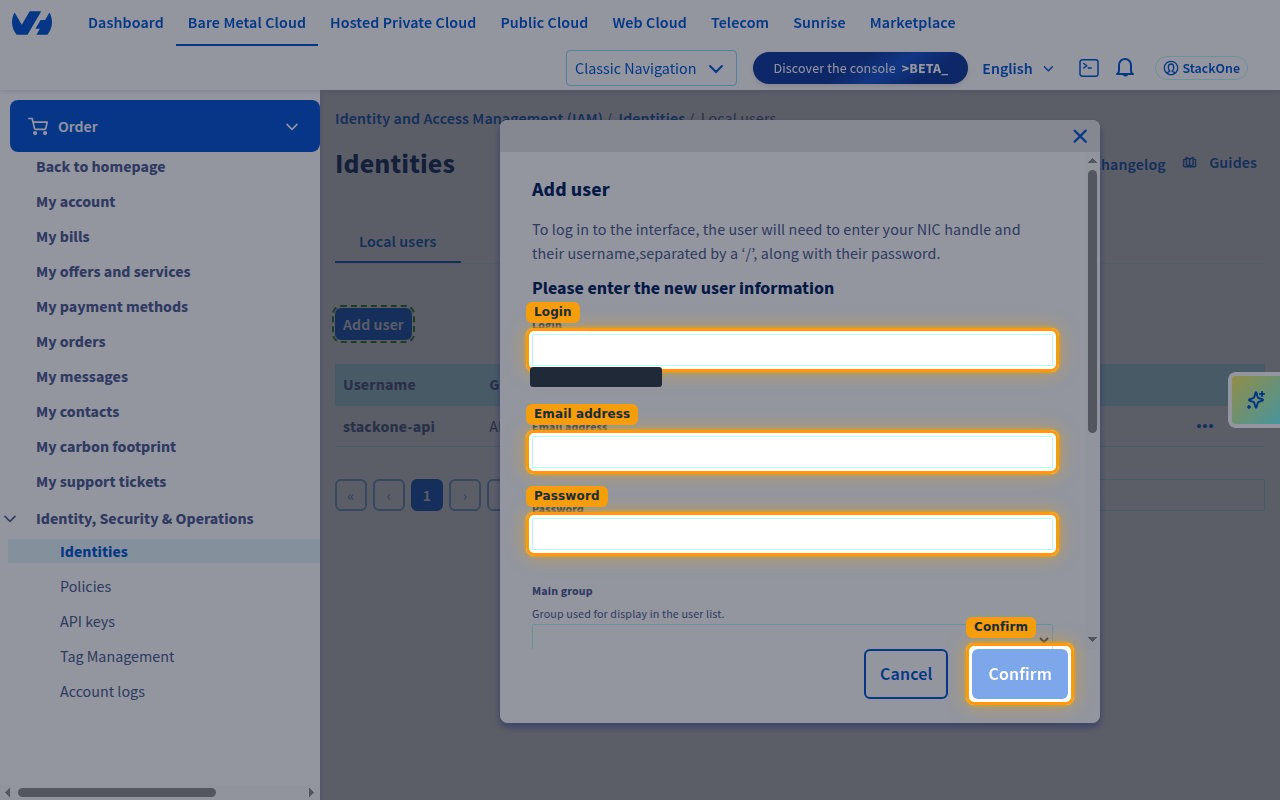
On the Add user form, complete Please enter the new user information, then click Confirm.
- Login: the username suffix for the user. OVHcloud prefixes it with your account ID and a
/, for example1234-567-89/stackone-integration. - Email address: an email for the user
- Password: a password for the user
- Main group: the group that sets the user’s base access. Choose UNPRIVILEGED for read-only access, or a higher-privilege group for write access. For access between these, leave the group and grant a policy in the next section.
- Description: an optional note such as
StackOne access.
Grant the user a policy (optional)
The user’s Main group already sets its base access. To grant access that is narrower than a
group, create a policy that lists the exact products and actions the connection uses and assign
it to the user. Skip this section if the group you chose already fits.
Create a policy
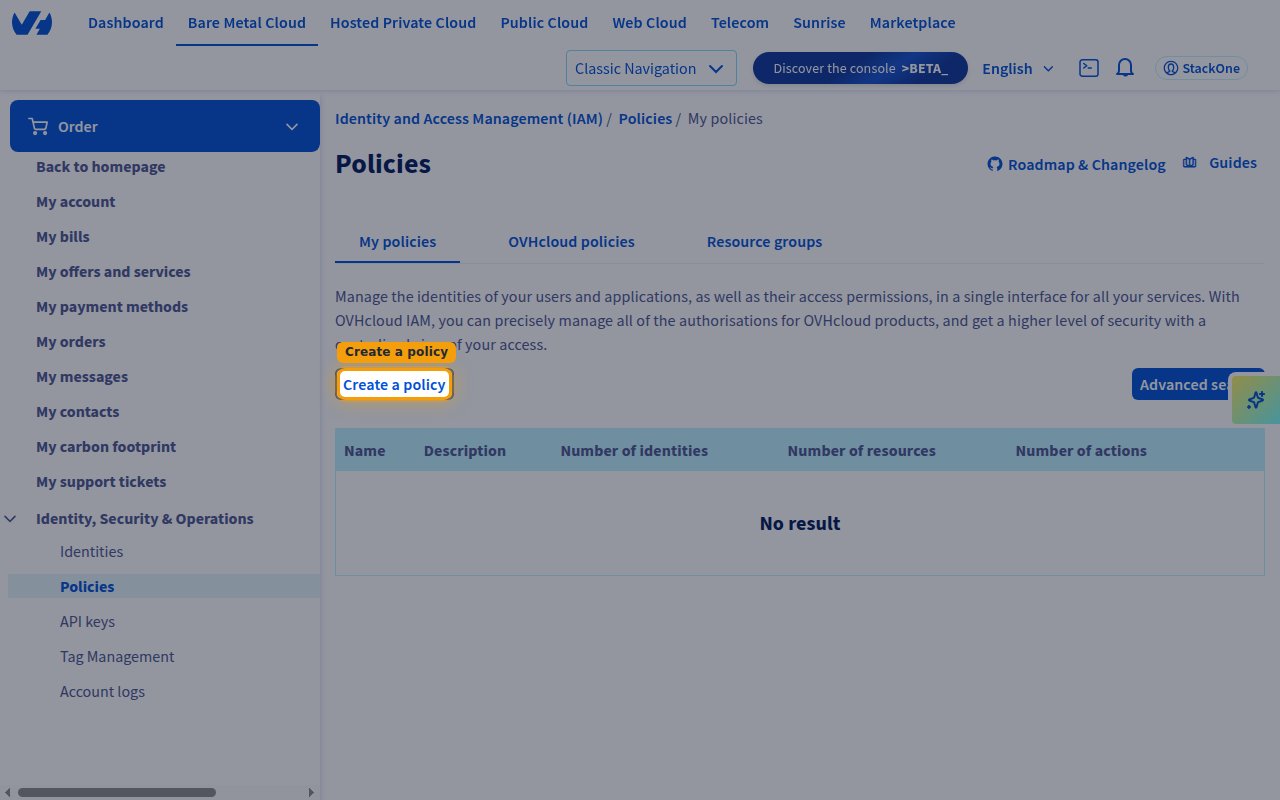
Navigate to Identity, Security & Operations > Policies, then click Create a policy.
Configure the policy
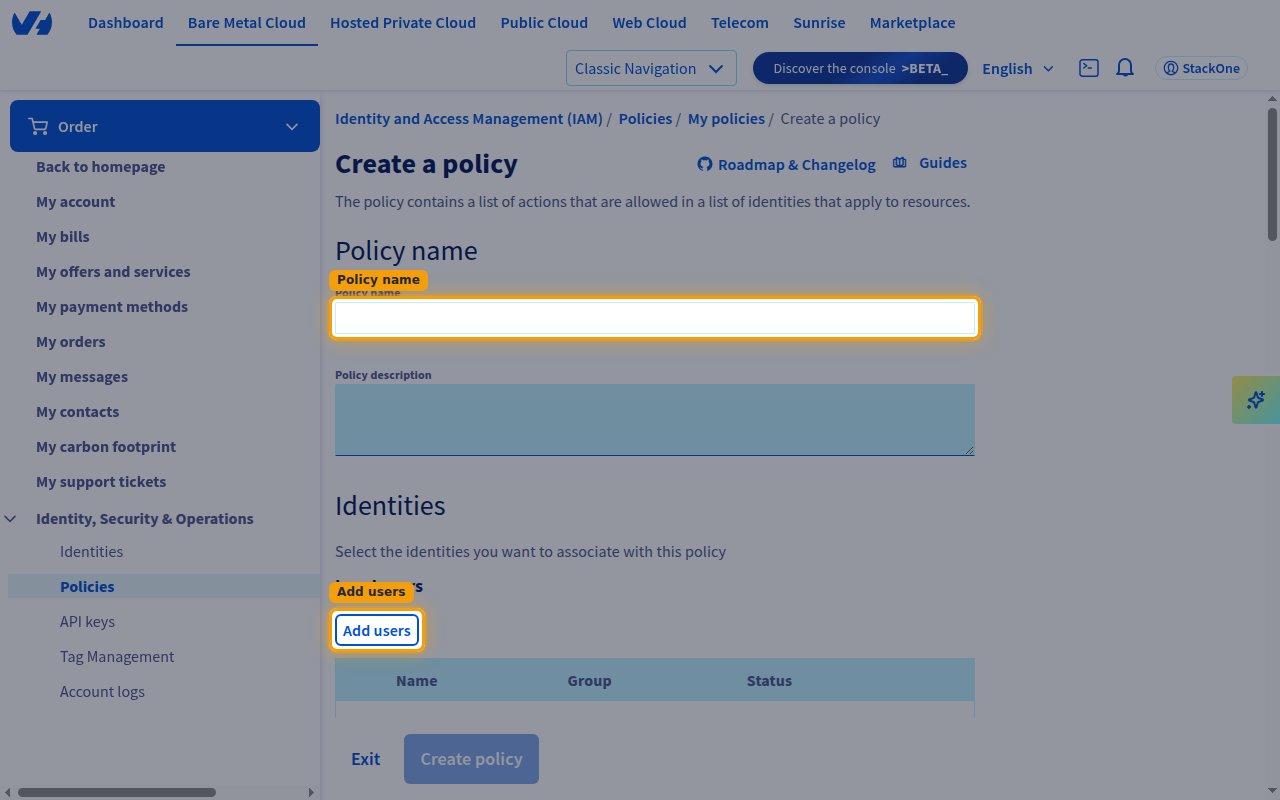
Complete the Create a policy form, then click Create policy.
- Policy name: a name for the policy, such as
stackone-access. - Under Identities, click Add users and select the user you created.
- Under Product types, select the OVHcloud products the connection uses, then add the matching entries under Resources.
- Add the actions the connection needs — read actions for a read-only connection, and write actions only for the operations you want to allow.
Create a Personal Access Token
Create a Personal Access Token for the user. The token inherits the user’s group and policy
permissions.
Open the token list
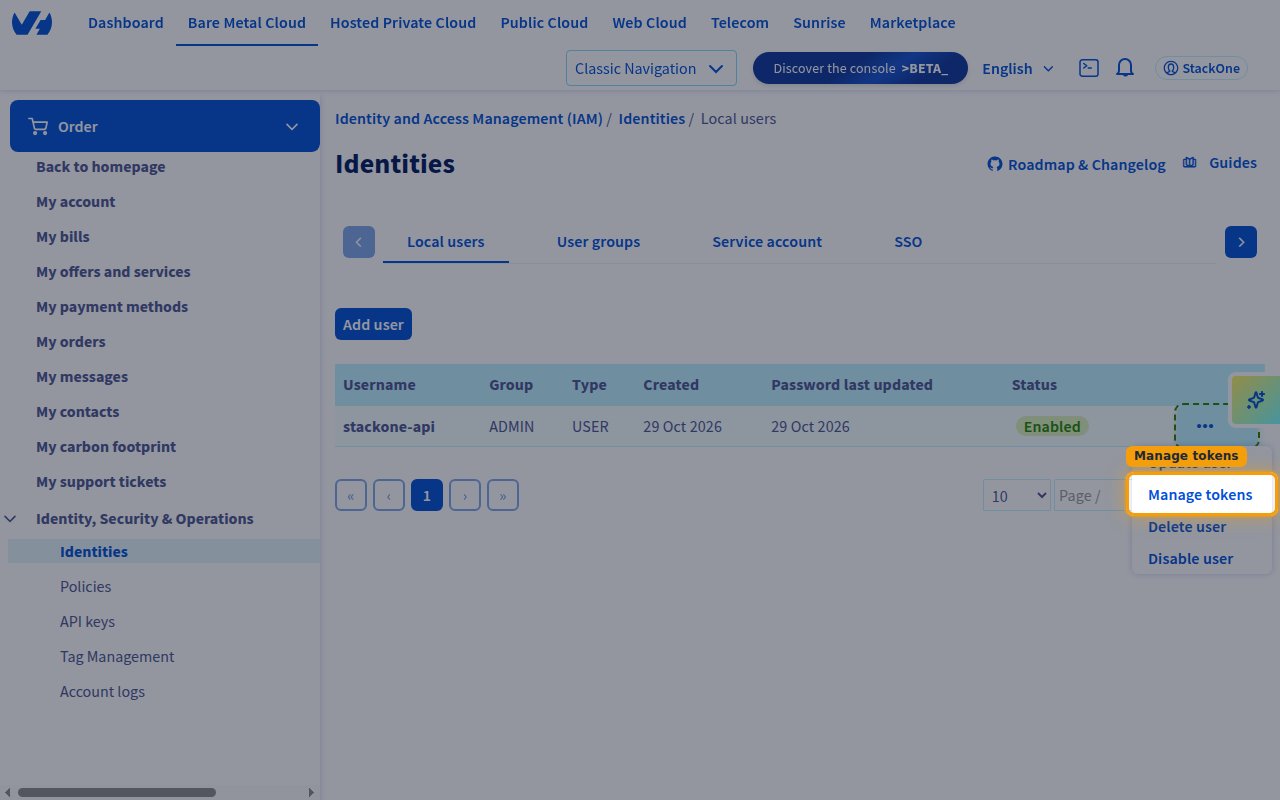
On Local users, click the actions menu at the end of the user’s row, then select Manage tokens.
Add a token
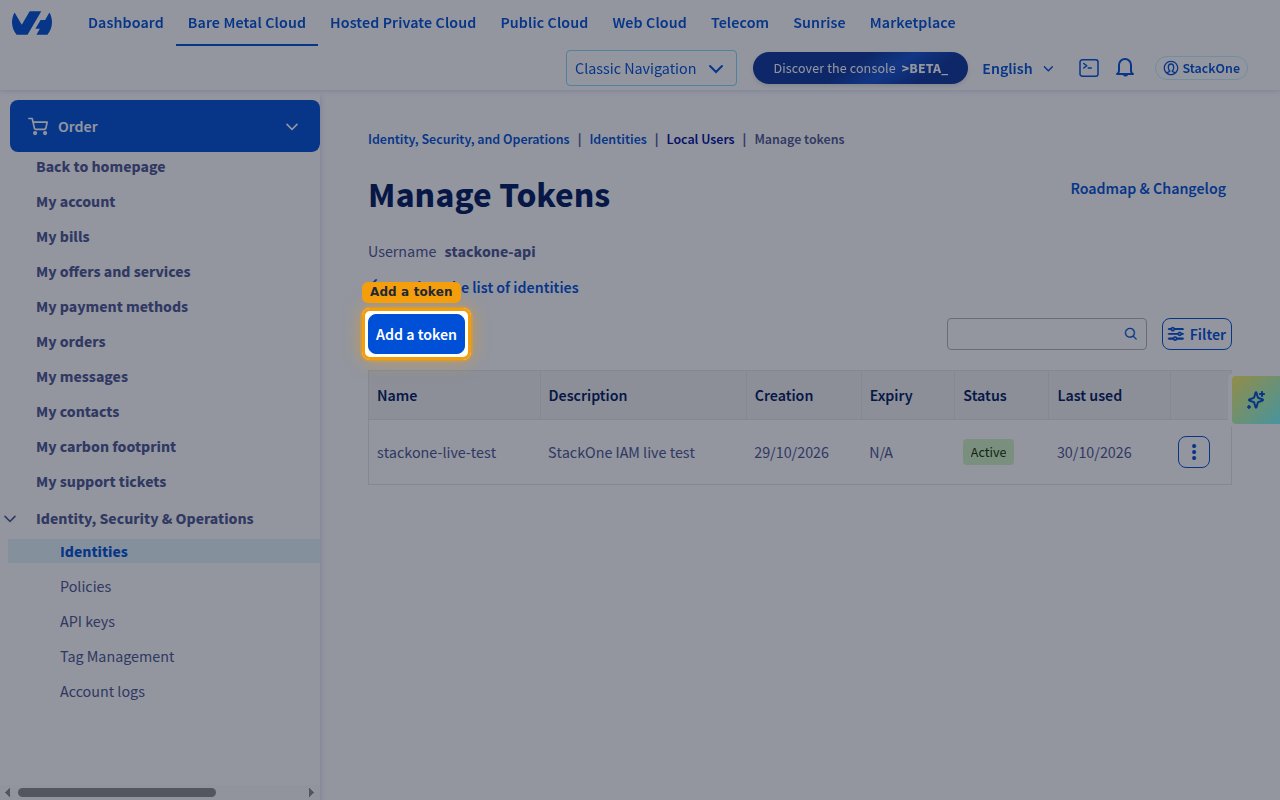
On the Manage Tokens page, click Add a token.
Create and copy the token
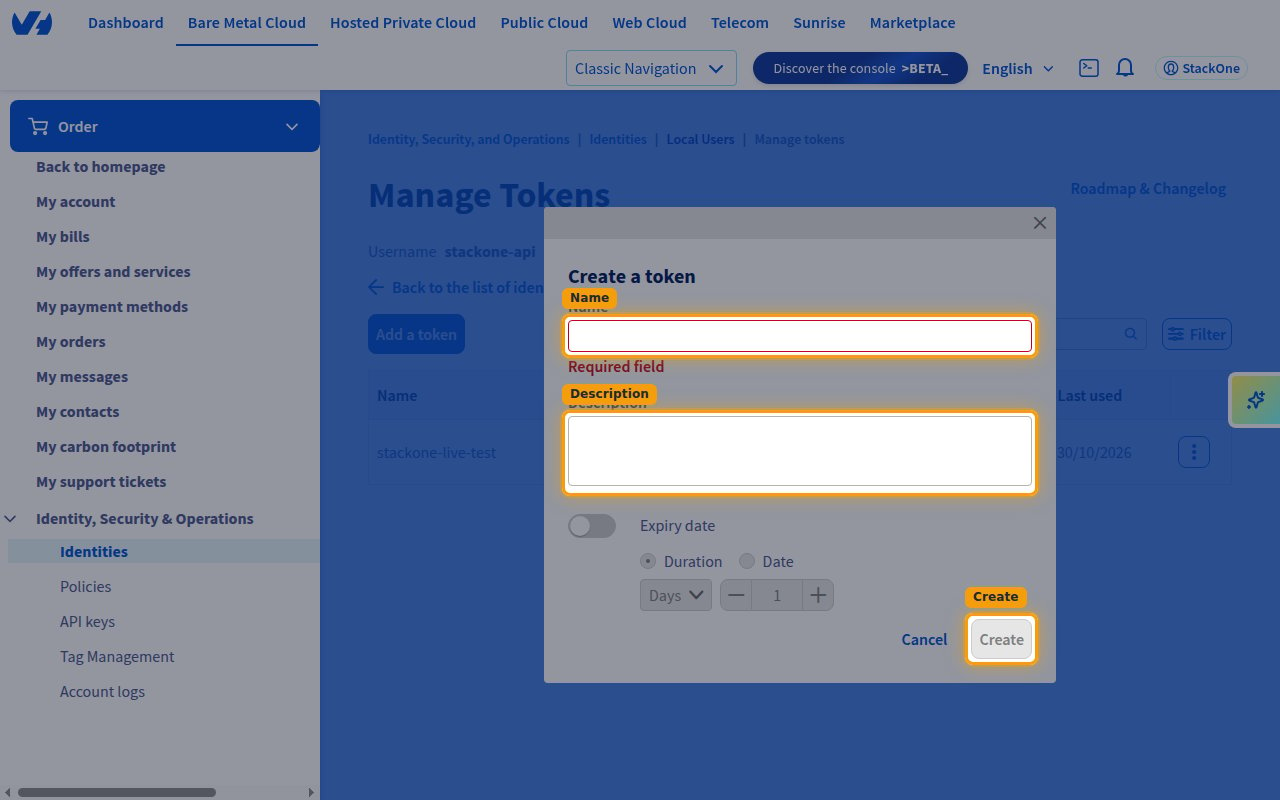
Complete the Create a token dialog, then click Create.
- Name: a name for the token, such as
stackone-access. - Description: an optional note describing how the token is used.
- Expiry date: leave the toggle off for a token that does not expire. Turn it on to set a Duration or a Date, after which the connection fails until you paste a new token.
- Copy the Personal Access Token into StackOne Hub. It is shown only once and cannot be retrieved afterward.
Enter your details in StackOne Hub
Enter the values you collected in StackOne Hub.
- Select your region in the Region field.
- Copy the Personal Access Token across.
Revoke the token
To stop StackOne from accessing your account, delete the token. This blocks further API calls
immediately.
- Navigate to Identity, Security & Operations > Identities > Local users, open the user’s Manage tokens page, click the actions menu at the end of the token’s row, then select Delete.
Link the Account
Connect
- Click Connect.
- If applicable, the provider will redirect you to a sign-in or authorization page. Complete the provider’s authorization flow.
- Once authorization is successful, you will see a confirmation popup.
Use Actions