

Register an application in Microsoft Entra ID
An app registration in Microsoft Entra ID holds the credentials and application permissions for the integration.
1
Create the app registration
Sign in to the Microsoft Entra admin center.
- If you have access to multiple tenants, click the Settings (gear) icon in the top-right corner.
- Select the desired tenant from the list under Directory + subscription.
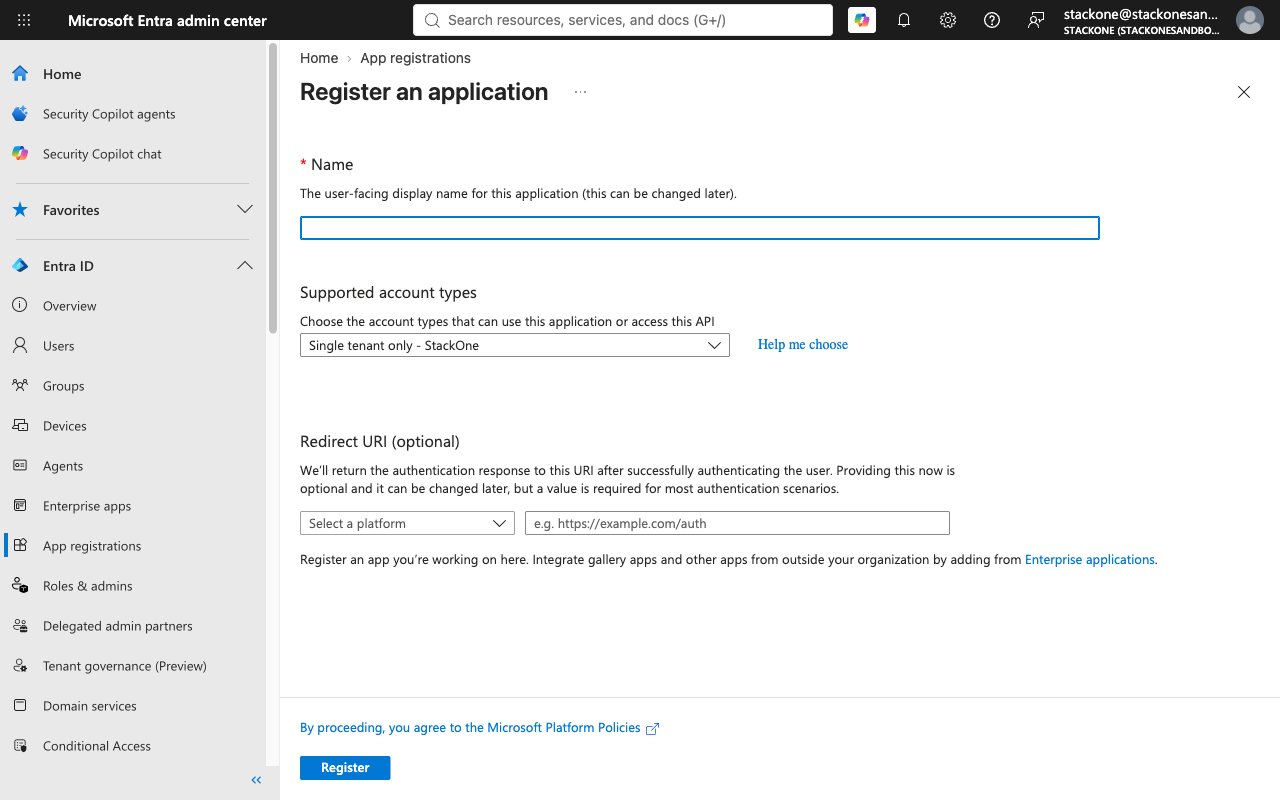
- Open Entra ID > App registrations.
- Click New registration.
- Name: A name that identifies this integration
- Supported account types: Accounts in this organizational directory only for single-tenant access
- Click Register.
2
Copy the Client ID and Tenant ID
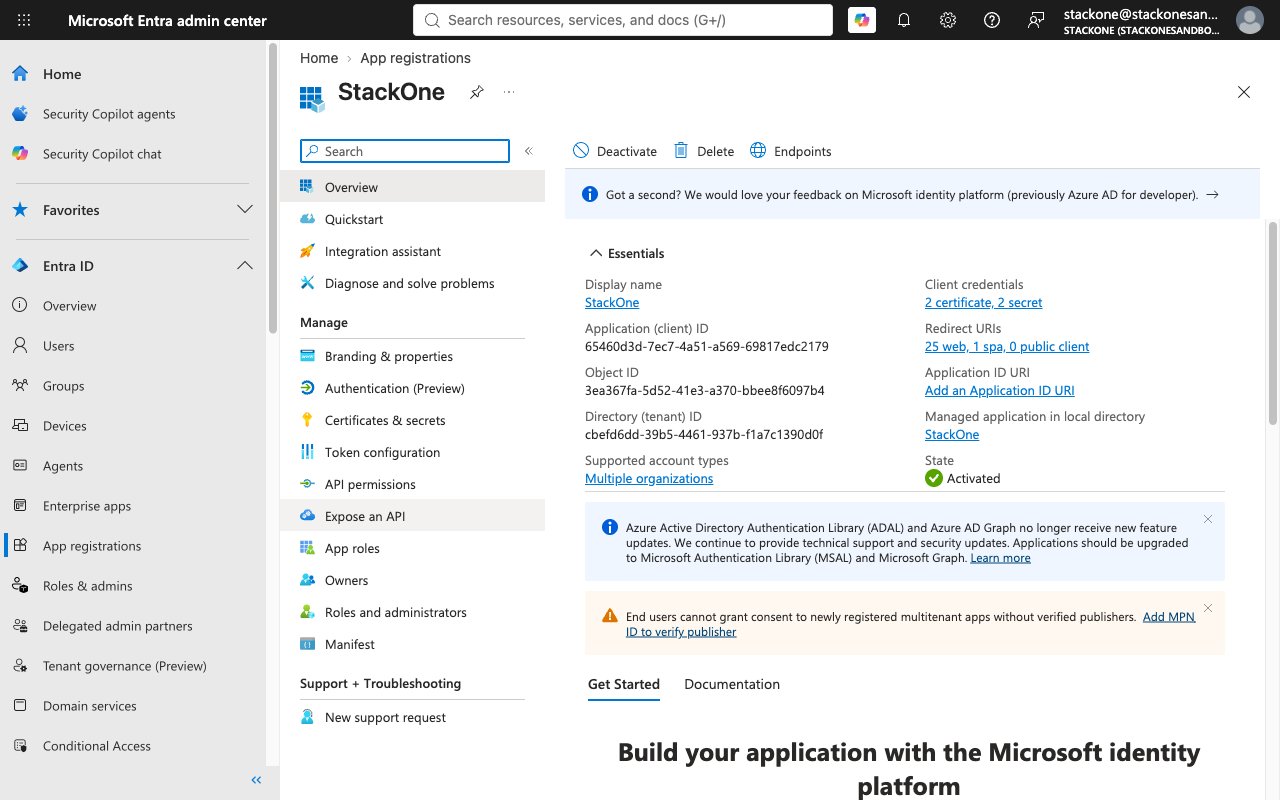
The app’s Overview page opens after registration. Its Essentials section lists both values.
- Copy the Application (client) ID across to Client ID.
- Copy the Directory (tenant) ID across to Tenant ID.
3
Add the application permissions
Enables actions: Assign Device Compliance Policy, Assign Device Configuration, Assign Mobile App, Bypass Activation Lock, Clean Windows Device, Create Role Definition, Delete Device Compliance Policy, Delete Device Configuration, Delete Managed Device, Delete Role Definition, Disable Lost Mode, Get Detected App, Get Device Category, Get Device Compliance Policy, Get Device Configuration, Get Device Enrollment Configuration, Get Managed Device, Get Mobile App, Get Mobile App Category, Get Role Definition, List Detected App Managed Devices, List Detected Apps, List Device Compliance Policies, List Device Configurations, List Device Enrollment Configurations, List Managed Devices, List Mobile App Categories, List Mobile Apps, List Role Assignments, List Role Definitions, Locate Device, Reboot Device, Remote Lock, Reset Passcode, Retire Managed Device, Shut Down Device, Sync Device, Update Role Definition, Windows Defender Scan, Windows Defender Update Signatures, Wipe Managed Device
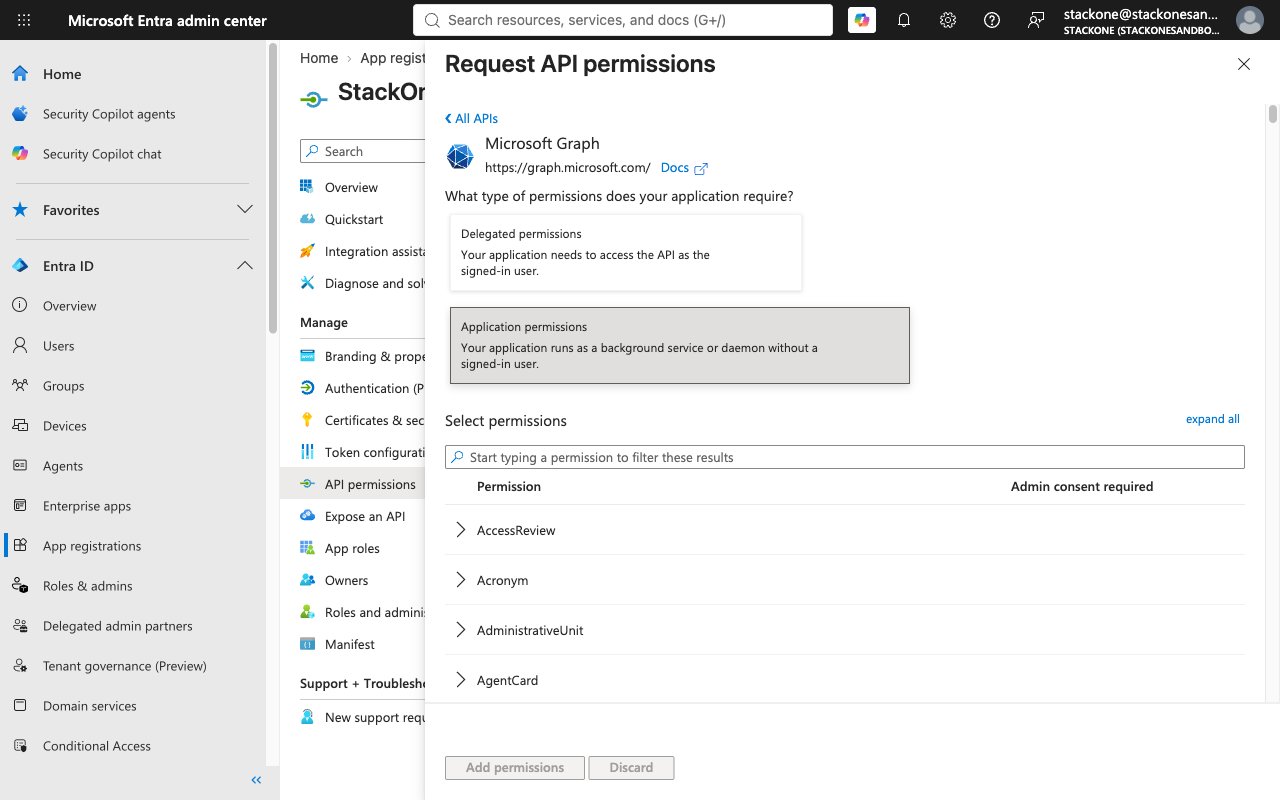
From the left menu under Manage, select API permissions.
- Click Add a permission.
- Select Microsoft Graph.
- Select Application permissions.
- Expand each category that starts with DeviceManagement and select each permission listed.
- Click Add permissions.
4
Grant admin consent
On the API permissions page, grant consent on behalf of the organization.
- Click Grant admin consent for [tenant name].
- Select Yes.
- Verify that the Status column shows a green checkmark for each permission.
5
Create the client secret
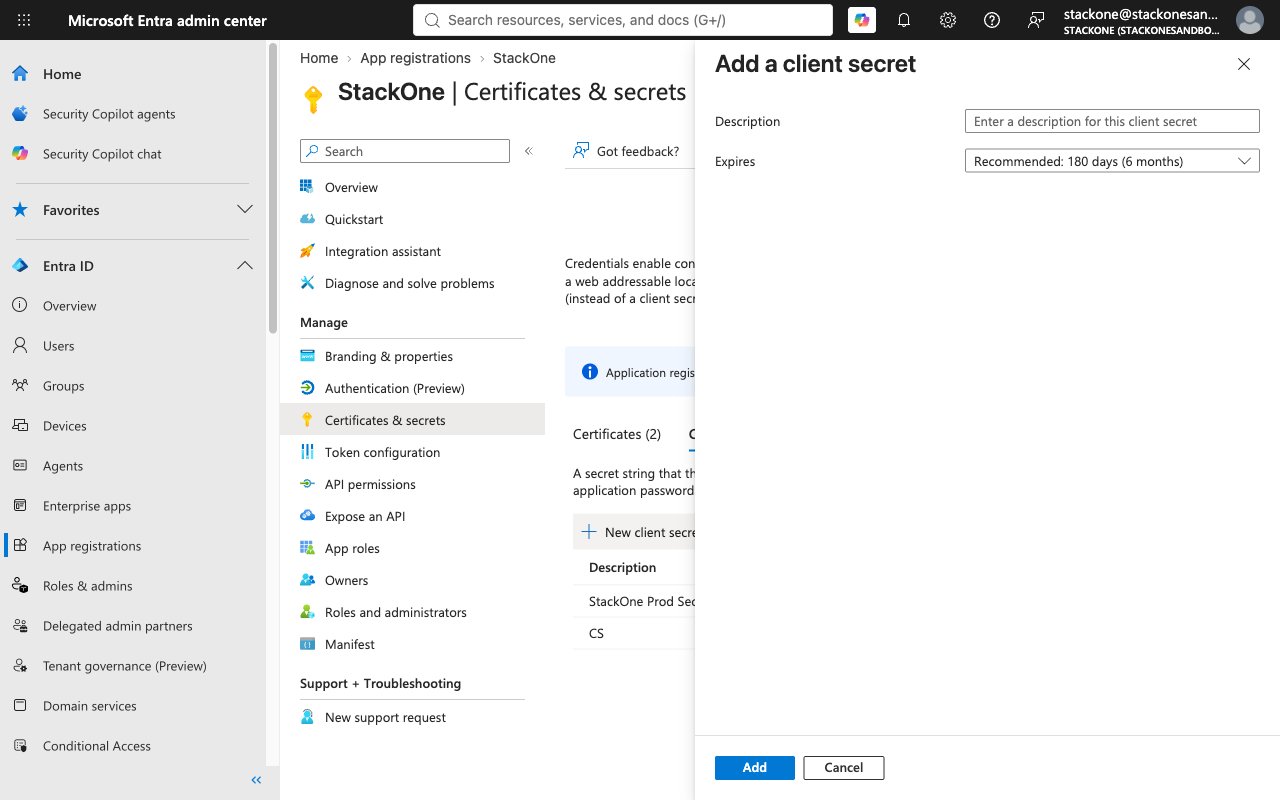
From the left menu under Manage, select Certificates & secrets.
- Under the Client secrets tab, click New client secret.
- Description: What the secret is used for
- Expires: How long the secret stays valid
- Click Add.
6
Copy the Client Secret
The Value of the new client secret is shown only once.
- Copy the Value across to Client Secret.
Link the Account
1
Connect
- Click Connect.
- If applicable, the provider will redirect you to a sign-in or authorization page. Complete the provider’s authorization flow.
- Once authorization is successful, you will see a confirmation popup.
2
Use Actions
Connect an AI platform to the linked account’s actions. See AI Platforms.Other ways to call actions are listed in Protocols & SDKs.