

Register an application in Microsoft Entra ID
An app registration in Microsoft Entra ID holds the credentials and delegated permissions for the integration. API access is controlled by the permissions granted to the app and by the Intune role assigned to the signing-in user.
Create the app registration
Sign in to the Microsoft Entra admin center.
- If you have access to multiple tenants, click the Settings (gear) icon in the top-right corner.
- Select the desired tenant from the list under Directory + subscription.
- Open Entra ID > App registrations.
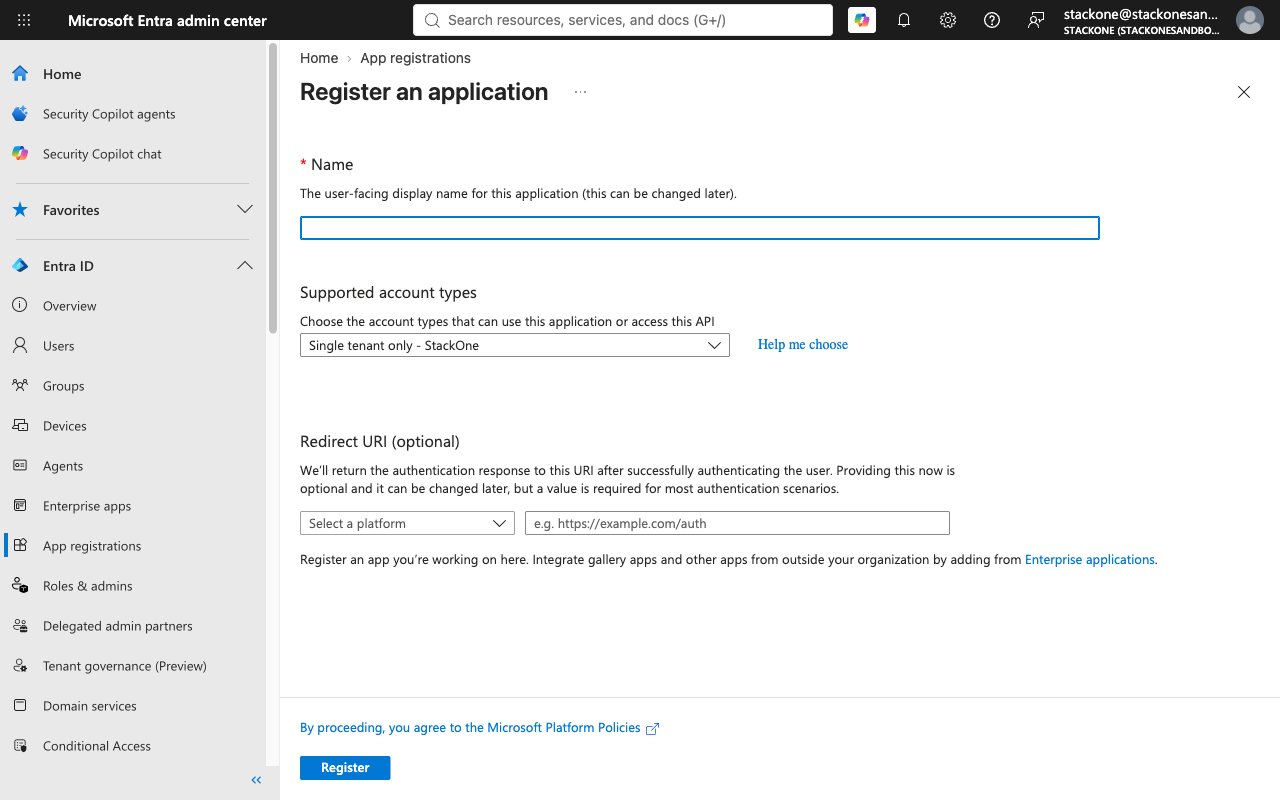
- Click New registration.
- Name: A name that identifies this integration
- Supported account types: Accounts in this organizational directory only for single-tenant access
- Redirect URI (optional): select Web, then enter the Callback URL from your Connector Profile
- Click Register.
Copy the Client ID
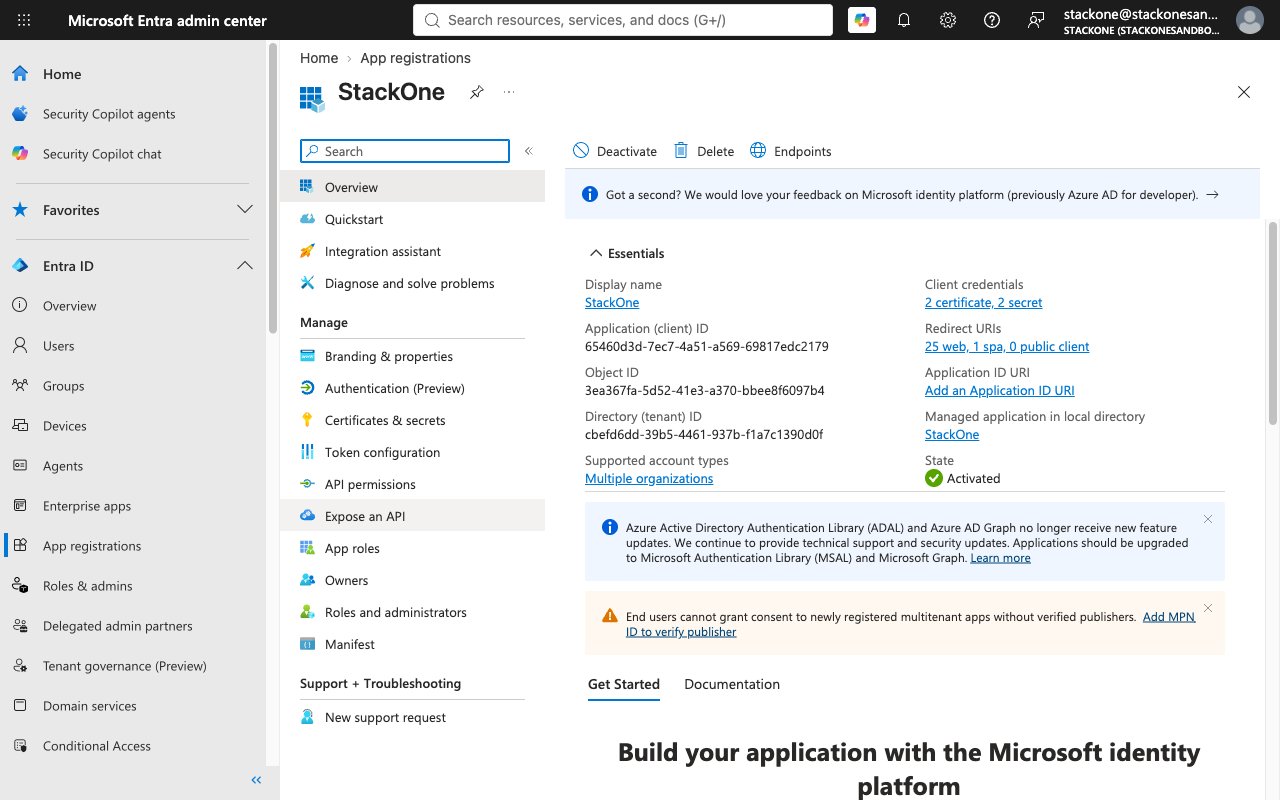
The app’s Overview page opens after registration. Its Essentials section lists the Application (client) ID.
- Copy the Application (client) ID to Client ID in your Connector Profile.
Add the delegated permissions
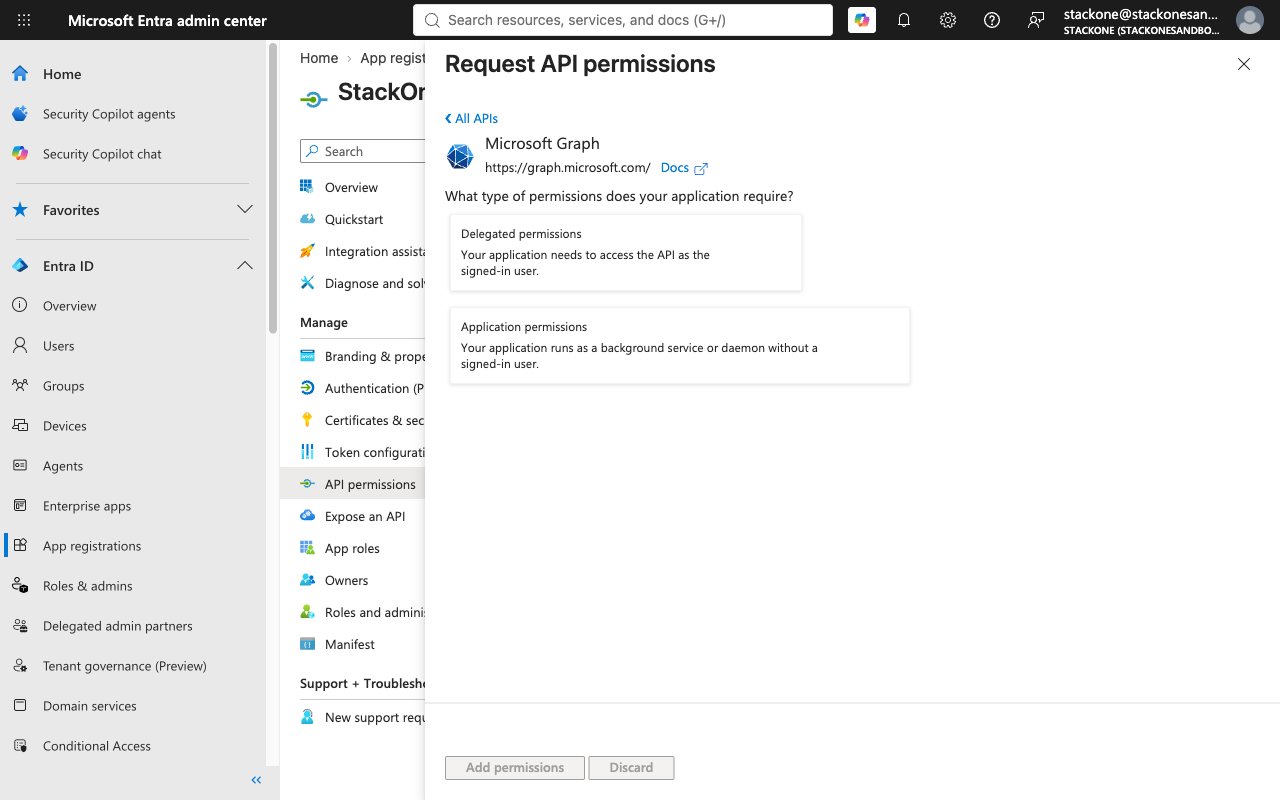
From the left menu under Manage, select API permissions.
- Click Add a permission.
- Select Microsoft Graph.
- Select Delegated permissions.
- Expand each category that starts with DeviceManagement and select each permission listed.
- Click Add permissions.
Grant admin consent
On the API permissions page, grant consent on behalf of the organization.
- Click Grant admin consent for [tenant name].
- Select Yes.
- Verify that the Status column shows a green checkmark for each permission.
Create the client secret
From the left menu under Manage, select Certificates & secrets.
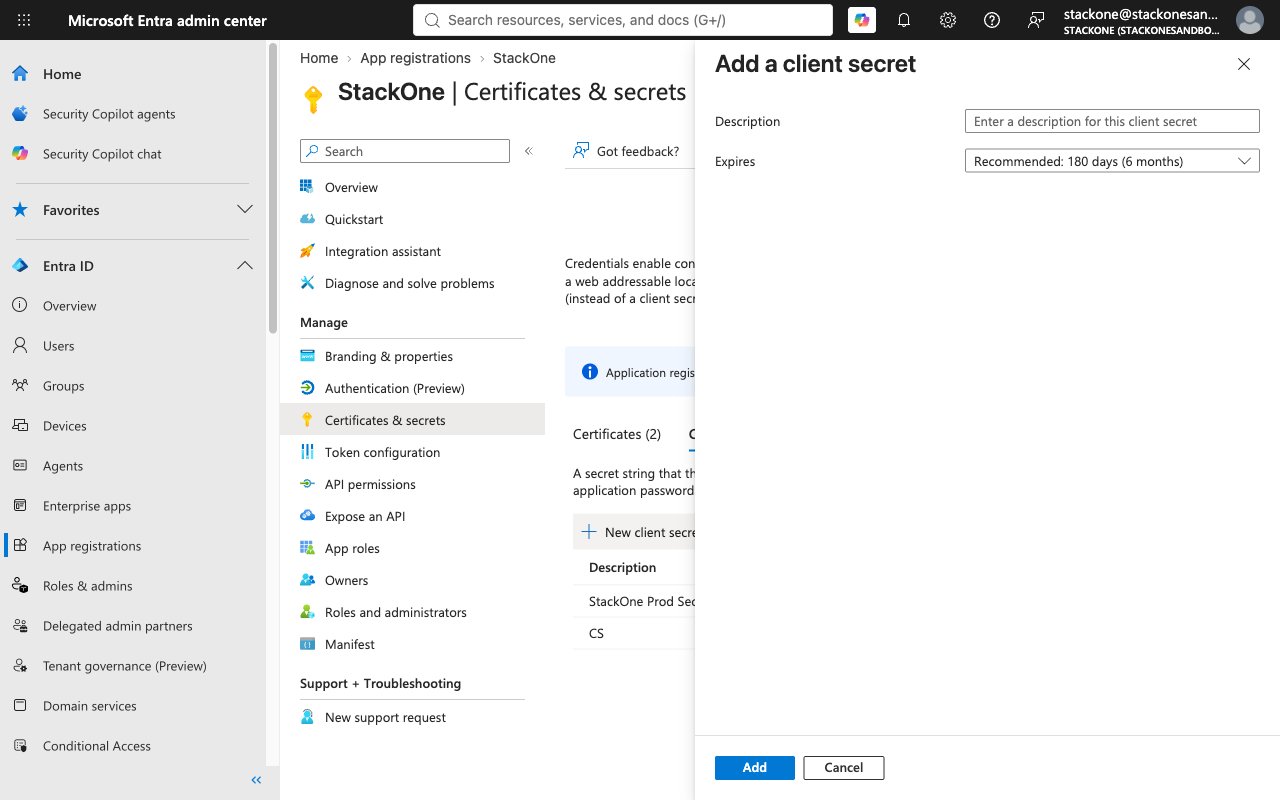
- Under the Client secrets tab, click New client secret.
- Description: What the secret is used for
- Expires: How long the secret stays valid
- Click Add.
Copy the Client Secret
The Value of the new client secret is shown only once.
- Copy the Value to Client Secret in your Connector Profile.
Find your tenant ID (single-tenant apps only)
Your tenant ID identifies your Microsoft Entra directory.
Copy the Directory (tenant) ID
Sign in to the Microsoft Entra admin center, then open Entra ID > App registrations.
- Select your app registration.
- Open the Overview page.
- Copy the Directory (tenant) ID from the Essentials section across to Tenant ID.
Create the StackOne Connector Profile
Create a Connector Profile
Link an Account