

Create the OAuth client
An OAuth client belongs to your tailnet, not to a person. It keeps working after its creator leaves the tailnet, and the access tokens it creates last one hour and renew automatically.
Sign in to Tailscale
Sign in to your Tailscale admin console.
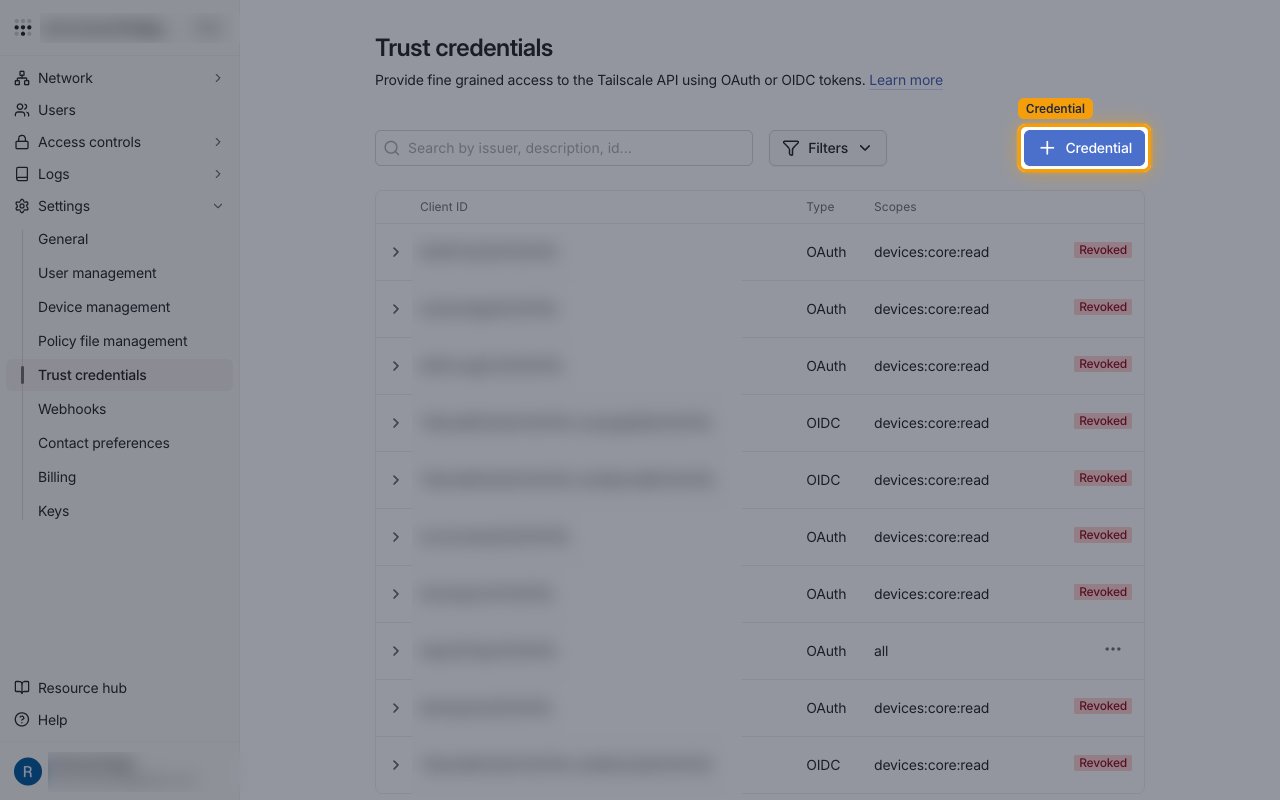
- Open the Trust credentials page under Settings.
- Select Credential.
Choose OAuth
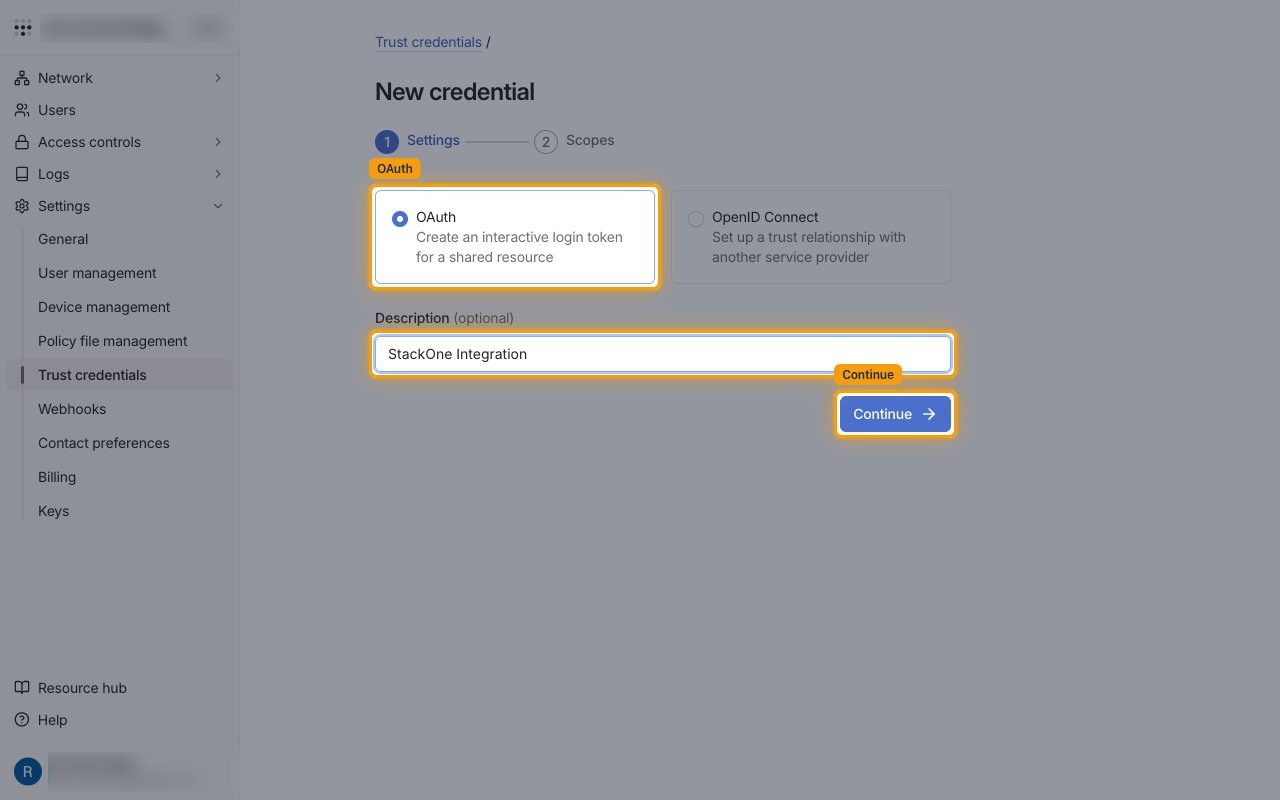
On the New credential page, select OAuth. In Description, enter a name you will recognize, such as StackOne Integration, then select Continue.
Choose the scopes
The Scopes step decides what the connection can read and change.
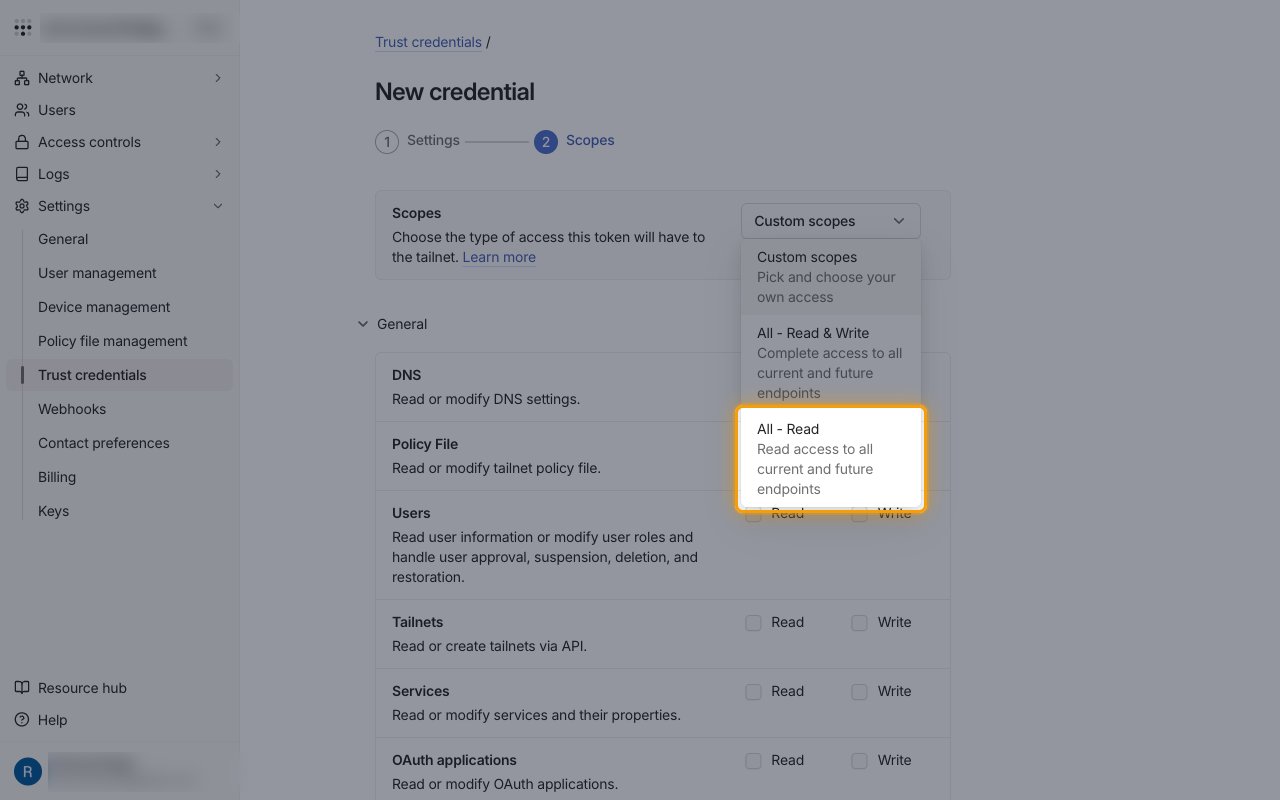
Select All - Read
Open the Scopes list and select All - Read.
- The connection test lists users, groups and pending invitations. Tailscale names no scope for pending invitations, so the client needs read access to the whole tailnet.
- All - Read cannot change anything. It reads users, devices, DNS, the policy file, logs, webhooks, settings and every access token in the tailnet, plus any read API Tailscale adds later.
Add write scopes you need
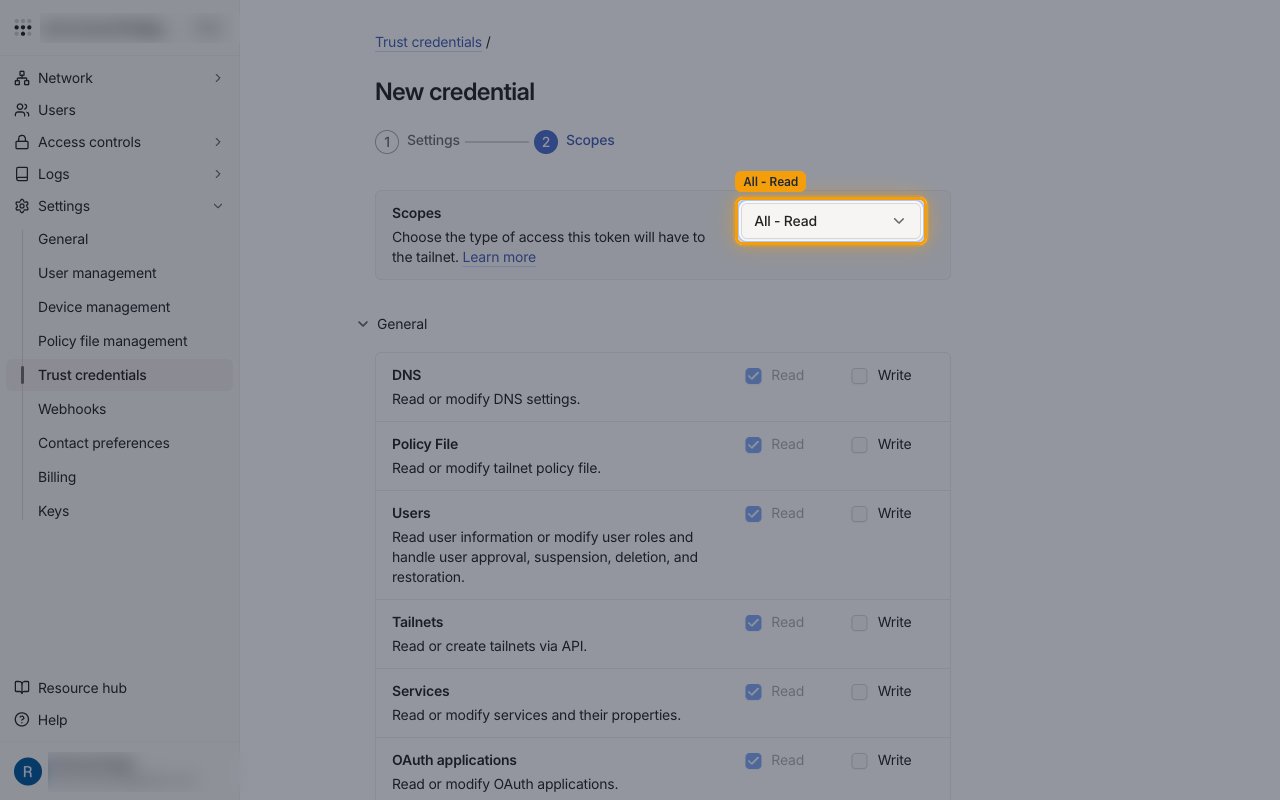
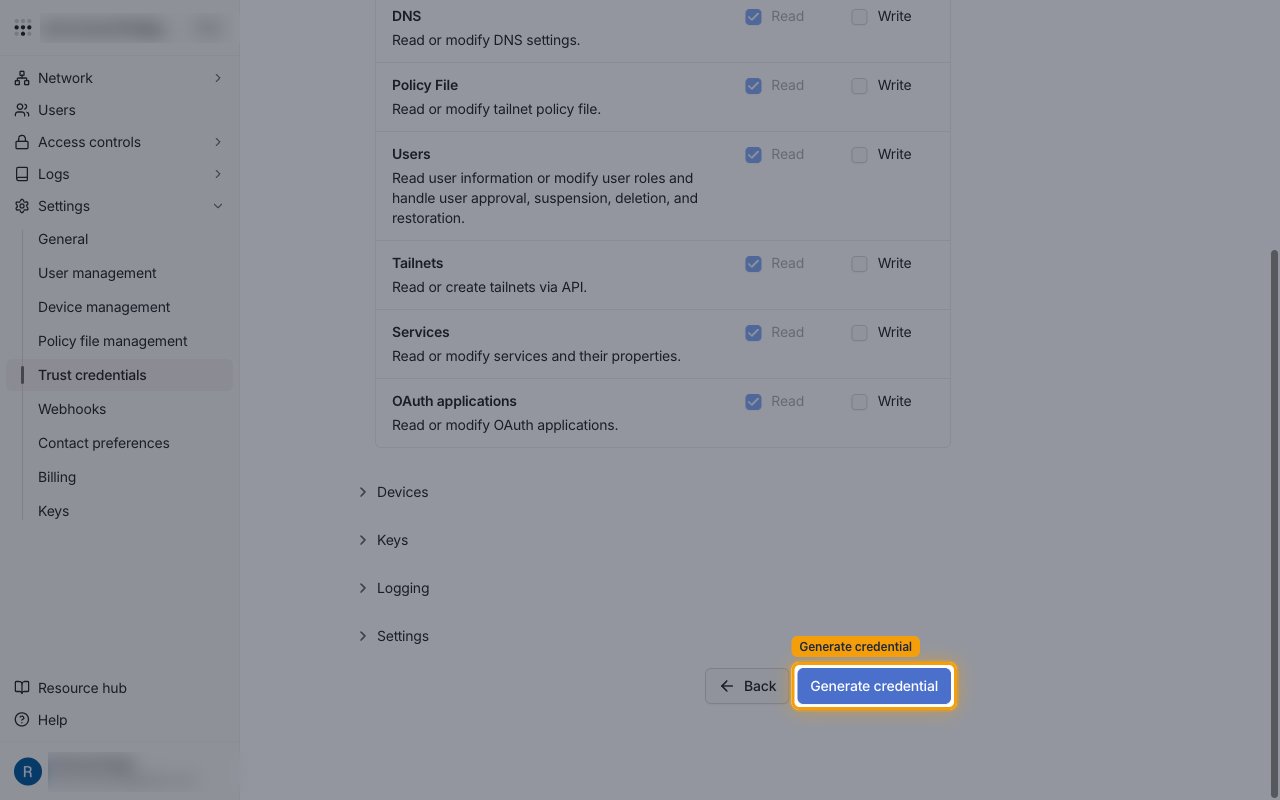
With All - Read selected, every Read box is ticked and locked, and each Write box stays available. Tick Write only for the actions you use.
- Users under General, to suspend, restore, approve, delete or change the role of users.
- Core under Devices, to authorize, tag or remove devices.
- DNS and Policy File under General, to change DNS or replace the policy file.
- Webhooks under Keys, so StackOne can create the webhook for event subscriptions.
- Leave every Write box clear to keep the connection read-only.
Generate the credential
Select Generate credential.
Copy the client ID and secret
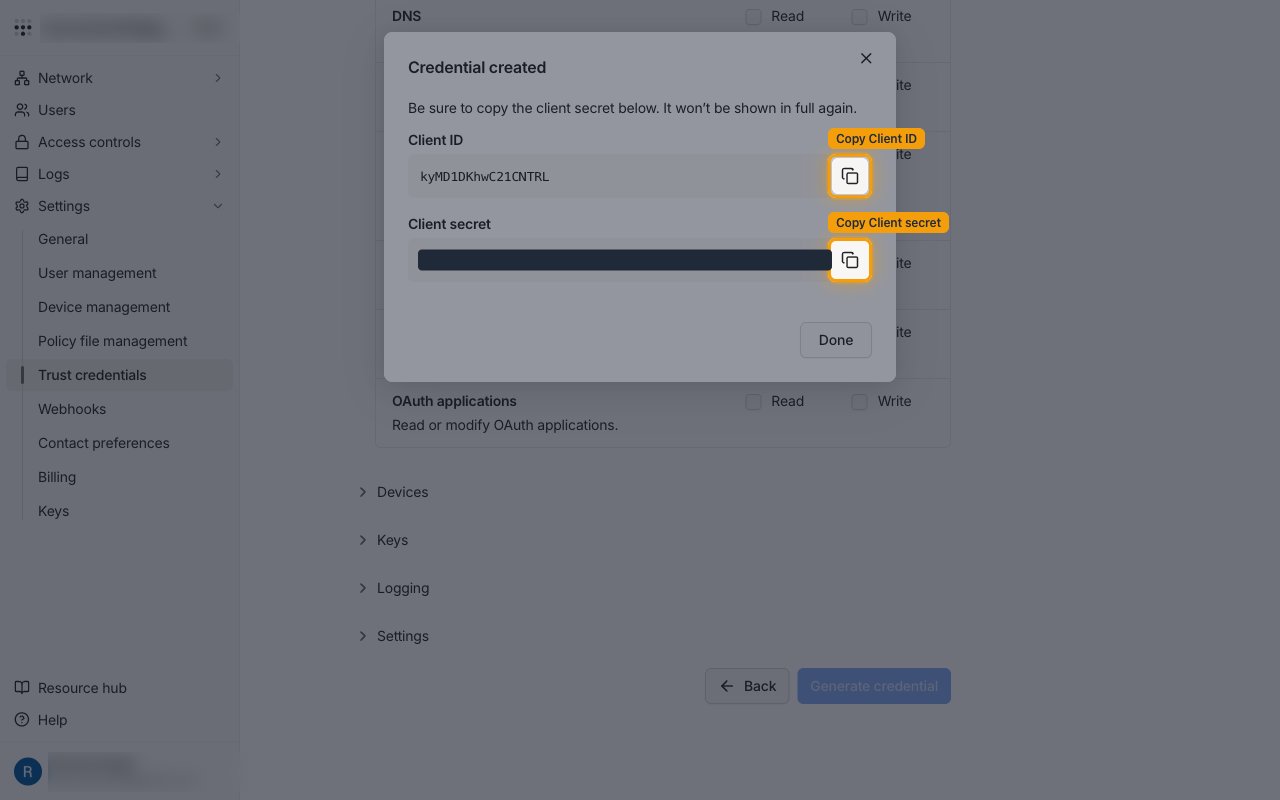
The Credential created dialog shows both values StackOne needs.
Copy both values
Copy the Client ID and the Client secret with the copy buttons, store them securely for use later, then select Done.
- The client secret is only displayed once and cannot be retrieved later. If you lose it, create a new credential.
- The client secret starts with
tskey-client-and is case-sensitive. - Paste the Client ID into the OAuth Client ID field and the Client secret into the OAuth Client Secret field in StackOne Hub.
Revoke the OAuth client
Tailscale OAuth clients do not expire. The client works until you revoke it.
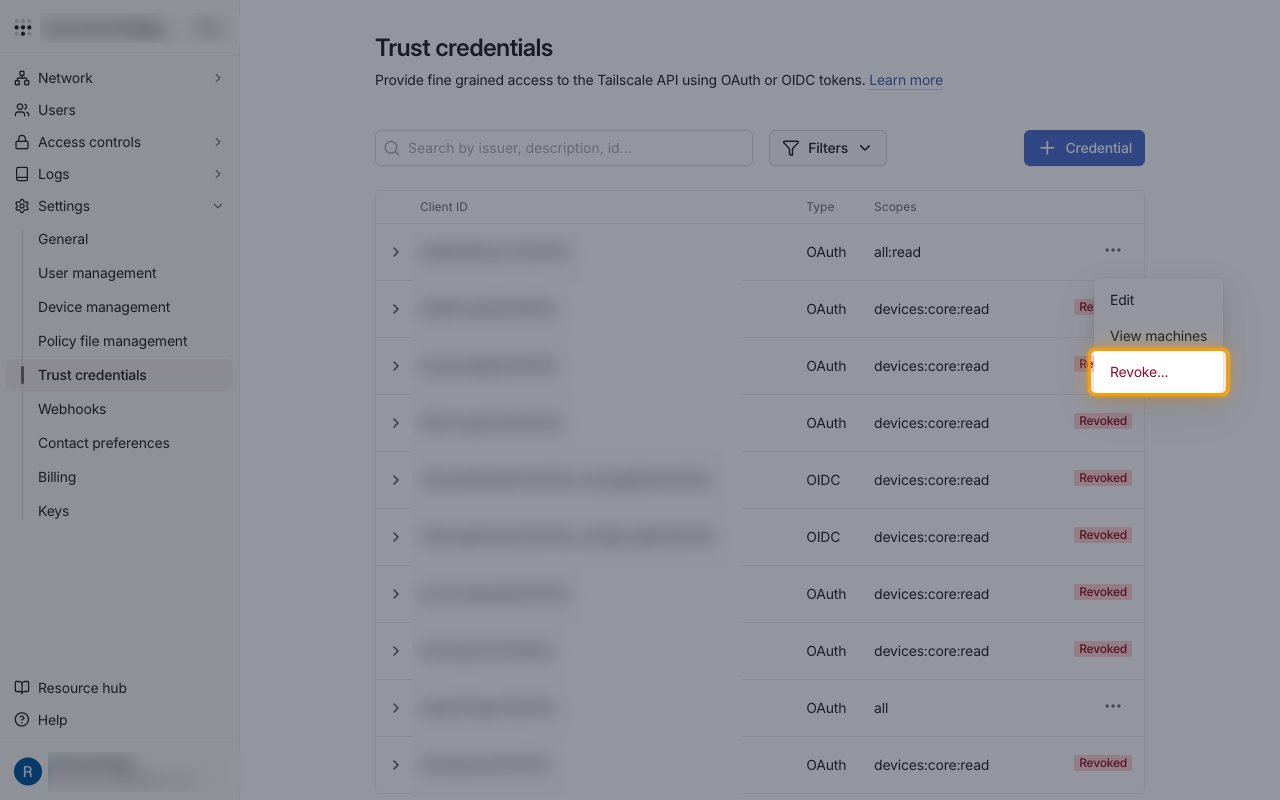
Open the credential menu
On the Trust credentials page, open the menu at the end of the credential’s row and select Revoke….
Confirm the revocation
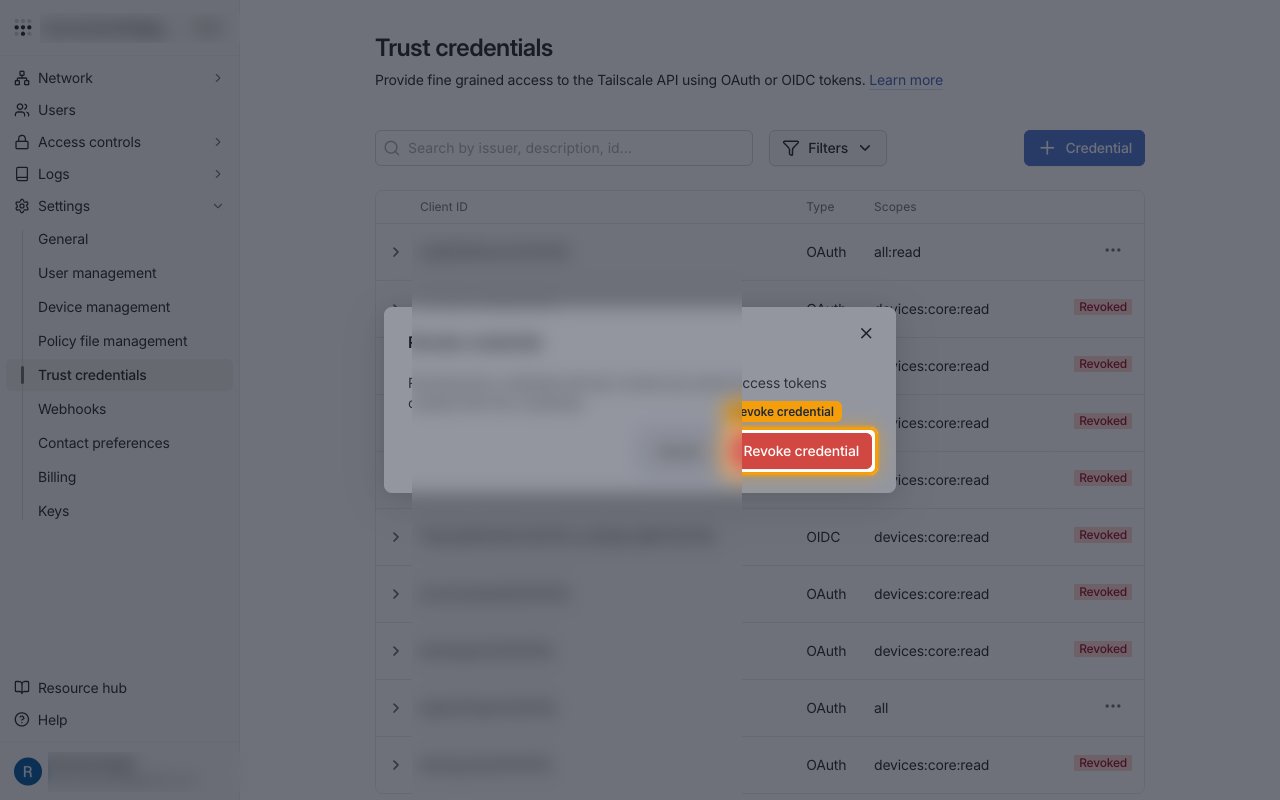
Select Revoke credential.
- Revoking the credential also revokes any active access tokens created with it, and the connection stops working until you paste a new client ID and secret into StackOne Hub.
Link the Account
Connect
- Click Connect.
- If applicable, the provider will redirect you to a sign-in or authorization page. Complete the provider’s authorization flow.
- Once authorization is successful, you will see a confirmation popup.
Use Actions
Next Steps
Webhooks setup
Configure receiving Events for Tailscale into StackOne.