

Sign in to Salesforce
Sign in to the Salesforce org that owns your Account Engagement business unit.
- Production — Salesforce login
- Developer — Salesforce login
- Sandbox — Salesforce sandbox login
- Create the app in the same environment you will connect — credentials differ per environment.
Create an External Client App
Register the Salesforce External Client App that StackOne uses to authenticate with Account Engagement.
Open the new External Client App form
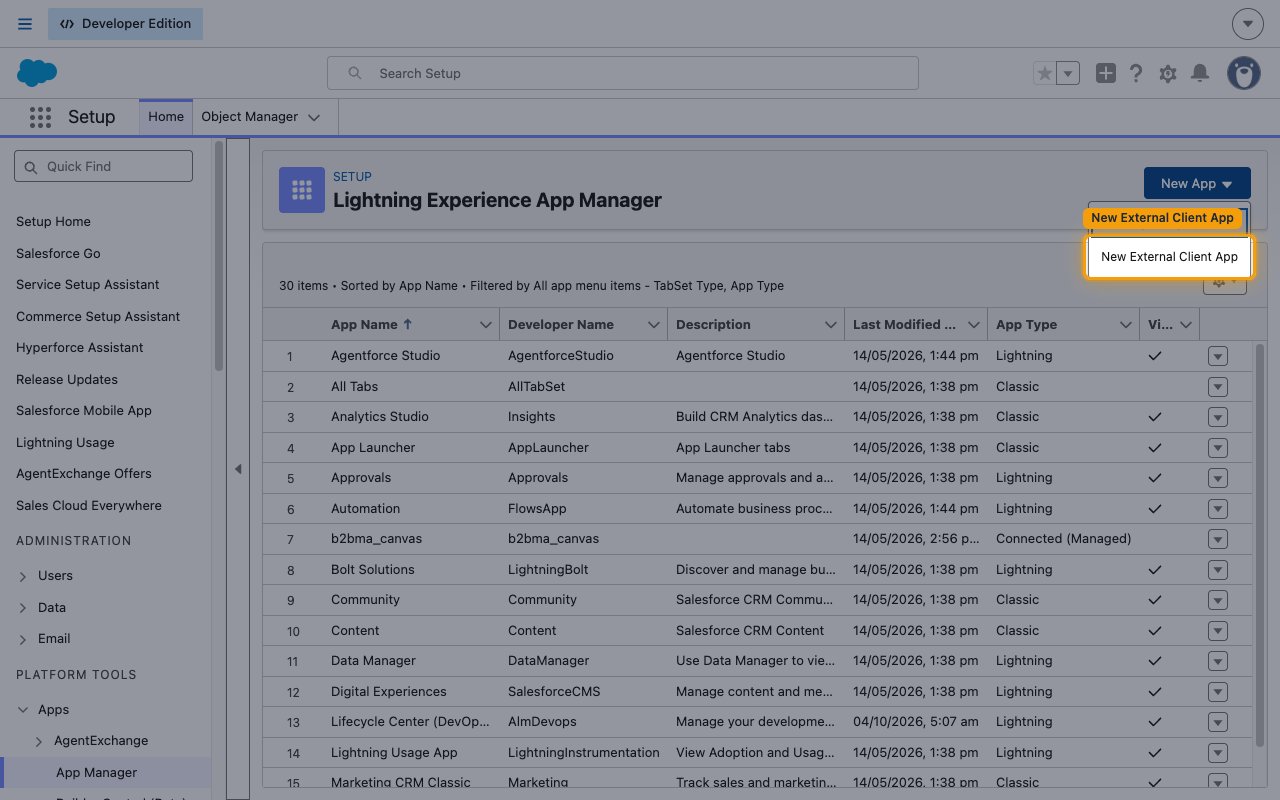
In Salesforce Setup, navigate to Platform Tools > Apps > App Manager.
- Click New App in the top-right corner, then choose New External Client App.
Fill in basic information
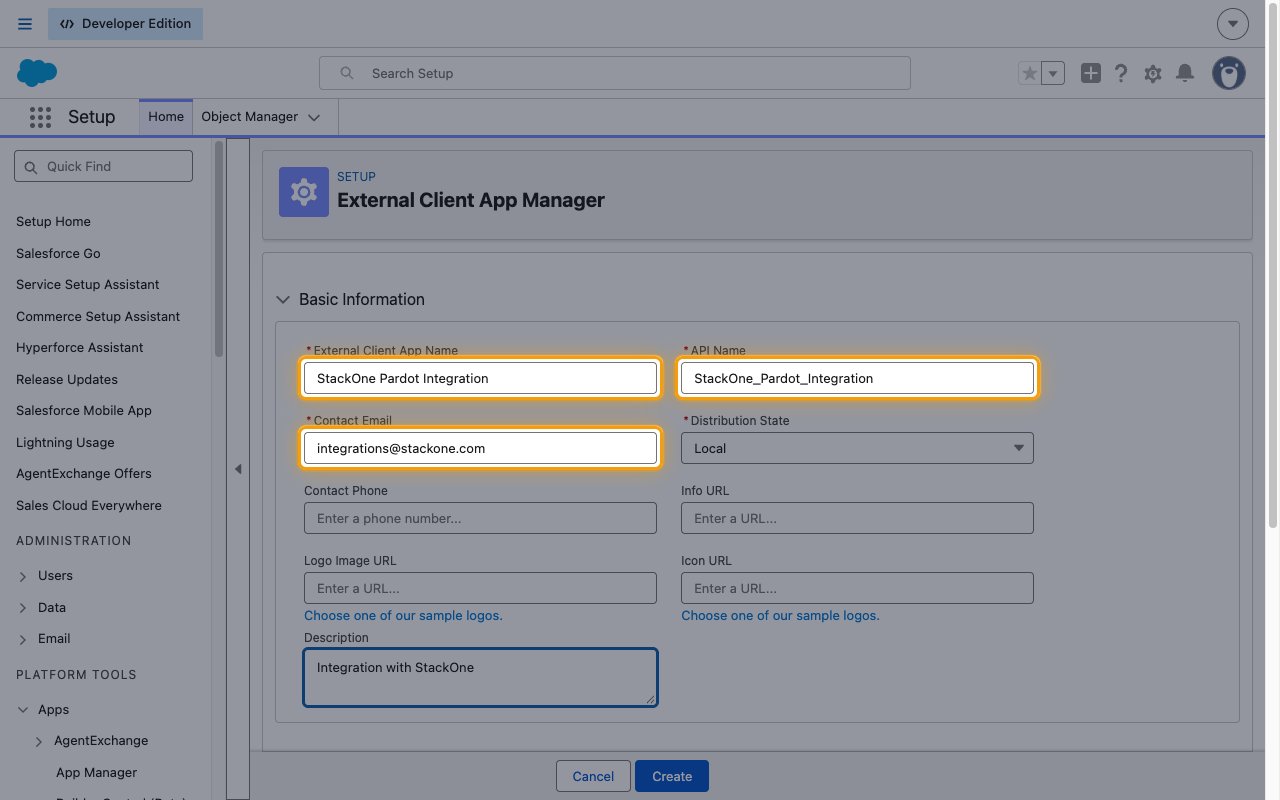
Complete the Basic Information section.
- External Client App Name:
StackOne Pardot Integration - API Name: fills in automatically from the External Client App Name
- Contact Email: an address your team monitors
- Leave Distribution State set to Local.
Enable OAuth and set the callback URL
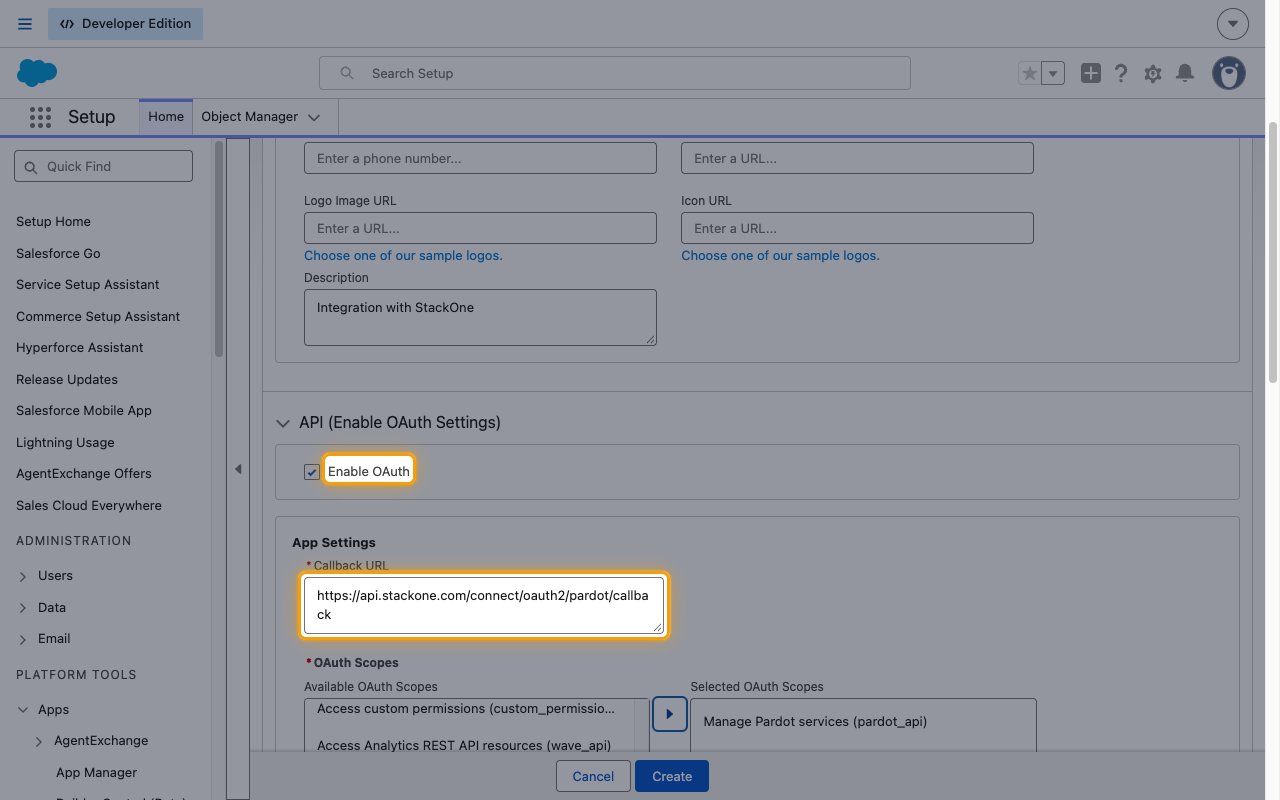
Expand API (Enable OAuth Settings) and select the Enable OAuth checkbox to reveal the App Settings fields.
- Callback URL: copy it from your Connector Profile
Select OAuth scopes
In OAuth Scopes, select each scope in Available OAuth Scopes and click the right-arrow button to move it to Selected OAuth Scopes.
Review the enforced security settings
Salesforce applies several settings in the Security section that an admin cannot change. Each is marked “To change this required setting, contact Support.”
- Require Proof Key for Code Exchange (PKCE) extension for Supported Authorization Flows is selected. StackOne sends PKCE, so no action is needed.
- Enable Refresh Token Rotation is selected. Salesforce issues a new refresh token on every refresh.
- Limit Idle Refresh Token Time-To-Live (TTL) to 30 Days is selected. A connection that sits idle longer than 30 days must be reauthorized.
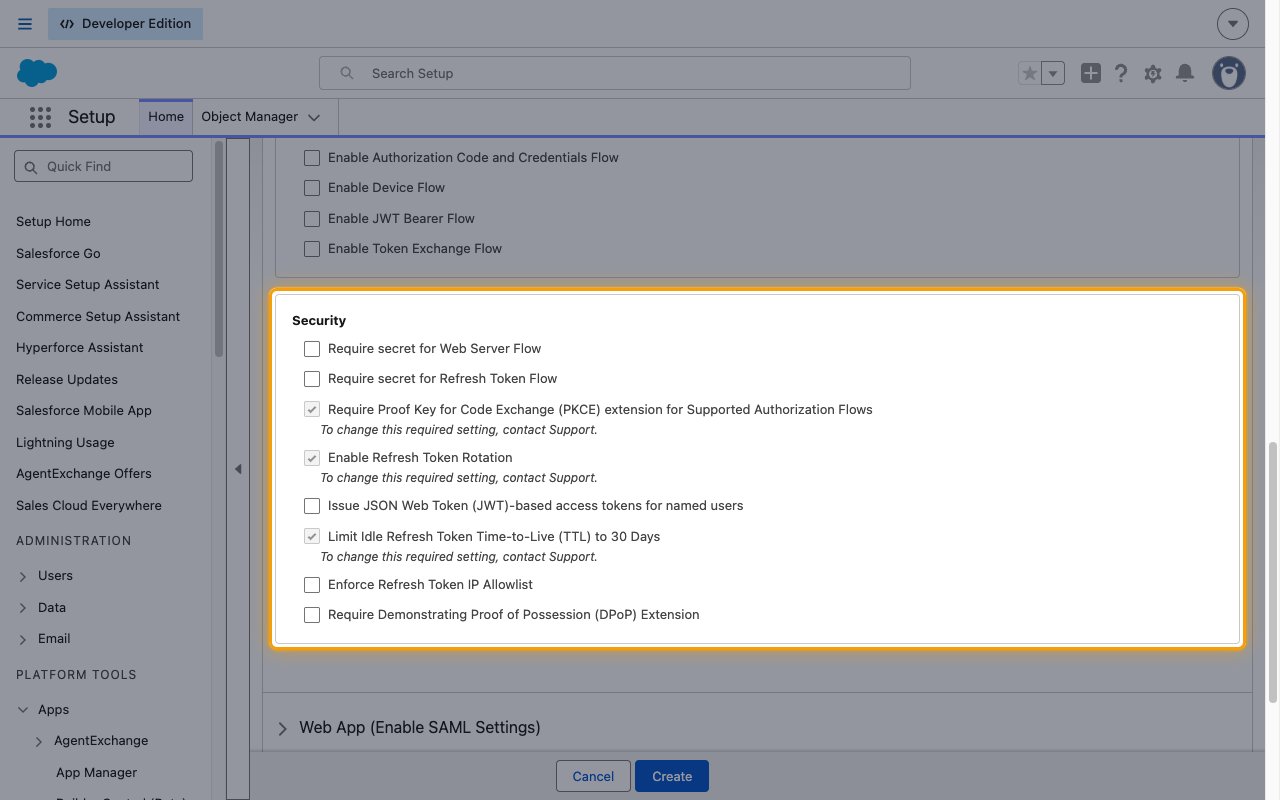
Create the External Client App
Click Create. The OAuth settings can take 2-10 minutes to propagate before the app accepts authorization requests.
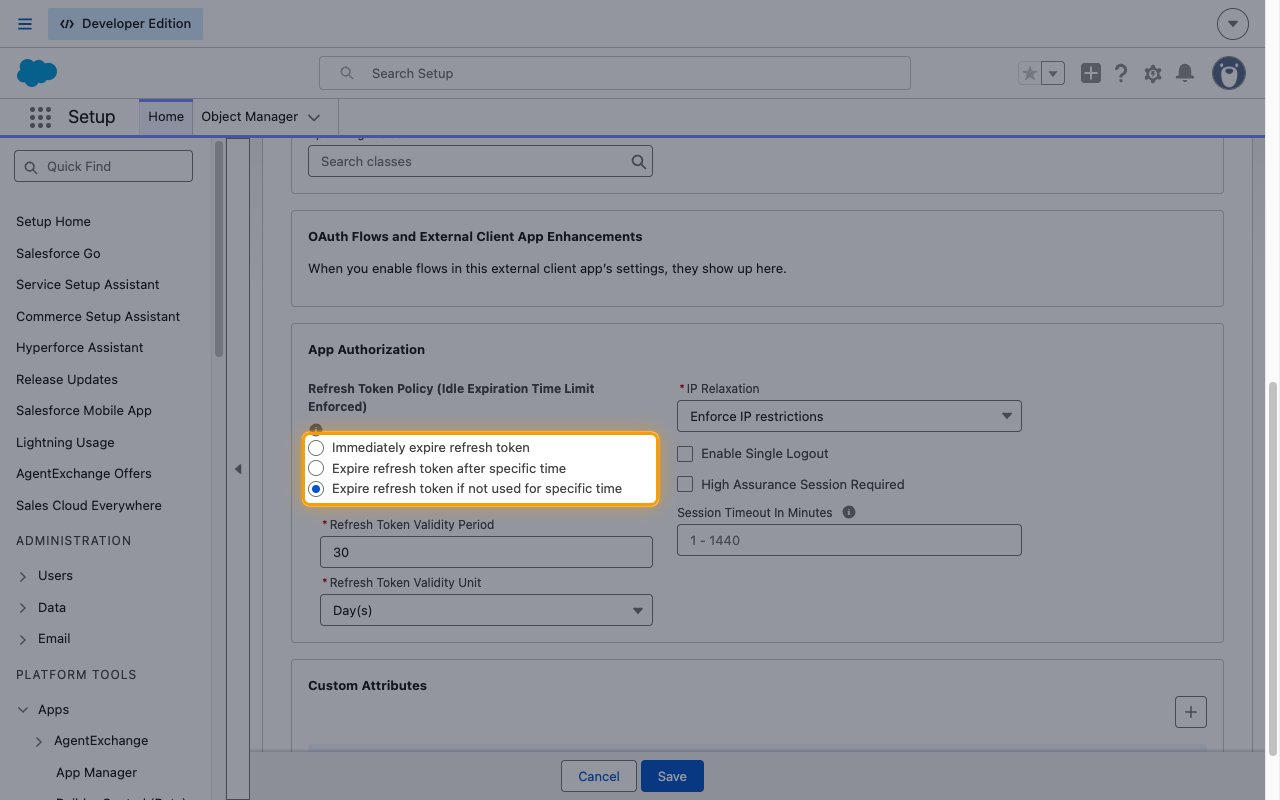
Set the Refresh Token Policy
The refresh token policy controls how long a connected account stays authorized. Salesforce enforces an idle expiration on External Client Apps, so the policy cannot be set to never expire.
Open the policy editor
Open the app from Platform Tools > Apps > External Client Apps > External Client App Manager, then go to the Policies tab and click Edit.
Choose a refresh token policy
In the App Authorization section, choose an option under Refresh Token Policy (Idle Expiration Time Limit Enforced).
- Expire refresh token if not used for specific time is the default. Set Refresh Token Validity Period and Refresh Token Validity Unit to the longest idle window your use case allows. StackOne refreshes the token on a regular schedule, so an active connection stays within the limit.
- Expire refresh token after specific time ends the session at a fixed age regardless of use. The end user must reauthorize once it elapses.
- Immediately expire refresh token ends the connection after a single use and is not suitable for StackOne.
- Click Save.
Retrieve the Client ID and Client Secret
The Consumer Key and Consumer Secret are the values StackOne needs to authenticate.
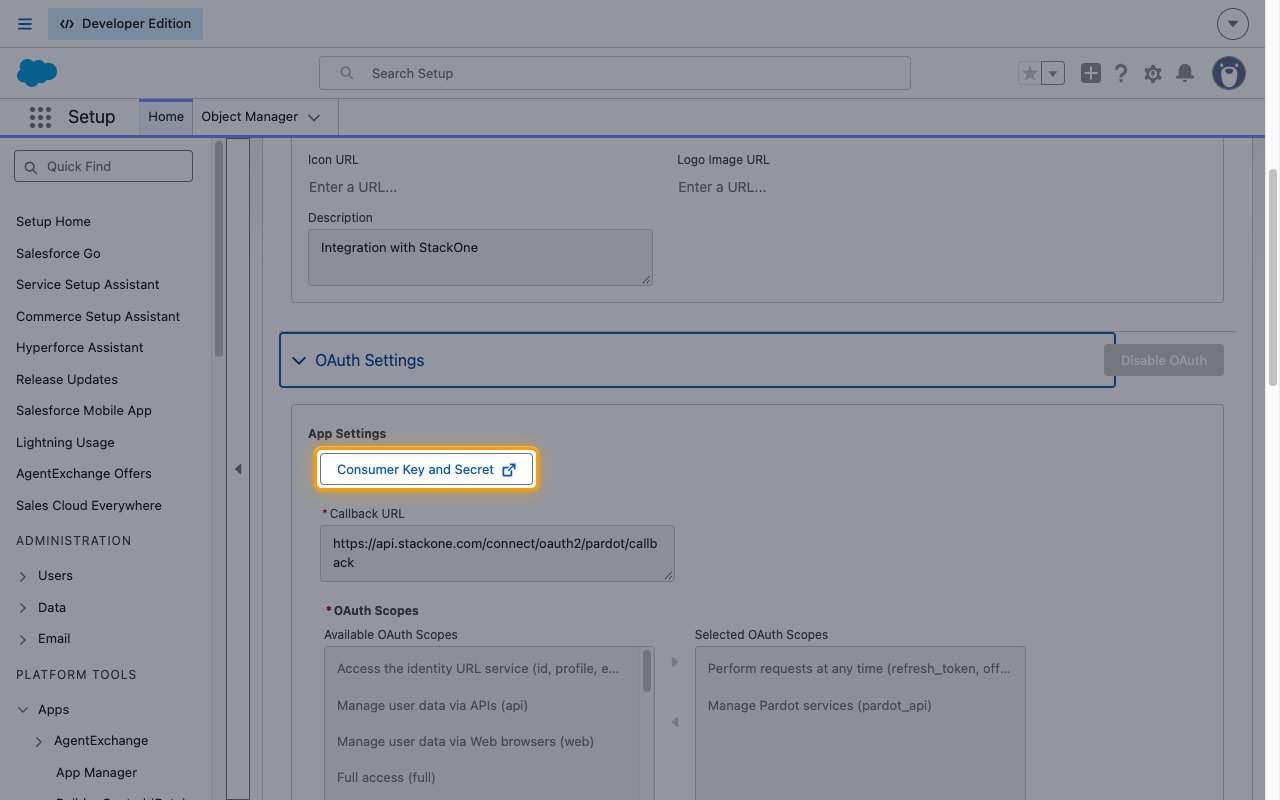
Open Consumer Key and Secret
Open the app from External Client App Manager, go to the Settings tab, expand OAuth Settings, and click Consumer Key and Secret.
- Salesforce may email you a verification code before it shows the values. Enter the code and click Verify.
Copy the values into StackOne
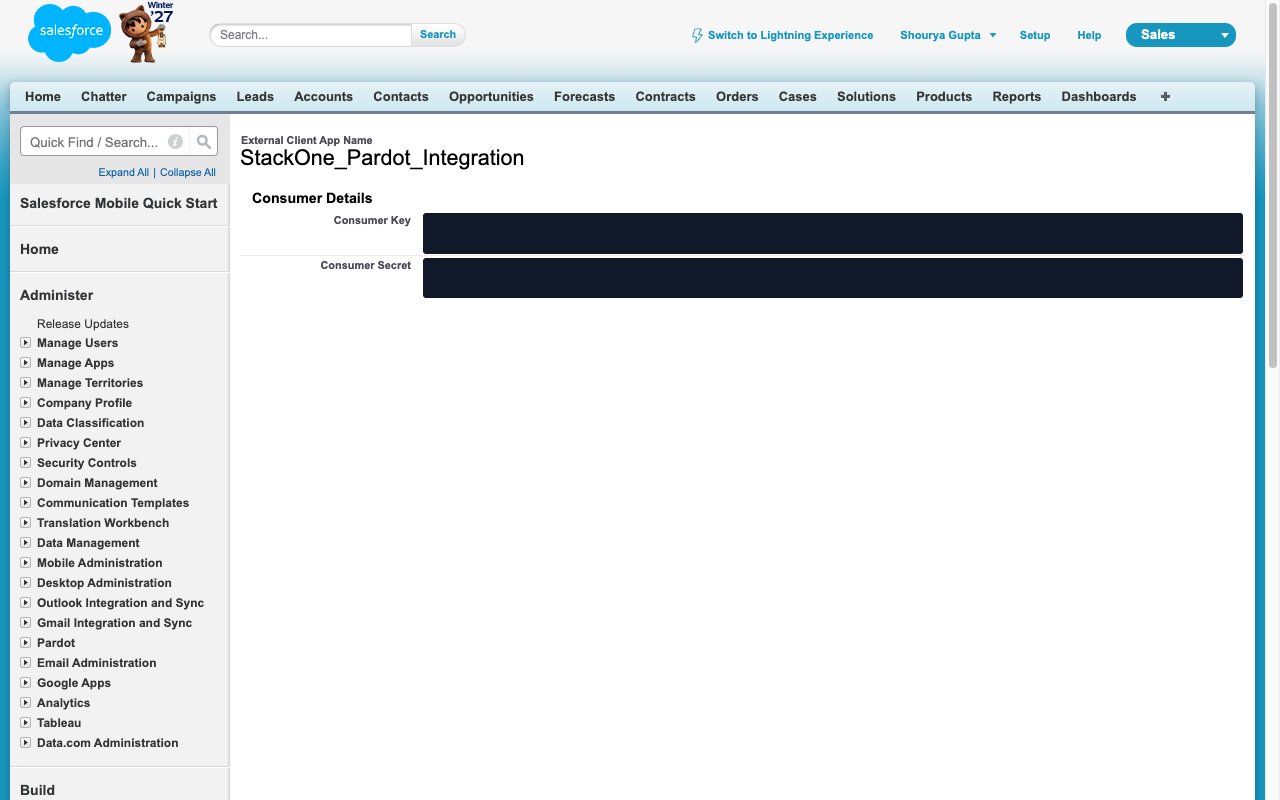
The Consumer Details page shows both values, each with its own Copy control.
- Copy the Consumer Key into the Client ID (Consumer Key) field in the StackOne Connector profile.
- Copy the Consumer Secret into the Client Secret (Consumer Secret) field in the StackOne Connector profile.
- Leave OAuth Scopes blank in the StackOne Connector profile to use the defaults, or enter the same space-separated scopes you selected on the app.
- Note: You can retrieve both values again from this screen later, but Salesforce asks you to verify your identity each time.
- Store both values securely for use later.
Creating the StackOne Connector Profile
To create the Connector Profile in StackOne for Pardot:Open the connector
Choose actions and events
- Click Add Profile.
- If the connector offers more than one authentication method, set the Auth Method filter to OAuth 2.0.
- Select the actions, and any events, to enable for this Connector Profile.
- Click Continue.
Set up authentication
- Select Authentication Type as OAuth 2.0.
- Fill out the fields using details retrieved from your provider:
- Client ID (Consumer Key)
- Client Secret (Consumer Secret)
- OAuth Scopes (Optional)
- Click Create Profile.