

Find your Instance URL
The Instance URL is the web address of your n8n instance: the host name, plus the port and base path if your address includes them.
- Open n8n in your browser and copy the address from the address bar.
- Delete everything after the host name, port and base path, such as
/home/workflowsor/projects/abc123/workflows. - Format on n8n Cloud:
https://{subdomain}.app.n8n.cloud - Format when self-hosted:
https://{host}, with:{port}and/{base path}if your address includes them - Example:
https://acme.app.n8n.cloud - Example with a base path:
https://example.com/n8n - Your n8n instance must be reachable from the internet over HTTPS, without a sign-in page in front of it. A self-hosted instance that only accepts plain HTTP cannot connect.
- Paste it into the Instance URL field in StackOne Hub.
Create the API key
An n8n API key can only use the scopes you grant it, and only those that the role of the user who creates it allows.
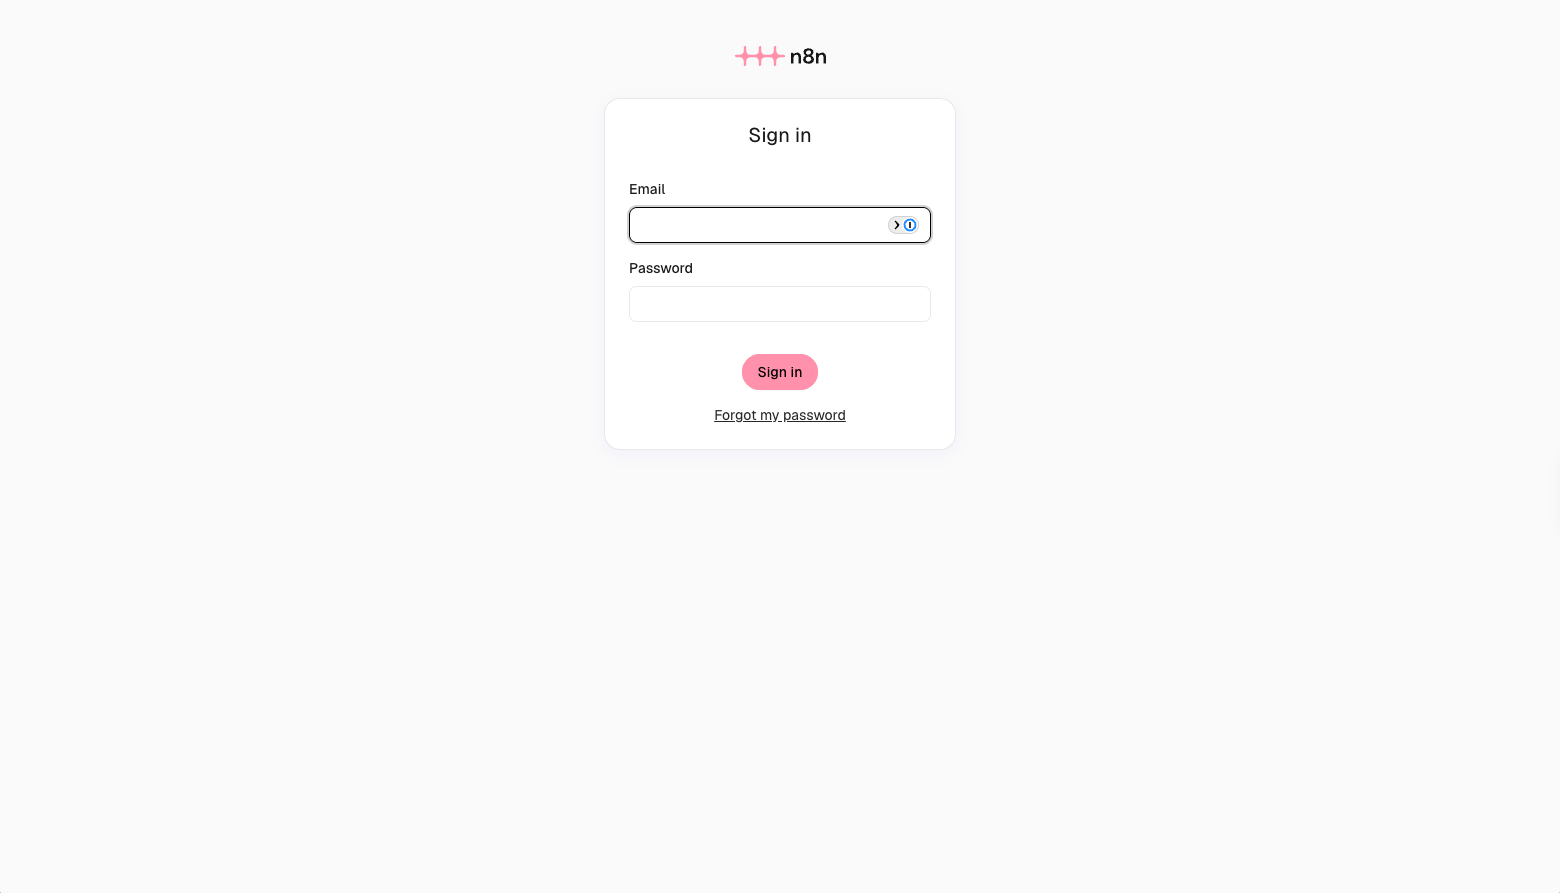
Sign in to n8n
Sign in to your n8n instance as an owner or, where your plan has the role, an admin.
- Enter your Email and Password, then select Sign in.
- A key can only hold the scopes that the signed-in user’s role allows, so sign in as an owner or admin rather than as a member.
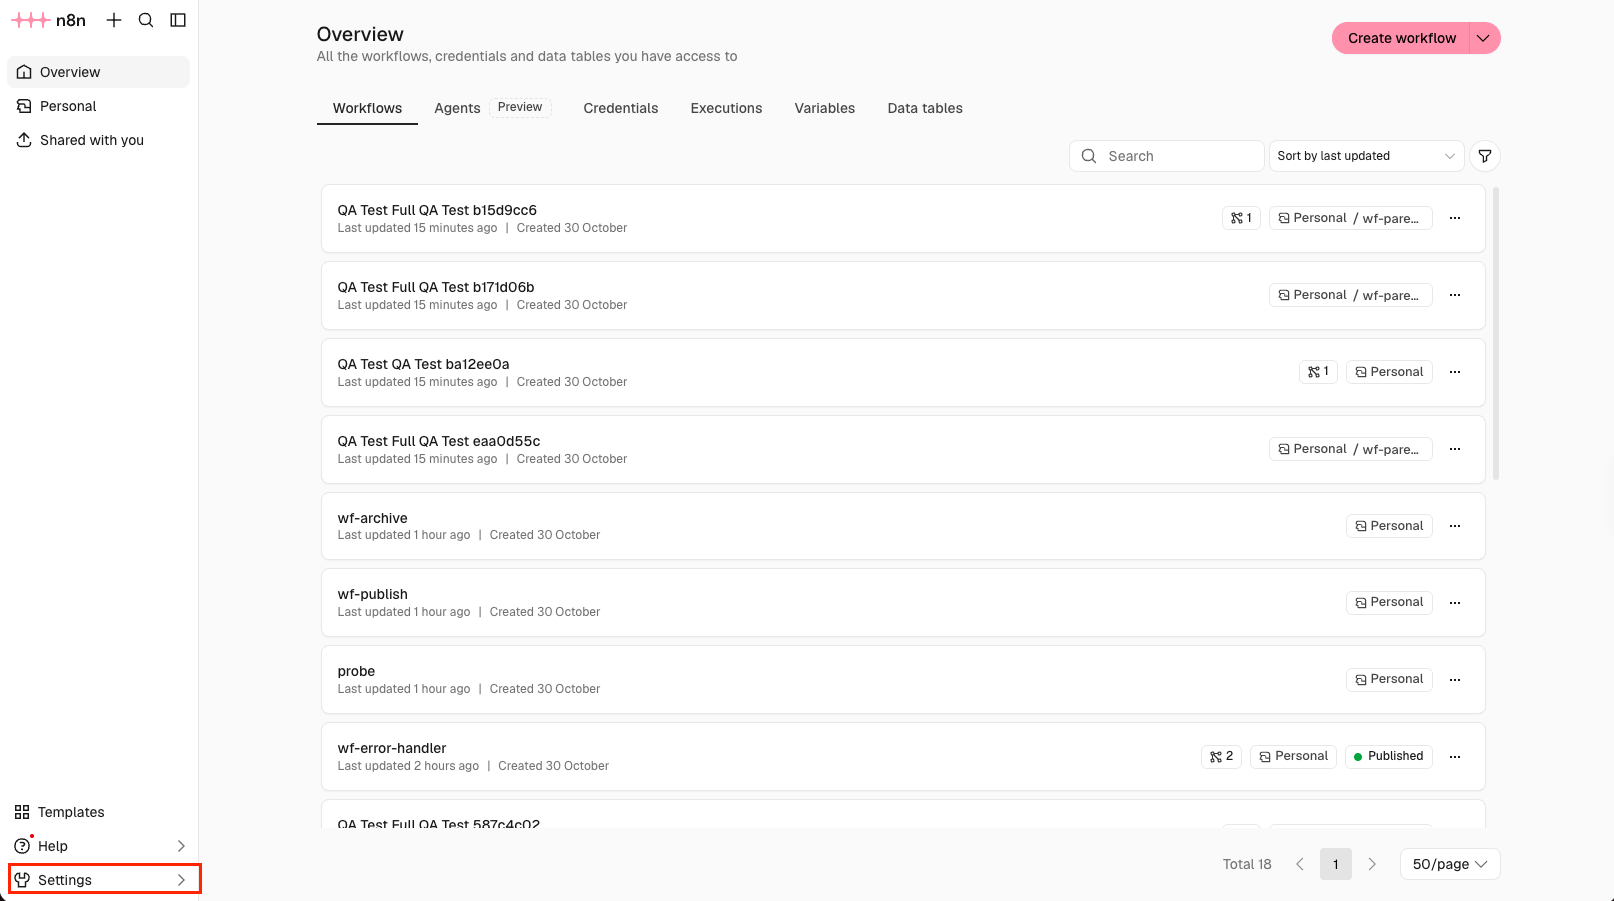
Open Settings
Select Settings at the bottom of the left sidebar.
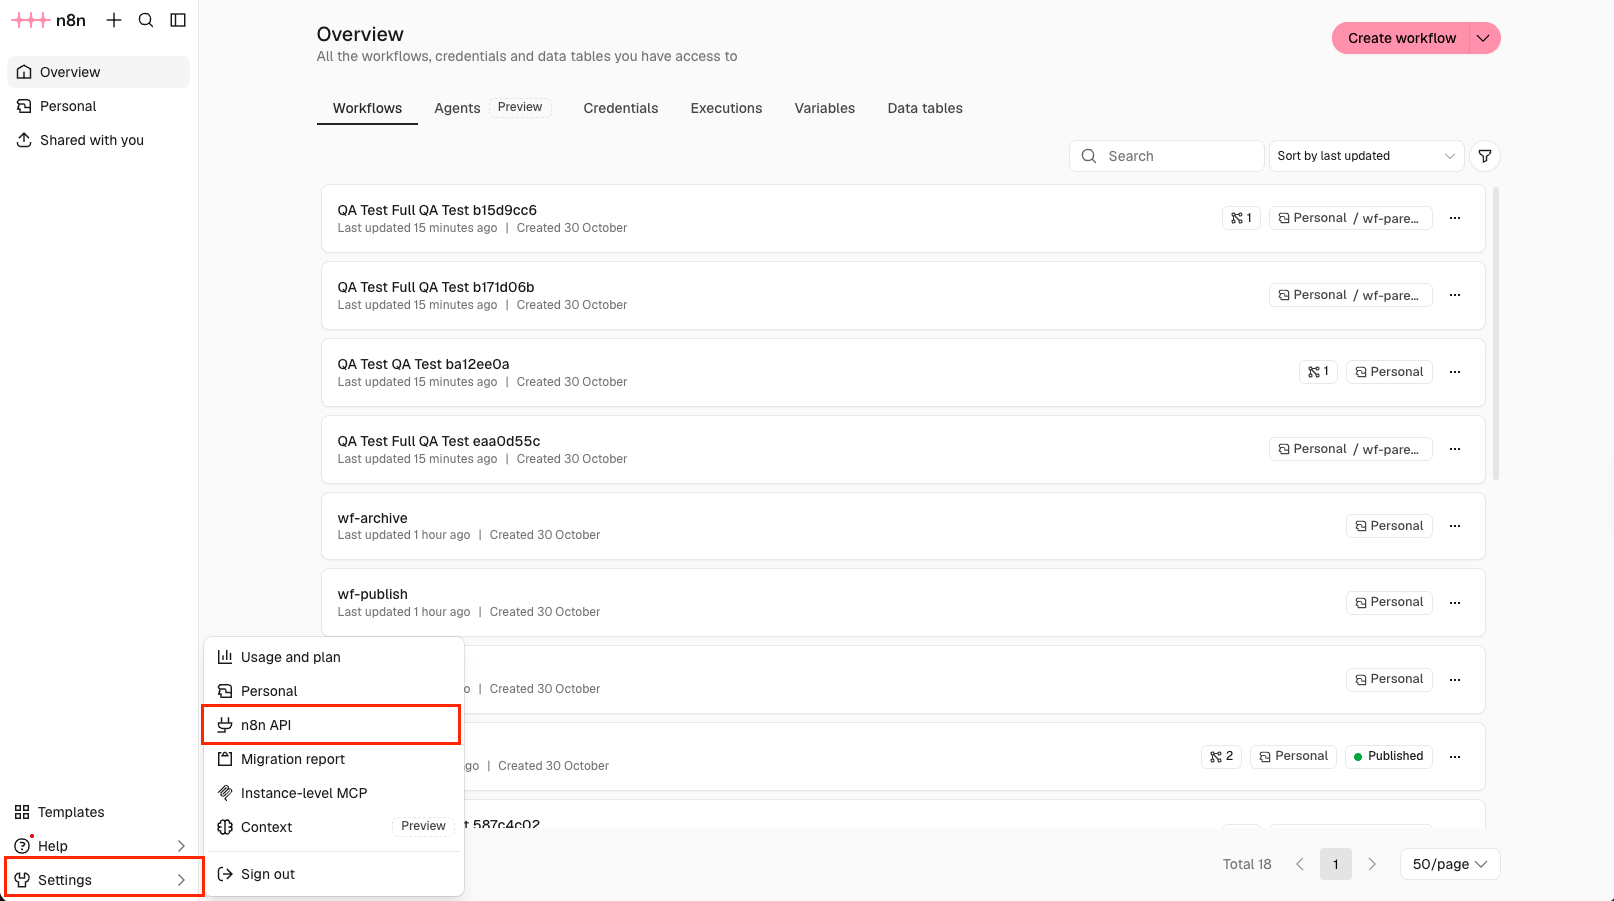
Open the n8n API settings
In the Settings menu, select n8n API.
- You can also open your Instance URL with
/settings/apiadded, for examplehttps://acme.app.n8n.cloud/settings/api.
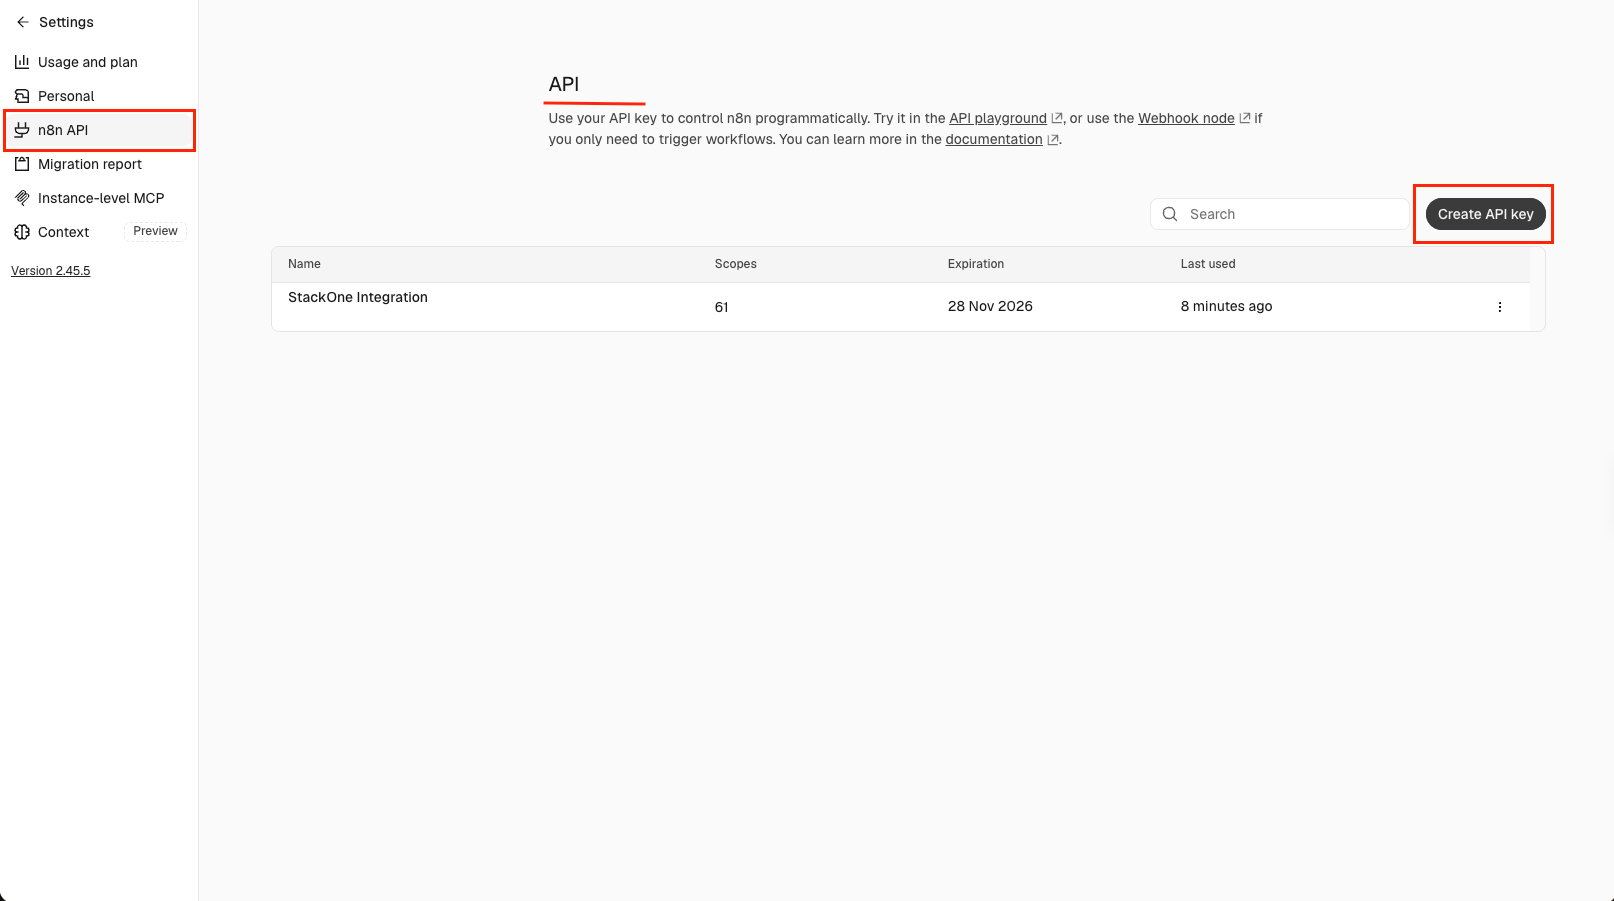
Create the key
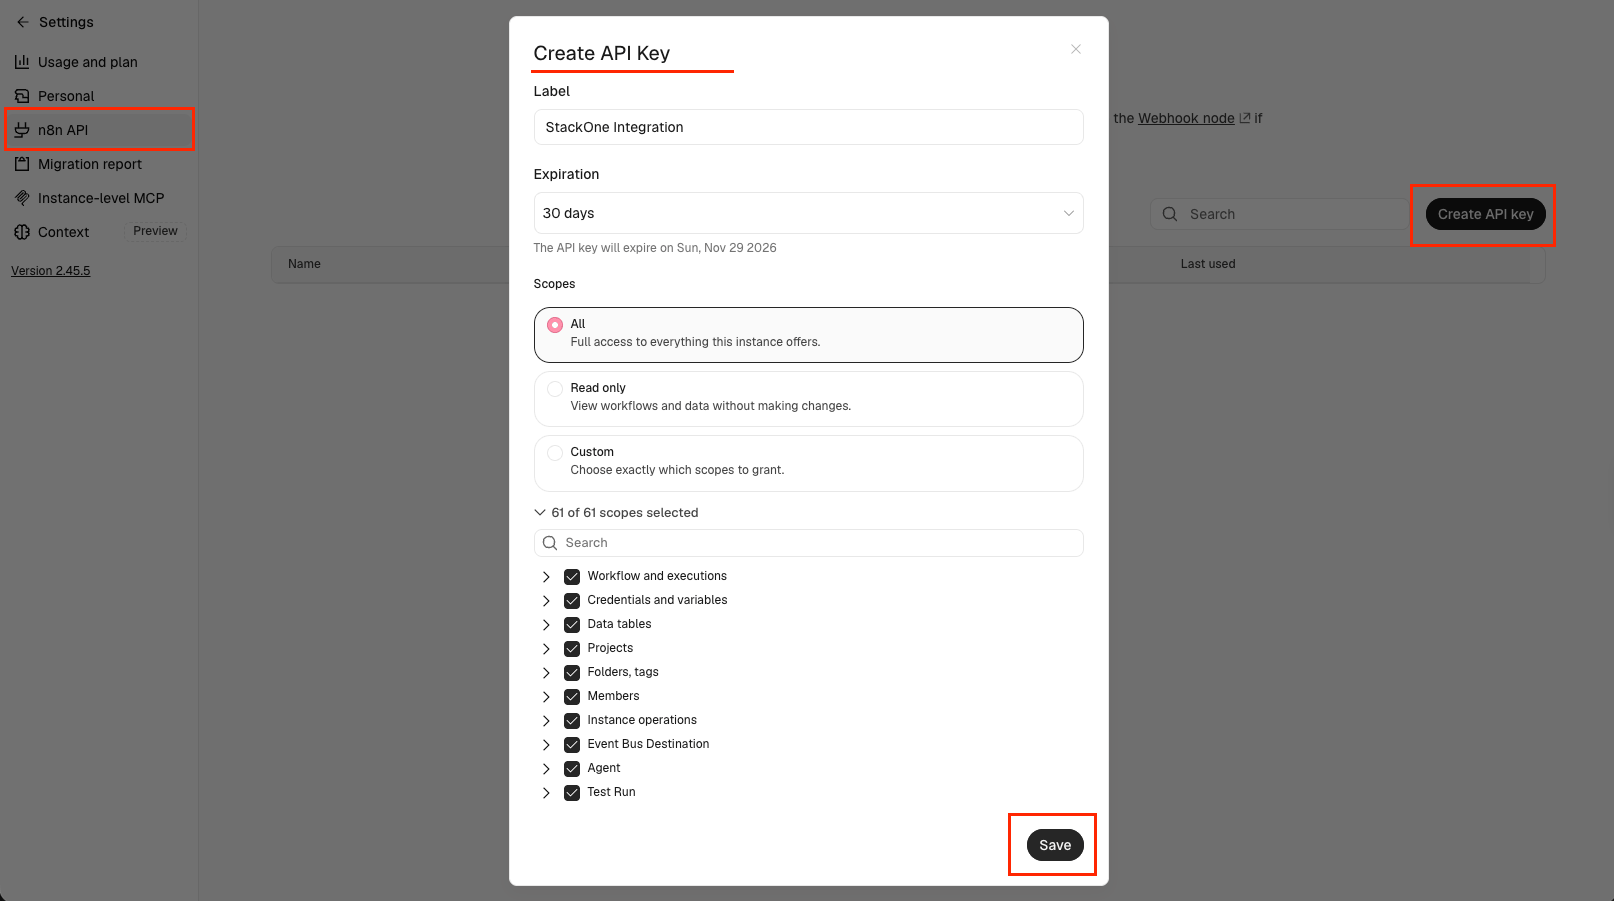
On the API page, select Create API key.
Name the key
In the Create API Key dialog, fill in the key details.
- Label:
StackOne Integration - Choose an Expiration: 7 days, 30 days (the default), 60 days, 90 days, Custom or Never. When the key expires, the connection stops working until you paste a new key into StackOne Hub.
Choose the scopes
Under Scopes, keep All to let StackOne use every action. To limit the key, select Custom and enable only the scopes for the actions you plan to use. The count below the options shows how many scopes your role allows: a member sees 61, while an owner or admin sees more.
Check what each scope covers
n8n groups the Custom scopes by resource. The notes below explain the most important scopes and where to find each group.
user:listanduser:readread the users, their global roles and the members of each team project.project:listreads team projects. Without it, project roles and groups cannot be read, and requests that expand them fail.role:listandrole:readread the role definitions. They are available on n8n 2.36.0 or later, where the connection test reads the role list and rejects a key withoutrole:list.- Workflow and executions covers workflows, versions, publishing, workflow tags, executions, retries and execution tags.
- Credentials and variables covers credentials and variables.
- Data tables covers data tables, their columns and rows.
- Projects covers team projects and their members.
- Folders, tags covers folders and tags.
- Members covers users.
- Instance operations covers source control, community packages, the security audit, insights, and credential and node type policies.
- Event Bus Destination covers log streaming destinations, which webhook events require.
- Agent covers agent export.
- Test Run covers test runs.
- A member key only lists the scopes that its role allows, so the
role,roleMappingRuleandgitConnectionscopes and the destination create and delete scopes do not appear. On an owner or admin key, find them with the scope search box. - Read only grants read access to workflows and data only, so any action that creates, changes or deletes something is rejected.
- On n8n releases earlier than 2.14.0, only Enterprise plans show Scopes, and keys on other plans have full access.
Copy the key
Select Save, then copy the key that n8n displays and store it securely for later use.
- The key is shown only once and cannot be retrieved later. n8n says “Make sure to copy your API key now as you will not be able to see this again.”
- Paste it into the API Key field in StackOne Hub.
Understand role and plan limits
On n8n 2.36.0 or later, a key created by a member is rejected when you connect, because n8n only allows owners and admins to read roles and projects. The error message states that an owner or admin key is required.
- On a licence without projects, users still load with their global roles, but their project roles and groups are empty, and listing groups is rejected with n8n’s licence message.
- On a licence with a user limit, n8n rejects the users list with its own message.
- Variables, LDAP, SAML, OIDC, log streaming, source control and environments are paid n8n features. On a plan without them, those actions are rejected even when the key has every scope.
Revoke the key
To stop StackOne from accessing your n8n instance, revoke the key.
- Navigate to Settings > n8n API.
- Open the actions menu on the key’s row and select Revoke.
- Confirm with Revoke.
- On n8n releases earlier than 2.26.0, select Delete next to the key and confirm with Delete Forever.
Link the Account
Connect
- Click Connect.
- If applicable, the provider will redirect you to a sign-in or authorization page. Complete the provider’s authorization flow.
- Once authorization is successful, you will see a confirmation popup.
Use Actions
Next Steps
Webhooks setup
Configure receiving Events for n8n into StackOne.