

Event categories
Connector events
Connector events
Fire from a connector - a new Notion page, a file dropped into SharePoint, a Salesforce record change. They’re configured on the connector profile for that connector.
- Programmatic - StackOne registers the subscription with the connector for every linked account, automatically. New accounts get subscribed the moment they’re linked.
- Manual - when a connector doesn’t expose a subscription API, you register StackOne’s webhook URL inside the connector’s own app config. These events are tagged Requires Setup on the profile.
- Data Sync - StackOne detects the change itself, by comparing each Data Sync run with the records it already stored, and sends an event for every record created, updated, or deleted.
Platform events
Platform events
Fire from StackOne itself, covering account lifecycle, so you can react when a customer connects or disconnects a tool without polling. See Platform Events for the full list of events and Handle Account Events for how to consume them.
Legacy unified events
Legacy unified events
Fire from the legacy connectors and have their own catalog and payload shape.
Where you configure events
There are two places, and they own different things. The outbound webhook has to exist first - that’s what you bind events to on the connector profile.- Webhooks page - the outbound endpoint: URL, signing secrets, delivery health, and recent volume. Create the webhook here before you try to route any events to it.
- Connector profile - which events fire from this connector in this project, and which webhook(s) each event is routed to. For programmatic events, toggling here provisions (or unprovisions) the underlying subscription with the connector for every linked account on the profile. Manual events are tagged Requires Setup and only fire once StackOne’s webhook URL is registered in the connector’s app config. See Scoping Connectors.
Quickstart
1
Create a webhook endpoint
On the Webhooks page, click Add Webhook and provide a name and an HTTPS URL. The URL must be publicly reachable and return
200 quickly.2
Enable events on a connector profile
In Connectors, open the connector you want events from and select its profile. Then:
- Connector events: on the Events tab, turn on the events you want, select the webhook you just created, and click Save Profile.
- Data Sync events (supported actions only): turn on events for each action and select the webhook, from the action’s Data Sync panel. See Data Sync Events.
3
Grab the signing secret (optional)
The Signing secrets tab on the Webhooks page has the current secret. Copy it into your endpoint’s config if you plan to verify signatures.
4
Verify and respond (optional)
On each request to your endpoint, verify the
x-stackone-signature header (see below) and return 200. The response body is ignored.5
Connect an account
Link an account in the Accounts section or via the Hub. For events tagged Requires Setup, register StackOne’s webhook URL in the connector’s own app config to start receiving them.
Verifying webhook signatures
Every delivery is signed with HMAC-SHA256 over the raw request body, using your signing secret as the key, base64url-encoded, and sent in thex-stackone-signature header.
- Hash the raw request bytes, not a re-serialized JSON string -
JSON.stringifydoesn’t guarantee byte-for-byte equality with what we sent. - Compare in constant time with
timingSafeEqual, not===, so an attacker can’t infer the signature byte-by-byte from response latency.
Simpler alternative. If you don’t need cryptographic verification, you can append a secret query parameter to your webhook URL (e.g.
?token=...) and check for its presence on every request. It’s less secure but adequate for non-sensitive event types.Rotating signing secrets
A project holds up to two signing secrets, and only one is active at a time. Deliveries sign with the active secret, so you can add the new one to your endpoint before switching over without dropping events.-
On the Signing secrets tab, click Generate on the Generate new signing secret row, then Confirm. The new secret starts inactive - deliveries continue to use the active secret.
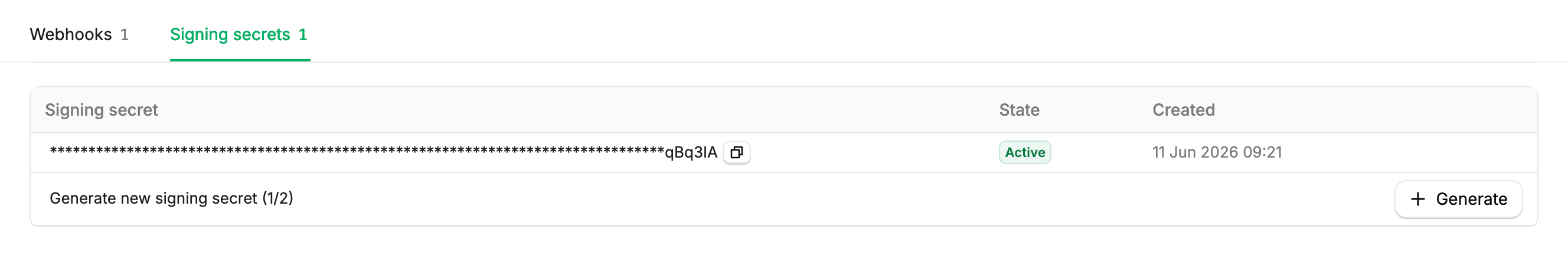
- Copy the new secret from the Generate Signing Secret dialog, or later with the copy button on its row.
- In your endpoint, accept signatures matching either the current secret or the new one.
-
Back in StackOne, open the … menu on the new secret’s row, click Activate (rotate), then Confirm. Deliveries now sign with the new secret, and the old secret switches to inactive.
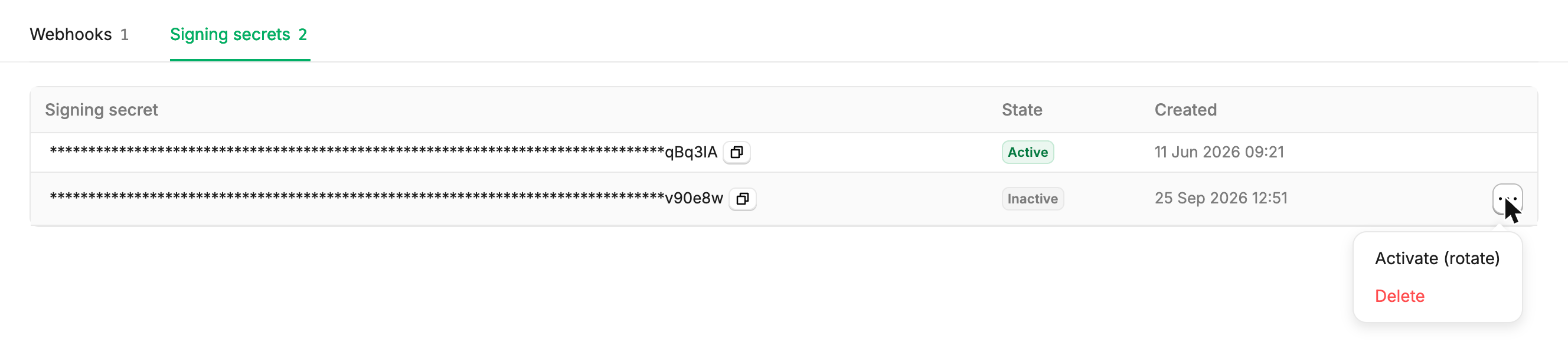
- Once you’ve confirmed everything’s still verifying, open the … menu on the old secret’s row and click Delete. Until you delete it, Activate (rotate) on the old secret switches back. You can’t retrieve or reactivate a deleted secret.
- Remove the old secret from your verification code.
Managing a webhook
- Disable - stops delivery to your URL. Subscriptions with the connector stay active, so events keep flowing into StackOne and resume on enable.
- Enable - resumes delivery using the existing subscriptions.
- Delete - removes the webhook and cleans up the programmatic subscriptions with the connector for events that no other webhook is using.
Troubleshooting
- Events aren’t arriving. Check that the event is enabled on the connector profile and subscribed by the webhook. Both are required.
- Signature mismatches. Verify against the raw body, not a re-serialized JSON string. Confirm you’re using the currently-active secret.
- Data Sync events aren’t arriving. A Linked Account’s first run sends no events, because it sets the baseline.
deletedevents only come from a full re-sync. See When events are sent. - Some accounts deliver, others don’t. Open the connector profile and confirm the linked account is active.
- 5xx loops. Your endpoint is returning an error and StackOne is retrying. Check your application logs and the webhook’s Last Triggered and 7-Day-Volume columns on the Webhooks page.
- Behind a firewall. Allow inbound traffic from StackOne’s outbound IP addresses.