

- A verified SSO connection between the organization and Okta. See Single Sign-On.
- The Organization Admin role in StackOne.
- Admin access to the StackOne application in Okta.
- (Optional) Okta set up to send
adminin the SCIMrolesfield for anyone who should join as an Organization Admin. Everyone else joins as an Organization Member. See Organization Roles.
The
roles value only counts when a user first joins. After that, their role can only be changed in StackOne.Link SCIM in StackOne
1
Open the SSO connection
- In the StackOne dashboard, go to Organization > Security > SSO.
- Open the verified SSO connection.
- Select the Provisioning tab.
2
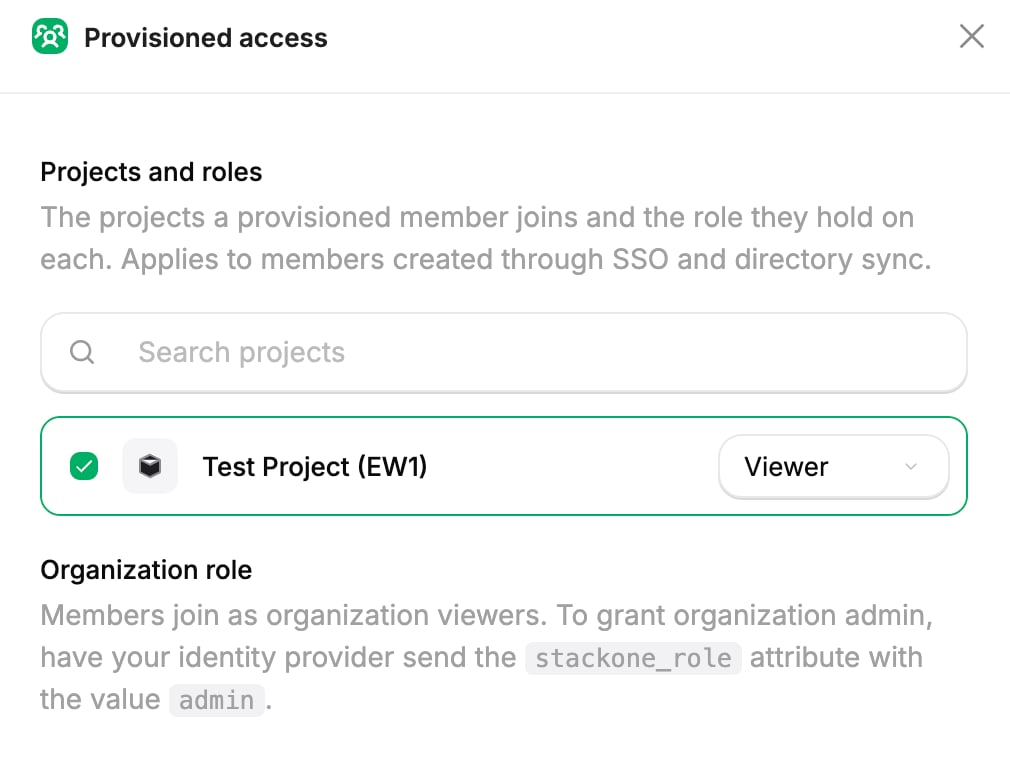
Choose projects and roles
- On the Provisioned access card, select Manage access.
- Pick the projects new users should join.
- Choose a role for each one. See Project Roles.
- Select Save changes.
3
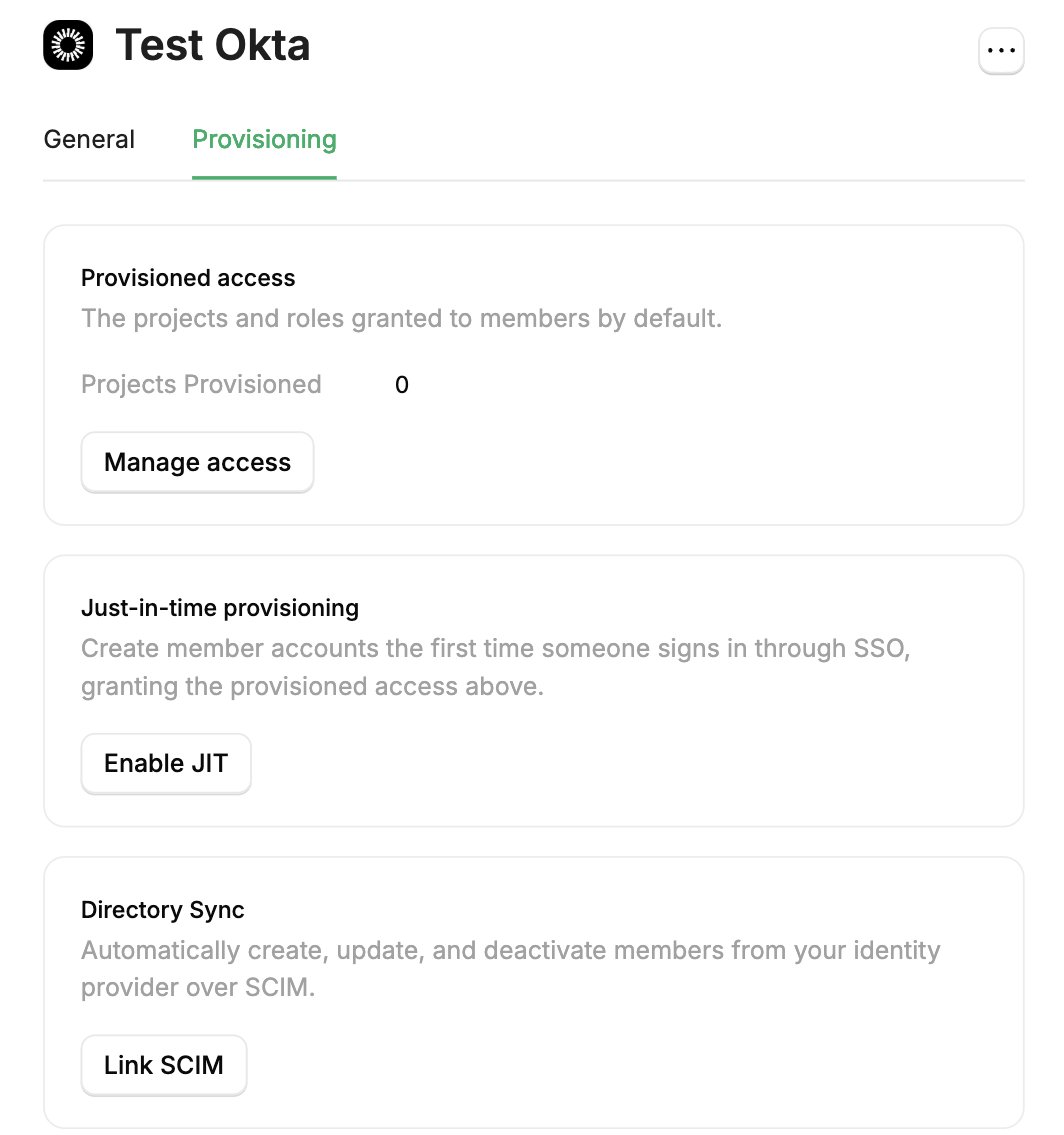
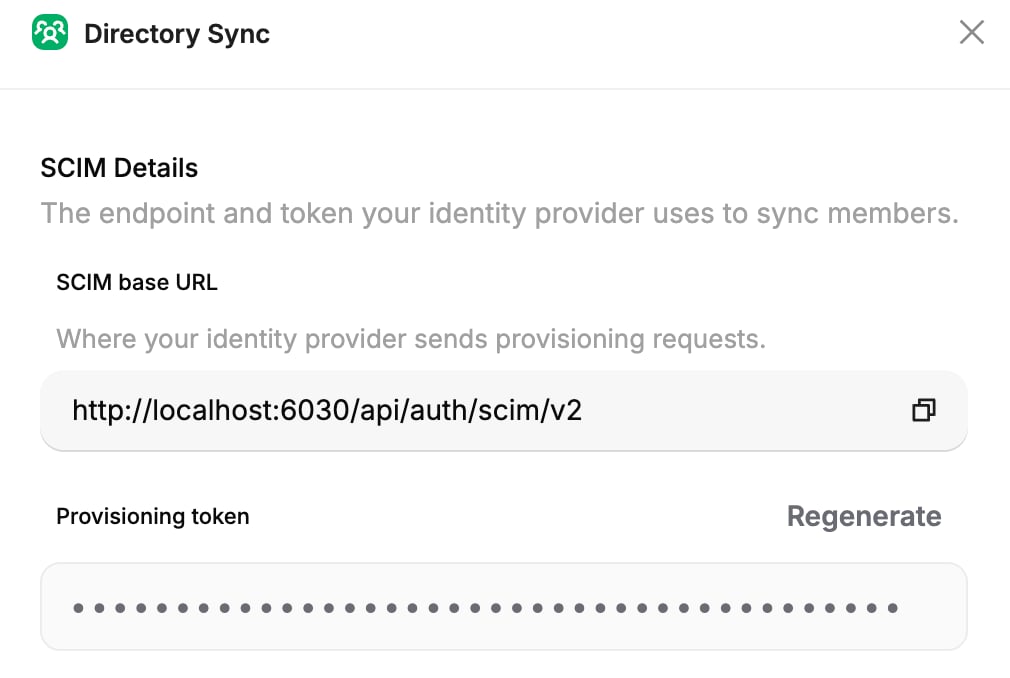
Link SCIM and copy the credentials
- On the Directory Sync card, select Link SCIM.
- In the SCIM Details section, copy the SCIM base URL and the Provisioning token. You paste both into the IdP.
Configure provisioning in Okta
1
Enable the API integration
- In the Okta admin console, go to Applications > Applications and open the app you created for StackOne SSO.
- Go to the Provisioning tab.
- Click Configure API Integration.
- Select Enable API integration.
2
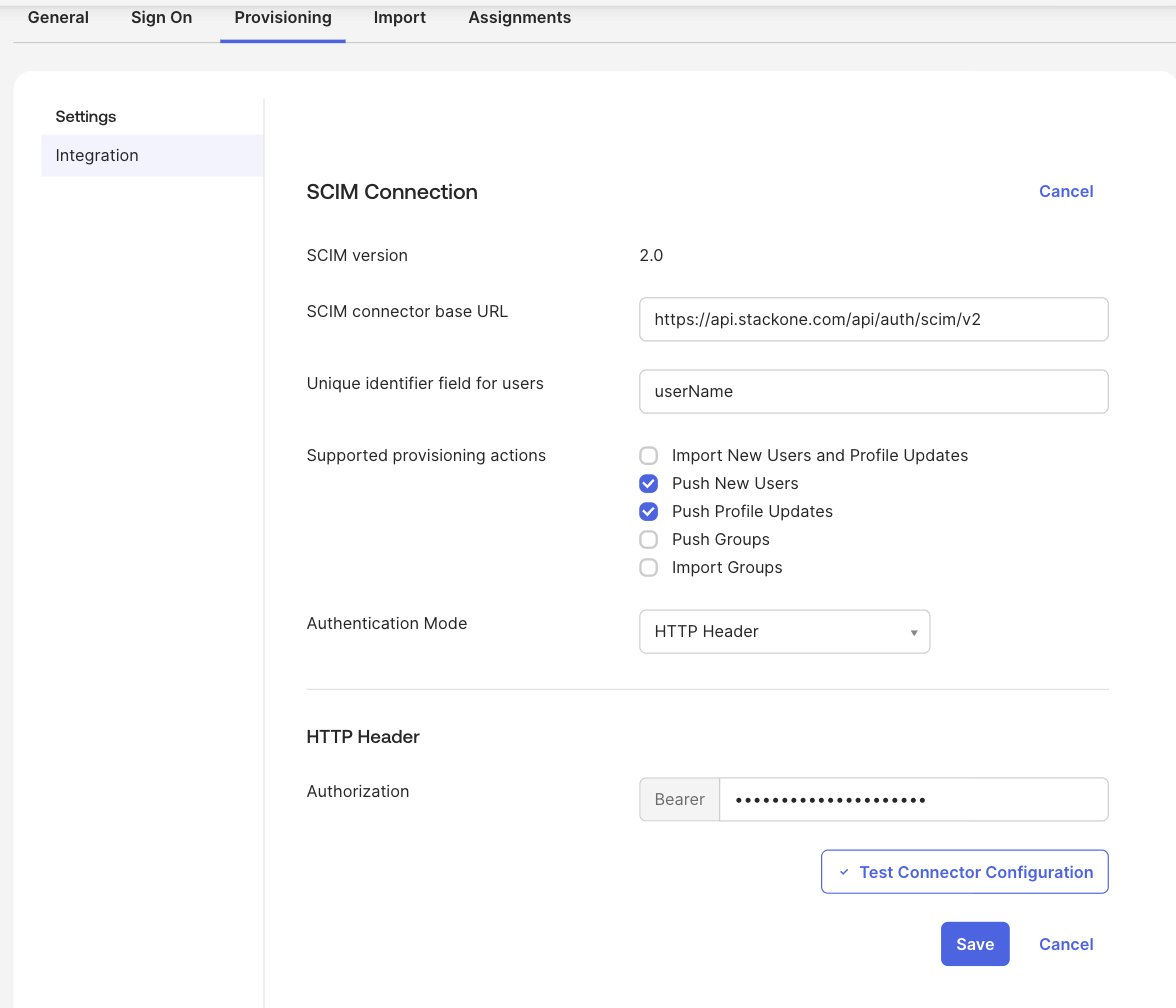
Add the SCIM endpoint and token
- Set the following:
- SCIM connector base URL: the SCIM base URL from StackOne.
- Unique identifier field for users:
userName. - Supported provisioning actions:
Push New UsersandPush Profile Updates. - Authentication Mode:
HTTP Header. - Authorization: the Provisioning token from StackOne.
- Click Test Connector Configuration to confirm Okta can reach StackOne.
- Click Save.
3
Turn on the provisioning actions
- Under Provisioning > To App, click Edit.
- Enable Create Users, Update User Attributes, and Deactivate Users.
- Click Save.
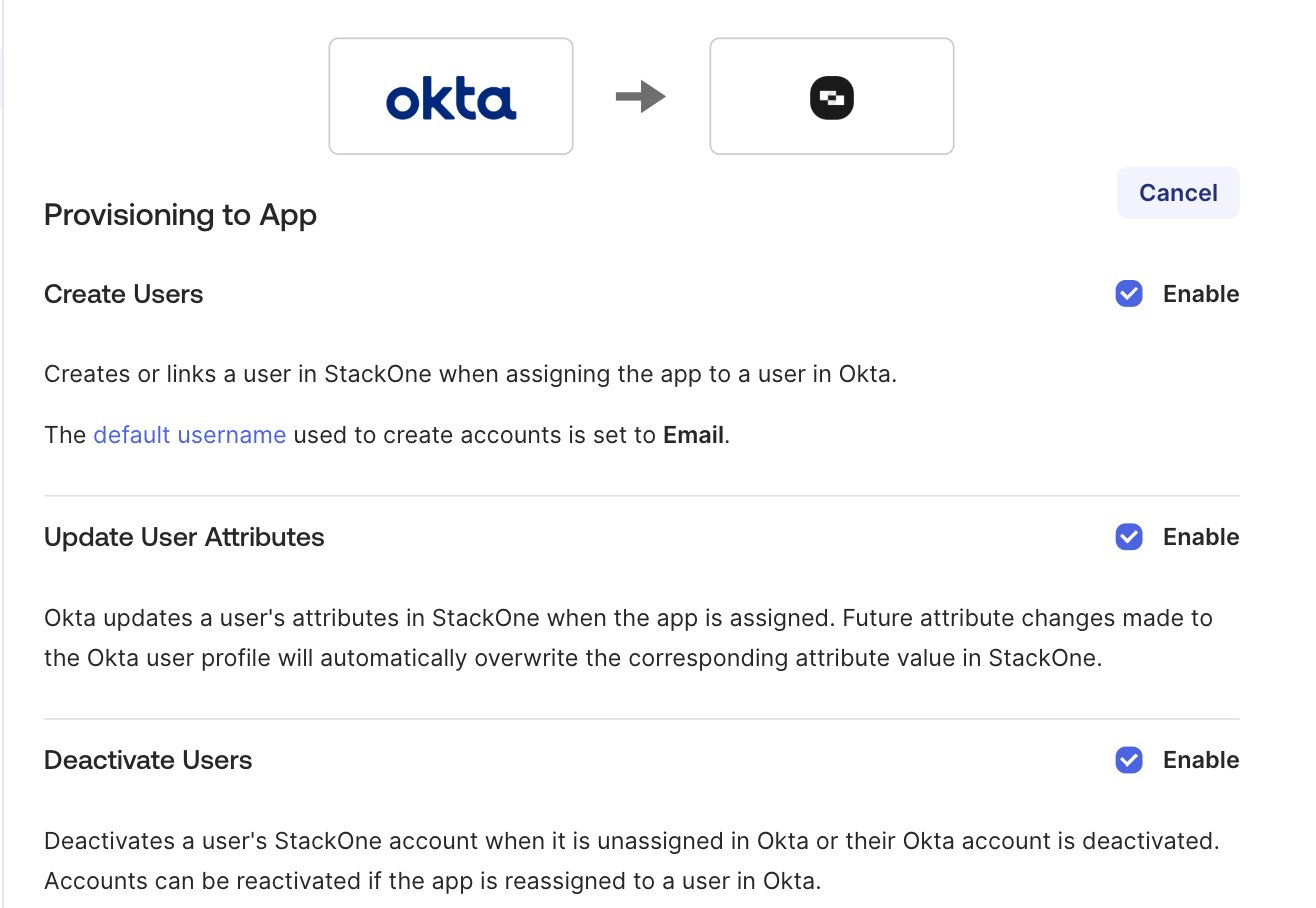
Assign members in Okta
1
Assign people to the app
- Open the Assignments tab of the StackOne app.
- Assign the people you want in StackOne.
Assigning an Okta group provisions its members as individual users. To bring the group itself into StackOne, with its membership kept in step, push it as well. See Push groups.
2
Confirm the sync
Return to the Directory Sync card in StackOne. The Synced members and Last synced values update as Okta pushes users, and new members appear in the projects you selected.
Push groups
Okta’s Group Push creates the group in StackOne as a synced group and keeps its members in step. Only members who are assigned to the StackOne app, and so already provisioned, are pushed.If StackOne already has a group with the same name, an empty one becomes the synced group and keeps its access.If the group has members, it’s left untouched, and StackOne creates a second, synced group with the same name instead. To set up a group’s access before anyone is pushed into it, see Prepare the access before you push.
1
Enable Push Groups on the app
- On the app’s Provisioning tab, under Integration, click Edit.
- Make sure Push Groups is enabled alongside Push New Users and Push Profile Updates.
- Click Save.
2
Push the group
- Open the app’s Push Groups tab.
- Click Push Groups, and choose Find groups by name. To push several groups that share a naming pattern, choose Find groups by rule instead.
- Select the Okta group, and leave Push group memberships immediately on.
- Click Save.
3
Confirm in StackOne
- Go to Organization > Manage Team and open the Groups tab. The group is listed with a Synced tag and its pushed members.
- Assign it to projects from its Projects tab.
Use different Okta groups for assigning the app and for Group Push. For example, assign the app to StackOne Users and push Finance. Okta doesn’t support using one group for both, and the group’s members in StackOne can end up different from Okta’s. See Okta’s App assignments and Group Push.
- To rename it, rename it in Okta.
-
To stop pushing it:
- On the Push Groups tab, choose Unlink pushed group on the group’s row.
- Choose whether to also delete the group in StackOne.
Next steps
SCIM Provisioning
How SCIM provisioning works across identity providers.
Microsoft Entra SCIM Provisioning
Provision members from Microsoft Entra ID instead.
SCIM Groups
Push the identity provider’s groups into StackOne and grant access through them.