

Connector Profile Access is only available on certain plans. See plans and pricing.
Project Admins can still view, edit and delete a restricted profile.
When to restrict a connector profile
Restrict a profile when its configuration is sensitive and only some people should connect through it. Each of them still links their own account.Only sales managers should get admin access to the CRM
Only sales managers should get admin access to the CRM
A sales team of account executives, with two sales managers who also fix records in bulk.
- Create two CRM connector profiles: one with admin scopes, and one with read-only scopes.
- Restrict the admin-scoped profile, and leave the read-only one Shared.
- Grant the sales managers Connector Profile Member on the admin-scoped profile.
- Each manager links their own CRM account through the admin-scoped profile.
- Everyone else links through the read-only profile.
Only the HR team should connect to the payroll system
Only the HR team should connect to the payroll system
An HR team that handles payroll.
- Restrict the HR connector profile that reaches payroll data.
- Grant the HR team’s group Connector Profile Member on it.
- Only the HR team can link accounts through it.
Access to a restricted connector profile
A grant gives a user or group one of two roles, Connector Profile Admin or Connector Profile Member. On a restricted connector profile:
Restrict a connector profile
Restricting a shared profile needs Project Admin or Organization Admin. Once it’s restricted, only a Connector Profile Admin can change its access.1
Open the profile's Access tab
- In Connectors, open the connector and select the profile’s card.
- Select its Access tab.
2
Switch it to Restricted
Under Who can use this profile, change the selector from Shared to Restricted. You become its Connector Profile Admin when you save, so you can’t lock yourself out.
Accounts already linked through the profile stay linked, and can still be re-authenticated through it without a grant.
3
Grant users and groups
- On the Users view, use Add users to pick each person.
- On the Groups view, use Add groups to pick each group.
- Set each row’s role to Admin (Connector Profile Admin) or Member (Connector Profile Member). Revoke removes a row.
4
Save
Click Save Access in the bar at the bottom of the page. Cancel discards the changes.
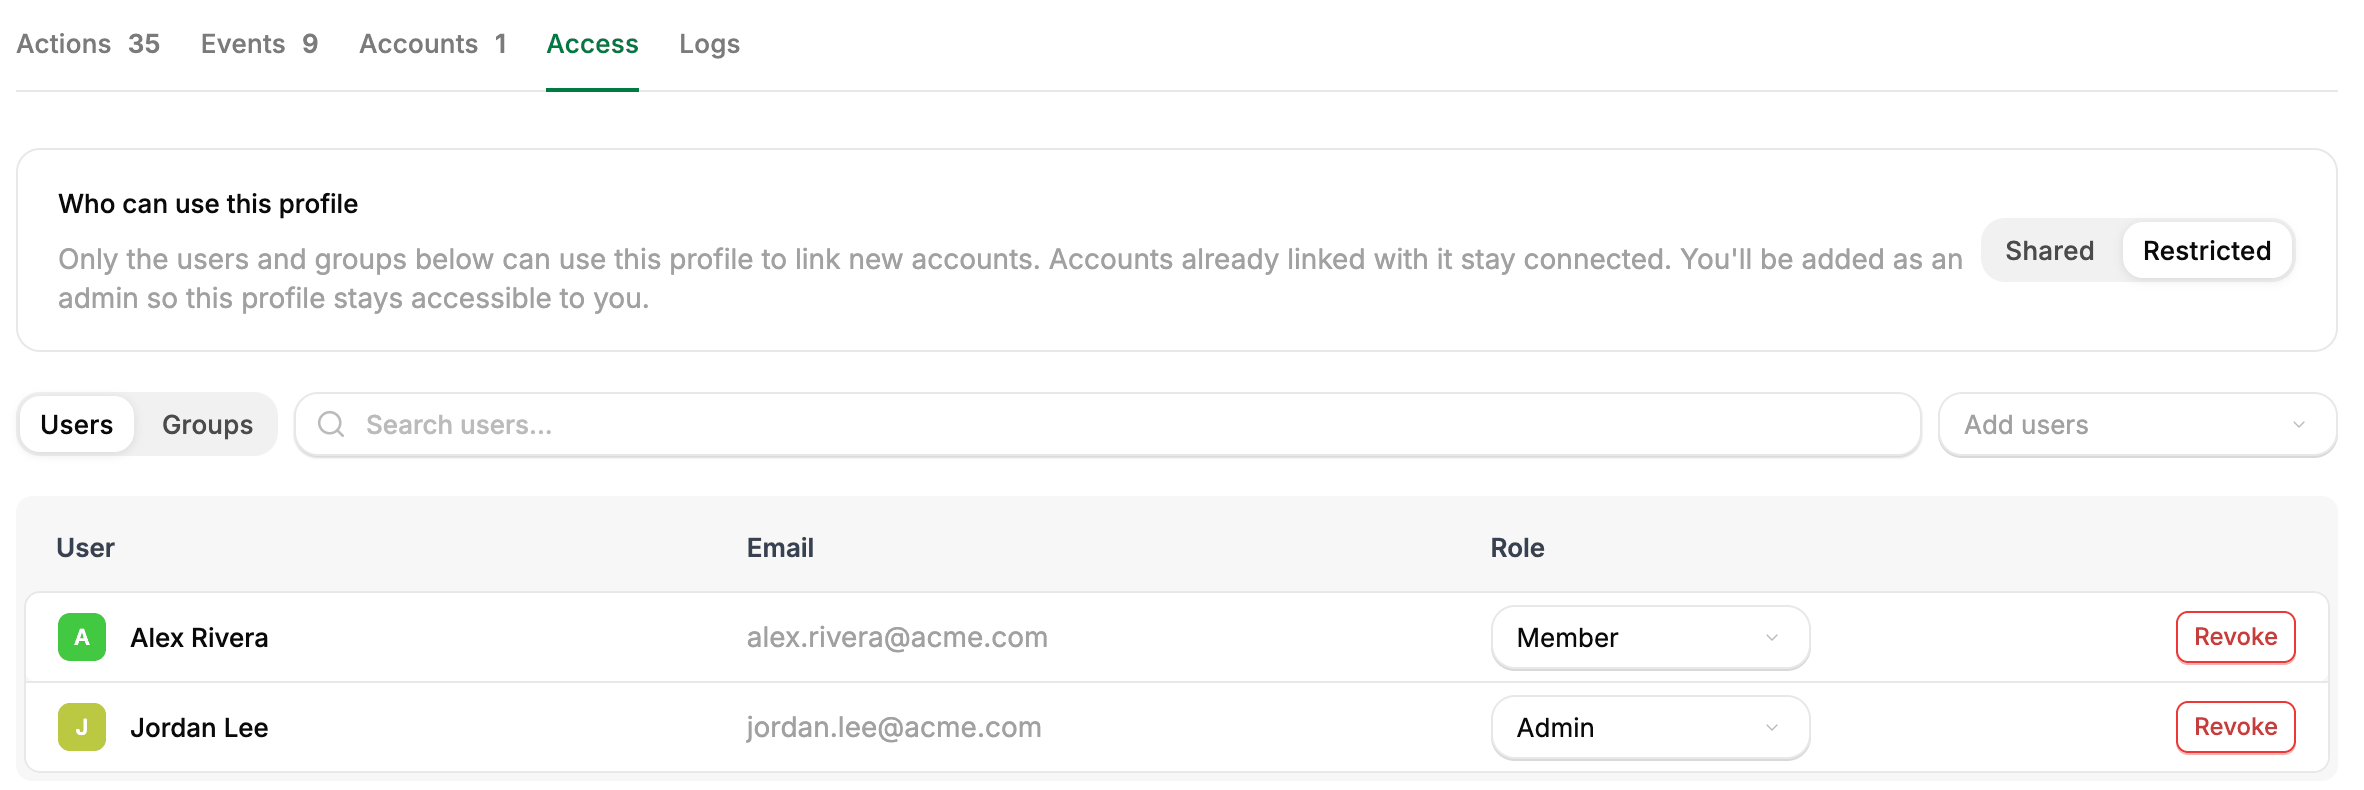
A restricted profile with two granted users
The default for new connector profiles
Each project has a Default Access setting that decides whether connector profiles created from then on start Shared or Restricted. Only an Organization Admin can change the default:- Go to Project Settings > Connector Profiles.
- Under Default Access, choose Shared or Restricted.
- Click Save.
Related
Scoping Connectors
Choose which of a profile’s actions and events are exposed.
Groups
Grant many users the same access at once with reusable groups.
Linking Accounts
Connect the provider accounts your agents act on.
Manage Team
Add people to the organization, and remove their access when they leave.