> ## Documentation Index
> Fetch the complete documentation index at: https://docs.stackone.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Manage Team
> Invite members, assign org and project roles, and manage organization security.
**Organization Admins** manage who can access your StackOne organization from the organization's **Members** settings.
StackOne has two independent layers of roles:
1. **Organization role**: Controls which projects a member can see and whether they can manage the organization itself.
2. **Project role**: Controls what a member can do within a specific project (assigned separately per project).
This means organization Admins automatically see all projects, while Members only see projects they're granted access to, directly or through a [group](/secure/identity-and-access/groups/overview).
| Organization role | Access |
| ----------------- | -------------------------------------------------------------------------------------------------------------------- |
| **Admin** | Manage members and security settings; create and access any [project](/gateway/concepts/organizations-and-projects). |
| **Member** | Only the projects they're granted access to, directly or through a group. The Team Members section is hidden. |
Organization and project roles are independent. A **Member** at the organization level can be **Admin** on a specific project, with full control of that project and no organization-wide access.
## Invite a member
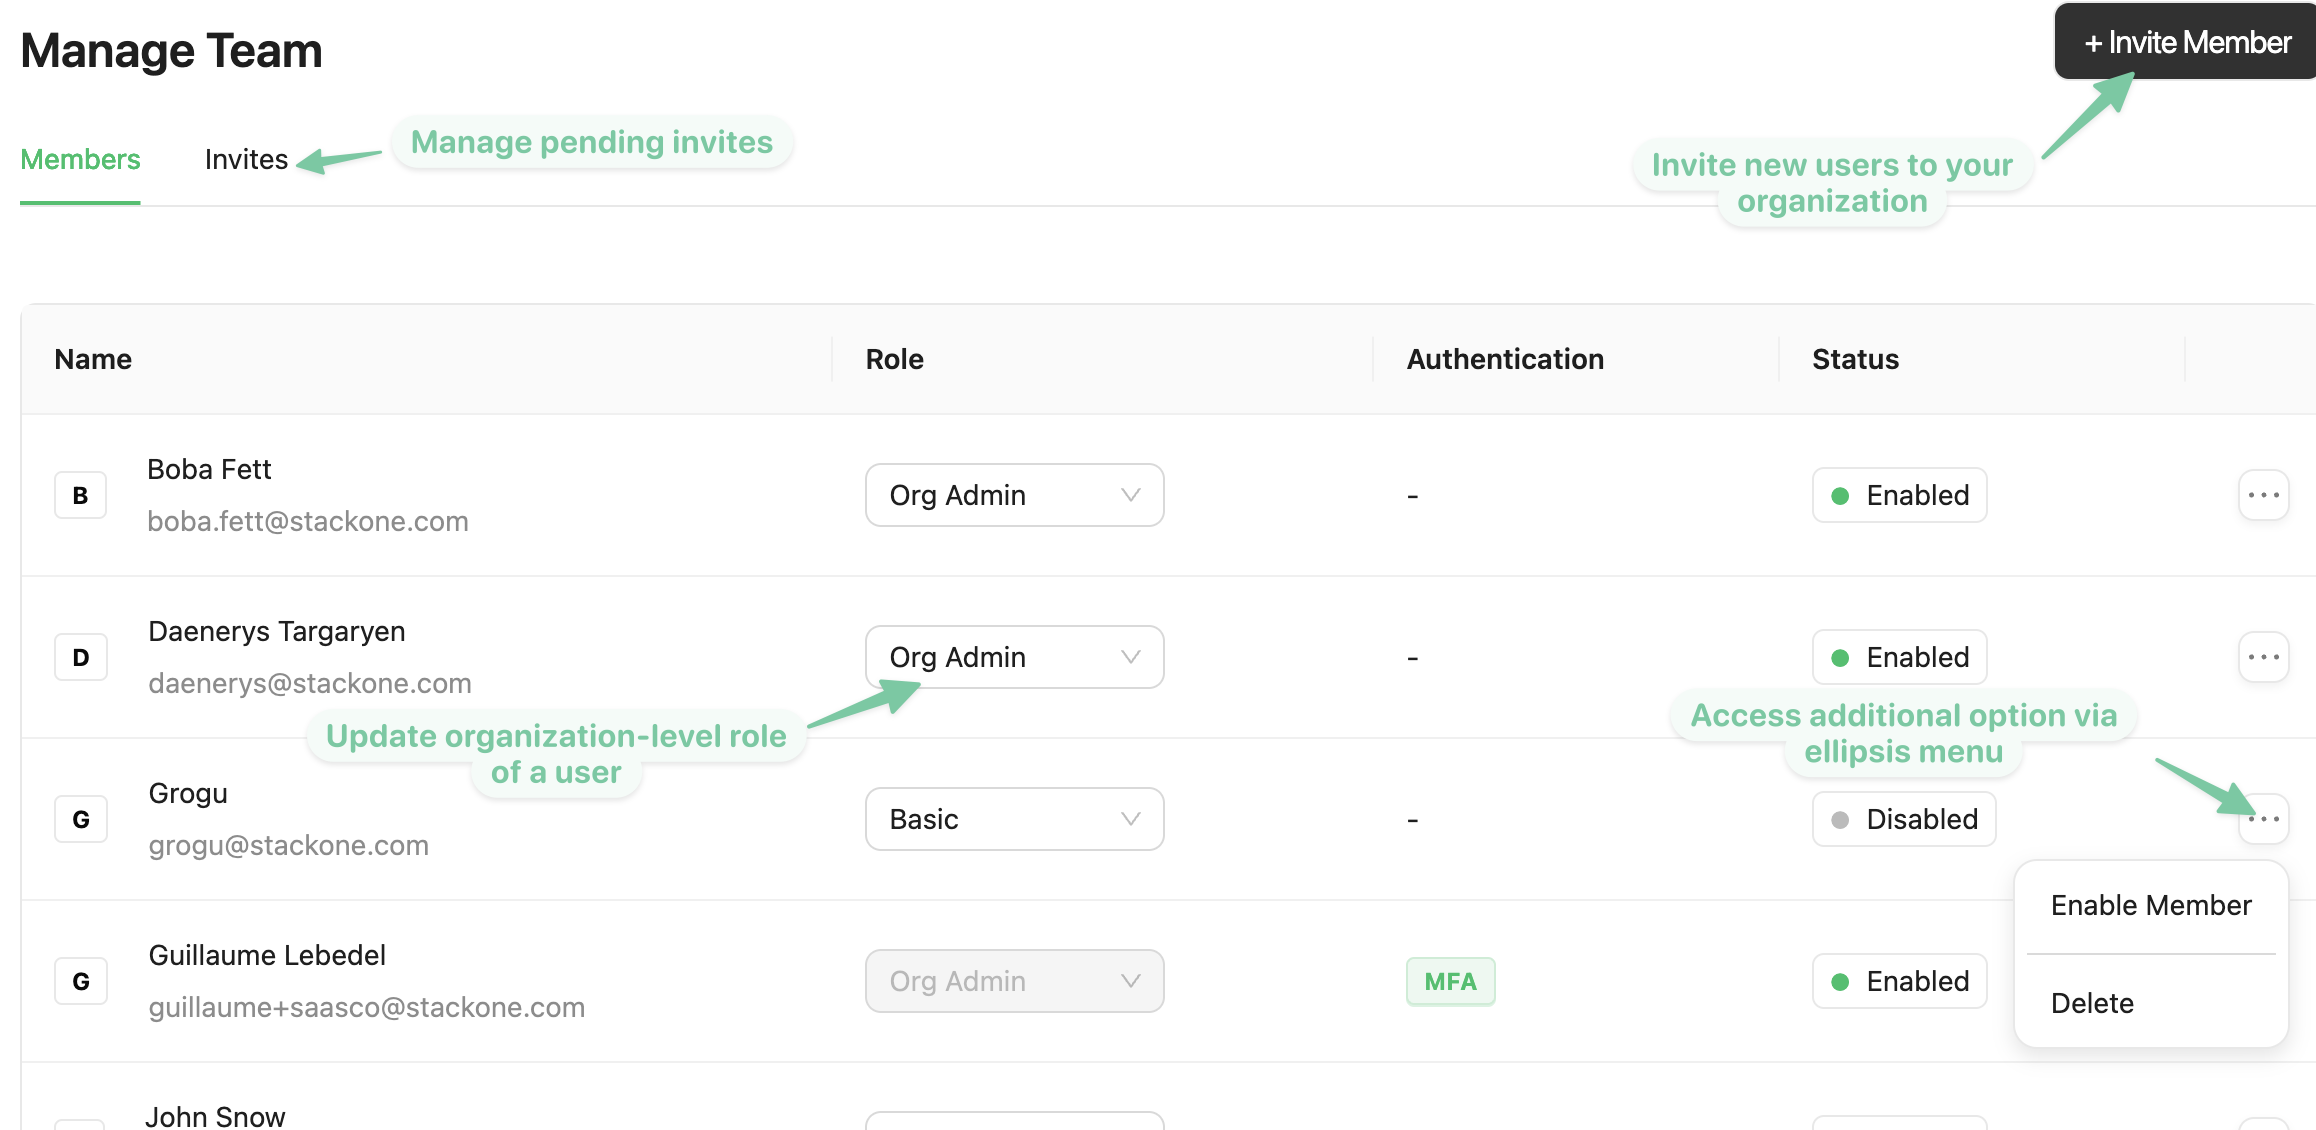
Invite people by email and assign their role at the time of invite. Pending invites can be resent or cancelled.
 ## Change a role
Change a member's org role from the Members list. Project-level access is assigned separately. See [Project members](#project-members).
## Project members
Project access is managed from **Project Settings → Team Members**, separately from org membership. Add or remove members per project and assign one of three roles:
| Resource | Admin | Member | Viewer |
| ---------------------------------------------------------- | ---------------------------------------------------------------------------------- | -------------------------------------------------------------------------- | -------------------------------------------- |
| [Linked accounts](/gateway/concepts/linked-accounts) | Link, edit, re-authenticate, suspend, delete, and run requests against any account | Link their own accounts, then edit, delete, and run requests against those | View status and details |
| [Connector profiles](/gateway/concepts/connector-profiles) | Create, configure, scope actions and events, and delete | View authentication type and enabled actions | View authentication type and enabled actions |
| [Request logs](/connect/troubleshooting) | View | View for their own accounts and accounts shared with them | View |
| [API keys](/embed/api-keys) | Create, scope, and revoke | No access | No access |
| [Webhooks](/connect/webhooks) | Create, route events, and delete | No access | No access |
| Project settings | Manage all settings | No access | No access |
**Member** is the role to use when a whole team needs to connect their own accounts. Each Member can only ever grant access to the accounts they linked themselves, so one project can serve a whole department without everyone seeing everyone else's connections. See [Who can grant access](/connect/ai-platforms/overview#who-can-grant-access) for how this plays out when someone connects an AI platform.
### Sharing a single account
Access can also be granted on one linked account at a time, which is how a shared connection reaches someone who is otherwise only a Member. Open the account, then manage its members:
| On a linked account | Can |
| ------------------- | -------------------------------------------------------------------------- |
| **Admin** | Run actions, edit, delete, re-authenticate, and manage who else has access |
| **Member** | Run actions only |
## Enable, disable, or delete a user
* **Disable** revokes access while keeping the account, so you can re-enable it later.
* **Delete** removes the user from the organization permanently.
From the Members list you can also unlock accounts locked by failed logins and reset another user's MFA.
## Organization security
Open the **Security** page from your user menu to manage these org-wide settings:
| Setting | What it does |
| -------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| MFA | Enforce time-based one-time-password MFA for all current and future members. Members without it are prompted on next login. They scan the QR code (or enter the secret) into any TOTP app, such as Google Authenticator, 1Password, or Bitwarden. |
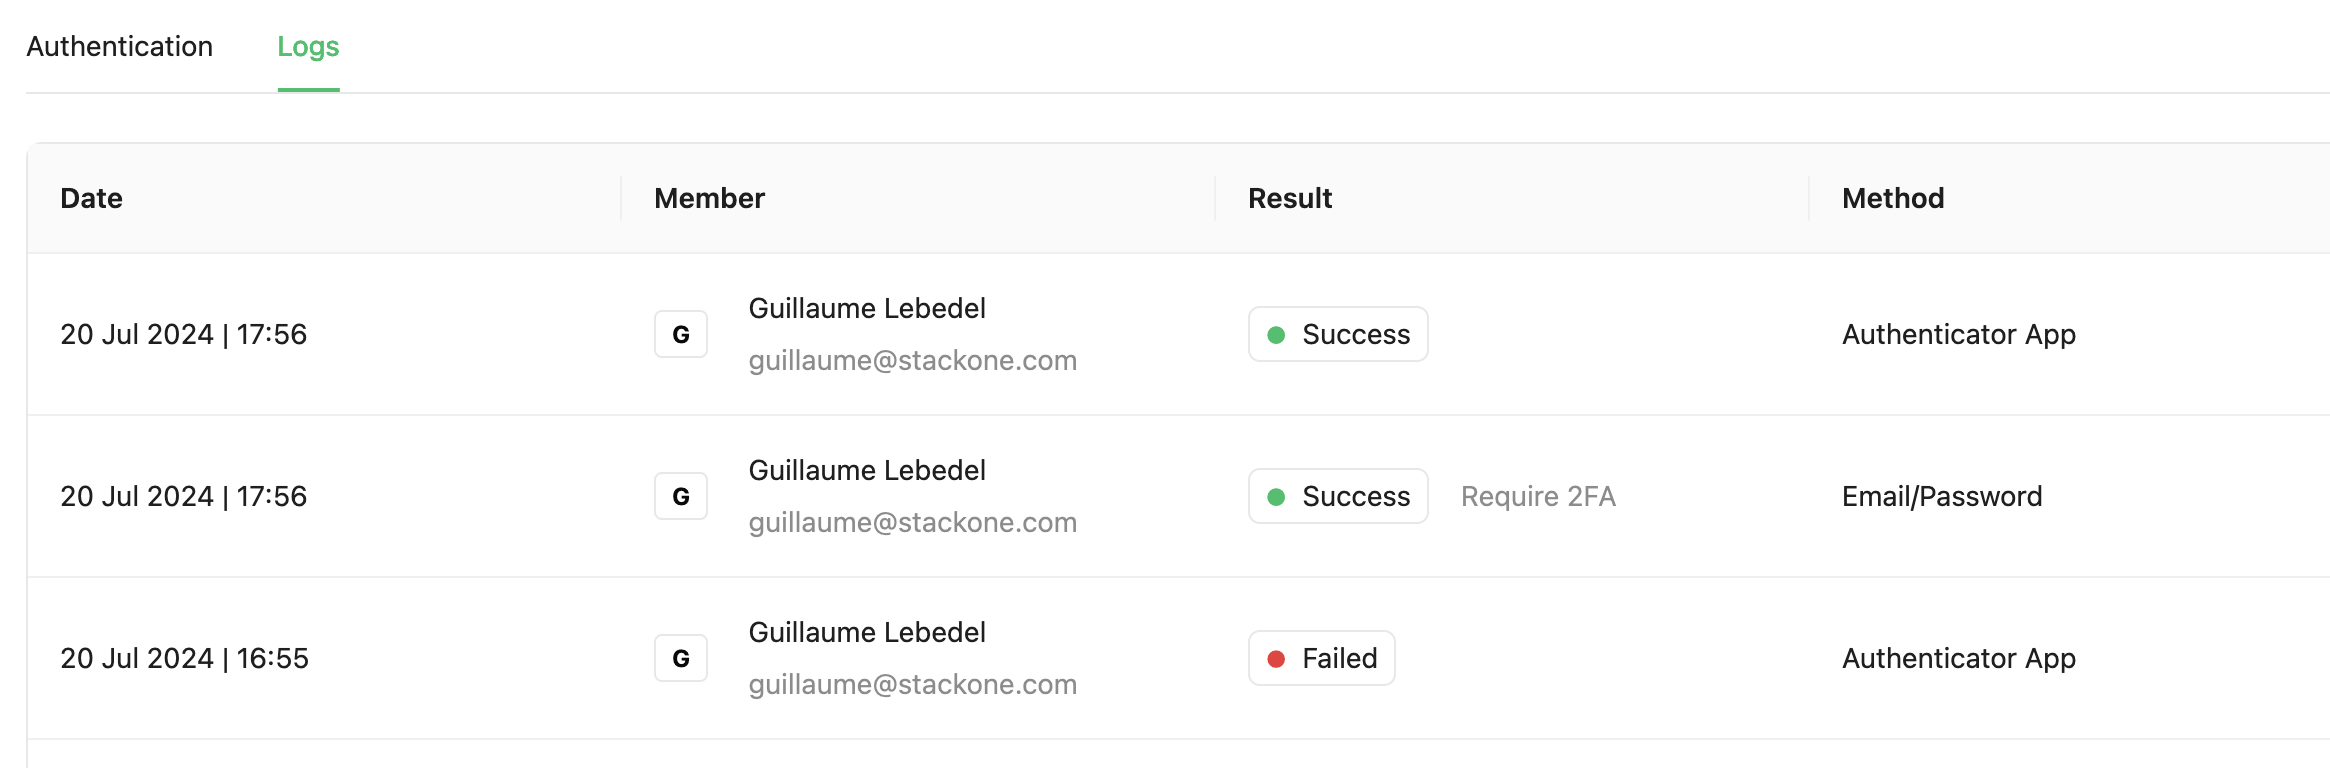
| [Security logs](https://app.stackone.com/organization/security_logs) | A record of every login attempt, success or failure, for monitoring and audit. |
| SSO | Configure SAML 2.0 single sign-on with your identity provider. See [Single Sign-On](/secure/identity-and-access/authentication/sso/overview). |