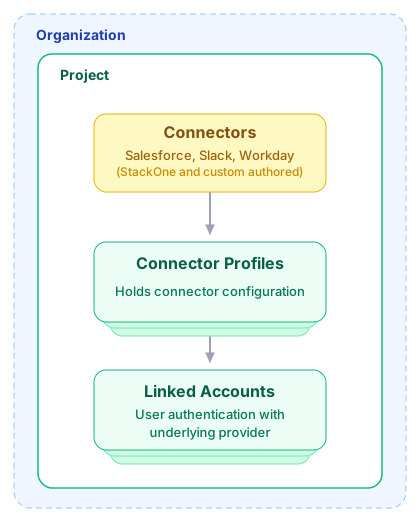
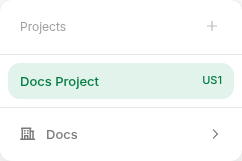
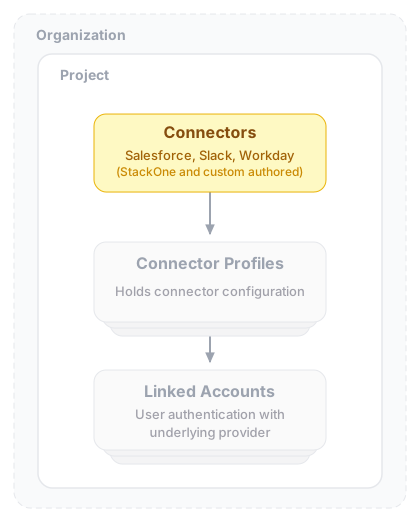
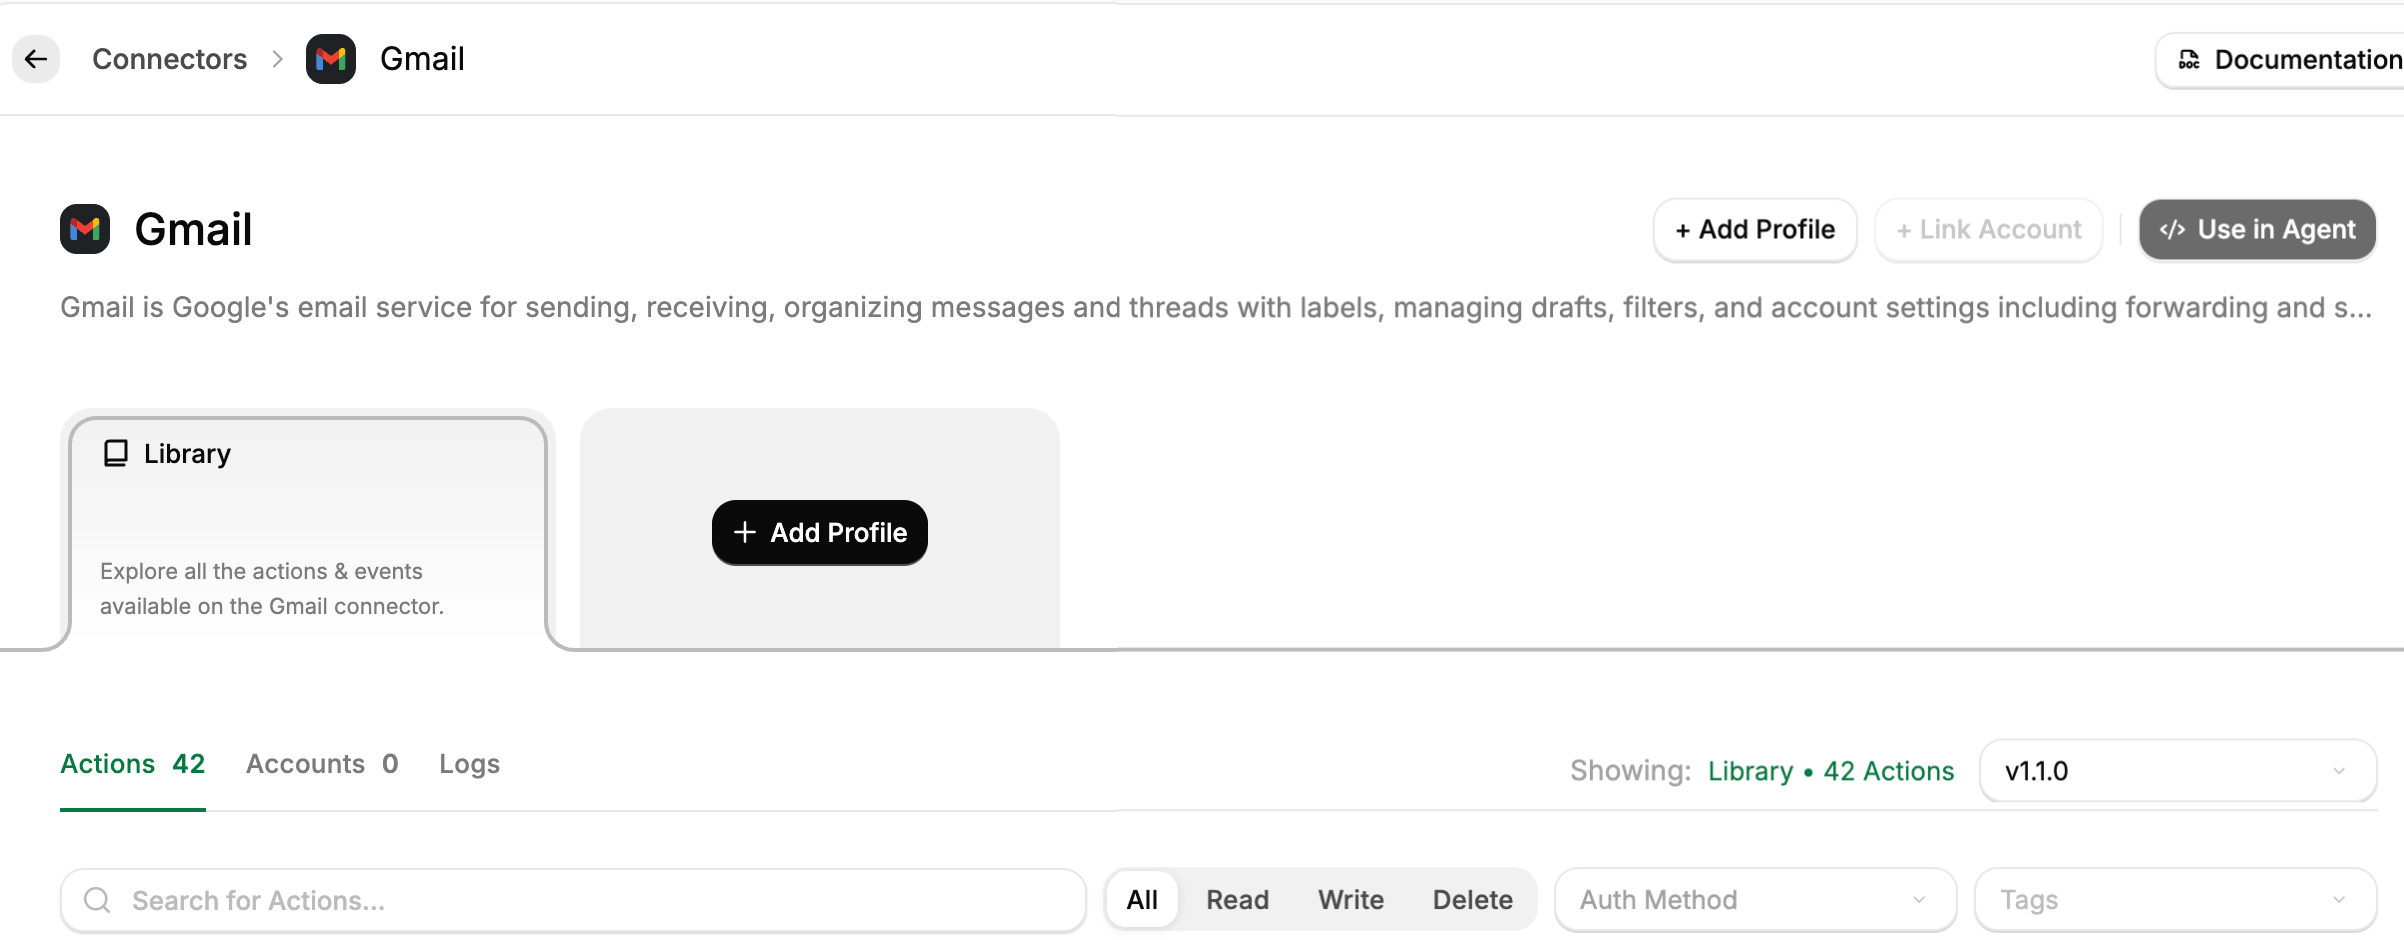
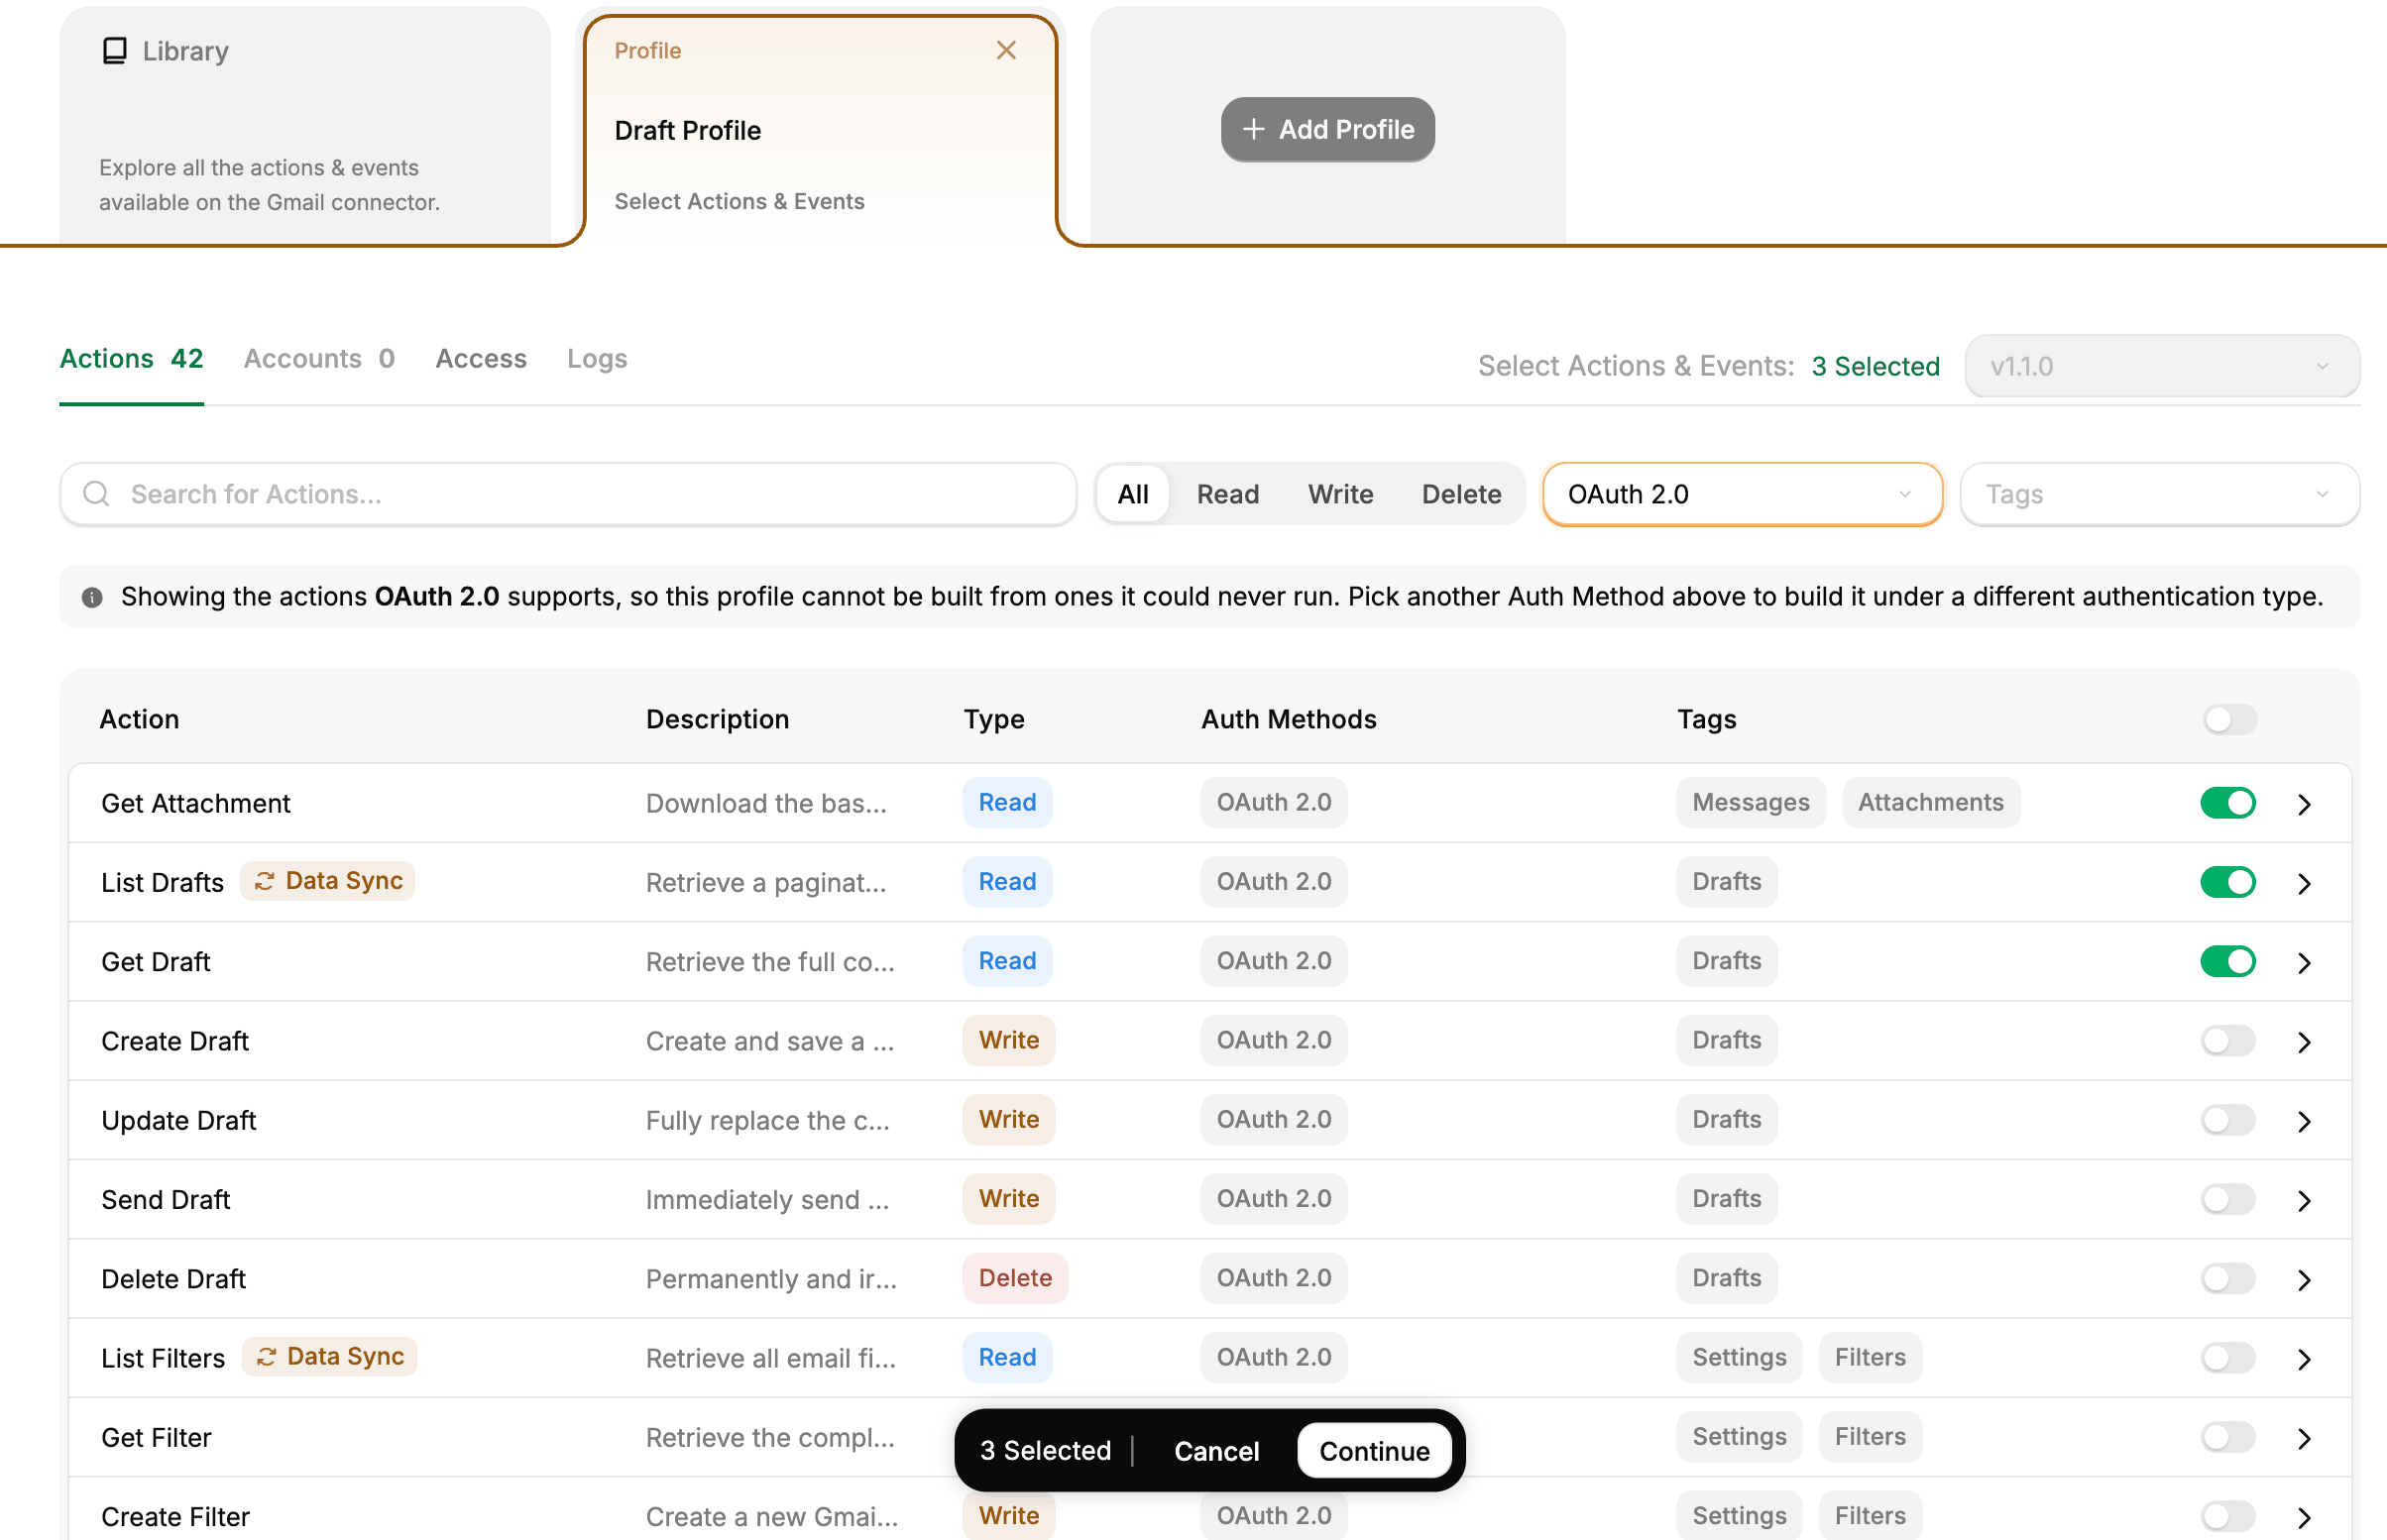
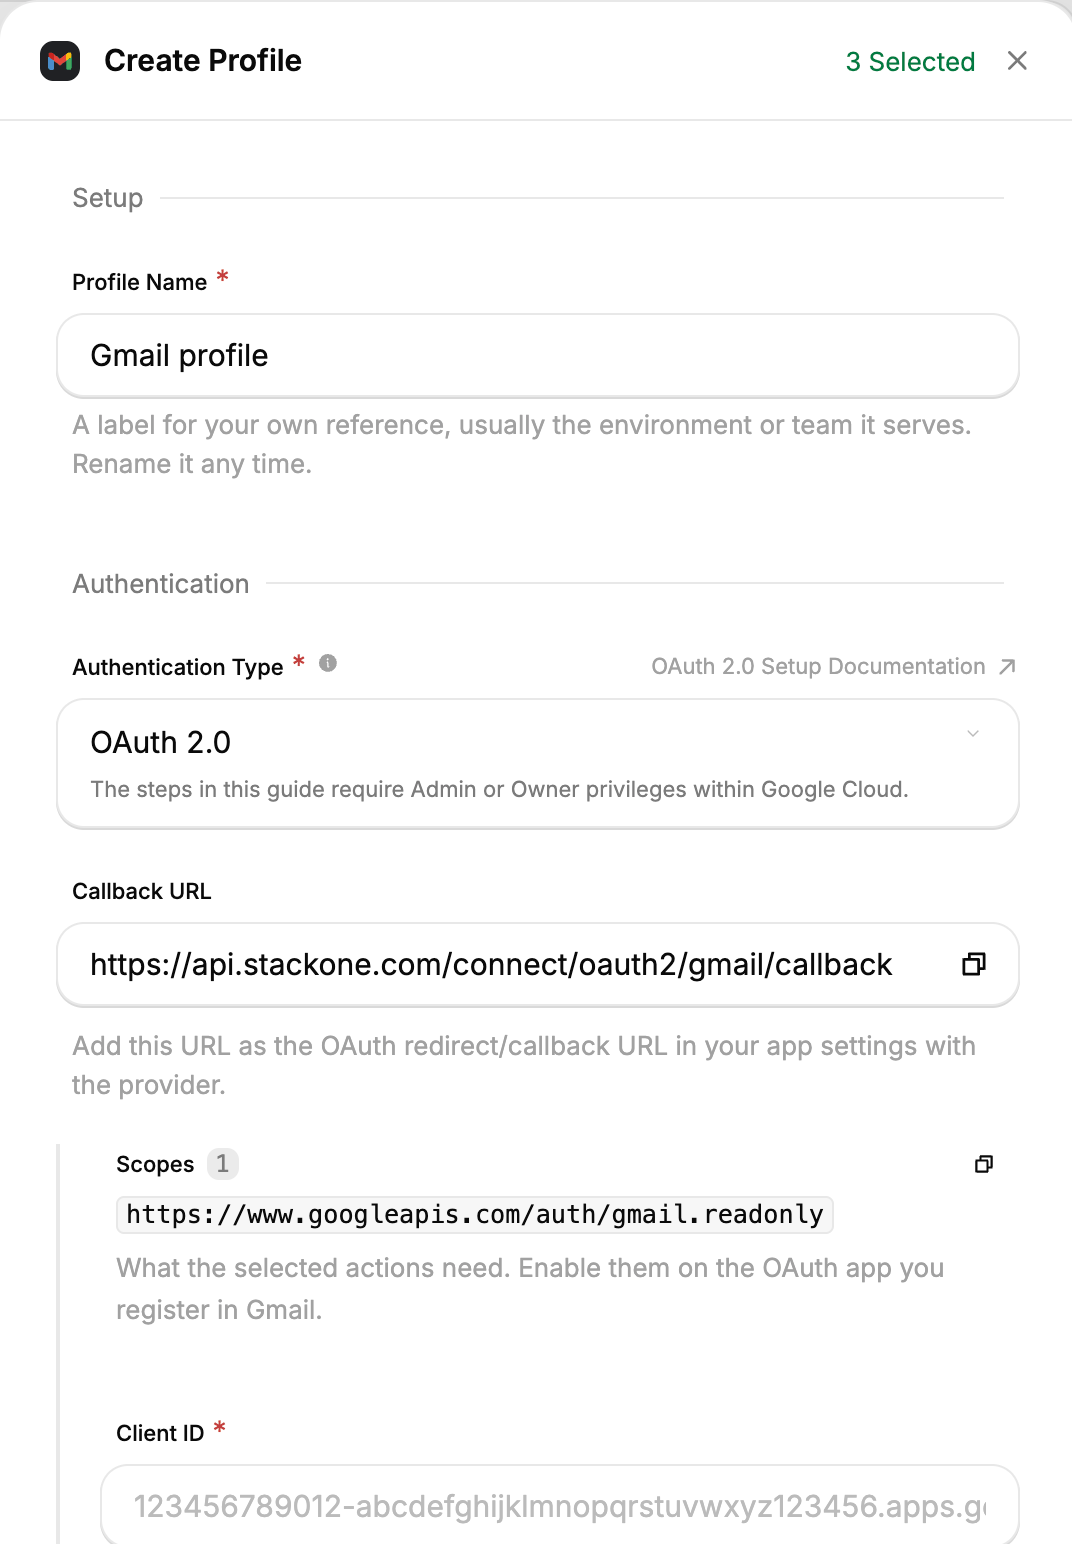
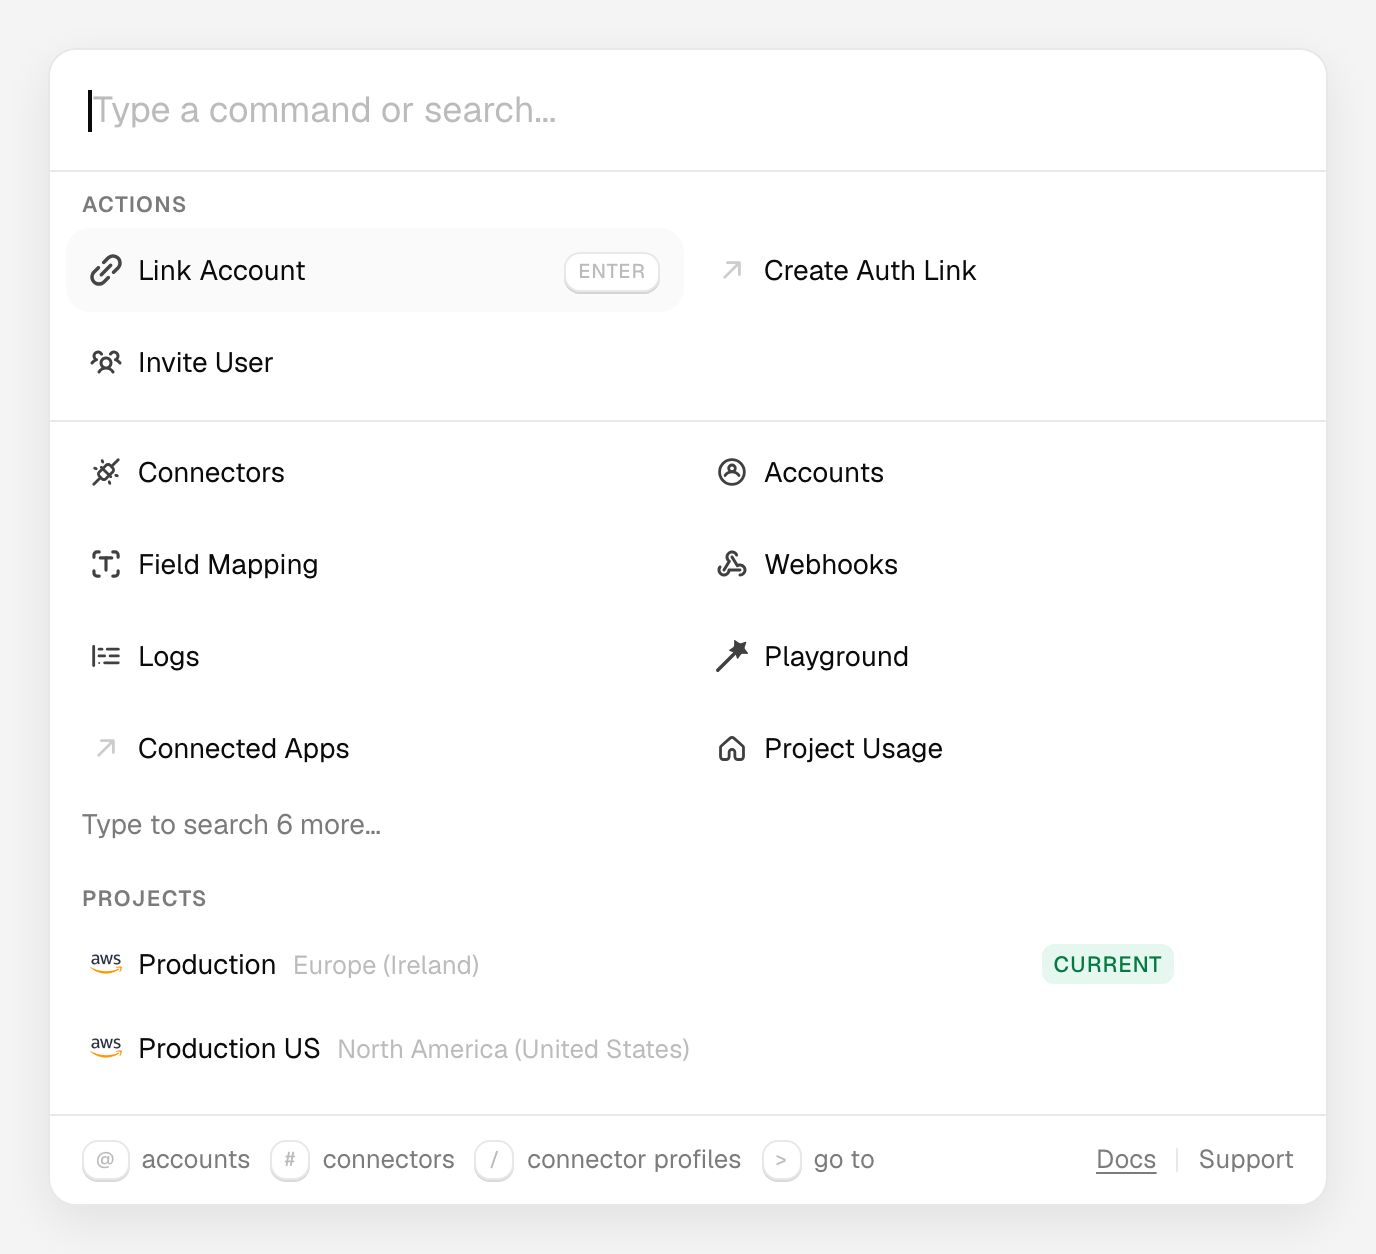
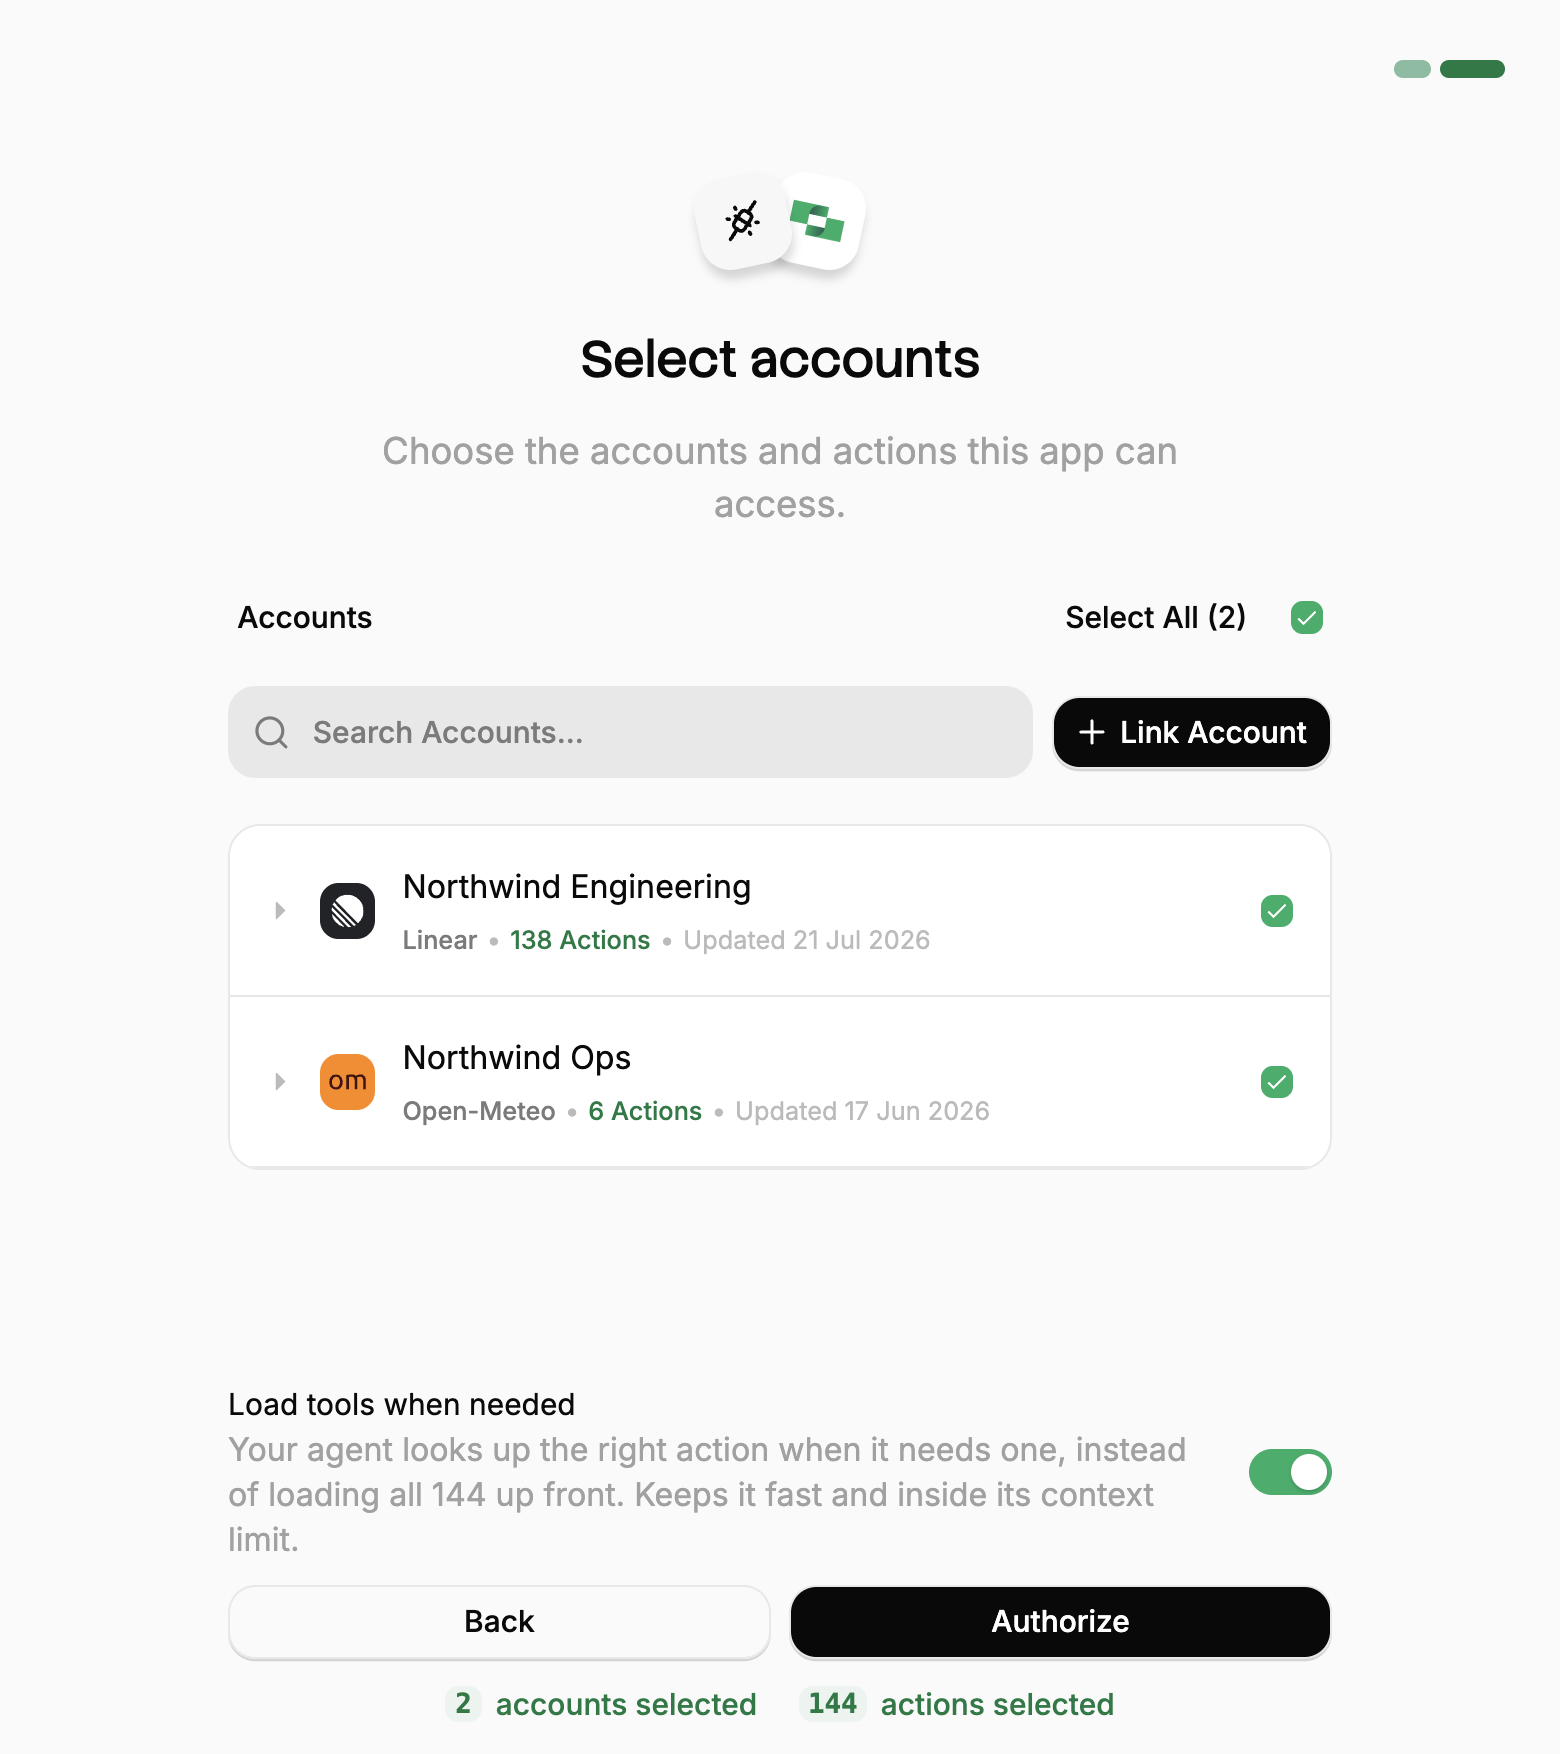
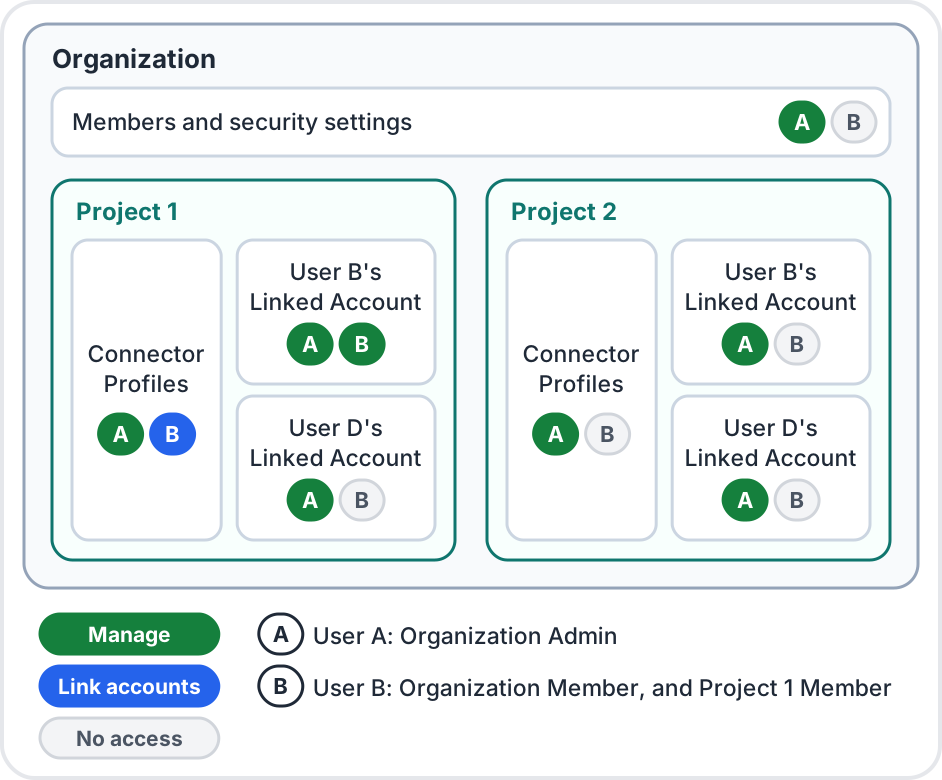
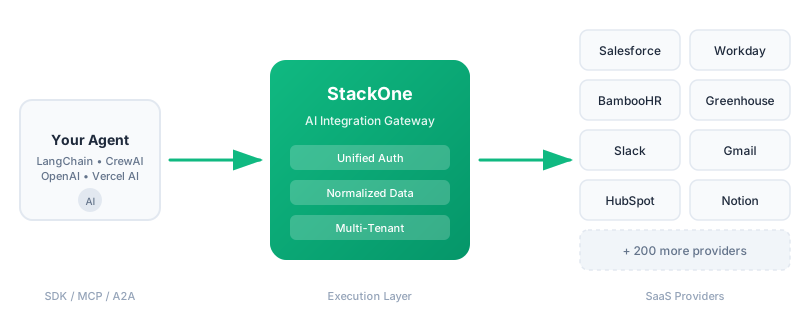
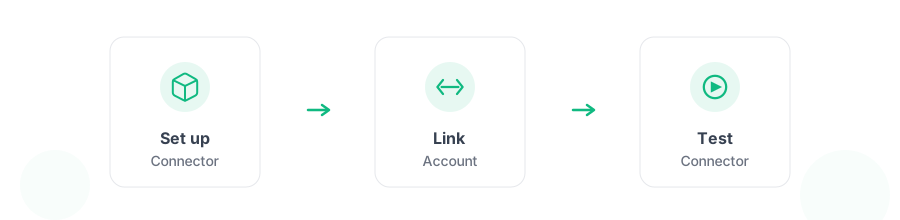
# Introduction Source: https://docs.stackone.com/introduction One gateway. Hundreds of systems. Thousands of actions. Start your journey with StackOne. StackOne is an integration gateway for AI agents. It connects your agents to the hundreds of SaaS systems you already access through one gateway, with any framework or protocol. Copy/paste this prompt into your agent to add context of StackOne: ```text wrap Read https://docs.stackone.com/llms.txt — StackOne's docs index. Use it as context to answer my questions and help me use StackOne. ``` ## Where do you want to start? I want to connect my AI agent to a system I already use and run my first actions. I want to use the StackOne MCP server in ChatGPT, Claude, Cursor, or another AI platform. I want to build a connector for a new system, or tailor an existing one. I want to manage my team's access, limit what agents can touch, and keep an audit trail of every action. I'm building an application and my customers need to connect the tools they already use. I'm building an agent and it needs to act on real business systems. ## Key capabilities Discover the right action from a large catalog, then run it. Search and aggregate synced provider records without calling the provider. Scan tool-call responses for prompt-injection attacks. Roles, SSO, MFA, and audit logs across projects. Call connector actions over MCP, SDKs, A2A, or HTTP. Audit logs, activity tracking, and data retention. # Core Concepts Source: https://docs.stackone.com/gateway/concepts/overview How connectors, profiles, linked accounts, actions, and events fit together, and what happens when your agent calls one. Your Organization contains Projects. Inside a Project, Connector Profiles hold the configuration for a Connector such as Salesforce, Slack, or Workday, and your end-users' Linked Accounts are authenticated against those profiles. A connector is ready to use once these are in place: 1. Set up your [organization and projects](/gateway/concepts/organizations-and-projects). 2. Pick the [connector](/gateway/concepts/connectors) you want and add a [connector profile](/gateway/concepts/connector-profiles) for it. 3. Enable the [actions](/gateway/concepts/actions) and [events](/gateway/concepts/events) you need. 4. [Link an account](/gateway/concepts/linked-accounts) against that profile. 5. [Connect your agent](/connect/overview), or [call actions](/embed/call-actions/rpc-http) directly. Follow the [Quickstart](/gateway/quickstart) guide to run your first action. ## How a request flows When your agent calls an action, the request is scoped to one linked account. StackOne authenticates with the provider, transforms the request to the provider's API format, then normalizes the response for the protocol or SDK you're using. ```mermaid sequenceDiagram participant App as App / Agent participant S as StackOne participant P as Provider Note over App: Organization → Project
(API key scopes the project) rect rgb(236, 253, 245) Note over App,P: Actions — your agent calls out App->>S: Call action for a Linked Account Note over S: Connector Profile —
connector authentication + enabled actions S->>P: Authenticated, transformed request P-->>S: Raw provider response S-->>App: Normalized response end rect rgb(219, 234, 254) Note over App,P: Events — the provider tells you P->>S: Provider webhook S->>App: Normalized event to your webhook end ``` StackOne handles OAuth token refresh, rate limiting, retries, schema normalization, error handling, and audit logging along the way, with optional [PII redaction](/secure/observability#pii-redaction) in request logs. [Events](/gateway/concepts/events) flow the other way. When something changes in a provider, StackOne normalizes it and delivers it to your webhook. # Organizations & Projects Source: https://docs.stackone.com/gateway/concepts/organizations-and-projects Projects are isolated workspaces inside your organization, each with its own region, API keys, and linked accounts. Your StackOne account is structured as an **organization** containing **projects**. Members and security are managed at the organization level; everything you build with lives in a project. ## Organization Your organization is the top level, holding your projects, organization members, and organization-wide security (roles, MFA, SSO). Organization members hold one of two organization roles: - **Admin**: manages who has access and creates projects. Organization Admins automatically see and can access all projects in the organization. - **Member**: only sees the projects they're granted access to, directly or through a [group](/secure/identity-and-access/roles-and-groups/groups). Organization and project roles are independent, so a **Member** at the organization level can be **Admin** on a specific project: full control of that project without organization-wide access. Invite members and assign organization and project roles. Single sign-on for your organization. ## Projects An isolated workspace inside the organization. Each project has its own: - **Name**: can be changed at any time without affecting linked accounts or other settings. - **Region**: set at creation and fixed afterward; it decides where data is stored and appears in the API key as `v1.{region}.xxxxx`. - **API keys**: scoped to one project, so a production key can't reach dev data. - **Project members**: project-level roles, so someone can be a project Admin without organization-wide access. - **Connector profiles and linked accounts**: its own [connector profiles](/gateway/concepts/connector-profiles) and [linked accounts](/gateway/concepts/linked-accounts). Use separate projects to keep environments or regions apart, for example dev vs production, EU vs US, or temporary projects for individual engineers and QA. More than one project is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). ### Create a project Click the project selector in the top-left of the sidebar and select [**Create a project**](https://app.stackone.com/project/new). Only organization Admins can create new projects. Create a Project form with name, description, and region selection | Area | Region | Data Center | Availability | |:-----|:-------|:------------|:-------------| | Europe | 🇮🇪 Ireland (Dublin) | AWS EU-WEST-1 | Available | | Europe | 🇧🇪 Belgium (St. Ghislain) | GCP EUROPE-WEST1 | Available | | North America | 🇺🇸 United States (N. Virginia) | AWS US-EAST-1 | Available | | Other | 🌍 Other regions (e.g. UK, APAC) | — | On request (add-on) | Need a region that isn't generally available? Contact your StackOne account manager. ### Switch projects The project selector in the top-left of the sidebar lists the projects you have access to. The region code appears next to each project name (e.g. `EU1` or `US1`). Project selector listing projects with their region codes ### Project settings Deleting a project (under **Danger Zone**) is immediate and irreversible. It removes everything inside it: linked accounts, API keys, webhooks, and all associated data. Configure a project from **Project Settings** in the dashboard sidebar. Each setting is covered where it's used: Create keys and set their scopes. Manage who has access to the project and what they can do. Request-log retention, error-only mode, and PII redaction. Prompt-injection scanning and blocking thresholds. Whether published connector versions can be overwritten. # Connectors Source: https://docs.stackone.com/gateway/concepts/connectors How StackOne knows to interact with a provider, and the actions and events available for use. Where Connectors sit in StackOne: a connector is configured by a connector profile inside your project, which your end-users' linked accounts are authenticated against. A connector is the definition StackOne uses to know how to interact with a provider. Connectors are scoped to a [project](/gateway/concepts/organizations-and-projects): every project has access to all StackOne-authored connectors, while any [custom connector](/connector-building/overview) you build is available only in the project it belongs to. These are the objects you work with on every connector: Reusable credentials and config, holding the authentication and enabled actions for a connector. An end-user's authenticated connection to a provider. The core unit of work an agent can perform. Real-time notifications from your connectors and from StackOne. ## Explore your connectors The **Connectors page** in the dashboard shows a summary of every connector, including the actions and events available and the profiles and accounts configured for each. Opening a particular connector also shows all logs related to it. For the full list of connectors and what each one supports, browse the [Connectors catalog](/connectors/introduction). # Connector Profiles Source: https://docs.stackone.com/gateway/concepts/connector-profiles The configuration for a connector, including its authentication and which actions and events are available. Where Connector Profiles sit in StackOne: a profile lives in your project, configures a connector, and is what your end-users' linked accounts are authenticated against. A **Connector Profile** holds the configuration for one connector in a project, including which of its actions and events are available to be used. ## What a profile holds | Setting | Description | |---------|-------------| | Authentication type | How end-users connect. The available methods depend on the connector, e.g. OAuth, API Key, or Basic Auth | | Credentials | The authentication fields for that type (e.g. Client ID and Client Secret for OAuth) | | Enabled actions | The [actions](/gateway/concepts/actions) [linked accounts](/gateway/concepts/linked-accounts) can call | | Enabled events | The webhook events the connector can emit | | Access | Whether the profile is **Shared** with the whole project or **Restricted** to granted members and groups | You can configure more than one profile per connector, for example, an API Key profile for some accounts and an OAuth profile for others. The default profile decides which authentication fields appear in the Hub. ## Shared vs restricted Every profile is either **Shared**, so anyone in the project who can link accounts may use it, or **Restricted**, so only the members and groups granted access can. A restricted profile is hidden from the linking flow for everyone else. Restricting controls use, not governance: project admins still view, edit, and delete the profile either way. See [Connector Profile Access](/secure/identity-and-access/roles-and-groups/connector-profile-access). Set up authentication, then choose which actions and events a profile exposes. Register your own OAuth app instead of using StackOne's shared credentials. Pin a profile to a connector version so its behavior stays fixed. Configure, secure, and version the connectors your projects use. ## Connection issues behind a firewall If a provider API or webhook endpoint is behind a firewall, allow inbound traffic from these StackOne IP addresses: | IP address | Location | |------------|----------| | `35.175.11.132` | US East | | `54.221.239.152` | US East | | `52.5.1.25` | US East | | `34.249.109.57` | Ireland | | `46.51.152.189` | Ireland | | `52.51.165.231` | Ireland | Requests from your infrastructure to the StackOne API may pass through [AWS edge locations](https://docs.aws.amazon.com/AmazonCloudFront/latest/DeveloperGuide/LocationsOfEdgeServers.html). If your firewall restricts outbound traffic, allow HTTPS traffic to the AWS edge location ranges and the StackOne IP addresses above. StackOne may add or remove IP addresses when regions or infrastructure change. Check this list when updating your firewall rules. Requests from StackOne use HTTPS with TLS 1.2 or later. StackOne calls providers and remote MCP servers over the public internet, so it needs a public HTTPS address for the system. A private address such as `10.0.4.12` or `metabase.internal` can't be reached. With either setup below, StackOne can reach only the one service you publish, not the rest of your network. Either of these setups works today: - **Publish one endpoint behind your firewall.** Put the system's API behind your existing reverse proxy, API gateway, or web application firewall, and allow only the StackOne IP addresses above. - **Run an outbound tunnel.** Run a tunnel client such as [Cloudflare Tunnel](https://developers.cloudflare.com/cloudflare-one/connections/connect-networks/) or [ngrok](https://ngrok.com/docs) on a host inside your network. It only makes outbound connections and gives you a public HTTPS URL that forwards to one internal service. Restrict that URL to the StackOne IP addresses above. Then point StackOne at the public URL: - **A connector that asks for your instance URL**, such as a self-hosted Grafana or OpenSearch. Enter the public URL when linking the account. - **Your own MCP server**, if MCP connectors are enabled for your organization. Enter the public URL as the **Remote MCP Server URL** when [adding the MCP connector](/connect/managing-connectors/adding-mcp-connectors). Keep authentication on the endpoint itself, such as the provider's own credentials or OAuth on your MCP server. An IP address list limits where requests come from, but StackOne's addresses are shared by every StackOne customer. A tunnel or proxy sign-in page meant for a person in a browser blocks StackOne's requests, so use IP rules at the tunnel instead. Expose only the service StackOne needs, never a whole subnet. Requests and responses pass through StackOne. If they must stay inside your network, contact your StackOne account team. # Linked Accounts Source: https://docs.stackone.com/gateway/concepts/linked-accounts An end-user's authenticated connection to a provider. Where Linked Accounts sit in StackOne: each account comes off a connector profile inside your project and represents one end-user's connection to a connector. A **Linked Account** is one end-user's authenticated connection to one provider, whether that's their Salesforce, Slack, or whichever system they use. StackOne creates it when they connect and stores the credentials. If you serve many customers, see [Multi-Tenant Accounts](/features/multi-tenant-accounts) for keeping their accounts separate. ## Account status An account's status tells you whether it can currently serve calls. | Status | Meaning | |--------|---------| | **Active** | Credentials are valid and the account is serving calls. | | **Suspended** | Manually paused, so no actions can be called against it. Credentials stay saved, so the account can be resumed later without re-authenticating. | | **Error** | Calls are failing, usually expired credentials or revoked provider access. Re-authenticate the account to recover it. | Subscribe to the `account.updated` and `account.deleted` [webhook events](/embed/handle-account-events) to react to status changes instead of polling. ## Related The ways your end-users connect their accounts. Segment, list, and monitor accounts per customer. React when accounts are created, re-authenticated, or removed. Which project roles can view, edit, and delete accounts. Inspect request logs for a failing account. # Actions Source: https://docs.stackone.com/gateway/concepts/actions The core unit of work an agent can perform. An **Action** is one operation your agent can perform against a provider, such as `salesforce_get_contact` or `gmail_list_messages`. StackOne provides thousands of actions across all connectors. ```mermaid sequenceDiagram participant App as App / Agent participant S as StackOne participant P as Provider rect rgb(236, 253, 245) Note over App,P: Actions — your agent calls out App->>S: Call action for a Linked Account Note over S: Connector Profile —
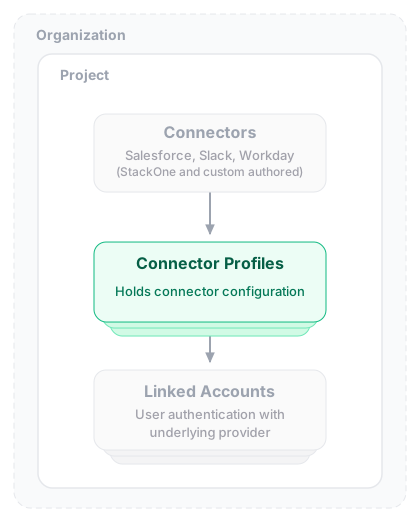
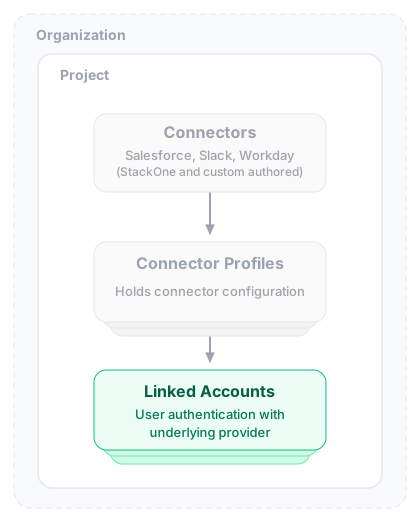
connector authentication + enabled actions S->>P: Authenticated, transformed request P-->>S: Raw provider response S-->>App: Normalized response end ``` ## Calling an action Each action is called against a [linked account](/gateway/concepts/linked-accounts), and its [connector profile](/gateway/concepts/connector-profiles) determines which actions are available. See [Connect](/connect/overview) for the ways to call them. Some read actions can also be synced on a schedule by [Data Sync](/optimize/data-sync/overview), which lets an agent search and aggregate their records with [Deep Query](/optimize/deep-query) instead of calling the provider. Each connector page lists its available actions. The ways to call an action from your agent or your code. # Events Source: https://docs.stackone.com/gateway/concepts/events Real-time notifications from your connectors and from StackOne. An **event** is something that happened — a Slack message arrived, a file was added, an account was connected — delivered to your **webhook** (an HTTPS endpoint) in real time, so your app reacts without polling. ```mermaid sequenceDiagram participant App as App / Agent participant S as StackOne participant P as Provider rect rgb(219, 234, 254) Note over App,P: Events — the provider tells you P->>S: Provider webhook Note over S: Connector Profile —
enabled events + webhook routing S->>App: Normalized event to your webhook end ``` ## Kinds of events - **Connector events**: fire from a provider (a new Notion page, a file dropped in SharePoint). Enabled per connector on its [connector profile](/gateway/concepts/connector-profiles). They include [Data Sync events](/optimize/data-sync/events), which StackOne sends when a sync run finds a record that was created, updated, or deleted at the provider, for example `bamboohr_list_employees.updated`. - **[Platform events](/platform-api/platform-events)**: fire from StackOne itself, covering account lifecycle: `account.created`, `account.updated`, `account.deleted`. Set up a webhook, subscribe to events, and verify delivery. # Quickstart Source: https://docs.stackone.com/gateway/quickstart Connect your agent to one or more of your existing systems and run your first actions. Connect your agent to one or more of the systems you already use — Zendesk, Gmail, Salesforce, and hundreds more — and run your first actions. Quickstart steps: Connect a system, Link an account, Run actions ## Connect through the dashboard If you currently don't have an organization or project, you'll be prompted to create them on first login. Once that's done, continue below to start using a connector. ### Setup Connector Profile Before linking an account, you need a [Connector Profile](/gateway/concepts/connector-profiles). It holds the connector's authentication and decides which actions and events your agent can use. You create it on the connector's own page. 1. In the StackOne dashboard sidebar, open [Connectors](https://app.stackone.com/connectors). 2. Search for the connector you want to use (e.g. Zendesk, Gmail, Salesforce) and select it. The connector page shows a row of cards. **Library** lists every action and event the connector offers, and each of your profiles for this connector gets a card next to it. 3. Click **Add Profile**. This starts a **Draft Profile**. Gmail connector page with a Library card, an Add Profile card, and Actions, Accounts and Logs tabs The draft starts with every action selected. To start small, turn off the switch in the table header to clear the selection, then turn on a few read actions. If the connector supports events, turn them on in the **Events** tab and choose the [webhook](/connect/webhooks) each one delivers to. See [Scoping Connectors](/secure/scoping-connectors). The **Auth Method** filter shows which authentication type the draft is built for. A profile can only include actions its authentication type can run, so pick another method there if the actions you need are hidden. Draft Profile on the Gmail connector page with three read actions switched on and a bar showing 3 Selected with Cancel and Continue Click **Continue**. The **Create Profile** panel opens. 1. Leave the **Profile Name** as the default value. It's a label to tell your profiles apart in the dashboard. 2. If more than one option exists, choose the **Authentication Type** you want to use. The link next to it opens that method's setup guide. 3. Fill in any credential fields the connector needs, such as a Client ID and Client Secret or an API key. If you're using [your own OAuth app](/connect/managing-connectors/using-your-own-oauth-apps), copy the **Callback URL** into its settings with the provider. 4. Leave **Update strategy** at its default. It controls which connector versions the profile moves to. See [Connector Versioning](/connector-building/connector-versioning). Some connectors need extra configuration on the provider side. Check the [Connector Guides](/connectors/introduction) and follow the relevant Connector Profile guide. Create Profile panel showing Profile Name, Authentication Type set to OAuth 2.0, the Callback URL with a copy button, the scopes the selected actions need, and the Client ID field 5. Click **Create Profile**. The profile appears as a card on the connector page. If you're a project admin, the profile is ready to link an account. If you're a project member, it's created disabled, and a project admin has to enable it first. ### Link Account There are multiple methods for linking an account. In this guide, we'll link one directly through the StackOne dashboard. At the top of the connector page, click **Link Account**. It becomes available once the connector has a profile. This opens the **Link an Account** popup. Link an Account popup showing the three connection methods with Method 2 - Authenticate Now selected These fields identify which of your customers the account belongs to. See [Multi-Tenant Accounts](/features/multi-tenant-accounts#identifying-the-client-on-each-account) for how they tie accounts to your clients. For this walkthrough, leave the default values and click **Next**. Confirm the Connector Profile you configured earlier is selected, then click **Next**. Depending on the Connector there may be additional fields to complete and/or additional configuration on the provider system. Click **Connection Guide** in the top right for more details if needed. Click **Connect**. You may need to complete authentication with the provider (e.g. via OAuth). A new window will pop up prompting you to sign in as needed. Once authorization is complete, your **Account** will now be linked in StackOne.
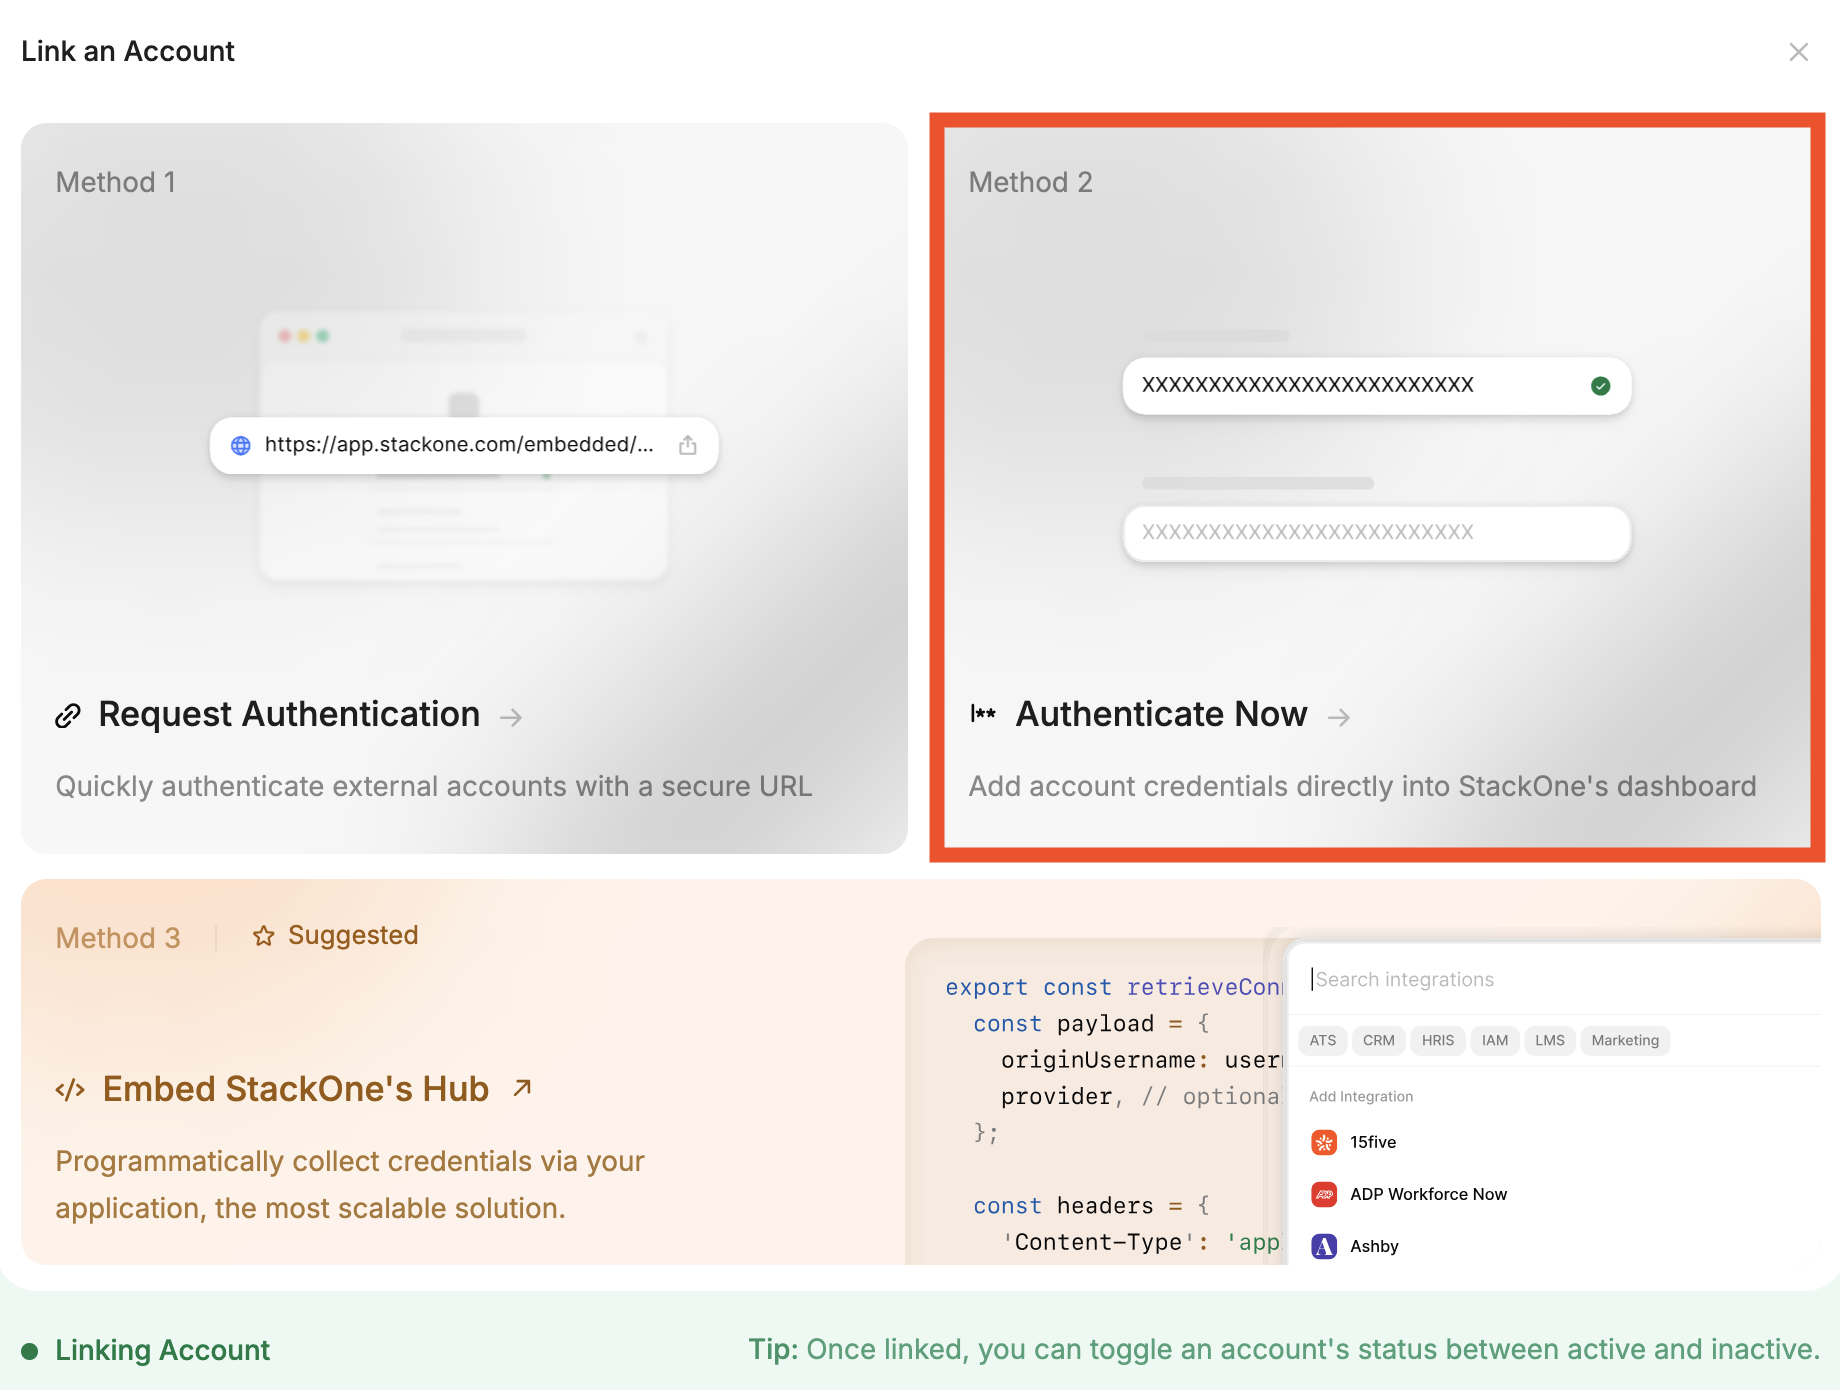
### Call Actions With a linked account in place, check it works in the [Playground](/embed/call-actions/troubleshooting/playground). Run actions in natural language, no code. In the dashboard sidebar, open [Playground](https://app.stackone.com/playground). Click **Manage Action Sources**, select the account you linked, and click **Done**. Try a prompt like: ```text What tools can I use? ``` ```text List the latest 5 records ``` ## Next steps Add the connector's actions to ChatGPT, Claude, Cursor, and more through the StackOne MCP server. Each user signs in with OAuth. Call the connector from your own code with the Agent SDK, MCP, A2A, or RPC/HTTP. # Dashboard Source: https://docs.stackone.com/gateway/dashboard Find your way around the StackOne dashboard. The [StackOne dashboard](https://app.stackone.com) is where you configure everything your agents use (connectors, API keys and webhooks) and where you monitor what they do. The project selector at the top of the sidebar [switches between projects](/gateway/concepts/organizations-and-projects#switch-projects), the **Organization** menu opens [team and security settings](/secure/identity-and-access/manage-team/overview), and your name at the bottom opens your account settings. ## Quick search (Cmd+K) Press `Cmd+K` (Mac) or `Ctrl+K` (Windows/Linux) anywhere in the dashboard, or click **Search** at the top of the sidebar, to open the command palette. It opens on actions such as **Link Account**, **Create Auth Link** and **Invite User**, then lists the dashboard's pages and your projects. The palette offers only the pages and actions your role can use, the same ones the sidebar shows you. Command palette showing the Link Account, Create Auth Link and Invite User actions, dashboard pages, and two projects with their regions Type to search pages, Linked Accounts, connectors, Connector Profiles and projects. Each project shows the region it runs in, and the project you're working in is tagged **Current**. If you belong to more than one organization, the results include your organizations, and selecting one switches to it. Sections with more than eight matches show the first eight, followed by a **Show more** row. ### Search one kind of result Start your search with one of these characters to search only one kind of result: | Type | To search | |------|-----------| | `@` | Linked Accounts, by name, account ID or connector | | `#` | Connectors | | `/` | Connector Profiles | | `>` | Dashboard pages and actions | The scope appears as a label in the search box. Command palette scoped to Accounts, with the search health matching two Linked Accounts and their connector, account ID and status ### Keyboard shortcuts | Key | What it does | |-----|--------------| | `Cmd+K` / `Ctrl+K` | Open the command palette | | `↑` / `↓` | Move through the results | | `Enter` | Open the selected result | | `Esc` | Clear the search. Press it again to close the palette | | `Backspace` | Remove the scope, when the search box is empty | # Platform Features Source: https://docs.stackone.com/gateway/platform-features Connect agents to any system, secure every call, and optimize for speed and cost. StackOne works across all your existing systems to **connect**, **secure**, and **optimize** your agents, not just an action caller. ## Connect Connect to everything your agents need, without writing the infrastructure to get there. Actions tested and ready to use straight away. Build or extend a connector via code in minutes. Connect your way with MCP, A2A, the Agent SDK, or RPC. Real-time event tracking for connectors and accounts. Add connectors to ChatGPT, Claude, Cursor, and more using config only, no code. One normalized schema per category — documents, identity, permissions — across every provider. ## Optimize Maximize agent efficiency for faster responses, higher accuracy, and fewer tokens. Reduce context and save tokens. Poll and store provider records on a schedule. Search and aggregate synced records without hitting the provider. ## Secure Controls to help your agent meet your security and compliance requirements. Block prompt injections before they reach your agent. Granular permissions per agent, per action. Trace every tool call, audit every step. Regional deployments with zero data retention. # Connect Source: https://docs.stackone.com/connect/overview The ways to call a connector's actions, from an AI platform or from your own code. Every connector needs a [connector profile](/gateway/quickstart#setup-connector-profile) and a [linked account](/gateway/quickstart#link-account) first. With an account linked, its actions are ready to use. Attach them to an [AI platform](#attach-an-ai-platform), or use one of the [protocols and SDKs](#protocols--sdks) that fits your stack. All share the same actions. ## Attach an AI platform Pick the platform your users already run. Each connects to the [StackOne MCP server](/connect/ai-platforms/overview) and signs in with OAuth: ## Protocols & SDKs Call the MCP server from your own product or agent framework with an API key and account ID. Build a custom agent with typed TypeScript or Python tools for LangChain, CrewAI, OpenAI, and Vercel AI. Orchestrate multiple agents with pre-built agents per integration, which keeps context lean. Call actions from a backend or script with no agent or framework. You can mix them, for example MCP for internal tools and the SDK for your product. For a fuller breakdown, see [Call Actions](/embed/call-actions/overview). ## Test your actions Try a connector's actions before wiring them into your product. Pick the tool that fits what you're checking: Explore actions with natural language for discovery and prototyping in the dashboard. Execute endpoints with structured parameters. Verify connections and debug responses. Test the MCP server with a pre-built collection. Inspect JSON-RPC requests directly. # Managing Connectors Source: https://docs.stackone.com/connect/managing-connectors/overview Configure, secure, version, and extend the connectors your projects use. Everything that keeps your connectors running, from setting up authentication to versioning and building new ones. This assumes you already have a connector profile. To create one, follow [Setup Connector Profile](/gateway/quickstart#setup-connector-profile) in the Quickstart. ## Connector Profiles A connector can have more than one [connector profile](/gateway/concepts/connector-profiles), with one set as default. That default is used when there is no specific connector profile supplied during the [account linking](/connect/managing-connectors/linking-accounts) process. You manage a connector's profiles on its page in [Connectors](https://app.stackone.com/connectors). Each profile is a card next to **Library**. Select a card to see that profile on the **Actions**, **Events**, **Accounts**, **Access**, and **Logs** tabs. Project admins can edit any profile there, and project members can edit the profiles they created. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles). The menu in the card's corner holds everything else: **Edit profile** for its name, credentials, and update strategy, and the options to make it the default, disable it, or delete it. Profile card menu with Edit profile, Copy ID, Copy Connector Key, Make Default Profile, Disable Profile, and Delete Profile Authentication, scopes, and the version pin all live on the profile, so a second profile is how you vary any of them for a subset of your accounts: | Reason | Example | |---|---| | Two authentication methods for the same connector | An API Key profile for customers without OAuth, and an OAuth profile for everyone else | | Different action and event scopes | A read-only profile for trial accounts, a full-access one for paid | | A staging profile for a new connector version | Pin one profile to `2.x.x` and test it before moving production profiles off `1.x.x` | A profile's authentication type is fixed once it exists. To switch types, create another profile. Disabling a connector profile takes it out of service without deleting anything. It disappears from the Hub, and its linked accounts go `inactive` until you re-enable it. The default profile can't be disabled, so make another profile the default first. Deleting a profile is more restricted: it has to have no linked accounts, and it has to be either the connector's only profile or a non-default one. Only project admins can enable, disable, or change the default profile. Requests against an `inactive` account are blocked, so disabling a connector profile stops live traffic for every account linked to it. A profile created by a project member who isn't an admin starts disabled. A project admin has to enable it before accounts can use it. ## Next steps Connect a remote MCP server and use its tools as actions. View, re-authenticate, and remove the accounts your agents act on. Choose which actions and events a profile exposes. Your brand on the consent screen and dedicated rate limits. Build or customize a connector when a pre-built one doesn't fit. # Adding MCP Connectors Source: https://docs.stackone.com/connect/managing-connectors/adding-mcp-connectors Add a remote MCP server from the dashboard and choose when to link an account. An MCP connector turns any remote MCP server into a StackOne [connector](/gateway/concepts/connectors). Its tools become [actions](/gateway/concepts/actions), and you govern it the same way as every other connector. Use one when the system your agents need already has an MCP server, such as one your team runs or one a provider publishes, and no [pre-built connector](/connectors/introduction) covers it. If MCP connectors are enabled for your organization, **Organization Admins**, **Project Admins**, and **Project Members** can connect remote MCP servers directly from the dashboard. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles) for what each role can do. 1. In the StackOne dashboard sidebar, open [Connectors](https://app.stackone.com/connectors). 2. Click **Add MCP Connector**. Set the following: - **Name**: what to call the connector in the connectors list. The connector's key is derived from it and can't be changed later. - **Remote MCP Server URL**: the public `https://` address where the server accepts MCP requests. - **OAuth Client ID** and **OAuth Client Secret**, under **Advanced Settings**: only needed when the server signs in through OAuth and doesn't register clients dynamically. Leave the secret empty for a public client that uses PKCE. **Organization Admins** and **Project Admins** choose one of: - **Link Now**: link an account in the StackOne Hub straight away to create a [linked account](/gateway/concepts/linked-accounts). Its tools load as soon as the account is linked. - **Link Later**: save the connector without an account. **Project Admins** and **Project Members** can link one from the connector's page, and its tools load once they do. **Project Members** always link their account straight away. The connector and the account stay disabled until a **Project Admin** or **Organization Admin** enables them. - With **Link Now**, click **Next**, then link the account in the StackOne Hub. - With **Link Later**, click **Save**. Closing the StackOne Hub before the account is linked **removes the connector**. Run through these steps again to add it. For **Organization Admins** and **Project Admins**, the connector is available once the account is linked. Each tool on the server appears as an action on the **Actions** tab. An MCP connector has no actions until an account is linked to it, so a connector saved with **Link Later** shows none at first. ## Next steps Choose which actions and events a profile exposes. Connect the client your agents run in to StackOne. View, re-authenticate, and remove the accounts your agents act on. # Linking Accounts Source: https://docs.stackone.com/connect/managing-connectors/linking-accounts Connect the provider accounts your agent will act on. Once a [connector profile](/gateway/concepts/connector-profiles) is enabled, the next step is for each end-user to **link their account**. They authenticate with the provider (OAuth or credentials) so StackOne can act on their behalf. The resulting linked account is what your agent, API calls, and tools then run against. ## Connection methods | Method | Best for | |--------|----------| | [Embedded Hub](/embed/account-linking/stackone-hub) | Production apps: in-app, branded | | [Auth Link](/embed/account-linking/auth-link) | Email flows, sales-led onboarding, demos | | Dashboard linking | Manual linking by your team: internal tools, ops, or on a customer's behalf | For Auth Links there's no frontend callback. Subscribe to account [webhooks](/connect/webhooks) to know when an account is linked. The profile picker only offers connector profiles you're allowed to use. A [restricted profile](/secure/identity-and-access/roles-and-groups/connector-profile-access) is hidden when linking, in the dashboard and in the Hub, unless you've been granted access to it. ## Link from the dashboard You can link accounts directly from the StackOne dashboard without embedding the Hub. The linking flow depends on your organization type: 1. In the dashboard, open [**Connectors**](https://app.stackone.com/connectors). 2. Select the connector. 3. Click **Link Account**. **Organization Admins** set the following: - **Account Name**: Optional. Default is your name in front of the connector name, for example `John's Slack`. - **Connector**: Select the [connector profile](/gateway/concepts/connector-profiles) to use. Click **Next**. **Project Members** skip this step and link with the project's default connector profile. 1. Enter any required credentials. 2. Click **Connect**. 3. If the provider asks you to authorize, for example through OAuth, complete authorization with the provider. Once authentication succeeds, the Linked Account is created. To confirm, open the connector's page and select the **Accounts** tab. **Organization Admins** use the account linking wizard to link an account on behalf of a customer. 1. In the dashboard, open [**Connectors**](https://app.stackone.com/connectors). 2. Select the connector. 3. Click **Link Account**. Select **Authenticate Now** to enter the customer's credentials yourself. **Project Members** skip the wizard and go straight to the Hub with the project's default connector profile. Continue from **Connect the account**. These details identify the customer the Linked Account is for. Set the following: - **Owner ID**: The customer's identifier in your system. - **Account Name**: The customer's name. - **Owner Username**: Optional. The username or email of the person linking the account. - **Multiple Linked Accounts**: Under **Advanced**. Whether this owner can link more than one account for the same connector. Click **Next**. The project's default [connector profile](/gateway/concepts/connector-profiles) is selected. To use a different one, select it. Click **Next**. 1. Enter any required credentials. 2. Click **Connect**. 3. If the provider asks you to authorize, for example through OAuth, complete authorization with the provider. Once authentication succeeds, the Linked Account is created. To confirm, open the connector's page and select the **Accounts** tab. ## If linking fails Linking a new account through a disabled connector profile fails with a `422` and the error code `AccountIntegrationInactiveError`. Enable the connector profile in the dashboard, or link the account through an enabled profile. ## Manage linked accounts View, re-authenticate, or remove accounts on the [Accounts page](https://app.stackone.com/accounts), or via the [List Accounts API](/platform/api-reference/v2/accounts/list-accounts). To update expired credentials, click **Reconnect** in a Linked Account's row menu or on its details page. Reconnecting updates the credentials on the existing Linked Account rather than creating a second one. `account.updated` and `account.deleted` webhooks fire on re-authentication and disconnect. ## Next steps Point an AI platform at the account you just linked. Choose which of a connector's actions and events are exposed. # Use Your Own OAuth Apps Source: https://docs.stackone.com/connect/managing-connectors/using-your-own-oauth-apps When to use StackOne's shared OAuth credentials vs registering your own When configuring OAuth connectors, you can use StackOne's shared credentials or register your own OAuth apps with each provider. The right choice depends on how you're using StackOne. ## Connecting your own tools If you're using StackOne to connect your own company's accounts (your Salesforce, your HubSpot, your Google Drive), StackOne's shared credentials work well. **When shared credentials work:** - Low-volume internal tools and automations - Connecting your team's SaaS accounts - Testing and development - Proof-of-concept integrations **When to consider your own OAuth app:** - You want your company name on the OAuth consent screen - You need dedicated rate limits for high-volume usage - Your security team requires it as a matter of policy ## Connecting your customers' tools If you're using StackOne to let your customers connect their accounts (embedded iPaaS), **use your own OAuth apps for production**. Your customers will see your brand during OAuth consent instead of a third party, you'll have dedicated rate limits, and if you ever want to list in a SaaS marketplace, you'll need your own credentials anyway. Register your OAuth apps early - verification can take weeks for some providers. In the meantime, you can use StackOne's credentials to keep testing. Contact support via in-app chat or Slack (or [support@stackone.com](mailto:support@stackone.com)) if you need additional [Connector Profiles](/gateway/concepts/connector-profiles) pre-configured with StackOne's OAuth apps. If you plan to list your integration in any major SaaS marketplace, this isn't optional. **HubSpot** requires your app to authorize requests with your own app ID. Apps using shared OAuth credentials are rejected during review. **Zendesk** explicitly prohibits using another developer's OAuth client. Their terms require third-party developers to use their own global OAuth client. **Microsoft** requires multitenant apps to register in your own Entra ID tenant. Since 2020, apps without Publisher Verification show warnings that the app is "risky to download." **Atlassian**, **Salesforce**, and **Google Workspace** all have similar requirements - partners must use their own OAuth applications registered under their own developer accounts. When your customer clicks "Connect to Salesforce" in your app, the OAuth consent screen shows who's requesting access. With StackOne's credentials, they see "StackOne is requesting access to your account." With your own, they see your company name and logo. This matters for trust. Your customers chose your product, not StackOne. Seeing an unfamiliar name during authorization creates confusion and support tickets. Google and Microsoft also tie verification badges to the OAuth app owner. The blue "verified" checkmark only appears if *you* complete publisher verification - it doesn't transfer from StackOne's credentials. Enterprise customers often require vendors to use their own OAuth credentials as part of security reviews. This shows up in security questionnaires and vendor assessments. Having your own OAuth app also gives you: - Direct access to each provider's developer console - Visibility into your app's usage and quotas - Control over scopes and permissions requested - Ability to respond to provider security notifications directly API rate limits are enforced per OAuth app, not per end-user or per StackOne customer. **Microsoft Graph** allows 130,000 requests per 10 seconds per app across all tenants using that app. **Google** quotas are per Cloud Project. **Slack** is particularly strict: non-Marketplace apps are limited to 1 request per minute for some endpoints, versus 50+ for verified apps. With shared credentials, one customer's bulk sync or misconfigured integration can exhaust limits for everyone. Your own OAuth app means your own quota - your customers aren't competing with other StackOne users. ## Setting up your own OAuth credentials Create an OAuth application in the provider's developer console (Google Cloud Console, Microsoft Entra ID, etc.). ``` https://api.stackone.com/connect/oauth2/{provider}/callback ``` Replace `{provider}` with the connector key (e.g., `hubspot`, `googledrive`). Many providers require OAuth verification for production. Start early as this can take days or weeks. In [Connectors](https://app.stackone.com/connectors), open the connector, click **Add Profile**, pick the actions and events the profile should allow, and click **Continue**. In the **Create Profile** panel, choose the OAuth authentication type and enter your Client ID and Client Secret. The panel also shows the **Callback URL** to register with the provider, with the connector key already filled in. To change the credentials on an existing profile, open the menu on its card and choose **Edit profile**. ### Provider-specific guides ## Decision guide | Use case | StackOne credentials | Your own OAuth app | |----------|---------------------|-------------------| | Testing / POC | ✅ Recommended | Optional | | Connecting your own accounts | ✅ Works well | Optional | | Low-volume internal tools | ✅ Works well | If required by policy | | High-volume usage | ⚠️ Shared rate limits | ✅ Dedicated limits | | Production with end-customers | ⚠️ Not recommended | ✅ Recommended | | Marketplace listing | ❌ Won't pass review | ✅ Required | # AI Platforms (MCP) Source: https://docs.stackone.com/connect/ai-platforms/overview Connect chat apps, coding agents and automation platforms to StackOne over MCP with one URL, and let each user choose the accounts and actions it can reach. The StackOne MCP server turns the [actions](/gateway/concepts/actions) on your [Linked Accounts](/gateway/concepts/linked-accounts) into tools that any client supporting the Model Context Protocol (MCP) can call. ## The server URL Everyone uses the same URL in their client: ``` https://mcp.stackone.com/mcp ``` The URL grants no access by itself, so you can publish it in an internal wiki or helpdesk article. Each person who adds it signs in to StackOne and chooses which of their Linked Accounts the client can reach. The client receives tools, and provider credentials stay in StackOne. Most clients open a sign-in prompt as soon as the server is added, and some wait until the first tool call. See [Client setup (OAuth)](#client-setup-oauth) for popular clients. ## What the user sees Authorization happens in the StackOne dashboard, against the user's own login. Sign in, pick a [project](/gateway/concepts/organizations-and-projects), select the [Linked Accounts](/gateway/concepts/linked-accounts) the client should reach, then **Authorize**. The granted accounts and actions become the client's tool list. Selecting an account grants every [action](/gateway/concepts/actions) enabled on its [Connector Profile](/gateway/concepts/connector-profiles). Expanding an account narrows the grant to individual actions. The same screen carries the **Load tools when needed** toggle, which puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). It is on by default. Under the client's logo, the screen shows where the connection returns after you approve, such as **Returns to claude.ai**. For a client that publishes its own details, such as Claude Code or VS Code, it also shows the domain it came from. Check that both match the client you are connecting. Any program on your device can catch a sign-in that returns to localhost or to an app on it, so only continue if you started the connection yourself, from that client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags Each client guide under [Client setup (OAuth)](#client-setup-oauth) walks through every screen. ## Who can grant access Users typically hold the [**Project Member** role](/secure/identity-and-access/roles-and-groups/project-roles), which is what the flow is built around. A Project Member sees the accounts they linked themselves, plus any they have been added to. That is what makes one URL safe to publish across an organization. Access can also be granted on a single Linked Account, which is how a shared account (a service mailbox, a company CRM login) reaches someone who is otherwise only a Project Member. Each person added to an account gets one of two levels: | On a Linked Account | Can | |---|---| | **Account Admin** | Run actions, edit, delete, re-authenticate, and manage who else has access | | **Account Member** | Run actions only | ## Choosing a connection method There are two ways to connect a client: | | [OAuth](#client-setup-oauth) | [Session token](#client-setup-session-token) | |---|---|---| | Best for | A person using a client interactively | Unattended use, such as a shared server or a scheduled workflow | | Who gets access | The person who signed in and approved | Anyone holding the URL | | Accounts covered | Several, chosen at approval time | One, fixed when generated | | Ends when | The grant is revoked under Connected Apps | The token expires or is regenerated | | Safe to circulate | Yes | No, treat it as a password | ## Client setup (OAuth) OAuth is the recommended way to connect. Each person authorizes with their own StackOne login, and their grant can be revoked at any time. ### Popular clients Here are step-by-step guides for some of the most popular clients: Here are guides for other clients: | Client | Setup | Their docs | |---|---|---| | Azure AI Foundry | URL only | [MCP tool](https://learn.microsoft.com/en-us/azure/ai-foundry/agents/how-to/tools/model-context-protocol) | | Postman | Detects OAuth on its own and offers an **Authorize** button | [MCP requests](https://learning.postman.com/docs/postman-ai-agent-builder/mcp-requests/overview/) | | Dust | URL only | [MCP in Dust](https://docs.dust.tt/docs/mcp) | | Amazon Quick | URL only | [MCP in Amazon Quick](https://docs.aws.amazon.com/quicksuite/latest/userguide/mcp.html) | | LangChain | Through the MCP adapters package | [langchain-mcp-adapters](https://github.com/langchain-ai/langchain-mcp-adapters) | | Gemini data connectors | URL only | [Gemini Enterprise](https://docs.cloud.google.com/gemini/enterprise/docs/overview) | ### Clients requiring Client ID and Secret Most clients identify themselves to StackOne automatically, which is why the URL is usually the whole configuration. Claude Code and VS Code publish their details at an address StackOne reads, and other clients, including Cursor, register on first connect. A few sign in from a fixed, hosted callback address instead and cannot self-register. Those need a client created in the dashboard first, and you paste its credentials into the client. Go to **Project Settings → MCP OAuth Clients → Create OAuth Client**. Give it a descriptive name, leave **Client type** set to `Confidential`, and add one **redirect URI** per line. This is the callback address the client returns to after sign-in, which the client's own documentation states. The **Common integrations** picker fills the redirect URI in for the clients we have confirmed: | Preset | Redirect URI | |---|---| | Gemini Enterprise | `https://vertexaisearch.cloud.google.com/oauth-redirect` | | Microsoft 365 Copilot | `https://teams.microsoft.com/api/platform/v1.0/oAuthRedirect` | | Claude | `https://claude.ai/api/mcp/auth_callback` | | Cursor | `https://www.cursor.com/agents/mcp/oauth/callback` | Redirect URIs must be `https` or a loopback address. **Generate** returns the client ID and secret. The secret is shown only once, so store it before you close the panel. If it is lost, create a new client rather than trying to recover it. Paste the credentials into the client along with the endpoints shown beside them: | Field | Value | |---|---| | MCP server URL | `https://mcp.stackone.com/mcp` | | Authorization endpoint | `https://idp-api.stackone.com/api/auth/oauth2/authorize` | | Token endpoint | `https://idp-api.stackone.com/api/auth/oauth2/token` | | Scopes | `mcp offline_access` | Then run the flow. The consent screen is the same one every other client shows, and [Who can grant access](#who-can-grant-access) applies unchanged. Clients that currently need this: | Client | Their docs | |---|---| | Gemini Enterprise | [Assistant actions](https://docs.cloud.google.com/gemini/enterprise/docs/assistant-actions) | | Microsoft 365 Copilot | [MCP actions](https://learn.microsoft.com/en-us/microsoft-copilot-studio/agent-extend-action-mcp), [authenticating it](https://learn.microsoft.com/en-us/microsoft-365/copilot/extensibility/plugin-authentication) | | Google ADK | [MCP tools](https://google.github.io/adk-docs/tools/mcp-tools/) | Access tokens last one hour and are renewed automatically using the `offline_access` refresh token. The grant itself lasts 90 days, after which the user runs the flow again. Revoking under **Connected Apps** ends it immediately. ### Client not listed? Any MCP client that speaks the Streamable HTTP transport and supports OAuth can connect. Point it at `https://mcp.stackone.com/mcp` and let it run the flow. If a client cannot open a browser for someone to approve the prompt, use a [session token](#client-setup-session-token) instead. ### Reviewing and revoking access Every authorization is a grant against the user who approved it, not against a project API key. Users manage their own grants under **Connected Apps** in the dashboard, where revoking one immediately stops that client's tool calls. Revoking access does not unlink the account or change the Connector Profile. The account keeps working for every other client. ## Client setup (session token) Session token URLs cover the cases OAuth cannot: a shared server, a scheduled job, or anywhere nobody is present to approve a prompt. The trade-off is that the access is built into the URL itself, so one leaked link exposes the account it was minted for. ``` https://api.stackone.com/mcp?token={session_token} ``` Generate one from **Connectors**, open a connector, then **Use in Agent**. Pick a linked account, set the expiry (one year by default), and copy the URL. Everything above is for clients your users run themselves, each signing in with their own StackOne login. To call the MCP server from your own product instead, with your API key and an account ID per end-user, see [MCP](/embed/call-actions/mcp) in the Embed tab. ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # ChatGPT Source: https://docs.stackone.com/connect/ai-platforms/chatgpt Connect StackOne MCP to ChatGPT as a custom MCP server with OAuth. ## Overview [ChatGPT](https://chatgpt.com) connects to remote MCP servers as **custom MCP servers**, added from **Plugins** and saved as a plugin. It registers itself with StackOne and runs the OAuth flow, so the URL is the whole configuration. Add the server in a browser at [chatgpt.com/plugins](https://chatgpt.com/plugins). What you create belongs to your ChatGPT account or workspace, and the desktop app picks it up from there once it exists. Adding a custom MCP server no longer requires Developer mode. Account and workspace policies still apply, so in a Business, Enterprise, or Edu workspace an admin may need to allow custom MCP servers first. The menu labels change often, so see OpenAI's [Connect and test your plugin](https://developers.openai.com/plugins/deploy/connect-chatgpt) guide for the current flow. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup 1. Go to [ChatGPT Plugins](https://chatgpt.com/plugins). 2. Select **+**, then **Add custom MCP server**. 3. Enter a name and description, for example `StackOne`. 4. Under **Connection**, enter the MCP server URL: ```text https://mcp.stackone.com/mcp ``` 5. Set authentication to **OAuth**. ChatGPT discovers the endpoints and registers itself, so leave the client ID and secret empty. No `mcp-remote` wrapper needed. 6. Review the risk warning and select **I understand and want to continue**. 7. Select **Create as a plugin**. If **Add custom MCP server** is missing from the menu, a policy on your account or workspace is blocking it. In a Business, Enterprise, or Edu workspace, ask a workspace admin or owner to allow custom MCP servers for your role. On a personal plan, check OpenAI's [Connect and test your plugin](https://developers.openai.com/plugins/deploy/connect-chatgpt) guide for current availability. ChatGPT opens StackOne in your browser. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). Back in ChatGPT, review the tools it discovered, then install the plugin. The plugin is yours as soon as it is installed. Sharing it with everyone else depends on your plan. Not applicable. A personal account has no workspace to publish to. Skip to the next step. An admin or owner opens **Workspace Settings → Apps → Drafts** and clicks **Publish**, reviewing the safety warnings for any write actions. Published apps show in the workspace's approved connectors list, labeled **custom**. They cannot be edited afterwards, so changing the tools or metadata means creating and publishing the app again. An admin or owner opens **Workspace Settings → Apps → Drafts** and clicks **Publish**. In the dialog that follows, **Configure Actions** selects which actions the app may run, and **Configure Access** limits it to specific groups. Both stay editable after publishing, from the ellipsis menu next to the app under **Workspace Settings → Apps**. Start a new chat, type `@`, select the StackOne plugin, and try: ```text What StackOne tools are available? ``` The plugin works in the ChatGPT desktop app as well as the browser. It is not available on mobile. OpenAI asks you to confirm that an OAuth provider issues refresh tokens. StackOne advertises `offline_access` in its discovery metadata and issues them, so ChatGPT renews access on its own. Nothing to configure. ## Keeping the tool list current ChatGPT works from a snapshot of the tools StackOne exposed when the server was added. Changing what StackOne exposes, by authorizing another linked account or enabling more actions on a [connector profile](/gateway/concepts/connector-profiles), does not reach ChatGPT until the snapshot is refreshed: - **A server you added yourself.** Open it at [ChatGPT Plugins](https://chatgpt.com/plugins) and select **Refresh**. - **An app an admin published to a workspace.** Enterprise and Edu admins refresh from the ellipsis menu next to the app under **Workspace Settings → Apps**. Business plans cannot refresh a published app, so it has to be created and published again. [Advanced Tool Search](/optimize/advanced-tool-search) sidesteps most of this. It replaces the per-action tool list with two stable tools, Search and Execute, so the snapshot holds however the underlying grant changes. To change which accounts or actions ChatGPT can reach, re-run the OAuth flow. To revoke it, use **Connected Apps** in the StackOne dashboard. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Paste the token URL as the MCP server URL and set authentication to **No Authentication**. One server then covers one linked account. ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Claude Code Source: https://docs.stackone.com/connect/ai-platforms/claude-code Connect StackOne MCP to Claude Code with OAuth using built-in MCP commands. ## Overview [Claude Code](https://code.claude.com/) is Anthropic's CLI for developers. It has built-in commands for managing MCP servers and runs the OAuth flow itself. For complete Claude Code MCP documentation, see the [official MCP guide](https://code.claude.com/docs/en/mcp). ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup ```bash claude mcp add --transport http --scope user stackone https://mcp.stackone.com/mcp ``` This command adds the server to your user scope, so it's available across all your projects. Remove `--scope user` if you only want it available in the current directory. See [Scope options](#scope-options). Claude Code waits for you to ask before opening a browser. Run `/mcp`, select **stackone**, then **Authenticate**. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). Check the server status: ```bash claude mcp list ``` Within a session, use `/mcp` to view server details and available tools, then select **View tools** to browse the operations you granted. One grant covers every account you approved, so a single `stackone` server is usually all you need. To change which accounts or actions it can reach, re-run `/mcp` and authenticate again; to revoke it, use **Connected Apps** in the StackOne dashboard. ## Scope options Control where the configuration is stored: | Scope | Flag | Storage location | Use case | |-------|------|------------------|----------| | Local | (default) | `.claude.json` in current directory | Project-specific | | Project | `--scope project` | `.mcp.json` at project root | Team collaboration (version controlled) | | User | `--scope user` | `~/.claude.json` | Personal tools across all projects | **Example with user scope** (available across all projects): ```bash claude mcp add --transport http --scope user stackone https://mcp.stackone.com/mcp ``` A `--scope project` entry is safe to commit, because the URL carries no access of its own. Each teammate authenticates as themselves and gets their own accounts. ## Management commands ```bash claude mcp list # View all configured servers claude mcp get stackone # Show details for a specific server claude mcp remove stackone # Remove a server ``` A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Pass the token URL to `claude mcp add`, one server per linked account: ```bash claude mcp add \ --transport http \ gsheets \ "https://api.stackone.com/mcp?token={session_token}" ``` Use short names for easier CLI usage: `gsheets`, `slack`, `hubspot-sales`. For multiple accounts, get a separate token for each and add them as distinct servers: ```bash claude mcp add --transport http gsheets "https://api.stackone.com/mcp?token={google_sheets_session_token}" claude mcp add --transport http slack "https://api.stackone.com/mcp?token={slack_session_token}" ``` If you prefer to use your API key and account ID directly, set your encoded API key as an environment variable first: ```bash export STACKONE_AUTH_TOKEN=$(echo -n "{stackone_api_key}:" | base64) ``` ```powershell $env:STACKONE_AUTH_TOKEN = [Convert]::ToBase64String([System.Text.Encoding]::UTF8.GetBytes("{stackone_api_key}:")) ``` Then add the server: ```bash claude mcp add \ --transport http \ --header "Authorization: Basic $STACKONE_AUTH_TOKEN" \ gsheets \ "https://api.stackone.com/mcp?x-account-id={account_id}" ``` ## Programmatic integration For programmatic integration with Anthropic's Claude API, see the [Anthropic SDK Framework Guide](/embed/call-actions/mcp/anthropic-sdk). ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Claude Desktop & Web Source: https://docs.stackone.com/connect/ai-platforms/claude-desktop Connect StackOne MCP to Claude on desktop, web and mobile as a custom connector with OAuth. ## Overview [Claude](https://claude.ai) connects to remote MCP servers as **custom connectors**, running the OAuth flow itself, with no config file and no `mcp-remote` wrapper. A connector is added once against your account and is then available in Claude on desktop, web and mobile. Custom connectors are available on Free, Pro, Max, Team and Enterprise plans, with Free limited to one. See Anthropic's [guide to custom connectors](https://support.claude.com/en/articles/11175166-get-started-with-custom-connectors-using-remote-mcp) for the current flow. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup How you add the connector depends on your Claude plan. On Pro and Max you add it yourself, and on Team and Enterprise an Owner adds it for everyone. 1. Go to **Customize → Connectors**. 2. Open the **Add** dropdown and select **Add custom connector**. 3. Set the name (e.g. `StackOne`) and the **Remote MCP Server URL**: ``` https://mcp.stackone.com/mcp ``` 4. Leave the **OAuth client ID** and **secret** fields empty (Claude discovers the endpoints and registers itself). 5. Click **Add**. 1. Go to **Organization settings → Connectors**. 2. Click **Add**, hover over **Custom**, then select **Web**. 3. Set the **Remote MCP Server URL**: ``` https://mcp.stackone.com/mcp ``` 4. Leave the OAuth credentials under **Advanced settings** empty (Claude discovers the endpoints and registers itself). 5. Click **Add**. Under **Customize → Connectors**, click **Connect** on the StackOne connector. Claude opens StackOne in your browser. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). StackOne appears under **Customize → Connectors**, where you can review each tool and set whether it runs automatically or asks first: Claude Desktop Connectors page showing tool permissions with options to enable or require approval for each tool Then try prompts like: ```text What StackOne tools are available? ``` ```text Search recent calls in Gong ``` One grant covers every account you approved, so a single connector is usually all you need. To change which accounts or actions it can reach, disconnect the current connector and then run the flow again; to revoke it, use **Connected Apps** in the StackOne dashboard. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` A token URL is not a remote OAuth connector, so it goes through the [`mcp-remote`](https://github.com/geelen/mcp-remote) package in `claude_desktop_config.json`. Open it from **Settings → Developer → Edit Config**: - **macOS**: `~/Library/Application Support/Claude/claude_desktop_config.json` - **Windows**: `%APPDATA%\Claude\claude_desktop_config.json` ```json { "mcpServers": { "gsheets": { "command": "npx", "args": [ "-y", "mcp-remote@latest", "https://api.stackone.com/mcp?token={session_token}" ] } } } ``` Restart Claude Desktop to load it. Servers added this way show under **Settings → Developer** with a green "running" badge; if you see "failed", click **Open Logs Folder**. For multiple [linked accounts](/gateway/concepts/linked-accounts), add an entry for each. Get each token from the dashboard by selecting the relevant account. Claude Desktop Connectors page showing multiple MCP servers configured for different integrations ```json { "mcpServers": { "gsheets": { "command": "npx", "args": [ "-y", "mcp-remote@latest", "https://api.stackone.com/mcp?token={google_sheets_session_token}" ] }, "slack": { "command": "npx", "args": [ "-y", "mcp-remote@latest", "https://api.stackone.com/mcp?token={slack_session_token}" ] } } } ``` If you prefer to use your API key and account ID directly, encode your API key first: ```bash echo -n "{stackone_api_key}:" | base64 ``` ```powershell [Convert]::ToBase64String([System.Text.Encoding]::UTF8.GetBytes("{stackone_api_key}:")) ``` ```cmd powershell -Command "[Convert]::ToBase64String([System.Text.Encoding]::UTF8.GetBytes(\"{stackone_api_key}:\"))" ``` Terminal showing base64 encoding command and output Then add to your config: ```json { "mcpServers": { "gsheets": { "command": "npx", "args": [ "-y", "mcp-remote@latest", "https://api.stackone.com/mcp?x-account-id={account_id}", "--header", "Authorization: Basic {base64_encoded_api_key}" ] } } } ``` ## Programmatic integration For programmatic integration with Anthropic's Claude API, see the [Anthropic SDK Framework Guide](/embed/call-actions/mcp/anthropic-sdk). ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Codex (OpenAI) Source: https://docs.stackone.com/connect/ai-platforms/codex Connect StackOne MCP to the OpenAI Codex CLI with OAuth. ## Overview [Codex](https://developers.openai.com/codex/cli/) is OpenAI's command-line coding agent. It connects to remote MCP servers over streamable HTTP natively and runs the OAuth flow itself, so no wrapper package is needed. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup ```bash codex mcp add stackone --url https://mcp.stackone.com/mcp ``` Or add it to `~/.codex/config.toml` by hand: ```toml [mcp_servers.stackone] url = "https://mcp.stackone.com/mcp" ``` ```bash codex mcp login stackone ``` Codex opens StackOne in your browser. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). Codex stores the tokens, so later runs start without a prompt. Run `codex` and ask: ```text What StackOne tools are available? ``` To change which accounts or actions Codex can reach, run `codex mcp login stackone` again. To revoke it, use **Connected Apps** in the StackOne dashboard. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Put the token URL in `url` instead: ```toml [mcp_servers.stackone] url = "https://api.stackone.com/mcp?token={session_token}" ``` For API-key auth instead, see [Authentication & Security](/embed/call-actions/mcp#calling-actions). Confirm the latest config format in [Codex's MCP docs](https://learn.chatgpt.com/docs/extend/mcp?surface=cli). ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Cursor Source: https://docs.stackone.com/connect/ai-platforms/cursor Connect StackOne MCP to the Cursor editor with OAuth. ## Overview [Cursor](https://cursor.com) is an AI code editor with native MCP support. It connects to remote Streamable HTTP servers directly, runs the OAuth flow itself, and needs no wrapper package. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup Add StackOne MCP configuration to Cursor via this link:
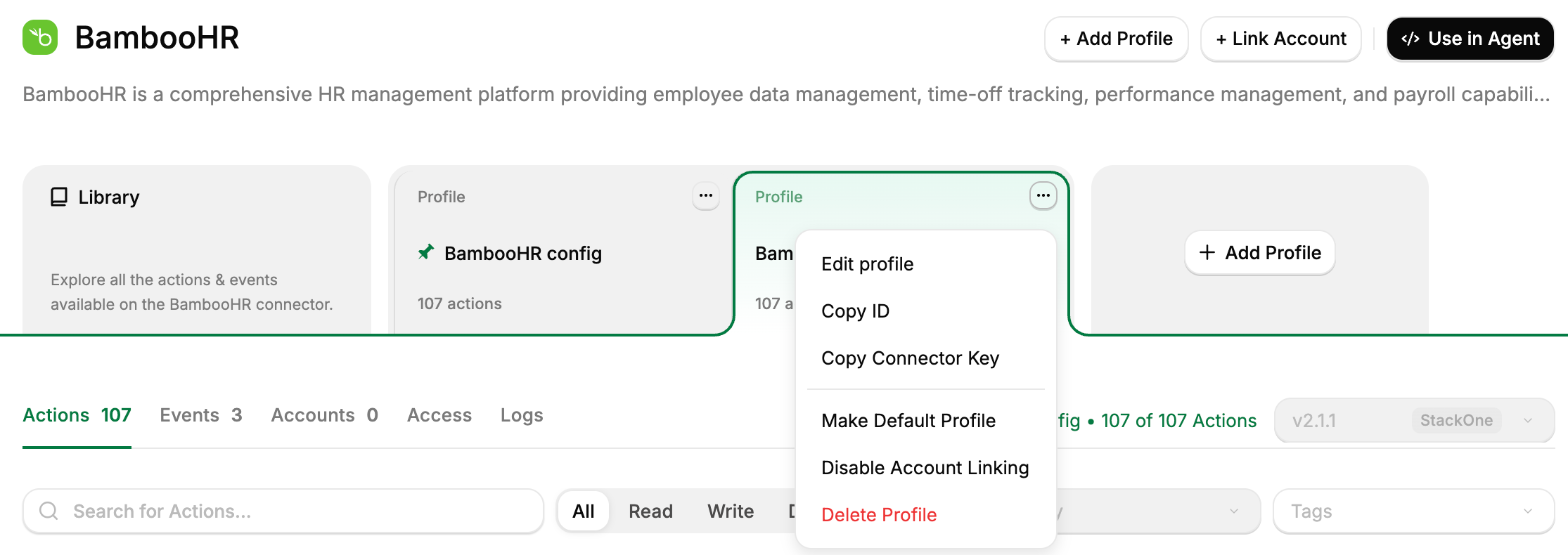
Add to Cursor
This opens Cursor and prompts to install the StackOne MCP Server. Click **Install**.
1. Open **Cursor** and navigate to **Customize → MCPs**. 2. Click **New MCP Server** to bring up the `mcp.json`. 3. Add a new entry: ```json { "mcpServers": { "StackOne": { "url": "https://mcp.stackone.com/mcp" } } } ``` You can also manually edit `~/.cursor/mcp.json` (global) or `.cursor/mcp.json` (per project) files as above.
The StackOne MCP Server appears with an **Authenticate** link.
Click **Authenticate**. Cursor opens StackOne in your browser so you can sign in. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). Open **Customize → MCPs** and confirm StackOne shows a green dot, then ask the agent: ```text What StackOne tools are available? ```
To change which accounts or actions Cursor can reach, re-run the flow. To revoke it, use **Connected Apps** in the StackOne dashboard. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Put the token URL in the same config field: ```json { "mcpServers": { "StackOne": { "url": "https://api.stackone.com/mcp?token={session_token}" } } } ``` For API-key auth instead, see [Authentication & Security](/embed/call-actions/mcp#calling-actions). ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Gemini CLI Source: https://docs.stackone.com/connect/ai-platforms/gemini Connect StackOne MCP to the Google Gemini CLI with OAuth. ## Overview The [Gemini CLI](https://github.com/google-gemini/gemini-cli) is Google's open-source command-line agent. It connects to MCP servers defined in its settings and discovers OAuth on a remote server on its own. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup ```bash gemini mcp add --transport http stackone https://mcp.stackone.com/mcp ``` Or add it to `~/.gemini/settings.json` under `mcpServers` by hand: ```json { "mcpServers": { "stackone": { "httpUrl": "https://mcp.stackone.com/mcp" } } } ``` Run `gemini`. The CLI discovers that StackOne uses OAuth and opens your browser. If it does not, authenticate from inside the session: ```text /mcp auth stackone ``` Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). Run `/mcp` to list connected servers and their tools. To change which accounts or actions the CLI can reach, re-run the flow with `/mcp auth stackone`. To revoke it, use **Connected Apps** in the StackOne dashboard. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Put the token URL in `httpUrl`: ```json { "mcpServers": { "stackone": { "httpUrl": "https://api.stackone.com/mcp?token={session_token}" } } } ``` For API-key auth instead, see [Authentication & Security](/embed/call-actions/mcp#calling-actions). Confirm the latest config format in the [Gemini CLI MCP docs](https://github.com/google-gemini/gemini-cli/blob/main/docs/tools/mcp-server.md). ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Glean Source: https://docs.stackone.com/connect/ai-platforms/glean Connect StackOne MCP to Glean as a vendor provided tool with OAuth, and hand the tools to Glean Chat and Agents. ## Overview [Glean](https://www.glean.com) is an enterprise AI platform whose chat and agents work over a company's own knowledge. It connects to remote MCP servers as **vendor provided tools**, added once by an admin from the Admin console. StackOne connects to Glean with OAuth, so each user authorizes their own toolset and only reaches the [linked accounts](/gateway/concepts/linked-accounts) they have access to. Adding an MCP server takes a Glean **Admin** or **Setup Admin** role, and agent support is in beta. Requirements and the menu labels change often, so see Glean's [Connect remote MCP servers](https://docs.glean.com/administration/tools/connect-remote-mcp-servers-to-glean) guide for the current flow. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup 1. Open the Glean [**Admin console**](https://app.glean.com/admin/tools). 2. On the **Tools** page, click **Add** in the top right. Glean Admin console Tools page on the Vendor Provided Tools via MCP tab, with an Add button in the top right 1. In the **Add tools** dialog, open the **Vendor provided tools (via MCP)** tab. 2. Click **Import tools from MCP server**. Glean Add tools dialog with the Vendor provided tools via MCP tab selected and the Import tools from MCP server option at the top On the **Configuration** tab, fill in: - **MCP server name** (e.g. `StackOne`). - **Description** (e.g. `MCPs powered by StackOne`). - **MCP server URL**: ```text https://mcp.stackone.com/mcp ``` - **Transport type**: Streaming HTTP. - **Authentication Method**: Dynamic Client Registration. Glean MCP server configuration form with the name StackOne, a description, and the StackOne MCP server URL filled in Click **Initiate connection**. Glean opens StackOne in your browser. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). **Connect to server** now shows **Connected**, and the discovered tools appear on the **Tools** tab. Your connection covers tool discovery and configuration only. Glean's [documentation](https://docs.glean.com/administration/tools/connect-remote-mcp-servers-to-glean) is explicit that it "does not authorize end users". Each teammate runs this same consent flow with their own StackOne login the first time they use a tool, so they only reach the accounts they have access to. 1. On the **Configuration** tab, under **Enable Tools** click **Edit Settings**. 2. Expand the surface you want the tools on: **Chat**, **Agents**, or **Glean MCP Server**. 3. For each tool in that surface, set: - **Access**, the teammates who can use it. **Copy to all tools** applies one choice to the rest. - **Run without user confirmation**, whether it runs without asking first. 4. Repeat for every surface the tools belong on, then click **Save**. Glean Enable tools screen with the Agents section expanded, showing the Stackone Search Actions, Execute Action, Execute S1query Action, and List Accounts tools with access set to all teammates and run without user confirmation set to yes A tool must be assigned to at least one teammate or team, or Glean disables it everywhere. **Run without user confirmation** applies to Agents only. See Glean's [tool visibility](https://docs.glean.com/administration/tools/managing-tools/tools-chat-vs-agents) and [run without user confirmation](https://docs.glean.com/administration/tools/managing-tools/run-without-user-confirmation) guides. The server appears under **Vendor Provided Tools (via MCP)** with status **Enabled**. Try a prompt in Glean Chat (if you enabled the tools for Chat): ```text What StackOne tools are available? ``` Every grant belongs to the teammate who approved it, so changing which accounts or actions Glean can reach means that person running the consent flow again. To revoke one, use **Connected Apps** in the StackOne dashboard. ## Adding tools to a Glean agent In Glean, go to the **Agents** tab and create an agent. In the panel on the right, open **Tools**, click **+**, choose **MCP**, and select the StackOne server you added. Glean agent builder with the Tools panel highlighted on the right and an Add tool button Click **Preview** and ask the agent: ```text What StackOne tools are available? ``` Then **Publish** to make it available to the teammates you granted access to. All of the server's tools are enabled on the agent automatically. Through the two [Advanced Tool Search](/optimize/advanced-tool-search) tools, Search and Execute, the agent can find and run the actions each teammate granted, against the linked accounts that teammate has access to. Glean supports MCP tools in **Plan and execute** steps and autonomous agents, not in single-step selections. They are also unavailable in Fast mode. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Follow the **Setup** steps, with two fields changed: 1. **MCP server URL**: Use the token URL. 2. **Authentication Method**: **None**. ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Goose CLI & Desktop Source: https://docs.stackone.com/connect/ai-platforms/goose Connect StackOne MCP to the Goose AI assistant with OAuth. ## Overview [Goose](https://goose-docs.ai) is an on-machine AI agent (CLI and Desktop) from Block with MCP support. It connects to remote servers over streamable HTTP as an extension. ## Prerequisites - Goose installed ([installation guide](https://goose-docs.ai/docs/getting-started/installation)). - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup ### Interactive configuration Run the configuration wizard: ```bash goose configure ``` When prompted, choose **Add Extension** from the menu. Select **Remote Extension (Streamable HTTP)**. Enter `stackone` (or any name you prefer). Paste `https://mcp.stackone.com/mcp`. Goose opens StackOne in your browser. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). ### Manual YAML configuration Find your Goose config file: - **Linux/Mac**: `~/.config/goose/config.yaml` - **Windows**: `%APPDATA%\goose\config.yaml` Add the following under `extensions`: ```yaml extensions: stackone: name: stackone type: streamable_http url: https://mcp.stackone.com/mcp enabled: true timeout: 300 ``` Goose prompts for authorization the first time the extension loads. If it does not, use a session token URL instead. One grant covers every account you approved, so a single `stackone` extension is usually all you need. To revoke it, use **Connected Apps** in the StackOne dashboard. ## Verify installation Start a Goose session and check available tools: ```bash goose session ``` Then ask: ```text what tools do you have? ``` You should see StackOne operations for the accounts you approved. ## Desktop application If using Goose Desktop, open **Settings → Extensions**. Your StackOne extension appears in the list, where you can toggle it on and off. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Put the token URL in the same `url` field, one extension per linked account: ```yaml extensions: stackone: name: stackone type: streamable_http url: https://api.stackone.com/mcp?token= enabled: true timeout: 300 ``` Add separate entries for each account: ```yaml extensions: salesforce: name: salesforce type: streamable_http url: https://api.stackone.com/mcp?token= enabled: true timeout: 300 slack: name: slack type: streamable_http url: https://api.stackone.com/mcp?token= enabled: true timeout: 300 ``` To authenticate with your API key and account ID directly: ```yaml extensions: stackone: name: stackone type: streamable_http url: https://api.stackone.com/mcp enabled: true timeout: 300 headers: Authorization: "Basic " x-account-id: "" ``` To generate the base64 token: ```bash echo -n ":" | base64 ``` Environment variables work too: ```yaml headers: Authorization: "Basic ${STACKONE_AUTH_TOKEN}" x-account-id: "${STACKONE_ACCOUNT_ID}" ``` See [Authentication & Security](/embed/call-actions/mcp#calling-actions) for details. ## Troubleshooting **Symptoms:** StackOne tools don't appear when asked "what tools do you have?" 1. Verify config file location: `goose info -v` 2. Check YAML syntax (indentation matters) 3. Ensure the extension is marked `enabled: true` 4. Restart Goose after config changes 5. Check logs: `goose logs` **Symptoms:** "401 Unauthorized" or "403 Forbidden" If you connected with OAuth, re-run `goose configure` to authorize again, and check the grant still exists under **Connected Apps** in the StackOne dashboard. If using a dashboard token, regenerate it with **Use in Agent** on the connector in the dashboard. If using manual API key auth: 1. Verify base64 encoding includes the trailing colon: `echo -n "your_api_key:" | base64` 2. Confirm the account ID matches your linked account 3. Check the API key is valid in [StackOne Dashboard](https://app.stackone.com) Increase the timeout in your config: ```yaml timeout: 600 # 10 minutes ``` 1. Confirm you approved at least one account on the consent screen 2. Check that actions are enabled on the account's [connector profile](/gateway/concepts/connector-profiles) 3. Review [StackOne Playground](https://app.stackone.com/playground) to see expected tools 1. Validate YAML syntax at [yamllint.com](https://www.yamllint.com/) 2. Check indentation (use spaces, not tabs) 3. Ensure quotes around header values 4. Run `goose info -v` to see config parsing errors ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # n8n Automation Source: https://docs.stackone.com/connect/ai-platforms/n8n Use StackOne MCP in n8n workflows with the MCP Client Tool node. ## Overview [n8n](https://n8n.io/) provides MCP support through its MCP Client Tool node for workflow automation. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup 1. Create a new workflow 2. Click **+** to add a node and search for "MCP Agent" 3. Under tools, click **+** and search for **MCP Client Tool** 4. Set **URL** to `https://mcp.stackone.com/mcp` 5. Set the transport to **HTTP Streamable**. StackOne does not serve SSE, so an SSE endpoint will not connect Set **Authentication** to **OAuth2** and complete the flow in the browser. n8n stores the result as a reusable credential. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). If your n8n version doesn't offer OAuth2 on this node, use a session token URL instead, see below. Click **Execute Step** to verify the connection and see available tools, then pick what the workflow needs from **Tools to include**. An OAuth grant belongs to the person who approved it, and n8n workflows usually run unattended long after that. A session token URL is often the better fit for a scheduled workflow, since it carries its own credential and doesn't depend on one person's grant. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` In the MCP Client Tool node, paste the token URL and set **Authentication** to **None**. One node then covers one linked account. To authenticate with your API key and account ID directly: 1. Set the URL to `https://api.stackone.com/mcp?x-account-id=` 2. Set **Authentication** to **Header Auth** (create new credentials if needed): - Header name: `Authorization` - Value: `Basic `, base64-encoding your API key followed by a colon (`your_api_key:`) See [Authentication & Security](/embed/call-actions/mcp#calling-actions) for details on obtaining your API key and account ID. ## Building workflows Once configured, use the MCP Client Tool node to execute StackOne actions on the accounts you granted. For detailed setup instructions, see n8n's [MCP Client Tool documentation](https://docs.n8n.io/integrations/builtin/cluster-nodes/sub-nodes/n8n-nodes-langchain.toolmcp/). ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # VS Code (Copilot) Source: https://docs.stackone.com/connect/ai-platforms/vscode Connect StackOne MCP to GitHub Copilot in VS Code with OAuth. ## Overview [VS Code](https://code.visualstudio.com) connects to MCP servers through GitHub Copilot's agent mode. It supports remote Streamable HTTP servers directly and runs the OAuth flow itself. ## Prerequisites - A StackOne [project](/gateway/concepts/organizations-and-projects) you are a member of. - A [connector profile](/gateway/concepts/connector-profiles) in the project for each provider the client should reach, with the actions you want exposed enabled. - (Optional) A [linked account](/gateway/concepts/linked-accounts) for each provider. Accounts can also be linked during the consent flow. ## Setup 1. Open VS Code. 2. Click this link to add StackOne MCP configuration to VS Code:
Add to VS Code
VS Code prompts you to install the StackOne MCP Server. Click **Install**.
1. Open the Command Palette and run **MCP: Add Server**, or create `.vscode/mcp.json` in your workspace. 2. Add a new entry: ```json { "servers": { "StackOne": { "type": "http", "url": "https://mcp.stackone.com/mcp" } } } ```
VS Code will prompt for permission to let StackOne authenticate. Click **Allow**. Sign in, pick the project and the [linked accounts](/gateway/concepts/linked-accounts) the connector should reach, then **Authorize**. 1. **Sign in to StackOne.** If you are already signed in to the dashboard you skip straight to the next step. 2. **Check where the connection returns.** The line under the client's logo shows where it goes after you approve. If it names localhost or an app on this device, only continue if you started the connection from that client. 3. **Select a project.** Select the project you would like to associate the connection with. 4. **Select accounts and actions.** Existing linked accounts are shown. New accounts can be linked by clicking **+ Link Account**. You can either select the whole account (all actions will be granted) or refine by toggling individual actions. 5. **(Optional) Load tools when needed.** On by default, and the toggle that puts the connection into [Advanced Tool Search](/optimize/advanced-tool-search). Leave it on for large action sets. Turn it off to hand the agent every selected action up front. 6. **Authorize.** Completes the connection; you can return to your client. StackOne authorization screen listing organizations, with a project selected inside one of them StackOne authorization screen showing two linked accounts, Linear and Open-Meteo, both selected, above the Load tools when needed toggle An expanded linked account showing individual actions with toggles, descriptions, and category tags If you see a sentence where the **Load tools when needed** toggle should be, an admin has already settled it for the whole project. See [project settings](/optimize/advanced-tool-search#setting-it-for-a-whole-project). Open Copilot Chat in **Agent** mode, click the tools icon to confirm StackOne's tools are listed, then ask: ```text What StackOne tools are available? ```
Copilot needs **Agent** mode to call tools at all. To change which accounts or actions it can reach, re-run the flow; to revoke it, use **Connected Apps** in the StackOne dashboard. A session token URL carries its own credential, so it covers the cases OAuth can't: a shared server, a scheduled job, or anywhere nobody is present to approve a consent screen. For a comparison of each connection method, see [Choosing a connection method](/connect/ai-platforms/overview#choosing-a-connection-method). From the StackOne dashboard, go to [**Connectors**](https://app.stackone.com/connectors), open a connector, then click **Use in Agent**. 1. Pick a linked account. 2. Set the expiry (one year by default). 3. Select **HTTPS MCP** and copy the URL. It should be in the format of: ``` https://api.stackone.com/mcp?token={session_token} ``` This URL covers one linked account, and anyone holding it has that access until it expires, so treat it like a password. To enable [Advanced Tool Search](/optimize/advanced-tool-search), add the `tool-mode` query parameter to the URL: ``` https://api.stackone.com/mcp?token={session_token}&tool-mode=search_execute ``` Put the token URL in the same config field: ```json { "servers": { "StackOne": { "type": "http", "url": "https://api.stackone.com/mcp?token={session_token}" } } } ``` For API-key auth instead, see [Authentication & Security](/embed/call-actions/mcp#calling-actions). Confirm the latest config format in VS Code's [MCP servers docs](https://code.visualstudio.com/docs/copilot/chat/mcp-servers). ## Optimize and secure With your agent connected, use StackOne's platform features to optimize performance and secure every call. Reduce context and save tokens. Search synced records for a fraction of the tokens. Block prompt injections before they reach your agent. # Protocols & SDKs Source: https://docs.stackone.com/connect/protocols-and-sdks The ways to call a connector's actions. The guides live under Call Actions. Every protocol exposes the same actions and uses the same two values: your API key and the account's `x-account-id`. The full guides live under [Call Actions](/embed/call-actions/overview): Typed TypeScript and Python tools for your agent framework. Fetch, filter, and execute. Call the MCP server from your own product or agent framework with an API key and account ID. Call a pre-built agent per integration, for multi-agent orchestration. Call an action from any backend or script with no agent or framework. To connect ChatGPT, Claude, Cursor, or another AI platform without writing code, use the StackOne MCP server through [AI Platforms](/connect/ai-platforms/overview) instead. Each user signs in with OAuth, so no API key is involved. # Webhooks Source: https://docs.stackone.com/connect/webhooks Subscribe to events from your connectors and from StackOne, delivered to your endpoint in real time. A **webhook** is the HTTPS endpoint StackOne delivers to. An **event** is what gets delivered. You enable events on a connector profile, create a webhook, and subscribe it to the events you care about. ## Event categories Fire from a connector - a new Notion page, a file dropped into SharePoint, a Salesforce record change. They're configured on the [connector profile](/secure/scoping-connectors) for that connector. - **Programmatic** - StackOne registers the subscription with the connector for every linked account, automatically. New accounts get subscribed the moment they're linked. - **Manual** - when a connector doesn't expose a subscription API, you register StackOne's webhook URL inside the connector's own app config. These events are tagged **Requires Setup** on the profile. - **Data Sync** - StackOne detects the change itself, by comparing each [Data Sync](/optimize/data-sync/events) run with the records it already stored, and sends an event for every record created, updated, or deleted. Fire from StackOne itself, covering account lifecycle, so you can react when a customer connects or disconnects a tool without polling. See [Platform Events](/platform-api/platform-events) for the full list of events and [Handle Account Events](/embed/handle-account-events) for how to consume them. Fire from the legacy connectors and have their own catalog and payload shape. ## Where you configure events There are two places, and they own different things. **The outbound webhook has to exist first** - that's what you bind events to on the connector profile. 1. **Webhooks page** - *the outbound endpoint*: URL, signing secrets, delivery health, and recent volume. Create the webhook here before you try to route any events to it. 2. **Connector profile** - *which events fire* from this connector in this project, and which webhook(s) each event is routed to. For programmatic events, toggling here provisions (or unprovisions) the underlying subscription with the connector for every linked account on the profile. Manual events are tagged **Requires Setup** and only fire once StackOne's webhook URL is registered in the connector's app config. See [Scoping Connectors](/secure/scoping-connectors#enable-or-disable-events). Enabling an event on the connector profile without routing it to a webhook means StackOne can receive the event from the connector but nothing leaves your project. Routing an event to a webhook without enabling it on a profile means nothing arrives. You need both. ## Quickstart On the [Webhooks](https://app.stackone.com/webhooks) page, click **Add Webhook** and provide a name and an HTTPS URL. The URL must be publicly reachable and return `200` quickly. In [Connectors](https://app.stackone.com/connectors), open the connector you want events from and select its profile. Then: - **Connector events**: on the **Events** tab, turn on the events you want, select the webhook you just created, and click **Save Profile**. - **Data Sync events** (supported actions only): turn on events for each action and select the webhook, from the action's **Data Sync** panel. See [Data Sync Events](/optimize/data-sync/events#turn-on-events-for-an-action). Programmatic and Data Sync events are provisioned automatically for every linked account on that profile. The **Signing secrets** tab on the Webhooks page has the current secret. Copy it into your endpoint's config if you plan to verify signatures. On each request to your endpoint, verify the `x-stackone-signature` header (see below) and return `200`. The response body is ignored. Link an account in the [Accounts](https://app.stackone.com/accounts) section or via the Hub. For events tagged **Requires Setup**, register StackOne's webhook URL in the connector's own app config to start receiving them. ## Verifying webhook signatures Every delivery is signed with HMAC-SHA256 over the raw request body, using your signing secret as the key, base64url-encoded, and sent in the `x-stackone-signature` header. ```javascript import { createHmac, timingSafeEqual } from 'crypto'; function isSignatureValid(signature, rawBody, signingSecret) { if (!signature) return false; const expected = createHmac('sha256', signingSecret) .update(rawBody) .digest('base64url'); const a = Buffer.from(expected); const b = Buffer.from(signature); return a.length === b.length && timingSafeEqual(a, b); } ``` Two things matter: - **Hash the raw request bytes**, not a re-serialized JSON string - `JSON.stringify` doesn't guarantee byte-for-byte equality with what we sent. - **Compare in constant time** with `timingSafeEqual`, not `===`, so an attacker can't infer the signature byte-by-byte from response latency. **Simpler alternative.** If you don't need cryptographic verification, you can append a secret query parameter to your webhook URL (e.g. `?token=...`) and check for its presence on every request. It's less secure but adequate for non-sensitive event types. ## Rotating signing secrets A project holds up to two signing secrets, and only one is active at a time. Deliveries sign with the active secret, so you can add the new one to your endpoint before switching over without dropping events. 1. On the **Signing secrets** tab, click **Generate** on the **Generate new signing secret** row, then **Confirm**. The new secret starts inactive - deliveries continue to use the active secret. ![Signing secrets tab listing the active secret with its state and creation date, and a Generate button to add a second secret](/images/webhooks/signing-secrets-generate.png) 2. Copy the new secret from the **Generate Signing Secret** dialog, or later with the copy button on its row. 3. In your endpoint, accept signatures matching **either** the current secret or the new one. 4. Back in StackOne, open the **...** menu on the new secret's row, click **Activate (rotate)**, then **Confirm**. Deliveries now sign with the new secret, and the old secret switches to inactive. ![Signing secrets tab with an active and an inactive secret, and the inactive secret's menu open showing Activate (rotate) and Delete](/images/webhooks/signing-secrets-activate.png) 5. Once you've confirmed everything's still verifying, open the **...** menu on the old secret's row and click **Delete**. Until you delete it, **Activate (rotate)** on the old secret switches back. You can't retrieve or reactivate a deleted secret. 6. Remove the old secret from your verification code. ## Managing a webhook - **Disable** - stops delivery to your URL. Subscriptions with the connector stay active, so events keep flowing into StackOne and resume on enable. - **Enable** - resumes delivery using the existing subscriptions. - **Delete** - removes the webhook and cleans up the programmatic subscriptions with the connector for events that no other webhook is using. Deleting a webhook is irreversible. ## Troubleshooting - **Events aren't arriving.** Check that the event is *enabled on the connector profile* **and** *subscribed by the webhook*. Both are required. - **Signature mismatches.** Verify against the raw body, not a re-serialized JSON string. Confirm you're using the currently-active secret. - **Data Sync events aren't arriving.** A Linked Account's first run sends no events, because it sets the baseline. `deleted` events only come from a full re-sync. See [When events are sent](/optimize/data-sync/events#when-events-are-sent). - **Some accounts deliver, others don't.** Open the connector profile and confirm the linked account is active. A disabled connector profile pauses delivery for every account on it. - **5xx loops.** Your endpoint is returning an error and StackOne is retrying. Check your application logs and the webhook's **Last Triggered** and **7-Day-Volume** columns on the Webhooks page. - **Behind a firewall.** Allow inbound traffic from [StackOne's outbound IP addresses](/gateway/concepts/connector-profiles#connection-issues-behind-a-firewall). # Troubleshooting Source: https://docs.stackone.com/connect/troubleshooting Monitor and troubleshoot API requests with StackOne's request logs. View detailed information about API calls, filter by various parameters, and analyze both the requests you make to StackOne and the underlying provider interactions. StackOne registers relevant information of requests made to the connected provider to fulfill any request it receives. This can be useful for: - Debugging issues with a particular account or integration - Auditing the operations StackOne performs on your behalf The [Logs](https://app.stackone.com/logs) page offers efficient find, filter, and analysis of API requests and HTTP status codes. ## Request logs When you execute an API query and want to investigate an API response, that's when the realization comes – logs review is inevitable. The page shows all requests made to StackOne and also allows you to see all requests that StackOne made to the [underlying providers](https://www.stackone.com/integrations) to fulfill them. By default, it shows the logs in descending order per when the request occurred. ### Accessing the request logs page After configuring Account integration and testing its connection, you can also access its specific request logs directly by clicking the `View Logs` option in the ellipsis menu. ![Request logs interface](../images/request-logs-interface.png)
You will be redirected to the logs page with a filter pre-applied in the search bar ![Logs page with an account filter pre-applied in the search bar](../images/request-logs.png) ### Filtering All filters are grouped in a single search bar. Hover over it and click ❌ to remove multiple filters at once. The possible filtering options are: | Filter | Description | Example values | | :------------------ | :----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | :------------------------------------------------------------------- | | Account | The [linked accounts](/gateway/concepts/linked-accounts)' `origin_owner_name` for the current project. You can also see & search within that filter for a specific provider in case multiple accounts have been linked for the same `origin_owner_name` | `Acme Inc.` `Sample Organization` | | Provider | The specific [connector](/connectors/introduction) associated with the request | `Workday` `Ashby` `Salesforce` | | Resource | The type of resource (and optionally sub resource requested and the action done on the resource. | `List Employees` `Create Candidates Note` `Get Applications Offer` | | Source | The source that originated the request - specifically the type of source allowing you to filter for requests made via the StackOne U.I. or an API key | `API Request` `Dashboard UI` `Webhook` `Test Connection` `Other` (e.g. Postman, API docs) | | Status | The response's [HTTP status code](https://developer.mozilla.org/en-US/docs/Web/HTTP/Status) | `200` `201` `400` `404` `502` | | Method | The HTTP method used to make the request | `post` `get` `patch` | | Start/End date time | A date and time window | `Jan 01, 2023 01:01` | ### Viewing log details Click ➡️ on a log entry — including successful requests — to open a detailed view with two tabs: 1. **Details**: Shows the details of the request made to StackOne, including request/response headers, body, query parameters, and status. > Note: Log storage duration can be configured in the [Advanced Logs](/secure/observability#advanced-logs) section of your Project Settings. ![Log detail view showing the Details tab with request and response information](../images/request-logs-details.png) 2. **Underlying Requests**: Displays all API calls made to the provider's API to fulfill your unified request to enable better debugging. ![Log detail view showing the Underlying Requests tab with provider API calls](../images/underlying-requests.png) ### Programmatic access via API You can also access request logs programmatically using the Logs API endpoints. For debugging failed calls, see [Request Log Debugging](/features/observability/request-log-debugging). These APIs allow you to integrate log data into your monitoring, alerting, or analytics systems. --- ## Error Explainer The **Error Explainer** is a built-in AI feature that helps you resolve errors without decoding raw logs or cryptic provider messages. Think of the Error Explainer as a smart resolution agent: - **Extracts key information** from error logs automatically. No reading through raw JSON or HTTP dumps. - **Looks up context** from multiple sources: provider documentation, StackOne documentation, and StackOne's error guides. - **Generates resolution steps** specific to your integration and the problem at hand. Expect three clear, actionable steps, prioritizing provider-specific errors as the root cause (e.g. "Refresh your access token with the correct scope", or "Verify that the API key has permissions to call this endpoint"). ```mermaid flowchart TD A[Connection Error] -->|Click to Generate| B(Extract Error Information) B --> C{Resolve Error} C --> D[Check Error Codes] C --> E[Search StackOne Docs] C --> F[Search Provider Docs] D --> G[Generate Resolution Steps] E --> G F --> G ``` Invoke it by clicking **Click to Generate** wherever it appears, in three places: - **Provider request logs**: run it across all underlying requests to identify and fix broken ones - **Individual requests**: generate tailored suggestions for a single error - **Account status page**: if an account has connection issues, run it directly from the account's page The Error Explainer can be enabled or disabled per project under **Project Settings → AI Settings**, individually or via the global AI toggle. It also needs [Advanced Logs](/secure/observability#advanced-logs) enabled to have request detail to work from. Your logs are only used to generate explanations for your own account. No PII is used in training or evaluation. Each explanation can be rated in the dashboard, on both usefulness and the accuracy of its suggested steps. # Optimize Source: https://docs.stackone.com/optimize/overview Make your agents faster, cheaper, and more accurate by searching large catalogs at runtime. Once your agents are connected, optimize how they work with your tools and data: Discover the right action from a large catalog at runtime. The context footprint stays flat however many actions exist. Poll a provider on a schedule and store its records, so Deep Query can read them without hitting the provider. Search, filter, and aggregate synced records without spending a provider request. # Advanced Tool Search Source: https://docs.stackone.com/optimize/advanced-tool-search Reduce token and agent context overload. Discover the right action by natural language, then run it. StackOne [actions](/gateway/concepts/actions) are exposed to agents as **tools**. An action in the catalog becomes a tool in your agent's hands. The two terms describe the same operation from either side. There is a real problem when an agent is exposed to hundreds of tools. Loading them all into the model's context: - **Burns tokens**: every tool definition consumes context before the agent does any work - **Hurts accuracy**: LLMs make worse tool selections as the candidate set grows; more tools without structure become noise - **Hits provider caps**: OpenAI caps function definitions at ~128 per request To help solve this issue, StackOne offers **Advanced Tool Search**. This replaces a long list of tools with two: 1. **Search** - finds actions by natural language 2. **Execute** - runs the action returned by **Search**. ## Key features Search returns only the relevant actions for each query, however large the catalog. Only relevant tools exposed per request, reducing misfires and hallucinations. Filters results to tools available for configured account IDs, respecting authentication boundaries. Returns a Tools collection with converters for OpenAI, LangChain, Vercel AI SDK, and more. ## What it saves Loading every tool definition scales with your catalog. Hundreds of actions can run to hundreds of thousands of tokens before the agent does any work. Advanced Tool Search keeps that footprint flat: two tools, whatever the catalog size.
Individual tools: 500 tools loaded · ~150,000 tokens
Advanced Tool Search: 2 tools · ~900 tokens
Illustrative, exact counts depend on the actions enabled and the model. ## Example flows | Linked connector | User prompt | Search tool finds | Execute tool runs | |------------------|-------------|-------------------|--------------------| | *Any* | A description of the task | Ranked actions with IDs and descriptions: only from the connectors you've linked | The chosen `action_id` with its params | | HiBob | "Request time off for Alice next Friday" | `hibob_create_time_off_request` | Creates the time-off request in HiBob | | Jira | "Look up ticket ABC-123" | `jira_get_issue` | Returns the issue details from Jira | | Google Drive | "Find training docs on GDPR" | `googledrive_list_files` | Searches the linked drive for matching files | ## Setting it for a whole project **Project Settings → General → MCP Settings** decides this for every new connection in a project, rather than leaving it to whoever authorizes: | Setting | Effect | |---|---| | **Allowed** | On by default. Turn it off and connections can only use individual tools, and Advanced Tool Search is refused even if a client requests it | | **Mode: Let the connecting user choose** | The default. The consent screen shows a **Load tools when needed** toggle, on unless the user turns it off | | **Mode: Enforced for all connections** | Always used, and the consent screen shows the decision instead of a toggle | The setting applies to new connections, so it does not change grants that already exist. Where a mode is not enforced here, each user chooses it on the consent screen while authorizing, with a toggle labelled **Load tools when needed**. See [AI Platforms](/connect/ai-platforms/overview#what-the-user-sees) for where it appears. ## When to use it Use Advanced Tool Search when your agent spans many SaaS systems — dozens to thousands of tools — or targets models with limited context windows. For a small, focused action set where you want the model to see every tool, use individual tools instead. Turn it on in an AI platform, with ready-to-paste configs for ChatGPT, Claude, Cursor, and more. Embedding StackOne into your own code? Implement Advanced Tool Search and the other discovery methods. # Data Sync Source: https://docs.stackone.com/optimize/data-sync/overview The engine that polls provider APIs on a schedule and stores the records in StackOne's indexes. Data Sync consumes credits from your allowance. See [plans and pricing](https://www.stackone.com/pricing/). Data Sync polls a provider on a schedule you set and stores the records it returns in a StackOne index. You don't read that index directly. [Deep Query](/optimize/deep-query) searches and aggregates the stored records for you, without calling the provider. You configure Data Sync once per action on a [Connector Profile](/gateway/concepts/connector-profiles). Every account on that profile is then synced automatically. ## How it works - You turn sync on for an action on a Connector Profile, and set how often it runs. - StackOne creates one sync per [Linked Account](/gateway/concepts/linked-accounts) on that profile, for accounts already linked and any linked later. - Each time a sync fires it is a **run**, which fetches records from the provider and writes them to the index. ## Turn on sync for an action In [Connectors](https://app.stackone.com/connectors), open the connector and select the profile's card. Data Sync is configured on a saved profile, not while you are creating one, and the action has to be switched on in that profile. On the **Actions** tab, actions that can be synced carry a **Data Sync** tag and a sync button next to their switch. Actions that need parameters to run, such as fetching one record by ID, can't be synced. 1. Click the sync button to open the **Data Sync** panel. 2. Turn on **Enable Data Sync**. 3. Set **Sync every** and **Full re-sync**. 4. To turn on sync for every action on the profile that supports it, turn on **Apply to all Actions**. To be notified about synced changes from the same panel, see [Data Sync Events](/optimize/data-sync/events). Click **Save Changes**. The first sync starts immediately for every Linked Account already on the profile. Data Sync panel for the List Unified Organizations action, with Enable Data Sync on, Sync every set to 1 day, Created, Updated and Deleted Events switches, a Deliver to webhook picker, and Apply to all Actions | Field | What it controls | Bounds | |-------|------------------|--------| | **Sync every** | How often StackOne fetches new and changed records. Actions that can't sync incrementally re-fetch everything on every run | 15 minutes to 365 days | | **Full re-sync** | How often StackOne re-fetches everything from scratch, to catch deletions and repair drift. Only shown for actions that support incremental syncs | At least 1 day, and less frequent than **Sync every** | Accounts linked after you save start syncing on their own first run, with no further configuration. You don't need to revisit the profile as your customers link accounts. ## Full and incremental runs Most runs are incremental, because they're cheap. Full runs happen on their own interval to catch what an incremental run structurally cannot. | | Incremental run | Full run | |---|---|---| | Fetches | Only records that changed since the last successful run, using a checkpoint the previous run left behind | Every record | | Runs | Every **Sync every** interval | The first run, then every **Full re-sync** interval, and whenever the connector's sync definition changes | | Writes | Into the current set of records, in place | A complete new set, swapped in only once the run succeeds, so a query never sees a half-written result | | Deletions at the provider | Not detected | Reflected | | If it fails | The checkpoint is unchanged, so the next run covers the same window again rather than skipping records | The previous records stay readable | Deletions only surface on a full run. A record deleted at the provider stays readable until the next full re-sync, because an incremental run has no way to learn that it's gone. Set **Full re-sync** to match how quickly you need deletions reflected. ## Monitor syncs Go to **Accounts**, open an account, and choose the **Data Sync** tab. Each synced action gets its own panel showing its cadence and when it next runs. Expand a sync to see its recent runs: whether each was full or incremental, how long it took, and how many records it created, updated, left unchanged, or deleted. The **Enabled** toggle is the one setting that's per-account. Turn it off to stop syncing an action for this account without touching the profile or any other account. | Run status | Meaning | |------------|---------| | `success` | The run finished and its records are readable | | `running` | The run is in progress. The previously synced records stay readable until it finishes | | `failed` | The run stopped on an error, shown in the row. The checkpoint is unchanged, so the next run retries the same window | | `truncated` | The run [stopped early](#runs-that-stop-early) at the page cap, or because the provider returned the same page twice | | `quota_exceeded` | The run [stopped early](#runs-that-stop-early), or didn't start, because the organization reached its record or storage [limit](#limits) | | `incomplete` | The run stopped without reporting a result. The next scheduled run resumes from the last checkpoint | A sync shows **Paused** when the action, or sync for that action, is switched off on the Connector Profile. Nothing runs until it's turned back on. ## Deeply nested data Data Sync stores every field a record has, however deeply it's nested, but [Deep Query](/optimize/deep-query) only indexes fields up to four levels deep. Each object a field sits inside counts as one level and each list of objects as two, so `address.city` is one level deep and `employment.history[].role` is three. Fields five or more levels deep, and lists of lists at any depth, are stored with the record without being indexed: - They come back with the record unless `source` leaves them out, and a change to one of them counts as a change to the record. - They can't be used to filter, sort, or aggregate. - A field five or more levels deep can still be named in `source`. The response then includes the whole nested object that holds it. Each record stores up to 64 KB of this unindexed data. Past that, the largest nested parts are left out of the stored record first. ## Data Sync events A sync can also send an event to a webhook for every record a run creates, updates, or deletes, so you hear about changes without querying for them. See [Data Sync Events](/optimize/data-sync/events). ## Limits | Limit | Default | |-------|---------| | Records stored per organization | 1,000,000 | | Storage per organization | 25 GiB | | Providers synced per organization | 100 | | Pages fetched in one run | 2,000 | | Duration of one run | 6 hours | | Record retention after the run that wrote it | 30 days | | [Deeply nested data](#deeply-nested-data) stored per record | 64 KB | The provider count means providers with at least one sync enabled, not actions. Syncing a second action on a provider you already sync costs nothing against it, and two Connector Profiles on the same provider count once. A connector can lower the per-run page and duration ceilings for an action that needs it, but never raise them. The page cap is usually hit first. In most cases, a run reaches 2,000 pages before it reaches 6 hours, so the duration ceiling is a backstop rather than the limit a run normally stops on. Turning on sync for an action fails if it would take the organization past 100 providers. The record and storage limits are checked as runs go, and a run that hits one stops early. Two more constraints are worth planning around rather than reading as numbers: - **Not every action can be synced.** Actions that need parameters to run, such as fetching one record by ID, have no sync. See [Turn on sync for an action](#turn-on-sync-for-an-action). - **Deletions wait for a full run.** Set **Full re-sync** to match how quickly you need them reflected. Records expire once that retention window passes without a run. Any enabled sync refreshes them well inside it, so expiry matters mainly for a sync you disable and leave off: its records drop out, and reads against them start reporting nothing synced. ### Runs that stop early A run stops early when it reaches the page cap, when the provider returns the same page twice, or when the organization reaches its record or storage limit. What happens next depends on the run: - **A full run is held.** Its records are discarded, the last complete sync stays readable, and no deletions are recorded. The next full run is attempted on the **Full re-sync** cadence. The run shows `truncated` or `quota_exceeded`. - **An incremental run keeps what it wrote**, but its checkpoint doesn't move, so the next run covers the same window again. Neither sends [events](/optimize/data-sync/events), so a day with an early-stopped run can have no events for that action. ## Next steps Search, filter, and aggregate the records a sync has stored. Where sync is configured, alongside actions and events. Send an event to a webhook for every record a run creates, updates, or deletes. # Data Sync Events Source: https://docs.stackone.com/optimize/data-sync/events Get notified at a webhook when a synced record is created, updated, or deleted, including for providers that have no webhooks of their own. [Data Sync](/optimize/data-sync/overview) can send an [event](/gateway/concepts/events) to a webhook for every record a run creates, updates, or deletes. StackOne works out the changes itself by comparing each run's records with the ones it already stored. Events are configured per action on a [Connector Profile](/gateway/concepts/connector-profiles), and every Linked Account with sync enabled for the action sends them. ## Turn on events for an action Events are delivered to a webhook in your project. If you don't have one yet, add it on the [Webhooks](/connect/webhooks#quickstart) page first, or create it from the connector page in step 4. Go to **Connectors**, open the connector, and select a saved Connector Profile. The action has to be switched on in that profile. Click the Data Sync icon on the action's row (**Set up Data Sync**). 1. Turn on **Enable Data Sync**, if it isn't on already. The event toggles stay disabled until it is. 2. Under **Events**, turn on **Created Events**, **Updated Events**, **Deleted Events**, or any combination. Select the webhook under **Deliver to**, or choose **+ Add Webhook** to create one. Click **Save Changes**. Events start with the next run of each Linked Account's sync. Subscribed actions show on the webhook's **Events** tab under **Connector**, tagged **Data Sync**, with a row for each change type. Each change type shows **Active**, or **Paused** when it's turned off or sync for the action isn't running. ## When events are sent Events go out once a run finishes, not the moment a record changes at the provider. How soon you hear about a change depends on **Sync every**. | Situation | What is sent | |-----------|--------------| | A Linked Account's first run | Nothing. The first run sets the baseline that later runs are compared with, so it sends no `created` event for the records that already existed | | The first run after sync was switched off for more than 30 days | Nothing. The stored records [expire after 30 days](/optimize/data-sync/overview#limits) without a run, so this run sets a new baseline, the same as a Linked Account's first run | | An incremental run | `created` and `updated` events for the records it fetched | | A full run | `created` and `updated` events, plus `deleted` for every previously stored record that is no longer at the provider | | A run that fails, or [stops early](/optimize/data-sync/overview#runs-that-stop-early) | Nothing for that run | | A record that didn't change | Nothing | | A change only in a [deeply nested field](/optimize/data-sync/overview#deeply-nested-data) | An `updated` event, as for any other field, unless that part was left out under the 64 KB per-record limit | `deleted` events only come from a full run, for the same reason [deletions only surface on one](/optimize/data-sync/overview#full-and-incremental-runs). Set **Full re-sync** to match how quickly you need to hear about deletions. ## Event payload The event name is the action ID followed by the change: - `{action_id}.created`: a record that wasn't in the stored set when the run started. - `{action_id}.updated`: a stored record whose fields changed since the last run. - `{action_id}.deleted`: a stored record a full run no longer found at the provider. For example, `bamboohr_list_employees.updated`. Each change is its own request to your webhook. | Field | Type | Description | |-------|------|-------------| | `event` | string | The event name, as above | | `project_id` | string | The project the Connector Profile belongs to | | `account_id` | string | The Linked Account the record was synced from | | `record_type` | string | The action ID | | `record_id` | string | The record's ID, taken from the field the action syncs on | | `event_date` | string (ISO 8601) | When StackOne prepared the event, after the run finished | | `sent_at` | string (ISO 8601) | When this delivery attempt was sent. Each retry gets a new value | | `event_data` | object | The full record as Data Sync stored it, the same shape Deep Query returns. Left out of `deleted` events, since the record is gone | ```json { "project_id": "proj_7f3a9c", "account_id": "acc_42d1e8", "event": "bamboohr_list_employees.updated", "event_date": "2026-09-29T09:15:02.114Z", "record_type": "bamboohr_list_employees", "record_id": "4127", "sent_at": "2026-09-29T09:15:02.530Z", "event_data": { "id": "4127", "first_name": "Ada", "last_name": "Lovelace", "work_email": "ada@example.com", "department": "Engineering" } } ``` `event_data` is read from the stored record when the event is prepared, after the run finishes. On a large run, preparing every event can take long enough for the next run to change the stored record first: - If the next run updates the record, the event carries the newer version. - If the next run removes the record, the event isn't sent, since there's no record left to send. ## Delivery Data Sync events are signed like every other webhook event, so the same [signature verification](/connect/webhooks#verifying-webhook-signatures) applies. Their delivery works as follows: - A delivery that doesn't get a `2xx` response is retried, starting after 5 seconds and backing off to every 10 minutes, for up to 20 attempts. - StackOne sends each change from a run once per webhook, and its own retries don't create duplicates. Your endpoint can still receive the same event twice if it returned `200` but the response was lost, so treat a repeat of the same `event`, `record_id`, and `event_date` as a duplicate. - Events arrive in batches and several are sent at once, so they aren't guaranteed to arrive in the order the records changed. Every delivery attempt is logged. **View logs** at the top of the webhook's page lists them. **View logs** on a Data Sync row in the webhook's **Events** tab opens that action's sync runs instead, with **Background Logs** turned on. ## Next steps Turn on sync for an action and set how often it runs. Create the webhook Data Sync events are delivered to, and verify their signatures. # Deep Query Source: https://docs.stackone.com/optimize/deep-query Search, filter, and aggregate synced records without calling the provider API. Deep Query searches, filters, and aggregates the records [Data Sync](/optimize/data-sync/overview) has stored, without calling the provider. Because it runs against StackOne's index rather than a third-party API, it's faster, consumes none of the provider's rate limit, and answers questions most provider APIs can't express at all. Deep Query covers any action that has a sync. Turn sync on for the action first, then everything below applies to it. ## Why query instead of calling the provider | | Live action call | Deep Query | |---|---|---| | Where it reads from | The provider, on every call | StackOne's index | | Provider rate limits | Every call counts against them | No provider request, so nothing counts | | Filtering | Only the query parameters that provider happens to expose | `term`, `terms`, `range`, `wildcard`, `match`, `match_phrase`, `exists`, and `bool` over any synced field up to four levels deep and outside lists of lists ([what is indexed](/optimize/data-sync/overview#deeply-nested-data)) | | Full-text search | Rarely offered | Free-text across every text field, ranked by relevance | | Aggregation | Not offered. Page through every record and count in your own code | One `aggs` query returns the numbers | | Field selection | Whatever the provider chooses to return | `source` returns only the fields you name | A query is billed like an action call. Listing queryable fields is not. ### Smaller responses, fewer tokens The last two rows are where an agent gains the most. Asking for three fields instead of forty shrinks the response the model has to read by the same proportion. Asking for a headcount by department returns a dozen numbers from one aggregation, where a live call means paging through every employee record and tallying them inside the context window. Deep Query and [Advanced Tool Search](/optimize/advanced-tool-search) work on the same budget from opposite ends: one shrinks what tool responses cost, the other shrinks what tool definitions cost. ## Query from an agent Once a sync has records, each synced action gains a companion tool named `{action}_s1query` - `bamboohr_list_employees_s1query` alongside `bamboohr_list_employees`. A `list_s1query_queryable_fields` tool tells the agent which fields it can filter and sort on. Both tools stay available, so the agent chooses: the Deep Query tool to search or aggregate across everything cheaply, the live tool when it needs the provider's current state. Records come back in the provider's own shape, with the provider's field names and nesting, not the normalized shape a regular action call returns. ## Try a query without code Open **Actions Request Tester** from the account page and pick the `(S1Query)` entry for the action. ## When to use it Use Deep Query when the same data is read repeatedly and tolerates being minutes to hours old, or when an agent needs to search or aggregate across the whole record set rather than page through it. For data that has to reflect the provider right now, call the [action](/gateway/concepts/actions) directly - both tools stay available to the agent. To be told when a synced record changes rather than querying for it, turn on [Data Sync events](/optimize/data-sync/events). Turn on the sync that Deep Query reads from, and set how often it refreshes. For developers querying the index from their own backend, with filters and aggregations. # Secure Source: https://docs.stackone.com/secure/overview Govern the connectors, members, access, and logs in your StackOne setup. Set up and govern how your team uses StackOne: connectors, members, access, and logs. Decide which tools your members' AI agents may use, which fields they see, which values they can send, and what data goes in and out, by user or group. Remove personal data from tool calls and from stored request logs. Choose which of a connector's actions and events each profile exposes. Choose who can link accounts through each connector profile. Manage your team, how they sign in, how they join, and which groups they belong to. Track activity and control how long data is kept. Run StackOne in your own environment for full data residency. How customer accounts stay isolated when you serve many clients from one setup. # Defender Source: https://docs.stackone.com/secure/defender Protect your AI agents from prompt injection attacks by scanning API tool call responses before they reach your LLM. **Defender** protects your AI agents from prompt injection attacks by scanning API tool call responses before they reach your LLM. When an MCP tool returns data from a third-party provider (emails, CRM records, documents), that data could contain instructions designed to hijack your agent's behavior. Responses are intercepted and classified by Defender, and depending on the **Protection Mode** you choose, Defender logs the verdict, removes high-risk content, or blocks the response before it reaches your agent. ## How it works Flow diagram. A tool call response enters the Scan Mode split: Light or Hybrid run the Light Scan of pattern matching and an ML classifier, Deep goes straight to the Deep Scan LLM review, and an uncertain Light Scan result escalates to the Deep Scan in Hybrid mode. Both scans feed Protection Mode, which acts on the verdict: Monitor passes the response unchanged with the verdict logged, Sanitize removes high-risk content, and Block refuses high or critical risk responses and sanitizes the rest Defender's standard check is the **Light Scan**, two checks run together on every response: - **Pattern matching**: A fast rule-based scan for known prompt injection signatures and risky field patterns, with negligible latency. - **ML classification**: A local ML model (MiniLM) scores the content for novel or subtle attacks that pattern matching would miss. It scans the SFE-filtered payload (or the `tier2Fields` subset when configured), and reports its score as `tier2Score` in the response metadata. Responses that exceed the configured size limits can skip scanning entirely (see [Advanced settings](#advanced-settings)). The **Deep Scan** is a third check on top: an LLM reviews the response for risks the Light Scan misses. It runs only in StackOne's hosted service, not in the open source `@stackone/defender` package. The **Scan Mode** setting decides which responses get a Deep Scan (see [Scan mode](#scan-mode)). Risk level and scan metadata are returned alongside every response in every mode, so you can see what Defender detected even when it changed nothing. ## When to use Defender - You are building AI agents or MCP-based workflows that process third-party API responses - Your integrations handle sensitive data such as emails, files, calendar events, or CRM records - You want to observe risk signals on tool call responses without necessarily blocking them ## Configure from the dashboard Navigate to your project in the StackOne dashboard, then open the **Defender** tab in project settings. This is the baseline for every account in the project. ![Defender Settings](/images/defender-settings.png) Defender settings apply project-wide. Per-account and per-request overrides take precedence where supported. ### Core settings | Setting | Description | |---|---| | **Status** | Enables Defender scanning for this project. Default: **On** for new projects. | | **Protection Mode** | What Defender does with positive matches. See [Protection mode](#protection-mode). | | **Scan Mode** | How thoroughly responses are scanned. See [Scan mode](#scan-mode). | ### Protection mode | Mode | What happens to the tool result | |---|---| | **Monitor** (Default) | Observe only. Defender scans and adds its verdict to the logs. The tool result reaches your agent unchanged. | | **Sanitize** | Defender removes detected high-risk content from the tool result before your agent sees it. | | **Block** | Responses classified as high or critical risk are blocked and an error is returned to your agent. Lower risk responses are cleaned as **Sanitize** would handle them. | Start in **Monitor** to see what Defender would act on in your traffic by reviewing logs. Move to **Sanitize** or **Block** when you are ready to enforce. ### Scan mode | Mode | What it runs | When to choose it | |---|---|---| | **Light** (Default) | The Light Scan on every response. | Fastest. No response goes through the LLM review. | | **Hybrid** | The Light Scan on every response, plus a Deep Scan when the result is uncertain. | Adds the LLM review only where the Light Scan could not classify confidently. | | **Deep** | A Deep Scan on every response, skipping the Light Scan. | Most thorough. Every response gets an LLM review. | Light is the default. The Light Scan is the same open source engine as the `@stackone/defender` package; the Deep Scan runs only within StackOne's hosted service, so Hybrid and Deep are available here but not in the package. ### Protection level The protection level sets how sensitive the Light Scan is. | Level | What it catches | |---|---| | **Low** (Default) | Overt attacks only, such as "ignore your instructions". | | **Medium** | Overt attacks and some subtler injections. | | **High** | The most attacks, including subtle injections. | Higher levels catch more attacks but also flag more benign responses. Start on **Low** in **Monitor**, review the logs, then raise the level if attacks are getting through. ### Advanced settings | Setting | Description | Default | |---|---|---| | **Large Response Behavior** | What to do when a response exceeds the size limits: `Skip scanning` (default), `Block the response`, or `Scan anyway` | Skip scanning | | **Max Response Size** | Byte threshold that triggers large response behavior | 1,048,576 (1 MB) | | **Max Response Words** | Word count threshold that triggers large response behavior | 10,000 | | **Annotate Tool Results** | Wrap sanitized tool results with boundary tags such as `[UD-abc123]...[/UD-abc123]` (where the suffix is a random per-response ID) so downstream prompts can reason about data boundaries. Pair this with `generateBoundaryInstructions()` from `@stackone/defender` in your system prompt when enabled. | Off | ## Implement it Override Defender per toolset in the Agent SDK. ## FAQ It depends on when your project was created. New projects have Defender on. Older projects start with it off: turn it on from the **Defender** tab in project settings when your agents consume third-party data. Once on, it runs in **Monitor**, so tool results are unchanged until you choose **Sanitize** or **Block**. The Light Scan adds little: pattern matching is negligible, and the ML classifier runs locally, so there is no external API call. The Semantic Field Extractor trims metadata and identifier fields before classification to keep latency low; for typical responses the added latency is under 100ms. A Deep Scan adds an LLM review to the responses it covers, which costs more time than the local checks. The tool call returns an error to your agent indicating the response was blocked. The agent can handle this like any other tool error: retry, skip, or surface it to the user. Yes. That is what **Monitor** mode does, and it is the default. Defender still scans and returns `riskLevel`, `tier2Score`, and `detections` in the response metadata, which you can inspect in your logs, but the tool result reaches your agent unchanged. No. The Light Scan's classification model runs locally within StackOne's infrastructure, and the Deep Scan's LLM is a model StackOne deploys and operates on its own inference endpoints. Your responses are not sent to a third-party AI service, and neither model is trained on your data. # Scoping Connectors Source: https://docs.stackone.com/secure/scoping-connectors Scope what each connector can do: which of its actions and events are available. A [Connector Profile](/gateway/concepts/connector-profiles) holds the credentials and config for one connector in a [project](/gateway/concepts/organizations-and-projects). It's how you control which actions a connector exposes and how end-users link their accounts. This assumes you already have a connector profile. To create one, follow the [Quickstart](/gateway/quickstart) or pick a connector in [Connectors](/connectors/introduction), then return here. ## Enable or disable actions Scope a profile to just the actions your app uses. This limits what every linked account on the profile can do and keeps the OAuth consent screen focused. In [Connectors](https://app.stackone.com/connectors), open the connector and select the profile's card. Each action has a switch showing whether it's enabled for this profile. The switch in the table header turns every action on or off at once. Enable only the actions your app calls and disable the rest. We recommend starting with a few read actions, then enabling more as you need them. Click **Save Profile** in the bar at the bottom of the page. Changes apply to every linked account on the profile. **Cancel** discards them. A Notion profile's Actions tab with one action switched off and a bar at the bottom offering Cancel and Save Profile The **Library** card shows every action and event the connector offers, whatever any profile allows. Use it to browse a connector before you create a profile. ## Enable or disable events The **Events** tab lists every event this connector can emit. Turn on the events you want, and pick which webhook each one fires to from the dropdown alongside it, then click **Save Profile**. Choose **+ Add Webhook** in the dropdown to create a new webhook without leaving the page. The webhook is created right away and belongs to the project, so it stays even if you cancel the profile edits. See [Webhooks](/connect/webhooks) for the model and the difference between programmatic and manual events. A profile's Events tab with the Page Created event switched on and its webhook dropdown open, listing project webhooks and an Add Webhook option Events tagged **Requires Setup** are manual events. They only fire once the StackOne webhook URL is registered in the provider's own platform. The connector's guide in [Connectors](/connectors/introduction) covers the provider side. # Tool Policies Source: https://docs.stackone.com/secure/policies Set agent tool policies to control which tools your agents use, which fields they see, and what data goes into and out of each call. Tool Policies is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). **Tool Policies** control which tools an agent may use, and how, on behalf of the member it acts for. StackOne checks the policies that apply to that member before a tool call reaches the provider, and refuses the call when an enforced policy denies it. Value rules, semantic rules and PII checks also look at the data itself. Value rules check the argument values a tool receives before it executes. Semantic rules and PII checks run on the tool's inputs before it executes and on the response before the agent sees it. Flow diagram with three lanes. An AI agent makes a tool call and Tool Policies are checked. Allowed: the provider is called and the response returns unchanged. Redact PII or Read a field: the provider is called and the response returns with PII redacted or fields masked. Denied, including Write a field denials: the provider is not called and a refusal is returned. All three responses come back to the AI agent. A note under the diagram says semantic rules and PII checks run on both the inputs and the response ## How a policy is evaluated A policy carries a single **rule** that allows or denies capabilities. Rules are made up of 4 parts: | Part | Options | What it means | | --- | --- | --- | | **Who it applies to** | **Everyone**, **Users**, **Groups** | The members whose agents the rule governs. Groups come from [Manage Groups](/secure/identity-and-access/roles-and-groups/groups). | | **What it does** | **Allow**, **Deny** | A deny rule refuses exactly what it covers for those users or groups. An allow rule restricts nothing and cannot undo a deny. | | **Capabilities** | **Use a tool**, **Read a field**, **Write a field**, **Value rule**, **Redact PII**, **Semantic rule** | The operations the rule covers. One capability per kind of access, each narrowed on its own terms. See [Capabilities](#capabilities) below. | | **Applies to** | **Everything**, **A connector category**, **A connector**, **An account**, **Specific tools** | Where the capability is covered. **Tools matching** narrows any target with a name pattern. | Four guarantees hold across every policy: When policies overlap, a matching deny refuses the call whatever any allow says. [Connector Profile scoping](/secure/scoping-connectors) and [account access](/secure/identity-and-access/roles-and-groups/connector-profile-access) apply restrictions before policies. Policies apply when the member is known, which is the case for [AI platform](/connect/overview) sessions. A call made with a project API key is memberless — govern that traffic with [Connector Profile scoping](/secure/scoping-connectors) instead. A policy belongs to the project it is created in and governs calls made in that project only. To apply the same rule in several projects, create it in each. ### Capabilities A **capability** is the kind of access a rule governs: running a tool, reading or writing a field, passing an argument value outside the range or list you set, passing PII through a call, or sending and receiving data that a semantic rule's question flags. Denying one removes that access for the users or groups the rule covers. | Capability | What denying it does | | --- | --- | | **Use a tool** | Refuses the call. The agent may not run the tool at all. | | **Read a field** | Masks the field in responses. | | **Write a field** | Refuses calls that would change the field. | | **Value rule** | Refuses calls whose argument values fall outside the condition, such as a payment amount outside 25 to 500 USD. Calls with values inside it keep their existing access. | | **Redact PII** | Finds the chosen classes of PII (email addresses, phone numbers, SSNs, or credit card numbers) in the tool's inputs and responses, then redacts the detected span or blocks the call. Record UUIDs, order numbers, and API keys stay intact. See [PII Redaction](/secure/pii-redaction). | | **Semantic rule** | Asks a plain-language question about the data in the call. On inputs, a matching answer refuses the call before the tool runs. On a response, it masks the field the answer applies to. | Rules can carry more than one capability. Capabilities are alternatives rather than conditions: the rule applies where **any** one of them matches, so adding a second says "or also" rather than narrowing the first. Each is scoped on its own terms, so one rule can deny a tool outright on one connector and only mask a field on another. ## Create a policy Select the project, open [**Project Settings > Policies**](https://app.stackone.com/settings/policies), and click **Create policy**. Give the policy a descriptive name. Choose an **Enforcement** level: - **Enforced**: Refuses calls the policy denies, masks fields, and blocks or redacts data according to the rule. - **Monitored**: Records decisions in the logs without blocking or modifying calls. - **Disabled**: Stores the policy without evaluating it. Start new deny rules in **Monitored**, verify the decisions in your logs, then switch to **Enforced**. Select **Everyone**, **Users**, or **Groups**, then search for the users or groups the rule covers. Select **Deny** to refuse the capability for those users or groups, or **Allow** to state permitted use without restricting anything. Add the [capabilities](#capabilities) the rule governs: Denying **Use a tool** refuses the call. Choose which targets it applies under **Applies to**: - **Everything** covers every tool in the project. - **A connector category** covers every tool on every connector in the category, including connectors added later. - **A connector** covers every tool on the connectors you pick. - **An account** covers the tools of specific [Linked Accounts](/gateway/concepts/linked-accounts). Search accounts by name or owner. - **Specific tools** lets you pick a connector, then the tools on it by name. To narrow the tools covered by the target selection, enter a name pattern under **Tools matching** (see the pattern syntax below). An empty pattern covers every tool the targets include, so a deny refuses every call to them. A capability takes either specific tools or a pattern, not both. Denying **Read a field** masks the field in responses. Choose which targets it applies under **Applies to**: - **Everything** covers every connector and account in the project. - **A connector category** covers every connector in the category, including ones added later. - **A connector** covers the connectors you pick. - **An account** covers specific [Linked Accounts](/gateway/concepts/linked-accounts). Search accounts by name or owner. To narrow the fields covered by the target selection, enter a pattern on the field's path in the response under **Fields matching** (see the pattern syntax below). An empty pattern covers every field the targets include, so a deny masks every field in scope. Denying **Write a field** refuses calls that would change the field. Choose which targets it applies under **Applies to**: - **Everything** covers every connector and account in the project. - **A connector category** covers every connector in the category, including ones added later. - **A connector** covers the connectors you pick. - **An account** covers specific [Linked Accounts](/gateway/concepts/linked-accounts). Search accounts by name or owner. To narrow the fields covered by the target selection, enter a pattern on the field's path under **Fields matching** (see the pattern syntax below). An empty pattern covers every field the targets include, so a deny refuses every call that would change one. Denying **Value rule** keeps a tool available and checks the values the agent passes in its arguments. Choose which targets it applies under **Applies to**, the same way as **Use a tool**, then pick the argument and the condition its value must meet: - **A range** for numbers, such as a payment amount between 25 and 500 with the currency `USD`. - **Allowed or blocked values**, such as an invoice status that may be `Draft` or `Submitted` but not `Authorized`, or a sharing type that may not be `anyone`. A call whose value falls outside the condition is refused before the tool runs. A call that leaves the argument out, or sends it in another type or currency, is refused too. Denying **Redact PII** checks calls for the chosen classes of PII. StackOne's own PII model scans the tool's inputs before it runs and the response before the agent sees it, including free-text fields such as ticket bodies and notes. Record UUIDs, order numbers, and API keys stay intact. The [PII Redaction benchmark](https://www.stackone.com/platform/pii-redaction/#benchmarks) compares the model with Microsoft Presidio on connector data. Choose which targets it applies under **Applies to**: - **Everything** covers every connector and account in the project. - **An account** covers specific [Linked Accounts](/gateway/concepts/linked-accounts). Search accounts by name or owner. Under **Which PII to redact**, select one or more classes. There is no pattern to enter. Then choose what a detection does: - **Redact** replaces each detected span in the inputs and in the response, and lets the call continue. The rest of the input or response is unchanged. - **Block** refuses the call. When the PII is in the inputs, the provider is never called. When it is detected in the response, the agent receives a refusal instead of the data. A response that cannot be scanned (it is streamed, above the scan size limit, or the scan fails) is returned unredacted, and the request log records which classes were not redacted. For how detection works, what changes in the call and what is recorded, see [PII Redaction](/secure/pii-redaction). Denying **Semantic rule** asks a decision model a question about each call in scope. Write the question in plain language, for example: > Does this message contain unreleased financial results? The model answers for each field or payload, so the rule holds whatever a connector calls the field. Choose which targets it applies under **Applies to**, the same way as **Use a tool**. For a rule about outgoing messages, pick the send tools on the connectors that matter, such as Slack, Gmail and Notion. Then choose where the question is asked: - **Inputs**: a matching answer refuses the call before the tool runs. - **Response**: a matching answer masks the field it applies to before the agent sees it. A field the model cannot decide is masked unless the rule allows it.
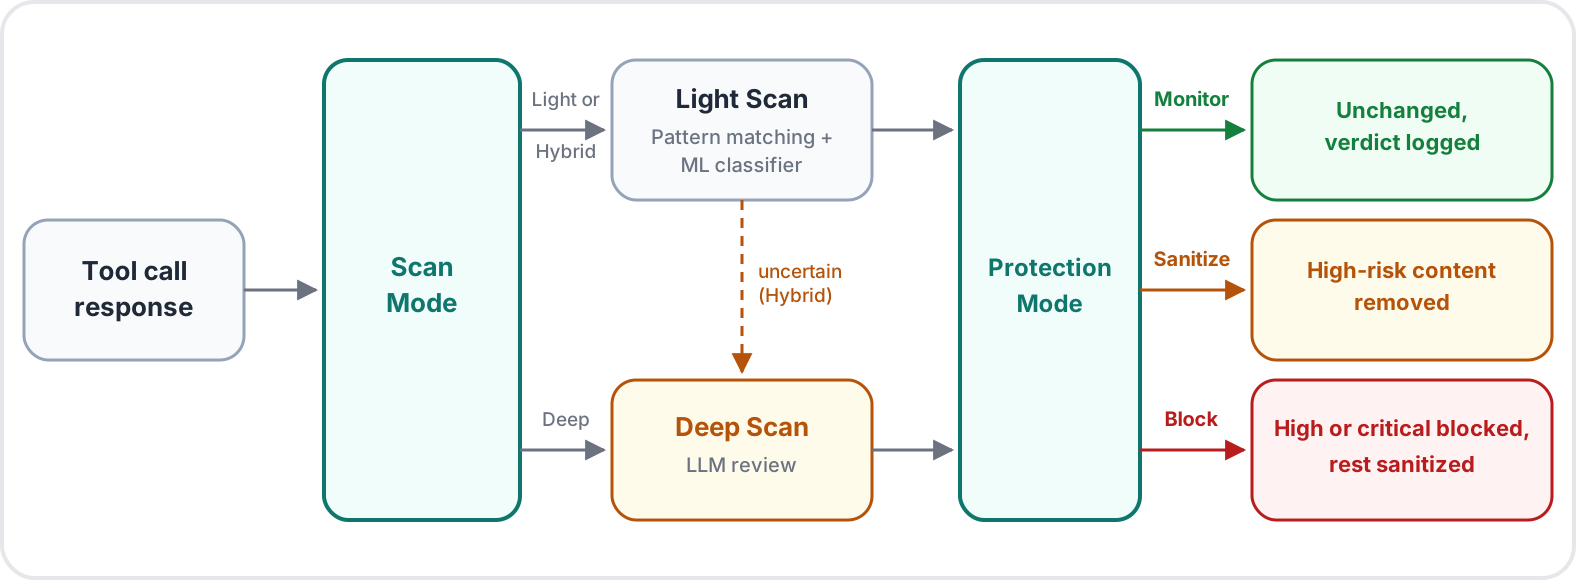
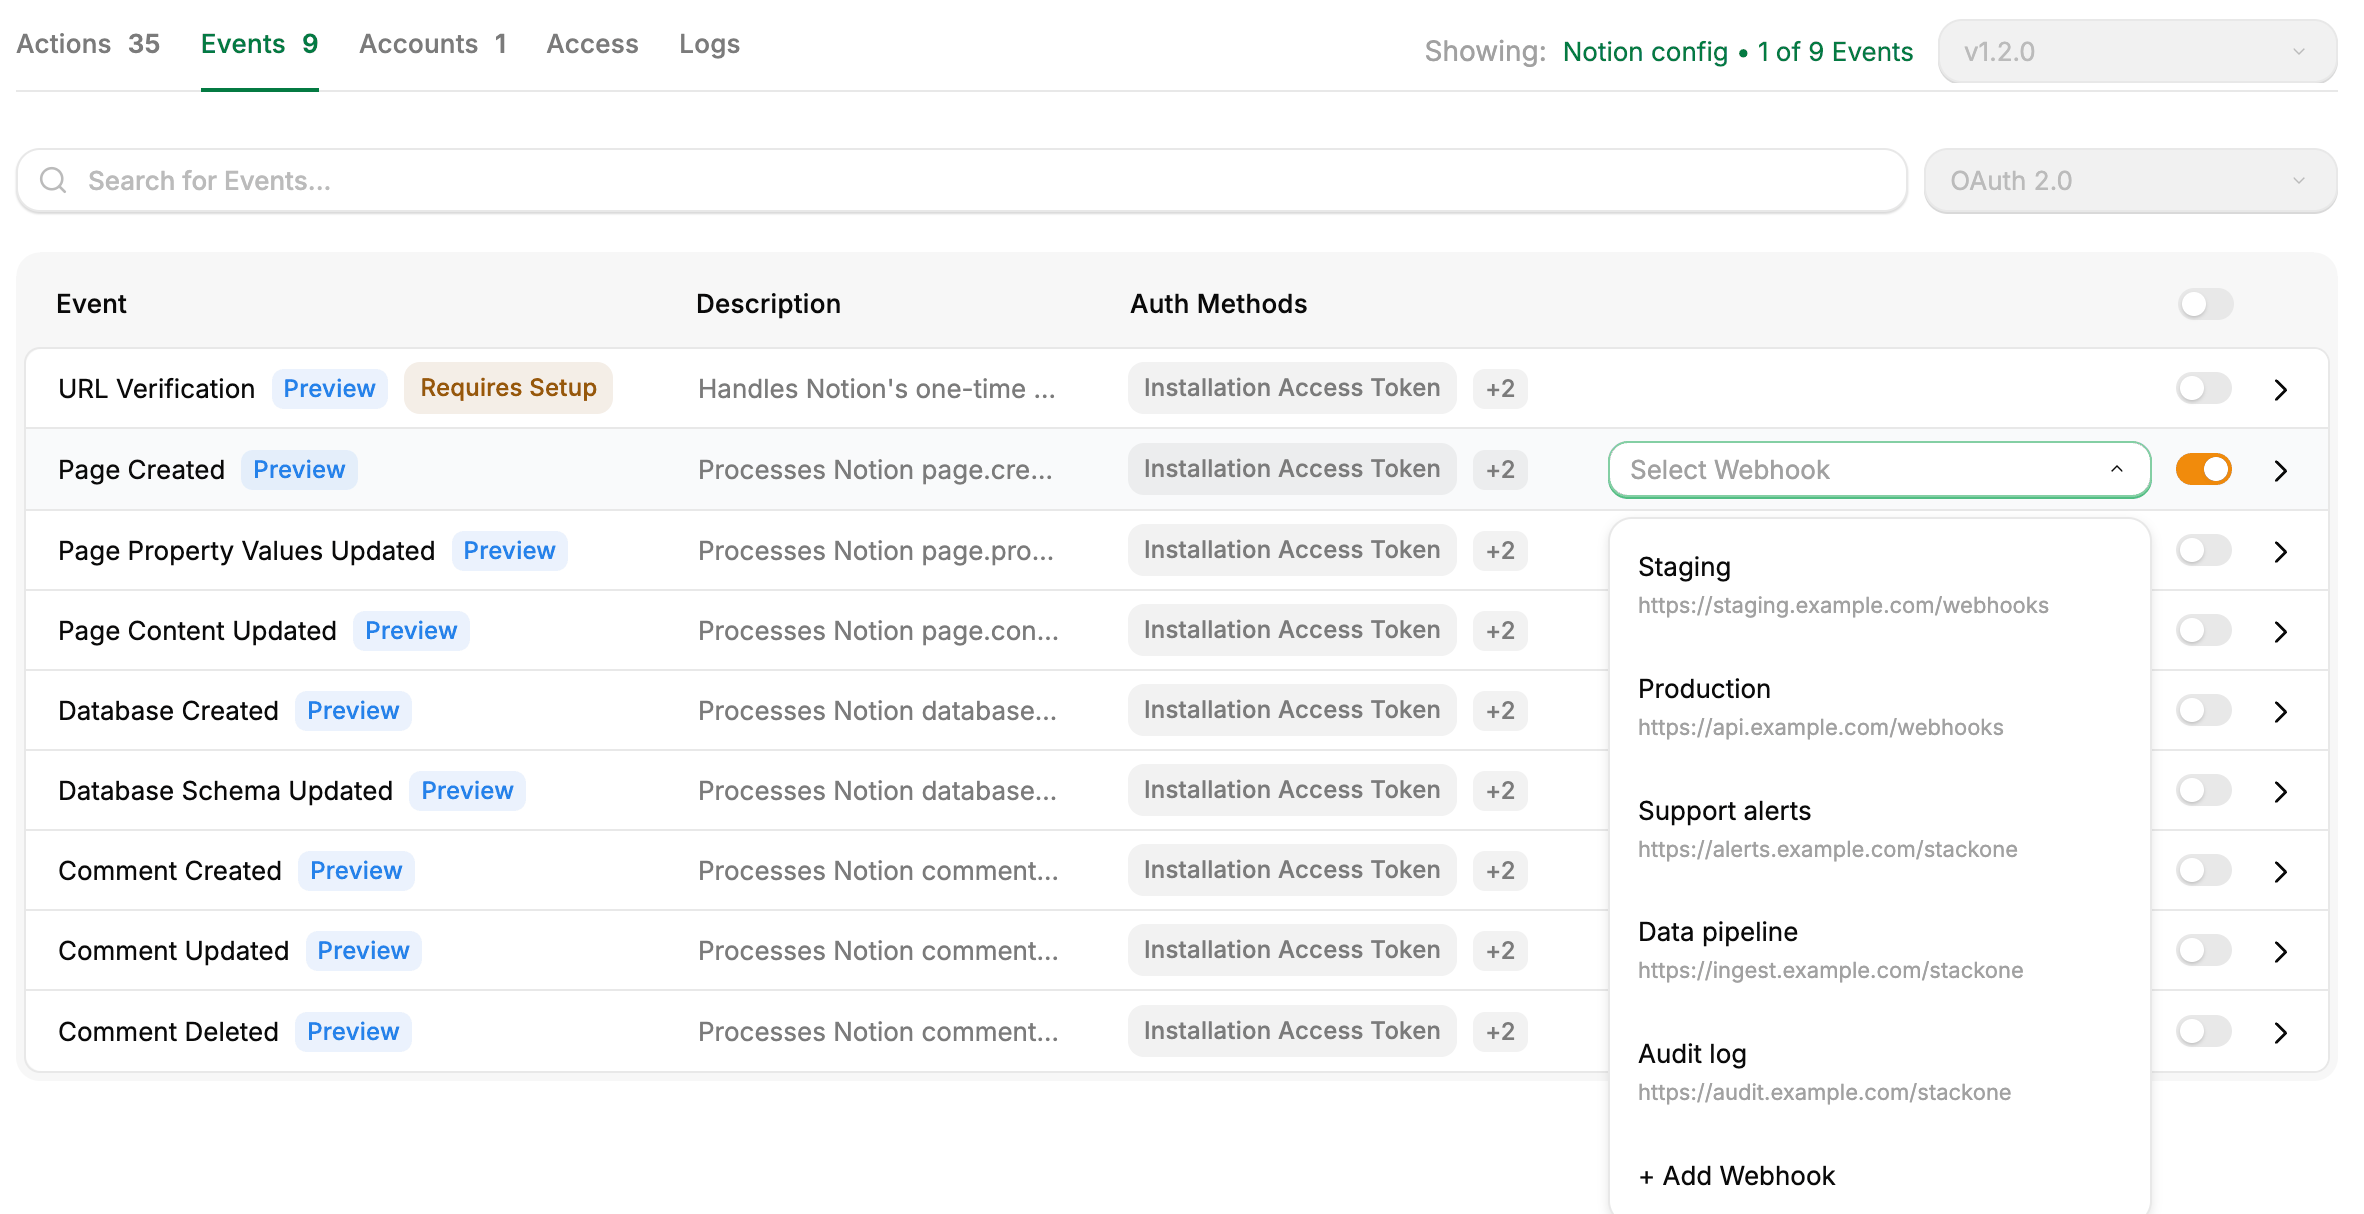
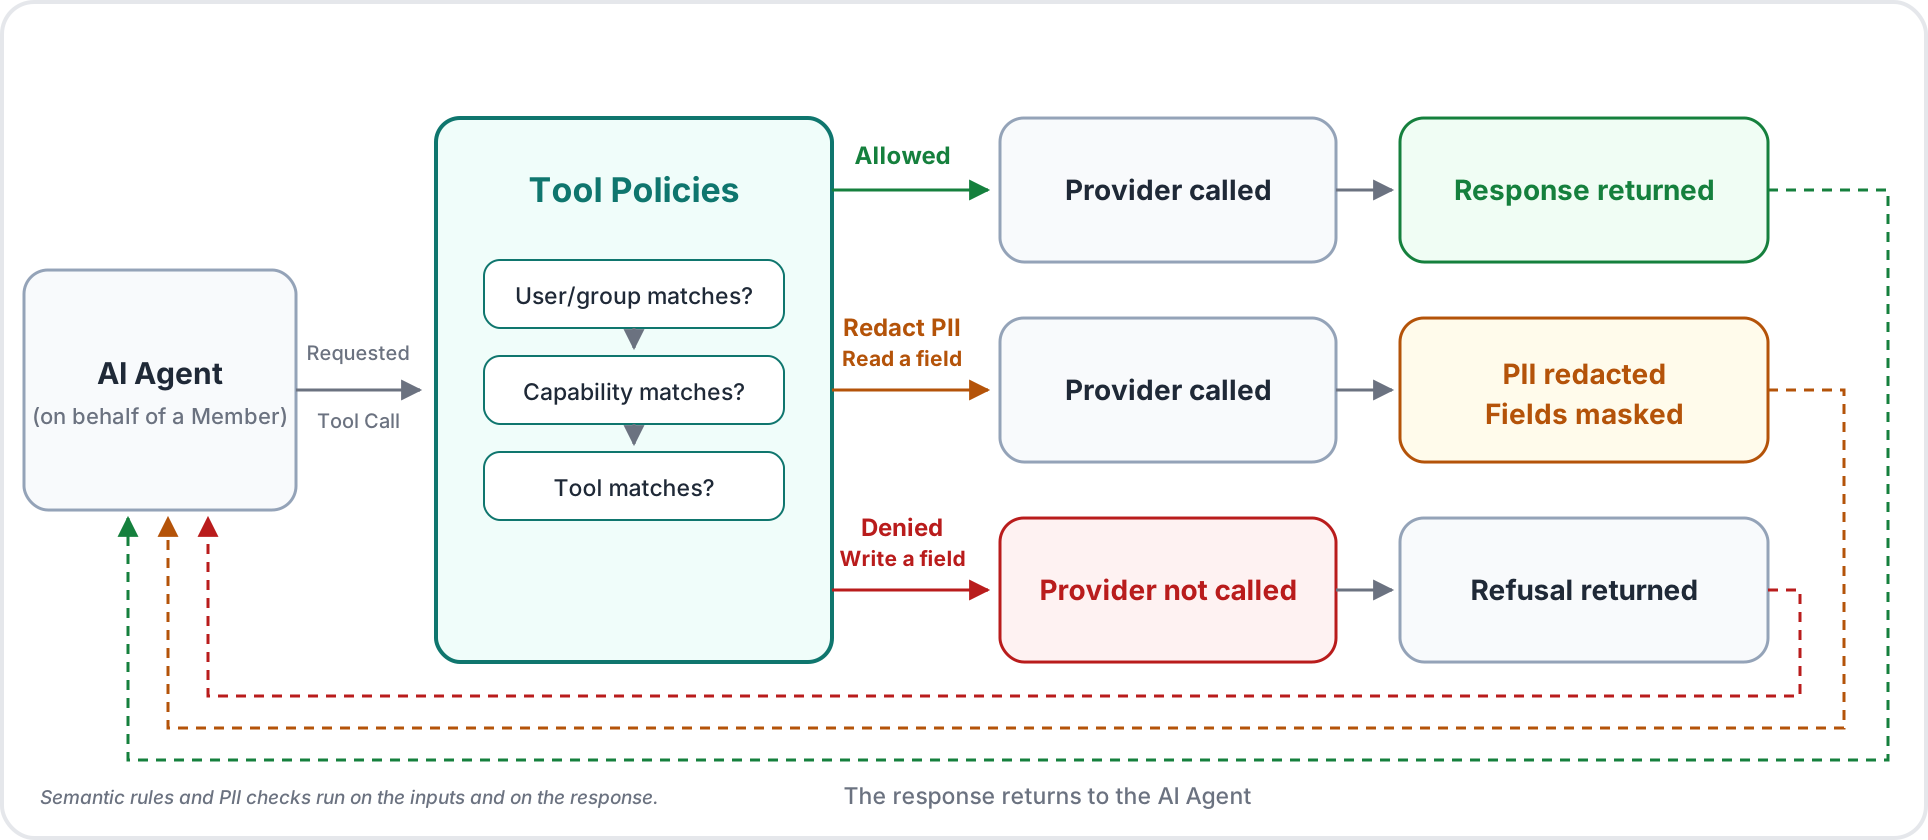
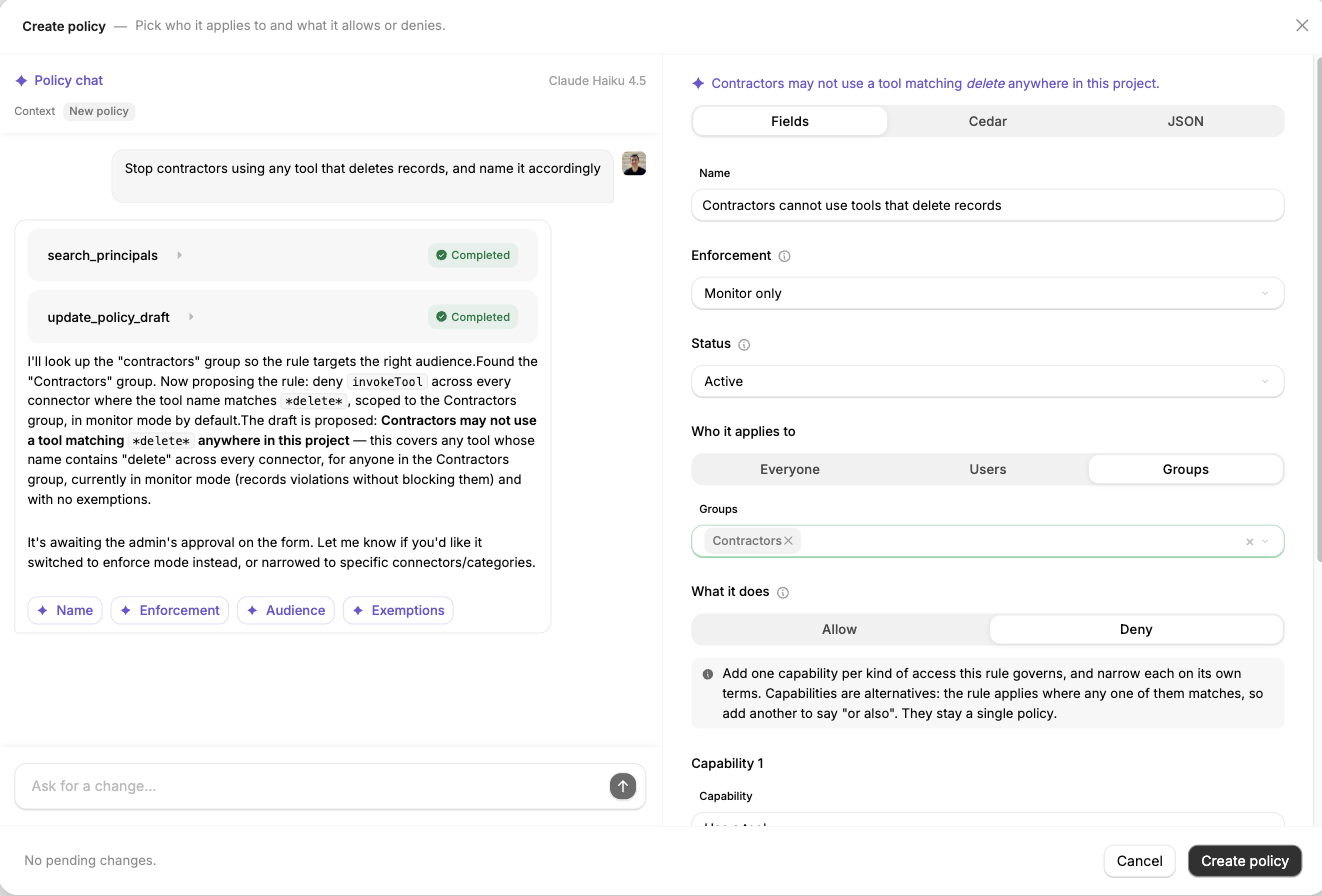
- `*` is the only wildcard, and it matches any run of characters. - A pattern has to cover the whole name: `salary` matches only something named exactly that, so use `*salary*` to match it anywhere. - Matching is case-sensitive. - `?`, `[a-z]`, and `{a,b}` are ordinary characters here, not wildcards. A pattern using one saves cleanly and then never matches anything. | Pattern | Matches | Does not match | | --- | --- | --- | | `*delete*` | `personio_delete_person` | `okta_remove_user_from_group` | | `salary` | `salary` | `employee.compensation.salary` | | `*Delete*` | Nothing, since matching is case-sensitive. | `personio_delete_person` |
For a deny rule, use **Exempt from this rule** to name users or groups the rule does not apply to. Another matching deny can still refuse the call. Review the policy: - **Plain Text**: the panel footer restates the rule in plain words, for example: > Everyone in this project may not use a tool matching `*delete*` on Workday, except Finance (Group). - **Cedar**: the exact statement the engine will evaluate, in [Cedar syntax](https://docs.cedarpolicy.com/policies/syntax-policy.html). The view is read-only; change the form and the statement follows. - **JSON**: the same statement in Cedar's JSON encoding. Then click **Create policy**. If you used the assistant, the button reads **Accept changes and create**. See [Build a policy with the Policy AI Assistant](#build-a-policy-with-the-policy-ai-assistant).
Create policy panel with Policy chat on the left and the form on the right, showing a policy named Contractors cannot use tools that delete records, the audience set to the Contractors group, and a Deny rule on the Use a tool capability ## Build a policy with the Policy AI Assistant The **Policy AI Assistant** opens beside the form, as **Policy chat**, whenever you create or edit a policy. Describe the rule in your own words and the assistant drafts it in the form for you to review: - Suggestions are highlighted in the form, with the previous value shown underneath. - Each suggestion can be applied or reverted individually. - All changes can be applied using the buttons at the top of the form or by clicking **Accept changes and create** or **Accept changes and save**. The assistant drafts every capability, including value rules, semantic rules and PII redaction. Ask for *Keep unreleased financial results out of Slack for everyone outside Finance* and it writes the semantic rule's question, picks the send tools, and sets the audience and exemption. Create policy panel split in two, with Policy chat on the left showing completed search_principals and update_policy_draft tool calls and an explanation of the proposed rule, and the policy form on the right with a bar reading 3 changes from the assistant need review ### What the assistant can access The assistant can look things up in the project as it drafts, and the transcript shows each lookup as it runs: | It can find | So you can say | | --- | --- | | Users and groups | *Exempt payroll*, (where you have a group defined as "payroll") | | Connectors and categories | *Block writes to any HRIS connector* | | The tools on a connector | *Stop the delete ones on Workday* | | Linked accounts | *Only the Acme production account* | | Related tool call logs | *Stop this tool returning some of the fields it returned* | By default, only a tool call's tool, connector and caller are exposed. With [advanced logging](/secure/observability#advanced-logs) enabled, the assistant can read the request/response payloads to help define field related capabilities. For example, using a prompt like: > Stop contractors deleting records 1. The assistant searches existing groups, sets **Who it applies to** to `Groups` and populates with `Contractors`. 2. Writes a deny on **Use a tool** with a `*delete*` pattern, with **applies to** set to `Everything`. The assistant also flags what a rule may miss. For example, a pattern matching `delete` does not catch a connector whose tools are named with `remove` or `archive`, so you can ask it to add those patterns too. ### Starting from logs Policy creation can be initiated from a specific log instead of the policies page. Go to [StackOne Logs](https://app.stackone.com/logs). Select the log of a call you want to create a policy from. Click **Use in policy** at the top of the panel. This takes you to the **Policies** page with the context of the log selected. Either select an existing policy **OR** create a new policy by clicking **Create policy**. The **Policy AI Assistant** now has the context of the selected log. Describe the policy you want. For example: > *This call should not have been allowed to return salary* > *This person should not have been allowed to make it* See [Build a policy with the Policy AI Assistant](#build-a-policy-with-the-policy-ai-assistant). ## Testing a policy before enforcing it Two checks come before enforcing: 1. **Test against personas**: in the create and edit panel, **Test this policy against personas** shows what the rule would decide for the members you choose, without making a call. 2. **Monitored**: set the policy's **Enforcement** to **Monitored** and applicable tool calls are flagged as calls the policy would have applied to, while continuing unaffected. Value rule matches, semantic rule answers and PII detections are recorded the same way. Only when **Enforcement** is set to **Enforced** are tool calls blocked or modified as defined by the policy. ## Change a policy's enforcement level The **Policies** table displays an **Enforcement** column showing each policy's current level: **Enforced**, **Monitored**, or **Disabled**. Select the project and open [**Project Settings > Policies**](https://app.stackone.com/settings/policies). On the policy's row in the table, click the **...** button and select the new level: - **Enforce** moves the policy to **Enforced**. - **Monitor** or **Stop enforcing** moves the policy to **Monitored**. - **Disable** moves the policy to **Disabled**. You can also edit the policy and change the **Enforcement** field in the side panel. ## Duplicating policies Instead of starting with a blank new policy, an existing policy can be used as a template. Select the project and open [**Project Settings > Policies**](https://app.stackone.com/settings/policies). On an existing policy's row in the table, click the **...** button and select **Duplicate**. A new policy is drafted with the original policy's details except: - **Name**: original name is appended with `(copy)`. - **Enforcement**: set to **Disabled**. Edit as needed, then click **Create policy**. A policy whose rule the builder cannot read, or that holds more than one statement, cannot be duplicated. ## Examples One **Use a tool** deny with **Applies to** set to **Everything** and **Tools matching** set to `*delete*`, for the `Contractors` group. Run it in **Monitored** first, check the logged decisions, then switch it to **Enforced**. A **Value rule** deny on the payment tools for NetSuite and Xero, on the payment amount, allowing amounts between 25 and 500 in `USD`. A payment outside that range, or in another currency, is refused before the tool runs, and payments inside it go through as before. A **Semantic rule** deny on the send tools for Slack, Gmail and Notion, asking *Does this message contain unreleased financial results?* on **Inputs**. It applies to **Everyone**, with the `Finance` group exempt. The agent can still summarize the month-end close for Finance, and a message that posts those numbers to a shared channel is refused. Two policies for the support agent's users: - **Zendesk**: a **Redact PII** deny on the Zendesk account, set to **Redact**, so responses reach the agent without email addresses, phone numbers or card numbers. The same policy adds **Read a field** on Zendesk, with **Fields matching** set to the card number's path, so that field is always masked. - **Jira and Slack**: a **Redact PII** deny on the Jira and Slack accounts, set to **Block**, so a write that contains PII is refused. The agent can still escalate the bug to Jira, without the customer's details. ## What a denied call returns When an enforced policy refuses a tool call before it runs, the request fails with HTTP `403` and nothing reaches the underlying provider. The refusal returns to the agent as the tool result. ```json { "message": "Action 'personio_delete_person' is not permitted by project policy", "errorType": "POLICY_DENIED_ERROR", "level": "project" } ``` A call refused by a value rule, a semantic rule or a PII block on its inputs fails the same way, before the provider is called. A PII block on a response refuses the call after the provider responds: the agent receives the refusal instead of the data. Masking and redaction on a response never fail the call: the agent receives the response with the denied fields masked and the detected spans redacted. ## Troubleshooting - **It matches nothing.** The pattern has to cover the whole name: `salary` only matches a tool named exactly that, so use `*salary*`. `?`, `[a-z]`, and `{a,b}` do not perform any special matching. - **It misses tools you expected.** Matching is case-sensitive: `*Delete*` misses `personio_delete_person`. A pattern matches exactly rather than describing a behavior: `*delete*` does not catch a tool named `okta_remove_user_from_group`. - **It matches more than you expected.** `*` matches any run of characters, underscores included, so `*create*` could cover `leaddocket_list_opportunities_created_since`. Check the following in order: 1. The policy's **Enforcement** is set to **Enforced** (not **Monitored** or **Disabled**). 2. The acting member is in its audience (and not exempt). 3. The call is made in the project the policy was created in. 4. The tool name or pattern matches exactly, including case. 5. The caller is a member connected through an [AI platform](/connect/overview), so the call carries their identity. A call made with a project API key alone names no member, so no policy governs it. Yes, on an action log. Open the record and select the **Policy** tab. ## Next steps Set which actions each Connector Profile exposes. Maintain the groups your policies apply to. Control who can link accounts on a profile. Configure request logging and retention. # PII Redaction Source: https://docs.stackone.com/secure/pii-redaction Remove personal data from tool inputs and responses, and from request and response bodies before Advanced Logs stores them. **PII Redaction** finds personally identifiable information (PII), such as email addresses and phone numbers, in the data passing through StackOne and replaces each value with a tag such as ``. It runs in two places, each turned on separately. A **Redact PII** rule in [Policies](/secure/policies) cleans what the agent sends to a tool and what the tool returns. The **Redact personal information (PII)** setting in [Advanced Logs](/secure/observability#advanced-logs) cleans request and response bodies before they are stored. ```mermaid graph TD Call["AI agent calls a tool"] --> RuleIn["Redact PII rule redacts or blocks the input"] RuleIn --> Action["StackOne runs the action"] Action --> Provider["Provider responds"] Provider --> Defender["Defender scans the response"] Defender --> RuleOut["Redact PII rule redacts or blocks the response"] RuleOut --> Receive["AI agent receives the response"] Action -.->|request and response bodies| LogScan["Advanced Logs PII redaction"] LogScan --> Log["Stored advanced log"] style Call fill:#f3f4f6,stroke:#d1d5db,stroke-width:2px,color:#374151 style Receive fill:#f3f4f6,stroke:#d1d5db,stroke-width:2px,color:#374151 style Provider fill:#f3f4f6,stroke:#d1d5db,stroke-width:2px,color:#374151 style Action fill:#dbeafe,stroke:#3b82f6,stroke-width:2px,color:#1e40af style Defender fill:#dbeafe,stroke:#3b82f6,stroke-width:2px,color:#1e40af style RuleIn fill:#16a34a,stroke:#15803d,stroke-width:2px,color:#fff style RuleOut fill:#16a34a,stroke:#15803d,stroke-width:2px,color:#fff style LogScan fill:#16a34a,stroke:#15803d,stroke-width:2px,color:#fff style Log fill:#f3f4f6,stroke:#d1d5db,stroke-width:2px,color:#374151 ``` ## Choose where to redact The two surfaces are independent, so a project can use either or both. | | **Redact PII** rule in Policies | **Redact personal information (PII)** in Advanced Logs | | --- | --- | --- | | **Protects** | The inputs your agent sends to a tool and the responses the tool returns. | The request and response bodies Advanced Logs stores. | | **Classes** | The ones you select: **Email address**, **Phone number**, **Social security number**, **Credit card number**. | Every kind of personal data the scan detects, including names, phone numbers, email addresses, postal addresses, government ID numbers, and payment card numbers. | | **Kept intact** | Everything outside the selected classes, including record UUIDs, order numbers, and API keys. | Log metadata such as the path, status code, connector, and Linked Account. | | **Scope** | The whole project, or specific Linked Accounts. | The whole project. | | **Calls covered** | Calls made by the users or groups the policy covers, through an [AI platform](/connect/overview). | Every call that writes an advanced log of an action. | | **On a match** | **Redact** replaces the value. **Block** refuses the call, whether the match is in the inputs or the response. | The value is replaced. | | **Rollout** | **Monitored** records what the rule would do, then **Enforced** acts. | On or off. | | **Configured in** | **Project Settings > Policies** | **Project Settings > Advanced Logs** | ### Redact PII and semantic rules **Redact PII** and the **Semantic rule** capability both use a model to work out what the data in a call contains, then apply your policy to it, on a tool's inputs and its response. A semantic rule answers a plain-language question you write. **Redact PII** looks for four fixed classes of PII with StackOne's own model, and finds them inside any field, including free text such as a ticket description. See [Capabilities](/secure/policies#capabilities) for both. ## How detection works StackOne scans every string value in the body, in two passes: 1. **Patterns** match well-formed values such as email addresses. 2. **StackOne's PII model**, a token classifier StackOne trained for this task, reads the text for personal data the patterns miss, such as a phone number inside a ticket comment. The model is about 24MB and runs inside StackOne's runtime, in the process that runs the action. Your data is not sent to a third-party detection service, and detection adds milliseconds rather than a network call. Only the matched span is replaced, so a ticket description keeps its text and loses the email address inside it. On a tool input, redaction runs before the call reaches the provider. On a response, it runs after [Defender](/secure/defender) has scanned the response, and before the agent receives it. ## Redact PII in tool calls A **Redact PII** rule is a [policy](/secure/policies) capability. Denying it for a class redacts that class from tool inputs and responses, or blocks any call where it appears. Every class you don't select passes through unchanged, so a customer number or record UUID next to a redacted email address stays as it was. 1. Select the project and open **Project Settings > Policies**. 2. Click **Create policy** and give the policy a descriptive name. 3. Set **Enforcement** to **Monitored**. 1. Under **Who it applies to**, select **Everyone**, **Users**, or **Groups**, then pick the users or groups. 2. Under **What it does**, select **Deny**. Under **Capabilities**, add **Redact PII**. Denying **Redact PII** checks calls for the chosen classes of PII. StackOne's own PII model scans the tool's inputs before it runs and the response before the agent sees it, including free-text fields such as ticket bodies and notes. Record UUIDs, order numbers, and API keys stay intact. The [PII Redaction benchmark](https://www.stackone.com/platform/pii-redaction/#benchmarks) compares the model with Microsoft Presidio on connector data. Choose which targets it applies under **Applies to**: - **Everything** covers every connector and account in the project. - **An account** covers specific [Linked Accounts](/gateway/concepts/linked-accounts). Search accounts by name or owner. Under **Which PII to redact**, select one or more classes. There is no pattern to enter. Then choose what a detection does: - **Redact** replaces each detected span in the inputs and in the response, and lets the call continue. The rest of the input or response is unchanged. - **Block** refuses the call. When the PII is in the inputs, the provider is never called. When it is detected in the response, the agent receives a refusal instead of the data. A response that cannot be scanned (it is streamed, above the scan size limit, or the scan fails) is returned unredacted, and the request log records which classes were not redacted. Review the rule in the panel footer, then click **Create policy**. Under **Monitored**, PII detections are recorded and the call goes through unchanged. Run real calls, then open an action log and select the **Policy** tab to review the record. Once the rule catches what you expect, edit the policy, set **Enforcement** to **Enforced**, and save. The rule acts from the project's next call. For every option on the policy form, see [Create a policy](/secure/policies#create-a-policy). ### What changes in the call With **Redact**, each match is replaced by a tag naming its class, such as ``, in the input the provider receives or the response the agent receives. The agent can tell a value was withheld by policy, and which class it was. With **Block**, the agent receives a [refusal](/secure/policies#what-a-denied-call-returns) as the tool result. If a chosen class is in the inputs, the provider is never called. If it is detected in the response, the agent gets the refusal instead of the data. When a rule removed something, the tool result also carries `policyMetadata`. Its `result` is `partial`, and `redactedClasses` names each class removed and the policy level, not the rule. For example, a response from which an email address was removed: ```json { "isError": false, "result": { "data": { "id": "8f2c1a7e-4b6d-4e3a-9c1f-2d7b5e0a3c91", "description": "Refund request. Email ." } }, "policyMetadata": { "result": "partial", "maskedFields": [], "redactedClasses": [ { "class": "email", "level": "project" } ] } } ``` The class values are `email`, `phone_number`, `ssn`, and `credit_card`. ## Redact PII in Advanced Logs Select the project and open **Project Settings > Advanced Logs**. 1. Turn **Status** on, if it is off. The other settings can only be changed while it is on. 2. Turn on **Redact personal information (PII)**. ![Advanced Logs settings: status, storage, background operations, and PII redaction](/images/project-advanced-logs.png) When **Redact personal information (PII)** is on, StackOne scans each body before the log is written and replaces each personal value it detects with a tag naming its type, such as `` or ``. Credential-like tokens the patterns catch have no type and become ``; named credential fields follow the **Credentials** rule below. Only the redacted copy is stored. - **Detection.** Patterns catch email addresses and credential-like tokens. A model finds names, phone numbers, postal addresses, government ID numbers, payment card numbers, and other personal data. - **Scope.** Request and response bodies only. Log metadata such as the path, status code, connector, and Linked Account stays intact, so logs remain searchable. - **Coverage.** The bodies of action call logs. - **Applies to new logs only.** Logs that are already stored are not changed. - **Credentials.** Fields whose names match a fixed list of credential names, such as `password`, `token`, `api_key`, `client_secret`, and `authorization`, are masked in every stored body whether or not PII redaction is on. The value is replaced with `**redacted**`, followed by its last five characters when it is longer than 10 characters. StackOne may not catch every instance of personal data. Don't treat redaction as the only control for regulated data. For the other Advanced Logs settings, see [Observability](/secure/observability#advanced-logs). ## What is recorded Each surface leaves a different trace: - **Redact PII rule.** Open the action log and select the **Policy** tab. A call the rule changed is recorded with result `partial`, and the rule that acted shows the effect `redacted`. Under **Monitored**, the record shows the PII the rule detected instead. - **Advanced Logs.** The stored body is the redacted copy. Nothing records which values were replaced. ## FAQ No. Both passes run inside StackOne's runtime, in the process that runs the action. No third-party detection service sees your data. On connector data, detection takes about a millisecond per field at the median, measured for detection alone on 4 CPU cores. Longer text, such as a full document, takes longer. Detection runs in the process that runs the action, so there is no extra network call. A **Redact PII** rule removes only the classes you select, and record UUIDs, order numbers, and API keys belong to none of them. The Advanced Logs setting detects them in stored bodies. The **Redact PII** rule covers the four classes listed in [Choose where to redact](#choose-where-to-redact). To keep a field such as a home address away from the agent, deny **Read a field** on it in a [policy](/secure/policies#capabilities). Span-level F1 score compared with Microsoft Presidio, on 247 Connector PII examples and 1,000 examples for each other dataset: | Dataset | StackOne | Presidio | | --- | --- | --- | | OpenPII (synthetic prose) | 89.3% | 67.3% | | Nemotron-PII (business documents) | 95.5% | 69.4% | | Privy (JSON, SQL, and XML payloads) | 98.9% | 51.3% | | Connector PII (connector field values) | 97.9% | 68.1% | On 129 connector field values with no personal data, StackOne's model flagged 3.1% as PII, and Presidio flagged 48.8%. The OpenPII row uses 1,000 English validation rows of [OpenPII 1.5M by Ai4Privacy / Ai Suisse SA (CC BY 4.0)](https://huggingface.co/datasets/ai4privacy/pii-masking-openpii-1.5m). All rows were measured in October 2026. StackOne's model was trained on the training splits of Nemotron-PII and Privy and on connector data, among other sources, and never on OpenPII. Connector PII is StackOne's own dataset. No test example appears in the training data. ## Next steps Combine Redact PII with tool and field rules for the same users. Configure Advanced Logs storage and retention. Scan tool responses for prompt injection. Limit which actions each Connector Profile exposes. Benchmark and examples. # Identity and Access Source: https://docs.stackone.com/secure/identity-and-access/overview Manage how your team signs in to StackOne and what each person can access. Enable your users to start using StackOne: Set up how users sign in. Use Single Sign-On (SSO) so users sign in through your identity provider (IdP), or keep passwords with MFA. Choose how users join and leave. Invite users, add them at their first SSO sign-in with Just-in-Time Provisioning, or sync them from your IdP's directory with SCIM Provisioning. Give users the access they need. Assign each user a role, from the whole organization down to a single linked account. Use groups to give many users the same project or account access. # Authentication Source: https://docs.stackone.com/secure/identity-and-access/authentication/overview Set up Single Sign-On with an identity provider, or use passwords with multi-factor authentication. StackOne can be set up to let users sign in with Single Sign-On or with a password and MFA. Connect the SAML identity provider and verify the domain so users sign in through the IdP. Change your password, turn on MFA, and require MFA for the whole organization. # Single Sign-On Source: https://docs.stackone.com/secure/identity-and-access/authentication/sso/overview Let users sign in to StackOne through your organization's SAML identity provider. SAML SSO is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). StackOne Single Sign-On (SSO) lets the organization's users sign in through its own SAML 2.0 identity provider (IdP). StackOne acts as the SAML service provider (SP), and the IdP authenticates users. Each organization has one SSO connection, bound to one email domain. Once that domain is verified, anyone whose work email is on it signs in through the IdP instead of with a StackOne password. They can start from the StackOne sign-in page by entering their email, or open the StackOne app from the IdP. Signing in with SSO doesn't add anyone to the organization. To add users, see [Manage Team](/secure/identity-and-access/manage-team/overview). ## Set up an SSO connection The guide for your SAML IdP takes you through each part of the setup: - Creating the SAML app in the IdP. - Registering it in StackOne. - Verifying the domain. - Managing the connection afterward. ## Require SSO Once the domain is verified, you can require users to sign in through SSO and turn off email and password sign-in. Enforcing doesn't check that sign-in works. A misconfigured SAML app, an unassigned user, or a certificate or issuer mismatch still enforces, and **anyone the IdP can't authenticate is locked out**. Before you enforce, open a private or incognito window and complete an SSO sign-in as a user assigned to the app in the IdP, not only your own account. 1. Go to [**Organization > Security > Authentication**](https://app.stackone.com/organization/security/authentication). 2. On the **Enforcement Policy** card, select **Edit policy**. 3. Add the SAML connection to **Enforced methods**. 4. Select **Save changes**. The Enforcement Policy panel under Organization > Security > Authentication, where you add the SSO connection to the enforced sign-in methods. Enforcement takes effect as soon as you save. Anyone whose session didn't come through an enforced method, including you, is asked to sign in through the IdP the next time they load a page or switch to the organization. Locked out after enforcing? An **Organization Admin** who can still reach the dashboard can remove the method from the **Enforcement Policy** to restore password sign-in. If no one can get in, contact StackOne support. ## Next steps Add users who aren't members yet when they sign in, and map an attribute to organization admin. Provision and deactivate members automatically from the IdP. Grant many members the same project or account access at once. # Okta SSO Source: https://docs.stackone.com/secure/identity-and-access/authentication/sso/okta Set up SAML Single Sign-On between Okta and StackOne. SAML SSO is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Connect Okta as the organization's SAML 2.0 identity provider (IdP), so users sign in to StackOne with their Okta credentials. Before setting up Okta SSO, you need: - The **Organization Admin** role in StackOne. - Administrator access to the **Okta Admin Console**. - The ability to add a DNS TXT record for your email domain, which proves you own it. ## Start the connection in StackOne 1. Go to [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). 2. Click **Get started**. 3. Select **Okta** as the provider. On the **Connection details** step, fill in both fields: - **Connection name**: a name for the connection. StackOne generates the connection's unique ID from it. - **Domain**: the email domain your users sign in with. The **Configure your identity provider** step has the values you need when you create the app in Okta: - **ACS URL (Single sign-on URL)**: where Okta posts the SAML assertion. - **Audience URI (SP Entity ID)**: identifies StackOne to Okta. - **Default RelayState**: the dashboard URL, where an IdP-initiated sign-in lands. Keep this StackOne tab open. You return to the wizard to register the provider after you build the Okta app. StackOne Configure step showing the ACS URL and SP Entity ID to copy into Okta ## Create the SAML app in Okta 1. In the **Okta Admin Console**, go to **Applications > Applications**. 2. Click **Create App Integration**. 3. Choose **SAML 2.0**. 4. Click **Next**. Okta Create App Integration dialog with SAML 2.0 selected 1. On **General Settings**, enter an **App name**, for example `StackOne SSO`. 2. Click **Next**. Okta general settings page with the app named StackOne SSO In **Configure SAML**, set the following: - **Single sign-on URL**: the **ACS URL** from StackOne. - **Audience URI (SP Entity ID)**: the **SP Entity ID** from StackOne. - **Default RelayState**: the **Default RelayState** from StackOne. - **Name ID format**: `EmailAddress`. - **Application username**: `Email`. Okta SAML settings filled with the StackOne ACS URL, Audience URI, EmailAddress Name ID, and Email username 1. Further down the same **Configure SAML** screen, under **Attribute Statements (optional)**, add two attributes: | Name | Name format | Value | |------|-------------|-------| | `givenName` | `Unspecified` | `user.firstName` | | `surname` | `Unspecified` | `user.lastName` | These set the user's display name in StackOne. 2. Click **Next**. 3. Click **Finish**. Adding these to an existing app only sets names for new users. To sync names for existing users, use [SCIM Provisioning](/secure/identity-and-access/manage-team/scim/okta). 1. Open the **Assignments** tab. 2. Assign the people or groups who should sign in to StackOne through Okta. Only assigned users can complete SSO. Okta Assignments tab for adding users to the StackOne SSO application Open the app's **Sign On** tab, then get the values StackOne needs. Download the **Identity Provider metadata** XML. 1. In the **SAML Setup** panel, click **View SAML setup instructions**. 2. Copy these values for StackOne: - **Identity Provider Issuer**: the Entity ID, for example `http://www.okta.com/exk...`. - **Identity Provider Single Sign-On URL**: Okta's login endpoint. - **X.509 Certificate**: the signing certificate in PEM format. Okta Sign On tab showing the Identity Provider Issuer, SSO URL, and X.509 certificate ## Register the provider in StackOne Switch back to the StackOne tab and continue to the **Register your SSO provider** step. Supply the three values from Okta. 1. Click **Upload SAML metadata file**. 2. Select the **Identity Provider metadata** XML you downloaded from Okta. StackOne fills in **Entity ID (Issuer)**, **SSO URL (Entry Point)**, and **X.509 Certificate**. 3. Review the imported values before continuing. StackOne Register step with the metadata upload option above the manual entry fields Set the following: - **Entity ID (Issuer)**: the **Identity Provider Issuer** from Okta. - **SSO URL (Entry Point)**: the **Identity Provider Single Sign-On URL** from Okta. - **X.509 Certificate**: the **X.509 Certificate** from Okta. StackOne Register form completed with the Okta issuer, SSO URL, and certificate Select **Continue**. The connection is registered, but stays inactive until the domain is verified. StackOne SSO connection card showing configuration details and pending domain verification ## Verify the domain Verification proves the organization owns the domain and activates SSO. Once it's verified, existing StackOne users on the domain are linked to the SSO connection, so they keep one account. On the wizard's **Verify your domain** step, copy the record's **Name** and **Value**. The **Value** has this form: ``` _stackone-sso-verification-token-{providerId}={token} ``` StackOne's Verify your domain step showing the DNS TXT record name and value. In the domain's DNS panel, add a TXT record: - **Name/Host**: the domain. Use `@` if it's the root of the DNS zone, or the subdomain label if the email domain is a subdomain. - **Value**: the full `_stackone-sso-verification-token-...` string, as its own value. Don't append it to an existing TXT value, such as an SPF record. Add the `_stackone-sso-verification-token-...` string as the record's **Value**, not its Name. It looks like a DNS host label, as `_dmarc` and `_domainkey` do, so it's easy to paste into **Name/Host** by mistake. A record on the wrong name fails verification without an error. 1. Go to **DNS > Records** and select **Add record**. 2. Set **Type** to `TXT` and **Name** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Content**. Cloudflare allows several TXT records at the same name, so add a new record rather than editing an existing one. 1. Open the hosted zone and select **Create record**. 2. Set **Record type** to `TXT`. Leave **Record name** blank for the root domain, or enter the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token in quotes. If a TXT record already exists at that name, edit it and add the token as a new line instead. 1. Open the zone and add a standard record set. 2. Set the type to `TXT`, with the DNS name set to the email domain, such as `acme.com` or `eu.acme.com`. 3. Paste the token. If a TXT record set already exists, edit it and add the token as a new item instead. 1. Open the domain's DNS records and select **Add New Record**. 2. Set **Type** to `TXT` and **Name** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Value**. 1. Open **Advanced DNS** and select **Add New Record**. 2. Choose **TXT Record**, and set **Host** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Value**. DNS changes can take up to 48 hours to propagate, though they often complete within minutes. Check what's publicly visible with [Google Admin Toolbox Dig](https://toolbox.googleapps.com/apps/dig/#TXT/). 1. Select **Verify**. Once the record is visible, the domain is verified and SSO is active. 2. Select **Finish** to close the wizard. If the check fails, wait for DNS to propagate and try again. To finish setup first, select **Verify Later**, then verify afterward from the **Trusted Domain** card on the connection's **General** tab. StackOne SSO connection card showing the domain as verified and SSO active ## Manage the connection Open the connection from [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). The **General** tab is where you maintain it after setup: - Select **Edit SAML** to update the identity provider values, either by uploading new metadata XML or by editing the **Entity ID (Issuer)**, **SSO URL (Entry Point)**, and **X.509 Certificate** directly. - Select **Edit Domain** to change the trusted domain. Changing it resets verification, so users stop being redirected until you verify it again. You can't change it while SSO is enforced. The connection's General tab, showing the SAML 2.0 Configuration values (Single sign-on URL, Audience URI, Default Relay State) and the Trusted Domain verification status. From the connection's page header: - **Settings** edits the **Connection name**. The **Provider ID** is generated at setup and can't be changed. - **Delete** removes the SSO connection. It's disabled while SSO is enforced, so turn off enforcement on the **Authentication** tab first. To require users to sign in through Okta, see [Require SSO](/secure/identity-and-access/authentication/sso/overview#require-sso). Deleting the connection sends users on the domain back to email and password sign-in, so make sure they have another way in first. To change SAML values, use **Edit SAML** instead. Deleting it also removes SCIM Provisioning, if linked, and revokes its token. Provisioning from Okta then fails with `401` until you link SCIM again and paste the new token into Okta. Users already provisioned keep their access. To add, update and deactivate users automatically from Okta, set up [Okta SCIM Provisioning](/secure/identity-and-access/manage-team/scim/okta) once the domain is verified. ## Troubleshooting | Symptom | Likely cause | Fix | |---------|--------------|-----| | `ERROR_UNMATCH_CERTIFICATE_DECLARATION_IN_METADATA` | The registered certificate doesn't match the one Okta signs with. Okta issues a new certificate per app. | Re-copy the **X.509 Certificate** from this app's **View SAML setup instructions** and update it via **Edit SAML**. | | `ERR_UNMATCH_ISSUER` | The **Entity ID (Issuer)** doesn't match the issuer Okta sends. | Copy the **Identity Provider Issuer** (`http://www.okta.com/exk...`) and update it via **Edit SAML**. | | "Provider domain has not been verified" | Domain verification hasn't completed. | Finish [Verify the domain](#verify-the-domain). | | Sign-in redirects to the wrong Okta, or a domain appears already taken | StackOne doesn't automatically reserve a domain to one organization, so another StackOne organization may have registered the same domain. | Contact StackOne support to resolve which organization should own SSO for the domain before you enforce it. | | Verification keeps failing | The TXT record is on the wrong name, not its own value, or DNS hasn't propagated. | Use `@` for a root domain or the subdomain label otherwise, add the token as its own TXT value, and check propagation with [Dig](https://toolbox.googleapps.com/apps/dig/#TXT/). | | Users not redirected to Okta | The domain isn't verified, or the user isn't assigned in Okta. | Verify the domain, and confirm the user is on the app's **Assignments** tab. | | New users show their email address as their name | The app sends no name attribute statements, so the assertion carries only the email subject. | Add the `givenName` / `surname` attribute statements to the Okta app (see the setup steps above). | | `403 Forbidden` when opening SSO | You lack the **Organization Admin** role. | Ask an **Organization Admin** to make the change or to grant you the role. | ## Next steps How SSO, domain verification, and SCIM Provisioning fit together. Set up SAML SSO with Entra ID instead of Okta. Connect any SAML 2.0 identity provider. # Microsoft Entra SSO Source: https://docs.stackone.com/secure/identity-and-access/authentication/sso/microsoft-entra Set up SAML Single Sign-On between Microsoft Entra ID and StackOne. SAML SSO is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Connect Microsoft Entra ID (formerly Azure AD) as the organization's SAML 2.0 identity provider (IdP), so users sign in to StackOne with their Entra credentials. Before setting up Microsoft Entra SSO, you need: - The **Organization Admin** role in StackOne. - Access to the **Microsoft Entra admin center** with permission to create enterprise applications, such as the **Application Administrator** or **Cloud Application Administrator** role. - The ability to add a DNS TXT record for your email domain, which proves you own it. ## Start the connection in StackOne 1. Go to [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). 2. Click **Get started**. 3. Select **Microsoft Entra ID** as the provider. On the **Connection details** step, fill in both fields, then select **Continue**: - **Connection name**: a name for the connection. StackOne generates the connection's unique ID from it. - **Domain**: the email domain your users sign in with. The **Configure your identity provider** step has the values you need when you create the app in Entra: - **Reply URL (ACS URL)**: where Entra posts the SAML assertion. - **Identifier (Entity ID)**: identifies StackOne to Entra. - **Default RelayState**: the dashboard URL, where an Entra-initiated sign-in lands. Keep this StackOne tab open. You return to the wizard to register the provider after you build the Entra app. StackOne SSO wizard showing the Reply URL and Identifier values to copy into Microsoft Entra. ## Create the SAML app in Microsoft Entra 1. In the **Microsoft Entra admin center**, go to **Identity > Applications > Enterprise applications**. 2. Select **New application > Create your own application**. 3. Enter a name, for example `StackOne SSO`. 4. Choose **Integrate any other application you don't find in the gallery (Non-gallery)**, then select **Create**. 1. Open the new application and go to **Single sign-on**. 2. Select **SAML**. 1. In **Basic SAML Configuration**, select **Edit**. 2. Set the following: - **Identifier (Entity ID)**: the **Identifier (Entity ID)** from StackOne. - **Reply URL (Assertion Consumer Service URL)**: the **Reply URL (ACS URL)** from StackOne. - **Relay State (Optional)**: the **Default RelayState** from StackOne. 3. Select **Save**. Microsoft Entra, Basic SAML Configuration, with Identifier (Entity ID) and Reply URL (ACS URL) set to the StackOne values. 1. In **Attributes & Claims**, select **Edit**. 2. Open **Unique User Identifier (Name ID)**. 3. Set the following: - **Name identifier format**: `Email address`. - **Source attribute**: `user.mail`. 4. Save the claim. Microsoft Entra, Attributes & Claims, with the unique user identifier (Name ID) source set to user.mail and format Email address. `user.mail` must be set for everyone who signs in. It's often empty for cloud-only accounts without an Exchange Online mailbox, and for users synced from on-premises Active Directory without a `mail` attribute. When it's empty, sign-in fails with "Unable to extract user ID or email from SAML response". If users' UPN matches their email address, use `user.userprincipalname` as the source attribute instead. Otherwise, set `mail` for each user before they sign in. 1. In **Attributes & Claims**, select **Add new claim**. 2. Set **Name** to `givenName`, leave **Namespace** blank, and set **Source attribute** to `user.givenname`. Select **Save**. 3. Repeat with **Name** set to `surname` and **Source attribute** set to `user.surname`. These set the user's display name in StackOne. Adding these to an existing app only sets names for new users. To sync names for existing users, use [SCIM Provisioning](/secure/identity-and-access/manage-team/scim/microsoft-entra). 1. Go to **Users and groups** and select **Add user/group**. 2. Assign the people or groups who should sign in to StackOne through Entra. Only assigned users can complete SSO. On the **Single sign-on** page, get the values StackOne needs. In **SAML Certificates**, download the **Federation Metadata XML**. 1. From **Set up [App name]**, copy the **Login URL** and the **Microsoft Entra Identifier**. 2. In **SAML Certificates**, download the **Certificate (Base64)**. Microsoft Entra, SAML Certificates, where you download the Federation Metadata XML or the Base64 certificate. ## Register the provider in StackOne Switch back to the StackOne tab and continue to the **Register your SSO provider** step. Supply the three values from Entra. 1. Select **Upload SAML metadata file**. 2. Select the **Federation Metadata XML** you downloaded. StackOne fills in **Entity ID (Issuer)**, **SSO URL (Entry Point)**, and **X.509 Certificate**. 3. Review the imported values before continuing. StackOne register step with fields for the issuer, SSO URL, and certificate, plus the metadata upload button. Set the following: - **Entity ID (Issuer)**: the **Microsoft Entra Identifier**. - **SSO URL (Entry Point)**: the **Login URL**. - **X.509 Certificate**: the contents of the **Certificate (Base64)** file. StackOne SSO registration form filled with the Microsoft Entra values before registering. Select **Continue**. The connection is registered, but stays inactive until the domain is verified. ## Verify the domain Verification proves the organization owns the domain and activates SSO. Once it's verified, existing StackOne users on the domain are linked to the SSO connection, so they keep one account. On the wizard's **Verify your domain** step, copy the record's **Name** and **Value**. The **Value** has this form: ``` _stackone-sso-verification-token-{providerId}={token} ``` StackOne's Verify your domain step showing the DNS TXT record name and value. In the domain's DNS panel, add a TXT record: - **Name/Host**: the domain. Use `@` if it's the root of the DNS zone, or the subdomain label if the email domain is a subdomain. - **Value**: the full `_stackone-sso-verification-token-...` string, as its own value. Don't append it to an existing TXT value, such as an SPF record. Add the `_stackone-sso-verification-token-...` string as the record's **Value**, not its Name. It looks like a DNS host label, as `_dmarc` and `_domainkey` do, so it's easy to paste into **Name/Host** by mistake. A record on the wrong name fails verification without an error. 1. Go to **DNS > Records** and select **Add record**. 2. Set **Type** to `TXT` and **Name** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Content**. Cloudflare allows several TXT records at the same name, so add a new record rather than editing an existing one. 1. Open the hosted zone and select **Create record**. 2. Set **Record type** to `TXT`. Leave **Record name** blank for the root domain, or enter the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token in quotes. If a TXT record already exists at that name, edit it and add the token as a new line instead. 1. Open the zone and add a standard record set. 2. Set the type to `TXT`, with the DNS name set to the email domain, such as `acme.com` or `eu.acme.com`. 3. Paste the token. If a TXT record set already exists, edit it and add the token as a new item instead. 1. Open the domain's DNS records and select **Add New Record**. 2. Set **Type** to `TXT` and **Name** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Value**. 1. Open **Advanced DNS** and select **Add New Record**. 2. Choose **TXT Record**, and set **Host** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Value**. DNS changes can take up to 48 hours to propagate, though they often complete within minutes. Check what's publicly visible with [Google Admin Toolbox Dig](https://toolbox.googleapps.com/apps/dig/#TXT/). 1. Select **Verify**. Once the record is visible, the domain is verified and SSO is active. 2. Select **Finish** to close the wizard. If the check fails, wait for DNS to propagate and try again. To finish setup first, select **Verify Later**, then verify afterward from the **Trusted Domain** card on the connection's **General** tab. StackOne SSO connection card showing the domain as verified and SSO active ## Manage the connection Open the connection from [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). The **General** tab is where you maintain it after setup: - Select **Edit SAML** to update the identity provider values, either by uploading new metadata XML or by editing the **Entity ID (Issuer)**, **SSO URL (Entry Point)**, and **X.509 Certificate** directly. - Select **Edit Domain** to change the trusted domain. Changing it resets verification, so users stop being redirected until you verify it again. You can't change it while SSO is enforced. The connection's General tab, showing the SAML 2.0 Configuration values (Single sign-on URL, Audience URI, Default Relay State) and the Trusted Domain verification status. From the connection's page header: - **Settings** edits the **Connection name**. The **Provider ID** is generated at setup and can't be changed. - **Delete** removes the SSO connection. It's disabled while SSO is enforced, so turn off enforcement on the **Authentication** tab first. To require users to sign in through Microsoft Entra, see [Require SSO](/secure/identity-and-access/authentication/sso/overview#require-sso). Deleting the connection sends users on the domain back to email and password sign-in, so make sure they have another way in first. To change SAML values, use **Edit SAML** instead. Deleting it also removes SCIM Provisioning, if linked, and revokes its token. Provisioning from Microsoft Entra then fails with `401` until you link SCIM again and paste the new token into Microsoft Entra. Users already provisioned keep their access. To add, update and deactivate users automatically from Microsoft Entra, set up [Microsoft Entra SCIM Provisioning](/secure/identity-and-access/manage-team/scim/microsoft-entra) once the domain is verified. ## Troubleshooting | Symptom | Likely cause | Fix | |---------|--------------|-----| | Sign-in fails with "Unable to extract user ID or email" | The Name ID is empty because `user.mail` isn't set for that user. | Populate `user.mail`, or set the Name ID source to `user.userprincipalname` if it matches the user's email. | | `ERROR_UNMATCH_CERTIFICATE_DECLARATION_IN_METADATA` | The registered certificate doesn't match the one Entra signs with, usually after Entra rotated or renewed it. | Download a fresh **Federation Metadata XML** (or **Certificate (Base64)**) from **SAML Certificates** and update it via **Edit SAML**. Entra signing certificates expire on a schedule, roughly every three years. | | `ERR_UNMATCH_ISSUER` | The **Entity ID (Issuer)** doesn't match the issuer Entra sends. | Copy the **Microsoft Entra Identifier** and update it via **Edit SAML**. | | "Provider domain has not been verified" | Domain verification hasn't completed. | Finish [Verify the domain](#verify-the-domain). | | Verification keeps failing | The TXT record is on the wrong name, not its own value, or DNS hasn't propagated. | Use `@` for a root domain or the subdomain label otherwise, add the token as its own TXT value, and check propagation with [Dig](https://toolbox.googleapps.com/apps/dig/#TXT/). | | Users not redirected to Entra | The domain isn't verified, or the user isn't assigned in Entra. | Verify the domain, and confirm the user is under **Users and groups** on the enterprise application. | | `403 Forbidden` when opening SSO | You lack the **Organization Admin** role. | Ask an **Organization Admin** to make the change or to grant you the role. | ## Next steps See how SSO, domain verification, and SCIM Provisioning fit together. Set up the same SAML connection with Okta instead of Entra. Connect any other identity provider that supports SAML 2.0. # Generic SAML SSO Source: https://docs.stackone.com/secure/identity-and-access/authentication/sso/saml-generic Set up SAML Single Sign-On with any SAML 2.0 identity provider. SAML SSO is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Connect any SAML 2.0 identity provider (IdP) to StackOne, so users sign in with their IdP credentials. If the IdP is Okta or Microsoft Entra ID, follow the [Okta](/secure/identity-and-access/authentication/sso/okta) or [Microsoft Entra](/secure/identity-and-access/authentication/sso/microsoft-entra) guide instead. Before setting up SAML SSO, you need: - The **Organization Admin** role in StackOne. - Admin access to the IdP, to create and configure a SAML application. - The ability to add a DNS TXT record for your email domain, which proves you own it. ## Start the connection in StackOne 1. Go to [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). 2. Click **Get started**. 3. Select **Other SAML 2.0 provider**, then click **Continue**. On the **Connection details** step, fill in both fields, then click **Continue**: - **Connection name**: a name for the connection. StackOne generates the connection's unique ID from it. - **Domain**: the email domain your users sign in with. The **Configure your identity provider** step has the values you need when you create the app in your IdP. Field names vary by IdP: - **ACS URL (Single sign-on URL)**: where the IdP posts the SAML assertion. Often called Assertion Consumer Service URL or Reply URL. - **SP Entity ID (Audience)**: identifies StackOne to the IdP. Often called Audience URI, Entity ID or Identifier. - **Default RelayState**: the dashboard URL, where an IdP-initiated sign-in lands. Set it only if the IdP supports IdP-initiated sign-in. Keep this StackOne tab open. You return to the wizard to register the provider after you build the app in your IdP. The Configure your identity provider step showing the ACS URL, SP Entity ID, and Default RelayState ## Create the SAML app in your IdP 1. In the IdP's admin console, create a new SAML 2.0 application for StackOne. 2. Set the following: - **Single sign-on URL** (or Assertion Consumer Service URL): the **ACS URL** from StackOne. - **Audience URI** (or Entity ID): the **SP Entity ID** from StackOne. - **Relay State** (optional): the **Default RelayState** from StackOne. Set the following: - **Name ID format**: `urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress`. - **Name ID value**: the user's work email, not a username, UPN or object ID. Optionally, also send the email as an attribute named `email`. StackOne uses it when present, and falls back to the Name ID otherwise. Add attributes named `givenName` and `surname`, or a single `displayName`. These set the user's display name in StackOne. Adding these to an existing app only sets names for new users. To sync names for existing users, use [SCIM Provisioning](/secure/identity-and-access/manage-team/scim/overview). Enable assertion signing in the IdP. StackOne validates the signature against the certificate you register in StackOne. Register the exact certificate the IdP signs with. A mismatch makes every sign-in fail with a certificate error, even when every other value is correct. Assign the users or groups who should sign in to StackOne through this application, then save the app. Only assigned users can complete SSO. From the IdP's SAML settings, get the values StackOne needs. Download the IdP's SAML metadata XML. Copy these values for StackOne: - **Issuer (Entity ID)**: the IdP's unique identifier. - **Single Sign-On URL**: the IdP's login endpoint. - **X.509 signing certificate**: in PEM format. ## Register the provider in StackOne Switch back to the StackOne tab and continue to the **Register your SSO provider** step. Supply the three values from the IdP. 1. Click **Upload SAML metadata file**. 2. Select the metadata XML you downloaded. StackOne fills in **Entity ID (Issuer)**, **SSO URL (Entry Point)**, and **X.509 Certificate**. 3. Review the imported values before continuing. Set the following: - **Entity ID (Issuer)**: the IdP's **Issuer (Entity ID)**. - **SSO URL (Entry Point)**: the IdP's **Single Sign-On URL**. - **X.509 Certificate**: the IdP's **X.509 signing certificate**. The Register your SSO provider step with the Entity ID, SSO URL, and X.509 Certificate fields Select **Continue**. The connection is registered, but stays inactive until the domain is verified. ## Verify the domain Verification proves the organization owns the domain and activates SSO. Once it's verified, existing StackOne users on the domain are linked to the SSO connection, so they keep one account. On the wizard's **Verify your domain** step, copy the record's **Name** and **Value**. The **Value** has this form: ``` _stackone-sso-verification-token-{providerId}={token} ``` StackOne's Verify your domain step showing the DNS TXT record name and value. In the domain's DNS panel, add a TXT record: - **Name/Host**: the domain. Use `@` if it's the root of the DNS zone, or the subdomain label if the email domain is a subdomain. - **Value**: the full `_stackone-sso-verification-token-...` string, as its own value. Don't append it to an existing TXT value, such as an SPF record. Add the `_stackone-sso-verification-token-...` string as the record's **Value**, not its Name. It looks like a DNS host label, as `_dmarc` and `_domainkey` do, so it's easy to paste into **Name/Host** by mistake. A record on the wrong name fails verification without an error. 1. Go to **DNS > Records** and select **Add record**. 2. Set **Type** to `TXT` and **Name** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Content**. Cloudflare allows several TXT records at the same name, so add a new record rather than editing an existing one. 1. Open the hosted zone and select **Create record**. 2. Set **Record type** to `TXT`. Leave **Record name** blank for the root domain, or enter the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token in quotes. If a TXT record already exists at that name, edit it and add the token as a new line instead. 1. Open the zone and add a standard record set. 2. Set the type to `TXT`, with the DNS name set to the email domain, such as `acme.com` or `eu.acme.com`. 3. Paste the token. If a TXT record set already exists, edit it and add the token as a new item instead. 1. Open the domain's DNS records and select **Add New Record**. 2. Set **Type** to `TXT` and **Name** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Value**. 1. Open **Advanced DNS** and select **Add New Record**. 2. Choose **TXT Record**, and set **Host** to `@` for the root domain, or the subdomain label, such as `eu` for `eu.acme.com`. 3. Paste the token into **Value**. DNS changes can take up to 48 hours to propagate, though they often complete within minutes. Check what's publicly visible with [Google Admin Toolbox Dig](https://toolbox.googleapps.com/apps/dig/#TXT/). 1. Select **Verify**. Once the record is visible, the domain is verified and SSO is active. 2. Select **Finish** to close the wizard. If the check fails, wait for DNS to propagate and try again. To finish setup first, select **Verify Later**, then verify afterward from the **Trusted Domain** card on the connection's **General** tab. StackOne SSO connection card showing the domain as verified and SSO active ## Manage the connection Open the connection from [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). The **General** tab is where you maintain it after setup: - Select **Edit SAML** to update the identity provider values, either by uploading new metadata XML or by editing the **Entity ID (Issuer)**, **SSO URL (Entry Point)**, and **X.509 Certificate** directly. - Select **Edit Domain** to change the trusted domain. Changing it resets verification, so users stop being redirected until you verify it again. You can't change it while SSO is enforced. The connection's General tab, showing the SAML 2.0 Configuration values (Single sign-on URL, Audience URI, Default Relay State) and the Trusted Domain verification status. From the connection's page header: - **Settings** edits the **Connection name**. The **Provider ID** is generated at setup and can't be changed. - **Delete** removes the SSO connection. It's disabled while SSO is enforced, so turn off enforcement on the **Authentication** tab first. To require users to sign in through your IdP, see [Require SSO](/secure/identity-and-access/authentication/sso/overview#require-sso). Deleting the connection sends users on the domain back to email and password sign-in, so make sure they have another way in first. To change SAML values, use **Edit SAML** instead. Deleting it also removes SCIM Provisioning, if linked, and revokes its token. Provisioning from your IdP then fails with `401` until you link SCIM again and paste the new token into your IdP. Users already provisioned keep their access. To add, update and deactivate users automatically from your IdP, set up [SCIM Provisioning](/secure/identity-and-access/manage-team/scim/overview) once the domain is verified. ## Troubleshooting | Symptom | Likely cause | Fix | |---------|--------------|-----| | `403 Forbidden` when opening SSO | You lack the **Organization Admin** role. | Ask an **Organization Admin** to make the change or to grant you the role. | | `ERROR_UNMATCH_CERTIFICATE_DECLARATION_IN_METADATA` | The registered certificate doesn't match the one the IdP signs with. | Re-copy the active **X.509 signing certificate** from the IdP and update it on the connection's **General** tab via **Edit SAML**. | | `ERR_UNMATCH_ISSUER` | The **Entity ID (Issuer)** doesn't match the issuer the IdP sends. | Copy the issuer from the IdP's SAML metadata and update it via **Edit SAML**. | | Sign-in fails or signs in the wrong user | The Name ID value isn't the user's email, the format is set to email address, but the value is still a username, UPN, or object ID. | Set the Name ID value to the user's work email (see [Set the Name ID to the user's email](#create-the-saml-app-in-your-idp)). | | "Provider domain has not been verified" | Domain verification hasn't completed. | Finish [Verify the domain](#verify-the-domain). | | Domain verification keeps failing | The TXT record is on the wrong name, was appended to an existing value, or DNS hasn't propagated. | Use `@` for a root domain or the subdomain label otherwise, add the token as its own TXT value, and check propagation with [Dig](https://toolbox.googleapps.com/apps/dig/#TXT/). | | Users not redirected to the IdP | The domain isn't verified, or the user isn't assigned to the SAML application. | Verify the domain, and confirm the user is assigned in the IdP. | ## Next steps How SSO, SCIM Provisioning, and domain verification fit together. The same setup with Okta's field names and screenshots. The same setup with Microsoft Entra ID. # Passwords and MFA Source: https://docs.stackone.com/secure/identity-and-access/authentication/passwords-and-mfa Change your password, turn on multi-factor authentication, and enforce it for the organization. Users change their own password and turn on MFA from their account settings. **Organization Admins** can also enforce MFA for everyone in the organization. ## Change your password Open your [account settings](https://app.stackone.com/account/security). You can also click your name in the bottom-left corner of the dashboard, then open **Account** settings. 1. Click **Change Password**. 2. Enter your **Current Password**. 3. Enter your new password in both **New Password** and **Confirm New Password**. 4. Click **Change Password**. ## Turn on MFA for your account Open your [account settings](https://app.stackone.com/account/security). You can also click your name in the bottom-left corner of the dashboard, then open **Account** settings. Click **Enable Multi-Factor Authentication**. Scan the QR code with your authenticator app, such as Google Authenticator, Microsoft Authenticator, or 1Password. MFA setup dialog with QR code, authentication secret, and code confirmation Enter the 6-digit code from your authenticator app to confirm. ## Enforce MFA for the organization **Organization Admins** can require multi-factor authentication (MFA) for everyone in the organization, current and future users alike. 1. Go to [**Organization > Security > Authentication**](https://app.stackone.com/organization/security/authentication). 2. On the **Multi-factor Authentication** card, select **Enable MFA**. 3. Select **Confirm**. Users without MFA set it up the next time they sign in. ## Help a user who is locked out An **Organization Admin** can unlock an account locked by failed sign-ins, or reset another user's MFA. Select **Unlock User** or **Reset MFA** from the user's menu on the **Users** tab of [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team). # Manage Team Source: https://docs.stackone.com/secure/identity-and-access/manage-team/overview Bring people into the organization, and make sure they lose access when they leave. [**Organization Admins**](/secure/identity-and-access/roles-and-groups/organization-roles) manage who can access the StackOne organization. Manage everyone in the organization, from the day they join to the day they leave. Users join in one of three ways: An **Organization Admin** sends an email invite and picks the user's role. Users join when they sign in with SSO and aren't a member yet. The identity provider adds and removes users as the directory changes. ## Using multiple provisioning methods An organization can use more than one of these at once. When multiple methods are used, user management can be taken over by the identity provider (IdP): | User's current status | Email invitation | Just-in-Time Provisioning | SCIM Provisioning | | --- | --- | --- | --- | | **Already a member** | Can't be sent to an existing member. | Leaves them as they are. | Starts managing them when the IdP assigns them. | | **Invited, but hasn't accepted yet** | Adds them with the invitation's role when they accept it. | Doesn't add them. They join only by accepting the invitation. | Adds them with the role the IdP sends, not the invitation's. The invitation should be removed. | | **Neither** | Adds them when they accept it. | Adds them the first time they sign in to StackOne with SSO. | Adds them when the IdP assigns them. | ## Removing access to the organization Disabling or deleting a user ends their access to the organization, including any [AI platform](/connect/ai-platforms/overview) connections they made to it. - **Disable** keeps their roles, group memberships and seat, so enabling them again restores their access. - **Delete** removes their roles and group memberships, and frees their seat. To give them access again, invite them back. An organization's last active **Organization Admin** cannot be disabled or deleted. How to remove someone depends on how the organization adds people: | The organization uses | Remove them by | |---|---| | Invitations only | Disabling or deleting them on the **Users** tab of [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team). | | Just-in-Time Provisioning | Following the steps in [Just-in-Time Provisioning > Remove access to the organization](/secure/identity-and-access/manage-team/jit#remove-access-to-the-organization). | | SCIM Provisioning | Following the steps in [SCIM Provisioning > Deprovisioning](/secure/identity-and-access/manage-team/scim/overview#deprovisioning). | # Invite Users Source: https://docs.stackone.com/secure/identity-and-access/manage-team/invite-users Add people to the organization by email, and choose their organization and project roles. Only **Organization Admins** can invite users. In the StackOne dashboard, go to [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team). Organization > Manage Team, showing the Users tab with each user's role, and the invites tab Click **Invite User** and enter the person's email address. To invite several people at once, separate their addresses with commas. 1. Pick their organization **Role**: **Organization Admin** or **Organization Member**. See [Organization Roles](/secure/identity-and-access/roles-and-groups/organization-roles). 2. Optionally, select the **Projects** to add them to, and their **Project Role**. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles). You can also add them to projects later, from **Project Settings > Access**. Click **Confirm**. Pending invites wait on the **Invites** tab, where you can resend or remove them. # Just-in-Time Provisioning Source: https://docs.stackone.com/secure/identity-and-access/manage-team/jit Add users to the organization automatically the first time they sign in with SSO. SAML SSO is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). **Just-in-Time (JIT) Provisioning** adds users from your identity provider (IdP) to the organization the first time they sign in with SSO. There's no invitation to send and no directory to sync. ## Set up JIT Before setting up JIT, you need: - A verified SSO connection between the organization and your IdP. See [Single Sign-On](/secure/identity-and-access/authentication/sso/overview). - The **Organization Admin** role in StackOne. - (Optional) The IdP set up to send the `stackone_role` attribute with the value `admin` for anyone who should join as an **Organization Admin**. Everyone else joins as an **Organization Member**. See [Organization Roles](/secure/identity-and-access/roles-and-groups/organization-roles). The IdP's value only counts when a user first joins. After that, their role can only be changed in StackOne. 1. In the StackOne dashboard, go to [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). 2. Open the verified SSO connection. 3. Select the **Provisioning** tab. 1. On the **Provisioned access** card, select **Manage access**. 2. Pick the projects new users should join. 3. Choose a role for each one. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles). 4. Select **Save changes**. Provisioned access applies to users added by both Just-in-Time Provisioning and SCIM Provisioning. The Provisioned access panel with a project checked and its own role dropdown set to Viewer, and a note that the organization role is set separately. On the **Just-in-time provisioning** card, select **Enable JIT**. Assign the users to the StackOne application in the IdP. Each one joins the organization the first time they sign in with SSO, with the provisioned access you chose. **Provisioned access** only applies when a user first joins, so JIT doesn't give back access you removed from an existing member. ## When a user isn't added A user can sign in with SSO and still not be added to the organization if: - Their email address isn't on the connection's verified domain. The match is exact, so `@eu.acme.com` doesn't count for `acme.com`. - The organization has no seats left. - The organization's required sign-in methods don't include SSO. - They have a pending invitation. They join when they accept it instead. See [Using multiple provisioning methods](/secure/identity-and-access/manage-team/overview#using-multiple-provisioning-methods). ## Remove access to the organization To stop a user accessing the organization: 1. Go to [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team). 2. On the **Users** tab, find the user. 3. Select **Disable User**. Their membership still exists, so JIT can't create a new one when they sign in. You can also unassign them from the StackOne application in the IdP, so they can't sign in with SSO at all. **Deleting a user** in StackOne doesn't keep them out while they can still sign in through the IdP. They rejoin at their next sign-in, as if they were joining for the first time. ## Next steps Grant many users the same project or linked account access at once. Add and remove users from the directory instead of at sign-in. # SCIM Provisioning Source: https://docs.stackone.com/secure/identity-and-access/manage-team/scim/overview Add, update and deactivate users automatically from your identity provider's directory. SCIM Provisioning is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). **SCIM Provisioning** creates and deactivates StackOne members automatically from your identity provider (IdP). It can also [sync the IdP's groups](/secure/identity-and-access/manage-team/scim/groups) into StackOne, where they can grant access to projects and linked accounts. Flow diagram with three lanes from an identity provider such as Okta or Microsoft Entra into StackOne. Assign a user: they join the organization and get their role and provisioned access. Push a group: it becomes a StackOne group you assign to projects and accounts. Deactivate or remove a user: their access is suspended, and they are removed from synced groups and signed out. ## Enable SCIM Provisioning To set up SCIM Provisioning with Okta or Microsoft Entra, follow the [Okta](/secure/identity-and-access/manage-team/scim/okta) or [Microsoft Entra](/secure/identity-and-access/manage-team/scim/microsoft-entra) guide instead. Google Workspace doesn't support SCIM Provisioning. Before setting up SCIM Provisioning, you need: - A verified SSO connection between the organization and your IdP. See [Single Sign-On](/secure/identity-and-access/authentication/sso/overview). - The **Organization Admin** role in StackOne. - Admin access to the StackOne application in your IdP. - (Optional) your IdP set up to send `admin` in the SCIM `roles` field for anyone who should join as an **Organization Admin**. Everyone else joins as an **Organization Member**. See [Organization Roles](/secure/identity-and-access/roles-and-groups/organization-roles). The `roles` value only counts when a user first joins. After that, their role can only be changed in StackOne. SCIM Provisioning only adds users whose email is on the organization's verified domain. Anyone else, including everyone assigned before the domain is verified, shows as an error in your IdP's provisioning log. 1. In the StackOne dashboard, go to [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). 2. Open the verified SSO connection. 3. Select the **Provisioning** tab. 1. On the **Provisioned access** card, select **Manage access**. 2. Pick the projects new users should join. 3. Choose a role for each one. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles). 4. Select **Save changes**. Provisioned access applies to users added by both Just-in-Time Provisioning and SCIM Provisioning. The Provisioned access panel with a project checked and its own role dropdown set to Viewer, and a note that the organization role is set separately. 1. On the **Directory Sync** card, select **Link SCIM**. 2. In the **SCIM Details** section, copy the **SCIM base URL** and the **Provisioning token**. You paste both into the IdP. The Provisioning tab on an SSO connection, showing the Provisioned access, Just-in-time provisioning, and Directory Sync cards with their Manage access, Enable JIT, and Link SCIM actions. The Directory Sync panel showing the SCIM base URL and the masked provisioning token with a Regenerate action. The token is only shown once. Store it somewhere safe before you close the panel. To replace a lost or leaked token, see [Rotate the token](/secure/identity-and-access/manage-team/scim/overview#rotate-the-token). In the IdP, enable provisioning for the StackOne application, paste in the SCIM base URL and token, and assign the users who should sync. ## When a user is assigned When you assign a user to the StackOne application in the IdP: - The user is added to the organization. - The user gets the connection's **provisioned access**. It's applied again on every update from the IdP, so a project you remove from the user in StackOne comes back. - The user joins any [synced groups](/secure/identity-and-access/manage-team/scim/groups) the IdP pushes them into, and gets the access those groups grant. ## Deprovisioning Deprovisioning affects every user the IdP manages through SCIM Provisioning, including people who first joined by invitation or Just-in-Time Provisioning. Users the IdP has never assigned are left untouched. When you deactivate or remove a user in the IdP: - The user's access to the organization is suspended. - The user is removed from their synced groups. - The user is signed out on any device where they're currently working in the organization. Reactivating the user in the IdP lifts the suspension, unless an **Organization Admin** also disabled them in StackOne. SCIM Provisioning never deactivates the organization's last active **Organization Admin**. To offboard them, first make someone else an **Organization Admin**. Until then, the IdP's provisioning log shows the deactivation as an error, and it retries on each sync. **Deleting a user** in StackOne doesn't remove them while the IdP still assigns them. The next sync adds them back, so deactivate or remove them in the IdP instead. ## Manage or remove SCIM Provisioning Manage SCIM Provisioning from the **Directory Sync** card on the SSO connection's **Provisioning** tab. ### Rotate the token 1. Select **Edit SCIM**. 2. Select **Regenerate**, then **Confirm rotate**. 3. Paste the new token into the IdP. The old token stops working immediately, so SCIM Provisioning fails until the IdP has the new one. ### Change provisioned access Select **Manage access** on the **Provisioned access** card. New users get the updated access. Users SCIM Provisioning already manages get any added projects on their next update from the IdP, but keep projects you removed and their role on projects they already had. Synced groups grant access separately. When a user has a project through both, the strongest role applies. See [Which role applies](/secure/identity-and-access/roles-and-groups/overview#which-role-applies). ### Unlink SCIM Provisioning Select **Unlink**. This stops all future provisioning and revokes the token. Users synced so far keep their access, and synced groups become normal groups that keep their members and assignments. If you link again later, the SCIM base URL stays the same, so you only paste the new token into the IdP. Deleting the SSO connection unlinks SCIM Provisioning in the same way. If you delete and recreate the connection, for example to replace a certificate, link SCIM again and paste the new token into the IdP. ## Next steps Enable SCIM provisioning on an Okta SSO connection. Enable SCIM provisioning on a Microsoft Entra SSO connection. Set up the SSO connection that SCIM Provisioning builds on. Push the IdP's groups into StackOne and grant access through them. # Okta SCIM Provisioning Source: https://docs.stackone.com/secure/identity-and-access/manage-team/scim/okta Connect Okta to StackOne with SCIM, assign users, and push Okta groups. SCIM Provisioning is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Sync users from Okta, your identity provider (IdP), into StackOne with SCIM. Once linked, assigning a person to the StackOne app in Okta adds them to the organization, and unassigning or deactivating them removes their access. For what happens to users once SCIM Provisioning is running, see the [SCIM Provisioning overview](/secure/identity-and-access/manage-team/scim/overview). Before setting up SCIM Provisioning, you need: - A verified SSO connection between the organization and Okta. See [Single Sign-On](/secure/identity-and-access/authentication/sso/overview). - The **Organization Admin** role in StackOne. - Admin access to the StackOne application in Okta. - (Optional) Okta set up to send `admin` in the SCIM `roles` field for anyone who should join as an **Organization Admin**. Everyone else joins as an **Organization Member**. See [Organization Roles](/secure/identity-and-access/roles-and-groups/organization-roles). The `roles` value only counts when a user first joins. After that, their role can only be changed in StackOne. SCIM Provisioning only adds users whose email is on the organization's verified domain. Anyone else, including everyone assigned before the domain is verified, shows as an error in Okta's provisioning log. ## Link SCIM in StackOne 1. In the StackOne dashboard, go to [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). 2. Open the verified SSO connection. 3. Select the **Provisioning** tab. 1. On the **Provisioned access** card, select **Manage access**. 2. Pick the projects new users should join. 3. Choose a role for each one. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles). 4. Select **Save changes**. Provisioned access applies to users added by both Just-in-Time Provisioning and SCIM Provisioning. The Provisioned access panel with a project checked and its own role dropdown set to Viewer, and a note that the organization role is set separately. 1. On the **Directory Sync** card, select **Link SCIM**. 2. In the **SCIM Details** section, copy the **SCIM base URL** and the **Provisioning token**. You paste both into the IdP. The Provisioning tab on an SSO connection, showing the Provisioned access, Just-in-time provisioning, and Directory Sync cards with their Manage access, Enable JIT, and Link SCIM actions. The Directory Sync panel showing the SCIM base URL and the masked provisioning token with a Regenerate action. The token is only shown once. Store it somewhere safe before you close the panel. To replace a lost or leaked token, see [Rotate the token](/secure/identity-and-access/manage-team/scim/overview#rotate-the-token). ## Configure provisioning in Okta 1. In the Okta admin console, go to **Applications > Applications** and open the app you created for StackOne SSO. 2. Go to the **Provisioning** tab. 3. Click **Configure API Integration**. 4. Select **Enable API integration**. 1. Set the following: - **SCIM connector base URL**: the **SCIM base URL** from StackOne. - **Unique identifier field for users**: `userName`. - **Supported provisioning actions**: `Push New Users` and `Push Profile Updates`. - **Authentication Mode**: `HTTP Header`. - **Authorization**: the **Provisioning token** from StackOne. 2. Click **Test Connector Configuration** to confirm Okta can reach StackOne. 3. Click **Save**. Okta, Provisioning > Integration, showing the SCIM Connection with the connector base URL, userName as the unique identifier, Push New Users and Push Profile Updates enabled, and HTTP Header bearer-token authentication. 1. Under **Provisioning > To App**, click **Edit**. 2. Enable **Create Users**, **Update User Attributes**, and **Deactivate Users**. 3. Click **Save**. These let Okta create members in StackOne, keep their profiles in sync, and remove access when you unassign or deactivate them. Okta, Provisioning > To App, with Create Users, Update User Attributes, and Deactivate Users all enabled. ## Assign members in Okta 1. Open the **Assignments** tab of the StackOne app. 2. Assign the people you want in StackOne. You can assign individuals or Okta groups. Either way, Okta adds each assigned person to the organization, with their organization role and provisioned access. Assigning an Okta group provisions its members as individual users. To bring the group itself into StackOne, with its membership kept in step, push it as well. See [Push groups](#push-groups). Return to the **Directory Sync** card in StackOne. The **Synced members** and **Last synced** values update as Okta pushes users, and new members appear in the projects you selected. ## Push groups Okta's **Group Push** creates the group in StackOne as a synced group and keeps its members in step. Only members who are assigned to the StackOne app, and so already provisioned, are pushed. If StackOne already has a group with the same name, an empty one becomes the synced group and keeps its access. If the group has members, it's left untouched, and StackOne creates a second, synced group with the same name instead. To set up a group's access before anyone is pushed into it, see [Prepare the access before you push](/secure/identity-and-access/manage-team/scim/groups#prepare-the-access-before-you-push). 1. On the app's **Provisioning** tab, under **Integration**, click **Edit**. 2. Make sure **Push Groups** is enabled alongside **Push New Users** and **Push Profile Updates**. 3. Click **Save**. 1. Open the app's **Push Groups** tab. 2. Click **Push Groups**, and choose **Find groups by name**. To push several groups that share a naming pattern, choose **Find groups by rule** instead. 3. Select the Okta group, and leave **Push group memberships immediately** on. 4. Click **Save**. Okta creates the group in StackOne. 1. Go to [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team) and open the **Groups** tab. The group is listed with a **Synced** tag and its pushed members. 2. Assign it to projects from its **Projects** tab. Use different Okta groups for assigning the app and for Group Push. For example, assign the app to ***StackOne Users*** and push ***Finance***. Okta doesn't support using one group for both, and the group's members in StackOne can end up different from Okta's. See Okta's [App assignments and Group Push](https://help.okta.com/en-us/content/topics/users-groups-profiles/app-assignments-group-push.htm). After a group is pushed: - **To rename it**, rename it in Okta. - **To stop pushing it**: 1. On the **Push Groups** tab, choose **Unlink pushed group** on the group's row. 2. Choose whether to also delete the group in StackOne. A group you keep stays a synced group in StackOne until you unlink SCIM Provisioning. ## Next steps How SCIM provisioning works across identity providers. Provision members from Microsoft Entra ID instead. Push the identity provider's groups into StackOne and grant access through them. # Microsoft Entra SCIM Provisioning Source: https://docs.stackone.com/secure/identity-and-access/manage-team/scim/microsoft-entra Connect Microsoft Entra ID to StackOne with SCIM, assign users, and provision Entra groups. SCIM Provisioning is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Sync users from Microsoft Entra ID, your identity provider (IdP), into StackOne with SCIM. Once linked, assigning a person to the StackOne application in Entra adds them to the organization, and unassigning or disabling them removes their access, except for the organization's last active **Organization Admin**. For what happens to users once SCIM Provisioning is running, see the [SCIM Provisioning overview](/secure/identity-and-access/manage-team/scim/overview). Before setting up SCIM Provisioning, you need: - A verified SSO connection between the organization and Microsoft Entra. See [Single Sign-On](/secure/identity-and-access/authentication/sso/overview). - The **Organization Admin** role in StackOne. - Admin access to the StackOne application in Microsoft Entra. - (Optional) Microsoft Entra set up to send `admin` in the SCIM `roles` field for anyone who should join as an **Organization Admin**. Everyone else joins as an **Organization Member**. See [Organization Roles](/secure/identity-and-access/roles-and-groups/organization-roles). The `roles` value only counts when a user first joins. After that, their role can only be changed in StackOne. SCIM Provisioning only adds users whose email is on the organization's verified domain. Anyone else, including everyone assigned before the domain is verified, shows as an error in Microsoft Entra's provisioning log. In Microsoft Entra, admin access means permission to manage the enterprise application, such as the **Application Administrator** role. ## Link SCIM in StackOne 1. In the StackOne dashboard, go to [**Organization > Security > SSO**](https://app.stackone.com/organization/security/sso). 2. Open the verified SSO connection. 3. Select the **Provisioning** tab. 1. On the **Provisioned access** card, select **Manage access**. 2. Pick the projects new users should join. 3. Choose a role for each one. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles). 4. Select **Save changes**. Provisioned access applies to users added by both Just-in-Time Provisioning and SCIM Provisioning. The Provisioned access panel with a project checked and its own role dropdown set to Viewer, and a note that the organization role is set separately. 1. On the **Directory Sync** card, select **Link SCIM**. 2. In the **SCIM Details** section, copy the **SCIM base URL** and the **Provisioning token**. You paste both into the IdP. The Provisioning tab on an SSO connection, showing the Provisioned access, Just-in-time provisioning, and Directory Sync cards with their Manage access, Enable JIT, and Link SCIM actions. The Directory Sync panel showing the SCIM base URL and the masked provisioning token with a Regenerate action. The token is only shown once. Store it somewhere safe before you close the panel. To replace a lost or leaked token, see [Rotate the token](/secure/identity-and-access/manage-team/scim/overview#rotate-the-token). ## Configure provisioning in Microsoft Entra Point the enterprise application at StackOne's SCIM endpoint. Use the same application you set up for SSO. 1. In the **Microsoft Entra admin center**, go to **Identity > Applications > Enterprise applications** and open the application you created for StackOne SSO. 2. Select **Provisioning**. 3. Select **Connect your application**. Under **Admin credentials**, set the following: - **Select authentication method**: `Bearer authentication`. - **Tenant URL**: the **SCIM base URL** from StackOne. - **Secret token**: the **Provisioning token** from StackOne. Microsoft Entra, Provisioning > Admin credentials, with Bearer authentication selected, the Tenant URL (SCIM base URL) and Secret token (provisioning token) entered, and the Test connection button. 1. Click **Test connection**. 2. When the test passes, select **Create** to save the configuration. Select **Start provisioning** to begin the first cycle. Microsoft Entra provisions the assigned users, then re-syncs roughly every 40 minutes. Microsoft Entra, the provisioning overview after connecting, with Start provisioning in the toolbar and the current cycle status. ## Assign users and groups Microsoft Entra provisions only the users you assign to the application. Assign the people who should have StackOne access. 1. In the same enterprise application, open **Users and groups**. 2. Add the users or groups to sync, such as the **Finance** group. On its next cycle, Microsoft Entra adds each assigned user to the organization, with their organization role and provisioned access. Unassign a user from the application, or disable their Microsoft Entra account, and the next cycle deactivates the matching StackOne member, removing their access automatically. ## Provision groups Microsoft Entra can provision the groups you assign to the application as well as their members. Each becomes a synced group in StackOne that keeps its membership in step with Entra. If StackOne already has a group with the same name, an empty one becomes the synced group and keeps its access. If the group has members, it's left untouched, and StackOne creates a second, synced group with the same name instead. To set up a group's access before anyone is provisioned into it, see [Prepare the access before you push](/secure/identity-and-access/manage-team/scim/groups#prepare-the-access-before-you-push). 1. In the application's **Provisioning** settings, open **Mappings**. 2. Make sure **Provision Microsoft Entra ID Groups** is `Enabled`. Under **Users and groups**, assign the group, such as **Finance**. On the next cycle, Entra provisions the group's direct members as StackOne members and the group itself as a synced group. Nested groups aren't expanded, so assign the groups that directly contain the people you want. 1. Go to [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team) and open the **Groups** tab. The group is listed with a **Synced** tag. 2. Assign it to projects from its **Projects** tab. After a group is provisioned: - **To rename it or change its members**, make the change in Entra. The synced group follows on the next cycle. - **To stop provisioning it**, unassign the group from the application. On the next cycle, Entra deprovisions the members who are no longer assigned to the application through any other assignment. ## Next steps How SCIM provisioning works and how it attaches to the SSO connection. Set up SCIM provisioning with Okta instead of Microsoft Entra. Push the identity provider's groups into StackOne and grant access through them. # SCIM Groups Source: https://docs.stackone.com/secure/identity-and-access/manage-team/scim/groups Push groups from the identity provider into StackOne over SCIM and grant access through them. SCIM Provisioning is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). SCIM Provisioning can push the identity provider's groups into StackOne as **synced groups**. The identity provider (IdP) owns each synced group's name and members, and you grant access with it in StackOne like any other group. Add someone to the group in the IdP and they gain the projects the group is assigned to. Remove them and that access goes with them. ## How synced groups work When the IdP pushes a group, StackOne creates a group of the same name on the **Groups** tab of **Organization > Manage Team**, marked with a **Synced** tag. From then on: - **The IdP manages the name and the members.** Rename the group there and it is renamed here. Add or remove members there and the membership follows. In StackOne the group is marked **Managed by the identity provider**, and renaming it, deleting it, and editing its members are disabled. - **You manage its access.** Assign the group to projects and accounts and choose a role, the same way as for any other group. See [Assign Group Access](/secure/identity-and-access/roles-and-groups/groups). - **Its members are people the directory has provisioned.** A synced group can only contain members that SCIM Provisioning created or linked through the same connection. Someone who is in the directory group but not assigned to the StackOne application isn't a StackOne member, so they don't appear in the group until they are. Synced groups never change anyone's organization role. See [Organization Roles](/secure/identity-and-access/roles-and-groups/organization-roles). ## Prerequisites - **SCIM Provisioning linked** on the SSO connection, with users provisioning. See [Enable SCIM Provisioning](/secure/identity-and-access/manage-team/scim/overview#enable-scim-provisioning). - [Groups](/secure/identity-and-access/roles-and-groups/groups) available in the organization. - Organization **Admin**, or **Admin** on the project, to assign a group to a project. ## Prepare the access before you push A pushed group takes over an existing StackOne group of the same name when that group has no members. Names match ignoring case and surrounding spaces. This lets you set up the access before anyone arrives: 1. On the **Groups** tab, click **Create group**. 2. Give it the exact name of the directory group, for example `Finance`. 3. Leave it empty. 1. Open the group's **Projects** tab. 2. Add the projects it should grant, each with a role. See [Manage Groups](/secure/identity-and-access/roles-and-groups/groups#assign-a-group-to-a-project). When the IdP pushes `Finance`, StackOne turns the empty group into the synced one and keeps its assignments. Its members gain that access as they are pushed. A StackOne group that already has members is never taken over. If the IdP pushes a group with the same name, StackOne creates a second group, tagged **Synced**, and leaves yours untouched. To end up with one `Finance` group, remove the members from yours before the push, or push the directory group under a different name. ## Push groups from the identity provider Push groups from the app's **Push Groups** tab. Provision the groups assigned to the application. ## What changes when | In the identity provider | In StackOne | |---------------------------|-------------| | A group is pushed for the first time. | A synced group appears, or an empty group of the same name becomes the synced group and keeps its access. | | A member is added to or removed from the group. | The membership updates, and the access the group grants follows. | | The group is renamed. | The group is renamed. Its assignments stay. | | The group is deleted, or its push is unlinked and the group deleted with it. | The group is deleted in StackOne. Its members lose the access it granted. | | A member is deactivated or unassigned from the application. | They leave every synced group, along with the rest of their access. If the IdP reactivates them, their memberships return. | If you stop pushing a group but keep it in StackOne, it stays a synced group and can't be edited until you unlink SCIM Provisioning. Delete it from the IdP's push instead, or unlink SCIM Provisioning to get every synced group back. ## When SCIM Provisioning is unlinked or replaced Unlinking SCIM Provisioning, or deleting the SSO connection it's on, hands every synced group back to you. Each becomes a normal group that keeps its members and its project and account assignments, and you can edit it again. Nobody loses access. If you link SCIM Provisioning again, on the same connection or a new one, a pushed group with the same name takes that group back as a synced group, members and assignments intact, rather than creating a second copy. ## Limits - A group push can contain at most **1,000** direct members. StackOne rejects larger pushes, and the IdP reports the error. - Synced group names must be unique within the SCIM Provisioning connection. A push that reuses the name of another synced group is rejected. A group you created by hand can share the name, which is how the takeover above works. - Members must already be provisioned. A push that lists someone SCIM Provisioning doesn't know is rejected until that person is assigned to the StackOne application and provisioned. ## Next steps Assign synced groups to projects and accounts, and manage groups created by hand. How provisioning works and how it attaches to the SSO connection. # Roles and Groups Source: https://docs.stackone.com/secure/identity-and-access/roles-and-groups/overview Give each user the access they need, from the whole organization down to a single linked account. Access follows the structure of the [organization](/gateway/concepts/organizations-and-projects). The organization holds projects, and each project holds its [connector profiles](/gateway/concepts/connector-profiles) and [linked accounts](/gateway/concepts/linked-accounts). Start from what the person needs: Let someone run the organization, or limit them to the projects they're added to. Hand someone a project, let a team connect their own accounts, or give read-only access. Limit who can link accounts through a sensitive connector profile. Let several people work through one linked account. Give the same roles to many people at once, and change them in one place. ## Give someone access to a provider A user can reach a provider by linking their own account through a connector profile, or by using an account someone else has already linked: | | [Connector Profile Access](/secure/identity-and-access/roles-and-groups/connector-profile-access) | [Shared Accounts](/secure/identity-and-access/roles-and-groups/shared-accounts) | |---|---|---| | Question it answers | Who may connect? | Who may use this connection? | | Whose credentials are used | Each user's own | The account owner's | | What gets created | A new linked account per user | Nothing new, just access to an existing one | | Typical reason | The configuration is privileged or sensitive | One login should serve several people | Use neither if: Everyone in the company books meetings from their own calendar. 1. Leave the calendar connector profile **Shared**. 2. Give each person **Project Member** on the project, as described in [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles). 3. Each person links their own account. Other Project Members can't use it unless it's shared with them. Use [Connector Profile Access](/secure/identity-and-access/roles-and-groups/connector-profile-access) if: A sales team of account executives, with two sales managers who also fix records in bulk. 1. Create two CRM connector profiles: one with admin scopes, and one with read-only scopes. 2. Restrict the admin-scoped profile, and leave the read-only one **Shared**. 3. Grant the sales managers **Connector Profile Member** on the admin-scoped profile. 4. Each manager links their own CRM account through the admin-scoped profile. 5. Everyone else links through the read-only profile. An HR team that handles payroll. 1. Restrict the HR connector profile that reaches payroll data. 2. Grant the HR team's group **Connector Profile Member** on it. 3. Only the HR team can link accounts through it. Use [Shared Accounts](/secure/identity-and-access/roles-and-groups/shared-accounts) if: A support lead and a team of agents who all answer customers from one shared inbox. 1. The support lead links the mailbox once. 2. They grant each agent **Account Member** on it. 3. Agents send replies through the mailbox without needing its password. A team of analysts sharing the company's single licensed seat on a reporting tool. 1. The person who links the reporting tool's single seat becomes its **Account Admin**. 2. They grant the analysts **Account Member** on it. 3. Everyone runs reports through that one seat. Use both if: The head of talent holds the only admin login for the recruiting system. Two recruiters need to use it, without connecting their own. 1. Restrict the recruiting system's connector profile to the head of talent, as **Connector Profile Member**. 2. The head of talent links the admin login through it. 3. They grant the two recruiters **Account Member** on that linked account. ## Which role applies A user's effective role on a resource is the **strongest** role they hold there. ### Roles from groups When a user holds one role directly and another through a group, the stronger one applies. For example: | Direct role | Group's role | Effective role | |-------------|--------------|----------------| | Project Viewer | Project Admin | **Project Admin** | | Project Member | Project Viewer | **Project Member** | To see each member's effective role on a project, open **Project Settings > Access**. ### Roles inherited by accounts An account also inherits access from the organization and from its parent project. Users with the following roles can access an account without being in its **Users** list: | Their standing | Inherited account access | |------|------| | **Organization Admin** | **Account Admin** on every account in the organization | | **Project Admin**, directly or through a group | **Account Admin** on every account under that project | | **Project Viewer**, directly or through a group | View every linked account under that project, but not run actions with them | A **Project Member** inherits nothing. They see only the accounts they linked and any they've been granted access to. ## Explicit account access By default, Organization Admins and Project Admins are **Account Admin** on every account they can reach, so they can run actions with anyone's linked account. **Explicit account access** removes that. With it enabled, admins can view every account, but need a grant to do more: | To | They need | |----|-----------| | Run actions on an account | **Account Member** | | Reconnect, edit, delete, or manage who has access | **Account Admin** | Explicit account access isn't a setting in the dashboard. Contact StackOne to enable it for the organization. # Organization Roles Source: https://docs.stackone.com/secure/identity-and-access/roles-and-groups/organization-roles Decide who runs the organization, and who only reaches the projects they're added to. Every user in the [organization](/gateway/concepts/organizations-and-projects#organization) is either an **Organization Admin** or an **Organization Member**: | Role | Access | |------|--------| | **Organization Admin** | Manage and view everything in the organization: members, security settings, and every project with its connector profiles and linked accounts. | | **Organization Member** | Only the projects they're granted access to, directly or through a group. **Organization > Manage Team** is hidden from them. | **Organization Admins** can't link accounts through a [restricted connector profile](/secure/identity-and-access/roles-and-groups/connector-profile-access) without a grant. If [explicit account access](/secure/identity-and-access/roles-and-groups/overview#explicit-account-access) is enabled, they can only view other people's accounts until granted a role on them. Organization roles shown for two users. User A, an Organization Admin, manages members and security settings and everything in Project 1 and Project 2. User B, an Organization Member who is a Project Member on Project 1, has no access to members and security settings or to Project 2. In Project 1, User B can link accounts through connector profiles and manages the account they linked, but has no access to the account User D linked. An **Organization Admin** can change a user's role at any time on the **Users** tab of [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team). ## Related Give people access to a project, from running it to only viewing it. Invite users and change their roles. # Project Roles Source: https://docs.stackone.com/secure/identity-and-access/roles-and-groups/project-roles Hand someone a project to run, let a team connect their own accounts, or give read-only access. Project-level RBAC is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Apart from **Organization Admins**, a user can only reach a [project](/gateway/concepts/organizations-and-projects#projects) once they're given a role on it: | Role | Access | |------|--------| | **Project Admin** | Manage everything in the project: every linked account, API keys, webhooks, and who has access. | | **Project Member** | Link their own accounts, and use and manage them. | | **Project Viewer** | See how everything in the project is set up, without changing anything. | **Organization Admins** act as **Project Admin** on every project, without being added to it. Add people to a project and choose their role in **Project Settings > Access**, or give a whole group a role with [Assign a group to a project](/secure/identity-and-access/roles-and-groups/groups#assign-a-group-to-a-project). Project roles shown for three users on Project 1. User A, the Project Admin, manages connector profiles and every linked account. User B, a Project Member, can link accounts through connector profiles, manages the account they linked, and has no access to the account User D linked. User C, a Project Viewer, can view connector profiles and every linked account. None of them can reach members and security settings or Project 2. ## What each role can do | Resource | Project Admin | Project Member | Project Viewer | |----------|---------------|--------|--------| | [Linked accounts](/gateway/concepts/linked-accounts) | Link, edit, re-authenticate, suspend, delete, and run requests against any account | Link their own accounts, then edit, delete, and run requests against those | View status and details | | [Connector profiles](/gateway/concepts/connector-profiles) | Create, configure, scope actions and events, and delete | Create their own, which they then manage, and link accounts through shared ones | View authentication type and enabled actions of shared profiles | | [MCP connectors](/connect/managing-connectors/adding-mcp-connectors) | Add, and enable ones a Project Member added | Add one by linking their account to it. The connector and the account stay disabled until a Project Admin enables them | View | | [Request logs](/connect/troubleshooting) | View | View for their own accounts and accounts shared with them | View | | [API keys](/embed/api-keys) | Create, scope, and revoke | No access | No access | | [Webhooks](/connect/webhooks) | Create, route events, and delete | No access | No access | | Project settings | Manage all settings | No access | No access | If [explicit account access](/secure/identity-and-access/roles-and-groups/overview#explicit-account-access) is enabled, a **Project Admin** can only view other people's accounts until granted a role on them. ## Related Which accounts a Project Member can hand to an AI platform. Limit who can link accounts through a sensitive connector profile. Let several people work through one linked account. # Connector Profile Access Source: https://docs.stackone.com/secure/identity-and-access/roles-and-groups/connector-profile-access Control sensitive connector profiles by restricting who can link accounts through them. Connector Profile Access is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). When someone links an account, they only see the [connector profiles](/gateway/concepts/connector-profiles) they're allowed to link through. Each profile is either **Shared** or **Restricted**: | Access | Who can link accounts through the profile | |--------|-------------------------------------------| | **Shared** | Every **Project Admin** and **Project Member** in the [project](/gateway/concepts/organizations-and-projects), and every **Organization Admin**. | | **Restricted** | Only the users and [groups](/secure/identity-and-access/roles-and-groups/groups) granted access on the profile. | Project Admins can still view, edit and delete a restricted profile. ## When to restrict a connector profile Restrict a profile when its configuration is sensitive and only some people should connect through it. Each of them still links their own account. A user can reach a provider by linking their own account through a connector profile, or by using an account someone else has already linked: | | [Connector Profile Access](/secure/identity-and-access/roles-and-groups/connector-profile-access) | [Shared Accounts](/secure/identity-and-access/roles-and-groups/shared-accounts) | |---|---|---| | Question it answers | Who may connect? | Who may use this connection? | | Whose credentials are used | Each user's own | The account owner's | | What gets created | A new linked account per user | Nothing new, just access to an existing one | | Typical reason | The configuration is privileged or sensitive | One login should serve several people | Example cases: A sales team of account executives, with two sales managers who also fix records in bulk. 1. Create two CRM connector profiles: one with admin scopes, and one with read-only scopes. 2. Restrict the admin-scoped profile, and leave the read-only one **Shared**. 3. Grant the sales managers **Connector Profile Member** on the admin-scoped profile. 4. Each manager links their own CRM account through the admin-scoped profile. 5. Everyone else links through the read-only profile. An HR team that handles payroll. 1. Restrict the HR connector profile that reaches payroll data. 2. Grant the HR team's group **Connector Profile Member** on it. 3. Only the HR team can link accounts through it. ## Access to a restricted connector profile A grant gives a user or group one of two roles, **Connector Profile Admin** or **Connector Profile Member**. On a restricted connector profile: | Capability | Project or Organization Admin, no grant | Project Member or Viewer, no grant | Connector Profile Member | Connector Profile Admin | |---|:---:|:---:|:---:|:---:| | **View the profile and its configuration** | Yes | Only if an account they can access was linked through it | Yes | Yes | | **Link accounts through it** | No | No | Yes | Yes | | **Edit its configuration** | Yes | No | No | Yes | | **Delete it** | Yes | No | No | Yes | | **Manage its access** | No | No | No | Yes | | **Enable or disable it** | Yes | No | No | No | Connector profile access shown for three users in Project 1. User A is a Project Admin, User B a Project Member granted Connector Profile Member on the restricted profile, and User C a Project Member with no grant. On the shared profile, User A manages it and Users B and C can link accounts through it. On the restricted profile, User A can edit it but not link accounts through it, User B can link accounts through it, and User C has no access. ## Restrict a connector profile Restricting a shared profile needs **Project Admin** or **Organization Admin**. Once it's restricted, only a **Connector Profile Admin** can change its access. 1. In [**Connectors**](https://app.stackone.com/connectors), open the connector and select the profile's card. 2. Select its **Access** tab. Under **Who can use this profile**, change the selector from **Shared** to **Restricted**. You become its **Connector Profile Admin** when you save, so you can't lock yourself out. Accounts already linked through the profile stay linked, and can still be re-authenticated through it without a grant. 1. On the **Users** view, use **Add users** to pick each person. 2. On the **Groups** view, use **Add groups** to pick each group. 3. Set each row's role to **Admin** (Connector Profile Admin) or **Member** (Connector Profile Member). **Revoke** removes a row. Click **Save Access** in the bar at the bottom of the page. **Cancel** discards the changes. A connector profile's Access tab set to Restricted, explaining that only the listed users and groups can link new accounts while already-linked accounts stay connected, above a user roster with Member and Admin roles and Revoke buttons A group's grant covers everyone in it, and follows the group as people join or leave. See [Groups](/secure/identity-and-access/roles-and-groups/groups). To change access later, a **Connector Profile Admin** edits the same **Access** tab and saves. A restricted profile must keep at least one **Connector Profile Admin**, so hand the role to someone else in the same save, or switch the profile back to **Shared**. ## The default for new connector profiles Each **project** has a **Default Access** setting that decides whether connector profiles created from then on start **Shared** or **Restricted**. Only an **Organization Admin** can change the default: 1. Go to [**Project Settings > Connector Profiles**](https://app.stackone.com/settings/connector-profiles). 2. Under **Default Access**, choose **Shared** or **Restricted**. 3. Click **Save**. ## Related Choose which of a profile's actions and events are exposed. Grant many users the same access at once with reusable groups. Connect the provider accounts your agents act on. Add people to the organization, and remove their access when they leave. # Shared Accounts Source: https://docs.stackone.com/secure/identity-and-access/roles-and-groups/shared-accounts Let several people work through one linked account instead of each linking their own. Account sharing is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Share an account when several people should work through one login, rather than each linking their own. Everyone acts through the same login, without needing its credentials. A user can reach a provider by linking their own account through a connector profile, or by using an account someone else has already linked: | | [Connector Profile Access](/secure/identity-and-access/roles-and-groups/connector-profile-access) | [Shared Accounts](/secure/identity-and-access/roles-and-groups/shared-accounts) | |---|---|---| | Question it answers | Who may connect? | Who may use this connection? | | Whose credentials are used | Each user's own | The account owner's | | What gets created | A new linked account per user | Nothing new, just access to an existing one | | Typical reason | The configuration is privileged or sensitive | One login should serve several people | Example cases: A support lead and a team of agents who all answer customers from one shared inbox. 1. The support lead links the mailbox once. 2. They grant each agent **Account Member** on it. 3. Agents send replies through the mailbox without needing its password. A team of analysts sharing the company's single licensed seat on a reporting tool. 1. The person who links the reporting tool's single seat becomes its **Account Admin**. 2. They grant the analysts **Account Member** on it. 3. Everyone runs reports through that one seat. The head of talent holds the only admin login for the recruiting system. Two recruiters need to use it, without connecting their own. 1. Restrict the recruiting system's connector profile to the head of talent, as **Connector Profile Member**. 2. The head of talent links the admin login through it. 3. They grant the two recruiters **Account Member** on that linked account. To share an account another user linked, grant a role on that [linked account](/gateway/concepts/linked-accounts): | Role | Access | |------|--------| | **Account Admin** | Run actions, edit, delete, re-authenticate, and manage who else has access. | | **Account Member** | Run actions only. | Account roles shown for two Project Members of Project 1, granted roles on the account User C linked. User A, the Account Admin, manages it. User B, the Account Member, uses it. Both can link accounts through the project's connector profiles, and neither has access to the account User D linked, members and security settings, or Project 2. ## Share an account Before sharing an account: - You need **Account Admin** on it. - The person must already be in the account's project, or be an **Organization Admin**. 1. Go to [**Accounts**](https://app.stackone.com/accounts) and open the account. 2. Select its **Access** tab. 3. Click **Add Users**, select the people, and choose **Account Admin** or **Account Member**. To share it with a whole group, see [Assign a group to an account](/secure/identity-and-access/roles-and-groups/groups#assign-a-group-to-an-account). ## Related Control who can connect through a connector profile in the first place. How a shared account's roles combine with project roles and groups. # Groups Source: https://docs.stackone.com/secure/identity-and-access/roles-and-groups/groups Give the same roles to many people at once, and change them in one place. A group with roles applied gives the same access to people who do the same job, such as a team or department. People who join or leave the group gain or lose that access automatically. Groups can be managed either: - [**Manual groups**](#manual-groups) (see below). - **Synced from the identity provider**, through [SCIM Groups](/secure/identity-and-access/manage-team/scim/groups). ## Manual groups These are the groups created in StackOne. Groups from the identity provider are managed there instead. ### Create a group Only **Organization Admins** can create groups, manage their members, and delete them. Go to [**Organization > Manage Team**](https://app.stackone.com/organization/manage_team) and select the **Groups** tab. The Groups tab in Manage Team listing each group with its current user count. 1. Click **Create group** to open the panel. 2. Enter a **Name**, for example a department, team or function. You can rename the group later with **Edit Details**. 3. Optionally, add **Users** from the organization. You can add more later. 4. Click **Create group** to finish. The Create group side panel with a required Name field and an optional Users selector. ### Manage group membership Open the group from the **Groups** tab. A group's Users tab listing its users, each with a Remove action, and an Add users button. - To add people, click **Add users**, select them, and confirm. - To remove someone, click **Remove** on their row and confirm. They lose any access the group gave them. ### Delete a group 1. Open the group from the **Groups** tab and click **Delete**. 2. Type the group's name, then click **Delete** to confirm. This can't be undone, and the group's members lose any access it gave them. ## Assign a group to a project Assigning a group to a project needs **Organization Admin** or **Project Admin**. Start from the project to add several groups to it at once, or from the group to add it to several projects: 1. Go to [**Project Settings > Access**](https://app.stackone.com/settings/members). 2. Switch the view from **Users** to **Groups**. Project Settings > Access with the Users / Groups switch set to Groups, showing each assigned group with its role and a Revoke action. 1. Click **Add Groups**. 2. Select one or more groups. 3. Choose a **Role**. It defaults to **Project Member**. See [Project Roles](/secure/identity-and-access/roles-and-groups/project-roles) for what each role allows. The Add Groups side panel on a project's Access view, with a Groups selector and a Role dropdown set to Project Member. Confirm the selection to add the groups. Every member of each selected group gains the chosen role on the project. 1. Open the group and select its **Projects** tab. 2. Click **Add project**, then select a **Project** and a **Role**. The role defaults to **Project Member**. 3. Click **Add project** to confirm. ## Assign a group to an account Before assigning a group to an account: - You need **Account Admin** on that account. - The group must already be assigned to the account's project. See [Assign a group to a project](#assign-a-group-to-a-project). Organization Admins and Project Admins are **Account Admin** on every account by default, unless [explicit account access](/secure/identity-and-access/roles-and-groups/overview#explicit-account-access) is enabled. 1. Go to [**Accounts**](https://app.stackone.com/accounts) and open the account. 2. Select its **Access** tab. 3. Switch the view to **Groups**. 1. Click **Add Groups**. 2. Select one or more groups. 3. Choose **Account Admin** or **Account Member**. It defaults to **Account Member**. See [Shared Accounts](/secure/identity-and-access/roles-and-groups/shared-accounts) for what each role allows. Confirm the selection to add the groups. Every member of each selected group gains the chosen role on the account. ## Change or remove a group's access Open the **Groups** view on the project or account, then: - To change the group's role, pick a new role on its row. - To remove the group's access, click **Revoke** on its row and confirm. Access a group gets through the project isn't listed on the account. Change or revoke it on the project instead. Revoking a group from a project also revokes it from every account in that project. To stop you locking yourself out, you can't revoke a group that is your only access to a project. **Organization Admins** can, because they always have access to every project. # IP Restrictions Source: https://docs.stackone.com/secure/ip-restrictions Restrict a project's API access to specific IP addresses, ranges, or CIDR blocks. IP allow-listing is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Restrict API access to specific IP addresses under **Project Settings → IP Restrictions**. Entries can take three formats: This setting controls which source IPs can call your project's StackOne API. To allow StackOne to reach a provider API or webhook endpoint behind a firewall, use [StackOne's outbound IP addresses](/gateway/concepts/connector-profiles#connection-issues-behind-a-firewall). | Format | Example | |--------|---------| | Single IP | `192.168.1.100` | | Range | `192.168.1.100-192.168.1.150` | | CIDR | `192.168.1.0/24` | If your network uses a NAT gateway, allow the gateway's external IP to permit all internal traffic. With no allowlist configured, all IPs are allowed. Once you add entries, only those IPs can access your project's API. # Observability Source: https://docs.stackone.com/secure/observability Track activity, redact personal data, and control how long request data is kept. StackOne records activity at two levels: security logs at the organization level and request logs at the project level. Together they cover who signed in and what calls your project made. ## What's logged | Log | Level | Covers | |-----|-------|--------| | Security logs | Organization | Every login attempt, success or failure. | | Request logs | Project | API and webhook requests, with status, payload detail, and optional PII redaction. See [Request Logs](/connect/troubleshooting). | ## Security logs Security logs are a record of every login attempt, success or failure, for monitoring and audit. Open them under [**Organization > Security > Logs**](https://app.stackone.com/organization/security/logs). Security Logs page listing login attempts with their outcomes ## Advanced Logs Advanced Logs stores the request and response bodies of your project's calls, so you can debug a failed request step by step. See [Request Logs](/features/observability/request-log-debugging#advanced-logs-request-and-response-bodies) for how to read them. Open **Project Settings → Advanced Logs** to configure it. Settings apply to the whole project. Advanced Logs is **off by default**. Turn it on before detailed request logging starts. Advanced Logs settings: status, storage, background operations, and PII redaction ### Settings | Setting | Description | Default | |---|---|---| | **Status** | Turns Advanced Logs on or off for the project. | Off | | **Storage Settings** | **Error Data Only** stores bodies only for failed requests (HTTP status 400 or above). **All Data** stores them for every request. | Error Data Only | | **Include Background Operations** | Also stores operations StackOne runs itself, such as token refreshes, alongside the requests your users make. | Off | | **Redact personal information (PII)** | Replaces personal data in stored bodies. See [PII redaction](#pii-redaction). | Off | | **Storage Duration** | How long logs are kept before they are deleted: 1, 7, or 30 days. | 30 days | | **Automatically Disable on Date** | Turns Advanced Logs off on the date you pick, so logging you turned on to debug an issue does not keep running. | None | The other settings can only be changed while **Status** is on. Advanced Logs settings: storage duration and automatic disable date Retention changes apply only to new logs. Existing logs keep the retention they were stored with. ### PII redaction PII redaction removes personally identifiable information (PII) from stored bodies. To redact PII from tool inputs and responses, see [PII Redaction](/secure/pii-redaction). When **Redact personal information (PII)** is on, StackOne scans each body before the log is written and replaces each personal value it detects with a tag naming its type, such as `` or ``. Credential-like tokens the patterns catch have no type and become ``; named credential fields follow the **Credentials** rule below. Only the redacted copy is stored. - **Detection.** Patterns catch email addresses and credential-like tokens. A model finds names, phone numbers, postal addresses, government ID numbers, payment card numbers, and other personal data. - **Scope.** Request and response bodies only. Log metadata such as the path, status code, connector, and Linked Account stays intact, so logs remain searchable. - **Coverage.** The bodies of action call logs. - **Applies to new logs only.** Logs that are already stored are not changed. - **Credentials.** Fields whose names match a fixed list of credential names, such as `password`, `token`, `api_key`, `client_secret`, and `authorization`, are masked in every stored body whether or not PII redaction is on. The value is replaced with `**redacted**`, followed by its last five characters when it is longer than 10 characters. StackOne may not catch every instance of personal data. Don't treat redaction as the only control for regulated data. For compliance requirements beyond these settings, contact your StackOne account manager. # Self-Hosted Deployment Source: https://docs.stackone.com/secure/self-hosted-deployment Run StackOne in your own environment for full data residency. Self-hosted deployment is only available on certain plans. {detail} See [plans and pricing](https://www.stackone.com/pricing/). Most customers use StackOne's managed cloud, where you choose a [region](/gateway/concepts/organizations-and-projects) for data residency at the project level. Self-hosting runs StackOne inside your own infrastructure instead. The key advantage: your integration data never leaves your environment, meeting strict data-residency, sovereignty, and compliance requirements that the managed regions don't cover. Reach your StackOne account manager or email support@stackone.com to scope a deployment. # Connectors Source: https://docs.stackone.com/connectors/introduction Explore 560+ connectors and 35000+ actions available through StackOne. Use via Actions RPC, Toolset SDK, MCP, or A2A. Browse StackOne's pre-built connectors — each connector page shows its actions, authentication guides, and events. New connectors ship continuously, and any system can be added on request or [built yourself](/connector-building/overview). To connect your first system and run an action, follow the [Quickstart](/gateway/quickstart). Need a system or action that isn't listed? [Talk to StackOne](https://www.stackone.com/demo) and our team builds and maintains it for you: - **Fast turnaround** — typically days, not weeks (when API access is provided) - **Full support** — we handle API mapping, auth, and testing - **QA pipeline** — automated tests, AI-driven optimization, and manual verification - **Fork & customize** — optionally fork and edit actions after delivery Prefer to build it yourself? Start with [Connector Building](/connector-building/overview). StackOne builds connectors by analyzing **thousands of documented APIs** using AI agents and manual QA. Each connector's actions are automatically tested, then **manually verified by StackOne**. Evaluation data continuously improves action quality. ## All Connectors --- # 15Five Source: https://docs.stackone.com/connectors/15five/index How to set up the 15Five connector, plus the actions that are available.
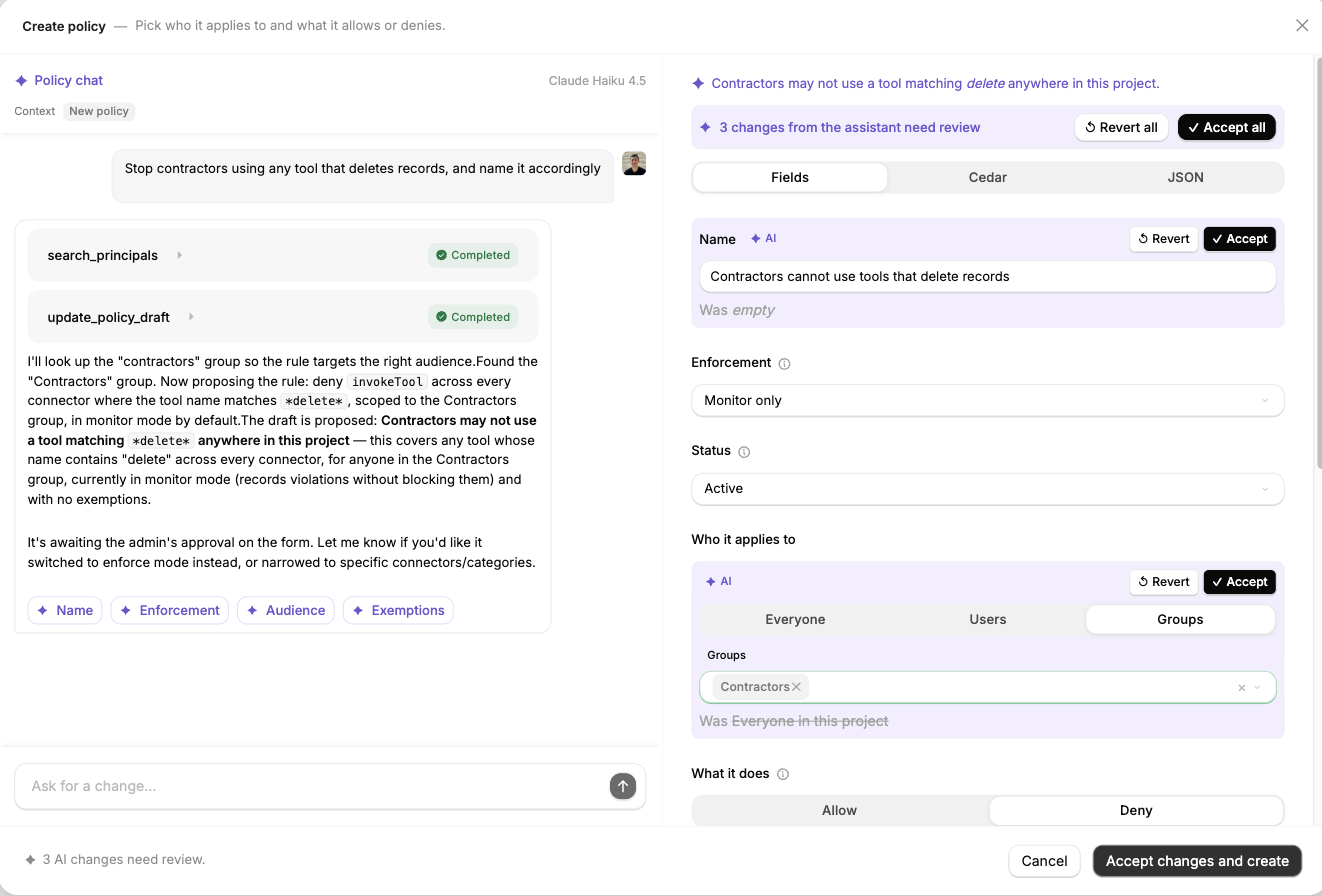
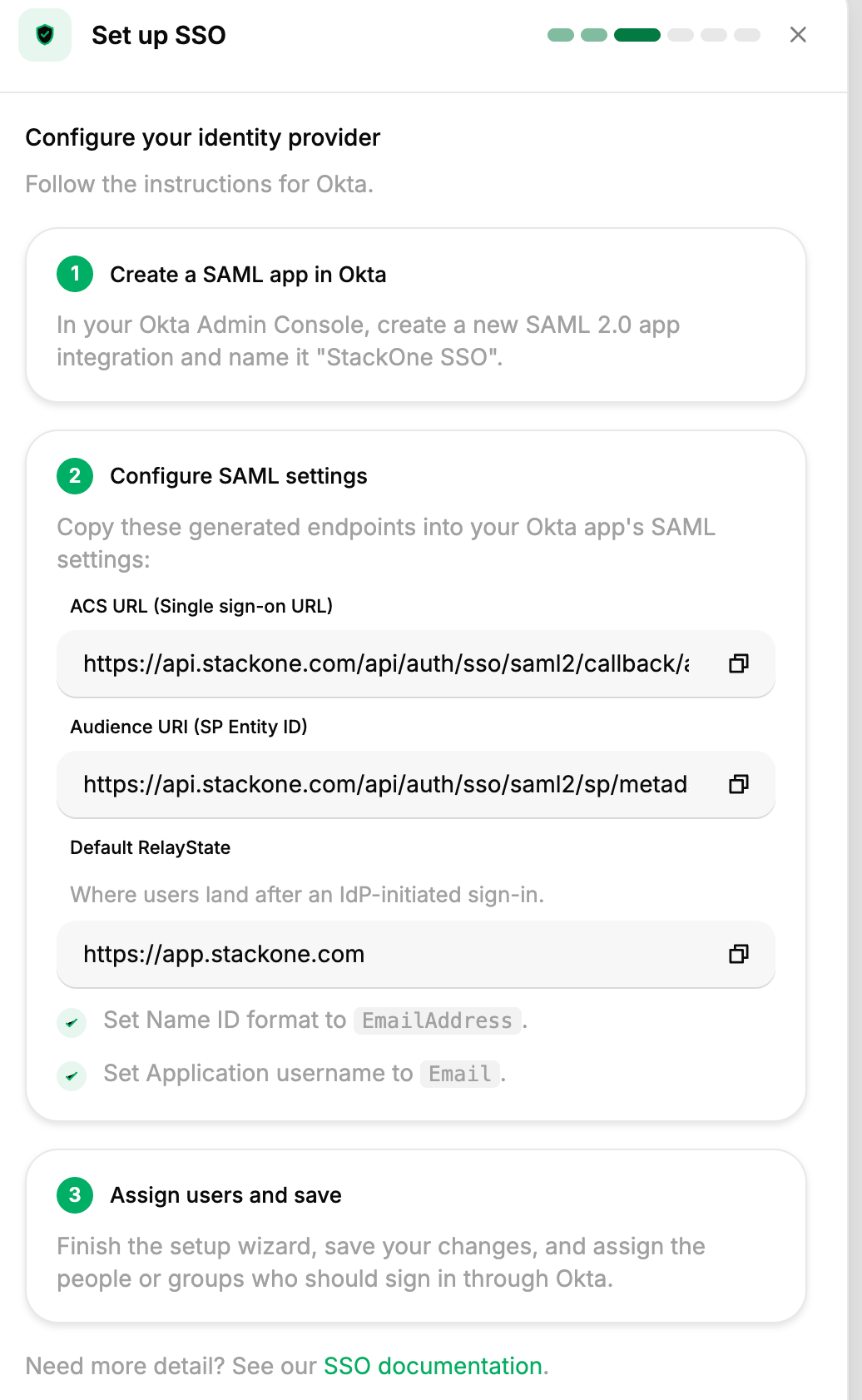
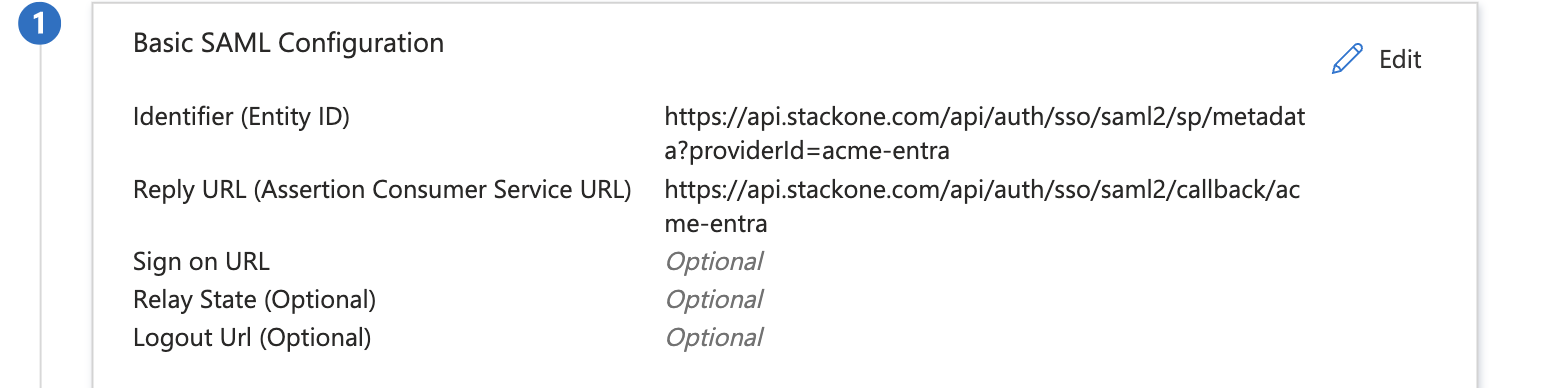
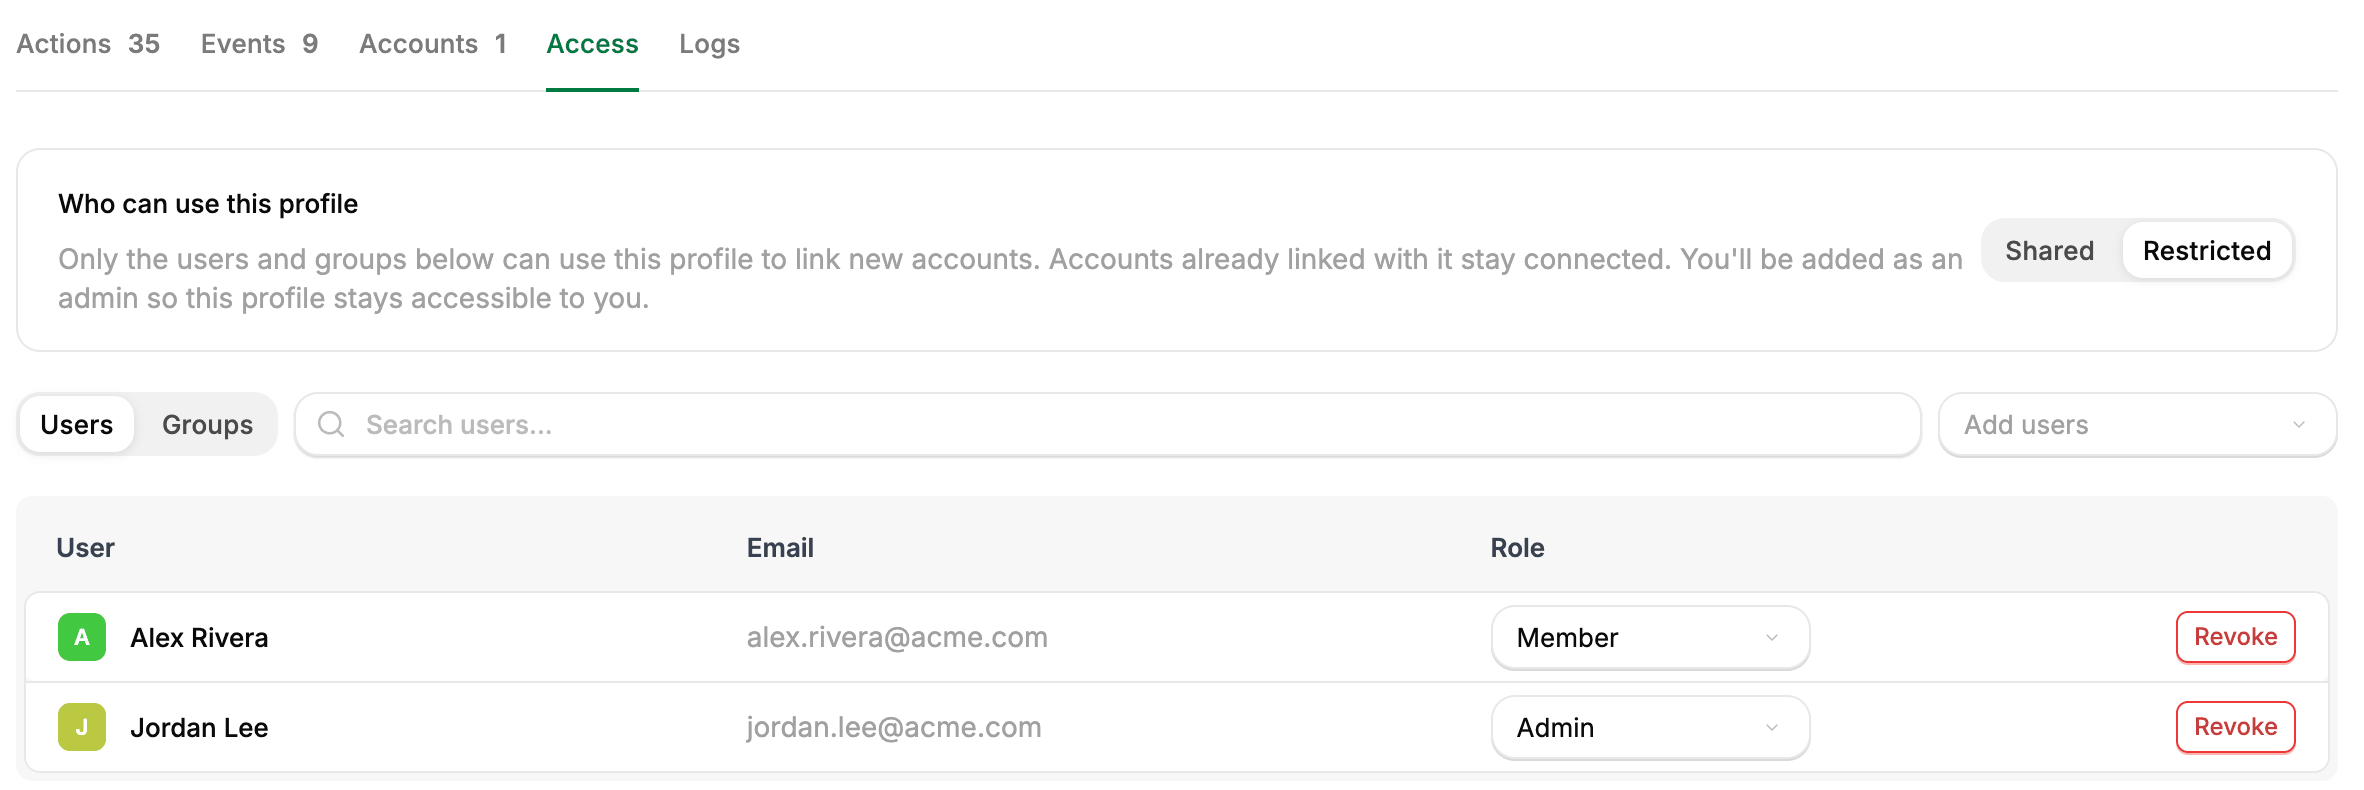
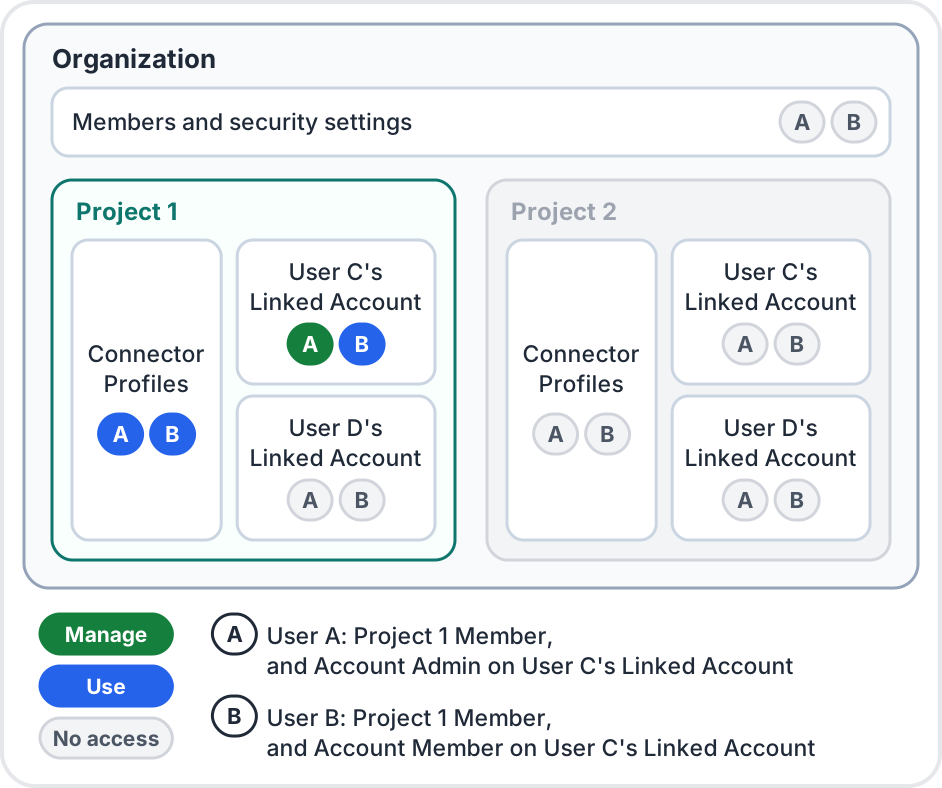
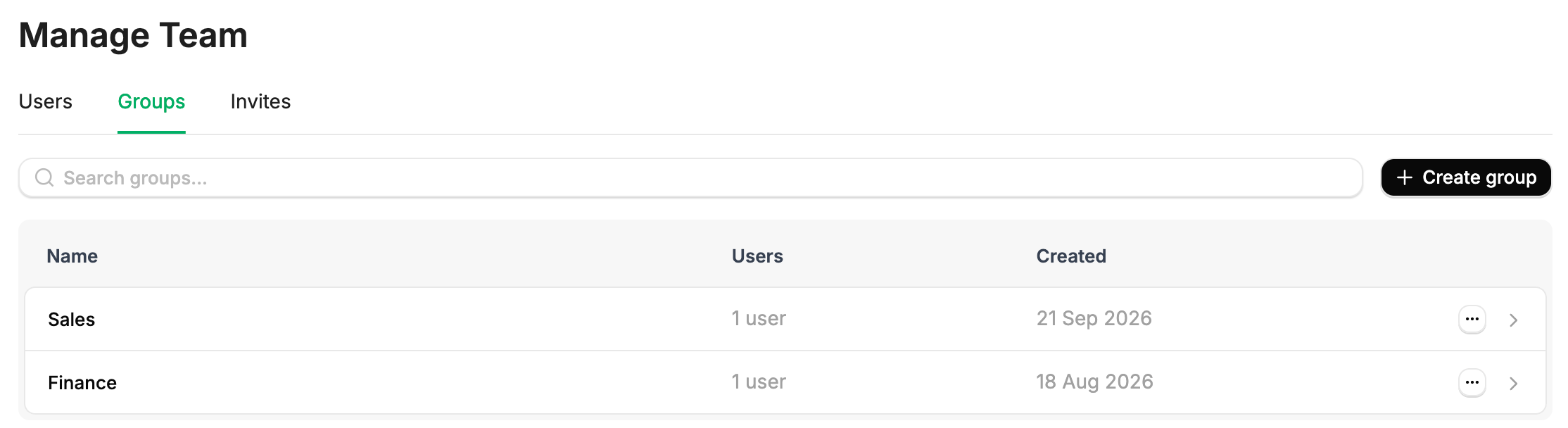
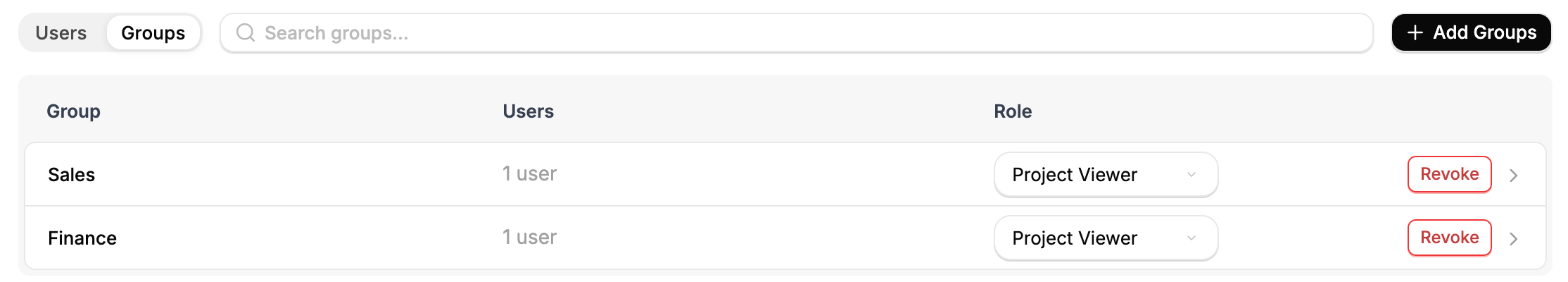
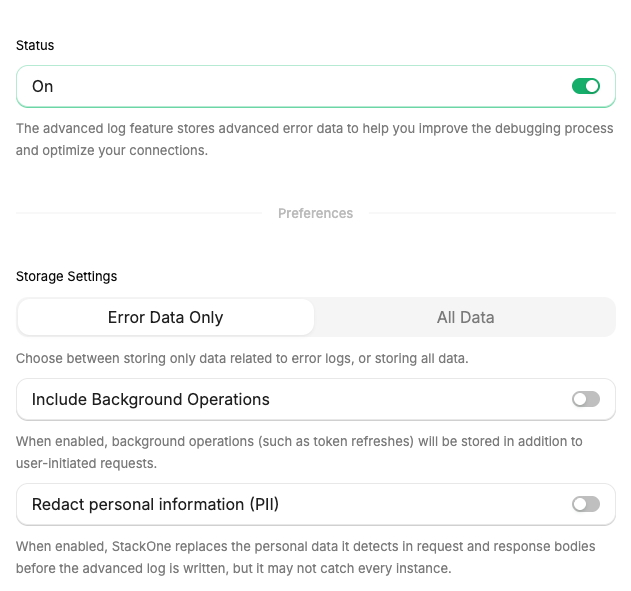
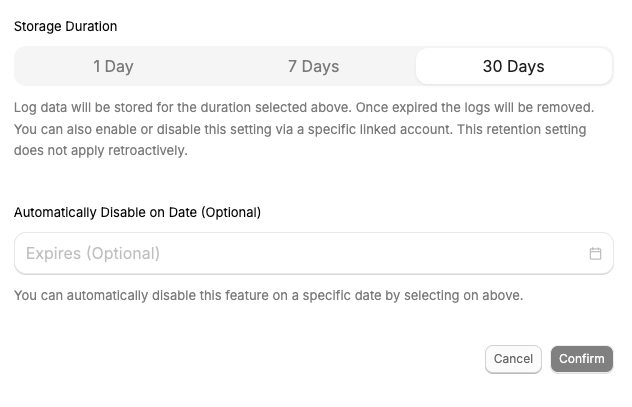
15Five
Previewv4.0.0
61 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses the 15Five API access token in the Authorization header as a raw value (no Bearer prefix, no base64 encoding). This... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/15five/index.md for the full list. # 15Five Changelog Source: https://docs.stackone.com/connectors/15five/changelog Release history for the 15Five connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `bug-fix` Key results now require an objective and a description on create — the provider rejects the request without them, so these are marked required up front instead of failing at call time. Priority sorting no longer offers sort-by-email or sort-by-employee-id, which 15Five accepts but silently ignores. `15five_create_bulk_user_update`, `15five_create_key_result`, `15five_list_people_attribute_values`, `15five_list_priorities`, `15five_update_key_result` `data-sync` `new-actions` `breaking` `bug-fix` Added data sync support so users, groups, objectives, check-ins, answers and 10 other collections can be kept continuously up to date, most of them fetching only what changed since the last sync. Removed the name_singular field from the group type create and update actions — 15Five ignores any value sent and always derives it from name_plural. `15five_create_bulk_user_import`, `15five_create_bulk_user_update`, `15five_create_company_vacation`, `15five_create_group_type`, `15five_create_key_result`, `15five_create_objective`, `15five_create_people_attribute`, `15five_create_people_attribute_value`, `15five_create_priority`, `15five_delete_company_vacation`, `15five_get_people_attribute`, `15five_get_people_attribute_value`, `15five_get_pulse`, `15five_list_answers`, `15five_list_check_ins`, `15five_list_company_vacations`, `15five_list_group_types`, `15five_list_groups`, `15five_list_high_fives`, `15five_list_objective_history`, `15five_list_objectives`, `15five_list_one_on_ones`, `15five_list_people_attribute_values`, `15five_list_people_attributes`, `15five_list_priorities`, `15five_list_pulses`, `15five_list_questions`, `15five_list_review_cycle_answers`, `15five_list_review_cycle_participants`, `15five_list_review_cycle_performance_measurements`, `15five_list_review_cycle_reviews`, `15five_list_review_cycles`, `15five_list_security_audit_events`, `15five_list_users`, `15five_patch_group_type`, `15five_update_key_result`, `15five_update_key_result_value`, `15five_update_objective`, `15five_update_user` `description-fix` Documented create_priority provider quirks (successful writes always return response body `data: []` — the created entity is not echoed inline; use `list_priorities(include_past_checkins=true)` to fetch it; write silently drops when target user has no open check-in cycle — pre-check via `list_check_ins` before firing) and removed the action-level `releaseStage: preview` from create_priority (connector-level `releaseStage` unchanged). Documented `hire_date_ts` / `start_date_ts` accepted formats (`YYYY-MM-DD` or ISO 8601 datetime — Unix epoch rejected 400 despite the `_ts` suffix) and PDT/PST display artifact (response looks one day earlier than sent, but the stored UTC calendar day is correct — avoid `YYYY-MM-DDT00:00:00Z`, the only ISO form that actually shifts the stored date back). `15five_create_priority`, `15five_update_user` `breaking-changes` `bug-fix` `description-fix` `guide-changes` BREAKING: create_bulk_user_import switched from `request` to `upload_file` — the CSV must now be base64-encoded on send; create_high_five now requires `creator_id` (provider rejects requests without it); list_check_ins.order_by enum narrowed to exclude provider values `id` and `report` (both trigger 502). Non-breaking: marked People Attributes and Objectives write actions (create_people_attribute, create_people_attribute_value, create_objective, create_key_result) plus their read counterparts as `releaseStage: preview` (workspace feature-flag / plan-tier gated on trial tenants); list_high_fives multi-value filters now use `arrayFormat: repeat` for correct serialization; group_types name_plural must end in "s" — provider silently rewrites otherwise (now documented in the field description, no more server-side value mutation on our end); documented update_user check-in cadence enums (reporting_period, biweekly_due_day_which_week, monthly_due_day_which_in_month) with UI-verified meanings and co-required-field preconditions; added feature/plan-tier enablement guide to the authentication section (Reviews, Objectives, People Attributes). `15five_create_bulk_user_import`, `15five_create_bulk_user_update`, `15five_create_company_vacation`, `15five_create_group_type`, `15five_create_high_five`, `15five_create_key_result`, `15five_create_objective`, `15five_create_people_attribute`, `15five_create_people_attribute_value`, `15five_delete_company_vacation`, `15five_get_objective_history`, `15five_get_people_attribute`, `15five_get_people_attribute_value`, `15five_list_company_vacations`, `15five_list_high_fives`, `15five_list_objective_history`, `15five_list_people_attribute_values`, `15five_list_people_attributes`, `15five_list_review_cycle_answers`, `15five_list_review_cycle_participants`, `15five_list_review_cycle_performance_measurements`, `15five_list_review_cycle_reviews`, `15five_list_security_audit_events`, `15five_patch_group_type`, `15five_update_company_vacation`, `15five_update_group_type`, `15five_update_user` `bug-fix` Standardized action category capitalization for more consistent portal filters. # 1Password Source: https://docs.stackone.com/connectors/onepassword/index How to set up the 1Password connector, plus the actions that are available.
1Password
Previewv1.2.0
24 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using a JWT bearer token generated for your 1Password Connect server. For more detail — https://developer.1... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/onepassword/index.md for the full list. # 1Password Changelog Source: https://docs.stackone.com/connectors/onepassword/changelog Release history for the 1Password connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for vaults, API activity logs, users, and groups, so these records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. # 360Learning Source: https://docs.stackone.com/connectors/360learning/index How to set up the 360Learning connector, plus the actions and events that are available.
360Learning
v1.2.1
78 actions · 38 events · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create OAuth2 credentials from Settings > API V2 in your 360Learning admin panel. Optionally, configure receiving Events for 360Learning into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/360learning/index.md for the full list. ## Events See https://docs.stackone.com/connectors/360learning/index.md for the full list. # 360Learning Changelog Source: https://docs.stackone.com/connectors/360learning/changelog Release history for the 360Learning connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` List Paths now applies the documented precedence when both modifiedAfter and modifiedAt.gte are supplied, which previously failed with a 400. Its date filter descriptions now state that 360Learning matches these values to the whole second, so both ends of a range include that second. `360learning_list_paths` `new-events` Added a webhook setup guide covering the thirty-eight event types, the webhooks:write scope the subscriptions need, and the limit of fifty webhook subscriptions an account allows - which one connection with every event enabled fills to thirty-eight. The twenty-eight event types verified against live deliveries stay preview; the ten that could not be triggered on the test account are now beta. `new-feature` `data-sync` Added DataSync support to nine list actions: users, courses, course statistics, groups, paths, tags, classrooms, custom fields, and external ID mappings. The paths action syncs incrementally via a new optional modifiedAfter filter; the other eight sync by full refresh. # 7shifts Source: https://docs.stackone.com/connectors/7shifts/index How to set up the 7shifts connector, plus the actions that are available.
7shifts
v1.4.0
59 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a long-lived Bearer token generated in Company Settings. Token inherits the permissions of the admin who created it... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/7shifts/index.md for the full list. # 7shifts Changelog Source: https://docs.stackone.com/connectors/7shifts/changelog Release history for the 7shifts connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added Data Sync support for companies, departments, locations, roles, shifts, time off, users and user contacts, with incremental sync on the five endpoints that filter by modified_since. On users, departments and locations that filter is now truncated to the YYYY-MM-DD form those endpoints require, so a full timestamp is accepted instead of rejected. `7shifts_list_companies`, `7shifts_list_departments`, `7shifts_list_locations`, `7shifts_list_roles`, `7shifts_list_shifts`, `7shifts_list_time_off`, `7shifts_list_user_contacts`, `7shifts_list_users` `bug-fix` Made create_time_punch breaks[].out required (provider returns 422 without it). Commented out list_shifts deleted and include_deleted params (provider ignores them, deleted shifts leak into default results). `7shifts_create_time_punch`, `7shifts_list_shifts`, `7shifts_update_shift` `improvement` `bug-fix` Improved action descriptions with conflict warnings, datetime format requirements, and required field documentation. Commented out plan-gated update_shift params (user_id, department_id, close). `7shifts_create_shift`, `7shifts_create_time_off`, `7shifts_create_time_punch`, `7shifts_create_user`, `7shifts_get_time_off_total_hours`, `7shifts_update_shift` `guide-fix` Improved connection guide with login URL, scope instructions, and Company ID section. Added inline test action to verify Company ID on connect. # Abacus.AI Source: https://docs.stackone.com/connectors/abacusai/index How to set up the Abacus.AI connector, plus the actions that are available.
Abacus.AI
Betav0.2.0
62 actions · 1 auth method
AI IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Abacus.AI account using an API key generated from the Abacus.AI dashboard. The key inherits the permissions... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/abacusai/index.md for the full list. # Abacus.AI Changelog Source: https://docs.stackone.com/connectors/abacusai/changelog Release history for the Abacus.AI connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the organization user, organization group, API key, pipeline, and refresh policy list actions for scheduled full record syncs. `abacusai_list_api_keys`, `abacusai_list_organization_groups`, `abacusai_list_organization_users`, `abacusai_list_pipelines`, `abacusai_list_refresh_policies` `new-connector` Initial Abacus.AI connector with 62 actions across 11 resources (projects, feature groups, datasets, models, deployments, batch predictions, refresh policies, model monitors, pipelines, webhooks, organization). # absence.io Source: https://docs.stackone.com/connectors/absenceio/index How to set up the absence.io connector, plus the actions that are available.
absence.io
v1.1.0
24 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses absence.io's customized OAuth 2.0 Client Credentials flow. The issued access token is user-mapped — calls operate w... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/absenceio/index.md for the full list. # absence.io Changelog Source: https://docs.stackone.com/connectors/absenceio/changelog Release history for the absence.io connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `improvement` Added data sync support to the users, absences, timespans, departments, teams, locations, reasons, and allowance type list actions, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. # AbsenceSoft Source: https://docs.stackone.com/connectors/absencesoft/index How to set up the AbsenceSoft connector, plus the actions that are available.
AbsenceSoft
Betav1.0.0
28 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). AbsenceSoft uses an OAuth 2.0 resource-owner password grant. Your Portal username and password are exchanged at your org... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/absencesoft/index.md for the full list. # Absolute Software Source: https://docs.stackone.com/connectors/absolutesoftware/index How to set up the Absolute Software connector, plus the actions that are available.
Absolute Software
Previewv1.1.3
119 actions · 1 auth method
Device Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses JWS (JSON Web Signature) with HS256 symmetric signing (HMAC). Requires a Token ID and Secret Key from the Absolute... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/absolutesoftware/index.md for the full list. # Absolute Software Changelog Source: https://docs.stackone.com/connectors/absolutesoftware/changelog Release history for the Absolute Software connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `description-improvements` Fixed edit and delete policy group actions to return confirmable data. Improved device group descriptions for better tool disambiguation. `absolutesoftware_delete_policy_group`, `absolutesoftware_edit_policy_group_properties`, `absolutesoftware_get_all_device_groups`, `absolutesoftware_get_all_device_groups_and_folders` `description-improvements` Enumerated valid select field values in device reporting action descriptions to prevent invalid field errors. `absolutesoftware_get_device_connectivity`, `absolutesoftware_get_device_details`, `absolutesoftware_get_device_details_advanced`, `absolutesoftware_get_device_license_details`, `absolutesoftware_get_device_security_status` `bug-fix` `description-improvements` Fixed JWS signing bug on cancel actions (file delete, messaging, wipe), made type and categoryCode required on update custom field definition, improved action descriptions for deviceUids validation and freeze message requirements, and added result.message confirmations for write operations. `absolutesoftware_activate_policy`, `absolutesoftware_cancel_file_delete_actions`, `absolutesoftware_cancel_messaging_actions`, `absolutesoftware_cancel_reach_actions`, `absolutesoftware_cancel_wipe_actions`, `absolutesoftware_create_custom_data_config`, `absolutesoftware_create_freeze_request`, `absolutesoftware_create_wipe_request`, `absolutesoftware_deactivate_policy`, `absolutesoftware_delete_custom_data_config`, `absolutesoftware_delete_device_group_or_folder`, `absolutesoftware_delete_freeze_message`, `absolutesoftware_delete_policy_group`, `absolutesoftware_download_script`, `absolutesoftware_edit_policy_group_properties`, `absolutesoftware_get_device_details`, `absolutesoftware_get_device_details_advanced`, `absolutesoftware_get_device_security_status`, `absolutesoftware_get_file_delete_actions`, `absolutesoftware_get_file_delete_actions_by_request`, `absolutesoftware_get_messaging_actions`, `absolutesoftware_get_messaging_actions_by_request`, `absolutesoftware_get_reach_actions`, `absolutesoftware_get_unenroll_actions`, `absolutesoftware_get_unenroll_actions_by_request`, `absolutesoftware_get_wipe_actions`, `absolutesoftware_get_wipe_actions_by_request`, `absolutesoftware_remove_freeze`, `absolutesoftware_update_action_threshold`, `absolutesoftware_update_agent_policy_groups`, `absolutesoftware_update_custom_field_definition`, `absolutesoftware_update_device_custom_fields`, `absolutesoftware_update_device_group_tree_node`, `absolutesoftware_update_freeze_message`, `absolutesoftware_update_geolocation_settings` `new-actions` `data-sync` Added DataSync support to 28 list actions for periodic data synchronisation of devices, users, roles, software, groups, geofences, policies, licences, and configuration resources. Includes incremental sync for device connectivity via lastUpdatedDateTimeUtc filter. # Accelo Source: https://docs.stackone.com/connectors/accelo/index How to set up the Accelo connector, plus the actions that are available.
Accelo
Betav1.1.0
67 actions · 1 auth method
CRM Project Management Ticketing Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Service account API key authentication. Create a service account in Accelo and generate an API token for server-to-serve... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/accelo/index.md for the full list. # Accelo Changelog Source: https://docs.stackone.com/connectors/accelo/changelog Release history for the Accelo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for 15 top-level collections (activities, affiliations, companies, contacts, contracts, expenses, invoices, issues, jobs, milestones, payments, prospects, quotes, staff and tasks), paginated with the standard _offset/_limit parameters. All collections full refresh on every run because Accelo exposes date_modified only inside the composite _filters string, not as a standalone request parameter. Also corrects every action's result mapping, which pointed at a non-existent step output key and returned an empty object. # ActiveCampaign Source: https://docs.stackone.com/connectors/activecampaign/index How to set up the ActiveCampaign connector, plus the actions that are available.
ActiveCampaign
v1.3.0
40 actions · 1 auth method
CRM Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using an API Key and API URL from your ActiveCampaign Developer settings. No app registration required; eac... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/activecampaign/index.md for the full list. # ActiveCampaign Changelog Source: https://docs.stackone.com/connectors/activecampaign/changelog Release history for the ActiveCampaign connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support to eleven list actions covering contacts, deals, accounts, campaigns, messages, lists, tags, users, pipelines, deal stages and deal custom fields, with incremental updates on contacts and deals. Fixed List Deals returning duplicate records and silently skipping others when reading beyond the first page. `activecampaign_list_accounts`, `activecampaign_list_campaigns`, `activecampaign_list_contacts`, `activecampaign_list_deal_custom_fields`, `activecampaign_list_deal_stages`, `activecampaign_list_deals`, `activecampaign_list_lists`, `activecampaign_list_messages`, `activecampaign_list_pipelines`, `activecampaign_list_tags`, `activecampaign_list_users` `new-actions` `bug-fix` `docs` Added 8 actions - list_pipelines, list_deal_stages, list_users and list_deal_custom_fields so the IDs create_deal requires can be discovered, list_contact_tags so a contact-tag association ID can be obtained for remove_contact_tag, plus update_tag, delete_deal and delete_account. Corrected create_deal's description, which wrongly promised that omitting group and stage auto-assigns a pipeline when ActiveCampaign rejects it. Documented that list_lists returns email-channel lists only and excludes SMS lists from meta.total. `activecampaign_delete_account`, `activecampaign_delete_deal`, `activecampaign_list_contact_tags`, `activecampaign_list_deal_custom_fields`, `activecampaign_list_deal_stages`, `activecampaign_list_pipelines`, `activecampaign_list_users`, `activecampaign_update_tag` `activecampaign_create_deal`, `activecampaign_list_lists` `new-actions` `bug-fix` Added 9 actions (create_tag, delete_tag, create_account, update_account, create_deal, update_deal, create_campaign, delete_list, delete_message), pagination params (limit/offset) on all list actions, contact filter params, custom field values on contact/account/deal writes, and additional update_message fields. Fixed list_contact_activities contact param to required. Connection guide updated with portal screenshots, navigation context, and corrected field labels. # AD Manager Source: https://docs.stackone.com/connectors/admanager/index How to set up the AD Manager connector, plus the actions and events that are available.
AD Manager
Previewv0.1.1
55 actions · 1 event · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a technician authtoken generated in the ADManager Plus console. The token carries that technician's delegated permi... Optionally, configure receiving Events for AD Manager into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/admanager/index.md for the full list. ## Events See https://docs.stackone.com/connectors/admanager/index.md for the full list. # AD Manager Changelog Source: https://docs.stackone.com/connectors/admanager/changelog Release history for the AD Manager connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `guide` Fixed accounts connecting with an invalid authtoken, which now fail with a clear authentication error, and expanded the API Key connection guide with token scope, built-in admin and REST API column steps. `admanager_list_domains` `new-connector` Initial release of the AD Manager connector with 55 actions covering Active Directory users, groups, group membership, computers, contacts, organizational units, domains, orchestration, workflow requests and admin settings, plus inbound webhook events and data sync for organization attributes, environment variables, domains and orchestration templates. # Adobe Commerce Source: https://docs.stackone.com/connectors/adobe_commerce/index How to set up the Adobe Commerce connector, plus the actions that are available.
Adobe Commerce
Betav1.1.0
61 actions · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/adobe_commerce/index.md for the full list. # Adobe Commerce Changelog Source: https://docs.stackone.com/connectors/adobe_commerce/changelog Release history for the Adobe Commerce connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for products, customers, orders, invoices, credit memos, shipments, CMS pages and blocks, customer groups, coupons, cart rules, tax rates, rules and classes, inventory source items, and store configuration. Paged list actions now also return total_count and search_criteria. # Adobe Experience Manager Source: https://docs.stackone.com/connectors/adobeexperiencemanager/index How to set up the Adobe Experience Manager connector, plus the actions that are available.
Adobe Experience Manager
Betav1.1.0
52 actions · 1 auth method
CMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth Web App credential on an AEM API in the Adobe Developer Console. Access tokens are valid f... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/adobeexperiencemanager/index.md for the full list. # Adobe Experience Manager Changelog Source: https://docs.stackone.com/connectors/adobeexperiencemanager/changelog Release history for the Adobe Experience Manager connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for the four top-level collections — list_content_fragments, list_content_fragment_models, list_delivery_fragments and list_workflows — so authored and delivered Content Fragments, their models, and workflow instances can be harvested on a schedule. All four use the AEM cursor paginator and full refresh on every run, since neither the Sites nor the Content Fragment Delivery API exposes an updated-since filter on a list endpoint. No change to any action's request behaviour, inputs or validation. # Adobe Learning Manager Source: https://docs.stackone.com/connectors/adobelearningmanager/index How to set up the Adobe Learning Manager connector, plus the actions that are available.
Adobe Learning Manager
v1.1.0
72 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Register your application in Adobe Learning Manager as Integration Admin to obtain Client ID and Client Secret. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/adobelearningmanager/index.md for the full list. # Adobe Learning Manager Changelog Source: https://docs.stackone.com/connectors/adobelearningmanager/changelog Release history for the Adobe Learning Manager connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added DataSync support for users, user groups, skills, catalogs, badges, jobs, boards, external profiles, managed offices, and recommendation products and roles. All syncs are full-refresh — the Prime API v2 exposes no updated-since filter on any list endpoint. # Adobe PDF Services Source: https://docs.stackone.com/connectors/adobepdfservices/index How to set up the Adobe PDF Services connector, plus the actions and events that are available.
Adobe PDF Services
Previewv1.2.1
48 actions · 3 events · 1 auth method
Documents IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Adobe PDF Services uses OAuth Server-to-Server authentication. Create a project in Adobe Developer Console and add the P... Optionally, configure receiving Events for Adobe PDF Services into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/adobepdfservices/index.md for the full list. ## Events See https://docs.stackone.com/connectors/adobepdfservices/index.md for the full list. # Adobe PDF Services Changelog Source: https://docs.stackone.com/connectors/adobepdfservices/changelog Release history for the Adobe PDF Services connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clearer guidance and error message for the Organization ID that the user, group and role actions need. `adobepdfservices_unified_get_group`, `adobepdfservices_unified_get_role`, `adobepdfservices_unified_get_user`, `adobepdfservices_unified_list_groups`, `adobepdfservices_unified_list_roles`, `adobepdfservices_unified_list_users` `new-feature` Added webhook events for PDF Services job completion and failure, delivered when a job is submitted with a CALLBACK notifier pointing at the account's Native Webhook URL. `new-actions` Added unified IAM actions for users, groups, roles and credentials, read from the Adobe Admin Console organization linked to the connection. # ADP Workforce Now Source: https://docs.stackone.com/connectors/adpworkforcenow/index How to set up the ADP Workforce Now connector, plus the actions and events that are available.
ADP Workforce Now
Previewv1.5.0
53 actions · 31 events · 1 auth method
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 with client credentials and mutual TLS (mTLS) certificate authentication. Requires API access su... Optionally, configure receiving Events for ADP Workforce Now into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/adpworkforcenow/index.md for the full list. ## Events See https://docs.stackone.com/connectors/adpworkforcenow/index.md for the full list. # ADP Workforce Now Changelog Source: https://docs.stackone.com/connectors/adpworkforcenow/changelog Release history for the ADP Workforce Now connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for workers, job requisitions, job applications, general ledger documents, associate work locations, business units, cost centers, departments and jobs, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the ADP Workforce Now API exposes no updated-since filter a sync can use. `adpworkforcenow_list_business_units`, `adpworkforcenow_list_cost_centers`, `adpworkforcenow_list_departments`, `adpworkforcenow_list_general_ledger_documents`, `adpworkforcenow_list_job_applications`, `adpworkforcenow_list_job_requisitions`, `adpworkforcenow_list_jobs`, `adpworkforcenow_list_work_locations`, `adpworkforcenow_list_workers` `new-actions` Add inbound webhook support for ADP Event Notifications — 30 per-event handlers (worker lifecycle, profile, communication, work assignment, dependents, time off, payroll) plus a webhooks.test ping handler, delivered via ADP API Central to the connection's Native Webhook URL, with an events setup guide. `new-actions` Added General Ledger document actions: list available G/L (general ledger) files and download a single G/L file by document ID, with optional OData $filter and roleCode support. `adpworkforcenow_download_general_ledger_document`, `adpworkforcenow_list_general_ledger_documents` `bug-fix` Fixed OData query params returning HTTP 500 (escaped $-prefixed arg names); added validation-table search/filter/version and pay-statement roleCode/numberoflastpaydates params; removed provider-unsupported query params (count, validation-table & pay-statement top/skip/filter, jobs filter); enum-validated roleCode and accountType; empty time-off and pay-statement responses now return an empty array; clearer action descriptions. `adpworkforcenow_list_jobs` `adpworkforcenow_get_job` `adpworkforcenow_add_worker_legal_address`, `adpworkforcenow_applicant_onboard`, `adpworkforcenow_change_base_remuneration`, `adpworkforcenow_change_pay_distribution`, `adpworkforcenow_change_worker_legal_address`, `adpworkforcenow_change_worker_legal_name`, `adpworkforcenow_change_worker_personal_address`, `adpworkforcenow_change_worker_preferred_name`, `adpworkforcenow_change_worker_reports_to`, `adpworkforcenow_get_organizational_pay_statements`, `adpworkforcenow_get_pay_distributions`, `adpworkforcenow_get_time_off_configurations`, `adpworkforcenow_get_time_off_requests`, `adpworkforcenow_get_worker`, `adpworkforcenow_get_worker_demographics`, `adpworkforcenow_get_worker_photo`, `adpworkforcenow_list_business_units`, `adpworkforcenow_list_cost_centers`, `adpworkforcenow_list_departments`, `adpworkforcenow_list_job_applications`, `adpworkforcenow_list_job_requisitions`, `adpworkforcenow_list_work_locations`, `adpworkforcenow_list_worker_demographics`, `adpworkforcenow_list_workers`, `adpworkforcenow_rehire_worker`, `adpworkforcenow_remove_worker_legal_address` `new-actions` Added list_time_entries_entry_codes action to list the valid entry codes for time entry modification. # ADP Workforce Now Next Generation Source: https://docs.stackone.com/connectors/adpworkforcenownextgen/index How to set up the ADP Workforce Now Next Generation connector, plus the actions that are available.
ADP Workforce Now Next Generation
Betav0.2.0
71 actions · 1 auth method
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 with client credentials and mutual TLS (mTLS) certificate authentication. Requires API access su... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/adpworkforcenownextgen/index.md for the full list. # ADP Workforce Now Next Generation Changelog Source: https://docs.stackone.com/connectors/adpworkforcenownextgen/changelog Release history for the ADP Workforce Now Next Generation connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for workers, worker demographics, job requisitions, payroll group pay periods, associate work locations, business units, departments and jobs, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the ADP Workforce Now Next Generation API exposes no updated-since filter a sync can use. `adpworkforcenownextgen_list_associate_work_locations`, `adpworkforcenownextgen_list_business_units`, `adpworkforcenownextgen_list_departments`, `adpworkforcenownextgen_list_job_requisitions`, `adpworkforcenownextgen_list_jobs`, `adpworkforcenownextgen_list_payroll_group_pay_periods`, `adpworkforcenownextgen_list_worker_demographics`, `adpworkforcenownextgen_list_workers` `new-connector` Initial release of the ADP Workforce Now Next Generation connector covering worker records and demographics, work assignment management, personal contacts, leaves of absence, time-off requests and balances, payroll input and deduction instructions, talent profile (memberships, degrees, and licenses), recruiting and applicant onboarding, benefit dependents, and organization validation tables. Authenticated via OAuth 2.0 client credentials with mutual TLS (mTLS) through ADP API Central; distinct from the classic ADP Workforce Now connector. # Adyen Source: https://docs.stackone.com/connectors/adyen/index How to set up the Adyen connector, plus the actions that are available.
Adyen
Previewv0.1.1
19 actions · 1 auth method
Payments IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses the API key of an Adyen API credential, sent in the X-API-Key header. Each Management API endpoint needs a matching... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/adyen/index.md for the full list. # Adyen Changelog Source: https://docs.stackone.com/connectors/adyen/changelog Release history for the Adyen connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Native actions are now tagged by resource, the API key guide covers the Merchant admin role and the step to save a new key, and a full user sync no longer re-fetches companies, merchants and merchant users on every page. `adyen_get_company`, `adyen_get_company_api_credential`, `adyen_get_company_user`, `adyen_get_me`, `adyen_get_merchant`, `adyen_get_merchant_api_credential`, `adyen_get_merchant_user`, `adyen_list_companies`, `adyen_list_company_api_credentials`, `adyen_list_company_merchants`, `adyen_list_company_users`, `adyen_list_merchant_api_credentials`, `adyen_list_merchant_users`, `adyen_list_merchants`, `adyen_unified_get_organization`, `adyen_unified_list_users` `new-connector` New Adyen connector for reading company and merchant accounts, Customer Area users, and API credentials, with unified IAM users, organizations and connection identity. # Affinity Source: https://docs.stackone.com/connectors/affinity/index How to set up the Affinity connector, plus the actions that are available.
Affinity
Previewv1.2.2
43 actions · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Affinity API key for authentication. Find it in Settings > API Keys Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/affinity/index.md for the full list. # Affinity Changelog Source: https://docs.stackone.com/connectors/affinity/changelog Release history for the Affinity connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed unified resource user lists failing with an error whenever a list had an owner or shared members. `affinity_unified_list_resource_users` `bug-fix` Fixed role lookups returning an empty result instead of a not-found error. `affinity_unified_get_me`, `affinity_unified_get_organization`, `affinity_unified_get_role`, `affinity_unified_get_user`, `affinity_unified_list_organizations`, `affinity_unified_list_resource_users`, `affinity_unified_list_roles`, `affinity_unified_list_users` `bug-fix` Fixed unified_list_roles / unified_get_role returning a single invented role instead of Affinity's real account roles. `affinity_unified_get_role`, `affinity_unified_get_user`, `affinity_unified_list_resource_users`, `affinity_unified_list_roles`, `affinity_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, credentials, and resource users. # Aha! Source: https://docs.stackone.com/connectors/aha/index How to set up the Aha! connector, plus the actions and events that are available.
Aha!
v1.2.0
91 actions · 34 events · 2 auth methods
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an OAuth app in Aha! Settings. Best for personal scripts and quick testing. Access is scoped to the permissions of the user who generated the key. Optionally, configure receiving Events for Aha! into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/aha/index.md for the full list. ## Events See https://docs.stackone.com/connectors/aha/index.md for the full list. # Aha! Changelog Source: https://docs.stackone.com/connectors/aha/changelog Release history for the Aha! connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data synchronisation support for 9 list actions including products, features, epics, initiatives, ideas, goals, tasks, approvals, and users. `aha_list_approvals`, `aha_list_epics`, `aha_list_features`, `aha_list_goals`, `aha_list_ideas`, `aha_list_initiatives`, `aha_list_products`, `aha_list_tasks`, `aha_list_users` `fix` `description` Removed unsupported 'creator_organization' visibility enum value from idea actions. Improved action descriptions for progress updates and workflow status constraints. `aha_create_idea`, `aha_create_initiative`, `aha_create_requirement`, `aha_update_epic_progress`, `aha_update_goal_progress`, `aha_update_idea`, `aha_update_release_progress` `guide` Rewrote the OAuth 2.0 and API Key connection guides with the sign-in URL and the full Settings, Personal and Developer navigation, and added portal screenshots to every step. Shortened the API Key field description to brief helper text. `webhook` `new-events` `guides` Added webhook events for 11 record types with create, update and destroy actions, events setup guide. # Airbyte Source: https://docs.stackone.com/connectors/airbyte/index How to set up the Airbyte connector, plus the actions that are available.
Airbyte
Previewv0.1.1
15 actions · 1 auth method
Data Integration IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses the client ID and secret of an Airbyte application, which acts as the user who created it with that user's roles. A... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/airbyte/index.md for the full list. # Airbyte Changelog Source: https://docs.stackone.com/connectors/airbyte/changelog Release history for the Airbyte connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` The connector description and OAuth setup guide are clearer, and looking up group membership during a user sync no longer breaks once a page has more than 75 users. `airbyte_unified_get_user`, `airbyte_unified_list_users` `new-connector` Initial Airbyte connector for reviewing who has access to an Airbyte organization, covering organization members, their organization roles and user groups, workspaces and permissions, for Airbyte Cloud and self-managed deployments. # Aircall Source: https://docs.stackone.com/connectors/aircall/index How to set up the Aircall connector, plus the actions and events that are available.
Aircall
Previewv1.2.0
82 actions · 8 events · 1 auth method
Telephony IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Admin privileges are required in your Aircall dashboard to generate an API key. Optionally, configure receiving Events for Aircall into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/aircall/index.md for the full list. ## Events See https://docs.stackone.com/connectors/aircall/index.md for the full list. # Aircall Changelog Source: https://docs.stackone.com/connectors/aircall/changelog Release history for the Aircall connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `guide` `bug-fix` Added webhook events for calls, conversation intelligence, users, contacts and numbers, with a setup guide listing them, and Data Sync for the main list actions. Write actions such as tagging and commenting on a call now confirm the change instead of returning an empty response. `aircall_add_phone_numbers`, `aircall_comment_a_call`, `aircall_create_a_dialer_campaign`, `aircall_insight_cards`, `aircall_list_all_calls`, `aircall_list_all_contacts`, `aircall_list_all_numbers`, `aircall_list_all_numbers_for_a_user_v2`, `aircall_list_all_tags`, `aircall_list_all_teams`, `aircall_list_all_users_v2`, `aircall_retrieve_a_user_v2`, `aircall_retrieve_list_of_users_availability`, `aircall_search_calls`, `aircall_search_contacts`, `aircall_start_an_outbound_call`, `aircall_tag_a_call`, `aircall_unified_list_groups`, `aircall_unified_list_organizations`, `aircall_unified_list_roles`, `aircall_unified_list_users` `bug-fix` Fixed member lists for numbers and teams failing with an error whenever users were assigned. `aircall_unified_list_resource_users` `new-actions` Added unified IAM actions for users, groups, organizations, roles, resource users, and credentials. # Airship Source: https://docs.stackone.com/connectors/airship/index How to set up the Airship connector, plus the actions that are available.
Airship
v1.2.0
39 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using App Key and Master Secret for server-to-server API access. Requires Admin privileges within Airship. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/airship/index.md for the full list. # Airship Changelog Source: https://docs.stackone.com/connectors/airship/changelog Release history for the Airship connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added Data Sync support for List Templates, List Pipelines, List Schedules, List Segments, List Attribute Lists, List Tag Lists, and List Static Lists, so these resources can be synced into StackOne on a schedule and read without calling Airship. All run as a full refresh on every sync, because Airship's list endpoints offer no last-updated filter. `airship_list_attribute_lists`, `airship_list_pipelines`, `airship_list_schedules`, `airship_list_segments`, `airship_list_static_lists`, `airship_list_tag_lists`, `airship_list_templates` `description-fix` Clarified how to specify a custom event trigger when creating a pipeline: the matcher's key must be "name" and the event name goes in value.equals. This prevents a "Could not parse request body" error that occurred when the trigger was built incorrectly. `airship_create_pipeline` `bug-fix` Corrected the pipeline trigger filter so only trigger types Airship actually supports can be selected. Subscription add/remove triggers are no longer offered as filter values (Airship rejects them), so filtering by trigger type now fails fast with a clear error instead of a confusing "unknown trigger filter" from the provider. `airship_list_filtered_pipelines` `bug-fix` Clearer descriptions so agents build these requests right the first time: the exact pipeline trigger shapes (custom event, first opt-in, subscription, region), delivery-window timing and tag-group conditions; the attribute operators allowed in segment criteria; and the rules that a template's push can't include device_types and that updating a template can't add brand-new variables. Also fixed the pipeline trigger filter so multiple trigger types are sent as separate query values instead of one comma-joined value the API rejects. `airship_create_pipeline`, `airship_create_schedule`, `airship_create_segment`, `airship_create_template`, `airship_list_filtered_pipelines`, `airship_update_segment`, `airship_update_template` `bug-fix` Fixed the Basic Auth connection guide navigation, region detection and UI labels to match the Airship portal, and corrected the App key and Master secret field descriptions. Added portal screenshots to the guide steps. `new-actions` `bug-fix` Added create_pipeline action plus missing inputs (list_templates sort/order, pipeline activation/deactivation and rate constraints); fixed pipeline trigger/constraint schemas, loosened schedule push audience typing, and removed unsupported schedule params (localization_ids, push_ids). # Airtable Source: https://docs.stackone.com/connectors/airtable/index How to set up the Airtable connector, plus the actions that are available.
Airtable
v1.3.0
33 actions · 2 auth methods
Databases IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for single-user integrations and scripts. Scoped tokens let you limit access to specific bases and actions. Requires registering an OAuth app. Uses PKCE with granular scopes per base. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/airtable/index.md for the full list. # Airtable Changelog Source: https://docs.stackone.com/connectors/airtable/changelog Release history for the Airtable connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added DataSync support for bases, users, and groups, synced as full refreshes. `airtable_list_bases`, `airtable_unified_list_groups`, `airtable_unified_list_users` `bug-fix` Fixed user and group list pagination failing for accounts with more than 100 members. `airtable_unified_get_group`, `airtable_unified_get_me`, `airtable_unified_get_role`, `airtable_unified_get_user`, `airtable_unified_list_groups`, `airtable_unified_list_resource_users`, `airtable_unified_list_roles`, `airtable_unified_list_users` `guide-changes` Connection guides now explain the SCIM API Token used for user and group sync, including that it requires a Business, Enterprise, or Enterprise Scale plan with SSO enabled. `new-actions` Added SCIM-backed unified IAM users and groups actions (list and get), plus an optional SCIM API Token credential for enterprise SCIM access. `airtable_unified_get_group`, `airtable_unified_get_user`, `airtable_unified_list_groups`, `airtable_unified_list_users` `new-actions` Added unified IAM actions for credentials, roles, and resource users (base and workspace collaborators). # Alchemy Source: https://docs.stackone.com/connectors/alchemy/index How to set up the Alchemy connector, plus the actions that are available.
Alchemy
v1.0.0
39 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an Alchemy App API key and a chain subdomain (e.g. \`eth-mainnet\`) that has been enabled on the App. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/alchemy/index.md for the full list. # Alchemy Changelog Source: https://docs.stackone.com/connectors/alchemy/changelog Release history for the Alchemy connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Standardized action category capitalization for more consistent portal filters. `bug-fix` `description-fix` Fixed summarize_nft_attributes — removed the in-flight lowercasing of contractAddress that was regressing every request to 400 'contractAddress should be a valid address', and updated the action, input, and step descriptions to make the EIP-55 checksum requirement explicit so callers pass the correctly-cased address through. Extended get_nft_metadata_batch's description to mirror get_nft_metadata's Network-Subdomain scoping caveat — cross-chain contracts (e.g. Base/Polygon tokens surfaced by the multi-chain Portfolio API) return tokenType NOT_A_CONTRACT when batched into the default-network endpoint. `alchemy_get_nft_metadata_batch`, `alchemy_summarize_nft_attributes` `guide-changes` `connection-testing` `description-fix` `bug-fix` Refined the connection guide against the live Alchemy portal — renamed Default Network to Network Subdomain, switched to an Enable-first flow on the Endpoints page, fixed the alch_ API key placeholder, and tightened auth field descriptions. Replaced the Prices test action with a chain-scoped JSON-RPC probe that validates the API Key, the subdomain, and chain enablement — works across every chain type Alchemy hosts (EVM, Solana, Starknet, Sei, Mantle, Sonic, and future additions). Tightened action descriptions from AGI-17581 findings — get_nft_metadata flags Network-Subdomain scoping (cross-chain contracts return NOT_A_CONTRACT); search_contract_metadata now instructs comparing the returned name/symbol against the user's intent before any downstream use, and refining the query or asking the user on mismatch (beta ranking is not canonical); get_nfts_by_address, get_nft_contracts_by_address, and get_token_balances spell out the hex-only requirement and how to route name-only vs name-plus-hex prompts (prefer hex when both are provided, ask the user or fall back to the single-chain NFT-API sibling when only a name is available). summarize_nft_attributes lowercases contractAddress in-flight so mixed-case inputs that sibling actions accept no longer hit its stricter EIP-55 validation. `alchemy_get_contracts_for_owner`, `alchemy_get_nft_contracts_by_address`, `alchemy_get_nft_metadata`, `alchemy_get_nfts_by_address`, `alchemy_get_nfts_for_owner`, `alchemy_get_token_balances`, `alchemy_search_contract_metadata`, `alchemy_summarize_nft_attributes` `new-connector` `guide-only` Initial release of the Alchemy connector — 39 actions across Portfolio, Token, Transfers, Prices, NFT v3, Utility, and standard EVM JSON-RPC. API key + default network configFields, with a full setup guide covering App creation and network selection. # Algolia Source: https://docs.stackone.com/connectors/algolia/index How to set up the Algolia connector, plus the actions that are available.
Algolia
v1.1.0
42 actions · 1 auth method
Search
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Algolia account using your Application ID and API Key from the Algolia dashboard. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/algolia/index.md for the full list. # Algolia Changelog Source: https://docs.stackone.com/connectors/algolia/changelog Release history for the Algolia connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for indices. `algolia_list_indices` `bug-fix` Fixed the API Key connection guide to match the live dashboard and added screenshots. # Amazon S3 Source: https://docs.stackone.com/connectors/awss3/index How to set up the Amazon S3 connector, plus the actions that are available.
Amazon S3
Previewv1.1.0
89 actions · 1 auth method
Storage
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use AWS IAM Access Keys to authenticate with Amazon S3. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/awss3/index.md for the full list. # Amazon S3 Changelog Source: https://docs.stackone.com/connectors/awss3/changelog Release history for the Amazon S3 connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for buckets, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. List Buckets now always sends a paginated request, so accounts with more than 10,000 buckets are supported. The sync is full-refresh, because the ListBuckets endpoint exposes no updated-since filter a sync can use. # Amplemarket Source: https://docs.stackone.com/connectors/amplemarket/index How to set up the Amplemarket connector, plus the actions that are available.
Amplemarket
v2.3.1
54 actions · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Amplemarket API key for authentication. Generate it from your Amplemarket account settings. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/amplemarket/index.md for the full list. # Amplemarket Changelog Source: https://docs.stackone.com/connectors/amplemarket/changelog Release history for the Amplemarket connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Get unified role returns 404 for a role no user holds, and list unified roles reads the roles held by up to 1,029 users instead of returning one fixed role. Role names are now Amplemarket's own role string. `amplemarket_unified_get_me`, `amplemarket_unified_get_organization`, `amplemarket_unified_get_role`, `amplemarket_unified_get_user`, `amplemarket_unified_list_organizations`, `amplemarket_unified_list_roles`, `amplemarket_unified_list_users` `data-sync` `bug-fix` Added Data Sync support to twelve list actions covering accounts, users, sequences, lead lists, mailboxes, calls, call dispositions, exclusion lists, and unified users, roles and organizations, so these collections can be synced on a schedule. All refresh in full on every run, because Amplemarket exposes no updated-since filter. Also capped the accounts page size at 49 — at exactly 50 Amplemarket omits its next-page link and silently truncates pagination after the first page. `amplemarket_list_accounts`, `amplemarket_list_call_dispositions`, `amplemarket_list_calls`, `amplemarket_list_excluded_domains`, `amplemarket_list_excluded_emails`, `amplemarket_list_lead_lists`, `amplemarket_list_mailboxes`, `amplemarket_list_sequences`, `amplemarket_list_users`, `amplemarket_unified_list_organizations`, `amplemarket_unified_list_roles`, `amplemarket_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, and credentials. `amplemarket_unified_get_me`, `amplemarket_unified_get_organization`, `amplemarket_unified_get_role`, `amplemarket_unified_get_user`, `amplemarket_unified_list_organizations`, `amplemarket_unified_list_roles`, `amplemarket_unified_list_users` `guide-images` Updated API Key guide screenshots — blurred personal info and highlighted the API key field and reveal (eye) icon. `guide` Regenerated the API Key connection guide from a live walkthrough of the Amplemarket portal (Settings > API), replacing the unverified prior version. Covers opening the API settings page, creating a named key, and revealing/copying its value. Deliberately omits the generic "shown once" warning: Amplemarket keys remain re-revealable from the same table at any time, so the guide documents that behavior instead of a false claim. `bug-fix` `description-fix` Fixed list pagination — bracket query params (page[size], page[after], filters) were not resolving and returned empty results; now fixed. Documented list_lead_lists status values, list_tasks inactive-user 400, and list_users primary-email filtering. `amplemarket_get_company_enrichment`, `amplemarket_get_email_validation`, `amplemarket_get_lead_list`, `amplemarket_get_people_enrichment`, `amplemarket_list_accounts`, `amplemarket_list_calls`, `amplemarket_list_contacts`, `amplemarket_list_excluded_domains`, `amplemarket_list_excluded_emails`, `amplemarket_list_job_openings`, `amplemarket_list_lead_lists`, `amplemarket_list_mailboxes`, `amplemarket_list_sequences`, `amplemarket_list_tasks`, `amplemarket_list_users` `new-actions` `new-fields` Added create_contact, list_job_openings, get_job_opening, and review_phone_number, plus missing filter parameters and constraint and enum validation across existing actions. Renamed the four enrichment actions to the provider's operation names (a breaking change to those action IDs). # Amplitude Source: https://docs.stackone.com/connectors/amplitude/index How to set up the Amplitude connector, plus the actions and events that are available.
Amplitude
v1.3.0
63 actions · 4 events · 1 auth method
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Basic authentication using API Key and Secret Key for Amplitude Analytics API access. Optionally, configure receiving Events for Amplitude into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/amplitude/index.md for the full list. ## Events See https://docs.stackone.com/connectors/amplitude/index.md for the full list. # Amplitude Changelog Source: https://docs.stackone.com/connectors/amplitude/changelog Release history for the Amplitude connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Webhook events can now be received from Amplitude Event Streaming and Cohort Webhooks destinations, covering streamed analytics events, user-property updates, and users entering or leaving a synced cohort. `data-sync` Cohorts, events, event types, event categories, user properties, project role assignments, and IAM users, groups, and roles can now be synced. `amplitude_get_event_categories`, `amplitude_get_event_types`, `amplitude_get_events`, `amplitude_get_user_properties`, `amplitude_list_cohorts`, `amplitude_list_project_role_assignments`, `amplitude_unified_list_groups`, `amplitude_unified_list_roles`, `amplitude_unified_list_users` `new-actions` Added identity and access actions for listing Amplitude users, permission groups, and roles, with optional SCIM and organization API keys. # Anaplan Source: https://docs.stackone.com/connectors/anaplan/index How to set up the Anaplan connector, plus the actions that are available.
Anaplan
Betav1.1.0
43 actions · 2 auth methods
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). HTTP Basic authentication using Anaplan username and password. Bearer token authentication for SCIM 2.0 user and group provisioning endpoints. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/anaplan/index.md for the full list. # Anaplan Changelog Source: https://docs.stackone.com/connectors/anaplan/changelog Release history for the Anaplan connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for the two tenant-level collections that need no workspace or model scope - list_workspaces and list_models - so workspace and model inventory can be pulled on a schedule. Both full refresh on every run, because the Anaplan APIs expose no updated-since filter. No change to any action's request behaviour or inputs. # Anthropic Source: https://docs.stackone.com/connectors/anthropic/index How to set up the Anthropic connector, plus the actions and events that are available.
Anthropic
v2.3.0
29 actions · 38 events · 2 auth methods
AI IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Anthropic account using an API key generated from the Anthropic Console. Connect your Anthropic account using an Admin API key to manage organization resources such as users, workspaces, invite... Optionally, configure receiving Events for Anthropic into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/anthropic/index.md for the full list. ## Events See https://docs.stackone.com/connectors/anthropic/index.md for the full list. # Anthropic Changelog Source: https://docs.stackone.com/connectors/anthropic/changelog Release history for the Anthropic connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` create_message and count_tokens accept claude-haiku-5-5 as a model. `anthropic_count_tokens`, `anthropic_create_message` `new-events` Added webhook event support covering the thirty-eight event types Anthropic emits across sessions, vaults and vault credentials, agents, deployments and deployment runs, environments and memory stores. Every event shares one envelope, so each is routed on data.type, reports the resource it concerns as the record id from data.id, and carries the envelope's RFC3339 created_at as the event date. Payloads carry identifiers rather than the resource itself. This connector exposes no actions for these resources, so a consumer that needs the full record fetches it from Anthropic's Managed Agents API by data.id. Webhook endpoints are created by hand in the Claude Console and point at the Native Webhook URL now shown on the linked account; a setup guide walks through that flow with screenshots and lists every event by the group the Console puts it in. The thirteen event types verified against live deliveries - across vaults, vault credentials, environments and memory stores - ship as preview; the twenty-five that could not be triggered on the available accounts ship as beta. `data-sync` Added DataSync support to all nine list actions — API keys, invites, models, organization users, workspaces, and the unified IAM users, groups, organizations and roles — so their records can be synced on a schedule and read back without calling Anthropic each time. Every action refreshes in full on each run, as the Anthropic Admin API exposes no updated-since filter on any list endpoint. `anthropic_list_api_keys`, `anthropic_list_invites`, `anthropic_list_models`, `anthropic_list_users`, `anthropic_list_workspaces`, `anthropic_unified_list_groups`, `anthropic_unified_list_organizations`, `anthropic_unified_list_roles`, `anthropic_unified_list_users` `description-fix` Clarified list_models description to reflect that it returns each model's ID, context window, and token limits but not per-model feature support (image input, PDF input, extended thinking), which is available via get_model. Refreshed get_model modelId example values to current models. `anthropic_get_model`, `anthropic_list_models` `enhancement` `breaking-change` Breaking: scoped actions by auth type — admin API actions (users, workspaces, invites, api_keys, org) now require admin_api_key, messages/models actions require standard API key. Removed old model enum values (claude-opus-4-0, claude-sonnet-4-0, claude-3-haiku-20240307), added latest models (claude-sonnet-5, claude-fable-5, claude-mythos-5, claude-opus-5, claude-opus-4-8, claude-opus-4-7). Improved pagination cursor descriptions for list_models. `anthropic_archive_workspace`, `anthropic_count_tokens`, `anthropic_create_invite`, `anthropic_create_message`, `anthropic_create_workspace`, `anthropic_delete_invite`, `anthropic_get_api_key`, `anthropic_get_invite`, `anthropic_get_model`, `anthropic_get_organization`, `anthropic_get_user`, `anthropic_get_workspace`, `anthropic_list_api_keys`, `anthropic_list_invites`, `anthropic_list_models`, `anthropic_list_users`, `anthropic_list_workspaces`, `anthropic_unified_get_group`, `anthropic_unified_get_me`, `anthropic_unified_get_organization`, `anthropic_unified_get_role`, `anthropic_unified_get_user`, `anthropic_unified_list_groups`, `anthropic_unified_list_organizations`, `anthropic_unified_list_roles`, `anthropic_unified_list_users`, `anthropic_update_api_key`, `anthropic_update_user`, `anthropic_update_workspace` `bug-fix` Fixed unified_get_organization returning an empty body on every call, and unified_list_users/unified_get_user shipping a null last_name on every call. # Apollo Source: https://docs.stackone.com/connectors/apollo/index How to set up the Apollo connector, plus the actions that are available.
Apollo
v1.7.0
57 actions · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key authentication provides programmatic access to Apollo APIs. Generate your API key from Apollo Developer Portal. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/apollo/index.md for the full list. # Apollo Changelog Source: https://docs.stackone.com/connectors/apollo/changelog Release history for the Apollo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` People Enrichment and Bulk People Enrichment now accept poll_only, run_waterfall_email and run_waterfall_phone, so phone and waterfall results no longer need a webhook. Fetch them with the new Poll Webhook Result action. `apollo_get_webhook_result` `apollo_bulk_enrich_people`, `apollo_enrich_person` `bug-fix` Resource owner lookups now read the account or contact directly instead of searching the first 100 (the API key needs the accounts show and contacts show permissions), and role lists and lookups now read up to 5,000 users instead of 100. `apollo_unified_get_role`, `apollo_unified_list_resource_types`, `apollo_unified_list_resource_users`, `apollo_unified_list_roles` `new-feature` `data-sync` Added DataSync support to nineteen list actions across accounts, contacts, deals, tasks, calls, sequences, outreach emails, stages, fields, lists, users and the unified IAM endpoints. All sync by full refresh, as Apollo exposes no updated-since filter. `apollo_get_a_list_of_all_lists`, `apollo_get_a_list_of_email_accounts`, `apollo_get_a_list_of_fields`, `apollo_get_a_list_of_users`, `apollo_list_account_stages`, `apollo_list_all_deals`, `apollo_list_contact_stages`, `apollo_list_deal_stages`, `apollo_organization_search`, `apollo_people_search`, `apollo_search_accounts`, `apollo_search_calls`, `apollo_search_contacts`, `apollo_search_outreach_emails`, `apollo_search_sequences`, `apollo_search_tasks`, `apollo_unified_list_organizations`, `apollo_unified_list_roles`, `apollo_unified_list_users` `bug-fix` Fixed user lists being truncated on large accounts, and user lookups failing for users beyond the first page. `apollo_unified_get_me`, `apollo_unified_get_role`, `apollo_unified_get_user`, `apollo_unified_list_organizations`, `apollo_unified_list_resource_users`, `apollo_unified_list_roles`, `apollo_unified_list_users` `bug-fix` Fixed base URL to include the /api path segment required by the Apollo API. `apollo_activate_sequence`, `apollo_add_contacts_to_sequence`, `apollo_archive_sequence`, `apollo_bulk_create_tasks`, `apollo_bulk_enrich_organizations`, `apollo_bulk_enrich_people`, `apollo_check_email_stats`, `apollo_create_account`, `apollo_create_call_record`, `apollo_create_contact`, `apollo_create_custom_field`, `apollo_create_deal`, `apollo_create_task`, `apollo_deactivate_sequence`, `apollo_enrich_organization`, `apollo_enrich_person`, `apollo_get_a_list_of_all_lists`, `apollo_get_a_list_of_email_accounts`, `apollo_get_a_list_of_fields`, `apollo_get_a_list_of_users`, `apollo_get_api_usage_stats`, `apollo_get_complete_organization_info`, `apollo_get_organization_job_postings`, `apollo_list_account_stages`, `apollo_list_all_deals`, `apollo_list_contact_stages`, `apollo_list_deal_stages`, `apollo_news_articles_search`, `apollo_organization_search`, `apollo_people_search`, `apollo_search_accounts`, `apollo_search_calls`, `apollo_search_contacts`, `apollo_search_outreach_emails`, `apollo_search_sequences`, `apollo_search_tasks`, `apollo_unified_get_me`, `apollo_unified_get_organization`, `apollo_unified_get_role`, `apollo_unified_get_user`, `apollo_unified_list_organizations`, `apollo_unified_list_resource_types`, `apollo_unified_list_resource_users`, `apollo_unified_list_roles`, `apollo_unified_list_users`, `apollo_update_account`, `apollo_update_account_owners`, `apollo_update_call_record`, `apollo_update_contact`, `apollo_update_contact_owners`, `apollo_update_contact_stages`, `apollo_update_contact_status_in_sequence`, `apollo_update_deal`, `apollo_view_account`, `apollo_view_contact`, `apollo_view_deal` `improvement` Renamed actions to match provider API naming conventions. Added linkedin_url, name, website, and details parameters to organization enrichment actions. `apollo_get_a_list_of_all_lists`, `apollo_get_a_list_of_email_accounts`, `apollo_get_a_list_of_fields`, `apollo_get_a_list_of_users`, `apollo_get_complete_organization_info`, `apollo_list_all_deals`, `apollo_news_articles_search`, `apollo_organization_search`, `apollo_people_search` `apollo_get_organization`, `apollo_list_deals`, `apollo_list_email_accounts`, `apollo_list_fields`, `apollo_list_lists`, `apollo_list_users`, `apollo_search_news_articles`, `apollo_search_organizations`, `apollo_search_people` `apollo_bulk_enrich_organizations`, `apollo_enrich_organization` `improvement` `bug-fix` Fixed user and role lookups returning an empty result instead of a not-found error. Restored general availability status. `apollo_unified_get_role`, `apollo_unified_get_user` `bug-fix` Fixed the IAM users list returning a duplicate first page and failing when the caller followed the next cursor. # Apple Business Manager Source: https://docs.stackone.com/connectors/applebusinessmanager/index How to set up the Apple Business Manager connector, plus the actions that are available.
Apple Business Manager
Previewv0.1.0
14 actions · 1 auth method
IAM Device Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an Apple Business API account, a client id plus a client assertion JWT that the customer signs offline with Apple's... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/applebusinessmanager/index.md for the full list. # Apple Business Manager Changelog Source: https://docs.stackone.com/connectors/applebusinessmanager/changelog Release history for the Apple Business Manager connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Adds an Apple Business Manager connector that reads users, user groups and organizational units, including unified IAM users, groups and organizations. # Apploi Source: https://docs.stackone.com/connectors/apploi/index How to set up the Apploi connector, plus the actions that are available.
Apploi
Betav1.1.0
25 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Apploi uses a partner API key sent in the X-Api-Key header. Your API key is issued by Apploi when you register as a part... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/apploi/index.md for the full list. # Apploi Changelog Source: https://docs.stackone.com/connectors/apploi/changelog Release history for the Apploi connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for job cities and job industries, so their records can be periodically pulled into StackOne and kept up to date. All syncs are full-refresh, because their endpoints expose no updated-since filter a sync can use. # ApprovalMax Source: https://docs.stackone.com/connectors/approvalmax/index How to set up the ApprovalMax connector, plus the actions that are available.
ApprovalMax
v1.3.0
70 actions · 1 auth method
Accounting IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Login to your ApprovalMax account to connect your data. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/approvalmax/index.md for the full list. # ApprovalMax Changelog Source: https://docs.stackone.com/connectors/approvalmax/changelog Release history for the ApprovalMax connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for the companies collection, covering both list_companies and unified_list_organizations. `approvalmax_list_companies`, `approvalmax_unified_list_organizations` `bug-fix` unified_get_user no longer requires filter.organization_id. The companyId is now encoded into the user's id (returned by unified_list_users), so get_user resolves the owning company from the id alone. `approvalmax_auth_test`, `approvalmax_unified_get_me`, `approvalmax_unified_get_organization`, `approvalmax_unified_get_user`, `approvalmax_unified_list_organizations`, `approvalmax_unified_list_users` `new-actions` Added unified IAM actions for users, organizations, and credentials, each gated with an action-level releaseStage (all six actions preview pending full post-merge QA). Fixed unified_get_me returning scopes as a space-delimited string instead of an array, and missing name/email mapping. # Articulate Source: https://docs.stackone.com/connectors/articulate/index How to set up the Articulate connector, plus the actions and events that are available.
Articulate
v1.1.0
37 actions · 4 events · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Reach 360 API key sent as a bearer token. The key inherits the permissions of the admin who generated it, and acc... Optionally, configure receiving Events for Articulate into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/articulate/index.md for the full list. ## Events See https://docs.stackone.com/connectors/articulate/index.md for the full list. # Articulate Changelog Source: https://docs.stackone.com/connectors/articulate/changelog Release history for the Articulate connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added native webhook support for course completed, course submitted, enrollments created, and user created events, provisioned automatically when the account is connected. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `new-feature` Added Data Sync support for List Users, List Courses, List Groups, List Learning Paths, and List Invitations, so these resources can be synced into StackOne on a schedule and read without calling Reach 360. All run as a full refresh on every sync, because the Reach 360 API offers no last-updated filter. `articulate_list_courses`, `articulate_list_groups`, `articulate_list_invitations`, `articulate_list_learning_paths`, `articulate_list_users` `guide-changes` Improved the API Key connection guide — added guidance to scroll to the API keys section in Settings, and the Hub connection guide button now links to the StackOne connection guide. `bug-fix` Clarified the List Users email filter so looking up a user by name works without errors. `articulate_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `articulate_add_user_to_group`, `articulate_create_group`, `articulate_create_invitation`, `articulate_delete_group`, `articulate_delete_invitation`, `articulate_delete_user`, `articulate_enroll_group_in_course`, `articulate_enroll_group_in_learning_path`, `articulate_enroll_user_in_course`, `articulate_enroll_user_in_learning_path`, `articulate_get_activity_report`, `articulate_get_course`, `articulate_get_course_report`, `articulate_get_group`, `articulate_get_group_courses_report`, `articulate_get_invitation`, `articulate_get_learner_report`, `articulate_get_learning_path`, `articulate_get_learning_path_courses_report`, `articulate_get_learning_path_learners_report`, `articulate_get_user`, `articulate_import_course_completion`, `articulate_list_courses`, `articulate_list_group_members`, `articulate_list_groups`, `articulate_list_invitations`, `articulate_list_learning_path_courses`, `articulate_list_learning_paths`, `articulate_list_user_favorites`, `articulate_list_user_groups`, `articulate_list_users`, `articulate_remove_user_from_group`, `articulate_unenroll_group_from_course`, `articulate_unenroll_group_from_learning_path`, `articulate_unenroll_user_from_course`, `articulate_unenroll_user_from_learning_path`, `articulate_update_group` `guide` Updated the API Key connection guide with step-by-step Reach 360 instructions and screenshots. `new-connector` Initial preview release of the Articulate Reach 360 connector — users, groups, group memberships, invitations, courses, learning paths, enrollments, completion imports, and learner activity reporting. # arXiv Source: https://docs.stackone.com/connectors/arxiv/index How to set up the arXiv connector, plus the actions that are available.
arXiv
v1.1.0
8 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). arXiv's Query API and OAI-PMH interface are fully open with no authentication. Respect the recommended cadence of 1 requ... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/arxiv/index.md for the full list. # arXiv Changelog Source: https://docs.stackone.com/connectors/arxiv/changelog Release history for the arXiv connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for the two OAI-PMH reference collections (oai_list_sets and oai_list_metadata_formats), so the arXiv subject taxonomy and supported metadata formats can be harvested on a schedule. No change to any action's request behaviour or validation. `arxiv_oai_list_metadata_formats`, `arxiv_oai_list_sets` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `new-connector` Initial release of the arXiv connector covering the Query API (keyword search, get by ID) and the OAI-PMH v2.0 interface (Identify, ListMetadataFormats, ListSets, ListRecords, ListIdentifiers, GetRecord, plus resumption-token continuation for records and identifiers) — 10 actions total, no authentication required. # Asana Source: https://docs.stackone.com/connectors/asana/index How to set up the Asana connector, plus the actions and events that are available.
Asana
v2.0.0
126 actions · 10 events · 3 auth methods
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for personal scripts, testing, and single-user integrations. Quick to set up, no app registration required. Requires an Asana Enterprise or Enterprise+ organization and a super admin to create the Service Account. Org-level bot... Requires registering an app in the Asana Developer Console. Supports granular scopes per resource type. Optionally, configure receiving Events for Asana into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/asana/index.md for the full list. ## Events See https://docs.stackone.com/connectors/asana/index.md for the full list. # Asana Changelog Source: https://docs.stackone.com/connectors/asana/changelog Release history for the Asana connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Added a Service Account Token connection (beta) for Enterprise+ organizations. Audit log events and organization exports now run only on this connection, as Asana rejects personal access and OAuth tokens for them, and all actions now declare per-connection auth requirements. `asana_add_custom_field_to_portfolio`, `asana_add_custom_field_to_project`, `asana_add_dependencies`, `asana_add_dependents`, `asana_add_followers_to_project`, `asana_add_followers_to_task`, `asana_add_item_to_portfolio`, `asana_add_members_to_project`, `asana_add_project_to_task`, `asana_add_subgoal`, `asana_add_tag_to_task`, `asana_add_task_to_section`, `asana_add_user_to_team`, `asana_add_user_to_workspace`, `asana_create_custom_field`, `asana_create_enum_option`, `asana_create_goal`, `asana_create_membership`, `asana_create_organization_export`, `asana_create_portfolio`, `asana_create_project`, `asana_create_section`, `asana_create_status_update`, `asana_create_story`, `asana_create_subtask`, `asana_create_tag`, `asana_create_task`, `asana_create_time_tracking_entry`, `asana_create_webhook`, `asana_delete_attachment`, `asana_delete_goal`, `asana_delete_membership`, `asana_delete_portfolio`, `asana_delete_project`, `asana_delete_section`, `asana_delete_status_update`, `asana_delete_story`, `asana_delete_task`, `asana_delete_time_tracking_entry`, `asana_delete_webhook`, `asana_duplicate_project`, `asana_duplicate_task`, `asana_get_attachment`, `asana_get_audit_log_events`, `asana_get_current_user`, `asana_get_custom_field`, `asana_get_events`, `asana_get_goal`, `asana_get_membership`, `asana_get_organization_export`, `asana_get_portfolio`, `asana_get_portfolio_items`, `asana_get_project`, `asana_get_project_tasks`, `asana_get_project_template`, `asana_get_section`, `asana_get_status_update`, `asana_get_story`, `asana_get_tag`, `asana_get_task`, `asana_get_task_template`, `asana_get_tasks_from_user_task_list`, `asana_get_team`, `asana_get_team_users`, `asana_get_time_period`, `asana_get_time_tracking_entry`, `asana_get_user`, `asana_get_user_favorites`, `asana_get_user_task_list`, `asana_get_user_team_memberships`, `asana_get_user_teams`, `asana_get_user_workspace_memberships`, `asana_get_webhook`, `asana_get_workspace`, `asana_instantiate_project_template`, `asana_instantiate_task_from_template`, `asana_list_attachments`, `asana_list_custom_fields`, `asana_list_goals`, `asana_list_memberships`, `asana_list_portfolios`, `asana_list_project_templates`, `asana_list_projects`, `asana_list_sections`, `asana_list_status_updates`, `asana_list_stories`, `asana_list_subtasks`, `asana_list_tags`, `asana_list_task_templates`, `asana_list_tasks`, `asana_list_teams`, `asana_list_time_periods`, `asana_list_time_tracking_entries`, `asana_list_users`, `asana_list_webhooks`, `asana_list_workspaces`, `asana_remove_custom_field_from_portfolio`, `asana_remove_custom_field_from_project`, `asana_remove_dependencies`, `asana_remove_dependents`, `asana_remove_followers_from_project`, `asana_remove_followers_from_task`, `asana_remove_item_from_portfolio`, `asana_remove_members_from_project`, `asana_remove_project_from_task`, `asana_remove_subgoal`, `asana_remove_tag_from_task`, `asana_remove_user_from_team`, `asana_remove_user_from_workspace`, `asana_search_tasks`, `asana_set_parent_task`, `asana_typeahead_search`, `asana_update_custom_field`, `asana_update_enum_option`, `asana_update_goal`, `asana_update_membership`, `asana_update_portfolio`, `asana_update_project`, `asana_update_section`, `asana_update_story`, `asana_update_tag`, `asana_update_task`, `asana_update_team`, `asana_update_time_tracking_entry`, `asana_update_webhook`, `asana_update_workspace` `data-sync` `bug-fix` Added data sync support for users, teams, projects, tags, custom fields, time periods, goals, and audit log events (audit logs sync incrementally by event time). List actions now return 100 results per page by default when no limit is set, so large workspaces paginate reliably. `asana_get_audit_log_events`, `asana_list_custom_fields`, `asana_list_goals`, `asana_list_projects`, `asana_list_tags`, `asana_list_teams`, `asana_list_time_periods`, `asana_list_users` `new-events` Added webhook event support for task (added/changed/removed/deleted), story (added/removed), section (added/changed), and project (added) events. Uses programmatic hybrid registration — a workspace-scoped subscription for project creation plus per-project subscriptions (via the new projectIds config field) for task/story/section events, since Asana does not propagate those to workspace-level webhooks. The X-Hook-Secret establishment handshake is completed automatically. # Ashby Source: https://docs.stackone.com/connectors/ashby/index How to set up the Ashby connector, plus the actions that are available.
Ashby
v3.0.3
138 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key authentication. Requires Admin privileges to generate a key. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ashby/index.md for the full list. # Ashby Changelog Source: https://docs.stackone.com/connectors/ashby/changelog Release history for the Ashby connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified how to link feedback to a scheduled interview so Ashby marks it as submitted, and which API key permission private notes need. `ashby_add_candidate_project`, `ashby_create_candidate_note_as_object`, `ashby_create_candidate_note_as_string`, `ashby_list_interview_events`, `ashby_remove_candidate_project`, `ashby_submit_application_feedback` `bug-fix` Fixed prerequisiteActions placement on application lookup action. `ashby_get_application_by_id`, `ashby_get_application_by_submitted_form_instance_id` `bug-fix` Form submissions and custom field updates now accept scores, checkboxes, multi-selects, rich text, locations and compensation amounts, which previously failed because only plain text was allowed. `ashby_create_offer`, `ashby_create_referral`, `ashby_set_custom_field_value`, `ashby_set_custom_field_values`, `ashby_submit_application_feedback`, `ashby_update_offer` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. `ashby_add_application_hiring_team_member`, `ashby_add_assessment_to_candidate`, `ashby_add_candidate_project`, `ashby_add_candidate_tag`, `ashby_add_email_message`, `ashby_add_hiring_team_member_to_application`, `ashby_add_hiring_team_member_to_job`, `ashby_add_hiring_team_member_to_opening`, `ashby_add_job_to_opening`, `ashby_add_opening_location`, `ashby_anonymize_candidate`, `ashby_approve_offer`, `ashby_archive_department`, `ashby_archive_location`, `ashby_cancel_interview_schedule`, `ashby_change_application_source`, `ashby_change_application_stage`, `ashby_create_application`, `ashby_create_candidate`, `ashby_create_candidate_note_as_object`, `ashby_create_candidate_note_as_string`, `ashby_create_candidate_tag`, `ashby_create_custom_field`, `ashby_create_department`, `ashby_create_interview_schedule`, `ashby_create_job`, `ashby_create_location`, `ashby_create_offer`, `ashby_create_opening`, `ashby_create_referral`, `ashby_create_survey_request`, `ashby_create_survey_submission`, `ashby_create_webhook`, `ashby_delete_webhook`, `ashby_generate_report`, `ashby_generate_report_synchronous`, `ashby_get_application_by_id`, `ashby_get_application_by_submitted_form_instance_id`, `ashby_get_candidate_by_external_mapping_id`, `ashby_get_candidate_by_id`, `ashby_get_custom_field`, `ashby_get_department`, `ashby_get_feedback_form_definition`, `ashby_get_file`, `ashby_get_interview`, `ashby_get_interview_stage`, `ashby_get_job`, `ashby_get_job_posting`, `ashby_get_location`, `ashby_get_offer`, `ashby_get_opening`, `ashby_get_project`, `ashby_get_referral_form`, `ashby_get_survey_form_definition`, `ashby_get_user`, `ashby_get_user_interviewer_settings`, `ashby_get_webhook`, `ashby_list_application_feedback`, `ashby_list_application_history`, `ashby_list_applications`, `ashby_list_approvals`, `ashby_list_archive_reasons`, `ashby_list_audit_log`, `ashby_list_brands`, `ashby_list_candidate_client_info`, `ashby_list_candidate_notes`, `ashby_list_candidate_projects`, `ashby_list_candidate_tags`, `ashby_list_candidates`, `ashby_list_close_reasons`, `ashby_list_communication_templates`, `ashby_list_custom_fields`, `ashby_list_departments`, `ashby_list_feedback_form_definitions`, `ashby_list_hiring_team_roles`, `ashby_list_interview_events`, `ashby_list_interview_plans`, `ashby_list_interview_schedules`, `ashby_list_interview_stage_groups`, `ashby_list_interview_stages`, `ashby_list_interviewer_pools`, `ashby_list_interviews`, `ashby_list_job_boards`, `ashby_list_job_postings`, `ashby_list_job_templates`, `ashby_list_jobs`, `ashby_list_locations`, `ashby_list_offers`, `ashby_list_openings`, `ashby_list_projects`, `ashby_list_source_tracking_links`, `ashby_list_sources`, `ashby_list_survey_requests`, `ashby_list_survey_submissions`, `ashby_list_users`, `ashby_move_department`, `ashby_move_location`, `ashby_remove_application_hiring_team_member`, `ashby_remove_candidate_project`, `ashby_remove_candidate_tag`, `ashby_remove_job_from_opening`, `ashby_remove_opening_location`, `ashby_restore_department`, `ashby_restore_location`, `ashby_search_candidates`, `ashby_search_jobs`, `ashby_search_openings`, `ashby_search_projects`, `ashby_search_users`, `ashby_set_custom_field_value`, `ashby_set_custom_field_values`, `ashby_set_job_status`, `ashby_set_opening_archived`, `ashby_set_opening_state`, `ashby_start_offer`, `ashby_start_offer_process`, `ashby_submit_application_feedback`, `ashby_transfer_application`, `ashby_update_application`, `ashby_update_application_history`, `ashby_update_approval_definition`, `ashby_update_candidate`, `ashby_update_custom_field_selectable_values`, `ashby_update_department`, `ashby_update_interview_schedule`, `ashby_update_job`, `ashby_update_job_compensation`, `ashby_update_job_posting`, `ashby_update_location_address`, `ashby_update_location_external_name`, `ashby_update_location_name`, `ashby_update_location_workplace_type`, `ashby_update_offer`, `ashby_update_opening`, `ashby_update_user_interviewer_settings`, `ashby_update_webhook`, `ashby_upload_candidate_file_complete`, `ashby_upload_candidate_resume_complete` Added Data Sync support to 27 list actions, so candidates, applications, jobs, users and related records can be periodically synced into StackOne. Most resources sync incrementally using Ashby's sync tokens, fetching only records changed since the previous sync. # Attentive Source: https://docs.stackone.com/connectors/attentive/index How to set up the Attentive connector, plus the actions that are available.
Attentive
v1.1.0
19 actions · 1 auth method
Marketing Messaging E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key by creating a Private app in your Attentive account. Requires admin privileges. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/attentive/index.md for the full list. # Attentive Changelog Source: https://docs.stackone.com/connectors/attentive/changelog Release history for the Attentive connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled Data Sync to the catalog uploads collection, so recent product catalog uploads can be kept in sync and searched without calling Attentive on every request. The sync refreshes in full on every run, because the endpoint exposes no updated-since filter. `attentive_list_catalog_uploads` `bug-fix` Fixed bulk opt-in (removed unsupported subscriptionType), added required salesChannel.channelType on purchase events, corrected eCommerce doc URLs, and improved the API key connection guide with screenshots. # Attio Source: https://docs.stackone.com/connectors/attio/index How to set up the Attio connector, plus the actions and events that are available.
Attio
v1.4.0
68 actions · 27 events · 2 auth methods
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth app in Attio. Best for single-workspace integrations and internal tools. Provides full API access scoped to your workspace. Optionally, configure receiving Events for Attio into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/attio/index.md for the full list. ## Events See https://docs.stackone.com/connectors/attio/index.md for the full list. # Attio Changelog Source: https://docs.stackone.com/connectors/attio/changelog Release history for the Attio connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to eleven collection actions — people, companies, tasks, notes, lists, objects, webhooks and workspace members, plus the unified users, roles and organizations — so these collections can be kept in sync and searched without calling Attio on every request. People, companies, tasks, notes and webhooks page through results automatically; the remaining collections are returned in full by a single request. All syncs use full refreshes because Attio's updated-since filter is available only as a nested query expression. `attio_list_companies`, `attio_list_lists`, `attio_list_notes`, `attio_list_objects`, `attio_list_people`, `attio_list_tasks`, `attio_list_webhooks`, `attio_list_workspace_members`, `attio_unified_list_organizations`, `attio_unified_list_roles`, `attio_unified_list_users` `new-actions` Added webhook event support for record, list, list-entry, note, task, comment, attribute, workspace-member, and call-recording events (27 events) with programmatic webhook registration. `new-actions` Added unified IAM actions for users, roles, organizations, resource users, and credentials. # Auth0 Source: https://docs.stackone.com/connectors/auth0/index How to set up the Auth0 connector, plus the actions and events that are available.
Auth0
v1.3.0
87 actions · 25 events · 2 auth methods
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 client credentials with a regular web application. Connect using a Management API token generated in the Auth0 dashboard. Tokens expire after 24 hours by default; for prod... Optionally, configure receiving Events for Auth0 into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/auth0/index.md for the full list. ## Events See https://docs.stackone.com/connectors/auth0/index.md for the full list. # Auth0 Changelog Source: https://docs.stackone.com/connectors/auth0/changelog Release history for the Auth0 connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added webhook support through Auth0 Event Streams, covering the twenty-five event types a tenant emits across connections, groups, organizations and users. StackOne creates the event stream automatically when an account is connected and deletes it on disconnect, subscribing it to exactly the events enabled rather than every type. Auth0 delivers CloudEvents envelopes, so each event is routed on the CloudEvent type and carries the RFC3339 time as its event date. The record id follows the resource the event concerns - the connection, group or organization for their own lifecycle events, the parent group or organization for membership and role changes, and user_id for user events. `bug-fix` Role lists now page past the first 100 roles, and user lists with roles read every role each user holds instead of stopping at 20 roles. `auth0_unified_list_roles`, `auth0_unified_list_users` `data-sync` `new-feature` Added DataSync support to 23 list actions covering users, roles, organizations, connections, rules, forms, grants, logs, and the unified IAM lists. All resources sync as full refreshes, because the Auth0 Management API exposes no updated-since filter for incremental sync. `auth0_get_connections`, `auth0_get_forms`, `auth0_get_grants`, `auth0_get_log_streams`, `auth0_get_logs`, `auth0_get_organizations`, `auth0_get_roles`, `auth0_get_rules`, `auth0_get_users`, `auth0_unified_list_organizations`, `auth0_unified_list_resource_users`, `auth0_unified_list_roles`, `auth0_unified_list_users` `bug-fix` Reduced the number of Auth0 API calls when listing large numbers of users. User lists now page on demand instead of re-fetching every earlier page, lowering the risk of hitting Auth0 rate limits on large tenants. `auth0_unified_get_me`, `auth0_unified_get_user`, `auth0_unified_list_organizations`, `auth0_unified_list_resource_users`, `auth0_unified_list_roles`, `auth0_unified_list_users` `bug-fix` Fixed unified_list_users mislabeling every MFA-enrolled user as TOTP; added accurate per-factor MFA data to unified_get_user via the enrollments endpoint. # Autodesk Source: https://docs.stackone.com/connectors/autodesk/index How to set up the Autodesk connector, plus the actions that are available.
Autodesk
Previewv4.0.1
65 actions · 2 auth methods
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connects on behalf of a specific Autodesk user. Best suited for accessing files, folders, hubs, projects, and webhooks w... Connects as your application without an end user signing in. Best suited for BIM 360 account administration — managing u... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/autodesk/index.md for the full list. # Autodesk Changelog Source: https://docs.stackone.com/connectors/autodesk/changelog Release history for the Autodesk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed version URN encoding for get_version, get_version_download_formats, and get_version_downloads. Made x-user-id required for update_project_user. Improved delete_bucket response and webhook expiry descriptions. `autodesk_create_webhook`, `autodesk_delete_bucket`, `autodesk_get_version`, `autodesk_get_version_download_formats`, `autodesk_get_version_downloads`, `autodesk_update_project_user`, `autodesk_update_webhook` `bug-fix` Remove list_buckets and list_webhooks from oauth2_client_credentials testActions `data-sync` Added DataSync support for account users, account companies, and hubs. Fixed the two-legged authentication guide to reference the correct application type. `autodesk_list_account_companies`, `autodesk_list_account_users`, `autodesk_list_hubs` `guides` Fixed the two-legged authentication guide to reference the correct application type (Traditional Web App) and improved guide language for clarity. `new-actions` `bug-fix` Added identity and access management data covering BIM 360 / ACC users, roles, companies as groups, the account as an organization, project membership, and the connected identity. Fixed the authentication configuration on several actions so they no longer ask for the wrong credentials. `autodesk_unified_get_group`, `autodesk_unified_get_me`, `autodesk_unified_get_organization`, `autodesk_unified_get_role`, `autodesk_unified_get_user`, `autodesk_unified_list_groups`, `autodesk_unified_list_organizations`, `autodesk_unified_list_resource_types`, `autodesk_unified_list_resource_users`, `autodesk_unified_list_roles`, `autodesk_unified_list_users` `guide-improvements` Updated Select APIs guide step to clarify that all APIs are enabled by default. Corrected guide language for both three-legged and two-legged OAuth flows. `enhancements` Migrated all actions from requiredScopes to authRequirements for per-auth-type scope and auth type filtering. `autodesk_create_account_company`, `autodesk_create_account_project`, `autodesk_create_account_user`, `autodesk_create_bucket`, `autodesk_create_business_units`, `autodesk_create_folder`, `autodesk_create_item`, `autodesk_create_project_user`, `autodesk_create_storage`, `autodesk_create_version`, `autodesk_create_webhook`, `autodesk_delete_bucket`, `autodesk_delete_object`, `autodesk_delete_webhook`, `autodesk_get_account_company`, `autodesk_get_account_user`, `autodesk_get_bucket_details`, `autodesk_get_folder`, `autodesk_get_hub`, `autodesk_get_item`, `autodesk_get_item_tip`, `autodesk_get_project`, `autodesk_get_signed_s3_download_url`, `autodesk_get_signed_s3_upload_urls`, `autodesk_get_version`, `autodesk_get_version_download_formats`, `autodesk_get_version_downloads`, `autodesk_get_webhook`, `autodesk_list_account_companies`, `autodesk_list_account_projects`, `autodesk_list_account_users`, `autodesk_list_bucket_objects`, `autodesk_list_buckets`, `autodesk_list_business_units`, `autodesk_list_folder_contents`, `autodesk_list_hubs`, `autodesk_list_item_versions`, `autodesk_list_project_industry_roles`, `autodesk_list_project_users`, `autodesk_list_projects`, `autodesk_list_top_folders`, `autodesk_list_webhooks`, `autodesk_list_webhooks_by_system`, `autodesk_search_folder`, `autodesk_signed_s3_upload`, `autodesk_update_account_company`, `autodesk_update_account_project`, `autodesk_update_account_user`, `autodesk_update_folder`, `autodesk_update_item`, `autodesk_update_project_user`, `autodesk_update_webhook`, `autodesk_upload_file_in_project_folder`, `autodesk_upload_to_s3` `bug-fixes` Removed non-persisted fields from create_account_user, commented out ignored offset and language params, added preview stage to untestable actions. # Autumn Source: https://docs.stackone.com/connectors/autumn/index How to set up the Autumn connector, plus the actions and events that are available.
Autumn
v1.0.0
62 actions · 5 events · 1 auth method
Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a server-side secret key (am\_sk\_) sent as a bearer token. Use an am\_sk\_test\_ key to target the sandbox. No OAuth or... Optionally, configure receiving Events for Autumn into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/autumn/index.md for the full list. ## Events See https://docs.stackone.com/connectors/autumn/index.md for the full list. # Autumn Changelog Source: https://docs.stackone.com/connectors/autumn/changelog Release history for the Autumn connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `autumn_aggregate_events`, `autumn_attach_plan`, `autumn_batch_track_usage`, `autumn_check_entitlement`, `autumn_create_balance`, `autumn_create_entity`, `autumn_create_feature`, `autumn_create_plan`, `autumn_create_referral_code`, `autumn_create_referral_program`, `autumn_create_reward`, `autumn_create_schedule`, `autumn_delete_balance`, `autumn_delete_customer`, `autumn_delete_entity`, `autumn_delete_feature`, `autumn_delete_plan`, `autumn_delete_referral_program`, `autumn_delete_reward`, `autumn_finalize_lock`, `autumn_get_customer`, `autumn_get_entity`, `autumn_get_feature`, `autumn_get_or_create_customer`, `autumn_get_plan`, `autumn_get_referral_program`, `autumn_get_reward`, `autumn_import_billing`, `autumn_insert_invoices`, `autumn_list_customers`, `autumn_list_entities`, `autumn_list_events`, `autumn_list_features`, `autumn_list_invoices`, `autumn_list_license_assignments`, `autumn_list_licenses`, `autumn_list_plans`, `autumn_list_referral_programs`, `autumn_list_rewards`, `autumn_mint_key`, `autumn_multi_attach`, `autumn_open_customer_portal`, `autumn_preview_attach`, `autumn_preview_multi_attach`, `autumn_preview_multi_update`, `autumn_preview_update`, `autumn_redeem_referral_code`, `autumn_redeem_reward_code`, `autumn_revoke_key`, `autumn_setup_payment`, `autumn_track_token_usage`, `autumn_track_usage`, `autumn_update_balance`, `autumn_update_customer`, `autumn_update_entity`, `autumn_update_feature`, `autumn_update_plan`, `autumn_update_referral_program`, `autumn_update_reward`, `autumn_update_subscription` `data-sync` Added Data Sync support for customers, entities, events, features, invoices, plans and referral programs, so these collections can be kept in sync on a schedule. Customers, entities, events and invoices page through Autumn's start_cursor and next_cursor tokens; features, plans and referral programs are returned in full by the API in a single call. Each sync is a full refresh. Rewards are not synced, because that endpoint returns coupons and feature grants as two separate lists. `autumn_list_customers`, `autumn_list_entities`, `autumn_list_events`, `autumn_list_features`, `autumn_list_invoices`, `autumn_list_plans`, `autumn_list_referral_programs` `breaking` Removed the multi-update subscription action. Autumn's endpoint accepts every request and applies nothing, so the action could only ever report success without cancelling or uncancelling anything — use the single subscription update action instead, once per subscription. `autumn_multi_update` `autumn_create_feature`, `autumn_list_plans`, `autumn_preview_multi_update`, `autumn_update_feature`, `autumn_update_subscription` `description-fix` Clarified that plan and feature identifiers must be IDs rather than display names and that a feature's label should be resolved with a lookup first, documented that recalculating balances on delete also requires a feature ID, mirrored the refund and proration mutual-exclusion rules onto the multi-update preview, noted that tiered credit schemas must be configured in the Autumn dashboard and that a reset interval is ignored on continuous-use features, and distinguished the single-record and list read actions. `autumn_attach_plan`, `autumn_create_balance`, `autumn_create_feature`, `autumn_create_schedule`, `autumn_delete_balance`, `autumn_get_customer`, `autumn_get_feature`, `autumn_multi_attach`, `autumn_multi_update`, `autumn_preview_attach`, `autumn_preview_multi_attach`, `autumn_preview_multi_update`, `autumn_preview_update`, `autumn_setup_payment`, `autumn_update_feature`, `autumn_update_subscription` `guide-changes` Added the Autumn dashboard URL to the API Key connection guide, corrected the Secret Key field description to point to Developer > API Keys and the environment switcher, and removed the external support link so the Connection guide button opens the StackOne guide. `description-fix` Clarified action descriptions from MCP agent testing. create_schedule now tells callers to reuse a fresh server timestamp (get_or_create_customer's created_at) for the first phase instead of guessing the current time; credit_schema is required for credit_system and rejected on ai_credit_system; track_token_usage.model_id needs the models.dev provider/model form; proration requires both on_increase and on_decrease; import_billing takes a plan id, not a display name; and a price needs exactly one of amount or tiers. `autumn_aggregate_events`, `autumn_attach_license`, `autumn_attach_plan`, `autumn_batch_track_usage`, `autumn_check_entitlement`, `autumn_create_balance`, `autumn_create_entity`, `autumn_create_feature`, `autumn_create_plan`, `autumn_create_referral_code`, `autumn_create_referral_program`, `autumn_create_reward`, `autumn_create_schedule`, `autumn_delete_balance`, `autumn_delete_customer`, `autumn_delete_entity`, `autumn_delete_feature`, `autumn_delete_plan`, `autumn_delete_referral_program`, `autumn_delete_reward`, `autumn_get_customer`, `autumn_get_entity`, `autumn_get_feature`, `autumn_get_or_create_customer`, `autumn_get_plan`, `autumn_get_referral_program`, `autumn_get_reward`, `autumn_import_billing`, `autumn_insert_invoices`, `autumn_list_entities`, `autumn_list_events`, `autumn_list_invoices`, `autumn_list_license_assignments`, `autumn_list_licenses`, `autumn_list_plans`, `autumn_mint_key`, `autumn_multi_attach`, `autumn_multi_update`, `autumn_open_customer_portal`, `autumn_preview_attach`, `autumn_preview_multi_attach`, `autumn_preview_multi_update`, `autumn_preview_update`, `autumn_redeem_referral_code`, `autumn_redeem_reward_code`, `autumn_release_license`, `autumn_revoke_key`, `autumn_setup_payment`, `autumn_track_token_usage`, `autumn_track_usage`, `autumn_update_balance`, `autumn_update_customer`, `autumn_update_entity`, `autumn_update_feature`, `autumn_update_plan`, `autumn_update_referral_program`, `autumn_update_reward`, `autumn_update_subscription` `new-actions` Initial Autumn connector with 64 actions across billing, balances, customers, entities, plans, features, referrals, rewards, licenses, keys, invoices, and events. Live-tested against the Autumn sandbox. Added the API Key connection guide and inbound webhook events (Svix-delivered). Doc-audit fixes — plan_id/new_plan_id/currency constraints and removal of the non-existent create_plan version param, and added track_token_usage timestamp/overage_behavior/async params; exposed optional start_cursor on paginated lists; enforced default_markup min via rules; removed deprecated create_schedule preserve_add_ons param; fixed nested price amount/currency/tier types, batch_track raw-array spread, create_reward duration.length, and documented provider cross-field rules. # Auvik Source: https://docs.stackone.com/connectors/auvik/index How to set up the Auvik connector, plus the actions and events that are available.
Auvik
v1.2.0
50 actions · 1 event · 1 auth method
Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Auvik account username and that user's API key as the password. The user must have the role permi... Optionally, configure receiving Events for Auvik into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/auvik/index.md for the full list. ## Events See https://docs.stackone.com/connectors/auvik/index.md for the full list. # Auvik Changelog Source: https://docs.stackone.com/connectors/auvik/changelog Release history for the Auvik connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Enabled Data Sync on seven list actions: alerts, device info, device details, interface info, network info, network details and tenants. Device info, interface info, network info and network details sync incrementally using the provider's modified-after filter; alerts, device details and tenants full-refresh. `auvik_list_alerts`, `auvik_list_devices_details`, `auvik_list_devices_info`, `auvik_list_interfaces_info`, `auvik_list_networks_details`, `auvik_list_networks_info`, `auvik_list_tenants` `native-webhooks` `guide-changes` Added inbound webhook event support for Auvik alerts with a computed Native Webhook URL and setup guide, and improved the authentication guide. # Avanquest PDF API Source: https://docs.stackone.com/connectors/avanquest/index How to set up the Avanquest PDF API connector, plus the actions that are available.
Avanquest PDF API
v1.0.0
29 actions · 1 auth method
Documents
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a license key sent in the X-API-KEY header. No app registration; a license key (including a free 30-day trial key)... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/avanquest/index.md for the full list. # Avanquest PDF API Changelog Source: https://docs.stackone.com/connectors/avanquest/changelog Release history for the Avanquest PDF API connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Fixed Download Operation Result so completed operations now return the processed file content instead of an empty response. `avanquest_download_operation_result` `new-actions` Initial preview release of the Avanquest PDF API connector with 29 actions across conversion, editing, security, extraction, and image AI, plus shared operation status and download actions for the asynchronous job model. # AWS Lambda Source: https://docs.stackone.com/connectors/awslambda/index How to set up the AWS Lambda connector, plus the actions that are available.
AWS Lambda
Previewv1.0.0
66 actions · 1 auth method
Infrastructure
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use AWS IAM Access Keys to authenticate with AWS Lambda. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/awslambda/index.md for the full list. # Azure Blob Storage Source: https://docs.stackone.com/connectors/azureblobstorage/index How to set up the Azure Blob Storage connector, plus the actions and events that are available.
Azure Blob Storage
v1.2.0
27 actions · 11 events · 1 auth method
Storage
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect Azure Blob Storage. This is Microsoft's recommended authent... Optionally, configure receiving Events for Azure Blob Storage into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/azureblobstorage/index.md for the full list. ## Events See https://docs.stackone.com/connectors/azureblobstorage/index.md for the full list. # Azure Blob Storage Changelog Source: https://docs.stackone.com/connectors/azureblobstorage/changelog Release history for the Azure Blob Storage connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled DataSync on list_containers, so StackOne can periodically pull and keep a full copy of the storage account's containers up to date. It uses Azure's continuation-token (marker) paging and refreshes the full set on each run. `azureblobstorage_list_containers` `new-actions` `bug-fix` `description-fix` Added the append_block action, which writes content to the end of an append blob (Azure's Append Block operation). Previously upload_blob could create an empty append blob but nothing could write bytes into it, so append-style log workflows could not complete; append_block closes that gap and can be called repeatedly to grow a log. upload_blob's description now points to append_block for writing append-blob content. Description hardening — copy_blob now explicitly requires reading the account blob endpoint (ServiceEndpoint) from list_containers and forbids guessing the host, which otherwise returns 409 CannotVerifyCopySource. `azureblobstorage_append_block` `azureblobstorage_copy_blob`, `azureblobstorage_upload_blob` `bug-fix` `description-fix` Behavioural bug-fixes from agent testing — upload_blob now sends the raw file bytes (switched from multipart/form-data to a binary body) so stored content is byte-faithful and Append/Page blobs create correctly (file_content is now optional for empty page/append creation); create_blob_snapshot now returns the x-ms-snapshot id (plus etag, lastModified, versionId) so the new snapshot is addressable. Description clarifications — copy_blob documents the same-account copySource URL format and the ServiceEndpoint from list_containers, undelete_blob notes it does not promote the base version on versioning-enabled accounts, list_blobs notes the permissions include is HNS-only, and create_container / set_container_acl / upload_blob expiryOption / abort_copy_blob document their storage-account requirements (public access, hierarchical namespace, asynchronous copy). `azureblobstorage_abort_copy_blob`, `azureblobstorage_copy_blob`, `azureblobstorage_create_blob_snapshot`, `azureblobstorage_create_container`, `azureblobstorage_list_blobs`, `azureblobstorage_set_container_acl`, `azureblobstorage_undelete_blob`, `azureblobstorage_upload_blob` `documentation` Setup guide improvements from documentation audit — Entra ID app-registration steps reordered so all Entra portal work is contiguous (client secret before RBAC), single-tenant account-type wording covers both portal label forms, added old-UI "Add a platform" fallback for the redirect URI step, noted offline_access is requested automatically, added storage-account discovery navigation and "Job function roles" hint to the RBAC step, added "Storage center | Blob Storage" landing note, and clarified the accountName field description in the connection form. `native-webhooks` Added inbound webhook event support via Azure Event Grid (Manual setup) — 10 events (Blob Created, Blob Deleted, Blob Tier Changed, Async Operation Initiated, Data Lake Gen2 Blob Renamed and Directory Created/Renamed/Deleted, plus Blob Inventory Policy Completed and Lifecycle Policy Completed), with the SubscriptionValidation handshake handled automatically and a per-connection native webhook URL for scoping subscriptions to a storage account. # Azure DevOps Source: https://docs.stackone.com/connectors/azuredevops/index How to set up the Azure DevOps connector, plus the actions and events that are available.
Azure DevOps
Previewv1.2.0
185 actions · 14 events · 2 auth methods
Project Management Ticketing Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an app registration in Microsoft Entra ID with Azure DevOps API permissions. Best for personal scripts, CI/CD pipelines, and single-user automation. Quick to set up with granular scope control. Optionally, configure receiving Events for Azure DevOps into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/azuredevops/index.md for the full list. ## Events See https://docs.stackone.com/connectors/azuredevops/index.md for the full list. # Azure DevOps Changelog Source: https://docs.stackone.com/connectors/azuredevops/changelog Release history for the Azure DevOps connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added periodic data sync for 11 organization-level collections — projects, teams, repositories, feeds, service hooks, agent pools, work item fields and relation types, users, groups, and user entitlements — so their records can be pulled into StackOne and kept up to date, with paging handled automatically. `azuredevops_list_agent_pools`, `azuredevops_list_entitlements`, `azuredevops_list_feeds`, `azuredevops_list_fields`, `azuredevops_list_groups`, `azuredevops_list_projects`, `azuredevops_list_repositories`, `azuredevops_list_service_hooks`, `azuredevops_list_teams`, `azuredevops_list_users`, `azuredevops_list_work_item_relation_types` `native-webhooks` Added webhook event support for work item, git push, pull request, build, and pipeline events (14 events) with programmatic Service Hook subscription management and optional project scoping (required for pipeline events). # BALLDONTLIE Source: https://docs.stackone.com/connectors/balldontlie/index How to set up the BALLDONTLIE connector, plus the actions and events that are available.
BALLDONTLIE
v1.2.0
30 actions · 15 events · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a personal API key sent as the raw value of the Authorization header. No app registration required. Keys are issued... Optionally, configure receiving Events for BALLDONTLIE into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/balldontlie/index.md for the full list. ## Events See https://docs.stackone.com/connectors/balldontlie/index.md for the full list. # BALLDONTLIE Changelog Source: https://docs.stackone.com/connectors/balldontlie/changelog Release history for the BALLDONTLIE connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added webhook support for the fourteen NBA event types — game started, ended, period ended and overtime; player scored, rebound, assist, steal, block, foul and turnover; and injury created, updated and cleared. Game events report the game as the record id, and player and injury events report the player. The webhook endpoint is created by hand in the BALLDONTLIE dashboard using the Native Webhook URL shown on the linked account, because managing webhooks over the API requires an ALL-ACCESS subscription. Only game started and game ended can be subscribed to on the Free plan. A catch-all handler acknowledges deliveries with no recognised NBA event type, including the dashboard's test event, so endpoint verification succeeds and BALLDONTLIE does not auto-disable the endpoint. A setup guide walks through creating the endpoint in the BALLDONTLIE dashboard, with screenshots of each screen, and lists every event with its plan. Game started, game ended and the catch-all are verified against live deliveries and ship as preview; the twelve event types that need ALL-ACCESS could not be received on a Free account and ship as beta. `new-feature` `data-sync` Twelve list actions can now be synced with Data Sync, covering teams, players, active players, games, live box scores, stats, advanced stats, player injuries, betting odds, opening odds, DFS slates and DFS draftables. Every action runs as a full refresh, because the available date filters select when a game was played rather than when a record last changed. `balldontlie_get_all_active_players`, `balldontlie_get_all_advanced_stats_v2`, `balldontlie_get_all_games`, `balldontlie_get_all_player_injuries`, `balldontlie_get_all_players`, `balldontlie_get_all_stats`, `balldontlie_get_all_teams`, `balldontlie_get_betting_odds`, `balldontlie_get_live_box_scores`, `balldontlie_get_opening_betting_odds`, `balldontlie_list_dfs_draftables`, `balldontlie_list_dfs_slates` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `guide-changes` Connection guide fixes for the API Key setup. The guide now says the FREE tier is enough to link the account and lists which actions each NBA tier covers, describes the Try GOAT free for 48 hours banner and its Start trial button as separate from the SUBSCRIBE button on the plan cards, and adds the Change NBA Plan confirmation dialog and the Stripe payment form as their own steps. Tier prices render correctly again in the tier list. `description-fix` Description accuracy pass on player search, team id provenance and game score attribution. The get_all_players and get_all_active_players actions now state that search takes a single name token matched as a case-insensitive substring of the first or last name, so a full "First Last" string returns nothing; first_name and last_name are documented as substring filters. Every team_ids input now says the values are the numeric ids returned by Get All Teams and are not derivable from names or abbreviations. The get_all_games and get_a_specific_game actions now spell out that a record's home_* fields belong to its home_team object and visitor_* to visitor_team, with both team objects included in each record. The get_current_user action is described as the action for questions about the account's own tier and subscriptions rather than a check to run before every data request, and every per_page description leads with the 1 to 100 range. `balldontlie_get_a_specific_game`, `balldontlie_get_all_active_players`, `balldontlie_get_all_advanced_stats_v2`, `balldontlie_get_all_games`, `balldontlie_get_all_player_injuries`, `balldontlie_get_all_players`, `balldontlie_get_all_stats`, `balldontlie_get_averages`, `balldontlie_get_betting_odds`, `balldontlie_get_current_user`, `balldontlie_get_game_lineups`, `balldontlie_get_opening_betting_odds`, `balldontlie_get_player_contracts`, `balldontlie_get_team_season_averages`, `balldontlie_list_dfs_draftables`, `balldontlie_list_dfs_slates` `new-connector` `new-actions` Initial action mappings for the BALLDONTLIE API — 29 read-only actions covering teams, players, games, box scores, play-by-play, player and team statistics, standings, leaders, injuries, contracts, betting odds, player props, and daily fantasy sports slates. # BambooHR Source: https://docs.stackone.com/connectors/bamboohr/index How to set up the BambooHR connector, plus the actions and events that are available.
BambooHR
v2.1.1
107 actions · 3 events · 2 auth methods
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Provides granular scope control over employee, compensation, time-off, and other data categories. Inherits the full permissions of the generating user. Simpler to set up but no granular scope control. Optionally, configure receiving Events for BambooHR into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bamboohr/index.md for the full list. ## Events See https://docs.stackone.com/connectors/bamboohr/index.md for the full list. # BambooHR Changelog Source: https://docs.stackone.com/connectors/bamboohr/changelog Release history for the BambooHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed new API key connections failing the connection check, which was calling five actions by names they had before an earlier rename. `improvement` Added data sync support to 24 list actions - including employees, the employee directory, time-off types and policies, benefits, holidays, time-tracking projects, reports, job openings, and job applications - so their records can be periodically pulled and kept up to date, with pagination handled automatically. `bamboohr_list_applicant_statuses`, `bamboohr_list_benefit_coverages`, `bamboohr_list_benefit_deduction_types`, `bamboohr_list_company_files`, `bamboohr_list_company_locations`, `bamboohr_list_countries`, `bamboohr_list_datasets`, `bamboohr_list_employees`, `bamboohr_list_employees_directory`, `bamboohr_list_fields`, `bamboohr_list_hiring_leads`, `bamboohr_list_holidays`, `bamboohr_list_job_applications`, `bamboohr_list_job_summaries`, `bamboohr_list_list_fields`, `bamboohr_list_member_benefit_events`, `bamboohr_list_monitor_fields`, `bamboohr_list_reports`, `bamboohr_list_tabular_fields`, `bamboohr_list_time_off_policies`, `bamboohr_list_time_off_types`, `bamboohr_list_time_tracking_projects`, `bamboohr_list_webhooks`, `bamboohr_list_whos_out` `improvement` `documentation` Clarified the time-tracking write actions so agents pick the right one for a worked-from/to timesheet entry - Create Or Update Clock Entries now states it records entries with explicit start and end times, and Create Hour Record states it stores only a total-hours figure without start/end times. List Employees now states up front that it resolves an employee ID from a name and filters employees by status, department, job title, pay type and other attributes. `bamboohr_create_hour_record`, `bamboohr_create_or_update_clock_entries`, `bamboohr_list_employees` `improvement` `documentation` `bug-fix` Removed pdf and xls formats from request_custom_report because the endpoint returns binary data that was being decoded as text, producing corrupt files; json, xml, and csv remain supported. `bamboohr_request_custom_report` `improvement` `documentation` `bug-fix` Fixed the employee-dependent relationship field to accept only the values BambooHR supports (child, spouse, domestic partner), so creating and updating dependents no longer fails with an invalid-relationship error. Clarified action guidance to match real provider behavior — the employee directory cannot filter or sort (use list employees), job summaries return job openings rather than candidate applications, custom-report fields take API field IDs sent as one array, table-row updates require exact list values, added employmentStatus and comment fields to the table-row actions so employee offboarding/termination via the employmentStatus table now works (previously there was no way to write the status value), project tasks can only be added when the project was created with tasks enabled, recording a used time-off history item conflicts when the approved request already has one, and time-off policy assignment sets or replaces the policy for a given time-off type (re-assigning the same policy is rejected as already-assigned). Documented time-tracking timesheet-type requirements (clock in/out needs a clock-in/out timesheet while hour entries need a total-hours timesheet) and improved time-tracking field typing and descriptions. `bamboohr_create_table_row`, `bamboohr_create_time_off_history_item`, `bamboohr_list_job_applications`, `bamboohr_request_custom_report`, `bamboohr_update_table_row` `improvement` `documentation` `bug-fix` Fixed the employee-dependent relationship field to accept only the values BambooHR supports (child, spouse, domestic partner), so creating and updating dependents no longer fails with an invalid-relationship error. Clarified action guidance to match real provider behavior — the employee directory cannot filter or sort (use list employees), job summaries return job openings rather than candidate applications, custom-report fields take API field IDs sent as one array, table-row updates require exact list values, employee termination is done by adding an employmentStatus table row, project tasks can only be added when the project was created with tasks enabled, recording a used time-off history item conflicts when the approved request already has one, and time-off policy assignment sets or replaces the policy for a given time-off type (re-assigning the same policy is rejected as already-assigned). Documented time-tracking timesheet-type requirements (clock in/out needs a clock-in/out timesheet while hour entries need a total-hours timesheet) and improved time-tracking field typing and descriptions. `bamboohr_assign_time_off_policies`, `bamboohr_create_project_task`, `bamboohr_create_table_row`, `bamboohr_create_time_off_history_item`, `bamboohr_list_job_summaries`, `bamboohr_request_custom_report` `improvement` `documentation` `bug-fix` Fixed the employee-dependent relationship field to use the values BambooHR actually accepts (child, spouse, domestic partner), so creating and updating dependents no longer fails with an invalid-relationship error. Clarified several action descriptions to match real behavior — the employee directory does not accept filters or sorting (use list employees for that), job summaries return job openings rather than candidate applications, custom-report fields take API field IDs (not display labels), and table-row updates require exact list values. Documented time-tracking timesheet-type requirements (clock in/out needs a clock-in/out timesheet while hour entries need a total-hours timesheet) and improved time-tracking field typing and descriptions. `bamboohr_clock_in_employee`, `bamboohr_clock_out_employee`, `bamboohr_create_employee_dependent`, `bamboohr_create_hour_record`, `bamboohr_create_or_update_clock_entries`, `bamboohr_create_or_update_hour_entries`, `bamboohr_create_project_task`, `bamboohr_create_time_tracking_project`, `bamboohr_delete_clock_entries`, `bamboohr_delete_hour_entries`, `bamboohr_delete_hour_record`, `bamboohr_get_hour_record`, `bamboohr_list_break_policies`, `bamboohr_list_break_policy_breaks`, `bamboohr_list_employees_directory`, `bamboohr_list_holidays`, `bamboohr_list_job_summaries`, `bamboohr_list_project_tasks`, `bamboohr_list_shift_differentials`, `bamboohr_list_time_tracking_projects`, `bamboohr_list_timesheet_entries`, `bamboohr_request_custom_report`, `bamboohr_update_employee_dependent`, `bamboohr_update_hour_record`, `bamboohr_update_table_row` `improvement` `documentation` `bug-fix` Overhauled the OAuth setup guide with step screenshots, clearer portal navigation, correct button labels, an application-name example, and a masked-credential reveal step, and aligned the documented application scopes with those actually requested (deduplicated to top-level scopes, since each write scope already includes its read). Corrected several action descriptions to match real BambooHR behavior — employee name-filter and sort-field formats (plus a new jobTitleName field), routing employment-status and termination changes through the employment-status table, the employeeCompDate companion-field rule (required for exempt/payRate, not payType), a required file extension on uploads, exact-value matching for list-type fields when adding table rows, and time-off policy listing (company-wide vs per-employee) and assignment (assigning an already-held policy is a silent no-op, not an error). `bamboohr_assign_time_off_policies`, `bamboohr_clock_in_employee`, `bamboohr_clock_out_employee`, `bamboohr_close_goal`, `bamboohr_create_application_comment`, `bamboohr_create_candidate`, `bamboohr_create_company_file_category`, `bamboohr_create_employee`, `bamboohr_create_employee_dependent`, `bamboohr_create_employee_file_category`, `bamboohr_create_employee_training_record`, `bamboohr_create_goal`, `bamboohr_create_goal_comment`, `bamboohr_create_hour_record`, `bamboohr_create_job_opening`, `bamboohr_create_or_update_clock_entries`, `bamboohr_create_or_update_hour_entries`, `bamboohr_create_or_update_list_values`, `bamboohr_create_project_task`, `bamboohr_create_table_row`, `bamboohr_create_time_off_history_item`, `bamboohr_create_time_off_request`, `bamboohr_create_time_tracking_project`, `bamboohr_create_training_category`, `bamboohr_create_training_type`, `bamboohr_create_webhook`, `bamboohr_delete_clock_entries`, `bamboohr_delete_company_file`, `bamboohr_delete_employee_training_record`, `bamboohr_delete_goal`, `bamboohr_delete_hour_entries`, `bamboohr_delete_hour_record`, `bamboohr_delete_table_row`, `bamboohr_delete_training_type`, `bamboohr_delete_webhook`, `bamboohr_estimate_future_time_off_balances`, `bamboohr_get_changed_employee_ids`, `bamboohr_get_company_file`, `bamboohr_get_company_information`, `bamboohr_get_dataset_data`, `bamboohr_get_dataset_fields`, `bamboohr_get_employee`, `bamboohr_get_employee_file_categories`, `bamboohr_get_employee_photo`, `bamboohr_get_employee_table_rows`, `bamboohr_get_employee_time_off_policies`, `bamboohr_get_field_options`, `bamboohr_get_hour_record`, `bamboohr_get_job_application_details`, `bamboohr_get_report`, `bamboohr_get_states_by_country`, `bamboohr_get_webhook`, `bamboohr_get_webhook_logs`, `bamboohr_list_applicant_statuses`, `bamboohr_list_benefit_coverages`, `bamboohr_list_benefit_deduction_types`, `bamboohr_list_break_policies`, `bamboohr_list_break_policy_breaks`, `bamboohr_list_company_files`, `bamboohr_list_company_locations`, `bamboohr_list_countries`, `bamboohr_list_datasets`, `bamboohr_list_employee_dependents`, `bamboohr_list_employee_files`, `bamboohr_list_employee_trainings`, `bamboohr_list_employees`, `bamboohr_list_employees_directory`, `bamboohr_list_fields`, `bamboohr_list_goal_alignment_options`, `bamboohr_list_goals`, `bamboohr_list_hiring_leads`, `bamboohr_list_holidays`, `bamboohr_list_job_applications`, `bamboohr_list_job_summaries`, `bamboohr_list_list_fields`, `bamboohr_list_member_benefit_events`, `bamboohr_list_monitor_fields`, `bamboohr_list_project_tasks`, `bamboohr_list_reports`, `bamboohr_list_shift_differentials`, `bamboohr_list_tabular_fields`, `bamboohr_list_time_off_policies`, `bamboohr_list_time_off_requests`, `bamboohr_list_time_off_types`, `bamboohr_list_time_tracking_projects`, `bamboohr_list_timesheet_entries`, `bamboohr_list_training_categories`, `bamboohr_list_training_types`, `bamboohr_list_users`, `bamboohr_list_webhooks`, `bamboohr_list_whos_out`, `bamboohr_reopen_goal`, `bamboohr_request_custom_report`, `bamboohr_update_applicant_status`, `bamboohr_update_company_file`, `bamboohr_update_employee`, `bamboohr_update_employee_dependent`, `bamboohr_update_employee_training_record`, `bamboohr_update_goal`, `bamboohr_update_hour_record`, `bamboohr_update_table_row`, `bamboohr_update_time_off_balance`, `bamboohr_update_time_off_request_status`, `bamboohr_update_webhook`, `bamboohr_upload_company_file`, `bamboohr_upload_employee_file`, `bamboohr_upload_employee_photo` `breaking` `new-actions` `bug-fix` Standardized several action names and folded the duplicate company-report action into request_custom_report (breaking). Added time-tracking lookup actions (projects, tasks, breaks, shift differentials, holidays) and goal alignment options, corrected field types and validation, and fixed binary file downloads and goal milestone updates. `bamboohr_create_hour_record`, `bamboohr_create_project_task`, `bamboohr_get_changed_employee_ids`, `bamboohr_list_benefit_deduction_types`, `bamboohr_list_break_policies`, `bamboohr_list_break_policy_breaks`, `bamboohr_list_goal_alignment_options`, `bamboohr_list_holidays`, `bamboohr_list_list_fields`, `bamboohr_list_member_benefit_events`, `bamboohr_list_monitor_fields`, `bamboohr_list_project_tasks`, `bamboohr_list_shift_differentials`, `bamboohr_list_time_tracking_projects`, `bamboohr_list_whos_out` `bamboohr_add_hour_record`, `bamboohr_get_benefit_deduction_types`, `bamboohr_get_changed_employees`, `bamboohr_get_company_report`, `bamboohr_get_list_field_details`, `bamboohr_get_member_benefit_events`, `bamboohr_get_monitor_fields`, `bamboohr_get_whos_out` `bamboohr_assign_time_off_policies`, `bamboohr_clock_in_employee`, `bamboohr_clock_out_employee`, `bamboohr_close_goal`, `bamboohr_create_application_comment`, `bamboohr_create_candidate`, `bamboohr_create_company_file_category`, `bamboohr_create_employee`, `bamboohr_create_employee_dependent`, `bamboohr_create_employee_file_category`, `bamboohr_create_employee_training_record`, `bamboohr_create_goal`, `bamboohr_create_goal_comment`, `bamboohr_create_job_opening`, `bamboohr_create_or_update_clock_entries`, `bamboohr_create_or_update_hour_entries`, `bamboohr_create_or_update_list_values`, `bamboohr_create_table_row`, `bamboohr_create_time_off_history_item`, `bamboohr_create_time_off_request`, `bamboohr_create_time_tracking_project`, `bamboohr_create_training_category`, `bamboohr_create_training_type`, `bamboohr_create_webhook`, `bamboohr_delete_clock_entries`, `bamboohr_delete_company_file`, `bamboohr_delete_employee_training_record`, `bamboohr_delete_goal`, `bamboohr_delete_hour_entries`, `bamboohr_delete_hour_record`, `bamboohr_delete_table_row`, `bamboohr_delete_training_type`, `bamboohr_delete_webhook`, `bamboohr_estimate_future_time_off_balances`, `bamboohr_get_company_file`, `bamboohr_get_company_information`, `bamboohr_get_dataset_data`, `bamboohr_get_dataset_fields`, `bamboohr_get_employee`, `bamboohr_get_employee_file_categories`, `bamboohr_get_employee_photo`, `bamboohr_get_employee_table_rows`, `bamboohr_get_employee_time_off_policies`, `bamboohr_get_field_options`, `bamboohr_get_hour_record`, `bamboohr_get_job_application_details`, `bamboohr_get_report`, `bamboohr_get_states_by_country`, `bamboohr_get_webhook`, `bamboohr_get_webhook_logs`, `bamboohr_list_applicant_statuses`, `bamboohr_list_benefit_coverages`, `bamboohr_list_company_files`, `bamboohr_list_company_locations`, `bamboohr_list_countries`, `bamboohr_list_datasets`, `bamboohr_list_employee_dependents`, `bamboohr_list_employee_files`, `bamboohr_list_employee_trainings`, `bamboohr_list_employees`, `bamboohr_list_employees_directory`, `bamboohr_list_fields`, `bamboohr_list_goals`, `bamboohr_list_hiring_leads`, `bamboohr_list_job_applications`, `bamboohr_list_job_summaries`, `bamboohr_list_reports`, `bamboohr_list_tabular_fields`, `bamboohr_list_time_off_policies`, `bamboohr_list_time_off_requests`, `bamboohr_list_time_off_types`, `bamboohr_list_timesheet_entries`, `bamboohr_list_training_categories`, `bamboohr_list_training_types`, `bamboohr_list_users`, `bamboohr_list_webhooks`, `bamboohr_reopen_goal`, `bamboohr_request_custom_report`, `bamboohr_update_applicant_status`, `bamboohr_update_company_file`, `bamboohr_update_employee`, `bamboohr_update_employee_dependent`, `bamboohr_update_employee_training_record`, `bamboohr_update_goal`, `bamboohr_update_hour_record`, `bamboohr_update_table_row`, `bamboohr_update_time_off_balance`, `bamboohr_update_time_off_request_status`, `bamboohr_update_webhook`, `bamboohr_upload_company_file`, `bamboohr_upload_employee_file`, `bamboohr_upload_employee_photo` `native webhooks` Added webhook event support for employee.created, employee.updated, and employee.deleted events with programmatic webhook registration. # Basecamp Source: https://docs.stackone.com/connectors/basecamp/index How to set up the Basecamp connector, plus the actions and events that are available.
Basecamp
v3.0.0
133 actions · 45 events · 1 auth method
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth application on the 37signals Launchpad. Uses authorization code flow with refresh tokens. Optionally, configure receiving Events for Basecamp into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/basecamp/index.md for the full list. ## Events See https://docs.stackone.com/connectors/basecamp/index.md for the full list. # Basecamp Changelog Source: https://docs.stackone.com/connectors/basecamp/changelog Release history for the Basecamp connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking-change` `data-sync` Added DataSync v2 support for 5 list actions (people, projects, templates, campfires, unified users). Schedule entry actions consolidated — get_a_schedule_entry and update_a_schedule_entry input renamed from id to entry_id, update now requires starts_at and ends_at on every call. `basecamp_create_a_schedule_entry`, `basecamp_get_a_schedule_entry`, `basecamp_get_all_people`, `basecamp_get_all_projects`, `basecamp_get_campfires`, `basecamp_get_people_on_a_project`, `basecamp_get_schedule_entries`, `basecamp_get_templates`, `basecamp_unified_list_users`, `basecamp_update_a_schedule_entry` `bug-fix` `improved-descriptions` Improved action descriptions across all resources for better agent callability, removed non-functional file_type search parameter, and clarified recording vs container distinctions. `basecamp_get_all_people`, `basecamp_get_all_projects`, `basecamp_get_documents`, `basecamp_get_recordings`, `basecamp_get_uploads`, `basecamp_move_a_column`, `basecamp_search_recordings`, `basecamp_subscribe_current_user`, `basecamp_update_a_project`, `basecamp_update_who_can_access_a_project` `bug-fix` `improved-descriptions` Made starts_at and ends_at required on schedule entry updates (prevents 422), improved action descriptions for update_account_logo, update_a_column, update_subscription, and search_recordings file_type filter. `basecamp_search_recordings`, `basecamp_update_a_column`, `basecamp_update_account_logo`, `basecamp_update_subscription` `bug-fix` `improved-descriptions` Removed invalid draft status from document and message creation (omit status for drafts), made content required on to-do updates, changed time_format to enum, and improved action descriptions for better discoverability. `basecamp_create_a_column`, `basecamp_create_a_document`, `basecamp_create_a_message`, `basecamp_get_a_to-do_list`, `basecamp_get_my_profile`, `basecamp_get_to-do_lists`, `basecamp_get_todos`, `basecamp_move_a_column`, `basecamp_search_recordings`, `basecamp_update_a_card_step`, `basecamp_update_a_todo`, `basecamp_update_a_tool`, `basecamp_update_my_personal_info`, `basecamp_update_who_can_access_a_project` `bug-fix` Fixed organization lookups that crashed instead of returning a not-found error, and role scopes that showed a placeholder instead of the real account id. Also fixed people and project member lists being silently cut off on large accounts. `basecamp_unified_get_me`, `basecamp_unified_get_organization`, `basecamp_unified_get_role`, `basecamp_unified_get_user`, `basecamp_unified_list_organizations`, `basecamp_unified_list_resource_users`, `basecamp_unified_list_roles`, `basecamp_unified_list_users` `guide` Improved OAuth setup guide with corrected UI labels, URL formatting, and clarified Account ID usage. `guide` `new-events` Added manual webhook support with 45 event actions and webhook setup guide, covering todos, todolists, messages, comments, documents, files, schedule entries, kanban cards, vaults, and questions. `bug-fix` Fixed IAM list pagination past page 1 - unified_list_users and unified_list_resource_users no longer emit a raw page-number result.next, replaced with a fixed page fan-out and StackOne virtual pagination. `basecamp_unified_list_resource_users`, `basecamp_unified_list_users` `bug-fix` `improvement` `new-actions` Schema and behavioural fixes. Fixed param names, URLs, types, and missing fields per Basecamp API docs. Added webhooks CRUD, comments CRUD, and trash_a_todo actions. Improved connection guide and action descriptions. # Bazaarvoice Source: https://docs.stackone.com/connectors/bazaarvoice/index How to set up the Bazaarvoice connector, plus the actions that are available.
Bazaarvoice
Betav2.0.0
38 actions · 4 auth methods
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Bazaarvoice API passkey for authentication. Covers the Conversations API, Product Sentiments API, and Authentic D... OAuth 2.0 authorization code flow for the Bazaarvoice Response API. Requires registering an OAuth application with Bazaa... OAuth 2.0 client credentials flow for the Bazaarvoice Privacy API. Machine-to-machine authentication with no user intera... Social Commerce Display API (edge.curalate.com) media actions. The API is scoped by a data source ID from Bazaarvoice Su... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bazaarvoice/index.md for the full list. # Bazaarvoice Changelog Source: https://docs.stackone.com/connectors/bazaarvoice/changelog Release history for the Bazaarvoice connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Each action is now bound to the authentication method its Bazaarvoice API accepts - Conversations, Sentiments, and Authentic Discovery actions require the API Key, Response API actions require OAuth 2.0 (Response API), Privacy API actions require OAuth 2.0 (Privacy API), and Social Commerce media actions require the Social Commerce API Token. Actions are no longer offered on accounts connected with an incompatible method. Social Commerce media actions now use the documented paths and parameters - get_media, get_top_image, report_media, and submit_media (now a multipart file upload to /v1/upload) changed endpoints, and datasourceId/mediaId inputs were renamed to dataSourceId/itemId. `bazaarvoice_authenticate_user`, `bazaarvoice_create_access_request`, `bazaarvoice_create_client_response`, `bazaarvoice_create_forget_request`, `bazaarvoice_delete_client_response`, `bazaarvoice_get_access_request`, `bazaarvoice_get_client_response`, `bazaarvoice_get_forget_request`, `bazaarvoice_get_media`, `bazaarvoice_get_review_for_response`, `bazaarvoice_get_structured_ugc`, `bazaarvoice_get_top_image`, `bazaarvoice_list_access_requests`, `bazaarvoice_list_answers`, `bazaarvoice_list_authors`, `bazaarvoice_list_categories`, `bazaarvoice_list_client_responses`, `bazaarvoice_list_expressions`, `bazaarvoice_list_feature_quotes`, `bazaarvoice_list_features`, `bazaarvoice_list_forget_requests`, `bazaarvoice_list_media`, `bazaarvoice_list_products`, `bazaarvoice_list_questions`, `bazaarvoice_list_quotes`, `bazaarvoice_list_review_comments`, `bazaarvoice_list_reviews`, `bazaarvoice_list_statistics`, `bazaarvoice_list_summarised_features`, `bazaarvoice_report_media`, `bazaarvoice_submit_answer`, `bazaarvoice_submit_feedback`, `bazaarvoice_submit_media`, `bazaarvoice_submit_question`, `bazaarvoice_submit_review`, `bazaarvoice_submit_review_comment`, `bazaarvoice_update_client_response`, `bazaarvoice_upload_photo` `data-sync` Added periodic data sync to nine list actions - reviews, review comments, questions, answers, authors, products, categories, and privacy access and forget requests. All collections refresh in full on every run, since the Bazaarvoice APIs expose no standalone updated-since query parameter. # Beekeeper Source: https://docs.stackone.com/connectors/beekeeper/index How to set up the Beekeeper connector, plus the actions that are available.
Beekeeper
Betav0.2.0
25 actions · 1 auth method
Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a Beekeeper bot token generated from the Beekeeper Dashboard under Extensions > Bot Accounts. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/beekeeper/index.md for the full list. # Beekeeper Changelog Source: https://docs.stackone.com/connectors/beekeeper/changelog Release history for the Beekeeper connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for users, groups, streams, and comments (full-refresh only). `beekeeper_list_comments`, `beekeeper_list_groups`, `beekeeper_list_streams`, `beekeeper_list_users` `new-actions` Initial connector release with 26 actions across users, groups, posts, streams, and comments. # Beeline Source: https://docs.stackone.com/connectors/beeline/index How to set up the Beeline connector, plus the actions that are available.
Beeline
Betav1.1.0
75 actions · 1 auth method
Vendor Management System
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires OAuth2 client credentials from your Beeline integration. Contact your Beeline administrator to obtain a Client... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/beeline/index.md for the full list. # Beeline Changelog Source: https://docs.stackone.com/connectors/beeline/changelog Release history for the Beeline connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for assignments, business areas, candidates, countries, locations, organizations, OU types, and request intake forms, with paging handled automatically. All syncs are full-refresh — the Beeline API exposes no updated-since filter. # Better Stack Source: https://docs.stackone.com/connectors/betterstack/index How to set up the Better Stack connector, plus the actions that are available.
Better Stack
Previewv0.1.2
8 actions · 1 auth method
IAM Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Better Stack global API token or a team-scoped Uptime API token. A connection reads one team's members, so a glob... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/betterstack/index.md for the full list. # Better Stack Changelog Source: https://docs.stackone.com/connectors/betterstack/changelog Release history for the Better Stack connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists and lookups now include pending invitations with a pending status, and user lists no longer return short pages. `betterstack_unified_get_user`, `betterstack_unified_list_users` `improvement` Native actions are now also listed under Observability, the API key guide uses the right menu path, and a full user sync no longer re-fetches the team roster for every page. `betterstack_get_team_member`, `betterstack_list_roles`, `betterstack_list_team_members`, `betterstack_unified_list_users` `new-connector` Initial Better Stack connector for reviewing who has access to a Better Stack team, covering team members and their roles, including unified IAM users, roles and connection details. # BigChange Source: https://docs.stackone.com/connectors/bigchange/index How to set up the BigChange connector, plus the actions that are available.
BigChange
Previewv1.2.0
103 actions · 1 auth method
Accounting IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Register your application in the BigChange Developer Portal to obtain API credentials. BigChange uses OAuth 2.0 Client C... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bigchange/index.md for the full list. # BigChange Changelog Source: https://docs.stackone.com/connectors/bigchange/changelog Release history for the BigChange connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the contact, job, invoice, resource, stock, worksheet, user, and related list actions for scheduled full record syncs. `bigchange_list_contact_groups`, `bigchange_list_contacts`, `bigchange_list_department_codes`, `bigchange_list_invoices`, `bigchange_list_job_groups`, `bigchange_list_job_types`, `bigchange_list_jobs`, `bigchange_list_nominal_codes`, `bigchange_list_note_types`, `bigchange_list_notes`, `bigchange_list_persons`, `bigchange_list_product_categories`, `bigchange_list_resource_groups`, `bigchange_list_resources`, `bigchange_list_stock_details`, `bigchange_list_stock_items`, `bigchange_list_stock_movements`, `bigchange_list_users`, `bigchange_list_vehicles`, `bigchange_list_worksheet_answers`, `bigchange_list_worksheet_groups`, `bigchange_list_worksheets`, `bigchange_unified_list_organizations`, `bigchange_unified_list_users` `new-actions` Added unified IAM actions for users, organizations, and credentials. # BigCommerce Source: https://docs.stackone.com/connectors/bigcommerce/index How to set up the BigCommerce connector, plus the actions that are available.
BigCommerce
Previewv1.1.0
120 actions · 1 auth method
E-Commerce Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create a Store-level API account in your BigCommerce admin panel to get API credentials. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bigcommerce/index.md for the full list. # BigCommerce Changelog Source: https://docs.stackone.com/connectors/bigcommerce/changelog Release history for the BigCommerce connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `bug-fix` `data-sync` Twenty-four list actions can now be synced with Data Sync, covering products, orders, customers, variants, inventory, categories, brands, coupons, price lists and store settings, with incremental sync on the six endpoints that expose a modified-since filter. Listing a V2 resource with no records now returns an empty list instead of an empty string. # Bill.com Source: https://docs.stackone.com/connectors/bill/index How to set up the Bill.com connector, plus the actions that are available.
Bill.com
Previewv0.3.0
66 actions · 2 auth methods
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Session-based authentication. Provide developer key, organization ID, email, and password — StackOne exchanges them for... For BILL users who sign in with single sign-on and have no password. Uses a sync token created in BILL instead of an ema... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bill/index.md for the full list. # Bill.com Changelog Source: https://docs.stackone.com/connectors/bill/changelog Release history for the Bill.com connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `auth` `guide` Added create_bills_bulk to create up to 100 bills in one call, and upload_bill_document, get_document_upload_status and list_bill_documents to attach a file to a bill and follow the upload. Added a Sync Token sign-in option for BILL users who sign in with single sign-on and have no password. `bill_create_bills_bulk`, `bill_get_document_upload_status`, `bill_list_bill_documents`, `bill_upload_bill_document` `bill_archive_accounting_class`, `bill_archive_bill`, `bill_archive_chart_of_account`, `bill_archive_customer`, `bill_archive_department`, `bill_archive_invoice`, `bill_archive_item`, `bill_archive_location`, `bill_archive_vendor`, `bill_cancel_payment`, `bill_create_accounting_class`, `bill_create_bank_account`, `bill_create_bill`, `bill_create_chart_of_account`, `bill_create_customer`, `bill_create_department`, `bill_create_invoice`, `bill_create_item`, `bill_create_location`, `bill_create_payment`, `bill_create_payment_term`, `bill_create_vendor`, `bill_create_vendor_bank_account`, `bill_delete_vendor_bank_account`, `bill_get_accounting_class`, `bill_get_bank_account`, `bill_get_bill`, `bill_get_chart_of_account`, `bill_get_customer`, `bill_get_department`, `bill_get_intl_payments_config`, `bill_get_invoice`, `bill_get_item`, `bill_get_location`, `bill_get_payment`, `bill_get_payment_term`, `bill_get_session_info`, `bill_get_vendor`, `bill_get_vendor_bank_account`, `bill_list_accounting_classes`, `bill_list_bank_accounts`, `bill_list_bills`, `bill_list_chart_of_accounts`, `bill_list_customers`, `bill_list_departments`, `bill_list_invoices`, `bill_list_items`, `bill_list_locations`, `bill_list_payment_terms`, `bill_list_payments`, `bill_list_vendors`, `bill_send_invoice`, `bill_update_accounting_class`, `bill_update_bill`, `bill_update_chart_of_account`, `bill_update_customer`, `bill_update_department`, `bill_update_invoice`, `bill_update_item`, `bill_update_location`, `bill_update_payment_term`, `bill_update_vendor` `data-sync` `new-feature` Added scheduled Data Sync to twelve collection actions: bills, vendors, customers, invoices, payments, bank accounts, chart of accounts, items, accounting classes, departments, locations and payment terms. These collections can now be kept in sync and searched without calling BILL on every request. Every sync refreshes in full on each run, because BILL exposes change tracking only through its combined filters expression. Sending sort or filters together with a page token is now rejected with a clear message, since BILL does not accept that combination. `bill_list_accounting_classes`, `bill_list_bank_accounts`, `bill_list_bills`, `bill_list_chart_of_accounts`, `bill_list_customers`, `bill_list_departments`, `bill_list_invoices`, `bill_list_items`, `bill_list_locations`, `bill_list_payment_terms`, `bill_list_payments`, `bill_list_vendors` `new-connector` Initial Bill.com connector with 62 actions across 14 core AP/AR resources (bills, vendors, vendor bank accounts, payments, payment terms, invoices, customers, bank accounts, chart of accounts, departments, accounting classes, locations, items, session) on the v3 API. # Bing Ads (Microsoft Ads) Source: https://docs.stackone.com/connectors/bingads/index How to set up the Bing Ads (Microsoft Ads) connector, plus the actions that are available.
Bing Ads (Microsoft Ads)
Previewv1.1.0
60 actions · 1 auth method
Advertising
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 via the Microsoft identity platform provides secure delegated access to Microsoft Advertising accounts without... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bingads/index.md for the full list. # Bing Ads (Microsoft Ads) Changelog Source: https://docs.stackone.com/connectors/bingads/changelog Release history for the Bing Ads (Microsoft Ads) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-features` Enable Data Sync for the shared budget library (get_budgets_by_ids) and UET tag library (get_uet_tags_by_ids), keeping those collections continuously synced. # Bitbucket Source: https://docs.stackone.com/connectors/bitbucket/index How to set up the Bitbucket connector, plus the actions and events that are available.
Bitbucket
Previewv2.3.1
142 actions · 26 events · 2 auth methods
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). For OAuth consumers Atlassian has not yet migrated to the Atlassian identity platform. Create an OAuth consumer for your... For OAuth consumers Atlassian has already migrated to the Atlassian identity platform. The authorization code and tokens... Optionally, configure receiving Events for Bitbucket into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bitbucket/index.md for the full list. ## Events See https://docs.stackone.com/connectors/bitbucket/index.md for the full list. # Bitbucket Changelog Source: https://docs.stackone.com/connectors/bitbucket/changelog Release history for the Bitbucket connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists with roles now return the workspace role for every member instead of only the first 100, with no extra API calls. `bitbucket_unified_get_organization`, `bitbucket_unified_get_user`, `bitbucket_unified_list_users` `new-feature` Added webhook events for repositories, commits, pull requests, and projects. StackOne creates and removes one Bitbucket workspace webhook automatically when you set the Webhook Workspace field. `new-feature` `data-sync` Added DataSync support for the workspace list and the unified organization, user, and role lists. Each action refreshes in full on every sync, since these Bitbucket endpoints expose no updated-since filter. `bitbucket_list_workspaces`, `bitbucket_unified_list_organizations`, `bitbucket_unified_list_roles`, `bitbucket_unified_list_users` `bug-fix` Fixed organization lists failing for some workspace types, workspace member and permission lists being cut short on large accounts, and user lists failing when the workspace filter was left out. Removed non-working filter and expand options from user lookups. `bitbucket_unified_get_me`, `bitbucket_unified_get_organization`, `bitbucket_unified_get_role`, `bitbucket_unified_get_user`, `bitbucket_unified_list_organizations`, `bitbucket_unified_list_resource_types`, `bitbucket_unified_list_resource_users`, `bitbucket_unified_list_roles`, `bitbucket_unified_list_users` `new-feature` User lists no longer require the workspace filter when the connection can only see one workspace — it is resolved automatically. Connections with several workspaces still pass the filter to choose one. `bitbucket_unified_list_users` `new-feature` Added a second OAuth 2.0 option for consumers Atlassian has migrated to the Atlassian identity platform, alongside the existing option for consumers still on bitbucket.org, and moved scopeDefinitions and requiredScopes to the granular bitbucket-legacy scope names the migrated platform grants. `bitbucket_add_default_reviewer`, `bitbucket_approve_commit`, `bitbucket_approve_pullrequest`, `bitbucket_create_branch_restrictions`, `bitbucket_create_branches`, `bitbucket_create_build`, `bitbucket_create_comments`, `bitbucket_create_commits`, `bitbucket_create_deploy_keys`, `bitbucket_create_environments`, `bitbucket_create_pipelines`, `bitbucket_create_project`, `bitbucket_create_project_deploy_key`, `bitbucket_create_pullrequest_comment`, `bitbucket_create_pullrequests`, `bitbucket_create_repository`, `bitbucket_create_schedules`, `bitbucket_create_src`, `bitbucket_create_ssh_keys`, `bitbucket_create_variables`, `bitbucket_decline_pullrequest`, `bitbucket_delete_branch_restrictions`, `bitbucket_delete_comments`, `bitbucket_delete_default_reviewers`, `bitbucket_delete_deploy_keys`, `bitbucket_delete_project`, `bitbucket_delete_project_default_reviewer`, `bitbucket_delete_project_deploy_key`, `bitbucket_delete_pullrequest_comment`, `bitbucket_delete_reports`, `bitbucket_delete_repository`, `bitbucket_delete_schedules`, `bitbucket_delete_ssh_keys`, `bitbucket_delete_variables`, `bitbucket_get_authenticated_user`, `bitbucket_get_branch_restrictions`, `bitbucket_get_branches`, `bitbucket_get_branching_model`, `bitbucket_get_branching_model_settings`, `bitbucket_get_build`, `bitbucket_get_comments`, `bitbucket_get_commit`, `bitbucket_get_default_reviewers`, `bitbucket_get_deploy_keys`, `bitbucket_get_deployments`, `bitbucket_get_diff`, `bitbucket_get_diffstat`, `bitbucket_get_environments`, `bitbucket_get_log`, `bitbucket_get_logs`, `bitbucket_get_patch`, `bitbucket_get_pipelines`, `bitbucket_get_pipelines_config`, `bitbucket_get_project`, `bitbucket_get_project_branching_model`, `bitbucket_get_project_branching_model_settings`, `bitbucket_get_project_default_reviewer`, `bitbucket_get_project_deploy_key`, `bitbucket_get_pullrequest_comment`, `bitbucket_get_pullrequest_diff`, `bitbucket_get_pullrequest_diffstat`, `bitbucket_get_pullrequest_patch`, `bitbucket_get_pullrequests`, `bitbucket_get_reports`, `bitbucket_get_repository`, `bitbucket_get_schedules`, `bitbucket_get_src`, `bitbucket_get_ssh_key`, `bitbucket_get_steps`, `bitbucket_get_user`, `bitbucket_get_variables`, `bitbucket_get_workspace`, `bitbucket_list_branch_restrictions`, `bitbucket_list_branches`, `bitbucket_list_comments`, `bitbucket_list_commit_pullrequests`, `bitbucket_list_commits`, `bitbucket_list_default_reviewers`, `bitbucket_list_deploy_keys`, `bitbucket_list_deployments`, `bitbucket_list_downloads`, `bitbucket_list_environments`, `bitbucket_list_forks`, `bitbucket_list_permissions`, `bitbucket_list_pipelines`, `bitbucket_list_project_default_reviewers`, `bitbucket_list_project_deploy_keys`, `bitbucket_list_projects`, `bitbucket_list_pullrequest_comments`, `bitbucket_list_pullrequest_commits`, `bitbucket_list_pullrequest_statuses`, `bitbucket_list_pullrequests`, `bitbucket_list_reports`, `bitbucket_list_repositories_in_workspace`, `bitbucket_list_repository_groups`, `bitbucket_list_repository_permissions`, `bitbucket_list_schedules`, `bitbucket_list_src`, `bitbucket_list_ssh_keys`, `bitbucket_list_statuses`, `bitbucket_list_steps`, `bitbucket_list_user_pullrequests`, `bitbucket_list_user_repository_permissions`, `bitbucket_list_variables`, `bitbucket_list_watchers`, `bitbucket_list_workspace_members`, `bitbucket_list_workspace_repository_permissions`, `bitbucket_list_workspaces`, `bitbucket_merge_pullrequest`, `bitbucket_remove_request_changes_pullrequest`, `bitbucket_request_changes_pullrequest`, `bitbucket_resolve_pullrequest_comment`, `bitbucket_stop_pipeline`, `bitbucket_unapprove_commit`, `bitbucket_unapprove_pullrequest`, `bitbucket_unified_get_me`, `bitbucket_unified_get_organization`, `bitbucket_unified_get_role`, `bitbucket_unified_get_user`, `bitbucket_unified_list_organizations`, `bitbucket_unified_list_resource_types`, `bitbucket_unified_list_resource_users`, `bitbucket_unified_list_roles`, `bitbucket_unified_list_users`, `bitbucket_unresolve_pullrequest_comment`, `bitbucket_update_branch_restrictions`, `bitbucket_update_build`, `bitbucket_update_build_number`, `bitbucket_update_comments`, `bitbucket_update_deploy_keys`, `bitbucket_update_environment`, `bitbucket_update_pipelines_config`, `bitbucket_update_project`, `bitbucket_update_project_default_reviewer`, `bitbucket_update_project_settings`, `bitbucket_update_pullrequest_comment`, `bitbucket_update_pullrequests`, `bitbucket_update_reports`, `bitbucket_update_schedules`, `bitbucket_update_settings`, `bitbucket_update_ssh_keys`, `bitbucket_update_variables` `bug-fix` Fixed IAM list pagination past page 1 by replacing the raw page-number result.next with a fixed page fan-out plus StackOne virtual pagination. `bitbucket_unified_list_organizations`, `bitbucket_unified_list_resource_users`, `bitbucket_unified_list_users` `new-actions` Added unified IAM actions for users, organizations, roles, resource users, and credentials. # Bitly Source: https://docs.stackone.com/connectors/bitly/index How to set up the Bitly connector, plus the actions that are available.
Bitly
v1.1.0
85 actions · 2 auth methods
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a Bitly Generic Access Token. Best suited for single-account integrations and quick setup. Connect Bitly accounts securely using OAuth 2.0 authorization for multi-user access. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bitly/index.md for the full list. # Bitly Changelog Source: https://docs.stackone.com/connectors/bitly/changelog Release history for the Bitly connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for campaigns, channels, groups and organizations, so their records can be periodically pulled into StackOne and kept up to date. All syncs are full-refresh, because the Bitly API exposes no updated-since filter a sync can use. `bitly_list_campaigns`, `bitly_list_channels`, `bitly_list_groups`, `bitly_list_organizations` `bug-fix` Improved the Access Token and OAuth connection guides: clearer field guidance, corrected the OAuth registration flow and the Client secret label to match the portal, and added portal screenshots to the guide steps. # Bitwarden Source: https://docs.stackone.com/connectors/bitwarden/index How to set up the Bitwarden connector, plus the actions that are available.
Bitwarden
Betav1.1.0
24 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 client credentials. Generate an organization API key from the Bitwarden Admin Console — the resu... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bitwarden/index.md for the full list. # Bitwarden Changelog Source: https://docs.stackone.com/connectors/bitwarden/changelog Release history for the Bitwarden connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added Data Sync support for listing members, groups, collections, and policies. # Bloomerang Source: https://docs.stackone.com/connectors/bloomerang/index How to set up the Bloomerang connector, plus the actions that are available.
Bloomerang
Betav1.1.0
104 actions · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a private API key for server-to-server access. Generate from your Bloomerang user settings as an Administrator. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bloomerang/index.md for the full list. # Bloomerang Changelog Source: https://docs.stackone.com/connectors/bloomerang/changelog Release history for the Bloomerang connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the constituent, transaction, interaction, campaign, fund, appeal, and related list actions for scheduled full record syncs. # BMC Helix ITSM (Remedy) Source: https://docs.stackone.com/connectors/bmchelix/index How to set up the BMC Helix ITSM (Remedy) connector, plus the actions that are available.
BMC Helix ITSM (Remedy)
Betav1.1.0
37 actions · 1 auth method
ITSM Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). BMC Helix ITSM (Remedy) authenticates with the AR System JWT scheme. StackOne exchanges the service-account username and... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bmchelix/index.md for the full list. # BMC Helix ITSM (Remedy) Changelog Source: https://docs.stackone.com/connectors/bmchelix/changelog Release history for the BMC Helix ITSM (Remedy) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the incident, change request, problem investigation, known error, work order, task, people, support group, and company list actions for scheduled full record syncs. `bmchelix_list_change_requests`, `bmchelix_list_companies`, `bmchelix_list_incidents`, `bmchelix_list_known_errors`, `bmchelix_list_people`, `bmchelix_list_problem_investigations`, `bmchelix_list_support_groups`, `bmchelix_list_tasks`, `bmchelix_list_work_orders` `bug-fix` Fixed authentication so the AR-JWT token from the login response is sent on requests. # Box Source: https://docs.stackone.com/connectors/box/index How to set up the Box connector, plus the actions and events that are available.
Box
v2.0.0
96 actions · 36 events · 1 auth method
Storage IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authentication provides secure access to Box APIs. Create a Custom App in the Box Developer Console to generat... Optionally, configure receiving Events for Box into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/box/index.md for the full list. ## Events See https://docs.stackone.com/connectors/box/index.md for the full list. # Box Changelog Source: https://docs.stackone.com/connectors/box/changelog Release history for the Box connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking-change` `new-actions` `description-fix` Breaking — the Download File action has been removed. Box delivers file content as a streamed download artifact rather than inline JSON, so the action always returned an empty body; use Get File to read metadata and retrieve content through the returned shared link. Update Task now requires message, because Box rejects any update body that omits it, and Search Content requires query, because this connector does not expose Box's metadata-filter alternative. Added Search Content so an item can be found by name in one call instead of walking folders, Unlock File so a lock applied through Update File can be removed, and Create Metadata Template so templates can be created rather than only read. Update File no longer states that unlocking is unavailable, Copy File explains that omitting name lets Box auto-rename while an explicit name already in use returns 409, and every delete action now returns an explicit confirmation message instead of an empty payload. `box_create_metadata_template`, `box_search_content`, `box_unlock_file` `box_download_file` `box_copy_file`, `box_delete_collaboration`, `box_delete_comment`, `box_delete_file`, `box_delete_file_metadata`, `box_delete_file_version`, `box_delete_folder`, `box_delete_folder_metadata`, `box_delete_group`, `box_delete_task`, `box_delete_task_assignment`, `box_delete_user`, `box_delete_user_avatar`, `box_permanently_delete_file`, `box_permanently_delete_folder`, `box_remove_user_from_group`, `box_update_file`, `box_update_task` `new-feature` Enabled scheduled data sync on five list actions — users, groups, trashed items, webhooks and metadata templates — so these collections can be kept in sync and read without calling Box on every request. Users, groups and trashed items page by offset; webhooks and metadata templates follow Box's marker cursor. Each syncs by full refresh, because the Box API exposes no updated-since filter on these endpoints (change tracking is only available through the Events API). `box_list_groups`, `box_list_metadata_templates`, `box_list_trashed_items`, `box_list_users`, `box_list_webhooks` `guide-changes` Clarified in the OAuth connection guide that the Write content permission is only required when connecting with the default scopes or using actions that create or modify content — read-only connections with custom scopes can omit it. `bug-fix` Fixed action descriptions for update_file (lock/unlock limitation), download_file (empty response clarification), query_by_metadata (enterprise scope format), update_task (completion_rule usage), update_task_assignment (resolution_state requirement), and commented out unsupported expires_at param on update_collaboration. `box_download_file`, `box_query_by_metadata`, `box_update_collaboration`, `box_update_file`, `box_update_task`, `box_update_task_assignment` `new-events` Added programmatic webhook support with 36 event types across files, folders, comments, collaborations, shared links, task assignments, metadata, and webhook lifecycle with connection guide. # Brainier Source: https://docs.stackone.com/connectors/brainier/index How to set up the Brainier connector, plus the actions that are available.
Brainier
v2.1.0
47 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses client credentials to obtain access tokens. Requires creating an API Client in the Brainier LMS administration sett... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/brainier/index.md for the full list. # Brainier Changelog Source: https://docs.stackone.com/connectors/brainier/changelog Release history for the Brainier connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support (full-refresh) for 9 list actions including users, groups, roles, learning objects, user object records, assignments, tags, authors, and bookmarks. `brainier_get_all_object_authors`, `brainier_get_bookmarked_objects`, `brainier_get_multiple_groups_info`, `brainier_get_multiple_learning_objects_info`, `brainier_get_multiple_roles_info`, `brainier_get_multiple_users_info`, `brainier_get_tags`, `brainier_get_user_object_records`, `brainier_list_assignments` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. `brainier_add_user_to_group`, `brainier_create_assigned_group`, `brainier_create_assigned_object`, `brainier_create_assigned_user`, `brainier_create_assignment`, `brainier_create_bookmark`, `brainier_create_group`, `brainier_create_object_access`, `brainier_create_user`, `brainier_create_user_object_record`, `brainier_get_all_object_authors`, `brainier_get_assigned_groups`, `brainier_get_assigned_objects`, `brainier_get_assigned_users`, `brainier_get_assignments_by_user`, `brainier_get_bookmarked_objects`, `brainier_get_class_schedules_info`, `brainier_get_form_options`, `brainier_get_form_questions_and_answers`, `brainier_get_learning_object_comments`, `brainier_get_learning_object_info`, `brainier_get_multiple_groups_info`, `brainier_get_multiple_learning_objects_info`, `brainier_get_multiple_roles_info`, `brainier_get_multiple_users_info`, `brainier_get_object_access`, `brainier_get_object_authors`, `brainier_get_objects_by_author`, `brainier_get_single_group_info`, `brainier_get_single_role_info`, `brainier_get_single_user_info`, `brainier_get_tags`, `brainier_get_user_form_answers`, `brainier_get_user_object_records`, `brainier_list_assignments`, `brainier_remove_assigned_group`, `brainier_remove_assigned_object`, `brainier_remove_assigned_user`, `brainier_remove_bookmark`, `brainier_remove_object_access`, `brainier_remove_user_from_group`, `brainier_send_form_answers`, `brainier_unregister_from_class`, `brainier_update_group_info`, `brainier_update_user_info`, `brainier_update_user_object_record`, `brainier_upload_user_avatar` `guide` Improved connection guide with corrected UI labels, login URL, scope examples, and API Client IP documentation. `brainier_add_user_to_group`, `brainier_create_assigned_group`, `brainier_create_assigned_object`, `brainier_create_assigned_user`, `brainier_create_assignment`, `brainier_create_bookmark`, `brainier_create_group`, `brainier_create_object_access`, `brainier_create_user`, `brainier_create_user_object_record`, `brainier_get_all_object_authors`, `brainier_get_assigned_groups`, `brainier_get_assigned_objects`, `brainier_get_assigned_users`, `brainier_get_assignments_by_user`, `brainier_get_bookmarked_objects`, `brainier_get_class_schedules_info`, `brainier_get_form_options`, `brainier_get_form_questions_and_answers`, `brainier_get_learning_object_comments`, `brainier_get_learning_object_info`, `brainier_get_multiple_groups_info`, `brainier_get_multiple_learning_objects_info`, `brainier_get_multiple_roles_info`, `brainier_get_multiple_users_info`, `brainier_get_object_access`, `brainier_get_object_authors`, `brainier_get_objects_by_author`, `brainier_get_single_group_info`, `brainier_get_single_role_info`, `brainier_get_single_user_info`, `brainier_get_tags`, `brainier_get_user_form_answers`, `brainier_get_user_object_records`, `brainier_list_assignments`, `brainier_remove_assigned_group`, `brainier_remove_assigned_object`, `brainier_remove_assigned_user`, `brainier_remove_bookmark`, `brainier_remove_object_access`, `brainier_remove_user_from_group`, `brainier_send_form_answers`, `brainier_unregister_from_class`, `brainier_update_group_info`, `brainier_update_user_info`, `brainier_update_user_object_record`, `brainier_upload_user_avatar` `guide` Improved connection guide with screenshots. # Braintree Source: https://docs.stackone.com/connectors/braintree/index How to set up the Braintree connector, plus the actions and events that are available.
Braintree
Previewv1.3.2
55 actions · 36 events · 1 auth method
Payments
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Braintree uses HTTP Basic Authentication for server-side API access. The public key serves as the username and the priva... Optionally, configure receiving Events for Braintree into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/braintree/index.md for the full list. ## Events See https://docs.stackone.com/connectors/braintree/index.md for the full list. # Braintree Changelog Source: https://docs.stackone.com/connectors/braintree/changelog Release history for the Braintree connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` The API key connection guide now matches the current Braintree Control Panel, covers the cookie banner and the role an API key needs, and no longer asks for an environment in the connection form. `bug-fix` Added ID-only searches for transactions and subscriptions so large result sets can be counted in one call and loaded in smaller batches, and clarified the subscription search error when a record cannot be loaded. `braintree_search_subscription_ids`, `braintree_search_transaction_ids` `braintree_remove_dispute_evidence`, `braintree_search_customers`, `braintree_search_subscriptions`, `braintree_search_transactions` `new-feature` Added 35 webhook events covering subscriptions, disputes, transactions, refunds, disbursements, payment methods, local payments, Account Updater and the Grant API, delivered through a Native Webhook URL configured in the Braintree Control Panel. `bug-fix` Fixed the subscription plan filter and the transaction status and source filters, which failed or were ignored, and added page selection to subscription and transaction search so results beyond the first 50 can be fetched. Dispute tools now explain how a dispute ID differs from the bank's case number. `braintree_accept_dispute`, `braintree_add_dispute_file_evidence`, `braintree_add_dispute_text_evidence`, `braintree_create_subscription`, `braintree_finalize_dispute`, `braintree_find_all_transaction_line_items`, `braintree_find_dispute`, `braintree_find_transaction`, `braintree_refund_transaction`, `braintree_remove_dispute_evidence`, `braintree_search_disputes`, `braintree_search_subscriptions`, `braintree_search_transactions`, `braintree_submit_transaction_for_partial_settlement`, `braintree_submit_transaction_for_settlement`, `braintree_update_subscription`, `braintree_update_transaction_details`, `braintree_void_transaction` `data-sync` Added data sync support to add-ons, discounts, plans, merchant accounts and dispute search, so these collections can be kept in sync automatically. Merchant accounts and dispute search also gained a page parameter for fetching further result pages. `braintree_list_add_ons`, `braintree_list_discounts`, `braintree_list_merchant_accounts`, `braintree_list_plans`, `braintree_search_disputes` `bug-fix` Fixed single-item add-on, discount and tax identifier lists, plus the dispute transaction-source filter, which previously failed on every request, and added validation that catches conflicting fields before they reach Braintree. Removed what Braintree rejects, answers unreliably or destroys data with — plan modification tokens, removing add-ons and discounts from a plan, the immutable plan billing frequency, the disputed dispute status and the subscription trial-period filter. # Brave Search Source: https://docs.stackone.com/connectors/brave/index How to set up the Brave Search connector, plus the actions that are available.
Brave Search
v1.0.4
13 actions · 1 auth method
Search
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. Uses a subscription token gated by the plans activated on your account. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/brave/index.md for the full list. # Brave Search Changelog Source: https://docs.stackone.com/connectors/brave/changelog Release history for the Brave Search connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `description-fix` Clarified agent-facing descriptions across the search actions. news_search and videos_search now state that offset is a zero-based page index (matching web_search) rather than a per-result offset. web_search documents that count caps the web.results section only and not locations, discussions, faq, videos or news, with resultFilter as the way to keep local-intent responses small, and where the rich.hint callback_key appears; web_rich points at the real rich.hint.callback_key path, the enableRichCallback input and the empty-results behaviour for expired keys. place_search describes the place records it returns and the fields they already include, llm_context_get describes its actual grounding and sources shape, and llm_context_post states that it differs from the GET variant only in transport. Removed the unobserved distance-value claims from the place_search geoloc and units inputs. `brave_llm_context_get`, `brave_llm_context_post`, `brave_news_search`, `brave_place_search`, `brave_videos_search`, `brave_web_rich`, `brave_web_search` `description-fix` `auth` Rewrote the API Key connection guide as a complete portal walkthrough — registration form fields, email verification, plan selection with Search as the recommended starting plan, payment activation and My plans confirmation, and API key creation with the "+ Add API key" dialog's Plan selection and the reveal/copy controls. Added portal screenshots, direct links and left-sidebar navigation for the Available plans and API keys sections, and pointed the API Key field helper link at the API keys page. `bug-fix` Fixed account connection verification failing with a provider 422. The connection test now uses a dedicated minimal web search probe instead of the place search action, which rejects parameterless requests. `bug-fix` Aligned parameters with Brave's API reference. Removed undocumented ui_lang (LLM context) and text_decorations (news search). Added safesearch to both LLM context actions, operators and include_fetch_metadata to news and video search, and lang to spellcheck. Fixed array query params (local POI ids, goggles) serializing as bracket notation the provider rejects, and renamed LLM context snippet/token limits and the goggles parameter to the documented wire names so they take effect. Documented the subscription plan gates on the Answers, Autosuggest, and Spellcheck endpoints and moved those three actions to the preview release stage. Encoded the place_search locator constraints (latitude/longitude pair, exclusive with location) as validation rules and clarified how to obtain web_rich callback keys and ephemeral POI IDs. # Braze Source: https://docs.stackone.com/connectors/braze/index How to set up the Braze connector, plus the actions and events that are available.
Braze
v1.2.0
98 actions · 105 events · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key with appropriate permissions required Optionally, configure receiving Events for Braze into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/braze/index.md for the full list. ## Events See https://docs.stackone.com/connectors/braze/index.md for the full list. # Braze Changelog Source: https://docs.stackone.com/connectors/braze/changelog Release history for the Braze connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` `guide` Added webhook support for 104 Braze events delivered through Currents and transactional email postbacks, and added a permission selector to the API key connection guide. `data-sync` Enabled periodic DataSync for campaigns, canvases, segments, catalogs, preference centers, email templates, and content blocks — with incremental syncing where Braze supports change tracking. `braze_list_campaigns`, `braze_list_canvas`, `braze_list_catalogs`, `braze_list_content_blocks`, `braze_list_email_templates`, `braze_list_preference_centers`, `braze_list_segments` `actions` Clarified agent-facing guidance on several actions — email-list queries need a date range or email, catalog-item id belongs in the path only, triggered campaign/canvas sends require recipients or broadcast, preference-center path id is the API id (not the name), email-template offset must be greater than 0, activated content blocks can't be renamed, and analytics ending_at must be in range. `braze_create_catalog_item`, `braze_create_preference_center_url`, `braze_create_user_alias`, `braze_get_campaign_analytics`, `braze_get_custom_events_analytics`, `braze_get_kpi_uninstalls`, `braze_get_preference_center`, `braze_get_purchases_analytics`, `braze_get_revenue_analytics`, `braze_get_segment_analytics`, `braze_get_send_analytics`, `braze_get_sessions_analytics`, `braze_list_email_templates`, `braze_query_hard_bounced_emails`, `braze_query_unsubscribed_emails`, `braze_schedule_triggered_campaign`, `braze_schedule_triggered_canvas`, `braze_update_content_block`, `braze_update_preference_center`, `braze_update_user_subscription_group_status` `auth` Made the App API Key optional when linking an account — it is now only needed for the KPI and analytics actions. `guide` Rebuilt the API key connection guide with step-by-step portal screenshots. # BreatheHR Source: https://docs.stackone.com/connectors/breathehr/index How to set up the BreatheHR connector, plus the actions that are available.
BreatheHR
v1.1.0
42 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges within BreatheHR. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/breathehr/index.md for the full list. # BreatheHR Changelog Source: https://docs.stackone.com/connectors/breathehr/changelog Release history for the BreatheHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `downstream-change` Added scheduled data sync to fourteen list actions — employees, departments, divisions, locations, salaries, absences, leave requests, sicknesses, benefits, bonuses, company documents, holiday allowances, other leave reasons and statutory holiday countries — so these collections can be kept in sync and searched without calling BreatheHR on every request. Each syncs by full refresh, because the BreatheHR API exposes no updated-since filter on any endpoint. Five of those actions also gained optional page and per_page inputs, which the endpoints accept but do not declare per-endpoint in the provider spec, and are marked preview while that new pagination settles. # BreezyHR Source: https://docs.stackone.com/connectors/breezyhr/index How to set up the BreezyHR connector, plus the actions and events that are available.
BreezyHR
v1.1.0
47 actions · 10 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using your BreezyHR administrator email and password. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/breezyhr/index.md for the full list. ## Events See https://docs.stackone.com/connectors/breezyhr/index.md for the full list. # BreezyHR Changelog Source: https://docs.stackone.com/connectors/breezyhr/changelog Release history for the BreezyHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added Data Sync support for companies, so the company list can be kept in sync and read back without calling BreezyHR on every request. The sync refreshes in full — the BreezyHR v3 API exposes no updated-since filter on any list endpoint. # Brevo Source: https://docs.stackone.com/connectors/brevo/index How to set up the Brevo connector, plus the actions and events that are available.
Brevo
v2.3.2
70 actions · 18 events · 1 auth method
Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key grants full account access with no granular scopes. IP whitelisting available for additional security. Optionally, configure receiving Events for Brevo into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/brevo/index.md for the full list. ## Events See https://docs.stackone.com/connectors/brevo/index.md for the full list. # Brevo Changelog Source: https://docs.stackone.com/connectors/brevo/changelog Release history for the Brevo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `documentation` Moved 32 actions from preview to beta. `brevo_create_and_send_whatsapp_campaign`, `brevo_create_email_campaign`, `brevo_create_update_product`, `brevo_create_whatsapp_template`, `brevo_delete_email_campaign`, `brevo_get_product`, `brevo_list_products`, `brevo_list_whatsapp_templates`, `brevo_manage_order_status`, `brevo_send_transactional_email`, `brevo_send_whatsapp_message`, `brevo_unified_get_me`, `brevo_unified_get_role`, `brevo_unified_get_user`, `brevo_unified_list_roles`, `brevo_unified_list_users`, `brevo_update_email_campaign` `events-guide` Added a webhook setup guide covering how Brevo event subscriptions are created and how events are delivered. `data-sync` Added DataSync support to 11 list actions for periodic record synchronization, with incremental sync on contacts, deals, companies, and products. `brevo_list_companies`, `brevo_list_contacts`, `brevo_list_deals`, `brevo_list_email_campaigns`, `brevo_list_email_templates`, `brevo_list_lists`, `brevo_list_notes`, `brevo_list_products`, `brevo_list_sms_campaigns`, `brevo_list_tasks`, `brevo_list_whatsapp_templates` `bug-fix` Standardized action category capitalization for more consistent portal filters. `brevo_unified_get_me`, `brevo_unified_get_role`, `brevo_unified_get_user`, `brevo_unified_list_roles`, `brevo_unified_list_users` `new-actions` Added unified IAM actions for users, roles, and credentials. `brevo_unified_get_me`, `brevo_unified_get_role`, `brevo_unified_get_user`, `brevo_unified_list_roles`, `brevo_unified_list_users` `events` `new-actions` Added webhook event support for 18 event types (transactional email, marketing email, and contact events) with programmatic setup. # BrightHR Source: https://docs.stackone.com/connectors/brighthr/index How to set up the BrightHR connector, plus the actions that are available.
BrightHR
Betav1.1.0
4 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a BrightHR administrator to register an API application in BrightHR API Management at account.brighthr.com/mana... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/brighthr/index.md for the full list. # BrightHR Changelog Source: https://docs.stackone.com/connectors/brighthr/changelog Release history for the BrightHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for list_employees, so the BrightHR employee directory can be pulled on a schedule using the endpoint's continuation-token pagination. Full-refresh only — the Customer API exposes no updated-since filter on employees. No change to any action's request behaviour or inputs. # Bronto Source: https://docs.stackone.com/connectors/bronto/index How to set up the Bronto connector, plus the actions and events that are available.
Bronto
v1.1.0
77 actions · 4 events · 1 auth method
Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Bronto account using an API key generated from the Bronto app. The key is sent as the X-BRONTO-API-KEY head... Optionally, configure receiving Events for Bronto into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bronto/index.md for the full list. ## Events See https://docs.stackone.com/connectors/bronto/index.md for the full list. # Bronto Changelog Source: https://docs.stackone.com/connectors/bronto/changelog Release history for the Bronto connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for monitors, monitor downtimes, logs, datasets, dashboards, widgets, groups, users, API keys, exports and tags, so these collections can be kept in sync rather than fetched on every request. `bronto_list_all_users`, `bronto_list_api_keys`, `bronto_list_dashboards`, `bronto_list_datasets`, `bronto_list_exports`, `bronto_list_groups`, `bronto_list_logs`, `bronto_list_monitor_downtimes`, `bronto_list_monitors`, `bronto_list_tags_by_name`, `bronto_list_users`, `bronto_list_widgets` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `description-fix` Clarified dashboard and search actions from behavioural testing — append_dashboard_widgets and remove_dashboard_widget now state their exact parameter names and casing and how the attach/detach flow works, list_dashboards warns that its widget fields come back empty even when widgets are attached (use get_dashboard instead), post_search documents that order_by is bare-field-only and cannot be combined with aggregate or group-by queries, and patch_widget notes that each widget_layouts entry requires its id. `bronto_add_group_members`, `bronto_append_dashboard_widgets`, `bronto_append_widget_widgets`, `bronto_assign_dataset_parser`, `bronto_create_dashboard`, `bronto_create_dataset`, `bronto_create_log`, `bronto_create_widget`, `bronto_deactivate_user`, `bronto_delete_api_key`, `bronto_delete_dashboard`, `bronto_delete_export_by_id`, `bronto_delete_group`, `bronto_delete_monitor`, `bronto_delete_tag`, `bronto_delete_user_by_id`, `bronto_delete_widget`, `bronto_detach_dashboard_from_template`, `bronto_get_dashboard`, `bronto_get_dataset_parser`, `bronto_get_export_by_id`, `bronto_get_group`, `bronto_get_monitor`, `bronto_get_monitor_events`, `bronto_get_user_by_id`, `bronto_get_user_preferences`, `bronto_get_widget`, `bronto_list_dashboards`, `bronto_list_dashboards_for_log`, `bronto_list_group_members`, `bronto_list_groups_for_member`, `bronto_list_memberships`, `bronto_list_monitor_notifications`, `bronto_list_monitors_for_log`, `bronto_patch_user_preferences`, `bronto_patch_widget`, `bronto_post_search`, `bronto_reactivate_user`, `bronto_remove_dashboard_widget`, `bronto_remove_group_members`, `bronto_remove_widget_widget`, `bronto_resend_user_invitation`, `bronto_search`, `bronto_unassign_dataset_parser`, `bronto_update_api_key`, `bronto_update_dashboard`, `bronto_update_group`, `bronto_update_monitor`, `bronto_update_monitor_status`, `bronto_update_tag`, `bronto_update_user`, `bronto_update_widget` `description-fix` Clarified action descriptions from behavioural testing — per-log usage endpoints (no log id filter; set usage_type + time window), delta_time_range accepted format, update_group full-replace behaviour, post_search aggregate/group-by syntax, patch_widget layout shape, and get_monitor_events absolute-timestamp guidance. `bronto_create_monitor`, `bronto_get_monitor_events`, `bronto_get_usage`, `bronto_get_usage_by_log_id`, `bronto_get_usage_by_user_per_log_id`, `bronto_patch_widget`, `bronto_post_search`, `bronto_update_group`, `bronto_update_monitor` `guide` Updated the API Key connection guide to help users reach the API Keys screen when they land on the onboarding wizard. `new-connector` Initial Bronto connector covering core log management, search, datasets, monitors, dashboards, widgets, users, groups, API keys, tags, exports, and usage. # Browserbase Source: https://docs.stackone.com/connectors/browserbase/index How to set up the Browserbase connector, plus the actions that are available.
Browserbase
v2.1.0
28 actions · 1 auth method
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key authentication. Requires your API key. The Project ID is optional and supplies a default project for create\_sess... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/browserbase/index.md for the full list. # Browserbase Changelog Source: https://docs.stackone.com/connectors/browserbase/changelog Release history for the Browserbase connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `auth` Added data sync support to list_projects, list_sessions and list_certificates. Made the Project ID connection field optional — it now supplies a default project and can be left blank to pass one explicitly per call. `browserbase_create_context`, `browserbase_create_session`, `browserbase_get_project`, `browserbase_get_project_usage`, `browserbase_list_certificates`, `browserbase_list_projects`, `browserbase_list_sessions` `breaking-change` `new-actions` `removed-actions` `bug-fix` `description-fix` `guide` Breaking — removed update_context, which the provider has withdrawn. Added 10 actions — a session replay surface replacing the deprecated rrweb get_session_recording, certificate upload and list that make proxySettings.caCertificates usable, plus fetch_page, web_search, list_downloads and upload_extension. Expanded create_session with full proxy and browserSettings support, documented the Enterprise gate on browserSettings.os, added an optional project selector to four actions, and fixed the web_search result mapping. Added a connection guide. # Bullhorn Source: https://docs.stackone.com/connectors/bullhorn/index How to set up the Bullhorn connector, plus the actions that are available.
Bullhorn
v2.2.2
80 actions · 2 auth methods
ATS CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Complete guide to set up OAuth 2.0 authentication for Bullhorn ATS/CRM. Obtain data center URLs and OAuth credentials to... OAuth 2.0 using Bullhorn's non-interactive login. The API user's credentials are supplied in the connection fields, so n... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/bullhorn/index.md for the full list. # Bullhorn Changelog Source: https://docs.stackone.com/connectors/bullhorn/changelog Release history for the Bullhorn connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified what quick-find results show for each record type, and corrected search guidance to name the right job-title field and explain that every search term needs a field name. `bullhorn_find_records`, `bullhorn_list_candidates`, `bullhorn_list_client_contacts`, `bullhorn_list_client_corporations`, `bullhorn_list_job_orders`, `bullhorn_list_job_submissions`, `bullhorn_list_notes`, `bullhorn_list_opportunities`, `bullhorn_list_placements`, `bullhorn_list_tasks`, `bullhorn_search_entity`, `bullhorn_search_entity_large_query` `bug-fix` Added a quick-find action that looks up candidates, contacts, companies, jobs, leads and opportunities by name, email, phone or ID in one call, and corrected tool guidance so agents pick dedicated actions over generic ones and know that requesting all fields is refused. `bullhorn_find_records` `bullhorn_create_entity`, `bullhorn_delete_entity`, `bullhorn_get_appointment`, `bullhorn_get_candidate`, `bullhorn_get_client_contact`, `bullhorn_get_client_corporation`, `bullhorn_get_entities`, `bullhorn_get_entity`, `bullhorn_get_job_order`, `bullhorn_get_job_submission`, `bullhorn_get_note`, `bullhorn_get_opportunity`, `bullhorn_get_placement`, `bullhorn_get_task`, `bullhorn_get_tearsheet`, `bullhorn_list_appointments`, `bullhorn_list_associated_entities`, `bullhorn_list_candidates`, `bullhorn_list_client_contacts`, `bullhorn_list_client_corporations`, `bullhorn_list_entity_files`, `bullhorn_list_job_orders`, `bullhorn_list_job_submissions`, `bullhorn_list_notes`, `bullhorn_list_opportunities`, `bullhorn_list_placements`, `bullhorn_list_tasks`, `bullhorn_list_tearsheets`, `bullhorn_query_entity`, `bullhorn_search_entity`, `bullhorn_search_entity_large_query`, `bullhorn_update_entity` `new-actions` `bug-fix` Added tearsheet (shortlist and hot list) management, file attachment listing and content retrieval, and remote-work fields on job orders, and corrected search and query guidance on dates, ID ranges, page sizes and child-record lookups to prevent silent empty or wrong results. `bullhorn_add_tearsheet_candidates`, `bullhorn_add_tearsheet_client_contacts`, `bullhorn_add_tearsheet_job_orders`, `bullhorn_create_tearsheet`, `bullhorn_get_file_content`, `bullhorn_get_tearsheet`, `bullhorn_list_entity_files`, `bullhorn_list_tearsheets`, `bullhorn_remove_tearsheet_candidates`, `bullhorn_remove_tearsheet_client_contacts`, `bullhorn_remove_tearsheet_job_orders`, `bullhorn_update_tearsheet` `bullhorn_create_job_order`, `bullhorn_create_opportunity`, `bullhorn_create_placement`, `bullhorn_delete_file`, `bullhorn_delete_opportunity`, `bullhorn_download_file`, `bullhorn_get_entity`, `bullhorn_get_entity_meta`, `bullhorn_get_opportunity`, `bullhorn_list_appointments`, `bullhorn_list_candidates`, `bullhorn_list_client_contacts`, `bullhorn_list_client_corporations`, `bullhorn_list_job_orders`, `bullhorn_list_job_submissions`, `bullhorn_list_notes`, `bullhorn_list_opportunities`, `bullhorn_list_placements`, `bullhorn_list_tasks`, `bullhorn_query_entity`, `bullhorn_search_entity`, `bullhorn_search_entity_large_query`, `bullhorn_update_job_order`, `bullhorn_update_opportunity`, `bullhorn_update_placement` `bug-fix` Clarified search versus query usage per entity (including tearsheets), supported search syntax and wildcards, decimal range filters, entity-specific fields and associations, and that client corporations cannot be deleted, preventing invalid-request errors and silent empty results. `bullhorn_list_associated_entities`, `bullhorn_list_candidates`, `bullhorn_list_client_contacts`, `bullhorn_list_client_corporations`, `bullhorn_list_job_orders`, `bullhorn_list_job_submissions`, `bullhorn_list_notes`, `bullhorn_list_opportunities`, `bullhorn_list_placements`, `bullhorn_list_searchable_fields`, `bullhorn_list_tasks`, `bullhorn_query_entity`, `bullhorn_search_entity`, `bullhorn_search_entity_large_query`, `bullhorn_update_client_corporation` `bug-fix` Clarified how to set association fields such as owner when mass-updating records, preventing invalid-request errors from incorrectly formatted field values. `bullhorn_mass_update_entity` `data-sync` `improvement` Added data sync support to candidate, client contact, client corporation, job order, job submission, note, opportunity, placement, task, and appointment list actions, so their records can be periodically pulled and kept up to date, with paging handled automatically and results ordered by ID for reliable pagination. `bullhorn_list_appointments`, `bullhorn_list_candidates`, `bullhorn_list_client_contacts`, `bullhorn_list_client_corporations`, `bullhorn_list_job_orders`, `bullhorn_list_job_submissions`, `bullhorn_list_notes`, `bullhorn_list_opportunities`, `bullhorn_list_placements`, `bullhorn_list_tasks` `bug-fix` File downloads now return base64-encoded content that decodes to the exact original file, and appointment date fields include clearer guidance for computing millisecond timestamps. `bullhorn_create_appointment`, `bullhorn_download_file`, `bullhorn_update_appointment` `new-actions` `auth` `breaking` Added opportunity management, file and resume parsing, generic entity read/write, batch reads, searchable-field introspection, and a non-interactive OAuth 2.0 login option. The appointment list action now filters with JPQL where clauses instead of Lucene queries, and the non-functional delete client corporation action was removed (Bullhorn does not support deleting client corporations - archive them via update instead). `bullhorn_create_entity`, `bullhorn_create_job_order`, `bullhorn_create_opportunity`, `bullhorn_delete_entity`, `bullhorn_delete_file`, `bullhorn_delete_opportunity`, `bullhorn_delete_placement`, `bullhorn_download_file`, `bullhorn_get_entities`, `bullhorn_get_opportunity`, `bullhorn_list_associated_entities`, `bullhorn_list_opportunities`, `bullhorn_list_options`, `bullhorn_list_searchable_fields`, `bullhorn_mass_update_entity`, `bullhorn_parse_resume_to_candidate`, `bullhorn_query_entity`, `bullhorn_search_entity_large_query`, `bullhorn_update_entity`, `bullhorn_update_opportunity`, `bullhorn_upload_file` `bullhorn_delete_client_corporation` `bullhorn_create_appointment`, `bullhorn_create_candidate`, `bullhorn_create_client_contact`, `bullhorn_create_client_corporation`, `bullhorn_create_job_submission`, `bullhorn_create_note`, `bullhorn_create_placement`, `bullhorn_create_task`, `bullhorn_delete_appointment`, `bullhorn_delete_candidate`, `bullhorn_delete_client_contact`, `bullhorn_delete_job_order`, `bullhorn_delete_job_submission`, `bullhorn_delete_note`, `bullhorn_delete_task`, `bullhorn_get_appointment`, `bullhorn_get_candidate`, `bullhorn_get_client_contact`, `bullhorn_get_client_corporation`, `bullhorn_get_entity`, `bullhorn_get_entity_meta`, `bullhorn_get_job_order`, `bullhorn_get_job_submission`, `bullhorn_get_note`, `bullhorn_get_placement`, `bullhorn_get_task`, `bullhorn_list_appointments`, `bullhorn_list_candidates`, `bullhorn_list_client_contacts`, `bullhorn_list_client_corporations`, `bullhorn_list_entity_types`, `bullhorn_list_job_orders`, `bullhorn_list_job_submissions`, `bullhorn_list_notes`, `bullhorn_list_placements`, `bullhorn_list_tasks`, `bullhorn_search_entity`, `bullhorn_update_appointment`, `bullhorn_update_candidate`, `bullhorn_update_client_contact`, `bullhorn_update_client_corporation`, `bullhorn_update_job_order`, `bullhorn_update_job_submission`, `bullhorn_update_note`, `bullhorn_update_placement`, `bullhorn_update_task` `bug-fix` Fixed appointment listing by routing it through Bullhorn's query API with JPQL filtering and sorting, and added clear validation errors when update requests contain no fields to update. `bullhorn_list_appointments`, `bullhorn_update_appointment`, `bullhorn_update_client_contact`, `bullhorn_update_client_corporation`, `bullhorn_update_job_order`, `bullhorn_update_placement` `new-actions` Added read/write support for custom fields on client contacts, client corporations, job orders, and placements (matching existing candidate and job submission support), with guidance for discovering account-specific custom field labels. `bullhorn_create_client_contact`, `bullhorn_create_client_corporation`, `bullhorn_create_placement`, `bullhorn_get_client_contact`, `bullhorn_get_client_corporation`, `bullhorn_get_job_order`, `bullhorn_get_placement`, `bullhorn_list_client_contacts`, `bullhorn_list_client_corporations`, `bullhorn_list_job_orders`, `bullhorn_list_placements`, `bullhorn_update_client_contact`, `bullhorn_update_client_corporation`, `bullhorn_update_job_order`, `bullhorn_update_placement` `new-actions` Added read/write support for custom fields on candidates and job submissions, with guidance for discovering account-specific custom field labels. # Cal.com Source: https://docs.stackone.com/connectors/calcom/index How to set up the Cal.com connector, plus the actions and events that are available.
Cal.com
v2.0.1
63 actions · 3 events · 1 auth method
Scheduling IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Cal.com account using an API key for simple, direct access to the Cal.com API. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/calcom/index.md for the full list. ## Events See https://docs.stackone.com/connectors/calcom/index.md for the full list. # Cal.com Changelog Source: https://docs.stackone.com/connectors/calcom/changelog Release history for the Cal.com connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified descriptions for the calendar connection check and event type locations. The connection check now states what each response means, including that Cal.com's 400 credentials-not-found error means the provider is not connected. The locations field now states that public is required on address, link and phone locations, and on update that omitting locations keeps the current ones while a supplied list replaces them all. `calcom_check_calendar_connection`, `calcom_create_event_type`, `calcom_update_event_type` `breaking` `data-sync` `bug-fix` `guide` Added scheduled data sync to eleven list actions, upgraded the API key connection guide with step-by-step screenshots, and fixed action behaviour across bookings, event types, slots and out-of-office. Every action's response now nests the provider payload under a top-level data key. `calcom_add_booking_attendee`, `calcom_add_booking_guests`, `calcom_cancel_booking`, `calcom_check_calendar_connection`, `calcom_confirm_booking`, `calcom_connect_conferencing_app`, `calcom_create_booking`, `calcom_create_event_type`, `calcom_create_out_of_office`, `calcom_create_schedule`, `calcom_create_team`, `calcom_create_webhook`, `calcom_decline_booking`, `calcom_delete_event_type`, `calcom_delete_out_of_office`, `calcom_delete_reserved_slot`, `calcom_delete_schedule`, `calcom_delete_webhook`, `calcom_disconnect_calendar`, `calcom_disconnect_conferencing_app`, `calcom_get_available_slots`, `calcom_get_booking`, `calcom_get_booking_attendee`, `calcom_get_booking_attendees`, `calcom_get_calendar_oauth_url`, `calcom_get_conferencing_oauth_url`, `calcom_get_default_conferencing_app`, `calcom_get_default_schedule`, `calcom_get_event_type`, `calcom_get_me`, `calcom_get_reserved_slot`, `calcom_get_schedule`, `calcom_get_stripe_connect_url`, `calcom_get_team`, `calcom_get_webhook`, `calcom_list_bookings`, `calcom_list_calendars`, `calcom_list_conferencing_apps`, `calcom_list_event_types`, `calcom_list_out_of_office`, `calcom_list_schedules`, `calcom_list_teams`, `calcom_list_webhooks`, `calcom_reschedule_booking`, `calcom_reserve_slot`, `calcom_set_default_conferencing_app`, `calcom_unified_list_groups`, `calcom_unified_list_organizations`, `calcom_unified_list_roles`, `calcom_unified_list_users`, `calcom_update_event_type`, `calcom_update_me`, `calcom_update_out_of_office`, `calcom_update_reserved_slot`, `calcom_update_schedule`, `calcom_update_webhook` `bug-fix` Fixed user and organization lookups that returned an empty result instead of a not-found error. Also fixed user lookups that could only see the caller's own account, and user records missing their IDs on team-based accounts. `calcom_unified_get_group`, `calcom_unified_get_me`, `calcom_unified_get_organization`, `calcom_unified_get_role`, `calcom_unified_get_user`, `calcom_unified_list_groups`, `calcom_unified_list_organizations`, `calcom_unified_list_resource_users`, `calcom_unified_list_roles`, `calcom_unified_list_users` `new-actions` Added inbound webhook event support for booking, meeting, and out-of-office events (auto-provisioned subscription with router and handlers). `calcom_create_webhook`, `calcom_update_webhook` `bug-fix` Fixed unified_list_users silently degrading to a one-element array wrapping /v2/me for callers without org-admin access; it now falls back to enumerating team memberships before returning an empty roster. # Calendly Source: https://docs.stackone.com/connectors/calendly/index How to set up the Calendly connector, plus the actions and events that are available.
Calendly
v1.2.0
47 actions · 12 events · 2 auth methods
Scheduling IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Calendly account securely using OAuth 2.0 authorization for multi-user access and enhanced security. Use a Personal Access Token for quick authentication. Best suited for testing, development, or single-user integrations. Optionally, configure receiving Events for Calendly into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/calendly/index.md for the full list. ## Events See https://docs.stackone.com/connectors/calendly/index.md for the full list. # Calendly Changelog Source: https://docs.stackone.com/connectors/calendly/changelog Release history for the Calendly connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `feature` Enabled Data Sync for the unified users, groups, organizations, and roles lists so they can be periodically synced into StackOne. `calendly_unified_list_groups`, `calendly_unified_list_organizations`, `calendly_unified_list_roles`, `calendly_unified_list_users` `bug-fix` Fixed IAM user last names always coming back empty, and renamed the list users role filter to role_id so it is no longer dropped. `calendly_unified_get_me`, `calendly_unified_get_user`, `calendly_unified_list_users` `new-actions` Added webhook event support for invitee, event type, contact, and routing form submission events (11 events) with programmatic organization-scoped webhook registration. # Campaign Monitor Source: https://docs.stackone.com/connectors/campaignmonitor/index How to set up the Campaign Monitor connector, plus the actions and events that are available.
Campaign Monitor
v1.3.0
84 actions · 4 events · 2 auth methods
Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for single-account integrations. Provides access to all clients and campaigns under your account. Requires registering an OAuth app with Campaign Monitor. Optionally, configure receiving Events for Campaign Monitor into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/campaignmonitor/index.md for the full list. ## Events See https://docs.stackone.com/connectors/campaignmonitor/index.md for the full list. # Campaign Monitor Changelog Source: https://docs.stackone.com/connectors/campaignmonitor/changelog Release history for the Campaign Monitor connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added webhook events for list subscribes, subscriber updates and deactivations. StackOne registers the webhook on each list in the new Webhook List IDs field. `bug-fix` Fixed the unified user list failing with an error on accounts that have administrators. `campaignmonitor_unified_list_users` `data-sync` `guide` `description-fix` Added DataSync for clients and administrators, rebuilt both connection guides with screenshots, and returned confirmation messages from empty-body mutations. `campaignmonitor_activate_webhook`, `campaignmonitor_copy_template`, `campaignmonitor_deactivate_webhook`, `campaignmonitor_delete_administrator`, `campaignmonitor_delete_campaign`, `campaignmonitor_delete_custom_field`, `campaignmonitor_delete_list`, `campaignmonitor_delete_segment`, `campaignmonitor_delete_template`, `campaignmonitor_delete_webhook`, `campaignmonitor_get_subscriber`, `campaignmonitor_list_administrators`, `campaignmonitor_list_clients`, `campaignmonitor_send_campaign_preview`, `campaignmonitor_update_custom_field_options`, `campaignmonitor_update_list`, `campaignmonitor_update_segment`, `campaignmonitor_update_subscriber`, `campaignmonitor_update_template` `new-actions` Added unified IAM actions for users, roles, organizations, credentials, and resource users. # Campfire Source: https://docs.stackone.com/connectors/campfire/index How to set up the Campfire connector, plus the actions that are available.
Campfire
Betav1.1.0
60 actions · 1 auth method
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. Token inherits the permissions of the user role that created it. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/campfire/index.md for the full list. # Campfire Changelog Source: https://docs.stackone.com/connectors/campfire/changelog Release history for the Campfire connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 13 list actions. 8 of them sync incrementally via the last_modified_at__gte filter; the rest refresh in full. # Candid Health Source: https://docs.stackone.com/connectors/candidhealth/index How to set up the Candid Health connector, plus the actions that are available.
Candid Health
Betav1.1.0
45 actions · 1 auth method
Healthcare Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Client ID and Client Secret issued by Candid Health during onboarding. Separate credentials are required per... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/candidhealth/index.md for the full list. # Candid Health Changelog Source: https://docs.stackone.com/connectors/candidhealth/changelog Release history for the Candid Health connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for eight collections - charge captures, coverages, encounters, insurance refunds, patients, payers, tasks and write-offs - so they can be pulled on a schedule. Tasks syncs incrementally via its updated_since filter; the other seven full-refresh because Candid exposes no updated-since filter on them. These eight list actions now use a plain request step instead of paginated_request, so a single call returns one provider page - the response envelope (item_count, items, next_page_token) rather than a pre-flattened array - and callers paginate with the page_token input, which is now wired through to the request. Data Sync walks every page via its own cursor paginator. # Canva Source: https://docs.stackone.com/connectors/canva/index How to set up the Canva connector, plus the actions that are available.
Canva
v2.0.0
36 actions · 2 auth methods
Design IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering a Canva integration in the Developer Portal. Covers designs, folders, assets, comments and brand te... For Canva Enterprise organizations. An organization admin creates a read-only Admin API client in Canva's organization s... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/canva/index.md for the full list. # Canva Changelog Source: https://docs.stackone.com/connectors/canva/changelog Release history for the Canva connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Added an Admin API connection (preview) for Canva Enterprise organizations. Users, teams, roles and the organization now need it and are no longer offered on the OAuth 2.0 connection, and the SCIM Key field is removed. `canva_auth_test`, `canva_create_asset_upload_job`, `canva_create_comment_thread`, `canva_create_design`, `canva_create_export_job`, `canva_create_folder`, `canva_create_reply`, `canva_delete_asset`, `canva_delete_folder`, `canva_get_asset`, `canva_get_asset_upload_job`, `canva_get_brand_template`, `canva_get_comment_thread`, `canva_get_current_user`, `canva_get_design`, `canva_get_export_job`, `canva_get_folder`, `canva_get_user_profile`, `canva_list_brand_templates`, `canva_list_design_pages`, `canva_list_designs`, `canva_list_folder_items`, `canva_list_replies`, `canva_move_folder_item`, `canva_publish_brand_template`, `canva_unified_get_group`, `canva_unified_get_me`, `canva_unified_get_organization`, `canva_unified_get_role`, `canva_unified_get_user`, `canva_unified_list_groups`, `canva_unified_list_organizations`, `canva_unified_list_roles`, `canva_unified_list_users`, `canva_update_asset`, `canva_update_folder` `data-sync` Added data sync support for designs, brand templates, organizations, users, groups, and roles, enabling periodic full-refresh syncing of these collections. `canva_list_brand_templates`, `canva_list_designs`, `canva_unified_list_groups`, `canva_unified_list_organizations`, `canva_unified_list_roles`, `canva_unified_list_users` `bug-fix` Fixed user and group list pagination failing for teams with more than 10 members, and moved the six user, group, and role IAM actions from beta to preview. `canva_unified_get_group`, `canva_unified_get_me`, `canva_unified_get_role`, `canva_unified_get_user`, `canva_unified_list_groups`, `canva_unified_list_organizations`, `canva_unified_list_roles`, `canva_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, and credentials via Canva's SCIM v2 bridge and Connect OAuth API. The connector remains GA, with the REST-based IAM actions (identity, organizations) at GA and the SCIM-dependent actions (users, groups, roles), which require a Canva Enterprise-tier SCIM key, at beta. # Capsule CRM Source: https://docs.stackone.com/connectors/capsulecrm/index How to set up the Capsule CRM connector, plus the actions and events that are available.
Capsule CRM
v6.0.0
136 actions · 19 events · 2 auth methods
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Personal Access Token generated from your own Capsule user account — this is the value StackOne uses as the API k... Requires registering an OAuth application on the Capsule Developer Portal, which signs in with a GitHub account rather t... Optionally, configure receiving Events for Capsule CRM into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/capsulecrm/index.md for the full list. ## Events See https://docs.stackone.com/connectors/capsulecrm/index.md for the full list. # Capsule CRM Changelog Source: https://docs.stackone.com/connectors/capsulecrm/changelog Release history for the Capsule CRM connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Migrated to authRequirements for per-auth-type scope control. Every action now declares its required Capsule scopes (read, write, user_preference) for both API Key and OAuth 2.0 connections, and webhook event actions are restricted to OAuth 2.0. `capsulecrm_add_opportunity_party`, `capsulecrm_add_project_party`, `capsulecrm_archive_board`, `capsulecrm_archive_pipeline`, `capsulecrm_create_board`, `capsulecrm_create_entry`, `capsulecrm_create_milestone`, `capsulecrm_create_opportunity`, `capsulecrm_create_opportunity_custom_field`, `capsulecrm_create_opportunity_tag`, `capsulecrm_create_party`, `capsulecrm_create_party_custom_field`, `capsulecrm_create_party_tag`, `capsulecrm_create_pipeline`, `capsulecrm_create_project`, `capsulecrm_create_project_custom_field`, `capsulecrm_create_project_tag`, `capsulecrm_create_stage`, `capsulecrm_create_task`, `capsulecrm_create_task_category`, `capsulecrm_create_track`, `capsulecrm_create_track_definition`, `capsulecrm_delete_entry`, `capsulecrm_delete_milestone`, `capsulecrm_delete_opportunity`, `capsulecrm_delete_opportunity_custom_field`, `capsulecrm_delete_opportunity_tag`, `capsulecrm_delete_party`, `capsulecrm_delete_party_custom_field`, `capsulecrm_delete_party_tag`, `capsulecrm_delete_project`, `capsulecrm_delete_project_custom_field`, `capsulecrm_delete_project_tag`, `capsulecrm_delete_stage`, `capsulecrm_delete_task`, `capsulecrm_delete_task_category`, `capsulecrm_delete_track_definition`, `capsulecrm_duplicate_pipeline`, `capsulecrm_filter_opportunities`, `capsulecrm_filter_parties`, `capsulecrm_filter_projects`, `capsulecrm_get_attachment`, `capsulecrm_get_board`, `capsulecrm_get_current_user`, `capsulecrm_get_entry`, `capsulecrm_get_milestone`, `capsulecrm_get_multiple_opportunities`, `capsulecrm_get_multiple_parties`, `capsulecrm_get_multiple_pipelines`, `capsulecrm_get_multiple_projects`, `capsulecrm_get_opportunity`, `capsulecrm_get_opportunity_custom_field`, `capsulecrm_get_opportunity_tag`, `capsulecrm_get_party`, `capsulecrm_get_party_custom_field`, `capsulecrm_get_party_tag`, `capsulecrm_get_pipeline`, `capsulecrm_get_project`, `capsulecrm_get_project_custom_field`, `capsulecrm_get_project_tag`, `capsulecrm_get_site`, `capsulecrm_get_stage`, `capsulecrm_get_task`, `capsulecrm_get_task_category`, `capsulecrm_get_team`, `capsulecrm_get_track_definition`, `capsulecrm_get_user`, `capsulecrm_list_activity_types`, `capsulecrm_list_board_stages`, `capsulecrm_list_boards`, `capsulecrm_list_deleted_opportunities`, `capsulecrm_list_deleted_parties`, `capsulecrm_list_deleted_projects`, `capsulecrm_list_entries`, `capsulecrm_list_lost_reasons`, `capsulecrm_list_milestones`, `capsulecrm_list_opportunities`, `capsulecrm_list_opportunity_custom_fields`, `capsulecrm_list_opportunity_entries`, `capsulecrm_list_opportunity_parties`, `capsulecrm_list_opportunity_projects`, `capsulecrm_list_opportunity_tags`, `capsulecrm_list_parties`, `capsulecrm_list_party_custom_fields`, `capsulecrm_list_party_employees`, `capsulecrm_list_party_entries`, `capsulecrm_list_party_opportunities`, `capsulecrm_list_party_projects`, `capsulecrm_list_party_tags`, `capsulecrm_list_pipeline_milestones`, `capsulecrm_list_pipelines`, `capsulecrm_list_project_custom_fields`, `capsulecrm_list_project_entries`, `capsulecrm_list_project_parties`, `capsulecrm_list_project_tags`, `capsulecrm_list_projects`, `capsulecrm_list_stages`, `capsulecrm_list_task_categories`, `capsulecrm_list_tasks`, `capsulecrm_list_teams`, `capsulecrm_list_track_definitions`, `capsulecrm_list_tracks`, `capsulecrm_list_users`, `capsulecrm_remove_opportunity_party`, `capsulecrm_remove_project_party`, `capsulecrm_restore_board`, `capsulecrm_restore_pipeline`, `capsulecrm_search_opportunities`, `capsulecrm_search_parties`, `capsulecrm_search_projects`, `capsulecrm_unified_get_group`, `capsulecrm_unified_get_me`, `capsulecrm_unified_get_organization`, `capsulecrm_unified_get_user`, `capsulecrm_unified_list_groups`, `capsulecrm_unified_list_organizations`, `capsulecrm_unified_list_users`, `capsulecrm_update_board`, `capsulecrm_update_entry`, `capsulecrm_update_milestone`, `capsulecrm_update_opportunity`, `capsulecrm_update_opportunity_custom_field`, `capsulecrm_update_opportunity_tag`, `capsulecrm_update_party`, `capsulecrm_update_party_custom_field`, `capsulecrm_update_party_tag`, `capsulecrm_update_pipeline`, `capsulecrm_update_project`, `capsulecrm_update_project_custom_field`, `capsulecrm_update_project_tag`, `capsulecrm_update_stage`, `capsulecrm_update_task`, `capsulecrm_update_task_category`, `capsulecrm_update_track_definition`, `capsulecrm_update_user`, `capsulecrm_upload_attachment` `data-sync` `bug-fix` `breaking` Added data sync support for 24 list actions, so their records can be periodically pulled into StackOne and kept up to date, with parties, opportunities and projects syncing incrementally. List Tasks status now accepts several statuses at once, and the unsupported since filter was removed from List Entries. `capsulecrm_list_activity_types`, `capsulecrm_list_boards`, `capsulecrm_list_entries`, `capsulecrm_list_lost_reasons`, `capsulecrm_list_milestones`, `capsulecrm_list_opportunities`, `capsulecrm_list_opportunity_custom_fields`, `capsulecrm_list_opportunity_tags`, `capsulecrm_list_parties`, `capsulecrm_list_party_custom_fields`, `capsulecrm_list_party_tags`, `capsulecrm_list_pipelines`, `capsulecrm_list_project_custom_fields`, `capsulecrm_list_project_tags`, `capsulecrm_list_projects`, `capsulecrm_list_stages`, `capsulecrm_list_task_categories`, `capsulecrm_list_tasks`, `capsulecrm_list_teams`, `capsulecrm_list_track_definitions`, `capsulecrm_list_users`, `capsulecrm_unified_list_groups`, `capsulecrm_unified_list_organizations`, `capsulecrm_unified_list_users` `new-actions` `bug-fix` `breaking` Added Create Track to apply a track to an existing contact, opportunity or project, and removed the unsupported tracks input from the update actions; tracks can be supplied when creating a record or applied later through Create Track. `capsulecrm_create_track` `capsulecrm_create_party`, `capsulecrm_create_track_definition`, `capsulecrm_filter_opportunities`, `capsulecrm_filter_projects`, `capsulecrm_update_opportunity`, `capsulecrm_update_party`, `capsulecrm_update_project` `description-fix` Clarified that link custom fields can't be given a value on a record, that link custom fields must be created with a URL, and which website services take a username instead of a full URL. `capsulecrm_create_opportunity`, `capsulecrm_create_opportunity_custom_field`, `capsulecrm_create_party`, `capsulecrm_create_party_custom_field`, `capsulecrm_create_project`, `capsulecrm_create_project_custom_field`, `capsulecrm_update_opportunity`, `capsulecrm_update_party`, `capsulecrm_update_project` `new-actions` `bug-fix` Added an action to list the tracks applied to a party, opportunity or project, and clarified filter fields, date formats and social profile types. Delete and link actions now return a confirmation. `capsulecrm_list_tracks` `capsulecrm_add_opportunity_party`, `capsulecrm_add_project_party`, `capsulecrm_create_opportunity`, `capsulecrm_create_party`, `capsulecrm_create_project`, `capsulecrm_create_track_definition`, `capsulecrm_delete_entry`, `capsulecrm_delete_milestone`, `capsulecrm_delete_opportunity`, `capsulecrm_delete_opportunity_custom_field`, `capsulecrm_delete_opportunity_tag`, `capsulecrm_delete_party`, `capsulecrm_delete_party_custom_field`, `capsulecrm_delete_party_tag`, `capsulecrm_delete_project`, `capsulecrm_delete_project_custom_field`, `capsulecrm_delete_project_tag`, `capsulecrm_delete_stage`, `capsulecrm_delete_task`, `capsulecrm_delete_task_category`, `capsulecrm_delete_track_definition`, `capsulecrm_filter_opportunities`, `capsulecrm_filter_parties`, `capsulecrm_filter_projects`, `capsulecrm_list_opportunities`, `capsulecrm_list_parties`, `capsulecrm_list_projects`, `capsulecrm_list_stages`, `capsulecrm_remove_opportunity_party`, `capsulecrm_remove_project_party`, `capsulecrm_search_parties`, `capsulecrm_update_party`, `capsulecrm_update_track_definition` `breaking` `bug-fix` Fixes fields that could not previously be saved — multi-select and link custom fields, yes/no and numeric custom field values, relative date filters, opportunity milestones, social profile links and task due times. `capsulecrm_create_opportunity`, `capsulecrm_create_opportunity_custom_field`, `capsulecrm_create_party`, `capsulecrm_create_party_custom_field`, `capsulecrm_create_project`, `capsulecrm_create_project_custom_field`, `capsulecrm_create_task`, `capsulecrm_create_track_definition`, `capsulecrm_filter_opportunities`, `capsulecrm_filter_parties`, `capsulecrm_filter_projects`, `capsulecrm_update_opportunity`, `capsulecrm_update_party`, `capsulecrm_update_project`, `capsulecrm_update_task`, `capsulecrm_update_track_definition` `auth` `breaking` `guide` OAuth scopes are now set on the connector profile instead of per linked account. Rewrote both connection guides from the live Capsule interface, with screenshots and corrected screen names. `removed-actions` Removed unified IAM roles actions (unified_list_roles, unified_get_role). Capsule has no role or permission API, so the catalog returned a single invented "user" role with no real access data. The inline roles[] expand on unified_list_users / unified_get_user is removed for the same reason. `capsulecrm_unified_get_role`, `capsulecrm_unified_list_roles` `capsulecrm_unified_get_me`, `capsulecrm_unified_get_organization`, `capsulecrm_unified_get_user`, `capsulecrm_unified_list_organizations`, `capsulecrm_unified_list_users` `new-actions` Added webhook event support for contact, project, opportunity, task, and user events (19 events) with programmatic REST Hook registration. `new-actions` Added unified IAM actions for users, roles, groups, organizations, and credentials. # Carta Source: https://docs.stackone.com/connectors/carta/index How to set up the Carta connector, plus the actions that are available.
Carta
Betav1.1.0
62 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Carta developer app to authorize StackOne to access cap-table, fund, portfolio, and compensation data on yo... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/carta/index.md for the full list. # Carta Changelog Source: https://docs.stackone.com/connectors/carta/changelog Release history for the Carta connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added Data Sync support for corporations, issuers, investor firms, and shareholder portfolios, so those records can be pulled into StackOne on a schedule and kept up to date. All four refresh in full on every run, because Carta exposes no updated-since filter on these endpoints. # Cascade HR Source: https://docs.stackone.com/connectors/cascadehr/index How to set up the Cascade HR connector, plus the actions that are available.
Cascade HR
v1.2.0
56 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 Client Credentials authentication for IRIS Cascade HR API. Requires Client Key and Client Secret obtained from... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cascadehr/index.md for the full list. # Cascade HR Changelog Source: https://docs.stackone.com/connectors/cascadehr/changelog Release history for the Cascade HR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to all 15 list actions, each syncing incrementally via a new optional updatedAfter filter on LastModifiedOn. # CatalystOne Source: https://docs.stackone.com/connectors/catalystone/index How to set up the CatalystOne connector, plus the actions that are available.
CatalystOne
Betav1.1.0
36 actions · 2 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires API client credentials (Client ID and Client Secret) configured in CatalystOne administration. Contact your Cat... User-based OAuth2 flow with PKCE for applications acting on behalf of individual users. Requires a registered OAuth clie... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/catalystone/index.md for the full list. # CatalystOne Changelog Source: https://docs.stackone.com/connectors/catalystone/changelog Release history for the CatalystOne connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for HRDP and SCIM users, groups, and schemas, plus projects, project categories, and performance reviews. All syncs are full-refresh — no CatalystOne list endpoint exposes an updated-since filter. # CATS Source: https://docs.stackone.com/connectors/cats/index How to set up the CATS connector, plus the actions and events that are available.
CATS
v1.3.0
56 actions · 24 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). CATS uses a static API key sent as a Token in the Authorization header. Optionally, configure receiving Events for CATS into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cats/index.md for the full list. ## Events See https://docs.stackone.com/connectors/cats/index.md for the full list. # CATS Changelog Source: https://docs.stackone.com/connectors/cats/changelog Release history for the CATS connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for activities, candidates, companies, contacts, jobs, pipelines, tasks, and users. `cats_list_activities`, `cats_list_candidates`, `cats_list_companies`, `cats_list_contacts`, `cats_list_jobs`, `cats_list_pipelines`, `cats_list_tasks`, `cats_list_users` `webhook` `new-actions` Added webhook support for all 24 CATS events. StackOne creates and removes the CATS subscription automatically, so nothing needs configuring in CATS. `bug-fix` `description-fix` Documented that text filters match whole words rather than substrings, so partial-word searches no longer silently return nothing, and explained how the count and total fields on every paginated response indicate whether more pages remain. `cats_create_pipeline`, `cats_filter_activities`, `cats_filter_candidates`, `cats_filter_companies`, `cats_filter_contacts`, `cats_filter_jobs`, `cats_filter_pipelines`, `cats_list_activities`, `cats_list_candidate_pipelines`, `cats_list_candidate_tasks`, `cats_list_candidates`, `cats_list_companies`, `cats_list_company_departments`, `cats_list_company_tasks`, `cats_list_contact_tasks`, `cats_list_contacts`, `cats_list_job_pipelines`, `cats_list_job_tasks`, `cats_list_jobs`, `cats_list_pipelines`, `cats_list_tasks`, `cats_list_users`, `cats_search_activities`, `cats_search_candidates`, `cats_search_companies`, `cats_search_contacts`, `cats_search_jobs` `new-actions` `new-fields` `bug-fix` `description-fix` Added list_users and get_user actions plus new check_duplicate, query, and value_boolean inputs, and fixed input typing, filter handling, and partial-update behavior across the existing actions. `cats_get_user`, `cats_list_users` `cats_create_candidate`, `cats_create_company`, `cats_create_contact`, `cats_create_job`, `cats_create_task`, `cats_delete_pipeline`, `cats_filter_activities`, `cats_filter_candidates`, `cats_filter_companies`, `cats_filter_contacts`, `cats_filter_jobs`, `cats_filter_pipelines`, `cats_update_candidate`, `cats_update_company`, `cats_update_contact`, `cats_update_job` `bug-fix` Improved the API Key connection guide: clarified the Subdomain example, added the missing Administration navigation step, corrected the Hub API Key field description, and added portal screenshots to the guide steps. # Cezanne Recruit (Occupop) Source: https://docs.stackone.com/connectors/cezannerecruit/index How to set up the Cezanne Recruit (Occupop) connector, plus the actions and events that are available.
Cezanne Recruit (Occupop)
Betav1.1.0
20 actions · 6 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Cezanne Recruit (Occupop) Private API token. Generate one from Settings > API Settings inside your Cezanne Re... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cezannerecruit/index.md for the full list. ## Events See https://docs.stackone.com/connectors/cezannerecruit/index.md for the full list. # Cezanne Recruit (Occupop) Changelog Source: https://docs.stackone.com/connectors/cezannerecruit/changelog Release history for the Cezanne Recruit (Occupop) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Enabled scheduled data sync on six list actions: candidates, live jobs, closed jobs, company labels, custom field definitions and webhooks. These collections can now be kept in sync and read without calling Cezanne Recruit on every request. All six refresh in full each run, because no Occupop list endpoint exposes an updated-since filter. Job-scoped candidates and hiring flow steps are not included, because both require a job id and a sync could only ever cover a single job. # CezanneHR Source: https://docs.stackone.com/connectors/cezannehr/index How to set up the CezanneHR connector, plus the actions and events that are available.
CezanneHR
v1.2.0
54 actions · 7 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authentication using Client ID and Client Secret from your CezanneHR Authorised Application. Optionally, configure receiving Events for CezanneHR into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cezannehr/index.md for the full list. ## Events See https://docs.stackone.com/connectors/cezannehr/index.md for the full list. # CezanneHR Changelog Source: https://docs.stackone.com/connectors/cezannehr/changelog Release history for the CezanneHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for absence events, absence event details, absence plans, addresses, bank details, benefits, companies, compensation, compensation history, cost centres, employees, employment contracts, employments, jobs, org units, photos, reporting lines, timesheets, timesheet details, timesheet activities, timesheet plans and timesheet projects, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the CezanneHR API exposes no updated-since filter a sync can use. `cezannehr_list_absence_event_details`, `cezannehr_list_absence_events`, `cezannehr_list_absence_plans`, `cezannehr_list_addresses`, `cezannehr_list_bank_details`, `cezannehr_list_benefits`, `cezannehr_list_companies`, `cezannehr_list_compensation`, `cezannehr_list_cost_centres`, `cezannehr_list_employee_timesheet_details`, `cezannehr_list_employee_timesheets`, `cezannehr_list_employees`, `cezannehr_list_employment_contracts`, `cezannehr_list_employments`, `cezannehr_list_jobs`, `cezannehr_list_org_units`, `cezannehr_list_photos`, `cezannehr_list_reports_to`, `cezannehr_list_timesheet_activities`, `cezannehr_list_timesheet_plans`, `cezannehr_list_timesheet_projects`, `cezannehr_search_compensation_history` `new-actions` Added inbound webhook event support across 9 record-type triggers (addresses, bank details, communications, marital status, person details, person development activities, absences, leavers, new hires) with a computed Native Webhook URL and setup guide. # Chargebee Source: https://docs.stackone.com/connectors/chargebee/index How to set up the Chargebee connector, plus the actions and events that are available.
Chargebee
v1.3.0
60 actions · 1 event · 1 auth method
Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses HTTP Basic Auth with an API key as the username and a dummy password. API keys are environment-specific (test vs li... Optionally, configure receiving Events for Chargebee into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/chargebee/index.md for the full list. ## Events See https://docs.stackone.com/connectors/chargebee/index.md for the full list. # Chargebee Changelog Source: https://docs.stackone.com/connectors/chargebee/changelog Release history for the Chargebee connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhooks` Added native inbound webhook support. Chargebee delivers a single generic event envelope for all ~209 event types (subscription, customer, payment, invoice, credit note, transaction, order, item catalog, coupon, and more), so one generic event action handles every type via its event_type; webhooks are configured manually in the Chargebee admin console since Chargebee has no API to manage them. Each connection shows a Native Webhook URL to register. `data-sync` Added Data Sync support for customers, subscriptions, invoices, credit notes, transactions, orders, coupons, items, item families, item prices, events, hosted pages, payment sources, and business entities. `chargebee_list_business_entities`, `chargebee_list_coupons`, `chargebee_list_credit_notes`, `chargebee_list_customers`, `chargebee_list_events`, `chargebee_list_hosted_pages`, `chargebee_list_invoices`, `chargebee_list_item_families`, `chargebee_list_item_prices`, `chargebee_list_items`, `chargebee_list_orders`, `chargebee_list_payment_sources`, `chargebee_list_subscriptions`, `chargebee_list_transactions` `guide-changes` `guide-images` Rebuilt the API Key connection guide with step-by-step screenshots of the Chargebee portal, corrected the on-screen labels for generating a Full-Access key and finding your site name, clarified that the environment is selected in StackOne Hub during account linking, and sharpened the API Key and Site Name field descriptions. `bug-fix` Fixed credit note creation, usage deletion, and tiered pricing on item prices, and added a billing country field for customer VAT validation. Improved several action descriptions for clearer usage. # Chargify (Maxio) Source: https://docs.stackone.com/connectors/chargify/index How to set up the Chargify (Maxio) connector, plus the actions that are available.
Chargify (Maxio)
v1.1.0
125 actions · 1 auth method
Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). A Chargify (Maxio) API Key with admin access is required. A free sandbox is available for testing. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/chargify/index.md for the full list. # Chargify (Maxio) Changelog Source: https://docs.stackone.com/connectors/chargify/changelog Release history for the Chargify (Maxio) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync v2 (full-refresh) to 16 list actions including customers, subscriptions, invoices, products, components, coupons, events, and more. `chargify_list_components`, `chargify_list_coupons`, `chargify_list_credit_notes`, `chargify_list_customers`, `chargify_list_endpoints`, `chargify_list_events`, `chargify_list_invoice_events`, `chargify_list_invoices`, `chargify_list_offers`, `chargify_list_payment_profiles`, `chargify_list_product_families`, `chargify_list_products`, `chargify_list_reason_codes`, `chargify_list_subscription_groups`, `chargify_list_subscriptions`, `chargify_list_webhooks` `action-descriptions` `action-release-stage` Fixed activate_subscription description (on_hold not activatable), added BEHAVIOUR notes for update_component metered constraints, improved disambiguation for metadata/coupon/invoice actions, marked create_subscription/create_customer/create_prepayment as preview due to untestable gateway and integration dependencies. `chargify_activate_subscription`, `chargify_create_customer`, `chargify_create_prepayment`, `chargify_create_subscription`, `chargify_list_coupons`, `chargify_list_metadata`, `chargify_record_payment_for_multiple_invoices`, `chargify_update_component`, `chargify_update_metadata` `action-descriptions` `action-inputs` Improved action descriptions and input validation: added enum values for tax_exempt_reason, clarified required fields for metafield updates, and enhanced details for components, invoices, and prepayments. `chargify_activate_subscription`, `chargify_create_customer`, `chargify_create_metadata`, `chargify_create_prepayment`, `chargify_create_product`, `chargify_create_product_price_point`, `chargify_create_quantity_component`, `chargify_list_invoices`, `chargify_list_metadata_for_resource_type`, `chargify_read_subscription_component`, `chargify_update_component`, `chargify_update_customer`, `chargify_update_metafield`, `chargify_update_product` `guide` Added the missing New API Key dialog step to the connection guide, and corrected the guide and the API Key field description to state that the key can be viewed again later from the API Keys list. `guide` Updated connection guide with improved instructions, screenshots, and field descriptions. # CharlieHR Source: https://docs.stackone.com/connectors/charliehr/index How to set up the CharlieHR connector, plus the actions that are available.
CharlieHR
v1.1.0
22 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Admin or Super Admin access is required to generate API keys. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/charliehr/index.md for the full list. # CharlieHR Changelog Source: https://docs.stackone.com/connectors/charliehr/changelog Release history for the CharlieHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support to eight list actions — Team Members, Bank Accounts, Leave Allowances, Leave Requests, Offices, Salaries, Team Member Note Types, and Teams — so their records can be kept in sync on a schedule. All syncs use CharlieHR's page-numbered pagination (25 records per page) as full refreshes, since the API exposes no updated-since filter. # ChartHop Source: https://docs.stackone.com/connectors/charthop/index How to set up the ChartHop connector, plus the actions that are available.
ChartHop
Betav1.1.0
67 actions · 1 auth method
HRIS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a ChartHop app API token. Apps are created by emailing support@charthop.com. The token is generated when ChartH... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/charthop/index.md for the full list. # ChartHop Changelog Source: https://docs.stackone.com/connectors/charthop/changelog Release history for the ChartHop connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for persons, jobs, groups, orgs, changes, events, comp reviews, bands, fields, categories, forms, form responses, processes, scenarios, tasks, time off, time off policies, users and roles, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the ChartHop API exposes no updated-since filter a sync can use. # Checkmk Source: https://docs.stackone.com/connectors/checkmk/index How to set up the Checkmk connector, plus the actions and events that are available.
Checkmk
v1.3.0
68 actions · 20 events · 1 auth method
Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using a Checkmk automation user's credentials. Automation users are machine accounts designed for API acces... Optionally, configure receiving Events for Checkmk into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/checkmk/index.md for the full list. ## Events See https://docs.stackone.com/connectors/checkmk/index.md for the full list. # Checkmk Changelog Source: https://docs.stackone.com/connectors/checkmk/changelog Release history for the Checkmk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added 20 webhook events for host and service state changes, acknowledgements, flapping and downtimes, delivered by a StackOne notification script, plus a webhook setup guide. `data-sync` Added DataSync support to 11 list actions (hosts, folders, users, groups, downtimes, rulesets, notification rules, and monitored hosts/services) so their collections can be periodically synced. `checkmk_list_all_services`, `checkmk_list_contact_groups`, `checkmk_list_downtimes`, `checkmk_list_folders`, `checkmk_list_host_groups`, `checkmk_list_hosts`, `checkmk_list_monitored_hosts`, `checkmk_list_notification_rules`, `checkmk_list_rulesets`, `checkmk_list_service_groups`, `checkmk_list_users` `description-fix` Improved rule action guidance — documented the host_name condition shape, clarified that numeric rule thresholds must be integers, and noted that rule IDs for moving a rule come from listing rules first. `checkmk_create_rule`, `checkmk_move_rule`, `checkmk_update_rule` `bug-fix` `description-fix` Fixed comment and downtime by-query 400s (target fields now mutually exclusive per type), removed the crash-prone refresh/tabula_rasa discovery modes, and constrained the notification-rule plugin option to a validated enum. # Checkr Source: https://docs.stackone.com/connectors/checkr/index How to set up the Checkr connector, plus the actions that are available.
Checkr
Betav1.2.0
67 actions · 1 auth method
Background Checks IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses HTTP Basic Auth with an API key as the username and an empty password. API keys are environment-specific (productio... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/checkr/index.md for the full list. # Checkr Changelog Source: https://docs.stackone.com/connectors/checkr/changelog Release history for the Checkr connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for candidates, invitations, subscriptions, packages, programs, geos, users, webhooks, and unified IAM users and organizations. `checkr_list_candidates`, `checkr_list_geos`, `checkr_list_invitations`, `checkr_list_packages`, `checkr_list_programs`, `checkr_list_subscriptions`, `checkr_list_users`, `checkr_list_webhooks`, `checkr_unified_list_organizations`, `checkr_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `checkr_unified_get_me`, `checkr_unified_get_organization`, `checkr_unified_get_user`, `checkr_unified_list_organizations`, `checkr_unified_list_users` `new-actions` Added unified IAM actions for users, organizations, and credentials. # Cin7 Core Source: https://docs.stackone.com/connectors/cin7core/index How to set up the Cin7 Core connector, plus the actions and events that are available.
Cin7 Core
Previewv0.1.0
54 actions · 11 events · 1 auth method
ERP CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an Account ID and API Application Key generated on the Cin7 Core API setup page. Keys do not expire and inherit... Optionally, configure receiving Events for Cin7 Core into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cin7core/index.md for the full list. ## Events See https://docs.stackone.com/connectors/cin7core/index.md for the full list. # Cin7 Core Changelog Source: https://docs.stackone.com/connectors/cin7core/changelog Release history for the Cin7 Core connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `new-events` `data-sync` Initial release with 54 actions across customers, products, purchases, sales, stock, suppliers, webhooks and reference data, covering order-to-cash and procure-to-pay plus stock adjustments, transfers and stock takes. Includes inbound webhook events for all 32 Cin7 Core event types with automatic registration, and Data Sync on 15 list actions. # CircleCI Source: https://docs.stackone.com/connectors/circleci/index How to set up the CircleCI connector, plus the actions and events that are available.
CircleCI
v1.2.0
82 actions · 2 events · 1 auth method
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your CircleCI account using a Personal API Token generated from the CircleCI web application. Optionally, configure receiving Events for CircleCI into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/circleci/index.md for the full list. ## Events See https://docs.stackone.com/connectors/circleci/index.md for the full list. # CircleCI Changelog Source: https://docs.stackone.com/connectors/circleci/changelog Release history for the CircleCI connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added webhook event support for workflow-completed and job-completed, with a setup guide. StackOne registers the outbound webhook on the configured CircleCI project when the account is connected and removes it on disconnect. Two new optional connection fields support this - Project ID, which scopes the webhook, and Webhook Signing Secret, which CircleCI uses to sign each delivery. Accounts that do not use events are unaffected. `data-sync` `new-feature` Enabled scheduled data sync on List Collaborations, so the set of organizations the connected user belongs to can be kept in sync and read without calling CircleCI on every request. It refreshes in full each run, because /me/collaborations returns the whole set in one call and exposes no updated-since filter. No other list action qualifies - every other collection endpoint in the CircleCI API requires an organization or project scope, which a sync schedule cannot enumerate. # ClayHR Source: https://docs.stackone.com/connectors/clayhr/index How to set up the ClayHR connector, plus the actions that are available.
ClayHR
Betav1.1.0
50 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using your ClayHR API Key and User ID. Generate your API key from My Integrations in the ClayHR app. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/clayhr/index.md for the full list. # ClayHR Changelog Source: https://docs.stackone.com/connectors/clayhr/changelog Release history for the ClayHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 11 list actions (users, currencies, expense reports, expense types, document library, forms, performance review templates, performance review assignments, projects, assigned tests, and PTO policies). Users sync incrementally via the lastupdatets filter; the rest refresh in full. # Clear Books Source: https://docs.stackone.com/connectors/clearbooks/index How to set up the Clear Books connector, plus the actions that are available.
Clear Books
Previewv0.1.0
44 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering a confidential OAuth application in the Clear Books developer portal, which can only be accessed on... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/clearbooks/index.md for the full list. # Clear Books Changelog Source: https://docs.stackone.com/connectors/clearbooks/changelog Release history for the Clear Books connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `data-sync` Initial release covering account codes, allocations, bank accounts, businesses, customers, payments, purchase documents, sales documents, suppliers and VAT reference data via the Clear Books REST API. # ClickUp Source: https://docs.stackone.com/connectors/clickup/index How to set up the ClickUp connector, plus the actions and events that are available.
ClickUp
v1.2.0
95 actions · 28 events · 2 auth methods
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for personal use, scripts, and testing. Provides access scoped to your own ClickUp account. Requires creating an OAuth app in ClickUp workspace settings. Admin or Owner permissions needed to register the app. Optionally, configure receiving Events for ClickUp into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/clickup/index.md for the full list. ## Events See https://docs.stackone.com/connectors/clickup/index.md for the full list. # ClickUp Changelog Source: https://docs.stackone.com/connectors/clickup/changelog Release history for the ClickUp connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added webhook support for 28 ClickUp events across tasks, lists, folders, spaces, goals, and key results, with the subscription created and removed automatically when an account connects or disconnects. `data-sync` Enabled DataSync v2 on nine list actions — get_filtered_team_tasks (page-paginated with incremental sync via the date_updated_gt watermark), search_docs (cursor-paginated), get_task_templates (page-paginated), get_spaces, get_goals, get_user_groups, get_custom_task_types, get_authorized_workspaces, and get_time_entries (full-refresh). get_filtered_team_tasks' date_updated_gt input now accepts a number or a numeric string so the incremental watermark round-trips, and get_task_templates' page input is now optional. # ClinicalTrials.gov Source: https://docs.stackone.com/connectors/clinicaltrialsgov/index How to set up the ClinicalTrials.gov connector, plus the actions that are available.
ClinicalTrials.gov
v1.1.0
9 actions · 1 auth method
Healthcare
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The ClinicalTrials.gov API v2 is fully public and read-only. No credentials, API key, or OAuth flow are required — simpl... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/clinicaltrialsgov/index.md for the full list. # ClinicalTrials.gov Changelog Source: https://docs.stackone.com/connectors/clinicaltrialsgov/changelog Release history for the ClinicalTrials.gov connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to five reference collections — the study data model and search areas, the enumeration catalogue, and the field value and field size statistics — so these can be kept in sync and searched without calling ClinicalTrials.gov on every request. Each is returned in full by a single request and syncs by full refresh, because ClinicalTrials.gov offers no last-updated filter. `clinicaltrialsgov_get_studies_metadata`, `clinicaltrialsgov_list_field_sizes_stats`, `clinicaltrialsgov_list_field_values_stats`, `clinicaltrialsgov_list_study_enums`, `clinicaltrialsgov_list_study_search_areas` `bug-fix` Clarified list_studies descriptions from MCP behavioural testing — query_cond/query_intr search expansion, valid fields (400 on unknown), agg_filters facet catalog (studyType/ages/phase), subset-count via count_total, and response-size guidance; noted list_field_sizes_stats unsupported fields. # Clockify Source: https://docs.stackone.com/connectors/clockify/index How to set up the Clockify connector, plus the actions and events that are available.
Clockify
Previewv1.3.0
116 actions · 50 events · 1 auth method
Time Tracking IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate your API key from your Clockify Profile Settings. Users with workspaces on subdomains must generate workspace-s... Optionally, configure receiving Events for Clockify into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/clockify/index.md for the full list. ## Events See https://docs.stackone.com/connectors/clockify/index.md for the full list. # Clockify Changelog Source: https://docs.stackone.com/connectors/clockify/changelog Release history for the Clockify connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to four collection actions — workspaces, and the unified groups, organizations and roles — so these collections can be kept in sync and searched without calling Clockify on every request. The unified groups page through results automatically; workspaces and the unified organizations and roles are returned in full by a single request. All sync by full refresh, because Clockify's list endpoints offer no last-updated filter. `clockify_list_workspaces`, `clockify_unified_list_groups`, `clockify_unified_list_organizations`, `clockify_unified_list_roles` `bug-fix` Standardized action category capitalization for more consistent portal filters. `clockify_unified_get_group`, `clockify_unified_get_me`, `clockify_unified_get_organization`, `clockify_unified_get_role`, `clockify_unified_get_user`, `clockify_unified_list_groups`, `clockify_unified_list_organizations`, `clockify_unified_list_resource_types`, `clockify_unified_list_resource_users`, `clockify_unified_list_roles`, `clockify_unified_list_users` `new-actions` Added unified IAM actions for users, groups, roles, organizations, credentials, and resource users (project-scoped). `clockify_unified_get_group`, `clockify_unified_get_me`, `clockify_unified_get_organization`, `clockify_unified_get_role`, `clockify_unified_get_user`, `clockify_unified_list_groups`, `clockify_unified_list_organizations`, `clockify_unified_list_resource_types`, `clockify_unified_list_resource_users`, `clockify_unified_list_roles`, `clockify_unified_list_users` `new-actions` Added inbound webhook events (auto-provisioned, per-event) with 50 event handlers and a webhook setup guide. # Clockwork Recruiting Source: https://docs.stackone.com/connectors/clockwork/index How to set up the Clockwork Recruiting connector, plus the actions that are available.
Clockwork Recruiting
Betav1.2.0
16 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires four credentials — API Key, API Secret, Firm Service Key, and your Firm Name (the subdomain in the API base pat... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/clockwork/index.md for the full list. # Clockwork Recruiting Changelog Source: https://docs.stackone.com/connectors/clockwork/changelog Release history for the Clockwork Recruiting connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the input-free list and search actions (people, companies, projects, people search, and project search) for scheduled full record syncs. `clockwork_list_companies`, `clockwork_list_people`, `clockwork_list_projects`, `clockwork_search_people`, `clockwork_search_projects` `bug-fix` `description-fix` Added the documented page_number pagination parameter to all list actions, the ids filter to search_people, and the name, do_not_contact and associated_to_project filters to list_companies. The personCustomFieldsAttributes object on create_person now declares its firmFieldId and value fields, and every action description has been rewritten from placeholder text. `clockwork_create_candidacy`, `clockwork_create_person`, `clockwork_delete_candidacy`, `clockwork_delete_person`, `clockwork_get_candidacy`, `clockwork_get_company`, `clockwork_get_person`, `clockwork_get_project`, `clockwork_list_candidacies`, `clockwork_list_companies`, `clockwork_list_people`, `clockwork_list_projects`, `clockwork_search_people`, `clockwork_search_projects`, `clockwork_update_candidacy`, `clockwork_update_person` `bug-fix` Fixed create_person, update_person, create_candidacy, and update_candidacy sending body fields as flat dotted keys. Request bodies are now nested under the person or candidacy key. # Close Source: https://docs.stackone.com/connectors/close/index How to set up the Close connector, plus the actions and events that are available.
Close
v1.2.0
81 actions · 14 events · 2 auth methods
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth app in Close. All OAuth apps receive full read/write access with automatic token refresh. No app registration required. API key inherits the permissions of the user who created it. Optionally, configure receiving Events for Close into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/close/index.md for the full list. ## Events See https://docs.stackone.com/connectors/close/index.md for the full list. # Close Changelog Source: https://docs.stackone.com/connectors/close/changelog Release history for the Close connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added scheduled data sync to the leads, contacts, opportunities, activities, tasks, users and other list actions, so their records can be kept in sync on a schedule; opportunities and tasks sync incrementally via date_updated, the rest by full refresh. `close_list_activities`, `close_list_calls`, `close_list_contact_custom_fields`, `close_list_contacts`, `close_list_emails`, `close_list_groups`, `close_list_lead_custom_fields`, `close_list_lead_statuses`, `close_list_leads`, `close_list_meetings`, `close_list_notes`, `close_list_opportunities`, `close_list_opportunity_custom_fields`, `close_list_opportunity_statuses`, `close_list_pipelines`, `close_list_roles`, `close_list_sequences`, `close_list_smart_views`, `close_list_sms`, `close_list_tasks`, `close_list_user_availabilities`, `close_list_users` `bug-fix` Delete actions now return a confirmation payload instead of an empty body, and clarified action guidance for activity list limits (max 100), logging external calls, opportunity smart-view queries, role visibility fields, and lead custom-field name uniqueness. `close_create_call`, `close_create_lead_custom_field`, `close_create_role`, `close_create_smart_view`, `close_delete_contact`, `close_delete_group`, `close_delete_lead`, `close_delete_lead_custom_field`, `close_delete_lead_status`, `close_delete_note`, `close_delete_opportunity`, `close_delete_opportunity_status`, `close_delete_pipeline`, `close_delete_role`, `close_delete_smart_view`, `close_delete_task`, `close_list_activities`, `close_list_calls`, `close_list_emails`, `close_list_meetings`, `close_list_notes`, `close_list_sms`, `close_update_role` `webhook` `new-actions` Added webhook event support. Close now delivers real-time notifications for lead, contact, opportunity, activity (calls, emails, SMS, notes, meetings, status changes), task, sequence subscription, and membership events, with the webhook subscription created and removed automatically when you connect or disconnect your account. # Cloudflare Source: https://docs.stackone.com/connectors/cloudflare/index How to set up the Cloudflare connector, plus the actions that are available.
Cloudflare
Previewv1.2.1
150 actions · 1 auth method
Infrastructure Observability IAM Security
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create an API Token from the Cloudflare dashboard with appropriate permissions for the resources you want to manage. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cloudflare/index.md for the full list. # Cloudflare Changelog Source: https://docs.stackone.com/connectors/cloudflare/changelog Release history for the Cloudflare connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed the Workers builds actions (list_workers_builds, get_workers_build, get_workers_build_logs), which called endpoints that do not exist. They now use the Workers Builds API, and list_workers_builds resolves the script name to its Worker tag. `cloudflare_get_workers_build`, `cloudflare_get_workers_build_logs`, `cloudflare_list_workers_builds` `data-sync` Added scheduled data sync to the input-free account and zone-wide list actions (zones, accounts, members, roles, audit logs, DNS zones, KV namespaces, R2 buckets, D1 databases, AI gateways, tunnels, load balancer pools and monitors, rulesets, rules lists, logpush jobs, pages projects, and workers scripts) for scheduled full record syncs. `cloudflare_list_account_logpush_jobs`, `cloudflare_list_account_members`, `cloudflare_list_account_roles`, `cloudflare_list_account_rulesets`, `cloudflare_list_accounts`, `cloudflare_list_ai_gateways`, `cloudflare_list_audit_logs`, `cloudflare_list_d1_databases`, `cloudflare_list_ip_access_rules`, `cloudflare_list_kv_namespaces`, `cloudflare_list_load_balancer_monitors`, `cloudflare_list_load_balancer_pools`, `cloudflare_list_pages_projects`, `cloudflare_list_r2_buckets`, `cloudflare_list_rules_lists`, `cloudflare_list_tunnels`, `cloudflare_list_workers_scripts`, `cloudflare_list_zones` `bug-fix` Fixed user, role, organization, and group lists being silently truncated on large accounts. They now page through the full result set instead of stopping at a fixed page count. `cloudflare_unified_get_group`, `cloudflare_unified_get_me`, `cloudflare_unified_list_groups`, `cloudflare_unified_list_organizations`, `cloudflare_unified_list_roles`, `cloudflare_unified_list_users` `bugfix` Fixed IAM list pagination on unified_list_users, unified_list_roles, unified_list_organizations, and unified_list_groups — replaced the raw provider page number forwarded as the StackOne cursor (which caused a 400 Invalid Cursor Format past page 1) with a fixed page fan-out plus StackOne virtual pagination. `cloudflare_unified_list_groups`, `cloudflare_unified_list_organizations`, `cloudflare_unified_list_roles`, `cloudflare_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, and credentials (preview); groups ships at beta pending Zero Trust Access verification on a QA account. # CloudTalk Source: https://docs.stackone.com/connectors/cloudtalk/index How to set up the CloudTalk connector, plus the actions that are available.
CloudTalk
Previewv0.1.0
8 actions · 1 auth method
Telephony IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a CloudTalk API key pair (Access Key ID and Secret) created by an administrator. The key belongs to the company acc... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cloudtalk/index.md for the full list. # CloudTalk Changelog Source: https://docs.stackone.com/connectors/cloudtalk/changelog Release history for the CloudTalk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Initial CloudTalk connector for reviewing who can sign in to a CloudTalk account, covering agents and agent groups, including unified IAM users, groups and connection details. # Cloudways Source: https://docs.stackone.com/connectors/cloudways/index How to set up the Cloudways connector, plus the actions that are available.
Cloudways
Betav1.1.0
82 actions · 1 auth method
Infrastructure
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Cloudways account with API access enabled. Uses email and API key to obtain a short-lived access token (60 mi... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cloudways/index.md for the full list. # Cloudways Changelog Source: https://docs.stackone.com/connectors/cloudways/changelog Release history for the Cloudways connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the server, project, alert, alert channel, and provider list actions for scheduled full record syncs. # Clover Source: https://docs.stackone.com/connectors/clover/index How to set up the Clover connector, plus the actions that are available.
Clover
Betav3.1.0
64 actions · 1 auth method
E-Commerce Payments
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authentication with expiring tokens required Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/clover/index.md for the full list. # Clover Changelog Source: https://docs.stackone.com/connectors/clover/changelog Release history for the Clover connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support with offset-based pagination to 19 list actions across all resources. `clover_list_cash_events`, `clover_list_categories`, `clover_list_customers`, `clover_list_devices`, `clover_list_discounts`, `clover_list_employee_shifts`, `clover_list_employees`, `clover_list_inventory_items`, `clover_list_modifiers`, `clover_list_order_line_items`, `clover_list_order_payments`, `clover_list_order_types`, `clover_list_orders`, `clover_list_payments`, `clover_list_refunds`, `clover_list_roles`, `clover_list_tags`, `clover_list_tax_rates`, `clover_list_tenders` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # Cohere Source: https://docs.stackone.com/connectors/cohere/index How to set up the Cohere connector, plus the actions that are available.
Cohere
v1.1.0
14 actions · 1 auth method
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Cohere account using an API Key from the Cohere Dashboard. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cohere/index.md for the full list. # Cohere Changelog Source: https://docs.stackone.com/connectors/cohere/changelog Release history for the Cohere connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `feature` Added DataSync support to list_datasets for periodic full-refresh syncing of datasets. `cohere_list_datasets` `bug-fix` Removed the unsupported 'unknown' value from the list_datasets validationStatus filter (it always returned 400); regenerated the API Key connection guide with screenshots and updated the API Key field description. # Comeet Source: https://docs.stackone.com/connectors/comeet/index How to set up the Comeet connector, plus the actions that are available.
Comeet
Betav1.1.0
26 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). JWT Bearer token authentication using API key and secret. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/comeet/index.md for the full list. # Comeet Changelog Source: https://docs.stackone.com/connectors/comeet/changelog Release history for the Comeet connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for candidates, positions, leads, locations, and questionnaires, with incremental syncing for candidates and positions. # Confluence Source: https://docs.stackone.com/connectors/confluence/index How to set up the Confluence connector, plus the actions that are available.
Confluence
v1.4.1
145 actions · 3 auth methods
Knowledge Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Each account brings its own OAuth app, with the client credentials entered at connect time. Use this when a customer req... One OAuth app registered once on the connector profile, reused by every account that connects. Each user still authorize... The steps in this guide require access to a Confluence workspace. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/confluence/index.md for the full list. # Confluence Changelog Source: https://docs.stackone.com/connectors/confluence/changelog Release history for the Confluence connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Listing the users with access to a space now pages through the whole space instead of stopping partway on spaces with many permissions. `confluence_unified_list_resource_users`, `confluence_unified_list_users` `new-feature` Added DataSync support to the unified list actions for drives, files, folders, users, groups, and roles, so they can be synced on a schedule. `confluence_unified_list_drives`, `confluence_unified_list_files`, `confluence_unified_list_folders`, `confluence_unified_list_groups`, `confluence_unified_list_roles`, `confluence_unified_list_users` `description-fix` Clarified the read:orgs:admin scope the organization admin API key needs, and added the missing setup guide for it on the API Key auth block. `confluence_unified_get_organization`, `confluence_unified_list_organizations` `feature` Added OAuth authentication. Fixed organization list pagination and user name listings. `confluence_create_attachment`, `confluence_create_attachment_labels`, `confluence_create_blog_post`, `confluence_create_blogpost_labels`, `confluence_create_blogpost_property`, `confluence_create_database`, `confluence_create_folder`, `confluence_create_footer_comment`, `confluence_create_inline_comment`, `confluence_create_page`, `confluence_create_page_labels`, `confluence_create_page_property`, `confluence_create_smart_link`, `confluence_create_space`, `confluence_create_space_property`, `confluence_create_whiteboard`, `confluence_delete_attachment`, `confluence_delete_attachment_label`, `confluence_delete_blog_post`, `confluence_delete_blogpost_label`, `confluence_delete_blogpost_property`, `confluence_delete_database`, `confluence_delete_folder`, `confluence_delete_footer_comment`, `confluence_delete_inline_comment`, `confluence_delete_page`, `confluence_delete_page_label`, `confluence_delete_page_property`, `confluence_delete_smart_link`, `confluence_delete_space`, `confluence_delete_space_default_classification_level`, `confluence_delete_space_property_by_id`, `confluence_delete_whiteboard`, `confluence_get_anonymous_user`, `confluence_get_attachment`, `confluence_get_attachment_comments`, `confluence_get_attachment_labels`, `confluence_get_blog_post`, `confluence_get_blog_post_footer_comments`, `confluence_get_blog_post_inline_comments`, `confluence_get_blog_post_like_count`, `confluence_get_blog_post_like_users`, `confluence_get_blog_posts_for_label`, `confluence_get_blog_posts_in_space`, `confluence_get_blogpost_classification_level`, `confluence_get_blogpost_labels`, `confluence_get_blogpost_properties`, `confluence_get_blogpost_property_by_id`, `confluence_get_blogpost_versions`, `confluence_get_current_user`, `confluence_get_custom_content_comments`, `confluence_get_custom_content_labels`, `confluence_get_database`, `confluence_get_database_classification_level`, `confluence_get_folder`, `confluence_get_footer_comment`, `confluence_get_footer_comment_children`, `confluence_get_footer_comment_like_count`, `confluence_get_footer_comment_like_users`, `confluence_get_inline_comment`, `confluence_get_inline_comment_children`, `confluence_get_inline_comment_like_count`, `confluence_get_inline_comment_like_users`, `confluence_get_multiple_users`, `confluence_get_page`, `confluence_get_page_ancestors`, `confluence_get_page_children`, `confluence_get_page_classification_level`, `confluence_get_page_footer_comments`, `confluence_get_page_inline_comments`, `confluence_get_page_labels`, `confluence_get_page_like_count`, `confluence_get_page_like_users`, `confluence_get_page_properties`, `confluence_get_page_property_by_id`, `confluence_get_page_versions`, `confluence_get_smart_link`, `confluence_get_space_by_id`, `confluence_get_space_content_labels`, `confluence_get_space_default_classification_level`, `confluence_get_space_labels`, `confluence_get_space_permissions_assignments`, `confluence_get_space_properties`, `confluence_get_space_property_by_id`, `confluence_get_space_role_mode`, `confluence_get_spaces`, `confluence_get_task`, `confluence_get_user`, `confluence_get_user_email`, `confluence_get_user_emails_bulk`, `confluence_get_user_groups`, `confluence_get_whiteboard`, `confluence_get_whiteboard_classification_level`, `confluence_list_attachments`, `confluence_list_blog_posts`, `confluence_list_blogpost_attachments`, `confluence_list_classification_levels`, `confluence_list_custom_content_attachments`, `confluence_list_footer_comments`, `confluence_list_inline_comments`, `confluence_list_label_attachments`, `confluence_list_labels`, `confluence_list_page_attachments`, `confluence_list_pages`, `confluence_list_pages_for_label`, `confluence_list_pages_in_space`, `confluence_list_tasks`, `confluence_reset_blogpost_classification_level`, `confluence_reset_database_classification_level`, `confluence_reset_page_classification_level`, `confluence_reset_whiteboard_classification_level`, `confluence_unified_download_file`, `confluence_unified_get_drive`, `confluence_unified_get_file`, `confluence_unified_get_folder`, `confluence_unified_get_group`, `confluence_unified_get_me`, `confluence_unified_get_organization`, `confluence_unified_get_role`, `confluence_unified_get_user`, `confluence_unified_list_drives`, `confluence_unified_list_files`, `confluence_unified_list_folders`, `confluence_unified_list_groups`, `confluence_unified_list_organizations`, `confluence_unified_list_resource_types`, `confluence_unified_list_resource_users`, `confluence_unified_list_roles`, `confluence_unified_list_users`, `confluence_unified_upload_file`, `confluence_update_blog_post`, `confluence_update_blogpost_classification_level`, `confluence_update_blogpost_property`, `confluence_update_database_classification_level`, `confluence_update_footer_comment`, `confluence_update_inline_comment`, `confluence_update_page`, `confluence_update_page_classification_level`, `confluence_update_page_property`, `confluence_update_page_title`, `confluence_update_space`, `confluence_update_space_default_classification_level`, `confluence_update_space_property_by_id`, `confluence_update_task`, `confluence_update_whiteboard_classification_level` `bug-fix` Fixed IAM actions — unified_get_role now accepts the id its own list action returns, and unified_list_resource_users reads up to 250 space permission rows per call instead of 25. `confluence_unified_get_group`, `confluence_unified_get_me`, `confluence_unified_get_role`, `confluence_unified_get_user`, `confluence_unified_list_resource_users`, `confluence_unified_list_users` `new-actions` Added unified IAM actions for users, groups, organizations, roles, resource users, and credentials. # Constant Contact Source: https://docs.stackone.com/connectors/constantcontact/index How to set up the Constant Contact connector, plus the actions that are available.
Constant Contact
v2.1.0
78 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 provides secure delegated access to Constant Contact resources. You need a Constant Contact developer account... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/constantcontact/index.md for the full list. # Constant Contact Changelog Source: https://docs.stackone.com/connectors/constantcontact/changelog Release history for the Constant Contact connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Adds DataSync support for user privileges, account emails, tags and custom fields. Tags and custom fields now always request a full page, using the account maximums Constant Contact documents (500 tags, 100 custom fields), so a sync returns the whole collection. Other collections are not synced because Constant Contact returns the paging cursor only inside a link URL, which leaves no way to read past the first page. `constantcontact_get_user_privileges`, `constantcontact_list_account_emails`, `constantcontact_list_custom_fields`, `constantcontact_list_tags` `guide` Updated OAuth 2.0 connection guide. It now walks the developer portal screen by screen with screenshots, matches the portal's actual labels, covers the redirect URI and secret confirmation dialogs, and explains which scopes to grant. `breaking` `bug-fix` `description-fix` Breaking — filtering an email bounces report by bounce code now takes several codes as a list rather than a single value. Also corrects input guidance across contacts, contact lists, custom fields, segments, events, campaigns, bulk imports, account emails and reporting so calls succeed on the first attempt. # Contentful Source: https://docs.stackone.com/connectors/contentful/index How to set up the Contentful connector, plus the actions and events that are available.
Contentful
v1.2.0
80 actions · 18 events · 2 auth methods
CMS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for single-user automation. The token inherits the role permissions of the user who generated it. Recommended for multi-user apps. Requires registering an OAuth application in Contentful. Access tokens expire after 30... Optionally, configure receiving Events for Contentful into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/contentful/index.md for the full list. ## Events See https://docs.stackone.com/connectors/contentful/index.md for the full list. # Contentful Changelog Source: https://docs.stackone.com/connectors/contentful/changelog Release history for the Contentful connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added DataSync support to list_spaces and list_organizations, so their records can be synced into StackOne on a schedule and read back without calling Contentful each time. Both refresh in full on every run, since Contentful exposes no change filter that applies to these two endpoints. `contentful_list_organizations`, `contentful_list_spaces` `new-actions` `guide-images` `config-update` `bug-fix` Added CMS actions for roles and organization memberships. Added image references to connection guides for Personal Access Token, OAuth 2.0, and webhook setup. Removed spaceId configField — space_id is now a per-call input on all space-scoped CMS actions (entries, assets, content types) so callers control which space they target. Added Webhook Space IDs configField for comma-separated multi-space webhook delivery using the iterator pattern. Fixed membership_id path param inconsistency in update/delete organization membership actions. Fixed resource link for list_organization_periodic_usages. # Copper Source: https://docs.stackone.com/connectors/copper/index How to set up the Copper connector, plus the actions that are available.
Copper
v2.0.0
58 actions · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for single-user integrations and internal tools. Quick to set up with no app registration — generate an API key fro... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/copper/index.md for the full list. # Copper Changelog Source: https://docs.stackone.com/connectors/copper/changelog Release history for the Copper connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking-change` `bug-fix` `docs` Removed schema fields that Copper's API rejects with 422 — socials.category "klout", create_activity type.category "system", related_resource on update_project/task, company_id/company_name on update_person, status_ids on list_projects, priority_ids on list_opportunities. Added missing custom_fields item properties (custom_field_definition_id required, value) on create_task/update_task and made custom_fields[].value polymorphic (string/number/boolean/number[]) across leads/people/companies/opportunities/projects/tasks to match Copper's data_type-dependent value shape. Documented custom_fields silent-drop and list_people.name exact-match behavior; enhanced relate_record_to_entity description as the sole cross-record link tool. Trimmed connection testActions to fetch_api_user. # Cornerstone Source: https://docs.stackone.com/connectors/cornerstone/index How to set up the Cornerstone connector, plus the actions and events that are available.
Cornerstone
v2.2.0
21 actions · 30 events · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). This connector powers a non-partnership integration allowing you to aggregate learning material and user data from Corne... Optionally, configure receiving Events for Cornerstone into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cornerstone/index.md for the full list. ## Events See https://docs.stackone.com/connectors/cornerstone/index.md for the full list. # Cornerstone Changelog Source: https://docs.stackone.com/connectors/cornerstone/changelog Release history for the Cornerstone connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` `guide` Added webhook event support for 29 Cornerstone Edge events covering training, employee, skills and purchase activity, with a setup guide for registering the webhook in your portal. `cornerstone_create_express_class`, `cornerstone_create_learning_object`, `cornerstone_get_approvals`, `cornerstone_get_assigned_trainings`, `cornerstone_get_inbox_items`, `cornerstone_get_sessions`, `cornerstone_get_suggested_trainings`, `cornerstone_get_tasks`, `cornerstone_get_transcripts_legacy` `data-sync` Added DataSync support for catalog search, transcript search, learning assignments, and users. `cornerstone_list_users`, `cornerstone_search_catalog`, `cornerstone_search_learning_assignments`, `cornerstone_search_transcripts` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # Coupa Source: https://docs.stackone.com/connectors/coupa/index How to set up the Coupa connector, plus the actions that are available.
Coupa
Betav0.2.0
80 actions · 1 auth method
Accounting Procurement Payments IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 client credentials from a Coupa OAuth2/OpenID Connect client. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/coupa/index.md for the full list. # Coupa Changelog Source: https://docs.stackone.com/connectors/coupa/changelog Release history for the Coupa connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for suppliers, supplier information and sites, users, invoices, payments, purchase orders, requisitions, contracts, expense reports, approvals, receipt requests, budget lines, account types, account validation rules, payment terms, tax registrations and financial counterparties. `coupa_list_account_types`, `coupa_list_account_validation_rules`, `coupa_list_approvals`, `coupa_list_budget_lines`, `coupa_list_contracts`, `coupa_list_expense_reports`, `coupa_list_financial_counterparties`, `coupa_list_invoices`, `coupa_list_payment_terms`, `coupa_list_payments`, `coupa_list_purchase_orders`, `coupa_list_receipt_requests`, `coupa_list_requisitions`, `coupa_list_supplier_information`, `coupa_list_supplier_information_sites`, `coupa_list_suppliers`, `coupa_list_tax_registrations`, `coupa_list_users` `new-connector` Initial action mapping of the Coupa connector for the Coupa Core API. # Coursera Source: https://docs.stackone.com/connectors/coursera/index How to set up the Coursera connector, plus the actions that are available.
Coursera
Previewv1.2.1
19 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an app on the Coursera Developer Portal. Uses client credentials grant with API Key and Client Secr... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/coursera/index.md for the full list. # Coursera Changelog Source: https://docs.stackone.com/connectors/coursera/changelog Release history for the Coursera connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `fixes` Added data synchronisation support for list users, list content, list programs, and list user assignments actions. List content supports incremental sync via modified-since filtering. Connector guide level fixes. `data-sync` Added data synchronisation support for list users, list content, list programs, and list user assignments actions. List content supports incremental sync via modified-since filtering. `coursera_list_content`, `coursera_list_programs`, `coursera_list_users`, `coursera_list_users_assignments` `new-actions` `bug-fixes` Added program membership actions (get, create, delete), connection guide improvements, action dependency hints in field descriptions, boolean condition fixes, and removed unsupported ids parameter from list programs. # Coveto Source: https://docs.stackone.com/connectors/coveto/index How to set up the Coveto connector, plus the actions that are available.
Coveto
Betav0.2.0
68 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an API key created in coveto (Einstellungen » REST API) and sent in the X-API-Key header. Each key is scoped per re... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/coveto/index.md for the full list. # Coveto Changelog Source: https://docs.stackone.com/connectors/coveto/changelog Release history for the Coveto connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the applicant, company, contact, job, requisition, location, task, and user list actions for scheduled full record syncs. `coveto_list_applicant_statuses`, `coveto_list_applicants`, `coveto_list_companies`, `coveto_list_company_statuses`, `coveto_list_contacts`, `coveto_list_job_adverts`, `coveto_list_job_categories`, `coveto_list_jobs`, `coveto_list_locations`, `coveto_list_requisitions`, `coveto_list_task_boards`, `coveto_list_task_types`, `coveto_list_tasks`, `coveto_list_users` `new-connector` Initial release of the Coveto connector — 68 actions across applicants, companies, contacts, jobs, job adverts, requisitions, locations, tasks, files, and users. API key (X-API-Key) auth with tenant-specific base URL and a full connection guide. # Crelate Source: https://docs.stackone.com/connectors/crelate/index How to set up the Crelate connector, plus the actions that are available.
Crelate
Betav1.1.2
61 actions · 1 auth method
ATS CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). An API key generated from your Crelate account is required. API access must be enabled for your organization by an admin... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/crelate/index.md for the full list. # Crelate Changelog Source: https://docs.stackone.com/connectors/crelate/changelog Release history for the Crelate connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed Update Contact failing when setting Current Position, which now takes the company, job title and dates. `crelate_update_contact` `bug-fix` Fixed Apply to Job so Crelate receives the applicant details and resume file and creates the application. `crelate_apply_to_job` `data-sync` Added data sync support for activities, applications, companies, contacts, jobs, notes, placements, and tasks, so these records can be periodically pulled into StackOne and kept up to date, with paging handled automatically and later syncs fetching only recently modified records. # CrelioHealth Source: https://docs.stackone.com/connectors/creliohealth/index How to set up the CrelioHealth connector, plus the actions that are available.
CrelioHealth
Betav0.1.0
24 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a lab API token issued by CrelioHealth during onboarding. The token travels in the request path, query string or fo... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/creliohealth/index.md for the full list. # CrelioHealth Changelog Source: https://docs.stackone.com/connectors/creliohealth/changelog Release history for the CrelioHealth connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial release covering patients, appointments, home collection, billing, lab directory data, reports and sample operations. # Culture Amp Source: https://docs.stackone.com/connectors/cultureamp/index How to set up the Culture Amp connector, plus the actions that are available.
Culture Amp
Betav1.1.0
9 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Machine-to-machine OAuth 2.0 client credentials flow. A short-lived JWT access token (~1 hour) is obtained from the toke... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cultureamp/index.md for the full list. # Culture Amp Changelog Source: https://docs.stackone.com/connectors/cultureamp/changelog Release history for the Culture Amp connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for employees, performance cycles and manager reviews, with incremental sync on performance cycles and manager reviews. # Customer.io Source: https://docs.stackone.com/connectors/customerio/index How to set up the Customer.io connector, plus the actions and events that are available.
Customer.io
Previewv2.2.0
57 actions · 72 events · 2 auth methods
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect to the Customer.io App API using an App API Key (bearer token). Provides access to campaigns, broadcasts, segmen... Connect to the Customer.io Track API using a Site ID and Track API Key (HTTP Basic auth). Use this to send behavioral da... Optionally, configure receiving Events for Customer.io into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/customerio/index.md for the full list. ## Events See https://docs.stackone.com/connectors/customerio/index.md for the full list. # Customer.io Changelog Source: https://docs.stackone.com/connectors/customerio/changelog Release history for the Customer.io connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Added 72 webhook events from Customer.io reporting webhooks, covering subscription changes and message activity across email, in-app, push, SMS, WhatsApp, Slack and webhook messages. StackOne creates the reporting webhook when an App API account connects and deletes it on disconnect. `data-sync` `new-feature` Enabled Data Sync on 9 App API list actions, so activities, exports, messages, newsletters, reporting webhooks, segments, sender identities, snippets and transactional messages stay in sync. `customerio_list_activities`, `customerio_list_exports`, `customerio_list_messages`, `customerio_list_newsletters`, `customerio_list_reporting_webhooks`, `customerio_list_segments`, `customerio_list_sender_identities`, `customerio_list_snippets`, `customerio_list_transactional` `auth-improvements` Split the single API Key auth into two separate auth methods - App API Key (bearer) and Track API Key (basic) - so each shows only its own required fields and test action. # CyberArk (Privilege Cloud) Source: https://docs.stackone.com/connectors/cyberark/index How to set up the CyberArk (Privilege Cloud) connector, plus the actions that are available.
CyberArk (Privilege Cloud)
Betav1.1.0
31 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses OAuth 2.0 client credentials flow with a CyberArk Identity service account. Token endpoint is on the identity tenan... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/cyberark/index.md for the full list. # CyberArk (Privilege Cloud) Changelog Source: https://docs.stackone.com/connectors/cyberark/changelog Release history for the CyberArk (Privilege Cloud) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added datasync support for accounts, users, groups, safes, and platforms with offset-based pagination. Added pagination inputs to users and groups endpoints. # Dagster Source: https://docs.stackone.com/connectors/dagster/index How to set up the Dagster connector, plus the actions that are available.
Dagster
v1.2.0
52 actions · 1 auth method
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Dagster+ uses a User Token sent in the \`Dagster-Cloud-Api-Token\` header. The connector also needs your organization slug... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dagster/index.md for the full list. # Dagster Changelog Source: https://docs.stackone.com/connectors/dagster/changelog Release history for the Dagster connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for asset nodes, code repositories and code location statuses, so these collections can be synced on a schedule and read back without calling Dagster each time. All three refresh in full on every run, because no Dagster GraphQL resolver on these endpoints accepts an updated-since filter or returns a delta token. `dagster_list_asset_nodes`, `dagster_list_location_statuses`, `dagster_list_repositories` `description-fix` Clarified 6 action descriptions to guide AI agents through backfill inspection, run-config validation, and dynamic-partition workflows, and documented the HTTP 502 wrapping on wrong `repositoryName` for list_sensors and list_schedules. # Dashlane Source: https://docs.stackone.com/connectors/dashlane/index How to set up the Dashlane connector, plus the actions that are available.
Dashlane
Previewv0.1.0
5 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Dashlane authenticates every public API request with a bearer API key of the form DLP\_teamUuid\_accessKey\_secretKey, sent... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dashlane/index.md for the full list. # Dashlane Changelog Source: https://docs.stackone.com/connectors/dashlane/changelog Release history for the Dashlane connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial release covering team members, member device information, team password health history, plan status, and the Dashlane server time endpoint. # Databricks Source: https://docs.stackone.com/connectors/databricks/index How to set up the Databricks connector, plus the actions that are available.
Databricks
v2.0.0
72 actions · 3 auth methods
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for account-level identity provisioning and admin automation of users, groups, and service principals. Use OAuth 2.0 with a Databricks service principal for machine-to-machine authentication. Best for automated workflows wh... Use OAuth 2.0 for interactive user authentication. Best when actions should be performed on behalf of a specific user ra... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/databricks/index.md for the full list. # Databricks Changelog Source: https://docs.stackone.com/connectors/databricks/changelog Release history for the Databricks connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` `bug-fix` `data-sync` Migrated to authRequirements for per-auth-type scope control, so SCIM Token connections run only the user, group and service principal actions. Added scheduled data sync for the SCIM user, group and service principal lists, and fixed creating and updating Unity Catalog metastores. `databricks_add_group_member`, `databricks_assign_metastore_to_workspace`, `databricks_create_budget`, `databricks_create_credential`, `databricks_create_custom_app_integration`, `databricks_create_group`, `databricks_create_ip_access_list`, `databricks_create_log_delivery_config`, `databricks_create_metastore`, `databricks_create_network`, `databricks_create_or_update_workspace_permission_assignment`, `databricks_create_service_principal`, `databricks_create_service_principal_secret`, `databricks_create_user`, `databricks_delete_budget`, `databricks_delete_credential`, `databricks_delete_custom_app_integration`, `databricks_delete_group`, `databricks_delete_ip_access_list`, `databricks_delete_metastore`, `databricks_delete_metastore_from_workspace`, `databricks_delete_network`, `databricks_delete_service_principal`, `databricks_delete_service_principal_secret`, `databricks_delete_user`, `databricks_delete_workspace_permission_assignment`, `databricks_download_billable_usage`, `databricks_get_budget`, `databricks_get_credential`, `databricks_get_custom_app_integration`, `databricks_get_group`, `databricks_get_ip_access_list`, `databricks_get_log_delivery_config`, `databricks_get_metastore`, `databricks_get_network`, `databricks_get_service_principal`, `databricks_get_storage_configuration`, `databricks_get_user`, `databricks_get_workspace`, `databricks_get_workspace_metastore`, `databricks_list_budgets`, `databricks_list_credentials`, `databricks_list_custom_app_integrations`, `databricks_list_groups`, `databricks_list_ip_access_lists`, `databricks_list_log_delivery_configs`, `databricks_list_metastore_workspace_assignments`, `databricks_list_metastores`, `databricks_list_networks`, `databricks_list_service_principal_secrets`, `databricks_list_service_principals`, `databricks_list_storage_configurations`, `databricks_list_users`, `databricks_list_workspace_permission_assignments`, `databricks_list_workspaces`, `databricks_remove_group_member`, `databricks_unified_get_group`, `databricks_unified_get_me`, `databricks_unified_get_organization`, `databricks_unified_get_role`, `databricks_unified_get_user`, `databricks_unified_list_groups`, `databricks_unified_list_organizations`, `databricks_unified_list_roles`, `databricks_unified_list_users`, `databricks_update_budget`, `databricks_update_custom_app_integration`, `databricks_update_group`, `databricks_update_log_delivery_config`, `databricks_update_metastore`, `databricks_update_service_principal`, `databricks_update_user` `feature` `bug-fix` Added scheduled data sync for users, groups, roles, workspaces, metastores, networks, credentials, storage configurations, budgets, IP access lists, log delivery configurations and OAuth app integrations. Fixed unified user and group lists failing once an account holds more than 100 users or groups. `databricks_list_budgets`, `databricks_list_credentials`, `databricks_list_custom_app_integrations`, `databricks_list_ip_access_lists`, `databricks_list_log_delivery_configs`, `databricks_list_metastores`, `databricks_list_networks`, `databricks_list_storage_configurations`, `databricks_list_workspaces`, `databricks_unified_list_groups`, `databricks_unified_list_roles`, `databricks_unified_list_users` `bug-fix` Fixed user and group lists stopping after the first page, role lookups by id rejecting valid ids, and unrecognized roles being misreported as the standard user role. Listing users now supports an expand parameter, and user roles are returned only when requested through it. # Databricks Workspace Source: https://docs.stackone.com/connectors/databricksworkspace/index How to set up the Databricks Workspace connector, plus the actions and events that are available.
Databricks Workspace
v1.3.0
51 actions · 6 events · 1 auth method
Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use OAuth 2.0 with a Databricks service principal for machine-to-machine authentication against workspace APIs. Best for... Optionally, configure receiving Events for Databricks Workspace into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/databricksworkspace/index.md for the full list. ## Events See https://docs.stackone.com/connectors/databricksworkspace/index.md for the full list. # Databricks Workspace Changelog Source: https://docs.stackone.com/connectors/databricksworkspace/changelog Release history for the Databricks Workspace connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-feature` Added webhook events for job runs — start, success, failure and duration warning, plus other job notifications — delivered through a StackOne notification destination created automatically when events are enabled. The connecting service principal must be a workspace admin. `data-sync` `new-feature` Added data sync support to 7 list actions — catalogs, clusters, jobs, job runs, SQL warehouses, Spark versions and node types. All sync by full refresh, as none of these endpoints exposes an updated-since filter. `databricksworkspace_list_catalogs`, `databricksworkspace_list_clusters`, `databricksworkspace_list_job_runs`, `databricksworkspace_list_jobs`, `databricksworkspace_list_node_types`, `databricksworkspace_list_spark_versions`, `databricksworkspace_list_sql_warehouses` `description-fix` Documented that list_tables and get_table both return each table's full columns[] array (name, type, nullability), so column-level schema comes from these actions rather than list_table_summaries, which returns only the table name and type. # Datadog Source: https://docs.stackone.com/connectors/datadog/index How to set up the Datadog connector, plus the actions and events that are available.
Datadog
v1.5.0
49 actions · 6 events · 2 auth methods
Observability IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate API and Application keys from your Datadog account settings. API keys are used for authentication while Applica... Standalone bearer token with no API key required, scoped to the creating user's permissions and time-limited (24 hours t... Optionally, configure receiving Events for Datadog into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/datadog/index.md for the full list. ## Events See https://docs.stackone.com/connectors/datadog/index.md for the full list. # Datadog Changelog Source: https://docs.stackone.com/connectors/datadog/changelog Release history for the Datadog connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added DDSQL query actions (Execute SQL Query, Get SQL Query Result), dashboard actions (list, get, create, update, delete), and read actions for notebooks and incidents. These need the timeseries_query, dashboards_read, dashboards_write, notebooks_read and incident_read scopes on scoped Application Keys. `datadog_create_dashboard`, `datadog_delete_dashboard`, `datadog_execute_sql_query`, `datadog_get_dashboard`, `datadog_get_incident`, `datadog_get_notebook`, `datadog_get_sql_query_result`, `datadog_list_dashboards`, `datadog_list_incidents`, `datadog_list_notebooks`, `datadog_update_dashboard` `datadog_list_logs`, `datadog_search_logs` `webhook` `new-actions` Added webhook events for Datadog monitor notifications — triggered, recovered, warning, no data, and renotify — plus a catch-all for other notifications such as incidents. StackOne creates the Datadog webhook automatically when events are enabled (requires the create_webhooks and manage_integrations scopes); add @webhook-stackone to a monitor's notification message to receive its alerts. An optional Webhook Name lets more than one StackOne account connect to the same Datadog organization. `data-sync` `new-feature` Enabled scheduled Data Sync on ten list actions covering monitors, logs, log indexes, service definitions, spans, APM retention filters, users, roles, teams and organizations, so these collections can be searched without calling Datadog on every request. Logs and spans sync incrementally from the last synced timestamp; the rest refresh in full, because no other Datadog endpoint exposes an updated-since filter. list_retention_filters is now marked preview — an organization returns no retention filters, not even Datadog's defaults, until APM has ingested its first trace. `datadog_list_log_indexes`, `datadog_list_logs`, `datadog_list_monitors`, `datadog_list_retention_filters`, `datadog_list_service_definitions`, `datadog_list_spans`, `datadog_unified_list_groups`, `datadog_unified_list_organizations`, `datadog_unified_list_roles`, `datadog_unified_list_users` `auth-improvements` Added Personal Access Token authentication as a second auth method. PATs authenticate standalone via Bearer header (no API key needed), are scoped and time-limited (24h to 1 year, no refresh). Service Access Tokens are also accepted. `datadog_aggregate_logs`, `datadog_aggregate_spans`, `datadog_auth_test`, `datadog_create_log_index`, `datadog_create_monitor`, `datadog_create_service_definition`, `datadog_delete_service_definition`, `datadog_get_metric_metadata`, `datadog_get_metric_tag_configuration`, `datadog_get_monitor`, `datadog_get_service_definition`, `datadog_list_active_metrics`, `datadog_list_log_indexes`, `datadog_list_logs`, `datadog_list_monitors`, `datadog_list_retention_filters`, `datadog_list_service_definitions`, `datadog_list_service_dependencies`, `datadog_list_spans`, `datadog_list_tags_by_metric`, `datadog_query_metrics`, `datadog_scalar_query`, `datadog_search_logs`, `datadog_search_spans`, `datadog_submit_metrics`, `datadog_timeseries_query`, `datadog_unified_get_group`, `datadog_unified_get_me`, `datadog_unified_get_organization`, `datadog_unified_get_role`, `datadog_unified_get_user`, `datadog_unified_list_groups`, `datadog_unified_list_organizations`, `datadog_unified_list_resource_types`, `datadog_unified_list_resource_users`, `datadog_unified_list_roles`, `datadog_unified_list_users`, `datadog_update_monitor` `bug-fix` Standardized action category capitalization for more consistent portal filters. `datadog_auth_test`, `datadog_unified_get_group`, `datadog_unified_get_me`, `datadog_unified_get_organization`, `datadog_unified_get_role`, `datadog_unified_get_user`, `datadog_unified_list_groups`, `datadog_unified_list_organizations`, `datadog_unified_list_resource_types`, `datadog_unified_list_resource_users`, `datadog_unified_list_roles`, `datadog_unified_list_users` `new-actions` Added unified IAM actions for users, roles, teams (groups), organizations, credentials, resource users, and resource types, all on the existing API Key + Application Key authentication. List Unified Users, List Unified Roles, and List Unified Groups page through the whole organization with no fixed page ceiling. # DataGrail Source: https://docs.stackone.com/connectors/datagrail/index How to set up the DataGrail connector, plus the actions that are available.
DataGrail
Betav0.1.0
39 actions · 1 auth method
Security
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires API access to be enabled on your DataGrail environment by an Account Manager. The key is created in the DataGra... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/datagrail/index.md for the full list. # DataGrail Changelog Source: https://docs.stackone.com/connectors/datagrail/changelog Release history for the DataGrail connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `initial` Initial DataGrail connector with privacy request, opt-out, consent audit log and responsible data discovery support. # Dayforce Source: https://docs.stackone.com/connectors/dayforce/index How to set up the Dayforce connector, plus the actions that are available.
Dayforce
Previewv3.1.0
61 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). To connect Dayforce, a System Administrator creates a dedicated, non-employee Web Services user inside your Dayforce ten... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dayforce/index.md for the full list. # Dayforce Changelog Source: https://docs.stackone.com/connectors/dayforce/changelog Release history for the Dayforce connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the employee, department, job, position and org-unit code lists and to the employment-status, status-reason, contact-type, pay-class and pay-type reference lists. `dayforce_list_contact_information_types`, `dayforce_list_department_codes`, `dayforce_list_employees`, `dayforce_list_employment_status_reasons`, `dayforce_list_employment_statuses`, `dayforce_list_job_codes`, `dayforce_list_org_unit_codes`, `dayforce_list_pay_classes`, `dayforce_list_pay_types`, `dayforce_list_position_codes` `breaking` `bug-fix` Removed employee, badge and work-assignment fields that Dayforce silently ignores on write, added telecommuter percentage to work assignments, and corrected date and filter guidance on time-off, address, org-unit and position actions. `dayforce_create_employee`, `dayforce_create_employee_address`, `dayforce_create_employee_contact`, `dayforce_create_employee_work_assignment`, `dayforce_create_time_off`, `dayforce_get_employee`, `dayforce_list_org_unit_codes`, `dayforce_list_org_units_detailed`, `dayforce_update_employee_address`, `dayforce_update_employee_contact`, `dayforce_update_employee_work_assignment`, `dayforce_update_position` `new-actions` `bug-fix` Renamed the department, job, position and org-unit list actions, removed the unusable time-off update and pay filters, and added paged lookups that return names with codes. `dayforce_list_department_codes`, `dayforce_list_departments_detailed`, `dayforce_list_job_codes`, `dayforce_list_jobs_detailed`, `dayforce_list_org_unit_codes`, `dayforce_list_org_units_detailed`, `dayforce_list_position_codes`, `dayforce_list_positions_detailed` `dayforce_list_departments`, `dayforce_list_jobs`, `dayforce_list_org_units`, `dayforce_list_positions`, `dayforce_update_time_off` `dayforce_create_department`, `dayforce_create_employee`, `dayforce_create_employee_address`, `dayforce_create_employee_contact`, `dayforce_create_employee_emergency_contact`, `dayforce_create_employee_schedule`, `dayforce_create_employee_work_assignment`, `dayforce_create_job`, `dayforce_create_org_unit`, `dayforce_create_position`, `dayforce_create_time_off`, `dayforce_get_department`, `dayforce_get_job`, `dayforce_get_org_unit`, `dayforce_get_position`, `dayforce_list_contact_information_types`, `dayforce_list_employee_addresses`, `dayforce_list_employee_contacts`, `dayforce_list_employee_emergency_contacts`, `dayforce_list_employee_employment_statuses`, `dayforce_list_employee_managers`, `dayforce_list_employee_punches`, `dayforce_list_employee_time_away`, `dayforce_list_employee_work_assignments`, `dayforce_list_employees`, `dayforce_list_employment_statuses`, `dayforce_update_department`, `dayforce_update_employee_address`, `dayforce_update_employee_contact`, `dayforce_update_employee_emergency_contact`, `dayforce_update_employee_schedule`, `dayforce_update_employee_work_assignment`, `dayforce_update_job`, `dayforce_update_org_unit`, `dayforce_update_position` `bug-fix` Improved employee, time-off, punch, position, address and contact action descriptions for agent tool-calling. `dayforce_create_employee`, `dayforce_create_employee_address`, `dayforce_create_employee_contact`, `dayforce_create_time_off`, `dayforce_get_position`, `dayforce_list_employee_punches`, `dayforce_list_employee_time_away`, `dayforce_list_employees`, `dayforce_update_employee_address`, `dayforce_update_employee_contact`, `dayforce_update_position`, `dayforce_update_time_off` `bug-fix` Behavioural fixes — improved action descriptions. `dayforce_create_employee_contact`, `dayforce_create_employee_emergency_contact`, `dayforce_create_employee_employment_status`, `dayforce_create_employee_work_assignment`, `dayforce_create_time_off`, `dayforce_get_department`, `dayforce_get_employee`, `dayforce_get_position`, `dayforce_list_departments`, `dayforce_list_employee_time_away`, `dayforce_list_employees`, `dayforce_list_jobs`, `dayforce_list_org_units`, `dayforce_list_positions`, `dayforce_update_employee_contact`, `dayforce_update_employee_emergency_contact`, `dayforce_update_job` `bug-fix` Removed non-working fields (contextDate from list_employment_status_reasons; FederatedId and HomePhone from update_employee) and documented that update_employee_punch requires at least one body field. `dayforce_list_employment_status_reasons`, `dayforce_update_employee`, `dayforce_update_employee_punch` `new-actions` `bug-fix` Added new reference-data actions (contact information types, pay classes, pay types, labor metric types). Improved existing actions that were failing in action testing by removing or updating fields and descriptions. # Deel Source: https://docs.stackone.com/connectors/deel/index How to set up the Deel connector, plus the actions and events that are available.
Deel
Previewv2.1.0
92 actions · 55 events · 2 auth methods
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a bearer token generated from the Deel Developer Center. Organization tokens grant full org access; personal tokens... Requires creating an OAuth app in the Deel Developer Center. Access tokens expire after 30 days, refresh tokens after 90... Optionally, configure receiving Events for Deel into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/deel/index.md for the full list. ## Events See https://docs.stackone.com/connectors/deel/index.md for the full list. # Deel Changelog Source: https://docs.stackone.com/connectors/deel/changelog Release history for the Deel connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-feature` `guide-changes` Added native webhook mapping for Deel events. `auth` `data-sync` `guide-improvements` `breaking` `downstream-change` `bug-fix` `new-actions` Migrated to authRequirements and Deel's X-Version 2026-01-01 API, renamed actions to Deel's documented operation names, and added create, update and delete actions across HRIS, payroll and timesheet resources. Removed the immigration actions and get_invoice_download_link. Enabled Data Sync on 37 list actions, with incremental sync on time-off requests and the ATS collections. # Defense.com Source: https://docs.stackone.com/connectors/defense/index How to set up the Defense.com connector, plus the actions that are available.
Defense.com
Betav0.1.0
22 actions · 1 auth method
Security
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Company Admin to create an API key in the Defense.com account settings. Keys carry a mandatory expiry date an... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/defense/index.md for the full list. # Defense.com Changelog Source: https://docs.stackone.com/connectors/defense/changelog Release history for the Defense.com connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial action mappings for Defense.com # Demio Source: https://docs.stackone.com/connectors/demio/index How to set up the Demio connector, plus the actions that are available.
Demio
v1.1.0
6 actions · 1 auth method
Events
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate API credentials from your Demio account settings. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/demio/index.md for the full list. # Demio Changelog Source: https://docs.stackone.com/connectors/demio/changelog Release history for the Demio connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for events, so their records can be periodically pulled into StackOne and kept up to date. The sync is full-refresh, because the Demio API exposes no updated-since filter a sync can use. `demio_list_events` `description-fix` `bug-fix` Clarified list_event_date_participants — documented that registrants appear as soon as they sign up (carrying "did not attend" until the session runs) and defined each participation status value. `demio_list_event_date_participants` `guide-fix` Fixed the API Key connection guide — clarified that Settings opens the General tab before the API tab, documented the REGENERATE button next to the API Secret field, and added portal screenshots. # Deputy Source: https://docs.stackone.com/connectors/deputy/index How to set up the Deputy connector, plus the actions and events that are available.
Deputy
v1.2.0
49 actions · 47 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 is the recommended authentication method for Deputy. Optionally, configure receiving Events for Deputy into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/deputy/index.md for the full list. ## Events See https://docs.stackone.com/connectors/deputy/index.md for the full list. # Deputy Changelog Source: https://docs.stackone.com/connectors/deputy/changelog Release history for the Deputy connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added scheduled data sync to fourteen collection actions — employees, employee agreements and agreement history, employee roles, workplaces, availability and appraisals, employment conditions, locations, operational units, rosters, categories, custom fields and events — so these collections can be kept in sync and searched without calling Deputy on every request. Each is returned in full by a single request, and all sync by full refresh, because Deputy exposes its modified-since filter only through the QUERY endpoints. `deputy_get_recent_rosters`, `deputy_list_categories`, `deputy_list_custom_fields`, `deputy_list_employee_agreement_history`, `deputy_list_employee_agreements`, `deputy_list_employee_appraisals`, `deputy_list_employee_availability`, `deputy_list_employee_roles`, `deputy_list_employee_workplaces`, `deputy_list_employees`, `deputy_list_employment_conditions`, `deputy_list_events`, `deputy_list_locations`, `deputy_list_operational_units` `new-actions` Added inbound webhook events (Model B auto-provisioned) with 47 event handlers, router, and a webhook setup guide. # Dialpad Source: https://docs.stackone.com/connectors/dialpad/index How to set up the Dialpad connector, plus the actions that are available.
Dialpad
Betav1.1.0
57 actions · 2 auth methods
Telephony
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Admin privileges are required in your Dialpad developer portal to create an OAuth app. Only Company Admins can generate API keys in Dialpad. Found in Admin Settings > My Company > Authentication > API Keys. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dialpad/index.md for the full list. # Dialpad Changelog Source: https://docs.stackone.com/connectors/dialpad/changelog Release history for the Dialpad connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for call centers, calls, contacts, departments, dispositions, numbers, offices, scheduled messages, users and webhooks, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Dialpad API exposes no updated-since filter a sync can use. # Discord Source: https://docs.stackone.com/connectors/discord/index How to set up the Discord connector, plus the actions that are available.
Discord
v2.3.0
91 actions · 2 auth methods
Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for user-facing apps that need to act on behalf of Discord users. Supports granular scope selection. Best for automated bots and integrations. Acts as the bot user within guilds it has been added to. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/discord/index.md for the full list. # Discord Changelog Source: https://docs.stackone.com/connectors/discord/changelog Release history for the Discord connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `description-fix` `guide` Added Create Auto Moderation Rule, so keyword, spam, preset and member-profile rules can be created from StackOne instead of only listed, read and deleted. Modify Current User now accepts remove_avatar and remove_banner to clear a bot's avatar or banner, which the connector could not previously express. Corrected the documented response for 17 actions that return a confirmation rather than an empty body, noted that a community server's built-in Mention Spam rule cannot be deleted, and clarified that the application name in both connection guides is an example. `discord_create_auto_moderation_rule` `discord_add_guild_member_role`, `discord_bulk_delete_messages`, `discord_create_guild_ban`, `discord_delete_application_emoji`, `discord_delete_auto_moderation_rule`, `discord_delete_channel_permission`, `discord_delete_guild_emoji`, `discord_delete_guild_role`, `discord_delete_guild_scheduled_event`, `discord_delete_own_reaction`, `discord_delete_user_reaction`, `discord_edit_channel_permissions`, `discord_join_thread`, `discord_leave_guild`, `discord_leave_thread`, `discord_modify_current_user`, `discord_remove_guild_member`, `discord_remove_guild_member_role`, `discord_remove_thread_member` `guide` Added illustrated connection guides for both authentication methods. The OAuth 2.0 guide walks through registering a Discord application, adding the StackOne redirect URI and selecting scopes. The Bot Token guide covers generating the bot token, enabling the privileged gateway intents needed to read members and message content, and installing the bot on a server. `bug-fix` `description-fix` Twenty-one actions that Discord answers with 204 No Content now return an explicit success confirmation instead of an empty value, so callers can tell a completed delete, role change, reaction or thread join from a silent no-op. Start Thread Without Message now accepts the message and applied tags needed to create posts in forum and media channels. Guild and channel ID parameters state that they take a numeric snowflake and name the action that returns it. `discord_add_guild_member`, `discord_add_guild_member_role`, `discord_bulk_delete_messages`, `discord_bulk_update_guild_role_positions`, `discord_create_channel_invite`, `discord_create_guild_ban`, `discord_create_guild_channel`, `discord_create_guild_emoji`, `discord_create_message`, `discord_create_reaction`, `discord_delete_all_reactions`, `discord_delete_all_reactions_for_emoji`, `discord_delete_application_emoji`, `discord_delete_auto_moderation_rule`, `discord_delete_channel`, `discord_delete_channel_permission`, `discord_delete_guild_emoji`, `discord_delete_guild_role`, `discord_delete_guild_scheduled_event`, `discord_delete_own_reaction`, `discord_delete_user_reaction`, `discord_edit_channel_permissions`, `discord_edit_message`, `discord_follow_announcement_channel`, `discord_get_auto_moderation_rule`, `discord_get_channel`, `discord_get_channel_message`, `discord_get_channel_messages`, `discord_get_current_user_guild_member`, `discord_get_guild`, `discord_get_guild_audit_log`, `discord_get_guild_emoji`, `discord_get_guild_member`, `discord_get_guild_onboarding`, `discord_get_guild_preview`, `discord_get_guild_role`, `discord_get_guild_role_member_counts`, `discord_get_guild_scheduled_event`, `discord_get_thread_member`, `discord_join_thread`, `discord_leave_guild`, `discord_leave_thread`, `discord_list_active_guild_threads`, `discord_list_auto_moderation_rules`, `discord_list_channel_invites`, `discord_list_guild_bans`, `discord_list_guild_channels`, `discord_list_guild_emojis`, `discord_list_guild_integrations`, `discord_list_guild_invites`, `discord_list_guild_members`, `discord_list_guild_roles`, `discord_list_guild_scheduled_event_users`, `discord_list_guild_scheduled_events`, `discord_list_reactions`, `discord_list_thread_members`, `discord_modify_channel`, `discord_modify_current_member`, `discord_modify_current_user`, `discord_modify_guild`, `discord_modify_guild_emoji`, `discord_remove_guild_member`, `discord_remove_guild_member_role`, `discord_remove_thread_member`, `discord_search_guild_members`, `discord_start_thread_from_message`, `discord_start_thread_without_message` `data-sync` `new-feature` Added Data Sync support for servers, members, roles and linked third-party accounts, all full refresh as Discord exposes no updated-since filter. `discord_list_current_user_connections`, `discord_unified_list_organizations`, `discord_unified_list_roles`, `discord_unified_list_users` `breaking-change` Every action now declares which authentication types it supports. Most of the Discord API is reachable only with a bot token, so server, channel and message actions are Bot Token only, and OAuth 2.0 connections no longer surface actions that would fail with a 401. # Discourse Source: https://docs.stackone.com/connectors/discourse/index How to set up the Discourse connector, plus the actions and events that are available.
Discourse
v1.2.0
67 actions · 50 events · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from your Discourse admin panel to authenticate requests. You will also need a username (typically s... Optionally, configure receiving Events for Discourse into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/discourse/index.md for the full list. ## Events See https://docs.stackone.com/connectors/discourse/index.md for the full list. # Discourse Changelog Source: https://docs.stackone.com/connectors/discourse/changelog Release history for the Discourse connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added 49 webhook events for topics, posts, users, groups, categories, tags, badges, the review queue, notifications, chat and the Solved, Assign, Topic Voting and Calendar plugins. StackOne creates and removes the Discourse webhook automatically. `data-sync` `guide` `bug-fix` Added Data Sync support for 9 list actions (badges, categories, tags, tag groups, groups, latest topics, top topics, users, notifications), all refreshing in full each run. Rebuilt the API Key connection guide with screenshots, and fixed category, post action, topic timer and badge actions that returned errors or silently did nothing. # Dixa Source: https://docs.stackone.com/connectors/dixa/index How to set up the Dixa connector, plus the actions and events that are available.
Dixa
v3.0.1
66 actions · 33 events · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. Access is limited to the permission groups selected when the API token is created. Optionally, configure receiving Events for Dixa into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dixa/index.md for the full list. ## Events See https://docs.stackone.com/connectors/dixa/index.md for the full list. # Dixa Changelog Source: https://docs.stackone.com/connectors/dixa/changelog Release history for the Dixa connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Updated the API Key connection guide so the copy-token step describes the created token page generically instead of naming a specific token. `breaking` `bug-fix` `new-actions` Transferring a conversation to a queue now returns a confirmation message instead of an empty response, and a new update_agent action fully replaces an agent - the only way to set additionalEmails or additionalPhoneNumbers, which Dixa silently ignores on patch_agent. `dixa_update_agent` `dixa_list_agent_teams`, `dixa_patch_agent`, `dixa_search_conversations`, `dixa_transfer_conversation_to_queue` `guide` Updated the API Key connection guide with screenshots, the required permission groups, and an example token format. `data-sync` Added Data Sync support for agent presence, contact endpoints, custom attributes, queues, tags, teams and webhooks, so these collections can be kept in sync on a schedule. Each is returned in full by the API in a single call and syncs as a full refresh. Agents, end users, knowledge collections and templates are not synced, because Dixa returns their next page only as a full URL that a cursor iterator cannot use; conversation flows are not synced because that endpoint is scoped to a single channel at a time. `dixa_list_agents_presence`, `dixa_list_contact_endpoints`, `dixa_list_custom_attributes`, `dixa_list_queues`, `dixa_list_tags`, `dixa_list_teams`, `dixa_list_webhooks` `bug-fix` `breaking` Conversation search now exposes its full filter schema (field types, operators and the 50-result page limit); filtering on custom-attribute values is no longer supported. Close, reopen, follow-up, tag and team-membership writes now return a confirmation message instead of an empty response. `dixa_add_team_members`, `dixa_close_conversation`, `dixa_followup_conversation`, `dixa_list_agents`, `dixa_list_end_users`, `dixa_remove_team_members`, `dixa_reopen_conversation`, `dixa_search_conversations`, `dixa_tag_conversation`, `dixa_untag_conversation` `new-actions` Added webhook event support for conversation, message delivery, agent moderation, typing, and SLA events (32 events) with programmatic webhook subscription registration. # Docebo Source: https://docs.stackone.com/connectors/docebo/index How to set up the Docebo connector, plus the actions and events that are available.
Docebo
v1.3.0
56 actions · 50 events · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Administrator privileges within Docebo. Optionally, configure receiving Events for Docebo into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/docebo/index.md for the full list. ## Events See https://docs.stackone.com/connectors/docebo/index.md for the full list. # Docebo Changelog Source: https://docs.stackone.com/connectors/docebo/changelog Release history for the Docebo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to seven list actions — users, courses, learning plans, categories, certifications, branches, and locations — so these collections can be kept in sync and read back without calling Docebo on every request. Each syncs by full refresh, because Docebo's updated-since filter requires a timestamp format that data sync cannot produce. `docebo_list_branches`, `docebo_list_categories`, `docebo_list_certifications`, `docebo_list_courses`, `docebo_list_learning_plans`, `docebo_list_locations`, `docebo_list_users` `bug-fix` `description-fix` Documented that the batch training-material import thumbnail field does not accept external image URLs (Docebo rejects them as "Invalid thumbnail"); callers should omit it and set the thumbnail via Docebo's pre-uploaded-image mechanism. `docebo_create_learning_objects` `bug-fix` `description-fix` Clarified the batch training-material import action to document that the S3 options block is batch-scoped, not per item, so file and URL learning objects cannot be created in the same call and must be split into separate batches. `docebo_create_learning_objects` `bug-fix` `description-fix` Improved action guidance and schema accuracy across users, branches, categories, learning plans, and learning objects. Clarified list pagination behavior, corrected the required fields for creating learning plans, and documented batch training-material import limitations (mutually exclusive file/URL fields, S3 credential requirements, and per-item success checking). `docebo_create_learning_objects`, `docebo_create_learning_plan`, `docebo_get_branch`, `docebo_get_child_categories`, `docebo_list_branches`, `docebo_list_learning_plans`, `docebo_list_users` `native-webhooks` `new-events` Added support for Docebo native webhooks. You can now receive real-time events for courses, enrollments, learning plans, training materials, certifications, branches, channels, groups, and instructor-led training sessions. Webhooks are configured manually in the Docebo admin UI. # DocuSign Source: https://docs.stackone.com/connectors/docusign/index How to set up the DocuSign connector, plus the actions that are available.
DocuSign
Previewv1.1.2
73 actions · 1 auth method
E-Signature IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). DocuSign uses OAuth 2.0 Authorization Code Grant for authentication. You'll need to create an app in DocuSign Admin to g... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/docusign/index.md for the full list. # DocuSign Changelog Source: https://docs.stackone.com/connectors/docusign/changelog Release history for the DocuSign connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists with groups now return every group each user belongs to, with no extra API calls. `docusign_unified_get_user`, `docusign_unified_list_users` `bug-fix` Fixed several unified IAM issues, including group and role lookups failing instead of returning a not-found error for unknown IDs, group lookups missing groups beyond the first 100, and account administrators being reported as basic users on expanded roles. Group and role types now keep the raw DocuSign value alongside the mapped one, user lists paginate through the platform cursor, and a non-working name filter was removed from the group list. `docusign_auth_test`, `docusign_unified_get_group`, `docusign_unified_get_me`, `docusign_unified_get_role`, `docusign_unified_get_user`, `docusign_unified_list_groups`, `docusign_unified_list_organizations`, `docusign_unified_list_roles`, `docusign_unified_list_users` `new-actions` Added unified IAM actions for users, groups, organizations, roles, and credentials. # Domo Source: https://docs.stackone.com/connectors/domo/index How to set up the Domo connector, plus the actions that are available.
Domo
Previewv1.1.0
23 actions · 1 auth method
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Domo developer account to generate a Client ID and Client Secret. Tokens are short-lived and automatically re... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/domo/index.md for the full list. # Domo Changelog Source: https://docs.stackone.com/connectors/domo/changelog Release history for the Domo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added scheduled data sync to the datasets, groups, streams, users, and unified users and groups list actions for scheduled full record syncs. `domo_list_datasets`, `domo_list_groups`, `domo_list_streams`, `domo_list_users`, `domo_unified_list_groups`, `domo_unified_list_users` `bug-fix` Fixed group lookups returning members without their identifiers when member details were requested. # Drata Source: https://docs.stackone.com/connectors/drata/index How to set up the Drata connector, plus the actions that are available.
Drata
Previewv1.1.1
64 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/drata/index.md for the full list. # Drata Changelog Source: https://docs.stackone.com/connectors/drata/changelog Release history for the Drata connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed unified user and organization lists failing when there is more than one page of results. `drata_unified_list_organizations`, `drata_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, and credentials (all preview, pending post-merge live QA). # Dropbox Source: https://docs.stackone.com/connectors/dropbox/index How to set up the Dropbox connector, plus the actions that are available.
Dropbox
v2.1.1
94 actions · 1 auth method
Storage IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create a Dropbox app in the App Console and configure OAuth 2.0 settings Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dropbox/index.md for the full list. # Dropbox Changelog Source: https://docs.stackone.com/connectors/dropbox/changelog Release history for the Dropbox connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Unified list users now works on Dropbox team accounts; it was sending include_removed as text, which Dropbox rejected. `dropbox_unified_list_users` `new-actions` All actions now return the Dropbox response under a data object instead of at the top level. Added scheduled data sync for folder contents, shared folders, mountable folders and file requests, each through a new action that walks a complete listing in a single call, with folder contents syncing incrementally. `dropbox_file_request_list_all`, `dropbox_list_folder_all`, `dropbox_list_shared_folders_all`, `dropbox_list_shared_mountable_folders_all` `dropbox_add_file_member`, `dropbox_add_folder_member`, `dropbox_add_property_template_for_user`, `dropbox_add_tag`, `dropbox_check_job_status`, `dropbox_check_remove_member_job_status`, `dropbox_check_share_job_status`, `dropbox_check_user`, `dropbox_copy_batch`, `dropbox_copy_batch_check`, `dropbox_copy_path`, `dropbox_copy_reference_get`, `dropbox_copy_reference_save`, `dropbox_create_folder`, `dropbox_create_shared_link`, `dropbox_delete_batch`, `dropbox_delete_batch_check`, `dropbox_delete_path`, `dropbox_export_file`, `dropbox_file_request_count`, `dropbox_file_request_create`, `dropbox_file_request_delete`, `dropbox_file_request_delete_all_closed`, `dropbox_file_request_get`, `dropbox_file_request_list`, `dropbox_file_request_list_continue`, `dropbox_file_request_update`, `dropbox_get_file_lock_batch`, `dropbox_get_file_metadata_batch`, `dropbox_get_file_metadata_shared`, `dropbox_get_folder_metadata`, `dropbox_get_latest_cursor`, `dropbox_get_metadata`, `dropbox_get_property_template_for_user`, `dropbox_get_shared_link_file`, `dropbox_get_shared_link_metadata`, `dropbox_get_tags`, `dropbox_get_temporary_link`, `dropbox_get_temporary_upload_link`, `dropbox_list_file_members`, `dropbox_list_file_members_batch`, `dropbox_list_file_members_continue`, `dropbox_list_folder`, `dropbox_list_folder_continue`, `dropbox_list_folder_members`, `dropbox_list_folder_members_continue`, `dropbox_list_revisions`, `dropbox_list_shared_folders`, `dropbox_list_shared_folders_continue`, `dropbox_list_shared_links`, `dropbox_list_shared_mountable_folders`, `dropbox_list_shared_mountable_folders_continue`, `dropbox_list_shared_received_files`, `dropbox_list_shared_received_files_continue`, `dropbox_lock_file_batch`, `dropbox_modify_shared_link_settings`, `dropbox_mount_folder`, `dropbox_move_batch`, `dropbox_move_batch_check`, `dropbox_move_path`, `dropbox_remove_file_member`, `dropbox_remove_folder_member`, `dropbox_remove_property_template_for_user`, `dropbox_remove_tag`, `dropbox_restore_file`, `dropbox_revoke_shared_link`, `dropbox_save_url`, `dropbox_search_continue`, `dropbox_search_files_and_folders`, `dropbox_set_profile_photo`, `dropbox_share_folder`, `dropbox_unlock_file_batch`, `dropbox_unmount_folder`, `dropbox_unshare_file`, `dropbox_unshare_folder`, `dropbox_update_file_member`, `dropbox_update_folder_member`, `dropbox_update_folder_policy` `bug-fix` Fixed file download actions (download_file, download_folder_as_zip, export_file, get_preview, get_thumbnail) that returned an empty result on success - they now return the file content as a base64-encoded string. `dropbox_download_file`, `dropbox_download_folder_as_zip`, `dropbox_export_file`, `dropbox_get_preview`, `dropbox_get_thumbnail` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. `dropbox_add_file_member`, `dropbox_add_folder_member`, `dropbox_add_property_template_for_user`, `dropbox_add_tag`, `dropbox_check_job_status`, `dropbox_check_remove_member_job_status`, `dropbox_check_share_job_status`, `dropbox_check_user`, `dropbox_copy_batch`, `dropbox_copy_batch_check`, `dropbox_copy_path`, `dropbox_copy_reference_get`, `dropbox_copy_reference_save`, `dropbox_create_folder`, `dropbox_create_shared_link`, `dropbox_delete_batch`, `dropbox_delete_batch_check`, `dropbox_delete_path`, `dropbox_download_file`, `dropbox_download_folder_as_zip`, `dropbox_export_file`, `dropbox_file_request_count`, `dropbox_file_request_create`, `dropbox_file_request_delete`, `dropbox_file_request_delete_all_closed`, `dropbox_file_request_get`, `dropbox_file_request_list`, `dropbox_file_request_list_continue`, `dropbox_file_request_update`, `dropbox_get_file_lock_batch`, `dropbox_get_file_metadata_batch`, `dropbox_get_file_metadata_shared`, `dropbox_get_folder_metadata`, `dropbox_get_latest_cursor`, `dropbox_get_metadata`, `dropbox_get_preview`, `dropbox_get_property_template_for_user`, `dropbox_get_shared_link_file`, `dropbox_get_shared_link_metadata`, `dropbox_get_tags`, `dropbox_get_temporary_link`, `dropbox_get_temporary_upload_link`, `dropbox_get_thumbnail`, `dropbox_list_file_members`, `dropbox_list_file_members_batch`, `dropbox_list_file_members_continue`, `dropbox_list_folder`, `dropbox_list_folder_continue`, `dropbox_list_folder_members`, `dropbox_list_folder_members_continue`, `dropbox_list_revisions`, `dropbox_list_shared_folders`, `dropbox_list_shared_folders_continue`, `dropbox_list_shared_links`, `dropbox_list_shared_mountable_folders`, `dropbox_list_shared_mountable_folders_continue`, `dropbox_list_shared_received_files`, `dropbox_list_shared_received_files_continue`, `dropbox_lock_file_batch`, `dropbox_modify_shared_link_settings`, `dropbox_mount_folder`, `dropbox_move_batch`, `dropbox_move_batch_check`, `dropbox_move_path`, `dropbox_remove_file_member`, `dropbox_remove_folder_member`, `dropbox_remove_property_template_for_user`, `dropbox_remove_tag`, `dropbox_restore_file`, `dropbox_revoke_shared_link`, `dropbox_save_url`, `dropbox_search_continue`, `dropbox_search_files_and_folders`, `dropbox_set_profile_photo`, `dropbox_share_folder`, `dropbox_unified_get_group`, `dropbox_unified_get_organization`, `dropbox_unified_get_role`, `dropbox_unified_get_user`, `dropbox_unified_list_groups`, `dropbox_unified_list_organizations`, `dropbox_unified_list_roles`, `dropbox_unified_list_users`, `dropbox_unlock_file_batch`, `dropbox_unmount_folder`, `dropbox_unshare_file`, `dropbox_unshare_folder`, `dropbox_update_file_member`, `dropbox_update_folder_member`, `dropbox_update_folder_policy` `bug-fix` Fixed group, role, and user lookups returning empty or broken results instead of proper not-found errors. Also fixed pagination and role scope issues. # Dropbox Sign Source: https://docs.stackone.com/connectors/dropboxsign/index How to set up the Dropbox Sign connector, plus the actions that are available.
Dropbox Sign
Previewv2.0.0
80 actions · 2 auth methods
E-Signature IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for server-side integrations and single-account access. Simple setup, no OAuth flow required. Requires registering an OAuth app. Allows actions on behalf of individual users. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dropboxsign/index.md for the full list. # Dropbox Sign Changelog Source: https://docs.stackone.com/connectors/dropboxsign/changelog Release history for the Dropbox Sign connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Migrated to authRequirements for per-auth-type scope control. Fax, fax line, report, signature request editing, remove-access, bulk embedded sending, team member and sub-team listing, and team info actions now run only with an API key, matching what Dropbox Sign allows over OAuth. `dropboxsign_add_team_member`, `dropboxsign_add_user_to_fax_line`, `dropboxsign_add_user_to_template`, `dropboxsign_auth_test`, `dropboxsign_bulk_create_embedded_signature_request_with_template`, `dropboxsign_cancel_signature_request`, `dropboxsign_create_account`, `dropboxsign_create_api_app`, `dropboxsign_create_embedded_signature_request`, `dropboxsign_create_embedded_signature_request_with_template`, `dropboxsign_create_embedded_template_draft`, `dropboxsign_create_embedded_unclaimed_draft`, `dropboxsign_create_embedded_unclaimed_draft_with_template`, `dropboxsign_create_report`, `dropboxsign_create_team`, `dropboxsign_create_template`, `dropboxsign_create_unclaimed_draft`, `dropboxsign_delete_api_app`, `dropboxsign_delete_fax`, `dropboxsign_delete_fax_line`, `dropboxsign_delete_team`, `dropboxsign_delete_template`, `dropboxsign_edit_and_resend_unclaimed_draft`, `dropboxsign_edit_embedded_signature_request`, `dropboxsign_edit_embedded_signature_request_with_template`, `dropboxsign_edit_signature_request`, `dropboxsign_edit_signature_request_with_template`, `dropboxsign_get_account`, `dropboxsign_get_api_app`, `dropboxsign_get_bulk_send_job`, `dropboxsign_get_embedded_edit_url`, `dropboxsign_get_embedded_sign_url`, `dropboxsign_get_fax`, `dropboxsign_get_fax_files`, `dropboxsign_get_fax_line`, `dropboxsign_get_fax_line_area_codes`, `dropboxsign_get_signature_request`, `dropboxsign_get_signature_request_files`, `dropboxsign_get_signature_request_files_as_data_uri`, `dropboxsign_get_signature_request_files_as_file_url`, `dropboxsign_get_team`, `dropboxsign_get_template`, `dropboxsign_get_template_files`, `dropboxsign_get_template_files_as_data_uri`, `dropboxsign_get_template_files_as_file_url`, `dropboxsign_list_api_apps`, `dropboxsign_list_bulk_send_jobs`, `dropboxsign_list_fax_lines`, `dropboxsign_list_faxes`, `dropboxsign_list_signature_requests`, `dropboxsign_list_sub_teams`, `dropboxsign_list_team_members`, `dropboxsign_list_templates`, `dropboxsign_purchase_fax_line`, `dropboxsign_release_signature_request_hold`, `dropboxsign_remove_signature_request_access`, `dropboxsign_remove_team_member`, `dropboxsign_remove_user_from_fax_line`, `dropboxsign_remove_user_from_template`, `dropboxsign_send_bulk_signature_request_with_template`, `dropboxsign_send_fax`, `dropboxsign_send_signature_request`, `dropboxsign_send_signature_request_reminder`, `dropboxsign_send_signature_request_with_template`, `dropboxsign_unified_delete_user`, `dropboxsign_unified_get_group`, `dropboxsign_unified_get_me`, `dropboxsign_unified_get_organization`, `dropboxsign_unified_get_role`, `dropboxsign_unified_get_user`, `dropboxsign_unified_list_groups`, `dropboxsign_unified_list_organizations`, `dropboxsign_unified_list_roles`, `dropboxsign_unified_list_users`, `dropboxsign_update_account`, `dropboxsign_update_api_app`, `dropboxsign_update_signature_request`, `dropboxsign_update_team`, `dropboxsign_update_template_files`, `dropboxsign_verify_account` `data-sync` Added DataSync support to ten list actions — signature requests, templates, faxes, fax lines, API apps, bulk send jobs, and the unified IAM users, groups, roles and organizations — so their records can be synced on a schedule and read back without calling Dropbox Sign each time. Every action refreshes in full on each run, as Dropbox Sign exposes no updated-since filter on any list endpoint. `dropboxsign_list_api_apps`, `dropboxsign_list_bulk_send_jobs`, `dropboxsign_list_fax_lines`, `dropboxsign_list_faxes`, `dropboxsign_list_signature_requests`, `dropboxsign_list_templates`, `dropboxsign_unified_list_groups`, `dropboxsign_unified_list_organizations`, `dropboxsign_unified_list_roles`, `dropboxsign_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, and credentials. All actions are gated to releaseStage preview pending post-merge live QA. # DuckDuckGo Source: https://docs.stackone.com/connectors/duckduckgo/index How to set up the DuckDuckGo connector, plus the actions that are available.
DuckDuckGo
v1.0.0
1 action · 1 auth method
Search
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The DuckDuckGo Instant Answer API is fully public and requires no credentials, API key, or OAuth flow. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/duckduckgo/index.md for the full list. # Duo Security Source: https://docs.stackone.com/connectors/duo/index How to set up the Duo Security connector, plus the actions that are available.
Duo Security
Previewv0.2.1
39 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Duo uses HMAC-SHA1 signed requests with HTTP Basic Authentication. The integration key is the username and the HMAC-SHA1... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/duo/index.md for the full list. # Duo Security Changelog Source: https://docs.stackone.com/connectors/duo/changelog Release history for the Duo Security connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Clarified the create_user description to state that status and custom attributes can be set in the single create call, so no follow-up update_user is needed when onboarding a user. Removed circular prerequisiteActions on create_admin and create_phone. `duo_create_admin`, `duo_create_phone`, `duo_create_user` `new-features` Added DataSync support to six list actions (users, groups, administrators, phones, hardware tokens, integrations) with offset pagination, enabling scheduled full-refresh syncs of these collections. `duo_list_admins`, `duo_list_groups`, `duo_list_integrations`, `duo_list_phones`, `duo_list_tokens`, `duo_list_users` `new-actions` Initial Duo Security connector with HMAC-SHA1 authenticated actions for users, groups, administrators, phones, hardware tokens, and integrations (full CRUD), bulk user create/trash/restore/operations, and read-only authentication, admin, and telephony logs. # E2B Source: https://docs.stackone.com/connectors/e2b/index How to set up the E2B connector, plus the actions and events that are available.
E2B
v1.2.1
62 actions · 6 events · 1 auth method
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a team API key sent in the X-API-Key header. No app registration required. The key is team-scoped, so it reaches on... Optionally, configure receiving Events for E2B into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/e2b/index.md for the full list. ## Events See https://docs.stackone.com/connectors/e2b/index.md for the full list. # E2B Changelog Source: https://docs.stackone.com/connectors/e2b/changelog Release history for the E2B connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` List Volumes is now marked beta. E2B's volumes feature is in a private beta that is not enabled for most teams, so the action cannot yet be verified against real volume data. `e2b_list_volumes` `new-events` Added webhook support. StackOne registers a webhook automatically when an account is connected and removes it on disconnect, handling the six sandbox lifecycle events — created, killed, paused, resumed, updated and checkpointed. Each event reports the sandbox it concerns as the record id. Four read-only actions cover the team's webhooks alongside that: listing them, reading one, and reading its delivery attempts and aggregate delivery statistics, which together show whether events are reaching StackOne. Registering, changing and removing webhooks stays with the managed lifecycle, so no action can alter the StackOne registration. A setup guide documents the team scoping and the full event catalogue. `e2b_get_webhook`, `e2b_get_webhook_statistics`, `e2b_list_webhook_deliveries`, `e2b_list_webhooks` `data-sync` Added scheduled data sync to five collection actions — sandboxes, snapshots, templates, secrets and volumes — so these collections can be kept in sync and read back without calling E2B on every request. Sandboxes, snapshots, templates and secrets page through results automatically using E2B's cursor; volumes are returned in full by a single request. All syncs use full refreshes, because no E2B list endpoint offers a last-updated filter. `e2b_list_sandboxes`, `e2b_list_secrets`, `e2b_list_snapshots`, `e2b_list_templates`, `e2b_list_volumes` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `description-fix` Corrected the pagination and reference documentation on the list actions — the next-page cursor comes back in the response body, not in an X-Next-Token header, and List Sandboxes no longer advertises a total running count that the response never carries, so counting means paging until the cursor is absent. Get Build Logs now states that a 502 from the temporary store is permanent rather than transient and those logs are read from the persistent store, Start Build's command fields note that a local service is addressed without a URL scheme, and Compose Files points at documentation matching the endpoint it calls. `e2b_compose_files`, `e2b_get_build_logs`, `e2b_list_sandboxes`, `e2b_list_secrets`, `e2b_list_snapshots`, `e2b_list_template_builds`, `e2b_list_templates`, `e2b_start_build` `bug-fix` `description-fix` Get Sandbox Health and Start Build now return an explicit confirmation message instead of an empty string, so a successful call is no longer indistinguishable from no data. Descriptions were corrected across templates and sandboxes — E2B's public built-in aliases such as "base" are accepted by Create Sandbox and its filters even though List Templates never returns them, Check Template Alias and List Template Builds only accept team-owned aliases and opaque IDs respectively, build logs read from the temporary store only while the builder is alive, and Fork Sandbox and Create Snapshot both require a running sandbox. `e2b_check_template_alias`, `e2b_create_sandbox`, `e2b_create_snapshot`, `e2b_fork_sandbox`, `e2b_get_build_logs`, `e2b_get_sandbox_health`, `e2b_list_sandboxes`, `e2b_list_template_builds`, `e2b_list_templates`, `e2b_start_build` `new-connector` `new-actions` Initial action mappings for the E2B API — 57 actions covering sandbox lifecycle, in-sandbox filesystem and process control, template builds and tags, persistent volumes, secrets, and usage metrics. # EasyCruit Source: https://docs.stackone.com/connectors/easycruit/index How to set up the EasyCruit connector, plus the actions that are available.
EasyCruit
Betav1.0.0
12 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticates via Visma Connect using the OAuth 2.0 client credentials grant. Requires registering an application in Vis... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/easycruit/index.md for the full list. # EasyLlama Source: https://docs.stackone.com/connectors/easyllama/index How to set up the EasyLlama connector, plus the actions and events that are available.
EasyLlama
v1.2.0
27 actions · 3 events · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). To obtain your API credentials, navigate to Settings > Integrations > API in your EasyLlama Dashboard and generate an Ac... Optionally, configure receiving Events for EasyLlama into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/easyllama/index.md for the full list. ## Events See https://docs.stackone.com/connectors/easyllama/index.md for the full list. # EasyLlama Changelog Source: https://docs.stackone.com/connectors/easyllama/changelog Release history for the EasyLlama connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhooks` Added native webhook support for the learner_training.chapter_completed, learner_training.completed and subscription.updated events, configured manually via the EasyLlama Webhook integration tile. `data-sync` Added Data Sync support for learners, trainings, learner trainings, locations, regions, departments, industries, and training categories, plus an optional page_size parameter on the region, location, department, industry, and learner training list actions. `easyllama_list_categories`, `easyllama_list_departments`, `easyllama_list_industries`, `easyllama_list_learner_trainings`, `easyllama_list_learners`, `easyllama_list_locations`, `easyllama_list_regions`, `easyllama_list_trainings` `guide-changes` `guide-images` Updated the API Key connection guide with the redirect URL and application name step required when connecting the EasyLlama API integration, corrected the access token steps to match the dashboard, and added screenshots. # Easyship Source: https://docs.stackone.com/connectors/easyship/index How to set up the Easyship connector, plus the actions and events that are available.
Easyship
v1.2.0
48 actions · 14 events · 1 auth method
Logistics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Bearer token authentication provides secure access to Easyship APIs. Generate your API access token from the Easyship da... Optionally, configure receiving Events for Easyship into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/easyship/index.md for the full list. ## Events See https://docs.stackone.com/connectors/easyship/index.md for the full list. # Easyship Changelog Source: https://docs.stackone.com/connectors/easyship/changelog Release history for the Easyship connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Enabled scheduled data sync on 13 list actions covering countries, states, addresses, account assets, boxes, couriers, link-your-own-courier options, shipments, item categories, stores, tags, trackings and supported courier services, so these collections can be kept in sync and read without calling Easyship on every request. Shipments sync incrementally using the existing optional updated_at_from filter as the watermark; the rest refresh in full, because no other endpoint exposes an updated-since filter. Two collections are deliberately left out: HS Codes has no unique per-record identifier, and Shipment Trackings cannot be paged past page 1 because /shipments/trackings advertises a next page and then rejects it with "expected :page in 1..1". No action inputs or responses changed. `easyship_list_addresses`, `easyship_list_assets`, `easyship_list_boxes`, `easyship_list_countries`, `easyship_list_couriers`, `easyship_list_item_categories`, `easyship_list_lyoc`, `easyship_list_shipments`, `easyship_list_states`, `easyship_list_stores`, `easyship_list_supported_couriers`, `easyship_list_tags`, `easyship_list_trackings` `description-fix` Improved action descriptions for create_shipment item category field and create_address default_for workflow to reduce agent errors. `easyship_activate_address`, `easyship_activate_asset`, `easyship_cancel_shipment`, `easyship_create_address`, `easyship_create_asset`, `easyship_create_box`, `easyship_create_courier`, `easyship_create_label`, `easyship_create_shipment`, `easyship_create_tag`, `easyship_create_tracking`, `easyship_deactivate_address`, `easyship_deactivate_asset`, `easyship_delete_asset`, `easyship_delete_box`, `easyship_delete_courier`, `easyship_delete_shipment`, `easyship_delete_tracking`, `easyship_get_account`, `easyship_get_account_settings`, `easyship_get_courier`, `easyship_get_shipment`, `easyship_get_tracking`, `easyship_list_addresses`, `easyship_list_all_trackings`, `easyship_list_assets`, `easyship_list_boxes`, `easyship_list_countries`, `easyship_list_courier_services`, `easyship_list_couriers`, `easyship_list_external_courier_services`, `easyship_list_hs_codes`, `easyship_list_item_categories`, `easyship_list_lyoc`, `easyship_list_shipments`, `easyship_list_states`, `easyship_list_stores`, `easyship_list_supported_couriers`, `easyship_list_tags`, `easyship_list_trackings`, `easyship_list_transaction_records`, `easyship_list_unavailable_couriers`, `easyship_update_address`, `easyship_update_asset`, `easyship_update_box`, `easyship_update_shipment`, `easyship_validate_address`, `easyship_validate_domestic_address` `new-events` Added programmatic webhook event support with 13 event types covering shipments, labels, tracking, batches, credits, companies, couriers, and OAuth access revocation. `description-fix` Description improvements. create_shipment (origin_address required, box/dimensions requirement explicit). update_shipment (PUT-like replace semantics warning). create_address (default_for not applied while draft). `easyship_create_address`, `easyship_create_shipment`, `easyship_list_supported_couriers`, `easyship_update_shipment` `description-fix` Description fixes for create_shipment (dimensions requirement), update_shipment (full address on updates), list_unavailable_couriers (rate prerequisite), and create_address (draft status). # Egnyte Source: https://docs.stackone.com/connectors/egnyte/index How to set up the Egnyte connector, plus the actions and events that are available.
Egnyte
Previewv1.2.0
38 actions · 21 events · 2 auth methods
Storage
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 Authorization Code flow. Egnyte issues access tokens that expire after 30 days plus a rotating refresh token p... For customer-built Internal Applications on a single Egnyte domain. Uses the OAuth 2.0 Resource Owner Password Credentia... Optionally, configure receiving Events for Egnyte into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/egnyte/index.md for the full list. ## Events See https://docs.stackone.com/connectors/egnyte/index.md for the full list. # Egnyte Changelog Source: https://docs.stackone.com/connectors/egnyte/changelog Release history for the Egnyte connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added DataSync support for comments, shared links, and trash, so these records can be synced on a schedule and read back without calling Egnyte each time. Comments and links sync incrementally; trash refreshes in full. `egnyte_get_groups_v2`, `egnyte_get_links_v2`, `egnyte_list_comments`, `egnyte_list_trash_v2`, `egnyte_list_users` `guide-changes` `field-labels` Refined OAuth (Public + Internal Application) connection guides per audit — clarified the async approval flow, split Egnyte-portal steps from StackOne-paste steps, added a Domain Admin verification path, and renamed OAuth setupFields labels from API Key/API Secret to Client ID/Client Secret. `native-webhooks` `guide-changes` Added native webhook event support for 21 event types across file system, links, comments, and groups, with programmatic subscription management and a webhook setup guide. # Eka Care Source: https://docs.stackone.com/connectors/ekacare/index How to set up the Eka Care connector, plus the actions and events that are available.
Eka Care
Previewv0.1.1
160 actions · 31 events · 3 auth methods
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Long-lived workspace token from the Eka Developer Console. No refresh needed. Bound to a single workspace. Requires an API client from the Eka Developer Console. Tokens are short-lived and renewed automatically. Optional Sharin... Delegated access as a signed-in Eka user via OpenID Connect. Requires a client with a registered redirect URI. Untested... Optionally, configure receiving Events for Eka Care into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ekacare/index.md for the full list. ## Events See https://docs.stackone.com/connectors/ekacare/index.md for the full list. # Eka Care Changelog Source: https://docs.stackone.com/connectors/ekacare/changelog Release history for the Eka Care connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Resolved behavioural issues in the Eka Care connector. Write actions now confirm what they changed, and tool descriptions are clearer. `ekacare_list_template_titles`, `ekacare_update_doctor`, `ekacare_upload_record` `ekacare_book_appointment_slot`, `ekacare_cancel_appointment`, `ekacare_complete_appointment`, `ekacare_confirm_follow_up_appointment`, `ekacare_create_an_ipd_admission`, `ekacare_create_case`, `ekacare_create_schedule`, `ekacare_delete_case`, `ekacare_delete_document`, `ekacare_delete_document_records`, `ekacare_get_appointment_slots`, `ekacare_get_document`, `ekacare_get_resolved_schedule`, `ekacare_get_service_conf_list`, `ekacare_get_sessions`, `ekacare_link_entities_batch`, `ekacare_link_entity`, `ekacare_list_registry`, `ekacare_list_templates`, `ekacare_parked_appointment`, `ekacare_parsed_report_result`, `ekacare_process_template`, `ekacare_record_an_admission_event`, `ekacare_retrieve_patient_profile_by_username`, `ekacare_search_symptoms_and_diagnoses`, `ekacare_send_notification`, `ekacare_step_1_upload_record`, `ekacare_update_an_ipd_admission`, `ekacare_update_appointment`, `ekacare_update_appointment_v2`, `ekacare_update_case`, `ekacare_update_document`, `ekacare_update_patient_profile_details`, `ekacare_update_schedule`, `ekacare_update_session`, `ekacare_upload_report` `new-actions` `data-sync` Initial release covering Eka Care EMR, IPD, EkaScribe, Health AI, health records and ABDM APIs, with data sync for clinics, doctors, IPD admissions, note templates, sessions, webhooks and the coding registry. # Elastic Cloud Source: https://docs.stackone.com/connectors/elasticcloud/index How to set up the Elastic Cloud connector, plus the actions that are available.
Elastic Cloud
Previewv1.3.4
62 actions · 1 auth method
Infrastructure IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate a Cloud API key from your Elastic Cloud Organization settings. Organization owner access is required. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/elasticcloud/index.md for the full list. # Elastic Cloud Changelog Source: https://docs.stackone.com/connectors/elasticcloud/changelog Release history for the Elastic Cloud connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists and lookups now include pending invitations with a pending status. `elasticcloud_unified_get_user`, `elasticcloud_unified_list_users` `descriptions` Documented provider response behaviours and limitations across 11 actions, including empty response patterns for async operations and subscription tier restrictions. `elasticcloud_add_role_assignments`, `elasticcloud_create_ruleset_association`, `elasticcloud_delete_extension`, `elasticcloud_delete_ruleset_association`, `elasticcloud_delete_traffic_filter_ruleset`, `elasticcloud_get_trusted_environments`, `elasticcloud_remove_role_assignments`, `elasticcloud_restart_deployment_elasticsearch_resource`, `elasticcloud_start_resource_instances`, `elasticcloud_stop_resource_instances`, `elasticcloud_update_deployment` `action-fixes` Fixed update_deployment schema to preserve kibana and integrations_server plan fields, removed unsupported node_attributes, and improved description guidance for alias and settings updates. `elasticcloud_create_deployment`, `elasticcloud_update_deployment` `guide-fixes` Fixed API Key field label and placeholder to match auth method name and show expected key format. `data-sync` Added DataSync support for 7 list actions (deployments, search deployments, extensions, organizations, traffic filter rulesets, unified users, unified organizations) with full refresh sync. `elasticcloud_list_deployments`, `elasticcloud_list_extensions`, `elasticcloud_list_organizations`, `elasticcloud_list_traffic_filter_rulesets`, `elasticcloud_search_deployments`, `elasticcloud_unified_list_organizations`, `elasticcloud_unified_list_users` `bug-fix` `improved-descriptions` Fixed update_deployment description to remove solution_type from updatable settings, documented azure_private_endpoint source format, clarified kibana plan.kibana requirement for alias updates, and marked create_extension as preview. `elasticcloud_create_extension`, `elasticcloud_create_traffic_filter_ruleset`, `elasticcloud_update_deployment`, `elasticcloud_update_traffic_filter_ruleset` `improved-descriptions` Improved action descriptions for update_deployment, cancel_pending_plan, and organization actions to clarify API requirements and prevent common agent errors. `elasticcloud_cancel_pending_plan`, `elasticcloud_delete_organization_invitations`, `elasticcloud_get_organization`, `elasticcloud_list_organization_invitations`, `elasticcloud_list_organization_members`, `elasticcloud_remove_members`, `elasticcloud_send_invitations`, `elasticcloud_update_deployment` `new-actions` `bug-fix` `improved-guides` Added upgrade_deployment and delete_organization_invitations actions, fixed required fields and Content-Type headers, improved connection guide with screenshots. `new-actions` Added unified IAM actions for users, roles, organizations, credentials, and resource users (all preview). # ElevenLabs Source: https://docs.stackone.com/connectors/elevenlabs/index How to set up the ElevenLabs connector, plus the actions and events that are available.
ElevenLabs
Previewv0.3.0
182 actions · 8 events · 1 auth method
AI IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an ElevenLabs user API key or service account API key. The roster needs the workspace\_members\_read permission; read... Optionally, configure receiving Events for ElevenLabs into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/elevenlabs/index.md for the full list. ## Events See https://docs.stackone.com/connectors/elevenlabs/index.md for the full list. # ElevenLabs Changelog Source: https://docs.stackone.com/connectors/elevenlabs/changelog Release history for the ElevenLabs connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Adds 67 actions for speech (audio file output, dialogue, sound effects), voice design, remix and cloning, voice collections, professional voice clone samples and training, speech to text, forced alignment, music, speech engines, Audio Native, workspace analytics, group members, resource sharing and single-use tokens. Text to speech and dialogue actions document the eleven_v4 and eleven_v4_turbo models. `elevenlabs_add_shared_voice`, `elevenlabs_add_voice`, `elevenlabs_add_voice_to_collection`, `elevenlabs_add_workspace_group_member`, `elevenlabs_compose_music`, `elevenlabs_create_audio_native_project`, `elevenlabs_create_dialogue`, `elevenlabs_create_dialogue_with_timing`, `elevenlabs_create_forced_alignment`, `elevenlabs_create_music_finetune`, `elevenlabs_create_music_plan`, `elevenlabs_create_pronunciation_dictionary_from_file`, `elevenlabs_create_single_use_token`, `elevenlabs_create_sound_effect`, `elevenlabs_create_speech`, `elevenlabs_create_speech_engine`, `elevenlabs_create_transcription`, `elevenlabs_create_voice_collection`, `elevenlabs_create_voice_from_preview`, `elevenlabs_delete_audio_isolation_history_item`, `elevenlabs_delete_music_finetune`, `elevenlabs_delete_pvc_voice_sample`, `elevenlabs_delete_speech_engine`, `elevenlabs_delete_transcription`, `elevenlabs_delete_voice_collection`, `elevenlabs_design_voice`, `elevenlabs_download_history_items`, `elevenlabs_duplicate_speech_engine`, `elevenlabs_edit_voice`, `elevenlabs_get_audio_native_settings`, `elevenlabs_get_dubbing_transcript`, `elevenlabs_get_music_finetune`, `elevenlabs_get_pvc_separated_speaker_audio`, `elevenlabs_get_pvc_speaker_separation_status`, `elevenlabs_get_pvc_voice_sample_audio`, `elevenlabs_get_pvc_voice_sample_waveform`, `elevenlabs_get_speech_engine`, `elevenlabs_get_transcription`, `elevenlabs_get_voice_collection`, `elevenlabs_get_voice_preview_audio`, `elevenlabs_get_voice_sample_audio`, `elevenlabs_get_workspace_usage`, `elevenlabs_invite_users`, `elevenlabs_list_api_requests`, `elevenlabs_list_audio_effects`, `elevenlabs_list_audio_isolation_history`, `elevenlabs_list_music_finetunes`, `elevenlabs_list_speech_engines`, `elevenlabs_list_voice_collections`, `elevenlabs_remix_voice`, `elevenlabs_remove_voice_from_collection`, `elevenlabs_remove_workspace_group_member`, `elevenlabs_request_pvc_manual_verification`, `elevenlabs_set_api_key_third_party_disabling_policy`, `elevenlabs_set_pronunciation_dictionary_rules`, `elevenlabs_share_workspace_resource`, `elevenlabs_start_pvc_speaker_separation`, `elevenlabs_train_pvc_voice`, `elevenlabs_unshare_workspace_resource`, `elevenlabs_update_audio_native_content`, `elevenlabs_update_audio_native_content_from_url`, `elevenlabs_update_music_finetune`, `elevenlabs_update_pvc_voice`, `elevenlabs_update_pvc_voice_sample`, `elevenlabs_update_service_account_api_key`, `elevenlabs_update_speech_engine`, `elevenlabs_update_voice_collection`, `elevenlabs_upload_music` `elevenlabs_add_pronunciation_dictionary_rules`, `elevenlabs_create_pronunciation_dictionary_from_rules`, `elevenlabs_create_speech_with_timing` `bug-fix` `new-actions` Adds knowledge base file upload and agent test runs with results. Delete and move actions now confirm success, Update Tool accepts the configuration returned by Get Tool, and dubbing accents are no longer case-sensitive. `elevenlabs_create_knowledge_base_document_from_file`, `elevenlabs_get_test_invocation`, `elevenlabs_list_test_invocations`, `elevenlabs_run_agent_tests` `elevenlabs_bulk_move_knowledge_base_documents`, `elevenlabs_bulk_move_tests`, `elevenlabs_cancel_batch_call`, `elevenlabs_create_dubbing`, `elevenlabs_create_knowledge_base_document_from_text`, `elevenlabs_delete_agent`, `elevenlabs_delete_batch_call`, `elevenlabs_delete_conversation`, `elevenlabs_delete_knowledge_base_document`, `elevenlabs_delete_secret`, `elevenlabs_delete_tool`, `elevenlabs_get_dubbed_file`, `elevenlabs_send_conversation_feedback`, `elevenlabs_update_tool` `new-actions` `webhook` `breaking` `guide` Adds 96 actions for agents, conversations, knowledge base, tools, phone numbers, batch calling, voices, speech, dubbing, history, pronunciation and workspace admin, plus post-call webhook events and data sync on 19 lists. Workspace, user and service account read actions are renamed from list_* or get_user_info to get_* names. `elevenlabs_add_pronunciation_dictionary_rules`, `elevenlabs_add_samples_to_pvc_voice`, `elevenlabs_bulk_delete_knowledge_base_documents`, `elevenlabs_bulk_move_knowledge_base_documents`, `elevenlabs_bulk_move_tests`, `elevenlabs_cancel_batch_call`, `elevenlabs_create_agent`, `elevenlabs_create_auth_connection`, `elevenlabs_create_dubbing`, `elevenlabs_create_knowledge_base_document_from_text`, `elevenlabs_create_knowledge_base_document_from_url`, `elevenlabs_create_knowledge_base_folder`, `elevenlabs_create_pronunciation_dictionary_from_rules`, `elevenlabs_create_pvc_voice`, `elevenlabs_create_secret`, `elevenlabs_create_service_account`, `elevenlabs_create_service_account_api_key`, `elevenlabs_create_speech_with_timing`, `elevenlabs_create_test`, `elevenlabs_create_tool`, `elevenlabs_create_workspace_webhook`, `elevenlabs_delete_agent`, `elevenlabs_delete_auth_connection`, `elevenlabs_delete_batch_call`, `elevenlabs_delete_conversation`, `elevenlabs_delete_dubbing`, `elevenlabs_delete_history_item`, `elevenlabs_delete_invite`, `elevenlabs_delete_knowledge_base_document`, `elevenlabs_delete_phone_number`, `elevenlabs_delete_secret`, `elevenlabs_delete_service_account_api_key`, `elevenlabs_delete_tool`, `elevenlabs_delete_voice`, `elevenlabs_delete_voice_sample`, `elevenlabs_delete_workspace_webhook`, `elevenlabs_duplicate_agent`, `elevenlabs_edit_voice_settings`, `elevenlabs_export_batch_call_results`, `elevenlabs_get_agent`, `elevenlabs_get_auth_connections`, `elevenlabs_get_batch_call`, `elevenlabs_get_conversation`, `elevenlabs_get_default_voice_settings`, `elevenlabs_get_dependent_agents_for_documents`, `elevenlabs_get_dubbed_file`, `elevenlabs_get_dubbing`, `elevenlabs_get_history_item`, `elevenlabs_get_history_item_audio`, `elevenlabs_get_knowledge_base_document`, `elevenlabs_get_phone_number`, `elevenlabs_get_pronunciation_dictionary`, `elevenlabs_get_pronunciation_dictionary_version`, `elevenlabs_get_pvc_verification_captcha`, `elevenlabs_get_secret`, `elevenlabs_get_service_account_api_keys`, `elevenlabs_get_service_accounts`, `elevenlabs_get_tool`, `elevenlabs_get_user`, `elevenlabs_get_user_subscription`, `elevenlabs_get_voice`, `elevenlabs_get_voice_accents`, `elevenlabs_get_voice_settings`, `elevenlabs_get_workspace_groups`, `elevenlabs_get_workspace_members`, `elevenlabs_import_phone_number`, `elevenlabs_invite_user`, `elevenlabs_list_agents`, `elevenlabs_list_audit_logs`, `elevenlabs_list_batch_calls`, `elevenlabs_list_conversations`, `elevenlabs_list_dubs`, `elevenlabs_list_generated_items`, `elevenlabs_list_knowledge_base_documents`, `elevenlabs_list_models`, `elevenlabs_list_phone_numbers`, `elevenlabs_list_pronunciation_dictionaries`, `elevenlabs_list_secrets`, `elevenlabs_list_shared_voices`, `elevenlabs_list_similar_voices`, `elevenlabs_list_tests`, `elevenlabs_list_tools`, `elevenlabs_list_voices`, `elevenlabs_list_voices_legacy`, `elevenlabs_list_workspace_webhooks`, `elevenlabs_query_agent_knowledge_base_rag`, `elevenlabs_remove_pronunciation_dictionary_rules`, `elevenlabs_retry_batch_call`, `elevenlabs_search_knowledge_base`, `elevenlabs_send_conversation_feedback`, `elevenlabs_submit_batch_call`, `elevenlabs_update_agent`, `elevenlabs_update_auth_connection`, `elevenlabs_update_knowledge_base_document`, `elevenlabs_update_member`, `elevenlabs_update_phone_number`, `elevenlabs_update_pronunciation_dictionary`, `elevenlabs_update_secret`, `elevenlabs_update_tool`, `elevenlabs_update_workspace_webhook`, `elevenlabs_verify_pvc_verification_captcha` `elevenlabs_get_user_info`, `elevenlabs_list_service_account_api_keys`, `elevenlabs_list_service_accounts`, `elevenlabs_list_workspace_groups`, `elevenlabs_list_workspace_members` `elevenlabs_unified_get_group`, `elevenlabs_unified_list_groups`, `elevenlabs_unified_list_users` `improvement` Workspace, user and service account actions are now also listed under AI, the API key guide says which plan and seat you need, and a full user sync no longer re-fetches the workspace roster and groups on every page. `elevenlabs_get_user_info`, `elevenlabs_get_workspace_resource`, `elevenlabs_list_service_account_api_keys`, `elevenlabs_list_service_accounts`, `elevenlabs_list_workspace_groups`, `elevenlabs_list_workspace_members`, `elevenlabs_search_workspace_groups`, `elevenlabs_unified_list_users` `new-connector` Initial ElevenLabs connector for reviewing who has access to an ElevenLabs workspace, covering workspace members, their seat types, user groups and service accounts, including unified IAM users, roles, groups and connection details. # Employment Hero Source: https://docs.stackone.com/connectors/employmenthero/index How to set up the Employment Hero connector, plus the actions and events that are available.
Employment Hero
v2.1.0
52 actions · 46 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth application in the Employment Hero Developer Portal. Access tokens expire after 15 minutes... Optionally, configure receiving Events for Employment Hero into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/employmenthero/index.md for the full list. ## Events See https://docs.stackone.com/connectors/employmenthero/index.md for the full list. # Employment Hero Changelog Source: https://docs.stackone.com/connectors/employmenthero/changelog Release history for the Employment Hero connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Added 45 webhook events for employees, bank accounts, employment histories, custom fields, leave requests, timesheet entries, certifications, employee certifications, custom form responses, goals and key results. Add the account's Native Webhook URL under Developer Portal > My Webhooks in Employment Hero (Platinum plan). `improvement` Clarified certification and work site descriptions — certification names must be unique within the organisation, the county field is a free-text region label, and work sites (with their departments and HR positions) are separate from work locations. `employmenthero_create_certification`, `employmenthero_list_work_sites`, `employmenthero_update_certification` `bug-fix` Creating or updating a certification now turns on approval automatically when approvers are given, and points to get_organisation for the organisation's country, which decides whether state, county or territory applies. `employmenthero_create_certification`, `employmenthero_get_organisation`, `employmenthero_update_certification` `bug-fix` Fixed certification and employee onboarding inputs that the Employment Hero API rejects — corrected the renewal period and salary period options, documented which regional field (state, county or territory) each country accepts, documented that approval and approvers must be set together, and corrected the certification attachment field to take file URLs. `employmenthero_create_employee_salary_version` `employmenthero_archive_certification`, `employmenthero_certification_polling_status`, `employmenthero_create_certification`, `employmenthero_create_department`, `employmenthero_create_employee_document`, `employmenthero_create_work_site`, `employmenthero_delete_certification`, `employmenthero_get_certification`, `employmenthero_get_employee`, `employmenthero_get_employee_superannuation`, `employmenthero_get_employee_tax_declaration`, `employmenthero_get_form`, `employmenthero_get_form_response`, `employmenthero_get_leave_request`, `employmenthero_get_leave_requests`, `employmenthero_get_organisation`, `employmenthero_get_rostered_shift`, `employmenthero_get_unavailability`, `employmenthero_list_certifications`, `employmenthero_list_contractor_job_histories`, `employmenthero_list_cost_centres`, `employmenthero_list_custom_fields`, `employmenthero_list_employee_bank_accounts`, `employmenthero_list_employee_certifications`, `employmenthero_list_employee_custom_fields`, `employmenthero_list_employee_documents`, `employmenthero_list_employee_emergency_contacts`, `employmenthero_list_employee_employment_histories`, `employmenthero_list_employee_pay_details`, `employmenthero_list_employee_payslips`, `employmenthero_list_employees`, `employmenthero_list_employing_entities`, `employmenthero_list_form_responses`, `employmenthero_list_forms`, `employmenthero_list_leave_categories`, `employmenthero_list_organisations`, `employmenthero_list_policies`, `employmenthero_list_rostered_shifts`, `employmenthero_list_team_employees`, `employmenthero_list_teams`, `employmenthero_list_timesheet_entries`, `employmenthero_list_unavailabilities`, `employmenthero_list_work_locations`, `employmenthero_list_work_sites`, `employmenthero_polling_onboard_employee`, `employmenthero_polling_onboard_result`, `employmenthero_quick_add_contractor`, `employmenthero_quick_add_employee`, `employmenthero_update_certification`, `employmenthero_update_department`, `employmenthero_upload_certification_files` `guide` `description-fix` Improved the OAuth 2.0 connection guides — listed the specific API scopes to enable (the reads the connection test needs, full read coverage, and the writes each mutating action requires), clarified that the application name is an example rather than a fixed value, and corrected the Organisation ID section to retrieve the API organisation UUID from GET /api/v1/organisations instead of the platform ID in the web app URL. Replaced the Organisation ID placeholder with an example UUID. `guide` Updated the OAuth 2.0 connection guides with verified Developer Portal steps and screenshots. `auth` `breaking` OAuth2 authorization now uses PKCE, which Employment Hero requires from September 2026. Existing connections may need to be reconnected before then. `employmenthero_archive_certification`, `employmenthero_certification_polling_status`, `employmenthero_create_certification`, `employmenthero_create_department`, `employmenthero_create_employee_document`, `employmenthero_create_work_site`, `employmenthero_delete_certification`, `employmenthero_get_certification`, `employmenthero_get_employee`, `employmenthero_get_employee_superannuation`, `employmenthero_get_employee_tax_declaration`, `employmenthero_get_form`, `employmenthero_get_form_response`, `employmenthero_get_leave_request`, `employmenthero_get_leave_requests`, `employmenthero_get_organisation`, `employmenthero_get_rostered_shift`, `employmenthero_get_unavailability`, `employmenthero_list_certifications`, `employmenthero_list_contractor_job_histories`, `employmenthero_list_cost_centres`, `employmenthero_list_custom_fields`, `employmenthero_list_employee_bank_accounts`, `employmenthero_list_employee_certifications`, `employmenthero_list_employee_custom_fields`, `employmenthero_list_employee_documents`, `employmenthero_list_employee_emergency_contacts`, `employmenthero_list_employee_employment_histories`, `employmenthero_list_employee_pay_details`, `employmenthero_list_employee_payslips`, `employmenthero_list_employees`, `employmenthero_list_employing_entities`, `employmenthero_list_form_responses`, `employmenthero_list_forms`, `employmenthero_list_leave_categories`, `employmenthero_list_organisations`, `employmenthero_list_policies`, `employmenthero_list_rostered_shifts`, `employmenthero_list_team_employees`, `employmenthero_list_teams`, `employmenthero_list_timesheet_entries`, `employmenthero_list_unavailabilities`, `employmenthero_list_work_locations`, `employmenthero_list_work_sites`, `employmenthero_polling_onboard_employee`, `employmenthero_polling_onboard_result`, `employmenthero_quick_add_contractor`, `employmenthero_quick_add_employee`, `employmenthero_update_certification`, `employmenthero_update_department`, `employmenthero_upload_certification_files` `new-feature` Enabled scheduled data sync on twelve list actions — employees, organisations, employing entities, work locations, work sites, teams, certifications, custom fields, cost centres, policies, leave categories and leave requests — so these collections can be kept in sync and searched without calling Employment Hero on every request. Each syncs by full refresh, because the Employment Hero API exposes no updated-since filter on any endpoint. # Envi Source: https://docs.stackone.com/connectors/envi/index How to set up the Envi connector, plus the actions that are available.
Envi
Betav0.3.0
104 actions · 1 auth method
ERP Logistics Accounting Documents Procurement
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses the OAuth 2.0 Resource Owner Password Credentials grant. Requires an Envi username and password, and the Envi envir... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/envi/index.md for the full list. # Envi Changelog Source: https://docs.stackone.com/connectors/envi/changelog Release history for the Envi connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `bug-fix` New actions list the items of a matched invoice, a receipt and a purchase order, and the invoices in an AP batch. Downloaded file attachments now arrive intact. Filter and sort tips for all list actions are corrected. `envi_list_ap_batch_invoices`, `envi_list_matched_invoice_items_by_invoice`, `envi_list_purchase_order_items_by_purchase_order`, `envi_list_receipt_items_by_receipt` `envi_create_ap_batch_export_history`, `envi_download_file_attachment`, `envi_export_ap_batch`, `envi_get_list_of_adjustment_items`, `envi_get_list_of_ap_batches`, `envi_get_list_of_classifications`, `envi_get_list_of_departments`, `envi_get_list_of_facilities`, `envi_get_list_of_files_by_entity_id`, `envi_get_list_of_inventory_items`, `envi_get_list_of_inventory_locations`, `envi_get_list_of_inventory_locations_cost_and_quantity`, `envi_get_list_of_inventory_snapshot_items`, `envi_get_list_of_inventory_snapshots`, `envi_get_list_of_inventory_vendors`, `envi_get_list_of_locations`, `envi_get_list_of_manufacturers`, `envi_get_list_of_matched_invoice_items`, `envi_get_list_of_matched_invoices`, `envi_get_list_of_par_area_items`, `envi_get_list_of_par_areas`, `envi_get_list_of_po_confirmation_items`, `envi_get_list_of_po_confirmations`, `envi_get_list_of_po_receipt_items`, `envi_get_list_of_po_receipts`, `envi_get_list_of_purchase_order_items`, `envi_get_list_of_purchase_orders`, `envi_get_list_of_requisition_fill_items`, `envi_get_list_of_requisition_fills`, `envi_get_list_of_requisition_items`, `envi_get_list_of_requisitions`, `envi_get_list_of_usage_items`, `envi_get_list_of_vendor_addresses`, `envi_get_list_of_vendor_contacts`, `envi_get_list_of_vendor_facilities`, `envi_get_list_of_vendors` `bug-fix` List actions now work when you pass top, skip, filter, orderby or search, and Data Sync can now page through Envi records. `envi_get_list_of_adjustment_items`, `envi_get_list_of_ap_batches`, `envi_get_list_of_classifications`, `envi_get_list_of_departments`, `envi_get_list_of_facilities`, `envi_get_list_of_files_by_entity_id`, `envi_get_list_of_inventory_items`, `envi_get_list_of_inventory_locations`, `envi_get_list_of_inventory_locations_cost_and_quantity`, `envi_get_list_of_inventory_snapshot_items`, `envi_get_list_of_inventory_snapshots`, `envi_get_list_of_inventory_vendors`, `envi_get_list_of_locations`, `envi_get_list_of_manufacturers`, `envi_get_list_of_matched_invoice_items`, `envi_get_list_of_matched_invoices`, `envi_get_list_of_par_area_items`, `envi_get_list_of_par_areas`, `envi_get_list_of_po_confirmation_items`, `envi_get_list_of_po_confirmations`, `envi_get_list_of_po_receipt_items`, `envi_get_list_of_po_receipts`, `envi_get_list_of_purchase_order_items`, `envi_get_list_of_purchase_orders`, `envi_get_list_of_requisition_fill_items`, `envi_get_list_of_requisition_fills`, `envi_get_list_of_requisition_items`, `envi_get_list_of_requisitions`, `envi_get_list_of_usage_items`, `envi_get_list_of_vendor_addresses`, `envi_get_list_of_vendor_contacts`, `envi_get_list_of_vendor_facilities`, `envi_get_list_of_vendors` `bug-fix` Connecting an Envi account now works. The sign-in request is sent in the format Envi requires. `data-sync` Enabled Data Sync across the full Envi catalog, including vendors, inventory, purchase orders, requisitions, receipts, invoices, PAR areas, facilities, locations and reference data. `envi_get_list_of_adjustment_items`, `envi_get_list_of_ap_batches`, `envi_get_list_of_classifications`, `envi_get_list_of_departments`, `envi_get_list_of_facilities`, `envi_get_list_of_inventory_items`, `envi_get_list_of_inventory_locations`, `envi_get_list_of_inventory_locations_cost_and_quantity`, `envi_get_list_of_inventory_snapshot_items`, `envi_get_list_of_inventory_snapshots`, `envi_get_list_of_inventory_vendors`, `envi_get_list_of_locations`, `envi_get_list_of_manufacturers`, `envi_get_list_of_matched_invoice_items`, `envi_get_list_of_matched_invoices`, `envi_get_list_of_par_area_items`, `envi_get_list_of_par_areas`, `envi_get_list_of_po_confirmation_items`, `envi_get_list_of_po_confirmations`, `envi_get_list_of_po_receipt_items`, `envi_get_list_of_po_receipts`, `envi_get_list_of_purchase_order_items`, `envi_get_list_of_purchase_orders`, `envi_get_list_of_requisition_fill_items`, `envi_get_list_of_requisition_fills`, `envi_get_list_of_requisition_items`, `envi_get_list_of_requisitions`, `envi_get_list_of_usage_items`, `envi_get_list_of_vendor_addresses`, `envi_get_list_of_vendor_contacts`, `envi_get_list_of_vendor_facilities`, `envi_get_list_of_vendors` `new-connector` Initial action mapping # Envoy Source: https://docs.stackone.com/connectors/envoy/index How to set up the Envoy connector, plus the actions that are available.
Envoy
v1.3.0
49 actions · 2 auth methods
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use an API Key for authentication. Recommended for simpler setup - provides full API access without token management. Use OAuth2 Password Grant for user-based authentication with username and password. Provides access based on user permis... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/envoy/index.md for the full list. # Envoy Changelog Source: https://docs.stackone.com/connectors/envoy/changelog Release history for the Envoy connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for employees, entries, flows, blocklists, work schedules, spaces, desks, locations, users, groups and organizations, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Envoy API exposes no updated-since filter a sync can use. `envoy_list_blocklists`, `envoy_list_desks`, `envoy_list_employees`, `envoy_list_entries`, `envoy_list_flows`, `envoy_list_locations`, `envoy_list_spaces`, `envoy_list_work_schedules`, `envoy_unified_list_groups`, `envoy_unified_list_organizations`, `envoy_unified_list_users` `guide-changes` Removed the unrelated external connection-guide links from the API Key and OAuth2 Password Grant auth methods so the embedded connection guide is used, and removed the duplicated scope list from the OAuth2 Link Account guide so scopes are documented once in the Connector profile setup. `description-fix` Clarified that invites are located by invitee or host email rather than by name, documented that the approval-status filter must be uppercase, and documented recurring-invite update limitations. `envoy_list_invites`, `envoy_update_recurring_invite` `docs` Added connection guides (setup and config) for the API Key and OAuth2 Password Grant auth methods, authored from a live walkthrough of the Envoy Dev Dashboard with step screenshots. `removed-actions` `bug-fix` Removed unified IAM roles (list_roles, get_role) — Envoy has no roles-enumeration API and the synthesized "employee" role described a record type, not a role. Fixed unified IAM users and groups list pagination to a fixed page fan-out so multi-page tenants no longer 400 on the second page. `envoy_unified_get_role`, `envoy_unified_list_roles` `envoy_unified_get_user`, `envoy_unified_list_groups`, `envoy_unified_list_organizations`, `envoy_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, and credentials (preview, live QA owed). # Eploy Source: https://docs.stackone.com/connectors/eploy/index How to set up the Eploy connector, plus the actions that are available.
Eploy
Previewv1.1.0
92 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Administrator privileges within Eploy. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/eploy/index.md for the full list. # Eploy Changelog Source: https://docs.stackone.com/connectors/eploy/changelog Release history for the Eploy connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for option values, file upload types, CV upload types and the application, candidate, company, contact, placement and vacancy question lists, so these reference collections can be pulled into StackOne and read without calling Eploy. All run as a full refresh on every sync, because Eploy exposes no updated-since filter on these endpoints. # Eurecia Source: https://docs.stackone.com/connectors/eurecia/index How to set up the Eurecia connector, plus the actions that are available.
Eurecia
Betav0.1.0
95 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. A persistent API token generated on an employee sheet is exchanged for a short-lived sessi... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/eurecia/index.md for the full list. # Eurecia Changelog Source: https://docs.stackone.com/connectors/eurecia/changelog Release history for the Eurecia connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial action mappings for Eurecia # Eventbrite Source: https://docs.stackone.com/connectors/eventbrite/index How to set up the Eventbrite connector, plus the actions and events that are available.
Eventbrite
Previewv2.0.4
90 actions · 15 events · 2 auth methods
Events IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Private Tokens provide quick authentication for single-user integrations without the OAuth flow. Requires registering an OAuth app. Optionally, configure receiving Events for Eventbrite into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/eventbrite/index.md for the full list. ## Events See https://docs.stackone.com/connectors/eventbrite/index.md for the full list. # Eventbrite Changelog Source: https://docs.stackone.com/connectors/eventbrite/changelog Release history for the Eventbrite connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed user and organization lists failing or returning extra empty pages. Users now include their email and name. `eventbrite_unified_get_user`, `eventbrite_unified_list_organizations`, `eventbrite_unified_list_users` `documentation` `events-guide` Moved 27 actions from preview to beta. Added events guide for webhook setup. `eventbrite_create_inventory_tier`, `eventbrite_create_multiple_inventory_tiers`, `eventbrite_create_team`, `eventbrite_get_attendee`, `eventbrite_get_order`, `eventbrite_list_attendees_by_team`, `eventbrite_list_event_custom_questions`, `eventbrite_list_event_inventory_tiers`, `eventbrite_list_events_by_series`, `eventbrite_list_teams`, `eventbrite_publish_event`, `eventbrite_retrieve_team`, `eventbrite_search_teams_by_name`, `eventbrite_set_structured_content_image`, `eventbrite_set_structured_content_video`, `eventbrite_unified_get_me`, `eventbrite_unified_get_organization`, `eventbrite_unified_get_role`, `eventbrite_unified_get_user`, `eventbrite_unified_list_organizations`, `eventbrite_unified_list_roles`, `eventbrite_unified_list_users` `documentation` Improved connection guides with screenshots, complete form field documentation, and clearer field descriptions for both Private Token and OAuth 2.0 authentication. `data-sync-improvements` Fixed list_subcategories DataSync pagination to sync all 216 records across pages. Changed changed_since input type to datetime_string. `eventbrite_list_orders_by_organization`, `eventbrite_list_subcategories` `data-sync` Added DataSync v2 support for 5 list actions (categories, formats, subcategories, organizations, unified organizations) with cursor-based pagination and continuation token inputs. `eventbrite_list_attendees_by_event`, `eventbrite_list_attendees_by_organization`, `eventbrite_list_categories`, `eventbrite_list_event_custom_questions`, `eventbrite_list_event_default_questions`, `eventbrite_list_events_by_organization`, `eventbrite_list_events_by_venue`, `eventbrite_list_formats`, `eventbrite_list_members_of_organization`, `eventbrite_list_orders_by_event`, `eventbrite_list_orders_by_organization`, `eventbrite_list_orders_by_user`, `eventbrite_list_organizations`, `eventbrite_list_organizations_by_user`, `eventbrite_list_roles_by_organization`, `eventbrite_list_subcategories`, `eventbrite_list_ticket_classes_by_event`, `eventbrite_list_ticket_groups_by_organization`, `eventbrite_list_venues_by_organization`, `eventbrite_list_webhooks_by_organization_id`, `eventbrite_unified_list_organizations` `webhook` `new-actions` Added programmatic webhook support for 15 event types including attendee, event, order, ticket, and venue changes. `bug-fix` Standardized action category capitalization for more consistent portal filters. `eventbrite_unified_get_me`, `eventbrite_unified_get_organization`, `eventbrite_unified_get_role`, `eventbrite_unified_get_user`, `eventbrite_unified_list_organizations`, `eventbrite_unified_list_roles`, `eventbrite_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, and credentials, built on Eventbrite's organization membership, roles, and current-user identity data. Role and user IDs include their organization, since a role can't be looked up or listed without specifying which organization it belongs to. Groups aren't supported, since Eventbrite has no organization-level groups, only event-specific attendee teams. # Exa Source: https://docs.stackone.com/connectors/exa/index How to set up the Exa connector, plus the actions that are available.
Exa
Betav0.2.0
35 actions · 1 auth method
Search
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key authentication. Exa accepts the key as a Bearer token in the Authorization header on every request. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/exa/index.md for the full list. # Exa Changelog Source: https://docs.stackone.com/connectors/exa/changelog Release history for the Exa connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for websets, monitors, imports and events, with incremental sync on events. `exa_list_events`, `exa_list_imports`, `exa_list_monitors`, `exa_list_websets` `bug-fix` Corrected the API key connection guide to use the Exa dashboard's actual button label, and added a suggested example name for the API key. `connection-guide` Added a step-by-step auth guide to connect an account. `new-connector` Initial release of the Exa connector for the Exa Search, and Websets APIs. # Expensify Source: https://docs.stackone.com/connectors/expensify/index How to set up the Expensify connector, plus the actions that are available.
Expensify
v1.2.1
27 actions · 1 auth method
Expense Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Partner User ID and Partner User Secret pair generated from the Expensify Integrations page. No app registration... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/expensify/index.md for the full list. # Expensify Changelog Source: https://docs.stackone.com/connectors/expensify/changelog Release history for the Expensify connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `description-fix` Clearer error and setup guidance when the connected credentials can't see any Expensify workspace. `expensify_unified_get_user`, `expensify_unified_list_users` `data-sync` Added scheduled data sync to the policies, organizations, and roles list actions — so these collections can be kept in sync and read back without calling Expensify on every request. Each refreshes in full on every run, since the Integration Server endpoints have no updated-since filter to drive incremental sync. `expensify_list_policies`, `expensify_unified_list_organizations`, `expensify_unified_list_roles` `description-fix` Aligned the create_report action description with its employeeEmail parameter guidance so agents call list_policies to resolve the email instead of omitting the effectively-required field (matching the create_expense fix). `expensify_create_report` `bug-fix` Standardized action category capitalization for more consistent portal filters. `expensify_auth_test`, `expensify_unified_get_me`, `expensify_unified_get_organization`, `expensify_unified_get_role`, `expensify_unified_get_user`, `expensify_unified_list_organizations`, `expensify_unified_list_resource_types`, `expensify_unified_list_resource_users`, `expensify_unified_list_roles`, `expensify_unified_list_users` `new-actions` Added unified IAM support for policy users, roles, organizations, credentials, and resource users, with an optional organization filter on single-user lookups and 404s instead of empty results for unknown ids. `expensify_auth_test`, `expensify_unified_get_me`, `expensify_unified_get_organization`, `expensify_unified_get_role`, `expensify_unified_get_user`, `expensify_unified_list_organizations`, `expensify_unified_list_resource_types`, `expensify_unified_list_resource_users`, `expensify_unified_list_roles`, `expensify_unified_list_users` `description-fix` Aligned the create_expense action description with its employeeEmail parameter guidance so agents call list_policies to resolve the email instead of omitting the effectively-required field. `expensify_create_expense` `bug-fix` Fixed create_expense 'requestJobDescription is missing' 500s by expanding request-body field-combination coverage. Improved action descriptions for create_expense, update_employee, and update_report_status to fix agent tool-use (email discoverability, self-approval limits, tax and approval prerequisites). `expensify_create_expense`, `expensify_update_employee`, `expensify_update_report_status` `bug-fix` Made employeeEmail optional on create_expense and create_report (unblocks self-service); expanded export_reports to cover all common filter/output combinations, fixing 500 'requestJobDescription is missing'; surfaced Expensify's embedded responseCode errors as real HTTP errors on create_expense/create_report/update_employee; restored update_employee upsert wording (marked preview for the approvalLimit backend limitation); corrected action descriptions. # Expo Source: https://docs.stackone.com/connectors/expo/index How to set up the Expo connector, plus the actions and events that are available.
Expo
v1.3.0
42 actions · 2 events · 1 auth method
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with an EAS access token (a personal access token or a robot-user token). The token is sent as a bearer tok... Optionally, configure receiving Events for Expo into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/expo/index.md for the full list. ## Events See https://docs.stackone.com/connectors/expo/index.md for the full list. # Expo Changelog Source: https://docs.stackone.com/connectors/expo/changelog Release history for the Expo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Webhook events are now delivered to the per-connection Native Webhook URL on the linked account. The previous routing that matched deliveries to a connection by the Expo account name is no longer supported and has been removed. `new-feature` Added inbound webhook support for EAS BUILD and SUBMIT events. EAS has no webhook dashboard UI, so webhooks are registered manually via the existing Create Webhook action using the new Native Webhook URL field, which carries a per-account routing token so events resolve to the correct connected account (the new Expo Account Name field is a fallback identifier). `new-feature` Added DataSync support for List Accounts, so the account list can be synced into StackOne on a schedule and read without calling Expo. It runs as a full refresh on every sync, since Expo's accounts endpoint offers no way to filter by last-updated time. `expo_list_accounts` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Standardized action category capitalization for more consistent portal filters. `expo_cancel_build`, `expo_cancel_submission`, `expo_create_app`, `expo_create_branch`, `expo_create_build`, `expo_create_channel`, `expo_create_environment_variable`, `expo_create_submission`, `expo_create_webhook`, `expo_delete_branch`, `expo_delete_build`, `expo_delete_channel`, `expo_delete_environment_variable`, `expo_delete_webhook`, `expo_get_account`, `expo_get_app`, `expo_get_branch`, `expo_get_build`, `expo_get_channel`, `expo_get_deployment`, `expo_get_me`, `expo_get_submission`, `expo_get_update`, `expo_get_webhook`, `expo_get_workflow`, `expo_get_workflow_run`, `expo_list_accounts`, `expo_list_apps`, `expo_list_branches`, `expo_list_builds`, `expo_list_channels`, `expo_list_deployments`, `expo_list_environment_variables`, `expo_list_submissions`, `expo_list_updates`, `expo_list_updates_by_group`, `expo_list_webhooks`, `expo_list_workflow_runs`, `expo_list_workflows`, `expo_update_channel`, `expo_update_environment_variable`, `expo_update_webhook` `bug-fix` Removed the Delete App action, which Expo does not allow through API access tokens, and clarified the branch-mapping format used when creating and updating channels. `expo_delete_app` `expo_create_channel`, `expo_update_channel` `new-connector` Initial Expo (EAS) connector — build, ship, and monitor apps via the Expo GraphQL API. Covers apps, builds, submissions, updates, branches, channels, deployments, workflows, workflow runs, environment variables, and webhooks. # Facebook Source: https://docs.stackone.com/connectors/facebook/index How to set up the Facebook connector, plus the actions that are available.
Facebook
Previewv1.0.1
80 actions · 1 auth method
Advertising
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Meta App with Facebook Login for Business configured. Business Verification and App Review are required for A... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/facebook/index.md for the full list. # Facebook Changelog Source: https://docs.stackone.com/connectors/facebook/changelog Release history for the Facebook connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the OAuth 2.0 documentation link with an illustrated connection guide covering creating a Meta app, registering the redirect URL, copying the App ID and App secret, and the permissions the connector requests. # Facebook Ads Source: https://docs.stackone.com/connectors/facebookads/index How to set up the Facebook Ads connector, plus the actions that are available.
Facebook Ads
Previewv1.0.1
53 actions · 2 auth methods
Advertising
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Meta App with Marketing API access and Facebook Login for Business configured. Business Verification and App... For server-to-server use without a browser OAuth flow. Generate a System User access token in Meta Business Settings > U... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/facebookads/index.md for the full list. # Facebook Ads Changelog Source: https://docs.stackone.com/connectors/facebookads/changelog Release history for the Facebook Ads connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the documentation links on both authentication methods with connection guides. The OAuth 2.0 guide covers creating a Meta app and registering the redirect URL; the illustrated System User Access Token guide covers creating a system user, giving it a role on the app, and generating the token in Meta Business Suite. # Facebook Lead Ads Source: https://docs.stackone.com/connectors/facebookleadads/index How to set up the Facebook Lead Ads connector, plus the actions that are available.
Facebook Lead Ads
Previewv1.0.1
8 actions · 2 auth methods
Advertising
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Meta App with Facebook Login for Business configured, the leads\_retrieval and pages\_manage\_ads permissions, a... For server-to-server lead sync without a browser OAuth flow. Generate a System User access token in Meta Business Settin... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/facebookleadads/index.md for the full list. # Facebook Lead Ads Changelog Source: https://docs.stackone.com/connectors/facebookleadads/changelog Release history for the Facebook Lead Ads connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the documentation links on both authentication methods with connection guides. The OAuth 2.0 guide covers creating a Meta app and registering the redirect URL; the illustrated System User Access Token guide covers creating a system user, assigning it the app and the Pages whose leads are retrieved, and generating the token in Meta Business Suite. # Factorial Source: https://docs.stackone.com/connectors/factorialhr/index How to set up the Factorial connector, plus the actions that are available.
Factorial
Previewv1.1.0
127 actions · 2 auth methods
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges in your Factorial account. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/factorialhr/index.md for the full list. # Factorial Changelog Source: https://docs.stackone.com/connectors/factorialhr/changelog Release history for the Factorial connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for 32 list actions, with incremental syncs for employees and custom field values. # Fastbill Source: https://docs.stackone.com/connectors/fastbill/index How to set up the Fastbill connector, plus the actions and events that are available.
Fastbill
v3.0.0
56 actions · 11 events · 1 auth method
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using your Fastbill email address and API key. Optionally, configure receiving Events for Fastbill into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fastbill/index.md for the full list. ## Events See https://docs.stackone.com/connectors/fastbill/index.md for the full list. # Fastbill Changelog Source: https://docs.stackone.com/connectors/fastbill/changelog Release history for the Fastbill connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `bug-fix` Removed Create Recurring Invoice, because FastBill reports a server error on every call even when the schedule is saved, so it cannot be used reliably. Also clarified that Cancel Invoice voids an issued invoice with a credit note while Delete Invoice removes drafts only, and documented paging and filters for List Recurring Invoices and List Time Entries. `fastbill_create_recurring_invoice` `fastbill_cancel_invoice`, `fastbill_delete_invoice`, `fastbill_list_recurring_invoices`, `fastbill_list_time_entries` `data-sync` Added Data Sync support for articles, contacts, customers, documents, estimates, expenses, invoices, projects, recurring invoices, revenues, templates and time entries, so these collections can be kept in sync on a schedule. Most page through FastBill's LIMIT and OFFSET parameters, and invoices also sync incrementally, pulling only records changed since the last run. Added LIMIT and OFFSET inputs to List Documents, which now requests a full page by default so its documents page correctly. `fastbill_list_articles`, `fastbill_list_contacts`, `fastbill_list_customers`, `fastbill_list_documents`, `fastbill_list_estimates`, `fastbill_list_expenses`, `fastbill_list_invoices`, `fastbill_list_projects`, `fastbill_list_recurring_invoices`, `fastbill_list_revenues`, `fastbill_list_templates`, `fastbill_list_time_entries` `breaking` `bug-fix` `description-fix` List Revenues no longer accepts CURRENCY_CODE, which Fastbill does not support for revenue entries; filter on the CURRENCY_CODE field of the returned rows instead. Update Article now requires TITLE alongside ARTICLE_ID, because Fastbill blanks an article title whenever an update omits it, so resend the current title on every update. Also fixes a 0% project VAT rate that would not save, and rejected document, invoice, revenue and recurring-schedule calls that previously looked successful. `fastbill_create_document`, `fastbill_create_estimate`, `fastbill_create_invoice`, `fastbill_create_recurring_invoice`, `fastbill_delete_estimate`, `fastbill_get_time_entry`, `fastbill_list_contacts`, `fastbill_list_customers`, `fastbill_list_estimates`, `fastbill_list_expenses`, `fastbill_list_invoices`, `fastbill_list_revenues`, `fastbill_send_invoice_email`, `fastbill_set_invoice_paid`, `fastbill_set_revenue_paid`, `fastbill_update_article`, `fastbill_update_contact`, `fastbill_update_customer`, `fastbill_update_invoice`, `fastbill_update_project` `new-actions` Added inbound webhook (events) support. StackOne now auto-provisions a Fastbill webhook on connect (covering the enabled events, via the webhook.create API service) and removes it on disconnect, routing customer, contact, invoice, and estimate events to your integration; includes a webhook events setup guide. # FastSpring Source: https://docs.stackone.com/connectors/fastspring/index How to set up the FastSpring connector, plus the actions and events that are available.
FastSpring
v1.2.1
59 actions · 42 events · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your FastSpring API credentials (username and password) for authentication. Generate these in the FastSpring app und... Optionally, configure receiving Events for FastSpring into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fastspring/index.md for the full list. ## Events See https://docs.stackone.com/connectors/fastspring/index.md for the full list. # FastSpring Changelog Source: https://docs.stackone.com/connectors/fastspring/changelog Release history for the FastSpring connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Removed data sync from List Product Prices. Each product's price list covers about 250 countries, which is more fields than synced storage can hold, so the sync could never finish. Call the action live to get prices. `fastspring_list_product_prices` `new-feature` Added native webhook events - 41 FastSpring event types (orders, chargebacks, PayPal disputes, subscriptions, co-term subscription groups, quotes, returns, payouts, fulfillment failures, mailing list entries, accounts and invoice reminders), delivered through a per-account Native Webhook URL that is pasted into Developer Tools > Webhooks. Batched deliveries are split so each event is emitted on its own. `bug-fix` Fixed create_quote/update_quote source (now an enum of MANAGER, BUYER, UNKNOWN - any other value returned a provider 502), added a full per-tier schema and the product-scoping rule to create_coupon discounts, clarified that create_session coupon takes a redemption code rather than a coupon ID, required a days/begin window on the event list actions so a missing window no longer reads as an empty event store, corrected list_orders days (it is not a lookback range - days=2 or higher excludes today, so begin should be used for recent-order windows), documented that the event endpoints only report the FIRST configured webhook, added clear error messages when update_webhook_key is given an unregistered URL and when get_subscription is given an unknown subscription id, and documented that list_quotes caps at 20 records with no way to page. `fastspring_create_coupon`, `fastspring_create_invoice`, `fastspring_create_quote`, `fastspring_create_session`, `fastspring_get_subscription`, `fastspring_list_orders`, `fastspring_list_processed_events`, `fastspring_list_quotes`, `fastspring_list_unprocessed_events`, `fastspring_update_quote`, `fastspring_update_webhook_key` `data-sync` Added DataSync support to 3 list actions (quotes, report jobs, product prices). All sync via full refresh as the provider has no updated-since filters on these endpoints. # Fathom Source: https://docs.stackone.com/connectors/fathom/index How to set up the Fathom connector, plus the actions and events that are available.
Fathom
v1.3.0
14 actions · 2 events · 1 auth method
IAM Notetaker
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using an API key generated from your Fathom account settings. Optionally, configure receiving Events for Fathom into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fathom/index.md for the full list. ## Events See https://docs.stackone.com/connectors/fathom/index.md for the full list. # Fathom Changelog Source: https://docs.stackone.com/connectors/fathom/changelog Release history for the Fathom connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Enabled scheduled data sync on six list actions — meetings, teams and team members, plus the unified users, groups and roles collections — so these can be kept in sync and read without calling Fathom on every request. Each refreshes in full on every run, because the Fathom API exposes no updated-since filter on any of these endpoints. `fathom_list_meetings`, `fathom_list_team_members`, `fathom_list_teams`, `fathom_unified_list_groups`, `fathom_unified_list_roles`, `fathom_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `fathom_unified_get_group`, `fathom_unified_get_me`, `fathom_unified_get_role`, `fathom_unified_get_user`, `fathom_unified_list_groups`, `fathom_unified_list_roles`, `fathom_unified_list_users` `new-actions` Added unified IAM actions for users, groups, roles, and credentials. `fathom_unified_get_group`, `fathom_unified_get_me`, `fathom_unified_get_role`, `fathom_unified_get_user`, `fathom_unified_list_groups`, `fathom_unified_list_roles`, `fathom_unified_list_users` `new-events` Added programmatic webhook support with newMeeting event type. Webhooks are auto-created/deleted via the Fathom API, delivering meeting transcripts, summaries, action items, and CRM matches in real-time. # Feedier Source: https://docs.stackone.com/connectors/feedier/index How to set up the Feedier connector, plus the actions that are available.
Feedier
Betav1.1.0
49 actions · 2 auth methods
Surveys
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Bearer token authentication using your Feedier API access token (recommended). HTTP Basic authentication using your Feedier account email and password. Feedier recommends the Access Token method over... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/feedier/index.md for the full list. # Feedier Changelog Source: https://docs.stackone.com/connectors/feedier/changelog Release history for the Feedier connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for feedback, reports, segments, users, teams, workflows and referentials. `feedier_list_feedback`, `feedier_list_referentials`, `feedier_list_reports`, `feedier_list_segments`, `feedier_list_teams`, `feedier_list_users`, `feedier_list_workflows` `bug-fix` `auth` Gave the Access Token and Basic Authentication methods unique identifiers to resolve an authentication configuration conflict. # Figma Source: https://docs.stackone.com/connectors/figma/index How to set up the Figma connector, plus the actions that are available.
Figma
v2.0.0
57 actions · 2 auth methods
Design IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration needed. Accepts a personal access token or an Organization/Enterprise plan access token. Optionally... Requires registering an OAuth app in the Figma Developer Portal. Some scopes are Enterprise-only. Optionally add a SCIM... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/figma/index.md for the full list. # Figma Changelog Source: https://docs.stackone.com/connectors/figma/changelog Release history for the Figma connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Migrated to authRequirements for per-auth-type scope control; gated get_activity_logs to OAuth 2.0 (not available with a Personal Access Token). `figma_auth_test`, `figma_bulk_create_dev_resources`, `figma_bulk_create_update_delete_variables`, `figma_bulk_update_dev_resources`, `figma_create_comment`, `figma_create_comment_reaction`, `figma_create_webhook`, `figma_delete_comment`, `figma_delete_comment_reaction`, `figma_delete_dev_resource`, `figma_delete_webhook`, `figma_get_activity_logs`, `figma_get_comment_reactions`, `figma_get_comments`, `figma_get_component`, `figma_get_component_set`, `figma_get_current_user`, `figma_get_file`, `figma_get_file_component_sets`, `figma_get_file_components`, `figma_get_file_metadata`, `figma_get_file_nodes`, `figma_get_file_styles`, `figma_get_file_versions`, `figma_get_image_fills`, `figma_get_library_analytics_component_actions`, `figma_get_library_analytics_component_usages`, `figma_get_library_analytics_style_actions`, `figma_get_library_analytics_style_usages`, `figma_get_library_analytics_variable_actions`, `figma_get_library_analytics_variable_usages`, `figma_get_local_variables`, `figma_get_project_files`, `figma_get_published_variables`, `figma_get_style`, `figma_get_team_component_sets`, `figma_get_team_components`, `figma_get_team_projects`, `figma_get_team_styles`, `figma_get_webhook`, `figma_get_webhook_requests`, `figma_get_webhooks`, `figma_list_configured_teams`, `figma_list_dev_resources`, `figma_render_images`, `figma_unified_get_group`, `figma_unified_get_me`, `figma_unified_get_organization`, `figma_unified_get_role`, `figma_unified_get_user`, `figma_unified_list_groups`, `figma_unified_list_organizations`, `figma_unified_list_resource_types`, `figma_unified_list_resource_users`, `figma_unified_list_roles`, `figma_unified_list_users`, `figma_update_webhook` `bug-fix` User lists now read up to 30,000 SCIM users and group lists up to 3000 groups; larger organizations get an error instead of a partial list. `figma_unified_list_groups`, `figma_unified_list_users` `bug-fix` Organization lookups now return the real error when the connection's token is invalid, expired or rate-limited, instead of failing with an unrelated error. `figma_unified_list_organizations` `data-sync` Added scheduled data sync to three unified list actions — users, organizations, and roles — so these collections can be kept in sync and read back without calling Figma on every request. Each refreshes in full on every run, since the Figma API has no updated-since filter to drive incremental sync. `figma_unified_list_organizations`, `figma_unified_list_roles`, `figma_unified_list_users` `auth` Team ID is now an optional connection field that accepts several comma-separated teams, team-scoped actions fall back to the first configured team and return a clear error when no team is known, a new list_configured_teams action lets agents discover the configured teams, and the Personal Access Token option documents Figma plan access tokens. `figma_list_configured_teams` `figma_get_team_component_sets`, `figma_get_team_components`, `figma_get_team_projects`, `figma_get_team_styles` `bug-fix` Fixed organization and role lookups returning the placeholder id "figma" instead of the real tenant id, moved the eight IAM actions from beta to preview, and documented that groups and roles do not list their members. `figma_unified_get_group`, `figma_unified_get_me`, `figma_unified_get_organization`, `figma_unified_get_role`, `figma_unified_get_user`, `figma_unified_list_groups`, `figma_unified_list_organizations`, `figma_unified_list_resource_types`, `figma_unified_list_resource_users`, `figma_unified_list_roles`, `figma_unified_list_users` `bug-fix` Fixed IAM SCIM list pagination (users, groups) — raw offset result.next replaced with fixed fan-out + virtual pagination — and promoted the REST-based IAM actions (credentials, organizations) to GA with the connector restored to GA (SCIM actions remain beta). `figma_auth_test`, `figma_unified_get_me`, `figma_unified_get_organization`, `figma_unified_list_groups`, `figma_unified_list_organizations`, `figma_unified_list_users` `new-actions` Added unified IAM actions for users, groups, roles, and resource users via the Figma SCIM API, plus organizations and credentials via the Figma REST API. SCIM-backed actions are gated to beta pending a QA account with Enterprise SCIM provisioned. # Filevine Source: https://docs.stackone.com/connectors/filevine/index How to set up the Filevine connector, plus the actions and events that are available.
Filevine
Betav1.1.1
53 actions · 15 events · 1 auth method
IAM Legal
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 client credentials with your Filevine API key and secret. Optionally, configure receiving Events for Filevine into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/filevine/index.md for the full list. ## Events See https://docs.stackone.com/connectors/filevine/index.md for the full list. # Filevine Changelog Source: https://docs.stackone.com/connectors/filevine/changelog Release history for the Filevine connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `events-guide` Added a webhook setup guide covering how Filevine event subscriptions are created and how events are delivered. `data-sync` Added DataSync v2 support to 7 list actions with page-based pagination. Incremental sync enabled for list_projects via modifiedSince filter. # Finastra Source: https://docs.stackone.com/connectors/finastra/index How to set up the Finastra connector, plus the actions that are available.
Finastra
Betav0.2.0
42 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Delegated access on behalf of a signed-in corporate user via FusionFabric.cloud OpenID Connect. Requires registering an... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/finastra/index.md for the full list. # Finastra Changelog Source: https://docs.stackone.com/connectors/finastra/changelog Release history for the Finastra connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the counterparties, beneficiaries, term deposit, transaction, pending transaction, and account balance list actions for scheduled full record syncs. `finastra_accounts_balances_by_type`, `finastra_beneficiaries_list`, `finastra_counterparties_list`, `finastra_term_deposits_list`, `finastra_transactions_list`, `finastra_transactions_pending_list` `new-actions` Initial release covering Finastra Corporate Banking Channels — accounts and balances, payment initiation, FX rates, beneficiaries, counterparties, term deposits, transactions and approvals. # Firebase Source: https://docs.stackone.com/connectors/firebase/index How to set up the Firebase connector, plus the actions that are available.
Firebase
v1.1.0
36 actions · 1 auth method
Developer Tools IAM Databases
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Owner or Editor privileges within a Google Cloud / Firebase project. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/firebase/index.md for the full list. # Firebase Changelog Source: https://docs.stackone.com/connectors/firebase/changelog Release history for the Firebase connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `bug-fix` `auth` Added Data Sync support for projects and available projects, so these collections can be synced on a schedule and read back without calling Firebase each time. Both refresh in full on every run, because the Management API accepts no updated-since filter on either endpoint. Also fixed OAuth authorization, which previously failed when connecting a Firebase account. # Fireflies.ai Source: https://docs.stackone.com/connectors/fireflies/index How to set up the Fireflies.ai connector, plus the actions and events that are available.
Fireflies.ai
v1.4.1
25 actions · 4 events · 1 auth method
Notetaker IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from your Fireflies dashboard (Integrations > Fireflies API). Optionally, configure receiving Events for Fireflies.ai into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fireflies/index.md for the full list. ## Events See https://docs.stackone.com/connectors/fireflies/index.md for the full list. # Fireflies.ai Changelog Source: https://docs.stackone.com/connectors/fireflies/changelog Release history for the Fireflies.ai connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Actions now return Fireflies' own error message with a matching status (not found, not permitted, rate limited) instead of a generic bad request. Get Analytics no longer fails on every request, and Set Transcript Privacy lists its accepted values. `fireflies_create_soundbite`, `fireflies_get_analytics`, `fireflies_get_meeting_analytics`, `fireflies_get_meeting_sentiments`, `fireflies_get_meeting_summary`, `fireflies_get_soundbite`, `fireflies_get_transcript`, `fireflies_get_user`, `fireflies_list_channels`, `fireflies_list_contacts`, `fireflies_list_soundbites`, `fireflies_list_transcripts`, `fireflies_list_users`, `fireflies_search_meetings`, `fireflies_set_transcript_privacy`, `fireflies_update_transcript_channel` `data-sync` Added periodic data sync to seven list actions - transcripts (paginated), team users, meeting contacts, and the unified user, group, organization, and role lists. Each refreshes in full on every run, since the Fireflies API exposes no updated-since filter. `fireflies_list_contacts`, `fireflies_list_transcripts`, `fireflies_list_users`, `fireflies_unified_list_groups`, `fireflies_unified_list_organizations`, `fireflies_unified_list_roles`, `fireflies_unified_list_users` `new-fields` Added downloadable media URLs - audio_url and video_url on get_transcript - and documented soundbite media downloads via get_soundbite sources. `fireflies_get_soundbite`, `fireflies_get_transcript`, `fireflies_list_soundbites` `new-events` Added webhook events and webhook setup guides. # Fivetran Source: https://docs.stackone.com/connectors/fivetran/index How to set up the Fivetran connector, plus the actions and events that are available.
Fivetran
Previewv1.3.0
172 actions · 16 events · 1 auth method
Data Integration IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a scoped API key that inherits RBAC permissions of the generating user. The API secret is shown only once at genera... Optionally, configure receiving Events for Fivetran into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fivetran/index.md for the full list. ## Events See https://docs.stackone.com/connectors/fivetran/index.md for the full list. # Fivetran Changelog Source: https://docs.stackone.com/connectors/fivetran/changelog Release history for the Fivetran connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for connections, destinations, groups, teams, users, roles, webhooks, system keys, connector SDK packages, hybrid deployment agents, log services, private links, proxy agents, connector metadata, transformations, transformation packages, transformation projects and organizations, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Fivetran API exposes no updated-since filter a sync can use. `fivetran_list_connections`, `fivetran_list_connector_metadata`, `fivetran_list_connector_sdk_packages`, `fivetran_list_destinations`, `fivetran_list_groups`, `fivetran_list_hybrid_deployment_agents`, `fivetran_list_log_services`, `fivetran_list_private_links`, `fivetran_list_proxy_agents`, `fivetran_list_roles`, `fivetran_list_system_keys`, `fivetran_list_teams`, `fivetran_list_transformation_packages`, `fivetran_list_transformation_projects`, `fivetran_list_transformations`, `fivetran_list_users`, `fivetran_list_webhooks`, `fivetran_unified_get_organization`, `fivetran_unified_list_groups`, `fivetran_unified_list_organizations`, `fivetran_unified_list_roles`, `fivetran_unified_list_users` `bug-fix` Added portal screenshots to the API key connection guide and a missing step for the confirmation dialog shown when generating a new secret, pointed the login link at the Fivetran login page, and corrected the API Key field description to say Profile name. `new-actions` Added inbound webhook event support for sync, transformation, connection, and connector lifecycle events (15 events) with automatic subscription provisioning. `fivetran_webhook_connection_failure`, `fivetran_webhook_connection_successful`, `fivetran_webhook_create_connector`, `fivetran_webhook_delete_connector`, `fivetran_webhook_edit_connector`, `fivetran_webhook_force_update_connector`, `fivetran_webhook_pause_connector`, `fivetran_webhook_resume_connector`, `fivetran_webhook_resync_connector`, `fivetran_webhook_resync_table`, `fivetran_webhook_sync_end`, `fivetran_webhook_sync_start`, `fivetran_webhook_test_event`, `fivetran_webhook_transformation_failed`, `fivetran_webhook_transformation_start`, `fivetran_webhook_transformation_succeeded` `bug-fix` Fixed add_team_user (role now required and always sent), add_group_user response envelope, and binary Connector SDK package download; documented service-specific config requirements, write-only fields, and provider limitations; sharpened action descriptions for agent callability and disambiguation. # Flatchr Source: https://docs.stackone.com/connectors/flatchr/index How to set up the Flatchr connector, plus the actions that are available.
Flatchr
Betav1.1.0
29 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Flatchr uses a static API key sent as a Bearer token. Generate it in your account under Settings > Advanced > API, where... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/flatchr/index.md for the full list. # Flatchr Changelog Source: https://docs.stackone.com/connectors/flatchr/changelog Release history for the Flatchr connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for vacancies, active vacancies, tasks, company tags and members. # Folks HR Source: https://docs.stackone.com/connectors/folks/index How to set up the Folks HR connector, plus the actions that are available.
Folks HR
Betav0.2.0
64 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Folks HR uses an OAuth 2.0 Client Credentials flow. A company administrator generates a "V2" API key (Client ID and Clie... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/folks/index.md for the full list. # Folks HR Changelog Source: https://docs.stackone.com/connectors/folks/changelog Release history for the Folks HR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for employees, absences, absence reasons, vacations, vacation types, overtimes, overtime types, departments, positions, working sites and custom fields, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Folks HR updated-since filters accept only a calendar date, which a sync cannot use. `folks_list_absence_reasons`, `folks_list_absences`, `folks_list_custom_fields`, `folks_list_departments`, `folks_list_employees`, `folks_list_overtime_types`, `folks_list_overtimes`, `folks_list_positions`, `folks_list_vacation_types`, `folks_list_vacations`, `folks_list_working_sites` `new-actions` Initial Folks HR connector — 64 actions across employees, absences, vacations, overtimes, positions, departments, working sites, custom fields, and electronic document management, with OAuth 2.0 Client Credentials authentication. # Fountain Source: https://docs.stackone.com/connectors/fountain/index How to set up the Fountain connector, plus the actions that are available.
Fountain
Betav1.1.0
62 actions · 1 auth method
ATS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API Key authentication for Fountain Hire API Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fountain/index.md for the full list. # Fountain Changelog Source: https://docs.stackone.com/connectors/fountain/changelog Release history for the Fountain connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for applicants, openings, hiring goals, workers, shifts, company attributes, locations, location groups, positions, roles, users, webhook settings, archived reasons and rejection reasons, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. Applicants, openings and hiring goals sync incrementally using Fountain's updated-since filters; the rest are full-refresh, because their endpoints expose no updated-since filter a sync can use. List Applicants gains an optional updated_at[gt] filter. # Fourth Source: https://docs.stackone.com/connectors/fourth/index How to set up the Fourth connector, plus the actions that are available.
Fourth
v2.1.1
28 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fourth/index.md for the full list. # Fourth Changelog Source: https://docs.stackone.com/connectors/fourth/changelog Release history for the Fourth connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Corrected the descriptions of the pay parts export actions, which wrongly promised shift-level pay data. Both export actions return a SuperJournal accounting export (nominal ledger codes and amounts), and List Pay Parts is now identified as the only source of shift-level pay part data. Get Pay Parts Export, Get Pay Parts Export by Employee, and Get Post Pay-Run Export are now marked preview because Fourth restricts these endpoints to selected customers and their behaviour could not be confirmed against a fully populated account. `fourth_get_pay_parts_export`, `fourth_get_pay_parts_export_by_employee`, `fourth_get_post_payrun_export`, `fourth_list_pay_parts` `data-sync` Added data sync support to ten list actions — Employees, Employments, Addresses, Passports, Country Specific Fields, Holiday Accrual, Divisions, Locations, Payment Details, and Payroll Periods — so their records can be kept in sync on a schedule. Fourth exposes no pagination and no usable change filter for unattended syncs, so each sync is a single-call full refresh. List Dependents, List Payslips, and List Employee Sources are not syncable (provider-side 502 on unbounded pulls, and no unique record identifiers respectively). `fourth_list_accrual`, `fourth_list_addresses`, `fourth_list_country_specific`, `fourth_list_divisions`, `fourth_list_employees`, `fourth_list_employments`, `fourth_list_locations`, `fourth_list_passports`, `fourth_list_payment_details`, `fourth_list_payroll_periods` `breaking` `fix` Removed Update Absence and Delete Absence. Live API verification showed those endpoints require an internal integer AbsenceID that no Fourth Employee API response ever returns (List Absences returns the separate Reference identifier, which the mutation endpoints do not accept, and the importer discards client-supplied AbsenceIDs on create, so the actions could never be exercised). Holiday records — References prefixed HO in List Absences — remain fully manageable through Create Holiday and Delete Holiday, which are keyed by employee number and date, and Create Absence now states that general absences are write-once via this API. Create Absence also dropped its ignored AbsenceID input. List Import Logs gained the verified importType value absence, giving absence submissions a checkable outcome, and now always sends its required query parameters, matching the gateway's requirement that every documented parameter be present on the wire (absent parameters return HTTP 405). List Next of Kin gained the time-range filters it actually supports and now documents that a non-empty range is required. List Absences states the one-week ceiling per call explicitly, with instructions to chunk longer periods into consecutive weekly windows. Get Pay Parts Export by Employee spells out the two-step workflow of assembling its four path parameters from List Payroll Periods and List Employees. `fourth_delete_absence`, `fourth_update_absence` `fourth_create_absence`, `fourth_list_absences`, `fourth_list_import_logs` `fix` `improvement` Corrected the absence and holiday identifier contracts based on live API verification. Absence create, update and delete now explain that Fourth never returns an AbsenceID (List Absences returns the separate Reference identifier, which the mutation endpoints do not accept, and the importer discards client-supplied AbsenceIDs on create), and that holiday records — References prefixed HO in List Absences — are managed without any ID through Create Holiday and Delete Holiday keyed by employee number and date. List Import Logs gained the verified importType value absence, giving every absence mutation a checkable outcome, and now always sends its required query parameters, matching the gateway's requirement that every documented parameter be present on the wire (absent parameters return HTTP 405). List Next of Kin gained the time-range filters it actually supports and now documents that a non-empty range is required. List Absences states the one-week ceiling per call explicitly, with instructions to chunk longer periods into consecutive weekly windows. Get Pay Parts Export by Employee spells out the two-step workflow of assembling its four path parameters from List Payroll Periods and List Employees. `fourth_create_absence`, `fourth_delete_absence`, `fourth_delete_holiday`, `fourth_get_pay_parts_export_by_employee`, `fourth_list_absences`, `fourth_list_import_logs`, `fourth_list_next_of_kin`, `fourth_update_absence` `improvement` Relative time-range inputs now reject week and year units up front with a clear message instead of failing as a provider error, since Fourth supports only days and calendar months. List actions that take only optional filters now state that the query object must always be included in the call, because omitting it entirely is rejected before the request is made. Documented the response-size and filtering limits of the list actions so callers stop hitting truncated results and gateway timeouts. List Employees now explains that its time range filters by when a record last changed rather than by hire date, and that showFormer=false and no time range should be used to look up a specific person. List Absences and List Pay Parts now explain that each call covers the whole organisation and that the date range must be kept narrow enough to complete within the gateway timeout. List Next of Kin, List Accrual and List Employments now state that Fourth offers no pagination and no per-employee filter, so results must be matched client-side. `fourth_list_absences`, `fourth_list_accrual`, `fourth_list_addresses`, `fourth_list_country_specific`, `fourth_list_dependents`, `fourth_list_employees`, `fourth_list_employments`, `fourth_list_import_logs`, `fourth_list_next_of_kin`, `fourth_list_passports`, `fourth_list_pay_parts`, `fourth_list_payment_details`, `fourth_list_payroll_periods`, `fourth_list_payslips`, `fourth_update_employee` `bugfix` Fixed List Employees and List Next of Kin returning HTTP 400 (absent optional query parameters were sent as the literal string "null"). Corrected create/update/delete success messages for absences, holidays, and multiple employments to reflect that Fourth processes these asynchronously, so a SubmissionID does not confirm the change was applied. Clarified that relative time-range inputs accept only days and calendar months (weeks and years are not supported by the provider). `fourth_create_absence`, `fourth_create_holiday`, `fourth_create_multiple_employment`, `fourth_delete_absence`, `fourth_delete_holiday`, `fourth_list_absences`, `fourth_list_addresses`, `fourth_list_country_specific`, `fourth_list_dependents`, `fourth_list_employees`, `fourth_list_employments`, `fourth_list_import_logs`, `fourth_list_next_of_kin`, `fourth_list_passports`, `fourth_list_payment_details`, `fourth_list_payslips`, `fourth_update_absence` `guide-changes` Renamed the authentication method to Basic Auth and updated the connection guide with instructions for obtaining credentials. # FreeAgent Source: https://docs.stackone.com/connectors/freeagent/index How to set up the FreeAgent connector, plus the actions that are available.
FreeAgent
Previewv1.1.1
105 actions · 1 auth method
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an app at the FreeAgent Developer Dashboard. Access tokens expire after 1 hour and are refreshed au... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/freeagent/index.md for the full list. # FreeAgent Changelog Source: https://docs.stackone.com/connectors/freeagent/changelog Release history for the FreeAgent connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide-changes` Updated the OAuth connection guide to note that connecting requires an active FreeAgent account (free trial or subscription), separate from the developer account. `data-sync` Added Data Sync support for contacts, invoices, bills, credit notes, estimates, expenses, tasks, timeslips, projects, recurring invoices, bank accounts, and users. # FreshBooks Source: https://docs.stackone.com/connectors/freshbooks/index How to set up the FreshBooks connector, plus the actions that are available.
FreshBooks
Previewv2.1.1
89 actions · 1 auth method
Accounting IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your FreshBooks account to access your accounting data. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/freshbooks/index.md for the full list. # FreshBooks Changelog Source: https://docs.stackone.com/connectors/freshbooks/changelog Release history for the FreshBooks connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed connecting failing when a custom scope list leaves out the profile scope, which is now always requested. `freshbooks_archive_client`, `freshbooks_archive_credit`, `freshbooks_archive_estimate`, `freshbooks_archive_expense`, `freshbooks_archive_invoice`, `freshbooks_archive_item`, `freshbooks_archive_payment`, `freshbooks_create_account`, `freshbooks_create_client`, `freshbooks_create_credit`, `freshbooks_create_estimate`, `freshbooks_create_expense`, `freshbooks_create_invoice`, `freshbooks_create_item`, `freshbooks_create_journal_entry`, `freshbooks_create_other_income`, `freshbooks_create_payment`, `freshbooks_create_project`, `freshbooks_create_service`, `freshbooks_create_service_rate`, `freshbooks_create_tax`, `freshbooks_create_time_entry`, `freshbooks_delete_other_income`, `freshbooks_delete_project`, `freshbooks_delete_tax`, `freshbooks_delete_time_entry`, `freshbooks_get_account`, `freshbooks_get_account_aging_report`, `freshbooks_get_balance_sheet_report`, `freshbooks_get_cash_flow_report`, `freshbooks_get_client`, `freshbooks_get_credit`, `freshbooks_get_current_user`, `freshbooks_get_estimate`, `freshbooks_get_expense`, `freshbooks_get_expense_category`, `freshbooks_get_expense_details_report`, `freshbooks_get_general_ledger_report`, `freshbooks_get_invoice`, `freshbooks_get_item`, `freshbooks_get_other_income`, `freshbooks_get_payment`, `freshbooks_get_project`, `freshbooks_get_service`, `freshbooks_get_service_rate`, `freshbooks_get_staff`, `freshbooks_get_tax`, `freshbooks_get_team_member`, `freshbooks_get_time_entry`, `freshbooks_list_accounts`, `freshbooks_list_bill_payments`, `freshbooks_list_bills`, `freshbooks_list_clients`, `freshbooks_list_credits`, `freshbooks_list_estimates`, `freshbooks_list_expense_categories`, `freshbooks_list_expenses`, `freshbooks_list_invoices`, `freshbooks_list_items`, `freshbooks_list_journal_entries`, `freshbooks_list_journal_entries_by_account`, `freshbooks_list_other_income`, `freshbooks_list_payments`, `freshbooks_list_projects`, `freshbooks_list_services`, `freshbooks_list_staff`, `freshbooks_list_taxes`, `freshbooks_list_team_members`, `freshbooks_list_time_entries`, `freshbooks_unified_get_me`, `freshbooks_unified_get_organization`, `freshbooks_unified_get_role`, `freshbooks_unified_get_user`, `freshbooks_unified_list_organizations`, `freshbooks_unified_list_roles`, `freshbooks_unified_list_users`, `freshbooks_update_client`, `freshbooks_update_credit`, `freshbooks_update_estimate`, `freshbooks_update_expense`, `freshbooks_update_invoice`, `freshbooks_update_item`, `freshbooks_update_journal_entry`, `freshbooks_update_other_income`, `freshbooks_update_payment`, `freshbooks_update_project`, `freshbooks_update_service_rate`, `freshbooks_update_tax`, `freshbooks_update_time_entry` `data-sync` Added Data Sync support for clients, invoices, estimates, expenses, expense categories, items, taxes, staff, payments, credits, other income, bills, bill payments, chart of accounts, projects, services, time entries, team members, and the unified users, organizations and roles, so these collections can be kept in sync on a schedule. Most page through FreshBooks' page and per_page parameters; the chart of accounts and the unified organization and role lists are returned in full by the API in a single call. Each sync is a full refresh, because FreshBooks ignores an updated-since filter on these endpoints. `freshbooks_list_accounts`, `freshbooks_list_bill_payments`, `freshbooks_list_bills`, `freshbooks_list_clients`, `freshbooks_list_credits`, `freshbooks_list_estimates`, `freshbooks_list_expense_categories`, `freshbooks_list_expenses`, `freshbooks_list_invoices`, `freshbooks_list_items`, `freshbooks_list_other_income`, `freshbooks_list_payments`, `freshbooks_list_projects`, `freshbooks_list_services`, `freshbooks_list_staff`, `freshbooks_list_taxes`, `freshbooks_list_team_members`, `freshbooks_list_time_entries`, `freshbooks_unified_list_organizations`, `freshbooks_unified_list_roles`, `freshbooks_unified_list_users` `breaking` `bug-fix` Breaking - list filters and include options now take a single value instead of a list; they previously failed or were silently ignored. Also corrects the fields required when creating accounts, credits, estimates, journal entries and time entries, documents the client company sizes FreshBooks accepts, and fixes project and time entry updates that previously failed. `freshbooks_create_account`, `freshbooks_create_credit`, `freshbooks_create_estimate`, `freshbooks_create_journal_entry`, `freshbooks_create_time_entry`, `freshbooks_get_client`, `freshbooks_get_estimate`, `freshbooks_get_expense`, `freshbooks_get_expense_category`, `freshbooks_get_invoice`, `freshbooks_get_payment`, `freshbooks_list_bills`, `freshbooks_list_clients`, `freshbooks_list_estimates`, `freshbooks_list_expense_categories`, `freshbooks_list_expenses`, `freshbooks_list_invoices`, `freshbooks_list_payments`, `freshbooks_list_staff`, `freshbooks_list_taxes`, `freshbooks_list_team_members`, `freshbooks_update_client`, `freshbooks_update_journal_entry`, `freshbooks_update_project`, `freshbooks_update_time_entry` `auth` `guide` Fixed the OAuth redirect URI so account connections complete successfully, and rebuilt the OAuth 2.0 setup guide with step-by-step screenshots and the exact scopes to grant. `freshbooks_archive_client`, `freshbooks_archive_credit`, `freshbooks_archive_estimate`, `freshbooks_archive_expense`, `freshbooks_archive_invoice`, `freshbooks_archive_item`, `freshbooks_archive_payment`, `freshbooks_create_account`, `freshbooks_create_client`, `freshbooks_create_credit`, `freshbooks_create_estimate`, `freshbooks_create_expense`, `freshbooks_create_invoice`, `freshbooks_create_item`, `freshbooks_create_journal_entry`, `freshbooks_create_other_income`, `freshbooks_create_payment`, `freshbooks_create_project`, `freshbooks_create_service`, `freshbooks_create_service_rate`, `freshbooks_create_tax`, `freshbooks_create_time_entry`, `freshbooks_delete_other_income`, `freshbooks_delete_project`, `freshbooks_delete_tax`, `freshbooks_delete_time_entry`, `freshbooks_get_account`, `freshbooks_get_account_aging_report`, `freshbooks_get_balance_sheet_report`, `freshbooks_get_cash_flow_report`, `freshbooks_get_client`, `freshbooks_get_credit`, `freshbooks_get_current_user`, `freshbooks_get_estimate`, `freshbooks_get_expense`, `freshbooks_get_expense_category`, `freshbooks_get_expense_details_report`, `freshbooks_get_general_ledger_report`, `freshbooks_get_invoice`, `freshbooks_get_item`, `freshbooks_get_other_income`, `freshbooks_get_payment`, `freshbooks_get_project`, `freshbooks_get_service`, `freshbooks_get_service_rate`, `freshbooks_get_staff`, `freshbooks_get_tax`, `freshbooks_get_team_member`, `freshbooks_get_time_entry`, `freshbooks_list_accounts`, `freshbooks_list_bill_payments`, `freshbooks_list_bills`, `freshbooks_list_clients`, `freshbooks_list_credits`, `freshbooks_list_estimates`, `freshbooks_list_expense_categories`, `freshbooks_list_expenses`, `freshbooks_list_invoices`, `freshbooks_list_items`, `freshbooks_list_journal_entries`, `freshbooks_list_journal_entries_by_account`, `freshbooks_list_other_income`, `freshbooks_list_payments`, `freshbooks_list_projects`, `freshbooks_list_services`, `freshbooks_list_staff`, `freshbooks_list_taxes`, `freshbooks_list_team_members`, `freshbooks_list_time_entries`, `freshbooks_unified_get_me`, `freshbooks_unified_get_organization`, `freshbooks_unified_get_role`, `freshbooks_unified_get_user`, `freshbooks_unified_list_organizations`, `freshbooks_unified_list_roles`, `freshbooks_unified_list_users`, `freshbooks_update_client`, `freshbooks_update_credit`, `freshbooks_update_estimate`, `freshbooks_update_expense`, `freshbooks_update_invoice`, `freshbooks_update_item`, `freshbooks_update_journal_entry`, `freshbooks_update_other_income`, `freshbooks_update_payment`, `freshbooks_update_project`, `freshbooks_update_service_rate`, `freshbooks_update_tax`, `freshbooks_update_time_entry` `bug-fix` Standardized action category capitalization for more consistent portal filters. `freshbooks_unified_get_me`, `freshbooks_unified_get_organization`, `freshbooks_unified_get_role`, `freshbooks_unified_get_user`, `freshbooks_unified_list_organizations`, `freshbooks_unified_list_roles`, `freshbooks_unified_list_users` `new-actions` Added unified IAM actions (users, roles, organizations, credentials) mapping FreshBooks team members, business memberships, and the synthesized role catalog to the StackOne IAM unified schema. Also updates how every action declares its required permissions, with no change in behavior for existing integrations. List Unified Users paginates through the full business's team members. # Freshchat Source: https://docs.stackone.com/connectors/freshchat/index How to set up the Freshchat connector, plus the actions that are available.
Freshchat
Previewv0.1.1
14 actions · 1 auth method
Customer Support IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses the account's Freshchat API key, which an account admin generates. The key reads the whole account, so no per-user... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/freshchat/index.md for the full list. # Freshchat Changelog Source: https://docs.stackone.com/connectors/freshchat/changelog Release history for the Freshchat connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Native actions are now also listed under Customer Support, and the API key guide now matches Freshchat's menu paths, key labels and key replacement steps. `freshchat_get_account_configuration`, `freshchat_get_agent`, `freshchat_list_agents`, `freshchat_list_groups`, `freshchat_list_roles` `new-connector` Initial Freshchat connector for reviewing who has access to a Freshchat account, covering agents, their roles and groups, and the account itself, including unified IAM users, roles, groups, organizations and connection details. # Freshdesk Source: https://docs.stackone.com/connectors/freshdesk/index How to set up the Freshdesk connector, plus the actions and events that are available.
Freshdesk
v1.2.0
73 actions · 2 events · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges within Freshdesk. Optionally, configure receiving Events for Freshdesk into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/freshdesk/index.md for the full list. ## Events See https://docs.stackone.com/connectors/freshdesk/index.md for the full list. # Freshdesk Changelog Source: https://docs.stackone.com/connectors/freshdesk/changelog Release history for the Freshdesk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added DataSync support to 13 list actions covering tickets, contacts, companies, agents, groups, roles, products, solution categories, time entries, canned response folders and field definitions. Tickets, contacts and companies sync incrementally using the updated_since filter. Removed the per_page and page inputs from list_canned_response_folders because Freshdesk ignores them on that endpoint. `freshdesk_list_agents`, `freshdesk_list_canned_response_folders`, `freshdesk_list_companies`, `freshdesk_list_company_fields`, `freshdesk_list_contact_fields`, `freshdesk_list_contacts`, `freshdesk_list_groups`, `freshdesk_list_products`, `freshdesk_list_roles`, `freshdesk_list_solution_categories`, `freshdesk_list_ticket_fields`, `freshdesk_list_tickets`, `freshdesk_list_time_entries` `bug-fix` Standardized action category capitalization for more consistent portal filters. `new-events` `native-webhooks` `guide-changes` Added native webhook mapping and setup guide for ticket creation and updates. # Freshsales Source: https://docs.stackone.com/connectors/freshsales/index How to set up the Freshsales connector, plus the actions and events that are available.
Freshsales
Previewv1.4.0
125 actions · 1 event · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. The API key inherits the permissions of the user who created it. Optionally, configure receiving Events for Freshsales into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/freshsales/index.md for the full list. ## Events See https://docs.stackone.com/connectors/freshsales/index.md for the full list. # Freshsales Changelog Source: https://docs.stackone.com/connectors/freshsales/changelog Release history for the Freshsales connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for sales activities, marketing lists, contact, deal and account views, contact, deal, account and sales activity fields, owners, territories, deal stages, deal pipelines, currencies, deal reasons, deal types, lead sources, industry types, business types, campaigns, deal payment statuses, deal products, contact statuses, lifecycle stages, sales activity types, sales activity outcomes, sales activity entity types, designations, and unified users and organizations, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Freshsales API exposes no updated-since filter a sync can use. `freshsales_list_business_types`, `freshsales_list_campaigns`, `freshsales_list_contact_fields`, `freshsales_list_contact_statuses`, `freshsales_list_contact_views`, `freshsales_list_currencies`, `freshsales_list_deal_fields`, `freshsales_list_deal_payment_statuses`, `freshsales_list_deal_pipelines`, `freshsales_list_deal_products`, `freshsales_list_deal_reasons`, `freshsales_list_deal_stages`, `freshsales_list_deal_types`, `freshsales_list_deal_views`, `freshsales_list_designations`, `freshsales_list_industry_types`, `freshsales_list_lead_sources`, `freshsales_list_lifecycle_stages`, `freshsales_list_lists`, `freshsales_list_owners`, `freshsales_list_sales_account_fields`, `freshsales_list_sales_account_views`, `freshsales_list_sales_activities`, `freshsales_list_sales_activity_entity_types`, `freshsales_list_sales_activity_fields`, `freshsales_list_sales_activity_outcomes`, `freshsales_list_sales_activity_types`, `freshsales_list_territories`, `freshsales_unified_list_organizations`, `freshsales_unified_list_users` `bug-fix` Fixed user lists failing when the full Freshsales address is entered as the domain, and added user names, emails and status. `freshsales_add_contacts_to_list`, `freshsales_bulk_assign_contact_owner`, `freshsales_bulk_assign_document_owner`, `freshsales_bulk_assign_product_owner`, `freshsales_bulk_delete_documents`, `freshsales_bulk_delete_products`, `freshsales_bulk_destroy_contacts`, `freshsales_bulk_destroy_deals`, `freshsales_bulk_destroy_sales_accounts`, `freshsales_bulk_restore_documents`, `freshsales_bulk_restore_products`, `freshsales_bulk_update_documents`, `freshsales_bulk_update_products`, `freshsales_bulk_upsert_contacts`, `freshsales_bulk_upsert_deals`, `freshsales_bulk_upsert_sales_accounts`, `freshsales_clone_contact`, `freshsales_clone_deal`, `freshsales_clone_sales_account`, `freshsales_create_appointment`, `freshsales_create_contact`, `freshsales_create_deal`, `freshsales_create_document`, `freshsales_create_file`, `freshsales_create_link`, `freshsales_create_list`, `freshsales_create_note`, `freshsales_create_product`, `freshsales_create_sales_account`, `freshsales_create_sales_activity`, `freshsales_create_task`, `freshsales_delete_appointment`, `freshsales_delete_contact`, `freshsales_delete_deal`, `freshsales_delete_document`, `freshsales_delete_note`, `freshsales_delete_product`, `freshsales_delete_sales_account`, `freshsales_delete_sales_activity`, `freshsales_delete_task`, `freshsales_filtered_search_contact`, `freshsales_forget_contact`, `freshsales_forget_deal`, `freshsales_forget_document`, `freshsales_forget_sales_account`, `freshsales_get_appointment`, `freshsales_get_contact`, `freshsales_get_deal`, `freshsales_get_document`, `freshsales_get_document_related_products`, `freshsales_get_job_status`, `freshsales_get_product`, `freshsales_get_sales_account`, `freshsales_get_sales_activity`, `freshsales_get_task`, `freshsales_list_activity_type_outcomes`, `freshsales_list_appointments`, `freshsales_list_business_types`, `freshsales_list_campaigns`, `freshsales_list_contact_activities`, `freshsales_list_contact_fields`, `freshsales_list_contact_files`, `freshsales_list_contact_statuses`, `freshsales_list_contact_views`, `freshsales_list_contacts`, `freshsales_list_contacts_in_list`, `freshsales_list_currencies`, `freshsales_list_deal_fields`, `freshsales_list_deal_files`, `freshsales_list_deal_payment_statuses`, `freshsales_list_deal_pipelines`, `freshsales_list_deal_products`, `freshsales_list_deal_reasons`, `freshsales_list_deal_stages`, `freshsales_list_deal_types`, `freshsales_list_deal_views`, `freshsales_list_deals`, `freshsales_list_designations`, `freshsales_list_industry_types`, `freshsales_list_lead_sources`, `freshsales_list_lifecycle_stages`, `freshsales_list_lists`, `freshsales_list_owners`, `freshsales_list_pipeline_deal_stages`, `freshsales_list_sales_account_fields`, `freshsales_list_sales_account_files`, `freshsales_list_sales_account_views`, `freshsales_list_sales_accounts`, `freshsales_list_sales_activities`, `freshsales_list_sales_activity_entity_types`, `freshsales_list_sales_activity_fields`, `freshsales_list_sales_activity_outcomes`, `freshsales_list_sales_activity_types`, `freshsales_list_tasks`, `freshsales_list_territories`, `freshsales_lookup`, `freshsales_manage_contact_team_members`, `freshsales_manage_deal_team_members`, `freshsales_manage_product_prices`, `freshsales_manage_sales_account_team_members`, `freshsales_move_contacts_between_lists`, `freshsales_remove_contacts_from_list`, `freshsales_restore_document`, `freshsales_restore_product`, `freshsales_search`, `freshsales_unified_get_me`, `freshsales_unified_get_organization`, `freshsales_unified_get_user`, `freshsales_unified_list_organizations`, `freshsales_unified_list_users`, `freshsales_update_appointment`, `freshsales_update_contact`, `freshsales_update_deal`, `freshsales_update_deal_products`, `freshsales_update_document`, `freshsales_update_document_products`, `freshsales_update_list`, `freshsales_update_note`, `freshsales_update_product`, `freshsales_update_sales_account`, `freshsales_update_sales_activity`, `freshsales_update_task`, `freshsales_upsert_contact`, `freshsales_upsert_deal`, `freshsales_upsert_sales_account` `bug-fix` Fixed unified user lists failing with an error and user lookups not finding the user. `freshsales_unified_get_user`, `freshsales_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `freshsales_unified_get_me`, `freshsales_unified_get_organization`, `freshsales_unified_get_user`, `freshsales_unified_list_organizations`, `freshsales_unified_list_users` `new-actions` Added unified IAM actions for users, credentials, and organizations. `freshsales_unified_get_me`, `freshsales_unified_get_organization`, `freshsales_unified_get_user`, `freshsales_unified_list_organizations`, `freshsales_unified_list_users` `new-actions` Freshsales: Native Webhook Mapping. Configure a Freshworks CRM Workflow "Trigger Webhook" action to post to the connection's Native Webhook URL and StackOne maps the event to your integration. # Freshservice Source: https://docs.stackone.com/connectors/freshservice/index How to set up the Freshservice connector, plus the actions and events that are available.
Freshservice
Previewv1.3.0
101 actions · 1 event · 1 auth method
ITSM Ticketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Agent access to your Freshservice account is required to retrieve an API key. Optionally, configure receiving Events for Freshservice into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/freshservice/index.md for the full list. ## Events See https://docs.stackone.com/connectors/freshservice/index.md for the full list. # Freshservice Changelog Source: https://docs.stackone.com/connectors/freshservice/changelog Release history for the Freshservice connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added scheduled data sync to nineteen collection actions — tickets, changes, problems, releases, agents, requesters, groups, departments, locations, assets, vendors, contracts and contract types, solution categories and folders, and the unified users, groups, organizations and roles — so these collections can be kept in sync and searched without calling Freshservice on every request. Most page through results automatically; the unified organizations and roles are returned in full by a single request. Tickets and changes sync incrementally using Freshservice's updated-since filter; the rest sync by full refresh, because their endpoints offer no last-updated filter. `freshservice_list_agents`, `freshservice_list_assets`, `freshservice_list_changes`, `freshservice_list_contract_types`, `freshservice_list_contracts`, `freshservice_list_departments`, `freshservice_list_groups`, `freshservice_list_locations`, `freshservice_list_problems`, `freshservice_list_releases`, `freshservice_list_requesters`, `freshservice_list_solution_categories`, `freshservice_list_solution_folders`, `freshservice_list_tickets`, `freshservice_list_vendors`, `freshservice_unified_list_groups`, `freshservice_unified_list_organizations`, `freshservice_unified_list_roles`, `freshservice_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `freshservice_unified_get_group`, `freshservice_unified_get_me`, `freshservice_unified_get_organization`, `freshservice_unified_get_role`, `freshservice_unified_get_user`, `freshservice_unified_list_groups`, `freshservice_unified_list_organizations`, `freshservice_unified_list_roles`, `freshservice_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, and credentials. `freshservice_unified_get_group`, `freshservice_unified_get_me`, `freshservice_unified_get_organization`, `freshservice_unified_get_role`, `freshservice_unified_get_user`, `freshservice_unified_list_groups`, `freshservice_unified_list_organizations`, `freshservice_unified_list_roles`, `freshservice_unified_list_users` `new-actions` Freshservice: Native Webhook Mapping. Configure a Freshservice Workflow Automator "Trigger Webhook" action to post to the connection's Native Webhook URL and StackOne maps the event to your integration. # Front Source: https://docs.stackone.com/connectors/front/index How to set up the Front connector, plus the actions and events that are available.
Front
v1.4.0
66 actions · 20 events · 1 auth method
Customer Support Ticketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Front API token with appropriate permissions to access the Core API. Optionally, configure receiving Events for Front into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/front/index.md for the full list. ## Events See https://docs.stackone.com/connectors/front/index.md for the full list. # Front Changelog Source: https://docs.stackone.com/connectors/front/changelog Release history for the Front connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to eight core list actions — accounts, contacts, conversations, tags, events, channels, inboxes, and teammates — so these collections can be kept in sync and read back without calling Front on every request. Each refreshes in full on every run, since Front's updated-since filter cannot drive incremental sync. `front_list_accounts`, `front_list_channels`, `front_list_contacts`, `front_list_conversations`, `front_list_events`, `front_list_inboxes`, `front_list_tags`, `front_list_teammates` `bug-fix` Standardized action category capitalization for more consistent portal filters. `front_auth_test`, `front_unified_get_group`, `front_unified_get_me`, `front_unified_get_organization`, `front_unified_get_role`, `front_unified_get_user`, `front_unified_list_groups`, `front_unified_list_organizations`, `front_unified_list_resource_types`, `front_unified_list_resource_users`, `front_unified_list_roles`, `front_unified_list_users` `description-fixes` Clarified the create_draft and send_message descriptions so agents know create_draft opens a draft-state conversation that can be updated, tagged, or commented on before sending, and that send_message sends an outbound customer-facing message through a channel configured for outbound sending (a channel not set up to compose outbound messages rejects the send). `front_create_draft`, `front_send_message` `new-actions` `auth` Added unified IAM actions covering users, roles, groups, organizations, credentials, and resource users (teammates, teams, and company-wide admin status), and tightened permission checks so each action only runs with the scopes it actually needs. `front_auth_test`, `front_unified_get_group`, `front_unified_get_me`, `front_unified_get_organization`, `front_unified_get_role`, `front_unified_get_user`, `front_unified_list_groups`, `front_unified_list_organizations`, `front_unified_list_resource_types`, `front_unified_list_resource_users`, `front_unified_list_roles`, `front_unified_list_users` `front_add_contact_handle`, `front_add_contact_note`, `front_add_conversation_comment`, `front_add_conversation_followers`, `front_add_conversation_tag`, `front_create_account`, `front_create_channel`, `front_create_child_tag`, `front_create_contact`, `front_create_draft`, `front_create_inbox`, `front_create_tag`, `front_delete_account`, `front_delete_contact`, `front_delete_conversation`, `front_delete_tag`, `front_get_account`, `front_get_channel`, `front_get_contact`, `front_get_conversation`, `front_get_event`, `front_get_inbox`, `front_get_message`, `front_get_tag`, `front_get_teammate`, `front_list_account_contacts`, `front_list_accounts`, `front_list_channels`, `front_list_child_tags`, `front_list_contact_conversations`, `front_list_contacts`, `front_list_conversation_comments`, `front_list_conversation_events`, `front_list_conversation_followers`, `front_list_conversation_messages`, `front_list_conversations`, `front_list_events`, `front_list_inbox_channels`, `front_list_inbox_conversations`, `front_list_inboxes`, `front_list_tagged_conversations`, `front_list_tags`, `front_list_teammates`, `front_remove_conversation_tag`, `front_search_conversations`, `front_send_message`, `front_update_account`, `front_update_channel`, `front_update_contact`, `front_update_conversation`, `front_update_conversation_assignee`, `front_update_tag`, `front_update_teammate` `webhook` `new-actions` Added native webhook event support. You can now receive real-time events for conversations, messages, comments, tags, and links (20 event types) by configuring a Front Rule that forwards to the StackOne webhook URL. `new-actions` `bug-fix` `downstream-change` Added create_channel action plus optional send_message/update_conversation/update_channel fields and highlight/sort_by enums; removed provider-unsupported inputs (send_message tag_ids now set via options.tags, list_conversations/list_contacts q filters, list_channels limit/page_token); corrected action descriptions. # Gem ATS Source: https://docs.stackone.com/connectors/gem/index How to set up the Gem ATS connector, plus the actions that are available.
Gem ATS
Betav1.1.0
34 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using an API key generated from the Gem admin dashboard. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gem/index.md for the full list. # Gem ATS Changelog Source: https://docs.stackone.com/connectors/gem/changelog Release history for the Gem ATS connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for applications, candidates, jobs, job stages, job posts, offers, openings, locations, scorecards, scheduled interviews, and users, with incremental updates on every collection except locations. # GitBook Source: https://docs.stackone.com/connectors/gitbook/index How to set up the GitBook connector, plus the actions and events that are available.
GitBook
v1.5.0
61 actions · 3 events · 1 auth method
Knowledge Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using your GitBook Personal Access Token. You can generate tokens from the Developer tools section in your GitBo... Optionally, configure receiving Events for GitBook into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gitbook/index.md for the full list. ## Events See https://docs.stackone.com/connectors/gitbook/index.md for the full list. # GitBook Changelog Source: https://docs.stackone.com/connectors/gitbook/changelog Release history for the GitBook connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for list_authenticated_user_organizations, unified_list_organizations, and unified_list_users actions (full refresh, cursor pagination). `gitbook_list_authenticated_user_organizations`, `gitbook_unified_list_organizations`, `gitbook_unified_list_users` `new-feature` User list, lookup, update, and removal no longer require the organization filter when the account belongs to a single organization — it is resolved automatically. Accounts in several organizations still pass the filter to choose one. `gitbook_unified_delete_user`, `gitbook_unified_get_user`, `gitbook_unified_list_users`, `gitbook_unified_update_user` `new-actions` `guide` Added event support for 3 event types (space content updated, site view, page feedback) with setup guide and screenshots. `gitbook_list_change_requests_in_space` `guide` `improvements` Improved connection guide with correct portal labels and screenshots. Enhanced action descriptions with dependency references for required input fields. # GitHub Source: https://docs.stackone.com/connectors/github/index How to set up the GitHub connector, plus the actions and events that are available.
GitHub
v3.6.1
123 actions · 25 events · 4 auth methods
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). GitHub Apps provide the most secure and feature-rich authentication method:... For GitHub Enterprise Server 3.19 or later. Requires registering a GitHub App on your own instance; user tokens last 8 h... Create a Personal Access Token from your GitHub account settings For GitHub Enterprise Server 3.19 or later. No app registration required; the token inherits the permissions of the user... Optionally, configure receiving Events for GitHub into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/github/index.md for the full list. ## Events See https://docs.stackone.com/connectors/github/index.md for the full list. # GitHub Changelog Source: https://docs.stackone.com/connectors/github/changelog Release history for the GitHub connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `webhook` Fixed updating a repository webhook so adding and removing events in the same request now applies both changes, and clarified that webhook config is replaced in full rather than merged. `github_list_webhooks`, `github_ping_webhook`, `github_update_webhook` `new-feature` Added GitHub Enterprise Server support and new reads for compliance checks, such as branch protection, pull request reviews and audit logs. `github_get_branch_protection`, `github_get_branch_rules`, `github_get_combined_status_for_ref`, `github_get_organization_ruleset`, `github_get_repository_ruleset`, `github_list_check_runs_for_ref`, `github_list_enterprise_audit_log`, `github_list_organization_audit_log`, `github_list_organization_branch_protection`, `github_list_organization_members_with_two_factor`, `github_list_organization_rulesets`, `github_list_outside_collaborators`, `github_list_pull_request_reviews`, `github_list_pull_requests_for_commit`, `github_list_repository_rulesets`, `github_list_repository_teams`, `github_list_team_members`, `github_list_team_repositories`, `github_search_pull_requests_with_reviews` `github_add_collaborator`, `github_add_team_member`, `github_add_team_repository`, `github_cancel_workflow_run`, `github_check_organization_membership`, `github_create_deployment`, `github_create_deployment_status`, `github_create_issue`, `github_create_issue_comment`, `github_create_or_update_file`, `github_create_organization_repository`, `github_create_pull_request`, `github_create_pull_request_review`, `github_create_pull_request_review_comment`, `github_create_ref`, `github_create_release`, `github_create_team`, `github_create_user_repository`, `github_create_webhook`, `github_create_workflow_dispatch`, `github_delete_deployment`, `github_delete_file`, `github_delete_ref`, `github_delete_release`, `github_delete_repository`, `github_delete_team`, `github_delete_webhook`, `github_download_artifact`, `github_fork_repository`, `github_get_authenticated_user`, `github_get_branch`, `github_get_commit`, `github_get_issue`, `github_get_latest_release`, `github_get_organization`, `github_get_organization_membership`, `github_get_pull_request`, `github_get_ref`, `github_get_repository`, `github_get_repository_content`, `github_get_team`, `github_get_user`, `github_get_webhook`, `github_get_workflow_run`, `github_invite_organization_member`, `github_list_artifacts`, `github_list_authenticated_user_organization_memberships`, `github_list_authenticated_user_organizations`, `github_list_authenticated_user_repositories`, `github_list_branches`, `github_list_code_scanning_alerts`, `github_list_collaborators`, `github_list_commits`, `github_list_dependabot_alerts`, `github_list_deployments`, `github_list_forks`, `github_list_issue_comments`, `github_list_issues`, `github_list_matching_refs`, `github_list_organization_members`, `github_list_organization_repositories`, `github_list_pull_requests`, `github_list_releases`, `github_list_secret_scanning_alerts`, `github_list_teams`, `github_list_user_organizations`, `github_list_user_repositories`, `github_list_users`, `github_list_webhooks`, `github_list_workflow_jobs`, `github_list_workflow_runs`, `github_merge_pull_request`, `github_ping_webhook`, `github_re_run_workflow`, `github_remove_collaborator`, `github_remove_organization_member`, `github_remove_team_member`, `github_search_code`, `github_search_issues`, `github_search_repositories`, `github_star_repository`, `github_unified_get_group`, `github_unified_get_me`, `github_unified_get_organization`, `github_unified_get_role`, `github_unified_get_user`, `github_unified_list_groups`, `github_unified_list_organizations`, `github_unified_list_roles`, `github_unified_list_users`, `github_unstar_repository`, `github_update_code_scanning_alert`, `github_update_dependabot_alert`, `github_update_issue`, `github_update_organization`, `github_update_pull_request`, `github_update_ref`, `github_update_release`, `github_update_repository`, `github_update_secret_scanning_alert`, `github_update_team`, `github_update_user`, `github_update_webhook`, `github_upload_release_asset` `new-feature` Personal access token connections can set an optional Enterprise slug to list a GitHub Enterprise Cloud enterprise's users across its organizations, with two-factor status for users who are not managed by an identity provider. `github_unified_get_user`, `github_unified_list_groups`, `github_unified_list_organizations`, `github_unified_list_users` `new-feature` Connections can set an optional Organization that IAM actions use instead of every organization the token can see. Without it, team lists read up to 100 extra pages of teams, user lists add pending invitations after the members, and get user answers only for members of the connection's organizations. `github_unified_get_user`, `github_unified_list_groups`, `github_unified_list_organizations`, `github_unified_list_users` `documentation` Moved 13 actions from preview to beta. `webhook` `new-actions` Added webhook events covering pushes, pull requests, issues, releases, deployments, workflow runs and security alerts, plus actions to create, update and manage repository webhooks. `github_create_webhook`, `github_delete_webhook`, `github_get_webhook`, `github_list_webhooks`, `github_ping_webhook`, `github_update_webhook` `github_cancel_workflow_run`, `github_create_workflow_dispatch`, `github_invite_organization_member`, `github_list_code_scanning_alerts`, `github_list_collaborators`, `github_list_dependabot_alerts`, `github_list_secret_scanning_alerts`, `github_re_run_workflow`, `github_remove_organization_member`, `github_update_code_scanning_alert`, `github_update_dependabot_alert`, `github_update_secret_scanning_alert`, `github_upload_release_asset` `bug-fix` Fixed create_pull_request_review_comment by removing subject_type parameter that caused 422 errors on line-level comments. `github_create_pull_request_review_comment` `data-sync` Added DataSync support to list_authenticated_user_repositories with page-based pagination and incremental sync via since filter. `github_add_team_repository`, `github_check_organization_membership`, `github_create_pull_request_review_comment`, `github_delete_ref`, `github_delete_release`, `github_delete_repository`, `github_delete_team`, `github_list_authenticated_user_repositories`, `github_remove_collaborator`, `github_remove_team_member`, `github_search_issues`, `github_star_repository`, `github_unstar_repository` `bug-fix` Fixed member, organization, and team lists being truncated on large accounts. They now page through the full result set instead of stopping after a fixed number of pages. Also fixed team lists crashing when an organization blocks token access, instead of skipping that organization as intended. `github_unified_get_group`, `github_unified_get_me`, `github_unified_get_organization`, `github_unified_get_role`, `github_unified_get_user`, `github_unified_list_groups`, `github_unified_list_organizations`, `github_unified_list_roles`, `github_unified_list_users` `bug-fix` `improvement` Removed legacy requiredScopes comments. Added missing filter/sort params across list actions. Fixed update_issue labels type (object to array). Updated descriptions with enum values, provider limitations, and error behaviour documentation. Marked upload_release_asset as preview (requires uploads.github.com host). `github_add_collaborator`, `github_add_team_member`, `github_add_team_repository`, `github_cancel_workflow_run`, `github_check_organization_membership`, `github_create_deployment`, `github_create_deployment_status`, `github_create_issue`, `github_create_issue_comment`, `github_create_or_update_file`, `github_create_organization_repository`, `github_create_pull_request`, `github_create_pull_request_review`, `github_create_pull_request_review_comment`, `github_create_ref`, `github_create_release`, `github_create_team`, `github_create_user_repository`, `github_create_workflow_dispatch`, `github_delete_deployment`, `github_delete_file`, `github_delete_ref`, `github_delete_release`, `github_delete_repository`, `github_delete_team`, `github_download_artifact`, `github_fork_repository`, `github_get_authenticated_user`, `github_get_branch`, `github_get_commit`, `github_get_issue`, `github_get_latest_release`, `github_get_organization`, `github_get_organization_membership`, `github_get_pull_request`, `github_get_ref`, `github_get_repository`, `github_get_repository_content`, `github_get_team`, `github_get_user`, `github_get_workflow_run`, `github_invite_organization_member`, `github_list_artifacts`, `github_list_authenticated_user_organization_memberships`, `github_list_authenticated_user_organizations`, `github_list_authenticated_user_repositories`, `github_list_branches`, `github_list_code_scanning_alerts`, `github_list_collaborators`, `github_list_commits`, `github_list_dependabot_alerts`, `github_list_deployments`, `github_list_forks`, `github_list_issue_comments`, `github_list_issues`, `github_list_matching_refs`, `github_list_organization_members`, `github_list_organization_repositories`, `github_list_pull_requests`, `github_list_releases`, `github_list_secret_scanning_alerts`, `github_list_teams`, `github_list_user_organizations`, `github_list_user_repositories`, `github_list_users`, `github_list_workflow_jobs`, `github_list_workflow_runs`, `github_merge_pull_request`, `github_re_run_workflow`, `github_remove_collaborator`, `github_remove_organization_member`, `github_remove_team_member`, `github_search_code`, `github_search_issues`, `github_search_repositories`, `github_star_repository`, `github_unified_get_group`, `github_unified_get_me`, `github_unified_get_organization`, `github_unified_get_role`, `github_unified_get_user`, `github_unified_list_groups`, `github_unified_list_organizations`, `github_unified_list_roles`, `github_unified_list_users`, `github_unstar_repository`, `github_update_code_scanning_alert`, `github_update_dependabot_alert`, `github_update_issue`, `github_update_organization`, `github_update_pull_request`, `github_update_ref`, `github_update_release`, `github_update_repository`, `github_update_secret_scanning_alert`, `github_update_team`, `github_update_user`, `github_upload_release_asset` `bug-fix` Fixed IAM list pagination past page 1 on unified_list_users, unified_list_groups, and unified_list_organizations — the raw page-number result.next overrode StackOne's virtual-pagination cursor and could not survive a round-trip, causing 400 Invalid cursor past the first page. Replaced with a fixed page fan-out that lets virtual pagination own the cursor end-to-end. Re-sourced unified_list_groups from GET /user/teams (which returns only the connected user's own teams) to a per-organization fan-out over GET /orgs/{org}/teams, so the action returns every team visible across the connection's organizations rather than just the caller's memberships. `github_unified_list_groups`, `github_unified_list_organizations`, `github_unified_list_users` `bug-fix` Fixed unified_get_me returning an empty body, broken pagination termination on the users/groups/organizations IAM lists, and unified_list_groups requiring an organization filter the platform never delivers. # GitLab Source: https://docs.stackone.com/connectors/gitlab/index How to set up the GitLab connector, plus the actions and events that are available.
GitLab
Previewv1.5.0
156 actions · 49 events · 3 auth methods
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create a GitLab OAuth application to connect: • Navigate to User Settings > Applications (or Admin Area > Applications f... For GitLab Self-Managed and GitLab Dedicated. Requires registering an OAuth application on your own GitLab instance; acc... Works on GitLab.com, GitLab Self-Managed and GitLab Dedicated. No app registration required; the token inherits the perm... Optionally, configure receiving Events for GitLab into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gitlab/index.md for the full list. ## Events See https://docs.stackone.com/connectors/gitlab/index.md for the full list. # GitLab Changelog Source: https://docs.stackone.com/connectors/gitlab/changelog Release history for the GitLab connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added reads for compliance checks, such as branch protection and merge request approvals, and unified users now include subgroup and project members. `gitlab_get_group_merge_request_approval_setting`, `gitlab_get_merge_request_approval_state`, `gitlab_get_merge_request_approvals`, `gitlab_get_metadata`, `gitlab_get_project_approval_configuration`, `gitlab_get_protected_branch`, `gitlab_list_all_group_members`, `gitlab_list_all_project_members`, `gitlab_list_billable_group_members`, `gitlab_list_billable_member_memberships`, `gitlab_list_enterprise_users`, `gitlab_list_group_branch_rules`, `gitlab_list_group_descendant_members`, `gitlab_list_group_merge_requests`, `gitlab_list_group_merge_requests_with_approvals`, `gitlab_list_group_project_members`, `gitlab_list_merge_requests_for_commit`, `gitlab_list_pending_group_members`, `gitlab_list_project_approval_rules`, `gitlab_list_protected_branches` `gitlab_add_group_member`, `gitlab_add_project_deploy_key`, `gitlab_add_project_member`, `gitlab_approve_merge_request`, `gitlab_archive_project`, `gitlab_cancel_merge_when_pipeline_succeeds`, `gitlab_cancel_pipeline`, `gitlab_cherry_pick_commit`, `gitlab_compare_branches`, `gitlab_create_branch`, `gitlab_create_commit`, `gitlab_create_environment`, `gitlab_create_file`, `gitlab_create_group`, `gitlab_create_issue`, `gitlab_create_issue_note`, `gitlab_create_merge_request`, `gitlab_create_merge_request_note`, `gitlab_create_pipeline`, `gitlab_create_project`, `gitlab_create_project_label`, `gitlab_create_project_milestone`, `gitlab_create_project_variable`, `gitlab_create_release`, `gitlab_create_snippet`, `gitlab_create_tag`, `gitlab_create_user`, `gitlab_delete_branch`, `gitlab_delete_file`, `gitlab_delete_group`, `gitlab_delete_issue`, `gitlab_delete_pipeline`, `gitlab_delete_project`, `gitlab_delete_project_deploy_key`, `gitlab_delete_project_label`, `gitlab_delete_project_milestone`, `gitlab_delete_project_variable`, `gitlab_delete_release`, `gitlab_delete_snippet`, `gitlab_delete_tag`, `gitlab_delete_user`, `gitlab_enable_project_deploy_key`, `gitlab_fork_project`, `gitlab_get_branch`, `gitlab_get_commit`, `gitlab_get_commit_diff`, `gitlab_get_current_user`, `gitlab_get_current_user_status`, `gitlab_get_environment`, `gitlab_get_file`, `gitlab_get_group`, `gitlab_get_issue`, `gitlab_get_job`, `gitlab_get_job_log`, `gitlab_get_merge_request`, `gitlab_get_merge_request_participants`, `gitlab_get_namespace`, `gitlab_get_pipeline`, `gitlab_get_pipeline_variables`, `gitlab_get_project`, `gitlab_get_project_label`, `gitlab_get_project_milestone`, `gitlab_get_project_variable`, `gitlab_get_release`, `gitlab_get_repository_contributors`, `gitlab_get_snippet`, `gitlab_get_user`, `gitlab_get_user_status`, `gitlab_list_branches`, `gitlab_list_commits`, `gitlab_list_environments`, `gitlab_list_group_members`, `gitlab_list_group_projects`, `gitlab_list_group_subgroups`, `gitlab_list_groups`, `gitlab_list_issue_notes`, `gitlab_list_issue_participants`, `gitlab_list_merge_request_commits`, `gitlab_list_merge_request_diffs`, `gitlab_list_merge_request_notes`, `gitlab_list_namespaces`, `gitlab_list_pipeline_jobs`, `gitlab_list_pipelines`, `gitlab_list_project_deploy_keys`, `gitlab_list_project_issues`, `gitlab_list_project_labels`, `gitlab_list_project_members`, `gitlab_list_project_merge_requests`, `gitlab_list_project_milestones`, `gitlab_list_project_variables`, `gitlab_list_projects`, `gitlab_list_related_merge_requests`, `gitlab_list_releases`, `gitlab_list_repository_tree`, `gitlab_list_snippets`, `gitlab_list_tags`, `gitlab_list_users`, `gitlab_merge_merge_request`, `gitlab_move_issue`, `gitlab_protect_branch`, `gitlab_rebase_merge_request`, `gitlab_remove_group_member`, `gitlab_remove_project_member`, `gitlab_retry_job`, `gitlab_retry_pipeline`, `gitlab_revert_commit`, `gitlab_search_globally`, `gitlab_search_in_group`, `gitlab_search_in_project`, `gitlab_stop_environment`, `gitlab_unarchive_project`, `gitlab_unified_get_group`, `gitlab_unified_get_me`, `gitlab_unified_get_organization`, `gitlab_unified_get_role`, `gitlab_unified_get_user`, `gitlab_unified_list_groups`, `gitlab_unified_list_organizations`, `gitlab_unified_list_resource_types`, `gitlab_unified_list_resource_users`, `gitlab_unified_list_roles`, `gitlab_unified_list_users`, `gitlab_unprotect_branch`, `gitlab_update_environment`, `gitlab_update_file`, `gitlab_update_group`, `gitlab_update_issue`, `gitlab_update_merge_request`, `gitlab_update_project`, `gitlab_update_project_label`, `gitlab_update_project_member`, `gitlab_update_project_milestone`, `gitlab_update_project_variable`, `gitlab_update_release`, `gitlab_update_snippet`, `gitlab_update_user` `new-feature` Added support for GitLab Self-Managed and GitLab Dedicated, with a new personal access token option and an OAuth option that uses an app registered on your own instance. `gitlab_add_group_member`, `gitlab_add_project_deploy_key`, `gitlab_add_project_member`, `gitlab_approve_merge_request`, `gitlab_archive_project`, `gitlab_cancel_merge_when_pipeline_succeeds`, `gitlab_cancel_pipeline`, `gitlab_cherry_pick_commit`, `gitlab_compare_branches`, `gitlab_create_branch`, `gitlab_create_commit`, `gitlab_create_environment`, `gitlab_create_file`, `gitlab_create_group`, `gitlab_create_issue`, `gitlab_create_issue_note`, `gitlab_create_merge_request`, `gitlab_create_merge_request_note`, `gitlab_create_pipeline`, `gitlab_create_project`, `gitlab_create_project_label`, `gitlab_create_project_milestone`, `gitlab_create_project_variable`, `gitlab_create_release`, `gitlab_create_snippet`, `gitlab_create_tag`, `gitlab_create_user`, `gitlab_delete_branch`, `gitlab_delete_file`, `gitlab_delete_group`, `gitlab_delete_issue`, `gitlab_delete_pipeline`, `gitlab_delete_project`, `gitlab_delete_project_deploy_key`, `gitlab_delete_project_label`, `gitlab_delete_project_milestone`, `gitlab_delete_project_variable`, `gitlab_delete_release`, `gitlab_delete_snippet`, `gitlab_delete_tag`, `gitlab_delete_user`, `gitlab_enable_project_deploy_key`, `gitlab_fork_project`, `gitlab_get_branch`, `gitlab_get_commit`, `gitlab_get_commit_diff`, `gitlab_get_current_user`, `gitlab_get_current_user_status`, `gitlab_get_environment`, `gitlab_get_file`, `gitlab_get_group`, `gitlab_get_issue`, `gitlab_get_job`, `gitlab_get_job_log`, `gitlab_get_merge_request`, `gitlab_get_merge_request_participants`, `gitlab_get_namespace`, `gitlab_get_pipeline`, `gitlab_get_pipeline_variables`, `gitlab_get_project`, `gitlab_get_project_label`, `gitlab_get_project_milestone`, `gitlab_get_project_variable`, `gitlab_get_release`, `gitlab_get_repository_contributors`, `gitlab_get_snippet`, `gitlab_get_user`, `gitlab_get_user_status`, `gitlab_list_branches`, `gitlab_list_commits`, `gitlab_list_environments`, `gitlab_list_group_members`, `gitlab_list_group_projects`, `gitlab_list_group_subgroups`, `gitlab_list_groups`, `gitlab_list_issue_notes`, `gitlab_list_issue_participants`, `gitlab_list_merge_request_commits`, `gitlab_list_merge_request_diffs`, `gitlab_list_merge_request_notes`, `gitlab_list_namespaces`, `gitlab_list_pipeline_jobs`, `gitlab_list_pipelines`, `gitlab_list_project_deploy_keys`, `gitlab_list_project_issues`, `gitlab_list_project_labels`, `gitlab_list_project_members`, `gitlab_list_project_merge_requests`, `gitlab_list_project_milestones`, `gitlab_list_project_variables`, `gitlab_list_projects`, `gitlab_list_related_merge_requests`, `gitlab_list_releases`, `gitlab_list_repository_tree`, `gitlab_list_snippets`, `gitlab_list_tags`, `gitlab_list_users`, `gitlab_merge_merge_request`, `gitlab_move_issue`, `gitlab_protect_branch`, `gitlab_rebase_merge_request`, `gitlab_remove_group_member`, `gitlab_remove_project_member`, `gitlab_retry_job`, `gitlab_retry_pipeline`, `gitlab_revert_commit`, `gitlab_search_globally`, `gitlab_search_in_group`, `gitlab_search_in_project`, `gitlab_stop_environment`, `gitlab_unarchive_project`, `gitlab_unified_get_group`, `gitlab_unified_get_me`, `gitlab_unified_get_organization`, `gitlab_unified_get_role`, `gitlab_unified_get_user`, `gitlab_unified_list_groups`, `gitlab_unified_list_organizations`, `gitlab_unified_list_resource_types`, `gitlab_unified_list_resource_users`, `gitlab_unified_list_roles`, `gitlab_unified_list_users`, `gitlab_unprotect_branch`, `gitlab_update_environment`, `gitlab_update_file`, `gitlab_update_group`, `gitlab_update_issue`, `gitlab_update_merge_request`, `gitlab_update_project`, `gitlab_update_project_label`, `gitlab_update_project_member`, `gitlab_update_project_milestone`, `gitlab_update_project_variable`, `gitlab_update_release`, `gitlab_update_snippet`, `gitlab_update_user` `bug-fix` List users now also returns the group's pending email invitations with status pending after its members, and members awaiting approval show status pending instead of enabled. `gitlab_unified_get_user`, `gitlab_unified_list_users` `bug-fix` List users now returns your GitLab group's members instead of GitLab.com users at large, and get user only returns members of that group. `gitlab_unified_get_user`, `gitlab_unified_list_users` `new-feature` Added 48 GitLab webhook events for pushes, tags, issues, work items, merge requests, comments, emoji reactions, pipelines, jobs, deployments, feature flags, releases, milestones, wiki pages, access tokens and group activity, with a setup guide for adding the StackOne webhook URL to a GitLab project. `bug-fix` Fixed unified group and project member lists failing with an error. `gitlab_unified_list_resource_users` `improvement` `data-sync` Added DataSync support to 9 list actions (projects, groups, namespaces, users, snippets, and the unified IAM users, groups, organizations, and roles lists), with incremental sync on projects via the updated_after filter. list_projects now auto-applies order_by=updated_at when filtering by updated_after/updated_before, which GitLab requires for those filters to take effect. `gitlab_list_groups`, `gitlab_list_namespaces`, `gitlab_list_projects`, `gitlab_list_snippets`, `gitlab_list_users`, `gitlab_unified_list_groups`, `gitlab_unified_list_organizations`, `gitlab_unified_list_roles`, `gitlab_unified_list_users` `bug-fix` Fixed IAM list pagination on unified_list_users, unified_list_groups, unified_list_organizations, and unified_list_resource_users — replaced the raw provider page number forwarded as the StackOne cursor (which caused a 400 Invalid Cursor Format past page 1) with a fixed page fan-out plus StackOne virtual pagination. # Gladly Source: https://docs.stackone.com/connectors/gladly/index How to set up the Gladly connector, plus the actions that are available.
Gladly
Betav1.1.0
65 actions · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require the API User permission in Gladly. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gladly/index.md for the full list. # Gladly Changelog Source: https://docs.stackone.com/connectors/gladly/changelog Release history for the Gladly connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for agents, audiences, business hours, topics, inboxes, teams and answers, so their records can be periodically pulled into StackOne and kept up to date. All syncs are full-refresh, because the Gladly API exposes no updated-since filter a sync can use. # Glean Source: https://docs.stackone.com/connectors/glean/index How to set up the Glean connector, plus the actions that are available.
Glean
Previewv0.1.1
87 actions · 2 auth methods
Knowledge Management AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Glean-issued API token created in the Admin Console under Platform then Client API Token Settings, with the scope... Requires an OAuth client registered on your Glean instance, created either by an admin in the Admin Console or through d... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/glean/index.md for the full list. # Glean Changelog Source: https://docs.stackone.com/connectors/glean/changelog Release history for the Glean connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide-changes` `description-fix` Fixed the Instance Name field and connection guides to point to About Glean in the Admin Console instead of asking users to infer the value from their backend host URL. `new-connector` Initial build of the Glean connector covering the full Client API surface (search, chat, agents, collections, answers, pins, shortcuts, announcements, documents, entities, verification, governance, tools, activity) plus experimental Platform API skill management, with API key and OAuth 2.0 authentication. # Globalization Partners Source: https://docs.stackone.com/connectors/globalizationpartners/index How to set up the Globalization Partners connector, plus the actions that are available.
Globalization Partners
Previewv2.1.1
24 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Integration requires a valid Client ID and Client Secret issued by Globalization Partners. Early Adopter access is requi... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/globalizationpartners/index.md for the full list. # Globalization Partners Changelog Source: https://docs.stackone.com/connectors/globalizationpartners/changelog Release history for the Globalization Partners connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified the time off allowance and employment list descriptions so they name the fields returned and where employee and employment IDs come from. `globalizationpartners_get_time_off_allowance`, `globalizationpartners_list_employments` `new-feature` `bug-fix` Added data sync support for contractors, contractor contracts, employees, jobs and time off allowances, and corrected action descriptions to match the fields each action returns. `globalizationpartners_fetch_contract_amendments`, `globalizationpartners_get_contract`, `globalizationpartners_get_contractor_contract`, `globalizationpartners_get_current_payroll`, `globalizationpartners_get_employee`, `globalizationpartners_get_employment`, `globalizationpartners_get_employment_compensation`, `globalizationpartners_get_payroll_history`, `globalizationpartners_list_contractor_contracts`, `globalizationpartners_list_contractors`, `globalizationpartners_list_employees`, `globalizationpartners_list_jobs`, `globalizationpartners_list_time_off_allowances` `bug-fix` Clarified how to look up a contractor's contracts via contractorId, and marked several list actions as preview. `globalizationpartners_get_contractor`, `globalizationpartners_get_payroll_history`, `globalizationpartners_list_contractors`, `globalizationpartners_list_employees`, `globalizationpartners_list_employments`, `globalizationpartners_list_jobs`, `globalizationpartners_list_time_off_allowances` `breaking` `bug-fix` Temporarily removed the contract and invoice PDF download actions while a file-download platform issue is resolved, and clarified change request submission constraints. `globalizationpartners_download_contract`, `globalizationpartners_download_invoice` `globalizationpartners_submit_change_request` `bug-fix` Fixed contract and invoice PDF downloads to stream correct binary content, and clarified change request and contractor contract action descriptions. `globalizationpartners_download_contract`, `globalizationpartners_download_invoice`, `globalizationpartners_get_contractor_contract`, `globalizationpartners_list_contractor_contracts`, `globalizationpartners_submit_change_request` `bug-fix` Standardized action category capitalization for more consistent portal filters. `globalizationpartners_get_change_request`, `globalizationpartners_list_change_requests`, `globalizationpartners_submit_change_request` `improvement` `bug-fix` Rebuilt the connection guide from the live G-P Developer Portal with step-by-step screenshots and corrected setup steps. `improvement` `bug-fix` Added employment change request support: List Change Requests, Get Change Request, and Submit Change Request (the connector's first write action, covering job-title and salary changes). Corrected the List Employees `status` filter to accept the provider's actual values (New, Onboarding, Active, Terminating, Inactive, Withdrawn, OnLeave) as a validated multi-select enum instead of the previously documented, incorrect NEW/ACTIVE/TERMINATED values. Renamed the `list_contract_amendments` action to `fetch_contract_amendments` to match the provider's official operation name. # Gmail Source: https://docs.stackone.com/connectors/gmail/index How to set up the Gmail connector, plus the actions that are available.
Gmail
v1.1.0
42 actions · 1 auth method
Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gmail/index.md for the full list. # Gmail Changelog Source: https://docs.stackone.com/connectors/gmail/changelog Release history for the Gmail connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Enabled scheduled Data Sync on seven list actions covering messages, threads, drafts, labels, filters, forwarding addresses and send-as aliases, so these collections can be searched without calling Gmail on every request. All seven refresh in full on each run, because Gmail exposes no updated-since filter on these endpoints. # Go1 Source: https://docs.stackone.com/connectors/go1/index How to set up the Go1 connector, plus the actions and events that are available.
Go1
Previewv2.2.1
70 actions · 14 events · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges in Go1. Optionally, configure receiving Events for Go1 into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/go1/index.md for the full list. ## Events See https://docs.stackone.com/connectors/go1/index.md for the full list. # Go1 Changelog Source: https://docs.stackone.com/connectors/go1/changelog Release history for the Go1 connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified which ids, dates and filter values Go1 accepts on learning object, enrollment, group and SCIM actions, and invalid values are now rejected before the request is sent. `go1_add_group_members`, `go1_create_restriction`, `go1_create_user`, `go1_get_learning_object`, `go1_list_enrollments`, `go1_list_learning_objects`, `go1_remove_group_members_bulk`, `go1_scim_create_user`, `go1_scim_replace_user`, `go1_update_learning_object`, `go1_update_restriction` `new-actions` `bug-fix` Added a get current user action, write actions now return explicit success confirmations, and SCIM, learning object, enrollment and webhook inputs now match what Go1 accepts. `go1_get_current_user` `go1_create_restriction`, `go1_create_user_login`, `go1_create_webhook`, `go1_delete_enrollment`, `go1_delete_group`, `go1_delete_group_assignment`, `go1_delete_learning_object`, `go1_get_learning_object`, `go1_list_learning_objects`, `go1_remove_group_member`, `go1_remove_group_members_bulk`, `go1_scim_create_group`, `go1_scim_deactivate_user`, `go1_scim_delete_group`, `go1_scim_get_group`, `go1_scim_get_schema`, `go1_scim_list_users`, `go1_scim_replace_group`, `go1_scim_replace_user`, `go1_scim_search_users`, `go1_scim_update_group`, `go1_scim_update_user`, `go1_set_learning_object_data`, `go1_update_enrollment`, `go1_update_learning_object`, `go1_update_webhook` `description-fix` Create plan, update plan and update plan entitlements are now in beta. Corrected the list groups description, which no longer supports filtering. `go1_create_plan`, `go1_list_groups`, `go1_update_plan`, `go1_update_plan_entitlements` `webhook` Added webhook events for enrollments (created, completed, deleted) and for content and library changes (added, updated, removed, decommissioned, library sync requests). The Go1 webhook is created automatically on connect and set to inactive on disconnect. `breaking` Removed the mine filter from list groups because it does not narrow results to the caller's groups. Use list user groups to find the groups a user belongs to. Create plan, update plan and update plan entitlements are now in preview. `go1_list_groups` `bug-fix` Fixed data sync for groups, learning objects and enrollments, which failed because the default page size exceeded the Go1 limit of 50. Also typed the link settings on the set learning object data action so invalid values are caught before the request, and corrected the list groups mine filter description to reflect its actual behaviour. Restriction create and update now require both category and provider lists, since an update replaces the stored configuration in full. `go1_create_restriction`, `go1_list_enrollments`, `go1_list_groups`, `go1_list_learning_objects`, `go1_list_restrictions`, `go1_set_learning_object_data`, `go1_update_restriction` `bug-fix` `new-actions` Fixed certificate and SCORM downloads to return valid files instead of corrupted data, and enabled setting link and module content on learning objects plus richer SCIM group and user updates. Also corrected required fields and include filters on the portal, learning object, enrollment, and user actions. `go1_create_enrollment`, `go1_create_learning_object`, `go1_create_portal`, `go1_download_certificate`, `go1_download_learning_object_scorm`, `go1_get_user`, `go1_list_groups`, `go1_scim_update_group`, `go1_scim_update_user`, `go1_set_learning_object_data` `new-feature` `data-sync` `guide` `auth` Added DataSync support to five list actions (users, enrollments, learning objects, groups, and restrictions) — enrollments syncs incrementally, the rest by full refresh. Also refreshed the OAuth 2.0 setup guide with myGo1 retirement and portal navigation notes and removed the unused Company Domain field. `go1_list_enrollments`, `go1_list_groups`, `go1_list_learning_objects`, `go1_list_restrictions`, `go1_list_users` `guide` `auth` Rebuilt the OAuth 2.0 connection guides with live portal screenshots and added per-action scope requirements for every action. # GoCardless Source: https://docs.stackone.com/connectors/gocardless/index How to set up the GoCardless connector, plus the actions and events that are available.
GoCardless
v2.0.0
66 actions · 34 events · 2 auth methods
Payments
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating a GoCardless Partner app. Issues permanent access tokens with no expiry or refresh. No app registration required. Token inherits the permissions of the user who created it. Optionally, configure receiving Events for GoCardless into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gocardless/index.md for the full list. ## Events See https://docs.stackone.com/connectors/gocardless/index.md for the full list. # GoCardless Changelog Source: https://docs.stackone.com/connectors/gocardless/changelog Release history for the GoCardless connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` `bug-fix` Migrated to per-auth-type authRequirements. Every action declares the read_only or read_write scope it needs for OAuth 2.0 and API Key, and the creditor bank account actions and update_creditor are now API Key only, since GoCardless always blocks those endpoints for partner (OAuth) apps. Creditor bank account descriptions now match GoCardless - new accounts become the default payout account unless set_as_default_payout_account is false, disabled accounts can be re-enabled by re-creating them, and per-country local bank detail formats are documented. `gocardless_cancel_billing_request`, `gocardless_cancel_instalment_schedule`, `gocardless_cancel_mandate`, `gocardless_cancel_payment`, `gocardless_cancel_subscription`, `gocardless_collect_bank_account_billing_request`, `gocardless_collect_customer_details_billing_request`, `gocardless_confirm_payer_details_billing_request`, `gocardless_create_billing_request`, `gocardless_create_billing_request_flow`, `gocardless_create_creditor_bank_account`, `gocardless_create_customer`, `gocardless_create_customer_bank_account`, `gocardless_create_instalment_schedule_with_dates`, `gocardless_create_instalment_schedule_with_schedule`, `gocardless_create_mandate`, `gocardless_create_payment`, `gocardless_create_refund`, `gocardless_create_subscription`, `gocardless_delete_customer`, `gocardless_disable_creditor_bank_account`, `gocardless_disable_customer_bank_account`, `gocardless_fallback_billing_request`, `gocardless_fulfil_billing_request`, `gocardless_get_billing_request`, `gocardless_get_creditor`, `gocardless_get_creditor_bank_account`, `gocardless_get_customer`, `gocardless_get_customer_bank_account`, `gocardless_get_event`, `gocardless_get_instalment_schedule`, `gocardless_get_mandate`, `gocardless_get_payment`, `gocardless_get_payout`, `gocardless_get_refund`, `gocardless_get_subscription`, `gocardless_get_tax_rate`, `gocardless_list_billing_requests`, `gocardless_list_creditor_bank_accounts`, `gocardless_list_creditors`, `gocardless_list_customer_bank_accounts`, `gocardless_list_customers`, `gocardless_list_events`, `gocardless_list_instalment_schedules`, `gocardless_list_mandates`, `gocardless_list_payments`, `gocardless_list_payout_items`, `gocardless_list_payouts`, `gocardless_list_refunds`, `gocardless_list_subscriptions`, `gocardless_list_tax_rates`, `gocardless_notify_billing_request_customer`, `gocardless_pause_subscription`, `gocardless_reinstate_mandate`, `gocardless_resume_subscription`, `gocardless_retry_payment`, `gocardless_run_scenario_simulator`, `gocardless_update_creditor`, `gocardless_update_customer`, `gocardless_update_customer_bank_account`, `gocardless_update_instalment_schedule`, `gocardless_update_mandate`, `gocardless_update_payment`, `gocardless_update_payout`, `gocardless_update_refund`, `gocardless_update_subscription` `new-events` Added webhook events for 33 GoCardless events across payments, mandates, subscriptions, instalment schedules, billing requests, refunds, and payouts, with a setup guide for adding the StackOne webhook URL in the GoCardless dashboard. Batched GoCardless deliveries are split so every event in a request is delivered. `data-sync` Added periodic data sync to thirteen list actions - customers, billing requests, creditors, creditor and customer bank accounts, events, instalment schedules, mandates, payments, payouts, refunds, subscriptions, and tax rates. Events sync incrementally via the created_at filter; all other collections refresh in full on every run, since the GoCardless API exposes no updated-since filter. # GoEthena Source: https://docs.stackone.com/connectors/goethena/index How to set up the GoEthena connector, plus the actions that are available.
GoEthena
Betav1.0.0
11 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). HTTP Basic Authentication using a username and API key provisioned by your Ethena sales representative. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/goethena/index.md for the full list. # Gong Source: https://docs.stackone.com/connectors/gong/index How to set up the Gong connector, plus the actions and events that are available.
Gong
v2.1.0
41 actions · 1 event · 2 auth methods
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for server-side integrations with a single Gong account. Uses Access Key and Access Key Secret pair. Requires creating an OAuth integration in Gong Admin Center. Supports granular scopes. Optionally, configure receiving Events for Gong into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gong/index.md for the full list. ## Events See https://docs.stackone.com/connectors/gong/index.md for the full list. # Gong Changelog Source: https://docs.stackone.com/connectors/gong/changelog Release history for the Gong connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added DataSync support to 10 list actions (calls, transcripts, users, workspaces, call outcomes, scorecards, trackers, and unified IAM users/roles/groups), including incremental sync for calls and transcripts. `gong_get_call_transcript`, `gong_get_scorecards`, `gong_list_call_outcomes`, `gong_list_calls`, `gong_list_scorecards`, `gong_list_trackers`, `gong_list_users`, `gong_list_workspaces`, `gong_unified_list_groups`, `gong_unified_list_roles`, `gong_unified_list_users` `auth` `breaking-change` Migrated all actions from the deprecated requiredScopes field to authRequirements for per-auth-type scope control. `gong_add_call`, `gong_add_call_media`, `gong_create_meeting`, `gong_delete_crm_integration`, `gong_delete_meeting`, `gong_get_activity_stats_aggregate`, `gong_get_activity_stats_by_period`, `gong_get_activity_stats_daily`, `gong_get_call`, `gong_get_call_transcript`, `gong_get_crm_entities`, `gong_get_crm_integration`, `gong_get_crm_request_status`, `gong_get_interaction_stats`, `gong_get_library_folder_content`, `gong_get_meeting_integration_status`, `gong_get_scorecards`, `gong_get_user`, `gong_get_user_settings_history`, `gong_list_call_outcomes`, `gong_list_calls`, `gong_list_crm_schema_fields`, `gong_list_library_folders`, `gong_list_scorecards`, `gong_list_tasks`, `gong_list_trackers`, `gong_list_users`, `gong_list_workspaces`, `gong_register_crm_integration`, `gong_search_calls`, `gong_search_users`, `gong_unified_get_group`, `gong_unified_get_me`, `gong_unified_get_role`, `gong_unified_get_user`, `gong_unified_list_groups`, `gong_unified_list_roles`, `gong_unified_list_users`, `gong_update_meeting`, `gong_update_task`, `gong_upload_crm_schema` `bug-fix` Fixed group and role lookups returning empty results instead of not-found errors. `gong_unified_get_group`, `gong_unified_get_role` `new-actions` Added inbound webhook (events) support. Configure a Gong Automation Rule to fire a webhook at the connection's Native Webhook URL and StackOne routes Gong call events to your integration. `bug-fix` Fixed IAM roles and groups — unified_list_roles and unified_get_role no longer send an empty workspaceId to Gong, and unified_get_group and unified_get_role now return a record instead of failing. # Google Ads Source: https://docs.stackone.com/connectors/googleads/index How to set up the Google Ads connector, plus the actions that are available.
Google Ads
Betav1.0.0
52 actions · 1 auth method
Advertising
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an OAuth app in Google Cloud Console with the Google Ads API enabled, plus a developer token from a Google Ads... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googleads/index.md for the full list. # Google Analytics Source: https://docs.stackone.com/connectors/googleanalytics/index How to set up the Google Analytics connector, plus the actions that are available.
Google Analytics
v1.1.0
33 actions · 1 auth method
Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googleanalytics/index.md for the full list. # Google Analytics Changelog Source: https://docs.stackone.com/connectors/googleanalytics/changelog Release history for the Google Analytics connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for accounts and account summaries, so these collections can be synced on a schedule and read back without calling Google Analytics each time. Both refresh in full on every run, because the Admin API accepts no updated-since filter on either endpoint. # Google BigQuery Source: https://docs.stackone.com/connectors/googlebigquery/index How to set up the Google BigQuery connector, plus the actions that are available.
Google BigQuery
v2.1.2
41 actions · 1 auth method
Databases Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 to access and manage Google BigQuery datasets, tables, jobs, and routines. Requires a Google Clo... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlebigquery/index.md for the full list. # Google BigQuery Changelog Source: https://docs.stackone.com/connectors/googlebigquery/changelog Release history for the Google BigQuery connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Corrected the formatting of the refresh-token note in the connection guide warning. `guide` Connection guide and setup screen now explain when Google may invalidate your refresh token and how to avoid the 7-day expiry by publishing your OAuth app. `data-sync` Added DataSync support for list_projects with cursor pagination for periodic full-refresh syncing. `googlebigquery_list_projects` `auth` Documented Google Cloud session control in the OAuth 2.0 connection guide and support description — the cause of periodic refresh token expired errors on Google Workspace domains that enforce re-authentication for Google Cloud scopes. `bug-fix` Added friendlyName warning to all datasetId path params and strengthened create_routine ordering guidance to prevent dataset-not-found errors. `googlebigquery_create_routine`, `googlebigquery_create_row_access_policy`, `googlebigquery_create_table`, `googlebigquery_delete_dataset`, `googlebigquery_delete_model`, `googlebigquery_delete_routine`, `googlebigquery_delete_table`, `googlebigquery_get_dataset`, `googlebigquery_get_model`, `googlebigquery_get_routine`, `googlebigquery_get_routine_iam_policy`, `googlebigquery_get_table`, `googlebigquery_get_table_iam_policy`, `googlebigquery_insert_table_data`, `googlebigquery_list_models`, `googlebigquery_list_routines`, `googlebigquery_list_row_access_policies`, `googlebigquery_list_table_data`, `googlebigquery_list_tables`, `googlebigquery_patch_dataset`, `googlebigquery_patch_model`, `googlebigquery_patch_table`, `googlebigquery_replace_dataset`, `googlebigquery_replace_table`, `googlebigquery_set_routine_iam_policy`, `googlebigquery_set_table_iam_policy`, `googlebigquery_test_routine_iam_permissions`, `googlebigquery_test_table_iam_permissions`, `googlebigquery_undelete_dataset`, `googlebigquery_update_routine` `breaking-change` Migrated requiredScopes to authRequirements for per-auth-type scope filtering. `googlebigquery_cancel_job`, `googlebigquery_create_dataset`, `googlebigquery_create_routine`, `googlebigquery_create_row_access_policy`, `googlebigquery_create_table`, `googlebigquery_delete_dataset`, `googlebigquery_delete_job`, `googlebigquery_delete_model`, `googlebigquery_delete_routine`, `googlebigquery_delete_table`, `googlebigquery_get_dataset`, `googlebigquery_get_job`, `googlebigquery_get_model`, `googlebigquery_get_query_results`, `googlebigquery_get_routine`, `googlebigquery_get_routine_iam_policy`, `googlebigquery_get_service_account`, `googlebigquery_get_table`, `googlebigquery_get_table_iam_policy`, `googlebigquery_insert_job`, `googlebigquery_insert_table_data`, `googlebigquery_list_datasets`, `googlebigquery_list_jobs`, `googlebigquery_list_models`, `googlebigquery_list_projects`, `googlebigquery_list_routines`, `googlebigquery_list_row_access_policies`, `googlebigquery_list_table_data`, `googlebigquery_list_tables`, `googlebigquery_patch_dataset`, `googlebigquery_patch_model`, `googlebigquery_patch_table`, `googlebigquery_query`, `googlebigquery_replace_dataset`, `googlebigquery_replace_table`, `googlebigquery_set_routine_iam_policy`, `googlebigquery_set_table_iam_policy`, `googlebigquery_test_routine_iam_permissions`, `googlebigquery_test_table_iam_permissions`, `googlebigquery_undelete_dataset`, `googlebigquery_update_routine` `improvement` Clarified projectId descriptions to use id field not friendlyName. Added ACL full-replacement warning on dataset access fields. Added dataset prerequisite to create_routine. # Google Calendar Source: https://docs.stackone.com/connectors/googlecalendar/index How to set up the Google Calendar connector, plus the actions and events that are available.
Google Calendar
v1.2.0
37 actions · 5 events · 1 auth method
Scheduling
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Optionally, configure receiving Events for Google Calendar into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlecalendar/index.md for the full list. ## Events See https://docs.stackone.com/connectors/googlecalendar/index.md for the full list. # Google Calendar Changelog Source: https://docs.stackone.com/connectors/googlecalendar/changelog Release history for the Google Calendar connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added webhook events for changes to calendar events, sharing rules, the calendar list and settings, with notification channels created automatically when an account connects. `new-actions` Enabled Data Sync on calendar list and settings for scheduled full record syncs. # Google Chat Source: https://docs.stackone.com/connectors/googlechat/index How to set up the Google Chat connector, plus the actions that are available.
Google Chat
v2.2.0
32 actions · 1 auth method
Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 to access Google Chat spaces, messages, members, reactions, and custom emojis. Requires a Google... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlechat/index.md for the full list. # Google Chat Changelog Source: https://docs.stackone.com/connectors/googlechat/changelog Release history for the Google Chat connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Documented the custom emoji format needed to react to a message, so reactions using workspace emojis now work first time. Also clarified when making a space discoverable to your organization actually takes effect. `googlechat_create_reaction`, `googlechat_patch_space` `data-sync` Added DataSync support for list_spaces and list_custom_emojis actions. `googlechat_list_custom_emojis`, `googlechat_list_spaces` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # Google Cloud Compute Source: https://docs.stackone.com/connectors/googlecloudcompute/index How to set up the Google Cloud Compute connector, plus the actions that are available.
Google Cloud Compute
Previewv1.0.1
40 actions · 1 auth method
Internal
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires Owner or Compute Admin role on the target GCP project. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlecloudcompute/index.md for the full list. # Google Cloud Data Source: https://docs.stackone.com/connectors/googleclouddata/index How to set up the Google Cloud Data connector, plus the actions that are available.
Google Cloud Data
Previewv2.1.0
50 actions · 1 auth method
Infrastructure Databases Internal
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires Cloud SQL Admin and Pub/Sub Admin roles (or Owner) on the target project. Subject to Google Cloud session contr... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googleclouddata/index.md for the full list. # Google Cloud Observability Source: https://docs.stackone.com/connectors/googlecloudobservability/index How to set up the Google Cloud Observability connector, plus the actions and events that are available.
Google Cloud Observability
Previewv1.1.0
46 actions · 4 events · 1 auth method
Internal Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires Logging and/or Monitoring Viewer (read) or Admin (write) on the target project. Scopes can be narrowed to Cloud... Optionally, configure receiving Events for Google Cloud Observability into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlecloudobservability/index.md for the full list. ## Events See https://docs.stackone.com/connectors/googlecloudobservability/index.md for the full list. # Google Cloud Observability Changelog Source: https://docs.stackone.com/connectors/googlecloudobservability/changelog Release history for the Google Cloud Observability connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `data-sync` Added webhook events for Cloud Monitoring incidents (opened, closed, and renotify reminders) plus a catch-all; StackOne creates its webhook notification channel automatically when events are enabled, and you add that channel to the alerting policies whose incidents you want. Added data sync for 9 list actions, whose project input now defaults to the connected account's GCP Project ID. `googlecloudobservability_list_alert_policies`, `googlecloudobservability_list_dashboards`, `googlecloudobservability_list_exclusions`, `googlecloudobservability_list_log_metrics`, `googlecloudobservability_list_metric_descriptors`, `googlecloudobservability_list_monitored_resource_descriptors`, `googlecloudobservability_list_notification_channels`, `googlecloudobservability_list_sinks`, `googlecloudobservability_list_uptime_check_configs` `bug-fix` Fixed time-series truncation with explicit pageToken continuation, added secondary aggregation and a default FULL view, and preserved per-entry logName and resource when writing logs without batch defaults. Time-series data remains an array, with nextPageToken, executionErrors, unit and unreachable returned alongside it when present. `googlecloudobservability_list_time_series`, `googlecloudobservability_write_log_entries` `bug-fix` Added Google Cloud Console screenshots to the OAuth 2.0 connection guides, covering project selection, API enablement, Google Auth Platform, scopes, OAuth client creation and the Project ID lookup. Noted that an existing OAuth consent screen opens as an edit form rather than the setup wizard. # Google Cloud Security Source: https://docs.stackone.com/connectors/googlecloudsecurity/index How to set up the Google Cloud Security connector, plus the actions that are available.
Google Cloud Security
Previewv1.0.0
56 actions · 1 auth method
Security IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). This connector grants broad read/write on IAM policies and secrets. Restrict to users with Security Admin or Organizatio... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlecloudsecurity/index.md for the full list. # Google Cloud Storage Source: https://docs.stackone.com/connectors/googlecloudstorage/index How to set up the Google Cloud Storage connector, plus the actions that are available.
Google Cloud Storage
Previewv1.1.0
30 actions · 1 auth method
Storage Internal
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires Storage Admin or Owner role on the target project. Subject to Google Cloud session control — Google Workspace d... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlecloudstorage/index.md for the full list. # Google Cloud Storage Changelog Source: https://docs.stackone.com/connectors/googlecloudstorage/changelog Release history for the Google Cloud Storage connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed default object ACL listing to return a clear precondition error instead of a server error when the bucket metageneration matches the excluded value. # Google Contacts Source: https://docs.stackone.com/connectors/googlecontacts/index How to set up the Google Contacts connector, plus the actions that are available.
Google Contacts
v2.1.0
21 actions · 1 auth method
Productivity
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 to securely access and manage Google Contacts on behalf of a user. Requires Admin or Owner privi... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlecontacts/index.md for the full list. # Google Contacts Changelog Source: https://docs.stackone.com/connectors/googlecontacts/changelog Release history for the Google Contacts connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `enhancement` Added DataSync capability to list_contact_groups for periodic data synchronisation. `googlecontacts_list_contact_groups` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # Google Directory Source: https://docs.stackone.com/connectors/googledirectory/index How to set up the Google Directory connector, plus the actions and events that are available.
Google Directory
v1.3.0
41 actions · 6 events · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Optionally, configure receiving Events for Google Directory into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googledirectory/index.md for the full list. ## Events See https://docs.stackone.com/connectors/googledirectory/index.md for the full list. # Google Directory Changelog Source: https://docs.stackone.com/connectors/googledirectory/changelog Release history for the Google Directory connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `data-sync` Added webhook events for users created, updated, deleted, restored and admin status changes, and data sync for users, groups, domains, organizational units and the unified users, groups, organizations and roles lists. list_orgunits now returns the whole organizational unit tree when type is omitted, instead of only top-level units. `googledirectory_list_domains`, `googledirectory_list_groups`, `googledirectory_list_orgunits`, `googledirectory_list_users`, `googledirectory_unified_list_groups`, `googledirectory_unified_list_organizations`, `googledirectory_unified_list_roles`, `googledirectory_unified_list_users` `bug-fix` User lists with roles expanded now read up to 2,000 admin role assignments and 1,000 members per role-bound group instead of the first 200 of each. `googledirectory_unified_list_users` `improvement` User listings now include the delegated admin access people get from a group, not only access granted directly to their own account. `googledirectory_auth_test`, `googledirectory_create_domain`, `googledirectory_create_group`, `googledirectory_create_member`, `googledirectory_create_orgunit`, `googledirectory_create_user`, `googledirectory_delete_domain`, `googledirectory_delete_group`, `googledirectory_delete_member`, `googledirectory_delete_orgunit`, `googledirectory_delete_user`, `googledirectory_get_domain`, `googledirectory_get_group`, `googledirectory_get_member`, `googledirectory_get_orgunit`, `googledirectory_get_user`, `googledirectory_has_member`, `googledirectory_list_domains`, `googledirectory_list_groups`, `googledirectory_list_members`, `googledirectory_list_orgunits`, `googledirectory_list_users`, `googledirectory_patch_group`, `googledirectory_patch_member`, `googledirectory_patch_orgunit`, `googledirectory_patch_user`, `googledirectory_unified_get_group`, `googledirectory_unified_get_me`, `googledirectory_unified_get_organization`, `googledirectory_unified_get_role`, `googledirectory_unified_get_user`, `googledirectory_unified_list_groups`, `googledirectory_unified_list_organizations`, `googledirectory_unified_list_resource_types`, `googledirectory_unified_list_resource_users`, `googledirectory_unified_list_roles`, `googledirectory_unified_list_users`, `googledirectory_update_group`, `googledirectory_update_member`, `googledirectory_update_orgunit`, `googledirectory_update_user` `bugfix` `docs` Corrected the org unit error guidance - Google's 'Invalid Ou Id' on create_orgunit and update_orgunit is a sibling name collision, not the transient error it was previously documented as, and 'Invalid Parent Orgunit Id' means the parent could not be resolved. `googledirectory_create_orgunit`, `googledirectory_update_orgunit` `bugfix` `docs` Documented the list_users search syntax, directed the group, member and user identifier parameters to resolve their value from a list call instead of accepting a display name, clarified that update_user's response only echoes the fields sent, and made delete_domain fail when the domain does not exist instead of reporting a successful deletion. `googledirectory_create_member`, `googledirectory_delete_domain`, `googledirectory_delete_group`, `googledirectory_delete_member`, `googledirectory_delete_user`, `googledirectory_get_group`, `googledirectory_get_member`, `googledirectory_get_user`, `googledirectory_has_member`, `googledirectory_list_groups`, `googledirectory_list_members`, `googledirectory_list_users`, `googledirectory_patch_group`, `googledirectory_patch_member`, `googledirectory_patch_user`, `googledirectory_unified_get_organization`, `googledirectory_update_group`, `googledirectory_update_member`, `googledirectory_update_user` `improvement` Changed the connector release stage from beta back to preview. `bug-fix` Fixed unified IAM schema conformance — unified_get_me now returns scopes as an array instead of a space-delimited string, and list_organizations/get_organization return created_at as an ISO 8601 datetime string instead of an epoch-milliseconds number. `googledirectory_unified_get_me`, `googledirectory_unified_get_organization`, `googledirectory_unified_list_organizations` `bug-fix` Documented the list_groups query search syntax (searchable fields, '=' exact vs ':' prefix with a required trailing '*', and single-quote wrapping for values containing whitespace) so agents stop forming invalid 'name:value' queries, and added behavior notes for the transient 412 'User creation is not complete' after create_user (update_user and patch_user) and the transient 400 'Invalid Ou Id' on create_orgunit. `googledirectory_create_orgunit`, `googledirectory_list_groups`, `googledirectory_patch_user`, `googledirectory_update_user` `bug-fix` Fixed unified IAM users/roles/resource_users emitting non-schema enum values (active/inactive, member) and a stale scope.resource_id, repaired the broken expand=users/groups JEXL gates on groups and users, and collapsed unified_get_me's duplicate field mapping. # Google Docs Source: https://docs.stackone.com/connectors/googledocs/index How to set up the Google Docs connector, plus the actions that are available.
Google Docs
v1.4.0
4 actions · 1 auth method
Documents IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googledocs/index.md for the full list. # Google Docs Changelog Source: https://docs.stackone.com/connectors/googledocs/changelog Release history for the Google Docs connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Removed insertRichLink title and mimeType fields (output-only, API rejects on insert). `googledocs_update_document` `bug-fix` Fix updateNamedStyle fields mask — namedStyleType must always be included as selector. Remove insertRichLink title field (output-only, API rejects on insert). `googledocs_update_document` `new-params` `bug-fix` `description-fix` Add tab management (addDocumentTab, deleteTab, updateDocumentTabProperties), updateNamedStyle, insertRichLink, insertDate request types to update_document. Fix insertPerson output-only name field, change unit fields to PT-only enum. Add drive scope for insertRichLink. Improve includeTabsContent description. `googledocs_create_document`, `googledocs_get_document`, `googledocs_unified_get_me`, `googledocs_update_document` `bug-fix` Added includeTabsContent and suggestionsViewMode query params to get_document. Enables reading all document tabs instead of only the first tab. `googledocs_create_document`, `googledocs_get_document`, `googledocs_update_document` `bug-fix` Fixed unified_get_me's dual field-mapping source, a constant enum leaking its source_value, and a nested status enum shipped as a bare scalar instead of the value/source_value shape. # Google Drive Source: https://docs.stackone.com/connectors/googledrive/index How to set up the Google Drive connector, plus the actions and events that are available.
Google Drive
v2.1.1
64 actions · 2 events · 2 auth methods
Storage IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Standard OAuth 2.0 for accessing files and folders. Best for integrations that need broad Drive access. Uses Google Picker UI to let users select specific files. Best when users should choose exactly which files to share. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googledrive/index.md for the full list. ## Events See https://docs.stackone.com/connectors/googledrive/index.md for the full list. # Google Drive Changelog Source: https://docs.stackone.com/connectors/googledrive/changelog Release history for the Google Drive connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Channel Sync and Change webhook events no longer use the watched feed's resource ID as the record ID, which was the same for every event. Drive notifications carry no file ID, so these events no longer set a record ID. `data-sync` Added data sync for files and shared drives, and for the unified files, folders, drives, users, groups, organizations and roles lists. `googledrive_list_drives`, `googledrive_list_files`, `googledrive_unified_list_drives`, `googledrive_unified_list_files`, `googledrive_unified_list_folders`, `googledrive_unified_list_groups`, `googledrive_unified_list_organizations`, `googledrive_unified_list_roles`, `googledrive_unified_list_users` `bug-fix` unified_download_file returns the file's name from its Drive metadata. `googledrive_unified_download_file` `description-fix` Corrected the create_file and update_file descriptions, which pointed to an upload_file_content action that doesn't exist, and clarified that no action edits an existing file's content. Also removed references to a list_labels action that doesn't exist from the upload actions, and named the unified IAM actions by their exact IDs in the Admin Directory scope descriptions. `googledrive_create_file`, `googledrive_unified_check_permissions`, `googledrive_update_file`, `googledrive_upload_file_multipart`, `googledrive_upload_file_resumable`, `googledrive_upload_file_simple` `breaking` `bug-fix` `description-fix` Breaking — upload_file_simple now requires a contentType input so the created file records the correct mimeType instead of defaulting to application/octet-stream, and unified file upload now rejects empty content rather than silently creating a zero-byte file. Also adds optional metadata (content hints, shortcuts, content restrictions, created and modified timestamps) to the multipart and resumable uploads, and corrects the documented upload size ceiling to approximately 4.1 MB. `googledrive_create_permission`, `googledrive_get_changes_start_page_token`, `googledrive_unified_upload_file`, `googledrive_update_drive`, `googledrive_upload_file_multipart`, `googledrive_upload_file_resumable`, `googledrive_upload_file_simple` `bug-fix` Fixed unified IAM schema conformance — unified_get_me now returns scopes as an array instead of a space-delimited string, and list_organizations/get_organization return created_at as an ISO 8601 datetime string instead of an epoch-milliseconds number. Corrected the resource_users resource_id documentation. `googledrive_unified_get_me`, `googledrive_unified_get_organization`, `googledrive_unified_list_organizations`, `googledrive_unified_list_resource_users` `bug-fix` Fixed unified_get_me returning an empty body, invalid RoleTypeEnum/UserStatusEnum values on roles/users/resource_users, broken expand fan-out on groups/users JEXL conditions, and several composite-id and schema-shape violations across the unified IAM actions. # Google Forms Source: https://docs.stackone.com/connectors/googleforms/index How to set up the Google Forms connector, plus the actions that are available.
Google Forms
v1.0.1
6 actions · 1 auth method
Surveys
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googleforms/index.md for the full list. # Google Gemini Source: https://docs.stackone.com/connectors/googlegemini/index How to set up the Google Gemini connector, plus the actions and events that are available.
Google Gemini
v4.0.0
37 actions · 10 events · 2 auth methods
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for quick prototyping and single-project use via Google AI Studio. Use for applications needing user-context authorization and broader GCP permissions. Supports tuning and retriever acces... Optionally, configure receiving Events for Google Gemini into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlegemini/index.md for the full list. ## Events See https://docs.stackone.com/connectors/googlegemini/index.md for the full list. # Google Gemini Changelog Source: https://docs.stackone.com/connectors/googlegemini/changelog Release history for the Google Gemini connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `breaking` Fixed paging through the webhook list, which previously failed after the first page. Listing webhooks now returns the webhooks directly and a page token that can be passed straight back to fetch the next page. `googlegemini_list_webhooks` `webhook` `new-actions` Added webhook support so batch job and video generation results arrive as they happen instead of needing to be polled. Also added actions to inspect and manage webhook subscriptions. `googlegemini_create_webhook`, `googlegemini_delete_webhook`, `googlegemini_get_webhook`, `googlegemini_list_webhooks`, `googlegemini_ping_webhook`, `googlegemini_rotate_webhook_signing_secret`, `googlegemini_update_webhook` `googlegemini_async_batch_embed_content`, `googlegemini_cancel_operation`, `googlegemini_create_cached_content`, `googlegemini_delete_cached_content`, `googlegemini_delete_file`, `googlegemini_delete_file_search_store`, `googlegemini_delete_file_search_store_document`, `googlegemini_generate_image`, `googlegemini_generate_video`, `googlegemini_get_cached_content`, `googlegemini_get_file`, `googlegemini_get_file_search_store_document`, `googlegemini_import_file_to_search_store`, `googlegemini_list_cached_contents`, `googlegemini_list_file_search_store_documents`, `googlegemini_list_files`, `googlegemini_list_operations`, `googlegemini_register_file`, `googlegemini_update_cached_content` `data-sync-improvements` Disabled DataSync on list_files and list_cached_contents to prevent sync failures on empty accounts (Google API returns 400 instead of empty array). `googlegemini_list_cached_contents`, `googlegemini_list_files` `data-sync` Added DataSync support to list_models, list_files, list_cached_contents, and list_file_search_stores with full-refresh cursor pagination. `googlegemini_list_cached_contents`, `googlegemini_list_file_search_stores`, `googlegemini_list_files`, `googlegemini_list_models` `auth` Documented Google Cloud session control in the OAuth 2.0 connection guide and support description — the cause of periodic refresh token expired errors on Google Workspace domains that enforce re-authentication for Google Cloud scopes. `improvement` Added deprecated model warnings to all model input descriptions across actions. `googlegemini_async_batch_embed_content`, `googlegemini_batch_embed_contents`, `googlegemini_count_tokens`, `googlegemini_create_cached_content`, `googlegemini_embed_content`, `googlegemini_generate_content`, `googlegemini_get_model`, `googlegemini_stream_generate_content` `breaking-change` `improvement` `bug-fix` Migrated requiredScopes to authRequirements. Updated model references, penalty limitations, and count_tokens model field docs. # Google Maps Source: https://docs.stackone.com/connectors/googlemaps/index How to set up the Google Maps connector, plus the actions that are available.
Google Maps
v1.0.0
41 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a Google Maps Platform API key. Create the key in the Google Cloud console under Google Maps Platform... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlemaps/index.md for the full list. # Google Maps Changelog Source: https://docs.stackone.com/connectors/googlemaps/changelog Release history for the Google Maps connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` `description-fix` Return image/binary responses (tiles, static maps, Street View, heatmap tiles, solar GeoTIFF) as base64 to fix UTF-8 corruption, and clarified action descriptions for air-quality forecast, compute_insights, search_nearby, search_text, and geocode. `googlemaps_air_quality_forecast`, `googlemaps_air_quality_heatmap_tile`, `googlemaps_compute_insights`, `googlemaps_geocode`, `googlemaps_get_2d_tile`, `googlemaps_get_3d_tile`, `googlemaps_get_static_map`, `googlemaps_get_street_view_image`, `googlemaps_get_street_view_tile`, `googlemaps_pollen_heatmap_tile`, `googlemaps_search_nearby`, `googlemaps_search_text`, `googlemaps_solar_geo_tiff` `bug-fix` Pointed the connection guide's Google Cloud console link at the console home page so it matches the navigation the step describes, and added a warning covering the first-time Google Maps Platform account setup that otherwise blocks access to Keys & Credentials and the API Library. `new-connector` Initial Google Maps Platform connector — 41 API-key actions across 17 Google Maps APIs (Geocoding, Places, Places Aggregate, Address Validation, Routes, Roads, Geolocation, Time Zone, Elevation, Maps Static, Street View, Map Tiles, Aerial View, Air Quality, Pollen, Solar, Weather). Multi-host per-step routing, classic-vs-new key injection (query vs X-Goog-Api-Key), datetime_string typing for RFC3339 params, validationRules for required one-of inputs, get_place_photo dual JSON/binary handling, and a connection guide with screenshots for creating/restricting the key and enabling the required APIs. # Google Meet Source: https://docs.stackone.com/connectors/googlemeet/index How to set up the Google Meet connector, plus the actions that are available.
Google Meet
v2.0.1
24 actions · 1 auth method
Meetings
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlemeet/index.md for the full list. # Google Meet Changelog Source: https://docs.stackone.com/connectors/googlemeet/changelog Release history for the Google Meet connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `action-fix` Applied preview on all new members actions. `googlemeet_create_member`, `googlemeet_delete_member`, `googlemeet_get_member`, `googlemeet_list_members`, `googlemeet_update_member` `auth` `breaking-changes` `data-sync` `new-actions` Migrated to authRequirements for per-auth-type scope control. Also added meeting space member actions (list, get, create, update, delete, batch update) and data sync support for conference records. `googlemeet_batch_update_members`, `googlemeet_create_member`, `googlemeet_delete_member`, `googlemeet_get_member`, `googlemeet_list_members`, `googlemeet_update_member` `googlemeet_create_space`, `googlemeet_end_active_conference`, `googlemeet_get_conference_record`, `googlemeet_get_participant`, `googlemeet_get_participant_session`, `googlemeet_get_recording`, `googlemeet_get_smart_note`, `googlemeet_get_space`, `googlemeet_get_transcript`, `googlemeet_get_transcript_entry`, `googlemeet_list_conference_records`, `googlemeet_list_participant_sessions`, `googlemeet_list_participants`, `googlemeet_list_recordings`, `googlemeet_list_smart_notes`, `googlemeet_list_transcript_entries`, `googlemeet_list_transcripts`, `googlemeet_update_space` `bug-fix` Reworked the OAuth setup guide (added portal screenshots, corrected the Google Meet REST API label, fixed the broken scopes link) and documented update_space resource-name and moderation preconditions. # Google Search Console Source: https://docs.stackone.com/connectors/googlesearchconsole/index How to set up the Google Search Console connector, plus the actions that are available.
Google Search Console
Previewv1.2.1
10 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlesearchconsole/index.md for the full list. # Google Search Console Changelog Source: https://docs.stackone.com/connectors/googlesearchconsole/changelog Release history for the Google Search Console connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `description-fix` Add Site, Delete Site, Submit Sitemap and Delete Sitemap now return a success message instead of an empty response. Clarified that List Sites reads live data and that List Sitemaps includes submitted URL counts for sitemaps Google has downloaded. `googlesearchconsole_add_site`, `googlesearchconsole_delete_site`, `googlesearchconsole_delete_sitemap`, `googlesearchconsole_list_sitemaps`, `googlesearchconsole_list_sites`, `googlesearchconsole_submit_sitemap` `data-sync` `new-feature` Added DataSync support to the site list action, so Search Console properties can be pulled into StackOne on a schedule. Sites refresh in full on each run, as the Search Console API exposes no updated-since filter. `googlesearchconsole_list_sites` `bug-fix` `guide` Fixed the sitemap index filter on list_sitemaps, which was previously ignored, and search analytics parameters now declare their valid values and ranges. Also refreshed the OAuth 2.0 connection guide with screenshots and added documentation links and tags to every action. # Google Sheets Source: https://docs.stackone.com/connectors/googlesheets/index How to set up the Google Sheets connector, plus the actions that are available.
Google Sheets
v1.0.1
17 actions · 1 auth method
Documents
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googlesheets/index.md for the full list. # Google Shopping Source: https://docs.stackone.com/connectors/googleshopping/index How to set up the Google Shopping connector, plus the actions and events that are available.
Google Shopping
v1.2.0
80 actions · 2 events · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud and Admin access to the Google Merchant Ce... Optionally, configure receiving Events for Google Shopping into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googleshopping/index.md for the full list. ## Events See https://docs.stackone.com/connectors/googleshopping/index.md for the full list. # Google Shopping Changelog Source: https://docs.stackone.com/connectors/googleshopping/changelog Release history for the Google Shopping connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added webhook events for product status changes and account service changes, with notification subscriptions created and removed automatically when an account is connected or disconnected. `data-sync` `new-feature` Added periodic data sync for 13 list endpoints — accounts, users, regions, programs, quota groups, data sources, conversion sources, products, online return policies, account services, account issues, notification subscriptions, and aggregate product statuses — so their records can be pulled into StackOne and kept up to date, with paging handled automatically. # Google Slides Source: https://docs.stackone.com/connectors/googleslides/index How to set up the Google Slides connector, plus the actions that are available.
Google Slides
v3.1.0
47 actions · 1 auth method
Documents
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googleslides/index.md for the full list. # Google Slides Changelog Source: https://docs.stackone.com/connectors/googleslides/changelog Release history for the Google Slides connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `bug-fix` Added the Google Drive read-only scope so videos stored in Drive can be embedded into slides. Clarified the find-and-replace guidance so text is replaced in one step. `googleslides_batch_update_presentation`, `googleslides_create_image`, `googleslides_create_line`, `googleslides_create_paragraph_bullets`, `googleslides_create_presentation`, `googleslides_create_shape`, `googleslides_create_sheets_chart`, `googleslides_create_slide`, `googleslides_create_table`, `googleslides_create_video`, `googleslides_delete_object`, `googleslides_delete_paragraph_bullets`, `googleslides_delete_table_column`, `googleslides_delete_table_row`, `googleslides_delete_text`, `googleslides_duplicate_object`, `googleslides_get_page`, `googleslides_get_page_thumbnail`, `googleslides_get_presentation`, `googleslides_group_objects`, `googleslides_insert_table_columns`, `googleslides_insert_table_rows`, `googleslides_insert_text`, `googleslides_merge_table_cells`, `googleslides_refresh_sheets_chart`, `googleslides_replace_all_shapes_with_image`, `googleslides_replace_all_shapes_with_sheets_chart`, `googleslides_replace_all_text`, `googleslides_replace_image`, `googleslides_reroute_line`, `googleslides_ungroup_objects`, `googleslides_unmerge_table_cells`, `googleslides_update_line_category`, `googleslides_update_line_properties`, `googleslides_update_page_element_alt_text`, `googleslides_update_page_element_transform`, `googleslides_update_page_elements_z_order`, `googleslides_update_page_properties`, `googleslides_update_paragraph_style`, `googleslides_update_shape_properties`, `googleslides_update_slide_properties`, `googleslides_update_slides_position`, `googleslides_update_table_cell_properties`, `googleslides_update_table_column_properties`, `googleslides_update_table_row_properties`, `googleslides_update_text_style`, `googleslides_update_video_properties` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. Added spreadsheets.readonly scope to chart actions for linked Sheets chart support. `googleslides_create_sheets_chart`, `googleslides_refresh_sheets_chart`, `googleslides_replace_all_shapes_with_sheets_chart` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # Google Tasks Source: https://docs.stackone.com/connectors/googletasks/index How to set up the Google Tasks connector, plus the actions that are available.
Google Tasks
v2.1.0
12 actions · 1 auth method
Productivity
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin or Owner privileges within Google Cloud. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googletasks/index.md for the full list. # Google Tasks Changelog Source: https://docs.stackone.com/connectors/googletasks/changelog Release history for the Google Tasks connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `datasync` Added DataSync support for List Task Lists action with cursor pagination. `googletasks_list_task_lists` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # Google Text-to-Speech Source: https://docs.stackone.com/connectors/googletexttospeech/index How to set up the Google Text-to-Speech connector, plus the actions that are available.
Google Text-to-Speech
Previewv0.2.0
7 actions · 1 auth method
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth client in a Google Cloud project with the Cloud Text-to-Speech API enabled. Uses the cloud... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googletexttospeech/index.md for the full list. # Google Text-to-Speech Changelog Source: https://docs.stackone.com/connectors/googletexttospeech/changelog Release history for the Google Text-to-Speech connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `bug-fix` `guide` Replaced the GCP Project ID field with GCP Project Number, which long audio synthesis and job listing now use, so long audio jobs are listed for every connection. Existing accounts need to be re-linked with the project number. `googletexttospeech_projects_locations_operations_get`, `googletexttospeech_projects_locations_operations_list`, `googletexttospeech_projects_locations_synthesize_long_audio` `bug-fix` `guide` Added GCP project ID validation to the connection test, updated the connection guides (billing step, project number, same steps as other Google connectors), and fixed long audio job listing and voice format guidance. `googletexttospeech_projects_locations_operations_get`, `googletexttospeech_projects_locations_operations_list`, `googletexttospeech_text_synthesize` `new-actions` Initial release covering speech synthesis, long audio synthesis, voice listing, and long-running operation management. # Google Translate Source: https://docs.stackone.com/connectors/googletranslate/index How to set up the Google Translate connector, plus the actions that are available.
Google Translate
v1.1.2
22 actions · 1 auth method
Translation
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 to securely access and manage Cloud Translation resources on behalf of a user. Requires Admin or... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/googletranslate/index.md for the full list. # Google Translate Changelog Source: https://docs.stackone.com/connectors/googletranslate/changelog Release history for the Google Translate connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Corrected the formatting of the refresh-token note in the connection guide warning. `guide` Connection guide and setup screen now explain when Google may invalidate your refresh token and how to avoid the 7-day expiry by publishing your OAuth app. `data-sync` `actions` Added DataSync support for list_glossaries, list_adaptive_mt_datasets, and list_supported_languages. Made the location field optional across all actions, defaulting to us-central1. `googletranslate_adaptive_mt_translate`, `googletranslate_batch_translate_document`, `googletranslate_batch_translate_text`, `googletranslate_create_adaptive_mt_dataset`, `googletranslate_create_glossary`, `googletranslate_create_glossary_entry`, `googletranslate_delete_adaptive_mt_dataset`, `googletranslate_delete_glossary`, `googletranslate_delete_glossary_entry`, `googletranslate_get_glossary`, `googletranslate_get_glossary_entry`, `googletranslate_import_adaptive_mt_file`, `googletranslate_list_adaptive_mt_datasets`, `googletranslate_list_glossaries`, `googletranslate_list_glossary_entries`, `googletranslate_list_supported_languages`, `googletranslate_translate_document`, `googletranslate_update_glossary`, `googletranslate_update_glossary_entry` `auth` Documented Google Cloud session control in the OAuth 2.0 connection guide and support description — the cause of periodic refresh token expired errors on Google Workspace domains that enforce re-authentication for Google Cloud scopes. Also corrected the support description, which incorrectly described the connector as managing Google Contacts. `bug-fixes` `breaking-changes` Fix create_adaptive_mt_dataset to auto-construct resource name from credentials, remove unsupported mimeType from batch_translate_document, remove cloud-platform scope, and improve connection guide `googletranslate_adaptive_mt_translate`, `googletranslate_batch_translate_document`, `googletranslate_batch_translate_text`, `googletranslate_create_adaptive_mt_dataset`, `googletranslate_create_glossary`, `googletranslate_create_glossary_entry`, `googletranslate_delete_adaptive_mt_dataset`, `googletranslate_delete_glossary`, `googletranslate_delete_glossary_entry`, `googletranslate_detect_language`, `googletranslate_get_glossary`, `googletranslate_get_glossary_entry`, `googletranslate_import_adaptive_mt_file`, `googletranslate_list_adaptive_mt_datasets`, `googletranslate_list_glossaries`, `googletranslate_list_glossary_entries`, `googletranslate_list_supported_languages`, `googletranslate_romanize_text`, `googletranslate_translate_document`, `googletranslate_translate_text`, `googletranslate_update_glossary`, `googletranslate_update_glossary_entry` `new-actions` Initial release of connector # Gorgias Source: https://docs.stackone.com/connectors/gorgias/index How to set up the Gorgias connector, plus the actions and events that are available.
Gorgias
v1.3.0
69 actions · 8 events · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Admin privileges are required to access the REST API settings. Optionally, configure receiving Events for Gorgias into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gorgias/index.md for the full list. ## Events See https://docs.stackone.com/connectors/gorgias/index.md for the full list. # Gorgias Changelog Source: https://docs.stackone.com/connectors/gorgias/changelog Release history for the Gorgias connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added webhook events for ticket created, updated, status and assignment changes, self-unsnoozed, handover, and ticket message created and failed, with Gorgias subscriptions created automatically on connect. `feature` Added DataSync support to eleven list actions (customers, tickets, messages, users, tags, teams, views, macros, rules, integrations, and settings) for periodic full-refresh syncing of records into StackOne. `gorgias_list_customers`, `gorgias_list_integrations`, `gorgias_list_macros`, `gorgias_list_messages`, `gorgias_list_rules`, `gorgias_list_settings`, `gorgias_list_tags`, `gorgias_list_teams`, `gorgias_list_tickets`, `gorgias_list_users`, `gorgias_list_views` `bug-fix` Clarified customer, macro, rule, view, message, and integration action guidance to prevent invalid requests, and required the always-mandatory macro name and message sender fields. `gorgias_create_integration`, `gorgias_create_message`, `gorgias_create_rule`, `gorgias_create_view`, `gorgias_list_customers`, `gorgias_merge_customers`, `gorgias_search_view_items`, `gorgias_update_macro`, `gorgias_update_message`, `gorgias_update_rule`, `gorgias_update_view` `guide` Updated API Key connection guide with corrected navigation and portal screenshots. # GoTo Webinar Source: https://docs.stackone.com/connectors/goto/index How to set up the GoTo Webinar connector, plus the actions that are available.
GoTo Webinar
Previewv2.1.0
61 actions · 1 auth method
Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Login to your GoTo account to connect your data. You must have webinar hosting privileges to use the API. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/goto/index.md for the full list. # GoTo Webinar Changelog Source: https://docs.stackone.com/connectors/goto/changelog Release history for the GoTo Webinar connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for unified IAM list actions (users, groups, roles) with full-refresh sync. `goto_unified_list_groups`, `goto_unified_list_roles`, `goto_unified_list_users` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. `goto_cancel_webinar`, `goto_copy_webinar`, `goto_create_co_organizers`, `goto_create_panelists`, `goto_create_registrant`, `goto_create_secret_key`, `goto_create_user_subscriptions`, `goto_create_webhooks`, `goto_create_webinar`, `goto_delete_coorganizer`, `goto_delete_registrant`, `goto_delete_user_subscriptions`, `goto_delete_webhooks`, `goto_delete_webinar_panelist`, `goto_get_account_webinars`, `goto_get_all_insession_webinars`, `goto_get_attendee`, `goto_get_attendee_poll_answers`, `goto_get_attendee_questions`, `goto_get_attendee_survey_answers`, `goto_get_attendees_for_all_webinar_sessions`, `goto_get_audio_information`, `goto_get_co_organizers`, `goto_get_current_user`, `goto_get_organizer_sessions`, `goto_get_performance_for_all_webinar_sessions`, `goto_get_registrant`, `goto_get_registrants`, `goto_get_registration_fields`, `goto_get_session_attendees`, `goto_get_session_performance`, `goto_get_user_subscription`, `goto_get_user_subscriptions`, `goto_get_webhook`, `goto_get_webhooks`, `goto_get_webinar`, `goto_get_webinar_meeting_times`, `goto_get_webinar_panelists`, `goto_get_webinar_session`, `goto_get_webinar_sessions`, `goto_get_webinars`, `goto_list_session_polls`, `goto_list_session_questions`, `goto_list_session_surveys`, `goto_resend_co_organizer_invitation`, `goto_resend_panelist_invitation`, `goto_search_for_completed_recording_assets`, `goto_unified_get_group`, `goto_unified_get_me`, `goto_unified_get_organization`, `goto_unified_get_role`, `goto_unified_get_user`, `goto_unified_list_groups`, `goto_unified_list_organizations`, `goto_unified_list_roles`, `goto_unified_list_users`, `goto_update_audio_information`, `goto_update_user_subscriptions`, `goto_update_webhooks`, `goto_update_webinar`, `goto_webinar_start_url` `bug-fix` Standardized action category capitalization for more consistent portal filters. `goto_unified_get_group`, `goto_unified_get_me`, `goto_unified_get_organization`, `goto_unified_get_role`, `goto_unified_get_user`, `goto_unified_list_groups`, `goto_unified_list_organizations`, `goto_unified_list_roles`, `goto_unified_list_users` `new-actions` Added unified IAM actions for account users, groups, role sets, organizations, and credentials. Existing connections need to reconnect to grant the new Admin Center permission before these actions work. # Grafana Source: https://docs.stackone.com/connectors/grafana/index How to set up the Grafana connector, plus the actions and events that are available.
Grafana
Previewv1.3.1
100 actions · 19 events · 1 auth method
Observability IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using a Grafana Service Account Token with appropriate permissions Optionally, configure receiving Events for Grafana into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/grafana/index.md for the full list. ## Events See https://docs.stackone.com/connectors/grafana/index.md for the full list. # Grafana Changelog Source: https://docs.stackone.com/connectors/grafana/changelog Release history for the Grafana connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists now include pending organization invitations with status pending, and user lookups resolve them; an unknown id now returns 404. `grafana_unified_get_user`, `grafana_unified_list_users` `new-events` Added webhook events for Grafana Alerting (alert firing and alert resolved) and Grafana IRM (alert group lifecycle, schedule, and shift swap events), with automatic contact point, notification policy, and IRM outgoing webhook setup on connect. `data-sync` Added DataSync support to 17 list actions (dashboards, dashboard tags, folders, teams, service accounts, data sources, alerting, playlists, library elements, correlations, org users, and unified IAM users, groups, organizations, and roles). Fixed snapshot creation by allowing the source dashboard uid to be passed. `grafana_create_snapshot`, `grafana_list_alert_rules`, `grafana_list_contact_points`, `grafana_list_correlations`, `grafana_list_dashboard_tags`, `grafana_list_datasources`, `grafana_list_folders`, `grafana_list_library_elements`, `grafana_list_mute_timings`, `grafana_list_org_users`, `grafana_list_playlists`, `grafana_list_service_accounts`, `grafana_list_teams`, `grafana_search_dashboards`, `grafana_unified_list_groups`, `grafana_unified_list_organizations`, `grafana_unified_list_roles`, `grafana_unified_list_users` `fix` Fixed looking up a single user by id, which previously returned nothing. `grafana_unified_get_user` `new-actions` Added unified IAM support (users, roles, groups, organizations, credentials, resource users) for permission-check and identity-sync use cases. Team group lists enumerate the full organization with no page ceiling. # Granola Source: https://docs.stackone.com/connectors/granola/index How to set up the Granola connector, plus the actions that are available.
Granola
Previewv0.1.0
4 actions · 1 auth method
Notetaker
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using a personal API key generated in the Granola desktop app. API access requires a Business or Enterprise plan... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/granola/index.md for the full list. # Granola Changelog Source: https://docs.stackone.com/connectors/granola/changelog Release history for the Granola connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Initial release with actions to list and retrieve meeting notes, page through full meeting transcripts, and list folders. Notes support incremental scheduled sync on updated_after; folders sync in full. # Greenhouse - Harvest v3 Source: https://docs.stackone.com/connectors/greenhouse/index How to set up the Greenhouse - Harvest v3 connector, plus the actions that are available.
Greenhouse - Harvest v3
v1.1.0
99 actions · 2 auth methods
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Default for most integrations. Requires a signed Greenhouse partnership agreement. For deployments where you self-host StackOne and connect your own Greenhouse tenant. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/greenhouse/index.md for the full list. # Greenhouse - Harvest v3 Changelog Source: https://docs.stackone.com/connectors/greenhouse/changelog Release history for the Greenhouse - Harvest v3 connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `feature` `bug-fix` Added Data Sync support to all 45 list actions, so Greenhouse records can be kept in sync with StackOne. Also fixed cursor pagination on list_openings and list_job_notes, which previously failed on the second page. # Groq Source: https://docs.stackone.com/connectors/groq/index How to set up the Groq connector, plus the actions that are available.
Groq
Betav1.1.0
20 actions · 1 auth method
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate API keys from your Groq console. Free tier (default, no card required) gives ~30 RPM / 14.4K RPD / 6K TPM — suf... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/groq/index.md for the full list. # Groq Changelog Source: https://docs.stackone.com/connectors/groq/changelog Release history for the Groq connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added scheduled data sync for models, files, batches and fine-tuning jobs, so these collections can be kept up to date and read back without calling Groq on every request. All four refresh in full on each run, because the API offers no updated-since filter. # Gusto Source: https://docs.stackone.com/connectors/gusto/index How to set up the Gusto connector, plus the actions and events that are available.
Gusto
v1.2.0
96 actions · 24 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin Payroll Role privileges in your Gusto account. Optionally, configure receiving Events for Gusto into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/gusto/index.md for the full list. ## Events See https://docs.stackone.com/connectors/gusto/index.md for the full list. # Gusto Changelog Source: https://docs.stackone.com/connectors/gusto/changelog Release history for the Gusto connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added scheduled data sync to ten collection actions — employees, contractors, departments, company locations, pay schedules, payrolls, company benefits, company bank accounts, company attachments and time off policies — so these collections can be kept in sync and searched without calling Gusto on every request. Employees, contractors, locations, pay schedules and payrolls sync page by page; the rest are returned in full by a single request. All sync by full refresh, because the Gusto API exposes no updated-since filter on these endpoints. `gusto_list_company_attachments`, `gusto_list_company_bank_accounts`, `gusto_list_company_benefits`, `gusto_list_company_locations`, `gusto_list_company_payrolls`, `gusto_list_contractors`, `gusto_list_departments`, `gusto_list_employees`, `gusto_list_pay_schedules`, `gusto_list_time_off_policies` `new-actions` Added inbound webhook event support across 22 resource types (company, employee, payroll, contractor, benefits, documents, and more) with automatic subscription provisioning and verification. # Hailey HR Source: https://docs.stackone.com/connectors/haileyhr/index How to set up the Hailey HR connector, plus the actions and events that are available.
Hailey HR
v1.3.1
35 actions · 2 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a long-lived personal access token generated from the Hailey dashboard. The token inherits the master-data permissi... Optionally, configure receiving Events for Hailey HR into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/haileyhr/index.md for the full list. ## Events See https://docs.stackone.com/connectors/haileyhr/index.md for the full list. # Hailey HR Changelog Source: https://docs.stackone.com/connectors/haileyhr/changelog Release history for the Hailey HR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide-fix` Clarified the Access Token link-account guide navigation (Settings gear location for the Integrations All and Added tabs, and the Hailey Company Id field label) and pointed the Access Token connection guide link to the StackOne docs page. `data-sync` Added dataSync configuration to 12 list actions enabling periodic data synchronisation. `haileyhr_list_casual_employments`, `haileyhr_list_certificates`, `haileyhr_list_company_certifications`, `haileyhr_list_company_salary_types`, `haileyhr_list_competences`, `haileyhr_list_document_folders`, `haileyhr_list_education_sessions`, `haileyhr_list_educations`, `haileyhr_list_employee_competences`, `haileyhr_list_employees`, `haileyhr_list_employments`, `haileyhr_list_salaries` `new-feature` `bug-fix` `improved-descriptions` Added Company ID configField with credentials fallback for list_public_employees, fixed update_education to require educationName, marked untestable actions as preview, and improved action descriptions. `haileyhr_clock_in`, `haileyhr_clock_out`, `haileyhr_end_break`, `haileyhr_import_one_to_one`, `haileyhr_import_time_off`, `haileyhr_list_public_employees`, `haileyhr_start_break`, `haileyhr_update_education` `new-feature` `improved-guides` Added webhook support for employee and company change events, improved connection guide with step-by-step screenshots, and refined action descriptions. # Harness Source: https://docs.stackone.com/connectors/harness/index How to set up the Harness connector, plus the actions that are available.
Harness
v1.5.0
152 actions · 1 auth method
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/harness/index.md for the full list. # Harness Changelog Source: https://docs.stackone.com/connectors/harness/changelog Release history for the Harness connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added 69 Harness FME actions covering projects, environments, SDK API keys, traffic types, attributes, identities, feature flags and flag definitions, flag sets, segments, change requests and rollout statuses. `harness_add_fme_segment_keys`, `harness_archive_fme_feature_flag`, `harness_bulk_save_fme_attributes`, `harness_create_fme_change_request`, `harness_create_fme_environment`, `harness_create_fme_feature_flag`, `harness_create_fme_feature_flag_definition`, `harness_create_fme_flag_set`, `harness_create_fme_large_segment`, `harness_create_fme_rule_based_segment`, `harness_create_fme_sdk_api_key`, `harness_create_fme_segment`, `harness_create_fme_traffic_type`, `harness_deactivate_fme_large_segment`, `harness_deactivate_fme_rule_based_segment`, `harness_deactivate_fme_segment`, `harness_delete_fme_attribute`, `harness_delete_fme_environment`, `harness_delete_fme_feature_flag`, `harness_delete_fme_flag_set`, `harness_delete_fme_identity`, `harness_delete_fme_large_segment`, `harness_delete_fme_rule_based_segment`, `harness_delete_fme_sdk_api_key`, `harness_delete_fme_segment`, `harness_delete_fme_traffic_type`, `harness_enable_fme_large_segment`, `harness_enable_fme_rule_based_segment`, `harness_enable_fme_segment`, `harness_get_fme_change_request`, `harness_get_fme_feature_flag`, `harness_get_fme_feature_flag_definition`, `harness_get_fme_flag_set`, `harness_get_fme_large_segment`, `harness_get_fme_rule_based_segment`, `harness_kill_fme_feature_flag`, `harness_list_fme_attributes`, `harness_list_fme_change_requests`, `harness_list_fme_environment_large_segments`, `harness_list_fme_environment_rule_based_segments`, `harness_list_fme_environment_segments`, `harness_list_fme_environments`, `harness_list_fme_feature_flag_definitions`, `harness_list_fme_feature_flags`, `harness_list_fme_flag_sets`, `harness_list_fme_large_segments`, `harness_list_fme_projects`, `harness_list_fme_rollout_statuses`, `harness_list_fme_rule_based_segments`, `harness_list_fme_segment_keys`, `harness_list_fme_segments`, `harness_list_fme_traffic_types`, `harness_reallocate_fme_feature_flag_traffic`, `harness_remove_fme_feature_flag_definition`, `harness_remove_fme_segment_keys`, `harness_replace_fme_feature_flag_definition`, `harness_restore_fme_feature_flag`, `harness_save_fme_attribute`, `harness_save_fme_identities`, `harness_save_fme_identity`, `harness_set_fme_feature_flag_tags`, `harness_unarchive_fme_feature_flag`, `harness_update_fme_attribute`, `harness_update_fme_change_request_status`, `harness_update_fme_environment`, `harness_update_fme_feature_flag`, `harness_update_fme_feature_flag_definition`, `harness_update_fme_identity`, `harness_update_fme_rule_based_segment_definition` `bug-fix` User lists now return pending account-level invitations as users with status pending after the last member page, and get user finds them by their invitation id. `harness_unified_get_user`, `harness_unified_list_users` `new-feature` Organizations, projects, roles, role assignments, user groups, users, service accounts and invites can now be kept in sync automatically. `harness_list_aggregated_users`, `harness_list_invites`, `harness_list_organizations`, `harness_list_pending_users`, `harness_list_projects`, `harness_list_role_assignments`, `harness_list_roles`, `harness_list_service_accounts`, `harness_list_user_groups`, `harness_list_users`, `harness_unified_list_groups`, `harness_unified_list_organizations`, `harness_unified_list_roles`, `harness_unified_list_users` `fix` User searches by email address now match regardless of capitalisation. `harness_unified_list_users` `improvement` User role lists now include roles granted through group membership, not only roles assigned directly to a user. `harness_unified_get_user`, `harness_unified_list_users` `bug-fix` Fixed user, group, role, and organization lists and lookups failing on every request, and fixed lists being truncated on large accounts. `harness_unified_get_group`, `harness_unified_get_me`, `harness_unified_get_organization`, `harness_unified_get_role`, `harness_unified_get_user`, `harness_unified_list_groups`, `harness_unified_list_organizations`, `harness_unified_list_roles`, `harness_unified_list_users` `bug-fix` Fixes on update_feature, update_segment, list_users, and list_organizations so agents resolve the "default" organization and "default_project" identifiers without an extra discovery call. No schema or request changes. `harness_list_organizations`, `harness_list_users`, `harness_update_feature`, `harness_update_segment` `bug-fix` Description fixes from behavioural-test triage across update_feature, create_segment, list_tags, update_user, and the invite actions (removed the non-existent invite timestamp field). No behavioural or schema changes to action calls. `harness_create_segment`, `harness_get_invite`, `harness_list_invites`, `harness_list_pending_users`, `harness_list_tags`, `harness_update_feature`, `harness_update_user` `bug-fix` `new-actions` Behavioural fixes across platform actions, new service account actions, and an updated connection guide. # Harness FME Source: https://docs.stackone.com/connectors/harnessfme/index How to set up the Harness FME connector, plus the actions that are available.
Harness FME
Previewv0.1.0
83 actions · 2 auth methods
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Recommended for production connections. A service account token acts as a Harness service account, not a person, so it k... Use this for quick setup, testing or personal use. A personal access token acts as the user who created it, with all of... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/harnessfme/index.md for the full list. # Harness FME Changelog Source: https://docs.stackone.com/connectors/harnessfme/changelog Release history for the Harness FME connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial release covering FME projects, environments, traffic types, feature flags and definitions, segments, rule-based and large segments, change requests, flag sets, attributes, tags and rollout statuses, plus Harness platform users, invites, user groups, projects and organizations. # Harvest Source: https://docs.stackone.com/connectors/harvest/index How to set up the Harvest connector, plus the actions that are available.
Harvest
v1.2.0
87 actions · 2 auth methods
Time Tracking IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth 2.0 application in the Harvest Developers portal. Users pick which Harvest account to auth... Requires generating a Personal Access Token in the Harvest Developers portal. The token inherits the permissions of the... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/harvest/index.md for the full list. # Harvest Changelog Source: https://docs.stackone.com/connectors/harvest/changelog Release history for the Harvest connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support to 19 list actions, so their records can be periodically pulled into StackOne and kept up to date. `harvest_list_clients`, `harvest_list_contacts`, `harvest_list_estimate_item_categories`, `harvest_list_estimates`, `harvest_list_expense_categories`, `harvest_list_expenses`, `harvest_list_invoice_item_categories`, `harvest_list_invoices`, `harvest_list_my_project_assignments`, `harvest_list_projects`, `harvest_list_roles`, `harvest_list_task_assignments`, `harvest_list_tasks`, `harvest_list_time_entries`, `harvest_list_user_assignments`, `harvest_list_users`, `harvest_unified_list_organizations`, `harvest_unified_list_roles`, `harvest_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, resource users, resource types, and account credentials. `harvest_unified_get_me`, `harvest_unified_get_organization`, `harvest_unified_get_role`, `harvest_unified_get_user`, `harvest_unified_list_organizations`, `harvest_unified_list_resource_types`, `harvest_unified_list_resource_users`, `harvest_unified_list_roles`, `harvest_unified_list_users` `bug-fix` Documented that update_user silently ignores access_roles changes for the account owner (200 OK, role unchanged); verify the returned access_roles before reporting success. # hc1 Source: https://docs.stackone.com/connectors/hc1/index How to set up the hc1 connector, plus the actions that are available.
hc1
Previewv0.1.0
19 actions · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Signs in as an hc1 user and acts with that user's role. The user must not have multi-factor authentication turned on. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hc1/index.md for the full list. # hc1 Changelog Source: https://docs.stackone.com/connectors/hc1/changelog Release history for the hc1 connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` New hc1 connector for reading CRM organizations, contacts, cases, tasks and memos, plus record type metadata, account settings and analytics dashboards. # Heap Source: https://docs.stackone.com/connectors/heap/index How to set up the Heap connector, plus the actions that are available.
Heap
v1.0.3
6 actions · 1 auth method
Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Heap account using your App ID to send server-side events and user properties. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/heap/index.md for the full list. # Heap Changelog Source: https://docs.stackone.com/connectors/heap/changelog Release history for the Heap connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide-improvements` Updated connector guide navigation instructions to match actual Heap UI. Corrected App ID location path to Account > Manage > Teams and projects > Projects. `bug-fix` Added reserved "id" key warning to add_user_properties description. Documented same-identifier-per-batch rule and atomic rejection behaviour in bulk_track_events description. `heap_add_user_properties`, `heap_bulk_track_events` `bug-fix` `improvement` Fixed properties field to required in add_user_properties. Improved action descriptions with dependency info and usage clarifications. # Help Scout Source: https://docs.stackone.com/connectors/helpscout/index How to set up the Help Scout connector, plus the actions and events that are available.
Help Scout
v1.2.0
36 actions · 28 events · 2 auth methods
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for server-to-server integrations with no user interaction. Acts with app-level permissions, not tied to a user. Recommended for user-facing integrations. Each user authorizes access scoped to their Help Scout permissions. Optionally, configure receiving Events for Help Scout into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/helpscout/index.md for the full list. ## Events See https://docs.stackone.com/connectors/helpscout/index.md for the full list. # Help Scout Changelog Source: https://docs.stackone.com/connectors/helpscout/changelog Release history for the Help Scout connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added native webhook support for 27 Help Scout event types covering conversations, customers, organizations, tags, ratings, surveys, user status and Beacon chats. StackOne creates the Help Scout webhook automatically when an account connects and removes it on disconnect. `data-sync` Enabled scheduled Data Sync on eight list actions — conversations, customers, tags, inboxes, users, user statuses, workflows and teams — so these collections can be searched and filtered without calling Help Scout on every request. Conversations and customers sync incrementally using the modifiedSince watermark; the remaining six refresh in full, because no other Help Scout endpoint exposes an updated-since filter. # Hexnode Source: https://docs.stackone.com/connectors/hexnode/index How to set up the Hexnode connector, plus the actions that are available.
Hexnode
Previewv0.2.1
96 actions · 1 auth method
Device Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses the portal's single API key, which has full admin-level API access. No app registration is needed. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hexnode/index.md for the full list. # Hexnode Changelog Source: https://docs.stackone.com/connectors/hexnode/changelog Release history for the Hexnode connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified which policy sections to leave out when creating or editing a policy, so resending what was read back is no longer rejected and no longer leaves the policy reporting errors on every later edit. `hexnode_create_policy`, `hexnode_edit_policy`, `hexnode_get_policy` `bug-fix` `new-actions` Added file upload and domain listing actions, clarified how group updates, policy edits, deletes and web apps behave, and made file uploads accept data URI content and refuse non-upload URLs cleanly. `hexnode_list_domains`, `hexnode_upload_file_content` `hexnode_add_app_to_list`, `hexnode_add_remove_app_catalog_apps`, `hexnode_add_remove_app_group_apps`, `hexnode_add_remove_device_group_devices`, `hexnode_add_remove_user_group_users`, `hexnode_archive_policy`, `hexnode_create_policy`, `hexnode_delete_app_catalog`, `hexnode_delete_app_group`, `hexnode_delete_device_group`, `hexnode_delete_files`, `hexnode_delete_user`, `hexnode_delete_user_group`, `hexnode_deploy_files`, `hexnode_edit_policy`, `hexnode_generate_presigned_upload_url`, `hexnode_initiate_automation`, `hexnode_list_organizational_units`, `hexnode_remove_app`, `hexnode_update_app_catalog`, `hexnode_update_app_group`, `hexnode_update_device_group`, `hexnode_update_user_group`, `hexnode_verify_file_upload` `new-actions` Initial action mappings for Hexnode # HiBob Source: https://docs.stackone.com/connectors/hibob/index How to set up the HiBob connector, plus the actions and events that are available.
HiBob
Previewv4.0.1
129 actions · 28 events · 2 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Access to a Hibob Service User is required. You can manage Service Users in \[Hibob's \*Integrations\* settings\](https://ap... Connect your HiBob account using OAuth 2.0. You will be redirected to HiBob to authorize access and select which employe... Optionally, configure receiving Events for HiBob into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hibob/index.md for the full list. ## Events See https://docs.stackone.com/connectors/hibob/index.md for the full list. # HiBob Changelog Source: https://docs.stackone.com/connectors/hibob/changelog Release history for the HiBob connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `documentation` Moved 69 actions from preview to beta. `hibob_add_policy_type_reason_codes`, `hibob_cancel_position`, `hibob_create_bank_account`, `hibob_create_employment_history_entry`, `hibob_create_equity_grant`, `hibob_create_goals`, `hibob_create_key_results`, `hibob_create_position`, `hibob_create_position_budget`, `hibob_create_position_opening`, `hibob_create_salary_entry`, `hibob_create_training_record`, `hibob_create_variable_payment`, `hibob_delete_bank_account`, `hibob_delete_equity_grant`, `hibob_delete_goal`, `hibob_delete_key_result`, `hibob_delete_position_opening`, `hibob_get_all_company_lists`, `hibob_get_employee`, `hibob_get_goal_type_metadata`, `hibob_get_goals_metadata`, `hibob_get_job_ad`, `hibob_get_job_families`, `hibob_get_job_families_metadata`, `hibob_get_job_family_groups`, `hibob_get_job_family_groups_metadata`, `hibob_get_job_profiles_metadata`, `hibob_get_job_roles`, `hibob_get_job_roles_metadata`, `hibob_get_key_results_metadata`, `hibob_get_position_budget_metadata`, `hibob_get_position_openings_metadata`, `hibob_get_positions_metadata`, `hibob_get_report_download_url`, `hibob_import_attendance_data`, `hibob_list_bulk_deduction_history`, `hibob_list_bulk_dependents_history`, `hibob_list_bulk_entitlement_history`, `hibob_list_bulk_equities_history`, `hibob_list_bulk_right_to_work_history`, `hibob_list_bulk_variable_history`, `hibob_list_employee_bank_accounts`, `hibob_search_employees`, `hibob_search_goal_types`, `hibob_search_goals`, `hibob_search_job_ads`, `hibob_search_job_profiles`, `hibob_search_key_results`, `hibob_search_position_budgets`, `hibob_search_position_openings`, `hibob_update_bank_account`, `hibob_update_employment_entry`, `hibob_update_equity_grant`, `hibob_update_goal`, `hibob_update_goal_status`, `hibob_update_key_results_details`, `hibob_update_key_results_progress`, `hibob_update_position`, `hibob_update_position_budget` `breaking` `bug-fix` `new-actions` Removed employee-table fields that hiBob silently ignores, corrected several field value sets and cursor types, and added six company-wide history actions. `hibob_list_bulk_deduction_history`, `hibob_list_bulk_dependents_history`, `hibob_list_bulk_entitlement_history`, `hibob_list_bulk_equities_history`, `hibob_list_bulk_right_to_work_history`, `hibob_list_bulk_variable_history` `hibob_add_item_to_list`, `hibob_add_policy_type_reason_codes`, `hibob_adjust_time_off_balance`, `hibob_cancel_position`, `hibob_cancel_time_off_request`, `hibob_create_bank_account`, `hibob_create_custom_field`, `hibob_create_employee`, `hibob_create_employment_history_entry`, `hibob_create_equity_grant`, `hibob_create_goals`, `hibob_create_key_results`, `hibob_create_position`, `hibob_create_position_budget`, `hibob_create_salary_entry`, `hibob_create_time_off_request`, `hibob_create_training_record`, `hibob_create_variable_payment`, `hibob_create_work_history_entry`, `hibob_delete_custom_field`, `hibob_delete_document_from_confidential_folder`, `hibob_delete_document_from_custom_folder`, `hibob_delete_document_from_shared_folder`, `hibob_delete_employment_entry`, `hibob_delete_equity_grant`, `hibob_delete_goal`, `hibob_delete_list_item`, `hibob_delete_position_opening`, `hibob_delete_salary_entry`, `hibob_delete_training_record`, `hibob_delete_variable_payment`, `hibob_delete_work_history_entry`, `hibob_get_all_company_lists`, `hibob_get_company_list_by_name`, `hibob_get_employee`, `hibob_get_employee_avatar`, `hibob_get_employee_time_off_balance`, `hibob_get_job_families`, `hibob_get_job_family_groups`, `hibob_get_job_roles`, `hibob_get_payroll_history`, `hibob_get_report_download_url`, `hibob_get_time_off_request`, `hibob_get_whos_out`, `hibob_get_whos_out_today`, `hibob_import_attendance_data`, `hibob_invite_employee`, `hibob_list_bulk_employment_history`, `hibob_list_bulk_lifecycle_history`, `hibob_list_bulk_salaries_history`, `hibob_list_bulk_work_history`, `hibob_list_employee_documents`, `hibob_list_employee_employment_history`, `hibob_list_employee_equity_grants`, `hibob_list_employee_lifecycle_history`, `hibob_list_employee_salary_history`, `hibob_list_employee_tasks`, `hibob_list_employee_training_records`, `hibob_list_employee_variable_payments`, `hibob_list_employee_work_history`, `hibob_mark_task_complete`, `hibob_search_actual_payments`, `hibob_search_employees`, `hibob_search_job_ads`, `hibob_search_job_profiles`, `hibob_search_position_budgets`, `hibob_search_position_openings`, `hibob_search_positions`, `hibob_terminate_employee`, `hibob_update_bank_account`, `hibob_update_custom_field`, `hibob_update_employee`, `hibob_update_employee_email`, `hibob_update_employee_start_date`, `hibob_update_employment_entry`, `hibob_update_equity_grant`, `hibob_update_goal`, `hibob_update_goal_status`, `hibob_update_key_results_details`, `hibob_update_list_item`, `hibob_update_position`, `hibob_update_position_budget`, `hibob_update_position_opening`, `hibob_update_work_history_entry`, `hibob_upload_document_from_url_to_confidential`, `hibob_upload_document_from_url_to_custom_folder`, `hibob_upload_document_from_url_to_shared`, `hibob_upload_employee_avatar`, `hibob_upload_file_to_confidential_folder`, `hibob_upload_file_to_custom_folder`, `hibob_upload_file_to_shared_folder` `auth` Restored the Service User authentication option alongside OAuth 2.0, for customers who manage their own service user credentials. `hibob_add_item_to_list`, `hibob_add_policy_type_reason_codes`, `hibob_adjust_time_off_balance`, `hibob_cancel_position`, `hibob_cancel_time_off_request`, `hibob_create_bank_account`, `hibob_create_custom_field`, `hibob_create_employee`, `hibob_create_employment_history_entry`, `hibob_create_equity_grant`, `hibob_create_goals`, `hibob_create_key_results`, `hibob_create_position`, `hibob_create_position_budget`, `hibob_create_position_opening`, `hibob_create_salary_entry`, `hibob_create_time_off_request`, `hibob_create_training_record`, `hibob_create_variable_payment`, `hibob_create_work_history_entry`, `hibob_delete_bank_account`, `hibob_delete_custom_field`, `hibob_delete_document_from_confidential_folder`, `hibob_delete_document_from_custom_folder`, `hibob_delete_document_from_shared_folder`, `hibob_delete_employment_entry`, `hibob_delete_equity_grant`, `hibob_delete_goal`, `hibob_delete_key_result`, `hibob_delete_list_item`, `hibob_delete_position_opening`, `hibob_delete_salary_entry`, `hibob_delete_training_record`, `hibob_delete_variable_payment`, `hibob_delete_work_history_entry`, `hibob_get_all_company_lists`, `hibob_get_all_fields`, `hibob_get_all_policy_types`, `hibob_get_avatar_by_email`, `hibob_get_company_list_by_name`, `hibob_get_company_reports`, `hibob_get_document_folders_metadata`, `hibob_get_employee`, `hibob_get_employee_avatar`, `hibob_get_employee_time_off_balance`, `hibob_get_goal_type_metadata`, `hibob_get_goals_metadata`, `hibob_get_job_ad`, `hibob_get_job_families`, `hibob_get_job_families_metadata`, `hibob_get_job_family_groups`, `hibob_get_job_family_groups_metadata`, `hibob_get_job_profiles_metadata`, `hibob_get_job_roles`, `hibob_get_job_roles_metadata`, `hibob_get_key_results_metadata`, `hibob_get_onboarding_wizards`, `hibob_get_payroll_history`, `hibob_get_policy_details`, `hibob_get_policy_names`, `hibob_get_policy_type_details`, `hibob_get_policy_type_reason_codes`, `hibob_get_position_budget_metadata`, `hibob_get_position_openings_metadata`, `hibob_get_positions_metadata`, `hibob_get_report_download_url`, `hibob_get_time_off_changes`, `hibob_get_time_off_request`, `hibob_get_whos_out`, `hibob_get_whos_out_today`, `hibob_import_attendance_data`, `hibob_invite_employee`, `hibob_list_all_open_tasks`, `hibob_list_bulk_employment_history`, `hibob_list_bulk_lifecycle_history`, `hibob_list_bulk_salaries_history`, `hibob_list_bulk_work_history`, `hibob_list_employee_bank_accounts`, `hibob_list_employee_documents`, `hibob_list_employee_employment_history`, `hibob_list_employee_equity_grants`, `hibob_list_employee_lifecycle_history`, `hibob_list_employee_salary_history`, `hibob_list_employee_tasks`, `hibob_list_employee_training_records`, `hibob_list_employee_variable_payments`, `hibob_list_employee_work_history`, `hibob_mark_task_complete`, `hibob_search_actual_payments`, `hibob_search_employees`, `hibob_search_goal_types`, `hibob_search_goals`, `hibob_search_job_ads`, `hibob_search_job_profiles`, `hibob_search_key_results`, `hibob_search_position_budgets`, `hibob_search_position_openings`, `hibob_search_positions`, `hibob_terminate_employee`, `hibob_uninvite_employee`, `hibob_update_bank_account`, `hibob_update_custom_field`, `hibob_update_employee`, `hibob_update_employee_email`, `hibob_update_employee_start_date`, `hibob_update_employment_entry`, `hibob_update_equity_grant`, `hibob_update_goal`, `hibob_update_goal_status`, `hibob_update_key_results_details`, `hibob_update_key_results_progress`, `hibob_update_list_item`, `hibob_update_position`, `hibob_update_position_budget`, `hibob_update_position_opening`, `hibob_update_work_history_entry`, `hibob_upload_document_from_url_to_confidential`, `hibob_upload_document_from_url_to_custom_folder`, `hibob_upload_document_from_url_to_shared`, `hibob_upload_employee_avatar`, `hibob_upload_file_to_confidential_folder`, `hibob_upload_file_to_custom_folder`, `hibob_upload_file_to_shared_folder` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. `hibob_add_item_to_list`, `hibob_add_policy_type_reason_codes`, `hibob_adjust_time_off_balance`, `hibob_cancel_position`, `hibob_cancel_time_off_request`, `hibob_create_bank_account`, `hibob_create_custom_field`, `hibob_create_employee`, `hibob_create_employment_history_entry`, `hibob_create_equity_grant`, `hibob_create_goals`, `hibob_create_key_results`, `hibob_create_position`, `hibob_create_position_budget`, `hibob_create_position_opening`, `hibob_create_salary_entry`, `hibob_create_time_off_request`, `hibob_create_training_record`, `hibob_create_variable_payment`, `hibob_create_work_history_entry`, `hibob_delete_bank_account`, `hibob_delete_custom_field`, `hibob_delete_document_from_confidential_folder`, `hibob_delete_document_from_custom_folder`, `hibob_delete_document_from_shared_folder`, `hibob_delete_employment_entry`, `hibob_delete_equity_grant`, `hibob_delete_goal`, `hibob_delete_key_result`, `hibob_delete_list_item`, `hibob_delete_position_opening`, `hibob_delete_salary_entry`, `hibob_delete_training_record`, `hibob_delete_variable_payment`, `hibob_delete_work_history_entry`, `hibob_get_all_company_lists`, `hibob_get_all_fields`, `hibob_get_all_policy_types`, `hibob_get_avatar_by_email`, `hibob_get_company_list_by_name`, `hibob_get_company_reports`, `hibob_get_document_folders_metadata`, `hibob_get_employee`, `hibob_get_employee_avatar`, `hibob_get_employee_time_off_balance`, `hibob_get_goal_type_metadata`, `hibob_get_goals_metadata`, `hibob_get_job_ad`, `hibob_get_job_families`, `hibob_get_job_families_metadata`, `hibob_get_job_family_groups`, `hibob_get_job_family_groups_metadata`, `hibob_get_job_profiles_metadata`, `hibob_get_job_roles`, `hibob_get_job_roles_metadata`, `hibob_get_key_results_metadata`, `hibob_get_onboarding_wizards`, `hibob_get_payroll_history`, `hibob_get_policy_details`, `hibob_get_policy_names`, `hibob_get_policy_type_details`, `hibob_get_policy_type_reason_codes`, `hibob_get_position_budget_metadata`, `hibob_get_position_openings_metadata`, `hibob_get_positions_metadata`, `hibob_get_report_download_url`, `hibob_get_time_off_changes`, `hibob_get_time_off_request`, `hibob_get_whos_out`, `hibob_get_whos_out_today`, `hibob_import_attendance_data`, `hibob_invite_employee`, `hibob_list_all_open_tasks`, `hibob_list_bulk_employment_history`, `hibob_list_bulk_lifecycle_history`, `hibob_list_bulk_salaries_history`, `hibob_list_bulk_work_history`, `hibob_list_employee_bank_accounts`, `hibob_list_employee_documents`, `hibob_list_employee_employment_history`, `hibob_list_employee_equity_grants`, `hibob_list_employee_lifecycle_history`, `hibob_list_employee_salary_history`, `hibob_list_employee_tasks`, `hibob_list_employee_training_records`, `hibob_list_employee_variable_payments`, `hibob_list_employee_work_history`, `hibob_mark_task_complete`, `hibob_search_actual_payments`, `hibob_search_employees`, `hibob_search_goal_types`, `hibob_search_goals`, `hibob_search_job_ads`, `hibob_search_job_profiles`, `hibob_search_key_results`, `hibob_search_position_budgets`, `hibob_search_position_openings`, `hibob_search_positions`, `hibob_terminate_employee`, `hibob_uninvite_employee`, `hibob_update_bank_account`, `hibob_update_custom_field`, `hibob_update_employee`, `hibob_update_employee_email`, `hibob_update_employee_start_date`, `hibob_update_employment_entry`, `hibob_update_equity_grant`, `hibob_update_goal`, `hibob_update_goal_status`, `hibob_update_key_results_details`, `hibob_update_key_results_progress`, `hibob_update_list_item`, `hibob_update_position`, `hibob_update_position_budget`, `hibob_update_position_opening`, `hibob_update_work_history_entry`, `hibob_upload_document_from_url_to_confidential`, `hibob_upload_document_from_url_to_custom_folder`, `hibob_upload_document_from_url_to_shared`, `hibob_upload_employee_avatar`, `hibob_upload_file_to_confidential_folder`, `hibob_upload_file_to_custom_folder`, `hibob_upload_file_to_shared_folder` `new-feature` Enabled Data Sync on 13 list actions covering the full employee dataset, company fields, open tasks, reports, document folders, onboarding wizards and job catalog and workforce planning metadata. Synced collections can be searched and filtered without consuming HiBob API quota. `hibob_get_all_fields`, `hibob_get_company_reports`, `hibob_get_document_folders_metadata`, `hibob_get_job_families_metadata`, `hibob_get_job_family_groups_metadata`, `hibob_get_job_profiles_metadata`, `hibob_get_job_roles_metadata`, `hibob_get_onboarding_wizards`, `hibob_get_payroll_history`, `hibob_get_position_budget_metadata`, `hibob_get_position_openings_metadata`, `hibob_get_positions_metadata`, `hibob_list_all_open_tasks` `fix` `action-descriptions` Fixed payFrequency and variableType fields from hardcoded enums to company-list-based strings. Corrected contract value format (space not hyphen). Documented mandatory filter requirement for position search actions. Made effectiveDate required on adjust_time_off_balance. `hibob_adjust_time_off_balance`, `hibob_create_employment_history_entry`, `hibob_create_salary_entry`, `hibob_create_training_record`, `hibob_create_variable_payment`, `hibob_search_position_budgets`, `hibob_search_position_openings`, `hibob_search_positions`, `hibob_update_employment_entry` `fix` Marked search_goals action as preview due to Talent API Module subscription requirement. `hibob_search_goals` `downstream-change` `auth` Remove the Service User authentication option. OAuth 2.0 is now the only supported authentication method, per HiBob's requirement that integrations authenticate via OAuth. `hibob_add_item_to_list`, `hibob_add_policy_type_reason_codes`, `hibob_adjust_time_off_balance`, `hibob_cancel_position`, `hibob_cancel_time_off_request`, `hibob_create_bank_account`, `hibob_create_custom_field`, `hibob_create_employee`, `hibob_create_employment_history_entry`, `hibob_create_equity_grant`, `hibob_create_goals`, `hibob_create_key_results`, `hibob_create_position`, `hibob_create_position_budget`, `hibob_create_position_opening`, `hibob_create_salary_entry`, `hibob_create_time_off_request`, `hibob_create_training_record`, `hibob_create_variable_payment`, `hibob_create_work_history_entry`, `hibob_delete_bank_account`, `hibob_delete_custom_field`, `hibob_delete_document_from_confidential_folder`, `hibob_delete_document_from_custom_folder`, `hibob_delete_document_from_shared_folder`, `hibob_delete_employment_entry`, `hibob_delete_equity_grant`, `hibob_delete_goal`, `hibob_delete_key_result`, `hibob_delete_list_item`, `hibob_delete_position_opening`, `hibob_delete_salary_entry`, `hibob_delete_training_record`, `hibob_delete_variable_payment`, `hibob_delete_work_history_entry`, `hibob_get_all_company_lists`, `hibob_get_all_fields`, `hibob_get_all_policy_types`, `hibob_get_avatar_by_email`, `hibob_get_company_list_by_name`, `hibob_get_company_reports`, `hibob_get_document_folders_metadata`, `hibob_get_employee`, `hibob_get_employee_avatar`, `hibob_get_employee_time_off_balance`, `hibob_get_goal_type_metadata`, `hibob_get_goals_metadata`, `hibob_get_job_ad`, `hibob_get_job_families`, `hibob_get_job_families_metadata`, `hibob_get_job_family_groups`, `hibob_get_job_family_groups_metadata`, `hibob_get_job_profiles_metadata`, `hibob_get_job_roles`, `hibob_get_job_roles_metadata`, `hibob_get_key_results_metadata`, `hibob_get_onboarding_wizards`, `hibob_get_payroll_history`, `hibob_get_policy_details`, `hibob_get_policy_names`, `hibob_get_policy_type_details`, `hibob_get_policy_type_reason_codes`, `hibob_get_position_budget_metadata`, `hibob_get_position_openings_metadata`, `hibob_get_positions_metadata`, `hibob_get_report_download_url`, `hibob_get_time_off_changes`, `hibob_get_time_off_request`, `hibob_get_whos_out`, `hibob_get_whos_out_today`, `hibob_import_attendance_data`, `hibob_invite_employee`, `hibob_list_all_open_tasks`, `hibob_list_bulk_employment_history`, `hibob_list_bulk_lifecycle_history`, `hibob_list_bulk_salaries_history`, `hibob_list_bulk_work_history`, `hibob_list_employee_bank_accounts`, `hibob_list_employee_documents`, `hibob_list_employee_employment_history`, `hibob_list_employee_equity_grants`, `hibob_list_employee_lifecycle_history`, `hibob_list_employee_salary_history`, `hibob_list_employee_tasks`, `hibob_list_employee_training_records`, `hibob_list_employee_variable_payments`, `hibob_list_employee_work_history`, `hibob_mark_task_complete`, `hibob_search_actual_payments`, `hibob_search_employees`, `hibob_search_goal_types`, `hibob_search_goals`, `hibob_search_job_ads`, `hibob_search_job_profiles`, `hibob_search_key_results`, `hibob_search_position_budgets`, `hibob_search_position_openings`, `hibob_search_positions`, `hibob_terminate_employee`, `hibob_uninvite_employee`, `hibob_update_bank_account`, `hibob_update_custom_field`, `hibob_update_employee`, `hibob_update_employee_email`, `hibob_update_employee_start_date`, `hibob_update_employment_entry`, `hibob_update_equity_grant`, `hibob_update_goal`, `hibob_update_goal_status`, `hibob_update_key_results_details`, `hibob_update_key_results_progress`, `hibob_update_list_item`, `hibob_update_position`, `hibob_update_position_budget`, `hibob_update_position_opening`, `hibob_update_work_history_entry`, `hibob_upload_document_from_url_to_confidential`, `hibob_upload_document_from_url_to_custom_folder`, `hibob_upload_document_from_url_to_shared`, `hibob_upload_employee_avatar`, `hibob_upload_file_to_confidential_folder`, `hibob_upload_file_to_custom_folder`, `hibob_upload_file_to_shared_folder` `downstream-change` `auth` Send partner-attribution headers on all API calls, with X-Global-Partner-Id for OAuth connections and Partner-token for Service User connections. `hibob_add_item_to_list`, `hibob_add_policy_type_reason_codes`, `hibob_adjust_time_off_balance`, `hibob_cancel_position`, `hibob_cancel_time_off_request`, `hibob_create_bank_account`, `hibob_create_custom_field`, `hibob_create_employee`, `hibob_create_employment_history_entry`, `hibob_create_equity_grant`, `hibob_create_goals`, `hibob_create_key_results`, `hibob_create_position`, `hibob_create_position_budget`, `hibob_create_position_opening`, `hibob_create_salary_entry`, `hibob_create_time_off_request`, `hibob_create_training_record`, `hibob_create_variable_payment`, `hibob_create_work_history_entry`, `hibob_delete_bank_account`, `hibob_delete_custom_field`, `hibob_delete_document_from_confidential_folder`, `hibob_delete_document_from_custom_folder`, `hibob_delete_document_from_shared_folder`, `hibob_delete_employment_entry`, `hibob_delete_equity_grant`, `hibob_delete_goal`, `hibob_delete_key_result`, `hibob_delete_list_item`, `hibob_delete_position_opening`, `hibob_delete_salary_entry`, `hibob_delete_training_record`, `hibob_delete_variable_payment`, `hibob_delete_work_history_entry`, `hibob_get_all_company_lists`, `hibob_get_all_fields`, `hibob_get_all_policy_types`, `hibob_get_avatar_by_email`, `hibob_get_company_list_by_name`, `hibob_get_company_reports`, `hibob_get_document_folders_metadata`, `hibob_get_employee`, `hibob_get_employee_avatar`, `hibob_get_employee_time_off_balance`, `hibob_get_goal_type_metadata`, `hibob_get_goals_metadata`, `hibob_get_job_ad`, `hibob_get_job_families`, `hibob_get_job_families_metadata`, `hibob_get_job_family_groups`, `hibob_get_job_family_groups_metadata`, `hibob_get_job_profiles_metadata`, `hibob_get_job_roles`, `hibob_get_job_roles_metadata`, `hibob_get_key_results_metadata`, `hibob_get_onboarding_wizards`, `hibob_get_payroll_history`, `hibob_get_policy_details`, `hibob_get_policy_names`, `hibob_get_policy_type_details`, `hibob_get_policy_type_reason_codes`, `hibob_get_position_budget_metadata`, `hibob_get_position_openings_metadata`, `hibob_get_positions_metadata`, `hibob_get_report_download_url`, `hibob_get_time_off_changes`, `hibob_get_time_off_request`, `hibob_get_whos_out`, `hibob_get_whos_out_today`, `hibob_import_attendance_data`, `hibob_invite_employee`, `hibob_list_all_open_tasks`, `hibob_list_bulk_employment_history`, `hibob_list_bulk_lifecycle_history`, `hibob_list_bulk_salaries_history`, `hibob_list_bulk_work_history`, `hibob_list_employee_bank_accounts`, `hibob_list_employee_documents`, `hibob_list_employee_employment_history`, `hibob_list_employee_equity_grants`, `hibob_list_employee_lifecycle_history`, `hibob_list_employee_salary_history`, `hibob_list_employee_tasks`, `hibob_list_employee_training_records`, `hibob_list_employee_variable_payments`, `hibob_list_employee_work_history`, `hibob_mark_task_complete`, `hibob_search_actual_payments`, `hibob_search_employees`, `hibob_search_goal_types`, `hibob_search_goals`, `hibob_search_job_ads`, `hibob_search_job_profiles`, `hibob_search_key_results`, `hibob_search_position_budgets`, `hibob_search_position_openings`, `hibob_search_positions`, `hibob_terminate_employee`, `hibob_uninvite_employee`, `hibob_update_bank_account`, `hibob_update_custom_field`, `hibob_update_employee`, `hibob_update_employee_email`, `hibob_update_employee_start_date`, `hibob_update_employment_entry`, `hibob_update_equity_grant`, `hibob_update_goal`, `hibob_update_goal_status`, `hibob_update_key_results_details`, `hibob_update_key_results_progress`, `hibob_update_list_item`, `hibob_update_position`, `hibob_update_position_budget`, `hibob_update_position_opening`, `hibob_update_work_history_entry`, `hibob_upload_document_from_url_to_confidential`, `hibob_upload_document_from_url_to_custom_folder`, `hibob_upload_document_from_url_to_shared`, `hibob_upload_employee_avatar`, `hibob_upload_file_to_confidential_folder`, `hibob_upload_file_to_custom_folder`, `hibob_upload_file_to_shared_folder` `guide-improvement` Improved guide visibility for environment selection — extracted inline bullet into dedicated "Sandbox vs Production Environment" section with sub-steps. # HighLevel Source: https://docs.stackone.com/connectors/highlevel/index How to set up the HighLevel connector, plus the actions that are available.
HighLevel
Previewv0.1.0
12 actions · 2 auth methods
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a HighLevel Marketplace app. An agency install reads every user and sub-account in the agency; a sub-account in... No app registration required. An agency token with the agency id reads every user and sub-account in the agency; a sub-a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/highlevel/index.md for the full list. # HighLevel Changelog Source: https://docs.stackone.com/connectors/highlevel/changelog Release history for the HighLevel connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` New HighLevel connector for reviewing who can access an agency or its sub-accounts, with their roles. # HiPeople Source: https://docs.stackone.com/connectors/hipeople/index How to set up the HiPeople connector, plus the actions that are available.
HiPeople
v1.1.0
3 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). HiPeople authenticates every REST request with a public/secret API key pair sent as the \`X-API-Key\` and \`X-API-Secret\` h... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hipeople/index.md for the full list. # HiPeople Changelog Source: https://docs.stackone.com/connectors/hipeople/changelog Release history for the HiPeople connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to the list open job roles action so open job roles can be periodically synced into StackOne by full refresh, with paging handled automatically. `hipeople_list_open_job_roles` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `guide-changes` `description-fix` Clarified the region-selection guide step with a login-page screenshot and corrected wording (region is chosen from the top-right dropdown, not a per-region URL), and tightened the Get Assessment Report description to state it returns only org-wide aggregate totals — no per-candidate/per-reference records or free-text. `hipeople_get_assessment_report` `new-actions` Initial HiPeople connector — list open job roles, view role candidates with profile and reference data, and retrieve assessment reports. # Hive Source: https://docs.stackone.com/connectors/hive/index How to set up the Hive connector, plus the actions and events that are available.
Hive
v2.2.1
29 actions · 7 events · 1 auth method
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. Hive issues a personal API key to each user, and it inherits that user's own workspace per... Optionally, configure receiving Events for Hive into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hive/index.md for the full list. ## Events See https://docs.stackone.com/connectors/hive/index.md for the full list. # Hive Changelog Source: https://docs.stackone.com/connectors/hive/changelog Release history for the Hive connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists now read members from up to 150 workspaces instead of the first 10, and user and group lists return an error above their limits instead of a partial list. `hive_unified_list_groups`, `hive_unified_list_users` `new-feature` `guide` Added webhook events for Hive actions (tasks), projects, form submissions and chat messages. StackOne creates the Hive webhooks in the workspace named by the new optional Workspace ID field when the account connects, and deletes them on disconnect. Updated the connection guide to explain where to find the Workspace ID and added a webhook setup guide. `new-actions` `bug-fix` Added a task search that finds actions by title, and added support for archiving tasks and projects, setting a task's status and milestone flag, and setting a project's start and finish dates. `hive_search_actions` `hive_create_action`, `hive_create_action_comment`, `hive_create_label`, `hive_create_project`, `hive_delete_action`, `hive_delete_label`, `hive_delete_project`, `hive_get_action`, `hive_get_label`, `hive_get_project`, `hive_list_action_comments`, `hive_list_actions`, `hive_list_labels`, `hive_list_projects`, `hive_list_workspace_users`, `hive_list_workspaces`, `hive_update_action`, `hive_update_label`, `hive_update_project` `breaking` `downstream-change` `bug-fix` Moved every action to the documented Hive v2 API, which adds forward cursor pagination, sorting and filtering to the list actions and returns complete workspace member lists. List actions now return the v2 edges and pageInfo envelope, and the get workspace action has been withdrawn because Hive serves workspaces as a collection only. `hive_get_workspace` `hive_create_action`, `hive_create_action_comment`, `hive_create_label`, `hive_create_project`, `hive_delete_action`, `hive_delete_label`, `hive_delete_project`, `hive_get_action`, `hive_get_label`, `hive_get_project`, `hive_list_action_comments`, `hive_list_actions`, `hive_list_labels`, `hive_list_projects`, `hive_list_workspace_users`, `hive_list_workspaces`, `hive_unified_get_group`, `hive_unified_get_role`, `hive_unified_get_user`, `hive_unified_list_groups`, `hive_unified_list_roles`, `hive_update_action`, `hive_update_label`, `hive_update_project` `new-actions` Added unified IAM support for users, roles, groups, organizations, and credentials. # Homerun Source: https://docs.stackone.com/connectors/homerun/index How to set up the Homerun connector, plus the actions that are available.
Homerun
Betav1.1.0
11 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an API key generated from the Integrations Page in the Homerun App. Scopes are assigned at key creation and can... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/homerun/index.md for the full list. # Homerun Changelog Source: https://docs.stackone.com/connectors/homerun/changelog Release history for the Homerun connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for job applications and vacancies, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. # Honeycomb Source: https://docs.stackone.com/connectors/honeycomb/index How to set up the Honeycomb connector, plus the actions and events that are available.
Honeycomb
v2.2.0
79 actions · 8 events · 2 auth methods
Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use this auth type for managing Honeycomb resources (boards, triggers, datasets, columns, SLOs, markers). Note: This is... Use this auth type for sending telemetry data (events, traces, logs) to Honeycomb. Note: Ingest keys can ONLY send event... Optionally, configure receiving Events for Honeycomb into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/honeycomb/index.md for the full list. ## Events See https://docs.stackone.com/connectors/honeycomb/index.md for the full list. # Honeycomb Changelog Source: https://docs.stackone.com/connectors/honeycomb/changelog Release history for the Honeycomb connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added webhook event support for Honeycomb alerts, covering triggers, SLO burn alerts, and anomaly detection. `honeycomb_create_burn_alert`, `honeycomb_create_query_result`, `honeycomb_create_recipient_slack`, `honeycomb_create_slo`, `honeycomb_delete_burn_alert`, `honeycomb_delete_slo`, `honeycomb_get_burn_alert`, `honeycomb_get_query_result`, `honeycomb_get_slo`, `honeycomb_get_slo_hourly_counts_history`, `honeycomb_get_slo_realtime_counts`, `honeycomb_list_burn_alerts`, `honeycomb_list_slos`, `honeycomb_update_burn_alert`, `honeycomb_update_recipient_slack`, `honeycomb_update_slo` `data-sync` Added DataSync support for List Boards, List Datasets, and List Recipients actions. `honeycomb_list_boards`, `honeycomb_list_datasets`, `honeycomb_list_recipients` `bug-fix` Removed non-functional in/not-in filter operations from board view actions that required unsupported array values. `honeycomb_create_board_view`, `honeycomb_update_board_view` `bug-fix` Fixed board view filter value type from object to string for create and update board view actions. `honeycomb_create_board_view`, `honeycomb_update_board_view` `bug-fix` Fixed board view filter value type to accept arrays for in/not-in operators, and improved action descriptions for triggers, markers, columns, and webhook recipients. `honeycomb_create_board_view`, `honeycomb_create_marker`, `honeycomb_delete_trigger`, `honeycomb_get_trigger`, `honeycomb_update_board_view`, `honeycomb_update_column`, `honeycomb_update_marker`, `honeycomb_update_recipient_webhook`, `honeycomb_update_trigger` `breaking-change` Fixed X-Honeycomb-Samplerate header type from number to string for agent compatibility. `honeycomb_create_event` `breaking-change` Migrated to authRequirements. Actions are now restricted to their compatible auth type (Configuration API Key or Ingest API Key). # Hootsuite Source: https://docs.stackone.com/connectors/hootsuite/index How to set up the Hootsuite connector, plus the actions that are available.
Hootsuite
Previewv1.3.0
52 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Hootsuite Developer Portal app with redirect URI configured. Refresh tokens are single-use and rotated on eve... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hootsuite/index.md for the full list. # Hootsuite Changelog Source: https://docs.stackone.com/connectors/hootsuite/changelog Release history for the Hootsuite connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Listing users now returns each user's email, name, status and dates instead of only ids. `hootsuite_unified_get_user`, `hootsuite_unified_list_users` `bug-fix` Updated the OAuth 2.0 connection guide to match the current Hootsuite developer area, with screenshots, the developer program registration step and a note that no extra app scopes are needed. `bug-fix` Fixed the social profile filter on list messages and clarified what the social profile, team, member and SCIM actions accept and return. `hootsuite_get_team`, `hootsuite_list_messages`, `hootsuite_list_my_social_profiles`, `hootsuite_list_organization_member_teams`, `hootsuite_list_organization_members`, `hootsuite_list_organization_teams`, `hootsuite_list_social_profiles`, `hootsuite_scim_create_group`, `hootsuite_scim_list_groups`, `hootsuite_scim_modify_user`, `hootsuite_scim_replace_user` `data-sync` `new-feature` Added DataSync support to six list actions: social profiles, the authenticated member's social profiles and organizations, and the unified user, group and organization lists. Hootsuite exposes no updated-since filter on any of them, so all six refresh in full. `hootsuite_list_my_organizations`, `hootsuite_list_my_social_profiles`, `hootsuite_list_social_profiles`, `hootsuite_unified_list_groups`, `hootsuite_unified_list_organizations`, `hootsuite_unified_list_users` `new-actions` Added unified IAM actions (users, groups, organizations, credentials) mapped from Hootsuite's REST 1.0 members, teams, and organizations endpoints. Unified user lists auto-resolve the organization when the connection sees exactly one, and ask for it explicitly when several are visible. # Hotjar Source: https://docs.stackone.com/connectors/hotjar/index How to set up the Hotjar connector, plus the actions that are available.
Hotjar
Betav1.0.0
4 actions · 1 auth method
Surveys
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 Client Credentials flow. Hotjar API access requires a Scale plan (Observe Scale or Ask Scale). API keys auto-e... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hotjar/index.md for the full list. # HR Cloud Source: https://docs.stackone.com/connectors/hrcloud/index How to set up the HR Cloud connector, plus the actions that are available.
HR Cloud
Previewv2.0.0
64 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). HR Cloud authenticates each request with two custom HTTP headers — Customer\_Key and Customer\_Secret — both minted in the... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hrcloud/index.md for the full list. # HR Cloud Changelog Source: https://docs.stackone.com/connectors/hrcloud/changelog Release history for the HR Cloud connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `data-sync` `bug-fix` Breaking: field selection is no longer offered on single-record lookups, where HR Cloud ignored it - use the matching list action with a filter instead; and new records must be created as Active, because creating one directly as Inactive left it unreachable and holding its code. Also adds incremental sync so employees, departments, divisions, locations, positions, tasks, time off and several history collections can fetch only what changed since the last run, corrects the employee reference on Create Rehire History and Create Employment Status History so those records can be created, and adds salary and bonus on employee creation plus an Identifier option on Upsert Applicant and Upsert Time Off Request. # HR Partner Source: https://docs.stackone.com/connectors/hrpartner/index How to set up the HR Partner connector, plus the actions that are available.
HR Partner
v1.1.0
48 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using an API Key from your HR Partner account. Requires admin access to the Integrations settings. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hrpartner/index.md for the full list. # HR Partner Changelog Source: https://docs.stackone.com/connectors/hrpartner/changelog Release history for the HR Partner connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync capability to 24 list actions enabling full-refresh data synchronisation across employees, absences, goals, notes, positions, training, benefits, skills, and more. `hrpartner_get_all_applicants`, `hrpartner_get_all_checklists`, `hrpartner_get_all_employees`, `hrpartner_get_all_goals`, `hrpartner_get_all_job_listings`, `hrpartner_get_all_projects_or_activities`, `hrpartner_get_all_reminders`, `hrpartner_get_all_timesheets`, `hrpartner_get_application_stage_tracking`, `hrpartner_list_absences`, `hrpartner_list_assets`, `hrpartner_list_attachments`, `hrpartner_list_benefits`, `hrpartner_list_dependents`, `hrpartner_list_education`, `hrpartner_list_employee_contacts`, `hrpartner_list_grievances`, `hrpartner_list_interviews`, `hrpartner_list_notes`, `hrpartner_list_positions`, `hrpartner_list_renewables`, `hrpartner_list_reviews`, `hrpartner_list_skills`, `hrpartner_list_training` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Standardized action category capitalization for more consistent portal filters. `hrpartner_add_or_update_applicant`, `hrpartner_add_or_update_application`, `hrpartner_add_timesheet_entry`, `hrpartner_delete_reminder`, `hrpartner_get_a_specific_employee`, `hrpartner_get_a_specific_leave_request`, `hrpartner_get_all_applicants`, `hrpartner_get_all_applications`, `hrpartner_get_all_checklists`, `hrpartner_get_all_employees`, `hrpartner_get_all_expense_claims`, `hrpartner_get_all_goals`, `hrpartner_get_all_job_listings`, `hrpartner_get_all_leave_balances`, `hrpartner_get_all_leave_requests`, `hrpartner_get_all_projects_or_activities`, `hrpartner_get_all_reminders`, `hrpartner_get_all_timesheets`, `hrpartner_get_application_stage_tracking`, `hrpartner_get_company`, `hrpartner_get_library_categories`, `hrpartner_get_library_documents`, `hrpartner_get_single_timesheet`, `hrpartner_get_specific_applicant`, `hrpartner_get_specific_application`, `hrpartner_get_specific_job_listing`, `hrpartner_get_specific_reminder`, `hrpartner_list_absences`, `hrpartner_list_anniversaries`, `hrpartner_list_assets`, `hrpartner_list_attachments`, `hrpartner_list_benefits`, `hrpartner_list_birthdays`, `hrpartner_list_dependents`, `hrpartner_list_education`, `hrpartner_list_employee_addresses`, `hrpartner_list_employee_contacts`, `hrpartner_list_grievances`, `hrpartner_list_interviews`, `hrpartner_list_lookups`, `hrpartner_list_notes`, `hrpartner_list_positions`, `hrpartner_list_renewables`, `hrpartner_list_reviews`, `hrpartner_list_skills`, `hrpartner_list_training`, `hrpartner_update_or_add_employee`, `hrpartner_update_reminder` `action-descriptions` Added BEHAVIOUR note for list_employee_contacts search filter incompatibility, improved get_all_applicants description to disambiguate from stage tracking. `hrpartner_get_all_applicants`, `hrpartner_list_employee_contacts` `guide-fix` Clarified the API Key connection guide: how to find your subdomain, enabling API access and resetting the token, and that the API Key field takes HR Partner's API Token. `improved-descriptions` Documented provider behaviour: get_all_employees returns 404 when the search filter matches no employees (instead of an empty array). `hrpartner_get_all_employees` `new-actions` Initial connector release with actions covering employees, absences, positions, goals, reviews, training, leave requests, leave balances, recruitment, timesheets, and more. # HubSpot Source: https://docs.stackone.com/connectors/hubspot/index How to set up the HubSpot connector, plus the actions that are available.
HubSpot
v3.2.1
90 actions · 2 auth methods
CRM IAM Customer Support
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges in your Hubspot account. Uses a static access token from a HubSpot Private App. Authenticates at the account level, not on behalf of a specific u... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/hubspot/index.md for the full list. # HubSpot Changelog Source: https://docs.stackone.com/connectors/hubspot/changelog Release history for the HubSpot connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `guide` Added per-auth-type scope requirements (authRequirements) to every action, so OAuth and Private App connections each declare the correct scopes — including granular ticket scopes for Private Apps, the correct crm.schemas.custom.write scope for custom object schema changes, and product, line item, quote, and lead scopes for the generic CRM object actions. Corrected the OAuth and Private App connection guides to match HubSpot's current portal. `hubspot_add_campaign_asset`, `hubspot_batch_create_associations`, `hubspot_batch_create_companies`, `hubspot_batch_create_contacts`, `hubspot_batch_create_deals`, `hubspot_batch_read_associations`, `hubspot_batch_update_companies`, `hubspot_batch_update_contacts`, `hubspot_batch_update_deals`, `hubspot_clone_marketing_email`, `hubspot_create_association`, `hubspot_create_campaign`, `hubspot_create_company`, `hubspot_create_contact`, `hubspot_create_crm_object`, `hubspot_create_custom_object_association`, `hubspot_create_custom_object_schema`, `hubspot_create_deal`, `hubspot_create_deal_pipeline`, `hubspot_create_deal_pipeline_stage`, `hubspot_create_marketing_email`, `hubspot_create_ticket`, `hubspot_delete_association`, `hubspot_delete_campaign`, `hubspot_delete_company`, `hubspot_delete_contact`, `hubspot_delete_crm_object`, `hubspot_delete_custom_object_association`, `hubspot_delete_custom_object_schema`, `hubspot_delete_deal`, `hubspot_delete_marketing_email`, `hubspot_delete_ticket`, `hubspot_get_account_details`, `hubspot_get_campaign`, `hubspot_get_company`, `hubspot_get_contact`, `hubspot_get_crm_object`, `hubspot_get_custom_object_schema`, `hubspot_get_deal`, `hubspot_get_deal_pipeline`, `hubspot_get_deal_pipeline_stage`, `hubspot_get_form`, `hubspot_get_marketing_email`, `hubspot_get_object_properties`, `hubspot_get_owner`, `hubspot_get_ticket`, `hubspot_get_ticket_pipeline`, `hubspot_get_ticket_pipeline_stage`, `hubspot_list_associations`, `hubspot_list_campaign_assets`, `hubspot_list_campaigns`, `hubspot_list_companies`, `hubspot_list_contacts`, `hubspot_list_crm_objects`, `hubspot_list_custom_object_schemas`, `hubspot_list_deal_pipeline_stages`, `hubspot_list_deal_pipelines`, `hubspot_list_deals`, `hubspot_list_form_submissions`, `hubspot_list_forms`, `hubspot_list_marketing_emails`, `hubspot_list_owners`, `hubspot_list_ticket_pipeline_stages`, `hubspot_list_ticket_pipelines`, `hubspot_list_tickets`, `hubspot_publish_marketing_email`, `hubspot_remove_campaign_asset`, `hubspot_search_companies`, `hubspot_search_contacts`, `hubspot_search_deals`, `hubspot_search_tickets`, `hubspot_unified_get_group`, `hubspot_unified_get_me`, `hubspot_unified_get_organization`, `hubspot_unified_get_role`, `hubspot_unified_get_user`, `hubspot_unified_list_groups`, `hubspot_unified_list_organizations`, `hubspot_unified_list_roles`, `hubspot_unified_list_users`, `hubspot_update_campaign`, `hubspot_update_company`, `hubspot_update_contact`, `hubspot_update_crm_object`, `hubspot_update_custom_object_schema`, `hubspot_update_deal`, `hubspot_update_deal_pipeline`, `hubspot_update_deal_pipeline_stage`, `hubspot_update_marketing_email`, `hubspot_update_ticket` `improvement` `new-feature` Added DataSync support to 15 list actions (contacts, companies, deals, tickets, campaigns, marketing emails, forms, owners, deal and ticket pipelines, custom object schemas, and unified users, roles, groups, and organizations) so their records can be periodically synced into StackOne and kept up to date. Added optional pagination inputs (limit and after) to List Owners. `hubspot_list_campaigns`, `hubspot_list_companies`, `hubspot_list_contacts`, `hubspot_list_custom_object_schemas`, `hubspot_list_deal_pipelines`, `hubspot_list_deals`, `hubspot_list_forms`, `hubspot_list_marketing_emails`, `hubspot_list_owners`, `hubspot_list_ticket_pipelines`, `hubspot_list_tickets`, `hubspot_unified_list_groups`, `hubspot_unified_list_organizations`, `hubspot_unified_list_roles`, `hubspot_unified_list_users` `bug-fix` `improvement` Added the IN, NOT_IN, and BETWEEN filter operators to the Search Contacts, Search Deals, and Search Tickets actions (Search Companies already supported them). IN/NOT_IN match a property against a list of values via the new `values` array, and BETWEEN matches a range via `value` (lower bound) and the new `highValue` (upper bound) — e.g. filtering by a list of hs_object_id values, which previously returned no results. Also raised the search page-size limit to 200 and documented HubSpot's 10,000-record search ceiling, and enriched the search filter documentation across all object types (filter-group limits, epoch-millisecond date values, IN/NOT_IN lowercase-string rule, CONTAINS_TOKEN wildcard support, and single-sort behavior). Fixed Search Contacts, Search Deals, and Search Tickets so a criteria-less search (empty body) returns all records instead of failing with HTTP 415 (Search Companies already behaved this way). `hubspot_search_companies`, `hubspot_search_contacts`, `hubspot_search_deals`, `hubspot_search_tickets` `breaking-change` `bug-fix` `improvement` Breaking: company, CRM-object, and deal-pipeline/stage action responses are now wrapped under a top-level `data` key for a consistent response shape. Also fixed empty-body company searches (no longer error) and empty deal-pipeline updates (now rejected up front with a clear message), typed deal-stage metadata so `probability` is enforced, and removed the optional custom pipeline/stage ID inputs from create-deal-pipeline (HubSpot now assigns these automatically) to avoid intermittent provider errors. `hubspot_batch_create_companies`, `hubspot_batch_update_companies`, `hubspot_create_company`, `hubspot_create_crm_object`, `hubspot_create_deal_pipeline`, `hubspot_create_deal_pipeline_stage`, `hubspot_delete_company`, `hubspot_delete_crm_object`, `hubspot_get_company`, `hubspot_get_crm_object`, `hubspot_get_deal_pipeline`, `hubspot_get_deal_pipeline_stage`, `hubspot_list_companies`, `hubspot_list_crm_objects`, `hubspot_list_deal_pipeline_stages`, `hubspot_list_deal_pipelines`, `hubspot_search_companies`, `hubspot_update_company`, `hubspot_update_crm_object`, `hubspot_update_deal_pipeline`, `hubspot_update_deal_pipeline_stage` `bug-fix` `improvement` Fixed group, organization, and role lookups returning empty results instead of not-found errors. `hubspot_unified_get_group`, `hubspot_unified_get_organization`, `hubspot_unified_get_role` `bug-fix` Fixed IAM actions — get-by-id now returns an empty record instead of failing, role and group scopes carry the connection's real portal id so they match the organization record, and nested role and group type fields return the full value and source value pair. `hubspot_unified_get_group`, `hubspot_unified_get_me`, `hubspot_unified_get_organization`, `hubspot_unified_get_role`, `hubspot_unified_get_user`, `hubspot_unified_list_groups`, `hubspot_unified_list_organizations`, `hubspot_unified_list_roles`, `hubspot_unified_list_users` `new-actions` Added unified IAM actions for users, groups, organizations, roles, and credentials. # Hugging Face Source: https://docs.stackone.com/connectors/huggingface/index How to set up the Hugging Face connector, plus the actions that are available.
Hugging Face
Previewv0.1.0
126 actions · 2 auth methods
AI Productivity Developer Tools IAM Storage Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. A token created from account settings, carrying either blanket read/write access or fine-g... Acts on behalf of a signed-in Hugging Face user with per-scope consent. Requires registering an OAuth application. Acces... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/huggingface/index.md for the full list. # Hugging Face Changelog Source: https://docs.stackone.com/connectors/huggingface/changelog Release history for the Hugging Face connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Added the Hugging Face connector with 126 actions covering models, datasets, Spaces, collections, discussions and pull requests, repositories, users and organizations, including committing files to repositories. Supports User Access Token and OAuth 2.0 authentication. # Humaans Source: https://docs.stackone.com/connectors/humaans/index How to set up the Humaans connector, plus the actions that are available.
Humaans
v1.1.0
117 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API access token in Humaans and use it for API requests. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/humaans/index.md for the full list. # Humaans Changelog Source: https://docs.stackone.com/connectors/humaans/changelog Release history for the Humaans connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 25 list actions. 14 of them sync incrementally via a new optional updatedAt[$gt] filter; the rest refresh in full. # incident.io Source: https://docs.stackone.com/connectors/incident/index How to set up the incident.io connector, plus the actions that are available.
incident.io
Betav0.2.0
174 actions · 1 auth method
Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. The key's roles are fixed when it is created in the incident.io dashboard and cannot be ch... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/incident/index.md for the full list. # incident.io Changelog Source: https://docs.stackone.com/connectors/incident/changelog Release history for the incident.io connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `action-fix` All actions are now marked beta while end-to-end testing against a live incident.io account completes. `new-actions` Initial action mappings for incident.io # InfoSec Source: https://docs.stackone.com/connectors/infosec/index How to set up the InfoSec connector, plus the actions that are available.
InfoSec
Previewv1.2.0
34 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Instructions for generating an API Key in InfoSec IQ. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/infosec/index.md for the full list. # InfoSec Changelog Source: https://docs.stackone.com/connectors/infosec/changelog Release history for the InfoSec connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added DataSync support for 11 list actions, with incremental sync on learners. # Insight Global Source: https://docs.stackone.com/connectors/insightglobal/index How to set up the Insight Global connector, plus the actions that are available.
Insight Global
v1.0.0
2 actions · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 client credentials flow. Requires a Client Key and Client Secret provided by Insight Global duri... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/insightglobal/index.md for the full list. # Insightly Source: https://docs.stackone.com/connectors/insightly/index How to set up the Insightly connector, plus the actions and events that are available.
Insightly
Previewv2.0.0
74 actions · 2 events · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses HTTP Basic auth with the personal API key as the username and an empty password. The pod (e.g. na1, eu1) is part of... Optionally, configure receiving Events for Insightly into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/insightly/index.md for the full list. ## Events See https://docs.stackone.com/connectors/insightly/index.md for the full list. # Insightly Changelog Source: https://docs.stackone.com/connectors/insightly/changelog Release history for the Insightly connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `new-events` `data-sync` `guide` `downstream-change` `bug-fix` Actions renamed to match Insightly's own verbs (list_* to get_*, create_* to add_*, search_* to get_*_filtered) — existing action ids will no longer resolve. New actions add_lead_source, add_lead_status, add_team, get_teams, get_custom_fields, get_emails and get_milestones are the discovery paths for TEAM_ID, CUSTOMFIELDS, MILESTONE_ID and CATEGORY_ID; these fields now say what an empty result means rather than leaving callers to guess an id and hit a bare 400. Restored the record-visibility fields (VISIBLE_TO, VISIBLE_TEAM_ID, PUBLICLY_VISIBLE); VISIBLE_TO no longer offers INDIVIDUALS, which v3.1 rejects. Update actions document partial-update semantics and no longer mark optional fields as required. BID_TYPE and FORECAST_CLOSE_DATE document undisclosed provider constraints that previously failed silently. Added webhooks — Insightly has no subscription API, so events come from a Workflow Automation webhook action pointed at the connection's Native Webhook URL, covering created, updated and deleted for six record types; a workflow whose criteria has no filter rows fires only on creation, so update events need one. Data Sync is available on 22 list actions as full refreshes, since Insightly accepts an updated-since filter only on its Search endpoints. The API key and webhook connection guides were rebuilt from the live portal with screenshots. # Instagram Source: https://docs.stackone.com/connectors/instagram/index How to set up the Instagram connector, plus the actions that are available.
Instagram
Previewv1.1.0
53 actions · 2 auth methods
Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Simpler setup for content publishing, comments, and messaging. Requires a professional Instagram account. Provides additional access to insights and shopping features. Requires Instagram account linked to a Facebook Page. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/instagram/index.md for the full list. # Instagram Changelog Source: https://docs.stackone.com/connectors/instagram/changelog Release history for the Instagram connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added unified_get_me, returning credentials information for the connected Instagram Business/Creator account (both Instagram Login and Facebook Login auth flows). # intelliHR Source: https://docs.stackone.com/connectors/intellihr/index How to set up the intelliHR connector, plus the actions that are available.
intelliHR
Betav0.2.0
76 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). intelliHR uses a static Bearer API key. Generate an Access Key in the intelliHR portal under Settings > Public API Acces... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/intellihr/index.md for the full list. # intelliHR Changelog Source: https://docs.stackone.com/connectors/intellihr/changelog Release history for the intelliHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for people, jobs, business entities, business units, locations, position titles, pay grades, employment conditions, qualifications, qualification library items, trainings, skills, skill disciplines and users, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the intelliHR API exposes no updated-since filter a sync can use. `intellihr_list_business_entities`, `intellihr_list_business_units`, `intellihr_list_employment_conditions`, `intellihr_list_jobs`, `intellihr_list_locations`, `intellihr_list_pay_grades`, `intellihr_list_people`, `intellihr_list_position_titles`, `intellihr_list_qualification_instances`, `intellihr_list_qualification_library_items`, `intellihr_list_skill_disciplines`, `intellihr_list_skills`, `intellihr_list_trainings`, `intellihr_list_users` `new-actions` Initial intelliHR connector — 72 Core HR actions across 19 resources (People, Jobs, org structure, compensation, qualifications, trainings, skills) with API key authentication. # Intercom Source: https://docs.stackone.com/connectors/intercom/index How to set up the Intercom connector, plus the actions and events that are available.
Intercom
v2.0.2
113 actions · 117 events · 2 auth methods
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 by creating an Intercom app in the Developer Hub. The steps in this guide require Admin privileges within Intercom. Optionally, configure receiving Events for Intercom into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/intercom/index.md for the full list. ## Events See https://docs.stackone.com/connectors/intercom/index.md for the full list. # Intercom Changelog Source: https://docs.stackone.com/connectors/intercom/changelog Release history for the Intercom connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Documented the search values and matching rules Intercom actually applies, so filters no longer come back silently empty. Ticket search by category takes 'request', 'task' or 'tracker' rather than the category name on the ticket, conversation search by source.type lists the channel values it accepts, and the text operators now state that '=' matches word by word while '~' matches a contiguous substring. `intercom_create_data_event`, `intercom_create_message`, `intercom_create_ticket_type`, `intercom_get_conversation`, `intercom_list_conversations`, `intercom_list_data_events`, `intercom_reply_to_conversation`, `intercom_search_conversations`, `intercom_search_tickets`, `intercom_untag_companies`, `intercom_update_ticket_type` `bug-fix` Documented the search values Intercom actually matches on, so filters no longer come back silently empty. Ticket search by category takes 'request', 'task' or 'tracker' rather than the category name shown on the ticket, conversation search by source.type lists the channel values it accepts, and the contains and starts-with operators are marked as working on free-text fields only. `intercom_search_conversations`, `intercom_search_tickets` `breaking` `bug-fix` Ticket and conversation search now accept multi-value IN and NIN filters and compound AND/OR conditions, quick reply options can be sent when replying to a ticket, non-duplicate contacts can be merged, and company contacts page through a cursor instead of a page number. Parameters that the provider rejects are now caught before the request is sent, and several parameter descriptions were corrected to match actual API behaviour. `intercom_add_tag_to_ticket`, `intercom_create_contact`, `intercom_create_data_attribute`, `intercom_create_data_event`, `intercom_create_message`, `intercom_create_ticket_type`, `intercom_create_ticket_type_attribute`, `intercom_detach_company_from_contact`, `intercom_detach_contact_from_company`, `intercom_enqueue_create_ticket`, `intercom_get_segment`, `intercom_list_attached_contacts`, `intercom_list_company_contacts`, `intercom_list_data_events`, `intercom_list_segments`, `intercom_merge_contacts`, `intercom_reply_to_conversation`, `intercom_reply_to_ticket`, `intercom_search_conversations`, `intercom_search_internal_articles`, `intercom_search_tickets`, `intercom_untag_companies`, `intercom_update_article`, `intercom_update_data_attribute`, `intercom_update_ticket`, `intercom_update_ticket_type` `data-sync` Enabled periodic data sync for 16 collections including contacts, conversations, companies, articles, teams, and tickets metadata. `intercom_list_admins`, `intercom_list_all_companies`, `intercom_list_articles`, `intercom_list_away_status_reasons`, `intercom_list_calls`, `intercom_list_collections`, `intercom_list_contacts`, `intercom_list_conversations`, `intercom_list_data_attributes`, `intercom_list_internal_articles`, `intercom_list_segments`, `intercom_list_subscription_types`, `intercom_list_tags`, `intercom_list_teams`, `intercom_list_ticket_states`, `intercom_list_ticket_types` `new-events` Added manual webhook support with 117 event topics across contacts, companies, conversations, tickets, articles, admin, audiences, calls, content stats, and more with connection guide. # InvGate Asset Management Source: https://docs.stackone.com/connectors/invgate/index How to set up the InvGate Asset Management connector, plus the actions that are available.
InvGate Asset Management
v1.1.0
64 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). InvGate Asset Management uses OAuth 2.0 Client Credentials. Create an OAuth application in your InvGate tenant Settings... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/invgate/index.md for the full list. # InvGate Asset Management Changelog Source: https://docs.stackone.com/connectors/invgate/changelog Release history for the InvGate Asset Management connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added DataSync support to 19 list actions — including assets, computers, servers, chromebooks, cloud assets, database systems, people, financials, vendors, tags, manufacturers, purchase orders, cost centers, custom fields, and custom field values — so their records can be periodically pulled into StackOne and kept up to date, with pagination handled automatically. Each syncs by full refresh, as InvGate exposes no updated-since filter for these endpoints. # IONOS Source: https://docs.stackone.com/connectors/ionos/index How to set up the IONOS connector, plus the actions that are available.
IONOS
Previewv0.1.0
18 actions · 1 auth method
Infrastructure IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an IONOS Cloud API token from the Token Manager. Create it as the contract owner or an administrator, since only th... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ionos/index.md for the full list. # IONOS Changelog Source: https://docs.stackone.com/connectors/ionos/changelog Release history for the IONOS connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Initial IONOS Cloud connector for reviewing who has access to an IONOS Cloud contract, covering users, groups, group privileges and the contract, including unified IAM users, groups, roles, organizations and connection details. # IPGeolocation Source: https://docs.stackone.com/connectors/ipgeolocation/index How to set up the IPGeolocation connector, plus the actions that are available.
IPGeolocation
v1.0.0
14 actions · 1 auth method
Developer Tools Security Localization
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an API key from the IPGeolocation.io dashboard. The key is sent as a query parameter, which is the only authenticat... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ipgeolocation/index.md for the full list. # IPGeolocation Changelog Source: https://docs.stackone.com/connectors/ipgeolocation/changelog Release history for the IPGeolocation connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `ipgeolocation_convert_timezone`, `ipgeolocation_get_astronomy`, `ipgeolocation_get_astronomy_time_series`, `ipgeolocation_get_caller_ip`, `ipgeolocation_get_ip_geolocation`, `ipgeolocation_get_ip_geolocation_bulk`, `ipgeolocation_get_timezone`, `ipgeolocation_parse_user_agent_header` `bug-fix` Clarified that IP geolocation lookups return no VPN, proxy, Tor, threat score, or abuse contact data, and pointed to the actions that provide them. `ipgeolocation_get_ip_geolocation` `new-connector` Initial action mapping of the IPGeolocation.io connector for IP, threat, time zone, astronomy, and user-agent lookups. # Ironclad Source: https://docs.stackone.com/connectors/ironclad/index How to set up the Ironclad connector, plus the actions and events that are available.
Ironclad
Betav1.1.0
64 actions · 12 events · 2 auth methods
Contract Lifecycle Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 Authorization Code grant — the connection acts on behalf of the authorizing Ironclad user, honoring that user'... OAuth 2.0 Client Credentials grant — server-to-server (app-only) access with no user sign-in. Most write actions require... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ironclad/index.md for the full list. ## Events See https://docs.stackone.com/connectors/ironclad/index.md for the full list. # Ironclad Changelog Source: https://docs.stackone.com/connectors/ironclad/changelog Release history for the Ironclad connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for records, workflows, obligations, entities and entity relationship types, with incremental sync on records. # Iterable Source: https://docs.stackone.com/connectors/iterable/index How to set up the Iterable connector, plus the actions and events that are available.
Iterable
v1.2.0
68 actions · 36 events · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). You need an Iterable account with permissions to create API keys. Generate a server-side API key in the Iterable web app... Optionally, configure receiving Events for Iterable into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/iterable/index.md for the full list. ## Events See https://docs.stackone.com/connectors/iterable/index.md for the full list. # Iterable Changelog Source: https://docs.stackone.com/connectors/iterable/changelog Release history for the Iterable connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `improvement` Added periodic data sync for campaigns, email templates, journeys, lists, and catalogs so their records can be pulled into StackOne and kept up to date, with paging handled automatically. `iterable_get_journeys`, `iterable_get_lists`, `iterable_get_templates`, `iterable_list_campaigns`, `iterable_list_catalogs` `description-improvement` Clarified Get Templates startDateTime/endDateTime descriptions to require a numeric UTC offset (e.g. +0000) rather than a zone abbreviation like 'UTC'. `iterable_get_templates` `improvement` Clarified action descriptions to help agents pick the right tool: Get Campaign and Get Email Template now state the richer detail they return (and that Get Email Template is email-only), Update User Subscriptions is marked as the tool for subscription changes (vs Update User), Bulk Update User and Index Catalog Item point to the single/bulk counterpart for multi-record work, Delete User By Email is distinguished from the permanent Forget erasure, and Create Campaign now warns that email templates must include an unsubscribe merge tag. `iterable_bulk_update_user`, `iterable_create_campaign`, `iterable_delete_user_by_email`, `iterable_get_campaign`, `iterable_get_email_template`, `iterable_index_catalog_item`, `iterable_update_subscriptions` `bug-fix` Added portal screenshots to the API Key connection guide and split the key-creation step so each screen has its own instruction. Shortened the API Key field description, which duplicated the whole guide. `native-webhooks` Added native webhook event support — 36 System Webhook event types (email, SMS, push, in-app, embedded, web push, journey/session) each mapped to its own handler, with a router keyed on eventName, an events setup guide, and nativeWebhookUrl on the API Key auth. Events are configured manually in the Iterable dashboard (Integrations → System Webhooks). Mapping verified offline for all 36 events. # Jamf Pro Source: https://docs.stackone.com/connectors/jamf/index How to set up the Jamf Pro connector, plus the actions that are available.
Jamf Pro
v1.3.0
62 actions · 2 auth methods
Device Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Jamf Pro uses OAuth 2.0 Client Credentials via API Roles & Clients (introduced in Jamf Pro 10.49.0). Permissions are NOT... Jamf Pro uses OAuth 2.0 Client Credentials via API Roles & Clients (introduced in Jamf Pro 10.49.0). Permissions are NOT... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jamf/index.md for the full list. # Jamf Pro Changelog Source: https://docs.stackone.com/connectors/jamf/changelog Release history for the Jamf Pro connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added unified IAM actions for Jamf Pro user accounts, account groups and privilege sets, including each user's effective privileges, plus the connection's own identity. `jamf_unified_get_group`, `jamf_unified_get_me`, `jamf_unified_get_role`, `jamf_unified_get_user`, `jamf_unified_list_groups`, `jamf_unified_list_roles`, `jamf_unified_list_users` `data-sync` `new-feature` Added Data Sync support to all list actions — computers, users, mobile devices, MDM commands, categories, scripts, buildings, departments, computer and mobile device groups, policies, and configuration profiles — so these collections can be synced into StackOne on a schedule with paging handled automatically. All sync by full refresh, as the Jamf Pro and Classic APIs expose no updated-since filter on their list endpoints. `jamf_find_macos_configuration_profiles`, `jamf_find_mobile_device_configuration_profiles`, `jamf_find_policies`, `jamf_get_categories`, `jamf_get_computers`, `jamf_get_mdm_commands`, `jamf_get_mobile_device_smart_groups`, `jamf_get_mobile_device_static_groups`, `jamf_get_mobile_devices`, `jamf_get_users`, `jamf_search_buildings`, `jamf_search_computer_smart_groups`, `jamf_search_computer_static_groups`, `jamf_search_departments`, `jamf_search_scripts` `bug-fix` Removed the unsupported PLUGINS and FONTS section values from Get Computer and Get Computers (the Jamf API rejects them), and clarified on Get Users that email/login identity lookups should filter on the username field. `jamf_get_computer`, `jamf_get_computers`, `jamf_get_users` `bug-fix` Fixed the computer section filter on Get Computer and Get Computers so requested sections (e.g. HARDWARE, OPERATING_SYSTEM) are now returned instead of only the General section. `jamf_get_computer`, `jamf_get_computers` `new-actions` `bug-fix` Renamed read and command actions to mirror Jamf Pro's own operation names (Search/Find/Get for collection reads, Create MDM Command, Replace Script). Also fixed and simplified MDM command listing (single RSQL filter input) and the supported command-type list, corrected script create/update options, added the computer section enum, fixed mobile device static group assignments, made category priority required, added the department name length limit, and removed the unsupported erase PIN option. `jamf_create_mdm_command`, `jamf_find_macos_configuration_profiles`, `jamf_find_mobile_device_configuration_profiles`, `jamf_find_policies`, `jamf_find_policy`, `jamf_get_categories`, `jamf_get_computers`, `jamf_get_mdm_commands`, `jamf_get_mobile_device_smart_groups`, `jamf_get_mobile_device_static_groups`, `jamf_get_mobile_devices`, `jamf_get_users`, `jamf_replace_script`, `jamf_search_buildings`, `jamf_search_computer_smart_groups`, `jamf_search_computer_static_groups`, `jamf_search_departments`, `jamf_search_scripts` `jamf_get_policy`, `jamf_list_buildings`, `jamf_list_categories`, `jamf_list_computer_smart_groups`, `jamf_list_computer_static_groups`, `jamf_list_computers`, `jamf_list_departments`, `jamf_list_macos_configuration_profiles`, `jamf_list_mdm_commands`, `jamf_list_mobile_device_configuration_profiles`, `jamf_list_mobile_device_smart_groups`, `jamf_list_mobile_device_static_groups`, `jamf_list_mobile_devices`, `jamf_list_policies`, `jamf_list_scripts`, `jamf_list_users`, `jamf_send_mdm_command`, `jamf_update_script` `jamf_create_building`, `jamf_create_category`, `jamf_create_computer_smart_group`, `jamf_create_computer_static_group`, `jamf_create_department`, `jamf_create_mobile_device_smart_group`, `jamf_create_mobile_device_static_group`, `jamf_create_policy`, `jamf_create_script`, `jamf_create_user`, `jamf_delete_building`, `jamf_delete_category`, `jamf_delete_computer`, `jamf_delete_computer_smart_group`, `jamf_delete_computer_static_group`, `jamf_delete_department`, `jamf_delete_policy`, `jamf_delete_script`, `jamf_delete_user`, `jamf_erase_mobile_device`, `jamf_get_building`, `jamf_get_computer`, `jamf_get_computer_detail`, `jamf_get_computer_filevault`, `jamf_get_mobile_device`, `jamf_get_mobile_device_detail`, `jamf_get_mobile_device_static_group`, `jamf_update_computer`, `jamf_update_mobile_device`, `jamf_update_policy`, `jamf_update_user` `auth-improvements` `guide-changes` Added an OAuth 2.0 Client Credentials (Managed) authentication method using Jamf Pro API Roles & Clients (Jamf Pro 10.49.0+). The API Client ID and Secret are configured once at the connector-profile level, so end users enter no credentials when linking an account. Includes a setup guide covering API Role and API Client creation. # JazzHR Source: https://docs.stackone.com/connectors/jazzhr/index How to set up the JazzHR connector, plus the actions that are available.
JazzHR
Betav1.1.0
26 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses API Key authentication. Provide your JazzHR API Key to authenticate. The key is passed as a query parameter with ea... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jazzhr/index.md for the full list. # JazzHR Changelog Source: https://docs.stackone.com/connectors/jazzhr/changelog Release history for the JazzHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled data synchronisation on 11 list actions for periodic record syncing. # JD Edwards Source: https://docs.stackone.com/connectors/jdedwards/index How to set up the JD Edwards connector, plus the actions that are available.
JD Edwards
Betav0.2.0
15 actions · 1 auth method
ERP
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses EnterpriseOne username/password exchanged at the AIS Server's tokenrequest service for a session token, which is se... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jdedwards/index.md for the full list. # JD Edwards Changelog Source: https://docs.stackone.com/connectors/jdedwards/changelog Release history for the JD Edwards connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for get_all_orchestrations, so the AIS Server's orchestration catalogue can be harvested on a schedule. The discovery service returns the whole catalogue in one response and exposes no updated-since filter, so the sync is full-refresh with no pagination, indexed on omwObjectName. The action's documentation link was corrected to the List Orchestrations reference for the /discover endpoint it actually calls. No input, step or result was changed on any action. `jdedwards_get_all_orchestrations` `new-actions` Initial build of the JD Edwards EnterpriseOne connector over the AIS Server REST API. # Jenkins Source: https://docs.stackone.com/connectors/jenkins/index How to set up the Jenkins connector, plus the actions that are available.
Jenkins
Previewv0.1.0
6 actions · 1 auth method
IAM Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses HTTP Basic authentication with a Jenkins username and that user's own API token. The connection reads with that use... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jenkins/index.md for the full list. # Jenkins Changelog Source: https://docs.stackone.com/connectors/jenkins/changelog Release history for the Jenkins connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Initial Jenkins connector for reviewing who can sign in to a self-hosted Jenkins controller, covering real user accounts and Role Strategy global roles, including unified IAM users, roles and connection details. # JetBrains YouTrack Source: https://docs.stackone.com/connectors/jetbrains/index How to set up the JetBrains YouTrack connector, plus the actions and events that are available.
JetBrains YouTrack
v1.0.0
58 actions · 11 events · 1 auth method
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a YouTrack permanent token. The token authorizes REST API calls with the permissions of the user who c... Optionally, configure receiving Events for JetBrains YouTrack into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jetbrains/index.md for the full list. ## Events See https://docs.stackone.com/connectors/jetbrains/index.md for the full list. # JetBrains YouTrack Changelog Source: https://docs.stackone.com/connectors/jetbrains/changelog Release history for the JetBrains YouTrack connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `jetbrains_count_issues`, `jetbrains_create_admin_project`, `jetbrains_create_command`, `jetbrains_create_issue`, `jetbrains_create_issue_attachment`, `jetbrains_create_issue_comment`, `jetbrains_create_issue_link`, `jetbrains_create_issue_tag`, `jetbrains_create_tag`, `jetbrains_create_time_tracking_work_item`, `jetbrains_delete_admin_project`, `jetbrains_delete_issue`, `jetbrains_delete_issue_attachment`, `jetbrains_delete_issue_comment`, `jetbrains_delete_issue_link`, `jetbrains_delete_issue_tag`, `jetbrains_delete_tag`, `jetbrains_delete_time_tracking_work_item`, `jetbrains_get_agile`, `jetbrains_get_agile_sprint`, `jetbrains_get_current_user`, `jetbrains_get_group`, `jetbrains_get_issue`, `jetbrains_get_issue_attachment`, `jetbrains_get_issue_comment`, `jetbrains_get_issue_custom_field`, `jetbrains_get_issue_link`, `jetbrains_get_issue_link_type`, `jetbrains_get_issue_tag`, `jetbrains_get_saved_query`, `jetbrains_get_tag`, `jetbrains_get_time_tracking_work_item`, `jetbrains_get_user`, `jetbrains_list_admin_projects`, `jetbrains_list_agile_sprints`, `jetbrains_list_agiles`, `jetbrains_list_groups`, `jetbrains_list_issue_attachments`, `jetbrains_list_issue_comments`, `jetbrains_list_issue_custom_fields`, `jetbrains_list_issue_link_types`, `jetbrains_list_issue_links`, `jetbrains_list_issue_tags`, `jetbrains_list_issues`, `jetbrains_list_saved_queries`, `jetbrains_list_tag_issues`, `jetbrains_list_tags`, `jetbrains_list_time_tracking_work_items`, `jetbrains_list_users`, `jetbrains_list_work_item_types`, `jetbrains_list_work_items`, `jetbrains_update_issue`, `jetbrains_update_issue_comment`, `jetbrains_update_issue_custom_field`, `jetbrains_update_tag`, `jetbrains_update_time_tracking_work_item` `bug-fix` `description-fix` Documented that selecting the write-only startingNumber field in project field selection makes YouTrack fail with a 502, that commands accept issue references by database id or readable id (and reject a readable id passed as id), that a count can be -1 while still being computed, and that setting an issue's parent turns it into a subtask without a separate link call. `jetbrains_count_issues`, `jetbrains_create_admin_project`, `jetbrains_create_command`, `jetbrains_get_admin_project`, `jetbrains_get_issue`, `jetbrains_list_admin_projects`, `jetbrains_update_admin_project`, `jetbrains_update_issue` `bug-fix` `description-fix` Delete actions now return a confirmation payload with the deleted resource ids instead of an empty body, made project leader a required input on create_admin_project, and clarified the create_command, create_issue_link, delete_issue_link, update_tag, and list_tag_issues tool descriptions (issue-link actions now state the linked issue must be referenced by its database id, not the readable id). `jetbrains_create_admin_project`, `jetbrains_create_command`, `jetbrains_create_issue_link`, `jetbrains_delete_admin_project`, `jetbrains_delete_issue`, `jetbrains_delete_issue_comment`, `jetbrains_delete_issue_link`, `jetbrains_delete_issue_tag`, `jetbrains_delete_tag`, `jetbrains_delete_time_tracking_work_item`, `jetbrains_list_tag_issues`, `jetbrains_update_tag` `guide-changes` `bug-fix` Improved the Permanent Token connection guide (added a step on obtaining a YouTrack instance, made the base URL examples plain text) and removed circular prerequisiteActions that blocked connector builds. `jetbrains_list_issue_attachments`, `jetbrains_list_issue_comments`, `jetbrains_list_issue_links`, `jetbrains_list_issue_tags`, `jetbrains_list_time_tracking_work_items` `data-sync` Enabled DataSync on 10 list actions (agiles, groups, issues, saved searches, users, tags, projects, issue link types, work item types, and work items) with offset pagination, plus incremental sync on work items. `jetbrains_list_admin_projects`, `jetbrains_list_agiles`, `jetbrains_list_groups`, `jetbrains_list_issue_link_types`, `jetbrains_list_issues`, `jetbrains_list_saved_queries`, `jetbrains_list_tags`, `jetbrains_list_users`, `jetbrains_list_work_item_types`, `jetbrains_list_work_items` `native-webhooks` Added 11 native webhook events (issue, comment, work item, and attachment created/updated/deleted) delivered via the YouTrack Webhook Triggers app (manual setup). `new-connector` Initial JetBrains YouTrack connector — 58 actions across issues, comments, attachments, time-tracking work items, tags, issue links, custom fields, projects, users, groups, agile boards, sprints, saved queries, and commands. Permanent-token authentication with a connection guide. # Jira Source: https://docs.stackone.com/connectors/jira/index How to set up the Jira connector, plus the actions and events that are available.
Jira
v1.1.0
147 actions · 47 events · 2 auth methods
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth app in the Atlassian Developer Console. Supports granular scopes across projects, issues,... Best for personal scripts and single-user automation. Uses email + API token for basic authentication. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jira/index.md for the full list. ## Events See https://docs.stackone.com/connectors/jira/index.md for the full list. # Jira Changelog Source: https://docs.stackone.com/connectors/jira/changelog Release history for the Jira connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `bug-fix` `description-fix` Added periodic data sync to 25 list actions covering boards, project categories, components, dashboards, fields, field configurations, filters, groups, issue link types, issue types, priorities, projects, project roles, resolutions, statuses, users, workflows, and workflow schemes, plus the unified user, group, and role lists. Each one refreshes in full on every run, since these Jira endpoints expose no updated-since filter. List Unified Groups now returns every group in the site instead of stopping at the first 200, and List Components no longer demands a project filter, so it can enumerate every component in the site. List All Users documents that expanding groups returns each user's full group membership, the only site-wide way to read that. Eight user, group, and worklog actions now reject invalid parameter combinations before the call reaches Jira, naming the missing or conflicting field instead of returning an unexplained 400 — this covers the project or issue scope the user-search actions require, the either-or between group ID and group name, and the time-spent and estimate-adjustment pairings on worklogs. Fixed a data-loss bug in the new data sync for boards, components, field search, and workflow search — Jira caps those endpoints at 50 records per page while the sync requested 100, so every other half-page of records was skipped on any account large enough to paginate. Corrected several action and field descriptions, including an incorrect claim that browse-permission search fails on team-managed projects and an incorrect claim that bulk permission checks reject an empty request body. `jira_create_issue_worklog`, `jira_create_project`, `jira_delete_issue_worklog`, `jira_get_all_boards`, `jira_get_all_users`, `jira_get_bulk_permissions`, `jira_get_favourite_filters`, `jira_get_field_configurations`, `jira_get_group_members`, `jira_get_issue_link_types`, `jira_get_my_filters`, `jira_list_categories`, `jira_list_components`, `jira_list_dashboards`, `jira_list_fields`, `jira_list_filters`, `jira_list_groups`, `jira_list_issue_types`, `jira_list_priorities`, `jira_list_project_roles`, `jira_list_projects`, `jira_list_resolutions`, `jira_list_statuses`, `jira_list_workflow_schemes`, `jira_search_dashboards`, `jira_search_fields`, `jira_search_users_assignable_to_issues`, `jira_search_users_assignable_to_projects`, `jira_search_users_with_browse_permission`, `jira_search_users_with_permissions`, `jira_search_workflows`, `jira_unified_list_groups`, `jira_unified_list_roles`, `jira_unified_list_users`, `jira_update_issue_worklog` `bug-fix` Fixed role lookups failing for ids returned by the role list, and an unrecognized role id now comes back as an Unknown record with a 200 instead of an error. Group records now report the group type instead of the group name. Status fields on the embedded user and group member records return the normalized value alongside Jira's raw active flag, and type fields return a value and source value pair, with group type reporting the fixed value group in both. The IAM action descriptions were rewritten. `jira_unified_get_group`, `jira_unified_get_me`, `jira_unified_get_role`, `jira_unified_get_user`, `jira_unified_list_groups`, `jira_unified_list_roles`, `jira_unified_list_users` `bug-fix` Clarified action guidance for searching issue comments, linking issues, and looking up project roles and versions so AI agents choose the right action and interpret responses correctly. # Jira Service Management Source: https://docs.stackone.com/connectors/jiraservicemanagement/index How to set up the Jira Service Management connector, plus the actions and events that are available.
Jira Service Management
v1.2.0
42 actions · 17 events · 2 auth methods
ITSM Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth app in the Atlassian Developer Console. Supports granular scopes for service desk requests... Best for personal scripts and single-user automation. Uses email + API token for basic authentication. Optionally, configure receiving Events for Jira Service Management into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jiraservicemanagement/index.md for the full list. ## Events See https://docs.stackone.com/connectors/jiraservicemanagement/index.md for the full list. # Jira Service Management Changelog Source: https://docs.stackone.com/connectors/jiraservicemanagement/changelog Release history for the Jira Service Management connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added 16 webhook events for requests, comments, attachments, issue links, worklogs and users, delivered from Jira webhooks, with a setup guide. `data-sync` Added data sync support for service desks, organizations, request types, and customer requests, so these collections can be periodically pulled and kept up to date. `jiraservicemanagement_list_customer_requests`, `jiraservicemanagement_list_organizations`, `jiraservicemanagement_list_request_types`, `jiraservicemanagement_list_service_desks` `bug-fix` `guide-changes` Fixed account linking accepting invalid API token credentials, rebuilt both connection guides with portal screenshots and current Atlassian Developer Console steps (including the required Access type field and the read:jira-user and read:jira-work scopes), and renamed the API Key auth method to API Token. # JobAdder Source: https://docs.stackone.com/connectors/jobadder/index How to set up the JobAdder connector, plus the actions and events that are available.
JobAdder
v2.0.0
247 actions · 43 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authentication for JobAdder API. Requires access to the JobAdder Developer Portal to register an application. Optionally, configure receiving Events for JobAdder into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jobadder/index.md for the full list. ## Events See https://docs.stackone.com/connectors/jobadder/index.md for the full list. # JobAdder Changelog Source: https://docs.stackone.com/connectors/jobadder/changelog Release history for the JobAdder connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `breaking-changes` Added data sync to 55 list actions, 16 of them paginated through the provider Offset and Limit parameters and 39 returning their full collection in one call. Nine actions also sync incrementally on the JobAdder UpdatedAt filter. Those nine replace the UpdatedAt input with updatedAfter and updatedBefore, which is a breaking change to their input surface. Fixed list_applications sending a timestamp with milliseconds, which JobAdder ignored so the action returned every record instead of the filtered set. `jobadder_list_all_candidate_attachments`, `jobadder_list_application_activity_settings`, `jobadder_list_application_custom_fields`, `jobadder_list_application_status_list`, `jobadder_list_application_workflows`, `jobadder_list_applications`, `jobadder_list_candidate_activity_settings`, `jobadder_list_candidate_attachment_categories`, `jobadder_list_candidate_custom_fields`, `jobadder_list_candidate_note_types`, `jobadder_list_candidate_sources`, `jobadder_list_candidate_status_list`, `jobadder_list_candidates`, `jobadder_list_companies`, `jobadder_list_company_activity_settings`, `jobadder_list_company_attachment_categories`, `jobadder_list_company_note_types`, `jobadder_list_company_status_list`, `jobadder_list_contact_activity_settings`, `jobadder_list_contact_attachment_categories`, `jobadder_list_contact_note_types`, `jobadder_list_contact_status_list`, `jobadder_list_contacts`, `jobadder_list_deleted_applications`, `jobadder_list_deleted_candidates`, `jobadder_list_deleted_companies`, `jobadder_list_deleted_contacts`, `jobadder_list_deleted_jobs`, `jobadder_list_deleted_placements`, `jobadder_list_event_subtypes`, `jobadder_list_events`, `jobadder_list_interviews`, `jobadder_list_job_activity_settings`, `jobadder_list_job_ads`, `jobadder_list_job_attachment_categories`, `jobadder_list_job_boards`, `jobadder_list_job_custom_fields`, `jobadder_list_job_note_types`, `jobadder_list_job_status_list`, `jobadder_list_jobs`, `jobadder_list_notes`, `jobadder_list_opportunities`, `jobadder_list_opportunity_stages`, `jobadder_list_partner_actions`, `jobadder_list_placement_activity_settings`, `jobadder_list_placement_attachment_categories`, `jobadder_list_placement_custom_fields`, `jobadder_list_placement_note_types`, `jobadder_list_placement_status_list`, `jobadder_list_placements`, `jobadder_list_requisition_custom_fields`, `jobadder_list_requisition_forms`, `jobadder_list_requisitions`, `jobadder_list_users`, `jobadder_list_webhooks` `new-events` Added programmatic webhook event support for all 41 JobAdder event types. StackOne automatically creates and deletes webhook subscriptions via POST /v2/webhooks and DELETE /v2/webhooks/{webhookId}. # JobDiva Source: https://docs.stackone.com/connectors/jobdiva/index How to set up the JobDiva connector, plus the actions that are available.
JobDiva
Betav1.1.0
41 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses credential-based authentication. Provide your Client ID, API username, and API password to authenticate. Tokens are... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jobdiva/index.md for the full list. # JobDiva Changelog Source: https://docs.stackone.com/connectors/jobdiva/changelog Release history for the JobDiva connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync v2 support to 2 list actions (open jobs, users). # JobScore Source: https://docs.stackone.com/connectors/jobscore/index How to set up the JobScore connector, plus the actions that are available.
JobScore
Betav1.1.0
40 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a JobScore API token. Generate it from the employer dashboard under Integrations > JobScore API & Webhooks. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jobscore/index.md for the full list. # JobScore Changelog Source: https://docs.stackone.com/connectors/jobscore/changelog Release history for the JobScore connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for candidates, jobs, offers, tasks, tags, users, departments, locations, disposition codes, and candidate EEO records, all with incremental updates so later syncs fetch only what changed. # Jobsoid Source: https://docs.stackone.com/connectors/jobsoid/index How to set up the Jobsoid connector, plus the actions that are available.
Jobsoid
v1.2.0
6 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses subdomain-based access. Provide your Jobsoid subdomain to connect. The public API requires no API key or token — on... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jobsoid/index.md for the full list. # Jobsoid Changelog Source: https://docs.stackone.com/connectors/jobsoid/changelog Release history for the Jobsoid connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for all list actions (jobs, locations, departments, divisions, functions). `jobsoid_list_departments`, `jobsoid_list_divisions`, `jobsoid_list_functions`, `jobsoid_list_jobs`, `jobsoid_list_locations` `bug-fix` Removed the `div` (division) filter on `list_jobs`. `jobsoid_list_divisions` `bug-fix` Removed the `div` (division) filter on `list_jobs`. `jobsoid_list_jobs` `guide-fix` Fixed connection guide with correct portal navigation (Settings > Tools > Careers Portal), added screenshots, concrete subdomain example, and clarified Hub field naming. # JOIN Source: https://docs.stackone.com/connectors/join/index How to set up the JOIN connector, plus the actions that are available.
JOIN
Previewv1.1.0
23 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an API token generated from User Settings > API. Tokens can be revoked at any time. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/join/index.md for the full list. # JOIN Changelog Source: https://docs.stackone.com/connectors/join/changelog Release history for the JOIN connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for jobs, applications, offices, categories, employment types, and seniority levels, so their records can be periodically pulled into StackOne and kept up to date. Jobs and applications sync incrementally, fetching only what changed since the last run. # JotForm Source: https://docs.stackone.com/connectors/jotform/index How to set up the JotForm connector, plus the actions that are available.
JotForm
Previewv1.1.1
44 actions · 1 auth method
Surveys
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Click your profile icon (top right) > Settings > API (left sidebar) > Create New Key. Select Read Access for read-only o... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jotform/index.md for the full list. # JotForm Changelog Source: https://docs.stackone.com/connectors/jotform/changelog Release history for the JotForm connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Reading a form setting that was never changed now returns a clean "not configured" answer instead of an error. `jotform_get_form_properties`, `jotform_get_form_property` `data-sync` Added DataSync support to three list actions (user forms, user submissions, and user reports), with offset pagination on forms and submissions. All three sync via full refresh. `jotform_list_user_forms`, `jotform_list_user_reports`, `jotform_list_user_submissions` `bug-fix` Resolved 13 behavioural issues. Submission create, bulk create and update now save answers and flags, question type names are corrected, and property, label and status handling is clearer. # Joveo Source: https://docs.stackone.com/connectors/joveo/index How to set up the Joveo connector, plus the actions that are available.
Joveo
Betav0.2.1
59 actions · 1 auth method
ATS Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a static API key plus a daily access token generated from an external API client id. Access tokens are valid for 24... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/joveo/index.md for the full list. # Joveo Changelog Source: https://docs.stackone.com/connectors/joveo/changelog Release history for the Joveo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the API Key documentation link with a full connection guide explaining that Joveo issues the API key and external API client ID to your agency rather than self-service, and where each value goes. `data-sync` Added data sync support for clients, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Joveo API exposes no updated-since filter a sync can use. `joveo_list_clients` `new-actions` Initial Joveo connector with 59 actions across clients, jobs, campaigns, job groups, feeds, postings, stats, reports, meta, rules, funnel tracking, and S2S events. Supports auto-refreshed and direct access-token authentication. # JumpCloud Source: https://docs.stackone.com/connectors/jumpcloud/index How to set up the JumpCloud connector, plus the actions and events that are available.
JumpCloud
Previewv1.4.4
78 actions · 1 event · 2 auth methods
IAM Device Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses client credentials with role-based access. Supports two client secrets for zero-downtime rotation. Inherits permissions of the generating admin. Expires after 30, 60, or 90 days. Optionally, configure receiving Events for JumpCloud into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jumpcloud/index.md for the full list. ## Events See https://docs.stackone.com/connectors/jumpcloud/index.md for the full list. # JumpCloud Changelog Source: https://docs.stackone.com/connectors/jumpcloud/changelog Release history for the JumpCloud connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified that system groups and policies are resolved by ObjectID via list_system_groups / list_policies (not by name), so delete/get/update of a group or policy by name chain through the list action first. `jumpcloud_create_policy`, `jumpcloud_create_system_group`, `jumpcloud_create_user_group`, `jumpcloud_delete_policy`, `jumpcloud_delete_system_group`, `jumpcloud_get_system_group`, `jumpcloud_update_system_group` `bug-fix` Clarified software app deployment (keep-updated now works via auto-update, with only Install/Uninstall deployment states, and display name required on update), user group dynamic query and attribute update rules, and suspended-user creation, so these actions succeed on the first attempt. `jumpcloud_create_software_app`, `jumpcloud_create_system_group`, `jumpcloud_create_system_user`, `jumpcloud_create_user_group`, `jumpcloud_unified_get_me`, `jumpcloud_update_application`, `jumpcloud_update_software_app`, `jumpcloud_update_system_group`, `jumpcloud_update_user_group` `bugfix` Fixed OAuth 2.0 (Service Account) authentication for EU-region tenants. The token request now uses the EU OAuth host when the EU API Region is selected, instead of always calling the US host. `webhooks` Added native webhook support for JumpCloud Directory Insights alerts. JumpCloud delivers a single fixed payload schema for every Insights Rule, so one generic event action handles all rule/event types; webhook channels and rules are configured manually in the Admin Portal since JumpCloud has no API to manage them. `jumpcloud_webhook_insights_alert` `new-actions` `bug-fix` Added list_policy_templates to discover template ids for create_policy, made delete and member-management actions return confirmation payloads, persisted previously-dropped fields (SSH keys on user creation, software desired state, application beta/learnMore), and clarified organization, command, tag, and user-group tool descriptions. Unified organization and identity lookups now degrade gracefully instead of failing when a service-account key cannot read /organizations. `jumpcloud_list_policy_templates` `jumpcloud_create_application`, `jumpcloud_create_command`, `jumpcloud_create_policy`, `jumpcloud_create_system_user`, `jumpcloud_delete_software_app`, `jumpcloud_get_organization`, `jumpcloud_manage_user_group_members`, `jumpcloud_unified_get_group`, `jumpcloud_unified_get_me`, `jumpcloud_unified_get_user`, `jumpcloud_unified_list_groups`, `jumpcloud_unified_list_organizations`, `jumpcloud_unified_list_users`, `jumpcloud_update_application`, `jumpcloud_update_command`, `jumpcloud_update_software_app`, `jumpcloud_update_system_group`, `jumpcloud_update_system_user`, `jumpcloud_update_user_group` `bug-fix` Unified group, resource member, role, and organization lists now return the full collection instead of stopping at a fixed limit (1,000 for groups and members, 300 for roles and organizations). `jumpcloud_unified_list_groups`, `jumpcloud_unified_list_organizations`, `jumpcloud_unified_list_resource_users`, `jumpcloud_unified_list_roles` `data-sync` Added Data Sync support for systems, system users, system groups, user groups, applications, commands, policies, organizations, and the unified IAM users, groups, roles, and organizations collections. `jumpcloud_list_active_directories`, `jumpcloud_list_application_templates`, `jumpcloud_list_applications`, `jumpcloud_list_command_results`, `jumpcloud_list_commands`, `jumpcloud_list_ip_lists`, `jumpcloud_list_ldap_servers`, `jumpcloud_list_organizations`, `jumpcloud_list_policies`, `jumpcloud_list_software_apps`, `jumpcloud_list_system_groups`, `jumpcloud_list_system_users`, `jumpcloud_list_systems`, `jumpcloud_list_user_groups`, `jumpcloud_unified_list_groups`, `jumpcloud_unified_list_organizations`, `jumpcloud_unified_list_roles`, `jumpcloud_unified_list_users` `bug-fix` Fixed IAM list pagination — replaced the raw offset result.next (which could not survive the engine's opaque cursor round-trip past page 1) with fixed offset fan-out plus StackOne virtual pagination across unified_list_users, unified_list_groups, unified_list_organizations, unified_list_roles, and unified_list_resource_users. `jumpcloud_unified_list_groups`, `jumpcloud_unified_list_organizations`, `jumpcloud_unified_list_resource_users`, `jumpcloud_unified_list_roles`, `jumpcloud_unified_list_users` `new-actions` Added unified IAM actions for users, groups, roles, organizations, credentials, and resource users. # JupiterOne Source: https://docs.stackone.com/connectors/jupiterone/index How to set up the JupiterOne connector, plus the actions that are available.
JupiterOne
Betav0.1.0
55 actions · 1 auth method
Security Observability IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a JupiterOne API key plus your Account ID. The key carries a fine-grained permission policy chosen when it is c... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/jupiterone/index.md for the full list. # JupiterOne Changelog Source: https://docs.stackone.com/connectors/jupiterone/changelog Release history for the JupiterOne connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial action mappings for JupiterOne # JustCall Source: https://docs.stackone.com/connectors/justcall/index How to set up the JustCall connector, plus the actions and events that are available.
JustCall
Previewv1.2.0
88 actions · 24 events · 1 auth method
Telephony Scheduling CRM IAM Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires Team plan or above. Generate API credentials from JustCall Dashboard under Profile, APIs and Webhooks. Optionally, configure receiving Events for JustCall into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/justcall/index.md for the full list. ## Events See https://docs.stackone.com/connectors/justcall/index.md for the full list. # JustCall Changelog Source: https://docs.stackone.com/connectors/justcall/changelog Release history for the JustCall connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added webhook events for calls, SMS, WhatsApp, Sales Dialer, contact status and appointments, with subscriptions created automatically when an account is connected. `bug-fix` Fixed list pagination for users and groups; paging could return an invalid next-page token and could skip the first page of results. # Justworks Source: https://docs.stackone.com/connectors/justworks/index How to set up the Justworks connector, plus the actions that are available.
Justworks
Betav1.1.0
21 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a registered Partner API application with Justworks. Access tokens are valid for 24 hours with 30-day refresh t... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/justworks/index.md for the full list. # Justworks Changelog Source: https://docs.stackone.com/connectors/justworks/changelog Release history for the Justworks connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the company custom field and company jurisdiction list actions for scheduled full record syncs. # Kameleoon Source: https://docs.stackone.com/connectors/kameleoon/index How to set up the Kameleoon connector, plus the actions that are available.
Kameleoon
v2.1.0
37 actions · 1 auth method
Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Kameleoon uses OAuth 2.0 Client Credentials for server-to-server authentication. Obtain your Client ID and Client Secret... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/kameleoon/index.md for the full list. # Kameleoon Changelog Source: https://docs.stackone.com/connectors/kameleoon/changelog Release history for the Kameleoon connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added data sync support to list_experiments, list_goals, list_segments, and list_variations (live-verified), including incremental sync by modification date (new optional modifiedSince input) on experiments, goals, and segments. Also added data sync and pagination inputs to list_feature_flags and list_personalizations as preview (pending verification on a plan with those products). `kameleoon_list_experiments`, `kameleoon_list_feature_flags`, `kameleoon_list_goals`, `kameleoon_list_personalizations`, `kameleoon_list_segments`, `kameleoon_list_variations` `bug-fix` Clarified that list_experiments and search_variations return the same full records as get_experiment and get_variation, and described the redirect field set per redirection type on create_variation (includeQueryParameters is now optional for PARAMETER_REDIRECTION). `kameleoon_create_variation`, `kameleoon_list_experiments`, `kameleoon_search_variations` `auth` `breaking` `guide` Removed the untested OAuth 2.0 (Authorization Code) method — Kameleoon issues those credentials only on request. Rebuilt the OAuth 2.0 (Client Credentials) guide from the live portal with corrected labels and screenshots. # Keap Source: https://docs.stackone.com/connectors/keap/index How to set up the Keap connector, plus the actions and events that are available.
Keap
Betav1.1.0
158 actions · 34 events · 2 auth methods
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Keap account using OAuth 2.0. You will need to create a developer application in the Keap Developer Portal... Authenticate using a Personal Access Token (PAT) or Service Account Key (SAK) from your Keap account settings. Intended... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/keap/index.md for the full list. ## Events See https://docs.stackone.com/connectors/keap/index.md for the full list. # Keap Changelog Source: https://docs.stackone.com/connectors/keap/changelog Release history for the Keap connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for contacts, contact link types, companies, notes, note templates, tasks, users, opportunities, opportunity stages, orders, products, subscriptions, payment methods, campaigns, automations, emails, tags and tag categories, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Keap API exposes no updated-since filter a sync can use. `keap_list_automations`, `keap_list_campaigns`, `keap_list_companies`, `keap_list_contact_link_types`, `keap_list_contacts`, `keap_list_emails`, `keap_list_note_templates`, `keap_list_notes`, `keap_list_opportunities`, `keap_list_opportunity_stages`, `keap_list_orders`, `keap_list_payment_methods`, `keap_list_products`, `keap_list_subscriptions`, `keap_list_tag_categories`, `keap_list_tags`, `keap_list_tasks`, `keap_list_users` `bug-fix` OAuth token refresh fixes # Keeper Source: https://docs.stackone.com/connectors/keeper/index How to set up the Keeper connector, plus the actions that are available.
Keeper
Previewv0.1.0
9 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses the SCIM bearer token generated for a Keeper Enterprise node's SCIM provisioning method. The token can also create... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/keeper/index.md for the full list. # Keeper Changelog Source: https://docs.stackone.com/connectors/keeper/changelog Release history for the Keeper connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Initial Keeper connector for reviewing who has access to Keeper, covering the users and teams in a Keeper node, including unified IAM users, groups and connection details. # Keka Source: https://docs.stackone.com/connectors/keka/index How to set up the Keka connector, plus the actions that are available.
Keka
Betav1.1.0
75 actions · 2 auth methods
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connects using Keka's Client Credentials flow (kekaapi grant type). Requires a Client ID, Client Secret, and API Key fro... For apps registered through the Keka App Developer Portal. Use this for third-party integration apps that require user a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/keka/index.md for the full list. # Keka Changelog Source: https://docs.stackone.com/connectors/keka/changelog Release history for the Keka connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support to 35 list actions covering employees, departments, locations, groups, job titles, documents, assets, attendance and leave policies, leave balances, salaries, pay groups, performance reviews, jobs, preboarding candidates, requisitions and skills, with incremental sync on the 13 endpoints that filter by lastModified. All other collections refresh in full on every run. # Kenjo Source: https://docs.stackone.com/connectors/kenjo/index How to set up the Kenjo connector, plus the actions that are available.
Kenjo
Betav1.1.0
63 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges within Kenjo. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/kenjo/index.md for the full list. # Kenjo Changelog Source: https://docs.stackone.com/connectors/kenjo/changelog Release history for the Kenjo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for 24 list actions covering employees and their detail sections, org structure, custom fields, compensation, time-off types, and company documents. All syncs are full-refresh — the Kenjo API exposes no updated-since filter. # Kit Source: https://docs.stackone.com/connectors/kit/index How to set up the Kit connector, plus the actions and events that are available.
Kit
v1.2.0
57 actions · 24 events · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create an OAuth2 application in Kit to get Client ID and Secret. Required for write operations. Kit API rate limit is 60... Optionally, configure receiving Events for Kit into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/kit/index.md for the full list. ## Events See https://docs.stackone.com/connectors/kit/index.md for the full list. # Kit Changelog Source: https://docs.stackone.com/connectors/kit/changelog Release history for the Kit connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `bug-fix` Added webhook events for 23 Kit events across subscribers, tags, custom fields, sequences, broadcasts, and posts. StackOne creates the Kit webhook endpoint automatically when the account connects and removes it on disconnect. Batched Kit deliveries are split so every event in a request is delivered. Fixed create_broadcast and update_broadcast so subscriber_filter tag and segment conditions are sent as the ids array Kit requires. `kit_create_broadcast`, `kit_update_broadcast` `data-sync` Added DataSync support to 11 list actions (subscribers, tags, forms, sequences, segments, broadcasts, broadcast stats, custom fields, email templates, purchases, and webhooks). Added pagination parameters (per_page, after, before, include_total_count) to list_webhooks. # KiwiHR Source: https://docs.stackone.com/connectors/kiwihr/index How to set up the KiwiHR connector, plus the actions that are available.
KiwiHR
v1.1.0
44 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). A KiwiHR (Tellent HR) Company API key generated by an account Administrator is required. Requests run on behalf of the f... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/kiwihr/index.md for the full list. # KiwiHR Changelog Source: https://docs.stackone.com/connectors/kiwihr/changelog Release history for the KiwiHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Employee records now return position, team, location and manager, time off balances return their time off type, and user filtering, address country format and timesheet rules are documented accurately. `kiwihr_create_project`, `kiwihr_create_timesheet_entry`, `kiwihr_create_user`, `kiwihr_get_user`, `kiwihr_list_time_off_balances`, `kiwihr_list_users`, `kiwihr_update_timesheet_entry`, `kiwihr_update_user` `bug-fix` Clarified in the connection guide that Tellent HR and KiwiHR are the same product, so the login step and image captions read as KiwiHR (Tellent HR) consistent with the rest of the guide. # Klaviyo Source: https://docs.stackone.com/connectors/klaviyo/index How to set up the Klaviyo connector, plus the actions and events that are available.
Klaviyo
v1.4.0
172 actions · 25 events · 2 auth methods
Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for server-side integrations within a single Klaviyo account. Never expose in client-side code. Recommended for partner integrations and multi-account apps. Each user authorizes access to their own Klaviyo data. Optionally, configure receiving Events for Klaviyo into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/klaviyo/index.md for the full list. ## Events See https://docs.stackone.com/connectors/klaviyo/index.md for the full list. # Klaviyo Changelog Source: https://docs.stackone.com/connectors/klaviyo/changelog Release history for the Klaviyo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Added native webhook support for 25 Klaviyo email, SMS, push and review events, with one webhook created and removed automatically for all enabled events. `new-feature` `data-sync` Added DataSync support to 19 list actions, with incremental sync where Klaviyo exposes an updated-since filter. `klaviyo_get_accounts`, `klaviyo_list_catalog_categories`, `klaviyo_list_catalog_items`, `klaviyo_list_catalog_variants`, `klaviyo_list_coupons`, `klaviyo_list_custom_metrics`, `klaviyo_list_events`, `klaviyo_list_flows`, `klaviyo_list_forms`, `klaviyo_list_images`, `klaviyo_list_lists`, `klaviyo_list_metrics`, `klaviyo_list_profiles`, `klaviyo_list_segments`, `klaviyo_list_tag_groups`, `klaviyo_list_tags`, `klaviyo_list_templates`, `klaviyo_list_universal_content`, `klaviyo_unified_list_organizations` `new-actions` Added unified IAM actions for users, roles, organizations, and credentials. # Kustomer Source: https://docs.stackone.com/connectors/kustomer/index How to set up the Kustomer connector, plus the actions that are available.
Kustomer
Betav1.1.0
53 actions · 2 auth methods
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 authorization code flow. Requires registering a Kustomer app via the Apps Platform API. Authenticate using a Kustomer API key with Bearer token authorization. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/kustomer/index.md for the full list. # Kustomer Changelog Source: https://docs.stackone.com/connectors/kustomer/changelog Release history for the Kustomer connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support to 7 list actions (customers, conversations, messages, users, notes, companies, and klasses), with incremental (last updated) syncing on customers via a new filter[updatedAt][gte] input. # Lacework FortiCNAPP Source: https://docs.stackone.com/connectors/lacework/index How to set up the Lacework FortiCNAPP connector, plus the actions that are available.
Lacework FortiCNAPP
Betav1.1.0
56 actions · 1 auth method
Security
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Lacework authenticates with an API access key. StackOne exchanges the key ID and secret at POST /api/v2/access/tokens (s... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lacework/index.md for the full list. # Lacework FortiCNAPP Changelog Source: https://docs.stackone.com/connectors/lacework/changelog Release history for the Lacework FortiCNAPP connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the alert channel, alert rule, cloud account, container registry, policy, query, resource group, team member, and vulnerability exception list actions for scheduled full record syncs. # Lara Translate Source: https://docs.stackone.com/connectors/laratranslate/index How to set up the Lara Translate connector, plus the actions that are available.
Lara Translate
Previewv0.3.0
47 actions · 1 auth method
Translation
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an Access Key ID and Access Key Secret generated in the Lara Translate dashboard under API credentials. Free pl... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/laratranslate/index.md for the full list. # Lara Translate Changelog Source: https://docs.stackone.com/connectors/laratranslate/changelog Release history for the Lara Translate connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added scheduled data sync for translation memories, glossaries and style guides, so these can be read from StackOne without calling Lara on every request. All three refresh in full — Lara exposes no updated-since filter on these endpoints. `laratranslate_list_glossaries`, `laratranslate_list_memories`, `laratranslate_list_styleguides` `bug-fix` `description-fix` Document and audio translation now accept the file directly, so no separate upload step is needed. Action descriptions now explain Lara's plan-gated translation options and image size requirements. `laratranslate_add_memory_translation`, `laratranslate_add_memory_translations_batch`, `laratranslate_create_audio_transcript_translation`, `laratranslate_create_audio_translation`, `laratranslate_create_document`, `laratranslate_get_audio_upload_url`, `laratranslate_get_document_upload_url`, `laratranslate_get_memory_import_status`, `laratranslate_translate_image`, `laratranslate_translate_image_text`, `laratranslate_translate_text` `new-connector` Initial release of the Lara Translate connector — 47 actions across text, detection, documents, audio, images, memories, glossaries, and style guides. HMAC-signed OAuth2 client-credentials auth. # LastPass Source: https://docs.stackone.com/connectors/lastpass/index How to set up the LastPass connector, plus the actions that are available.
LastPass
v1.1.2
34 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a LastPass Business or Enterprise account. Uses CID (account number) and provisioning hash for authentication.... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lastpass/index.md for the full list. # LastPass Changelog Source: https://docs.stackone.com/connectors/lastpass/changelog Release history for the LastPass connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed unified group listing and lookup returning garbled ids and names instead of the group's name. `lastpass_unified_get_group`, `lastpass_unified_list_groups` `bug-fix` Fixed unified resource user listing failing when a shared folder is shared with a group instead of an individual user. `lastpass_unified_list_resource_users` `data-sync` Added scheduled data sync to four list actions — users, groups, organizations, and roles — so these collections can be kept in sync and read back without calling LastPass on every request. Each refreshes in full on every run, since the LastPass Provisioning API has no updated-since filter to drive incremental sync. `lastpass_unified_list_groups`, `lastpass_unified_list_organizations`, `lastpass_unified_list_roles`, `lastpass_unified_list_users` `bug-fix` Fixed several unified IAM issues, including mismatched release stages between list and detail actions, missing role scope information, an organization not-found error, incomplete group membership data, and invalid credentials reporting a not-found error instead of an authentication error. `lastpass_unified_get_group`, `lastpass_unified_get_me`, `lastpass_unified_get_organization`, `lastpass_unified_get_role`, `lastpass_unified_get_user`, `lastpass_unified_list_groups`, `lastpass_unified_list_organizations`, `lastpass_unified_list_resource_types`, `lastpass_unified_list_resource_users`, `lastpass_unified_list_roles`, `lastpass_unified_list_users` `bug-fix` `connection-guide` Fixed the connection test so invalid credentials are rejected — the LastPass Provisioning API returns HTTP 200 with an error body for a wrong account number or provisioning hash, so the get_user_data test action now maps that response to a 401 instead of connecting successfully. Rebuilt the config connection guide with live Admin Console screenshots covering the Advanced > Enterprise API navigation, the account number, and the provisioning hash creation and copy steps, and corrected the Account Number (CID) field description to point to the Advanced > Enterprise API page. `lastpass_get_user_data` `bug-fix` Fixed unified IAM credentials, organizations, roles, resource users, and users actions that shipped raw or malformed data despite declaring correct field mappings, plus a decorative resource_id filter and expand input. # Lattice Source: https://docs.stackone.com/connectors/lattice/index How to set up the Lattice connector, plus the actions that are available.
Lattice
v1.1.0
34 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from Admin > Platform > API Keys in your Lattice account. This is for Lattice Talent API (v1) only. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lattice/index.md for the full list. # Lattice Changelog Source: https://docs.stackone.com/connectors/lattice/changelog Release history for the Lattice connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added DataSync support for users, departments, tags, review cycles, feedbacks, updates, and goals. # Lattice Talent Source: https://docs.stackone.com/connectors/lattice_talent/index How to set up the Lattice Talent connector, plus the actions that are available.
Lattice Talent
v1.0.0
26 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from Admin > Platform > API Keys in your Lattice account Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lattice_talent/index.md for the full list. # LaunchDarkly Source: https://docs.stackone.com/connectors/launchdarkly/index How to set up the LaunchDarkly connector, plus the actions and events that are available.
LaunchDarkly
v4.2.1
96 actions · 41 events · 1 auth method
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect with an access token. Admin role recommended for full access to feature flags, segments, and experiments. Optionally, configure receiving Events for LaunchDarkly into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/launchdarkly/index.md for the full list. ## Events See https://docs.stackone.com/connectors/launchdarkly/index.md for the full list. # LaunchDarkly Changelog Source: https://docs.stackone.com/connectors/launchdarkly/changelog Release history for the LaunchDarkly connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` The team, custom role and flag trigger write actions are now marked beta. They only work on a LaunchDarkly plan that includes Teams, Custom Roles and Flag Triggers, and are rejected on other plans. `launchdarkly_create_custom_role`, `launchdarkly_create_flag_trigger`, `launchdarkly_create_team`, `launchdarkly_delete_custom_role`, `launchdarkly_delete_team`, `launchdarkly_update_custom_role`, `launchdarkly_update_team` `new-actions` `bug-fix` AI configs can now be created in judge mode with an evaluation metric. Policy statements on custom roles and integration subscriptions now document their required fields and resource syntax, so permission and event filters are accepted first time. `launchdarkly_create_ai_config`, `launchdarkly_create_custom_role`, `launchdarkly_create_flag_trigger`, `launchdarkly_create_integration_subscription`, `launchdarkly_create_team`, `launchdarkly_create_webhook`, `launchdarkly_delete_flag_trigger`, `launchdarkly_delete_integration_subscription`, `launchdarkly_get_flag_trigger`, `launchdarkly_get_integration_subscription`, `launchdarkly_list_integration_subscriptions`, `launchdarkly_update_ai_config`, `launchdarkly_update_custom_role`, `launchdarkly_update_flag_trigger`, `launchdarkly_update_integration_subscription`, `launchdarkly_update_team`, `launchdarkly_update_webhook` `webhook` `new-actions` `bug-fix` Added webhook events covering feature flags, segments, experiments, projects, environments, members, teams, roles and account configuration. Fixed the enabled option when creating webhooks and integration subscriptions, which was previously ignored. `launchdarkly_copy_feature_flag`, `launchdarkly_create_ai_config`, `launchdarkly_create_experiment`, `launchdarkly_create_integration_subscription`, `launchdarkly_create_model_config`, `launchdarkly_create_webhook`, `launchdarkly_delete_flag_trigger`, `launchdarkly_get_custom_role`, `launchdarkly_get_flag_trigger`, `launchdarkly_get_integration_subscription`, `launchdarkly_get_model_config`, `launchdarkly_get_team`, `launchdarkly_invite_member`, `launchdarkly_list_custom_roles`, `launchdarkly_list_model_configs`, `launchdarkly_list_teams`, `launchdarkly_unified_get_group`, `launchdarkly_unified_get_me`, `launchdarkly_unified_get_organization`, `launchdarkly_unified_get_role`, `launchdarkly_unified_get_user`, `launchdarkly_unified_list_groups`, `launchdarkly_unified_list_organizations`, `launchdarkly_unified_list_resource_types`, `launchdarkly_unified_list_resource_users`, `launchdarkly_unified_list_roles`, `launchdarkly_unified_list_users`, `launchdarkly_update_flag_trigger`, `launchdarkly_update_model_config` `breaking-change` `bug-fix` Inviting account members now works - the action accepts a list of members as the LaunchDarkly API requires. Delete actions now return a confirmation message instead of an empty response. `launchdarkly_create_custom_role`, `launchdarkly_create_flag_trigger`, `launchdarkly_create_team`, `launchdarkly_delete_ai_config`, `launchdarkly_delete_context_instance`, `launchdarkly_delete_custom_role`, `launchdarkly_delete_environment`, `launchdarkly_delete_feature_flag`, `launchdarkly_delete_flag_trigger`, `launchdarkly_delete_integration_subscription`, `launchdarkly_delete_member`, `launchdarkly_delete_metric`, `launchdarkly_delete_model_config`, `launchdarkly_delete_project`, `launchdarkly_delete_segment`, `launchdarkly_delete_team`, `launchdarkly_delete_webhook`, `launchdarkly_get_context_kind`, `launchdarkly_get_custom_role`, `launchdarkly_get_experiment_results`, `launchdarkly_get_team`, `launchdarkly_invite_member`, `launchdarkly_list_custom_roles`, `launchdarkly_list_integration_subscriptions`, `launchdarkly_list_teams`, `launchdarkly_update_custom_role`, `launchdarkly_update_member`, `launchdarkly_update_team` `bug-fix` Role lists now return every built-in and custom role at any page size, and return an error above 1000 custom roles instead of a partial list. `launchdarkly_unified_list_roles` `breaking` `bug-fix` Update AI Config and Update Model Configuration now take the fields to change directly instead of a JSON Patch array, which the provider silently ignored. Metric, AI config and segment filter parameters now document LaunchDarkly's real filter grammar, and Delete Webhook returns a deletion confirmation. `launchdarkly_delete_integration_subscription`, `launchdarkly_delete_webhook`, `launchdarkly_get_integration_subscription`, `launchdarkly_get_member`, `launchdarkly_list_ai_configs`, `launchdarkly_list_metrics`, `launchdarkly_list_segments`, `launchdarkly_update_ai_config`, `launchdarkly_update_integration_subscription`, `launchdarkly_update_model_config` `data-sync` Added DataSync support to 10 list actions for periodic data synchronization, including incremental sync for audit log entries. `launchdarkly_list_audit_log_entries`, `launchdarkly_list_custom_roles`, `launchdarkly_list_members`, `launchdarkly_list_projects`, `launchdarkly_list_teams`, `launchdarkly_list_webhooks`, `launchdarkly_unified_list_groups`, `launchdarkly_unified_list_organizations`, `launchdarkly_unified_list_roles`, `launchdarkly_unified_list_users` `internal` Removed empty authRequirements blocks from unified IAM actions. `launchdarkly_unified_get_group`, `launchdarkly_unified_get_me`, `launchdarkly_unified_get_organization`, `launchdarkly_unified_get_role`, `launchdarkly_unified_get_user`, `launchdarkly_unified_list_groups`, `launchdarkly_unified_list_organizations`, `launchdarkly_unified_list_resource_types`, `launchdarkly_unified_list_resource_users`, `launchdarkly_unified_list_roles`, `launchdarkly_unified_list_users` `bug-fix` Fixed getting an organization by an unknown id, which returned an empty record instead of a not-found error. Fixed listing roles failing when the account's plan does not include custom roles; the built-in roles are now returned instead. `launchdarkly_unified_get_organization`, `launchdarkly_unified_list_roles` `fix` `action-descriptions` `preview` Fixed filter and sort descriptions for metrics, AI configs, and environments. Clarified configKey as URL-safe identifier. Commented out plan-gated unbounded segment field. Marked get/update/delete_flag_trigger, delete_context_instance, and list_integration_subscriptions as preview (untestable in sandbox). `launchdarkly_create_segment`, `launchdarkly_delete_ai_config`, `launchdarkly_delete_context_instance`, `launchdarkly_delete_flag_trigger`, `launchdarkly_get_ai_config`, `launchdarkly_get_flag_trigger`, `launchdarkly_list_ai_configs`, `launchdarkly_list_environments`, `launchdarkly_list_integration_subscriptions`, `launchdarkly_list_metrics`, `launchdarkly_update_ai_config`, `launchdarkly_update_flag_trigger` `action-descriptions` Improved input descriptions across all resources: clarified projectKey usage, added sort field allowed values, and enhanced parameter guidance. `launchdarkly_copy_feature_flag`, `launchdarkly_create_ai_config`, `launchdarkly_create_context_kind`, `launchdarkly_create_custom_role`, `launchdarkly_create_environment`, `launchdarkly_create_experiment`, `launchdarkly_create_feature_flag`, `launchdarkly_create_flag_trigger`, `launchdarkly_create_metric`, `launchdarkly_create_model_config`, `launchdarkly_create_segment`, `launchdarkly_delete_ai_config`, `launchdarkly_delete_context_instance`, `launchdarkly_delete_custom_role`, `launchdarkly_delete_environment`, `launchdarkly_delete_feature_flag`, `launchdarkly_delete_flag_trigger`, `launchdarkly_delete_metric`, `launchdarkly_delete_model_config`, `launchdarkly_delete_project`, `launchdarkly_delete_segment`, `launchdarkly_delete_team`, `launchdarkly_get_ai_config`, `launchdarkly_get_context_attribute_names`, `launchdarkly_get_context_attribute_values`, `launchdarkly_get_context_kind`, `launchdarkly_get_contexts`, `launchdarkly_get_custom_role`, `launchdarkly_get_environment`, `launchdarkly_get_experiment`, `launchdarkly_get_experiment_results`, `launchdarkly_get_expiring_targets_for_flag`, `launchdarkly_get_feature_flag`, `launchdarkly_get_flag_trigger`, `launchdarkly_get_metric`, `launchdarkly_get_model_config`, `launchdarkly_get_project`, `launchdarkly_get_segment`, `launchdarkly_get_team`, `launchdarkly_list_ai_configs`, `launchdarkly_list_context_kinds`, `launchdarkly_list_custom_roles`, `launchdarkly_list_environments`, `launchdarkly_list_experiments`, `launchdarkly_list_feature_flags`, `launchdarkly_list_flag_triggers`, `launchdarkly_list_members`, `launchdarkly_list_metrics`, `launchdarkly_list_model_configs`, `launchdarkly_list_projects`, `launchdarkly_list_segments`, `launchdarkly_list_teams`, `launchdarkly_search_context_instances`, `launchdarkly_search_contexts`, `launchdarkly_update_ai_config`, `launchdarkly_update_context_kind`, `launchdarkly_update_custom_role`, `launchdarkly_update_environment`, `launchdarkly_update_experiment`, `launchdarkly_update_expiring_targets_for_flag`, `launchdarkly_update_feature_flag`, `launchdarkly_update_flag_trigger`, `launchdarkly_update_metric`, `launchdarkly_update_model_config`, `launchdarkly_update_project`, `launchdarkly_update_segment` `new-actions` Added unified IAM actions for users, roles, groups, organizations, credentials, and resource users. `launchdarkly_unified_get_group`, `launchdarkly_unified_get_me`, `launchdarkly_unified_get_organization`, `launchdarkly_unified_get_role`, `launchdarkly_unified_get_user`, `launchdarkly_unified_list_groups`, `launchdarkly_unified_list_organizations`, `launchdarkly_unified_list_resource_types`, `launchdarkly_unified_list_resource_users`, `launchdarkly_unified_list_roles`, `launchdarkly_unified_list_users` `bug-fix` `breaking` Fixed context kind endpoints (POST to PUT upsert), corrected context attribute URLs, renamed model config and flag trigger fields, added pagination and expand parameters across actions. # LeadDocket Source: https://docs.stackone.com/connectors/leaddocket/index How to set up the LeadDocket connector, plus the actions that are available.
LeadDocket
Betav1.1.0
26 actions · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using your LeadDocket API key found in Manage > Settings > Account Settings. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/leaddocket/index.md for the full list. # LeadDocket Changelog Source: https://docs.stackone.com/connectors/leaddocket/changelog Release history for the LeadDocket connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync v2 support to 3 list actions (unprocessed opportunities, statuses, users). # Leapsome Source: https://docs.stackone.com/connectors/leapsome/index How to set up the Leapsome connector, plus the actions that are available.
Leapsome
Betav1.1.0
29 actions · 2 auth methods
HRIS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use the Leapsome Content API to read goals, reviews, employees, feedback, payroll cycles, absences, timesheets, work loc... Use the Leapsome SCIM 2.0 API for user and group provisioning. Customers generate a static bearer token in the Leapsome... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/leapsome/index.md for the full list. # Leapsome Changelog Source: https://docs.stackone.com/connectors/leapsome/changelog Release history for the Leapsome connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added Data Sync support for employees, access roles, goals, tags, reviews, feedback, document categories, timesheets, payroll cycles, work locations, and absences (incremental sync on reviews via last_modified_after; full-refresh on the rest). # Lemlist Source: https://docs.stackone.com/connectors/lemlist/index How to set up the Lemlist connector, plus the actions and events that are available.
Lemlist
v2.4.0
76 actions · 10 events · 1 auth method
Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key authentication. Find your key under Settings > Integrations. Optionally, configure receiving Events for Lemlist into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lemlist/index.md for the full list. ## Events See https://docs.stackone.com/connectors/lemlist/index.md for the full list. # Lemlist Changelog Source: https://docs.stackone.com/connectors/lemlist/changelog Release history for the Lemlist connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled Data Sync to nine collection actions — campaigns, contacts, schedules, unsubscribes, webhooks and team senders, plus the unified users, roles and organizations — so these collections can be kept in sync and searched without calling Lemlist on every request. Campaigns, contacts, schedules and unsubscribes page through results automatically; the rest are returned in full by a single request. All syncs use full refreshes, because no Lemlist endpoint behind these actions exposes an updated-since filter. `lemlist_get_many_contacts`, `lemlist_get_many_webhooks`, `lemlist_get_team_senders`, `lemlist_retrieve_campaigns`, `lemlist_retrieve_schedules`, `lemlist_retrieve_unsubscribes`, `lemlist_unified_list_organizations`, `lemlist_unified_list_roles`, `lemlist_unified_list_users` `bug-fix` `improvement` Corrected the add sequence step delay to be in days (not seconds), fixed the one-to-one send to require exactly one recipient and accept CC as a list, and clarified the send, campaign start-vs-create, and schedule-association guidance. `lemlist_add_sequence_step`, `lemlist_associate_schedule_with_campaign`, `lemlist_create_campaign`, `lemlist_delete_sequence_step`, `lemlist_get_team_senders`, `lemlist_send_email`, `lemlist_send_linkedin_message`, `lemlist_start_campaign` `bug-fix` `improvement` Fixed listing users failing with a server error, and active team members now include their email address and role. Refreshed the API key connection guide. `lemlist_unified_get_me`, `lemlist_unified_get_organization`, `lemlist_unified_get_role`, `lemlist_unified_list_organizations`, `lemlist_unified_list_resource_types`, `lemlist_unified_list_roles`, `lemlist_unified_list_users` `native-webhooks` `new-events` Added native webhook event support — StackOne programmatically registers and removes Lemlist webhook subscriptions and routes lead, email, LinkedIn, WhatsApp, SMS, call, campaign, enrichment, and system events. `lemlist_launch_lead`, `lemlist_send_email`, `lemlist_send_linkedin_message` `lemlist_add_webhook`, `lemlist_update_campaign` `new-actions` `bug-fix` Fixed some action IDs and labels to match the provider's naming, and added missing fields and blocking actions. `lemlist_add_custom_variables`, `lemlist_duplicate_campaign`, `lemlist_erase_values_of_custom_variables`, `lemlist_get_many_contacts`, `lemlist_get_many_webhooks`, `lemlist_retrieve_activities`, `lemlist_retrieve_campaigns`, `lemlist_retrieve_schedules`, `lemlist_retrieve_unsubscribes`, `lemlist_update_values_of_custom_variables` `lemlist_list_activities`, `lemlist_list_campaigns`, `lemlist_list_contacts`, `lemlist_list_schedules`, `lemlist_list_unsubscribes`, `lemlist_list_webhooks` `lemlist_create_lead_in_campaign`, `lemlist_get_campaign_leads`, `lemlist_get_campaign_stats`, `lemlist_unified_list_resource_users`, `lemlist_update_campaign` `new-actions` Added unified IAM actions for users, roles, organizations, credentials, and resource users. Gated the 7 actions that hit a plan-tier-limited endpoint to beta and the 2 live-verified actions to preview. # Lever Source: https://docs.stackone.com/connectors/lever/index How to set up the Lever connector, plus the actions and events that are available.
Lever
v2.1.0
77 actions · 10 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authentication provides secure access to Lever APIs. Register your application through Lever's Partner Program... Optionally, configure receiving Events for Lever into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lever/index.md for the full list. ## Events See https://docs.stackone.com/connectors/lever/index.md for the full list. # Lever Changelog Source: https://docs.stackone.com/connectors/lever/changelog Release history for the Lever connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added webhook event support with manual setup. Copy the Native Webhook URL from the linked account and add it to each event under Settings > Integrations and API > Webhooks in Lever - the URL is stored per event, so an event left without it never sends. Ten events are handled: application created, candidate hired, candidate stage change, candidate archive state change, candidate deleted, interview created, updated and deleted, and contact created and updated. A Lever Super Admin is required to open the Webhooks page. `breaking-changes` `new-feature` Enabled scheduled data sync on twelve list actions — opportunities, deleted opportunities, postings, requisitions, requisition fields, users, sources, tags, stages, archive reasons, feedback templates and EEO responses — so these collections can be kept in sync and read without calling Lever on every request. Nine follow Lever's opaque cursor (the `offset` continuation token), while feedback templates, requisition fields and stages return their full set in a single call. Opportunities and postings sync incrementally using the `updated_at_start` filter; the rest refresh in full, because Lever exposes no updated-since filter on those endpoints. BREAKING - the `updated_at_start` input on List Opportunities and List Postings is now a string rather than a number, so integrations passing it as a numeric value must send it as a string (the value itself is unchanged - Unix milliseconds). # Liferay Source: https://docs.stackone.com/connectors/liferay/index How to set up the Liferay connector, plus the actions and events that are available.
Liferay
v1.2.0
104 actions · 10 events · 2 auth methods
CMS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Liferay instance using OAuth 2.0. Requires an OAuth2 application registered in Liferay's OAuth2 A... Authenticate with your Liferay instance using OAuth 2.0 Client Credentials. Requires a Headless Server OAuth2 applicatio... Optionally, configure receiving Events for Liferay into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/liferay/index.md for the full list. ## Events See https://docs.stackone.com/connectors/liferay/index.md for the full list. # Liferay Changelog Source: https://docs.stackone.com/connectors/liferay/changelog Release history for the Liferay connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added DataSync support to accounts, organizations, roles, user groups, user accounts, sites, and the unified IAM list actions, so their records can be synced into StackOne on a schedule. All refresh in full each run. `liferay_list_accounts`, `liferay_list_my_sites`, `liferay_list_organizations`, `liferay_list_roles`, `liferay_list_user_accounts`, `liferay_list_user_groups`, `liferay_unified_list_groups`, `liferay_unified_list_organizations`, `liferay_unified_list_roles`, `liferay_unified_list_users` `new-actions` Added unified IAM actions for users, groups, organizations, roles, resource users, and credentials. # Lightspeed Retail X-Series Source: https://docs.stackone.com/connectors/lightspeed/index How to set up the Lightspeed Retail X-Series connector, plus the actions and events that are available.
Lightspeed Retail X-Series
Previewv1.1.0
57 actions · 8 events · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authorisation code flow. Lightspeed issues short-lived access tokens (24h) plus rotating refresh tokens. The r... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lightspeed/index.md for the full list. ## Events See https://docs.stackone.com/connectors/lightspeed/index.md for the full list. # Lightspeed Retail X-Series Changelog Source: https://docs.stackone.com/connectors/lightspeed/changelog Release history for the Lightspeed Retail X-Series connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support to 19 list actions — Brands, Consignments, Customers, Outlets, Payment Types, Price Books, Price Book Products, Product Categories, Product Types, Products, Promotions, Registers, Sales, Stock Adjustments, Store Credits, Suppliers, Taxes, Users and Webhooks — so their records can be kept in sync on a schedule. X-Series paginates and tracks changes with one monotonic `after` version watermark, so syncs page by cursor and resume incrementally from the last version seen; Product Categories, Promotions, Store Credits and Webhooks have no change tracking and full-refresh each run. List Gift Cards and List Inventory are not syncable — both take their next-page token from the last record of the previous page, which DataSync's cursor strategy cannot express. # Lilt Source: https://docs.stackone.com/connectors/lilt/index How to set up the Lilt connector, plus the actions that are available.
Lilt
Betav0.2.1
58 actions · 1 auth method
Localization AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Lilt REST API key (Business plan) via HTTP Basic auth, with the key supplied as both the username and the passwor... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lilt/index.md for the full list. # Lilt Changelog Source: https://docs.stackone.com/connectors/lilt/changelog Release history for the Lilt connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the API Key documentation link with a full connection guide covering creating an organization API key from Manage > API keys, including the Administrator and Business plan requirements. `data-sync` Added DataSync support to eight list actions (Lilt Create content, domains, files, jobs, memories, projects, uploads and workflow templates). Jobs page through results via offset and limit; the other seven are returned in full by a single request. All sync by full refresh, as Lilt exposes no updated-since filter. `lilt_list_domains`, `lilt_list_files`, `lilt_list_jobs`, `lilt_list_lilt_create_content`, `lilt_list_memories`, `lilt_list_projects`, `lilt_list_uploads`, `lilt_list_workflow_templates` `new-actions` Initial Lilt connector with 58 actions across create, documents, domains, files, jobs, languages, memories, projects, segments, translate, uploads, and workflows, using API-key HTTP Basic authentication. # Linear Source: https://docs.stackone.com/connectors/linear/index How to set up the Linear connector, plus the actions and events that are available.
Linear
v2.1.0
138 actions · 43 events · 2 auth methods
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). You can create a Personal API Key from your Linear account settings. Create an OAuth2 application in your Linear workspace settings to get Client ID and Secret. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/linear/index.md for the full list. ## Events See https://docs.stackone.com/connectors/linear/index.md for the full list. # Linear Changelog Source: https://docs.stackone.com/connectors/linear/changelog Release history for the Linear connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support to 18 list actions including issues, customers, teams, users, comments, documents, cycles, initiatives, workflow states and labels, so these collections can be synced into StackOne on a schedule and read back without calling Linear each time. Each syncs by full refresh, because Linear's updated-since filter is a nested GraphQL object that the sync watermark cannot drive. `linear_list_comments`, `linear_list_customer_needs`, `linear_list_customer_statuses`, `linear_list_customer_tiers`, `linear_list_customers`, `linear_list_cycles`, `linear_list_documents`, `linear_list_favorites`, `linear_list_initiatives`, `linear_list_issue_labels`, `linear_list_issues`, `linear_list_project_labels`, `linear_list_project_milestones`, `linear_list_project_statuses`, `linear_list_teams`, `linear_list_users`, `linear_list_webhooks`, `linear_list_workflow_states` `auth` `breaking-changes` Migrated all actions from the deprecated requiredScopes field to authRequirements for per-auth-type scope control. OAuth 2.0 connections are gated by the corresponding Linear scope (read, write, admin, issues:create, comments:create); API Key connections are unrestricted. `linear_archive_cycle`, `linear_archive_initiative`, `linear_archive_issue`, `linear_archive_project`, `linear_archive_project_status`, `linear_batch_create_issues`, `linear_batch_update_issues`, `linear_complete_release`, `linear_create_attachment`, `linear_create_comment`, `linear_create_custom_view`, `linear_create_customer`, `linear_create_customer_need`, `linear_create_customer_status`, `linear_create_customer_tier`, `linear_create_cycle`, `linear_create_document`, `linear_create_favorite`, `linear_create_initiative`, `linear_create_initiative_to_project`, `linear_create_initiative_update`, `linear_create_issue`, `linear_create_issue_label`, `linear_create_issue_relation`, `linear_create_notification_subscription`, `linear_create_project`, `linear_create_project_label`, `linear_create_project_milestone`, `linear_create_project_status`, `linear_create_project_update`, `linear_create_reaction`, `linear_create_release`, `linear_create_team`, `linear_create_team_membership`, `linear_create_template`, `linear_create_webhook`, `linear_create_workflow_state`, `linear_delete_attachment`, `linear_delete_comment`, `linear_delete_custom_view`, `linear_delete_customer`, `linear_delete_customer_need`, `linear_delete_customer_status`, `linear_delete_customer_tier`, `linear_delete_document`, `linear_delete_favorite`, `linear_delete_initiative`, `linear_delete_initiative_to_project`, `linear_delete_issue`, `linear_delete_issue_label`, `linear_delete_issue_relation`, `linear_delete_project`, `linear_delete_project_label`, `linear_delete_project_milestone`, `linear_delete_reaction`, `linear_delete_release`, `linear_delete_team`, `linear_delete_team_membership`, `linear_delete_template`, `linear_delete_webhook`, `linear_file_upload`, `linear_get_agentSession`, `linear_get_application_info`, `linear_get_comment`, `linear_get_customer`, `linear_get_customer_need`, `linear_get_customer_status`, `linear_get_customer_tier`, `linear_get_cycle`, `linear_get_document`, `linear_get_external_user`, `linear_get_initiative`, `linear_get_issue`, `linear_get_issue_label`, `linear_get_project`, `linear_get_project_label`, `linear_get_project_milestone`, `linear_get_project_status`, `linear_get_team`, `linear_get_user`, `linear_get_viewer`, `linear_get_webhook`, `linear_get_workflow_state`, `linear_issue_filter_suggestion`, `linear_list_agentSessions`, `linear_list_comments`, `linear_list_customer_needs`, `linear_list_customer_statuses`, `linear_list_customer_tiers`, `linear_list_customers`, `linear_list_cycles`, `linear_list_documents`, `linear_list_external_users`, `linear_list_favorites`, `linear_list_initiatives`, `linear_list_issue_labels`, `linear_list_issues`, `linear_list_project_labels`, `linear_list_project_milestones`, `linear_list_project_statuses`, `linear_list_projects`, `linear_list_team_memberships`, `linear_list_teams`, `linear_list_users`, `linear_list_webhooks`, `linear_list_workflow_states`, `linear_organization_invite_create`, `linear_organization_update`, `linear_resolve_comment`, `linear_rotate_webhook_secret`, `linear_search_issues`, `linear_unarchive_issue`, `linear_unified_get_me`, `linear_unresolve_comment`, `linear_update_attachment`, `linear_update_comment`, `linear_update_custom_view`, `linear_update_customer`, `linear_update_customer_need`, `linear_update_customer_status`, `linear_update_customer_tier`, `linear_update_cycle`, `linear_update_document`, `linear_update_initiative`, `linear_update_issue`, `linear_update_issue_label`, `linear_update_project`, `linear_update_project_label`, `linear_update_project_milestone`, `linear_update_project_status`, `linear_update_release`, `linear_update_team`, `linear_update_template`, `linear_update_user`, `linear_update_webhook`, `linear_update_workflow_state`, `linear_upsert_customer`, `linear_user_suspend` `bug-fix` Fixed pagination for list actions - response now includes pageInfo with hasNextPage and endCursor alongside nodes, enabling proper cursor-based pagination. Affected actions include list_customers, list_issues, list_users, list_projects, list_teams, list_comments, and all other list actions. `linear_list_agentSessions`, `linear_list_comments`, `linear_list_customer_needs`, `linear_list_customer_statuses`, `linear_list_customer_tiers`, `linear_list_customers`, `linear_list_cycles`, `linear_list_documents`, `linear_list_external_users`, `linear_list_favorites`, `linear_list_initiatives`, `linear_list_issue_labels`, `linear_list_issues`, `linear_list_project_labels`, `linear_list_project_milestones`, `linear_list_project_statuses`, `linear_list_projects`, `linear_list_team_memberships`, `linear_list_teams`, `linear_list_users`, `linear_list_webhooks`, `linear_list_workflow_states`, `linear_search_issues` `bug-fix` Fixed tool-selection issues from MCP testing - delete_document now documents the working move-to-trash and update_document drops the non-functional trashed field, delete_attachment and update_attachment are disambiguated, and create_initiative_update marks body optional with body and bodyData mutually exclusive. `linear_create_initiative_update`, `linear_delete_attachment`, `linear_delete_document`, `linear_update_attachment`, `linear_update_document` `new-actions` `bug-fix` Added list_favorites and list_team_memberships so delete_favorite and delete_team_membership can resolve the IDs they need. Fixed customer tier renames and the list_comments issue filter, and clarified several tool descriptions (file_upload, batch_update_issues, update_user, update_customer_need priority, list_issue_labels, create_favorite). No authentication changes. `linear_list_favorites`, `linear_list_team_memberships` `linear_batch_update_issues`, `linear_create_customer_need`, `linear_create_favorite`, `linear_file_upload`, `linear_get_customer_need`, `linear_get_customer_tier`, `linear_list_comments`, `linear_list_issue_labels`, `linear_update_customer_need`, `linear_update_customer_tier`, `linear_update_user` `bug-fix` `guide-fix` Added the admin scope to the default OAuth 2.0 scope request (read,write,admin) so admin-gated actions — webhook management, organization/workspace settings, and customer status, customer tier, and project status create/update/delete — work after reconnecting; Linear treats admin as a separate token grant from the user's role, so these previously failed with "admin required" even for workspace admins. Corrected requiredScopes from write to admin on the customer-status, customer-tier, and project-status create/update/delete/archive actions to match Linear's real permission requirements (their read/list/get actions remain on read). Also updated the OAuth scope guide to explain the admin requirement. Existing OAuth connections must reconnect to grant the admin scope. `linear_archive_cycle`, `linear_archive_initiative`, `linear_archive_issue`, `linear_archive_project`, `linear_archive_project_status`, `linear_batch_create_issues`, `linear_batch_update_issues`, `linear_complete_release`, `linear_create_attachment`, `linear_create_comment`, `linear_create_custom_view`, `linear_create_customer`, `linear_create_customer_need`, `linear_create_customer_status`, `linear_create_customer_tier`, `linear_create_cycle`, `linear_create_document`, `linear_create_favorite`, `linear_create_initiative`, `linear_create_initiative_to_project`, `linear_create_initiative_update`, `linear_create_issue`, `linear_create_issue_label`, `linear_create_issue_relation`, `linear_create_notification_subscription`, `linear_create_project`, `linear_create_project_label`, `linear_create_project_milestone`, `linear_create_project_status`, `linear_create_project_update`, `linear_create_reaction`, `linear_create_release`, `linear_create_team`, `linear_create_team_membership`, `linear_create_template`, `linear_create_webhook`, `linear_create_workflow_state`, `linear_delete_attachment`, `linear_delete_comment`, `linear_delete_custom_view`, `linear_delete_customer`, `linear_delete_customer_need`, `linear_delete_customer_status`, `linear_delete_customer_tier`, `linear_delete_document`, `linear_delete_favorite`, `linear_delete_initiative`, `linear_delete_initiative_to_project`, `linear_delete_issue`, `linear_delete_issue_label`, `linear_delete_issue_relation`, `linear_delete_project`, `linear_delete_project_label`, `linear_delete_project_milestone`, `linear_delete_reaction`, `linear_delete_release`, `linear_delete_team`, `linear_delete_team_membership`, `linear_delete_template`, `linear_delete_webhook`, `linear_file_upload`, `linear_get_agentSession`, `linear_get_application_info`, `linear_get_comment`, `linear_get_customer`, `linear_get_customer_need`, `linear_get_customer_status`, `linear_get_customer_tier`, `linear_get_cycle`, `linear_get_document`, `linear_get_external_user`, `linear_get_initiative`, `linear_get_issue`, `linear_get_issue_label`, `linear_get_project`, `linear_get_project_label`, `linear_get_project_milestone`, `linear_get_project_status`, `linear_get_team`, `linear_get_user`, `linear_get_viewer`, `linear_get_webhook`, `linear_get_workflow_state`, `linear_issue_filter_suggestion`, `linear_list_agentSessions`, `linear_list_comments`, `linear_list_customer_needs`, `linear_list_customer_statuses`, `linear_list_customer_tiers`, `linear_list_customers`, `linear_list_cycles`, `linear_list_documents`, `linear_list_external_users`, `linear_list_initiatives`, `linear_list_issue_labels`, `linear_list_issues`, `linear_list_project_labels`, `linear_list_project_milestones`, `linear_list_project_statuses`, `linear_list_projects`, `linear_list_teams`, `linear_list_users`, `linear_list_webhooks`, `linear_list_workflow_states`, `linear_organization_invite_create`, `linear_organization_update`, `linear_resolve_comment`, `linear_rotate_webhook_secret`, `linear_search_issues`, `linear_unarchive_issue`, `linear_unified_get_me`, `linear_unresolve_comment`, `linear_update_attachment`, `linear_update_comment`, `linear_update_custom_view`, `linear_update_customer`, `linear_update_customer_need`, `linear_update_customer_status`, `linear_update_customer_tier`, `linear_update_cycle`, `linear_update_document`, `linear_update_initiative`, `linear_update_issue`, `linear_update_issue_label`, `linear_update_project`, `linear_update_project_label`, `linear_update_project_milestone`, `linear_update_project_status`, `linear_update_release`, `linear_update_team`, `linear_update_template`, `linear_update_user`, `linear_update_webhook`, `linear_update_workflow_state`, `linear_upsert_customer`, `linear_user_suspend` `guide-fix` `improvement` Added a connection test action (get_viewer) for the API Key auth method, added portal-step screenshots to the API Key config and OAuth 2.0 setup connection guides, and fixed guide audit findings — added the create-key step, corrected UI labels (Security & access, Redirect URIs, the New OAuth application + button), documented the optional OAuth application fields and toggles, added a Developer URL example, and added detailed OAuth scope guidance plus the minimum Read permission requirement. # LinkedIn Source: https://docs.stackone.com/connectors/linkedin/index How to set up the LinkedIn connector, plus the actions that are available.
LinkedIn
Previewv1.0.0
2 actions · 2 auth methods
Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a LinkedIn Developer app with OpenID Connect and Share products enabled. Use a pre-obtained LinkedIn access token directly. Useful for testing or when managing tokens externally. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/linkedin/index.md for the full list. # LinkedIn Learning Source: https://docs.stackone.com/connectors/linkedinlearning/index How to set up the LinkedIn Learning connector, plus the actions that are available.
LinkedIn Learning
Previewv1.0.0
7 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/linkedinlearning/index.md for the full list. # LogicMelon Source: https://docs.stackone.com/connectors/logicmelon/index How to set up the LogicMelon connector, plus the actions that are available.
LogicMelon
v1.1.0
27 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Contact LogicMelon support at support@logicmelon.com to request your API Key and master password. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/logicmelon/index.md for the full list. # LogicMelon Changelog Source: https://docs.stackone.com/connectors/logicmelon/changelog Release history for the LogicMelon connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Added Data Sync support for users, organisations, adverts, applications, public feeds, and currencies. # Lokalise Source: https://docs.stackone.com/connectors/lokalise/index How to set up the Lokalise connector, plus the actions and events that are available.
Lokalise
v1.3.0
111 actions · 33 events · 1 auth method
Translation IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate your API token from your Lokalise Profile Settings under the API tokens tab. Optionally, configure receiving Events for Lokalise into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lokalise/index.md for the full list. ## Events See https://docs.stackone.com/connectors/lokalise/index.md for the full list. # Lokalise Changelog Source: https://docs.stackone.com/connectors/lokalise/changelog Release history for the Lokalise connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` `bug-fix` Added 32 Lokalise webhook events (keys, translations, files, branches, languages, tasks, contributors and orders) with a setup guide, and fixed update_language so language name and plural form changes are applied. `lokalise_update_language` `data-sync` Added data sync support to list_projects, list_teams, list_system_languages, list_payment_cards, unified_list_users, unified_list_groups, unified_list_organizations, and unified_list_roles (full-refresh; Lokalise exposes no updated-since filters on these endpoints). `lokalise_list_payment_cards`, `lokalise_list_projects`, `lokalise_list_system_languages`, `lokalise_list_teams`, `lokalise_unified_list_groups`, `lokalise_unified_list_organizations`, `lokalise_unified_list_roles`, `lokalise_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, and resource users. Listing users can target a team via filter.organization_id; other team-scoped actions require the connection to see exactly one team. # Loket Source: https://docs.stackone.com/connectors/loket/index How to set up the Loket connector, plus the actions that are available.
Loket
Betav1.1.0
61 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Loket uses OAuth 2.0 Authorization Code flow. The user authorizes your application to access the Loket API on their beha... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/loket/index.md for the full list. # Loket Changelog Source: https://docs.stackone.com/connectors/loket/changelog Release history for the Loket connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for employers, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Loket API exposes no updated-since filter a sync can use. # Loom Source: https://docs.stackone.com/connectors/loom/index How to set up the Loom connector, plus the actions that are available.
Loom
Previewv0.2.0
7 actions · 1 auth method
IAM Media
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an Atlassian organization API key created by an organization admin in Atlassian Administration. A key with scopes a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/loom/index.md for the full list. # Loom Changelog Source: https://docs.stackone.com/connectors/loom/changelog Release history for the Loom connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Connections can set the Atlassian Organization ID, so API keys with scopes can list Loom users, groups and workspaces. `loom_list_workspaces`, `loom_unified_get_group`, `loom_unified_get_organization`, `loom_unified_get_user`, `loom_unified_list_groups`, `loom_unified_list_organizations`, `loom_unified_list_users` `new-connector` Added Loom connector for reviewing who can sign in, covering organization lookups and Loom workspace user access, including unified IAM. # Lucca Source: https://docs.stackone.com/connectors/lucca/index How to set up the Lucca connector, plus the actions and events that are available.
Lucca
Betav3.3.0
49 actions · 12 events · 2 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 Client Credentials flow for the Lucca API (v5). Recommended for new integrations. Legacy API key authentication for Lucca v3/v4 APIs. Each key has role-based access rights. Optionally, configure receiving Events for Lucca into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lucca/index.md for the full list. ## Events See https://docs.stackone.com/connectors/lucca/index.md for the full list. # Lucca Changelog Source: https://docs.stackone.com/connectors/lucca/changelog Release history for the Lucca connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added a Create an employee action using the legacy Directory v3 users API, available with API key authentication. `lucca_create_employee`, `lucca_download_portrait` `lucca_retrieve_portrait` `events-guide` Added a webhook setup guide covering how Lucca event subscriptions are created and how events are delivered. `data-sync` Added DataSync support for 16 list actions with cursor-based pagination. `lucca_list_business_establishments`, `lucca_list_departments`, `lucca_list_employee_attribute_definitions`, `lucca_list_employee_attributes`, `lucca_list_employee_personal_records`, `lucca_list_employees`, `lucca_list_employment_templates`, `lucca_list_employments`, `lucca_list_job_positions`, `lucca_list_job_qualifications`, `lucca_list_legal_entities`, `lucca_list_occupation_categories`, `lucca_list_probationary_periods`, `lucca_list_professions`, `lucca_list_taxonomies`, `lucca_list_taxonomy_labels` `auth` `breaking-changes` Migrated to per-auth-type scope requirements. All actions are now accessible with both OAuth 2.0 and API Key authentication. # Lucid Source: https://docs.stackone.com/connectors/lucid/index How to set up the Lucid connector, plus the actions that are available.
Lucid
Betav1.0.0
60 actions · 2 auth methods
IAM Documents Storage
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth 2.0 client on the Lucid developer portal. Uses the authorization code flow with granular p... Uses a long-lived Lucid API key created on the Lucid team administration page. The key acts on behalf of the user who cr... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lucid/index.md for the full list. # Lucid Changelog Source: https://docs.stackone.com/connectors/lucid/changelog Release history for the Lucid connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Migrated to authRequirements for per-auth-type scope control; gated the share-link actions to OAuth 2.0 (not available with API Key) and removed the non-functional create_user action. `lucid_create_user` `lucid_add_team_users`, `lucid_archive_team`, `lucid_copy_document`, `lucid_create_document`, `lucid_create_document_share_link`, `lucid_create_folder`, `lucid_create_folder_share_link`, `lucid_create_mermaid_diagram`, `lucid_create_team`, `lucid_create_thread_comment`, `lucid_delete_document_share_link`, `lucid_delete_folder_share_link`, `lucid_export_document_async`, `lucid_get_account`, `lucid_get_document`, `lucid_get_document_content`, `lucid_get_document_export_status`, `lucid_get_document_share_link`, `lucid_get_document_team_collaborator`, `lucid_get_document_user_collaborator`, `lucid_get_folder`, `lucid_get_folder_share_link`, `lucid_get_folder_team_collaborator`, `lucid_get_folder_user_collaborator`, `lucid_get_mermaid_diagram`, `lucid_get_profile`, `lucid_get_team`, `lucid_get_user`, `lucid_list_document_collaborators`, `lucid_list_document_threads`, `lucid_list_folder_collaborators`, `lucid_list_folder_contents`, `lucid_list_mermaid_diagrams`, `lucid_list_root_contents`, `lucid_list_team_users`, `lucid_list_teams`, `lucid_list_thread_comments`, `lucid_list_users`, `lucid_remove_document_team_collaborator`, `lucid_remove_document_user_collaborator`, `lucid_remove_folder_team_collaborator`, `lucid_remove_folder_user_collaborator`, `lucid_remove_team_users`, `lucid_restore_folder`, `lucid_restore_team`, `lucid_search_documents`, `lucid_search_folders`, `lucid_search_users`, `lucid_set_document_team_collaborator`, `lucid_set_document_user_collaborator`, `lucid_set_folder_team_collaborator`, `lucid_set_folder_user_collaborator`, `lucid_trash_document`, `lucid_trash_folder`, `lucid_update_document`, `lucid_update_document_share_link`, `lucid_update_folder`, `lucid_update_folder_share_link`, `lucid_update_mermaid_diagram`, `lucid_update_team` `data-sync` Enabled Data Sync for the account-wide list actions (users, teams, root contents), paging through records with the next-page cursor from the Link response header. `lucid_list_root_contents`, `lucid_list_teams`, `lucid_list_users` `new-actions` Initial Lucid connector with 60 actions across documents, folders, users, teams, collaborators, share links, comments, and Mermaid diagrams. Supports OAuth 2.0 and API key authentication. # LunarCrush Source: https://docs.stackone.com/connectors/lunarcrush/index How to set up the LunarCrush connector, plus the actions that are available.
LunarCrush
Betav0.2.0
37 actions · 1 auth method
Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticates with a LunarCrush API key sent as a Bearer token. Keys are generated per account (up to 10 active) from th... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lunarcrush/index.md for the full list. # LunarCrush Changelog Source: https://docs.stackone.com/connectors/lunarcrush/changelog Release history for the LunarCrush connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for coins, stocks, NFTs, topics, categories, creators and saved searches. `lunarcrush_list_categories`, `lunarcrush_list_coins`, `lunarcrush_list_creators`, `lunarcrush_list_nfts`, `lunarcrush_list_searches`, `lunarcrush_list_stocks`, `lunarcrush_list_topics` `new-connector` Initial action mapping # Lusha Source: https://docs.stackone.com/connectors/lusha/index How to set up the Lusha connector, plus the actions that are available.
Lusha
Previewv1.1.1
40 actions · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate and retrieve your Lusha API key from the Lusha Dashboard under API > Manage API Keys. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/lusha/index.md for the full list. # Lusha Changelog Source: https://docs.stackone.com/connectors/lusha/changelog Release history for the Lusha connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` The four filter search actions now state the search text rules and reject text that is too short or uses unsupported characters before calling Lusha. `lusha_search_company_locations`, `lusha_search_company_names`, `lusha_search_company_technologies`, `lusha_search_contact_locations` `new-feature` `data-sync` Added data sync support to 8 list actions, covering webhook subscriptions and the company and contact filter lists, synced as full refreshes. Action release stages updated, with existing preview actions moved to beta. # Magento Source: https://docs.stackone.com/connectors/magento/index How to set up the Magento connector, plus the actions that are available.
Magento
Previewv1.0.0
128 actions · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/magento/index.md for the full list. # Magnit Client(PRO Unlimited Wand VMS) Source: https://docs.stackone.com/connectors/magnit/index How to set up the Magnit Client(PRO Unlimited Wand VMS) connector, plus the actions that are available.
Magnit Client(PRO Unlimited Wand VMS)
Betav1.0.0
15 actions · 1 auth method
Vendor Management System
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Magnit uses an OAuth 2.0 resource-owner password grant. Your API credentials (Client ID/Secret for HTTP Basic and an API... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/magnit/index.md for the full list. # Magnit (PRO Unlimited Wand VMS) Changelog Source: https://docs.stackone.com/connectors/magnit/changelog Release history for the Magnit (PRO Unlimited Wand VMS) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Initial Magnit (PRO Unlimited Wand VMS) connector release with action mapping across cost centers, locations, managers, custom fields, workers (inbound/outbound), purchase orders, approvals, onboarding items, statuses, and sourcing requests. # Magnit Gateway Source: https://docs.stackone.com/connectors/magnitgateway/index How to set up the Magnit Gateway connector, plus the actions that are available.
Magnit Gateway
Betav0.1.0
32 actions · 1 auth method
Vendor Management System
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an active Magnit Gateway subscription. A supplier user with API Admin or Group API Admin permission generates t... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/magnitgateway/index.md for the full list. # Magnit Gateway Changelog Source: https://docs.stackone.com/connectors/magnitgateway/changelog Release history for the Magnit Gateway connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Initial Magnit Gateway (Supplier API) connector with actions for staffing and SOW requests, candidate submissions, worker profiles, staffing engagements, timecards, billing items, invoices, and webhook subscriptions. # Mailchimp Source: https://docs.stackone.com/connectors/mailchimp/index How to set up the Mailchimp connector, plus the actions and events that are available.
Mailchimp
v1.2.0
91 actions · 7 events · 2 auth methods
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth app. Best for single-account integrations and scripts. The datacenter prefix is automatically extracted from your API key. Optionally, configure receiving Events for Mailchimp into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mailchimp/index.md for the full list. ## Events See https://docs.stackone.com/connectors/mailchimp/index.md for the full list. # Mailchimp Changelog Source: https://docs.stackone.com/connectors/mailchimp/changelog Release history for the Mailchimp connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `bug-fix` Added data sync for audiences, automations, campaigns, templates, template folders, landing pages, Facebook ads, batch operations, and batch webhooks. Create Landing Page now accepts template type and template ID, fixing a 400 error. `mailchimp_create_landing_page`, `mailchimp_list_audiences`, `mailchimp_list_automations`, `mailchimp_list_batch_requests`, `mailchimp_list_batch_webhooks`, `mailchimp_list_campaigns`, `mailchimp_list_email_templates`, `mailchimp_list_facebook_ads`, `mailchimp_list_landing_pages`, `mailchimp_list_template_folders` `new-actions` Added webhook event support for audience events (subscribe, unsubscribe, profile, upemail, cleaned, campaign) with programmatic per-audience webhook registration via comma-separated audience IDs. # MailerLite Source: https://docs.stackone.com/connectors/mailerlite/index How to set up the MailerLite connector, plus the actions and events that are available.
MailerLite
v1.1.1
51 actions · 12 events · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an account-issued API token as a Bearer token in the Authorization header. No OAuth app registration or scopes; the... Optionally, configure receiving Events for MailerLite into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mailerlite/index.md for the full list. ## Events See https://docs.stackone.com/connectors/mailerlite/index.md for the full list. # MailerLite Changelog Source: https://docs.stackone.com/connectors/mailerlite/changelog Release history for the MailerLite connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `description-fix` Clarified that List Forms and List Segments return only form and segment summaries, and pointed to List Form Subscribers and List Segment Subscribers for the subscribers behind them. `mailerlite_list_forms`, `mailerlite_list_segments` `data-sync` Added Data Sync support for automations, campaigns, campaign languages, custom fields, groups, segments, subscribers, timezones and webhooks, so these collections can be kept in sync and paged through in full rather than fetched one page at a time. `mailerlite_list_automations`, `mailerlite_list_campaign_languages`, `mailerlite_list_campaigns`, `mailerlite_list_fields`, `mailerlite_list_groups`, `mailerlite_list_segments`, `mailerlite_list_subscribers`, `mailerlite_list_timezones`, `mailerlite_list_webhooks` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `description-fix` Documented the exact A/B and multivariate test settings that create_campaign requires, and clarified that get_campaign and get_subscriber_activity take numeric IDs rather than names or email addresses. `mailerlite_create_campaign`, `mailerlite_get_campaign`, `mailerlite_get_subscriber_activity`, `mailerlite_update_campaign` `new-actions` MailerLite connector with 45 actions plus auto-provisioned inbound webhook events for 11 subscriber and campaign events. # Mailgun Source: https://docs.stackone.com/connectors/mailgun/index How to set up the Mailgun connector, plus the actions and events that are available.
Mailgun
v1.3.0
96 actions · 9 events · 1 auth method
Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Mailgun private API key for authentication. Access API Security from your account dropdown menu in the top-righ... Optionally, configure receiving Events for Mailgun into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mailgun/index.md for the full list. ## Events See https://docs.stackone.com/connectors/mailgun/index.md for the full list. # Mailgun Changelog Source: https://docs.stackone.com/connectors/mailgun/changelog Release history for the Mailgun connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added webhook events for message activity - accepted, delivered, opened, clicked, unsubscribed, complained, and permanent and temporary failures. StackOne registers the Mailgun webhooks automatically when events are enabled. `data-sync` Added periodic data sync to nine list actions - domains, mailing lists, account templates, routes, webhooks, IPs, users, and the unified user and role lists. Each refreshes in full on every run, since Mailgun exposes no updated-since filters. `mailgun_list_account_templates`, `mailgun_list_domains`, `mailgun_list_ips`, `mailgun_list_mailing_lists`, `mailgun_list_routes`, `mailgun_list_users`, `mailgun_list_webhooks`, `mailgun_unified_list_roles`, `mailgun_unified_list_users` `new-actions` Added unified IAM users, roles, groups, and credentials actions. # Mailjet Source: https://docs.stackone.com/connectors/mailjet/index How to set up the Mailjet connector, plus the actions and events that are available.
Mailjet
v1.2.0
59 actions · 8 events · 1 auth method
Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses HTTP Basic authentication with your Mailjet API Key as the username and Secret Key as the password. Both are found... Optionally, configure receiving Events for Mailjet into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mailjet/index.md for the full list. ## Events See https://docs.stackone.com/connectors/mailjet/index.md for the full list. # Mailjet Changelog Source: https://docs.stackone.com/connectors/mailjet/changelog Release history for the Mailjet connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added native webhook support for Mailjet message events — sent, open, click, bounce, blocked, spam, and unsubscribe — delivered through the Event API and routed by event type. `data-sync` Added scheduled data sync to ten list actions — contacts, contact lists, segments, contact properties, event callbacks, senders, templates, messages, campaign drafts, and campaigns — so these collections can be kept in sync and read back without calling Mailjet on every request. Each refreshes in full on every run, since Mailjet has no consistent updated-since filter to drive incremental sync. `mailjet_list_campaign_drafts`, `mailjet_list_campaigns`, `mailjet_list_contact_lists`, `mailjet_list_contact_properties`, `mailjet_list_contacts`, `mailjet_list_event_callbacks`, `mailjet_list_messages`, `mailjet_list_segments`, `mailjet_list_senders`, `mailjet_list_templates` `bug-fix` Required double-quoted string values in create/update_segment expressions, removed the invalid Unverified sender Status filter, documented ID-only sorting on list_segments and list_campaign_drafts, and added recovery/precondition guidance to create_sender and schedule_campaign_draft. # Make Source: https://docs.stackone.com/connectors/make/index How to set up the Make connector, plus the actions and events that are available.
Make
Previewv2.1.0
70 actions · 1 event · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API token from your Make account settings. Admin privileges may be required for certain operations. Optionally, configure receiving Events for Make into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/make/index.md for the full list. ## Events See https://docs.stackone.com/connectors/make/index.md for the full list. # Make Changelog Source: https://docs.stackone.com/connectors/make/changelog Release history for the Make connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for organizations, user roles, unified organizations, unified groups, unified roles and unified users, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Make API exposes no updated-since filter a sync can use. `make_list_organizations`, `make_list_user_roles`, `make_unified_list_groups`, `make_unified_list_organizations`, `make_unified_list_roles`, `make_unified_list_users` `breaking` `bug-fix` Users now include their avatar, last login time, and a pending status for invited users (needs the organizations:read scope), and every action now declares the exact token scopes it requires. `make_create_agent`, `make_create_ai_agent`, `make_create_connection`, `make_create_data_structure`, `make_create_device_request`, `make_create_key`, `make_create_organization`, `make_create_scenario`, `make_create_scenario_folder`, `make_create_team`, `make_delete_agent`, `make_delete_ai_agent`, `make_delete_connection`, `make_delete_data_structure`, `make_delete_organization`, `make_delete_scenario`, `make_get_agent`, `make_get_ai_agent`, `make_get_connection`, `make_get_connection_editable_schema`, `make_get_current_user`, `make_get_organization`, `make_get_organization_subscription`, `make_get_organization_usage`, `make_get_scenario`, `make_get_team`, `make_get_team_llm_configuration`, `make_get_team_usage`, `make_get_user_organization_role`, `make_get_user_team_role`, `make_list_agents`, `make_list_ai_agent_scenarios`, `make_list_ai_agents`, `make_list_connections`, `make_list_data_structures`, `make_list_devices`, `make_list_keys`, `make_list_llm_providers`, `make_list_organizations`, `make_list_scenario_folders`, `make_list_scenarios`, `make_list_teams`, `make_list_user_organization_roles`, `make_list_user_roles`, `make_list_user_team_roles`, `make_list_users`, `make_rename_connection`, `make_run_ai_agent`, `make_run_scenario`, `make_start_scenario`, `make_stop_scenario`, `make_unified_get_group`, `make_unified_get_me`, `make_unified_get_organization`, `make_unified_get_role`, `make_unified_get_user`, `make_unified_list_groups`, `make_unified_list_organizations`, `make_unified_list_roles`, `make_unified_list_users`, `make_update_agent`, `make_update_ai_agent`, `make_update_connection_data`, `make_update_organization`, `make_update_scenario`, `make_update_team_llm_configuration`, `make_update_user`, `make_update_user_team_role`, `make_verify_connection`, `make_verify_connection_scoped` `description-fix` List User Roles now states it returns the role catalog (used to name the usersRoleId in a user's role assignments), and Get Connection Editable Schema now states it returns the editable parameter names rather than a yes/no flag. `make_get_connection_editable_schema`, `make_list_user_roles` `guide-changes` The API Token guide now lists the exact token scopes to tick in Make's Add token dialog, and explains that this dialog is the only place a token's scopes are set. `guide-changes` Reworked the API Token connection guide with screenshots for every portal step, the exact scopes to select when creating a token, and how to find your zone. `bug-fix` Standardized action category capitalization for more consistent portal filters. `make_unified_get_group`, `make_unified_get_me`, `make_unified_get_organization`, `make_unified_get_role`, `make_unified_get_user`, `make_unified_list_groups`, `make_unified_list_organizations`, `make_unified_list_roles`, `make_unified_list_users` `new-actions` Add unified IAM actions for users, roles, teams, and organizations, plus a credentials/identity action for the connected API token. `make_unified_get_group`, `make_unified_get_me`, `make_unified_get_organization`, `make_unified_get_role`, `make_unified_get_user`, `make_unified_list_groups`, `make_unified_list_organizations`, `make_unified_list_roles`, `make_unified_list_users` `new-actions` Add native inbound webhook support — paste the Native Webhook URL into a Make scenario's HTTP module to deliver events to StackOne. # Manatal Source: https://docs.stackone.com/connectors/manatal/index How to set up the Manatal connector, plus the actions that are available.
Manatal
Betav2.2.0
132 actions · 1 auth method
ATS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Manatal uses API token authentication. The token must be sent as "Token <value>" in the Authorization header. Enterprise... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/manatal/index.md for the full list. # Manatal Changelog Source: https://docs.stackone.com/connectors/manatal/changelog Release history for the Manatal connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support to thirteen list actions: candidates, contacts, jobs, matches, organizations, users, unified users, job pipelines, match stages, currencies, industries, languages, and nationalities. Candidates, contacts, jobs, matches, and organizations sync incrementally using the updated_at__gte filter; the other eight sync by full refresh. `manatal_list_candidates`, `manatal_list_contacts`, `manatal_list_currencies`, `manatal_list_industries`, `manatal_list_job_pipelines`, `manatal_list_jobs`, `manatal_list_languages`, `manatal_list_match_stages`, `manatal_list_matches`, `manatal_list_nationalities`, `manatal_list_organizations`, `manatal_list_users`, `manatal_unified_list_users` `new-actions` Added unified IAM user lookups, so you can list and review the people who have a Manatal account. # Manufact Source: https://docs.stackone.com/connectors/manufact/index How to set up the Manufact connector, plus the actions that are available.
Manufact
v1.1.0
71 actions · 1 auth method
Developer Tools AI IAM Billing Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key authentication. Manufact accepts the key as a bearer token in the Authorization header on every request. There i... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/manufact/index.md for the full list. # Manufact Changelog Source: https://docs.stackone.com/connectors/manufact/changelog Release history for the Manufact connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Servers, deployments, agents, server pools, organizations and API keys can now be kept in sync automatically, so they stay up to date without polling them yourself. `manufact_list_agents`, `manufact_list_api_keys`, `manufact_list_deployments`, `manufact_list_organizations`, `manufact_list_server_pools`, `manufact_list_servers` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `new-actions` `bug-fix` Added actions to list GitHub App installations and the repositories each can access, so a repository can now be connected to a server end to end. Clarified which agents can be modified and when repository actions do not apply. `manufact_list_github_installations`, `manufact_list_installation_repositories` `manufact_delete_agent`, `manufact_get_deployment_runtime_logs`, `manufact_get_server_analytics_health`, `manufact_get_server_requests_by_country`, `manufact_list_agents`, `manufact_list_server_actor_labels`, `manufact_list_server_client_breakdown`, `manufact_list_server_tool_breakdown`, `manufact_list_server_tool_errors`, `manufact_set_server_repository`, `manufact_start_agent_chat`, `manufact_unlink_server_repository`, `manufact_update_agent` `new-connector` Initial action mapping of the Manufact Cloud connector for MCP server deployment, hosting, monitoring and distribution, with an API key setup guide. # Marketo Source: https://docs.stackone.com/connectors/marketo/index How to set up the Marketo connector, plus the actions that are available.
Marketo
Betav1.1.0
59 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 client credentials issued by a Marketo Custom Service (Admin then LaunchPoint then New Service,... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/marketo/index.md for the full list. # Marketo Changelog Source: https://docs.stackone.com/connectors/marketo/changelog Release history for the Marketo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for eight collection actions — the Asset API browse endpoints (list_email_templates, list_forms, list_landing_pages, list_landing_page_templates, get_programs) on offset pagination, the Lead Database field schema (get_lead_fields) on nextPageToken cursor pagination, and the two single-call reference collections (get_activity_types, get_lead_partitions). All eight full-refresh on every run. No change to any action's request behaviour, inputs or validation. # Matillion Source: https://docs.stackone.com/connectors/matillion/index How to set up the Matillion connector, plus the actions and events that are available.
Matillion
v1.2.0
40 actions · 6 events · 1 auth method
Data Integration
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses OAuth2 client credentials flow with client\_id and client\_secret to obtain a 30-minute JWT bearer token. Only Super... Optionally, configure receiving Events for Matillion into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/matillion/index.md for the full list. ## Events See https://docs.stackone.com/connectors/matillion/index.md for the full list. # Matillion Changelog Source: https://docs.stackone.com/connectors/matillion/changelog Release history for the Matillion connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to the list projects, list agents, list pipeline executions, and list test executions actions. `matillion_list_agents`, `matillion_list_pipeline_executions`, `matillion_list_projects`, `matillion_list_test_executions` `guide` Updated OAuth 2.0 (Client Credentials) connection guide. `matillion_list_pipeline_executions`, `matillion_list_test_executions`, `matillion_update_agent` `new-events` Added webhook events and webhook setup guides. # Medium Source: https://docs.stackone.com/connectors/medium/index How to set up the Medium connector, plus the actions that are available.
Medium
Betav1.0.0
5 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a pre-existing integration token. Medium stopped issuing new tokens on January 1, 2025. Only accounts with tokens c... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/medium/index.md for the full list. # MeisterTask Source: https://docs.stackone.com/connectors/meistertask/index How to set up the MeisterTask connector, plus the actions that are available.
MeisterTask
Previewv1.0.0
56 actions · 2 auth methods
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authorization code flow delegated to MindMeister (shared Meister SSO per https://developers.mindmeister.com/do... Static personal access token generated at https://www.mindmeister.com/api. Sent as \`Authorization Bearer <token>\` on eve... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/meistertask/index.md for the full list. ## References Full REST API reference for MeisterTask. Bearer token and OAuth 2.0 details. How to register an OAuth client for MeisterTask (shared Meister SSO). How to generate a personal access token. # Mercury Source: https://docs.stackone.com/connectors/mercury/index How to set up the Mercury connector, plus the actions that are available.
Mercury
v1.1.0
47 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses static subscription-key + tenant-id headers issued by Mercury via Azure API Management. Requires per-customer onboa... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mercury/index.md for the full list. # Mercury Changelog Source: https://docs.stackone.com/connectors/mercury/changelog Release history for the Mercury connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for contacts, vacancies, clients, users, activity purposes, placements, placement fees, contact skills, contact education, and contact work history. pageNumber is now optional on list contacts and list vacancies — it is derived from pageCookie when omitted — and contact skills, education, and work history gained optional pageCookie and pageNumber query parameters for paging. `mercury_get_all_activity_purposes`, `mercury_get_all_clients`, `mercury_get_all_contact_education`, `mercury_get_all_contact_skills`, `mercury_get_all_contact_work_history`, `mercury_get_all_contacts`, `mercury_get_all_placement_fees`, `mercury_get_all_placements`, `mercury_get_all_users`, `mercury_get_all_vacancies` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Standardized action category capitalization for more consistent portal filters. `mercury_create_client`, `mercury_create_contact`, `mercury_create_contact_activity`, `mercury_create_contact_annotation`, `mercury_create_placement_compliance`, `mercury_create_vacancies_batch`, `mercury_cv_parse_create_candidate`, `mercury_cv_parse_update_candidate`, `mercury_get_activities_by_contact`, `mercury_get_all_activity_purposes`, `mercury_get_all_clients`, `mercury_get_all_contact_education`, `mercury_get_all_contact_skills`, `mercury_get_all_contact_work_history`, `mercury_get_all_contacts`, `mercury_get_all_placement_fees`, `mercury_get_all_placements`, `mercury_get_all_users`, `mercury_get_all_vacancies`, `mercury_get_annotations_by_contact`, `mercury_get_candidate`, `mercury_get_candidate_company`, `mercury_get_client`, `mercury_get_compliance`, `mercury_get_compliance_by_placement`, `mercury_get_contact`, `mercury_get_contact_cv`, `mercury_get_file_content`, `mercury_get_file_details_by_contact`, `mercury_get_finance_rates_by_placement`, `mercury_get_placement`, `mercury_get_placement_fees_by_placement`, `mercury_get_placements_by_candidate`, `mercury_get_shortlists_by_vacancy`, `mercury_get_user`, `mercury_get_vacancy`, `mercury_patch_client`, `mercury_patch_compliance`, `mercury_patch_contact`, `mercury_patch_skill_level`, `mercury_patch_vacancies_batch`, `mercury_patch_work_history`, `mercury_update_vacancies_batch`, `mercury_upload_candidate_document`, `mercury_upload_compliance_evidence`, `mercury_upload_contact_cv`, `mercury_upload_contact_document` `description-fix` `config-changes` Description fixes on contacts, vacancies and placements: `User Field N` key format for custom fields, Permanent vs Contract/Temporary detail-block rules (Benefits + BonusShares required, no mixing), `get_shortlists_by_vacancy` 404-on-empty, direct HiringManager `{Name, Email}` on `create_vacancies_batch`, clearer `get_all_vacancies` pagination, and removal of the non-functional `advertiseOnWebsite` filter from `get_all_vacancies` (provider silently ignored the param — verified against the tenant). `mercury_create_contact`, `mercury_create_vacancies_batch`, `mercury_get_all_vacancies`, `mercury_get_placement`, `mercury_get_shortlists_by_vacancy`, `mercury_patch_contact`, `mercury_patch_vacancies_batch`, `mercury_update_vacancies_batch` `new-connector` Initial release of the Mercury (Mercury xRM) connector — 47 actions across contacts, candidates, clients, vacancies, placements, activities, annotations, documents, users, skills, education, and work history, with preview support for compliance records and candidate companies. Custom subscription-key + tenant-id header authentication via Azure API Management, plus a full connection guide walking through the Mercury Public API developer portal to obtain credentials. # Metabase Source: https://docs.stackone.com/connectors/metabase/index How to set up the Metabase connector, plus the actions that are available.
Metabase
Previewv0.1.1
14 actions · 1 auth method
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Metabase API key sent in the X-API-Key header, for self-hosted Metabase or Metabase Cloud. The key acts with the... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/metabase/index.md for the full list. # Metabase Changelog Source: https://docs.stackone.com/connectors/metabase/changelog Release history for the Metabase connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Native actions are now also listed under Analytics, the API key guide opens API keys from the Authentication menu and names the Key name and Group fields, and some group and user descriptions now name the Metabase version or plan they apply to. `metabase_get_current_user`, `metabase_get_group`, `metabase_get_user`, `metabase_list_api_keys`, `metabase_list_group_memberships`, `metabase_list_groups`, `metabase_list_users`, `metabase_unified_get_user`, `metabase_unified_list_groups`, `metabase_unified_list_users` `new-connector` Initial Metabase connector for reviewing who has access to a Metabase instance, covering people, groups, group memberships, admin and group manager roles, and API keys, including unified IAM users, groups, roles and connection details. # Microsoft Dynamics 365 Business Central Source: https://docs.stackone.com/connectors/dynamics365bc/index How to set up the Microsoft Dynamics 365 Business Central connector, plus the actions and events that are available.
Microsoft Dynamics 365 Business Central
v3.0.0
70 actions · 64 events · 1 auth method
ERP
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect Business Central. You'll need to register an Azure applicat... Optionally, configure receiving Events for Microsoft Dynamics 365 Business Central into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/dynamics365bc/index.md for the full list. ## Events See https://docs.stackone.com/connectors/dynamics365bc/index.md for the full list. # Microsoft Dynamics 365 Business Central Changelog Source: https://docs.stackone.com/connectors/dynamics365bc/changelog Release history for the Microsoft Dynamics 365 Business Central connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` `bug-fix` Company ID is now required when connecting an account and is checked at connection time, so data sync works for every company-scoped list action. `auth` `breaking` `webhook` `data-sync` Migrated to authRequirements for per-auth-type scope control. Added webhook events for 62 Business Central change types with subscriptions created automatically in every company, data sync for 21 list actions, and an optional default Company ID connection setting. # Microsoft Entra ID Source: https://docs.stackone.com/connectors/microsoftentraid/index How to set up the Microsoft Entra ID connector, plus the actions and events that are available.
Microsoft Entra ID
Previewv1.2.0
68 actions · 6 events · 2 auth methods
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth app in Microsoft Entra ID. Uses delegated permissions on behalf of a signed-in user. Requi... Requires registering an OAuth app in Microsoft Entra ID. Restricts authentication to a single tenant using the Tenant ID... Optionally, configure receiving Events for Microsoft Entra ID into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/microsoftentraid/index.md for the full list. ## Events See https://docs.stackone.com/connectors/microsoftentraid/index.md for the full list. # Microsoft Entra ID Changelog Source: https://docs.stackone.com/connectors/microsoftentraid/changelog Release history for the Microsoft Entra ID connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added webhook event support for 4 event types (users and groups updated or permanently deleted), delivered through Microsoft Graph subscriptions that StackOne creates and removes automatically. `microsoftentraid_delete_group` `data-sync` `bug-fix` Added Data Sync support for 12 list actions (users, groups, devices, applications, service principals, OAuth2 permission grants, conditional access policies, named locations, organizations, domains, directory roles, role templates), all refreshing in full each run. All 21 list actions now return the full Microsoft Graph response, and the 8 paginated ones accept a skiptoken input and return a next token so callers can page past the first page. `microsoftentraid_list_applications`, `microsoftentraid_list_conditional_access_policies`, `microsoftentraid_list_device_member_of`, `microsoftentraid_list_device_registered_owners`, `microsoftentraid_list_device_registered_users`, `microsoftentraid_list_devices`, `microsoftentraid_list_directory_role_members`, `microsoftentraid_list_directory_roles`, `microsoftentraid_list_domain_service_configuration_records`, `microsoftentraid_list_domain_verification_dns_records`, `microsoftentraid_list_domains`, `microsoftentraid_list_group_members`, `microsoftentraid_list_groups`, `microsoftentraid_list_named_locations`, `microsoftentraid_list_oauth2_permission_grants`, `microsoftentraid_list_organizations`, `microsoftentraid_list_role_templates`, `microsoftentraid_list_service_principal_app_role_assignments`, `microsoftentraid_list_service_principals`, `microsoftentraid_list_user_app_role_assignments`, `microsoftentraid_list_users` `bug-fix` Documented $search "property:value" syntax and the $filter startswith alternative (contains() unsupported) on list_users, list_service_principals, list_applications, and list_groups. Corrected the all-zeros appRoleId guidance on the app-role-assignment creates to match Microsoft Graph docs (valid when the resource service principal has no declared appRoles). # Microsoft Excel Source: https://docs.stackone.com/connectors/microsoftexcel/index How to set up the Microsoft Excel connector, plus the actions that are available.
Microsoft Excel
Previewv1.2.0
102 actions · 1 auth method
Productivity
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect Microsoft Excel. You'll need to register an Azure applicati... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/microsoftexcel/index.md for the full list. # Microsoft Excel Changelog Source: https://docs.stackone.com/connectors/microsoftexcel/changelog Release history for the Microsoft Excel connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Enabled scheduled data sync on List Excel Files, so the set of Excel workbooks in the connected user's OneDrive can be kept in sync and read without searching Microsoft Graph on every request. It refreshes in full each run, because the Graph search endpoint exposes no updated-since filter. The action also returns a new result key, next, holding the bare skiptoken taken from the Graph @odata.nextLink URL, which is what lets the sync engine request the following page; existing fields are unchanged. No other list action qualifies, because every other Excel collection is addressed inside one workbook and requires a file_id, which a sync schedule cannot enumerate. `microsoftexcel_list_excel_files` `bug-fix` `description-fix` Added empty body rejection warnings to 11 actions. Removed unsupported Custom from update_chart_legend position enum. Added limitation warnings to get_chart_point, get_named_item_range, create_chart_series, apply_table_sort, update_table_sort_icon. Added dimension normalization note to update_chart. Updated list_chart_points select description. # Microsoft Intune Source: https://docs.stackone.com/connectors/microsoftintune/index How to set up the Microsoft Intune connector, plus the actions that are available.
Microsoft Intune
v1.1.0
43 actions · 2 auth methods
Device Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). App-only access using client credentials flow. No user sign-in required. Uses application permissions granted by an admi... Delegated access on behalf of a signed-in user, using an app registration in Microsoft Entra ID. Access is limited to th... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/microsoftintune/index.md for the full list. # Microsoft Intune Changelog Source: https://docs.stackone.com/connectors/microsoftintune/changelog Release history for the Microsoft Intune connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Enabled scheduled data sync on eight list actions covering managed devices, device compliance policies, device configurations, device enrollment configurations, detected apps, mobile apps, mobile app categories and Intune role definitions, so these collections can be kept in sync and read without calling Microsoft Graph on every request. All eight refresh in full each run, because Graph filters changes on these endpoints only through a whole $filter expression and exposes no delta query under deviceManagement. Detected app managed devices and role assignments are not included, because each is scoped to a single parent id that a sync schedule cannot enumerate. `microsoftintune_list_detected_apps`, `microsoftintune_list_device_compliance_policies`, `microsoftintune_list_device_configurations`, `microsoftintune_list_device_enrollment_configurations`, `microsoftintune_list_managed_devices`, `microsoftintune_list_mobile_app_categories`, `microsoftintune_list_mobile_apps`, `microsoftintune_list_role_definitions` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `description-fix` Improved assign_device_configuration action descriptions for agentic use case. `microsoftintune_assign_device_configuration` `description-fix` Improved action descriptions for agentic use — added @odata.type not-selectable warning to all list actions, clarified get vs list projection differences for managed devices and role definitions, documented nextLink paging behavior on filtered role queries, warned against non-existent members property on role assignments, and noted @odata.count inconsistency on mobileApps. Removed unsupported $search from compliance policies and device configurations. `microsoftintune_get_managed_device`, `microsoftintune_get_role_definition`, `microsoftintune_list_detected_apps`, `microsoftintune_list_device_compliance_policies`, `microsoftintune_list_device_configurations`, `microsoftintune_list_device_enrollment_configurations`, `microsoftintune_list_managed_devices`, `microsoftintune_list_mobile_app_categories`, `microsoftintune_list_mobile_apps`, `microsoftintune_list_role_assignments`, `microsoftintune_list_role_definitions` `new-feature` `auth-improvements` Added a delegated OAuth 2.0 authorization code flow alongside the existing client credentials option, with client ID and secret at the setup level and tenant ID per account. `microsoftintune_assign_device_compliance_policy`, `microsoftintune_assign_device_configuration`, `microsoftintune_assign_device_enrollment_configuration`, `microsoftintune_assign_mobile_app`, `microsoftintune_bypass_activation_lock`, `microsoftintune_clean_windows_device`, `microsoftintune_create_role_definition`, `microsoftintune_delete_device_compliance_policy`, `microsoftintune_delete_device_configuration`, `microsoftintune_delete_managed_device`, `microsoftintune_delete_role_definition`, `microsoftintune_disable_lost_mode`, `microsoftintune_get_detected_app`, `microsoftintune_get_device_category`, `microsoftintune_get_device_compliance_policy`, `microsoftintune_get_device_configuration`, `microsoftintune_get_device_enrollment_configuration`, `microsoftintune_get_managed_device`, `microsoftintune_get_mobile_app`, `microsoftintune_get_mobile_app_category`, `microsoftintune_get_role_definition`, `microsoftintune_list_detected_app_managed_devices`, `microsoftintune_list_detected_apps`, `microsoftintune_list_device_compliance_policies`, `microsoftintune_list_device_configurations`, `microsoftintune_list_device_enrollment_configurations`, `microsoftintune_list_managed_devices`, `microsoftintune_list_mobile_app_categories`, `microsoftintune_list_mobile_apps`, `microsoftintune_list_role_assignments`, `microsoftintune_list_role_definitions`, `microsoftintune_locate_device`, `microsoftintune_reboot_device`, `microsoftintune_remote_lock`, `microsoftintune_reset_passcode`, `microsoftintune_retire_managed_device`, `microsoftintune_set_enrollment_priority`, `microsoftintune_shut_down_device`, `microsoftintune_sync_device`, `microsoftintune_update_role_definition`, `microsoftintune_windows_defender_scan`, `microsoftintune_windows_defender_update_signatures`, `microsoftintune_wipe_managed_device` `description-fix` `guide-fix` Updated setup guide with concrete permission instructions and corrected field descriptions to reference Microsoft Entra admin center. `new-actions` Initial Microsoft Intune connector with 43 actions covering managed devices, compliance policies, device configurations, mobile apps, RBAC roles, enrollment configurations, and detected apps. Uses client credentials OAuth2 with application permissions. # Microsoft OneDrive Source: https://docs.stackone.com/connectors/microsoftonedrive/index How to set up the Microsoft OneDrive connector, plus the actions that are available.
Microsoft OneDrive
v1.1.0
46 actions · 1 auth method
Storage Documents IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect Microsoft OneDrive. You'll need to register an Azure applic... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/microsoftonedrive/index.md for the full list. # Microsoft OneDrive Changelog Source: https://docs.stackone.com/connectors/microsoftonedrive/changelog Release history for the Microsoft OneDrive connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `downstream-change` Enable DataSync v2 on the 6 list actions without required inputs (list_drives, list_followed_items, list_users, unified_list_drives, unified_list_files, unified_list_folders) using cursor pagination over the Graph skiptoken. Adds the unmapped skipToken and top query parameters to list_users and list_followed_items, and a nextSkipToken response field on the DataSync-enabled non-unified list actions. `microsoftonedrive_list_drives`, `microsoftonedrive_list_followed_items`, `microsoftonedrive_list_users`, `microsoftonedrive_unified_list_drives`, `microsoftonedrive_unified_list_files`, `microsoftonedrive_unified_list_folders` `bug-fix` `description-fix` Fix checkin_drive_item 502 by removing invalid "unspecified" checkInAs enum value, improve get_drive_item_thumbnails description for better agent discoverability. `microsoftonedrive_checkin_drive_item`, `microsoftonedrive_get_drive_item_thumbnails` `description-fix` Fix copy parentReference camelCase, improve sharing/permissions/thumbnail/download descriptions. `microsoftonedrive_add_permission`, `microsoftonedrive_copy_drive_item`, `microsoftonedrive_create_sharing_link`, `microsoftonedrive_download_drive_item`, `microsoftonedrive_get_drive_item_thumbnails`, `microsoftonedrive_list_users`, `microsoftonedrive_restore_drive_item`, `microsoftonedrive_update_drive_item` `description-fix` Description fixes for error handling across search, copy, sharing, checkin, path lookup, and version download actions. # Microsoft Outlook Source: https://docs.stackone.com/connectors/microsoftoutlook/index How to set up the Microsoft Outlook connector, plus the actions and events that are available.
Microsoft Outlook
v2.2.0
39 actions · 5 events · 1 auth method
Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect Microsoft Outlook. You'll need to register an Azure applica... Optionally, configure receiving Events for Microsoft Outlook into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/microsoftoutlook/index.md for the full list. ## Events See https://docs.stackone.com/connectors/microsoftoutlook/index.md for the full list. # Microsoft Outlook Changelog Source: https://docs.stackone.com/connectors/microsoftoutlook/changelog Release history for the Microsoft Outlook connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added webhook events for messages added, changed and removed in a connected mailbox. StackOne creates and removes the Microsoft subscription automatically. `microsoftoutlook_move_mail_folder`, `microsoftoutlook_permanently_delete_mail_folder`, `microsoftoutlook_permanently_delete_message`, `microsoftoutlook_reply_all_message` `data-sync` Added DataSync support for list messages, list mail folders, and list message rules with offset pagination and incremental sync. `microsoftoutlook_list_mail_folders`, `microsoftoutlook_list_message_rules`, `microsoftoutlook_list_messages` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # Microsoft Teams Source: https://docs.stackone.com/connectors/microsoftteams/index How to set up the Microsoft Teams connector, plus the actions and events that are available.
Microsoft Teams
v2.2.0
72 actions · 15 events · 3 auth methods
IAM Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Delegated access on behalf of a signed-in user. Required for actions on chats, user profiles, and /me endpoints. App-only access without a signed-in user. Best for background services and automation. Cannot access user-specific endpo... Delegated access with bot messaging capabilities. Uses a single app registration for both Graph API and Bot Framework. T... Optionally, configure receiving Events for Microsoft Teams into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/microsoftteams/index.md for the full list. ## Events See https://docs.stackone.com/connectors/microsoftteams/index.md for the full list. ## References Full REST API reference for Microsoft Graph. Guide for building bots to leverage the messaging API for agentic use cases. # Microsoft Teams Changelog Source: https://docs.stackone.com/connectors/microsoftteams/changelog Release history for the Microsoft Teams connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added DataSync support to teams, users, chats and subscriptions. Teams, users and chats page through Microsoft Graph continuation tokens and now expose that token as a next result key, with a matching optional skiptoken input. All four sync by full refresh. `microsoftteams_list_chats`, `microsoftteams_list_subscriptions`, `microsoftteams_list_teams`, `microsoftteams_list_users` `description-fix` Disambiguated list_channels vs list_all_channels descriptions (owned-only vs including shared). Documented $select limitation on list_team_members (email/userId not selectable). Added owner requirement for private/shared channel creation. Clarified all bot_* actions that conversationId must be a Bot Framework id, not a Graph chat/thread id (19:...@thread.v2). `microsoftteams_bot_delete_activity`, `microsoftteams_bot_get_conversation_member`, `microsoftteams_bot_get_conversation_members`, `microsoftteams_bot_get_conversation_paged_members`, `microsoftteams_bot_reply_to_activity`, `microsoftteams_bot_send_to_conversation`, `microsoftteams_bot_update_activity`, `microsoftteams_create_channel`, `microsoftteams_list_all_channels`, `microsoftteams_list_channels`, `microsoftteams_list_team_members` `bug-fix` Added attachment id field (required) to send_channel_message, send_message_reply, and send_chat_message so card attachments are accepted by Graph. Fixed template@odata.bind URL quotes in create_team. Updated skiptoken description as opaque nextLink value. Added ConsistencyLevel requiredIf for $count. Disambiguated bot_get_conversation_members vs bot_get_conversation_paged_members descriptions. Documented create_channel members-at-creation and add_channel_member parent-team prerequisite. `microsoftteams_add_channel_member`, `microsoftteams_add_chat_member`, `microsoftteams_add_team_member`, `microsoftteams_add_team_members_bulk`, `microsoftteams_archive_channel`, `microsoftteams_archive_team`, `microsoftteams_bot_create_conversation`, `microsoftteams_bot_delete_activity`, `microsoftteams_bot_get_conversation_member`, `microsoftteams_bot_get_conversation_members`, `microsoftteams_bot_get_conversation_paged_members`, `microsoftteams_bot_reply_to_activity`, `microsoftteams_bot_send_to_conversation`, `microsoftteams_bot_update_activity`, `microsoftteams_change_password`, `microsoftteams_clone_team`, `microsoftteams_create_channel`, `microsoftteams_create_chat`, `microsoftteams_create_team`, `microsoftteams_create_user`, `microsoftteams_delete_channel`, `microsoftteams_delete_channel_tab`, `microsoftteams_delete_chat`, `microsoftteams_delete_team`, `microsoftteams_delete_user`, `microsoftteams_get_channel`, `microsoftteams_get_channel_files_folder`, `microsoftteams_get_channel_member`, `microsoftteams_get_channel_message`, `microsoftteams_get_channel_message_reply`, `microsoftteams_get_channel_tab`, `microsoftteams_get_chat`, `microsoftteams_get_chat_member`, `microsoftteams_get_chat_message`, `microsoftteams_get_current_user`, `microsoftteams_get_primary_channel`, `microsoftteams_get_subscription`, `microsoftteams_get_team`, `microsoftteams_get_team_member`, `microsoftteams_get_user`, `microsoftteams_list_all_channel_members`, `microsoftteams_list_all_channel_messages`, `microsoftteams_list_all_channels`, `microsoftteams_list_channel_members`, `microsoftteams_list_channel_message_replies`, `microsoftteams_list_channel_messages`, `microsoftteams_list_channel_tabs`, `microsoftteams_list_channels`, `microsoftteams_list_chat_members`, `microsoftteams_list_chat_messages`, `microsoftteams_list_chats`, `microsoftteams_list_incoming_channels`, `microsoftteams_list_subscriptions`, `microsoftteams_list_team_members`, `microsoftteams_list_teams`, `microsoftteams_list_users`, `microsoftteams_remove_channel_member`, `microsoftteams_remove_chat_member`, `microsoftteams_remove_team_member`, `microsoftteams_remove_team_members_bulk`, `microsoftteams_send_channel_message`, `microsoftteams_send_chat_message`, `microsoftteams_send_message_reply`, `microsoftteams_soft_delete_channel_message`, `microsoftteams_soft_delete_chat_message`, `microsoftteams_unarchive_channel`, `microsoftteams_unarchive_team`, `microsoftteams_undo_soft_delete_chat_message`, `microsoftteams_update_channel`, `microsoftteams_update_channel_message`, `microsoftteams_update_chat`, `microsoftteams_update_team` `bug-fix` Migrated all actions from requiredScopes to authRequirements with per-auth-type scoping: bot_* actions scoped to oauth2_bot only, /me/ actions (list_chats, get_chat, change_password, get_current_user) scoped to oauth2+oauth2_bot, send/soft-delete message actions scoped away from client credentials, list_all_channel_messages scoped to client credentials only. Removed create/update/delete subscription actions, classification field, unknownFutureValue sentinel from enums, meeting from chatType enum, hiddenMembership from update visibility enum, codesnippet/announcement from update attachments, summary/reactions from update_channel_message. Added validationRules (requiredIf for ConsistencyLevel+search, atLeastOneOf for update_team body, mutuallyExclusive for create_team displayName/group_id). Fixed group@odata.bind URL quotes. Documented soft-delete behavior, SharePoint folder provisioning, permanent tabs, education specialization, and teamsApp $expand requirement. `microsoftteams_create_subscription`, `microsoftteams_delete_subscription`, `microsoftteams_update_subscription`, `microsoftteams_webhook_channel_created`, `microsoftteams_webhook_channel_deleted`, `microsoftteams_webhook_channel_message_created`, `microsoftteams_webhook_channel_message_deleted`, `microsoftteams_webhook_channel_message_updated`, `microsoftteams_webhook_channel_updated`, `microsoftteams_webhook_chat_member_created`, `microsoftteams_webhook_chat_member_deleted`, `microsoftteams_webhook_chat_message_created`, `microsoftteams_webhook_chat_message_deleted`, `microsoftteams_webhook_chat_message_updated`, `microsoftteams_webhook_team_created`, `microsoftteams_webhook_team_deleted`, `microsoftteams_webhook_team_updated`, `microsoftteams_webhook_validation_check` `microsoftteams_add_channel_member`, `microsoftteams_add_chat_member`, `microsoftteams_add_team_member`, `microsoftteams_add_team_members_bulk`, `microsoftteams_archive_channel`, `microsoftteams_archive_team`, `microsoftteams_bot_create_conversation`, `microsoftteams_bot_delete_activity`, `microsoftteams_bot_get_conversation_member`, `microsoftteams_bot_get_conversation_members`, `microsoftteams_bot_get_conversation_paged_members`, `microsoftteams_bot_reply_to_activity`, `microsoftteams_bot_send_to_conversation`, `microsoftteams_bot_update_activity`, `microsoftteams_change_password`, `microsoftteams_clone_team`, `microsoftteams_create_channel`, `microsoftteams_create_chat`, `microsoftteams_create_team`, `microsoftteams_create_user`, `microsoftteams_delete_channel`, `microsoftteams_delete_channel_tab`, `microsoftteams_delete_chat`, `microsoftteams_delete_team`, `microsoftteams_delete_user`, `microsoftteams_get_channel`, `microsoftteams_get_channel_files_folder`, `microsoftteams_get_channel_member`, `microsoftteams_get_channel_message`, `microsoftteams_get_channel_message_reply`, `microsoftteams_get_channel_tab`, `microsoftteams_get_chat`, `microsoftteams_get_chat_member`, `microsoftteams_get_chat_message`, `microsoftteams_get_current_user`, `microsoftteams_get_primary_channel`, `microsoftteams_get_subscription`, `microsoftteams_get_team`, `microsoftteams_get_team_member`, `microsoftteams_get_user`, `microsoftteams_list_all_channel_members`, `microsoftteams_list_all_channel_messages`, `microsoftteams_list_all_channels`, `microsoftteams_list_channel_members`, `microsoftteams_list_channel_message_replies`, `microsoftteams_list_channel_messages`, `microsoftteams_list_channel_tabs`, `microsoftteams_list_channels`, `microsoftteams_list_chat_members`, `microsoftteams_list_chat_messages`, `microsoftteams_list_chats`, `microsoftteams_list_incoming_channels`, `microsoftteams_list_subscriptions`, `microsoftteams_list_team_members`, `microsoftteams_list_teams`, `microsoftteams_list_users`, `microsoftteams_remove_channel_member`, `microsoftteams_remove_chat_member`, `microsoftteams_remove_team_member`, `microsoftteams_remove_team_members_bulk`, `microsoftteams_send_channel_message`, `microsoftteams_send_chat_message`, `microsoftteams_send_message_reply`, `microsoftteams_soft_delete_channel_message`, `microsoftteams_soft_delete_chat_message`, `microsoftteams_unarchive_channel`, `microsoftteams_unarchive_team`, `microsoftteams_undo_soft_delete_chat_message`, `microsoftteams_update_channel`, `microsoftteams_update_channel_message`, `microsoftteams_update_chat`, `microsoftteams_update_team` `new-events` Added webhook event support with 14 events (+ validation handshake) across channel messages, chat messages, teams, channels, and chat members via Microsoft Graph subscriptions with programmatic lifecycle management. `microsoftteams_webhook_channel_created`, `microsoftteams_webhook_channel_deleted`, `microsoftteams_webhook_channel_message_created`, `microsoftteams_webhook_channel_message_deleted`, `microsoftteams_webhook_channel_message_updated`, `microsoftteams_webhook_channel_updated`, `microsoftteams_webhook_chat_member_created`, `microsoftteams_webhook_chat_member_deleted`, `microsoftteams_webhook_chat_message_created`, `microsoftteams_webhook_chat_message_deleted`, `microsoftteams_webhook_chat_message_updated`, `microsoftteams_webhook_team_created`, `microsoftteams_webhook_team_deleted`, `microsoftteams_webhook_team_updated`, `microsoftteams_webhook_validation_check` `bug-fix` Fixed bot update activity description to clarify text/attachment constraint, and simplified bot get conversation members by removing unsupported pagination parameters. # Mintlify Source: https://docs.stackone.com/connectors/mintlify/index How to set up the Mintlify connector, plus the actions that are available.
Mintlify
Previewv2.1.3
16 actions · 2 auth methods
Knowledge Management Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use for managing docs configuration, pages, and settings. Requires dashboard admin access. Use for AI assistant and search features only. Separate from admin operations. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mintlify/index.md for the full list. # Mintlify Changelog Source: https://docs.stackone.com/connectors/mintlify/changelog Release history for the Mintlify connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide-changes` Updated the Project ID field placeholder to a realistic 24-character identifier so users can recognise the correct format. `guide-changes` `guide-images` Refreshed the Admin and Assistant API Key connection guides with accurate portal navigation, the current API key creation flow, and screenshots. `bug-fix` Fixed Assistant API Key account connection, which previously failed because the connection test ran admin-only and input-requiring actions. `data-sync` Added Data Sync support for the analytics collections (page views, unique visitors, assistant conversations, user feedback, and search queries). `mintlify_get_assistant_conversations`, `mintlify_get_page_views`, `mintlify_get_search_queries`, `mintlify_get_unique_visitors`, `mintlify_get_user_feedback` `auth` `breaking-changes` Added per-auth-type authRequirements binding. Admin API Key actions (deployments, agent jobs, analytics, feedback) and Assistant API Key actions (search, page content, AI chat) are now each restricted to their required auth type, since the two keys are not interchangeable. Also fixed the Assistant API Key connection test to use an assistant action instead of an admin-only one. # Miro Source: https://docs.stackone.com/connectors/miro/index How to set up the Miro connector, plus the actions that are available.
Miro
v3.1.1
95 actions · 2 auth methods
Design IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate your app to access Miro boards, teams, and projects on behalf of users For Miro Enterprise organizations. Uses its own Miro app with the organization read permissions, connected by a Company... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/miro/index.md for the full list. # Miro Changelog Source: https://docs.stackone.com/connectors/miro/changelog Release history for the Miro connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed a token refresh issue that could permanently disconnect an account, and connecting an Enterprise organization account no longer fails on plans without organization access. `new-actions` Added unified IAM actions for users, roles, teams, the organization and the current connection, plus a new Enterprise organization connection type. User, team and organization lookups need that connection, set up by a Company Admin with a dedicated Miro app. `miro_unified_get_group`, `miro_unified_get_me`, `miro_unified_get_organization`, `miro_unified_get_role`, `miro_unified_get_user`, `miro_unified_list_groups`, `miro_unified_list_organizations`, `miro_unified_list_roles`, `miro_unified_list_users` `miro_attach_tag_to_item`, `miro_create_app_card`, `miro_create_board`, `miro_create_card`, `miro_create_connector`, `miro_create_doc`, `miro_create_document`, `miro_create_document_from_file`, `miro_create_embed`, `miro_create_frame`, `miro_create_group`, `miro_create_image`, `miro_create_image_from_file`, `miro_create_project`, `miro_create_shape`, `miro_create_sticky_note`, `miro_create_tag`, `miro_create_text`, `miro_delete_app_card`, `miro_delete_board`, `miro_delete_card`, `miro_delete_connector`, `miro_delete_doc`, `miro_delete_document`, `miro_delete_embed`, `miro_delete_frame`, `miro_delete_group`, `miro_delete_image`, `miro_delete_item`, `miro_delete_project`, `miro_delete_shape`, `miro_delete_sticky_note`, `miro_delete_tag`, `miro_delete_text`, `miro_detach_tag_from_item`, `miro_get_app_card`, `miro_get_board`, `miro_get_board_member`, `miro_get_card`, `miro_get_connector`, `miro_get_current_user`, `miro_get_doc`, `miro_get_document`, `miro_get_embed`, `miro_get_frame`, `miro_get_group`, `miro_get_image`, `miro_get_item`, `miro_get_items_by_tag`, `miro_get_oembed_data`, `miro_get_project`, `miro_get_shape`, `miro_get_sticky_note`, `miro_get_tag`, `miro_get_tags_from_item`, `miro_get_text`, `miro_list_board_members`, `miro_list_boards`, `miro_list_connectors`, `miro_list_frame_items`, `miro_list_group_items`, `miro_list_groups`, `miro_list_items`, `miro_list_projects`, `miro_list_tags`, `miro_remove_board_member`, `miro_share_board`, `miro_ungroup_items`, `miro_update_app_card`, `miro_update_board`, `miro_update_board_member`, `miro_update_card`, `miro_update_connector`, `miro_update_document`, `miro_update_document_from_file`, `miro_update_embed`, `miro_update_frame`, `miro_update_group`, `miro_update_image`, `miro_update_image_from_file`, `miro_update_item`, `miro_update_project`, `miro_update_shape`, `miro_update_sticky_note`, `miro_update_tag`, `miro_update_text` `breaking-change` `data-sync` Changed list_boards limit/offset input types from string to number. Added DataSync support for list_boards with offset-based pagination and full-refresh sync. `miro_list_boards` `breaking-change` `auth` Migrated all 85 actions from deprecated requiredScopes to authRequirements with per-auth-type scope arrays. `miro_attach_tag_to_item`, `miro_create_app_card`, `miro_create_board`, `miro_create_card`, `miro_create_connector`, `miro_create_doc`, `miro_create_document`, `miro_create_document_from_file`, `miro_create_embed`, `miro_create_frame`, `miro_create_group`, `miro_create_image`, `miro_create_image_from_file`, `miro_create_project`, `miro_create_shape`, `miro_create_sticky_note`, `miro_create_tag`, `miro_create_text`, `miro_delete_app_card`, `miro_delete_board`, `miro_delete_card`, `miro_delete_connector`, `miro_delete_doc`, `miro_delete_document`, `miro_delete_embed`, `miro_delete_frame`, `miro_delete_group`, `miro_delete_image`, `miro_delete_item`, `miro_delete_project`, `miro_delete_shape`, `miro_delete_sticky_note`, `miro_delete_tag`, `miro_delete_text`, `miro_detach_tag_from_item`, `miro_get_app_card`, `miro_get_board`, `miro_get_board_member`, `miro_get_card`, `miro_get_connector`, `miro_get_current_user`, `miro_get_doc`, `miro_get_document`, `miro_get_embed`, `miro_get_frame`, `miro_get_group`, `miro_get_image`, `miro_get_item`, `miro_get_items_by_tag`, `miro_get_project`, `miro_get_shape`, `miro_get_sticky_note`, `miro_get_tag`, `miro_get_tags_from_item`, `miro_get_text`, `miro_list_board_members`, `miro_list_boards`, `miro_list_connectors`, `miro_list_frame_items`, `miro_list_group_items`, `miro_list_groups`, `miro_list_items`, `miro_list_projects`, `miro_list_tags`, `miro_remove_board_member`, `miro_share_board`, `miro_ungroup_items`, `miro_update_app_card`, `miro_update_board`, `miro_update_board_member`, `miro_update_card`, `miro_update_connector`, `miro_update_document`, `miro_update_document_from_file`, `miro_update_embed`, `miro_update_frame`, `miro_update_group`, `miro_update_image`, `miro_update_image_from_file`, `miro_update_item`, `miro_update_project`, `miro_update_shape`, `miro_update_sticky_note`, `miro_update_tag`, `miro_update_text` `fix` `action-descriptions` Commented out Enterprise-plan-gated board policy fields and coowner/owner role values (deterministic 502 from Miro API). Improved get_group and get_item descriptions to reduce agent tool-selection errors. `miro_create_board`, `miro_get_group`, `miro_get_item`, `miro_update_board`, `miro_update_board_member` `fix` `description` Fixed list_items type enum (removed invalid connector value), improved action descriptions for list_frame_items, list_tags, and get_tags_from_item to reduce agent tool-selection errors. `miro_get_tags_from_item`, `miro_list_frame_items`, `miro_list_items`, `miro_list_tags` `guide` Improved OAuth setup guide with screenshots, corrected UI labels, and clarified scope selection. # Mistral AI Source: https://docs.stackone.com/connectors/mistral/index How to set up the Mistral AI connector, plus the actions that are available.
Mistral AI
v1.2.1
68 actions · 1 auth method
AI IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using a Mistral AI API key generated from the Mistral AI console. An optional Admin API key from the Backof... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mistral/index.md for the full list. # Mistral AI Changelog Source: https://docs.stackone.com/connectors/mistral/changelog Release history for the Mistral AI connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists now include unexpired pending Organization invitations with status pending, and user lookups resolve them. `mistral_unified_get_user`, `mistral_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups (Workspaces), organizations and the current connection. Users, roles and groups need an Admin API key, a new optional credential available on Enterprise plans. `mistral_unified_get_group`, `mistral_unified_get_me`, `mistral_unified_get_organization`, `mistral_unified_get_role`, `mistral_unified_get_user`, `mistral_unified_list_groups`, `mistral_unified_list_organizations`, `mistral_unified_list_roles`, `mistral_unified_list_users` `new-feature` Enabled Data Sync on six list actions covering models, files, batch jobs, agents, conversations and libraries. Added the page_token cursor parameter to list_libraries, the provider's supported replacement for its now-deprecated page parameter. # Mixpanel Source: https://docs.stackone.com/connectors/mixpanel/index How to set up the Mixpanel connector, plus the actions and events that are available.
Mixpanel
v2.4.0
54 actions · 4 events · 1 auth method
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Service Account authentication using HTTP Basic Auth for Mixpanel API access. Optionally, configure receiving Events for Mixpanel into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mixpanel/index.md for the full list. ## Events See https://docs.stackone.com/connectors/mixpanel/index.md for the full list. # Mixpanel Changelog Source: https://docs.stackone.com/connectors/mixpanel/changelog Release history for the Mixpanel connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Webhook events are now delivered to the per-connection Native Webhook URL on the linked account. The previous routing that matched deliveries to a connection by Mixpanel Project ID is no longer supported and has been removed. `webhooks` Added inbound webhook support for Custom Alert notifications and Cohort Sync deliveries (full, members added, members removed), routed to the connected account by Project ID. `new-actions` Enabled Data Sync on annotation tags, lookup tables, schemas, and users, groups, and organizations for scheduled full record syncs. `mixpanel_list_annotation_tags`, `mixpanel_list_lookup_tables`, `mixpanel_list_schemas`, `mixpanel_unified_list_groups`, `mixpanel_unified_list_organizations`, `mixpanel_unified_list_users` `bug-fix` Lookups for missing users, roles, groups, and organizations now return a not-found error. `mixpanel_unified_get_group`, `mixpanel_unified_get_me`, `mixpanel_unified_get_organization`, `mixpanel_unified_get_role`, `mixpanel_unified_get_user`, `mixpanel_unified_list_groups`, `mixpanel_unified_list_organizations`, `mixpanel_unified_list_resource_users`, `mixpanel_unified_list_roles`, `mixpanel_unified_list_users` `behavioral-bug-fix` Clarified the Set and Union list-property write actions (profiles and groups) so Set overwrites a property's full value — replacing a whole list with the exact array provided — while Union only extends an existing list, preserving current items and ignoring duplicates. `mixpanel_set_group_properties`, `mixpanel_set_profile_properties`, `mixpanel_union_group_list_property`, `mixpanel_union_profile_list_property` `bug-fix` Delete User Profile and Delete Group now return Mixpanel's real result instead of always reporting "deleted successfully", so a failed deletion surfaces the actual error. Clarified the profile and group write action descriptions to state that a Project Token must be set on the connection, and improved the Import Events guidance. `mixpanel_append_profile_list_property`, `mixpanel_delete_group`, `mixpanel_delete_profile`, `mixpanel_import_events`, `mixpanel_increment_profile_properties`, `mixpanel_remove_group_list_property`, `mixpanel_remove_profile_list_property`, `mixpanel_set_group_properties`, `mixpanel_set_group_properties_once`, `mixpanel_set_profile_properties`, `mixpanel_set_profile_properties_once`, `mixpanel_union_group_list_property`, `mixpanel_union_profile_list_property`, `mixpanel_unset_group_properties`, `mixpanel_unset_profile_properties` `bug-fix` `breaking` Fixed the profile, group, and identity write actions that required an unknowable project token in each request and could silently fail; they now use a new Project Token connection field and target a single record directly. Removed the redundant batch group and profile update actions. `mixpanel_batch_update_groups`, `mixpanel_batch_update_profiles` `mixpanel_append_profile_list_property`, `mixpanel_create_alias`, `mixpanel_create_identity`, `mixpanel_delete_group`, `mixpanel_delete_profile`, `mixpanel_increment_profile_properties`, `mixpanel_remove_group_list_property`, `mixpanel_remove_profile_list_property`, `mixpanel_set_group_properties`, `mixpanel_set_group_properties_once`, `mixpanel_set_profile_properties`, `mixpanel_set_profile_properties_once`, `mixpanel_union_group_list_property`, `mixpanel_union_profile_list_property`, `mixpanel_unset_group_properties`, `mixpanel_unset_profile_properties` `guide-changes` Added portal screenshots to the Service Account connection guide and corrected the settings navigation, Create Service Account form fields, and where to find the Project ID, Organization ID, and Data Residency. `bug-fix` Fix Data Residency region check at connection time. Removed the lookup-tables action from the connection test because it worked on both US and EU hosts and let accounts connect with the wrong region selected. Now connecting with the wrong region correctly fails. # MoEngage Source: https://docs.stackone.com/connectors/moengage/index How to set up the MoEngage connector, plus the actions that are available.
MoEngage
Previewv1.3.1
44 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses your Workspace ID plus two legacy MoEngage API keys, the Data key and the Campaign report key, each authenticating... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/moengage/index.md for the full list. # MoEngage Changelog Source: https://docs.stackone.com/connectors/moengage/changelog Release history for the MoEngage connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `description-fix` Corrected the connection guide and field help to explain which MoEngage API key goes in each field, with screenshots. `moengage_get_user_subscription_preferences` `new-actions` `bug-fix` Added subscription preference reads and updates by customer ID or email, fixed campaign creation and campaign updates, and corrected guidance for nested content blocks and segment filters. `moengage_get_subscription_preferences`, `moengage_list_subscription_categories`, `moengage_update_subscription_preferences` `moengage_add_catalog_attributes`, `moengage_bulk_update_subscription_preferences`, `moengage_create_business_event`, `moengage_create_campaign`, `moengage_create_catalog`, `moengage_create_content_block`, `moengage_create_custom_in_app_template`, `moengage_create_custom_push_template`, `moengage_create_custom_sms_template`, `moengage_create_email_template`, `moengage_create_filter_segment`, `moengage_delete_catalog_items`, `moengage_export_user_s2s`, `moengage_get_user_subscription_preferences`, `moengage_ingest_catalog_items`, `moengage_search_campaigns`, `moengage_search_catalog_items`, `moengage_trigger_business_event`, `moengage_update_campaign`, `moengage_update_catalog_items`, `moengage_update_content_block`, `moengage_update_custom_in_app_template`, `moengage_update_custom_push_template`, `moengage_update_custom_sms_template`, `moengage_update_filter_segment`, `moengage_update_user_subscription_preferences` `new-actions` `bug-fix` Added bulk subscription-preference updates by customer ID, fixed email template attachments and campaign search filters, and content block writes now return the saved block. `moengage_bulk_update_subscription_preferences` `moengage_create_content_block`, `moengage_create_email_template`, `moengage_create_filter_segment`, `moengage_get_campaign_meta`, `moengage_get_user_subscription_preferences`, `moengage_search_campaigns`, `moengage_search_content_blocks`, `moengage_update_campaign`, `moengage_update_content_block`, `moengage_update_filter_segment`, `moengage_update_user_subscription_preferences` `new-feature` `data-sync` Added DataSync support to the custom segments and email templates list actions so their records can be periodically synced by full refresh. # Monday.com Source: https://docs.stackone.com/connectors/monday/index How to set up the Monday.com connector, plus the actions that are available.
Monday.com
Previewv1.1.2
110 actions · 1 auth method
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API token authentication provides secure access to Monday.com APIs. Get API token from the Monday.com Developer Center. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/monday/index.md for the full list. # Monday.com Changelog Source: https://docs.stackone.com/connectors/monday/changelog Release history for the Monday.com connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed user list email filtering being silently ignored, and fixed group and user lookups returning empty results instead of not-found errors. `monday_unified_get_group`, `monday_unified_get_me`, `monday_unified_get_role`, `monday_unified_get_user`, `monday_unified_list_groups`, `monday_unified_list_organizations`, `monday_unified_list_resource_types`, `monday_unified_list_resource_users`, `monday_unified_list_roles`, `monday_unified_list_users` `bug-fix` Turned off pagination on the IAM roles list, which returns a fixed catalogue that always fits one page. `monday_unified_get_group`, `monday_unified_list_groups`, `monday_unified_list_roles` `new-actions` Added unified IAM actions for users, roles, groups, organizations, credentials, resource types, and resource users. # Moneybird Source: https://docs.stackone.com/connectors/moneybird/index How to set up the Moneybird connector, plus the actions and events that are available.
Moneybird
v1.3.0
68 actions · 62 events · 2 auth methods
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Moneybird account via OAuth 2.0 to access your accounting data. Requires creating an API token in the administration settings. The token is valid for a single administration. Optionally, configure receiving Events for Moneybird into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/moneybird/index.md for the full list. ## Events See https://docs.stackone.com/connectors/moneybird/index.md for the full list. # Moneybird Changelog Source: https://docs.stackone.com/connectors/moneybird/changelog Release history for the Moneybird connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added 61 webhook events for contacts, contact persons, sales invoices, estimates, payments, documents, products, ledger accounts, tax rates and financial accounts. StackOne registers and removes the Moneybird webhook automatically when events are enabled on an account. `data-sync` `description-fix` Added data sync support for contacts, estimates, financial accounts, ledger accounts, products, purchase invoices, sales invoices and tax rates, so these collections can be kept continuously up to date in StackOne. Corrected the financial accounts documentation and removed its page and per_page inputs, which the endpoint ignores. `moneybird_filter_contacts`, `moneybird_list_contacts`, `moneybird_list_estimates`, `moneybird_list_financial_accounts`, `moneybird_list_ledger_accounts`, `moneybird_list_products`, `moneybird_list_purchase_invoices`, `moneybird_list_sales_invoices`, `moneybird_list_tax_rates` `description-fix` Clarified when to use filter contacts versus list contacts, so a plain name or email lookup is not sent to the structured-filter action. Documented the mandate_type filter key and noted that any filter supplied replaces the endpoint defaults. `moneybird_filter_contacts`, `moneybird_list_contacts` `description-fix` Marked the purchase invoice line item description as required, since the provider rejects blank line item descriptions. Clarified list action descriptions so retrieval is not confused with creation, noted that financial accounts and tax rates are read-only, and explained that customer_id search and sales invoice filters still return summary records. `moneybird_create_purchase_invoice`, `moneybird_list_contacts`, `moneybird_list_estimates`, `moneybird_list_financial_accounts`, `moneybird_list_products`, `moneybird_list_purchase_invoices`, `moneybird_list_sales_invoices`, `moneybird_list_tax_rates`, `moneybird_update_purchase_invoice` `descriptions` `guide` Clarified action descriptions to disambiguate contact creation vs lookup, customer_id vs name lookups, payment recording endpoints, and list vs get detail retrieval. Updated OAuth 2.0 and Personal Access Token connection guides with portal walkthrough screenshots. # MongoDB Atlas Source: https://docs.stackone.com/connectors/mongodb/index How to set up the MongoDB Atlas connector, plus the actions and events that are available.
MongoDB Atlas
v1.3.0
71 actions · 2 events · 1 auth method
Databases Observability IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using a MongoDB Atlas Service Account (OAuth 2.0 client credentials). Create a Service Account under Organizatio... Optionally, configure receiving Events for MongoDB Atlas into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mongodb/index.md for the full list. ## Events See https://docs.stackone.com/connectors/mongodb/index.md for the full list. # MongoDB Atlas Changelog Source: https://docs.stackone.com/connectors/mongodb/changelog Release history for the MongoDB Atlas connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added native webhook support for MongoDB Atlas alert events, delivered through a project Webhook integration and routed by alert type. `new-feature` Added Data Sync support for List Projects, List Organizations, List Unified Organizations, List Unified Users, List Unified Groups, and List Unified Roles, so these resources can be synced into StackOne on a schedule and read without calling MongoDB Atlas. All six run as a full refresh on every sync, because the Atlas Administration API offers no way to filter by last-updated time. `mongodb_list_organizations`, `mongodb_list_projects`, `mongodb_unified_list_groups`, `mongodb_unified_list_organizations`, `mongodb_unified_list_roles`, `mongodb_unified_list_users` `bug-fix` Project ID fields now warn against passing a project name or label instead of the 24-character ID, and create custom database role clarifies that a role must grant at least one privilege (an action or an inherited role). `mongodb_acknowledge_alert`, `mongodb_create_alert_config`, `mongodb_create_backup_restore_job`, `mongodb_create_backup_snapshot`, `mongodb_create_cluster`, `mongodb_create_custom_db_role`, `mongodb_create_database_user`, `mongodb_create_flex_cluster`, `mongodb_create_ip_access_list_entries`, `mongodb_delete_alert_config`, `mongodb_delete_cluster`, `mongodb_delete_custom_db_role`, `mongodb_delete_database_user`, `mongodb_delete_flex_cluster`, `mongodb_delete_ip_access_list_entry`, `mongodb_delete_project`, `mongodb_get_alert`, `mongodb_get_alert_config`, `mongodb_get_backup_snapshot`, `mongodb_get_cluster`, `mongodb_get_custom_db_role`, `mongodb_get_database_user`, `mongodb_get_flex_cluster`, `mongodb_get_ip_access_list_entry`, `mongodb_get_project`, `mongodb_list_alert_configs`, `mongodb_list_alerts`, `mongodb_list_backup_restore_jobs`, `mongodb_list_backup_snapshots`, `mongodb_list_clusters`, `mongodb_list_custom_db_roles`, `mongodb_list_database_users`, `mongodb_list_flex_clusters`, `mongodb_list_ip_access_list_entries`, `mongodb_list_project_events`, `mongodb_update_alert_config`, `mongodb_update_cluster`, `mongodb_update_custom_db_role`, `mongodb_update_database_user`, `mongodb_update_project` `new-actions` Added unified IAM actions for organization users, teams, roles, and project-scoped access, mapped from MongoDB Atlas's org and project user, team, and role-assignment endpoints. List actions request pages until Atlas returns an empty page, so results are not capped at a fixed page count. Organization-scoped listings ask for the organization when several are visible to the connection, and user lists accept an optional organization filter. `mongodb_unified_get_group`, `mongodb_unified_get_me`, `mongodb_unified_get_organization`, `mongodb_unified_get_role`, `mongodb_unified_get_user`, `mongodb_unified_list_groups`, `mongodb_unified_list_organizations`, `mongodb_unified_list_resource_types`, `mongodb_unified_list_resource_users`, `mongodb_unified_list_roles`, `mongodb_unified_list_users` `bug-fix` Clearer action descriptions so agents get two calls right the first time — deleting or reading an IP access list entry for a CIDR range (the slash must be written as %2F) and creating or updating a custom database role (now explains the fields for inherited roles and privilege actions). `mongodb_create_custom_db_role`, `mongodb_delete_ip_access_list_entry`, `mongodb_get_ip_access_list_entry`, `mongodb_update_custom_db_role` `connection-guide` Update the OAuth 2.0 Service Account connection guide. `new-connector` Initial MongoDB Atlas connector with 60 actions across 14 resources (projects, clusters, organizations, database users, custom roles, alerts, backups, IP access list, teams, API keys, flex clusters, and events). OAuth 2.0 Service Account authentication. # Moss Source: https://docs.stackone.com/connectors/moss/index How to set up the Moss connector, plus the actions that are available.
Moss
Betav1.1.0
30 actions · 1 auth method
Expense Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires API keys created by an admin in Settings > Company Settings > API Keys. Uses client credentials flow with 1-hou... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/moss/index.md for the full list. # Moss Changelog Source: https://docs.stackone.com/connectors/moss/changelog Release history for the Moss connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for expenses, suppliers, users, teams, departments, expense accounts, payment terms, tax rates, bank accounts, and dimensions, with incremental updates for expenses and suppliers. # MyGlue Source: https://docs.stackone.com/connectors/myglue/index How to set up the MyGlue connector, plus the actions that are available.
MyGlue
Betav1.1.0
43 actions · 1 auth method
Knowledge Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an IT Glue API key generated from Account > Settings > API Keys. Keys are automatically revoked after 90 days o... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/myglue/index.md for the full list. # MyGlue Changelog Source: https://docs.stackone.com/connectors/myglue/changelog Release history for the MyGlue connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 6 list actions (organizations, organization types, organization statuses, users, groups, and password categories). Organizations sync incrementally via a new updated_after filter; the others full-refresh. Passwords are deliberately not syncable because those records hold live credentials. # n8n test Source: https://docs.stackone.com/connectors/mcp_n8ntest/index How to set up the n8n test connector, plus the actions that are available.
n8n test
v1.0.0
54 actions · 1 auth method
MCP
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authorize through the MCP server. Endpoints and client registration are discovered at connect time. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mcp_n8ntest/index.md for the full list. # Namely Source: https://docs.stackone.com/connectors/namely/index How to set up the Namely connector, plus the actions that are available.
Namely
Betav1.1.0
54 actions · 2 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Three-legged OAuth for partner integrations built for mutual Namely clients. Access tokens expire after 15 minutes and a... Personal Access Token (bearer) for a client building its own integration. The token inherits the permissions of the user... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/namely/index.md for the full list. # Namely Changelog Source: https://docs.stackone.com/connectors/namely/changelog Release history for the Namely connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for profiles, groups, group types, teams, job tiers, job titles, profile fields and sections, folders, resources and countries. # National Park Service Source: https://docs.stackone.com/connectors/nationalparkservice/index How to set up the National Park Service connector, plus the actions that are available.
National Park Service
v1.1.0
29 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a free API key from the NPS Developer portal. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/nationalparkservice/index.md for the full list. # National Park Service Changelog Source: https://docs.stackone.com/connectors/nationalparkservice/changelog Release history for the National Park Service connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Enabled scheduled data sync on 24 list actions — parks, alerts, events, articles, people, places, news releases, lesson plans, activities, things to do, topics, amenities, campgrounds, visitor centers, parking lots, galleries, videos, webcams, tours, road events, fees and passes, passport stamp locations and parks by activity or topic — so these collections can be kept in sync and read without calling the National Park Service on every request. Each syncs by full refresh, because the NPS API exposes no updated-since filter on any endpoint. List Audio is excluded, as NPS truncates its responses for records with very large embedded transcripts, which would leave a sync incomplete. `nationalparkservice_list_activities`, `nationalparkservice_list_alerts`, `nationalparkservice_list_amenities`, `nationalparkservice_list_articles`, `nationalparkservice_list_campgrounds`, `nationalparkservice_list_events`, `nationalparkservice_list_fees_and_passes`, `nationalparkservice_list_galleries`, `nationalparkservice_list_lesson_plans`, `nationalparkservice_list_news_releases`, `nationalparkservice_list_parking_lots`, `nationalparkservice_list_parks`, `nationalparkservice_list_parks_by_activity`, `nationalparkservice_list_parks_by_topic`, `nationalparkservice_list_passport_stamp_locations`, `nationalparkservice_list_people`, `nationalparkservice_list_places`, `nationalparkservice_list_road_events`, `nationalparkservice_list_things_to_do`, `nationalparkservice_list_topics`, `nationalparkservice_list_tours`, `nationalparkservice_list_videos`, `nationalparkservice_list_visitor_centers`, `nationalparkservice_list_webcams` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `description-fix` Clarify list_amenities_at_visitor_centers q parameter filters amenities by name directly, avoiding unnecessary preparatory lookups. `nationalparkservice_list_amenities_at_visitor_centers` `bug-fix` `description-fix` Fixed list_fees_and_passes statecode parameter to use camelCase stateCode for consistency across all actions. Added array format guidance to query_parkCode and query_id descriptions. Added pagination recommendations to 12 large-response actions. Clarified list_events uses pageSize/pageNumber (not limit/start). `nationalparkservice_list_events`, `nationalparkservice_list_fees_and_passes` `bug-fix` Corrected the API Key connection guide to use the NPS sign-up page's actual title, and added portal screenshots to the registration and sign-up steps. `description-fix` Improved array parameter descriptions to guide correct usage and added pagination recommendations to 12 actions with large response payloads. `nationalparkservice_list_amenities_at_parks_places`, `nationalparkservice_list_amenities_at_visitor_centers`, `nationalparkservice_list_articles`, `nationalparkservice_list_campgrounds`, `nationalparkservice_list_events`, `nationalparkservice_list_fees_and_passes`, `nationalparkservice_list_gallery_assets`, `nationalparkservice_list_parks_by_activity`, `nationalparkservice_list_parks_by_topic`, `nationalparkservice_list_people`, `nationalparkservice_list_things_to_do`, `nationalparkservice_list_tours`, `nationalparkservice_list_visitor_centers` `new-connector` Initial release of the National Park Service connector with 29 read-only actions covering parks, activities, alerts, amenities, campgrounds, events, multimedia, topics, and visitor information. # National Weather Service Source: https://docs.stackone.com/connectors/nws/index How to set up the National Weather Service connector, plus the actions that are available.
National Weather Service
v1.1.0
67 actions · 1 auth method
Weather
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The NWS API is public and free with no API key. A User-Agent header identifying your application is required on every re... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/nws/index.md for the full list. # National Weather Service Changelog Source: https://docs.stackone.com/connectors/nws/changelog Release history for the National Weather Service connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to seven collection actions — forecast and county zones, text products and product types, the weather glossary, active alerts, and radar stations and servers — so these can be kept in sync and searched without calling the National Weather Service on every request. Each is returned in full by a single request and syncs by full refresh, because the API offers no last-updated filter. `nws_list_active_alerts`, `nws_list_glossary_terms`, `nws_list_product_types`, `nws_list_products`, `nws_list_radar_servers`, `nws_list_radar_stations`, `nws_list_zones` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `guide` Added a connection guide explaining what to enter in the User-Agent field, including the required format and an example. `description-fix` `bug-fix` Forecast icon, satellite thumbnail, office briefing and weather story downloads now return valid base64 file content instead of raw bytes. Clarified icon condition codes, the mutually exclusive alert geographic filters, the 4-letter ICAO office format for text products, and how to obtain briefing, weather story and TAF identifiers. `nws_get_dual_condition_icon`, `nws_get_icon`, `nws_get_office_briefing`, `nws_get_office_briefing_download`, `nws_get_office_weather_story`, `nws_get_office_weather_story_image`, `nws_get_product`, `nws_get_satellite_thumbnail`, `nws_get_station_taf`, `nws_list_active_alerts`, `nws_list_alerts`, `nws_list_products`, `nws_list_radio_transmitters`, `nws_list_station_tafs`, `nws_list_stations`, `nws_list_zones`, `nws_list_zones_by_type` `new-connector` Initial National Weather Service (NWS) connector with 67 read actions across 12 resources (alerts, aviation, gridpoints, points, stations, zones, offices, products, radar, radio, icons, glossary) built from the official api.weather.gov OpenAPI spec (v3.11.0). # Netlify Source: https://docs.stackone.com/connectors/netlify/index How to set up the Netlify connector, plus the actions and events that are available.
Netlify
v1.3.0
42 actions · 21 events · 1 auth method
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 to authorize access to Netlify resources. Optionally, configure receiving Events for Netlify into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/netlify/index.md for the full list. ## Events See https://docs.stackone.com/connectors/netlify/index.md for the full list. # Netlify Changelog Source: https://docs.stackone.com/connectors/netlify/changelog Release history for the Netlify connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added 20 webhook events for deploys, form submissions, split tests and dev servers, received through the account's Native Webhook URL. `bug-fix` Corrected the DNS record hostname guidance (root records use the zone's own domain name, not @), clarified the DNS zone account slug filter, and documented that DNS records are replaced rather than edited. `netlify_create_dns_record`, `netlify_create_dns_zone`, `netlify_create_site_deploy`, `netlify_delete_dns_record`, `netlify_get_dns_zones`, `netlify_list_site_deploys`, `netlify_restore_site_deploy` `data-sync` Added DataSync support to six list actions (list_sites, list_accounts, get_dns_zones, unified_list_organizations, unified_list_users, unified_list_roles), enabling periodic syncing of sites, accounts, DNS zones, organizations, users, and roles. `netlify_get_dns_zones`, `netlify_list_accounts`, `netlify_list_sites`, `netlify_unified_list_organizations`, `netlify_unified_list_roles`, `netlify_unified_list_users` `guide` Corrected the OAuth 2.0 connector profile guide to match the Netlify portal: the newly created app appears as a collapsed row that must be expanded, and the credential field is labelled Secret rather than Client Secret. Added portal screenshots to the guide steps. # NetSuite Source: https://docs.stackone.com/connectors/netsuite/index How to set up the NetSuite connector, plus the actions that are available.
NetSuite
v1.6.0
80 actions · 2 auth methods
ERP IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an integration record in NetSuite with OAuth 2.0 Authorization Code Grant enabled and REST Web Service... Each connected account creates its own NetSuite integration record and enters its own Client ID and Client Secret at con... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/netsuite/index.md for the full list. # NetSuite Changelog Source: https://docs.stackone.com/connectors/netsuite/changelog Release history for the NetSuite connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to twenty-four list actions across accounting, transactions, items, and identity (customers, vendors, employees, invoices, sales orders, journal entries, items, subsidiaries, and more), so these collections can be kept in sync and read back without calling NetSuite on every request. `netsuite_list_accounts`, `netsuite_list_credit_memos`, `netsuite_list_currencies`, `netsuite_list_customer_payments`, `netsuite_list_customers`, `netsuite_list_departments`, `netsuite_list_deposits`, `netsuite_list_employees`, `netsuite_list_expense_reports`, `netsuite_list_inventory_items`, `netsuite_list_invoices`, `netsuite_list_journal_entries`, `netsuite_list_locations`, `netsuite_list_non_inventory_sale_items`, `netsuite_list_purchase_orders`, `netsuite_list_sales_orders`, `netsuite_list_service_sale_items`, `netsuite_list_subsidiaries`, `netsuite_list_vendor_bills`, `netsuite_list_vendor_payments`, `netsuite_list_vendors`, `netsuite_unified_list_organizations`, `netsuite_unified_list_roles`, `netsuite_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `netsuite_unified_get_me`, `netsuite_unified_get_organization`, `netsuite_unified_get_role`, `netsuite_unified_get_user`, `netsuite_unified_list_organizations`, `netsuite_unified_list_roles`, `netsuite_unified_list_users` `new-actions` Added unified identity and access management actions for users, roles, organizations, and connection credentials. `netsuite_unified_get_me`, `netsuite_unified_get_organization`, `netsuite_unified_get_role`, `netsuite_unified_get_user`, `netsuite_unified_list_organizations`, `netsuite_unified_list_roles`, `netsuite_unified_list_users` `auth` Added an account-level OAuth 2.0 option so a connected account can use its own NetSuite integration credentials instead of the ones configured on the connector profile. `netsuite_create_account`, `netsuite_create_credit_memo`, `netsuite_create_customer`, `netsuite_create_customer_payment`, `netsuite_create_deposit`, `netsuite_create_employee`, `netsuite_create_expense_report`, `netsuite_create_inventory_item`, `netsuite_create_invoice`, `netsuite_create_journal_entry`, `netsuite_create_non_inventory_sale_item`, `netsuite_create_purchase_order`, `netsuite_create_sales_order`, `netsuite_create_service_sale_item`, `netsuite_create_vendor`, `netsuite_create_vendor_bill`, `netsuite_create_vendor_payment`, `netsuite_delete_customer`, `netsuite_delete_invoice`, `netsuite_delete_journal_entry`, `netsuite_delete_purchase_order`, `netsuite_delete_sales_order`, `netsuite_delete_vendor`, `netsuite_delete_vendor_bill`, `netsuite_execute_suiteql_query`, `netsuite_get_account`, `netsuite_get_credit_memo`, `netsuite_get_currency`, `netsuite_get_customer`, `netsuite_get_customer_payment`, `netsuite_get_department`, `netsuite_get_deposit`, `netsuite_get_employee`, `netsuite_get_expense_report`, `netsuite_get_inventory_item`, `netsuite_get_invoice`, `netsuite_get_journal_entry`, `netsuite_get_location`, `netsuite_get_purchase_order`, `netsuite_get_sales_order`, `netsuite_get_subsidiary`, `netsuite_get_vendor`, `netsuite_get_vendor_bill`, `netsuite_get_vendor_payment`, `netsuite_list_accounts`, `netsuite_list_credit_memos`, `netsuite_list_currencies`, `netsuite_list_customer_payments`, `netsuite_list_customers`, `netsuite_list_departments`, `netsuite_list_deposits`, `netsuite_list_employees`, `netsuite_list_expense_reports`, `netsuite_list_inventory_items`, `netsuite_list_invoices`, `netsuite_list_journal_entries`, `netsuite_list_locations`, `netsuite_list_non_inventory_sale_items`, `netsuite_list_purchase_orders`, `netsuite_list_sales_orders`, `netsuite_list_service_sale_items`, `netsuite_list_subsidiaries`, `netsuite_list_vendor_bills`, `netsuite_list_vendor_payments`, `netsuite_list_vendors`, `netsuite_update_account`, `netsuite_update_customer`, `netsuite_update_invoice`, `netsuite_update_journal_entry`, `netsuite_update_purchase_order`, `netsuite_update_sales_order`, `netsuite_update_vendor`, `netsuite_update_vendor_bill` `fix` Moved Create Vendor Payment to preview while its end-to-end reliability is being verified, and improved SuiteQL guidance — a vendor's open bills and unpaid balances can be retrieved in a single query using the transaction table's foreignamountunpaid column and open status, transaction totals should be read via the dedicated Get actions rather than unsupported amount columns, and date filters should use TO_DATE. `netsuite_create_vendor_payment`, `netsuite_execute_suiteql_query` `fix` Clarified that on accounts with "Make Location Mandatory" enabled a location must be set on each transaction line item (not only the header) across invoices, vendor bills, sales orders, purchase orders and credit memos, steered location lookups to the List Locations action, and documented the required item structure of the vendor payment bill-application list. `netsuite_create_credit_memo`, `netsuite_create_invoice`, `netsuite_create_purchase_order`, `netsuite_create_sales_order`, `netsuite_create_vendor_bill`, `netsuite_create_vendor_payment` `feature` `fix` Added an optional Department field to the invoice, vendor bill, credit memo, sales order and purchase order actions so transactions can be classified by department, and a Replace option on the update actions so changing a line item overwrites the existing line instead of adding a duplicate. Also clarified that a deposit's cash-back line requires a non-bank account. `netsuite_create_credit_memo`, `netsuite_create_deposit`, `netsuite_create_invoice`, `netsuite_create_purchase_order`, `netsuite_create_sales_order`, `netsuite_create_vendor_bill`, `netsuite_update_invoice`, `netsuite_update_journal_entry`, `netsuite_update_purchase_order`, `netsuite_update_sales_order`, `netsuite_update_vendor_bill` `feature` `fix` Added a Locations resource (list and get locations) so a transaction's location can be resolved reliably. Corrected the create-record guidance across invoices, vendor bills, journal entries, credit memos, deposits, payments, items, employees and customers so those records post on the first attempt, and made the customer-payment deposit account and individual-customer name fields optional where NetSuite does not require them. `netsuite_get_location`, `netsuite_list_locations` `netsuite_create_credit_memo`, `netsuite_create_customer`, `netsuite_create_customer_payment`, `netsuite_create_deposit`, `netsuite_create_employee`, `netsuite_create_inventory_item`, `netsuite_create_invoice`, `netsuite_create_journal_entry`, `netsuite_create_purchase_order`, `netsuite_create_sales_order`, `netsuite_create_service_sale_item`, `netsuite_create_vendor_bill`, `netsuite_execute_suiteql_query`, `netsuite_list_deposits` `guide` Reworked the OAuth 2.0 setup and account connection guides with step-by-step NetSuite navigation and screenshots — signing in first, enabling REST Web Services and OAuth 2.0 on the SuiteCloud subtab, granting a recommended role permission set on the Permissions subtab, plus notes on refresh-token validity and the NetSuite login URL. `bug-fix` `improvement` Improved agent-facing action descriptions so name and field lookups route to SuiteQL instead of the REST list q-filter (which only supports pre-indexed identifiers), documented the required taxSchedule and OneWorld location on transaction and item creation, clarified that id parameters take the internal record ID rather than the printed document number and that reference fields take the numeric internal ID rather than the name, corrected the SuiteQL account-name column, and added location inputs to sales orders and purchase orders. `netsuite_create_credit_memo`, `netsuite_create_customer`, `netsuite_create_customer_payment`, `netsuite_create_deposit`, `netsuite_create_employee`, `netsuite_create_expense_report`, `netsuite_create_inventory_item`, `netsuite_create_invoice`, `netsuite_create_journal_entry`, `netsuite_create_non_inventory_sale_item`, `netsuite_create_purchase_order`, `netsuite_create_sales_order`, `netsuite_create_service_sale_item`, `netsuite_create_vendor`, `netsuite_create_vendor_bill`, `netsuite_create_vendor_payment`, `netsuite_delete_invoice`, `netsuite_delete_journal_entry`, `netsuite_delete_purchase_order`, `netsuite_delete_sales_order`, `netsuite_delete_vendor_bill`, `netsuite_execute_suiteql_query`, `netsuite_get_credit_memo`, `netsuite_get_customer_payment`, `netsuite_get_deposit`, `netsuite_get_invoice`, `netsuite_get_journal_entry`, `netsuite_get_purchase_order`, `netsuite_get_sales_order`, `netsuite_get_subsidiary`, `netsuite_get_vendor_bill`, `netsuite_get_vendor_payment`, `netsuite_list_accounts`, `netsuite_list_credit_memos`, `netsuite_list_currencies`, `netsuite_list_customer_payments`, `netsuite_list_customers`, `netsuite_list_departments`, `netsuite_list_deposits`, `netsuite_list_employees`, `netsuite_list_expense_reports`, `netsuite_list_inventory_items`, `netsuite_list_invoices`, `netsuite_list_journal_entries`, `netsuite_list_non_inventory_sale_items`, `netsuite_list_purchase_orders`, `netsuite_list_sales_orders`, `netsuite_list_service_sale_items`, `netsuite_list_subsidiaries`, `netsuite_list_vendor_bills`, `netsuite_list_vendor_payments`, `netsuite_list_vendors`, `netsuite_update_invoice`, `netsuite_update_journal_entry`, `netsuite_update_purchase_order`, `netsuite_update_sales_order`, `netsuite_update_vendor_bill` `guide` Rebuilt the OAuth 2.0 setup and config connection guides from the live NetSuite portal with step-by-step screenshots and corrected UI labels (uppercase field, checkbox, and scope names). `new-actions` `bug-fix` Added create actions for inventory/non-inventory/service items, employees, expense reports, and deposits; create actions now surface the new record id from the Location header. Fixed acctType/generalRate/cashFlowRate/customForm to object type, removed expandSubResources from list actions (GET-only), aligned required fields (subsidiary, companyName) with the provider, added required taxSchedule to item creates and line items to create_deposit, and removed undocumented params. # New Relic Source: https://docs.stackone.com/connectors/newrelic/index How to set up the New Relic connector, plus the actions and events that are available.
New Relic
Previewv1.3.0
135 actions · 6 events · 1 auth method
Observability IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a personal User API Key for both REST v2 and NerdGraph API access. No app registration required. Token inherits the... Optionally, configure receiving Events for New Relic into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/newrelic/index.md for the full list. ## Events See https://docs.stackone.com/connectors/newrelic/index.md for the full list. # New Relic Changelog Source: https://docs.stackone.com/connectors/newrelic/changelog Release history for the New Relic connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added webhook events for New Relic alert issues (activated, acknowledged, priority changed, closed, and other updates). StackOne creates the webhook destination, channel, and workflow automatically when the account connects, and removes them on disconnect. `data-sync` Enabled data sync on 19 list actions (accounts, alert policies, notification channels, policy notification channels, applications, dashboards, synthetic monitors, private locations, muting rules, workloads, notification destinations and workflows, authentication domains, browser and mobile applications, and unified IAM users, groups, roles, and organizations). Fixed dashboard list pagination, added per-page limit and cursor inputs to entity search and notification list actions, and hardened GraphQL list actions to fail on NerdGraph errors instead of returning empty results. `newrelic_list_accounts`, `newrelic_list_alert_policies`, `newrelic_list_applications`, `newrelic_list_authentication_domains`, `newrelic_list_browser_applications`, `newrelic_list_dashboards`, `newrelic_list_key_transactions`, `newrelic_list_mobile_applications`, `newrelic_list_muting_rules`, `newrelic_list_notification_channels`, `newrelic_list_notification_destinations`, `newrelic_list_notification_workflows`, `newrelic_list_policy_notification_channels`, `newrelic_list_synthetic_monitors`, `newrelic_list_synthetic_private_locations`, `newrelic_list_workloads`, `newrelic_unified_list_groups`, `newrelic_unified_list_organizations`, `newrelic_unified_list_roles`, `newrelic_unified_list_users` `new-actions` Added unified IAM support for users, groups, roles, organizations, and credentials. Lists cover the organization's authentication domains and return a clear error when an organization is too large to fully enumerate; user and group lookups match directly by ID. # NinjaOne Source: https://docs.stackone.com/connectors/ninjaone/index How to set up the NinjaOne connector, plus the actions that are available.
NinjaOne
Betav1.3.1
105 actions · 2 auth methods
Device Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). \*\*OAuth 2.0 Authorization Code — user authorization\*\* Use this when actions must run on behalf of a specific NinjaOne u... \*\*OAuth 2.0 Client Credentials — machine-to-machine\*\* Use this for fully automated server-to-server integrations where... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ninjaone/index.md for the full list. # NinjaOne Changelog Source: https://docs.stackone.com/connectors/ninjaone/changelog Release history for the NinjaOne connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Looking up a role that does not exist now returns a not-found error instead of an empty result, users requested with roles return an error instead of empty roles when the role list cannot be read, and device access descriptions now make clear they list assigned technicians. `ninjaone_unified_get_role`, `ninjaone_unified_get_user`, `ninjaone_unified_list_resource_types`, `ninjaone_unified_list_resource_users`, `ninjaone_unified_list_users` `data-sync` Enabled Data Sync for 40 NinjaOne list actions, including device inventory reports, backup jobs, billing records, asset relationships, software licences, and unified users, roles, and organizations. `ninjaone_list_alerts`, `ninjaone_list_asset_relationship_types`, `ninjaone_list_asset_relationships_all`, `ninjaone_list_asset_tags`, `ninjaone_list_automation_scripts`, `ninjaone_list_backup_integrity_check_jobs`, `ninjaone_list_backup_jobs`, `ninjaone_list_billing_accounts`, `ninjaone_list_billing_agreements`, `ninjaone_list_billing_invoices`, `ninjaone_list_billing_products`, `ninjaone_list_checklist_templates`, `ninjaone_list_contacts`, `ninjaone_list_device_custom_fields`, `ninjaone_list_document_templates`, `ninjaone_list_end_users`, `ninjaone_list_groups`, `ninjaone_list_jobs`, `ninjaone_list_node_roles`, `ninjaone_list_policies`, `ninjaone_list_queries_computer_systems`, `ninjaone_list_queries_device_health`, `ninjaone_list_queries_disks`, `ninjaone_list_queries_network_interfaces`, `ninjaone_list_queries_operating_systems`, `ninjaone_list_queries_os_patches`, `ninjaone_list_queries_software`, `ninjaone_list_queries_software_patches`, `ninjaone_list_queries_volumes`, `ninjaone_list_queries_windows_services`, `ninjaone_list_software`, `ninjaone_list_software_licenses`, `ninjaone_list_technicians`, `ninjaone_list_ticket_forms`, `ninjaone_list_user_roles`, `ninjaone_list_users`, `ninjaone_list_vulnerability_management_scan_groups`, `ninjaone_unified_list_organizations`, `ninjaone_unified_list_roles`, `ninjaone_unified_list_users` `bug-fix` Added the US2 and Canada regions to the instance region selector, alongside the existing US, Europe, and Oceania options. `bug-fix` `auth` Gave the Authorization Code and Client Credentials OAuth methods unique identifiers to resolve an authentication configuration conflict. `ninjaone_create_asset_relationship_types`, `ninjaone_create_asset_relationships`, `ninjaone_create_asset_tags`, `ninjaone_create_asset_tags_batch`, `ninjaone_create_asset_tags_delete`, `ninjaone_create_asset_tags_merge`, `ninjaone_create_backup_integrity_check_job`, `ninjaone_create_billing_accounts`, `ninjaone_create_billing_agreements`, `ninjaone_create_billing_invoices`, `ninjaone_create_billing_products`, `ninjaone_create_checklist_templates`, `ninjaone_create_checklist_templates_delete`, `ninjaone_create_contact`, `ninjaone_create_custom_fields`, `ninjaone_create_custom_tabs`, `ninjaone_create_devices_approval`, `ninjaone_create_document_templates`, `ninjaone_create_end_user`, `ninjaone_create_knowledge_base_articles`, `ninjaone_create_organization`, `ninjaone_create_organization_document`, `ninjaone_create_organization_documents`, `ninjaone_create_related_items_attachment`, `ninjaone_create_related_items_entities`, `ninjaone_create_related_items_entity`, `ninjaone_create_related_items_secure`, `ninjaone_create_software_licenses`, `ninjaone_create_staged_device`, `ninjaone_create_technician`, `ninjaone_create_ticketing_ticket`, `ninjaone_create_unmanaged_device`, `ninjaone_create_unmanaged_devices_decommission`, `ninjaone_delete_asset_relationships`, `ninjaone_delete_related_items`, `ninjaone_get_device`, `ninjaone_get_organization`, `ninjaone_list_activities`, `ninjaone_list_alerts`, `ninjaone_list_asset_relationship_types`, `ninjaone_list_asset_relationships_all`, `ninjaone_list_asset_tags`, `ninjaone_list_automation_scripts`, `ninjaone_list_backup_integrity_check_jobs`, `ninjaone_list_backup_jobs`, `ninjaone_list_billing_accounts`, `ninjaone_list_billing_agreements`, `ninjaone_list_billing_invoices`, `ninjaone_list_billing_products`, `ninjaone_list_checklist_templates`, `ninjaone_list_contacts`, `ninjaone_list_custom_fields_paginated`, `ninjaone_list_custom_tabs_end_user`, `ninjaone_list_custom_tabs_organization_location`, `ninjaone_list_device_custom_fields`, `ninjaone_list_devices`, `ninjaone_list_devices_detailed`, `ninjaone_list_devices_search`, `ninjaone_list_document_templates`, `ninjaone_list_end_users`, `ninjaone_list_groups`, `ninjaone_list_jobs`, `ninjaone_list_locations`, `ninjaone_list_node_roles`, `ninjaone_list_organization_documents`, `ninjaone_list_organizations`, `ninjaone_list_organizations_detailed`, `ninjaone_list_policies`, `ninjaone_list_queries_computer_systems`, `ninjaone_list_queries_custom_fields`, `ninjaone_list_queries_device_health`, `ninjaone_list_queries_disks`, `ninjaone_list_queries_network_interfaces`, `ninjaone_list_queries_operating_systems`, `ninjaone_list_queries_os_patch_installs`, `ninjaone_list_queries_os_patches`, `ninjaone_list_queries_processors`, `ninjaone_list_queries_scoped_custom_fields`, `ninjaone_list_queries_software`, `ninjaone_list_queries_software_patch_installs`, `ninjaone_list_queries_software_patches`, `ninjaone_list_queries_volumes`, `ninjaone_list_queries_windows_services`, `ninjaone_list_related_items`, `ninjaone_list_software`, `ninjaone_list_software_licenses`, `ninjaone_list_technicians`, `ninjaone_list_ticket_forms`, `ninjaone_list_user_roles`, `ninjaone_list_users`, `ninjaone_list_vulnerability_management_scan_groups`, `ninjaone_reset_alert`, `ninjaone_unified_get_me`, `ninjaone_unified_get_organization`, `ninjaone_unified_get_role`, `ninjaone_unified_get_user`, `ninjaone_unified_list_organizations`, `ninjaone_unified_list_resource_types`, `ninjaone_unified_list_resource_users`, `ninjaone_unified_list_roles`, `ninjaone_unified_list_users`, `ninjaone_update_checklist_templates`, `ninjaone_update_custom_fields`, `ninjaone_update_knowledge_base_articles`, `ninjaone_update_organization` `new-actions` Added unified IAM users, roles, organizations, credentials, and resource users/types. Organization enumeration reads up to 1000 organizations (10 pages of 100). # Nmbrs Source: https://docs.stackone.com/connectors/nmbrs/index How to set up the Nmbrs connector, plus the actions and events that are available.
Nmbrs
Previewv2.0.0
70 actions · 1 event · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an integration in the Nmbrs developer portal and subscribing to an API product for a Subscription K... Optionally, configure receiving Events for Nmbrs into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/nmbrs/index.md for the full list. ## Events See https://docs.stackone.com/connectors/nmbrs/index.md for the full list. # Nmbrs Changelog Source: https://docs.stackone.com/connectors/nmbrs/changelog Release history for the Nmbrs connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `new-actions` `webhook` `bug-fix` Added payroll run webhooks, employee document upload, absence creation and salary table versions. Renamed the end contract reasons year parameter, replaced the fixed hours period and year filters with a single period filter, and removed the duplicated employee id from update employee cost center. # Notion Source: https://docs.stackone.com/connectors/notion/index How to set up the Notion connector, plus the actions and events that are available.
Notion
v1.2.0
35 actions · 9 events · 3 auth methods
Knowledge Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for internal tools and single-workspace integrations. You manually share specific pages with the integration. Best for personal and developer-owned workflows. A Personal Access Token (PAT) acts as you and uses your own workspace m... Recommended for public integrations serving multiple users. Users choose which pages to share during authorization. Optionally, configure receiving Events for Notion into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/notion/index.md for the full list. ## Events See https://docs.stackone.com/connectors/notion/index.md for the full list. # Notion Changelog Source: https://docs.stackone.com/connectors/notion/changelog Release history for the Notion connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added Data Sync support for List Users, List Unified Users, and List Unified Organizations, so these resources can be synced into StackOne on a schedule and read without calling Notion. All three run as a full refresh on every sync, because Notion's user and workspace endpoints offer no way to filter by last-updated time. `notion_list_users`, `notion_unified_list_organizations`, `notion_unified_list_users` `bug-fix` `improvement` Fixed organization lookups crashing instead of returning a not-found error. Restored general availability status. `notion_unified_get_organization` `bug-fix` Removed a duplicate copy of the IAM unified_get_me field mapping so the two copies cannot drift apart. No change to the response. # Nutshell Source: https://docs.stackone.com/connectors/nutshell/index How to set up the Nutshell connector, plus the actions and events that are available.
Nutshell
v1.4.0
75 actions · 26 events · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Nutshell email and API key for Basic Authentication. Optionally, configure receiving Events for Nutshell into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/nutshell/index.md for the full list. ## Events See https://docs.stackone.com/connectors/nutshell/index.md for the full list. # Nutshell Changelog Source: https://docs.stackone.com/connectors/nutshell/changelog Release history for the Nutshell connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 21 list actions covering contacts, accounts, leads, activities, notes, tasks, users, tags, sources, products, product categories, industries, outcomes, account and activity types, and the contact, account and lead custom field definitions, so their records can be pulled into StackOne on a schedule and kept up to date, with paging handled automatically. Every action refreshes in full on each run, because Nutshell's list endpoints filter only on creation time and ignore a modified-time filter. The contact, account and lead list-item actions, list_users and get_activities gained optional paging inputs to expose Nutshell's page[page] and page[limit] parameters. `nutshell_get_activities`, `nutshell_list_account_custom_field_attributes`, `nutshell_list_account_items`, `nutshell_list_account_types`, `nutshell_list_accounts`, `nutshell_list_activity_types`, `nutshell_list_contact_custom_field_attributes`, `nutshell_list_contact_items`, `nutshell_list_contacts`, `nutshell_list_industries`, `nutshell_list_lead_custom_field_attributes`, `nutshell_list_lead_items`, `nutshell_list_leads`, `nutshell_list_notes`, `nutshell_list_outcomes`, `nutshell_list_product_categories`, `nutshell_list_products`, `nutshell_list_sources`, `nutshell_list_tags`, `nutshell_list_tasks`, `nutshell_list_users` `description-fix` Document stage moves not supported via API (milestone patch returns 502). Clarify set_lead_stageset sets pipeline only, not stage. Add variants to update_lead value field for object support. `nutshell_set_lead_stageset`, `nutshell_update_lead` `bug-fix` `description-fix` Fix JSON-Patch value field using variants (string | object array) so update_contact/update_account can patch both scalar and array fields (emails, phones, urls). Fix update_task dueTime requiring Unix timestamp (ISO format causes 502). Clarify set_lead_stageset sets pipeline not stage. Document update_task relatedEntity as immutable after creation. Add nested properties to array variant for agent guidance. Improve create_contact phone format description. `nutshell_create_contact`, `nutshell_set_lead_stageset`, `nutshell_update_account`, `nutshell_update_contact`, `nutshell_update_task` `bug-fix` `description-fix` Fix custom field creation by using capitalized type enums (Text, Number, Enum, Date). Clarify JSON-Patch array-field paths for update_contact/update_account, full PUT semantics for update_activity, required fields for create_activity, lead name/links for create_lead, stageset ID source for set_lead_stageset, relatedEntity link path for update_task, and pagination params for list_contacts. # Officient Source: https://docs.stackone.com/connectors/officient/index How to set up the Officient connector, plus the actions that are available.
Officient
Betav0.2.0
71 actions · 2 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a personal access token generated from the Officient developer portal. Recommended for integrating wit... OAuth 2.0 for third-party integrations. Register a client app in the Officient developer portal and configure the OAuth... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/officient/index.md for the full list. # Officient Changelog Source: https://docs.stackone.com/connectors/officient/changelog Release history for the Officient connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to twelve collection actions — people, people search, contracts, assets, asset types, days off requests, custom fields, expense categories, teams, departments, functions and cost centers — so these collections can be kept in sync and searched without calling Officient on every request. People, contracts, assets and days off requests page through results automatically; the remaining collections are returned in full by a single request. All syncs use full refreshes because Officient offers no last-updated filter. `officient_list_asset_types`, `officient_list_assets`, `officient_list_contracts`, `officient_list_cost_centers`, `officient_list_custom_fields`, `officient_list_days_off_requests`, `officient_list_departments`, `officient_list_expense_categories`, `officient_list_functions`, `officient_list_people`, `officient_list_teams`, `officient_search_people` `new-connector` Initial Officient (Exact Officient) HR connector — 71 Core-HR actions across people, contracts, calendar, wages, expenses, expense categories, budgets, assets, asset types, fleet, documents, teams, departments, functions, cost centers, custom fields, performance reviews and account. Bearer access-token auth plus best-effort OAuth 2.0. # Okta Source: https://docs.stackone.com/connectors/okta/index How to set up the Okta connector, plus the actions and events that are available.
Okta
v3.3.1
115 actions · 21 events · 3 auth methods
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an OAuth app registered in Okta Admin Console. Supports OIDC and granular API scopes. Each user signs in with their own Okta account and the token inherits their permissions. The OAuth app Client ID and Sec... Best for admin scripts and internal tools. Token inherits the permissions of the admin who created it. Optionally, configure receiving Events for Okta into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/okta/index.md for the full list. ## Events See https://docs.stackone.com/connectors/okta/index.md for the full list. # Okta Changelog Source: https://docs.stackone.com/connectors/okta/changelog Release history for the Okta connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Added a webhook setup guide covering the Okta admin permissions and org limits that event hook provisioning depends on, how endpoint verification is handled automatically, and the full catalogue of available events. `bug-fix` User lifecycle and application activation actions now return the resulting status, and group assignment returns a success confirmation, instead of an empty response. `okta_activate_application`, `okta_activate_user`, `okta_add_user_to_group`, `okta_deactivate_user`, `okta_list_user_assigned_roles`, `okta_list_user_authenticator_enrollments`, `okta_list_user_factors`, `okta_list_user_roles`, `okta_reset_password`, `okta_suspend_user` `new-actions` `auth` Added user lifecycle, application and group assignment, MFA factor, admin role, device assurance and Identity Governance actions. `okta_activate_application`, `okta_activate_group_rule`, `okta_activate_user`, `okta_assign_group_to_application`, `okta_assign_user_to_application`, `okta_cancel_access_request`, `okta_create_access_request`, `okta_deactivate_application`, `okta_deactivate_group_rule`, `okta_deactivate_user`, `okta_expire_password`, `okta_get_access_request`, `okta_get_campaign`, `okta_get_device_assurance_policy`, `okta_get_request_type`, `okta_get_review`, `okta_get_user_factor`, `okta_launch_campaign`, `okta_list_access_requests`, `okta_list_campaigns`, `okta_list_device_assurance_policies`, `okta_list_group_assigned_applications`, `okta_list_group_owners`, `okta_list_request_types`, `okta_list_reviews`, `okta_list_supported_factors`, `okta_list_user_app_links`, `okta_list_user_assigned_roles`, `okta_list_user_devices`, `okta_publish_request_type`, `okta_reactivate_user`, `okta_reassign_reviews`, `okta_reset_password`, `okta_revoke_user_sessions`, `okta_suspend_device`, `okta_suspend_user`, `okta_unassign_group_from_application`, `okta_unassign_user_from_application`, `okta_unlock_user`, `okta_unpublish_request_type`, `okta_unsuspend_device`, `okta_unsuspend_user` `okta_activate_device`, `okta_activate_policy`, `okta_activate_policy_rule`, `okta_add_user_to_group`, `okta_clone_policy`, `okta_create_group`, `okta_create_policy`, `okta_create_policy_rule`, `okta_create_policy_simulation`, `okta_create_realm`, `okta_create_user`, `okta_create_user_type`, `okta_deactivate_device`, `okta_deactivate_policy`, `okta_deactivate_policy_rule`, `okta_delete_device`, `okta_delete_group`, `okta_delete_policy`, `okta_delete_policy_rule`, `okta_delete_realm`, `okta_delete_user`, `okta_delete_user_type`, `okta_get_application`, `okta_get_application_group`, `okta_get_application_user`, `okta_get_device`, `okta_get_group`, `okta_get_group_rule`, `okta_get_policy`, `okta_get_policy_rule`, `okta_get_realm`, `okta_get_user`, `okta_get_user_type`, `okta_get_userinfo`, `okta_list_api_tokens`, `okta_list_application_groups`, `okta_list_application_users`, `okta_list_applications`, `okta_list_authenticator_methods`, `okta_list_authenticators`, `okta_list_custom_roles`, `okta_list_devices`, `okta_list_event_hooks`, `okta_list_group_members`, `okta_list_group_rules`, `okta_list_groups`, `okta_list_identity_providers`, `okta_list_network_zones`, `okta_list_policies`, `okta_list_policy_apps`, `okta_list_policy_mappings`, `okta_list_policy_rules`, `okta_list_realms`, `okta_list_system_logs`, `okta_list_trusted_origins`, `okta_list_user_authenticator_enrollments`, `okta_list_user_blocks`, `okta_list_user_factors`, `okta_list_user_groups`, `okta_list_user_roles`, `okta_list_user_types`, `okta_list_users`, `okta_list_users_with_role_assignments`, `okta_remove_user_from_group`, `okta_replace_policy`, `okta_replace_policy_rule`, `okta_replace_user`, `okta_replace_user_type`, `okta_retrieve_policy_mapping`, `okta_update_group`, `okta_update_realm`, `okta_update_user`, `okta_update_user_type` `new-actions` Added read actions for group rules, user MFA factors and authenticator enrollments, user groups and admin roles, authenticators, and org security settings such as API tokens, network zones, identity providers, trusted origins and event hooks. `okta_get_group_rule`, `okta_list_api_tokens`, `okta_list_authenticator_methods`, `okta_list_authenticators`, `okta_list_custom_roles`, `okta_list_event_hooks`, `okta_list_group_rules`, `okta_list_identity_providers`, `okta_list_network_zones`, `okta_list_trusted_origins`, `okta_list_user_authenticator_enrollments`, `okta_list_user_factors`, `okta_list_user_groups`, `okta_list_user_roles`, `okta_list_users_with_role_assignments` `documentation` Moved 10 actions from preview to beta. `okta_create_policy_simulation`, `okta_create_realm`, `okta_delete_realm`, `okta_get_realm`, `okta_list_realms`, `okta_list_user_blocks`, `okta_update_realm` `data-sync` Added DataSync support for users, groups, devices, applications, system logs, realms, and user types with incremental sync for users, groups, and devices. Breaking change: list_user_types response is now wrapped in a data object. `okta_list_applications`, `okta_list_devices`, `okta_list_groups`, `okta_list_realms`, `okta_list_system_logs`, `okta_list_user_types`, `okta_list_users` `description-improvements` Documented factorPromptMode and factorLifetime requirements for MFA sign-on policy rules in create_policy_rule action. `okta_create_policy_rule` `description-improvements` `bug-fixes` Improved action descriptions with cross-action dependency hints. Fixed list_applications by removing non-functional expand parameter. Documented create_policy_rule required fields, OFF_NETWORK constraint, and list_policies sortBy valid values. `okta_activate_device`, `okta_add_user_to_group`, `okta_create_policy_rule`, `okta_deactivate_device`, `okta_delete_device`, `okta_delete_group`, `okta_delete_user`, `okta_get_application`, `okta_get_application_group`, `okta_get_application_user`, `okta_get_device`, `okta_get_group`, `okta_get_user`, `okta_list_application_groups`, `okta_list_application_users`, `okta_list_applications`, `okta_list_group_members`, `okta_list_policies`, `okta_list_user_blocks`, `okta_remove_user_from_group`, `okta_replace_policy_rule`, `okta_replace_user`, `okta_update_group`, `okta_update_user` `new-actions` Added 6 new Application actions (list_applications, get_application, list_application_groups, get_application_group, list_application_users, get_application_user) with pagination, filtering, and expand support. Added okta.apps.read and okta.apps.manage scope definitions. `okta_get_application`, `okta_get_application_group`, `okta_get_application_user`, `okta_list_application_groups`, `okta_list_application_users`, `okta_list_applications` `okta_activate_device`, `okta_activate_policy`, `okta_activate_policy_rule`, `okta_add_user_to_group`, `okta_clone_policy`, `okta_create_group`, `okta_create_policy`, `okta_create_policy_rule`, `okta_create_policy_simulation`, `okta_create_realm`, `okta_create_user`, `okta_create_user_type`, `okta_deactivate_device`, `okta_deactivate_policy`, `okta_deactivate_policy_rule`, `okta_delete_device`, `okta_delete_group`, `okta_delete_policy`, `okta_delete_policy_rule`, `okta_delete_realm`, `okta_delete_user`, `okta_delete_user_type`, `okta_get_device`, `okta_get_group`, `okta_get_policy`, `okta_get_policy_rule`, `okta_get_realm`, `okta_get_user`, `okta_get_user_type`, `okta_get_userinfo`, `okta_list_devices`, `okta_list_group_members`, `okta_list_groups`, `okta_list_policies`, `okta_list_policy_apps`, `okta_list_policy_mappings`, `okta_list_policy_rules`, `okta_list_realms`, `okta_list_system_logs`, `okta_list_user_blocks`, `okta_list_user_types`, `okta_list_users`, `okta_remove_user_from_group`, `okta_replace_policy`, `okta_replace_policy_rule`, `okta_replace_user`, `okta_replace_user_type`, `okta_retrieve_policy_mapping`, `okta_update_group`, `okta_update_realm`, `okta_update_user`, `okta_update_user_type` `new-actions` `guides` Added System Log API support (list_system_logs action) with filtering, keyword search, time range, and cursor-based pagination. `okta_list_system_logs` `okta_activate_device`, `okta_activate_policy`, `okta_activate_policy_rule`, `okta_add_user_to_group`, `okta_clone_policy`, `okta_create_group`, `okta_create_policy`, `okta_create_policy_rule`, `okta_create_policy_simulation`, `okta_create_realm`, `okta_create_user`, `okta_create_user_type`, `okta_deactivate_device`, `okta_deactivate_policy`, `okta_deactivate_policy_rule`, `okta_delete_device`, `okta_delete_group`, `okta_delete_policy`, `okta_delete_policy_rule`, `okta_delete_realm`, `okta_delete_user`, `okta_delete_user_type`, `okta_get_device`, `okta_get_group`, `okta_get_policy`, `okta_get_policy_rule`, `okta_get_realm`, `okta_get_user`, `okta_get_user_type`, `okta_get_userinfo`, `okta_list_devices`, `okta_list_group_members`, `okta_list_groups`, `okta_list_policies`, `okta_list_policy_apps`, `okta_list_policy_mappings`, `okta_list_policy_rules`, `okta_list_realms`, `okta_list_user_blocks`, `okta_list_user_types`, `okta_list_users`, `okta_remove_user_from_group`, `okta_replace_policy`, `okta_replace_policy_rule`, `okta_replace_user`, `okta_replace_user_type`, `okta_retrieve_policy_mapping`, `okta_update_group`, `okta_update_realm`, `okta_update_user`, `okta_update_user_type` `guides` Added screenshots and improved connection guide steps for OAuth and API key authentication. `new-actions` `auth` `breaking` Added 19 policy actions (CRUD, lifecycle, rules, mappings, simulation) with data envelope responses. Migrated all actions to authRequirements for per-auth-type scope control. # Oneflow Source: https://docs.stackone.com/connectors/oneflow/index How to set up the Oneflow connector, plus the actions and events that are available.
Oneflow
v1.3.1
98 actions · 45 events · 1 auth method
E-Signature
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Oneflow authenticates with a static account API token plus the email of a registered Oneflow user that the request acts... Optionally, configure receiving Events for Oneflow into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/oneflow/index.md for the full list. ## Events See https://docs.stackone.com/connectors/oneflow/index.md for the full list. # Oneflow Changelog Source: https://docs.stackone.com/connectors/oneflow/changelog Release history for the Oneflow connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Clarified that import contract delivery channels depend on the channels your account has enabled (with the none fallback when a channel is unavailable), and documented that updating a contract's signing order requires the acting user to hold the contract update permission. `oneflow_import_contract`, `oneflow_update_contract` `new-feature` `bug-fix` Added participant permission support to the create contract and import contract actions so signatory participants can be created, and clarified the signatory permission and sign order requirements across the contract actions. `oneflow_active_check`, `oneflow_create_contact`, `oneflow_create_contract`, `oneflow_create_contract_party`, `oneflow_create_tag`, `oneflow_create_template_type`, `oneflow_create_webhook`, `oneflow_delete_contact`, `oneflow_delete_contract`, `oneflow_delete_contract_participant`, `oneflow_delete_contract_party`, `oneflow_delete_tag`, `oneflow_delete_webhook`, `oneflow_get_account`, `oneflow_get_contact`, `oneflow_get_contract`, `oneflow_get_contract_participant`, `oneflow_get_contract_party`, `oneflow_get_tag`, `oneflow_get_template_type`, `oneflow_get_webhook`, `oneflow_get_workspace`, `oneflow_import_contract`, `oneflow_list_contacts`, `oneflow_list_contract_data_fields`, `oneflow_list_contract_files`, `oneflow_list_contract_parties`, `oneflow_list_contract_products`, `oneflow_list_contracts`, `oneflow_list_tags`, `oneflow_list_template_types`, `oneflow_list_templates`, `oneflow_list_users`, `oneflow_list_webhooks`, `oneflow_list_workspaces`, `oneflow_update_contact`, `oneflow_update_contract`, `oneflow_update_contract_party`, `oneflow_update_tag`, `oneflow_update_webhook` `new-feature` Added scheduled data sync to the users, templates, contracts, workspaces, tags, and template types list actions for scheduled full record syncs. `oneflow_list_contracts`, `oneflow_list_tags`, `oneflow_list_template_types`, `oneflow_list_templates`, `oneflow_list_users`, `oneflow_list_workspaces` `webhook` `new-actions` Added webhook event support. Oneflow now delivers real-time notifications for contract, participant, party, product, data field, comment, and reminder events (44 event types), with the webhook subscription created and removed automatically when you connect or disconnect your account. # OneLogin Source: https://docs.stackone.com/connectors/onelogin/index How to set up the OneLogin connector, plus the actions that are available.
OneLogin
Previewv1.2.0
119 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create API credentials in OneLogin Administration > Developers > API Credentials. Select appropriate scopes for the oper... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/onelogin/index.md for the full list. # OneLogin Changelog Source: https://docs.stackone.com/connectors/onelogin/changelog Release history for the OneLogin connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for 19 list actions, including incremental sync for users (list_users) and events. `onelogin_list_apps`, `onelogin_list_auth_servers`, `onelogin_list_brands`, `onelogin_list_connectors`, `onelogin_list_custom_attributes`, `onelogin_list_event_types`, `onelogin_list_events`, `onelogin_list_groups`, `onelogin_list_hook_env_vars`, `onelogin_list_hooks`, `onelogin_list_mapping_actions`, `onelogin_list_mapping_conditions`, `onelogin_list_risk_rules`, `onelogin_list_roles`, `onelogin_list_user_mappings`, `onelogin_list_users`, `onelogin_unified_list_groups`, `onelogin_unified_list_roles`, `onelogin_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, credentials, and resource users. # OneNote Source: https://docs.stackone.com/connectors/onenote/index How to set up the OneNote connector, plus the actions that are available.
OneNote
Previewv1.1.0
37 actions · 1 auth method
Productivity IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect Microsoft OneNote. You'll need to register an Azure applica... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/onenote/index.md for the full list. # OneNote Changelog Source: https://docs.stackone.com/connectors/onenote/changelog Release history for the OneNote connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added Data Sync support for notebooks, sections, section groups and directory users, all full refresh as no updated-since filter is configured. List Users gains an optional skiptoken input and returns a next value, so paging can follow Microsoft Graph's skip token. `onenote_list_notebooks`, `onenote_list_section_groups`, `onenote_list_sections`, `onenote_list_users` `description-fix` Added Client Credentials auth, description fixes for list_pages/copy/list_users error handling, and documented cross-user access limitation on user-scoped actions. # OneSignal Source: https://docs.stackone.com/connectors/onesignal/index How to set up the OneSignal connector, plus the actions and events that are available.
OneSignal
v1.1.1
63 actions · 24 events · 1 auth method
Developer Tools Marketing Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses OneSignal API keys sent as an Authorization header with the literal prefix "Key". The App API Key and App ID cover... Optionally, configure receiving Events for OneSignal into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/onesignal/index.md for the full list. ## Events See https://docs.stackone.com/connectors/onesignal/index.md for the full list. # OneSignal Changelog Source: https://docs.stackone.com/connectors/onesignal/changelog Release history for the OneSignal connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed data syncs failing part-way with a rate-limit error on accounts with large message or template histories, and cut the number of requests needed to sync segments. `onesignal_view_segments` `new-events` Added webhook support through OneSignal Event Streams, covering the twenty-four message event kinds across push, in-app messages, email, SMS and Live Activities. Push Delivered is verified against a live delivery and ships as preview; the other twenty-three could not be produced on a sandbox app with no subscribed device and no email or SMS channel, and ship as beta. Each event reports the message it concerns as the record id. The Event Stream is created by hand in the OneSignal dashboard under Data > Event streams, because OneSignal exposes no API for creating one; a setup guide walks through the dashboard flow with screenshots and gives the exact JSON body to paste, which the payload shape depends on, plus the Content-Type header OneSignal does not send on its own. Routing reads flat, underscored keys - event_kind and message_id - rather than the dotted keys in OneSignal's own documentation example, which no router path can address. The deprecated message.email.sent and message.sms.sent kinds are not included - they cannot be added to new Event Streams. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `onesignal_bulk_update_or_delete_message_state`, `onesignal_cancel_message`, `onesignal_copy_template_to_another_app`, `onesignal_count_unsaved`, `onesignal_create_alias`, `onesignal_create_alias_by_subscription`, `onesignal_create_an_app`, `onesignal_create_api_key`, `onesignal_create_inbox_broadcast_message`, `onesignal_create_push_notification`, `onesignal_create_subscription`, `onesignal_create_template`, `onesignal_create_user`, `onesignal_delete_alias`, `onesignal_delete_api_key`, `onesignal_delete_subscription`, `onesignal_delete_template`, `onesignal_delete_user`, `onesignal_export_csv_of_events`, `onesignal_export_subscriptions_csv`, `onesignal_fetch_aliases`, `onesignal_fetch_identity_by_subscription`, `onesignal_rotate_api_key`, `onesignal_transfer_subscription`, `onesignal_update_an_app`, `onesignal_update_api_key`, `onesignal_update_message_state`, `onesignal_update_subscription`, `onesignal_update_subscription_by_token`, `onesignal_update_template`, `onesignal_update_user`, `onesignal_view_an_app`, `onesignal_view_api_keys`, `onesignal_view_apps`, `onesignal_view_broadcasts`, `onesignal_view_message`, `onesignal_view_messages`, `onesignal_view_segment`, `onesignal_view_segments`, `onesignal_view_template`, `onesignal_view_templates`, `onesignal_view_user`, `onesignal_view_user_inbox_messages`, `onesignal_view_user_unread_message_count` `bug-fix` Corrected the site_name description on Create An App and Update An App - a web-push-configured app can be renamed through the API when the request includes the Safari certificate fields alongside the web push origins. `onesignal_create_an_app`, `onesignal_update_an_app` `data-sync` `new-feature` `bug-fix` Added Data Sync support for messages, templates, segments, inbox broadcasts, journeys, apps and app API keys, all full refresh as OneSignal exposes no updated-since filter. Update API Key now returns a confirmation message instead of an empty body, and several action descriptions were clarified. `onesignal_count_unsaved`, `onesignal_create_user`, `onesignal_fetch_identity_by_subscription`, `onesignal_update_an_app`, `onesignal_update_api_key`, `onesignal_view_api_keys`, `onesignal_view_apps`, `onesignal_view_broadcasts`, `onesignal_view_journeys`, `onesignal_view_messages`, `onesignal_view_segments`, `onesignal_view_templates` `bug-fix` `breaking` Message templates can now set push titles, subtitles, email subjects and BCC recipients, and template-based or silent sends no longer require a message body. Removed message outcome metrics and last-active delivery, which need a paid OneSignal plan. `onesignal_count_unsaved`, `onesignal_create_an_app`, `onesignal_create_api_key`, `onesignal_create_email_message`, `onesignal_create_push_notification`, `onesignal_create_sms_message`, `onesignal_create_subscription`, `onesignal_create_template`, `onesignal_transfer_subscription`, `onesignal_update_api_key`, `onesignal_update_template`, `onesignal_update_user`, `onesignal_view_broadcasts`, `onesignal_view_message`, `onesignal_view_segment`, `onesignal_view_user_inbox_messages` `new-actions` Initial OneSignal connector with 63 actions covering messaging, users, subscriptions, segments, templates, journeys, inbox, exports and app administration. # Ontra Source: https://docs.stackone.com/connectors/ontra/index How to set up the Ontra connector, plus the actions that are available.
Ontra
Betav0.2.0
70 actions · 1 auth method
Legal Contract Lifecycle Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Machine-to-machine access using an Ontra API client. Production requires mutual TLS (mTLS) with a self-signed certificat... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ontra/index.md for the full list. # Ontra Changelog Source: https://docs.stackone.com/connectors/ontra/changelog Release history for the Ontra connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the account, entity, external entity, person, ownership relationship, contractual relationship, tax identifier, entity registration, tag, and related reference list actions, with incremental syncs by update time where Ontra supports it. `ontra_list_accounts`, `ontra_list_contractual_relationship_types`, `ontra_list_contractual_relationships`, `ontra_list_currencies`, `ontra_list_entities`, `ontra_list_entity_purposes`, `ontra_list_entity_registrations`, `ontra_list_entity_types`, `ontra_list_external_entities`, `ontra_list_jurisdictions`, `ontra_list_ownership_relationship_types`, `ontra_list_ownership_relationships`, `ontra_list_persons`, `ontra_list_registered_agents`, `ontra_list_registration_authorities`, `ontra_list_tags`, `ontra_list_tax_identifier_types`, `ontra_list_tax_identifiers`, `ontra_list_tax_treatments` `new-connector` Initial preview release of the Ontra connector with 70 actions covering legal entities, external entities, ownership relationships, contractual relationships, people, tax identifiers, entity registrations and tags, plus the reference lookups those writes require. Authenticated via OAuth 2.0 client credentials with mutual TLS (mTLS), which Ontra requires in production. # Open Library Source: https://docs.stackone.com/connectors/openlibrary/index How to set up the Open Library connector, plus the actions that are available.
Open Library
v1.0.0
25 actions · 2 auth methods
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No credentials, covers all read actions. Per Open Library policy, requests must identify the calling application via a U... Authenticates with the Internet Archive S3 API keys of your Open Library account, enabling the list write actions on top... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/openlibrary/index.md for the full list. # Open Library Changelog Source: https://docs.stackone.com/connectors/openlibrary/changelog Release history for the Open Library connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `description-improvement` Improved action descriptions for get_subject (clarified published_in filters on edition dates) and search_lists (clarified global public catalog scope vs user-specific lists). `openlibrary_get_subject`, `openlibrary_search_lists` `bug-fix` Removed broken provider params (ebooks, details, lang), added date-scoped pagination for recent changes with validationRules, made list_user_lists limit required, added atLeastOneOf validation for update_list_seeds, and fixed setup guide labels. `openlibrary_get_subject`, `openlibrary_list_recent_changes`, `openlibrary_list_user_lists`, `openlibrary_search_books`, `openlibrary_update_list_seeds` `new-connector` Added the Open Library connector with catalog search, work, edition, author, subject, and reading list actions, plus search inside books, the Volumes API, lists containing a seed, reading-log shelves, and recent changes. # Open-Meteo Source: https://docs.stackone.com/connectors/openmeteo/index How to set up the Open-Meteo connector, plus the actions that are available.
Open-Meteo
Previewv1.0.0
6 actions · 2 auth methods
Weather
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No authentication required for free non-commercial use. API key for commercial use with higher rate limits. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/openmeteo/index.md for the full list. # OpenAI Source: https://docs.stackone.com/connectors/openai/index How to set up the OpenAI connector, plus the actions and events that are available.
OpenAI
v1.2.3
121 actions · 16 events · 3 auth methods
AI IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate API keys from your OpenAI account settings. Project-scoped keys are recommended for better security. Admin API... Use a standard project-scoped or user API key. Suitable for accessing models, completions, embeddings, audio, and other... Use an admin API key for organization and project management features. Only organization owners and admins can create ad... Optionally, configure receiving Events for OpenAI into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/openai/index.md for the full list. ## Events See https://docs.stackone.com/connectors/openai/index.md for the full list. # OpenAI Changelog Source: https://docs.stackone.com/connectors/openai/changelog Release history for the OpenAI connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Compacting a response now requires a previous response id or input items up front, matching what the API accepts. `openai_compact_response` `bug-fix` `auth` Speech audio and skill/container file downloads now return intact base64 content, empty-body requests no longer fail, and inputs now state the API's model and format rules. Admin actions are now offered only on connections with an admin API key and standard actions only on connections with a user API key, with connection tests matched to each. `openai_add_group_user`, `openai_add_project_group`, `openai_archive_organization_project`, `openai_assign_organization_role_to_group`, `openai_assign_project_group_role`, `openai_assign_project_user_role`, `openai_cancel_response`, `openai_compact_response`, `openai_count_response_input_tokens`, `openai_create_admin_api_key`, `openai_create_client_secret`, `openai_create_container`, `openai_create_container_file`, `openai_create_conversation`, `openai_create_conversation_items`, `openai_create_organization_group`, `openai_create_organization_invite`, `openai_create_organization_project`, `openai_create_organization_role`, `openai_create_project_role`, `openai_create_project_service_account`, `openai_create_project_user`, `openai_create_response`, `openai_create_skill`, `openai_create_skill_version`, `openai_create_speech`, `openai_create_transcription`, `openai_create_translation`, `openai_delete_admin_api_key`, `openai_delete_container`, `openai_delete_container_file`, `openai_delete_conversation`, `openai_delete_conversation_item`, `openai_delete_fine_tuned_model`, `openai_delete_organization_group`, `openai_delete_organization_invite`, `openai_delete_organization_role`, `openai_delete_organization_user`, `openai_delete_project_api_key`, `openai_delete_project_role`, `openai_delete_project_service_account`, `openai_delete_project_user`, `openai_delete_response`, `openai_delete_skill`, `openai_delete_skill_version`, `openai_download_skill_content`, `openai_download_skill_version_content`, `openai_get_audio_speeches_usage`, `openai_get_audio_transcriptions_usage`, `openai_get_code_interpreter_sessions_usage`, `openai_get_completions_usage`, `openai_get_costs`, `openai_get_embeddings_usage`, `openai_get_images_usage`, `openai_get_moderations_usage`, `openai_get_skill`, `openai_get_skill_version`, `openai_get_vector_stores_usage`, `openai_list_admin_api_keys`, `openai_list_audit_logs`, `openai_list_container_files`, `openai_list_containers`, `openai_list_conversation_items`, `openai_list_group_organization_role_assignments`, `openai_list_group_users`, `openai_list_models`, `openai_list_organization_groups`, `openai_list_organization_invites`, `openai_list_organization_projects`, `openai_list_organization_roles`, `openai_list_organization_users`, `openai_list_project_api_keys`, `openai_list_project_group_roles`, `openai_list_project_groups`, `openai_list_project_rate_limits`, `openai_list_project_roles`, `openai_list_project_service_accounts`, `openai_list_project_user_roles`, `openai_list_project_users`, `openai_list_response_input_items`, `openai_list_skill_versions`, `openai_list_skills`, `openai_modify_organization_project`, `openai_modify_organization_user`, `openai_modify_project_rate_limit`, `openai_modify_project_user`, `openai_remove_group_user`, `openai_remove_project_group`, `openai_retrieve_admin_api_key`, `openai_retrieve_container`, `openai_retrieve_container_file`, `openai_retrieve_container_file_content`, `openai_retrieve_conversation`, `openai_retrieve_conversation_item`, `openai_retrieve_model`, `openai_retrieve_organization_invite`, `openai_retrieve_organization_project`, `openai_retrieve_organization_user`, `openai_retrieve_project_api_key`, `openai_retrieve_project_service_account`, `openai_retrieve_project_user`, `openai_retrieve_response`, `openai_unassign_organization_role_from_group`, `openai_unassign_project_group_role`, `openai_unassign_project_user_role`, `openai_unified_get_group`, `openai_unified_get_me`, `openai_unified_get_organization`, `openai_unified_get_role`, `openai_unified_get_user`, `openai_unified_list_groups`, `openai_unified_list_organizations`, `openai_unified_list_resource_types`, `openai_unified_list_resource_users`, `openai_unified_list_roles`, `openai_unified_list_users`, `openai_update_conversation`, `openai_update_organization_group`, `openai_update_organization_role`, `openai_update_project_role`, `openai_update_skill` `bug-fix` Fixed role and organization lookups returning a placeholder record instead of a not-found error for unrecognized IDs. `openai_unified_get_group`, `openai_unified_get_me`, `openai_unified_get_organization`, `openai_unified_get_role`, `openai_unified_list_groups`, `openai_unified_list_organizations`, `openai_unified_list_resource_users`, `openai_unified_list_roles`, `openai_unified_list_users` `bug-fix` Fixed missing last names on user records, incorrect admin permissions on several user and group actions, and broken resource user lookups. Project member and resource-user lookups now read up to 1,000 records per project instead of silently stopping at 25. `openai_unified_get_group`, `openai_unified_get_me`, `openai_unified_get_role`, `openai_unified_get_user`, `openai_unified_list_groups`, `openai_unified_list_resource_types`, `openai_unified_list_resource_users`, `openai_unified_list_users` `feature` Added native webhook event support — 15 event types (batch, background responses, eval runs, realtime/live calls, and video) each mapped to its own handler, with a router, an events setup guide, and nativeWebhookUrl on all auth types. Events are configured manually in the OpenAI dashboard. Verified end-to-end delivery and mapping for all 15 events. `bug-fix` Fixed unified IAM schema conformance — list_users/get_user and list_resource_users now return created_at as an ISO 8601 datetime string instead of an epoch-seconds number. # OpenSearch Source: https://docs.stackone.com/connectors/opensearch/index How to set up the OpenSearch connector, plus the actions that are available.
OpenSearch
Previewv0.1.0
69 actions · 4 auth methods
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Basic HTTP authentication against the OpenSearch Security Plugin. Same credentials carry across every REST endpoint. Com... OpenSearch API key authentication. Preferred over basic auth when the cluster's Security Plugin has API keys enabled (Op... JWT bearer-token authentication via the Security Plugin's \`jwt\_auth\_domain\`. The caller supplies a pre-issued JWT (typic... AWS Signature Version 4 signing — the only accepted auth mode for AWS OpenSearch Serverless (service \`aoss\`) and for AWS... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/opensearch/index.md for the full list. # OpenSearch Changelog Source: https://docs.stackone.com/connectors/opensearch/changelog Release history for the OpenSearch connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Initial release of the OpenSearch connector covering the REST data plane (documents, search, indices, cluster, snapshots, cat, tasks) plus the OpenSearch Dashboards saved-objects surface via an optional dashboardsBaseUrl credential. Supports four authentication modes — Basic Authentication, API Key, JWT Bearer Token, and AWS IAM (SigV4) — each with a per-platform connection guide covering self-hosted clusters, AWS OpenSearch Service (Managed), AWS OpenSearch Serverless, Aiven for OpenSearch, and Bonsai. # OpenStreetMap Source: https://docs.stackone.com/connectors/openstreetmap/index How to set up the OpenStreetMap connector, plus the actions that are available.
OpenStreetMap
v2.1.0
85 actions · 2 auth methods
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OpenStreetMap requires OAuth 2.0 for all editing operations (create/update/delete elements, changesets, notes, GPS trace... Connect without credentials to use OpenStreetMap's public APIs only: Nominatim geocoding (search/reverse/lookup/details/... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/openstreetmap/index.md for the full list. # OpenStreetMap Changelog Source: https://docs.stackone.com/connectors/openstreetmap/changelog Release history for the OpenStreetMap connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` GPS trace downloads now return the trace file as base64-encoded content instead of an empty result. GPS trace create, read, update, download, and delete actions are now generally available, and the moderator-only hide and redaction actions are marked beta. `openstreetmap_create_gpx_trace`, `openstreetmap_create_note`, `openstreetmap_delete_gpx_trace`, `openstreetmap_get_gpx_trace_data`, `openstreetmap_get_gpx_trace_details`, `openstreetmap_hide_changeset_comment`, `openstreetmap_hide_note`, `openstreetmap_redact_node_version`, `openstreetmap_redact_relation_version`, `openstreetmap_redact_way_version`, `openstreetmap_unhide_changeset_comment`, `openstreetmap_update_gpx_trace` `data-sync` `new-feature` Enabled data sync on the own GPS traces list action, so the authenticated user's uploaded traces can be periodically pulled into StackOne and kept up to date. Full refresh on each run, as OpenStreetMap exposes no updated-since filter. `openstreetmap_list_own_gpx_traces` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `guide` Improved connection guides: clarified which OAuth 2.0 permissions are required for your selected actions and streamlined the No Authentication setup instructions. `new-connector` Initial release. 85 actions across three OpenStreetMap services — the OSM Editing API v0.6 (nodes, ways, relations, changesets, notes, GPS traces, user preferences, and messages), Nominatim geocoding (search/reverse/lookup/details), and Overpass QL feature queries. Offers OAuth 2.0 for editing and private data plus a credential-less No-Authentication method for the public read/query APIs, across Production and Sandbox environments. # OpenVPN CloudConnexa Source: https://docs.stackone.com/connectors/openvpncloudconnexa/index How to set up the OpenVPN CloudConnexa connector, plus the actions that are available.
OpenVPN CloudConnexa
Previewv2.0.0
68 actions · 1 auth method
Security IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Owner privileges within your OpenVPN CloudConnexa tenant. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/openvpncloudconnexa/index.md for the full list. # OpenVPN CloudConnexa Changelog Source: https://docs.stackone.com/connectors/openvpncloudconnexa/changelog Release history for the OpenVPN CloudConnexa connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `data-sync` `new-actions` `new-feature` BREAKING - most collection actions have been renamed from `list_*` to `get_*` (`list_networks` is now `get_networks`, `list_users` is now `get_users`, and likewise for access groups, devices, DNS records, hosts, host connectors, location contexts, network connectors, routes and user groups). `list_sessions` and `list_vpn_regions` keep their names - there is no `get_sessions` or `get_vpn_regions`. Update any integration calling the old names. The `connectorId` input on Delete Host Connector is now `id`, and free-text fields across networks, network connectors, users and sessions are now validated enums, so values outside the documented set are rejected up front instead of failing at CloudConnexa. Adds Get Route for fetching a single route by ID, and scheduled Data Sync for 13 collections - networks, network connectors, hosts, host connectors, users, user groups, devices, DNS records, access groups, location contexts, VPN regions, and the unified users and groups - so they can be kept in sync without calling CloudConnexa on every request. Each refreshes in full on every run, because CloudConnexa offers no updated-since filter. Routes and Sessions cannot be synced, as each requires an input that would limit a sync to a single network or a single page. Sessions `size` is now capped at the documented provider maximum of 100, and the access group source/destination guidance now reflects that the two sides accept different item types. `openvpncloudconnexa_get_access_groups`, `openvpncloudconnexa_get_devices`, `openvpncloudconnexa_get_dns_records`, `openvpncloudconnexa_get_host_connectors`, `openvpncloudconnexa_get_hosts`, `openvpncloudconnexa_get_location_contexts`, `openvpncloudconnexa_get_network_connectors`, `openvpncloudconnexa_get_networks`, `openvpncloudconnexa_get_route`, `openvpncloudconnexa_get_routes`, `openvpncloudconnexa_get_user_groups`, `openvpncloudconnexa_get_users` `openvpncloudconnexa_list_access_groups`, `openvpncloudconnexa_list_devices`, `openvpncloudconnexa_list_dns_records`, `openvpncloudconnexa_list_host_connectors`, `openvpncloudconnexa_list_hosts`, `openvpncloudconnexa_list_location_contexts`, `openvpncloudconnexa_list_network_connectors`, `openvpncloudconnexa_list_networks`, `openvpncloudconnexa_list_routes`, `openvpncloudconnexa_list_user_groups`, `openvpncloudconnexa_list_users` `openvpncloudconnexa_activate_host_connector`, `openvpncloudconnexa_activate_network_connector`, `openvpncloudconnexa_activate_user`, `openvpncloudconnexa_create_access_group`, `openvpncloudconnexa_create_device`, `openvpncloudconnexa_create_dns_record`, `openvpncloudconnexa_create_host`, `openvpncloudconnexa_create_host_connector`, `openvpncloudconnexa_create_location_context`, `openvpncloudconnexa_create_network`, `openvpncloudconnexa_create_network_connector`, `openvpncloudconnexa_create_route`, `openvpncloudconnexa_create_user`, `openvpncloudconnexa_create_user_group`, `openvpncloudconnexa_delete_access_group`, `openvpncloudconnexa_delete_device`, `openvpncloudconnexa_delete_dns_record`, `openvpncloudconnexa_delete_host`, `openvpncloudconnexa_delete_host_connector`, `openvpncloudconnexa_delete_location_context`, `openvpncloudconnexa_delete_network`, `openvpncloudconnexa_delete_network_connector`, `openvpncloudconnexa_delete_route`, `openvpncloudconnexa_delete_user`, `openvpncloudconnexa_delete_user_group`, `openvpncloudconnexa_get_access_group`, `openvpncloudconnexa_get_device`, `openvpncloudconnexa_get_dns_record`, `openvpncloudconnexa_get_host`, `openvpncloudconnexa_get_host_connector`, `openvpncloudconnexa_get_location_context`, `openvpncloudconnexa_get_network`, `openvpncloudconnexa_get_network_connector`, `openvpncloudconnexa_get_user`, `openvpncloudconnexa_get_user_group`, `openvpncloudconnexa_list_sessions`, `openvpncloudconnexa_list_vpn_regions`, `openvpncloudconnexa_suspend_host_connector`, `openvpncloudconnexa_suspend_network_connector`, `openvpncloudconnexa_suspend_user`, `openvpncloudconnexa_unified_get_group`, `openvpncloudconnexa_unified_get_user`, `openvpncloudconnexa_unified_list_groups`, `openvpncloudconnexa_unified_list_users`, `openvpncloudconnexa_update_access_group`, `openvpncloudconnexa_update_device`, `openvpncloudconnexa_update_dns_record`, `openvpncloudconnexa_update_host`, `openvpncloudconnexa_update_host_connector`, `openvpncloudconnexa_update_location_context`, `openvpncloudconnexa_update_network`, `openvpncloudconnexa_update_network_connector`, `openvpncloudconnexa_update_route`, `openvpncloudconnexa_update_user`, `openvpncloudconnexa_update_user_group` `new-actions` Added unified IAM actions for users, groups, and credentials, using the connector's existing OAuth 2.0 client credentials authentication. List Unified Users and List Unified Groups request pages until CloudConnexa returns an empty page, so they enumerate the full tenant regardless of size. # Oracle Fusion Source: https://docs.stackone.com/connectors/oraclefusion/index How to set up the Oracle Fusion connector, plus the actions that are available.
Oracle Fusion
Previewv0.2.0
16 actions · 3 auth methods
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Basic Authentication requires a username and password with access to HCM REST APIs. OAuth 2.0 authentication uses client credentials to obtain an access token from Oracle Identity Cloud Service. Three-legged OAuth that acts on behalf of a signed-in Oracle user. Requires a confidential application in Oracle Identit... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/oraclefusion/index.md for the full list. # Oracle Fusion Changelog Source: https://docs.stackone.com/connectors/oraclefusion/changelog Release history for the Oracle Fusion connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the workers and digital learning providers list actions, so these collections can be kept in sync and read back without calling Oracle Fusion on every request. Both sync in a stable primary-key order for reliable pagination and refresh in full (Oracle exposes no dedicated updated-since filter). `oraclefusion_list_digital_learning_providers`, `oraclefusion_list_workers` `new-connector` Initial release of the Oracle Fusion learning connector for Oracle Learning Cloud (OLC): manage digital learning content providers and metadata, learning events, and learner learning records, plus push learner activity (start/completion) via xAPI statements. Includes a read-only Workers module (list/get) to source the worker Person ID used as the learning assignee (assignedToId). # Oracle Fusion HCM Source: https://docs.stackone.com/connectors/oraclehcm/index How to set up the Oracle Fusion HCM connector, plus the actions that are available.
Oracle Fusion HCM
Previewv0.2.0
120 actions · 3 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Basic Authentication requires a username and password with access to HCM REST APIs. OAuth 2.0 authentication uses client credentials to obtain an access token from Oracle Identity Cloud Service. Three-legged OAuth that acts on behalf of a signed-in Oracle user. Requires a confidential application in Oracle Identit... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/oraclehcm/index.md for the full list. # Oracle Fusion HCM Changelog Source: https://docs.stackone.com/connectors/oraclehcm/changelog Release history for the Oracle Fusion HCM connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to seventeen list actions — workers, employees, organizations, jobs, absences, benefit enrollments, digital learning providers, document records, goal plans, performance goals, recruiting candidates, job offers, job requisitions, salaries, talent person profiles, time records, and worker journey tasks — so these collections can be kept in sync and read back without calling Oracle HCM on every request. Each syncs in a stable primary-key order for reliable pagination and refreshes in full (Oracle exposes no dedicated updated-since filter). `oraclehcm_list_absences`, `oraclehcm_list_benefit_enrollments`, `oraclehcm_list_digital_learning_providers`, `oraclehcm_list_document_records`, `oraclehcm_list_emps`, `oraclehcm_list_goal_plans`, `oraclehcm_list_jobs_resource`, `oraclehcm_list_organizations`, `oraclehcm_list_performance_goals`, `oraclehcm_list_recruiting_candidates`, `oraclehcm_list_recruiting_job_offers`, `oraclehcm_list_recruiting_job_requisitions`, `oraclehcm_list_salaries`, `oraclehcm_list_talent_person_profiles`, `oraclehcm_list_time_records`, `oraclehcm_list_worker_journey_tasks`, `oraclehcm_list_workers` `bug-fix` Fixed list_absence_types silently dropping the search term and effective date filters due to an unparsable JEXL expression. `oraclehcm_list_absence_types` `description-fix` Rewrote action descriptions to read as plain, human-friendly sentences of what each action does, removing internal agent-guidance, technical shorthand, and field-name jargon from the customer-facing description field. `oraclehcm_assign_performance_goal`, `oraclehcm_create_absence`, `oraclehcm_create_candidate_attachment`, `oraclehcm_create_document_record`, `oraclehcm_create_document_record_attachment`, `oraclehcm_create_emp`, `oraclehcm_create_goal_plan`, `oraclehcm_create_learner_learning_record`, `oraclehcm_create_learning_event`, `oraclehcm_create_recruiting_candidate`, `oraclehcm_create_recruiting_job_requisition`, `oraclehcm_create_worker`, `oraclehcm_delete_absence`, `oraclehcm_delete_document_record`, `oraclehcm_delete_goal_plan`, `oraclehcm_delete_recruiting_candidate`, `oraclehcm_delete_recruiting_job_requisition`, `oraclehcm_download_candidate_attachment`, `oraclehcm_download_document_record_attachment`, `oraclehcm_download_document_record_attachments_bulk`, `oraclehcm_download_stack_trace`, `oraclehcm_get_absence`, `oraclehcm_get_absence_type_balance`, `oraclehcm_get_benefit_enrollment_opportunity`, `oraclehcm_get_candidate_attachment`, `oraclehcm_get_digital_learning_provider`, `oraclehcm_get_document_record`, `oraclehcm_get_emp`, `oraclehcm_get_learner_learning_record`, `oraclehcm_get_learning_event`, `oraclehcm_get_recruiting_candidate`, `oraclehcm_get_salary`, `oraclehcm_get_user_access_details`, `oraclehcm_get_worker`, `oraclehcm_get_worker_journey_task`, `oraclehcm_get_xapi_statement`, `oraclehcm_import_performance_goals`, `oraclehcm_list_absence_types`, `oraclehcm_list_absences`, `oraclehcm_list_benefit_enrollment_dependents`, `oraclehcm_list_benefit_enrollment_opportunities`, `oraclehcm_list_benefit_enrollments`, `oraclehcm_list_emp_assignments`, `oraclehcm_list_emps`, `oraclehcm_list_goal_plans`, `oraclehcm_list_organizations`, `oraclehcm_list_performance_goal_associated_goal_plans`, `oraclehcm_list_performance_goals`, `oraclehcm_list_salaries`, `oraclehcm_list_talent_person_profiles`, `oraclehcm_list_worker_journey_tasks`, `oraclehcm_list_workers`, `oraclehcm_reprocess_absences_and_run_post_approval_process`, `oraclehcm_restrict_absence_edit`, `oraclehcm_show_absence_plan_usage`, `oraclehcm_sync_goal_plan_with_performance_documents`, `oraclehcm_update_absence`, `oraclehcm_update_emp`, `oraclehcm_update_goal_plan`, `oraclehcm_update_learner_learning_record`, `oraclehcm_update_learning_event`, `oraclehcm_update_recruiting_candidate`, `oraclehcm_update_recruiting_job_requisition`, `oraclehcm_update_worker`, `oraclehcm_upload_hdl_file` `new-actions` `description-fix` Added a List Absence Types action so a valid absence type can be looked up before creating an absence, and clarified absence date-range filtering, document attachment file encoding, and the employee assignment lookup chain. `oraclehcm_list_absence_types` `oraclehcm_create_absence`, `oraclehcm_create_document_record_attachment`, `oraclehcm_create_emp_assignment`, `oraclehcm_get_emp`, `oraclehcm_get_emp_assignment`, `oraclehcm_list_absences`, `oraclehcm_list_emp_assignments`, `oraclehcm_update_emp_assignment` `new-connector` Initial release of the standalone Oracle Fusion HCM connector covering core HR, workforce and assignment management, absence and time tracking, salaries and benefits, recruiting, performance, talent, documents, and learning management. Learning-only integrations are now served by the separate Oracle Fusion connector. # Orderspace Source: https://docs.stackone.com/connectors/orderspace/index How to set up the Orderspace connector, plus the actions and events that are available.
Orderspace
v1.2.0
42 actions · 15 events · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create a Custom Integration in your Orderspace admin panel to obtain OAuth2 Client Credentials. Optionally, configure receiving Events for Orderspace into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/orderspace/index.md for the full list. ## Events See https://docs.stackone.com/connectors/orderspace/index.md for the full list. # Orderspace Changelog Source: https://docs.stackone.com/connectors/orderspace/changelog Release history for the Orderspace connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `improvement` Added data sync support to customer groups, price lists, payment terms, tax rates, and pre-order windows, so their records can be periodically pulled and kept up to date. # Outlook Calendar Source: https://docs.stackone.com/connectors/outlookcalendar/index How to set up the Outlook Calendar connector, plus the actions and events that are available.
Outlook Calendar
v1.2.0
77 actions · 5 events · 1 auth method
Scheduling IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect Outlook Calendar. You'll need to register an Azure applicat... Optionally, configure receiving Events for Outlook Calendar into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/outlookcalendar/index.md for the full list. ## Events See https://docs.stackone.com/connectors/outlookcalendar/index.md for the full list. # Outlook Calendar Changelog Source: https://docs.stackone.com/connectors/outlookcalendar/changelog Release history for the Outlook Calendar connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added webhook support for calendar event created, updated and deleted. StackOne creates and removes the Microsoft Graph subscription on /me/events automatically, so nothing is configured in Outlook or Azure. Notifications carry the event id rather than the event, and cover only the calendar of the user who authorized the connection. Graph expires the subscription after seven days without renewing it, so reconnect the account to resume delivery. `new-feature` `data-sync` Added DataSync support to four list actions: my events, my default calendar events, my calendar groups, and users. Users also exposes a next cursor so the sync can page past the first 100 directory records. All four sync by full refresh. # Outreach Source: https://docs.stackone.com/connectors/outreach/index How to set up the Outreach connector, plus the actions that are available.
Outreach
Betav0.3.0
253 actions · 1 auth method
CRM IAM Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth application in the Outreach developer portal. Uses the authorization code flow with per-re... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/outreach/index.md for the full list. # Outreach Changelog Source: https://docs.stackone.com/connectors/outreach/changelog Release history for the Outreach connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for all list actions, paging through records with the JSON:API page[after] cursor from each response's links.next. `outreach_list_account_notes`, `outreach_list_accounts`, `outreach_list_audit_logs`, `outreach_list_batch_items`, `outreach_list_batches`, `outreach_list_call_dispositions`, `outreach_list_call_purposes`, `outreach_list_calls`, `outreach_list_compliance_requests`, `outreach_list_content_categories`, `outreach_list_content_category_memberships`, `outreach_list_content_category_ownerships`, `outreach_list_duties`, `outreach_list_email_addresses`, `outreach_list_events`, `outreach_list_favorites`, `outreach_list_kaia_recordings`, `outreach_list_mail_aliases`, `outreach_list_mailboxes`, `outreach_list_mailings`, `outreach_list_opportunities`, `outreach_list_opportunity_prospect_roles`, `outreach_list_opportunity_stages`, `outreach_list_personas`, `outreach_list_phone_numbers`, `outreach_list_products`, `outreach_list_profiles`, `outreach_list_prospect_notes`, `outreach_list_prospects`, `outreach_list_purchases`, `outreach_list_recipients`, `outreach_list_roles`, `outreach_list_rulesets`, `outreach_list_sequence_states`, `outreach_list_sequence_steps`, `outreach_list_sequence_templates`, `outreach_list_sequences`, `outreach_list_snippets`, `outreach_list_stages`, `outreach_list_task_dispositions`, `outreach_list_task_priorities`, `outreach_list_task_purposes`, `outreach_list_tasks`, `outreach_list_teams`, `outreach_list_templates`, `outreach_list_users`, `outreach_list_webhooks` `new-actions` `bug-fix` Expanded to complete Outreach API coverage (every documented endpoint) — added the full IAM surface (profiles, roles, teams, audit logs, mail aliases, duties), all remaining resources (notes, products, purchases, content categories, rulesets, webhooks, recipients, favorites, events, dispositions/purposes/priorities, Kaia recordings, compliance requests), and every lifecycle and bulk action (task advance/complete/snooze/reschedule, mailbox test/link, sequence-template activate, batch bulk operations, and imports), and set the required JSON:API Content-Type header on every request. `outreach_activate_sequence_template`, `outreach_advance_task`, `outreach_batch_accounts_add_assignments`, `outreach_batch_accounts_add_tags`, `outreach_batch_accounts_assign_owner`, `outreach_batch_accounts_bulk_modify`, `outreach_batch_accounts_destroy_all`, `outreach_batch_accounts_remove_all_assignments`, `outreach_batch_accounts_remove_assignments`, `outreach_batch_accounts_remove_tags`, `outreach_batch_custom_object_bulk_delete`, `outreach_batch_custom_object_bulk_modify`, `outreach_batch_prospects_add_assignments`, `outreach_batch_prospects_add_tags`, `outreach_batch_prospects_add_to_sequence`, `outreach_batch_prospects_assign_account`, `outreach_batch_prospects_assign_opportunity`, `outreach_batch_prospects_assign_owner`, `outreach_batch_prospects_bulk_modify`, `outreach_batch_prospects_destroy_all`, `outreach_batch_prospects_finish_all`, `outreach_batch_prospects_pause_all`, `outreach_batch_prospects_remove_all_assignments`, `outreach_batch_prospects_remove_assignments`, `outreach_batch_prospects_remove_tags`, `outreach_cancel_batch`, `outreach_complete_task`, `outreach_confirm_batch`, `outreach_create_account_note`, `outreach_create_call_disposition`, `outreach_create_call_purpose`, `outreach_create_compliance_request`, `outreach_create_content_category`, `outreach_create_content_category_membership`, `outreach_create_content_category_ownership`, `outreach_create_custom_duty`, `outreach_create_favorite`, `outreach_create_kaia_voice_import`, `outreach_create_opportunity_prospect_role`, `outreach_create_product`, `outreach_create_profile`, `outreach_create_prospect_note`, `outreach_create_purchase`, `outreach_create_recipient`, `outreach_create_role`, `outreach_create_ruleset`, `outreach_create_task_disposition`, `outreach_create_task_purpose`, `outreach_create_team`, `outreach_create_webhook`, `outreach_deactivate_sequence_template`, `outreach_delete_account_note`, `outreach_delete_call_disposition`, `outreach_delete_call_purpose`, `outreach_delete_content_category`, `outreach_delete_content_category_membership`, `outreach_delete_content_category_ownership`, `outreach_delete_favorite`, `outreach_delete_opportunity_prospect_role`, `outreach_delete_product`, `outreach_delete_profile`, `outreach_delete_prospect_note`, `outreach_delete_purchase`, `outreach_delete_recipient`, `outreach_delete_role`, `outreach_delete_ruleset`, `outreach_delete_task_disposition`, `outreach_delete_task_purpose`, `outreach_delete_team`, `outreach_delete_webhook`, `outreach_deliver_task`, `outreach_get_account_note`, `outreach_get_batch`, `outreach_get_batch_item`, `outreach_get_call_disposition`, `outreach_get_call_purpose`, `outreach_get_compliance_request`, `outreach_get_content_category`, `outreach_get_content_category_membership`, `outreach_get_event`, `outreach_get_favorite`, `outreach_get_import`, `outreach_get_kaia_recording`, `outreach_get_mail_alias`, `outreach_get_opportunity_prospect_role`, `outreach_get_org_settings`, `outreach_get_product`, `outreach_get_profile`, `outreach_get_prospect_note`, `outreach_get_purchase`, `outreach_get_recipient`, `outreach_get_role`, `outreach_get_ruleset`, `outreach_get_task_disposition`, `outreach_get_task_priority`, `outreach_get_task_purpose`, `outreach_get_team`, `outreach_get_webhook`, `outreach_import_accounts`, `outreach_import_bulk_upsert`, `outreach_import_custom_object_bulk_upsert`, `outreach_import_generate_upload_link`, `outreach_import_prospects`, `outreach_import_validate_upload`, `outreach_link_mailbox_ews_master_account`, `outreach_list_account_notes`, `outreach_list_audit_logs`, `outreach_list_batch_items`, `outreach_list_batches`, `outreach_list_call_dispositions`, `outreach_list_call_purposes`, `outreach_list_compliance_requests`, `outreach_list_content_categories`, `outreach_list_content_category_memberships`, `outreach_list_content_category_ownerships`, `outreach_list_duties`, `outreach_list_events`, `outreach_list_favorites`, `outreach_list_kaia_recordings`, `outreach_list_mail_aliases`, `outreach_list_opportunity_prospect_roles`, `outreach_list_products`, `outreach_list_profiles`, `outreach_list_prospect_notes`, `outreach_list_purchases`, `outreach_list_recipients`, `outreach_list_roles`, `outreach_list_rulesets`, `outreach_list_task_dispositions`, `outreach_list_task_priorities`, `outreach_list_task_purposes`, `outreach_list_teams`, `outreach_list_webhooks`, `outreach_log_task_meet_in_person`, `outreach_reassign_task_owner`, `outreach_reschedule_task`, `outreach_snooze_task`, `outreach_test_mailbox_send`, `outreach_test_mailbox_sync`, `outreach_unlink_mailbox_ews_master_account`, `outreach_update_account_note`, `outreach_update_call_disposition`, `outreach_update_call_purpose`, `outreach_update_content_category`, `outreach_update_opportunity_prospect_role`, `outreach_update_org_settings`, `outreach_update_product`, `outreach_update_profile`, `outreach_update_prospect_note`, `outreach_update_purchase`, `outreach_update_recipient`, `outreach_update_role`, `outreach_update_ruleset`, `outreach_update_task_disposition`, `outreach_update_task_note`, `outreach_update_task_opportunity_association`, `outreach_update_task_purpose`, `outreach_update_team`, `outreach_update_webhook` `outreach_activate_sequence`, `outreach_create_account`, `outreach_create_call`, `outreach_create_email_address`, `outreach_create_mailbox`, `outreach_create_mailing`, `outreach_create_opportunity`, `outreach_create_opportunity_stage`, `outreach_create_persona`, `outreach_create_phone_number`, `outreach_create_prospect`, `outreach_create_sequence`, `outreach_create_sequence_state`, `outreach_create_sequence_step`, `outreach_create_sequence_template`, `outreach_create_snippet`, `outreach_create_stage`, `outreach_create_task`, `outreach_create_template`, `outreach_create_user`, `outreach_deactivate_sequence`, `outreach_delete_account`, `outreach_delete_call`, `outreach_delete_email_address`, `outreach_delete_mailbox`, `outreach_delete_opportunity`, `outreach_delete_opportunity_stage`, `outreach_delete_persona`, `outreach_delete_phone_number`, `outreach_delete_prospect`, `outreach_delete_sequence`, `outreach_delete_sequence_state`, `outreach_delete_sequence_template`, `outreach_delete_snippet`, `outreach_delete_stage`, `outreach_delete_task`, `outreach_delete_template`, `outreach_finish_sequence_state`, `outreach_get_account`, `outreach_get_call`, `outreach_get_email_address`, `outreach_get_mailbox`, `outreach_get_mailing`, `outreach_get_opportunity`, `outreach_get_opportunity_stage`, `outreach_get_persona`, `outreach_get_phone_number`, `outreach_get_prospect`, `outreach_get_sequence`, `outreach_get_sequence_state`, `outreach_get_sequence_step`, `outreach_get_sequence_template`, `outreach_get_snippet`, `outreach_get_stage`, `outreach_get_task`, `outreach_get_template`, `outreach_get_user`, `outreach_list_accounts`, `outreach_list_calls`, `outreach_list_email_addresses`, `outreach_list_mailboxes`, `outreach_list_mailings`, `outreach_list_opportunities`, `outreach_list_opportunity_stages`, `outreach_list_personas`, `outreach_list_phone_numbers`, `outreach_list_prospects`, `outreach_list_sequence_states`, `outreach_list_sequence_steps`, `outreach_list_sequence_templates`, `outreach_list_sequences`, `outreach_list_snippets`, `outreach_list_stages`, `outreach_list_tasks`, `outreach_list_templates`, `outreach_list_users`, `outreach_pause_sequence_state`, `outreach_resume_sequence_state`, `outreach_update_account`, `outreach_update_email_address`, `outreach_update_mailbox`, `outreach_update_opportunity`, `outreach_update_opportunity_stage`, `outreach_update_persona`, `outreach_update_phone_number`, `outreach_update_prospect`, `outreach_update_sequence`, `outreach_update_sequence_step`, `outreach_update_sequence_template`, `outreach_update_snippet`, `outreach_update_stage`, `outreach_update_task`, `outreach_update_template`, `outreach_update_user` `new-actions` Initial Outreach connector with 94 actions across prospects, accounts, opportunities, sequences, sequence states/steps/templates, mailings, mailboxes, templates, snippets, calls, tasks, users, personas, stages, opportunity stages, email addresses, and phone numbers. OAuth 2.0 authorization code with rotating refresh tokens. # Oxylabs Source: https://docs.stackone.com/connectors/oxylabs/index How to set up the Oxylabs connector, plus the actions that are available.
Oxylabs
v1.0.0
7 actions · 1 auth method
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses API user credentials (username and password) created in the Oxylabs dashboard. Provides access to Web Scraper API a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/oxylabs/index.md for the full list. # Oxylabs Changelog Source: https://docs.stackone.com/connectors/oxylabs/changelog Release history for the Oxylabs connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` `description-improvement` Removed stale google_ai_mode references from descriptions. Moved chatgpt and perplexity to async-only (realtime returns 422). Removed ebay_search, target_category, and grainger_search (613 faulted). Clarified get_scraping_job returns status only, not scraped content. `oxylabs_create_batch_scraping_job`, `oxylabs_create_scraping_job`, `oxylabs_get_scraping_job`, `oxylabs_scrape_url` `bug-fix` `description-improvement` Removed 24 non-functional scraping sources from body_source enum that return 613 (faulted after retries), 400 (create error), or timeout on the Free Trial plan. Improved get_scraping_job_results description to clarify that results are empty while a job is still pending. `oxylabs_create_batch_scraping_job`, `oxylabs_create_scraping_job`, `oxylabs_get_scraping_job_results`, `oxylabs_scrape_url` `guide` Corrected the API Credentials connection guide to use the Oxylabs dialog's actual Username and Password field labels, and reordered the steps so credentials are copied from the Integration section straight after the free trial is started. Clarified the Username and Password field descriptions as Web Scraper API credentials. `new-connector` Initial release with realtime scraping, async job management, batch scraping, usage statistics, and callback IP listing across 114 sources. # Oyster HR Source: https://docs.stackone.com/connectors/oysterhr/index How to set up the Oyster HR connector, plus the actions and events that are available.
Oyster HR
v1.1.0
59 actions · 45 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 by creating a Developer App in the Oyster Developer Portal. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/oysterhr/index.md for the full list. ## Events See https://docs.stackone.com/connectors/oysterhr/index.md for the full list. # Oyster HR Changelog Source: https://docs.stackone.com/connectors/oysterhr/changelog Release history for the Oyster HR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to thirteen list actions — engagements, contract changes, bank accounts, departments, expenses, payroll runs, payroll changes, payroll change source types (default and current), time off entitlements, time off requests, time sheets, and webhooks — so these collections can be kept in sync and read back without calling Oyster HR on every request. All thirteen refresh in full, as the Oyster HR API exposes no updated-since filter. Also added the missing optional page parameter to List Contract Changes and List Payroll Changes so both can be paginated beyond the first page. # Paddle Source: https://docs.stackone.com/connectors/paddle/index How to set up the Paddle connector, plus the actions and events that are available.
Paddle
v1.3.0
54 actions · 57 events · 1 auth method
Payments
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Paddle API Key for authentication. Create API keys in Developer tools > Authentication. Keys are 69 characters... Optionally, configure receiving Events for Paddle into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/paddle/index.md for the full list. ## Events See https://docs.stackone.com/connectors/paddle/index.md for the full list. # Paddle Changelog Source: https://docs.stackone.com/connectors/paddle/changelog Release history for the Paddle connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `description-fix` Added data sync to ten list actions. Nine page through the provider after cursor and one returns its whole collection in a single call. Each paginated action gains a nextPageToken result key that exposes the after cursor taken from meta.pagination.next, because Paddle returns that field as a full URL rather than a bare cursor. The after input description now points callers at that key. No action syncs incrementally, because Paddle accepts the documented date operators on transactions and then returns every record regardless. `paddle_list_customers`, `paddle_list_discount_groups`, `paddle_list_discounts`, `paddle_list_event_types`, `paddle_list_events`, `paddle_list_notifications`, `paddle_list_prices`, `paddle_list_products`, `paddle_list_subscriptions`, `paddle_list_transactions` `bug-fix` `description-fix` Fix create_price description field required. Fix resume_subscription effective_from required and type. Clarify cancel_subscription rejects end-of-period on paused subs. Fix scheduled_change removal via renamed schedule input with spread null pattern. Improve pause_subscription conflict resolution workflow. `paddle_cancel_subscription`, `paddle_create_price`, `paddle_pause_subscription`, `paddle_resume_subscription`, `paddle_update_subscription` `new-events` Added programmatic webhook event support for all 55 Paddle event types across addresses, adjustments, API keys, businesses, client tokens, customers, discounts, discount groups, payment methods, payouts, prices, products, reports, subscriptions, and transactions. # PagerDuty Source: https://docs.stackone.com/connectors/pagerduty/index How to set up the PagerDuty connector, plus the actions and events that are available.
PagerDuty
v1.4.0
50 actions · 31 events · 1 auth method
ITSM Ticketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from your PagerDuty account settings. Requires appropriate permissions based on the actions you need... Optionally, configure receiving Events for PagerDuty into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pagerduty/index.md for the full list. ## Events See https://docs.stackone.com/connectors/pagerduty/index.md for the full list. # PagerDuty Changelog Source: https://docs.stackone.com/connectors/pagerduty/changelog Release history for the PagerDuty connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added webhook support for the thirty-one v3 event types PagerDuty emits across incidents and services, covering the incident lifecycle, responders and roles, tasks, action invocations and workflows. StackOne creates one account-wide webhook subscription when an account is connected and deletes it on disconnect, subscribed to exactly the events enabled. Each event is routed on event.event_type. Incident events report the incident as the record id, because the sub-resource events carry the note, responder or status update in event.data and some have no id of their own; service events report the service. The fifteen event types verified against live deliveries ship as preview; the sixteen that could not be triggered on the available account ship as beta. `data-sync` Added DataSync support to fifteen list actions, covering audit records, escalation policies, incidents, incident types, licenses, license allocations, schedules, services, teams, users, vendors and the unified IAM users, groups, organizations and roles, so their records can be synced on a schedule and read back without calling PagerDuty each time. Every action refreshes in full on each run, because PagerDuty's since and until filters select records by creation time rather than by modification time. list_priorities is not included, because the endpoint ignores the limit and offset parameters it documents. `pagerduty_list_audit_records`, `pagerduty_list_escalation_policies`, `pagerduty_list_incident_types`, `pagerduty_list_incidents`, `pagerduty_list_license_allocations`, `pagerduty_list_licenses`, `pagerduty_list_schedules`, `pagerduty_list_services`, `pagerduty_list_teams`, `pagerduty_list_users`, `pagerduty_list_vendors`, `pagerduty_unified_list_groups`, `pagerduty_unified_list_organizations`, `pagerduty_unified_list_users` `description-fix` Document list_on_calls since/until 3-month max range constraint. Document create_service scheduled_actions max 1 entry limit. `pagerduty_create_service`, `pagerduty_list_on_calls`, `pagerduty_update_service` `bug-fix` `description-fix` Add missing days_of_week to create_service support_hours. Fix update_service status enum to only settable values (active/disabled). Clarify incident type canonical name vs display_name for get_incident_type and create_incident. Document auth_test 400 with account-level tokens. Clarify delete_team P-prefixed ID and create_schedule rotation vs restriction. `pagerduty_auth_test`, `pagerduty_create_incident`, `pagerduty_create_schedule`, `pagerduty_create_service`, `pagerduty_delete_team`, `pagerduty_get_incident_type`, `pagerduty_update_incident`, `pagerduty_update_service` `guide` Corrected the API Key connection guide to add the login URL, the Developer Portal to dashboard navigation step, the real dialog names and the Read-only API Key checkbox, and shortened the API Key field description. Added portal screenshots to the guide steps. `new-actions` Added unified IAM actions for users, groups, organizations, roles, resource users, and credentials. # Parallel Source: https://docs.stackone.com/connectors/parallel/index How to set up the Parallel connector, plus the actions and events that are available.
Parallel
v1.2.0
29 actions · 11 events · 1 auth method
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Parallel AI account using an API key generated from the Parallel Platform. Optionally, configure receiving Events for Parallel into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/parallel/index.md for the full list. ## Events See https://docs.stackone.com/connectors/parallel/index.md for the full list. # Parallel Changelog Source: https://docs.stackone.com/connectors/parallel/changelog Release history for the Parallel connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added native webhook events for task runs, FindAll runs and monitors (10 events), received by passing the new Native Webhook URL as webhook.url. `data-sync` Added DataSync support to the list_monitors action (cursor pagination, full-refresh sync of all monitors). # Pardot Source: https://docs.stackone.com/connectors/pardot/index How to set up the Pardot connector, plus the actions that are available.
Pardot
Previewv2.0.1
88 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Salesforce External Client App with the \`pardot\_api\`, \`refresh\_token\`, and \`offline\_access\` scopes. Pardot au... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pardot/index.md for the full list. # Pardot Changelog Source: https://docs.stackone.com/connectors/pardot/changelog Release history for the Pardot connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` Connections now use PKCE for Salesforce apps that require it, and always request refresh_token so a custom scope list cannot break sign-in. `pardot_add_campaign_tag`, `pardot_add_dynamic_content_tag`, `pardot_add_file_tag`, `pardot_add_landing_page_tag`, `pardot_add_prospect_tag`, `pardot_add_user_tag`, `pardot_connect_salesforce_campaign`, `pardot_create_custom_field`, `pardot_create_custom_redirect`, `pardot_create_dynamic_content`, `pardot_create_file`, `pardot_create_form`, `pardot_create_landing_page`, `pardot_create_list`, `pardot_create_list_membership`, `pardot_create_prospect`, `pardot_create_tag`, `pardot_delete_custom_field`, `pardot_delete_custom_redirect`, `pardot_delete_file`, `pardot_delete_form`, `pardot_delete_list`, `pardot_delete_list_membership`, `pardot_delete_prospect`, `pardot_delete_tag`, `pardot_download_engagement_program_structure`, `pardot_get_account`, `pardot_get_campaign`, `pardot_get_custom_field`, `pardot_get_custom_redirect`, `pardot_get_dynamic_content`, `pardot_get_email`, `pardot_get_email_template`, `pardot_get_engagement_studio_program`, `pardot_get_file`, `pardot_get_folder`, `pardot_get_folder_contents`, `pardot_get_form`, `pardot_get_landing_page`, `pardot_get_list`, `pardot_get_list_email`, `pardot_get_list_email_stats`, `pardot_get_list_membership`, `pardot_get_opportunity`, `pardot_get_prospect`, `pardot_get_tag`, `pardot_get_tagged_object`, `pardot_get_user`, `pardot_get_visitor_activity`, `pardot_list_campaigns`, `pardot_list_custom_fields`, `pardot_list_custom_redirects`, `pardot_list_dynamic_contents`, `pardot_list_email_templates`, `pardot_list_emails`, `pardot_list_engagement_studio_programs`, `pardot_list_files`, `pardot_list_folder_contents`, `pardot_list_folders`, `pardot_list_forms`, `pardot_list_landing_pages`, `pardot_list_list_emails`, `pardot_list_list_memberships`, `pardot_list_lists`, `pardot_list_opportunities`, `pardot_list_prospects`, `pardot_list_tagged_objects`, `pardot_list_tags`, `pardot_list_users`, `pardot_list_visitor_activities`, `pardot_merge_tags`, `pardot_remove_campaign_tag`, `pardot_remove_dynamic_content_tag`, `pardot_remove_file_tag`, `pardot_remove_landing_page_tag`, `pardot_remove_prospect_tag`, `pardot_remove_user_tag`, `pardot_send_list_email`, `pardot_send_one_to_one_email`, `pardot_undelete_prospect`, `pardot_update_custom_field`, `pardot_update_custom_redirect`, `pardot_update_file`, `pardot_update_list`, `pardot_update_list_membership`, `pardot_update_prospect`, `pardot_update_tag`, `pardot_upsert_prospect_by_email` `data-sync` `breaking` `bug-fix` Added scheduled Data Sync to all 21 collection actions, paging through the v5 nextPageToken cursor; fifteen sync incrementally on the updatedAtAfter filter and six refresh in full, because Account Engagement has no updated-since filter on those objects. Removed the deprecated offset parameter from every list action: Salesforce deprecated it, it caps out at 2000 records, and sending it stops the API returning a page token at all. Date filters now accept any ISO-8601 timestamp and normalise it to the UTC offset the v5 API requires. Also fixed List Landing Pages, which failed every call by requesting content and scriptFragment, fields v5 does not allow on a list query. # Paychex Source: https://docs.stackone.com/connectors/paychex/index How to set up the Paychex connector, plus the actions and events that are available.
Paychex
Betav1.1.0
41 actions · 13 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect to Paychex using OAuth 2.0 client credentials. Register an application in the Paychex Developer Portal and reque... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/paychex/index.md for the full list. ## Events See https://docs.stackone.com/connectors/paychex/index.md for the full list. # Paychex Changelog Source: https://docs.stackone.com/connectors/paychex/changelog Release history for the Paychex connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for companies, so their records can be periodically pulled into StackOne and kept up to date. The sync is full-refresh, because the Paychex API exposes no updated-since filter a sync can use. # Paycor Source: https://docs.stackone.com/connectors/paycor/index How to set up the Paycor connector, plus the actions and events that are available.
Paycor
Betav1.1.0
38 actions · 49 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an application in the Paycor Developer Portal. Uses authorization code flow with PKCE. Access is scope... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/paycor/index.md for the full list. ## Events See https://docs.stackone.com/connectors/paycor/index.md for the full list. # Paycor Changelog Source: https://docs.stackone.com/connectors/paycor/changelog Release history for the Paycor connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added datasync support for 14 list actions and defaulted legalEntityId from credentials across 12 actions. `paycor_list_activity_types`, `paycor_list_departments`, `paycor_list_employee_onboarding`, `paycor_list_employees`, `paycor_list_job_titles`, `paycor_list_labor_codes`, `paycor_list_legal_entities`, `paycor_list_legal_entity_deductions`, `paycor_list_legal_entity_earnings`, `paycor_list_pay_groups`, `paycor_list_persons`, `paycor_list_time_off_plans`, `paycor_list_time_off_types`, `paycor_list_work_locations` `bug-fix` Fixed employee and legal entity lists failing on every request. # PayFit Source: https://docs.stackone.com/connectors/payfit/index How to set up the PayFit connector, plus the actions that are available.
PayFit
v1.1.0
23 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an API key that an admin generates in the PayFit dashboard. The scopes selected when the key is created determine w... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/payfit/index.md for the full list. # PayFit Changelog Source: https://docs.stackone.com/connectors/payfit/changelog Release history for the PayFit connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for collaborators, contracts, absences, health insurance contracts, provident fund contracts, income tax documents and auto-enrolment documents, so these collections can be kept in sync and paged through in full rather than fetched one page at a time. `payfit_list_absences`, `payfit_list_auto_enrolment_documents`, `payfit_list_collaborators`, `payfit_list_contracts`, `payfit_list_health_insurance_contracts`, `payfit_list_income_taxes_documents`, `payfit_list_provident_fund_contracts` `bug-fix` `description-fix` Corrected the api-key guide scope list to match the live PayFit portal (mapped every scope to its exact portal group/label, disambiguated time:read from contracts:time-information:read). Fixed MCP agentic-testing bugs — list_absences status now accepts a comma-separated multi-status string (was a single-value enum), create_contract description now tells the agent to retrieve the new contractId via get_collaborator and complete every requested benefit affiliation, and clarified list_collaborators email-only filtering (no name search). `payfit_create_contract`, `payfit_update_health_insurance_affiliation`, `payfit_update_provident_fund_affiliation` `bug-fix` `description-fix` Fixed MCP agentic-testing bugs — list_absences status now accepts comma-separated multi-status (was single-value enum), and clarified create_contract async behavior (no contractId returned, contract appears via list_contracts after 2-5 min) and list_collaborators email-only filtering (no name search). `payfit_create_contract`, `payfit_list_absences`, `payfit_list_collaborators` `guide-changes` Rebuilt the api-key connection guide from the live portal — added portal screenshots, navigation to the API access page, the create-key dialog and scope-selection behaviour, and a corrected scope list, and fixed the API Key field description and its broken link. # Paylocity Source: https://docs.stackone.com/connectors/paylocity/index How to set up the Paylocity connector, plus the actions and events that are available.
Paylocity
v2.1.1
49 actions · 5 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges in your Paylocity account. Optionally, configure receiving Events for Paylocity into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/paylocity/index.md for the full list. ## Events See https://docs.stackone.com/connectors/paylocity/index.md for the full list. # Paylocity Changelog Source: https://docs.stackone.com/connectors/paylocity/changelog Release history for the Paylocity connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `documentation` Moved 5 actions from preview to beta. `data-sync` Added DataSync v2 support to 12 list actions including cursor-based pagination for employees and offset pagination for reference data endpoints. `paylocity_get_company_tax_codes`, `paylocity_get_cost_centers`, `paylocity_get_deduction_codes`, `paylocity_get_earning_codes`, `paylocity_get_pay_frequency_codes`, `paylocity_get_pay_grades`, `paylocity_get_position_codes`, `paylocity_get_rate_codes`, `paylocity_get_workers_compensation_codes`, `paylocity_list_employees`, `paylocity_list_job_codes`, `paylocity_list_work_location_codes` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. `paylocity_create_deduction`, `paylocity_create_employee`, `paylocity_create_employee_earning`, `paylocity_create_job_code`, `paylocity_create_local_tax`, `paylocity_delete_deduction`, `paylocity_delete_employee_earning_by_resourceId`, `paylocity_delete_job_code`, `paylocity_get_company_info`, `paylocity_get_company_shifts`, `paylocity_get_company_tax_codes`, `paylocity_get_cost_centers`, `paylocity_get_custom_fields`, `paylocity_get_deduction_codes`, `paylocity_get_direct_deposit`, `paylocity_get_earning_codes`, `paylocity_get_employee`, `paylocity_get_employee_deduction_by_resourceId`, `paylocity_get_employee_earning_by_resourceId`, `paylocity_get_employee_shifts`, `paylocity_get_employee_with_benefits`, `paylocity_get_job_code`, `paylocity_get_local_taxes`, `paylocity_get_open_shifts`, `paylocity_get_pay_details`, `paylocity_get_pay_frequency_codes`, `paylocity_get_pay_grades`, `paylocity_get_pay_summary`, `paylocity_get_position_codes`, `paylocity_get_rate_codes`, `paylocity_get_sensitive_data`, `paylocity_get_tax_codes`, `paylocity_get_workers_compensation_codes`, `paylocity_list_deductions`, `paylocity_list_employee_deductions_by_code`, `paylocity_list_employee_earnings`, `paylocity_list_employee_earnings_by_code`, `paylocity_list_employees`, `paylocity_list_job_codes`, `paylocity_list_pay_details_by_year_and_checkdate`, `paylocity_list_work_location_codes`, `paylocity_update_benefit_setup`, `paylocity_update_deduction`, `paylocity_update_employee`, `paylocity_update_employee_earning_by_resourceId`, `paylocity_update_job_code`, `paylocity_upsert_emergency_contacts`, `paylocity_upsert_non_primary_state_tax`, `paylocity_upsert_primary_state_tax` `webhook` `new-actions` Added webhook event support for 5 event types (New Hire, Termination, Employee Change, Payroll Processed, Time Off Approval). Sensitive pay data excluded by default from list_employees and get_employee — opt in via the include parameter. # PayPal Source: https://docs.stackone.com/connectors/paypal/index How to set up the PayPal connector, plus the actions and events that are available.
PayPal
v1.3.0
64 actions · 51 events · 1 auth method
Payments IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). PayPal uses OAuth 2.0 Client Credentials for server-to-server API access. You need a PayPal Developer account with a RES... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/paypal/index.md for the full list. ## Events See https://docs.stackone.com/connectors/paypal/index.md for the full list. # PayPal Changelog Source: https://docs.stackone.com/connectors/paypal/changelog Release history for the PayPal connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added unified IAM user lookups for the staff users on a PayPal business account, including each user's account permissions, and a connection identity lookup that shows the app and the scopes PayPal granted it. `paypal_unified_get_me`, `paypal_unified_get_user`, `paypal_unified_list_users` `new-feature` Added Data Sync support for List Products, List Subscription Plans, List Invoices, List Disputes, List Webhooks, and List Balances, so these resources can be synced into StackOne on a schedule and read without calling PayPal. Disputes sync incrementally on updated time, while the others run as a full refresh because PayPal's list endpoints offer no last-updated filter. # Peec AI Source: https://docs.stackone.com/connectors/peecai/index How to set up the Peec AI connector, plus the actions that are available.
Peec AI
Betav0.1.0
36 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Peec AI authenticates every request with an API key sent in the x-api-key header. Keys are created in the Peec AI app an... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/peecai/index.md for the full list. # Peec AI Changelog Source: https://docs.stackone.com/connectors/peecai/changelog Release history for the Peec AI connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial release. 36 actions covering AI-visibility actions, brands, products and shopping analytics, categories, prompts, topics, tags and model channels, with API key authentication and data sync on 15 list actions. # PeopleFluent Source: https://docs.stackone.com/connectors/peoplefluent/index How to set up the PeopleFluent connector, plus the actions that are available.
PeopleFluent
Previewv1.1.0
54 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Access requires administrator privileges within PeopleFluent LMS. HTTP Basic Authentication is used with username and pa... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/peoplefluent/index.md for the full list. # PeopleFluent Changelog Source: https://docs.stackone.com/connectors/peoplefluent/changelog Release history for the PeopleFluent connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for users, direct reports, assignments, competencies, awarded competencies, assigned job profiles, learning paths, articles, reference resources, batch reports, training records, external training records and requests, enrollment and withdrawal requests, supervisor assessments, mailbox messages, and recent activity. The format parameter is now optional on every action that supports JSON and defaults to json when omitted. # PeopleHR Source: https://docs.stackone.com/connectors/peoplehr/index How to set up the PeopleHR connector, plus the actions that are available.
PeopleHR
Betav1.1.0
58 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). PeopleHR uses API key authentication. The API key is passed in the JSON request body of every API call. All endpoints us... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/peoplehr/index.md for the full list. # PeopleHR Changelog Source: https://docs.stackone.com/connectors/peoplehr/changelog Release history for the PeopleHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for List Employees so the full employee directory can be pulled and kept up to date on a schedule, and made its IncludeLeavers input optional to match the PeopleHR API. # Perplexity Source: https://docs.stackone.com/connectors/perplexity/index How to set up the Perplexity connector, plus the actions that are available.
Perplexity
Previewv1.1.1
11 actions · 1 auth method
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Perplexity API key (prefixed pplx-) sent as a Bearer token. There is no OAuth flow and no scopes — the key grants... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/perplexity/index.md for the full list. # Perplexity Changelog Source: https://docs.stackone.com/connectors/perplexity/changelog Release history for the Perplexity connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `description-changes` Clarified the chat completion, web search, agent, and async tool descriptions so integrations pick the right action and build valid arguments. Web search returns links only while chat completion returns written answers (including SEC and academic search modes); the agent action is for multi-step orchestration and for specific openai/anthropic models or fallback chains; async is only for sonar-deep-research. Chat completion's model is limited to the four Sonar values and its messages must be a real array, and heavy deep-research work is routed straight to the async or agent background paths instead of the sync call that can hit the gateway timeout. Agent responses that select an Anthropic model now default max_output_tokens automatically when it is not supplied, since Anthropic models reject the request without it. `perplexity_create_agent_response`, `perplexity_create_async_chat_completion`, `perplexity_create_chat_completion`, `perplexity_retrieve_agent_response`, `perplexity_search_web` `data-sync` Added scheduled data sync to the models and async chat completions list actions so these collections can be kept in sync and read back without calling Perplexity on every request. Async listing now accepts optional limit and next_token cursor params; both actions refresh in full each run, since neither endpoint offers an updated-since filter. `perplexity_list_async_chat_completions`, `perplexity_list_models` `bug-fix` `guide-fix` Fixed connection validation - switched the credential test action to list_async_chat_completions because the previous list_models endpoint is unauthenticated, so invalid API keys were accepted. Corrected the connection guide (API key field description, Buy more credits prerequisite, copy-icon label). # Personio Source: https://docs.stackone.com/connectors/personio/index How to set up the Personio connector, plus the actions and events that are available.
Personio
v1.2.0
54 actions · 21 events · 1 auth method
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Access to Personio API credentials is required. Generate API credentials in Settings > Integrations > API credentials. Optionally, configure receiving Events for Personio into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/personio/index.md for the full list. ## Events See https://docs.stackone.com/connectors/personio/index.md for the full list. # Personio Changelog Source: https://docs.stackone.com/connectors/personio/changelog Release history for the Personio connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added webhook events for 20 Personio events across persons, employments, absence periods, attendance periods, and documents. StackOne creates the Personio webhook subscription automatically when the account connects and removes it on disconnect. `description-fix` Corrected and clarified pagination documentation on the list actions. The limit parameter on list_absence_periods, list_applications, list_attendance_periods, list_jobs and list_persons now states that it caps one page rather than the total, with verified ranges and defaults, and the cursor parameter on those actions plus list_candidates now describes the actual {data, next_cursor} response envelope instead of the incorrect _meta.links.next and _data references. list_document_categories now documents that its records nest fields under attributes, so the category name is addressed as attributes.name. `personio_create_compensation`, `personio_get_absence_period_breakdowns`, `personio_list_absence_periods`, `personio_list_absence_types`, `personio_list_applications`, `personio_list_attendance_periods`, `personio_list_candidates`, `personio_list_compensation_types`, `personio_list_compensations`, `personio_list_cost_centers`, `personio_list_document_categories`, `personio_list_documents`, `personio_list_jobs`, `personio_list_legal_entities`, `personio_list_person_employments`, `personio_list_persons`, `personio_list_project_members`, `personio_list_projects`, `personio_list_workplaces`, `personio_update_document`, `personio_upload_document` `new-feature` Enabled scheduled Data Sync on 16 list actions spanning employees, absences, attendances, compensations, cost centres, workplaces, legal entities, projects, documents and recruiting, so these collections can be searched without calling Personio each time. Employees, absence periods, applications, candidates and jobs sync incrementally; the rest refresh in full. list_cost_centers and list_projects now return {data, next_cursor} instead of the raw response body and are marked preview. # Phenom Source: https://docs.stackone.com/connectors/phenom/index How to set up the Phenom connector, plus the actions that are available.
Phenom
Betav1.1.0
87 actions · 1 auth method
ATS HRIS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires OAuth2 client credentials provisioned by Phenom. Contact api-management@phenom.com to request API access and ob... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/phenom/index.md for the full list. # Phenom Changelog Source: https://docs.stackone.com/connectors/phenom/changelog Release history for the Phenom connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to four collection actions — applications, SCIM users, SCIM groups and SCIM roles — so these collections can be kept in sync and searched without calling Phenom on every request. Applications page through results automatically; the remaining collections are returned in full by a single request. All syncs use full refreshes because Phenom offers no last-updated filter. # Pinecone Source: https://docs.stackone.com/connectors/pinecone/index How to set up the Pinecone connector, plus the actions that are available.
Pinecone
Betav0.1.0
35 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The Pinecone Admin API authenticates with a service account access token. A service account is created in the Pinecone c... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pinecone/index.md for the full list. # Pinecone Changelog Source: https://docs.stackone.com/connectors/pinecone/changelog Release history for the Pinecone connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial release covering the Pinecone Admin API — projects, organizations, API keys, users, invites, service accounts, role bindings and cost usage exports. # PingOne Source: https://docs.stackone.com/connectors/pingone/index How to set up the PingOne connector, plus the actions and events that are available.
PingOne
Previewv1.4.0
124 actions · 42 events · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Delegated admin access using OAuth 2.0 Authorization Code. An administrator signs in to PingOne, and the connector acts... Optionally, configure receiving Events for PingOne into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pingone/index.md for the full list. ## Events See https://docs.stackone.com/connectors/pingone/index.md for the full list. # PingOne Changelog Source: https://docs.stackone.com/connectors/pingone/changelog Release history for the PingOne connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added PingOne webhook events. `bug-fix` Cached the role catalog lookup for expanded user lists across pages instead of re-fetching it on every page, cutting one PingOne request per page after the first. `pingone_unified_list_users` `new-feature` User lists can now include each user's roles and groups when expanded, role lists and lookups include custom admin roles, and roles assigned to a population are labelled as population roles. When PingOne cannot return a user's or group's roles or groups, the request now fails, or leaves the field out if access is denied, instead of showing an empty list. `pingone_unified_get_group`, `pingone_unified_get_me`, `pingone_unified_get_role`, `pingone_unified_get_user`, `pingone_unified_list_roles`, `pingone_unified_list_users` `data-sync` Added DataSync support for users, groups, populations, applications, certificates, identity providers, roles, and policies. Added page-limit and cursor inputs to the applications, certificates, and identity-provider lists, and an updated-after filter to the user list. `pingone_list_applications`, `pingone_list_certificates`, `pingone_list_custom_roles`, `pingone_list_device_auth_policies`, `pingone_list_groups`, `pingone_list_identity_providers`, `pingone_list_password_policies`, `pingone_list_populations`, `pingone_list_sign_on_policies`, `pingone_list_system_roles`, `pingone_list_users`, `pingone_unified_list_groups`, `pingone_unified_list_organizations`, `pingone_unified_list_roles`, `pingone_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `pingone_unified_get_group`, `pingone_unified_get_me`, `pingone_unified_get_organization`, `pingone_unified_get_role`, `pingone_unified_get_user`, `pingone_unified_list_groups`, `pingone_unified_list_organizations`, `pingone_unified_list_resource_types`, `pingone_unified_list_resource_users`, `pingone_unified_list_roles`, `pingone_unified_list_users` `new-actions` Added unified IAM actions for users, groups, roles, organizations, credentials, and resource users. List Unified Users, List Unified Groups, and List Unified Resource Users page through PingOne's cursor-based pagination, so results beyond the first page are returned. # Pinpoint Source: https://docs.stackone.com/connectors/pinpoint/index How to set up the Pinpoint connector, plus the actions that are available.
Pinpoint
v1.1.0
91 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). You need API access enabled in your Pinpoint account to generate an API key. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pinpoint/index.md for the full list. # Pinpoint Changelog Source: https://docs.stackone.com/connectors/pinpoint/changelog Release history for the Pinpoint connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added Data Sync support to all 25 list actions, covering jobs, candidates, applications, interviews, users and every other collection, so their records can be pulled into StackOne on a schedule and read back without calling Pinpoint each time. Twenty-two of them sync incrementally using Pinpoint's updated-since filter; users, custom fields and structure links refresh in full, because those endpoints offer no such filter. # Pipedrive Source: https://docs.stackone.com/connectors/pipedrive/index How to set up the Pipedrive connector, plus the actions and events that are available.
Pipedrive
v1.3.1
132 actions · 11 events · 2 auth methods
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an app in the Pipedrive Developer Hub. Best for personal scripts and single-account integrations. Quick to set up, no app registration needed. Optionally, configure receiving Events for Pipedrive into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pipedrive/index.md for the full list. ## Events See https://docs.stackone.com/connectors/pipedrive/index.md for the full list. # Pipedrive Changelog Source: https://docs.stackone.com/connectors/pipedrive/changelog Release history for the Pipedrive connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed unified resource user listing failing when a role assignment belongs to a user who was removed from the account. `pipedrive_unified_list_resource_users` `new-feature` `data-sync` Added DataSync support to 25 list actions, with incremental sync where Pipedrive exposes an updated-since filter. `pipedrive_get_goals`, `pipedrive_list_activities`, `pipedrive_list_activity_types`, `pipedrive_list_deal_fields`, `pipedrive_list_deals`, `pipedrive_list_files`, `pipedrive_list_filters`, `pipedrive_list_lead_labels`, `pipedrive_list_lead_sources`, `pipedrive_list_leads`, `pipedrive_list_notes`, `pipedrive_list_organization_fields`, `pipedrive_list_organizations`, `pipedrive_list_permission_sets`, `pipedrive_list_person_fields`, `pipedrive_list_persons`, `pipedrive_list_pipelines`, `pipedrive_list_product_fields`, `pipedrive_list_products`, `pipedrive_list_stages`, `pipedrive_list_users`, `pipedrive_unified_list_groups`, `pipedrive_unified_list_organizations`, `pipedrive_unified_list_roles`, `pipedrive_unified_list_users` `bug-fix` Documented the required request-body structures for creating goals, filters, activity attendees and leads, and the pipeline precondition for setting deal probability. `pipedrive_add_activity`, `pipedrive_add_filter`, `pipedrive_add_goal`, `pipedrive_add_lead`, `pipedrive_list_organizations`, `pipedrive_update_activity`, `pipedrive_update_deal`, `pipedrive_update_filter` `webhook-events` `improve-guide` Added webhook events for deals, leads, persons, organizations, activities, notes, pipelines, stages, products, projects, and users, with automatic subscription setup on account connection. Also refreshed the OAuth and API-token connection guides. `pipedrive_create_webhook` `new-actions` Added unified IAM actions for users, groups, roles, organizations, resource users, and credentials. All 11 IAM actions are gated to releaseStage preview pending live QA. # Pipeliner CRM Source: https://docs.stackone.com/connectors/pipeliner_crm/index How to set up the Pipeliner CRM connector, plus the actions and events that are available.
Pipeliner CRM
v1.2.1
59 actions · 112 events · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API application credentials with Basic authentication. Requires Business or Enterprise plan with Administrator access. Optionally, configure receiving Events for Pipeliner CRM into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pipeliner_crm/index.md for the full list. ## Events See https://docs.stackone.com/connectors/pipeliner_crm/index.md for the full list. # Pipeliner CRM Changelog Source: https://docs.stackone.com/connectors/pipeliner_crm/changelog Release history for the Pipeliner CRM connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Webhook deliveries are now matched to the connected account through its own webhook URL instead of the Pipeliner space id in the payload. `new-events` Added 111 webhook events covering every Pipeliner record type, including accounts, contacts, leads, opportunities, quotes, projects, custom entities, products, price lists, currencies and activities. StackOne creates and removes the Pipeliner webhook subscription automatically when an account connects. `bug-fix` `guide` `description-fix` Every list action can now search server-side on any field, including finding records where a field is empty, so a named record is found in one call instead of paging the whole collection. Notes attach to a contact, lead, opportunity, project, quote or custom record instead of only an account, and lead, task, contact and opportunity fields state the values Pipeliner actually accepts. The Basic Auth connection guide has been rebuilt from current Coevera screens, with realistic credential examples and the regional Service URL issued by the API Access dialog. `pipeliner_crm_create_account`, `pipeliner_crm_create_appointment`, `pipeliner_crm_create_contact`, `pipeliner_crm_create_lead`, `pipeliner_crm_create_note`, `pipeliner_crm_create_opportunity`, `pipeliner_crm_create_task`, `pipeliner_crm_get_account`, `pipeliner_crm_get_appointment`, `pipeliner_crm_get_contact`, `pipeliner_crm_get_lead`, `pipeliner_crm_get_note`, `pipeliner_crm_get_opportunity`, `pipeliner_crm_get_oppty_product_relation`, `pipeliner_crm_get_product`, `pipeliner_crm_get_task`, `pipeliner_crm_list_account_types`, `pipeliner_crm_list_accounts`, `pipeliner_crm_list_appointments`, `pipeliner_crm_list_clients`, `pipeliner_crm_list_contacts`, `pipeliner_crm_list_currencies`, `pipeliner_crm_list_leads`, `pipeliner_crm_list_notes`, `pipeliner_crm_list_opportunities`, `pipeliner_crm_list_oppty_product_relations`, `pipeliner_crm_list_pipelines`, `pipeliner_crm_list_products`, `pipeliner_crm_list_sales_units`, `pipeliner_crm_list_steps`, `pipeliner_crm_list_tags`, `pipeliner_crm_list_tasks`, `pipeliner_crm_update_account`, `pipeliner_crm_update_appointment`, `pipeliner_crm_update_contact`, `pipeliner_crm_update_lead`, `pipeliner_crm_update_note`, `pipeliner_crm_update_opportunity`, `pipeliner_crm_update_task` `guide` `description-fix` Updated the Basic Auth connection guide with current Coevera (Pipeliner CRM) screens for creating an API application and copying its credentials. Listed every record type the connection test reads under Records permissions, replaced the templated credential placeholders with realistic examples, and corrected the Service URL example to the regional Coevera host issued by the API Access dialog. `data-sync` Added DataSync support to all 16 list actions, enabling scheduled full and incremental record syncs. # Plaid Source: https://docs.stackone.com/connectors/plaid/index How to set up the Plaid connector, plus the actions that are available.
Plaid
Previewv2.0.1
59 actions · 2 auth methods
Payments
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Sandbox-only auto-mint flow. StackOne calls /sandbox/public\_token/create and /item/public\_token/exchange behind the scen... Production auth flow. Run Plaid Link in your own app to authenticate the end user with their bank, capture the resulting... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/plaid/index.md for the full list. # Plaid Changelog Source: https://docs.stackone.com/connectors/plaid/changelog Release history for the Plaid connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide-changes` Clarified in the setup guide that the Plaid Link redirect URI is a page in your own application, not a StackOne callback URL, and documented which platforms actually require one. # Planday Source: https://docs.stackone.com/connectors/planday/index How to set up the Planday connector, plus the actions that are available.
Planday
Previewv3.1.1
77 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an API app in your Planday portal. Planday apps issue only an Application ID (the OAuth client ID) and... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/planday/index.md for the full list. # Planday Changelog Source: https://docs.stackone.com/connectors/planday/changelog Release history for the Planday connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Bank account, birth date and social security number fields can now be read and written, because the default connection scopes request Planday's matching permissions. Clarified the descriptions of employee listing, employee creation, deactivation, employee groups and position deletion. `planday_approve_absence_request`, `planday_approve_shift`, `planday_assign_shift`, `planday_change_employee_username`, `planday_create_absence_adjustment`, `planday_create_accrued_account_type`, `planday_create_department`, `planday_create_employee`, `planday_create_employee_group`, `planday_create_or_update_employee_period_salary`, `planday_create_or_update_revenue`, `planday_create_position`, `planday_create_shift`, `planday_create_shift_type`, `planday_create_skill`, `planday_create_transaction`, `planday_deactivate_employee`, `planday_decline_absence_record`, `planday_delete_account_type`, `planday_delete_department`, `planday_delete_employee_group`, `planday_delete_position`, `planday_delete_revenue`, `planday_delete_shift`, `planday_delete_skill`, `planday_deny_absence_request`, `planday_get_absence_records`, `planday_get_absence_request_draft`, `planday_get_account_balance`, `planday_get_accrued_account_type`, `planday_get_department`, `planday_get_employee`, `planday_get_employee_field_definition`, `planday_get_employee_group`, `planday_get_employee_group_employee_payrates`, `planday_get_employee_payrates_all_groups`, `planday_get_employee_period_salary`, `planday_get_employee_salary_allocation`, `planday_get_position`, `planday_get_shift`, `planday_invite_employee`, `planday_list_absence_accounts`, `planday_list_absence_adjustments`, `planday_list_absence_requests`, `planday_list_absence_types`, `planday_list_account_transactions`, `planday_list_account_types`, `planday_list_deactivated_employees`, `planday_list_department_revenue_units`, `planday_list_departments`, `planday_list_employee_account_balances`, `planday_list_employee_groups`, `planday_list_employee_shifts_today`, `planday_list_employee_types`, `planday_list_employees`, `planday_list_payroll`, `planday_list_positions`, `planday_list_punchclock_shifts`, `planday_list_revenue`, `planday_list_revenue_units`, `planday_list_salary_types`, `planday_list_shift_types`, `planday_list_shifts`, `planday_list_skills`, `planday_list_supervisors`, `planday_publish_draft_shifts`, `planday_reactivate_employee`, `planday_submit_absence_request`, `planday_update_accrued_account_type`, `planday_update_department`, `planday_update_employee`, `planday_update_employee_group`, `planday_update_employee_group_payrates`, `planday_update_position`, `planday_update_shift`, `planday_update_shift_type`, `planday_update_skill` `data-sync` Added data sync support for absence accounts, absence records, absence requests, absence types, account types, deactivated employees, departments, employee groups, employee types, employees, positions, revenue, revenue units, salary types, shift types, shifts, skills, supervisors and today's employee shifts, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. Employees, deactivated employees and shifts sync incrementally using Planday's updated-since filters; the rest are full-refresh, because their endpoints expose no updated-since filter a sync can use. `planday_get_absence_records`, `planday_list_absence_accounts`, `planday_list_absence_requests`, `planday_list_absence_types`, `planday_list_account_types`, `planday_list_deactivated_employees`, `planday_list_departments`, `planday_list_employee_groups`, `planday_list_employee_shifts_today`, `planday_list_employee_types`, `planday_list_employees`, `planday_list_positions`, `planday_list_revenue`, `planday_list_revenue_units`, `planday_list_salary_types`, `planday_list_shift_types`, `planday_list_shifts`, `planday_list_skills`, `planday_list_supervisors` `guide` Clarified the OAuth 2.0 connection guide and profile field. The Planday Application ID is your Client ID, and Planday apps do not use a Client Secret. `breaking` `new-actions` `bug-fix` Write actions now confirm what they changed instead of returning an empty response, and seven actions return their payload without an extra nesting level. Adds revenue unit lookups, all-employee absence balances in one call, and draft shift publishing. `planday_list_department_revenue_units`, `planday_list_employee_account_balances`, `planday_list_revenue_units`, `planday_publish_draft_shifts` `planday_approve_absence_request`, `planday_approve_shift`, `planday_assign_shift`, `planday_change_employee_username`, `planday_create_accrued_account_type`, `planday_create_employee`, `planday_create_or_update_revenue`, `planday_create_position`, `planday_create_shift`, `planday_create_shift_type`, `planday_create_skill`, `planday_create_transaction`, `planday_deactivate_employee`, `planday_decline_absence_record`, `planday_delete_account_type`, `planday_delete_department`, `planday_delete_employee_group`, `planday_delete_position`, `planday_delete_revenue`, `planday_delete_shift`, `planday_delete_skill`, `planday_deny_absence_request`, `planday_get_account_balance`, `planday_get_accrued_account_type`, `planday_get_department`, `planday_get_employee`, `planday_get_shift`, `planday_invite_employee`, `planday_list_deactivated_employees`, `planday_list_employee_shifts_today`, `planday_list_employees`, `planday_list_revenue`, `planday_reactivate_employee`, `planday_submit_absence_request`, `planday_update_accrued_account_type`, `planday_update_department`, `planday_update_employee`, `planday_update_employee_group`, `planday_update_employee_group_payrates`, `planday_update_position`, `planday_update_shift`, `planday_update_shift_type`, `planday_update_skill` `breaking` `guide` `bug-fix` Rewrote the OAuth 2.0 connection guide from a walkthrough of the live Planday portal, adding screenshots for every step. It now links the Planday login and sign-up pages directly, spells out that API access sits at the bottom of the Settings sidebar (not behind the Integrations card), lists the exact resource and permission boxes to tick in the Scopes grid, and explains that Planday's Application ID is the OAuth client ID. The Token Secret field was removed: Planday issues no client secret, its token endpoint authenticates on client_id alone, and the value was never validated. # Polymer Source: https://docs.stackone.com/connectors/polymer/index How to set up the Polymer connector, plus the actions and events that are available.
Polymer
v1.2.0
27 actions · 2 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Polymer Hire uses a static API key sent as a Bearer token. An admin generates it from the Polymer Hire settings page. Optionally, configure receiving Events for Polymer into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/polymer/index.md for the full list. ## Events See https://docs.stackone.com/connectors/polymer/index.md for the full list. # Polymer Changelog Source: https://docs.stackone.com/connectors/polymer/changelog Release history for the Polymer connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Added DataSync support to five list actions: candidates, jobs, job applications, active users, and deactivated users. Candidates, jobs and job applications sync incrementally using the provider's updated_since filter; the two organization-user actions full-refresh on every run. `polymer_list_active_users`, `polymer_list_candidates`, `polymer_list_deactivated_users`, `polymer_list_job_applications`, `polymer_list_jobs` `webhook` Added real-time webhook events for new job applications and newly published jobs, with a step-by-step guide for configuring the webhook in Polymer. # PostHog Source: https://docs.stackone.com/connectors/posthog/index How to set up the PostHog connector, plus the actions and events that are available.
PostHog
v6.0.0
100 actions · 10 events · 1 auth method
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Admin access required to generate personal API keys Optionally, configure receiving Events for PostHog into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/posthog/index.md for the full list. ## Events See https://docs.stackone.com/connectors/posthog/index.md for the full list. # PostHog Changelog Source: https://docs.stackone.com/connectors/posthog/changelog Release history for the PostHog connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `bug-fix` `breaking-changes` Added HogQL query, data warehouse, event and property definition, and insight variable actions. Event definition name, tag and sort filters now take the formats PostHog actually accepts, and parameters the API rejects for customer accounts have been removed. `posthog_cancel_query`, `posthog_create_insight_variable`, `posthog_create_warehouse_saved_query`, `posthog_create_warehouse_table`, `posthog_create_warehouse_view_link`, `posthog_delete_insight_variable`, `posthog_delete_warehouse_saved_query`, `posthog_delete_warehouse_table`, `posthog_delete_warehouse_view_link`, `posthog_get_event_definition`, `posthog_get_insight_variable`, `posthog_get_project`, `posthog_get_property_definition`, `posthog_get_query_status`, `posthog_get_warehouse_saved_query`, `posthog_get_warehouse_table`, `posthog_get_warehouse_view_link`, `posthog_list_event_definitions`, `posthog_list_insight_variables`, `posthog_list_property_definitions`, `posthog_list_warehouse_saved_queries`, `posthog_list_warehouse_tables`, `posthog_list_warehouse_view_links`, `posthog_run_query`, `posthog_update_insight_variable`, `posthog_update_warehouse_saved_query`, `posthog_update_warehouse_table` `webhook` `new-actions` Added webhook events for page views, user and group identification, feature flag evaluations, errors, and your own custom events. StackOne sets up and removes the PostHog destination automatically when an account is connected. `posthog_change_project_organization`, `posthog_complete_product_onboarding`, `posthog_create_groups_type_metric`, `posthog_create_project`, `posthog_delete_groups_type`, `posthog_delete_groups_type_metric`, `posthog_delete_project`, `posthog_delete_user`, `posthog_get_groups_type_metric`, `posthog_get_session_recording`, `posthog_get_user`, `posthog_list_activity_log`, `posthog_list_groups_type_metrics`, `posthog_update_groups_type_metric`, `posthog_update_groups_types_metadata`, `posthog_update_user` `data-sync` Added DataSync support to list_organizations, list_projects, list_users, unified_list_users, and unified_list_organizations for periodic data synchronisation. `posthog_list_organizations`, `posthog_list_projects`, `posthog_list_users`, `posthog_unified_list_organizations`, `posthog_unified_list_users` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. `posthog_change_project_organization`, `posthog_complete_product_onboarding`, `posthog_create_action`, `posthog_create_dashboard`, `posthog_create_feature_flag`, `posthog_create_groups_type_metric`, `posthog_create_insight`, `posthog_create_organization`, `posthog_create_project`, `posthog_create_role`, `posthog_create_role_membership`, `posthog_delete_action`, `posthog_delete_groups_type`, `posthog_delete_groups_type_metric`, `posthog_delete_insight`, `posthog_delete_member`, `posthog_delete_organization`, `posthog_delete_project`, `posthog_delete_role`, `posthog_delete_role_membership`, `posthog_delete_session_recording`, `posthog_delete_user`, `posthog_get_action`, `posthog_get_dashboard`, `posthog_get_feature_flag`, `posthog_get_groups_type_metric`, `posthog_get_insight`, `posthog_get_organization`, `posthog_get_organization_project`, `posthog_get_role`, `posthog_get_role_membership`, `posthog_get_session_recording`, `posthog_get_user`, `posthog_list_actions`, `posthog_list_activity_log`, `posthog_list_alerts`, `posthog_list_dashboards`, `posthog_list_feature_flags`, `posthog_list_groups_type_metrics`, `posthog_list_groups_types`, `posthog_list_insights`, `posthog_list_members`, `posthog_list_organization_integrations`, `posthog_list_organization_projects`, `posthog_list_organizations`, `posthog_list_role_memberships`, `posthog_list_roles`, `posthog_list_session_recordings`, `posthog_list_users`, `posthog_unified_get_organization`, `posthog_unified_get_user`, `posthog_unified_list_organizations`, `posthog_unified_list_resource_users`, `posthog_unified_list_users`, `posthog_update_action`, `posthog_update_dashboard`, `posthog_update_feature_flag`, `posthog_update_groups_type_metric`, `posthog_update_groups_types_metadata`, `posthog_update_insight`, `posthog_update_member`, `posthog_update_organization`, `posthog_update_project`, `posthog_update_role`, `posthog_update_session_recording`, `posthog_update_user` `bug-fix` Fixed user lookups by ID returning an empty result instead of a not-found error, and widened the lookup to scan up to 3000 organization members instead of only the first 1000. `posthog_unified_get_me`, `posthog_unified_get_user`, `posthog_unified_list_organizations`, `posthog_unified_list_resource_users`, `posthog_unified_list_roles`, `posthog_unified_list_users` `bug-fix` Fixed unified_list_users and unified_get_user returning only the requesting API key's own account instead of the organization roster. `posthog_unified_get_user`, `posthog_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, resource users, and credentials. # Postmark Source: https://docs.stackone.com/connectors/postmark/index How to set up the Postmark connector, plus the actions and events that are available.
Postmark
v1.1.4
76 actions · 7 events · 1 auth method
Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses Server API Token for server-level operations (email, templates, bounces, webhooks) and optionally an Account API To... Optionally, configure receiving Events for Postmark into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/postmark/index.md for the full list. ## Events See https://docs.stackone.com/connectors/postmark/index.md for the full list. # Postmark Changelog Source: https://docs.stackone.com/connectors/postmark/changelog Release history for the Postmark connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` `webhook` `bug-fix` Added a webhook setup guide for Postmark events and corrected the event identifiers so they are no longer reported as empty or duplicated. `postmark_bypass_rules_for_blocked_inbound_message`, `postmark_inbound_message_details`, `postmark_opens_for_single_message`, `postmark_retry_failed_inbound_message_for_processing` `guide` Fixed the connection guide screenshots so they load correctly for every step. `guides` Improved connection guide with step-by-step screenshots, clearer navigation instructions, and updated field descriptions. `action-descriptions` Improved action descriptions for better tool selection and added releaseStage preview to delete_a_server. `postmark_delete_a_server`, `postmark_get_delivery_stats`, `postmark_get_outbound_overview`, `postmark_send_email_with_template` `data-sync` Added DataSync support for list_webhooks and list_message_streams actions. # PrismHR Source: https://docs.stackone.com/connectors/prismhr/index How to set up the PrismHR connector, plus the actions that are available.
PrismHR
Betav1.1.0
30 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Session-based token authentication using PrismHR Web Service User credentials. Provide your Web Service User ID, passwor... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/prismhr/index.md for the full list. # PrismHR Changelog Source: https://docs.stackone.com/connectors/prismhr/changelog Release history for the PrismHR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data synchronisation support to 14 list actions across employees, companies, locations, benefits, time off, payroll, and system resources. # Prismic Source: https://docs.stackone.com/connectors/prismic/index How to set up the Prismic connector, plus the actions and events that are available.
Prismic
v1.2.0
24 actions · 7 events · 1 auth method
CMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a permanent write token for full API access. Generate in API & Security (Write APIs tab). Token does not expire unl... Optionally, configure receiving Events for Prismic into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/prismic/index.md for the full list. ## Events See https://docs.stackone.com/connectors/prismic/index.md for the full list. # Prismic Changelog Source: https://docs.stackone.com/connectors/prismic/changelog Release history for the Prismic connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Webhook events can now be received from Prismic, covering document publishing, releases being created, edited or deleted, and tags being created or deleted, with a setup guide for adding the webhook in the Prismic dashboard. `data-sync` Added DataSync support to four list actions (assets, asset tags, custom types, and shared slices), with cursor pagination on assets. All four sync via full refresh as the Prismic APIs provide no updated-since filtering. # Privacy.com Source: https://docs.stackone.com/connectors/privacy/index How to set up the Privacy.com connector, plus the actions that are available.
Privacy.com
Betav0.2.1
8 actions · 1 auth method
Payments
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a paid Privacy.com plan (Plus, Pro, or Premium) to generate an API key. The key is unscoped and inherits full a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/privacy/index.md for the full list. # Privacy.com Changelog Source: https://docs.stackone.com/connectors/privacy/changelog Release history for the Privacy.com connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the API Key documentation link with a full connection guide covering generating the secret key from your Privacy account page. `data-sync` `new-feature` Added data sync support for cards, transactions, and funding sources, so their records can be periodically pulled into StackOne and kept up to date. Syncs are full-refresh — the Privacy API filters only on creation date, which would miss later status changes. `privacy_list_cards`, `privacy_list_funding_sources`, `privacy_list_transactions` `bug-fix` Standardized action category capitalization for more consistent portal filters. `privacy_create_card`, `privacy_get_api_status`, `privacy_get_card`, `privacy_list_cards`, `privacy_list_funding_sources`, `privacy_list_transactions`, `privacy_share_card`, `privacy_update_card` `new-connector` Initial preview release of the Privacy.com connector — virtual card issuing and management (list, get, create, update, share), linked bank funding sources, and card transaction history. # Procurify Source: https://docs.stackone.com/connectors/procurify/index How to set up the Procurify connector, plus the actions that are available.
Procurify
Betav0.2.0
52 actions · 1 auth method
Accounting Procurement Payments IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Machine-to-machine access using OAuth 2.0 client credentials. Requires creating an API application under Settings > Inte... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/procurify/index.md for the full list. # Procurify Changelog Source: https://docs.stackone.com/connectors/procurify/changelog Release history for the Procurify connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for 23 collection actions - users, vendors, departments, locations, account codes, budgets, catalog items and bundles, orders and order items, bills and bill items, payments, pay transactions, payment methods, permissions, permission groups, currencies, custom fields, receipt items, and PO billing history. Payments sync incrementally on updated_at_after and AP bills on last_modified_datetime_0; the remaining 21 full-refresh on each run. No action's request behaviour, inputs, or result shape changed. `procurify_account_codes_list`, `procurify_accounts_list`, `procurify_ap_bills_list`, `procurify_ap_company_payment_methods_list`, `procurify_ap_items_list`, `procurify_ap_vendor_payment_methods_list`, `procurify_catalog_bundles_list`, `procurify_catalog_items_list`, `procurify_currencies_list`, `procurify_custom_fields_order_items_list`, `procurify_departments_list`, `procurify_global_order_items_list`, `procurify_global_orders_list`, `procurify_locations_list`, `procurify_order_items_list`, `procurify_permissions_groups_list`, `procurify_permissions_list`, `procurify_public_v1_pay_transactions_list`, `procurify_public_v1_payments_list`, `procurify_purchase_orders_billing_history_retrieve`, `procurify_receipt_items_list`, `procurify_users_list`, `procurify_vendors_list` `new-connector` Initial release. 52 actions across the procure-to-pay lifecycle — requisitions, purchase orders, receiving, accounts payable, payments, vendors, catalog, budgets, and account codes. OAuth 2.0 (client credentials) authentication. # Proliant Source: https://docs.stackone.com/connectors/proliant/index How to set up the Proliant connector, plus the actions that are available.
Proliant
Betav1.1.0
88 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connects using Proliant's Client Credentials flow. Requires a Client Key and Client Secret issued by your Proliant Accou... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/proliant/index.md for the full list. # Proliant Changelog Source: https://docs.stackone.com/connectors/proliant/changelog Release history for the Proliant connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 22 list actions covering employees, companies, accrual, deduction, job and shift codes, cost centers, local taxes, and lookup code lists. Employees sync incrementally via a new optional lastChangeDateStart filter, and the three employee list actions gain optional pageSize and pageNumber inputs; the other actions sync by full refresh. # PubMed Source: https://docs.stackone.com/connectors/pubmed/index How to set up the PubMed connector, plus the actions that are available.
PubMed
v1.0.0
9 actions · 2 auth methods
Healthcare
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No authentication required. Anonymous access is limited to 3 requests/second per IP. Optional NCBI API key that raises the rate limit to 10 requests/second. Create one from your NCBI account settings page. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pubmed/index.md for the full list. # PubMed Changelog Source: https://docs.stackone.com/connectors/pubmed/changelog Release history for the PubMed connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` General release. `description-fix` Removed the NCBI account settings URL from the API Key authentication description — the documentation card's character limit truncated it into a broken 404 link; the full link remains in the setup guide. `description-fix` Clarified the Get Article Summaries and Get Articles descriptions so it is clear that summaries return bibliographic metadata only while full records include the abstract and complete data. `pubmed_get_article_summaries`, `pubmed_get_articles` `guide-changes` Fixed the NCBI API key setup guide — corrected the broken account-settings link, updated the Account settings navigation to the profile dropdown (with a matching screenshot), covered copying an existing key, and removed the duplicate No Authentication setup guide. `new-connector` Initial PubMed (NCBI E-utilities) connector with 9 actions across articles, related, citations, search, history, and databases — optional API key auth, JSON/XML output, and esearch error refinement. # Pydantic Logfire Source: https://docs.stackone.com/connectors/logfire/index How to set up the Pydantic Logfire connector, plus the actions that are available.
Pydantic Logfire
Previewv3.0.0
50 actions · 2 auth methods
Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Organization-wide key covering projects, alerts, dashboards, variables, notification channels, schedules, invitations an... Scoped to a single project. Required for querying telemetry (logs, traces, exceptions, metrics) and for variable types,... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/logfire/index.md for the full list. # Pydantic Logfire Changelog Source: https://docs.stackone.com/connectors/logfire/changelog Release history for the Pydantic Logfire connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `auth` `breaking` `guide` Added telemetry querying — search logs, traces and exceptions, list reporting services, inspect the queryable schema, or run SQL — plus alert schedules and project write-token management. Authentication is now split into two connection types: an Organization API Key for projects, alerts, dashboards, variables, channels and organization settings, and a Project API Key for querying telemetry and variable types. Existing connections must be re-created against the key type they hold. `logfire_create_project_write_token`, `logfire_create_schedule`, `logfire_delete_project_write_token`, `logfire_delete_schedule`, `logfire_expire_project_write_token`, `logfire_get_read_token_info`, `logfire_get_schedule`, `logfire_get_schemas`, `logfire_get_trace`, `logfire_list_exceptions`, `logfire_list_project_write_tokens`, `logfire_list_services`, `logfire_query_records`, `logfire_rotate_project_write_token`, `logfire_search_records`, `logfire_update_schedule` `logfire_create_alert`, `logfire_create_channel`, `logfire_create_dashboard`, `logfire_create_instance_organization`, `logfire_create_organization_invitation`, `logfire_create_project`, `logfire_create_variable`, `logfire_create_variable_type`, `logfire_delete_alert`, `logfire_delete_channel`, `logfire_delete_current_organization`, `logfire_delete_dashboard`, `logfire_delete_project`, `logfire_get_alert`, `logfire_get_channel`, `logfire_get_current_organization`, `logfire_get_dashboard`, `logfire_get_project_info`, `logfire_get_variable_by_name`, `logfire_get_variable_type_by_name`, `logfire_get_variables_config`, `logfire_list_alerts`, `logfire_list_channels`, `logfire_list_dashboards`, `logfire_list_instance_organizations`, `logfire_list_organization_invitations`, `logfire_list_projects`, `logfire_list_variable_types`, `logfire_update_alert`, `logfire_update_channel`, `logfire_update_current_organization`, `logfire_update_dashboard`, `logfire_update_project`, `logfire_update_variable` `data-sync` `new-feature` Added scheduled data sync for projects, notification channels, organization invitations and variable types, so these collections can be kept up to date and read back without calling Logfire on every request. All four refresh in full on each run, because the API offers no updated-since filter on any of them. `logfire_list_channels`, `logfire_list_instance_organizations`, `logfire_list_organization_invitations`, `logfire_list_projects`, `logfire_list_variable_types` `breaking` `new-actions` `auth` `guide` Added variable-type and organization-invitation actions, plus an optional Project API Key for the variable-type actions. Removed the alert channel schedule field, which Logfire gives customers no way to create. `logfire_create_variable_type`, `logfire_get_variable_type_by_name`, `logfire_list_organization_invitations`, `logfire_list_variable_types` `logfire_create_alert`, `logfire_create_channel`, `logfire_create_dashboard`, `logfire_create_organization_invitation`, `logfire_create_variable`, `logfire_delete_current_organization`, `logfire_get_dashboard`, `logfire_list_alerts`, `logfire_list_channels`, `logfire_list_dashboards`, `logfire_list_projects`, `logfire_update_alert`, `logfire_update_channel`, `logfire_update_current_organization`, `logfire_update_dashboard`, `logfire_update_project`, `logfire_update_variable` `new-actions` `new-params` `description-fix` `guide-changes` - Replaced the deprecated /v1/organizations/ actions with their current equivalents (/v1/organization/, /v1/instance/organizations/, /v1/invitations/) and updated scopes accordingly. - Added missing body params from the API spec — environments (create/update alert) and template_inputs_schema (create/update variable). - Added spec constraints — project_name and description length/pattern rules, type_id uuid format, and made variable overrides required. - Clarified alert time_window/frequency/watermark as ISO 8601 durations and added format:uuid rules to all UUID path params. `logfire_create_instance_organization`, `logfire_create_organization_invitation`, `logfire_delete_current_organization`, `logfire_get_current_organization`, `logfire_list_instance_organizations`, `logfire_update_current_organization` `logfire_create_organization`, `logfire_create_self_hosted_organization_invitation`, `logfire_delete_organization`, `logfire_get_organization`, `logfire_list_organizations`, `logfire_update_organization` `logfire_create_alert`, `logfire_create_channel`, `logfire_create_dashboard`, `logfire_create_project`, `logfire_create_variable`, `logfire_delete_alert`, `logfire_delete_channel`, `logfire_delete_dashboard`, `logfire_delete_project`, `logfire_get_alert`, `logfire_get_channel`, `logfire_get_dashboard`, `logfire_get_project_info`, `logfire_get_variable_by_name`, `logfire_get_variables_config`, `logfire_list_alerts`, `logfire_list_dashboards`, `logfire_update_alert`, `logfire_update_channel`, `logfire_update_dashboard`, `logfire_update_project`, `logfire_update_variable` `description-fix` Renamed the connector to Pydantic Logfire and switched to the official Pydantic logo. # Pylon Source: https://docs.stackone.com/connectors/pylon/index How to set up the Pylon connector, plus the actions that are available.
Pylon
Previewv1.2.0
63 actions · 1 auth method
Customer Support Ticketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/pylon/index.md for the full list. # Pylon Changelog Source: https://docs.stackone.com/connectors/pylon/changelog Release history for the Pylon connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for accounts, contacts, users, teams, tags, ticket forms, user roles, knowledge bases, feature requests, and unified IAM actions. Added pagination inputs to list accounts, users, teams, and issues. `pylon_list_accounts`, `pylon_list_contacts`, `pylon_list_issues`, `pylon_list_knowledge_bases`, `pylon_list_tags`, `pylon_list_teams`, `pylon_list_ticket_forms`, `pylon_list_user_roles`, `pylon_list_users`, `pylon_search_feature_requests`, `pylon_unified_list_groups`, `pylon_unified_list_organizations`, `pylon_unified_list_roles`, `pylon_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, credentials, resource users, and resource types. # Qlik Source: https://docs.stackone.com/connectors/qlik/index How to set up the Qlik connector, plus the actions and events that are available.
Qlik
v2.2.0
112 actions · 20 events · 2 auth methods
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 authorization code flow for user-delegated access to Qlik Cloud resources. Authenticate using a Qlik Cloud API key. API keys provide the same permissions as the user who created them. Keys cannot... Optionally, configure receiving Events for Qlik into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/qlik/index.md for the full list. ## Events See https://docs.stackone.com/connectors/qlik/index.md for the full list. # Qlik Changelog Source: https://docs.stackone.com/connectors/qlik/changelog Release history for the Qlik connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added webhook event support. StackOne registers a tenant-level webhook automatically when an account is connected and removes it on disconnect, handling twenty events across apps, automations, data integration tasks, reloads, users and API keys. Inbound events are mapped from the CloudEvent attributes rather than the legacy fields Qlik removes on 6 October 2026. Fifteen of the twenty event handlers are verified against live deliveries and ship as preview; the five that could not be triggered on a standard tenant - API key validation and the four data integration task events - ship as beta. A setup guide documents the tenant admin requirement and the full event catalogue. `bug-fix` Group lists now return system groups (such as com.qlik.Everyone) once, after the last regular group, instead of on every page, where they pushed regular groups out at small page sizes. `qlik_unified_list_groups` `new-feature` `data-sync` Twelve list actions can now be synced with Data Sync, covering audit events, users, groups, roles, items, collections, spaces, API keys, automations and the unified IAM users, roles and organizations. Listing users also accepts a new optional startingAfter cursor, which Qlik returns on that endpoint when no filter is applied. `qlik_list_api_keys`, `qlik_list_audit_events`, `qlik_list_automations`, `qlik_list_collections`, `qlik_list_groups`, `qlik_list_items`, `qlik_list_roles`, `qlik_list_spaces`, `qlik_list_users`, `qlik_unified_list_organizations`, `qlik_unified_list_roles`, `qlik_unified_list_users` `breaking-change` Every action now declares which authentication types it supports. The seven API key management actions are API Key only, because Qlik does not allow OAuth clients to be granted the api-keys scope, while the remaining 105 actions work with both OAuth 2.0 and API Key and now carry their required OAuth scopes. `qlik_activate_brand`, `qlik_add_item_to_collection`, `qlik_change_automation_owner`, `qlik_change_automation_space`, `qlik_copy_automation`, `qlik_count_users`, `qlik_create_api_key`, `qlik_create_automation`, `qlik_create_automation_run`, `qlik_create_collection`, `qlik_create_group`, `qlik_create_role`, `qlik_create_space`, `qlik_create_space_assignment`, `qlik_create_space_share`, `qlik_create_user`, `qlik_deactivate_brand`, `qlik_delete_api_key`, `qlik_delete_automation`, `qlik_delete_brand`, `qlik_delete_brand_file`, `qlik_delete_collection`, `qlik_delete_extension`, `qlik_delete_group`, `qlik_delete_item`, `qlik_delete_role`, `qlik_delete_space`, `qlik_delete_space_assignment`, `qlik_delete_space_share`, `qlik_delete_task`, `qlik_delete_user`, `qlik_disable_automation`, `qlik_enable_automation`, `qlik_export_automation_run_log`, `qlik_filter_groups`, `qlik_filter_users`, `qlik_get_active_brand`, `qlik_get_api_key`, `qlik_get_api_keys_config`, `qlik_get_audit_event`, `qlik_get_audit_settings`, `qlik_get_automation`, `qlik_get_automation_run`, `qlik_get_automation_usage_metrics`, `qlik_get_brand`, `qlik_get_brand_file`, `qlik_get_collection`, `qlik_get_collection_item`, `qlik_get_current_user`, `qlik_get_extension`, `qlik_get_extension_archive`, `qlik_get_extension_file`, `qlik_get_favorites_collection`, `qlik_get_group`, `qlik_get_group_settings`, `qlik_get_item`, `qlik_get_items_settings`, `qlik_get_role`, `qlik_get_space`, `qlik_get_space_assignment`, `qlik_get_space_share`, `qlik_get_task`, `qlik_get_user`, `qlik_invite_user`, `qlik_list_api_keys`, `qlik_list_archived_audit_events`, `qlik_list_audit_event_types`, `qlik_list_audit_events`, `qlik_list_audit_sources`, `qlik_list_automation_runs`, `qlik_list_automations`, `qlik_list_brands`, `qlik_list_collection_items`, `qlik_list_collections`, `qlik_list_extensions`, `qlik_list_groups`, `qlik_list_item_collections`, `qlik_list_items`, `qlik_list_roles`, `qlik_list_space_assignments`, `qlik_list_space_shares`, `qlik_list_space_types`, `qlik_list_spaces`, `qlik_list_tasks`, `qlik_list_users`, `qlik_move_automation`, `qlik_remove_item_from_collection`, `qlik_retry_automation_run`, `qlik_start_task`, `qlik_stop_automation_run`, `qlik_unified_get_group`, `qlik_unified_get_me`, `qlik_unified_get_organization`, `qlik_unified_get_role`, `qlik_unified_get_user`, `qlik_unified_list_groups`, `qlik_unified_list_organizations`, `qlik_unified_list_resource_types`, `qlik_unified_list_resource_users`, `qlik_unified_list_roles`, `qlik_unified_list_users`, `qlik_update_api_key_description`, `qlik_update_api_keys_config`, `qlik_update_automation`, `qlik_update_brand`, `qlik_update_collection`, `qlik_update_group`, `qlik_update_item`, `qlik_update_role`, `qlik_update_space`, `qlik_update_space_assignment`, `qlik_update_user` `bug-fix` Fixed group list errors and incorrect email filtering on user lists. # Quartr Source: https://docs.stackone.com/connectors/quartr/index How to set up the Quartr connector, plus the actions that are available.
Quartr
Betav0.2.0
35 actions · 1 auth method
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an API key generated in the Quartr Portal. Keys do not expire and are sent as the x-api-key header. Each key in... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/quartr/index.md for the full list. # Quartr Changelog Source: https://docs.stackone.com/connectors/quartr/changelog Release history for the Quartr connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the company, event, event type, document, document type, report, slide deck, transcript, audio, live event, live audio, and live transcript list actions, with incremental sync via updatedAfter on all except event types and document types. `quartr_list_audio`, `quartr_list_companies`, `quartr_list_document_types`, `quartr_list_documents`, `quartr_list_event_types`, `quartr_list_events`, `quartr_list_live_audio`, `quartr_list_live_events`, `quartr_list_live_transcripts`, `quartr_list_reports`, `quartr_list_slide_decks`, `quartr_list_transcripts` `new-connector` Initial release of the Quartr connector with 35 read-only actions covering companies, events, documents, reports, slide decks, transcripts, earnings call audio and live streams, plus AI-generated summaries and parsed document text. # QuickBooks Online Source: https://docs.stackone.com/connectors/quickbooksonline/index How to set up the QuickBooks Online connector, plus the actions and events that are available.
QuickBooks Online
v1.5.0
95 actions · 1 event · 1 auth method
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an app in the Intuit Developer Portal. Connecting users will need their Company ID (Realm ID). Optionally, configure receiving Events for QuickBooks Online into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/quickbooksonline/index.md for the full list. ## Events See https://docs.stackone.com/connectors/quickbooksonline/index.md for the full list. # QuickBooks Online Changelog Source: https://docs.stackone.com/connectors/quickbooksonline/changelog Release history for the QuickBooks Online connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Webhook events are now delivered to the per-connection Native Webhook URL on the linked account. The previous routing that matched deliveries to a connection by QuickBooks Company ID (Realm ID) is no longer supported and has been removed. `webhooks` Added inbound webhook support so QuickBooks Online entity changes (customers, invoices, bills, payments, vendors, and more) can be pushed to StackOne in real time instead of relying only on polling. `data-sync` Added scheduled data sync to all fifteen list actions — customers, invoices, bills, vendors, accounts, items, payments, and more — so these collections can be synced into StackOne on a schedule and kept current with incremental (changed-since) updates. `quickbooksonline_list_accounts`, `quickbooksonline_list_bill_payments`, `quickbooksonline_list_bills`, `quickbooksonline_list_customers`, `quickbooksonline_list_invoices`, `quickbooksonline_list_items`, `quickbooksonline_list_payments`, `quickbooksonline_list_purchase_orders`, `quickbooksonline_list_purchases`, `quickbooksonline_list_refund_receipts`, `quickbooksonline_list_sales_receipts`, `quickbooksonline_list_tax_codes`, `quickbooksonline_list_tax_rates`, `quickbooksonline_list_vendor_credits`, `quickbooksonline_list_vendors` `bug-fix` `auth` Update connector to adhere to RealmID and new Callback Parameters `quickbooksonline_create_account`, `quickbooksonline_create_bill`, `quickbooksonline_create_bill_payment`, `quickbooksonline_create_class`, `quickbooksonline_create_credit_memo`, `quickbooksonline_create_customer`, `quickbooksonline_create_department`, `quickbooksonline_create_deposit`, `quickbooksonline_create_employee`, `quickbooksonline_create_estimate`, `quickbooksonline_create_invoice`, `quickbooksonline_create_item`, `quickbooksonline_create_journal_entry`, `quickbooksonline_create_payment`, `quickbooksonline_create_payment_method`, `quickbooksonline_create_purchase`, `quickbooksonline_create_purchase_order`, `quickbooksonline_create_refund_receipt`, `quickbooksonline_create_sales_receipt`, `quickbooksonline_create_term`, `quickbooksonline_create_transfer`, `quickbooksonline_create_vendor`, `quickbooksonline_create_vendor_credit`, `quickbooksonline_delete_bill`, `quickbooksonline_delete_bill_payment`, `quickbooksonline_delete_credit_memo`, `quickbooksonline_delete_deposit`, `quickbooksonline_delete_estimate`, `quickbooksonline_delete_invoice`, `quickbooksonline_delete_journal_entry`, `quickbooksonline_delete_payment`, `quickbooksonline_delete_purchase`, `quickbooksonline_delete_purchase_order`, `quickbooksonline_delete_refund_receipt`, `quickbooksonline_delete_sales_receipt`, `quickbooksonline_delete_transfer`, `quickbooksonline_delete_vendor_credit`, `quickbooksonline_get_account`, `quickbooksonline_get_account_list_detail_report`, `quickbooksonline_get_aged_payables_report`, `quickbooksonline_get_aged_receivables_report`, `quickbooksonline_get_balance_sheet_report`, `quickbooksonline_get_bill`, `quickbooksonline_get_bill_payment`, `quickbooksonline_get_cash_flow_report`, `quickbooksonline_get_class`, `quickbooksonline_get_company_info`, `quickbooksonline_get_credit_memo`, `quickbooksonline_get_customer`, `quickbooksonline_get_department`, `quickbooksonline_get_deposit`, `quickbooksonline_get_employee`, `quickbooksonline_get_estimate`, `quickbooksonline_get_invoice`, `quickbooksonline_get_item`, `quickbooksonline_get_journal_entry`, `quickbooksonline_get_payment`, `quickbooksonline_get_payment_method`, `quickbooksonline_get_profit_and_loss_report`, `quickbooksonline_get_purchase`, `quickbooksonline_get_purchase_order`, `quickbooksonline_get_refund_receipt`, `quickbooksonline_get_sales_receipt`, `quickbooksonline_get_tax_code`, `quickbooksonline_get_tax_rate`, `quickbooksonline_get_term`, `quickbooksonline_get_transfer`, `quickbooksonline_get_vendor`, `quickbooksonline_get_vendor_credit`, `quickbooksonline_list_accounts`, `quickbooksonline_list_bill_payments`, `quickbooksonline_list_bills`, `quickbooksonline_list_customers`, `quickbooksonline_list_invoices`, `quickbooksonline_list_items`, `quickbooksonline_list_payments`, `quickbooksonline_list_purchase_orders`, `quickbooksonline_list_purchases`, `quickbooksonline_list_refund_receipts`, `quickbooksonline_list_sales_receipts`, `quickbooksonline_list_tax_codes`, `quickbooksonline_list_tax_rates`, `quickbooksonline_list_vendor_credits`, `quickbooksonline_list_vendors`, `quickbooksonline_query`, `quickbooksonline_update_account`, `quickbooksonline_update_bill`, `quickbooksonline_update_bill_payment`, `quickbooksonline_update_customer`, `quickbooksonline_update_estimate`, `quickbooksonline_update_invoice`, `quickbooksonline_update_item`, `quickbooksonline_update_payment`, `quickbooksonline_update_vendor`, `quickbooksonline_update_vendor_credit` `bug-fix` `auth` Strip spaces from the Company ID (Realm ID) credential before building request URLs, since QuickBooks Online displays the value with spaces that break the API request when copied as-is. # Rally Source: https://docs.stackone.com/connectors/rally/index How to set up the Rally connector, plus the actions and events that are available.
Rally
v2.0.0
72 actions · 18 events · 1 auth method
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a Rally API key generated from your Rally account settings. Optionally, configure receiving Events for Rally into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/rally/index.md for the full list. ## Events See https://docs.stackone.com/connectors/rally/index.md for the full list. # Rally Changelog Source: https://docs.stackone.com/connectors/rally/changelog Release history for the Rally connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking-change` `data-sync` Added DataSync support to all 15 list actions with incremental sync. List actions now return full record fields by default instead of compact references. `rally_list_attachments`, `rally_list_defects`, `rally_list_features`, `rally_list_initiatives`, `rally_list_iterations`, `rally_list_milestones`, `rally_list_projects`, `rally_list_releases`, `rally_list_tags`, `rally_list_tasks`, `rally_list_test_cases`, `rally_list_user_stories`, `rally_list_users`, `rally_list_webhooks`, `rally_list_workspaces` `improved` `actions-updated` `bug-fix` Clarified query syntax guidance, documented CapitalApproval limitations on create actions, clarified iteration assignment constraints, and clarified workspace ObjectID usage. Updated connection guide with screenshots and corrected navigation steps. # Ramp Source: https://docs.stackone.com/connectors/ramp/index How to set up the Ramp connector, plus the actions and events that are available.
Ramp
v1.3.1
75 actions · 42 events · 1 auth method
Expense Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). User-delegated access via Ramp's OAuth consent screen — the end user authorizes the connection on behalf of their Ramp b... Optionally, configure receiving Events for Ramp into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ramp/index.md for the full list. ## Events See https://docs.stackone.com/connectors/ramp/index.md for the full list. # Ramp Changelog Source: https://docs.stackone.com/connectors/ramp/changelog Release history for the Ramp connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `description-fix` Fixed OAuth authorization failing with an unavailable scope error by no longer requesting applications:read and spend_requests:read, which Ramp only grants to partner apps. `ramp_create_accounting_accounts`, `ramp_create_accounting_codings`, `ramp_create_accounting_connection`, `ramp_create_accounting_field_options`, `ramp_create_accounting_fields`, `ramp_create_accounting_ready_to_sync`, `ramp_create_accounting_syncs`, `ramp_create_accounting_vendors`, `ramp_create_departments`, `ramp_create_locations`, `ramp_create_memos`, `ramp_create_physical_card`, `ramp_create_receipts`, `ramp_create_spend_programs`, `ramp_create_user`, `ramp_create_vendors`, `ramp_delete_accounting_account`, `ramp_delete_accounting_field_option`, `ramp_delete_vendor`, `ramp_get_accounting_account`, `ramp_get_accounting_connection`, `ramp_get_accounting_field`, `ramp_get_accounting_vendor`, `ramp_get_bill`, `ramp_get_business`, `ramp_get_business_balance`, `ramp_get_department`, `ramp_get_entity`, `ramp_get_fund`, `ramp_get_location`, `ramp_get_memo`, `ramp_get_physical_card`, `ramp_get_receipt`, `ramp_get_reimbursement`, `ramp_get_spend_program`, `ramp_get_transaction`, `ramp_get_transfer`, `ramp_get_trip`, `ramp_get_user`, `ramp_get_user_deferred_status`, `ramp_get_vendor`, `ramp_get_virtual_card`, `ramp_list_accounting_accounts`, `ramp_list_accounting_connections`, `ramp_list_accounting_field_options`, `ramp_list_accounting_fields`, `ramp_list_accounting_vendors`, `ramp_list_bills`, `ramp_list_departments`, `ramp_list_entities`, `ramp_list_funds`, `ramp_list_locations`, `ramp_list_memos`, `ramp_list_merchants`, `ramp_list_physical_cards`, `ramp_list_purchase_orders`, `ramp_list_receipts`, `ramp_list_reimbursements`, `ramp_list_repayments`, `ramp_list_spend_programs`, `ramp_list_transactions`, `ramp_list_transfers`, `ramp_list_trips`, `ramp_list_users`, `ramp_list_vendors`, `ramp_list_virtual_cards`, `ramp_manage_user_invite`, `ramp_update_accounting_account`, `ramp_update_accounting_field_option`, `ramp_update_department`, `ramp_update_location`, `ramp_update_physical_card`, `ramp_update_transaction`, `ramp_update_user`, `ramp_update_vendor` `new-feature` `data-sync` Added data sync support to 23 list actions, including transactions, vendors, users, bills and cards, with incremental sync for reimbursements and vendors. Existing action behaviour is unchanged. `ramp_list_accounting_accounts`, `ramp_list_accounting_connections`, `ramp_list_accounting_fields`, `ramp_list_accounting_vendors`, `ramp_list_bills`, `ramp_list_departments`, `ramp_list_entities`, `ramp_list_funds`, `ramp_list_locations`, `ramp_list_memos`, `ramp_list_merchants`, `ramp_list_physical_cards`, `ramp_list_purchase_orders`, `ramp_list_receipts`, `ramp_list_reimbursements`, `ramp_list_repayments`, `ramp_list_spend_programs`, `ramp_list_transactions`, `ramp_list_transfers`, `ramp_list_trips`, `ramp_list_users`, `ramp_list_vendors`, `ramp_list_virtual_cards` `bug-fix` Webhook subscriptions now finish Ramp's verification handshake instead of staying unverified, so events are delivered again. `bug-fix` Rejected list requests now return Ramp's own validation message instead of a bare HTTP 422, so callers can see what to correct. `ramp_list_accounting_accounts`, `ramp_list_accounting_field_options`, `ramp_list_accounting_fields`, `ramp_list_accounting_vendors`, `ramp_list_bills`, `ramp_list_departments`, `ramp_list_entities`, `ramp_list_funds`, `ramp_list_locations`, `ramp_list_memos`, `ramp_list_merchants`, `ramp_list_physical_cards`, `ramp_list_purchase_orders`, `ramp_list_receipts`, `ramp_list_reimbursements`, `ramp_list_repayments`, `ramp_list_spend_programs`, `ramp_list_transactions`, `ramp_list_transfers`, `ramp_list_trips`, `ramp_list_vendors`, `ramp_list_virtual_cards` `bug-fix` Webhook verification now confirms the exact subscription StackOne created instead of guessing the newest pending one, so event delivery starts reliably even when several subscriptions are awaiting verification. Webhook events are marked as preview. `new-actions` `bug-fix` `description-fix` Added accounting field-option update and delete actions, surfaced Ramp's real validation messages on failed writes, and corrected transaction-split and card-issuance guidance. `ramp_delete_accounting_field_option`, `ramp_update_accounting_field_option` `ramp_create_accounting_field_options`, `ramp_create_physical_card`, `ramp_create_receipts`, `ramp_list_transactions`, `ramp_list_users`, `ramp_update_accounting_account`, `ramp_update_physical_card`, `ramp_update_transaction`, `ramp_update_vendor` `native-webhooks` Added native webhook event mapping — 41 Ramp events with fully programmatic subscription lifecycle (create, verify, delete) and events setup guide. `ramp_create_accounting_accounts`, `ramp_create_accounting_codings`, `ramp_create_accounting_connection`, `ramp_create_accounting_field_options`, `ramp_create_accounting_fields`, `ramp_create_accounting_ready_to_sync`, `ramp_create_accounting_syncs`, `ramp_create_accounting_vendors`, `ramp_create_departments`, `ramp_create_locations`, `ramp_create_memos`, `ramp_create_physical_card`, `ramp_create_receipts`, `ramp_create_spend_programs`, `ramp_create_user`, `ramp_create_vendors`, `ramp_delete_accounting_account`, `ramp_delete_vendor`, `ramp_get_accounting_account`, `ramp_get_accounting_connection`, `ramp_get_accounting_field`, `ramp_get_accounting_vendor`, `ramp_get_bill`, `ramp_get_business`, `ramp_get_business_balance`, `ramp_get_department`, `ramp_get_entity`, `ramp_get_fund`, `ramp_get_location`, `ramp_get_memo`, `ramp_get_physical_card`, `ramp_get_receipt`, `ramp_get_reimbursement`, `ramp_get_spend_program`, `ramp_get_transaction`, `ramp_get_transfer`, `ramp_get_trip`, `ramp_get_user`, `ramp_get_user_deferred_status`, `ramp_get_vendor`, `ramp_get_virtual_card`, `ramp_list_accounting_accounts`, `ramp_list_accounting_connections`, `ramp_list_accounting_field_options`, `ramp_list_accounting_fields`, `ramp_list_accounting_vendors`, `ramp_list_bills`, `ramp_list_departments`, `ramp_list_entities`, `ramp_list_funds`, `ramp_list_locations`, `ramp_list_memos`, `ramp_list_merchants`, `ramp_list_physical_cards`, `ramp_list_purchase_orders`, `ramp_list_receipts`, `ramp_list_reimbursements`, `ramp_list_repayments`, `ramp_list_spend_programs`, `ramp_list_transactions`, `ramp_list_transfers`, `ramp_list_trips`, `ramp_list_users`, `ramp_list_vendors`, `ramp_list_virtual_cards`, `ramp_manage_user_invite`, `ramp_update_accounting_account`, `ramp_update_department`, `ramp_update_location`, `ramp_update_physical_card`, `ramp_update_transaction`, `ramp_update_user`, `ramp_update_vendor` `bug-fix` Clarified transactions and cards guidance from cross-SDK testing — requires_memo semantics, virtual-vs-physical card lookups, and physical-card rename limits. `ramp_get_physical_card`, `ramp_list_transactions`, `ramp_update_accounting_account`, `ramp_update_physical_card` `bug-fix` Clarified action guidance flagged in behavioural testing — GL account deactivation, virtual vs physical card lookups, repayment-to-transfer resolution, transaction approval filters, and department coding via splits. # Range Source: https://docs.stackone.com/connectors/range/index How to set up the Range connector, plus the actions that are available.
Range
v1.1.1
13 actions · 1 auth method
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from your Range developer settings at range.co/\_/settings/developer Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/range/index.md for the full list. # Range Changelog Source: https://docs.stackone.com/connectors/range/changelog Release history for the Range connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Added API Key connection guide. `data-sync` Added data sync support for teams, enabling periodic full-refresh syncing of all teams in the organization. `range_list_teams` `bug-fix` Improved action descriptions for record_interaction, update_user_profile, list_users, list_updates, and find_user to document provider constraints and prevent agent errors. # Re:amaze Source: https://docs.stackone.com/connectors/reamaze/index How to set up the Re:amaze connector, plus the actions that are available.
Re:amaze
v2.3.1
39 actions · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Admin privileges required to generate API tokens Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/reamaze/index.md for the full list. # Re:amaze Changelog Source: https://docs.stackone.com/connectors/reamaze/changelog Release history for the Re:amaze connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `action-fix` Added success confirmation message to update_article response for improved mutation verification. `reamaze_update_article` `data-sync` Added DataSync capability to 9 list actions (articles, contacts, conversations, staff, channels, incidents, systems, response templates, satisfaction ratings) with incremental sync support on satisfaction ratings. `reamaze_list_articles`, `reamaze_list_channels`, `reamaze_list_contacts`, `reamaze_list_conversations`, `reamaze_list_incidents`, `reamaze_list_response_templates`, `reamaze_list_satisfaction_ratings`, `reamaze_list_staff`, `reamaze_list_systems` `new-actions` `bug-fix` Added status field to update_article for setting article visibility (published, draft, internal). Added sandbox limitation note to create_message. `reamaze_create_message`, `reamaze_update_article` `guide` `fix` Improved connector guide with registration flow, login URL, and field guidance. Made user and category required on create_conversation. `reamaze_create_conversation`, `reamaze_update_article` `breaking` `new-actions` Fixed create_conversation documentation, removed invalid igsid enum value, documented update_incident split-call limitation. `reamaze_create_contact_identity`, `reamaze_create_conversation`, `reamaze_update_incident` `breaking` `new-actions` Removed undocumented fields (friendly_name, status, topic_id, role, subject). Added incidents and systems resource (6 new actions). Added missing parameters across conversations, contacts, and reports. # RECRU Source: https://docs.stackone.com/connectors/recru/index How to set up the RECRU connector, plus the actions and events that are available.
RECRU
Previewv1.1.0
66 actions · 2 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). RECRU exposes a JSON-RPC API at a single per-tenant endpoint. Credentials are an \`api\` username (fixed) plus a password... Optionally, configure receiving Events for RECRU into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/recru/index.md for the full list. ## Events See https://docs.stackone.com/connectors/recru/index.md for the full list. # RECRU Changelog Source: https://docs.stackone.com/connectors/recru/changelog Release history for the RECRU connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `data-sync` `webhooks` `docs` Added webhook support for job offer publish and unpublish events, delivered through RECRU's Site API Listener. Documented the shape of the paging, search, specialFilter, profilePhoto, filesPreview and CV data objects, corrected action descriptions that named parameters the API does not accept, added list_project_close_reasons, and replaced account-specific code lists on project type, phases and close reason with pointers to the actions that resolve them. Allowed search values to be arrays for the in and notIn conditions, documented that notLike compares the value as given so a substring negation needs %value%, and documented the fields the provider truncates, overrides or does not store. Added validation so a request that would be silently ignored is rejected instead — jobseeker_source and source_name are now mutually exclusive, status_closed_reason is required when a project is closed, and the candidate tag actions require the candidate and tag ids. Added length limits on the department postal code and NACE fields so an over-long value is rejected instead of silently truncated, documented which fields the project-candidate list can be ordered by, recorded that a rejection phase requires a rejection reason, and removed the candidate status field, which the API accepts but never stores. Removing a candidate from a project now reports the real outcome — the provider commits the removal and then fails on a follow-up query, so the result is verified before being returned. Constrained the sortable columns on the project-candidate list, and removed the event id and the project-phase filter, which the API accepts but ignores. Documented that a project needs a type set before its pipeline can be used — without one, phase events and candidate removals fail with a database error. Corrected the file attachment fields — department files use isLogo, documentType now carries its real id list, and the stored name is the supplied filename with a unique prefix rather than a replacement. # Recruit CRM Source: https://docs.stackone.com/connectors/recruitcrm/index How to set up the Recruit CRM connector, plus the actions that are available.
Recruit CRM
Betav0.2.1
83 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a static API token sent as a Bearer token. Only the account owner can generate the token, and a Business plan or hi... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/recruitcrm/index.md for the full list. # Recruit CRM Changelog Source: https://docs.stackone.com/connectors/recruitcrm/changelog Release history for the Recruit CRM connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the API Token documentation link with a full connection guide covering enabling the token under Admin Settings > API, including the Account Owner and Business plan requirements. `data-sync` Added DataSync support to 31 list actions covering candidates, companies, contacts, deals, hotlists, jobs, notes, tasks, users, teams, collaborators, custom fields and lookup lists. All resources sync as full refreshes, because the Recruit CRM API exposes no updated-since filter on its list endpoints. `recruitcrm_list_call_types`, `recruitcrm_list_candidate_custom_fields`, `recruitcrm_list_candidates`, `recruitcrm_list_collaborators`, `recruitcrm_list_companies`, `recruitcrm_list_company_custom_fields`, `recruitcrm_list_contact_custom_fields`, `recruitcrm_list_contacts`, `recruitcrm_list_currencies`, `recruitcrm_list_custom_fields`, `recruitcrm_list_deal_custom_fields`, `recruitcrm_list_deal_pipeline_stages`, `recruitcrm_list_deals`, `recruitcrm_list_hiring_pipelines`, `recruitcrm_list_hotlists`, `recruitcrm_list_industries`, `recruitcrm_list_job_associated_custom_fields`, `recruitcrm_list_job_custom_fields`, `recruitcrm_list_job_pipeline_stages`, `recruitcrm_list_jobs`, `recruitcrm_list_languages`, `recruitcrm_list_meeting_types`, `recruitcrm_list_note_types`, `recruitcrm_list_notes`, `recruitcrm_list_proficiencies`, `recruitcrm_list_qualifications`, `recruitcrm_list_salary_types`, `recruitcrm_list_task_types`, `recruitcrm_list_tasks`, `recruitcrm_list_teams`, `recruitcrm_list_users` `new-actions` Initial Recruit CRM connector with 83 actions covering candidates, contacts, companies, jobs, deals, tasks, notes, hotlists, custom fields, users, and lookups. # Recruitee Source: https://docs.stackone.com/connectors/recruitee/index How to set up the Recruitee connector, plus the actions that are available.
Recruitee
v1.0.0
26 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Access requires API token generation from Settings > Apps and plugins > Personal API Tokens Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/recruitee/index.md for the full list. # Recruiterflow Source: https://docs.stackone.com/connectors/recruiterflow/index How to set up the Recruiterflow connector, plus the actions that are available.
Recruiterflow
Betav1.0.0
49 actions · 1 auth method
ATS CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Recruiterflow uses an API key sent in the RF-Api-Key header. API keys are issued by the Recruiterflow team — they are no... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/recruiterflow/index.md for the full list. # Recurly Source: https://docs.stackone.com/connectors/recurly/index How to set up the Recurly connector, plus the actions that are available.
Recurly
Previewv2.0.2
139 actions · 1 auth method
Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using your Recurly API key via HTTP Basic Auth. The API key is used as the username with an empty password. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/recurly/index.md for the full list. # Recurly Changelog Source: https://docs.stackone.com/connectors/recurly/changelog Release history for the Recurly connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `description-fix` Clarified tool descriptions that led agents to wrong calls. Create Pending Purchase now documents its line item fields and the prepayment-only rule, Create Line Item no longer suggests USD as a default currency, List Subscriptions no longer points to an action that does not exist, and Cancel Subscription and Update Subscription explain the difference between cancelling and turning off auto-renew. Get Invoice notes that uuids and pending-purchase invoices cannot be fetched. `recurly_cancel_subscription`, `recurly_create_line_item`, `recurly_create_pending_purchase`, `recurly_get_invoice`, `recurly_list_subscriptions`, `recurly_update_subscription` `bug-fix` Fixed prepayment line items, pending purchases and custom field values that Recurly rejected, and account note deletion now confirms which note was removed. `recurly_cancel_subscription`, `recurly_create_account`, `recurly_create_coupon`, `recurly_create_item`, `recurly_create_line_item`, `recurly_create_measured_unit`, `recurly_create_pending_purchase`, `recurly_create_plan`, `recurly_create_subscription`, `recurly_create_subscription_change`, `recurly_preview_subscription_change`, `recurly_remove_account_note`, `recurly_update_account`, `recurly_update_item`, `recurly_update_measured_unit`, `recurly_update_plan`, `recurly_update_subscription` `breaking` `bug-fix` `new-actions` `guide` Fixed ramp and setup-fee plan pricing, purchase subscription entries and billing-info updates that Recurly rejected, and added an account-level subscriptions list. Clarified value formats across usage, coupons, measured units and accounting codes, and refreshed the API key connection guide with screenshots. `recurly_list_account_subscriptions` `recurly_cancel_purchase`, `recurly_cancel_subscription`, `recurly_collect_invoice`, `recurly_create_account`, `recurly_create_account_note`, `recurly_create_authorize_purchase`, `recurly_create_billing_info`, `recurly_create_capture_purchase`, `recurly_create_coupon`, `recurly_create_coupon_redemption`, `recurly_create_gift_card`, `recurly_create_invoice`, `recurly_create_item`, `recurly_create_line_item`, `recurly_create_measured_unit`, `recurly_create_pending_purchase`, `recurly_create_plan`, `recurly_create_plan_add_on`, `recurly_create_purchase`, `recurly_create_shipping_address`, `recurly_create_shipping_method`, `recurly_create_subscription`, `recurly_create_subscription_change`, `recurly_create_usage`, `recurly_deactivate_account`, `recurly_deactivate_coupon`, `recurly_deactivate_item`, `recurly_deactivate_shipping_method`, `recurly_get_account`, `recurly_get_account_acquisition`, `recurly_get_account_balance`, `recurly_get_account_note`, `recurly_get_billing_info`, `recurly_get_business_entity`, `recurly_get_coupon`, `recurly_get_coupon_redemption`, `recurly_get_credit_payment`, `recurly_get_custom_field_definition`, `recurly_get_dunning_campaign`, `recurly_get_export_dates`, `recurly_get_export_files`, `recurly_get_gift_card`, `recurly_get_invoice`, `recurly_get_invoice_template`, `recurly_get_item`, `recurly_get_line_item`, `recurly_get_measured_unit`, `recurly_get_plan`, `recurly_get_plan_add_on`, `recurly_get_price_segment`, `recurly_get_shipping_address`, `recurly_get_shipping_method`, `recurly_get_site`, `recurly_get_subscription`, `recurly_get_subscription_change`, `recurly_get_subscription_coupon_redemption`, `recurly_get_subscription_renewal`, `recurly_get_transaction`, `recurly_get_usage`, `recurly_list_account_acquisition`, `recurly_list_account_coupon_redemptions`, `recurly_list_account_credit_payments`, `recurly_list_account_invoices`, `recurly_list_account_line_items`, `recurly_list_account_notes`, `recurly_list_account_transactions`, `recurly_list_accounts`, `recurly_list_active_coupon_redemptions`, `recurly_list_billing_infos`, `recurly_list_business_entities`, `recurly_list_coupons`, `recurly_list_credit_payments`, `recurly_list_custom_field_definitions`, `recurly_list_dunning_campaigns`, `recurly_list_gift_cards`, `recurly_list_invoice_coupon_redemptions`, `recurly_list_invoice_line_items`, `recurly_list_invoice_templates`, `recurly_list_invoices`, `recurly_list_items`, `recurly_list_line_items`, `recurly_list_measured_units`, `recurly_list_plan_add_ons`, `recurly_list_plans`, `recurly_list_price_segments`, `recurly_list_shipping_addresses`, `recurly_list_shipping_methods`, `recurly_list_sites`, `recurly_list_subscription_coupon_redemptions`, `recurly_list_subscription_invoices`, `recurly_list_subscription_line_items`, `recurly_list_subscriptions`, `recurly_list_transactions`, `recurly_list_usage`, `recurly_mark_invoice_failed`, `recurly_mark_invoice_successful`, `recurly_pause_subscription`, `recurly_preview_gift_card`, `recurly_preview_purchase`, `recurly_preview_subscription_change`, `recurly_put_dunning_campaign_bulk_update`, `recurly_reactivate_account`, `recurly_reactivate_item`, `recurly_reactivate_subscription`, `recurly_redeem_gift_card`, `recurly_refund_invoice`, `recurly_remove_account_acquisition`, `recurly_remove_account_note`, `recurly_remove_billing_info`, `recurly_remove_coupon_redemption`, `recurly_remove_coupon_redemption_by_id`, `recurly_remove_line_item`, `recurly_remove_measured_unit`, `recurly_remove_plan`, `recurly_remove_plan_add_on`, `recurly_remove_shipping_address`, `recurly_remove_subscription_change`, `recurly_remove_subscription_coupon_redemption`, `recurly_remove_usage`, `recurly_reopen_invoice`, `recurly_restore_coupon`, `recurly_resume_subscription`, `recurly_update_account`, `recurly_update_account_acquisition`, `recurly_update_billing_info`, `recurly_update_coupon`, `recurly_update_invoice`, `recurly_update_item`, `recurly_update_measured_unit`, `recurly_update_plan`, `recurly_update_plan_add_on`, `recurly_update_shipping_address`, `recurly_update_shipping_method`, `recurly_update_subscription`, `recurly_update_usage`, `recurly_verify_billing_info`, `recurly_verify_billing_info_cvv`, `recurly_void_invoice` `data-sync` Added DataSync support to 19 list actions. 13 of them sync incrementally via an updated_at watermark (begin_time paired with sort=updated_at); the rest refresh in full. # Reddit Source: https://docs.stackone.com/connectors/reddit/index How to set up the Reddit connector, plus the actions that are available.
Reddit
Betav1.1.0
57 actions · 2 auth methods
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering a Web app at reddit.com/prefs/apps. Issues a short-lived access token (1 hour) and a long-lived ref... For Reddit "script" apps that authenticate as a single user (the app's developer). No refresh token is issued; the conne... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/reddit/index.md for the full list. # Reddit Changelog Source: https://docs.stackone.com/connectors/reddit/changelog Release history for the Reddit connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for the nine account-scoped Reddit listings that need no scoping input — the front-page hot, new and top feeds, the inbox, unread and sent message listings, and the subscribed, moderated and popular subreddit listings. All nine walk Reddit's standard Listing cursor (the after fullname) and full refresh on every run, since Reddit listings expose no updated-since filter. No change to any action's request behaviour or inputs. # Remote Source: https://docs.stackone.com/connectors/remote/index How to set up the Remote connector, plus the actions and events that are available.
Remote
v2.1.1
68 actions · 50 events · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API token from your Remote account under Company settings > Integrations > Integrations & APIs > Remote API. Optionally, configure receiving Events for Remote into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/remote/index.md for the full list. ## Events See https://docs.stackone.com/connectors/remote/index.md for the full list. # Remote Changelog Source: https://docs.stackone.com/connectors/remote/changelog Release history for the Remote connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `description-fix` Clarified descriptions for country holidays, country form schemas, the country list, employments, employment contract updates, incentives, custom field values and time off so agents choose the right action and send valid requests. `remote_cancel_timeoff`, `remote_decline_cancel_request`, `remote_get_country_form_schema`, `remote_get_custom_field_value`, `remote_list_countries`, `remote_list_country_holidays`, `remote_list_employments`, `remote_list_incentives`, `remote_list_recurring_incentives`, `remote_list_timeoffs`, `remote_update_employment` `data-sync` Added data sync support for employments, companies, company managers, custom fields, time off, time off types, timesheets, expenses, incentives, recurring incentives, payslips, payroll runs, contractor invoices, offboardings, benefit offers and countries, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Remote API exposes no updated-since filter a sync can use. `remote_list_benefit_offers`, `remote_list_companies`, `remote_list_company_managers`, `remote_list_contractor_invoices`, `remote_list_countries`, `remote_list_custom_fields`, `remote_list_employments`, `remote_list_expenses`, `remote_list_incentives`, `remote_list_offboardings`, `remote_list_payroll_runs`, `remote_list_payslips`, `remote_list_recurring_incentives`, `remote_list_timeoff_types`, `remote_list_timeoffs`, `remote_list_timesheets` `bug-fix` Documented that update_employment can set bank_account_details and billing_address_details only once per employment, as Remote returns 404 on a repeat write. `remote_update_employment` `bug-fix` Fixed update_employment so an employment can be unassigned from its department by sending an empty department_id (passed to Remote as null), and documented that update_expense rejects reason unless status is declined. `remote_update_employment`, `remote_update_expense` `bug-fix` `breaking` Breaking: update_expense no longer accepts reviewed_at or reviewer_id, and create_recurring_incentive duration_in_months is now a number. Fixed upload_file and incentive, expense, and offboarding inputs, and clarified employment and form schema descriptions. `remote_create_expense`, `remote_create_incentive`, `remote_create_offboarding`, `remote_create_recurring_incentive`, `remote_get_country_form_schema`, `remote_list_incentives`, `remote_update_employment`, `remote_update_expense`, `remote_upload_file` `new-actions` Added inbound webhook (events) support. StackOne now auto-provisions a Remote webhook callback on connect (covering the enabled events, via the Webhook Callbacks API) and removes it on disconnect, routing company, employment, contract, expense, offboarding, payslip, and time off events to your integration; includes a webhook events setup guide. # Render Source: https://docs.stackone.com/connectors/render/index How to set up the Render connector, plus the actions and events that are available.
Render
v1.2.0
98 actions · 63 events · 1 auth method
Infrastructure IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from your Render account settings to authenticate API requests. Optionally, configure receiving Events for Render into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/render/index.md for the full list. ## Events See https://docs.stackone.com/connectors/render/index.md for the full list. # Render Changelog Source: https://docs.stackone.com/connectors/render/changelog Release history for the Render connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added native webhook events. StackOne now creates one Render workspace webhook when an account connects, covering 62 event types across deploys, service availability, scaling, Postgres, Key Value and disks, and deletes it on disconnect. A new optional Webhook Workspace ID field selects the workspace; without it, the first workspace the API key can access is used. Render webhooks require a Pro plan or higher. `bug-fix` Corrected action inputs and descriptions against the Render OpenAPI spec. update_service_notification_override now exposes Render's real previewNotificationsEnabled values (default/true/false instead of the rejected enabled/disabled) and notificationsToSend as an enum including default. list_deploys replaces the rejected deploy_failed status with the accepted queued and update_failed. update_owner_notification_settings can now send emailEnabled and previewNotificationsEnabled as false. update_secret_file, update_env_var, update_env_vars and update_secret_files now state Render's key naming rule (letters, digits, _, - and . only, no leading digit, no slashes, not a single dot), which previously surfaced only as a 400 about environment variable keys. Gated seven actions to releaseStage preview after behavioural testing (AGI-9164) could not exercise them on the sandbox — restore_disk_snapshot, retrieve_job, cancel_job, retrieve_blueprint, update_blueprint, delete_blueprint and list_blueprint_syncs. verify_custom_domain returns an acknowledgement for Render's empty 202, and delete_environment maps Render's 5xx on a non-empty or last-remaining environment to a non-retryable 400. list_service_events now exposes all 43 event types Render accepts (was 22, missing suspender_added/removed, image_pull_failed, the disk-usage and maintenance events and others). Documented that create_service_preview is image-backed only (no pullRequestPreviewsEnabled precondition), that deployMode deploy_only cannot be combined with clearCache, commitId or imageUrl, that list_service_instances returns only instance id and createdAt and can answer a plain null, that a workspace cannot be muted by disabling every notification destination, and how to resolve ownerId and service-event triggeredByUser ids. `render_cancel_job`, `render_create_registry_credential`, `render_create_service_preview`, `render_delete_blueprint`, `render_delete_environment`, `render_list_blueprint_syncs`, `render_list_deploys`, `render_list_registry_credentials`, `render_list_service_events`, `render_list_service_instances`, `render_restore_disk_snapshot`, `render_retrieve_blueprint`, `render_retrieve_job`, `render_trigger_deploy`, `render_update_blueprint`, `render_update_env_var`, `render_update_env_vars`, `render_update_owner_notification_settings`, `render_update_secret_file`, `render_update_secret_files`, `render_update_service_autoscaling`, `render_update_service_notification_override`, `render_verify_custom_domain` `new-feature` `data-sync` Added DataSync support to eight list actions (services, projects, registry credentials, notification overrides, owners, and the unified IAM organizations, roles, and users lists), with incremental sync on services, projects, and registry credentials. list_registry_credentials now requests up to 100 credentials by default (the endpoint is single-page and previously returned the provider default of 20). `render_list_notification_overrides`, `render_list_owners`, `render_list_projects`, `render_list_registry_credentials`, `render_list_services`, `render_unified_list_organizations`, `render_unified_list_roles`, `render_unified_list_users` `bug-fix` Fixed unified IAM list users and get user failing with "Invalid compositeId, unknown identifier" on every call, and get user now returns 404 for an unknown user id instead of a server error. `render_unified_get_user`, `render_unified_list_users` `bug-fix` Fixed a JEXL parse error that crashed unified IAM list users on every call, an invalid composite-id role lookup, and unified IAM data-shape issues in credentials, roles, organizations, and user role fields. # Reo.dev Source: https://docs.stackone.com/connectors/reodev/index How to set up the Reo.dev connector, plus the actions that are available.
Reo.dev
Betav1.2.0
13 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Contact Reo.dev support to obtain your API key. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/reodev/index.md for the full list. # Reo.dev Changelog Source: https://docs.stackone.com/connectors/reodev/changelog Release history for the Reo.dev connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for segments, audiences, and custom lists, so these collections can now be periodically synced into StackOne. # Resend Source: https://docs.stackone.com/connectors/resend/index How to set up the Resend connector, plus the actions and events that are available.
Resend
Previewv0.3.2
38 actions · 20 events · 2 auth methods
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a secret API key as a bearer token. Keys can be scoped to full access or sending-only and optionally restricted to... Authorization code flow with PKCE. Requires registering an OAuth client with Resend. Scopes are either emails:send or fu... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/resend/index.md for the full list. ## Events See https://docs.stackone.com/connectors/resend/index.md for the full list. # Resend Changelog Source: https://docs.stackone.com/connectors/resend/changelog Release history for the Resend connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide-changes` Clarified the OAuth 2.0 connection guide — added a concrete curl example for registering the OAuth client (client_name, redirect_uris, grant_types, token_endpoint_auth_method), noted client_name is an example, explained that scopes are the space-separated scope field in the registration request body, and documented that public clients (token_endpoint_auth_method none) authenticate with PKCE alone so the Client Secret is not verified. `description-changes` Clarified action descriptions from behavioural QA — email scheduling eventual-consistency (retrieve/update/cancel 404s), contact custom-property keys must pre-exist, segment membership is not queryable, list_emails last_event values, and the verify_domain state machine. `resend_cancel_email`, `resend_create_contact`, `resend_list_broadcasts`, `resend_list_contacts`, `resend_list_emails`, `resend_list_segments`, `resend_retrieve_contact`, `resend_retrieve_email`, `resend_retrieve_segment`, `resend_update_contact`, `resend_update_email`, `resend_verify_domain` `new-actions` `webhook` Add native webhook event support for 20 event types across emails, contacts, domains and suppressions (Svix delivery, programmatic setup). `data-sync` Enable periodic DataSync for list_contacts, list_api_keys, list_domains and list_segments. `resend_list_api_keys`, `resend_list_contacts`, `resend_list_domains`, `resend_list_segments` `new-actions` Initial release covering emails, domains, api_keys, contacts, broadcasts, segments and suppressions. # Retool Source: https://docs.stackone.com/connectors/retool/index How to set up the Retool connector, plus the actions and events that are available.
Retool
Previewv1.3.0
55 actions · 1 event · 1 auth method
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Optionally, configure receiving Events for Retool into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/retool/index.md for the full list. ## Events See https://docs.stackone.com/connectors/retool/index.md for the full list. # Retool Changelog Source: https://docs.stackone.com/connectors/retool/changelog Release history for the Retool connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for users, user invites, groups, folders, workflows, resources, spaces, roles, custom component libraries, unified users, unified groups, unified roles and unified organizations, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the Retool API exposes no updated-since filter a sync can use. `retool_list_custom_component_libraries`, `retool_list_folders`, `retool_list_groups`, `retool_list_resources`, `retool_list_roles`, `retool_list_spaces`, `retool_list_user_invites`, `retool_list_users`, `retool_list_workflows`, `retool_unified_list_groups`, `retool_unified_list_organizations`, `retool_unified_list_roles`, `retool_unified_list_users` `bug-fix` User lists now include unclaimed, unexpired user invites with status pending (Retool Cloud or self-hosted 3.24.0+), and return 400 when Retool pages the invite list instead of dropping invites. `retool_unified_get_user`, `retool_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `retool_unified_delete_user`, `retool_unified_get_group`, `retool_unified_get_me`, `retool_unified_get_organization`, `retool_unified_get_role`, `retool_unified_get_user`, `retool_unified_list_groups`, `retool_unified_list_organizations`, `retool_unified_list_roles`, `retool_unified_list_users`, `retool_unified_update_user` `new-actions` Added unified IAM actions for users, groups, roles, organizations, and credentials. `retool_unified_delete_user`, `retool_unified_get_group`, `retool_unified_get_me`, `retool_unified_get_organization`, `retool_unified_get_role`, `retool_unified_get_user`, `retool_unified_list_groups`, `retool_unified_list_organizations`, `retool_unified_list_roles`, `retool_unified_list_users`, `retool_unified_update_user` `new-actions` Added inbound webhook (events) support — a Native Webhook URL and a generic event handler that receives events POSTed from a Retool workflow's HTTP block and emits them as retool.event; includes a webhook events setup guide. # Rijksmuseum Source: https://docs.stackone.com/connectors/rijksmuseum/index How to set up the Rijksmuseum connector, plus the actions that are available.
Rijksmuseum
v1.0.0
2 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No credentials required. The Rijksmuseum Data Services APIs are fully public and open access. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/rijksmuseum/index.md for the full list. # Rijksmuseum Changelog Source: https://docs.stackone.com/connectors/rijksmuseum/changelog Release history for the Rijksmuseum connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `improved-descriptions` Updated connection guide text for clarity. `bug-fix` Fixed search_collection sending undefined for optional imageAvailable parameter when omitted, causing 422 errors. `rijksmuseum_search_collection` `new-actions` Initial connector with Linked Art Search and Persistent Identifier Resolver via the public data.rijksmuseum.nl API. # Rillet Source: https://docs.stackone.com/connectors/rillet/index How to set up the Rillet connector, plus the actions that are available.
Rillet
Betav0.2.0
83 actions · 1 auth method
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires Rillet to enable API access for your organization before a key can be created. The key is a non-expiring bearer... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/rillet/index.md for the full list. # Rillet Changelog Source: https://docs.stackone.com/connectors/rillet/changelog Release history for the Rillet connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for accounts, bank accounts, bank transactions, bills, books, charges, contracts, credit memos, customers, custom fields, invoice payments, invoices, journal entries, products, reimbursements, subsidiaries, tax rates, vendor credits and vendors, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. Accounts, bank transactions, bills, charges, credit memos, customers, custom fields, invoice payments, invoices, journal entries, reimbursements, vendor credits and vendors sync incrementally using Rillet's updated-since filters; the rest are full-refresh, because their endpoints expose no updated-since filter a sync can use. `rillet_list_accounts`, `rillet_list_bank_accounts`, `rillet_list_bank_transactions`, `rillet_list_bills`, `rillet_list_books`, `rillet_list_charges`, `rillet_list_contracts`, `rillet_list_credit_memos`, `rillet_list_customers`, `rillet_list_fields`, `rillet_list_invoice_payments`, `rillet_list_invoices`, `rillet_list_journal_entries`, `rillet_list_products`, `rillet_list_reimbursements`, `rillet_list_subsidiaries`, `rillet_list_tax_rates`, `rillet_list_vendor_credits`, `rillet_list_vendors` `new-connector` Initial release of the Rillet connector with 83 actions covering the chart of accounts, custom fields, customers, products, contracts, AR invoices and payments, credit memos, vendors, vendor credits, AP bills and payments, charges, reimbursements, journal entries, bank accounts and transactions, tax rates, financial reports and organization discovery. # RingCentral Source: https://docs.stackone.com/connectors/ringcentral/index How to set up the RingCentral connector, plus the actions that are available.
RingCentral
Betav0.3.0
87 actions · 2 auth methods
Telephony Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating a REST API app in the RingCentral Developer Console with 3-legged OAuth and refresh tokens turned on.... Testing-only authentication method — accepts any placeholder value and performs NO credential validation against RingCen... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ringcentral/index.md for the full list. # RingCentral Changelog Source: https://docs.stackone.com/connectors/ringcentral/changelog Release history for the RingCentral connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Fixed connecting accounts with OAuth 2.0, and leaving Scopes empty now uses the permissions selected on your RingCentral app. `ringcentral_add_a2p_sms_opt_outs`, `ringcentral_address_book_bulk_upload`, `ringcentral_aggregate_a2p_sms_statuses`, `ringcentral_analytics_calls_aggregation_fetch`, `ringcentral_analytics_calls_timeline_fetch`, `ringcentral_archive_glip_team_new`, `ringcentral_assign_multiple_automatic_location_updates_users`, `ringcentral_bulk_add_devices_v2`, `ringcentral_bulk_delete_users_v2`, `ringcentral_create_a2p_sms_batch`, `ringcentral_create_call_out_call_session`, `ringcentral_create_conference_call_session`, `ringcentral_create_data_export_task_new`, `ringcentral_create_extension`, `ringcentral_create_fax_message`, `ringcentral_create_glip_team_new`, `ringcentral_create_message_store_report`, `ringcentral_create_mms`, `ringcentral_create_ring_out_call`, `ringcentral_create_sms_message`, `ringcentral_create_task_new`, `ringcentral_create_user_profile_image`, `ringcentral_delete_call_session`, `ringcentral_delete_message`, `ringcentral_delete_message_by_filter`, `ringcentral_delete_ring_out_call`, `ringcentral_delete_user_call_log`, `ringcentral_delete_user_profile_image`, `ringcentral_extension_bulk_update`, `ringcentral_favorite_glip_chat_new`, `ringcentral_get_address_book_bulk_upload_task`, `ringcentral_get_extension_bulk_update_task`, `ringcentral_get_video_meeting`, `ringcentral_list_administered_sites`, `ringcentral_list_call_queues`, `ringcentral_list_chat_tasks_new`, `ringcentral_list_company_active_calls`, `ringcentral_list_data_export_tasks_new`, `ringcentral_list_directory_entries`, `ringcentral_list_extension_active_calls`, `ringcentral_list_extension_devices`, `ringcentral_list_extensions`, `ringcentral_list_favorite_chats_new`, `ringcentral_list_favorite_contacts`, `ringcentral_list_glip_teams_new`, `ringcentral_list_messages`, `ringcentral_list_states`, `ringcentral_list_user_assigned_roles`, `ringcentral_list_user_roles`, `ringcentral_list_user_templates`, `ringcentral_list_video_meetings`, `ringcentral_patch_message`, `ringcentral_post_batch_provision_users`, `ringcentral_read_a2p_sms_opt_outs`, `ringcentral_read_automatic_location_updates_task`, `ringcentral_read_call_queue_presence`, `ringcentral_read_call_session_status`, `ringcentral_read_data_export_task_new`, `ringcentral_read_event_new`, `ringcentral_read_extension`, `ringcentral_read_extension_call_queue_presence`, `ringcentral_read_glip_events_new`, `ringcentral_read_message`, `ringcentral_read_message_store_configuration`, `ringcentral_read_message_store_report_task`, `ringcentral_read_ring_out_call_status`, `ringcentral_read_state`, `ringcentral_read_unified_presence`, `ringcentral_read_user_call_log`, `ringcentral_read_user_presence_status`, `ringcentral_read_user_profile_image`, `ringcentral_read_user_template`, `ringcentral_search_directory_entries`, `ringcentral_send_activation_email_v2`, `ringcentral_send_welcome_email_v2`, `ringcentral_unarchive_glip_team_new`, `ringcentral_update_call_queue_presence`, `ringcentral_update_extension_call_queue_presence`, `ringcentral_update_favorite_contact_list`, `ringcentral_update_message`, `ringcentral_update_message_store_configuration`, `ringcentral_update_unified_presence`, `ringcentral_update_user_administered_sites`, `ringcentral_update_user_assigned_roles`, `ringcentral_update_user_call_queues`, `ringcentral_update_user_presence_status`, `ringcentral_update_user_profile_image` `data-sync` Enabled Data Sync for extensions, call queues, user roles, directory entries, states and teams. `ringcentral_list_call_queues`, `ringcentral_list_directory_entries`, `ringcentral_list_extensions`, `ringcentral_list_glip_teams_new`, `ringcentral_list_states`, `ringcentral_list_user_roles` `new-connector` Initial action mapping of the RingCentral connector. # Rippling Source: https://docs.stackone.com/connectors/rippling/index How to set up the Rippling connector, plus the actions that are available.
Rippling
Previewv1.1.0
37 actions · 1 auth method
HRIS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Rippling account using an API token from the API Tokens app in Rippling Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/rippling/index.md for the full list. # Rippling Changelog Source: https://docs.stackone.com/connectors/rippling/changelog Release history for the Rippling connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to all 16 list actions, which sync by full refresh with cursor pagination handled automatically. Also exposed the limit page-size parameter where it was missing. # Rollbar Source: https://docs.stackone.com/connectors/rollbar/index How to set up the Rollbar connector, plus the actions and events that are available.
Rollbar
v1.2.0
25 actions · 8 events · 1 auth method
Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Account Access Tokens provide access to account-level operations including managing projects, teams, users, and invitati... Optionally, configure receiving Events for Rollbar into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/rollbar/index.md for the full list. ## Events See https://docs.stackone.com/connectors/rollbar/index.md for the full list. # Rollbar Changelog Source: https://docs.stackone.com/connectors/rollbar/changelog Release history for the Rollbar connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added webhook events for 8 Rollbar notification types (new, repeating, high-rate, resolved, reopened and reactivated items, plus deploys), set up automatically for a chosen project. `data-sync` Added periodic data sync for users, teams, and projects so their records can be pulled into StackOne and kept up to date by full refresh. `rollbar_list_projects`, `rollbar_list_teams`, `rollbar_list_users` `bug-fix` Rebuilt the Account Access Token connection guide from the live portal (corrected UI labels, added screenshots) and documented that list_team_projects can return stale references to deleted projects. # RT (Request Tracker) Source: https://docs.stackone.com/connectors/requesttracker/index How to set up the RT (Request Tracker) connector, plus the actions that are available.
RT (Request Tracker)
v1.1.0
24 actions · 1 auth method
Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with an RT auth token, sent in the Authorization header as \`token <TOKEN>\`. Requires RT 5.0+ with the built... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/requesttracker/index.md for the full list. # RT (Request Tracker) Changelog Source: https://docs.stackone.com/connectors/requesttracker/changelog Release history for the RT (Request Tracker) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support so tickets, queues, users, transactions, and custom fields stay continuously synced. `requesttracker_list_customfields`, `requesttracker_list_queues`, `requesttracker_list_transactions`, `requesttracker_list_users`, `requesttracker_search_tickets` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Standardized action category capitalization for more consistent portal filters. `requesttracker_comment_ticket`, `requesttracker_create_customfield`, `requesttracker_create_queue`, `requesttracker_create_ticket`, `requesttracker_delete_ticket`, `requesttracker_get_attachment`, `requesttracker_get_customfield`, `requesttracker_get_queue`, `requesttracker_get_queue_customfields`, `requesttracker_get_ticket`, `requesttracker_get_ticket_attachments`, `requesttracker_get_ticket_history`, `requesttracker_get_transaction`, `requesttracker_get_user`, `requesttracker_list_customfields`, `requesttracker_list_queues`, `requesttracker_list_transactions`, `requesttracker_list_users`, `requesttracker_reply_ticket`, `requesttracker_search_tickets`, `requesttracker_steal_ticket`, `requesttracker_take_ticket`, `requesttracker_untake_ticket`, `requesttracker_update_ticket` `description-fix` Clarified the Take Ticket action description so "assign it to me" requests are handled by the single self-assignment call instead of a user lookup plus ticket update. `requesttracker_take_ticket` `bug-fix` `guide` Fixed connection validation so an instance URL with a trailing slash no longer lets an invalid token connect, and clarified the connection guide. `requesttracker_comment_ticket`, `requesttracker_create_customfield`, `requesttracker_create_queue`, `requesttracker_create_ticket`, `requesttracker_delete_ticket`, `requesttracker_get_attachment`, `requesttracker_get_customfield`, `requesttracker_get_queue`, `requesttracker_get_queue_customfields`, `requesttracker_get_ticket`, `requesttracker_get_ticket_attachments`, `requesttracker_get_ticket_history`, `requesttracker_get_transaction`, `requesttracker_get_user`, `requesttracker_list_customfields`, `requesttracker_list_queues`, `requesttracker_list_transactions`, `requesttracker_list_users`, `requesttracker_reply_ticket`, `requesttracker_search_tickets`, `requesttracker_steal_ticket`, `requesttracker_take_ticket`, `requesttracker_untake_ticket`, `requesttracker_update_ticket` `new-connector` Initial RT (Request Tracker) connector — ticketing over the REST2 API. Covers tickets, queues, users, transactions, attachments, and custom fields. # Saba Source: https://docs.stackone.com/connectors/saba/index How to set up the Saba connector, plus the actions and events that are available.
Saba
Previewv1.3.0
122 actions · 10 events · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Certificate-based authentication for Saba Cloud API access Optionally, configure receiving Events for Saba into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/saba/index.md for the full list. ## Events See https://docs.stackone.com/connectors/saba/index.md for the full list. # Saba Changelog Source: https://docs.stackone.com/connectors/saba/changelog Release history for the Saba connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Added webhook events for Saba triggered notifications, with dedicated events for Course added to profile and seven compensation notifications and a generic Notification event for every other notification. Webhooks are set up manually in Saba with a Webhook Action per notification, and the connection guide covers the template and Content-Type header Saba needs. `data-sync` Added Data Sync support to 15 list actions, so courses, content inventory, content folders, task definitions, delivery modes, session templates, pricelists, enrollments and foundation data (facilities, locations, job families, job types, roles, competencies and locales) can be kept continuously in sync. The count and startPage inputs on list_content_inventory and list_content_folders now accept numbers, matching every other list action. `saba_find_content_inventory`, `saba_get_locales`, `saba_list_competencies`, `saba_list_content_folders`, `saba_list_content_inventory`, `saba_list_courses`, `saba_list_delivery_modes`, `saba_list_enrollments`, `saba_list_facilities`, `saba_list_job_families`, `saba_list_job_types`, `saba_list_locations`, `saba_list_pricelists`, `saba_list_roles`, `saba_list_session_templates`, `saba_list_tasks` `new-fields` `bug-fix` Added new optional fields (e.g. publish_to_catalog, group, learning-request and recurring-course attributes) across course, curriculum and task actions; fixed reference-field type mismatches (string to object), attendance learnerSessions type-wrapper/@type, and transcript credit/customValues array wrappers (transcript customValues is connector-wrapped in Saba's ["list", [...]] format so callers pass a plain array); corrected certification/curriculum customValues docs to clarify the provider expects a plain object there, not the list wrapper; made create_task securityDomain required; documented provider constraints (closed allowlists, read-only/auto-assigned fields, recurring-course-only attributes, post-delete GET-back behavior) and fixed description grammar. # Sage HR Source: https://docs.stackone.com/connectors/sagehr/index How to set up the Sage HR connector, plus the actions that are available.
Sage HR
v1.1.0
35 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Admin access is required to enable API access and generate API keys. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sagehr/index.md for the full list. # Sage HR Changelog Source: https://docs.stackone.com/connectors/sagehr/changelog Release history for the Sage HR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added Data Sync support so employee, leave, document and organization lists can be kept continuously in sync. `sagehr_delete_document`, `sagehr_get_document`, `sagehr_get_leave_allowances_report`, `sagehr_list_document_categories`, `sagehr_list_documents`, `sagehr_list_employees`, `sagehr_list_employees_out_of_office`, `sagehr_list_leave_policies`, `sagehr_list_leave_requests`, `sagehr_list_offboarding_categories`, `sagehr_list_onboarding_categories`, `sagehr_list_positions`, `sagehr_list_teams`, `sagehr_list_terminated_employees`, `sagehr_list_termination_reasons`, `sagehr_update_document` `bug-fix` Made update_employee work_start_date required and corrected document id and custom-field value descriptions. `sagehr_delete_document`, `sagehr_get_document`, `sagehr_update_document`, `sagehr_update_employee`, `sagehr_update_employee_custom_field` `bug-fix` Added screenshots to the API Key connection guide and clarified the Integrations to API navigation and the enable/disable API access states. # Sage People Source: https://docs.stackone.com/connectors/sagepeople/index How to set up the Sage People connector, plus the actions that are available.
Sage People
Betav1.0.1
8 actions · 2 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Standard Salesforce OAuth 2.0 authorization code flow. Requires an External Client App in the customer's Salesforce org... Salesforce username-password OAuth2 flow. Deprecated by Salesforce in 2023+ and disabled by default on new orgs; include... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sagepeople/index.md for the full list. # Sage People Changelog Source: https://docs.stackone.com/connectors/sagepeople/changelog Release history for the Sage People connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` Connections now use PKCE for Salesforce apps that require it, and always request refresh_token so a custom scope list cannot break sign-in. # Salesforce Source: https://docs.stackone.com/connectors/salesforce/index How to set up the Salesforce connector, plus the actions and events that are available.
Salesforce
v1.3.1
380 actions · 15 events · 1 auth method
CRM Customer Support Ticketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an External Client App in your Salesforce org. Uses PKCE and supports refresh token rotation. Optionally, configure receiving Events for Salesforce into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/salesforce/index.md for the full list. ## Events See https://docs.stackone.com/connectors/salesforce/index.md for the full list. # Salesforce Changelog Source: https://docs.stackone.com/connectors/salesforce/changelog Release history for the Salesforce connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Connections now work when a custom scope list leaves out refresh_token, and the setup guide explains Salesforce's Allow Access screen. `salesforce_abort_bulk_ingest_job`, `salesforce_abort_bulk_query_job`, `salesforce_activate_contract`, `salesforce_activate_order`, `salesforce_add_campaign_member`, `salesforce_add_group_member`, `salesforce_assign_permission_set`, `salesforce_assign_resource_to_appointment`, `salesforce_assign_topic_to_record`, `salesforce_complete_task`, `salesforce_composite_batch`, `salesforce_composite_graph`, `salesforce_create_account`, `salesforce_create_account_contact_role`, `salesforce_create_asset`, `salesforce_create_attachment`, `salesforce_create_bulk_ingest_job`, `salesforce_create_bulk_query_job`, `salesforce_create_campaign_member`, `salesforce_create_case`, `salesforce_create_case_comment`, `salesforce_create_contact`, `salesforce_create_contract`, `salesforce_create_email_message`, `salesforce_create_entitlement`, `salesforce_create_event`, `salesforce_create_feed_comment`, `salesforce_create_feed_item`, `salesforce_create_individual`, `salesforce_create_lead`, `salesforce_create_location`, `salesforce_create_note`, `salesforce_create_opportunity`, `salesforce_create_opportunity_contact_role`, `salesforce_create_opportunity_line_item`, `salesforce_create_order`, `salesforce_create_order_item`, `salesforce_create_partner`, `salesforce_create_pricebook`, `salesforce_create_pricebook_entry`, `salesforce_create_product`, `salesforce_create_return_order`, `salesforce_create_service_appointment`, `salesforce_create_service_contract`, `salesforce_create_service_resource`, `salesforce_create_solution`, `salesforce_create_task`, `salesforce_create_topic`, `salesforce_create_work_order`, `salesforce_create_work_order_line_item`, `salesforce_delete_account`, `salesforce_delete_account_contact_role`, `salesforce_delete_asset`, `salesforce_delete_attachment`, `salesforce_delete_bulk_ingest_job`, `salesforce_delete_bulk_query_job`, `salesforce_delete_campaign_member`, `salesforce_delete_case`, `salesforce_delete_case_comment`, `salesforce_delete_contact`, `salesforce_delete_content_document`, `salesforce_delete_content_document_link`, `salesforce_delete_contract`, `salesforce_delete_document`, `salesforce_delete_email_message`, `salesforce_delete_entitlement`, `salesforce_delete_event`, `salesforce_delete_feed_comment`, `salesforce_delete_feed_element`, `salesforce_delete_feed_item`, `salesforce_delete_individual`, `salesforce_delete_lead`, `salesforce_delete_location`, `salesforce_delete_note`, `salesforce_delete_opportunity`, `salesforce_delete_opportunity_contact_role`, `salesforce_delete_opportunity_line_item`, `salesforce_delete_order`, `salesforce_delete_order_item`, `salesforce_delete_partner`, `salesforce_delete_pricebook`, `salesforce_delete_pricebook_entry`, `salesforce_delete_product`, `salesforce_delete_return_order`, `salesforce_delete_service_contract`, `salesforce_delete_solution`, `salesforce_delete_task`, `salesforce_delete_topic`, `salesforce_delete_work_order`, `salesforce_describe_dashboard`, `salesforce_describe_global`, `salesforce_describe_quick_action`, `salesforce_describe_sobject`, `salesforce_download_attachment`, `salesforce_download_content_version`, `salesforce_download_document`, `salesforce_execute_composite_request`, `salesforce_execute_soql_query`, `salesforce_execute_sosl_search`, `salesforce_get_account`, `salesforce_get_account_history`, `salesforce_get_activity_history`, `salesforce_get_api_limits`, `salesforce_get_api_versions`, `salesforce_get_approval_layout`, `salesforce_get_approval_processes`, `salesforce_get_asset`, `salesforce_get_asset_hierarchy`, `salesforce_get_attachment`, `salesforce_get_bulk_ingest_job`, `salesforce_get_bulk_job_failed_results`, `salesforce_get_bulk_job_successful_results`, `salesforce_get_bulk_job_unprocessed_records`, `salesforce_get_bulk_query_job`, `salesforce_get_bulk_query_results`, `salesforce_get_business_hours`, `salesforce_get_campaign`, `salesforce_get_campaign_member`, `salesforce_get_campaign_statistics`, `salesforce_get_case`, `salesforce_get_case_comment`, `salesforce_get_case_history`, `salesforce_get_compact_layouts`, `salesforce_get_contact`, `salesforce_get_contact_history`, `salesforce_get_content_note`, `salesforce_get_content_version`, `salesforce_get_contract`, `salesforce_get_contract_history`, `salesforce_get_current_user`, `salesforce_get_dashboard`, `salesforce_get_dashboard_status`, `salesforce_get_default_business_hours`, `salesforce_get_document`, `salesforce_get_email_message`, `salesforce_get_email_template`, `salesforce_get_emails_for_record`, `salesforce_get_entitlement`, `salesforce_get_event`, `salesforce_get_events_for_contact`, `salesforce_get_feed_element`, `salesforce_get_feed_item`, `salesforce_get_folder`, `salesforce_get_forecast_by_category`, `salesforce_get_global_picklist_values`, `salesforce_get_group`, `salesforce_get_group_member`, `salesforce_get_holiday`, `salesforce_get_individual`, `salesforce_get_knowledge_article`, `salesforce_get_lead`, `salesforce_get_lead_history`, `salesforce_get_location`, `salesforce_get_milestone`, `salesforce_get_my_events`, `salesforce_get_my_tasks`, `salesforce_get_note`, `salesforce_get_open_activities`, `salesforce_get_opportunity`, `salesforce_get_opportunity_field_history`, `salesforce_get_opportunity_forecast_category`, `salesforce_get_opportunity_history`, `salesforce_get_opportunity_line_item`, `salesforce_get_opportunity_products_summary`, `salesforce_get_order`, `salesforce_get_order_item`, `salesforce_get_orders_for_account`, `salesforce_get_organization_info`, `salesforce_get_overdue_tasks`, `salesforce_get_page_layouts`, `salesforce_get_partner`, `salesforce_get_pipeline_by_stage`, `salesforce_get_pricebook`, `salesforce_get_pricebook_entry`, `salesforce_get_product`, `salesforce_get_product_pricing`, `salesforce_get_profile`, `salesforce_get_queue_sobjects`, `salesforce_get_recent_activities`, `salesforce_get_recently_viewed`, `salesforce_get_record_type`, `salesforce_get_record_type_by_name`, `salesforce_get_report`, `salesforce_get_return_order`, `salesforce_get_role_hierarchy`, `salesforce_get_service_appointment`, `salesforce_get_service_contract`, `salesforce_get_service_resource`, `salesforce_get_service_territory`, `salesforce_get_solution`, `salesforce_get_standard_pricebook`, `salesforce_get_tabs`, `salesforce_get_task`, `salesforce_get_tasks_due_today`, `salesforce_get_tasks_for_contact`, `salesforce_get_themes`, `salesforce_get_topic`, `salesforce_get_topics_for_record`, `salesforce_get_upcoming_events`, `salesforce_get_user`, `salesforce_get_user_permissions`, `salesforce_get_user_role`, `salesforce_get_users_in_group`, `salesforce_get_work_order`, `salesforce_like_feed_element`, `salesforce_link_solution_to_case`, `salesforce_list_account_contact_roles`, `salesforce_list_accounts`, `salesforce_list_active_opportunity_stages`, `salesforce_list_all_groups`, `salesforce_list_apex_actions`, `salesforce_list_assets`, `salesforce_list_assigned_resources`, `salesforce_list_attachments`, `salesforce_list_authorization_form_consents`, `salesforce_list_bulk_ingest_jobs`, `salesforce_list_bulk_query_jobs`, `salesforce_list_business_hours`, `salesforce_list_campaign_member_statuses`, `salesforce_list_campaign_members`, `salesforce_list_campaigns`, `salesforce_list_case_comments`, `salesforce_list_case_milestones`, `salesforce_list_case_solutions`, `salesforce_list_case_statuses`, `salesforce_list_cases`, `salesforce_list_chatter_groups`, `salesforce_list_contact_point_consents`, `salesforce_list_contacts`, `salesforce_list_content_documents`, `salesforce_list_content_versions`, `salesforce_list_contract_statuses`, `salesforce_list_contracts`, `salesforce_list_custom_invocable_actions`, `salesforce_list_dashboards`, `salesforce_list_data_category_groups`, `salesforce_list_documents`, `salesforce_list_email_message_relations`, `salesforce_list_email_messages`, `salesforce_list_email_templates`, `salesforce_list_entitlement_processes`, `salesforce_list_entitlements`, `salesforce_list_events`, `salesforce_list_feed_comments`, `salesforce_list_feed_items`, `salesforce_list_flow_actions`, `salesforce_list_folders`, `salesforce_list_group_members`, `salesforce_list_holidays`, `salesforce_list_individuals`, `salesforce_list_knowledge_articles`, `salesforce_list_lead_statuses`, `salesforce_list_leads`, `salesforce_list_locations`, `salesforce_list_milestones`, `salesforce_list_notes`, `salesforce_list_opportunities`, `salesforce_list_opportunity_contact_roles`, `salesforce_list_opportunity_line_items`, `salesforce_list_opportunity_stages`, `salesforce_list_order_items`, `salesforce_list_order_statuses`, `salesforce_list_orders`, `salesforce_list_org_wide_email_addresses`, `salesforce_list_partners`, `salesforce_list_periods`, `salesforce_list_permission_sets`, `salesforce_list_pricebook_entries`, `salesforce_list_pricebooks`, `salesforce_list_process_instance_steps`, `salesforce_list_process_instance_work_items`, `salesforce_list_process_instances`, `salesforce_list_products`, `salesforce_list_profiles`, `salesforce_list_public_case_comments`, `salesforce_list_public_groups`, `salesforce_list_queues`, `salesforce_list_quick_actions_global`, `salesforce_list_record_types`, `salesforce_list_report_instances`, `salesforce_list_reports`, `salesforce_list_return_order_line_items`, `salesforce_list_return_orders`, `salesforce_list_service_appointments`, `salesforce_list_service_contracts`, `salesforce_list_service_resources`, `salesforce_list_service_territories`, `salesforce_list_setup_audit_trail`, `salesforce_list_sobjects`, `salesforce_list_solution_statuses`, `salesforce_list_solutions`, `salesforce_list_task_statuses`, `salesforce_list_tasks`, `salesforce_list_topic_assignments`, `salesforce_list_topics`, `salesforce_list_user_licenses`, `salesforce_list_user_roles`, `salesforce_list_users`, `salesforce_list_users_by_profile`, `salesforce_list_users_by_role`, `salesforce_list_work_order_line_items`, `salesforce_list_work_order_statuses`, `salesforce_list_work_orders`, `salesforce_parameterized_search`, `salesforce_post_comment`, `salesforce_post_feed_element`, `salesforce_recall_approval`, `salesforce_refresh_dashboard`, `salesforce_remove_group_member`, `salesforce_remove_permission_set`, `salesforce_remove_topic_from_record`, `salesforce_run_report_async`, `salesforce_run_report_sync`, `salesforce_schedule_meeting`, `salesforce_search_accounts`, `salesforce_search_assets`, `salesforce_search_campaign_members`, `salesforce_search_campaigns`, `salesforce_search_cases`, `salesforce_search_contacts`, `salesforce_search_contracts`, `salesforce_search_knowledge_articles`, `salesforce_search_leads`, `salesforce_search_locations`, `salesforce_search_opportunities`, `salesforce_search_orders`, `salesforce_search_pricebook_entries`, `salesforce_search_solutions`, `salesforce_search_suggest_records`, `salesforce_search_topics`, `salesforce_search_users`, `salesforce_search_work_orders`, `salesforce_send_email`, `salesforce_sobject_collections_create`, `salesforce_sobject_collections_delete`, `salesforce_sobject_collections_update`, `salesforce_transfer_record_ownership`, `salesforce_unified_get_group`, `salesforce_unified_get_me`, `salesforce_unified_get_organization`, `salesforce_unified_get_role`, `salesforce_unified_get_user`, `salesforce_unified_list_groups`, `salesforce_unified_list_organizations`, `salesforce_unified_list_roles`, `salesforce_unified_list_users`, `salesforce_unlink_solution_from_case`, `salesforce_update_account`, `salesforce_update_account_contact_role`, `salesforce_update_asset`, `salesforce_update_campaign_member`, `salesforce_update_case`, `salesforce_update_case_comment`, `salesforce_update_contact`, `salesforce_update_contract`, `salesforce_update_entitlement`, `salesforce_update_event`, `salesforce_update_individual`, `salesforce_update_lead`, `salesforce_update_location`, `salesforce_update_note`, `salesforce_update_opportunity`, `salesforce_update_opportunity_contact_role`, `salesforce_update_opportunity_forecast_category`, `salesforce_update_opportunity_line_item`, `salesforce_update_order`, `salesforce_update_order_item`, `salesforce_update_pricebook`, `salesforce_update_pricebook_entry`, `salesforce_update_product`, `salesforce_update_return_order`, `salesforce_update_service_appointment`, `salesforce_update_service_contract`, `salesforce_update_service_resource`, `salesforce_update_solution`, `salesforce_update_task`, `salesforce_update_topic`, `salesforce_update_user`, `salesforce_update_work_order`, `salesforce_upload_bulk_job_data` `new-feature` Create and update actions for most records, including Cases, can now set your org's custom fields and record types. `salesforce_create_account`, `salesforce_create_asset`, `salesforce_create_campaign_member`, `salesforce_create_case`, `salesforce_create_contact`, `salesforce_create_contract`, `salesforce_create_email_message`, `salesforce_create_entitlement`, `salesforce_create_event`, `salesforce_create_individual`, `salesforce_create_lead`, `salesforce_create_location`, `salesforce_create_opportunity`, `salesforce_create_opportunity_contact_role`, `salesforce_create_opportunity_line_item`, `salesforce_create_order`, `salesforce_create_order_item`, `salesforce_create_pricebook`, `salesforce_create_pricebook_entry`, `salesforce_create_product`, `salesforce_create_return_order`, `salesforce_create_service_appointment`, `salesforce_create_service_contract`, `salesforce_create_service_resource`, `salesforce_create_solution`, `salesforce_create_task`, `salesforce_create_work_order`, `salesforce_create_work_order_line_item`, `salesforce_update_account`, `salesforce_update_asset`, `salesforce_update_campaign_member`, `salesforce_update_case`, `salesforce_update_contact`, `salesforce_update_contract`, `salesforce_update_entitlement`, `salesforce_update_event`, `salesforce_update_individual`, `salesforce_update_lead`, `salesforce_update_location`, `salesforce_update_opportunity`, `salesforce_update_opportunity_contact_role`, `salesforce_update_opportunity_line_item`, `salesforce_update_order`, `salesforce_update_order_item`, `salesforce_update_pricebook`, `salesforce_update_pricebook_entry`, `salesforce_update_product`, `salesforce_update_return_order`, `salesforce_update_service_appointment`, `salesforce_update_service_contract`, `salesforce_update_service_resource`, `salesforce_update_solution`, `salesforce_update_task`, `salesforce_update_user`, `salesforce_update_work_order` `auth` Connections now use PKCE, so Salesforce apps that require it (every External Client App created on or after 9 July 2026) can connect. `salesforce_abort_bulk_ingest_job`, `salesforce_abort_bulk_query_job`, `salesforce_activate_contract`, `salesforce_activate_order`, `salesforce_add_campaign_member`, `salesforce_add_group_member`, `salesforce_assign_permission_set`, `salesforce_assign_resource_to_appointment`, `salesforce_assign_topic_to_record`, `salesforce_complete_task`, `salesforce_composite_batch`, `salesforce_composite_graph`, `salesforce_create_account`, `salesforce_create_account_contact_role`, `salesforce_create_asset`, `salesforce_create_attachment`, `salesforce_create_bulk_ingest_job`, `salesforce_create_bulk_query_job`, `salesforce_create_campaign_member`, `salesforce_create_case`, `salesforce_create_case_comment`, `salesforce_create_contact`, `salesforce_create_contract`, `salesforce_create_email_message`, `salesforce_create_entitlement`, `salesforce_create_event`, `salesforce_create_feed_comment`, `salesforce_create_feed_item`, `salesforce_create_individual`, `salesforce_create_lead`, `salesforce_create_location`, `salesforce_create_note`, `salesforce_create_opportunity`, `salesforce_create_opportunity_contact_role`, `salesforce_create_opportunity_line_item`, `salesforce_create_order`, `salesforce_create_order_item`, `salesforce_create_partner`, `salesforce_create_pricebook`, `salesforce_create_pricebook_entry`, `salesforce_create_product`, `salesforce_create_return_order`, `salesforce_create_service_appointment`, `salesforce_create_service_contract`, `salesforce_create_service_resource`, `salesforce_create_solution`, `salesforce_create_task`, `salesforce_create_topic`, `salesforce_create_work_order`, `salesforce_create_work_order_line_item`, `salesforce_delete_account`, `salesforce_delete_account_contact_role`, `salesforce_delete_asset`, `salesforce_delete_attachment`, `salesforce_delete_bulk_ingest_job`, `salesforce_delete_bulk_query_job`, `salesforce_delete_campaign_member`, `salesforce_delete_case`, `salesforce_delete_case_comment`, `salesforce_delete_contact`, `salesforce_delete_content_document`, `salesforce_delete_content_document_link`, `salesforce_delete_contract`, `salesforce_delete_document`, `salesforce_delete_email_message`, `salesforce_delete_entitlement`, `salesforce_delete_event`, `salesforce_delete_feed_comment`, `salesforce_delete_feed_element`, `salesforce_delete_feed_item`, `salesforce_delete_individual`, `salesforce_delete_lead`, `salesforce_delete_location`, `salesforce_delete_note`, `salesforce_delete_opportunity`, `salesforce_delete_opportunity_contact_role`, `salesforce_delete_opportunity_line_item`, `salesforce_delete_order`, `salesforce_delete_order_item`, `salesforce_delete_partner`, `salesforce_delete_pricebook`, `salesforce_delete_pricebook_entry`, `salesforce_delete_product`, `salesforce_delete_return_order`, `salesforce_delete_service_contract`, `salesforce_delete_solution`, `salesforce_delete_task`, `salesforce_delete_topic`, `salesforce_delete_work_order`, `salesforce_describe_dashboard`, `salesforce_describe_global`, `salesforce_describe_quick_action`, `salesforce_describe_sobject`, `salesforce_download_attachment`, `salesforce_download_content_version`, `salesforce_download_document`, `salesforce_execute_composite_request`, `salesforce_execute_soql_query`, `salesforce_execute_sosl_search`, `salesforce_get_account`, `salesforce_get_account_history`, `salesforce_get_activity_history`, `salesforce_get_api_limits`, `salesforce_get_api_versions`, `salesforce_get_approval_layout`, `salesforce_get_approval_processes`, `salesforce_get_asset`, `salesforce_get_asset_hierarchy`, `salesforce_get_attachment`, `salesforce_get_bulk_ingest_job`, `salesforce_get_bulk_job_failed_results`, `salesforce_get_bulk_job_successful_results`, `salesforce_get_bulk_job_unprocessed_records`, `salesforce_get_bulk_query_job`, `salesforce_get_bulk_query_results`, `salesforce_get_business_hours`, `salesforce_get_campaign`, `salesforce_get_campaign_member`, `salesforce_get_campaign_statistics`, `salesforce_get_case`, `salesforce_get_case_comment`, `salesforce_get_case_history`, `salesforce_get_compact_layouts`, `salesforce_get_contact`, `salesforce_get_contact_history`, `salesforce_get_content_note`, `salesforce_get_content_version`, `salesforce_get_contract`, `salesforce_get_contract_history`, `salesforce_get_current_user`, `salesforce_get_dashboard`, `salesforce_get_dashboard_status`, `salesforce_get_default_business_hours`, `salesforce_get_document`, `salesforce_get_email_message`, `salesforce_get_email_template`, `salesforce_get_emails_for_record`, `salesforce_get_entitlement`, `salesforce_get_event`, `salesforce_get_events_for_contact`, `salesforce_get_feed_element`, `salesforce_get_feed_item`, `salesforce_get_folder`, `salesforce_get_forecast_by_category`, `salesforce_get_global_picklist_values`, `salesforce_get_group`, `salesforce_get_group_member`, `salesforce_get_holiday`, `salesforce_get_individual`, `salesforce_get_knowledge_article`, `salesforce_get_lead`, `salesforce_get_lead_history`, `salesforce_get_location`, `salesforce_get_milestone`, `salesforce_get_my_events`, `salesforce_get_my_tasks`, `salesforce_get_note`, `salesforce_get_open_activities`, `salesforce_get_opportunity`, `salesforce_get_opportunity_field_history`, `salesforce_get_opportunity_forecast_category`, `salesforce_get_opportunity_history`, `salesforce_get_opportunity_line_item`, `salesforce_get_opportunity_products_summary`, `salesforce_get_order`, `salesforce_get_order_item`, `salesforce_get_orders_for_account`, `salesforce_get_organization_info`, `salesforce_get_overdue_tasks`, `salesforce_get_page_layouts`, `salesforce_get_partner`, `salesforce_get_pipeline_by_stage`, `salesforce_get_pricebook`, `salesforce_get_pricebook_entry`, `salesforce_get_product`, `salesforce_get_product_pricing`, `salesforce_get_profile`, `salesforce_get_queue_sobjects`, `salesforce_get_recent_activities`, `salesforce_get_recently_viewed`, `salesforce_get_record_type`, `salesforce_get_record_type_by_name`, `salesforce_get_report`, `salesforce_get_return_order`, `salesforce_get_role_hierarchy`, `salesforce_get_service_appointment`, `salesforce_get_service_contract`, `salesforce_get_service_resource`, `salesforce_get_service_territory`, `salesforce_get_solution`, `salesforce_get_standard_pricebook`, `salesforce_get_tabs`, `salesforce_get_task`, `salesforce_get_tasks_due_today`, `salesforce_get_tasks_for_contact`, `salesforce_get_themes`, `salesforce_get_topic`, `salesforce_get_topics_for_record`, `salesforce_get_upcoming_events`, `salesforce_get_user`, `salesforce_get_user_permissions`, `salesforce_get_user_role`, `salesforce_get_users_in_group`, `salesforce_get_work_order`, `salesforce_like_feed_element`, `salesforce_link_solution_to_case`, `salesforce_list_account_contact_roles`, `salesforce_list_accounts`, `salesforce_list_active_opportunity_stages`, `salesforce_list_all_groups`, `salesforce_list_apex_actions`, `salesforce_list_assets`, `salesforce_list_assigned_resources`, `salesforce_list_attachments`, `salesforce_list_authorization_form_consents`, `salesforce_list_bulk_ingest_jobs`, `salesforce_list_bulk_query_jobs`, `salesforce_list_business_hours`, `salesforce_list_campaign_member_statuses`, `salesforce_list_campaign_members`, `salesforce_list_campaigns`, `salesforce_list_case_comments`, `salesforce_list_case_milestones`, `salesforce_list_case_solutions`, `salesforce_list_case_statuses`, `salesforce_list_cases`, `salesforce_list_chatter_groups`, `salesforce_list_contact_point_consents`, `salesforce_list_contacts`, `salesforce_list_content_documents`, `salesforce_list_content_versions`, `salesforce_list_contract_statuses`, `salesforce_list_contracts`, `salesforce_list_custom_invocable_actions`, `salesforce_list_dashboards`, `salesforce_list_data_category_groups`, `salesforce_list_documents`, `salesforce_list_email_message_relations`, `salesforce_list_email_messages`, `salesforce_list_email_templates`, `salesforce_list_entitlement_processes`, `salesforce_list_entitlements`, `salesforce_list_events`, `salesforce_list_feed_comments`, `salesforce_list_feed_items`, `salesforce_list_flow_actions`, `salesforce_list_folders`, `salesforce_list_group_members`, `salesforce_list_holidays`, `salesforce_list_individuals`, `salesforce_list_knowledge_articles`, `salesforce_list_lead_statuses`, `salesforce_list_leads`, `salesforce_list_locations`, `salesforce_list_milestones`, `salesforce_list_notes`, `salesforce_list_opportunities`, `salesforce_list_opportunity_contact_roles`, `salesforce_list_opportunity_line_items`, `salesforce_list_opportunity_stages`, `salesforce_list_order_items`, `salesforce_list_order_statuses`, `salesforce_list_orders`, `salesforce_list_org_wide_email_addresses`, `salesforce_list_partners`, `salesforce_list_periods`, `salesforce_list_permission_sets`, `salesforce_list_pricebook_entries`, `salesforce_list_pricebooks`, `salesforce_list_process_instance_steps`, `salesforce_list_process_instance_work_items`, `salesforce_list_process_instances`, `salesforce_list_products`, `salesforce_list_profiles`, `salesforce_list_public_case_comments`, `salesforce_list_public_groups`, `salesforce_list_queues`, `salesforce_list_quick_actions_global`, `salesforce_list_record_types`, `salesforce_list_report_instances`, `salesforce_list_reports`, `salesforce_list_return_order_line_items`, `salesforce_list_return_orders`, `salesforce_list_service_appointments`, `salesforce_list_service_contracts`, `salesforce_list_service_resources`, `salesforce_list_service_territories`, `salesforce_list_setup_audit_trail`, `salesforce_list_sobjects`, `salesforce_list_solution_statuses`, `salesforce_list_solutions`, `salesforce_list_task_statuses`, `salesforce_list_tasks`, `salesforce_list_topic_assignments`, `salesforce_list_topics`, `salesforce_list_user_licenses`, `salesforce_list_user_roles`, `salesforce_list_users`, `salesforce_list_users_by_profile`, `salesforce_list_users_by_role`, `salesforce_list_work_order_line_items`, `salesforce_list_work_order_statuses`, `salesforce_list_work_orders`, `salesforce_parameterized_search`, `salesforce_post_comment`, `salesforce_post_feed_element`, `salesforce_recall_approval`, `salesforce_refresh_dashboard`, `salesforce_remove_group_member`, `salesforce_remove_permission_set`, `salesforce_remove_topic_from_record`, `salesforce_run_report_async`, `salesforce_run_report_sync`, `salesforce_schedule_meeting`, `salesforce_search_accounts`, `salesforce_search_assets`, `salesforce_search_campaign_members`, `salesforce_search_campaigns`, `salesforce_search_cases`, `salesforce_search_contacts`, `salesforce_search_contracts`, `salesforce_search_knowledge_articles`, `salesforce_search_leads`, `salesforce_search_locations`, `salesforce_search_opportunities`, `salesforce_search_orders`, `salesforce_search_pricebook_entries`, `salesforce_search_solutions`, `salesforce_search_suggest_records`, `salesforce_search_topics`, `salesforce_search_users`, `salesforce_search_work_orders`, `salesforce_send_email`, `salesforce_sobject_collections_create`, `salesforce_sobject_collections_delete`, `salesforce_sobject_collections_update`, `salesforce_transfer_record_ownership`, `salesforce_unified_get_group`, `salesforce_unified_get_me`, `salesforce_unified_get_organization`, `salesforce_unified_get_role`, `salesforce_unified_get_user`, `salesforce_unified_list_groups`, `salesforce_unified_list_organizations`, `salesforce_unified_list_roles`, `salesforce_unified_list_users`, `salesforce_unlink_solution_from_case`, `salesforce_update_account`, `salesforce_update_account_contact_role`, `salesforce_update_asset`, `salesforce_update_campaign_member`, `salesforce_update_case`, `salesforce_update_case_comment`, `salesforce_update_contact`, `salesforce_update_contract`, `salesforce_update_entitlement`, `salesforce_update_event`, `salesforce_update_individual`, `salesforce_update_lead`, `salesforce_update_location`, `salesforce_update_note`, `salesforce_update_opportunity`, `salesforce_update_opportunity_contact_role`, `salesforce_update_opportunity_forecast_category`, `salesforce_update_opportunity_line_item`, `salesforce_update_order`, `salesforce_update_order_item`, `salesforce_update_pricebook`, `salesforce_update_pricebook_entry`, `salesforce_update_product`, `salesforce_update_return_order`, `salesforce_update_service_appointment`, `salesforce_update_service_contract`, `salesforce_update_service_resource`, `salesforce_update_solution`, `salesforce_update_task`, `salesforce_update_topic`, `salesforce_update_user`, `salesforce_update_work_order`, `salesforce_upload_bulk_job_data` `data-sync` Added scheduled data sync to seventeen reference list actions — organization details, opportunity stages, case, lead, order, solution, task, work order, and contract statuses, business hours, holidays, fiscal periods, milestone types, entitlement processes, user licenses, and org-wide email addresses — so these collections can be kept in sync and read back without calling Salesforce on every request. `salesforce_list_active_opportunity_stages`, `salesforce_list_business_hours`, `salesforce_list_case_statuses`, `salesforce_list_contract_statuses`, `salesforce_list_entitlement_processes`, `salesforce_list_holidays`, `salesforce_list_lead_statuses`, `salesforce_list_milestones`, `salesforce_list_opportunity_stages`, `salesforce_list_order_statuses`, `salesforce_list_org_wide_email_addresses`, `salesforce_list_periods`, `salesforce_list_solution_statuses`, `salesforce_list_task_statuses`, `salesforce_list_user_licenses`, `salesforce_list_work_order_statuses`, `salesforce_unified_list_organizations` `bug-fix` Fixed the IAM unified_get_me response — the embedded user status now returns the same value and source value pair the user actions already return, instead of a plain string. # Salesforce Marketing Cloud Source: https://docs.stackone.com/connectors/salesforcemc/index How to set up the Salesforce Marketing Cloud connector, plus the actions that are available.
Salesforce Marketing Cloud
Previewv1.3.0
57 actions · 1 auth method
Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Salesforce Marketing Cloud account using OAuth 2.0 client credentials. Requires an Installed Package with a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/salesforcemc/index.md for the full list. # Salesforce Marketing Cloud Changelog Source: https://docs.stackone.com/connectors/salesforcemc/changelog Release history for the Salesforce Marketing Cloud connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added identity and access actions to list and look up the account users who sign in to Marketing Cloud with their roles, list and look up business units, and read the connection's own identity and scopes. `salesforcemc_unified_get_me`, `salesforcemc_unified_get_organization`, `salesforcemc_unified_get_user`, `salesforcemc_unified_list_organizations`, `salesforcemc_unified_list_users` `data-sync` `new-feature` Enabled scheduled data sync on five list actions: Get Assets, Get Categories, Get Campaigns, Search Journeys and Get All Attribute Set Definitions. These collections can now be kept in sync and read without calling Marketing Cloud on every request. All five refresh in full each run, because no eligible endpoint exposes an updated-since filter. Search Contacts is not included: the endpoint ignores page and pageSize as both query and body parameters, so a sync could not read past the first 50 contacts. Get Audit Events and Get Security Events are not included either, because neither returned any records to verify the mapping against. `salesforcemc_get_all_attribute_set_definitions`, `salesforcemc_get_assets`, `salesforcemc_get_campaigns`, `salesforcemc_get_categories`, `salesforcemc_search_journeys` `new-actions` Added actions for querying Data Extensions data — get_data_extension_rows (by ID) and get_data_extension_rows_by_key (by external key) with support for pagination, filtering, sorting, and field selection. # Salesforce Service Cloud Source: https://docs.stackone.com/connectors/salesforceservicecloud/index How to set up the Salesforce Service Cloud connector, plus the actions that are available.
Salesforce Service Cloud
Previewv3.0.0
52 actions · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an External Client App in your Salesforce org. Uses PKCE and supports refresh token rotation. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/salesforceservicecloud/index.md for the full list. # Salesforce Service Cloud Changelog Source: https://docs.stackone.com/connectors/salesforceservicecloud/changelog Release history for the Salesforce Service Cloud connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `breaking` Added eighteen actions for looking up and creating business hours, pricebooks, record types, email messages, social posts, users, contacts, email templates and activities, so IDs referenced by cases, work orders and service contracts can now be discovered rather than guessed. Fields that Salesforce does not expose on the underlying object have been removed, and Case now accepts RecordTypeId so callers can set the record type that drives page layout and picklist values. Case also accepts AssetId, EntitlementId, ServiceContractId and BusinessHoursId, each with the lookup action that supplies a valid id. Email message subject and body are documented as optional, matching what Salesforce actually accepts. `salesforceservicecloud_create_business_hours`, `salesforceservicecloud_create_email_message`, `salesforceservicecloud_create_pricebook`, `salesforceservicecloud_create_record_type`, `salesforceservicecloud_create_social_post`, `salesforceservicecloud_list_activities`, `salesforceservicecloud_list_available_record_types`, `salesforceservicecloud_list_business_hours`, `salesforceservicecloud_list_contacts`, `salesforceservicecloud_list_email_messages`, `salesforceservicecloud_list_email_templates`, `salesforceservicecloud_list_outbound_social_accounts`, `salesforceservicecloud_list_pricebooks`, `salesforceservicecloud_list_record_types`, `salesforceservicecloud_list_sla_processes`, `salesforceservicecloud_list_social_personas`, `salesforceservicecloud_list_social_posts`, `salesforceservicecloud_list_users` `salesforceservicecloud_create_case`, `salesforceservicecloud_create_case_comment`, `salesforceservicecloud_create_entitlement`, `salesforceservicecloud_create_knowledge_article`, `salesforceservicecloud_create_service_contract`, `salesforceservicecloud_create_work_order`, `salesforceservicecloud_delete_case`, `salesforceservicecloud_delete_case_comment`, `salesforceservicecloud_delete_entitlement`, `salesforceservicecloud_delete_knowledge_article`, `salesforceservicecloud_delete_service_contract`, `salesforceservicecloud_delete_work_order`, `salesforceservicecloud_get_case`, `salesforceservicecloud_get_case_comment`, `salesforceservicecloud_get_entitlement`, `salesforceservicecloud_get_knowledge_article`, `salesforceservicecloud_get_service_contract`, `salesforceservicecloud_get_work_order`, `salesforceservicecloud_list_case_comments`, `salesforceservicecloud_list_cases`, `salesforceservicecloud_list_entitlements`, `salesforceservicecloud_list_knowledge_articles`, `salesforceservicecloud_list_service_contracts`, `salesforceservicecloud_list_work_orders`, `salesforceservicecloud_publish_knowledge_article`, `salesforceservicecloud_search_cases`, `salesforceservicecloud_search_knowledge_articles`, `salesforceservicecloud_search_work_orders`, `salesforceservicecloud_update_case`, `salesforceservicecloud_update_case_comment`, `salesforceservicecloud_update_entitlement`, `salesforceservicecloud_update_knowledge_article`, `salesforceservicecloud_update_service_contract`, `salesforceservicecloud_update_work_order` `new-actions` `breaking` Cases, entitlements, service contracts, work orders and knowledge articles can now be kept continuously in sync. Listing these records now accepts a last-modified filter, and paging through them returns a stable, repeatable order. `salesforceservicecloud_list_cases`, `salesforceservicecloud_list_entitlements`, `salesforceservicecloud_list_knowledge_articles`, `salesforceservicecloud_list_service_contracts`, `salesforceservicecloud_list_work_orders` `auth` Connections now use PKCE, so Salesforce apps that require it (every External Client App created on or after 9 July 2026) can connect. # Salesloft Source: https://docs.stackone.com/connectors/salesloft/index How to set up the Salesloft connector, plus the actions that are available.
Salesloft
v2.0.1
69 actions · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Salesloft API key for direct authentication. Suitable for personal integrations and testing. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/salesloft/index.md for the full list. # Salesloft Changelog Source: https://docs.stackone.com/connectors/salesloft/changelog Release history for the Salesloft connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Role lists now return the Admin and User roles once, after the last custom role, at any page size, instead of on the first page only, where they pushed custom roles out at small page sizes. `salesloft_unified_list_roles`, `salesloft_unified_list_users` `breaking-changes` `new-actions` `data-sync` `bug-fix` Added sixteen actions covering tags, account stages and tiers, custom fields, call dispositions and sentiments, cadence steps, cadence actions, call data records and imports, most of them syncable. Removed filter and body fields that Salesloft accepts but never applies, and task_type is now required when creating a task. `salesloft_create_a_call_data_record`, `salesloft_create_a_custom_field`, `salesloft_create_an_import`, `salesloft_delete_a_custom_field`, `salesloft_delete_an_import`, `salesloft_list_account_stages`, `salesloft_list_account_tiers`, `salesloft_list_actions`, `salesloft_list_cadence_steps`, `salesloft_list_call_data_records`, `salesloft_list_call_dispositions`, `salesloft_list_call_sentiments`, `salesloft_list_custom_fields`, `salesloft_list_email_template_attachments`, `salesloft_list_imports`, `salesloft_list_tags` `salesloft_create_a_cadence_import`, `salesloft_create_a_call`, `salesloft_create_a_note`, `salesloft_create_a_person`, `salesloft_create_a_task`, `salesloft_create_an_account`, `salesloft_create_an_email_template`, `salesloft_list_accounts`, `salesloft_list_activity_histories`, `salesloft_list_cadence_memberships`, `salesloft_list_cadences`, `salesloft_list_calls`, `salesloft_list_email_templates`, `salesloft_list_notes`, `salesloft_list_people`, `salesloft_list_person_stages`, `salesloft_list_tasks`, `salesloft_list_users`, `salesloft_update_a_person`, `salesloft_update_a_task`, `salesloft_update_an_account`, `salesloft_update_an_email_template` `bug-fix` Fixed unified user, group, member and role lookups failing with an error, and unified lists breaking whenever there is more than one page of results. `salesloft_unified_get_group`, `salesloft_unified_get_role`, `salesloft_unified_get_user`, `salesloft_unified_list_groups`, `salesloft_unified_list_resource_users`, `salesloft_unified_list_roles`, `salesloft_unified_list_users` `bug-fix` Documented the accepted values for call dispositions and sentiments, email template merge tags, and cadence import steps so requests succeed on the first attempt. `salesloft_create_a_cadence_import`, `salesloft_create_a_call`, `salesloft_create_a_person`, `salesloft_create_an_email_template`, `salesloft_list_accounts`, `salesloft_list_cadences`, `salesloft_list_calls`, `salesloft_list_people`, `salesloft_list_tasks` `data-sync` Added data sync support for accounts, people, tasks, notes, calls, cadences, email templates, users, and roles. `salesloft_auth_test`, `salesloft_list_accounts`, `salesloft_list_activity_histories`, `salesloft_list_cadence_memberships`, `salesloft_list_cadences`, `salesloft_list_calls`, `salesloft_list_email_templates`, `salesloft_list_notes`, `salesloft_list_people`, `salesloft_list_person_stages`, `salesloft_list_tasks`, `salesloft_list_users`, `salesloft_unified_get_group`, `salesloft_unified_get_me`, `salesloft_unified_get_organization`, `salesloft_unified_get_role`, `salesloft_unified_get_user`, `salesloft_unified_list_groups`, `salesloft_unified_list_organizations`, `salesloft_unified_list_resource_types`, `salesloft_unified_list_resource_users`, `salesloft_unified_list_roles`, `salesloft_unified_list_users` `bug-fix` Fixed role lookups crashing instead of returning a not-found error. `salesloft_auth_test`, `salesloft_unified_get_me`, `salesloft_unified_get_role`, `salesloft_unified_list_groups`, `salesloft_unified_list_organizations`, `salesloft_unified_list_resource_users`, `salesloft_unified_list_roles`, `salesloft_unified_list_users` `guide` Corrected the API Key connection guide to require signing in to the Developer Portal, removed the inaccurate scroll and single-view claims, and shortened the API Key field description. Added portal screenshots to the guide steps. `new-actions` `bug-fix` Added create/delete cadence membership actions; added ids and updated_at filters to list cadence memberships. `salesloft_create_a_cadence_membership`, `salesloft_delete_a_cadence_membership` `salesloft_create_a_cadence_import`, `salesloft_create_a_person`, `salesloft_create_a_task`, `salesloft_create_an_account`, `salesloft_create_an_email_template`, `salesloft_list_activity_histories`, `salesloft_list_cadence_memberships`, `salesloft_list_people`, `salesloft_list_tasks`, `salesloft_update_a_person`, `salesloft_update_a_task` `new-actions` Added unified IAM actions for users, groups, organizations, roles, credentials, and resource users. # Sanity Source: https://docs.stackone.com/connectors/sanity/index How to set up the Sanity connector, plus the actions and events that are available.
Sanity
v1.2.0
33 actions · 3 events · 2 auth methods
CMS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect with a Sanity project robot token (project > API > Tokens) with the Editor, Access Manager, and Blueprints Deplo... Recommended for multi-user apps acting on behalf of Sanity users. Requires OAuth client credentials that Sanity provisio... Optionally, configure receiving Events for Sanity into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sanity/index.md for the full list. ## Events See https://docs.stackone.com/connectors/sanity/index.md for the full list. # Sanity Changelog Source: https://docs.stackone.com/connectors/sanity/changelog Release history for the Sanity connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `guide` Added webhook events for document created, updated, and deleted, with the Sanity webhook created automatically on connect. Updated the API token guide to the new multi-select permissions, including Blueprints Deployer, which webhook events require. `new-feature` Added DataSync support to list_projects, list_datasets, list_roles, list_access_permissions, list_access_users, and list_invites, so their records can be synced into StackOne on a schedule. All refresh in full each run, since Sanity exposes no change filter for these endpoints. # SAP Fieldglass Source: https://docs.stackone.com/connectors/fieldglass/index How to set up the SAP Fieldglass connector, plus the actions that are available.
SAP Fieldglass
Betav1.1.0
15 actions · 1 auth method
Vendor Management System Analytics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with SAP Fieldglass using the OAuth 2.0 client-credentials flow. The Client ID is a valid SAP Fieldglass us... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/fieldglass/index.md for the full list. # SAP Fieldglass Changelog Source: https://docs.stackone.com/connectors/fieldglass/changelog Release history for the SAP Fieldglass connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for the three all-optional collection actions - retrieve_all_work_items_for_approval (pending-approval work items), get_all_reports (Business Analytics report catalog), and list_odata_providers (OData analytic providers) - so each can be harvested on a schedule. Approvals syncs with offset pagination over its documented limit and offset parameters, which are now exposed as optional inputs on both approvals list actions; the other two are single-call full-refresh. Every action's resources link now points at its own SAP Help Portal operation page, and the connector-level link at the REST API overview page, instead of the product landing page, and the module_id, for_user and OData $top field descriptions - plus the approvals action details, which had presented the nested Attributes fields as top-level siblings - were corrected against those pages. All 15 actions now inherit the connector's beta release stage instead of each declaring releaseStage preview. # SAP S/4HANA Source: https://docs.stackone.com/connectors/saps4hana/index How to set up the SAP S/4HANA connector, plus the actions that are available.
SAP S/4HANA
Betav1.1.0
117 actions · 1 auth method
ERP
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 client credentials issued by an SAP S/4HANA Cloud Public Edition Communication Arrangement. Requ... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/saps4hana/index.md for the full list. # SAP S/4HANA Changelog Source: https://docs.stackone.com/connectors/saps4hana/changelog Release history for the SAP S/4HANA connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added data sync support for business partner, product, and sales order list endpoints. # SAP SuccessFactors Source: https://docs.stackone.com/connectors/sapsuccessfactors/index How to set up the SAP SuccessFactors connector, plus the actions that are available.
SAP SuccessFactors
v3.0.0
120 actions · 1 auth method
HRIS ATS LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 with client credentials grant type. Requires Admin access to SAP SuccessFactors Admin Center to... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sapsuccessfactors/index.md for the full list. # SAP SuccessFactors Changelog Source: https://docs.stackone.com/connectors/sapsuccessfactors/changelog Release history for the SAP SuccessFactors connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `new-actions` `bug-fix` Renames list_bank_details to list_payment_information_details and removes or requires some inputs on job, employment, personal, relationship and time-balance actions (breaking). Adds attachment, job location, requisition template, learning history and completion, pay scale level and time account actions, field selection and sorting on most list and get actions, and corrected field, code and ID guidance in action descriptions. `sapsuccessfactors_create_attachment`, `sapsuccessfactors_create_job_location`, `sapsuccessfactors_delete_job_location`, `sapsuccessfactors_list_job_requisition_templates`, `sapsuccessfactors_list_learning_history`, `sapsuccessfactors_list_pay_scale_levels`, `sapsuccessfactors_list_payment_information_details`, `sapsuccessfactors_list_time_accounts`, `sapsuccessfactors_record_external_learning_event`, `sapsuccessfactors_record_learning_event` `sapsuccessfactors_list_bank_details` `sapsuccessfactors_assign_learning_item`, `sapsuccessfactors_create_candidate`, `sapsuccessfactors_create_employee_time`, `sapsuccessfactors_create_job_application`, `sapsuccessfactors_create_job_requisition`, `sapsuccessfactors_create_learning_user`, `sapsuccessfactors_create_ocn_completion`, `sapsuccessfactors_create_ocn_course`, `sapsuccessfactors_create_user`, `sapsuccessfactors_create_user_course_assignment`, `sapsuccessfactors_delete_employee_time`, `sapsuccessfactors_generate_next_person_id`, `sapsuccessfactors_get_available_time_type`, `sapsuccessfactors_get_candidate`, `sapsuccessfactors_get_compensation_record`, `sapsuccessfactors_get_country`, `sapsuccessfactors_get_employee_address`, `sapsuccessfactors_get_employee_personal_details`, `sapsuccessfactors_get_employee_personal_info`, `sapsuccessfactors_get_employee_time`, `sapsuccessfactors_get_employment`, `sapsuccessfactors_get_employment_termination`, `sapsuccessfactors_get_entity_metadata`, `sapsuccessfactors_get_job_application`, `sapsuccessfactors_get_job_location`, `sapsuccessfactors_get_job_offer`, `sapsuccessfactors_get_job_record`, `sapsuccessfactors_get_job_requisition`, `sapsuccessfactors_get_legacy_picklist`, `sapsuccessfactors_get_person_email`, `sapsuccessfactors_get_person_phone`, `sapsuccessfactors_get_person_relationship`, `sapsuccessfactors_get_person_type`, `sapsuccessfactors_get_photo`, `sapsuccessfactors_get_picklist`, `sapsuccessfactors_get_picklist_value`, `sapsuccessfactors_get_position`, `sapsuccessfactors_get_user`, `sapsuccessfactors_list_available_time_types`, `sapsuccessfactors_list_benefit_enrollments`, `sapsuccessfactors_list_benefit_programs`, `sapsuccessfactors_list_benefits`, `sapsuccessfactors_list_business_units`, `sapsuccessfactors_list_calibration_sessions`, `sapsuccessfactors_list_candidate_education`, `sapsuccessfactors_list_candidate_work_experience`, `sapsuccessfactors_list_candidates`, `sapsuccessfactors_list_companies`, `sapsuccessfactors_list_compensation_records`, `sapsuccessfactors_list_competencies`, `sapsuccessfactors_list_cost_centers`, `sapsuccessfactors_list_countries`, `sapsuccessfactors_list_departments`, `sapsuccessfactors_list_employee_addresses`, `sapsuccessfactors_list_employee_awards`, `sapsuccessfactors_list_employee_education`, `sapsuccessfactors_list_employee_languages`, `sapsuccessfactors_list_employee_person_info`, `sapsuccessfactors_list_employee_personal_details`, `sapsuccessfactors_list_employee_time`, `sapsuccessfactors_list_employee_work_experience`, `sapsuccessfactors_list_employment_terminations`, `sapsuccessfactors_list_employments`, `sapsuccessfactors_list_event_reasons`, `sapsuccessfactors_list_goal_plan_templates`, `sapsuccessfactors_list_goals`, `sapsuccessfactors_list_holiday_calendars`, `sapsuccessfactors_list_interviews`, `sapsuccessfactors_list_job_applications`, `sapsuccessfactors_list_job_codes`, `sapsuccessfactors_list_job_locations`, `sapsuccessfactors_list_job_offers`, `sapsuccessfactors_list_job_records`, `sapsuccessfactors_list_job_requisitions`, `sapsuccessfactors_list_learning_courses`, `sapsuccessfactors_list_learning_users`, `sapsuccessfactors_list_legacy_picklist`, `sapsuccessfactors_list_legacy_picklist_options`, `sapsuccessfactors_list_ocn_sources`, `sapsuccessfactors_list_one_time_payments`, `sapsuccessfactors_list_pay_grades`, `sapsuccessfactors_list_person_emails`, `sapsuccessfactors_list_person_phones`, `sapsuccessfactors_list_person_relationships`, `sapsuccessfactors_list_person_types`, `sapsuccessfactors_list_photos`, `sapsuccessfactors_list_picklist_values`, `sapsuccessfactors_list_picklists`, `sapsuccessfactors_list_positions`, `sapsuccessfactors_list_recurring_pay_components`, `sapsuccessfactors_list_skills`, `sapsuccessfactors_list_talent_pools`, `sapsuccessfactors_list_time_account_balances`, `sapsuccessfactors_list_time_account_types`, `sapsuccessfactors_list_users`, `sapsuccessfactors_list_workflow_requests`, `sapsuccessfactors_list_workflow_steps`, `sapsuccessfactors_unassign_learning_item`, `sapsuccessfactors_update_user`, `sapsuccessfactors_upsert_address`, `sapsuccessfactors_upsert_candidate`, `sapsuccessfactors_upsert_employment`, `sapsuccessfactors_upsert_job`, `sapsuccessfactors_upsert_job_application`, `sapsuccessfactors_upsert_learning_user`, `sapsuccessfactors_upsert_person`, `sapsuccessfactors_upsert_person_email`, `sapsuccessfactors_upsert_person_phone`, `sapsuccessfactors_upsert_person_relationship`, `sapsuccessfactors_upsert_personal` `breaking` `bug-fix` `auth` `guide` Employee sorting now accepts only server-sortable fields (breaking change for callers passing a free-text sort); write actions have corrected date, country, and picklist-code guidance with clearer error messages; adds full-refresh Data Sync across HR, recruiting, foundation, payroll, time, and learning list actions; and refreshes the OAuth connection setup guide. # SD Worx Source: https://docs.stackone.com/connectors/sdworx/index How to set up the SD Worx connector, plus the actions that are available.
SD Worx
Betav0.2.0
76 actions · 2 auth methods
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). SD Worx Cobra API uses OAuth 2.0 authorization code flow for user-delegated access. SD Worx Cobra API uses OAuth 2.0 client credentials for server-to-server access. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sdworx/index.md for the full list. # SD Worx Changelog Source: https://docs.stackone.com/connectors/sdworx/changelog Release history for the SD Worx connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for all 23 list actions with offset pagination `sdworx_list_calculated_salary_components`, `sdworx_list_companies`, `sdworx_list_cost_center_allocations`, `sdworx_list_current_employments`, `sdworx_list_departments`, `sdworx_list_functions`, `sdworx_list_lease_cars`, `sdworx_list_leave_entitlements`, `sdworx_list_org_chart`, `sdworx_list_organizations`, `sdworx_list_payrolls`, `sdworx_list_person_contacts`, `sdworx_list_person_contracts`, `sdworx_list_person_documents`, `sdworx_list_person_leave_entitlements`, `sdworx_list_person_leave_hours`, `sdworx_list_person_leaves`, `sdworx_list_person_salaries`, `sdworx_list_person_time_schedules`, `sdworx_list_persons`, `sdworx_list_runs`, `sdworx_list_salary_components`, `sdworx_list_salary_employments` `new-actions` Initial release # SEC EDGAR Source: https://docs.stackone.com/connectors/secedgar/index How to set up the SEC EDGAR connector, plus the actions that are available.
SEC EDGAR
v1.0.0
7 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). SEC EDGAR is a free public API. No authentication credentials are required, but a User-Agent header identifying your org... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/secedgar/index.md for the full list. # Segment Source: https://docs.stackone.com/connectors/segment/index How to set up the Segment connector, plus the actions that are available.
Segment
Betav1.0.0
61 actions · 1 auth method
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Segment is a customer data platform for collecting, unifying, and routing customer event data. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/segment/index.md for the full list. # Semrush Source: https://docs.stackone.com/connectors/semrush/index How to set up the Semrush connector, plus the actions that are available.
Semrush
Betav1.1.0
20 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a per-account API key passed as a query parameter. API units are consumed per request and expire at the end of each... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/semrush/index.md for the full list. # Semrush Changelog Source: https://docs.stackone.com/connectors/semrush/changelog Release history for the Semrush connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for 12 list and collection actions across domain analytics, keyword analytics, backlinks, traffic analytics, and projects. # SendGrid Source: https://docs.stackone.com/connectors/sendgrid/index How to set up the SendGrid connector, plus the actions that are available.
SendGrid
v1.3.1
110 actions · 1 auth method
Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from your SendGrid account settings with appropriate scopes for the operations you need. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sendgrid/index.md for the full list. # SendGrid Changelog Source: https://docs.stackone.com/connectors/sendgrid/changelog Release history for the SendGrid connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists no longer skip teammates or repeat pending invitations across pages; they read up to 1,500 teammates and all pending invitations, and leave out expired invitations. `sendgrid_unified_get_user`, `sendgrid_unified_list_users` `bug-fix` `description-fix` Fifteen actions that SendGrid answers with an empty body now return an explicit success confirmation, so callers can tell a completed delete, resend or send from a silent no-op. Deleting a list still returns the job_id when delete_contacts starts an asynchronous contact deletion. Send Email now states that the from address must be a verified sender or an authenticated domain, and names the actions that find one. `sendgrid_delete_api_key`, `sendgrid_delete_blocks`, `sendgrid_delete_bounces`, `sendgrid_delete_design`, `sendgrid_delete_invalid_emails`, `sendgrid_delete_list`, `sendgrid_delete_segment`, `sendgrid_delete_single_send`, `sendgrid_delete_spam_reports`, `sendgrid_delete_suppression_group`, `sendgrid_delete_template`, `sendgrid_delete_template_version`, `sendgrid_delete_verified_sender`, `sendgrid_resend_verification_email`, `sendgrid_send_email` `new-feature` `data-sync` Ten list actions can now be synced with Data Sync, covering designs, prebuilt designs, marketing lists, single sends, single send search, API keys, authenticated domains, teammates, segments and verified senders. The five cursor-paginated actions also return a new next result key holding the bare page token. `sendgrid_list_all_lists`, `sendgrid_list_api_keys`, `sendgrid_list_authenticated_domains`, `sendgrid_list_designs`, `sendgrid_list_prebuilt_designs`, `sendgrid_list_segments`, `sendgrid_list_single_sends`, `sendgrid_list_teammates`, `sendgrid_list_verified_senders`, `sendgrid_search_single_sends` `bug-fix` Fixed user and group lookups returning the wrong error for unmatched records, corrected documentation for group permission scopes, and fixed the connection's identity name occasionally showing blank when the account had an empty email or username. `sendgrid_unified_get_group`, `sendgrid_unified_get_me`, `sendgrid_unified_get_role`, `sendgrid_unified_get_user`, `sendgrid_unified_list_groups`, `sendgrid_unified_list_organizations`, `sendgrid_unified_list_roles`, `sendgrid_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, and credentials (preview) covering account teammates and subusers. # Sentinel XS Source: https://docs.stackone.com/connectors/sentinelxs/index How to set up the Sentinel XS connector, plus the actions that are available.
Sentinel XS
v1.0.0
69 actions · 1 auth method
Security
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Sentinel XS uses SOAP-based authentication with username and password embedded in each SOAP request. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sentinelxs/index.md for the full list. # Sentry Source: https://docs.stackone.com/connectors/sentry/index How to set up the Sentry connector, plus the actions and events that are available.
Sentry
v3.0.0
85 actions · 15 events · 3 auth methods
Observability IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for personal scripts, CI/CD, and single-user automation. Scoped to your account permissions. Generate via Personal... For server-side integrations where the client secret can be kept secure on your server. For client-side or mobile apps where the client secret cannot be stored securely. Uses PKCE. Optionally, configure receiving Events for Sentry into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sentry/index.md for the full list. ## Events See https://docs.stackone.com/connectors/sentry/index.md for the full list. # Sentry Changelog Source: https://docs.stackone.com/connectors/sentry/changelog Release history for the Sentry connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `webhook` `breaking-change` Webhook events are now available only on Auth Token connections, which are the only connections Sentry can deliver events to. `webhook` `guide` Verified webhook events against a live Sentry organisation. Events confirmed working end to end are now preview, and those that could not be fired during testing are marked beta with the reason recorded. `guide` Added a step-by-step setup guide for receiving Sentry webhook events. Actions that could not be verified against live data are now marked beta. `sentry_bulk_mutate_a_list_of_issues`, `sentry_bulk_mutate_an_organizations_issues`, `sentry_delete_replay`, `sentry_get_organization_stats_summary`, `sentry_get_organization_stats_v2`, `sentry_get_replay`, `sentry_get_replay_recording_segment`, `sentry_list_a_projects_error_events`, `sentry_list_a_tags_values`, `sentry_list_replay_recording_segments`, `sentry_list_replay_viewed_by`, `sentry_list_repository_commits`, `sentry_retrieve_a_project_releases_file`, `sentry_retrieve_an_organization_releases_file`, `sentry_update_organization_member_roles` `bug-fix` User lists with groups now read every team each member belongs to, instead of only the first 20 teams. `sentry_unified_list_users` `data-sync` Added DataSync support for unified IAM list actions (users, groups, organisations), enabling periodic background synchronisation. `sentry_unified_list_groups`, `sentry_unified_list_organizations`, `sentry_unified_list_users` `bug-fix` `description-fix` Fixed IAM list pagination for users, groups, organizations, and resource users so large Sentry accounts no longer stop early or fail on later pages, and shortened the IAM action descriptions. `sentry_unified_get_group`, `sentry_unified_get_me`, `sentry_unified_get_organization`, `sentry_unified_get_role`, `sentry_unified_get_user`, `sentry_unified_list_groups`, `sentry_unified_list_organizations`, `sentry_unified_list_resource_users`, `sentry_unified_list_roles`, `sentry_unified_list_users` `description-fix` Clarified age search operator syntax in issue query descriptions to prevent incorrect filter usage. `sentry_list_a_projects_issues`, `sentry_list_an_organizations_issues` `description-fix` `guide-fix` Improved action descriptions for search query syntax and slug resolution, and fixed connection guide labels to match Sentry portal UI. `sentry_delete_a_team`, `sentry_list_a_projects_issues`, `sentry_list_an_organizations_issues` `description-fix` Improved action descriptions to clarify slug vs display name usage and ownership rule format. `sentry_create_a_new_project`, `sentry_delete_a_project`, `sentry_delete_a_team`, `sentry_delete_an_organization_member_from_a_team`, `sentry_list_a_teams_projects`, `sentry_update_ownership_configuration_for_a_project` `auth` `breaking` `bug-fix` `guide` Migrated to authRequirements, added missing parameters, fixed enums and types, improved connector guides, and added releaseStage preview to untestable actions. `sentry_add_a_team_to_a_project`, `sentry_add_an_organization_member_to_a_team`, `sentry_add_organization_member`, `sentry_bulk_mutate_a_list_of_issues`, `sentry_bulk_mutate_an_organizations_issues`, `sentry_bulk_remove_a_list_of_issues`, `sentry_bulk_remove_an_organizations_issues`, `sentry_create_a_new_project`, `sentry_create_a_new_team`, `sentry_delete_a_project`, `sentry_delete_a_team`, `sentry_delete_a_team_from_a_project`, `sentry_delete_an_organization_member_from_a_team`, `sentry_delete_organization_member`, `sentry_delete_replay`, `sentry_get_organization`, `sentry_get_organization_member`, `sentry_get_organization_stats_summary`, `sentry_get_organization_stats_v2`, `sentry_get_replay`, `sentry_get_replay_recording_segment`, `sentry_list_a_project_releases_commits`, `sentry_list_a_projects_client_keys`, `sentry_list_a_projects_data_filters`, `sentry_list_a_projects_error_events`, `sentry_list_a_projects_issues`, `sentry_list_a_projects_organization_members`, `sentry_list_a_projects_release_files`, `sentry_list_a_projects_teams`, `sentry_list_a_projects_users`, `sentry_list_a_releases_deploys`, `sentry_list_a_tags_values`, `sentry_list_a_tags_values_for_an_issue`, `sentry_list_a_teams_members`, `sentry_list_a_teams_projects`, `sentry_list_a_users_teams_for_an_organization`, `sentry_list_an_issues_events`, `sentry_list_an_issues_hashes`, `sentry_list_an_organization_releases_commits`, `sentry_list_an_organizations_issues`, `sentry_list_an_organizations_release_files`, `sentry_list_an_organizations_releases`, `sentry_list_an_organizations_teams`, `sentry_list_organization_members`, `sentry_list_organization_projects`, `sentry_list_organization_replays`, `sentry_list_organization_repositories`, `sentry_list_organization_selectors`, `sentry_list_replay_recording_segments`, `sentry_list_replay_viewed_by`, `sentry_list_repository_commits`, `sentry_list_your_organizations`, `sentry_remove_an_issue`, `sentry_resolve_event_id`, `sentry_resolve_short_id`, `sentry_retrieve_a_project`, `sentry_retrieve_a_project_releases_file`, `sentry_retrieve_a_team`, `sentry_retrieve_an_event_for_a_project`, `sentry_retrieve_an_issue`, `sentry_retrieve_an_issue_event`, `sentry_retrieve_an_organization_releases_file`, `sentry_retrieve_an_organizations_release`, `sentry_retrieve_event_counts_for_a_project`, `sentry_retrieve_files_changed_in_a_releases_commits`, `sentry_retrieve_ownership_configuration_for_a_project`, `sentry_retrieve_statuses_of_release_thresholds_alpha`, `sentry_retrieve_tag_details`, `sentry_unified_get_group`, `sentry_unified_get_me`, `sentry_unified_get_organization`, `sentry_unified_get_role`, `sentry_unified_get_user`, `sentry_unified_list_groups`, `sentry_unified_list_organizations`, `sentry_unified_list_resource_types`, `sentry_unified_list_resource_users`, `sentry_unified_list_roles`, `sentry_unified_list_users`, `sentry_update_a_team`, `sentry_update_an_issue`, `sentry_update_an_organization_members_team_role`, `sentry_update_organization`, `sentry_update_organization_member_roles`, `sentry_update_ownership_configuration_for_a_project` `bug-fix` Fixed unified_get_role rejecting the id that unified_list_roles returns, and stopped an unrecognised role key coming back labelled as the Billing role. `sentry_unified_get_me`, `sentry_unified_get_role`, `sentry_unified_list_roles` `new-actions` Added unified IAM actions for users, groups, organizations, roles, resource users, and credentials. # ServiceNow Source: https://docs.stackone.com/connectors/servicenow/index How to set up the ServiceNow connector, plus the actions and events that are available.
ServiceNow
v1.2.0
77 actions · 19 events · 2 auth methods
ITSM Ticketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). You need an account with appropriate permissions to access the ServiceNow Table API. API Key authentication requires the com.glide.tokenbased\_auth plugin to be installed on your ServiceNow instance. Optionally, configure receiving Events for ServiceNow into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/servicenow/index.md for the full list. ## Events See https://docs.stackone.com/connectors/servicenow/index.md for the full list. # ServiceNow Changelog Source: https://docs.stackone.com/connectors/servicenow/changelog Release history for the ServiceNow connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Delete actions now confirm the deleted record ID, and problem, change request, knowledge article, and knowledge category actions accept previously missing fields (workaround, category, change model, justification and plans, search keywords, parent knowledge base). Guidance for resolving incidents and editing published articles is corrected. `servicenow_create_catalog_request_item`, `servicenow_create_change_request`, `servicenow_create_incident`, `servicenow_create_kb_category`, `servicenow_create_knowledge_article`, `servicenow_create_user`, `servicenow_delete_catalog_request`, `servicenow_delete_catalog_request_item`, `servicenow_delete_change_request`, `servicenow_delete_group`, `servicenow_delete_incident`, `servicenow_delete_knowledge_article`, `servicenow_delete_problem`, `servicenow_delete_table_record`, `servicenow_delete_task`, `servicenow_delete_user`, `servicenow_delete_webhook`, `servicenow_update_change_request`, `servicenow_update_incident`, `servicenow_update_knowledge_article`, `servicenow_update_problem` `new-feature` `data-sync` Added DataSync support to sixteen list actions (incidents, problems, change requests, tasks, catalog requests and items, knowledge articles and categories, knowledge bases, users, groups, roles, role assignments, locations, departments, and tables) so their records can be periodically synced by full refresh. `servicenow_list_catalog_request_items`, `servicenow_list_catalog_requests`, `servicenow_list_change_requests`, `servicenow_list_departments`, `servicenow_list_groups`, `servicenow_list_incidents`, `servicenow_list_kb_categories`, `servicenow_list_kb_knowledge_bases`, `servicenow_list_knowledge_articles`, `servicenow_list_locations`, `servicenow_list_problems`, `servicenow_list_tables`, `servicenow_list_tasks`, `servicenow_list_user_role_assignments`, `servicenow_list_user_roles`, `servicenow_list_users` `bug-fix` Fixed table metadata, column, choice list, and reference qualifier lookups ignoring the requested table and returning unfiltered results. `servicenow_get_choice_list`, `servicenow_get_reference_qualifiers`, `servicenow_get_table_metadata`, `servicenow_list_table_columns` `guide-changes` Rewrote Basic Auth and API Key connection guides with portal screenshots, prerequisites, StackOne credential mapping, and corrected navigation and policy-setup steps for the current ServiceNow UI. # Sesame HR Source: https://docs.stackone.com/connectors/sesame/index How to set up the Sesame HR connector, plus the actions that are available.
Sesame HR
Previewv1.1.0
60 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an API key generated by an admin in Settings > Integrations > API. Token inherits the permissions of the admin... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sesame/index.md for the full list. # Sesame HR Changelog Source: https://docs.stackone.com/connectors/sesame/changelog Release history for the Sesame HR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for 16 list actions including employees, departments, offices, absences, time entries, and trainings, with incremental updates for work entries and check incidences. # SharePoint Source: https://docs.stackone.com/connectors/sharepoint/index How to set up the SharePoint connector, plus the actions that are available.
SharePoint
v1.2.0
33 actions · 1 auth method
Documents
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Microsoft Entra ID account to connect SharePoint. You'll need to register an Azure application wi... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sharepoint/index.md for the full list. # SharePoint Changelog Source: https://docs.stackone.com/connectors/sharepoint/changelog Release history for the SharePoint connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added file download and upload actions - download files (with optional PDF, HTML or image conversion and byte ranges), earlier versions, thumbnails and files from sharing links; upload new files, replace file content, and upload large files in chunks through upload sessions. `sharepoint_cancel_upload_session`, `sharepoint_complete_upload_session`, `sharepoint_convert_drive_item_content`, `sharepoint_create_upload_session`, `sharepoint_create_upload_session_for_existing_file`, `sharepoint_download_drive_item_content`, `sharepoint_download_drive_item_thumbnail_content`, `sharepoint_download_drive_item_version_content`, `sharepoint_download_shared_drive_item_content`, `sharepoint_get_upload_session`, `sharepoint_list_drive_item_versions`, `sharepoint_replace_drive_item_content`, `sharepoint_upload_bytes_to_upload_session`, `sharepoint_upload_drive_item_content` `data-sync` Added Data Sync support for list_sites (full refresh each run). list_sites now also returns a next field for fetching the next page. `sharepoint_list_sites` `bug-fix` Added a dynamic scope selector to the setup guide and refined action descriptions per behavioural retest feedback. `sharepoint_list_items`, `sharepoint_list_subsites` `bug-fix` Refreshed the connection guide, refined the Scopes field description, and clarified provider-behavior gaps flagged in behavioural testing. # ShipStation Source: https://docs.stackone.com/connectors/shipstation/index How to set up the ShipStation connector, plus the actions and events that are available.
ShipStation
v1.2.0
45 actions · 6 events · 1 auth method
Logistics
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses HTTP Basic Auth with an API Key and API Secret. Generated by the Account Owner in ShipStation's Account API Setting... Optionally, configure receiving Events for ShipStation into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/shipstation/index.md for the full list. ## Events See https://docs.stackone.com/connectors/shipstation/index.md for the full list. # ShipStation Changelog Source: https://docs.stackone.com/connectors/shipstation/changelog Release history for the ShipStation connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Added native webhook support for 6 ShipStation order, shipment and fulfillment events, with one webhook created and removed automatically per enabled event. `data-sync` Added DataSync support to 8 list actions, with incremental sync for orders. # Shopify Source: https://docs.stackone.com/connectors/shopify/index How to set up the Shopify connector, plus the actions and events that are available.
Shopify
Previewv1.4.0
90 actions · 22 events · 1 auth method
E-Commerce IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Optionally, configure receiving Events for Shopify into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/shopify/index.md for the full list. ## Events See https://docs.stackone.com/connectors/shopify/index.md for the full list. # Shortcut Source: https://docs.stackone.com/connectors/shortcut_pm/index How to set up the Shortcut connector, plus the actions and events that are available.
Shortcut
v1.3.0
92 actions · 6 events · 1 auth method
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API token from your Shortcut account settings to authenticate API requests. Optionally, configure receiving Events for Shortcut into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/shortcut_pm/index.md for the full list. ## Events See https://docs.stackone.com/connectors/shortcut_pm/index.md for the full list. # Shortcut Changelog Source: https://docs.stackone.com/connectors/shortcut_pm/changelog Release history for the Shortcut connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added DataSync support to 14 list actions, synced as full refreshes. # Simployer One Source: https://docs.stackone.com/connectors/simployer/index How to set up the Simployer One connector, plus the actions that are available.
Simployer One
Previewv1.2.0
55 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using your Simployer Access Token. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/simployer/index.md for the full list. # Simployer One Changelog Source: https://docs.stackone.com/connectors/simployer/changelog Release history for the Simployer One connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for companies, compensations, cost centres, departments, employees, employment types, employments, leave types, leaves, offices, projects and teams, so these collections can be kept in sync on a schedule. All twelve page through Simployer's limit and offset parameters, which matters because the API returns only the first 100 records when no limit is sent. Employees and employments also sync incrementally, pulling only records changed since the last run, and each gains an optional updated_after input for that. The other ten refresh in full, because Simployer does not allow filtering them on the updated field. `simployer_list_companies`, `simployer_list_compensations`, `simployer_list_cost_centers`, `simployer_list_departments`, `simployer_list_employees`, `simployer_list_employment_types`, `simployer_list_employments`, `simployer_list_leave_types`, `simployer_list_leaves`, `simployer_list_offices`, `simployer_list_projects`, `simployer_list_teams` `new-actions` `bug-fix` Added create_office action and new list inputs (id filter, sort, leave-type relations) plus employee tax/bankAccount/homeAddress and leave-type archived fields; fixed the leave-type minimumDuration enum (removed unsupported half_day) and relations values, and sharpened action descriptions for reliable agent callability and disambiguation. # Slack Source: https://docs.stackone.com/connectors/slack/index How to set up the Slack connector, plus the actions that are available.
Slack
v5.0.0
51 actions · 4 auth methods
Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate your app to perform automated actions as a bot. Best for integrations, automation, and managing workspace o... Authenticate with your personal Slack account to perform actions as yourself. Provides access to your profile, private c... No refresh flow. Uses a static Bot User OAuth Token (xoxb-) copied from your Slack app; actions run as the app's bot use... No refresh flow. Uses a static User OAuth Token (xoxp-) copied from your Slack app; actions run as the user who installe... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/slack/index.md for the full list. # Slack Changelog Source: https://docs.stackone.com/connectors/slack/changelog Release history for the Slack connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `auth` `new-actions` `bug-fix` `guide` Added a Search Messages action and a separate Bot Access Token auth type. Breaking change — the Access Token auth now accepts only user tokens (xoxp-), so accounts connected with a bot token (xoxb-) must reconnect using Bot Access Token. Schedule Message now accepts markdown_text or blocks without text, and the connection guides were refreshed. `slack_search_messages` `slack_auth_test`, `slack_complete_file_upload`, `slack_create_conversation`, `slack_delete_file`, `slack_delete_message`, `slack_delete_scheduled_message`, `slack_get_conversation`, `slack_get_file`, `slack_get_message_permalink`, `slack_get_upload_url`, `slack_get_user`, `slack_get_user_by_email`, `slack_get_user_presence`, `slack_get_user_profile`, `slack_invite_shared_conversation`, `slack_invite_users_to_conversation`, `slack_join_conversation`, `slack_kick_user_from_conversation`, `slack_leave_conversation`, `slack_list_connect_invites`, `slack_list_conversation_members`, `slack_list_conversations`, `slack_list_files`, `slack_list_messages`, `slack_list_scheduled_messages`, `slack_list_thread_replies`, `slack_list_user_conversations`, `slack_list_users`, `slack_lookup_discoverable_contact`, `slack_open_conversation`, `slack_rename_conversation`, `slack_revoke_file_public_url`, `slack_schedule_message`, `slack_send_ephemeral_message`, `slack_send_message`, `slack_set_user_presence`, `slack_set_user_profile`, `slack_share_file_public_url`, `slack_unified_get_group`, `slack_unified_get_me`, `slack_unified_get_organization`, `slack_unified_get_role`, `slack_unified_get_user`, `slack_unified_list_groups`, `slack_unified_list_organizations`, `slack_unified_list_resource_types`, `slack_unified_list_resource_users`, `slack_unified_list_roles`, `slack_unified_list_users`, `slack_update_message` `breaking` `new-feature` `datasync` `auth` Enabled DataSync for Slack list actions (conversations, user conversations, users, files, scheduled messages, Slack Connect invites, and unified users/roles/organizations) so their records can be periodically synced with full pagination. Breaking change — list_users now returns the full Slack response body instead of a bare members array (read the members field). Also added a token-rotation setup notice with a clearer error when rotation is not enabled, and switched the Slack Connect invite actions to the conversations.connect:manage scope. `slack_auth_test`, `slack_complete_file_upload`, `slack_create_conversation`, `slack_delete_file`, `slack_delete_message`, `slack_delete_scheduled_message`, `slack_get_conversation`, `slack_get_file`, `slack_get_message_permalink`, `slack_get_upload_url`, `slack_get_user`, `slack_get_user_by_email`, `slack_get_user_presence`, `slack_get_user_profile`, `slack_invite_shared_conversation`, `slack_invite_users_to_conversation`, `slack_join_conversation`, `slack_kick_user_from_conversation`, `slack_leave_conversation`, `slack_list_connect_invites`, `slack_list_conversation_members`, `slack_list_conversations`, `slack_list_files`, `slack_list_messages`, `slack_list_scheduled_messages`, `slack_list_thread_replies`, `slack_list_user_conversations`, `slack_list_users`, `slack_lookup_discoverable_contact`, `slack_open_conversation`, `slack_rename_conversation`, `slack_revoke_file_public_url`, `slack_schedule_message`, `slack_send_ephemeral_message`, `slack_send_message`, `slack_set_user_presence`, `slack_set_user_profile`, `slack_share_file_public_url`, `slack_unified_get_group`, `slack_unified_get_me`, `slack_unified_get_organization`, `slack_unified_get_role`, `slack_unified_get_user`, `slack_unified_list_groups`, `slack_unified_list_organizations`, `slack_unified_list_resource_types`, `slack_unified_list_resource_users`, `slack_unified_list_roles`, `slack_unified_list_users`, `slack_update_message` `enhancement` Added unfurl_links and unfurl_media options to schedule_message so scheduled messages can suppress link and media previews, matching send_message. Both accept false to disable the default previews. `slack_schedule_message` `bug-fix` Corrected misleading action descriptions that promised a capability Slack's API does not offer. list_conversations and list_users no longer claim to find IDs by name — Slack's conversations.list and users.list have no server-side name filter, so the descriptions now explain that a name must be resolved by paging through results and matching client-side (and direct email lookups to get_user_by_email). Also removed the deprecated "or a name" hint from the channel_id parameter of send_message, update_message, send_ephemeral_message, and schedule_message, since Slack deprecates passing a channel name and always expects the encoded ID. `slack_auth_test`, `slack_complete_file_upload`, `slack_create_conversation`, `slack_delete_file`, `slack_delete_message`, `slack_delete_scheduled_message`, `slack_get_conversation`, `slack_get_file`, `slack_get_message_permalink`, `slack_get_upload_url`, `slack_get_user`, `slack_get_user_by_email`, `slack_get_user_presence`, `slack_get_user_profile`, `slack_invite_shared_conversation`, `slack_invite_users_to_conversation`, `slack_join_conversation`, `slack_kick_user_from_conversation`, `slack_leave_conversation`, `slack_list_connect_invites`, `slack_list_conversation_members`, `slack_list_conversations`, `slack_list_files`, `slack_list_messages`, `slack_list_scheduled_messages`, `slack_list_thread_replies`, `slack_list_user_conversations`, `slack_list_users`, `slack_lookup_discoverable_contact`, `slack_open_conversation`, `slack_rename_conversation`, `slack_revoke_file_public_url`, `slack_schedule_message`, `slack_send_ephemeral_message`, `slack_send_message`, `slack_set_user_presence`, `slack_set_user_profile`, `slack_share_file_public_url`, `slack_unified_get_group`, `slack_unified_get_me`, `slack_unified_get_organization`, `slack_unified_get_role`, `slack_unified_get_user`, `slack_unified_list_groups`, `slack_unified_list_organizations`, `slack_unified_list_resource_types`, `slack_unified_list_resource_users`, `slack_unified_list_roles`, `slack_unified_list_users`, `slack_update_message` `bug-fix` Brought the unified IAM composite-identifier config into conformance — the roles and resource_users list/get actions now declare their id field mapping explicitly, and the auth_test debug action no longer carries a composite-identifier block so its raw response passes through untouched. Also clarified the list_users and resource_users descriptions (page_size controls how many records the caller receives; resource_id accepts both raw and encoded channel ids). `slack_auth_test`, `slack_unified_get_role`, `slack_unified_list_resource_users`, `slack_unified_list_roles`, `slack_unified_list_users` `bug-fix` Fixed unified IAM schema conformance and error handling — created_at/updated_at on groups, organizations, and users now return ISO 8601 datetime strings instead of epoch-seconds numbers, revoked and inactive tokens now map to 401, and role resource_id now uses a JSONPath reference. # SmartAdvocate Source: https://docs.stackone.com/connectors/smartadvocate/index How to set up the SmartAdvocate connector, plus the actions that are available.
SmartAdvocate
Betav1.1.0
60 actions · 1 auth method
Legal
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your SmartAdvocate username and password. No app registration required. A JWT bearer token is obtained... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/smartadvocate/index.md for the full list. # SmartAdvocate Changelog Source: https://docs.stackone.com/connectors/smartadvocate/changelog Release history for the SmartAdvocate connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 15 list actions (users, full user profiles, case roles, firm roles, titles, offices, departments, permission groups, teams, appointment types, document categories, document tags, task types, task statuses, and task priorities), each synced as a single full-refresh pull. # Smartling Source: https://docs.stackone.com/connectors/smartling/index How to set up the Smartling connector, plus the actions and events that are available.
Smartling
v1.1.1
70 actions · 23 events · 1 auth method
Localization
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Smartling brands this "OAuth 2.0", but it is a token exchange keyed on a user-generated API Token (User Identifier + Use... Optionally, configure receiving Events for Smartling into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/smartling/index.md for the full list. ## Events See https://docs.stackone.com/connectors/smartling/index.md for the full list. # Smartling Changelog Source: https://docs.stackone.com/connectors/smartling/changelog Release history for the Smartling connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Webhook events are now delivered to the per-connection webhook subscription URL on the linked account. The previous routing that matched deliveries to a connection by Smartling account UID is no longer supported and has been removed. `data-sync` Added Data Sync support for locales, projects, account jobs and account custom fields, so these collections can be kept in sync on a schedule. Projects and account jobs page through Smartling's limit and offset parameters; locales and custom fields are returned in full by the API in a single call. Each sync is a full refresh, because Smartling does not expose a changed-since filter on these endpoints. `smartling_list_account_custom_fields`, `smartling_list_account_jobs`, `smartling_list_locales`, `smartling_list_projects` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `description-fix` Document the 100-result maximum on the list_files limit parameter to prevent invalid pagination requests. `smartling_list_files` `new-actions` Initial Smartling connector with 70 actions across projects, locales, files, jobs, job batches, strings, custom fields, and tags. # SmartRecruiters Source: https://docs.stackone.com/connectors/smartrecruiters/index How to set up the SmartRecruiters connector, plus the actions and events that are available.
SmartRecruiters
v2.1.0
169 actions · 15 events · 1 auth method
ATS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API key authentication. Requires Administrator privileges to generate a key. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/smartrecruiters/index.md for the full list. ## Events See https://docs.stackone.com/connectors/smartrecruiters/index.md for the full list. # SmartRecruiters Changelog Source: https://docs.stackone.com/connectors/smartrecruiters/changelog Release history for the SmartRecruiters connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `new-feature` Fixed an action ID collision on list_access_groups, where the Configuration API and User API access-group endpoints shared one ID and the Configuration API copy was unreachable as a result. list_access_groups keeps its existing behaviour - the User API endpoint /user-api/v201804/access-groups with the users_read scope - so callers are unaffected. The Configuration API endpoint /configuration/access-groups is now reachable as the new action list_configuration_access_groups, which takes pageSize and pageId and needs configuration_read. `smartrecruiters_list_configuration_access_groups` `smartrecruiters_get_access_group`, `smartrecruiters_list_access_groups`, `smartrecruiters_update_access_group` `breaking-changes` `new-feature` Enabled scheduled data sync on 22 list actions covering candidates, jobs, offers, users, access groups, interview templates and the configuration and reference lookups, so these collections can be kept in sync and read without calling SmartRecruiters on every request. Candidates, jobs and users sync incrementally using the existing updatedAfter filter; the rest refresh in full, because their endpoints expose only creation or release time filters. BREAKING - List Predefined Locations previously declared its page size input as limit, which SmartRecruiters ignores. It is now pageSize, the parameter the API actually accepts, so that endpoint paginates instead of returning every location on one page. Integrations passing limit to that action must send pageSize instead. `smartrecruiters_list_access_groups`, `smartrecruiters_list_approvals`, `smartrecruiters_list_candidate_properties`, `smartrecruiters_list_career_sites`, `smartrecruiters_list_departments`, `smartrecruiters_list_experience_levels`, `smartrecruiters_list_functions`, `smartrecruiters_list_hiring_processes`, `smartrecruiters_list_industries`, `smartrecruiters_list_interview_templates`, `smartrecruiters_list_job_properties`, `smartrecruiters_list_offer_properties`, `smartrecruiters_list_predefined_locations`, `smartrecruiters_list_rejection_reasons`, `smartrecruiters_list_system_roles`, `smartrecruiters_list_types_of_employment`, `smartrecruiters_list_users`, `smartrecruiters_list_withdrawal_reasons`, `smartrecruiters_search_candidates`, `smartrecruiters_search_jobs`, `smartrecruiters_search_offers` `bug-fix` Clarified how job reference fields work. create_job and update_job now state that industry, function, experienceLevel and typeOfEmployment take exact ids from the matching lookup action and that any other value is rejected, replacing wording that wrongly said unknown values are ignored. The job property actions now say they cover custom properties only and point to the lookup actions for the standard attributes. `smartrecruiters_create_job`, `smartrecruiters_get_job_property_values`, `smartrecruiters_list_job_properties`, `smartrecruiters_update_job` `new-actions` Add taxonomy lookup actions (list_industries, list_functions, list_experience_levels, list_types_of_employment) for discovering valid IDs required by create_job. `smartrecruiters_list_experience_levels`, `smartrecruiters_list_functions`, `smartrecruiters_list_industries`, `smartrecruiters_list_types_of_employment` `new-actions` Add taxonomy lookup actions (list_industries, list_functions, list_experience_levels, list_types_of_employment) for discovering valid IDs required by create_job. Breaking change — all action results now wrapped under a data key (result.data instead of result directly). # Smartsheet Source: https://docs.stackone.com/connectors/smartsheet/index How to set up the Smartsheet connector, plus the actions and events that are available.
Smartsheet
Previewv1.3.0
203 actions · 9 events · 2 auth methods
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an app in Smartsheet Developer Tools. Best for personal scripts and single-user integrations. Access is scoped to the token creator's permissions. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/smartsheet/index.md for the full list. ## Events See https://docs.stackone.com/connectors/smartsheet/index.md for the full list. # Smartsheet Changelog Source: https://docs.stackone.com/connectors/smartsheet/changelog Release history for the Smartsheet connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhooks` Added native inbound webhook support so Smartsheet sheet, row, column, cell, attachment, discussion, and comment changes can be pushed to StackOne in real time instead of relying only on polling. Each connection shows a Native Webhook URL to register per sheet via the existing webhook actions, plus an optional Webhook Shared Secret for signature verification. Also enabled sheet creation and deletion by requesting the CREATE_SHEETS and DELETE_SHEETS OAuth scopes. `smartsheet_add_alternate_emails`, `smartsheet_add_attachment`, `smartsheet_add_columns`, `smartsheet_add_favorite`, `smartsheet_add_group_members`, `smartsheet_add_report_columns`, `smartsheet_add_report_scope`, `smartsheet_add_rows`, `smartsheet_add_summary_fields`, `smartsheet_add_user`, `smartsheet_auth_test`, `smartsheet_copy_dashboard`, `smartsheet_copy_folder`, `smartsheet_copy_rows`, `smartsheet_copy_sheet`, `smartsheet_copy_workspace`, `smartsheet_create_comment`, `smartsheet_create_cross_sheet_ref`, `smartsheet_create_discussion`, `smartsheet_create_folder`, `smartsheet_create_folder_in_workspace`, `smartsheet_create_group`, `smartsheet_create_home_folder`, `smartsheet_create_proof`, `smartsheet_create_proof_discussion`, `smartsheet_create_proof_requests`, `smartsheet_create_proof_version`, `smartsheet_create_report`, `smartsheet_create_row_discussion`, `smartsheet_create_sheet`, `smartsheet_create_sheet_in_folder`, `smartsheet_create_sheet_in_workspace`, `smartsheet_create_update_request`, `smartsheet_create_webhook`, `smartsheet_create_workspace`, `smartsheet_deactivate_user`, `smartsheet_delete_alternate_email`, `smartsheet_delete_attachment`, `smartsheet_delete_attachment_versions`, `smartsheet_delete_automation_rule`, `smartsheet_delete_column`, `smartsheet_delete_comment`, `smartsheet_delete_dashboard`, `smartsheet_delete_dashboard_share`, `smartsheet_delete_discussion`, `smartsheet_delete_favorite`, `smartsheet_delete_favorites_by_type`, `smartsheet_delete_folder`, `smartsheet_delete_group`, `smartsheet_delete_group_member`, `smartsheet_delete_proof`, `smartsheet_delete_proof_requests`, `smartsheet_delete_proof_version`, `smartsheet_delete_report`, `smartsheet_delete_report_share`, `smartsheet_delete_rows`, `smartsheet_delete_sent_update_request`, `smartsheet_delete_sheet`, `smartsheet_delete_sheet_share`, `smartsheet_delete_summary_fields`, `smartsheet_delete_token`, `smartsheet_delete_update_request`, `smartsheet_delete_webhook`, `smartsheet_delete_workspace`, `smartsheet_delete_workspace_share`, `smartsheet_downgrade_user`, `smartsheet_edit_comment`, `smartsheet_get_alternate_email`, `smartsheet_get_attachment`, `smartsheet_get_automation_rule`, `smartsheet_get_column`, `smartsheet_get_comment`, `smartsheet_get_contact`, `smartsheet_get_cross_sheet_ref`, `smartsheet_get_current_user`, `smartsheet_get_dashboard`, `smartsheet_get_dashboard_path`, `smartsheet_get_dashboard_publish`, `smartsheet_get_dashboard_share`, `smartsheet_get_discussion`, `smartsheet_get_folder`, `smartsheet_get_folder_metadata`, `smartsheet_get_folder_path`, `smartsheet_get_group`, `smartsheet_get_proof`, `smartsheet_get_report`, `smartsheet_get_report_path`, `smartsheet_get_report_publish`, `smartsheet_get_report_share`, `smartsheet_get_row`, `smartsheet_get_sent_update_request`, `smartsheet_get_server_info`, `smartsheet_get_sheet`, `smartsheet_get_sheet_path`, `smartsheet_get_sheet_publish`, `smartsheet_get_sheet_share`, `smartsheet_get_sheet_version`, `smartsheet_get_update_request`, `smartsheet_get_user`, `smartsheet_get_webhook`, `smartsheet_get_workspace`, `smartsheet_get_workspace_children`, `smartsheet_get_workspace_metadata`, `smartsheet_get_workspace_share`, `smartsheet_import_sheet`, `smartsheet_is_favorite`, `smartsheet_list_alternate_emails`, `smartsheet_list_attachment_versions`, `smartsheet_list_attachments`, `smartsheet_list_automation_rules`, `smartsheet_list_columns`, `smartsheet_list_contacts`, `smartsheet_list_cross_sheet_refs`, `smartsheet_list_dashboard_shares`, `smartsheet_list_dashboards`, `smartsheet_list_discussion_attachments`, `smartsheet_list_discussions`, `smartsheet_list_events`, `smartsheet_list_favorites`, `smartsheet_list_filtered_events`, `smartsheet_list_folder_children`, `smartsheet_list_folders`, `smartsheet_list_groups`, `smartsheet_list_image_urls`, `smartsheet_list_org_sheets`, `smartsheet_list_proof_attachments`, `smartsheet_list_proof_discussions`, `smartsheet_list_proof_request_actions`, `smartsheet_list_proof_versions`, `smartsheet_list_proofs`, `smartsheet_list_public_templates`, `smartsheet_list_report_shares`, `smartsheet_list_reports`, `smartsheet_list_row_attachments`, `smartsheet_list_row_discussions`, `smartsheet_list_sent_update_requests`, `smartsheet_list_sheet_shares`, `smartsheet_list_sheets`, `smartsheet_list_summary`, `smartsheet_list_summary_fields`, `smartsheet_list_templates`, `smartsheet_list_update_requests`, `smartsheet_list_user_plans`, `smartsheet_list_users`, `smartsheet_list_webhooks`, `smartsheet_list_workspace_folders`, `smartsheet_list_workspace_shares`, `smartsheet_list_workspaces`, `smartsheet_move_dashboard`, `smartsheet_move_folder`, `smartsheet_move_rows`, `smartsheet_move_sheet`, `smartsheet_promote_alternate_email`, `smartsheet_reactivate_user`, `smartsheet_remove_report_scope`, `smartsheet_remove_user`, `smartsheet_remove_user_from_plan`, `smartsheet_reset_webhook_secret`, `smartsheet_search_everything`, `smartsheet_search_sheet`, `smartsheet_send_report_via_email`, `smartsheet_send_rows_via_email`, `smartsheet_send_sheet_via_email`, `smartsheet_set_dashboard_publish`, `smartsheet_set_report_publish`, `smartsheet_set_sheet_publish`, `smartsheet_share_dashboard`, `smartsheet_share_report`, `smartsheet_share_sheet`, `smartsheet_share_workspace`, `smartsheet_sort_rows`, `smartsheet_unified_delete_user`, `smartsheet_unified_get_group`, `smartsheet_unified_get_me`, `smartsheet_unified_get_organization`, `smartsheet_unified_get_role`, `smartsheet_unified_get_user`, `smartsheet_unified_list_groups`, `smartsheet_unified_list_organizations`, `smartsheet_unified_list_resource_types`, `smartsheet_unified_list_resource_users`, `smartsheet_unified_list_roles`, `smartsheet_unified_list_users`, `smartsheet_unified_update_user`, `smartsheet_update_automation_rule`, `smartsheet_update_column`, `smartsheet_update_dashboard`, `smartsheet_update_dashboard_share`, `smartsheet_update_folder`, `smartsheet_update_group`, `smartsheet_update_proof`, `smartsheet_update_report_definition`, `smartsheet_update_report_share`, `smartsheet_update_rows`, `smartsheet_update_sheet`, `smartsheet_update_sheet_share`, `smartsheet_update_summary_fields`, `smartsheet_update_update_request`, `smartsheet_update_user`, `smartsheet_update_webhook`, `smartsheet_update_workspace`, `smartsheet_update_workspace_share`, `smartsheet_upgrade_user` `bug-fix` Fixed unified member lists failing with an error on shared workspaces and sheets, and unified lists failing whenever there is more than one page of results. `smartsheet_unified_list_groups`, `smartsheet_unified_list_resource_users`, `smartsheet_unified_list_users` `data-sync` Added scheduled data sync to sixteen list actions — sheets, org sheets, dashboards, reports, groups, users, workspaces, contacts, folders, public templates, webhooks, favorites, and the unified users, groups, organizations, and roles — so these collections can be kept in sync and read back without calling Smartsheet on every request. Sheets, dashboards, reports, groups, and contacts sync incrementally via modifiedSince; the rest refresh in full. `smartsheet_list_contacts`, `smartsheet_list_dashboards`, `smartsheet_list_favorites`, `smartsheet_list_folders`, `smartsheet_list_groups`, `smartsheet_list_org_sheets`, `smartsheet_list_public_templates`, `smartsheet_list_reports`, `smartsheet_list_sheets`, `smartsheet_list_users`, `smartsheet_list_webhooks`, `smartsheet_list_workspaces`, `smartsheet_unified_list_groups`, `smartsheet_unified_list_organizations`, `smartsheet_unified_list_roles`, `smartsheet_unified_list_users` `bug-fix` Fixed unified_get_me shipping user.id and remote_id as raw JSON numbers instead of strings; the credentials action was skipping the typecast step. `smartsheet_unified_get_me` `new-actions` Added unified IAM actions for users, groups, roles, organizations, credentials, and resource users. # Snowflake Source: https://docs.stackone.com/connectors/snowflake/index How to set up the Snowflake connector, plus the actions that are available.
Snowflake
v1.4.0
98 actions · 3 auth methods
Databases IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an OAuth security integration in Snowflake. Access is scoped to a specific Snowflake role. The OAuth security integration is created in the connecting Snowflake account and its credentials are entered at connect... Uses RSA key pair authentication with automatic JWT refresh. Requires assigning a public key to a Snowflake user; the co... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/snowflake/index.md for the full list. # Snowflake Changelog Source: https://docs.stackone.com/connectors/snowflake/changelog Release history for the Snowflake connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support for databases, roles, users, warehouses, and the unified IAM users, roles and organization. Each sync refreshes the full list on every run. `snowflake_list_databases`, `snowflake_list_roles`, `snowflake_list_users`, `snowflake_list_warehouses`, `snowflake_unified_list_organizations`, `snowflake_unified_list_roles`, `snowflake_unified_list_users` `bug-fix` Fixed OAuth account linking failing with an "invalid response" error on the callback. `snowflake_alter_table`, `snowflake_alter_warehouse`, `snowflake_call_procedure`, `snowflake_cancel_statement`, `snowflake_check_statement_status`, `snowflake_clone_database`, `snowflake_clone_table`, `snowflake_create_database`, `snowflake_create_function`, `snowflake_create_pipe`, `snowflake_create_procedure`, `snowflake_create_role`, `snowflake_create_schema`, `snowflake_create_stage`, `snowflake_create_stream`, `snowflake_create_table`, `snowflake_create_table_as_select`, `snowflake_create_task`, `snowflake_create_user`, `snowflake_create_view`, `snowflake_create_warehouse`, `snowflake_delete_database`, `snowflake_delete_function`, `snowflake_delete_pipe`, `snowflake_delete_procedure`, `snowflake_delete_role`, `snowflake_delete_schema`, `snowflake_delete_stage`, `snowflake_delete_stream`, `snowflake_delete_table`, `snowflake_delete_task`, `snowflake_delete_user`, `snowflake_delete_view`, `snowflake_delete_warehouse`, `snowflake_execute_query`, `snowflake_execute_sql_statement`, `snowflake_execute_task`, `snowflake_fetch_database`, `snowflake_fetch_function`, `snowflake_fetch_pipe`, `snowflake_fetch_procedure`, `snowflake_fetch_schema`, `snowflake_fetch_stage`, `snowflake_fetch_stream`, `snowflake_fetch_table`, `snowflake_fetch_task`, `snowflake_fetch_user`, `snowflake_fetch_view`, `snowflake_fetch_warehouse`, `snowflake_get_role_tags`, `snowflake_get_statement_results`, `snowflake_grant_future_privileges`, `snowflake_grant_privileges`, `snowflake_grant_role_to_user`, `snowflake_list_databases`, `snowflake_list_functions`, `snowflake_list_future_grants`, `snowflake_list_grants`, `snowflake_list_grants_of`, `snowflake_list_grants_on`, `snowflake_list_pipes`, `snowflake_list_procedures`, `snowflake_list_roles`, `snowflake_list_schemas`, `snowflake_list_stages`, `snowflake_list_streams`, `snowflake_list_tables`, `snowflake_list_tasks`, `snowflake_list_users`, `snowflake_list_views`, `snowflake_list_warehouses`, `snowflake_resume_task`, `snowflake_revoke_future_grants`, `snowflake_revoke_grants`, `snowflake_revoke_role_from_user`, `snowflake_set_role_tags`, `snowflake_start_warehouse`, `snowflake_suspend_task`, `snowflake_suspend_warehouse`, `snowflake_undrop_database`, `snowflake_undrop_table`, `snowflake_unified_get_me`, `snowflake_unified_get_organization`, `snowflake_unified_get_role`, `snowflake_unified_get_user`, `snowflake_unified_list_organizations`, `snowflake_unified_list_resource_types`, `snowflake_unified_list_resource_users`, `snowflake_unified_list_roles`, `snowflake_unified_list_users`, `snowflake_unset_role_tags`, `snowflake_update_database`, `snowflake_update_pipe`, `snowflake_update_schema`, `snowflake_update_stage`, `snowflake_update_table`, `snowflake_update_task`, `snowflake_update_user` `bug-fix` Fixed user and role list pagination on large accounts, fixed role lookups crashing for unmatched roles, and corrected pagination documentation for several other actions. `snowflake_list_databases`, `snowflake_list_roles`, `snowflake_list_schemas`, `snowflake_list_streams`, `snowflake_list_tables`, `snowflake_list_tasks`, `snowflake_list_users`, `snowflake_list_views`, `snowflake_unified_get_me`, `snowflake_unified_get_organization`, `snowflake_unified_get_role`, `snowflake_unified_get_user`, `snowflake_unified_list_organizations`, `snowflake_unified_list_resource_users`, `snowflake_unified_list_roles`, `snowflake_unified_list_users` `new-feature` Added an account-level OAuth option where the security integration credentials are entered when connecting the account, so each connected account can use its own Snowflake OAuth integration. `snowflake_alter_table`, `snowflake_alter_warehouse`, `snowflake_call_procedure`, `snowflake_cancel_statement`, `snowflake_check_statement_status`, `snowflake_clone_database`, `snowflake_clone_table`, `snowflake_create_database`, `snowflake_create_function`, `snowflake_create_pipe`, `snowflake_create_procedure`, `snowflake_create_role`, `snowflake_create_schema`, `snowflake_create_stage`, `snowflake_create_stream`, `snowflake_create_table`, `snowflake_create_table_as_select`, `snowflake_create_task`, `snowflake_create_user`, `snowflake_create_view`, `snowflake_create_warehouse`, `snowflake_delete_database`, `snowflake_delete_function`, `snowflake_delete_pipe`, `snowflake_delete_procedure`, `snowflake_delete_role`, `snowflake_delete_schema`, `snowflake_delete_stage`, `snowflake_delete_stream`, `snowflake_delete_table`, `snowflake_delete_task`, `snowflake_delete_user`, `snowflake_delete_view`, `snowflake_delete_warehouse`, `snowflake_execute_query`, `snowflake_execute_sql_statement`, `snowflake_execute_task`, `snowflake_fetch_database`, `snowflake_fetch_function`, `snowflake_fetch_pipe`, `snowflake_fetch_procedure`, `snowflake_fetch_schema`, `snowflake_fetch_stage`, `snowflake_fetch_stream`, `snowflake_fetch_table`, `snowflake_fetch_task`, `snowflake_fetch_user`, `snowflake_fetch_view`, `snowflake_fetch_warehouse`, `snowflake_get_role_tags`, `snowflake_get_statement_results`, `snowflake_grant_future_privileges`, `snowflake_grant_privileges`, `snowflake_grant_role_to_user`, `snowflake_list_databases`, `snowflake_list_functions`, `snowflake_list_future_grants`, `snowflake_list_grants`, `snowflake_list_grants_of`, `snowflake_list_grants_on`, `snowflake_list_pipes`, `snowflake_list_procedures`, `snowflake_list_roles`, `snowflake_list_schemas`, `snowflake_list_stages`, `snowflake_list_streams`, `snowflake_list_tables`, `snowflake_list_tasks`, `snowflake_list_users`, `snowflake_list_views`, `snowflake_list_warehouses`, `snowflake_resume_task`, `snowflake_revoke_future_grants`, `snowflake_revoke_grants`, `snowflake_revoke_role_from_user`, `snowflake_set_role_tags`, `snowflake_start_warehouse`, `snowflake_suspend_task`, `snowflake_suspend_warehouse`, `snowflake_undrop_database`, `snowflake_undrop_table`, `snowflake_unified_get_me`, `snowflake_unified_get_organization`, `snowflake_unified_get_role`, `snowflake_unified_get_user`, `snowflake_unified_list_organizations`, `snowflake_unified_list_resource_types`, `snowflake_unified_list_resource_users`, `snowflake_unified_list_roles`, `snowflake_unified_list_users`, `snowflake_unset_role_tags`, `snowflake_update_database`, `snowflake_update_pipe`, `snowflake_update_schema`, `snowflake_update_stage`, `snowflake_update_table`, `snowflake_update_task`, `snowflake_update_user` `bug-fix` `new-fields` `description-fix` Added FOREIGN KEY constraint support, renamed role tag actions to get_role_tags/set_role_tags/unset_role_tags, removed the unsupported LEGACY_SERVICE user type, and fixed several action and field descriptions. # Snyk Source: https://docs.stackone.com/connectors/snyk/index How to set up the Snyk connector, plus the actions and events that are available.
Snyk
v1.2.0
71 actions · 2 events · 2 auth methods
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses your Snyk account Auth Token — the token shown under Account settings > General — sent in the Authorization header... Uses a Snyk Personal Access Token (PAT) — created under Account settings > Personal Access Tokens — sent in the Authoriz... Optionally, configure receiving Events for Snyk into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/snyk/index.md for the full list. ## Events See https://docs.stackone.com/connectors/snyk/index.md for the full list. # Snyk Changelog Source: https://docs.stackone.com/connectors/snyk/changelog Release history for the Snyk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added native webhook support for the Snyk project snapshot event, provisioned automatically when the account is connected. `data-sync` Added data sync support to the organizations and groups list actions, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. `snyk_list_groups`, `snyk_list_organizations` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `guide-changes` Corrected the Auth Token and Personal Access Token connection guides to describe the real Snyk navigation — Account settings is opened from the profile menu at the bottom of the left sidebar, not a main-sidebar item — and retitled the Auth Token section to "Find your Auth Token". `bug-fix` Clarified that the list_targets created_gte filter requires a full RFC 3339 date-time (a plain calendar date is rejected with HTTP 400). `snyk_list_targets` `new-actions` Initial Snyk connector — manage the Snyk developer-security platform through the Snyk REST API. Covers organizations and groups, members and invitations, service accounts, monitored projects and scan targets, security issues (vulnerability, license, code, cloud, config and secrets findings), project collections, policies, audit logs, and SBOM generation and testing. # softgarden Source: https://docs.stackone.com/connectors/softgarden/index How to set up the softgarden connector, plus the actions that are available.
softgarden
Betav1.1.0
32 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses softgarden's OAuth 2.0 Client Credentials flow. Confidential client credentials (client\_id + client\_secret) must be... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/softgarden/index.md for the full list. # softgarden Changelog Source: https://docs.stackone.com/connectors/softgarden/changelog Release history for the softgarden connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for applications, application sources, jobboards and posting channels, so these records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh, because the softgarden Frontend API exposes no updated-since filter on any list endpoint. # SonarQube Cloud Source: https://docs.stackone.com/connectors/sonarcloud/index How to set up the SonarQube Cloud connector, plus the actions and events that are available.
SonarQube Cloud
Previewv1.3.0
102 actions · 6 events · 1 auth method
Developer Tools IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). SonarQube Cloud Personal Access Token sent as \`Authorization: Bearer <token>\` on every request. Generated from My accoun... Optionally, configure receiving Events for SonarQube Cloud into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sonarcloud/index.md for the full list. ## Events See https://docs.stackone.com/connectors/sonarcloud/index.md for the full list. # SonarQube Cloud Changelog Source: https://docs.stackone.com/connectors/sonarcloud/changelog Release history for the SonarQube Cloud connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Enabled scheduled data sync on 18 list actions, including projects, issues, rules, components, metrics, quality profiles, user groups, webhooks, and unified IAM users, groups, and organizations. Every sync refreshes in full each run, because SonarQube Cloud exposes no updated-since filter. `sonarcloud_components_search`, `sonarcloud_favorites_search`, `sonarcloud_issues_search`, `sonarcloud_languages_list`, `sonarcloud_metrics_search`, `sonarcloud_permissions_search_templates`, `sonarcloud_projects_search`, `sonarcloud_qualityprofiles_search`, `sonarcloud_rules_repositories`, `sonarcloud_rules_search`, `sonarcloud_settings_list_definitions`, `sonarcloud_unified_list_groups`, `sonarcloud_unified_list_organizations`, `sonarcloud_unified_list_users`, `sonarcloud_user_groups_search`, `sonarcloud_user_tokens_search`, `sonarcloud_webhooks_list`, `sonarcloud_webservices_list` `bug-fix` Standardized action category capitalization for more consistent portal filters. `sonarcloud_unified_get_group`, `sonarcloud_unified_get_me`, `sonarcloud_unified_get_organization`, `sonarcloud_unified_get_user`, `sonarcloud_unified_list_groups`, `sonarcloud_unified_list_organizations`, `sonarcloud_unified_list_users` `new-actions` Added identity and access management support for listing and viewing users, groups, organizations, and the current authenticated user. `sonarcloud_unified_get_group`, `sonarcloud_unified_get_me`, `sonarcloud_unified_get_organization`, `sonarcloud_unified_get_user`, `sonarcloud_unified_list_groups`, `sonarcloud_unified_list_organizations`, `sonarcloud_unified_list_users` `new-events` `new-actions` `native-webhooks` Added native webhook event support — 5 analysis-result events (project_analysis_completed, quality_gate_passed, quality_gate_failed, project_analysis_failed, project_analysis_canceled) split by background-task status and quality-gate result, with programmatic org-level webhook registration. Added 6 webhook management actions (list, create, update, delete, deliveries, delivery). Region is now a select field (EU/US). # Sophos Central Source: https://docs.stackone.com/connectors/sophos/index How to set up the Sophos Central connector, plus the actions that are available.
Sophos Central
Previewv1.2.0
54 actions · 1 auth method
Security IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 Client Credentials flow for machine-to-machine authentication with Sophos Central. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sophos/index.md for the full list. # Sophos Central Changelog Source: https://docs.stackone.com/connectors/sophos/changelog Release history for the Sophos Central connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `description-fix` Fixed Trigger Update Check, which failed on every call because it sent no request body. Create Policy now accepts only the fifteen policy types that work without a licence beyond Sophos Endpoint, and documents that policies targeting users are limited to five types and cannot mix endpoint and user targets. Clarified that creating an admin requires the directory user to have an email, that revoking an admin's only role deletes the admin record, that admin users cannot be deleted from the directory, and that endpoint group search needs searchFields. Six endpoint actions that cannot be exercised without an enrolled device are marked preview. `sophos_create_admin`, `sophos_create_policy`, `sophos_delete_user`, `sophos_list_admins`, `sophos_list_endpoint_groups`, `sophos_revoke_admin_role`, `sophos_trigger_update_check` `data-sync` `new-feature` Enabled scheduled data sync on nine list actions: directory users, user groups, admins, endpoint policies, roles and role permission sets, plus the unified IAM users, groups and roles actions. These collections can now be kept in sync and read without calling Sophos Central on every request. All nine refresh in full each run, because no endpoint in scope exposes an updated-since filter. Endpoint groups, endpoints, alerts and alert search are not included, because all four returned no records on the account used for verification. `sophos_list_admins`, `sophos_list_permission_sets`, `sophos_list_policies`, `sophos_list_roles`, `sophos_list_user_groups`, `sophos_list_users`, `sophos_unified_list_groups`, `sophos_unified_list_roles`, `sophos_unified_list_users` `bug-fix` Fixed user and group lists being truncated on large accounts. `sophos_unified_get_group`, `sophos_unified_get_me`, `sophos_unified_get_user`, `sophos_unified_list_groups`, `sophos_unified_list_roles`, `sophos_unified_list_users` `bug-fix` Fixed IAM list pagination past page 1 on unified_list_users and unified_list_groups — the raw response-derived result.next overrode StackOne's virtual-pagination cursor and could not survive a round-trip, causing 400 Invalid cursor past the first page. Replaced with a fixed page fan-out that lets virtual pagination own the cursor end-to-end. # SourceWhale Source: https://docs.stackone.com/connectors/sourcewhale/index How to set up the SourceWhale connector, plus the actions that are available.
SourceWhale
Betav0.2.0
6 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a static API key sent in the api-key header. The key is generated in the SourceWhale admin console and requires Adm... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sourcewhale/index.md for the full list. # SourceWhale Changelog Source: https://docs.stackone.com/connectors/sourcewhale/changelog Release history for the SourceWhale connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Enabled data synchronization for the campaigns and projects list endpoints. `sourcewhale_list_campaigns`, `sourcewhale_list_projects` `new-actions` Initial beta release of the SourceWhale connector with 6 actions covering campaigns, candidates, projects, and statistics. # Spark Hire Source: https://docs.stackone.com/connectors/sparkhire/index How to set up the Spark Hire connector, plus the actions that are available.
Spark Hire
Betav1.0.0
47 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires OAuth client credentials (Client ID and Client Secret) from your Spark Hire account. Contact your Spark Hire ac... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sparkhire/index.md for the full list. # Specter Source: https://docs.stackone.com/connectors/specter/index How to set up the Specter connector, plus the actions that are available.
Specter
Betav0.3.0
82 actions · 1 auth method
CRM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Specter uses a single team-level API key sent in the \`X-API-Key\` header on every request. Rate and credit limits apply a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/specter/index.md for the full list. # Specter Changelog Source: https://docs.stackone.com/connectors/specter/changelog Release history for the Specter connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync v2 support to 9 list actions including organisation members, network endpoints, revenue signals, and list/search indexes. `specter_get_network_companies`, `specter_get_network_people`, `specter_get_revenue_signals_by_date`, `specter_list_api_call_logs`, `specter_list_company_lists`, `specter_list_investor_lists`, `specter_list_organization_members`, `specter_list_people_lists`, `specter_list_saved_searches` `bugfix` Fixed delete action effects, corrected truncated descriptions, and improved AI search documentation. `specter_ai_search`, `specter_delete_company_list`, `specter_delete_investor_list`, `specter_delete_people_list`, `specter_delete_search`, `specter_get_acquisition_by_id`, `specter_get_talent_signal_by_id` `action-inputs-added` Fixed partial reference wiring and added missing pagination parameters (page, limit) to the get_network_connections_at_a_company action. # Spendesk Source: https://docs.stackone.com/connectors/spendesk/index How to set up the Spendesk connector, plus the actions that are available.
Spendesk
Betav1.2.0
33 actions · 1 auth method
Expense Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 with PKCE for user-authorized access to Spendesk spend data on behalf of a specific user. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/spendesk/index.md for the full list. # Spendesk Changelog Source: https://docs.stackone.com/connectors/spendesk/changelog Release history for the Spendesk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for suppliers, users, companies, settlements, purchase orders, analytical fields, cost centers, and payables, plus the unified user and organization lists, with incremental updates for suppliers. `spendesk_list_analytical_fields`, `spendesk_list_companies`, `spendesk_list_cost_centers`, `spendesk_list_purchase_orders`, `spendesk_list_settlements`, `spendesk_list_suppliers`, `spendesk_list_users`, `spendesk_search_payables`, `spendesk_unified_list_organizations`, `spendesk_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `spendesk_unified_get_me`, `spendesk_unified_get_organization`, `spendesk_unified_get_user`, `spendesk_unified_list_organizations`, `spendesk_unified_list_users` `new-actions` Added unified IAM actions for users, organizations, and credentials. # SpotDraft Source: https://docs.stackone.com/connectors/spotdraft/index How to set up the SpotDraft connector, plus the actions and events that are available.
SpotDraft
Previewv2.1.0
99 actions · 39 events · 1 auth method
Contract Lifecycle Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). SpotDraft uses dual custom HTTP headers (client-id and client-secret) for authentication. Credentials are generated from... Optionally, configure receiving Events for SpotDraft into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/spotdraft/index.md for the full list. ## Events See https://docs.stackone.com/connectors/spotdraft/index.md for the full list. # SpotDraft Changelog Source: https://docs.stackone.com/connectors/spotdraft/changelog Release history for the SpotDraft connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for contract types, contracts, counterparties, legal intakes, organization entities, templates and users, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. Contracts sync incrementally using SpotDraft's updated-since filter; the rest are full-refresh, because their endpoints expose no updated-since filter a sync can use. `spotdraft_auth_users_retrieve`, `spotdraft_contract_types_retrieve`, `spotdraft_counter_parties_list`, `spotdraft_legal_intake_retrieve`, `spotdraft_list_contracts`, `spotdraft_organizations_entities_retrieve`, `spotdraft_templates_list` `description-fix` Clarified where counterparty contact IDs and the primary-contact flag are returned in the counterparty list and contact update descriptions. `spotdraft_counter_parties_contacts_partial_update`, `spotdraft_counter_parties_list` `bug-fix` `breaking` Fixed template tag filters and documented the address fields for counterparty and entity creation, added a counterparty name filter, and delete actions now return a confirmation. `spotdraft_counter_parties_contacts_destroy`, `spotdraft_counter_parties_create`, `spotdraft_counter_parties_list`, `spotdraft_counter_parties_partial_update`, `spotdraft_list_contracts`, `spotdraft_organizations_entities_create`, `spotdraft_templates_list`, `spotdraft_webhooks_create`, `spotdraft_webhooks_destroy` `new-actions` Added inbound webhook event support for contract, approval, review, signature, counterparty, and email activity events (39 events) with automatic subscription provisioning. # Spotify Source: https://docs.stackone.com/connectors/spotify/index How to set up the Spotify connector, plus the actions that are available.
Spotify
Previewv1.1.0
47 actions · 1 auth method
Media
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 provides secure access to Spotify Web API. Create a Spotify App in the Developer Dashboard to get started. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/spotify/index.md for the full list. # Spotify Changelog Source: https://docs.stackone.com/connectors/spotify/changelog Release history for the Spotify connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to six library list actions (saved tracks, albums, shows, episodes, audiobooks, and the current user's playlists) so their records can be periodically synced into StackOne by full refresh, with paging handled automatically. # SPS Commerce Source: https://docs.stackone.com/connectors/spscommerce/index How to set up the SPS Commerce connector, plus the actions that are available.
SPS Commerce
Betav1.1.0
24 actions · 3 auth methods
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 Client Credentials for direct server-to-server access. Recommended when you are integrating SPS... Connect using OAuth 2.0 Authorization Code flow. Use this when StackOne is acting on behalf of an SPS customer (e.g., a... Connect using OAuth 2.0 Authorization Code flow with PKCE. Use this for desktop, mobile, or single-page apps that cannot... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/spscommerce/index.md for the full list. # SPS Commerce Changelog Source: https://docs.stackone.com/connectors/spscommerce/changelog Release history for the SPS Commerce connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added Data Sync support for submission forms, shipping labels, packing slips, and transaction history list endpoints. # Square Source: https://docs.stackone.com/connectors/square/index How to set up the Square connector, plus the actions and events that are available.
Square
Previewv1.3.0
137 actions · 96 events · 1 auth method
Payments E-Commerce IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 provides secure, delegated access to Square resources without sharing credentials. You need a Square Developer... Optionally, configure receiving Events for Square into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/square/index.md for the full list. ## Events See https://docs.stackone.com/connectors/square/index.md for the full list. # Square Changelog Source: https://docs.stackone.com/connectors/square/changelog Release history for the Square connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` `auth` Added 95 Square webhook events covering payments, orders, invoices, customers, catalog, inventory, bookings, loyalty, team and labor, set up manually with each linked account’s Native Webhook URL, plus a webhook setup guide. Added the APPOINTMENTS_READ and DEVICE_CREDENTIAL_MANAGEMENT scopes for booking and Terminal device events. `square_accept_dispute`, `square_add_group_to_customer`, `square_auth_test`, `square_batch_change_inventory`, `square_batch_delete_catalog_objects`, `square_batch_retrieve_catalog_objects`, `square_batch_retrieve_inventory_changes`, `square_batch_retrieve_inventory_counts`, `square_batch_retrieve_orders`, `square_batch_upsert_catalog_objects`, `square_bulk_create_customers`, `square_bulk_create_team_members`, `square_bulk_delete_customers`, `square_bulk_retrieve_customers`, `square_bulk_update_customers`, `square_bulk_update_team_members`, `square_calculate_order`, `square_cancel_invoice`, `square_cancel_payment`, `square_cancel_payment_by_idempotency_key`, `square_cancel_subscription`, `square_clone_order`, `square_complete_payment`, `square_create_break_type`, `square_create_card`, `square_create_customer`, `square_create_customer_group`, `square_create_dispute_evidence_text`, `square_create_gift_card`, `square_create_gift_card_activity`, `square_create_invoice`, `square_create_job`, `square_create_location`, `square_create_order`, `square_create_payment`, `square_create_payment_link`, `square_create_subscription`, `square_create_team_member`, `square_create_timecard`, `square_delete_break_type`, `square_delete_catalog_object`, `square_delete_customer`, `square_delete_customer_group`, `square_delete_dispute_evidence`, `square_delete_invoice`, `square_delete_payment_link`, `square_delete_timecard`, `square_disable_card`, `square_get_bank_account`, `square_get_break_type`, `square_get_invoice`, `square_get_payment`, `square_get_payment_refund`, `square_get_payout`, `square_link_customer_to_gift_card`, `square_list_bank_accounts`, `square_list_break_types`, `square_list_cards`, `square_list_catalog`, `square_list_customer_groups`, `square_list_customer_segments`, `square_list_customers`, `square_list_dispute_evidence`, `square_list_disputes`, `square_list_gift_card_activities`, `square_list_gift_cards`, `square_list_invoices`, `square_list_jobs`, `square_list_locations`, `square_list_merchants`, `square_list_payment_links`, `square_list_payment_refunds`, `square_list_payments`, `square_list_payout_entries`, `square_list_payouts`, `square_list_subscription_events`, `square_pay_order`, `square_publish_invoice`, `square_refund_payment`, `square_remove_group_from_customer`, `square_resume_subscription`, `square_retrieve_card`, `square_retrieve_catalog_object`, `square_retrieve_customer`, `square_retrieve_customer_group`, `square_retrieve_customer_segment`, `square_retrieve_dispute`, `square_retrieve_dispute_evidence`, `square_retrieve_gift_card`, `square_retrieve_gift_card_from_gan`, `square_retrieve_inventory_adjustment`, `square_retrieve_inventory_count`, `square_retrieve_inventory_physical_count`, `square_retrieve_job`, `square_retrieve_location`, `square_retrieve_merchant`, `square_retrieve_order`, `square_retrieve_payment_link`, `square_retrieve_subscription`, `square_retrieve_team_member`, `square_retrieve_timecard`, `square_retrieve_wage_setting`, `square_search_catalog_items`, `square_search_catalog_objects`, `square_search_customers`, `square_search_invoices`, `square_search_orders`, `square_search_subscriptions`, `square_search_team_members`, `square_search_timecards`, `square_submit_evidence`, `square_unified_get_group`, `square_unified_get_me`, `square_unified_get_organization`, `square_unified_get_role`, `square_unified_get_user`, `square_unified_list_groups`, `square_unified_list_organizations`, `square_unified_list_resource_types`, `square_unified_list_resource_users`, `square_unified_list_roles`, `square_unified_list_users`, `square_unlink_customer_from_gift_card`, `square_update_break_type`, `square_update_customer`, `square_update_customer_group`, `square_update_invoice`, `square_update_job`, `square_update_location`, `square_update_order`, `square_update_payment`, `square_update_payment_link`, `square_update_subscription`, `square_update_team_member`, `square_update_timecard`, `square_update_wage_setting`, `square_upsert_catalog_object` `data-sync` `bug-fix` Added Data Sync support to 28 list actions, and fixed unified IAM user and resource user listing failing whenever a page size was supplied. `square_batch_retrieve_inventory_counts`, `square_list_bank_accounts`, `square_list_break_types`, `square_list_cards`, `square_list_catalog`, `square_list_customer_groups`, `square_list_customer_segments`, `square_list_customers`, `square_list_disputes`, `square_list_gift_card_activities`, `square_list_gift_cards`, `square_list_jobs`, `square_list_locations`, `square_list_merchants`, `square_list_payment_links`, `square_list_payment_refunds`, `square_list_payments`, `square_list_payouts`, `square_search_catalog_items`, `square_search_catalog_objects`, `square_search_customers`, `square_search_subscriptions`, `square_search_team_members`, `square_search_timecards`, `square_unified_list_groups`, `square_unified_list_organizations`, `square_unified_list_resource_users`, `square_unified_list_roles`, `square_unified_list_users` `new-actions` Added unified IAM support for users, roles, groups, organizations, credentials, and resource users. # Squarespace Source: https://docs.stackone.com/connectors/squarespace/index How to set up the Squarespace connector, plus the actions and events that are available.
Squarespace
v2.0.2
27 actions · 10 events · 2 auth methods
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API key from your Squarespace site settings to authenticate Commerce API requests. Requires a Squarespace developer app, which starts in Demo Mode until reviewed. Idle connections expire after 7 days. Optionally, configure receiving Events for Squarespace into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/squarespace/index.md for the full list. ## Events See https://docs.stackone.com/connectors/squarespace/index.md for the full list. # Squarespace Changelog Source: https://docs.stackone.com/connectors/squarespace/changelog Release history for the Squarespace connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `improvement` Declared auth requirements on every action. Webhook events are now marked OAuth 2.0 only, with the scopes each topic needs. `squarespace_get_site_information` `guide` Updated the OAuth 2.0 connection guide for Squarespace self-service Developer Apps, with screenshots, Demo Mode and review steps, and the scopes to request. `squarespace_adjust_inventory`, `squarespace_assign_product_image_to_variant`, `squarespace_create_order`, `squarespace_create_product`, `squarespace_create_product_variant`, `squarespace_delete_product`, `squarespace_delete_product_image`, `squarespace_delete_product_variant`, `squarespace_fulfill_order`, `squarespace_get_inventory`, `squarespace_get_order`, `squarespace_get_product`, `squarespace_get_product_image_status`, `squarespace_get_profile`, `squarespace_get_site_information`, `squarespace_get_transaction`, `squarespace_list_inventory`, `squarespace_list_orders`, `squarespace_list_products`, `squarespace_list_profiles`, `squarespace_list_store_pages`, `squarespace_list_transactions`, `squarespace_reorder_product_image`, `squarespace_update_product`, `squarespace_update_product_image`, `squarespace_update_product_variant`, `squarespace_upload_product_image` `data-sync` Added DataSync support to six list actions (products, inventory, orders, profiles, transactions, and store pages) using cursor pagination, enabling periodic full-refresh syncs of each collection. `squarespace_list_inventory`, `squarespace_list_orders`, `squarespace_list_products`, `squarespace_list_profiles`, `squarespace_list_store_pages`, `squarespace_list_transactions` `guide-changes` `bug-fix` Aligned the API key setup guide with Squarespace's on-screen labels, and made afterImageId (reorder) and imageId (assign to variant) optional so omitting them sends null for the first-position and remove-assignment paths. `squarespace_assign_product_image_to_variant`, `squarespace_reorder_product_image` `description-fix` Clarified action descriptions for create_product, create_product_variant, and upload_product_image. `squarespace_create_product`, `squarespace_create_product_variant`, `squarespace_upload_product_image` `guide-changes` `guide-images` Updated the connection guide with clearer setup steps and added portal screenshots. # StackOne Source: https://docs.stackone.com/connectors/mcp_stackone/index How to set up the StackOne connector, plus the actions that are available.
StackOne
v1.0.0
637 actions · 1 auth method
MCP
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authorize through the MCP server. Endpoints and client registration are discovered at connect time. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mcp_stackone/index.md for the full list. # stackone 2 Source: https://docs.stackone.com/connectors/mcp_stackone2/index How to set up the stackone 2 connector, plus the actions that are available.
stackone 2
v1.0.0
4 actions · 1 auth method
MCP
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authorize through the MCP server. Endpoints and client registration are discovered at connect time. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/mcp_stackone2/index.md for the full list. # Staffology HR Source: https://docs.stackone.com/connectors/staffologyhr/index How to set up the Staffology HR connector, plus the actions that are available.
Staffology HR
Betav1.1.1
46 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using your Staffology HR username and password. The system will exchange credentials for access tokens. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/staffologyhr/index.md for the full list. # Staffology HR Changelog Source: https://docs.stackone.com/connectors/staffologyhr/changelog Release history for the Staffology HR connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the documentation link with a full connection guide covering enabling the API module in System Configuration and creating an API user to generate the username and password used to connect. `data-sync` Added data sync support for lookup types, so their records can be periodically pulled into StackOne and kept up to date. The sync is a full refresh, because the Staffology HR API exposes no updated-since filter a sync can use. # Statuspage Source: https://docs.stackone.com/connectors/statuspage/index How to set up the Statuspage connector, plus the actions that are available.
Statuspage
Previewv0.1.0
7 actions · 1 auth method
IAM Observability
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an Atlassian organization API key created by an organization admin in Atlassian Administration. The key is organiza... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/statuspage/index.md for the full list. # Statuspage Changelog Source: https://docs.stackone.com/connectors/statuspage/changelog Release history for the Statuspage connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-connector` Added Statuspage connector for reviewing who can sign in, covering organization lookups and Statuspage user access, including unified IAM. # Stripe Source: https://docs.stackone.com/connectors/stripe/index How to set up the Stripe connector, plus the actions and events that are available.
Stripe
Previewv1.1.0
138 actions · 49 events · 1 auth method
Payments Billing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Stripe Secret API Key or Restricted API Key for authentication. Find these in your Stripe Dashboard under Devel... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/stripe/index.md for the full list. ## Events See https://docs.stackone.com/connectors/stripe/index.md for the full list. # Stripe Changelog Source: https://docs.stackone.com/connectors/stripe/changelog Release history for the Stripe connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Added identity and access actions for listing Stripe team members and their SCIM-synced groups, with an optional SCIM API key. # StubHub Source: https://docs.stackone.com/connectors/stubhub/index How to set up the StubHub connector, plus the actions that are available.
StubHub
Betav0.2.0
81 actions · 2 auth methods
Events
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Delegated access on behalf of a signed-in StubHub user. Required for every seller listing, sale, payment, account and we... App-only access without a signed-in user. Reaches public catalog data only - events, venues and categories. Cannot acces... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/stubhub/index.md for the full list. # StubHub Changelog Source: https://docs.stackone.com/connectors/stubhub/changelog Release history for the StubHub connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `action-fix` All actions are now marked beta while end-to-end testing against a live StubHub account completes. `new-connector` `data-sync` New StubHub connector covering the event and venue catalog, seller listings and inventory, e-ticket fulfilment, sales, shipments and seller payouts. Supports both StubHub sign-in options, and keeps events, venues, seller listings, seller events, sales, addresses and payment methods up to date automatically with data sync. # SugarCRM Source: https://docs.stackone.com/connectors/sugarcrm/index How to set up the SugarCRM connector, plus the actions that are available.
SugarCRM
Betav1.1.0
47 actions · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses OAuth 2.0 Resource Owner Password Credentials grant. Requires a Sugar username, password, and instance URL. Tokens... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/sugarcrm/index.md for the full list. # SugarCRM Changelog Source: https://docs.stackone.com/connectors/sugarcrm/changelog Release history for the SugarCRM connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the input-free list actions (accounts, calls, cases, contacts, leads, meetings, notes, opportunities, tasks, and users) for scheduled full record syncs. # Supabase Source: https://docs.stackone.com/connectors/supabase/index How to set up the Supabase connector, plus the actions and events that are available.
Supabase
v2.1.1
138 actions · 9 events · 2 auth methods
Databases IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for personal scripts, CLI usage, and single-user automation. Requires registering an OAuth app. Supports fine-grained scopes across database, storage, and project management. Optionally, configure receiving Events for Supabase into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/supabase/index.md for the full list. ## Events See https://docs.stackone.com/connectors/supabase/index.md for the full list. # Supabase Changelog Source: https://docs.stackone.com/connectors/supabase/changelog Release history for the Supabase connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Updated the Personal Access Token and OAuth 2.0 connection guides to match the current Supabase dashboard, with screenshots for every step, and added a guide for authorizing the OAuth app. `data-sync` `bug-fix` Added data sync support for projects, organizations, SQL snippets, and the unified organization, role and user lists. Also resolved 9 behavioural issues, including listing all JIT database access, project logs with no time range, confirmations for realtime updates, and making service health and bulk function updates available. `supabase_bulk_update_functions`, `supabase_get_jit_access`, `supabase_get_project_logs`, `supabase_get_services_health`, `supabase_list_all_organizations`, `supabase_list_all_projects`, `supabase_list_all_snippets`, `supabase_list_jit_access`, `supabase_shutdown_realtime_connections`, `supabase_unified_list_organizations`, `supabase_unified_list_roles`, `supabase_unified_list_users`, `supabase_update_auth_config`, `supabase_update_function`, `supabase_update_realtime_config` `auth` `breaking` `bug-fix` `downstream-change` Actions that Supabase only allows with a personal access token are no longer offered on OAuth connections, project logs use Supabase's new logs endpoint, OAuth scopes now match Supabase's (including edge_functions and analytics:read), and fixes to service health names, bulk function updates, query parameters, function deploys and secret write confirmations. `supabase_activate_custom_hostname`, `supabase_activate_vanity_subdomain`, `supabase_apply_database_migration`, `supabase_authorize_jit_access`, `supabase_bulk_create_secrets`, `supabase_bulk_delete_secrets`, `supabase_bulk_update_functions`, `supabase_cancel_project_restoration`, `supabase_check_vanity_subdomain_availability`, `supabase_count_action_runs`, `supabase_create_a_branch`, `supabase_create_api_key`, `supabase_create_function`, `supabase_create_legacy_signing_key`, `supabase_create_login_role`, `supabase_create_organization`, `supabase_create_project`, `supabase_create_project_signing_key`, `supabase_create_sso_provider`, `supabase_create_tpa_integration`, `supabase_deactivate_vanity_subdomain`, `supabase_delete_a_branch`, `supabase_delete_api_key`, `supabase_delete_function`, `supabase_delete_jit_access`, `supabase_delete_login_roles`, `supabase_delete_project`, `supabase_delete_sso_provider`, `supabase_delete_tpa_integration`, `supabase_deploy_function`, `supabase_diff_a_branch`, `supabase_disable_preview_branching`, `supabase_disable_readonly_mode_temporarily`, `supabase_enable_database_webhook`, `supabase_generate_typescript_types`, `supabase_get_a_branch`, `supabase_get_a_branch_config`, `supabase_get_action_run`, `supabase_get_action_run_logs`, `supabase_get_all_projects_for_organization`, `supabase_get_api_key`, `supabase_get_auth_config`, `supabase_get_available_regions`, `supabase_get_database_config`, `supabase_get_database_metadata`, `supabase_get_function`, `supabase_get_function_body`, `supabase_get_function_combined_statistics`, `supabase_get_hostname_config`, `supabase_get_jit_access`, `supabase_get_jit_access_config`, `supabase_get_legacy_signing_key`, `supabase_get_migration_entry`, `supabase_get_network_restrictions`, `supabase_get_organization`, `supabase_get_pgsodium_config`, `supabase_get_pooler_config`, `supabase_get_postgres_upgrade_eligibility`, `supabase_get_postgres_upgrade_status`, `supabase_get_postgrest_config`, `supabase_get_project`, `supabase_get_project_api_keys`, `supabase_get_project_logs`, `supabase_get_project_pgbouncer_config`, `supabase_get_project_signing_key`, `supabase_get_readonly_mode_status`, `supabase_get_realtime_config`, `supabase_get_services_health`, `supabase_get_snippet`, `supabase_get_ssl_enforcement_config`, `supabase_get_sso_provider`, `supabase_get_storage_config`, `supabase_get_tpa_integration`, `supabase_get_usage_api_counts`, `supabase_get_usage_api_requests_count`, `supabase_get_vanity_subdomain_config`, `supabase_initialize_custom_hostname`, `supabase_list_action_runs`, `supabase_list_all_backups`, `supabase_list_all_branches`, `supabase_list_all_buckets`, `supabase_list_all_functions`, `supabase_list_all_organizations`, `supabase_list_all_projects`, `supabase_list_all_secrets`, `supabase_list_all_snippets`, `supabase_list_jit_access`, `supabase_list_migration_history`, `supabase_list_organization_members`, `supabase_list_project_signing_keys`, `supabase_list_sso_providers`, `supabase_list_tpa_integrations`, `supabase_merge_a_branch`, `supabase_patch_migration_entry`, `supabase_pause_project`, `supabase_push_a_branch`, `supabase_read_only_query`, `supabase_remove_project_signing_key`, `supabase_remove_read_replica`, `supabase_reset_a_branch`, `supabase_restore_a_branch`, `supabase_restore_pitr_backup`, `supabase_restore_project`, `supabase_reverify_dns_config`, `supabase_rollback_database_migrations`, `supabase_run_query`, `supabase_shutdown_realtime_connections`, `supabase_unified_get_me`, `supabase_unified_get_organization`, `supabase_unified_get_role`, `supabase_unified_get_user`, `supabase_unified_list_organizations`, `supabase_unified_list_resource_types`, `supabase_unified_list_resource_users`, `supabase_unified_list_roles`, `supabase_unified_list_users`, `supabase_update_a_branch_config`, `supabase_update_action_run_status`, `supabase_update_api_key`, `supabase_update_auth_config`, `supabase_update_custom_hostname`, `supabase_update_database_config`, `supabase_update_database_password`, `supabase_update_function`, `supabase_update_jit_access`, `supabase_update_jit_access_config`, `supabase_update_network_restrictions`, `supabase_update_pgsodium_config`, `supabase_update_pooler_config`, `supabase_update_postgrest_config`, `supabase_update_project`, `supabase_update_project_signing_key`, `supabase_update_realtime_config`, `supabase_update_ssl_enforcement_config`, `supabase_update_sso_provider`, `supabase_update_storage_config`, `supabase_upgrade_postgres_version`, `supabase_upsert_migration_without_applying` `new-feature` User roles now include project-level access, user list and user lookup return them only when requested with expand=roles, the role list comes straight from Supabase and now needs the organizations:read scope, unknown users return a not-found error, and user ids now come from Supabase's newer member list, so they can differ from earlier releases. `supabase_unified_get_me`, `supabase_unified_get_role`, `supabase_unified_get_user`, `supabase_unified_list_resource_types`, `supabase_unified_list_resource_users`, `supabase_unified_list_roles`, `supabase_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `supabase_unified_get_me`, `supabase_unified_get_organization`, `supabase_unified_get_role`, `supabase_unified_get_user`, `supabase_unified_list_organizations`, `supabase_unified_list_resource_types`, `supabase_unified_list_resource_users`, `supabase_unified_list_roles`, `supabase_unified_list_users` `new-actions` Added unified IAM support for organization members, roles, organizations, and current-connection credentials. User lists and lookups accept an optional organization filter — resolved automatically when the connection sees exactly one organization, with a clear error asking for it when several are visible. `supabase_unified_get_me`, `supabase_unified_get_organization`, `supabase_unified_get_role`, `supabase_unified_get_user`, `supabase_unified_list_organizations`, `supabase_unified_list_resource_types`, `supabase_unified_list_resource_users`, `supabase_unified_list_roles`, `supabase_unified_list_users` `new-events` `guide-images` Added manual webhook event support for storage objects, storage buckets, and auth users (9 events across INSERT/UPDATE/DELETE) via Supabase Database Webhooks, with a Native Webhook URL config field and a dashboard setup guide. # SurveyMonkey Source: https://docs.stackone.com/connectors/surveymonkey/index How to set up the SurveyMonkey connector, plus the actions that are available.
SurveyMonkey
v2.1.1
115 actions · 1 auth method
Surveys IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). You will need a paid SurveyMonkey plan with API access to create and use OAuth applications. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/surveymonkey/index.md for the full list. # SurveyMonkey Changelog Source: https://docs.stackone.com/connectors/surveymonkey/changelog Release history for the SurveyMonkey connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Updated Connector guide. `data-sync` Surveys, contacts, templates, folders and webhooks can now be kept in sync automatically, with surveys pulling only what changed since the last run. Scope requirements are now declared per authentication method, and fields that SurveyMonkey silently ignored have been removed so writes no longer appear to succeed when nothing was saved. `surveymonkey_copy_contact_list`, `surveymonkey_create_collector_message`, `surveymonkey_create_collector_response`, `surveymonkey_create_contact`, `surveymonkey_create_contact_in_list`, `surveymonkey_create_contact_list`, `surveymonkey_create_contacts_bulk`, `surveymonkey_create_contacts_bulk_global`, `surveymonkey_create_survey`, `surveymonkey_create_survey_collector`, `surveymonkey_create_survey_folder`, `surveymonkey_create_survey_language_translation`, `surveymonkey_create_survey_page`, `surveymonkey_create_survey_question`, `surveymonkey_create_survey_share`, `surveymonkey_create_webhook`, `surveymonkey_delete_all_collector_responses`, `surveymonkey_delete_collector`, `surveymonkey_delete_collector_message`, `surveymonkey_delete_collector_response`, `surveymonkey_delete_contact`, `surveymonkey_delete_contact_list`, `surveymonkey_delete_survey`, `surveymonkey_delete_survey_language_translation`, `surveymonkey_delete_survey_page`, `surveymonkey_delete_survey_question`, `surveymonkey_delete_webhook`, `surveymonkey_get_bulk_collector_responses`, `surveymonkey_get_bulk_survey_responses`, `surveymonkey_get_collector`, `surveymonkey_get_collector_message`, `surveymonkey_get_collector_recipient`, `surveymonkey_get_collector_response`, `surveymonkey_get_collector_response_details`, `surveymonkey_get_collector_stats`, `surveymonkey_get_contact`, `surveymonkey_get_contact_field`, `surveymonkey_get_contact_list`, `surveymonkey_get_current_user`, `surveymonkey_get_error`, `surveymonkey_get_message_stats`, `surveymonkey_get_survey`, `surveymonkey_get_survey_details`, `surveymonkey_get_survey_language_translation`, `surveymonkey_get_survey_page`, `surveymonkey_get_survey_page_rollups`, `surveymonkey_get_survey_page_trends`, `surveymonkey_get_survey_question`, `surveymonkey_get_survey_question_rollups`, `surveymonkey_get_survey_question_trends`, `surveymonkey_get_survey_response`, `surveymonkey_get_survey_response_details`, `surveymonkey_get_survey_rollups`, `surveymonkey_get_survey_trends`, `surveymonkey_get_webhook`, `surveymonkey_list_all_survey_languages`, `surveymonkey_list_collector_messages`, `surveymonkey_list_collector_recipients`, `surveymonkey_list_collector_responses`, `surveymonkey_list_contact_fields`, `surveymonkey_list_contact_lists`, `surveymonkey_list_contacts`, `surveymonkey_list_contacts_bulk`, `surveymonkey_list_contacts_in_list`, `surveymonkey_list_contacts_in_list_bulk`, `surveymonkey_list_errors`, `surveymonkey_list_message_recipients`, `surveymonkey_list_question_bank_questions`, `surveymonkey_list_roles`, `surveymonkey_list_survey_categories`, `surveymonkey_list_survey_collectors`, `surveymonkey_list_survey_folders`, `surveymonkey_list_survey_languages`, `surveymonkey_list_survey_pages`, `surveymonkey_list_survey_questions`, `surveymonkey_list_survey_responses`, `surveymonkey_list_survey_shares`, `surveymonkey_list_survey_templates`, `surveymonkey_list_surveys`, `surveymonkey_list_team_survey_templates`, `surveymonkey_list_webhooks`, `surveymonkey_merge_contact_lists`, `surveymonkey_replace_collector`, `surveymonkey_replace_collector_response`, `surveymonkey_replace_contact`, `surveymonkey_replace_contact_list`, `surveymonkey_replace_survey`, `surveymonkey_replace_survey_page`, `surveymonkey_replace_survey_question`, `surveymonkey_replace_webhook`, `surveymonkey_send_collector_message`, `surveymonkey_unified_get_group`, `surveymonkey_unified_get_me`, `surveymonkey_unified_get_organization`, `surveymonkey_unified_get_role`, `surveymonkey_unified_get_user`, `surveymonkey_unified_list_groups`, `surveymonkey_unified_list_organizations`, `surveymonkey_unified_list_resource_types`, `surveymonkey_unified_list_resource_users`, `surveymonkey_unified_list_roles`, `surveymonkey_unified_list_users`, `surveymonkey_update_collector`, `surveymonkey_update_collector_message`, `surveymonkey_update_collector_response`, `surveymonkey_update_contact`, `surveymonkey_update_contact_field`, `surveymonkey_update_contact_list`, `surveymonkey_update_survey`, `surveymonkey_update_survey_language_translation`, `surveymonkey_update_survey_page`, `surveymonkey_update_survey_question`, `surveymonkey_update_survey_response`, `surveymonkey_update_survey_share`, `surveymonkey_update_webhook` `bug-fix` Unified IAM users now return email, names and status, plus team roles and workgroups when you ask for roles and groups. Every role on a user can be looked up by id. `surveymonkey_unified_get_group`, `surveymonkey_unified_get_me`, `surveymonkey_unified_get_organization`, `surveymonkey_unified_get_role`, `surveymonkey_unified_get_user`, `surveymonkey_unified_list_groups`, `surveymonkey_unified_list_organizations`, `surveymonkey_unified_list_resource_types`, `surveymonkey_unified_list_resource_users`, `surveymonkey_unified_list_roles`, `surveymonkey_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, resource users, and credentials. Covers SurveyMonkey team members, workgroups, and the organization role catalog. # Swagger Source: https://docs.stackone.com/connectors/swagger/index How to set up the Swagger connector, plus the actions and events that are available.
Swagger
v1.2.0
62 actions · 2 events · 1 auth method
Developer Tools
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Swagger (SwaggerHub) authenticates with a single account-level API key sent in the Authorization header. The same key is... Optionally, configure receiving Events for Swagger into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/swagger/index.md for the full list. ## Events See https://docs.stackone.com/connectors/swagger/index.md for the full list. # Swagger Changelog Source: https://docs.stackone.com/connectors/swagger/changelog Release history for the Swagger connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added native webhook support for API version saved and published events, delivered through SwaggerHub webhook integrations added per API. `data-sync` Added scheduled data sync to the templates and portals list actions, so these collections can be kept in sync and read back without calling Swagger on every request. Both sync by full refresh, since Swagger exposes no updated-since filter for these endpoints. `swagger_list_portals`, `swagger_list_templates` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Mutating API, domain and project actions now return a confirmation message and the affected resource identifiers instead of an empty body. `swagger_add_project_spec`, `swagger_clone_api_version`, `swagger_create_or_update_api`, `swagger_create_or_update_domain`, `swagger_create_project`, `swagger_delete_api`, `swagger_delete_api_version`, `swagger_delete_domain`, `swagger_delete_domain_version`, `swagger_delete_project`, `swagger_fork_api_version`, `swagger_set_api_default_version`, `swagger_update_project` `bug-fix` Standardized action category capitalization for more consistent portal filters. `swagger_add_project_spec`, `swagger_clone_api_version`, `swagger_create_api_integration`, `swagger_create_or_update_api`, `swagger_create_or_update_domain`, `swagger_create_or_update_template`, `swagger_create_portal`, `swagger_create_portal_product`, `swagger_create_portal_template`, `swagger_create_project`, `swagger_create_section_table_of_contents`, `swagger_delete_api`, `swagger_delete_api_integration`, `swagger_delete_api_version`, `swagger_delete_domain`, `swagger_delete_domain_version`, `swagger_delete_portal`, `swagger_delete_portal_template`, `swagger_delete_product`, `swagger_delete_project`, `swagger_delete_table_of_contents`, `swagger_delete_template`, `swagger_fork_api_version`, `swagger_fork_template_version`, `swagger_get_api_definition`, `swagger_get_api_integration`, `swagger_get_api_standardization`, `swagger_get_api_validation`, `swagger_get_api_versions`, `swagger_get_attachment`, `swagger_get_document`, `swagger_get_domain_definition`, `swagger_get_domain_versions`, `swagger_get_portal`, `swagger_get_portal_template`, `swagger_get_product`, `swagger_get_product_sections`, `swagger_get_project`, `swagger_get_project_members`, `swagger_get_published_content`, `swagger_get_section`, `swagger_get_section_table_of_contents`, `swagger_get_template_versions`, `swagger_list_api_integrations`, `swagger_list_attachments`, `swagger_list_owner_apis`, `swagger_list_owner_domains`, `swagger_list_portal_access_requests`, `swagger_list_portal_products`, `swagger_list_portal_templates`, `swagger_list_portals`, `swagger_list_projects`, `swagger_list_templates`, `swagger_search_apis_and_domains`, `swagger_set_api_default_version`, `swagger_update_api_integration`, `swagger_update_document`, `swagger_update_portal`, `swagger_update_portal_template`, `swagger_update_product`, `swagger_update_project`, `swagger_update_table_of_contents` `new-actions` Initial Swagger (SmartBear) connector — manage API and Domain design assets in the SwaggerHub Registry (versioning, clone/fork, lifecycle, standardization, validation, integrations, projects, templates) and the consumer-facing Swagger Portal (portals, products, sections, table of contents, documents, attachments). # Tableau Source: https://docs.stackone.com/connectors/tableau/index How to set up the Tableau connector, plus the actions and events that are available.
Tableau
Previewv1.2.0
122 actions · 23 events · 1 auth method
Analytics IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Tableau Personal Access Token (PAT) for secure API authentication. PATs are long-lived tokens that can be revok... Optionally, configure receiving Events for Tableau into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/tableau/index.md for the full list. ## Events See https://docs.stackone.com/connectors/tableau/index.md for the full list. # Tableau Changelog Source: https://docs.stackone.com/connectors/tableau/changelog Release history for the Tableau connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `data-sync` Added webhook event support for 22 event types, and data sync support for site users, custom views, extract refresh tasks, authentication configurations, sites, schedules, Active Directory domains and the unified IAM users, groups and roles lists. `tableau_get_users_on_site`, `tableau_list_authentication_configurations`, `tableau_list_custom_views`, `tableau_list_extract_refresh_tasks_for_site`, `tableau_list_schedules`, `tableau_list_server_active_directory_domains`, `tableau_list_sites`, `tableau_unified_list_groups`, `tableau_unified_list_roles`, `tableau_unified_list_users` `bug-fix` Group lists now read up to 50,000 groups per site instead of the first 1000. `tableau_unified_list_groups` `bug-fix` User lookups now return the Tableau login name as the username. `tableau_unified_get_user`, `tableau_unified_list_users` `bug-fix` Marked revoke_admin_personal_access_tokens as preview (Server-only). Removed retired CreateRefreshMetrics capability and wrapped add_default_workbook/datasource_permissions responses in the data envelope. Improved add_user_to_site/update_user, query_jobs, and update_workbook descriptions; made update_user.language an enum. `tableau_add_datasource_permissions`, `tableau_add_default_datasource_permissions`, `tableau_add_default_workbook_permissions`, `tableau_add_project_permissions`, `tableau_add_user_to_site`, `tableau_add_workbook_permissions`, `tableau_create_project`, `tableau_delete_default_workbook_permissions_for_group`, `tableau_delete_default_workbook_permissions_for_user`, `tableau_delete_workbook_permission_for_group`, `tableau_delete_workbook_permission_for_user`, `tableau_query_jobs`, `tableau_revoke_admin_personal_access_tokens`, `tableau_update_datasource`, `tableau_update_embedding_settings`, `tableau_update_project`, `tableau_update_user`, `tableau_update_workbook` `new-fields` `bug-fix` Added language and locale to update_user and view selection (views.view) to update_workbook; corrected update_workbook weekDay to a title-case enum. `tableau_update_user`, `tableau_update_workbook` `bug-fix` Fixed unified IAM groups, resource users, and users list/get actions that silently returned empty data, corrected the resource types identifier shape, repaired the get_role name/description expressions, and wired the users email filter. # Taleez Source: https://docs.stackone.com/connectors/taleez/index How to set up the Taleez connector, plus the actions that are available.
Taleez
Betav1.1.0
34 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a Taleez API secret key. Generate it from your Taleez account settings under API integrations. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/taleez/index.md for the full list. # Taleez Changelog Source: https://docs.stackone.com/connectors/taleez/changelog Release history for the Taleez connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for candidates, jobs, pools, recruiters, units, events, candidate and job properties, and spontaneous questions. All syncs are full-refresh — the Taleez API exposes no updated-since filter. # Talend Source: https://docs.stackone.com/connectors/talend/index How to set up the Talend connector, plus the actions that are available.
Talend
Previewv1.2.2
71 actions · 2 auth methods
Data Integration IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 Client Credentials flow using Service Accounts for machine-to-machine authentication. Best for personal use and development. Provides access scoped to your Talend Cloud account. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/talend/index.md for the full list. # Talend Changelog Source: https://docs.stackone.com/connectors/talend/changelog Release history for the Talend connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists now return service accounts after the last user at any page size instead of only when the first page had room. `talend_unified_list_users` `bug-fix` Fixed unified user lists failing when the connection can't list service accounts, unified lists failing whenever there is more than one page of results, and a single user lookup breaking when the connection can't read that user's roles or groups. `talend_unified_get_user`, `talend_unified_list_groups`, `talend_unified_list_resource_users`, `talend_unified_list_roles`, `talend_unified_list_users` `data-sync` Enabled DataSync for list actions to periodically sync records into StackOne. `talend_list_artifacts`, `talend_list_connections`, `talend_list_environments`, `talend_list_groups`, `talend_list_plan_executions`, `talend_list_plans`, `talend_list_remote_engine_clusters`, `talend_list_remote_engines`, `talend_list_roles`, `talend_list_schedules`, `talend_list_tasks`, `talend_list_users`, `talend_list_workspaces`, `talend_unified_list_groups`, `talend_unified_list_organizations`, `talend_unified_list_roles`, `talend_unified_list_users` `guide-changes` Refreshed the OAuth 2.0 and Personal Access Token connection guides from Talend Cloud's current documentation, including service account and personal access token steps and the Management Console access requirements. # TalentLMS Source: https://docs.stackone.com/connectors/talentlms/index How to set up the TalentLMS connector, plus the actions that are available.
TalentLMS
Betav1.2.0
43 actions · 1 auth method
LMS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using your TalentLMS API key with HTTP Basic Auth. Only super administrators can activate API support and o... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/talentlms/index.md for the full list. # TalentLMS Changelog Source: https://docs.stackone.com/connectors/talentlms/changelog Release history for the TalentLMS connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for users, courses, categories, groups, and branches, for custom registration and course fields, and for the unified user, group, and organization lists. `talentlms_get_custom_course_fields`, `talentlms_get_custom_registration_fields`, `talentlms_list_branches`, `talentlms_list_categories`, `talentlms_list_courses`, `talentlms_list_groups`, `talentlms_list_users`, `talentlms_unified_list_groups`, `talentlms_unified_list_organizations`, `talentlms_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `talentlms_unified_get_group`, `talentlms_unified_get_me`, `talentlms_unified_get_organization`, `talentlms_unified_get_user`, `talentlms_unified_list_groups`, `talentlms_unified_list_organizations`, `talentlms_unified_list_users` `new-actions` Added unified IAM actions for users, groups, organizations, and credentials. # TalentLyft Source: https://docs.stackone.com/connectors/talentlyft/index How to set up the TalentLyft connector, plus the actions and events that are available.
TalentLyft
v1.2.0
44 actions · 28 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Access Token authentication requires generating a token from your TalentLyft account settings. Optionally, configure receiving Events for TalentLyft into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/talentlyft/index.md for the full list. ## Events See https://docs.stackone.com/connectors/talentlyft/index.md for the full list. # TalentLyft Changelog Source: https://docs.stackone.com/connectors/talentlyft/changelog Release history for the TalentLyft connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-events` Add 27 webhook events (candidates, jobs, calendar events, blog posts and GDPR requests) with automatic subscription setup. `data-sync` Add DataSync support to 12 list actions (candidates, jobs, employees, departments, members, pipelines, tags, job tags, forms, events, rejection reasons) — page-based or single-call full refresh. `talentlyft_list_candidates`, `talentlyft_list_departments`, `talentlyft_list_employees`, `talentlyft_list_events`, `talentlyft_list_forms`, `talentlyft_list_job_tags_paged`, `talentlyft_list_jobs`, `talentlyft_list_jobtags`, `talentlyft_list_members`, `talentlyft_list_pipelines`, `talentlyft_list_rejection_reasons`, `talentlyft_list_tags` `behavioral-fixes` update_candidate — document PreferredLanguage (ISO 639-1 code) and Location (geocodable Address). update_job — remove AdditionalLocations (never persists on update). `talentlyft_create_candidate`, `talentlyft_update_candidate`, `talentlyft_update_job` `behavioral-fixes` Behavioral testing fixes for candidate, job, employee, and pipeline actions. `talentlyft_create_job`, `talentlyft_delete_job`, `talentlyft_list_jobs`, `talentlyft_move_to_stage`, `talentlyft_update_candidate`, `talentlyft_update_employee`, `talentlyft_update_job`, `talentlyft_update_pipeline` `guide-changes` `guide-images` Updated the connection guide with setup steps and screenshots. # Talkdesk Source: https://docs.stackone.com/connectors/talkdesk/index How to set up the Talkdesk connector, plus the actions and events that are available.
Talkdesk
Betav2.1.0
36 actions · 7 events · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using OAuth 2.0 Authorization Code flow. Provides user-level access to Talkdesk APIs. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/talkdesk/index.md for the full list. ## Events See https://docs.stackone.com/connectors/talkdesk/index.md for the full list. # Talkdesk Changelog Source: https://docs.stackone.com/connectors/talkdesk/changelog Release history for the Talkdesk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data synchronisation support for 8 list actions with page-based pagination, including incremental sync for cases and prompts. `talkdesk_attribute_categories_list`, `talkdesk_list_attributes`, `talkdesk_list_campaigns`, `talkdesk_list_cases`, `talkdesk_list_contacts`, `talkdesk_list_prompts`, `talkdesk_list_queues`, `talkdesk_list_users` `auth` `breaking-changes` Migrated from requiredScopes to authRequirements for per-auth-type scope control. # TazWorks Source: https://docs.stackone.com/connectors/tazworks/index How to set up the TazWorks connector, plus the actions that are available.
TazWorks
Betav0.2.0
83 actions · 1 auth method
Background Checks IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a JWT API token generated from an API Application in the TazAPI Developer Portal. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/tazworks/index.md for the full list. # TazWorks Changelog Source: https://docs.stackone.com/connectors/tazworks/changelog Release history for the TazWorks connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for clients and CRA base products, enabling scheduled full-refresh syncs of the client directory and base product catalog. `tazworks_list_base_products`, `tazworks_list_clients` `new-actions` Initial release with 83 actions covering background check ordering and results, applicant management with detail data, order attachments, continuous-monitoring searches, and CRA client, user, and product administration. # Teamleader Focus Source: https://docs.stackone.com/connectors/teamleader/index How to set up the Teamleader Focus connector, plus the actions and events that are available.
Teamleader Focus
Previewv2.1.2
62 actions · 8 events · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authorisation code flow. Teamleader issues 1-hour Bearer access tokens (RS256 JWT) plus single-use refresh tok... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/teamleader/index.md for the full list. ## Events See https://docs.stackone.com/connectors/teamleader/index.md for the full list. # Teamleader Focus Changelog Source: https://docs.stackone.com/connectors/teamleader/changelog Release history for the Teamleader Focus connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists now include deactivated users and read up to 1000 users, returning an error on larger accounts instead of a partial list. Team and account lookups now return a not-found error for an unknown id. `teamleader_unified_get_group`, `teamleader_unified_get_me`, `teamleader_unified_get_organization`, `teamleader_unified_get_user`, `teamleader_unified_list_groups`, `teamleader_unified_list_organizations`, `teamleader_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `teamleader_list_activity_types`, `teamleader_list_ticket_statuses`, `teamleader_list_work_types`, `teamleader_unified_get_group`, `teamleader_unified_get_me`, `teamleader_unified_get_organization`, `teamleader_unified_get_user`, `teamleader_unified_list_groups`, `teamleader_unified_list_organizations`, `teamleader_unified_list_users` `new-actions` Added unified IAM actions for users, groups, organizations, and credentials. `teamleader_unified_get_group`, `teamleader_unified_get_me`, `teamleader_unified_get_organization`, `teamleader_unified_get_user`, `teamleader_unified_list_groups`, `teamleader_unified_list_organizations`, `teamleader_unified_list_users` `teamleader_accept_quotation`, `teamleader_book_invoice`, `teamleader_cancel_event`, `teamleader_complete_task`, `teamleader_create_company`, `teamleader_create_contact`, `teamleader_create_deal`, `teamleader_create_event`, `teamleader_create_invoice_draft`, `teamleader_create_quotation`, `teamleader_create_task`, `teamleader_create_ticket`, `teamleader_delete_company`, `teamleader_delete_contact`, `teamleader_delete_deal`, `teamleader_delete_invoice`, `teamleader_delete_quotation`, `teamleader_delete_task`, `teamleader_get_company`, `teamleader_get_contact`, `teamleader_get_current_user`, `teamleader_get_deal`, `teamleader_get_department`, `teamleader_get_event`, `teamleader_get_invoice`, `teamleader_get_quotation`, `teamleader_get_task`, `teamleader_get_ticket`, `teamleader_get_user`, `teamleader_list_activity_types`, `teamleader_list_companies`, `teamleader_list_contacts`, `teamleader_list_deals`, `teamleader_list_departments`, `teamleader_list_events`, `teamleader_list_invoices`, `teamleader_list_quotations`, `teamleader_list_tasks`, `teamleader_list_ticket_statuses`, `teamleader_list_tickets`, `teamleader_list_users`, `teamleader_list_work_types`, `teamleader_lose_deal`, `teamleader_register_invoice_payment`, `teamleader_send_invoice`, `teamleader_send_quotation`, `teamleader_update_company`, `teamleader_update_contact`, `teamleader_update_deal`, `teamleader_update_event`, `teamleader_update_invoice`, `teamleader_update_quotation`, `teamleader_update_task`, `teamleader_update_ticket`, `teamleader_win_deal` `bug-fix` `new-actions` `schema-change` Breaking: object-typed inputs (page, sort, custom_fields, filter, expiry, expected_payment_method, grouped_lines, and other nested objects) now declare structured child properties instead of prose-only descriptions — callers sending undocumented sub-fields will be rejected by input validation. Enum constraints added to initial_reply and language. Added 3 catalog list actions (list_activity_types, list_ticket_statuses, list_work_types) for in-connector ID discovery. Hardened input schema documentation across CRM/invoicing actions. Moved send_quotation and send_invoice to preview. # Teamtailor Source: https://docs.stackone.com/connectors/teamtailor/index How to set up the Teamtailor connector, plus the actions and events that are available.
Teamtailor
v1.2.0
106 actions · 16 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Company Admin access in your Teamtailor account is required to generate API keys. Optionally, configure receiving Events for Teamtailor into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/teamtailor/index.md for the full list. ## Events See https://docs.stackone.com/connectors/teamtailor/index.md for the full list. # Teamtailor Changelog Source: https://docs.stackone.com/connectors/teamtailor/changelog Release history for the Teamtailor connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added 15 Teamtailor webhook events for candidates, jobs, job applications, users and audit events, delivered through a Native Webhook URL added under Settings > Integrations > Webhooks, with a setup guide. `data-sync` `bug-fix` Added data sync support for list actions, fixed requisition create and update payloads with full field coverage, and surfaced provider errors that Teamtailor replays with a 200 status. # TeamViewer Source: https://docs.stackone.com/connectors/teamviewer/index How to set up the TeamViewer connector, plus the actions that are available.
TeamViewer
Betav1.2.0
102 actions · 1 auth method
Device Management IAM Meetings
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with a TeamViewer Script Token created in the Management Console. The token is a static bearer credential c... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/teamviewer/index.md for the full list. # TeamViewer Changelog Source: https://docs.stackone.com/connectors/teamviewer/changelog Release history for the TeamViewer connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for users, user groups, user roles, contacts, groups, device groups, managed devices, company managed devices, meetings and the unified users, groups, roles and organizations. `teamviewer_list_company_managed_devices`, `teamviewer_list_contacts`, `teamviewer_list_device_groups`, `teamviewer_list_groups`, `teamviewer_list_managed_devices`, `teamviewer_list_meetings`, `teamviewer_list_user_groups`, `teamviewer_list_user_roles`, `teamviewer_list_users`, `teamviewer_unified_list_groups`, `teamviewer_unified_list_organizations`, `teamviewer_unified_list_roles`, `teamviewer_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `teamviewer_unified_get_group`, `teamviewer_unified_get_me`, `teamviewer_unified_get_organization`, `teamviewer_unified_get_role`, `teamviewer_unified_get_user`, `teamviewer_unified_list_groups`, `teamviewer_unified_list_organizations`, `teamviewer_unified_list_resource_types`, `teamviewer_unified_list_resource_users`, `teamviewer_unified_list_roles`, `teamviewer_unified_list_users` `new-actions` Added unified IAM actions for users, roles, groups, organizations, credentials, resource users, and resource types, using the connector's existing Script Token authentication. # Teamwork Source: https://docs.stackone.com/connectors/teamwork/index How to set up the Teamwork connector, plus the actions and events that are available.
Teamwork
Previewv2.2.0
125 actions · 124 events · 1 auth method
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your API Token from Teamwork Profile Settings. Admin privileges may be required for some operations. Optionally, configure receiving Events for Teamwork into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/teamwork/index.md for the full list. ## Events See https://docs.stackone.com/connectors/teamwork/index.md for the full list. # Teamwork Changelog Source: https://docs.stackone.com/connectors/teamwork/changelog Release history for the Teamwork connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Added webhook events for 124 Teamwork event types covering projects, tasks, task lists, milestones, messages, comments, files, notebooks, links, people, companies, teams, time entries, invoices, budgets, risks, forms, workflows and portfolio boards, with webhooks created automatically when an account connects. `data-sync` `new-feature` Added data sync support to 17 list actions, covering projects, tasks, tasklists, time entries, people, companies, comments, messages, milestones, notebooks, risks, tags and project updates. Added the missing updatedAfter filter to list_notebooks, and moved get_all_risks to preview because the Risk Register requires a paid Teamwork plan. `teamwork_get_all_project_updates`, `teamwork_get_all_risks`, `teamwork_get_all_running_timers`, `teamwork_get_all_tags`, `teamwork_get_all_tasklists`, `teamwork_get_all_tasks`, `teamwork_get_all_template_task_lists`, `teamwork_get_all_time_entries`, `teamwork_list_comments`, `teamwork_list_companies`, `teamwork_list_messages`, `teamwork_list_milestones`, `teamwork_list_notebooks`, `teamwork_list_people`, `teamwork_list_project_templates`, `teamwork_list_projects`, `teamwork_list_starred_projects` `bug-fix` `breaking-change` Consolidated create/update request bodies into single object inputs and switched delete/complete/lock actions to return the raw provider response. # Telegram Source: https://docs.stackone.com/connectors/telegram/index How to set up the Telegram connector, plus the actions and events that are available.
Telegram
v1.2.0
38 actions · 28 events · 1 auth method
Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create a Telegram bot and obtain the Bot Token from BotFather. Open Telegram, search for @BotFather, send /newbot, follo... Optionally, configure receiving Events for Telegram into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/telegram/index.md for the full list. ## Events See https://docs.stackone.com/connectors/telegram/index.md for the full list. # Telegram Changelog Source: https://docs.stackone.com/connectors/telegram/changelog Release history for the Telegram connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added inbound webhook events for all 27 Telegram update types (messages, channel posts, business messages, reactions, inline and callback queries, payments, polls, chat members, boosts, and managed bots). StackOne registers the bot's webhook automatically via setWebhook and removes it on disconnect. `bug-fix` `guide` Fixed reply_markup so inline and custom keyboards can be sent across all message actions, clarified where chat owner and administrator details are returned, and refreshed the Bot Token connection guide. # Terraform Source: https://docs.stackone.com/connectors/terraform/index How to set up the Terraform connector, plus the actions and events that are available.
Terraform
v3.1.0
130 actions · 10 events · 1 auth method
Infrastructure IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Generate an API token from your Terraform Cloud or Terraform Enterprise account settings. Optionally, configure receiving Events for Terraform into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/terraform/index.md for the full list. ## Events See https://docs.stackone.com/connectors/terraform/index.md for the full list. # Terraform Changelog Source: https://docs.stackone.com/connectors/terraform/changelog Release history for the Terraform connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to six collection actions — organizations, the current user's organization memberships, and the unified users, groups, organizations and roles — so these collections can be kept in sync and searched without calling Terraform on every request. Organizations and the unified users, groups and organizations page through results automatically; memberships and the unified roles are returned in full by a single request. All syncs use full refreshes, because Terraform's list endpoints offer no last-updated filter. `terraform_list_organizations`, `terraform_list_own_memberships`, `terraform_unified_list_groups`, `terraform_unified_list_organizations`, `terraform_unified_list_roles`, `terraform_unified_list_users` `breaking` `bug-fix` Removes the two configuration version download actions - over MCP they returned an empty result with no file and reported errors as a generic 500. List SSH Keys is now generally available, and the run timeframe, notification and organization descriptions now match what the API actually accepts. `terraform_download_configuration_version`, `terraform_download_run_configuration_version` `terraform_create_notification_config`, `terraform_list_organizations`, `terraform_list_runs_in_organization`, `terraform_list_runs_in_workspace`, `terraform_list_ssh_keys` `breaking` `bug-fix` `new-actions` Settings that were silently dropped when creating workspaces, notifications, projects, runs and state versions now apply. Adds List SSH Keys and three project fields; create_project tag-bindings now takes JSON API resource objects. `terraform_list_ssh_keys` `terraform_assign_ssh_key`, `terraform_create_notification_config`, `terraform_create_project`, `terraform_create_run`, `terraform_create_state_version`, `terraform_create_workspace`, `terraform_delete_variable_from_set`, `terraform_download_configuration_version`, `terraform_download_run_configuration_version`, `terraform_get_run`, `terraform_get_state_version`, `terraform_get_variable_set`, `terraform_list_organizations`, `terraform_list_runs_in_organization`, `terraform_list_runs_in_workspace`, `terraform_list_workspaces`, `terraform_update_notification_config` `new-actions` Added unified IAM actions for users, groups, organizations, roles, resource users, and credentials. `terraform_unified_delete_user`, `terraform_unified_get_group`, `terraform_unified_get_me`, `terraform_unified_get_organization`, `terraform_unified_get_role`, `terraform_unified_get_user`, `terraform_unified_list_groups`, `terraform_unified_list_organizations`, `terraform_unified_list_resource_types`, `terraform_unified_list_resource_users`, `terraform_unified_list_roles`, `terraform_unified_list_users` `new-actions` Added webhook event support for run and health-assessment events (9 events) with a manual notification setup guide. `bug-fix` Corrected the API Token connection guide (accurate portal labels, token shown inline on the Tokens page, consistent Terraform Host wording) and added portal screenshots. # The Metropolitan Museum of Art Source: https://docs.stackone.com/connectors/metmuseum/index How to set up the The Metropolitan Museum of Art connector, plus the actions that are available.
The Metropolitan Museum of Art
v1.2.0
4 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The Met Collection API is fully open access and requires no credentials. All artwork data is public domain (CC0). Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/metmuseum/index.md for the full list. # The Metropolitan Museum of Art Changelog Source: https://docs.stackone.com/connectors/metmuseum/changelog Release history for the The Metropolitan Museum of Art connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Moved Search Objects to The Met's v1.1 search endpoint, because the original search endpoint was retired on 2026-10-01 and now returns an error. Results are now paginated with new offset and limit inputs, and the search term is optional so filter-only searches work. `metmuseum_search_objects` `data-sync` Added DataSync support to List Departments, so The Met's curatorial departments can be synced into StackOne on a schedule and read without calling the API. The action syncs as a full refresh on every run, because the departments endpoint offers no last-updated filter. `metmuseum_list_departments` `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `auth` `actions` Added a Link Account guide explaining that the connector requires no authentication, and clarified on search_objects that dateBegin and dateEnd must be provided together with examples. `metmuseum_search_objects` `new-connector` Added The Metropolitan Museum of Art connector with object search, object detail, and department actions. # Thrive Learning Source: https://docs.stackone.com/connectors/thrive/index How to set up the Thrive Learning connector, plus the actions that are available.
Thrive Learning
Previewv1.1.0
44 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses basic authentication with tenant-id and API key. Requires Administrator privileges in Thrive Learning. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/thrive/index.md for the full list. # Thrive Learning Changelog Source: https://docs.stackone.com/connectors/thrive/changelog Release history for the Thrive Learning connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for activities, audiences, completions, content, CPD categories, CPD entries, CPD requirements, skill levels, tags and users, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. Audiences, content, tags and users sync incrementally using Thrive Learning's updated-since filter; the rest are full-refresh, because their endpoints expose no updated-since filter a sync can use. # Ticketmaster Source: https://docs.stackone.com/connectors/ticketmaster/index How to set up the Ticketmaster connector, plus the actions that are available.
Ticketmaster
v1.0.0
13 actions · 1 auth method
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses an API key passed as the apikey query parameter on every request. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ticketmaster/index.md for the full list. # Ticketmaster Changelog Source: https://docs.stackone.com/connectors/ticketmaster/changelog Release history for the Ticketmaster connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `new-feature` Enabled scheduled data sync on Search Classifications, so the Ticketmaster classification taxonomy can be kept in sync and read without calling the Discovery API on every request. It refreshes in full on each run, because the Discovery API exposes no updated-since filter. Data sync is not offered on Search Events, Search Attractions or Search Venues- the Discovery API rejects any request where page * size exceeds 1,000, so those collections (10,000 records each) cannot be paged through completely. `ticketmaster_search_classifications` `improvement` Clarified the search_classifications description to distinguish its paginated overview from the complete per-segment taxonomy returned by get_segment_details, improving LLM tool selection for full-breakdown requests. `ticketmaster_search_classifications` `improvement` `bug-fix` Improved action descriptions for better LLM tool selection, added rules validation for size/page params, removed non-functional params on classifications and single-entity GET endpoints (includeLicensedContent, source, sort), and fixed date range array serialization with arrayFormat comma. `ticketmaster_get_classification_details`, `ticketmaster_get_segment_details`, `ticketmaster_search_attractions`, `ticketmaster_search_events` `new-connector` Initial connector with Discovery API v2 support for events, attractions, venues, classifications, event images, and suggestions. # TikTok Ads Source: https://docs.stackone.com/connectors/tiktokads/index How to set up the TikTok Ads connector, plus the actions that are available.
TikTok Ads
Previewv1.0.0
50 actions · 2 auth methods
Advertising
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your TikTok Ads account using OAuth 2.0 for secure access to campaign management, reporting, and audience data. Use a TikTok Ads sandbox access token for testing without affecting live ad accounts. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/tiktokads/index.md for the full list. # Timesheet Portal Source: https://docs.stackone.com/connectors/timesheetportal/index How to set up the Timesheet Portal connector, plus the actions that are available.
Timesheet Portal
v3.1.0
67 actions · 4 auth methods
IAM Time Tracking Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Timesheet Portal issues a session API token from POST /token using the email and password of an API-authorised System Ad... Timesheet Portal issues a session API token from POST /token using the email and password of an API-authorised System Ad... OAuth 2.0 Client Credentials. Generate a Client ID and Client Secret in Settings > Account > Account > API access (requi... OAuth 2.0 Client Credentials. Generate a Client ID and Client Secret in Settings > Account > Account > API access (requi... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/timesheetportal/index.md for the full list. # Timesheet Portal Changelog Source: https://docs.stackone.com/connectors/timesheetportal/changelog Release history for the Timesheet Portal connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync to 23 list actions (clients, jobs, placements, projects, users, approvers, purchase orders, invoices and more), with incremental updates where the API supports a modified-since filter. get_third_parties gains a ModifiedSince filter. `timesheetportal_get_administrators_v2`, `timesheetportal_get_admins`, `timesheetportal_get_approvers`, `timesheetportal_get_approvers_v2`, `timesheetportal_get_clients`, `timesheetportal_get_clients_v2`, `timesheetportal_get_contractors`, `timesheetportal_get_contractors_v2`, `timesheetportal_get_cost_centres`, `timesheetportal_get_cost_centres_v2`, `timesheetportal_get_custom_lists`, `timesheetportal_get_custom_reports`, `timesheetportal_get_exchange_rates`, `timesheetportal_get_invoice_templates`, `timesheetportal_get_invoices`, `timesheetportal_get_jobs`, `timesheetportal_get_placements`, `timesheetportal_get_projects`, `timesheetportal_get_purchase_orders`, `timesheetportal_get_rate_types`, `timesheetportal_get_rates`, `timesheetportal_get_report_fields`, `timesheetportal_get_third_parties`, `timesheetportal_get_users` `bug` `auth` Further reduced intermittent "Authorization has been denied for this request" 401 errors on the Email & Password authentication methods by re-minting the session token more often, so it is replaced before the provider expires it even on cycles where its lifetime is short. `breaking` Removed the get_login_token action (single sign-on login token generation is no longer offered through this connector). `timesheetportal_get_login_token` `improved-descriptions` Documentation accuracy pass verified against the live API. The role-specific people actions (approvers, contractors, administrators, third-party users) now say when to use them instead of the generic user actions, recruitment jobs are separated from Project-edition projects and charge codes, and activity records are distinguished from timesheet time logging. Every upsert action documents the import-summary response, its update-in-place behaviour, and that an unknown reference code silently rejects the record while still returning HTTP 200. create_approver now requires clientCode, create_job requires chargeCodeGroupCode and create_working_pattern requires itemGroups (omitting it crashes the endpoint), while the working pattern rate code is documented as unvalidated. Every list filter states whether an unmatched value errors, returns an empty list, or is ignored and returns everything. The report actions map common requests onto their grouping, task-filter, payroll and output-format fields, AuditLogins is documented as returning its own fixed columns, and the custom-field inputs explain that either write form persists and that get_custom_fields reports dataType as a number rather than a name. Six actions leave preview, each now verified against real data — get_invoice, get_invoice_pdf, mark_invoices_exported and create_invoices against a real invoice, get_custom_report against a saved report, and get_expense_receipt against an assigned receipt. create_invoices documents that an invoice item needs a tax rate with a non-empty code, get_custom_report that its id and dates go in the query string, get_expense_receipt that the GUID arrives comma-separated from the report field, and the expense reports that omitting expenseStatusFilters silently returns no rows. `timesheetportal_create_activities`, `timesheetportal_create_admin`, `timesheetportal_create_approver`, `timesheetportal_create_charge_code`, `timesheetportal_create_client`, `timesheetportal_create_client_user`, `timesheetportal_create_contractor`, `timesheetportal_create_expense_category`, `timesheetportal_create_invoices`, `timesheetportal_create_job`, `timesheetportal_create_or_update_timesheets`, `timesheetportal_create_perm_placement`, `timesheetportal_create_project`, `timesheetportal_create_rate`, `timesheetportal_create_third_party`, `timesheetportal_create_third_party_user`, `timesheetportal_create_user`, `timesheetportal_create_working_pattern`, `timesheetportal_get_administrators_v2`, `timesheetportal_get_admins`, `timesheetportal_get_approvers`, `timesheetportal_get_approvers_v2`, `timesheetportal_get_builtin_report`, `timesheetportal_get_charge_codes`, `timesheetportal_get_clients`, `timesheetportal_get_clients_v2`, `timesheetportal_get_contractors`, `timesheetportal_get_contractors_v2`, `timesheetportal_get_custom_fields`, `timesheetportal_get_custom_report`, `timesheetportal_get_expense_entries_report`, `timesheetportal_get_expense_forms_report`, `timesheetportal_get_expense_receipt`, `timesheetportal_get_invoice`, `timesheetportal_get_invoice_pdf`, `timesheetportal_get_jobs`, `timesheetportal_get_leave_bookings_report`, `timesheetportal_get_leave_bookings_summary`, `timesheetportal_get_placements`, `timesheetportal_get_projects`, `timesheetportal_get_purchase_orders`, `timesheetportal_get_rates`, `timesheetportal_get_third_parties`, `timesheetportal_get_timesheets_report`, `timesheetportal_get_users`, `timesheetportal_mark_invoices_exported`, `timesheetportal_mark_timesheets_exported`, `timesheetportal_search_users` `improved-descriptions` Improved action descriptions — documented the working include values for expanding placement approvers, commission splits and rates, report status-filter guidance to avoid empty results, consultant field alternatives for the TimesheetStatus report, and how to list charge code groups (Location/Site/Branch). `timesheetportal_get_builtin_report`, `timesheetportal_get_jobs`, `timesheetportal_get_placements`, `timesheetportal_get_timesheets_report` `bug-fix` `improved-descriptions` Fixed idle-session 401s (tokens now refresh every 8 minutes). Renamed export_invoices and export_timesheets to mark_invoices_exported and mark_timesheets_exported with correct write effects. Marked required parent fields (clientCode, chargeCodeGroupCode, paidDate, postedDate), removed broken or undocumented params and report types, and improved action descriptions with dependency chains and provider error guidance. `timesheetportal_mark_invoices_exported`, `timesheetportal_mark_timesheets_exported` `timesheetportal_export_invoices`, `timesheetportal_export_timesheets` `timesheetportal_approve_invoices`, `timesheetportal_create_charge_code`, `timesheetportal_create_client_user`, `timesheetportal_create_expense_category`, `timesheetportal_create_project`, `timesheetportal_get_builtin_report`, `timesheetportal_get_clients_v2`, `timesheetportal_get_expense_entries_report`, `timesheetportal_get_expense_forms_report`, `timesheetportal_get_invoice_report`, `timesheetportal_get_invoice_report_v2`, `timesheetportal_get_invoice_report_v2api`, `timesheetportal_get_leave_bookings_report`, `timesheetportal_get_rate_types`, `timesheetportal_get_third_parties`, `timesheetportal_get_timesheets_report`, `timesheetportal_mark_invoices_paid`, `timesheetportal_mark_invoices_posted` `new-actions` `new-fields` Added the Timesheet Portal V2 API surface (placements, purchase orders, timesheets, invoice lifecycle, activities, settings, and delta-sync lists) and scoped actions to the Project and Recruitment auth methods. Both editions share one unified V1+V2 REST API. `timesheetportal_create_activities`, `timesheetportal_create_admin`, `timesheetportal_create_approver`, `timesheetportal_create_contractor`, `timesheetportal_create_invoices`, `timesheetportal_create_job`, `timesheetportal_create_or_update_timesheets`, `timesheetportal_create_perm_placement`, `timesheetportal_create_placement_activities`, `timesheetportal_create_third_party_user`, `timesheetportal_create_working_pattern`, `timesheetportal_get_administrators_v2`, `timesheetportal_get_admins`, `timesheetportal_get_approvers`, `timesheetportal_get_approvers_v2`, `timesheetportal_get_clients_v2`, `timesheetportal_get_contractors`, `timesheetportal_get_contractors_v2`, `timesheetportal_get_cost_centres_v2`, `timesheetportal_get_custom_lists`, `timesheetportal_get_exchange_rates`, `timesheetportal_get_expense_entries_report`, `timesheetportal_get_expense_forms_report`, `timesheetportal_get_invoice`, `timesheetportal_get_invoice_pdf`, `timesheetportal_get_invoice_report_v2api`, `timesheetportal_get_invoice_templates`, `timesheetportal_get_invoices`, `timesheetportal_get_jobs`, `timesheetportal_get_placements`, `timesheetportal_get_purchase_orders`, `timesheetportal_get_rate_types`, `timesheetportal_get_rates`, `timesheetportal_get_timesheets`, `timesheetportal_mark_invoices_paid`, `timesheetportal_mark_invoices_posted`, `timesheetportal_search_contractors` `timesheetportal_create_expense_entry`, `timesheetportal_create_expense_form`, `timesheetportal_create_invoice`, `timesheetportal_create_token`, `timesheetportal_get_token` `timesheetportal_approve_invoices`, `timesheetportal_create_charge_code`, `timesheetportal_create_client`, `timesheetportal_create_client_user`, `timesheetportal_create_expense_category`, `timesheetportal_create_project`, `timesheetportal_create_rate`, `timesheetportal_create_third_party`, `timesheetportal_create_user`, `timesheetportal_email_invoices`, `timesheetportal_export_invoices`, `timesheetportal_export_timesheets`, `timesheetportal_get_builtin_report`, `timesheetportal_get_charge_codes`, `timesheetportal_get_clients`, `timesheetportal_get_cost_centres`, `timesheetportal_get_custom_fields`, `timesheetportal_get_custom_report`, `timesheetportal_get_custom_reports`, `timesheetportal_get_expense_receipt`, `timesheetportal_get_invoice_report`, `timesheetportal_get_invoice_report_v2`, `timesheetportal_get_leave_bookings_report`, `timesheetportal_get_leave_bookings_summary`, `timesheetportal_get_login_token`, `timesheetportal_get_projects`, `timesheetportal_get_report_fields`, `timesheetportal_get_third_parties`, `timesheetportal_get_timesheets_report`, `timesheetportal_get_users`, `timesheetportal_search_users` `guide-changes` Improved the account-linking guides for both auth methods — added the Timesheet Portal login URL, clarified where to find the Settings menu, and simplified the "Email & Password" auth method name. `timesheetportal_approve_invoices`, `timesheetportal_create_charge_code`, `timesheetportal_create_client`, `timesheetportal_create_client_user`, `timesheetportal_create_expense_category`, `timesheetportal_create_expense_entry`, `timesheetportal_create_expense_form`, `timesheetportal_create_invoice`, `timesheetportal_create_project`, `timesheetportal_create_rate`, `timesheetportal_create_third_party`, `timesheetportal_create_token`, `timesheetportal_create_user`, `timesheetportal_email_invoices`, `timesheetportal_export_invoices`, `timesheetportal_export_timesheets`, `timesheetportal_get_builtin_report`, `timesheetportal_get_charge_codes`, `timesheetportal_get_clients`, `timesheetportal_get_cost_centres`, `timesheetportal_get_custom_fields`, `timesheetportal_get_custom_report`, `timesheetportal_get_custom_reports`, `timesheetportal_get_expense_receipt`, `timesheetportal_get_invoice_report`, `timesheetportal_get_invoice_report_v2`, `timesheetportal_get_leave_bookings_report`, `timesheetportal_get_leave_bookings_summary`, `timesheetportal_get_login_token`, `timesheetportal_get_projects`, `timesheetportal_get_report_fields`, `timesheetportal_get_third_parties`, `timesheetportal_get_timesheets_report`, `timesheetportal_get_token`, `timesheetportal_get_users`, `timesheetportal_search_users` `new-actions` Initial Timesheet Portal (Standard/Project edition) connector with 36 actions across clients, projects, charge codes, users, timesheets, expenses, invoices, rates, and reports; email/password session-token auth with automatic refresh; poll-based sync via ModifiedSince/lastModified (provider has no webhooks). # tl;dv Source: https://docs.stackone.com/connectors/tldv/index How to set up the tl;dv connector, plus the actions that are available.
tl;dv
Betav0.2.0
6 actions · 1 auth method
Notetaker
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using an API key generated from your tl;dv Personal Settings. API access requires a Pro or Business plan. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/tldv/index.md for the full list. # tl;dv Changelog Source: https://docs.stackone.com/connectors/tldv/changelog Release history for the tl;dv connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the meetings list action for scheduled full record syncs. `tldv_list_meetings` `new-connector` Initial beta release — meetings, transcripts, notes, import, and download URL. # Todoist Source: https://docs.stackone.com/connectors/todoist/index How to set up the Todoist connector, plus the actions and events that are available.
Todoist
v2.0.0
62 actions · 25 events · 2 auth methods
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires creating an app in the Todoist App Management Console with the Token refresh setting enabled. Access tokens exp... No app registration required. Uses the personal API token of a single Todoist user, which does not expire and has full a... Optionally, configure receiving Events for Todoist into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/todoist/index.md for the full list. ## Events See https://docs.stackone.com/connectors/todoist/index.md for the full list. # Todoist Changelog Source: https://docs.stackone.com/connectors/todoist/changelog Release history for the Todoist connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` `improvement` Webhook events are now only available on OAuth 2.0 connections, since Todoist only delivers webhooks to users who authorized the OAuth app. Webhook events are now delivered to the per-connection Native Webhook URL on the linked account. The previous routing that matched deliveries to a connection by Todoist user ID is no longer supported and has been removed. `description-fix` Corrected action and input descriptions to match how the Todoist API actually behaves, covering the activity log filter format and ignored filters, label search wildcards, fields required on updates, plan-limited features such as reminders and task durations, and conflicting due date and section or parent combinations. `todoist_create_comment`, `todoist_create_project`, `todoist_create_task`, `todoist_get_activity_logs`, `todoist_get_task`, `todoist_move_task`, `todoist_quick_add_task`, `todoist_search_labels`, `todoist_update_label`, `todoist_update_notification_setting`, `todoist_update_project`, `todoist_update_task` `auth` Added API key authentication with a Todoist personal API token as an alternative to OAuth 2.0, supported by every action. Webhook events still require OAuth 2.0. `todoist_archive_project`, `todoist_archive_section`, `todoist_auth_test`, `todoist_close_task`, `todoist_create_comment`, `todoist_create_label`, `todoist_create_project`, `todoist_create_section`, `todoist_create_task`, `todoist_delete_comment`, `todoist_delete_label`, `todoist_delete_project`, `todoist_delete_section`, `todoist_delete_task`, `todoist_delete_upload`, `todoist_get_activity_logs`, `todoist_get_comment`, `todoist_get_label`, `todoist_get_productivity_stats`, `todoist_get_project`, `todoist_get_project_permissions`, `todoist_get_section`, `todoist_get_task`, `todoist_get_tasks_by_filter`, `todoist_get_tasks_completed_by_completion_date`, `todoist_get_tasks_completed_by_due_date`, `todoist_get_user_info`, `todoist_join_project`, `todoist_list_archived_projects`, `todoist_list_comments`, `todoist_list_labels`, `todoist_list_project_collaborators`, `todoist_list_projects`, `todoist_list_sections`, `todoist_list_shared_labels`, `todoist_list_tasks`, `todoist_move_task`, `todoist_quick_add_task`, `todoist_remove_shared_label`, `todoist_rename_shared_label`, `todoist_reopen_task`, `todoist_search_labels`, `todoist_search_projects`, `todoist_search_sections`, `todoist_unarchive_project`, `todoist_unarchive_section`, `todoist_unified_get_me`, `todoist_unified_get_organization`, `todoist_unified_get_role`, `todoist_unified_get_user`, `todoist_unified_list_organizations`, `todoist_unified_list_resource_types`, `todoist_unified_list_resource_users`, `todoist_unified_list_roles`, `todoist_unified_list_users`, `todoist_update_comment`, `todoist_update_label`, `todoist_update_notification_setting`, `todoist_update_project`, `todoist_update_section`, `todoist_update_task`, `todoist_upload_file` `bug-fix` User lists now include pending workspace invitations with status pending and read up to 5,000 memberships across 50 workspaces, returning 400 above either. `todoist_unified_get_user`, `todoist_unified_list_users` `bug-fix` Looking up an unknown user or role now returns a not-found error. User lookups search the workspace named in the id, up to 5,000 members, and the role list shows each Todoist role once, including Guest. `todoist_unified_get_role`, `todoist_unified_get_user`, `todoist_unified_list_resource_users`, `todoist_unified_list_roles`, `todoist_unified_list_users` `bug-fix` `auth` Fixed connections dropping after one hour. Todoist apps with token refresh enabled issue access tokens that expire after an hour, and the connector had no way to renew them, so every call returned 401 until the account was reconnected by hand. The access token is now refreshed automatically, and the rotated refresh token is stored on each refresh. The OAuth 2.0 setup guide was rebuilt with step-by-step screenshots, covering the app Token refresh setting this relies on. `new-feature` Added scheduled data sync to six collection actions — tasks, projects, archived projects, sections, labels and activity logs — so these collections can be kept in sync and searched without calling Todoist on every request. Each walks the API cursor to completion and syncs by full refresh, because the Todoist REST API exposes no updated-since filter on these endpoints. `todoist_get_activity_logs`, `todoist_list_archived_projects`, `todoist_list_labels`, `todoist_list_projects`, `todoist_list_sections`, `todoist_list_tasks`, `todoist_unified_list_organizations`, `todoist_unified_list_roles`, `todoist_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `todoist_auth_test`, `todoist_unified_get_me`, `todoist_unified_get_organization`, `todoist_unified_get_role`, `todoist_unified_get_user`, `todoist_unified_list_organizations`, `todoist_unified_list_resource_types`, `todoist_unified_list_resource_users`, `todoist_unified_list_roles`, `todoist_unified_list_users` `new-actions` Added unified IAM actions for identity, workspace users, roles, organizations, and project-scoped resource users. `todoist_auth_test`, `todoist_unified_get_me`, `todoist_unified_get_organization`, `todoist_unified_get_role`, `todoist_unified_get_user`, `todoist_unified_list_organizations`, `todoist_unified_list_resource_types`, `todoist_unified_list_resource_users`, `todoist_unified_list_roles`, `todoist_unified_list_users` `todoist_archive_project`, `todoist_archive_section`, `todoist_close_task`, `todoist_create_comment`, `todoist_create_label`, `todoist_create_project`, `todoist_create_section`, `todoist_create_task`, `todoist_delete_comment`, `todoist_delete_label`, `todoist_delete_project`, `todoist_delete_section`, `todoist_delete_task`, `todoist_delete_upload`, `todoist_get_activity_logs`, `todoist_get_comment`, `todoist_get_label`, `todoist_get_productivity_stats`, `todoist_get_project`, `todoist_get_project_permissions`, `todoist_get_section`, `todoist_get_task`, `todoist_get_tasks_by_filter`, `todoist_get_tasks_completed_by_completion_date`, `todoist_get_tasks_completed_by_due_date`, `todoist_get_user_info`, `todoist_join_project`, `todoist_list_archived_projects`, `todoist_list_comments`, `todoist_list_labels`, `todoist_list_project_collaborators`, `todoist_list_projects`, `todoist_list_sections`, `todoist_list_shared_labels`, `todoist_list_tasks`, `todoist_move_task`, `todoist_quick_add_task`, `todoist_remove_shared_label`, `todoist_rename_shared_label`, `todoist_reopen_task`, `todoist_search_labels`, `todoist_search_projects`, `todoist_search_sections`, `todoist_unarchive_project`, `todoist_unarchive_section`, `todoist_update_comment`, `todoist_update_label`, `todoist_update_notification_setting`, `todoist_update_project`, `todoist_update_section`, `todoist_update_task`, `todoist_upload_file` `new-actions` Added webhook event support for task, comment, project, section, label, filter, and reminder events (25 events). # Toggl Source: https://docs.stackone.com/connectors/toggl/index How to set up the Toggl connector, plus the actions and events that are available.
Toggl
v2.1.0
92 actions · 29 events · 1 auth method
IAM Time Tracking
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Optionally, configure receiving Events for Toggl into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/toggl/index.md for the full list. ## Events See https://docs.stackone.com/connectors/toggl/index.md for the full list. # Toggl Changelog Source: https://docs.stackone.com/connectors/toggl/changelog Release history for the Toggl connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Added the recurring schedule fields for projects, and corrected the accepted values for workspace roles and for rate and labor cost change modes so these updates succeed on the first try. `toggl_add_project_user`, `toggl_create_project`, `toggl_list_time_entries`, `toggl_update_project`, `toggl_update_project_user`, `toggl_update_workspace_user_settings` `guide` Refreshed the API Token connection guide to match the current Toggl Track profile page, named the Reset button, explained why Admin rights are needed, and added screenshots. `bug-fix` Fixed connection testing so an invalid API token is rejected when linking an account. `breaking` `bug-fix` Client and group updates now require the fields Toggl needs on every update, and bulk time entry edits accept numbers, booleans, and tag lists. Also clarifies tag removal, time entry date limits, new project status, and user ID fields, and confirms organization updates. `toggl_bulk_edit_time_entries`, `toggl_create_organization`, `toggl_create_project`, `toggl_delete_workspace_user`, `toggl_get_me_clients`, `toggl_get_me_projects`, `toggl_get_me_tags`, `toggl_get_workspace_statistics`, `toggl_get_workspace_users`, `toggl_list_organization_users`, `toggl_list_organization_workspace_users`, `toggl_list_project_groups`, `toggl_list_project_users`, `toggl_list_time_entries`, `toggl_list_workspace_groups`, `toggl_list_workspace_users`, `toggl_list_workspaces`, `toggl_update_client`, `toggl_update_group`, `toggl_update_organization`, `toggl_update_organization_user`, `toggl_update_time_entry`, `toggl_update_workspace_user_settings` `new-feature` Added periodic data sync for clients, projects, tags, time entries, workspaces, organizations, and workspace features to keep records continuously up to date. `toggl_get_me_clients`, `toggl_get_me_features`, `toggl_get_me_organizations`, `toggl_get_me_projects`, `toggl_get_me_tags`, `toggl_get_me_tasks`, `toggl_get_me_track_reminders`, `toggl_list_time_entries`, `toggl_list_workspaces` `guide-changes` Added a webhook (events) setup guide documenting the auto-provisioned Toggl webhook subscription and available events. # Traffit Source: https://docs.stackone.com/connectors/traffit/index How to set up the Traffit connector, plus the actions that are available.
Traffit
Betav1.1.0
70 actions · 1 auth method
ATS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connects using Traffit's OAuth 2.0 Client Credentials flow. Requires an API client created in your Traffit account setti... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/traffit/index.md for the full list. # Traffit Changelog Source: https://docs.stackone.com/connectors/traffit/changelog Release history for the Traffit connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for candidates, jobs, job posts, published job posts, clients, CRM persons, CRM activities, users, user groups, permission groups, talent pools, consents, consent types, sources, workflows and dictionaries, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. All syncs are full-refresh — the Traffit API exposes no updated-since filter a sync can use. # Trello Source: https://docs.stackone.com/connectors/trello/index How to set up the Trello connector, plus the actions and events that are available.
Trello
Previewv1.1.0
133 actions · 67 events · 1 auth method
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Trello uses a long-lived API token tied to a Power-Up API key. Tokens do not expire when set to "never" and only need to... Optionally, configure receiving Events for Trello into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/trello/index.md for the full list. ## Events See https://docs.stackone.com/connectors/trello/index.md for the full list. # Trello Changelog Source: https://docs.stackone.com/connectors/trello/changelog Release history for the Trello connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added webhook events for 65 Trello actions across cards, comments, checklists, boards, lists, labels, Workspaces, and members. StackOne creates the Trello webhook on the connected member automatically when the account connects and deletes it on disconnect. # Tribepad Source: https://docs.stackone.com/connectors/tribepad/index How to set up the Tribepad connector, plus the actions that are available.
Tribepad
Betav1.1.0
56 actions · 2 auth methods
ATS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect using your Tribepad OAuth2 client credentials. Access tokens expire after 5 minutes and are automatically refres... Connect using an API key provided by Tribepad support. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/tribepad/index.md for the full list. # Tribepad Changelog Source: https://docs.stackone.com/connectors/tribepad/changelog Release history for the Tribepad connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support so applications, users, jobs, hierarchies, requisitions, templates and reference options can be bulk-synced and kept up to date. # Twelve Data Source: https://docs.stackone.com/connectors/twelvedata/index How to set up the Twelve Data connector, plus the actions that are available.
Twelve Data
Previewv0.3.1
75 actions · 1 auth method
Accounting
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a personal API key sent in the Authorization header. No app registration required. Keys are issued instantly with a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/twelvedata/index.md for the full list. # Twelve Data Changelog Source: https://docs.stackone.com/connectors/twelvedata/changelog Release history for the Twelve Data connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Updated the API Key field placeholder on the connection form to show an example in the format of a real Twelve Data API key. `breaking` `new-actions` `guide` `data-sync` Breaking: 22 actions renamed to match Twelve Data's Get operations: 20 collection actions from list_* to get_* (e.g. list_stocks is now get_stocks), convert_currency is now get_currency_conversion and search_symbols is now get_symbol_search. Added 13 actions: Momentum, Rate of Change, Stochastic RSI, Keltner Channel, KAMA, DEMA, TEMA, PPO, NATR and WMA indicators, get_logo, get_time_series_cross and batch_requests. The instrument type filter on 23 market-data and indicator actions now lists the provider's asset classes (get_exchanges keeps stock, etf, index, which is what its API accepts), get_ichimoku include_ahead_span_period is a boolean, list_press_releases gains page and get_api_usage gains timezone, 45 actions gain format (JSON or CSV) and delimiter for CSV output, and documented value ranges for outputsize, time_period, period and rolling_period. Instrument endpoints and list_press_releases now require one of symbol, figi, isin, or cusip, and get_stocks accepts any one of symbol, exchange, country, figi, isin, cusip, cik, or mic_code. Descriptions now state plan gates (figi, prepost, statement date ranges, calendars), that prepost needs intraday intervals of 30min or less. Removed params Twelve Data ignores (verified live): previous_close on the 27 indicator actions (still on get_time_series), get_ichimoku include_ohlc and lagging_span_period, and get_commodities category. get_funds now defaults outputsize to 50 so an unfiltered call no longer times out. list_press_releases start_date and end_date now work: plain YYYY-MM-DD dates are expanded to the start or end of the day, because Twelve Data silently returned no results for any format other than YYYY-MM-DDTHH:MM:SS. prepost is only sent for intervals of 30min or less (it previously caused a 404 on longer intervals), and the plan-gated historical date range on balance sheet, cash flow and income statement (Ultra or Enterprise) now returns 403 instead of 400. The 57 actions with any Twelve Data plan gate are released as beta: the earnings and ipo calendars, market movers and exchange schedule (unavailable below Grow, Pro or Ultra), the dividends and splits calendars (need an instrument identifier below Grow), and every action with a plan-gated input (figi, prepost, statement date ranges, get_etfs page), each marked Plan-gated in its description. Added data sync to 13 collections (bonds, funds, ETFs, commodities, forex pairs, cryptocurrencies, exchanges, cryptocurrency exchanges, countries, market state, exchange schedule, and the dividends and splits calendars) as full-refresh syncs; Twelve Data has no updated-since filter. Action descriptions now say when to use each of the similar price, quote, dividend, split, earnings, fund, exchange and analyst actions, and that symbol is a ticker resolved with get_symbol_search. The API Key connection guide was refreshed from the live Twelve Data portal with new screenshots. `twelvedata_batch_requests`, `twelvedata_get_bonds`, `twelvedata_get_commodities`, `twelvedata_get_countries`, `twelvedata_get_cross_listings`, `twelvedata_get_cryptocurrencies`, `twelvedata_get_cryptocurrency_exchanges`, `twelvedata_get_currency_conversion`, `twelvedata_get_dema`, `twelvedata_get_dividends_calendar`, `twelvedata_get_earnings_calendar`, `twelvedata_get_etfs`, `twelvedata_get_exchange_schedule`, `twelvedata_get_exchanges`, `twelvedata_get_forex_pairs`, `twelvedata_get_funds`, `twelvedata_get_instrument_types`, `twelvedata_get_intervals`, `twelvedata_get_ipo_calendar`, `twelvedata_get_kama`, `twelvedata_get_keltner`, `twelvedata_get_logo`, `twelvedata_get_market_movers`, `twelvedata_get_mom`, `twelvedata_get_natr`, `twelvedata_get_ppo`, `twelvedata_get_roc`, `twelvedata_get_splits_calendar`, `twelvedata_get_stochrsi`, `twelvedata_get_stocks`, `twelvedata_get_symbol_search`, `twelvedata_get_technical_indicators`, `twelvedata_get_tema`, `twelvedata_get_time_series_cross`, `twelvedata_get_wma` `twelvedata_convert_currency`, `twelvedata_list_bonds`, `twelvedata_list_commodities`, `twelvedata_list_countries`, `twelvedata_list_cross_listings`, `twelvedata_list_cryptocurrencies`, `twelvedata_list_cryptocurrency_exchanges`, `twelvedata_list_dividends_calendar`, `twelvedata_list_earnings_calendar`, `twelvedata_list_etfs`, `twelvedata_list_exchange_schedule`, `twelvedata_list_exchanges`, `twelvedata_list_forex_pairs`, `twelvedata_list_funds`, `twelvedata_list_instrument_types`, `twelvedata_list_intervals`, `twelvedata_list_ipo_calendar`, `twelvedata_list_market_movers`, `twelvedata_list_splits_calendar`, `twelvedata_list_stocks`, `twelvedata_list_technical_indicators`, `twelvedata_search_symbols` `twelvedata_get_adx`, `twelvedata_get_analyst_ratings_us_equities`, `twelvedata_get_api_usage`, `twelvedata_get_aroon`, `twelvedata_get_atr`, `twelvedata_get_balance_sheet`, `twelvedata_get_bbands`, `twelvedata_get_cash_flow`, `twelvedata_get_cci`, `twelvedata_get_dividends`, `twelvedata_get_earliest_timestamp`, `twelvedata_get_earnings`, `twelvedata_get_earnings_estimate`, `twelvedata_get_ema`, `twelvedata_get_eod`, `twelvedata_get_exchange_rate`, `twelvedata_get_growth_estimates`, `twelvedata_get_ichimoku`, `twelvedata_get_income_statement`, `twelvedata_get_macd`, `twelvedata_get_market_cap`, `twelvedata_get_market_state`, `twelvedata_get_mfi`, `twelvedata_get_obv`, `twelvedata_get_price`, `twelvedata_get_price_target`, `twelvedata_get_profile`, `twelvedata_get_quote`, `twelvedata_get_recommendations`, `twelvedata_get_rsi`, `twelvedata_get_sar`, `twelvedata_get_sma`, `twelvedata_get_splits`, `twelvedata_get_statistics`, `twelvedata_get_stoch`, `twelvedata_get_supertrend`, `twelvedata_get_time_series`, `twelvedata_get_vwap`, `twelvedata_get_willr`, `twelvedata_list_press_releases` `enhancement` Expanded Twelve Data from 24 to 62 actions for the initial mapping. Added full parameter coverage to the existing actions (instrument identifiers, exchange/mic_code/country/type disambiguation, sort, pagination, data-shaping) and curated new families (12 common technical indicators, core company fundamentals, analyst estimates, corporate-event calendars, and fund and reference endpoints). Plan-gated actions (earnings and ipo calendars, market movers, exchange schedule) are held at releaseStage preview. Documented the per-ma_type data-window requirement and the list_stocks filter requirement. `twelvedata_get_adx`, `twelvedata_get_analyst_ratings_us_equities`, `twelvedata_get_aroon`, `twelvedata_get_atr`, `twelvedata_get_balance_sheet`, `twelvedata_get_cash_flow`, `twelvedata_get_cci`, `twelvedata_get_dividends`, `twelvedata_get_earnings`, `twelvedata_get_earnings_estimate`, `twelvedata_get_growth_estimates`, `twelvedata_get_ichimoku`, `twelvedata_get_income_statement`, `twelvedata_get_market_cap`, `twelvedata_get_mfi`, `twelvedata_get_obv`, `twelvedata_get_price_target`, `twelvedata_get_profile`, `twelvedata_get_recommendations`, `twelvedata_get_sar`, `twelvedata_get_splits`, `twelvedata_get_statistics`, `twelvedata_get_stoch`, `twelvedata_get_supertrend`, `twelvedata_get_vwap`, `twelvedata_get_willr`, `twelvedata_list_bonds`, `twelvedata_list_commodities`, `twelvedata_list_cross_listings`, `twelvedata_list_dividends_calendar`, `twelvedata_list_earnings_calendar`, `twelvedata_list_exchange_schedule`, `twelvedata_list_funds`, `twelvedata_list_intervals`, `twelvedata_list_ipo_calendar`, `twelvedata_list_market_movers`, `twelvedata_list_press_releases`, `twelvedata_list_splits_calendar` `twelvedata_get_bbands`, `twelvedata_get_earliest_timestamp`, `twelvedata_get_ema`, `twelvedata_get_eod`, `twelvedata_get_exchange_rate`, `twelvedata_get_macd`, `twelvedata_get_price`, `twelvedata_get_quote`, `twelvedata_get_rsi`, `twelvedata_get_sma`, `twelvedata_get_time_series`, `twelvedata_list_cryptocurrencies`, `twelvedata_list_etfs`, `twelvedata_list_forex_pairs`, `twelvedata_list_stocks`, `twelvedata_search_symbols` `new-connector` Added the Twelve Data connector with market data, technical indicator, and reference catalog actions. # Twilio Source: https://docs.stackone.com/connectors/twilio/index How to set up the Twilio connector, plus the actions and events that are available.
Twilio
v2.2.1
59 actions · 20 events · 4 auth methods
Messaging Telephony IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Your primary account credentials. Provides full access to all Twilio resources under your account. Recommended for production. API keys can be independently rotated and revoked without affecting your main credentials. Requires creating an OAuth app in the Twilio Console. Access tokens expire after 1 hour and are automatically refreshed. Required for the unified IAM actions (users, roles, organizations, /me), which call Twilio's Organization-level Role and... Optionally, configure receiving Events for Twilio into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/twilio/index.md for the full list. ## Events See https://docs.stackone.com/connectors/twilio/index.md for the full list. # Twilio Changelog Source: https://docs.stackone.com/connectors/twilio/changelog Release history for the Twilio connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `events-guide` Added a webhook setup guide covering how Twilio Event Streams subscriptions are created and how events are delivered. `data-sync` Added DataSync support for unified IAM roles and users actions, enabling periodic synchronisation of organisation roles and SCIM users. `twilio_unified_list_roles`, `twilio_unified_list_users` `bug-fix` Fixed role lookups returning an empty result instead of a not-found error, made role list pagination more reliable, and moved all eight IAM actions (users, roles, organizations, credentials) from beta to preview. `twilio_auth_test`, `twilio_unified_get_me`, `twilio_unified_get_organization`, `twilio_unified_get_role`, `twilio_unified_get_user`, `twilio_unified_list_organizations`, `twilio_unified_list_roles`, `twilio_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, and credentials. All 8 IAM actions are gated to releaseStage beta pending live QA against an account connected via the OAuth 2.0 (Organizations API) auth type. `twilio_auth_test`, `twilio_unified_get_me`, `twilio_unified_get_organization`, `twilio_unified_get_role`, `twilio_unified_get_user`, `twilio_unified_list_organizations`, `twilio_unified_list_roles`, `twilio_unified_list_users` `twilio_create_account`, `twilio_create_call`, `twilio_create_conversation`, `twilio_create_conversation_message`, `twilio_create_conversation_participant`, `twilio_create_conversation_user`, `twilio_create_event_sink`, `twilio_create_event_subscription`, `twilio_create_message`, `twilio_delete_call`, `twilio_delete_conversation`, `twilio_delete_conversation_message`, `twilio_delete_conversation_participant`, `twilio_delete_conversation_user`, `twilio_delete_event_sink`, `twilio_delete_event_subscription`, `twilio_delete_message`, `twilio_delete_message_media`, `twilio_get_account`, `twilio_get_call`, `twilio_get_conversation`, `twilio_get_conversation_message`, `twilio_get_conversation_participant`, `twilio_get_conversation_user`, `twilio_get_event_sink`, `twilio_get_event_subscription`, `twilio_get_event_type`, `twilio_get_message`, `twilio_get_message_media`, `twilio_list_accounts`, `twilio_list_call_recordings`, `twilio_list_calls`, `twilio_list_conversation_messages`, `twilio_list_conversation_participants`, `twilio_list_conversation_users`, `twilio_list_conversation_webhooks`, `twilio_list_conversations`, `twilio_list_event_sinks`, `twilio_list_event_subscriptions`, `twilio_list_event_types`, `twilio_list_message_media`, `twilio_list_messages`, `twilio_list_subscribed_events`, `twilio_list_user_conversations`, `twilio_update_account`, `twilio_update_call`, `twilio_update_conversation`, `twilio_update_conversation_message`, `twilio_update_conversation_participant`, `twilio_update_conversation_user`, `twilio_update_message` `improvement` Removed redundant region selector from Basic Auth and OAuth 2.0 authentication configurations. # Typeform Source: https://docs.stackone.com/connectors/typeform/index How to set up the Typeform connector, plus the actions and events that are available.
Typeform
v1.3.1
36 actions · 1 event · 1 auth method
Surveys IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Create an OAuth application in Typeform to get client credentials Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/typeform/index.md for the full list. ## Events See https://docs.stackone.com/connectors/typeform/index.md for the full list. # Typeform Changelog Source: https://docs.stackone.com/connectors/typeform/changelog Release history for the Typeform connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` Connecting with a custom scope list no longer fails when it leaves out offline access, because it is now always requested. `typeform_add_workspace_member`, `typeform_create_form`, `typeform_create_image`, `typeform_create_theme`, `typeform_create_workspace`, `typeform_delete_form`, `typeform_delete_image`, `typeform_delete_responses`, `typeform_delete_theme`, `typeform_delete_workspace`, `typeform_get_background_by_size`, `typeform_get_choice_image_by_size`, `typeform_get_form`, `typeform_get_form_messages`, `typeform_get_image`, `typeform_get_image_by_size`, `typeform_get_theme`, `typeform_get_workspace`, `typeform_list_forms`, `typeform_list_images`, `typeform_list_responses`, `typeform_list_themes`, `typeform_list_workspaces`, `typeform_patch_theme`, `typeform_remove_workspace_member`, `typeform_unified_get_group`, `typeform_unified_get_me`, `typeform_unified_get_organization`, `typeform_unified_get_role`, `typeform_unified_get_user`, `typeform_unified_list_groups`, `typeform_unified_list_organizations`, `typeform_unified_list_roles`, `typeform_unified_list_users`, `typeform_update_form`, `typeform_update_theme` `bug-fix` User lists now read up to 80 workspaces instead of failing on accounts with more than one, and users can include their roles and workspaces. Organizations now use the real Typeform account id. `typeform_unified_get_group`, `typeform_unified_get_me`, `typeform_unified_get_organization`, `typeform_unified_get_role`, `typeform_unified_get_user`, `typeform_unified_list_groups`, `typeform_unified_list_organizations`, `typeform_unified_list_roles`, `typeform_unified_list_users` `new-feature` `data-sync` Added DataSync support to seven list actions - forms, themes, workspaces, images, and the unified groups, organizations, and roles endpoints. All sync by full refresh, as Typeform exposes no updated-since filter. `typeform_list_forms`, `typeform_list_images`, `typeform_list_themes`, `typeform_list_workspaces`, `typeform_unified_list_groups`, `typeform_unified_list_organizations`, `typeform_unified_list_roles` `bug-fix` unified_list_users now auto-resolves the workspace instead of returning an empty list, and unified_get_user returns 404 for an unknown user instead of an empty stub. `typeform_unified_get_user`, `typeform_unified_list_users` `new-actions` Added unified IAM actions for users, groups, roles, organizations, and credentials. # Udemy Source: https://docs.stackone.com/connectors/udemy/index How to set up the Udemy connector, plus the actions that are available.
Udemy
Previewv1.1.0
9 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Admin privileges in your Udemy Business account. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/udemy/index.md for the full list. # Udemy Changelog Source: https://docs.stackone.com/connectors/udemy/changelog Release history for the Udemy connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added data sync support for courses, learning paths, and the user activity, path activity, lab activity, assessment activity, course activity, and learning activity attempt reports, so their records can be periodically pulled into StackOne and kept up to date. All syncs are full refresh, because the Udemy reporting filters bound a reporting window rather than tracking when a record last changed. `udemy_get_learning_activity_attempt`, `udemy_get_user_activity_report`, `udemy_get_user_assessment_activity`, `udemy_get_user_course_activity`, `udemy_get_user_lab_activity`, `udemy_get_user_path_activity`, `udemy_list_courses`, `udemy_list_learning_paths` `bug-fix` Fixed get_user_course_activity to cursor-based pagination; corrected get_course description to metadata-only (no curriculum, categories may be 'Uncategorized'); clarified get_user_activity_report from_date four-month rolling lookback. # UKG Pro Source: https://docs.stackone.com/connectors/ukg-pro/index How to set up the UKG Pro connector, plus the actions that are available.
UKG Pro
v3.0.0
56 actions · 2 auth methods
HRIS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect to UKG Pro using Service Account credentials for REST API access. Supports employee data, compensation, payroll,... Connect to UKG Pro SOAP Web Services using LoginService token authentication. Requires Service Account or Web User crede... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ukg-pro/index.md for the full list. # UKG Pro Changelog Source: https://docs.stackone.com/connectors/ukg-pro/changelog Release history for the UKG Pro connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync support to 32 actions (27 REST, 5 SOAP) enabling periodic full-refresh synchronisation of employee, compensation, payroll, benefits, PTO, and configuration data. Fixed response format for list_international_employees, get_user_details, and get_security_roles to use standard result wrapper. # UKG Ready Source: https://docs.stackone.com/connectors/ukg-ready/index How to set up the UKG Ready connector, plus the actions and events that are available.
UKG Ready
Previewv2.0.1
163 actions · 1 event · 1 auth method
HRIS ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect to UKG Ready using OAuth 2.0 client credentials for secure API access. Requires OAuth app configuration in UKG R... Optionally, configure receiving Events for UKG Ready into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/ukg-ready/index.md for the full list. ## Events See https://docs.stackone.com/connectors/ukg-ready/index.md for the full list. # UKG Ready Changelog Source: https://docs.stackone.com/connectors/ukg-ready/changelog Release history for the UKG Ready connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` Webhook events are now delivered to the linked account using the per-connection Webhook Auth Token. The previous routing that matched deliveries to a connection by UKG Ready company name is no longer supported and has been removed. `breaking` `bug-fix` The option to pick cost centers up from external rules is no longer offered when creating or updating a rate table. UKG accepts that setting and always stores it as off, so a request that asked for it reported success while changing nothing; removing it makes clear the behaviour is not available rather than silently ignored. `ukg-ready_create_rate_table`, `ukg-ready_update_rate_table` `new-feature` Adds native inbound webhooks through UKG Ready Webhook Subscriptions. Each connection now shows a Native Webhook URL and a Webhook Auth Token; paste the URL as the subscription Endpoint URL and the token as its Bearer token, because UKG Ready drops URL query strings when it sends events. A setup guide covers creating the subscription and choosing payload fields. `description-fix` Linking a rate table to another now explains what the API actually requires: the alternate tables are stored only when an external table is named in the same create request and at least one of the three positional slots carries a table, so a request that sends the operators alone is accepted and stores nothing. Rate schedule updates state that a row's basis cannot be changed there — a differing basis is discarded while the new rate is still applied, which would leave a per-unit rate charged per hour — and that the way to change it is to delete the row and recreate it. Timesheet actions explain that reopen and correct depend on a pay period having been closed by payroll and should be treated as available only when the timesheet lists them. Rate table currency now names the action that reveals whether multi-currency is enabled for the company, and the rate table list warns that each entry carries a long download link so it should be paged when looking a table up by name. `ukg-ready_create_rate_table`, `ukg-ready_list_rate_tables`, `ukg-ready_timesheet_action`, `ukg-ready_update_rate_table`, `ukg-ready_update_rate_table_schedule` `bug-fix` `description-fix` `new-actions` A timesheet action no longer fails when the optional comment is left out. Timesheet actions also explain that the actions a timesheet will accept depend on its state and are listed on the timesheet itself, so a refused action is a state conflict rather than a permissions problem. Rate schedule updates now ask only for the rate items, because a row's basis is fixed when the row is created and a different basis sent on an update is ignored while the new rate is still applied — a rate meant per unit would otherwise be charged per hour — so a basis is changed by deleting the row and recreating it. Creating a rate table likewise asks only for a name, and a rate row only for its rate items. A rate table's external and alternate table links are set when the table is created, using the full three-slot form the API documents, and cannot be changed afterwards; the new Get Rate Table action returns a single table together with those links, which the rate table list leaves out entirely. The option to include cost centers from external rules is described as commonly not stored whatever is sent, so it should be read back before being reported as enabled. `ukg-ready_get_rate_table` `ukg-ready_create_rate_table`, `ukg-ready_create_rate_table_schedule`, `ukg-ready_timesheet_action`, `ukg-ready_update_rate_table`, `ukg-ready_update_rate_table_schedule` `bug-fix` `description-fix` Employee timesheets are now generally available, so the timesheet submit, approve, reject, reopen and correct operations can be reached from an employee and pay period rather than needing an internally sourced id. Extra-pay time entries document that they accept only a date and an amount, and that any other field is reported as a security violation rather than as a field error. Cost center lookups state that the configured trees cannot be discovered and that an index reported as not used simply means that tree is not configured, so an index is better taken from existing time entry or rate schedule data than found by scanning. Rate table currency no longer claims a specific cause for being ignored and states that the company's configured currency may be used regardless. Base compensation explains that an earning rejected for auto-pay reports the same message as one that does not exist, and the two compensation history actions now say which covers one employee and which covers everyone. `ukg-ready_batch_update_time_entries`, `ukg-ready_create_employee_base_compensation`, `ukg-ready_create_rate_table`, `ukg-ready_list_compensation_history`, `ukg-ready_list_employee_compensation_history`, `ukg-ready_list_employee_timesheets`, `ukg-ready_lookup_cost_centers`, `ukg-ready_timesheet_action`, `ukg-ready_update_employee_base_compensation`, `ukg-ready_update_rate_table` `description-fix` Corrected action descriptions across rate tables, time entries and base compensation to match how UKG Ready actually behaves. Batch time-entry updates now explain that both modes replace a date's entries rather than adding to them, and that clock times without a UTC offset are read as UTC. Rate table actions document the 20-character name limit, the settings UKG stores only under certain company configuration, the row-ordering rule for rate rows, and that a rate row's type is fixed once created. Base compensation documents that the effective date cannot be changed after creation, that only one record per date is allowed, and that auto-pay accepts only auto-pay eligible earnings. Paging limits and cost-center tree behaviour are now stated, and the overtime request action explains that it records planned overtime for approval rather than worked hours. # Unbounce Source: https://docs.stackone.com/connectors/unbounce/index How to set up the Unbounce connector, plus the actions and events that are available.
Unbounce
v1.2.0
23 actions · 1 event · 2 auth methods
Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for single-account integrations and internal tools. Requires registering an OAuth app. Optionally, configure receiving Events for Unbounce into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/unbounce/index.md for the full list. ## Events See https://docs.stackone.com/connectors/unbounce/index.md for the full list. # Unbounce Changelog Source: https://docs.stackone.com/connectors/unbounce/changelog Release history for the Unbounce connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added Data Sync support for accounts and landing pages, so these collections can be kept in sync on a schedule. Both refresh in full on every run, because Unbounce's date filters match on creation date and its records carry no last-updated timestamp. `unbounce_list_accounts`, `unbounce_list_pages` `bug-fix` Standardized action category capitalization for more consistent portal filters. `new-events` `native-webhooks` `guide-changes` `guide-images` `auth` Added native webhook support for landing page lead submissions (Page Lead Created), with an illustrated setup guide covering the per-page webhook configuration. Marked the two user actions and the three lead-deletion actions as OAuth 2.0 only, since Unbounce rejects them on API key connections. # Unleashed Source: https://docs.stackone.com/connectors/unleashed/index How to set up the Unleashed connector, plus the actions and events that are available.
Unleashed
Previewv1.1.0
64 actions · 24 events · 1 auth method
ERP
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an Unleashed API Id and API Key (HMAC-SHA256 signed requests). Generated from the Unleashed app under Integrati... Optionally, configure receiving Events for Unleashed into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/unleashed/index.md for the full list. ## Events See https://docs.stackone.com/connectors/unleashed/index.md for the full list. # Unleashed Changelog Source: https://docs.stackone.com/connectors/unleashed/changelog Release history for the Unleashed connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `bug-fix` Added webhook event support for 23 event types covering customers, products, sales orders, sales shipments, credit notes, purchase orders, supplier returns, assemblies and warehouse stock transfers. StackOne creates and removes the Unleashed webhook subscription automatically. Sharpened action details across customers, sales/purchase orders, stock adjustments, BOMs, assemblies, and delete_customer_contact, added a strict OrderStatus enum on sales orders, and rewrote the connection guide with screenshots for the Access Workspace login flow. # Unthread Source: https://docs.stackone.com/connectors/unthread/index How to set up the Unthread connector, plus the actions that are available.
Unthread
Betav0.2.0
70 actions · 1 auth method
Customer Support
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Unthread authenticates with a Service Account key sent in the \`X-Api-Key\` header. The key is created in the Unthread das... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/unthread/index.md for the full list. # Unthread Changelog Source: https://docs.stackone.com/connectors/unthread/changelog Release history for the Unthread connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to the input-free list actions (users, conversations, customers, accounts, tags, ticket types, collaborator types, user groups, surveys, SLA policies and instances, knowledge base articles, and outbound messages) for scheduled full record syncs. `unthread_list_accounts`, `unthread_list_collaborator_types`, `unthread_list_conversations`, `unthread_list_customers`, `unthread_list_kb_articles`, `unthread_list_outbounds`, `unthread_list_sla_instances`, `unthread_list_sla_policies`, `unthread_list_surveys`, `unthread_list_tags`, `unthread_list_ticket_types`, `unthread_list_user_groups`, `unthread_list_users` `new-actions` Initial Unthread connector — manage the Unthread support platform through the Unthread REST API. Covers conversations (tickets), messages, customers, accounts, users and user groups, tags, ticket types, knowledge base articles, outbound messages, SLA policies and instances, surveys, approval requests, automations, collaborator types, Slack user groups, and time-series reporting. # Veremark Source: https://docs.stackone.com/connectors/veremark/index How to set up the Veremark connector, plus the actions and events that are available.
Veremark
v1.2.0
22 actions · 2 events · 1 auth method
Background Checks IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). API tokens are provided by Veremark and cannot be self-generated. Contact your Veremark Account Manager to request sandb... Optionally, configure receiving Events for Veremark into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/veremark/index.md for the full list. ## Events See https://docs.stackone.com/connectors/veremark/index.md for the full list. # Veremark Changelog Source: https://docs.stackone.com/connectors/veremark/changelog Release history for the Veremark connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added a Request Status Changed webhook event that notifies you whenever a background check request or one of its checks changes status. Set the linked account's Native Webhook URL as the webhook URL when creating a request to receive it. `veremark_create_request` `new-feature` `data-sync` Added DataSync support to all five list actions (candidates, checks, criteria, requests, and users). Each action refreshes in full on every sync — Veremark's list endpoints return complete unpaginated collections, and the requests status-change filter only accepts date-only values, so no incremental watermark is possible. # Vimeo Source: https://docs.stackone.com/connectors/vimeo/index How to set up the Vimeo connector, plus the actions that are available.
Vimeo
v2.1.0
100 actions · 2 auth methods
Media
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering a Vimeo developer app. Uses OAuth 2.0 authorization code flow with granular scopes per resource. Requires creating a Vimeo developer app to generate a Personal Access Token. No OAuth redirect flow needed. Token inheri... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/vimeo/index.md for the full list. # Vimeo Changelog Source: https://docs.stackone.com/connectors/vimeo/changelog Release history for the Vimeo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added DataSync v2 support for 10 list actions enabling full-refresh synchronisation of videos, folders, showcases, channels, groups, categories, content ratings, liked videos, watch later, and watch history. `vimeo_list_categories`, `vimeo_list_channels`, `vimeo_list_content_ratings`, `vimeo_list_folders`, `vimeo_list_groups`, `vimeo_list_showcases`, `vimeo_list_user_liked_videos`, `vimeo_list_videos`, `vimeo_list_watch_history`, `vimeo_list_watch_later` `description-improvements` Improved action descriptions to disambiguate self-account vs other-user variants, clarified album_id as numeric ID, added brand_color hex format and showcase privacy plan-gate notes. `vimeo_add_showcase_video`, `vimeo_add_showcase_video_by_user_id`, `vimeo_delete_showcase`, `vimeo_delete_showcase_by_user_id`, `vimeo_get_folder`, `vimeo_get_folder_by_user_id`, `vimeo_get_showcase`, `vimeo_get_showcase_by_user_id`, `vimeo_list_showcase_videos`, `vimeo_list_showcase_videos_by_user_id`, `vimeo_remove_showcase_video`, `vimeo_remove_showcase_video_by_user_id`, `vimeo_update_folder`, `vimeo_update_folder_by_user_id`, `vimeo_update_showcase`, `vimeo_update_showcase_by_user_id` `auth-requirements` `guide-improvements` Migrated to authRequirements with scoped access for all 100 actions. Improved auth guides with screenshots, clearer steps, and field descriptions. # Vincere Source: https://docs.stackone.com/connectors/vincere/index How to set up the Vincere connector, plus the actions that are available.
Vincere
Previewv1.2.1
232 actions · 2 auth methods
ATS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires app registration. Use this authentication method for testing with an existing refresh token. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/vincere/index.md for the full list. # Vincere Changelog Source: https://docs.stackone.com/connectors/vincere/changelog Release history for the Vincere connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` The Tenant field now checks its format when connecting, so entering a full URL or an invalid subdomain shows a clear error instead of a failed connection. `new-feature` Added an action to upload a document to a candidate, such as a resume, cover letter, or offer letter, from a URL or base64 content, with options to set it as the original CV and give it an expiry date. `vincere_post_candidate_id_file` `new-feature` `data-sync` Added DataSync support to 46 reference, user, application, and placement list actions, including application rejection reasons and substatuses, placement amendment reasons, candidate and contact sources, functional and sub-functional expertises, user summaries, offer approvers, and all definition lists (countries, currencies, stages, statuses, job types, document types, teams, branches, divisions, and more). Each action refreshes in full on every sync, since these Vincere endpoints expose no updated-since filter. `vincere_get_application_rejection-reasons`, `vincere_get_application_substatus`, `vincere_get_candidatesources`, `vincere_get_contactsources`, `vincere_get_def_activity_categories`, `vincere_get_def_activity_names`, `vincere_get_def_branches`, `vincere_get_def_brands`, `vincere_get_def_candidate_documenttypes`, `vincere_get_def_companystages`, `vincere_get_def_contactstages`, `vincere_get_def_contractlengthtypes`, `vincere_get_def_countries`, `vincere_get_def_currencies`, `vincere_get_def_custom_status_job`, `vincere_get_def_divisions`, `vincere_get_def_employmenttypes`, `vincere_get_def_genders`, `vincere_get_def_jobstatus`, `vincere_get_def_jobsubtypes`, `vincere_get_def_jobtypes`, `vincere_get_def_language`, `vincere_get_def_languagelevels`, `vincere_get_def_locations`, `vincere_get_def_maritalstatuses`, `vincere_get_def_meetingstatuses`, `vincere_get_def_nationalities`, `vincere_get_def_paycalculations`, `vincere_get_def_payintervals`, `vincere_get_def_paymethods`, `vincere_get_def_relocations`, `vincere_get_def_salarytypes`, `vincere_get_def_stages`, `vincere_get_def_status_candidate`, `vincere_get_def_status_company`, `vincere_get_def_status_contact`, `vincere_get_def_teams`, `vincere_get_def_timetypes`, `vincere_get_def_user_documenttypes`, `vincere_get_functionalexpertises`, `vincere_get_placement_amendment_reasons`, `vincere_get_subfunctionalexpertises`, `vincere_get_user_approvers`, `vincere_get_user_summaries_active`, `vincere_get_user_summaries_administrator`, `vincere_get_user_summaries_all` `improvement` Added support for a custom OAuth redirect URI. `vincere_add_candidate_to_talentpool`, `vincere_create_contact`, `vincere_delete_activity_meeting_id`, `vincere_delete_activity_task_id`, `vincere_delete_application_id`, `vincere_delete_candidate_id_notes_noteid`, `vincere_delete_company_id`, `vincere_delete_company_location_loc_id`, `vincere_delete_contact`, `vincere_getContactEmailActivity`, `vincere_get_activities_id`, `vincere_get_activity_comment_id`, `vincere_get_activity_comment_id_candidates`, `vincere_get_activity_comment_id_categories`, `vincere_get_activity_comment_id_companies`, `vincere_get_activity_comment_id_contacts`, `vincere_get_activity_comment_id_notifyees`, `vincere_get_activity_comment_id_positions`, `vincere_get_activity_meeting_id`, `vincere_get_activity_meeting_id_attendees`, `vincere_get_activity_meeting_id_candidates`, `vincere_get_activity_meeting_id_categories`, `vincere_get_activity_meeting_id_companies`, `vincere_get_activity_meeting_id_contacts`, `vincere_get_activity_meeting_id_notifyees`, `vincere_get_activity_meeting_id_positions`, `vincere_get_activity_task_id`, `vincere_get_application_id`, `vincere_get_application_id_log_list`, `vincere_get_application_log_list_range`, `vincere_get_application_rejection-reasons`, `vincere_get_application_substatus`, `vincere_get_candidate_id`, `vincere_get_candidate_id_applications`, `vincere_get_candidate_id_applications_active`, `vincere_get_candidate_id_applications_status`, `vincere_get_candidate_id_branches`, `vincere_get_candidate_id_brands`, `vincere_get_candidate_id_candidatestatus`, `vincere_get_candidate_id_companylocation`, `vincere_get_candidate_id_compliance`, `vincere_get_candidate_id_corefields`, `vincere_get_candidate_id_currentlocation`, `vincere_get_candidate_id_customfields`, `vincere_get_candidate_id_desiredfunctionalexpertises`, `vincere_get_candidate_id_desiredjobtypes`, `vincere_get_candidate_id_educationdetails`, `vincere_get_candidate_id_emailactivity`, `vincere_get_candidate_id_file_doc_id`, `vincere_get_candidate_id_files`, `vincere_get_candidate_id_functionalexpertises`, `vincere_get_candidate_id_industries`, `vincere_get_candidate_id_languageskills`, `vincere_get_candidate_id_notes`, `vincere_get_candidate_id_owners`, `vincere_get_candidate_id_personallocation`, `vincere_get_candidate_id_placementstatus`, `vincere_get_candidate_id_sourcecontact`, `vincere_get_candidate_id_subfunctionalexpertises`, `vincere_get_candidate_id_workexperiences`, `vincere_get_candidate_id_workingstate`, `vincere_get_candidate_search_matrix_vars`, `vincere_get_candidates_by_talentpool`, `vincere_get_candidatesources`, `vincere_get_company_id`, `vincere_get_company_id_branches`, `vincere_get_company_id_brands`, `vincere_get_company_id_companystatus`, `vincere_get_company_id_customfields`, `vincere_get_company_id_files`, `vincere_get_company_id_firstlocation`, `vincere_get_company_id_industries`, `vincere_get_company_id_locations`, `vincere_get_company_id_logo`, `vincere_get_company_location_loc_id`, `vincere_get_company_search_matrix_vars`, `vincere_get_configurablefield_candidatefield`, `vincere_get_configurablefield_companyfield`, `vincere_get_configurablefield_contactfield`, `vincere_get_configurablefield_placementfield`, `vincere_get_configurablefield_positionfield`, `vincere_get_contact`, `vincere_get_contact_branches`, `vincere_get_contact_brands`, `vincere_get_contact_cus_field`, `vincere_get_contact_id_files`, `vincere_get_contact_id_photo`, `vincere_get_contact_ind`, `vincere_get_contact_jobs`, `vincere_get_contact_per_loc`, `vincere_get_contact_search_matrix_vars`, `vincere_get_contact_status`, `vincere_get_contact_work_loc`, `vincere_get_contacts_by_distribution_list`, `vincere_get_contactsources`, `vincere_get_def_activity_categories`, `vincere_get_def_activity_names`, `vincere_get_def_branches`, `vincere_get_def_brands`, `vincere_get_def_candidate_documenttypes`, `vincere_get_def_companystages`, `vincere_get_def_contactstages`, `vincere_get_def_contractlengthtypes`, `vincere_get_def_countries`, `vincere_get_def_currencies`, `vincere_get_def_custom_status_job`, `vincere_get_def_divisions`, `vincere_get_def_employmenttypes`, `vincere_get_def_genders`, `vincere_get_def_jobstatus`, `vincere_get_def_jobsubtypes`, `vincere_get_def_jobtypes`, `vincere_get_def_language`, `vincere_get_def_languagelevels`, `vincere_get_def_locations`, `vincere_get_def_maritalstatuses`, `vincere_get_def_meetingstatuses`, `vincere_get_def_nationalities`, `vincere_get_def_paycalculations`, `vincere_get_def_payintervals`, `vincere_get_def_paymethods`, `vincere_get_def_relocations`, `vincere_get_def_salarytypes`, `vincere_get_def_stages`, `vincere_get_def_status_candidate`, `vincere_get_def_status_company`, `vincere_get_def_status_contact`, `vincere_get_def_teams`, `vincere_get_def_timetypes`, `vincere_get_def_user_documenttypes`, `vincere_get_distlist_user_contacts`, `vincere_get_distributionlists_contact_contact_id_user_user_id`, `vincere_get_distributionlists_user_user_id`, `vincere_get_first_loc`, `vincere_get_functionalexpertise_id_subfunctionalexpertises`, `vincere_get_functionalexpertises`, `vincere_get_placement_amendment_reasons`, `vincere_get_placement_branches`, `vincere_get_placement_customfields`, `vincere_get_placement_id`, `vincere_get_placement_profitsplits`, `vincere_get_placement_yourcompanydetail`, `vincere_get_position_id`, `vincere_get_position_id_applications`, `vincere_get_position_id_branches`, `vincere_get_position_id_brands`, `vincere_get_position_id_compensation`, `vincere_get_position_id_customfields`, `vincere_get_position_id_logo`, `vincere_get_position_id_owners`, `vincere_get_position_id_placements`, `vincere_get_position_id_positionstatus`, `vincere_get_position_id_ratingskills`, `vincere_get_position_id_screeningquestions`, `vincere_get_position_search_matrix_vars`, `vincere_get_report_statistics_filters`, `vincere_get_setting_offerapproval`, `vincere_get_setting_twilio`, `vincere_get_subfunctionalexpertises`, `vincere_get_talentpool_id_user_user_id_candidates`, `vincere_get_talentpools_candidate_candidate_id_user_user_id`, `vincere_get_talentpools_user_user_id`, `vincere_get_umbrellacompany_umbrellacompanies`, `vincere_get_user`, `vincere_get_user_approvers`, `vincere_get_user_exists`, `vincere_get_user_me`, `vincere_get_user_search_matrix_vars`, `vincere_get_user_summaries`, `vincere_get_user_summaries_active`, `vincere_get_user_summaries_administrator`, `vincere_get_user_summaries_all`, `vincere_patch_activity_comment_id`, `vincere_patch_candidate_id`, `vincere_post_activities`, `vincere_post_activity_comment`, `vincere_post_activity_meeting`, `vincere_post_activity_search`, `vincere_post_activity_task`, `vincere_post_application`, `vincere_post_application_actions`, `vincere_post_application_filter`, `vincere_post_application_id_stage_next_interview`, `vincere_post_application_id_stage_next_sent`, `vincere_post_application_id_stage_reject`, `vincere_post_candidate`, `vincere_post_candidate_activities`, `vincere_post_candidate_id_note`, `vincere_post_company`, `vincere_post_company_activities`, `vincere_post_company_id_file`, `vincere_post_contact_activities`, `vincere_post_contact_id_file`, `vincere_post_contact_work_loc`, `vincere_post_placement_acceptoffer`, `vincere_post_placement_rejectoffer`, `vincere_post_position_activities`, `vincere_post_user_activities`, `vincere_put_activity_meeting_id`, `vincere_put_activity_task_id`, `vincere_put_candidate_id_candidatestatus`, `vincere_put_candidate_id_companylocation`, `vincere_put_candidate_id_currentlocation`, `vincere_put_candidate_id_desiredfunctionalexpertises`, `vincere_put_candidate_id_fe_sfe`, `vincere_put_candidate_id_file_doc_id`, `vincere_put_candidate_id_functionalexpertises`, `vincere_put_candidate_id_notes_noteid`, `vincere_put_candidate_id_personallocation`, `vincere_put_candidate_id_sourcecontact`, `vincere_put_candidate_id_subfunctionalexpertises`, `vincere_put_candidate_id_workingstate`, `vincere_put_company_id`, `vincere_put_company_id_companystatus`, `vincere_put_company_id_customfields`, `vincere_put_contact_cus_field`, `vincere_put_contact_per_loc`, `vincere_put_contact_status`, `vincere_put_position_id_customfields`, `vincere_put_position_id_positionstatus`, `vincere_put_position_id_ratingskill_r_id`, `vincere_remove_candidate_from_talentpool`, `vincere_updateEmailSubscription`, `vincere_update_contact` `new-actions` `guide-changes` Added new actions to the placement resource and updated the setup guide. # Vtiger Source: https://docs.stackone.com/connectors/vtiger/index How to set up the Vtiger connector, plus the actions and events that are available.
Vtiger
v1.3.0
57 actions · 1 event · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses email and access key for basic authentication. Access key can be found under My Preferences in the Vtiger CRM UI. Optionally, configure receiving Events for Vtiger into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/vtiger/index.md for the full list. ## Events See https://docs.stackone.com/connectors/vtiger/index.md for the full list. # Vtiger Changelog Source: https://docs.stackone.com/connectors/vtiger/changelog Release history for the Vtiger connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhooks` Added support for receiving Vtiger Workflow webhook events, delivered by adding a Webhook action to a Vtiger Workflow and pointing it at the connector's native webhook URL. `vtiger_webhook_record_event` `data-sync` Added data sync support to the accounts, contacts, deals, leads, tasks, products, documents, and users list actions, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically. # WeatherAPI.com Source: https://docs.stackone.com/connectors/weatherapi/index How to set up the WeatherAPI.com connector, plus the actions that are available.
WeatherAPI.com
v1.0.0
21 actions · 1 auth method
Weather
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. A single API key unlocks every endpoint, with data depth (history range, forecast days, bu... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/weatherapi/index.md for the full list. # WeatherAPI.com Changelog Source: https://docs.stackone.com/connectors/weatherapi/changelog Release history for the WeatherAPI.com connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Clarified what the marine and IP lookup actions return - the marine daily-summary interval omits swell, wave-height and water-temperature data, and IP lookup returns the local time at the located address alongside its time zone. `weatherapi_bulk_forecast_weather`, `weatherapi_bulk_future_weather`, `weatherapi_bulk_history_weather`, `weatherapi_bulk_ip_lookup`, `weatherapi_bulk_marine_weather`, `weatherapi_get_forecast_weather`, `weatherapi_get_future_weather`, `weatherapi_get_history_weather`, `weatherapi_get_ip_lookup`, `weatherapi_get_marine_weather` `new-connector` Initial release of the WeatherAPI.com connector - 21 actions covering realtime conditions, 14 day forecasts, historical and future weather, marine and tide data, government alerts, astronomy, time zone lookup, sports events and location/IP search, each weather resource also available as a bulk variant for up to 50 locations per call. API key authentication with a connection guide covering key retrieval and rotation. # Webex Source: https://docs.stackone.com/connectors/webex/index How to set up the Webex connector, plus the actions and events that are available.
Webex
Previewv3.1.1
115 actions · 27 events · 2 auth methods
IAM Messaging Meetings
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Log in to your Webex account to connect your data. The Webex integration credentials are configured once on the StackOne connector profile, so users connect by logging in... Optionally, configure receiving Events for Webex into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/webex/index.md for the full list. ## Events See https://docs.stackone.com/connectors/webex/index.md for the full list. # Webex Changelog Source: https://docs.stackone.com/connectors/webex/changelog Release history for the Webex connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `guide` Documented the prerequisites behind common Webex errors — the scopes each webhook resource needs, that announcement mode requires a locked space, and that a failed moderator invite still adds the person as a member. Corrected the connection guide to match the current Webex for Developers portal. `webex_create_membership`, `webex_create_room`, `webex_create_webhook`, `webex_get_organization_details`, `webex_get_role_details`, `webex_list_reports`, `webex_update_room` `webhook` `auth` `bug-fix` Added webhook events for messages, spaces, memberships, meetings, recordings and calls, with subscriptions created and removed automatically when an account is connected or disconnected. Corrected the OAuth scopes required to manage webhooks — reconnect the account so the new scopes take effect. `webex_auth_test`, `webex_create_attachment_action`, `webex_create_device`, `webex_create_location`, `webex_create_meeting`, `webex_create_meeting_invitee`, `webex_create_membership`, `webex_create_message`, `webex_create_person`, `webex_create_report`, `webex_create_room`, `webex_create_team`, `webex_create_team_membership`, `webex_create_webhook`, `webex_create_workspace`, `webex_delete_device`, `webex_delete_location`, `webex_delete_meeting`, `webex_delete_meeting_invitee`, `webex_delete_membership`, `webex_delete_message`, `webex_delete_person`, `webex_delete_recording`, `webex_delete_recording_admin`, `webex_delete_report`, `webex_delete_room`, `webex_delete_team`, `webex_delete_team_membership`, `webex_delete_webhook`, `webex_delete_workspace`, `webex_download_meeting_transcript`, `webex_get_attachment_action_details`, `webex_get_device_details`, `webex_get_event_details`, `webex_get_hybrid_cluster_details`, `webex_get_hybrid_connector_details`, `webex_get_license_details`, `webex_get_location_details`, `webex_get_meeting_details`, `webex_get_meeting_invitee`, `webex_get_meeting_participant_details`, `webex_get_meeting_preferences`, `webex_get_meeting_qualities`, `webex_get_membership_details`, `webex_get_message_details`, `webex_get_my_details`, `webex_get_organization_details`, `webex_get_person_details`, `webex_get_personal_meeting_room_options`, `webex_get_recording_details`, `webex_get_report_details`, `webex_get_resource_group_details`, `webex_get_resource_group_membership_details`, `webex_get_role_details`, `webex_get_room_details`, `webex_get_scheduling_options`, `webex_get_team_details`, `webex_get_team_membership_details`, `webex_get_webhook_details`, `webex_get_workspace_details`, `webex_list_admin_audit_events`, `webex_list_compliance_events`, `webex_list_devices`, `webex_list_events`, `webex_list_hybrid_clusters`, `webex_list_hybrid_connectors`, `webex_list_licenses`, `webex_list_locations`, `webex_list_meeting_invitees`, `webex_list_meeting_participants`, `webex_list_meeting_sites`, `webex_list_meeting_transcripts`, `webex_list_meetings`, `webex_list_memberships`, `webex_list_messages`, `webex_list_organizations`, `webex_list_people`, `webex_list_recordings`, `webex_list_recordings_admin`, `webex_list_report_templates`, `webex_list_reports`, `webex_list_resource_group_memberships`, `webex_list_resource_groups`, `webex_list_roles`, `webex_list_rooms`, `webex_list_team_memberships`, `webex_list_teams`, `webex_list_transcript_snippets`, `webex_list_webhooks`, `webex_list_workspaces`, `webex_unified_get_group`, `webex_unified_get_me`, `webex_unified_get_organization`, `webex_unified_get_role`, `webex_unified_get_user`, `webex_unified_list_groups`, `webex_unified_list_organizations`, `webex_unified_list_resource_types`, `webex_unified_list_resource_users`, `webex_unified_list_roles`, `webex_unified_list_users`, `webex_update_location`, `webex_update_meeting`, `webex_update_meeting_invitee`, `webex_update_meeting_participant`, `webex_update_membership`, `webex_update_message`, `webex_update_person`, `webex_update_personal_meeting_room_options`, `webex_update_resource_group_membership`, `webex_update_room`, `webex_update_team`, `webex_update_team_membership`, `webex_update_webhook`, `webex_update_workspace` `bug-fix` Documented the organization prerequisites behind Webex's most common 403 and 400 responses — the space-moderation entitlement needed for moderator and locked-space options, Webex Calling enabled locations for the people location filter, org public-space discovery for listing public spaces, and the Hybrid Calendar service for workspace calendar setup. `webex_create_attachment_action`, `webex_create_device`, `webex_create_location`, `webex_create_meeting`, `webex_create_meeting_invitee`, `webex_create_membership`, `webex_create_report`, `webex_create_room`, `webex_create_webhook`, `webex_create_workspace`, `webex_delete_device`, `webex_delete_location`, `webex_delete_meeting`, `webex_delete_meeting_invitee`, `webex_delete_membership`, `webex_delete_recording`, `webex_delete_recording_admin`, `webex_delete_report`, `webex_delete_team_membership`, `webex_delete_workspace`, `webex_download_meeting_transcript`, `webex_get_device_details`, `webex_get_event_details`, `webex_get_hybrid_cluster_details`, `webex_get_hybrid_connector_details`, `webex_get_meeting_details`, `webex_get_meeting_invitee`, `webex_get_meeting_participant_details`, `webex_get_meeting_preferences`, `webex_get_meeting_qualities`, `webex_get_personal_meeting_room_options`, `webex_get_recording_details`, `webex_get_report_details`, `webex_get_scheduling_options`, `webex_list_admin_audit_events`, `webex_list_compliance_events`, `webex_list_events`, `webex_list_meeting_invitees`, `webex_list_meeting_participants`, `webex_list_meeting_sites`, `webex_list_meeting_transcripts`, `webex_list_meetings`, `webex_list_messages`, `webex_list_people`, `webex_list_recordings`, `webex_list_recordings_admin`, `webex_list_report_templates`, `webex_list_rooms`, `webex_list_transcript_snippets`, `webex_update_location`, `webex_update_meeting`, `webex_update_meeting_invitee`, `webex_update_meeting_participant`, `webex_update_membership`, `webex_update_personal_meeting_room_options`, `webex_update_resource_group_membership`, `webex_update_room`, `webex_update_team_membership`, `webex_update_workspace` `breaking-changes` `bug-fix` Removed the uc_counters, serviceApp and adminBatchJobs webhook resources that Webex rejects for user OAuth connections, and changed list_messages mentionedPeople from an array to a comma-separated string so the mention filter is applied. Documented the meeting scopes webhook subscriptions need, the list_people id exclusivity rule, the ISO 3166-1 alpha-2 country format, the list_webhooks max range and the list_messages before timestamp format. `webex_auth_test`, `webex_create_membership`, `webex_create_message`, `webex_create_person`, `webex_create_room`, `webex_create_team`, `webex_create_team_membership`, `webex_create_webhook`, `webex_create_workspace`, `webex_delete_message`, `webex_delete_person`, `webex_delete_room`, `webex_delete_team`, `webex_delete_webhook`, `webex_get_attachment_action_details`, `webex_get_license_details`, `webex_get_location_details`, `webex_get_membership_details`, `webex_get_message_details`, `webex_get_my_details`, `webex_get_organization_details`, `webex_get_person_details`, `webex_get_resource_group_details`, `webex_get_resource_group_membership_details`, `webex_get_role_details`, `webex_get_room_details`, `webex_get_team_details`, `webex_get_team_membership_details`, `webex_get_webhook_details`, `webex_get_workspace_details`, `webex_list_devices`, `webex_list_hybrid_clusters`, `webex_list_hybrid_connectors`, `webex_list_licenses`, `webex_list_locations`, `webex_list_memberships`, `webex_list_messages`, `webex_list_organizations`, `webex_list_people`, `webex_list_reports`, `webex_list_resource_group_memberships`, `webex_list_resource_groups`, `webex_list_roles`, `webex_list_rooms`, `webex_list_team_memberships`, `webex_list_teams`, `webex_list_webhooks`, `webex_list_workspaces`, `webex_unified_get_group`, `webex_unified_get_me`, `webex_unified_get_organization`, `webex_unified_get_role`, `webex_unified_get_user`, `webex_unified_list_groups`, `webex_unified_list_organizations`, `webex_unified_list_resource_types`, `webex_unified_list_resource_users`, `webex_unified_list_roles`, `webex_unified_list_users`, `webex_update_message`, `webex_update_person`, `webex_update_room`, `webex_update_team`, `webex_update_webhook`, `webex_update_workspace` `action-fixes` Marked get_event_details as preview due to Compliance Officer role requirement. Corrected list_events limitation description. `webex_get_event_details`, `webex_list_events` `data-sync` Added data synchronisation support for unified users, groups, roles, organizations, and custom organizations, roles, and licenses actions. `webex_list_licenses`, `webex_list_organizations`, `webex_list_roles`, `webex_unified_list_groups`, `webex_unified_list_organizations`, `webex_unified_list_roles`, `webex_unified_list_users` `bug-fix` Fixed user lists and user lookups returning role entries without their identifiers. `webex_auth_test`, `webex_unified_get_group`, `webex_unified_get_me`, `webex_unified_get_organization`, `webex_unified_get_role`, `webex_unified_get_user`, `webex_unified_list_groups`, `webex_unified_list_organizations`, `webex_unified_list_resource_types`, `webex_unified_list_resource_users`, `webex_unified_list_roles`, `webex_unified_list_users` `new-feature` Added a managed OAuth option where the Webex app credentials are configured once at the connector level, so users can connect by logging in without creating their own Webex integration. `webex_auth_test`, `webex_create_attachment_action`, `webex_create_device`, `webex_create_location`, `webex_create_meeting`, `webex_create_meeting_invitee`, `webex_create_membership`, `webex_create_message`, `webex_create_person`, `webex_create_report`, `webex_create_room`, `webex_create_team`, `webex_create_team_membership`, `webex_create_webhook`, `webex_create_workspace`, `webex_delete_device`, `webex_delete_location`, `webex_delete_meeting`, `webex_delete_meeting_invitee`, `webex_delete_membership`, `webex_delete_message`, `webex_delete_person`, `webex_delete_recording`, `webex_delete_recording_admin`, `webex_delete_report`, `webex_delete_room`, `webex_delete_team`, `webex_delete_team_membership`, `webex_delete_webhook`, `webex_delete_workspace`, `webex_download_meeting_transcript`, `webex_get_attachment_action_details`, `webex_get_device_details`, `webex_get_event_details`, `webex_get_hybrid_cluster_details`, `webex_get_hybrid_connector_details`, `webex_get_license_details`, `webex_get_location_details`, `webex_get_meeting_details`, `webex_get_meeting_invitee`, `webex_get_meeting_participant_details`, `webex_get_meeting_preferences`, `webex_get_meeting_qualities`, `webex_get_membership_details`, `webex_get_message_details`, `webex_get_my_details`, `webex_get_organization_details`, `webex_get_person_details`, `webex_get_personal_meeting_room_options`, `webex_get_recording_details`, `webex_get_report_details`, `webex_get_resource_group_details`, `webex_get_resource_group_membership_details`, `webex_get_role_details`, `webex_get_room_details`, `webex_get_scheduling_options`, `webex_get_team_details`, `webex_get_team_membership_details`, `webex_get_webhook_details`, `webex_get_workspace_details`, `webex_list_admin_audit_events`, `webex_list_compliance_events`, `webex_list_devices`, `webex_list_events`, `webex_list_hybrid_clusters`, `webex_list_hybrid_connectors`, `webex_list_licenses`, `webex_list_locations`, `webex_list_meeting_invitees`, `webex_list_meeting_participants`, `webex_list_meeting_sites`, `webex_list_meeting_transcripts`, `webex_list_meetings`, `webex_list_memberships`, `webex_list_messages`, `webex_list_organizations`, `webex_list_people`, `webex_list_recordings`, `webex_list_recordings_admin`, `webex_list_report_templates`, `webex_list_reports`, `webex_list_resource_group_memberships`, `webex_list_resource_groups`, `webex_list_roles`, `webex_list_rooms`, `webex_list_team_memberships`, `webex_list_teams`, `webex_list_transcript_snippets`, `webex_list_webhooks`, `webex_list_workspaces`, `webex_unified_get_group`, `webex_unified_get_me`, `webex_unified_get_organization`, `webex_unified_get_role`, `webex_unified_get_user`, `webex_unified_list_groups`, `webex_unified_list_organizations`, `webex_unified_list_resource_types`, `webex_unified_list_resource_users`, `webex_unified_list_roles`, `webex_unified_list_users`, `webex_update_location`, `webex_update_meeting`, `webex_update_meeting_invitee`, `webex_update_meeting_participant`, `webex_update_membership`, `webex_update_message`, `webex_update_person`, `webex_update_personal_meeting_room_options`, `webex_update_resource_group_membership`, `webex_update_room`, `webex_update_team`, `webex_update_team_membership`, `webex_update_webhook`, `webex_update_workspace` `breaking-change` Migrated to authRequirements. Added missing filter parameters, new device/location actions, fixed enum values, updated OAuth scopes, and improved action documentation. # Webflow Source: https://docs.stackone.com/connectors/webflow/index How to set up the Webflow connector, plus the actions and events that are available.
Webflow
v2.2.0
98 actions · 15 events · 2 auth methods
CMS E-Commerce IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Workspace-level access across all sites with granular OAuth scopes. Required for Custom Code endpoints. Scoped to a single site. Quick to set up but cannot access Custom Code endpoints. Max 5 tokens per site. Optionally, configure receiving Events for Webflow into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/webflow/index.md for the full list. ## Events See https://docs.stackone.com/connectors/webflow/index.md for the full list. # Webflow Changelog Source: https://docs.stackone.com/connectors/webflow/changelog Release history for the Webflow connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Added 14 webhook events for form submissions, site publishing, pages, CMS items, ecommerce orders and inventory, and comments. StackOne creates one webhook per selected event on the site set in the new Webhook Site ID field, and deletes them on disconnect. `new-feature` `data-sync` Added DataSync support to list_sites. `webflow_list_sites` `guide-changes` `guide-images` Added connection guides for OAuth 2.0 and Site Token authentication, with step-by-step screenshots of the Webflow portal and guidance on which permissions to grant. `auth-improvements` Migrated all actions from requiredScopes to authRequirements, restricting the Custom Code actions and introspect_token to OAuth 2.0 since Site Tokens cannot call those endpoints. `webflow_create_asset_folder`, `webflow_create_collection`, `webflow_create_collection_field`, `webflow_create_collection_items`, `webflow_create_live_collection_items`, `webflow_create_product`, `webflow_create_redirect`, `webflow_create_site`, `webflow_create_sku`, `webflow_create_webhook`, `webflow_delete_asset`, `webflow_delete_collection`, `webflow_delete_collection_field`, `webflow_delete_collection_item`, `webflow_delete_collection_items`, `webflow_delete_form_submission`, `webflow_delete_page_custom_code`, `webflow_delete_redirect`, `webflow_delete_robots_txt`, `webflow_delete_site`, `webflow_delete_site_custom_code`, `webflow_delete_webhook`, `webflow_delete_well_known_files`, `webflow_fulfill_order`, `webflow_get_asset`, `webflow_get_asset_folder`, `webflow_get_authorized_user`, `webflow_get_collection`, `webflow_get_collection_item`, `webflow_get_comment_thread`, `webflow_get_component_content`, `webflow_get_component_properties`, `webflow_get_custom_domains`, `webflow_get_ecommerce_settings`, `webflow_get_form_schema`, `webflow_get_form_submission`, `webflow_get_live_collection_item`, `webflow_get_order`, `webflow_get_page_content`, `webflow_get_page_custom_code`, `webflow_get_page_metadata`, `webflow_get_product`, `webflow_get_redirects`, `webflow_get_registered_scripts`, `webflow_get_robots_txt`, `webflow_get_site`, `webflow_get_site_activity_logs`, `webflow_get_site_custom_code`, `webflow_get_site_plan`, `webflow_get_webhook`, `webflow_introspect_token`, `webflow_list_asset_folders`, `webflow_list_assets`, `webflow_list_collection_items`, `webflow_list_collections`, `webflow_list_comment_replies`, `webflow_list_comment_threads`, `webflow_list_components`, `webflow_list_custom_code_blocks`, `webflow_list_form_submissions`, `webflow_list_form_submissions_by_site`, `webflow_list_forms`, `webflow_list_inventory`, `webflow_list_live_collection_items`, `webflow_list_orders`, `webflow_list_pages`, `webflow_list_products`, `webflow_list_sites`, `webflow_list_webhooks`, `webflow_publish_collection_items`, `webflow_publish_site`, `webflow_refund_order`, `webflow_register_hosted_script`, `webflow_register_inline_script`, `webflow_replace_robots_txt`, `webflow_set_well_known_file`, `webflow_unfulfill_order`, `webflow_unpublish_live_collection_items`, `webflow_update_asset`, `webflow_update_collection_field`, `webflow_update_collection_item`, `webflow_update_collection_items`, `webflow_update_component_content`, `webflow_update_component_properties`, `webflow_update_form_submission`, `webflow_update_inventory`, `webflow_update_live_collection_items`, `webflow_update_order`, `webflow_update_page_content`, `webflow_update_page_metadata`, `webflow_update_product`, `webflow_update_redirect`, `webflow_update_robots_txt`, `webflow_update_site`, `webflow_update_sku`, `webflow_upload_asset`, `webflow_upsert_page_custom_code`, `webflow_upsert_site_custom_code` `removed-actions` Removed unified IAM actions (users, roles, organizations, credentials). Neither auth type exposes a workspace-members or roles API, so list_users returned only the token-owning user and list_roles returned an invented literal role with no real workspace data. `webflow_unified_get_me`, `webflow_unified_get_organization`, `webflow_unified_get_role`, `webflow_unified_get_user`, `webflow_unified_list_organizations`, `webflow_unified_list_roles`, `webflow_unified_list_users` `new-actions` Added unified IAM users, roles, organizations, and credentials actions. # Weights & Biases Source: https://docs.stackone.com/connectors/weightsandbiases/index How to set up the Weights & Biases connector, plus the actions and events that are available.
Weights & Biases
v2.0.0
35 actions · 4 events · 1 auth method
AI
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires a W&B API key minted at https://wandb.ai/authorize. The key inherits the minter's W&B permissions (no scopes);... Optionally, configure receiving Events for Weights & Biases into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/weightsandbiases/index.md for the full list. ## Events See https://docs.stackone.com/connectors/weightsandbiases/index.md for the full list. # Weights & Biases Changelog Source: https://docs.stackone.com/connectors/weightsandbiases/changelog Release history for the Weights & Biases connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking-change` Fixed list_artifacts advertising the unsupported "+versionIndex" sort column (backend returns HTTP 400 — only created_at is orderable). Removed the misleading `description` input from create_run and update_run — W&B's `upsertBucket` accepts `description` in its input schema, but the server silently normalizes it; reads (via get_run or the UI) always return the composite `displayName + '\n' + notes`, so any caller-supplied `description` value is discarded. Callers should now use `notes` for descriptive text; both action `details` and the `notes` input description now spell out the actual W&B semantics. # Welcome to the Jungle Source: https://docs.stackone.com/connectors/welcometothejungle/index How to set up the Welcome to the Jungle connector, plus the actions that are available.
Welcome to the Jungle
Betav1.1.1
35 actions · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Static API token issued by Welcome to the Jungle support. Scopes are baked into the token at issuance and cannot be chan... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/welcometothejungle/index.md for the full list. # Welcome to the Jungle Changelog Source: https://docs.stackone.com/connectors/welcometothejungle/changelog Release history for the Welcome to the Jungle connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Replaced the API Token documentation link with a full connection guide explaining that Welcome to the Jungle issues the token to your organization on request, and how to confirm it carries the scopes you need. `new-actions` Added Data Sync support for organizations, jobs, languages, tools, sectors, and articles list endpoints. # WhatsApp Business Source: https://docs.stackone.com/connectors/whatsapp-business/index How to set up the WhatsApp Business connector, plus the actions and events that are available.
WhatsApp Business
v2.0.0
81 actions · 14 events · 2 auth methods
Messaging IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 via Facebook Login for Business. Requires a Meta App with Facebook Login for Business configured and WhatsApp... Uses a long-lived System User access token generated in Meta Business Settings. The system user needs control of your Me... Optionally, configure receiving Events for WhatsApp Business into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/whatsapp-business/index.md for the full list. ## Events See https://docs.stackone.com/connectors/whatsapp-business/index.md for the full list. # WhatsApp Business Changelog Source: https://docs.stackone.com/connectors/whatsapp-business/changelog Release history for the WhatsApp Business connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `breaking` `new-events` `new-actions` `new-feature` `bug-fix` `guide` Renamed 8 actions to match Meta's API names, added Flows, media, and webhook event actions plus System User auth, and fixed template and group schemas. `whatsapp-business_check_call_permissions`, `whatsapp-business_configure_conversational_automation`, `whatsapp-business_create_business_user`, `whatsapp-business_create_flow`, `whatsapp-business_create_whatsapp_business_account_phone_number`, `whatsapp-business_delete_flow`, `whatsapp-business_delete_media`, `whatsapp-business_deprecate_flow`, `whatsapp-business_download_media`, `whatsapp-business_edit_template`, `whatsapp-business_get_active_groups`, `whatsapp-business_get_blocked_users`, `whatsapp-business_get_client_whatsapp_business_accounts`, `whatsapp-business_get_flow`, `whatsapp-business_get_message_templates`, `whatsapp-business_get_owned_whatsapp_business_accounts`, `whatsapp-business_get_whatsapp_business_account_phone_numbers`, `whatsapp-business_list_flow_assets`, `whatsapp-business_list_flows`, `whatsapp-business_publish_flow`, `whatsapp-business_retrieve_media_url`, `whatsapp-business_update_flow_json`, `whatsapp-business_update_flow_metadata`, `whatsapp-business_upload_media` `whatsapp-business_get_call_permissions`, `whatsapp-business_invite_business_user`, `whatsapp-business_list_active_groups`, `whatsapp-business_list_blocked_users`, `whatsapp-business_list_phone_numbers`, `whatsapp-business_list_templates`, `whatsapp-business_set_conversational_automation`, `whatsapp-business_update_template` `whatsapp-business_add_assigned_user`, `whatsapp-business_approve_join_requests`, `whatsapp-business_block_users`, `whatsapp-business_create_group`, `whatsapp-business_create_schedule`, `whatsapp-business_create_template`, `whatsapp-business_delete_group`, `whatsapp-business_delete_group_invite_link`, `whatsapp-business_delete_template`, `whatsapp-business_deregister_phone_number`, `whatsapp-business_get_assigned_users`, `whatsapp-business_get_business_profile`, `whatsapp-business_get_group`, `whatsapp-business_get_group_invite_link`, `whatsapp-business_get_join_requests`, `whatsapp-business_get_message_history`, `whatsapp-business_get_phone_number`, `whatsapp-business_get_schedules`, `whatsapp-business_get_subscribed_apps`, `whatsapp-business_get_template`, `whatsapp-business_get_whatsapp_business_account`, `whatsapp-business_list_business_users`, `whatsapp-business_list_system_users`, `whatsapp-business_manage_call`, `whatsapp-business_mark_message_as_read`, `whatsapp-business_register_phone_number`, `whatsapp-business_reject_join_requests`, `whatsapp-business_remove_assigned_user`, `whatsapp-business_remove_group_participants`, `whatsapp-business_request_verification_code`, `whatsapp-business_reset_group_invite_link`, `whatsapp-business_send_audio_message`, `whatsapp-business_send_contact_message`, `whatsapp-business_send_document_message`, `whatsapp-business_send_group_invite_template`, `whatsapp-business_send_group_message`, `whatsapp-business_send_image_message`, `whatsapp-business_send_interactive_message`, `whatsapp-business_send_location_message`, `whatsapp-business_send_reaction`, `whatsapp-business_send_sticker_message`, `whatsapp-business_send_template_message`, `whatsapp-business_send_text_message`, `whatsapp-business_send_video_message`, `whatsapp-business_set_two_step_pin`, `whatsapp-business_unblock_users`, `whatsapp-business_unified_get_me`, `whatsapp-business_unified_get_organization`, `whatsapp-business_unified_get_role`, `whatsapp-business_unified_list_organizations`, `whatsapp-business_unified_list_resource_types`, `whatsapp-business_unified_list_resource_users`, `whatsapp-business_unified_list_roles`, `whatsapp-business_update_business_profile`, `whatsapp-business_update_group`, `whatsapp-business_update_whatsapp_business_account`, `whatsapp-business_verify_code` `data-sync` Added DataSync support for message templates, phone numbers, schedules, subscribed apps, organizations, and roles. `whatsapp-business_get_schedules`, `whatsapp-business_get_subscribed_apps`, `whatsapp-business_list_phone_numbers`, `whatsapp-business_list_templates`, `whatsapp-business_unified_list_organizations`, `whatsapp-business_unified_list_roles` `bug-fix` Fixed a missing permission declaration on the current-user action and removed a duplicated internal field mapping. # Whois Source: https://docs.stackone.com/connectors/whois/index How to set up the Whois connector, plus the actions that are available.
Whois
v1.0.0
20 actions · 1 auth method
Security
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a single account API key shared across every WhoisXML product, passed as a query parameter (or in the request body... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/whois/index.md for the full list. # Whois Changelog Source: https://docs.stackone.com/connectors/whois/changelog Release history for the Whois connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Corrected the API key connection guide to link to the WhoisXML API sign-in page, and added the missing step for opening the account menu from the profile icon to reach My products, with a screenshot. `new-connector` Initial release of the Whois (WhoisXML API) connector with 20 domain, IP, email, and threat intelligence actions. # Wikipedia Source: https://docs.stackone.com/connectors/wikipedia/index How to set up the Wikipedia connector, plus the actions that are available.
Wikipedia
v1.0.2
15 actions · 3 auth methods
Knowledge Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a Wikimedia bearer access token issued by an owner-only OAuth 2.0 client on Meta-Wiki. The token is long-lived and... Delegated access on behalf of a signed-in Wikimedia user. Requires registering an OAuth 2.0 consumer on Meta-Wiki. Acces... App-only access without a signed-in user, using a Wikimedia OAuth 2.0 owner consumer. Access tokens expire after 4 hours... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/wikipedia/index.md for the full list. # Wikipedia Changelog Source: https://docs.stackone.com/connectors/wikipedia/changelog Release history for the Wikipedia connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `doc-change` Documented an upstream Wikimedia limitation on Get Page History Counts — the expensive count types (minor, editors, anonymous, reverted, and the *edits variants) scan a page's full revision history and time out with a 502 Bad Gateway on pages with very large histories (e.g. Earth). The action details and the type parameter now warn about this and recommend using the cheaper edits count or a smaller page. `wikipedia_get_page_history_counts` `bug-fix` `guide-fix` Restricted the Language Code field to a validated dropdown of 337 supported Wikipedia editions so a connection can no longer be created with an unrecognized language code that fails at request time. Renamed the Personal API Token authentication and its Hub field to Access Token to match the credential issued by Meta-Wiki, and aligned the field helper text. Improved the connection guides — added the manual navigation path to the OAuth consumer registration form, corrected Meta-Wiki portal labels, and documented the Applicable project, Allowed IP ranges, and Allowed pages for editing fields. `wikipedia_create_page`, `wikipedia_get_featured_content`, `wikipedia_get_file`, `wikipedia_get_on_this_day`, `wikipedia_get_page`, `wikipedia_get_page_history`, `wikipedia_get_page_history_counts`, `wikipedia_get_page_language_links`, `wikipedia_get_page_media_files`, `wikipedia_get_page_metadata`, `wikipedia_get_page_with_html`, `wikipedia_get_revision`, `wikipedia_search_pages`, `wikipedia_search_titles`, `wikipedia_update_page` `new-actions` Initial Wikipedia connector with 15 actions across pages (read plus create/update), revisions, search, daily feeds, and files, and Personal API Token, OAuth 2.0, and OAuth 2.0 Client Credentials authentication. # Windsor.ai Source: https://docs.stackone.com/connectors/windsorai/index How to set up the Windsor.ai connector, plus the actions that are available.
Windsor.ai
v1.0.0
12 actions · 1 auth method
Marketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). A single API key covering every endpoint, with no app registration required. The key is tied to the individual Windsor.a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/windsorai/index.md for the full list. # Windsor.ai Changelog Source: https://docs.stackone.com/connectors/windsorai/changelog Release history for the Windsor.ai connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `windsorai_generate_co_user_url`, `windsorai_get_connector_connect_info`, `windsorai_get_connector_options`, `windsorai_list_co_user_linked_accounts`, `windsorai_list_connected_accounts`, `windsorai_list_connector_actions`, `windsorai_list_connectors`, `windsorai_list_custom_fields`, `windsorai_retrieve_available_connector_fields` `description-fix` Description wording fixes from agentic MCP retesting — list_co_user_linked_accounts now states it reports link provenance only, not connection status; list_connector_actions describes its result as a catalogue that performs nothing; retrieve_available_connector_fields states it returns field metadata for connected sources only, replacing a procedural pre-check instruction on its connector input. `windsorai_list_co_user_linked_accounts`, `windsorai_list_connector_actions`, `windsorai_retrieve_available_connector_fields` `description-fix` `bug-fix` `data-sync` Description fixes from agentic MCP testing — data source inputs now state that ids are Windsor.ai slugs rather than platform display names, and four actions describe their real scope and response shape. Added DataSync support for list_custom_fields, plus a placeholder and format detail on the API Key field. `windsorai_get_connector_connect_info`, `windsorai_get_connector_options`, `windsorai_list_co_user_linked_accounts`, `windsorai_list_connected_accounts`, `windsorai_list_custom_fields`, `windsorai_retrieve_available_connector_fields` `new-connector` Initial Windsor.ai connector with 12 actions across 6 resources (reporting data, connectors, connected accounts, connector actions, co-user linked accounts, custom fields). Covers cross-source reporting via get_connector_data with field discovery, connector and option catalogues, co-user authorization links, and write-action execution on connected platforms. Authenticated with a single API key passed as a query parameter. Added the API Key connection guide. # Wistia Source: https://docs.stackone.com/connectors/wistia/index How to set up the Wistia connector, plus the actions and events that are available.
Wistia
Previewv2.0.0
63 actions · 19 events · 2 auth methods
Media
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Wistia account securely using OAuth 2.0 authorization for multi-user access and enhanced security. Use an API Token for quick authentication. Best suited for testing, development, or single-account integrations. Optionally, configure receiving Events for Wistia into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/wistia/index.md for the full list. ## Events See https://docs.stackone.com/connectors/wistia/index.md for the full list. # Wistia Changelog Source: https://docs.stackone.com/connectors/wistia/changelog Release history for the Wistia connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `breaking` Migrated to authRequirements for per-auth-type scope control; gated create_expiring_token to the API Token auth type (OAuth cannot create expiring tokens because its access tokens expire), and marked OAuth 2.0 as beta pending end-to-end testing. `wistia_archive_medias`, `wistia_bulk_delete_subfolders`, `wistia_copy_folder`, `wistia_copy_media`, `wistia_create_allowed_domain`, `wistia_create_caption`, `wistia_create_channel`, `wistia_create_channel_episode`, `wistia_create_expiring_token`, `wistia_create_folder`, `wistia_create_subfolder`, `wistia_create_tag`, `wistia_create_webinar`, `wistia_create_webinar_registration`, `wistia_delete_allowed_domain`, `wistia_delete_caption`, `wistia_delete_channel`, `wistia_delete_channel_episode`, `wistia_delete_customizations`, `wistia_delete_folder`, `wistia_delete_media`, `wistia_delete_subfolder`, `wistia_delete_tag`, `wistia_delete_webinar`, `wistia_get_account`, `wistia_get_allowed_domain`, `wistia_get_caption`, `wistia_get_channel`, `wistia_get_customizations`, `wistia_get_folder`, `wistia_get_media`, `wistia_get_media_analytics`, `wistia_get_media_stats`, `wistia_get_subfolder`, `wistia_get_webinar`, `wistia_list_all_captions`, `wistia_list_all_episodes`, `wistia_list_allowed_domains`, `wistia_list_channel_episodes`, `wistia_list_channels`, `wistia_list_folders`, `wistia_list_media_captions`, `wistia_list_medias`, `wistia_list_sharings`, `wistia_list_subfolders`, `wistia_list_tags`, `wistia_list_webinars`, `wistia_move_medias`, `wistia_publish_channel_episode`, `wistia_purchase_captions`, `wistia_restore_medias`, `wistia_swap_media`, `wistia_translate_media`, `wistia_unpublish_channel_episode`, `wistia_update_caption`, `wistia_update_channel`, `wistia_update_channel_episode`, `wistia_update_customizations`, `wistia_update_folder`, `wistia_update_media`, `wistia_update_subfolder`, `wistia_update_webinar`, `wistia_upload_media` `bug-fix` `description-fix` Fixed create_expiring_token rejecting all expiry times by typing expires_at as an ISO 8601 string (previously a Unix number that always returned 502) and permissions as an array, bulk_delete_subfolders now returns a success message instead of an empty body, and documented provider-side error behaviour (create_expiring_token's two-day expiry limit and delete_tag's 404 for an unknown tag name). `wistia_bulk_delete_subfolders`, `wistia_create_expiring_token`, `wistia_delete_tag` `bug-fix` `description-fix` Fixed the channel episodes media_id filter returning 502 and delete_tag returning an empty response, corrected update_folder to send anonymous upload/download flags in the format Wistia applies, and clarified several action and parameter descriptions. `wistia_copy_folder`, `wistia_create_expiring_token`, `wistia_delete_tag`, `wistia_get_account`, `wistia_get_folder`, `wistia_list_all_episodes`, `wistia_list_channel_episodes`, `wistia_list_channels`, `wistia_list_folders`, `wistia_list_medias`, `wistia_list_tags`, `wistia_update_folder` `data-sync` Added Data Sync support for medias, folders, channels, channel episodes, captions, allowed domains, tags, and webinars. `wistia_list_all_captions`, `wistia_list_all_episodes`, `wistia_list_allowed_domains`, `wistia_list_channels`, `wistia_list_folders`, `wistia_list_medias`, `wistia_list_tags`, `wistia_list_webinars` `new-actions` Added native inbound webhook support with 19 event actions (media lifecycle, viewing-session, and live-event/webinar events), an event router keyed on the batched events[].type envelope, an externalAccountIdExtractor for multi-tenant routing, and a manual-setup events connection guide. Verified end-to-end delivery for the media.* lifecycle events. # WooCommerce Source: https://docs.stackone.com/connectors/woocommerce/index How to set up the WooCommerce connector, plus the actions that are available.
WooCommerce
v2.1.0
72 actions · 1 auth method
E-Commerce
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate using WooCommerce REST API keys (Consumer Key and Consumer Secret) generated from your WooCommerce store se... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/woocommerce/index.md for the full list. # WooCommerce Changelog Source: https://docs.stackone.com/connectors/woocommerce/changelog Release history for the WooCommerce connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for 13 collections (orders, customers, products, product categories, tags, attributes, reviews, coupons, tax rates, tax classes, shipping zones, payment gateways and webhooks). Orders, products and coupons sync incrementally on modified_after; the other ten full-refresh on each run. Those three actions gain three optional inputs documented by WooCommerce but not previously mapped - modified_after, modified_before and dates_are_gmt - and send dates_are_gmt as true whenever a modified date filter is supplied, so the filter is compared in GMT rather than the store's local timezone. Existing after and before behaviour is unchanged. No request step, result or existing input was altered. Those three actions are marked releaseStage preview as they carry these config changes. `woocommerce_list_coupons`, `woocommerce_list_customers`, `woocommerce_list_orders`, `woocommerce_list_payment_gateways`, `woocommerce_list_product_attributes`, `woocommerce_list_product_categories`, `woocommerce_list_product_reviews`, `woocommerce_list_product_tags`, `woocommerce_list_products`, `woocommerce_list_shipping_zones`, `woocommerce_list_tax_classes`, `woocommerce_list_tax_rates`, `woocommerce_list_webhooks` `breaking` `bug-fix` Renamed the order refund restock flag to api_restock so it now controls restocking, and corrected sort options and behaviour notes across product, order, coupon, tax and webhook actions. # Workable Source: https://docs.stackone.com/connectors/workable/index How to set up the Workable connector, plus the actions and events that are available.
Workable
v2.2.3
70 actions · 7 events · 1 auth method
ATS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). The steps in this guide require Super Admin privileges within Workable. Optionally, configure receiving Events for Workable into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/workable/index.md for the full list. ## Events See https://docs.stackone.com/connectors/workable/index.md for the full list. # Workable Changelog Source: https://docs.stackone.com/connectors/workable/changelog Release history for the Workable connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `guide` Updated the API Key connection guide with screenshots, the exact Workable labels, where to find Settings and Company profile, and the API scopes this connection needs. `description-fix` Delete Department explains that it deletes only with force, and that a call without force only checks for attached resources and returns a conflict error listing them. List Legal Entities, Get Job Members and List Custom Attributes now explain which entries to use and which related action covers employee fields or external recruiters. `workable_delete_department`, `workable_get_job_members`, `workable_list_custom_attributes`, `workable_list_legal_entities` `bug-fix` `description-fix` Update Department can now rename a top-level department or move a department to the top level by omitting the parent, and Delete Webhook Subscription returns a deletion confirmation. Create Employee lists the fields Workable requires, Tag Candidate explains how Workable shortens tags, Delete Department documents its pre-delete check, and Get Job Activities, Get Employee Documents, Invite Member and Create Talent Pool Candidate document the provider's ordering, page-size, collaboration-rule and stage values. List Employees, List Candidates and List Time Off Requests now explain how to find a record by name, and List Departments and List Employees note that they include records created since the last data sync. `workable_create_employee`, `workable_create_talent_pool_candidate`, `workable_delete_department`, `workable_delete_subscription`, `workable_get_candidate_files`, `workable_get_employee_documents`, `workable_get_job_activities`, `workable_invite_member`, `workable_list_candidates`, `workable_list_departments`, `workable_list_employees`, `workable_list_timeoff_requests`, `workable_tag_candidate`, `workable_update_candidate`, `workable_update_department` `data-sync` Added scheduled data sync to twelve collection actions — employees and employee fields, departments, stages, recruiters, accounts, legal entities, custom attributes, disqualification reasons, work schedules, time off categories and webhook subscriptions — so these collections can be kept in sync and searched without calling Workable on every request. Employees page through results automatically; the remaining collections are returned in full by a single request. All syncs use full refreshes because the endpoints mapped here offer no last-updated filter. `workable_list_accounts`, `workable_list_custom_attributes`, `workable_list_departments`, `workable_list_disqualification_reasons`, `workable_list_employee_fields`, `workable_list_employees`, `workable_list_legal_entities`, `workable_list_permission_sets`, `workable_list_recruiters`, `workable_list_stages`, `workable_list_subscriptions`, `workable_list_timeoff_categories`, `workable_list_work_schedules` `new-actions` Added inbound webhook (events) support: StackOne auto-provisions Workable webhook subscriptions on connect (one per enabled event, via the Subscriptions API) and removes them on disconnect, routing candidate, employee, onboarding, and time off events to your integration; includes a webhook events setup guide. `bug-fix` `new-actions` `schema` Standardized list/get output: non-paginated collections return the items array under data, paginated collections return the full provider body (preserving paging/total_count), and single-resource gets return the entity object directly. Candidate skills input changed from a comma-separated string to an array. Newly required existing params: account-token member_id/employee_id, move_candidate_to_stage member_id, update_department parent_id, and update_employee multi-value row_id. Added filter params, score_card, requisition_attributes, updated_after; documented per-action pagination (cursor/offset) and date/enum/recruiter_key/legal_entity/work_schedule constraints; marked account-limited write actions preview. # Workday (Rest and Soap) Source: https://docs.stackone.com/connectors/workday/index How to set up the Workday (Rest and Soap) connector, plus the actions that are available.
Workday (Rest and Soap)
v1.4.1
162 actions · 3 auth methods
HRIS ATS LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). StackOne manages the OAuth credentials. Uses user login flow — each user authorizes via their Workday account. Uses client credentials with a static refresh token. No interactive login required. You manage the OAuth credentials. Uses user login flow — each user authorizes via their Workday account. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/workday/index.md for the full list. # Workday (Rest and Soap) Changelog Source: https://docs.stackone.com/connectors/workday/changelog Release history for the Workday (Rest and Soap) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` `description-fix` `new-feature` Added a worker search action that finds a worker by name or employee ID and returns their Workday ID, person ID and current job in a single small response, and corrected guidance across worker listing, WQL, time off, recruiting, learning, org types and holiday calendars. `workday_search_workers` `workday_close_job_requisition`, `workday_create_employee`, `workday_create_feedback`, `workday_create_home_contact_change`, `workday_create_interview_feedback`, `workday_create_job_posting`, `workday_create_leave_of_absence`, `workday_create_position`, `workday_create_time_off_request`, `workday_create_work_contact_change`, `workday_create_worker_checkin`, `workday_create_worker_explicit_skill`, `workday_create_worker_skill_items`, `workday_get_custom_object_definition`, `workday_get_interview_feedback`, `workday_get_job_change_reason`, `workday_get_job_posting`, `workday_get_people`, `workday_get_people_home_addresses`, `workday_get_people_home_emails`, `workday_get_people_home_phones`, `workday_get_people_legal_name`, `workday_get_people_personal_information`, `workday_get_people_preferred_name`, `workday_get_people_work_addresses`, `workday_get_people_work_emails`, `workday_get_people_work_phones`, `workday_get_time_off_detail`, `workday_get_worker`, `workday_get_worker_documents`, `workday_get_worker_event_history`, `workday_get_worker_skill_item`, `workday_get_worker_time_off_entry`, `workday_get_worker_time_off_plan`, `workday_list_absence_balances`, `workday_list_background_checks`, `workday_list_benefit_elections`, `workday_list_candidates`, `workday_list_custom_object_definitions`, `workday_list_custom_object_fields`, `workday_list_eligible_absence_types`, `workday_list_federal_tax_elections`, `workday_list_feedback`, `workday_list_holiday_calendars`, `workday_list_job_posting_questionnaires`, `workday_list_job_postings`, `workday_list_job_requisitions`, `workday_list_learning_content`, `workday_list_learning_courses_soap`, `workday_list_learning_enrollments_soap`, `workday_list_learning_programs_soap`, `workday_list_leaves_of_absence`, `workday_list_payment_messages`, `workday_list_payroll_results`, `workday_list_payslips`, `workday_list_people`, `workday_list_positions`, `workday_list_supervisory_organizations`, `workday_list_tax_elections`, `workday_list_time_off_details`, `workday_list_worker_checkins`, `workday_list_worker_explicit_skills`, `workday_list_worker_service_dates`, `workday_list_worker_skill_items`, `workday_list_worker_time_off_entries`, `workday_list_worker_time_off_plans`, `workday_list_workers`, `workday_list_year_end_documents`, `workday_submit_home_contact_change`, `workday_submit_work_contact_change`, `workday_unpost_job`, `workday_update_home_address`, `workday_update_home_email_address`, `workday_update_home_phone_number`, `workday_update_interview`, `workday_update_learning_lesson_soap`, `workday_update_learning_program_soap`, `workday_update_time_off_request`, `workday_update_work_email_address`, `workday_update_work_phone_number`, `workday_upsert_candidate`, `workday_wql_query`, `workday_wql_query_post` `new-feature` `bug-fix` `description-fix` Added 30 actions - 28 employee-lifecycle actions across Benefits (elections, benefit change events, dependents), Payroll (payslips, payroll results, state/local and federal W-4 tax elections, EFW2 year-end filing data), Time Off (cancel, deny, rescind, and correct requests), Time Tracking (time clock events, reported time blocks), HR (legal/preferred name changes, personal information, flexible work arrangements), Talent (give and list feedback), Compensation (request compensation change), Staffing (organization assignment changes, terminations) and worker business-process event history, plus submit_home_contact_change and submit_work_contact_change, without which contact-information changes were staged but never applied. Also migrated Absence Management to v5 and Staffing to v8, and corrected the guidance agents rely on across time off, recruiting, learning, skills, WQL and the Person API - including that get_worker (person.id) is the only route into the get_people actions, that time off and payment messages return oldest-first, and that job postings carry no requisition link. `workday_cancel_time_off_or_leave_request`, `workday_create_benefit_change_event`, `workday_create_compensation_change`, `workday_create_dependent`, `workday_create_feedback`, `workday_create_flexible_work_arrangement`, `workday_create_legal_name_change`, `workday_create_org_assignment_change`, `workday_create_preferred_name_change`, `workday_create_termination`, `workday_create_time_clock_event`, `workday_deny_time_off_or_leave_request`, `workday_end_flexible_work_arrangement`, `workday_get_worker_event_history`, `workday_list_benefit_elections`, `workday_list_federal_tax_elections`, `workday_list_feedback`, `workday_list_payroll_results`, `workday_list_payslips`, `workday_list_tax_elections`, `workday_list_year_end_documents`, `workday_rescind_time_off_or_leave_request`, `workday_submit_weekly_time`, `workday_update_dependent`, `workday_update_federal_tax_election`, `workday_update_personal_information`, `workday_update_tax_election`, `workday_update_time_off_request` `workday_change_job`, `workday_create_home_contact_change`, `workday_create_work_contact_change`, `workday_create_worker_checkin`, `workday_create_worker_explicit_skill`, `workday_create_worker_skill_items`, `workday_get_absence_balance`, `workday_get_employee_employment_info`, `workday_get_references`, `workday_get_time_off_detail`, `workday_get_worker`, `workday_get_worker_skill_item`, `workday_list_absence_balances`, `workday_list_eligible_absence_types`, `workday_list_learning_content`, `workday_list_leaves_of_absence`, `workday_list_time_off_details`, `workday_list_worker_checkins`, `workday_list_worker_explicit_skills`, `workday_list_worker_service_dates`, `workday_list_worker_skill_items`, `workday_list_workers` `new-feature` `bug-fix` `description-fix` Added submit_home_contact_change and submit_work_contact_change so contact-information changes can actually be applied, and corrected the guidance agents rely on across time off, recruiting, learning, WQL, custom objects and the Person API - including that get_worker (person.id) is the only route into the get_people actions, that time off and payment messages return oldest-first, that job postings carry no requisition link, and how to filter requisitions by status. `workday_submit_home_contact_change`, `workday_submit_work_contact_change` `workday_create_employee`, `workday_create_home_contact_change`, `workday_create_prospect`, `workday_create_work_contact_change`, `workday_create_worker_explicit_skill`, `workday_create_worker_skill_items`, `workday_get_custom_object_field`, `workday_get_job_posting_sites`, `workday_get_people`, `workday_get_people_home_addresses`, `workday_get_people_home_emails`, `workday_get_people_home_phones`, `workday_get_people_legal_name`, `workday_get_people_personal_information`, `workday_get_people_preferred_name`, `workday_get_people_work_addresses`, `workday_get_people_work_emails`, `workday_get_people_work_phones`, `workday_get_references`, `workday_get_supervisory_organization`, `workday_get_time_off_detail`, `workday_get_worker`, `workday_list_background_checks`, `workday_list_candidates`, `workday_list_holiday_calendars`, `workday_list_job_posting_questionnaires`, `workday_list_job_postings`, `workday_list_job_requisitions`, `workday_list_learning_content`, `workday_list_learning_content_lessons`, `workday_list_learning_courses_soap`, `workday_list_learning_enrollments_soap`, `workday_list_leaves_of_absence`, `workday_list_payment_messages`, `workday_list_people`, `workday_list_positions`, `workday_list_skills_wql`, `workday_list_supervisory_organizations`, `workday_list_time_off_details`, `workday_list_worker_explicit_skills`, `workday_list_worker_skill_items`, `workday_list_workers`, `workday_update_home_address`, `workday_update_home_email_address`, `workday_update_home_phone_number`, `workday_update_work_address`, `workday_update_work_phone_number`, `workday_upsert_location`, `workday_wql_query`, `workday_wql_query_post` `bug-fix` `description-fix` Fixed list_workers (SOAP Get_Workers) so Response_Filter Page/Count pagination and Request_Criteria Organization_Reference/Include_Subordinate_Organizations/Exclude_Inactive_Workers filters are declared in the action schema and forwarded to the request, with guidance pointing broad or field-selective retrieval to wql_query. `workday_list_workers` `bug-fix` `description-fix` Fixed create_prospect sending an empty request body when neither email nor phone_number was provided (now rejected with a clear validation message), and clarified agent-facing guidance across change_job, list_people vs list_workers, time off worker IDs, job posting sites, organization types, and location usage IDs. `workday_approve_time_off_or_leave_request`, `workday_change_job`, `workday_create_home_contact_change`, `workday_create_job_posting`, `workday_create_leave_of_absence`, `workday_create_payment_election_enrollment`, `workday_create_position`, `workday_create_prospect`, `workday_create_time_off_request`, `workday_create_work_contact_change`, `workday_create_worker_checkin`, `workday_create_worker_explicit_skill`, `workday_create_worker_skill_items`, `workday_get_absence_balance`, `workday_get_data_source_fields`, `workday_get_people`, `workday_get_time_off_detail`, `workday_get_worker`, `workday_get_worker_skill_item`, `workday_get_worker_time_off_entry`, `workday_get_worker_time_off_plan`, `workday_list_absence_balances`, `workday_list_eligible_absence_types`, `workday_list_learning_enrollments_soap`, `workday_list_leaves_of_absence`, `workday_list_organization_types`, `workday_list_people`, `workday_list_positions`, `workday_list_time_off_details`, `workday_list_worker_checkins`, `workday_list_worker_explicit_skills`, `workday_list_worker_service_dates`, `workday_list_worker_skill_items`, `workday_list_worker_time_off_entries`, `workday_list_worker_time_off_plans`, `workday_list_workers`, `workday_update_interview`, `workday_update_job_requisition`, `workday_upsert_candidate`, `workday_upsert_location`, `workday_wql_query`, `workday_wql_query_post` `new-feature` Added put_worker_document and get_worker_documents actions to upload, update, and download documents (e.g. payslips, contracts) on a worker's record via the Staffing SOAP web service, plus an Include_Worker_Documents option on list_workers to enumerate a worker's documents. `workday_get_worker_documents`, `workday_put_worker_document` `workday_list_workers` `bug-fix` Standardized action category capitalization for more consistent portal filters. `workday_change_job` `description-fix` Documents the Change Job work space constraint - a location change on a worker who holds a work space also needs Work_Space_Reference. # Workday VNDLY Source: https://docs.stackone.com/connectors/vndly/index How to set up the Workday VNDLY connector, plus the actions that are available.
Workday VNDLY
Betav1.1.0
59 actions · 1 auth method
IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). VNDLY Program Services API uses per-user API tokens sent as \`Authorization: Token <api\_token>\`. Users generate their own... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/vndly/index.md for the full list. # Workday VNDLY Changelog Source: https://docs.stackone.com/connectors/vndly/changelog Release history for the Workday VNDLY connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Added Data Sync support for 16 list actions, so collections such as contractors, work orders, jobs and applicants can be kept in sync. Contractors and work orders sync incrementally on their modified-since filter; the other 14 refresh in full each run. # Workforce.com Source: https://docs.stackone.com/connectors/workforce/index How to set up the Workforce.com connector, plus the actions that are available.
Workforce.com
Betav0.2.0
78 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses a long-lived personal access token generated in Workforce.com. The token is scoped to a single organisation and inh... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/workforce/index.md for the full list. # Workforce.com Changelog Source: https://docs.stackone.com/connectors/workforce/changelog Release history for the Workforce.com connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to thirteen collection actions — users, inactive users, clocked-in users, teams, user pay fields, locations, organisations, devices, qualifications, shift details, active shifts, availability requests and current timesheets — so these collections can be kept in sync and searched without calling Workforce.com on every request. Users, inactive users, teams and user pay fields page through results automatically; the remaining collections are returned in full by a single request. Users, inactive users, clocked-in users, teams, locations, organisations, devices, availability requests and current timesheets sync incrementally using Workforce.com's updated-since filter; the rest sync by full refresh, because their endpoints offer no last-updated filter. `workforce_get_current_timesheets`, `workforce_list_active_shifts`, `workforce_list_availability_requests`, `workforce_list_clocked_in_users`, `workforce_list_departments`, `workforce_list_devices`, `workforce_list_inactive_users`, `workforce_list_locations`, `workforce_list_organisations`, `workforce_list_qualifications`, `workforce_list_shift_details`, `workforce_list_user_pay_fields`, `workforce_list_users` `new-actions` Initial Workforce.com connector covering core workforce management — users, schedules, rosters, timesheets, shifts, leave, availability, departments, locations, pay fields, devices, clock-ins and more. # Workiva Source: https://docs.stackone.com/connectors/workiva/index How to set up the Workiva connector, plus the actions that are available.
Workiva
Betav0.2.0
266 actions · 1 auth method
IAM Documents
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Uses OAuth 2.0 client credentials created for an API-enabled user in Workiva. Tokens expire after 10 minutes and are ref... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/workiva/index.md for the full list. # Workiva Changelog Source: https://docs.stackone.com/connectors/workiva/changelog Release history for the Workiva connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Data Sync support for eight workspace collections (activity actions, documents, files, trashed files, processes, spreadsheets, sustainability programs and tasks), so they can be harvested on a schedule via the Workiva $next cursor. All eight full refresh on every run, as the Workiva API exposes no standalone updated-since request parameter. Those eight actions now also return a top-level next field carrying the bare cursor extracted from the response's @nextLink URL, null on the last page. No change to any action's request behaviour or inputs. `workiva_get_activity_actions`, `workiva_get_documents`, `workiva_get_files`, `workiva_get_programs`, `workiva_get_spreadsheets`, `workiva_get_tasks`, `workiva_get_trashed_files`, `workiva_list_processes` `bug-fix` Standardized action category capitalization for more consistent portal filters. `workiva_assign_organization_user_roles`, `workiva_assign_user_to_organization`, `workiva_assign_workspace_membership_roles`, `workiva_batch_deletion_metric_values`, `workiva_batch_update_process`, `workiva_batch_upsertion_metric_values`, `workiva_copy_file`, `workiva_copy_section`, `workiva_copy_sheet`, `workiva_create_dimension`, `workiva_create_edits`, `workiva_create_file`, `workiva_create_matrix`, `workiva_create_metric`, `workiva_create_organization_user`, `workiva_create_process`, `workiva_create_program`, `workiva_create_sample`, `workiva_create_section`, `workiva_create_sheet`, `workiva_create_task`, `workiva_create_topic`, `workiva_create_value`, `workiva_create_workspace`, `workiva_create_workspace_group`, `workiva_create_workspace_membership`, `workiva_delete_dataset_by_sheet_id`, `workiva_delete_metric_by_id`, `workiva_delete_metric_value_by_id`, `workiva_delete_milestone_by_id`, `workiva_delete_organization_user_by_id`, `workiva_delete_section_by_id`, `workiva_delete_sheet_by_id`, `workiva_delete_task_by_id`, `workiva_delete_topic_by_id`, `workiva_delete_workspace_group_by_id`, `workiva_delete_workspace_membership_by_id`, `workiva_destination_link_source_conversion`, `workiva_document_export`, `workiva_document_filters_reapplication`, `workiva_document_links_destination_replacement`, `workiva_document_links_publication`, `workiva_document_permissions_modification`, `workiva_edit_bookmarks`, `workiva_edit_sections`, `workiva_export_file_by_id`, `workiva_file_permissions_modification`, `workiva_get_activity_action_by_id`, `workiva_get_activity_actions`, `workiva_get_activity_by_id`, `workiva_get_anchor_by_id`, `workiva_get_batch_upsertion_metric_values_results`, `workiva_get_bookmark`, `workiva_get_bookmark_collection`, `workiva_get_column_properties`, `workiva_get_copy_file_results`, `workiva_get_custom_schema`, `workiva_get_datasets`, `workiva_get_destination_link_by_id`, `workiva_get_destination_link_source_conversion_results`, `workiva_get_dimension_by_id`, `workiva_get_dimensions`, `workiva_get_document_by_id`, `workiva_get_document_milestones`, `workiva_get_document_permissions`, `workiva_get_document_table_collection`, `workiva_get_documents`, `workiva_get_drawing_anchor_by_id`, `workiva_get_drawing_anchor_extensions`, `workiva_get_drawing_anchors`, `workiva_get_drawing_elements_by_id`, `workiva_get_file_by_id`, `workiva_get_file_permissions`, `workiva_get_files`, `workiva_get_image_by_id`, `workiva_get_image_upload_creation_results`, `workiva_get_import_file_results`, `workiva_get_matrices`, `workiva_get_matrix_attachment_by_id`, `workiva_get_matrix_attachments`, `workiva_get_matrix_by_id`, `workiva_get_metric_by_id`, `workiva_get_metric_value_by_id`, `workiva_get_metrics`, `workiva_get_milestone_by_id`, `workiva_get_milestone_creation_results`, `workiva_get_operation_by_id`, `workiva_get_org_report_users`, `workiva_get_organization_activities`, `workiva_get_organization_by_id`, `workiva_get_organization_roles`, `workiva_get_organization_solutions`, `workiva_get_organization_user_by_id`, `workiva_get_organization_user_role_list`, `workiva_get_organization_users`, `workiva_get_organization_workspace_activities`, `workiva_get_organization_workspace_membership_roles`, `workiva_get_organization_workspace_roles`, `workiva_get_organizations`, `workiva_get_patch_document_results`, `workiva_get_patch_presentation_results`, `workiva_get_patch_section_results`, `workiva_get_patch_sheet_results`, `workiva_get_patch_slide_layout_results`, `workiva_get_patch_slide_results`, `workiva_get_patch_spreadsheet_results`, `workiva_get_patch_table_properties_results`, `workiva_get_permission_by_id`, `workiva_get_permissions`, `workiva_get_presentation_by_id`, `workiva_get_presentation_milestones`, `workiva_get_presentation_permissions`, `workiva_get_presentation_table_collection`, `workiva_get_process`, `workiva_get_process_run`, `workiva_get_program_by_id`, `workiva_get_program_permissions`, `workiva_get_programs`, `workiva_get_range_link_by_id`, `workiva_get_range_link_destinations`, `workiva_get_range_link_edit_results`, `workiva_get_range_links`, `workiva_get_record_by_id`, `workiva_get_records`, `workiva_get_rich_text_anchor_by_id`, `workiva_get_rich_text_anchor_creation_results`, `workiva_get_rich_text_anchor_extensions`, `workiva_get_rich_text_anchors`, `workiva_get_rich_text_batch_edit_results`, `workiva_get_rich_text_duplication_edit_results`, `workiva_get_rich_text_links_batch_edit_results`, `workiva_get_rich_text_paragraphs`, `workiva_get_row_properties`, `workiva_get_sample_attachment_by_id`, `workiva_get_sample_attachments`, `workiva_get_sample_by_id`, `workiva_get_samples`, `workiva_get_section_by_id`, `workiva_get_section_permissions`, `workiva_get_sections`, `workiva_get_sheet_by_id`, `workiva_get_sheet_data`, `workiva_get_sheet_permissions`, `workiva_get_sheets`, `workiva_get_slide_by_id`, `workiva_get_slide_layout_by_id`, `workiva_get_slide_layouts`, `workiva_get_slide_permissions`, `workiva_get_slides`, `workiva_get_spreadsheet_by_id`, `workiva_get_spreadsheet_milestones`, `workiva_get_spreadsheet_permissions`, `workiva_get_spreadsheets`, `workiva_get_style_guide_by_id`, `workiva_get_table_anchor_by_id`, `workiva_get_table_anchor_creation_results`, `workiva_get_table_anchor_extensions`, `workiva_get_table_anchors`, `workiva_get_table_cell_edit_results`, `workiva_get_table_cells`, `workiva_get_table_edit_results`, `workiva_get_table_links_edit_results`, `workiva_get_table_properties`, `workiva_get_table_reapply_filter_results`, `workiva_get_task_by_id`, `workiva_get_tasks`, `workiva_get_test_form_by_id`, `workiva_get_test_forms`, `workiva_get_test_phase_attachment_by_id`, `workiva_get_test_phase_attachments`, `workiva_get_test_phase_by_id`, `workiva_get_test_phases`, `workiva_get_topic_by_id`, `workiva_get_topics`, `workiva_get_trashed_files`, `workiva_get_type_by_id`, `workiva_get_types`, `workiva_get_values`, `workiva_get_values_by_range`, `workiva_get_workspace_by_id`, `workiva_get_workspace_group_by_id`, `workiva_get_workspace_group_members`, `workiva_get_workspace_groups`, `workiva_get_workspace_membership_by_id`, `workiva_get_workspace_memberships`, `workiva_get_workspace_solutions`, `workiva_get_workspace_solutions_by_id`, `workiva_get_workspaces`, `workiva_graph_report_export`, `workiva_image_upload`, `workiva_import_file`, `workiva_list_processes`, `workiva_matrix_attachment_download_by_id`, `workiva_matrix_attachment_export_by_id`, `workiva_matrix_attachment_upload`, `workiva_milestone_creation`, `workiva_modify_workspace_group_members`, `workiva_partially_update_custom_schema`, `workiva_partially_update_dimension_by_id`, `workiva_partially_update_document_by_id`, `workiva_partially_update_file_by_id`, `workiva_partially_update_metric_by_id`, `workiva_partially_update_metric_value_by_id`, `workiva_partially_update_milestone_by_id`, `workiva_partially_update_organization_by_id`, `workiva_partially_update_organization_user_by_id`, `workiva_partially_update_presentation_by_id`, `workiva_partially_update_process_by_id`, `workiva_partially_update_program_by_id`, `workiva_partially_update_sample_by_id`, `workiva_partially_update_section_by_id`, `workiva_partially_update_sheet_by_id`, `workiva_partially_update_slide_by_id`, `workiva_partially_update_slide_layout_by_id`, `workiva_partially_update_spreadsheet_by_id`, `workiva_partially_update_table_properties`, `workiva_partially_update_task_by_id`, `workiva_partially_update_topic_by_id`, `workiva_partially_update_workspace_by_id`, `workiva_partially_update_workspace_group_by_id`, `workiva_presentation_export`, `workiva_presentation_filters_reapplication`, `workiva_presentation_links_destination_replacement`, `workiva_presentation_links_publication`, `workiva_presentation_permissions_modification`, `workiva_program_permissions_modification`, `workiva_restore_file_by_id`, `workiva_revoke_organization_user_roles`, `workiva_revoke_workspace_membership_roles`, `workiva_rich_text_anchor_creation`, `workiva_rich_text_batch_edit`, `workiva_rich_text_duplication_edit`, `workiva_rich_text_links_batch_edit`, `workiva_run_process`, `workiva_sample_attachment_download_by_id`, `workiva_sample_attachment_export_by_id`, `workiva_sample_attachment_upload`, `workiva_sample_insertion`, `workiva_sample_update`, `workiva_section_permissions_modification`, `workiva_sheet_permissions_modification`, `workiva_slide_permissions_modification`, `workiva_spreadsheet_export`, `workiva_spreadsheet_filters_reapplication`, `workiva_spreadsheet_links_destination_replacement`, `workiva_spreadsheet_links_publication`, `workiva_spreadsheet_permissions_modification`, `workiva_style_guide_export`, `workiva_style_guide_import`, `workiva_submit_task_action`, `workiva_table_anchor_creation`, `workiva_table_cells_batch_edit`, `workiva_table_edit`, `workiva_table_filters_reapplication`, `workiva_table_links_batch_edit`, `workiva_table_range_links_edit`, `workiva_test_form_export`, `workiva_test_phase_attachment_download_by_id`, `workiva_test_phase_attachment_export_by_id`, `workiva_test_phase_attachment_upload`, `workiva_trash_file_by_id`, `workiva_update_sheet`, `workiva_update_values_by_range`, `workiva_upsert_datasets`, `workiva_validate_process`, `workiva_workspace_membership_creation_with_options` `new-connector` Initial Workiva connector with 266 actions across 17 resources (documents, spreadsheets, presentations, content, files, tasks, processes, milestones, sustainability programs, test forms, graph, activities, permissions, custom fields, reports, operations, and organization admin) on the Workiva Platform API 2026-01-01. # WorkOS Source: https://docs.stackone.com/connectors/workos/index How to set up the WorkOS connector, plus the actions that are available.
WorkOS
Betav0.1.0
234 actions · 1 auth method
IAM AI Security
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). No app registration required. The secret key is bound to a single WorkOS environment, so Staging and Production each nee... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/workos/index.md for the full list. # WorkOS Changelog Source: https://docs.stackone.com/connectors/workos/changelog Release history for the WorkOS connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` Initial WorkOS connector covering AuthKit users, organizations and memberships, invitations, SSO connections, Directory Sync (SCIM), audit logs and the events feed. # Wrangle Source: https://docs.stackone.com/connectors/wrangle/index How to set up the Wrangle connector, plus the actions and events that are available.
Wrangle
v2.1.1
11 actions · 3 events · 2 auth methods
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticates the connecting user with a Slack OAuth 2.0 sign-in. The Slack user ID and workspace ID are taken from Slac... Uses a static API token issued from the Wrangle web app under Integrations > Wrangle API. The token, Slack Workspace ID,... Optionally, configure receiving Events for Wrangle into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/wrangle/index.md for the full list. ## Events See https://docs.stackone.com/connectors/wrangle/index.md for the full list. # Wrangle Changelog Source: https://docs.stackone.com/connectors/wrangle/changelog Release history for the Wrangle connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `feature` Added native webhook events for ticket created and ticket updated. `feature` Added scheduled data sync for inboxes and workflows. `wrangle_list_inboxes`, `wrangle_list_workflows` `breaking` `bug-fix` Breaking — Update Inbox now rejects a request that leaves out userRoles, matching what the API has always enforced, so callers relying on an empty body must supply the roles object. Also documented several provider behaviours that were previously silent — creating a ticket fails outright when a form-field value names a field that does not exist on the inbox, whereas updating a ticket accepts the request and quietly discards that value; users set to NO_ACCESS disappear from an inbox's user roles; and a satisfaction score needs the survey setting switched on for the inbox. `wrangle_create_ticket`, `wrangle_delete_ticket`, `wrangle_get_inbox`, `wrangle_get_ticket`, `wrangle_get_workflow`, `wrangle_list_inboxes`, `wrangle_list_tickets`, `wrangle_list_workflows`, `wrangle_start_workflow`, `wrangle_update_inbox`, `wrangle_update_ticket` `guide` Corrected the Slack Sign-In connection guide to cover returning to the Slack API dashboard after choosing a workspace and the Slack consent screen when signing in to Wrangle, and renamed the authentication type to OAuth 2.0 (Slack Sign-In). `wrangle_create_ticket`, `wrangle_delete_ticket`, `wrangle_get_inbox`, `wrangle_get_ticket`, `wrangle_get_workflow`, `wrangle_list_inboxes`, `wrangle_list_tickets`, `wrangle_list_workflows`, `wrangle_start_workflow`, `wrangle_update_inbox`, `wrangle_update_ticket` `auth` `guide` Added a Slack Sign-In option that takes your Slack user and workspace from Slack itself instead of asking you to enter them. Added connection guides for both authentication types. # Wrike Source: https://docs.stackone.com/connectors/wrike/index How to set up the Wrike connector, plus the actions and events that are available.
Wrike
v1.2.0
48 actions · 43 events · 1 auth method
IAM Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Authenticate with your Wrike account using OAuth 2.0. You'll need to register an application in the Wrike App Console to... Optionally, configure receiving Events for Wrike into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/wrike/index.md for the full list. ## Events See https://docs.stackone.com/connectors/wrike/index.md for the full list. # Wrike Changelog Source: https://docs.stackone.com/connectors/wrike/changelog Release history for the Wrike connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added scheduled data sync to nine list actions: tasks, folders and projects, spaces, custom fields, contacts, groups, workflows, webhooks, and the account. These collections can now be kept in sync and read back without calling Wrike on every request. Tasks and groups page through Wrike's cursor, and the rest return their full collection in one call. All nine refresh in full, because Wrike's only updated-since filter takes a nested date range that scheduled sync cannot send. `wrike_get_folder_tree`, `wrike_get_spaces`, `wrike_list_contacts`, `wrike_list_custom_fields`, `wrike_list_tasks`, `wrike_list_webhooks`, `wrike_query_accounts`, `wrike_query_groups`, `wrike_query_workflows` `new-events` Added programmatic webhook support with 43 event types across tasks, folders, projects, comments, attachments, approvals, and timelogs with connection guide. # X (Twitter) Source: https://docs.stackone.com/connectors/x/index How to set up the X (Twitter) connector, plus the actions that are available.
X (Twitter)
Previewv2.0.0
60 actions · 2 auth methods
Marketing Messaging
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use for actions on behalf of a user (posting, liking, following). Requires user authorization. Use for read-only access to public data (search, lookups). No user authorization needed. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/x/index.md for the full list. # X (Twitter) Changelog Source: https://docs.stackone.com/connectors/x/changelog Release history for the X (Twitter) connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `auth` `bug-fix` `new-actions` `data-sync` `guide` `breaking` Action IDs now follow X's post terminology (for example create_tweet is now create_post, retweet is now repost_post, and send_dm_to_user is now create_dm_message_by_participant_id). Added media upload actions (single and chunked), plus search, timeline, and field-selection parameters across read actions. User-context actions are offered only on OAuth 2.0 connections, each action declares the exact scopes X requires, OAuth requests every scope by default, the setup guide shows which scopes each action needs, and 22 list actions support data sync (post timelines sync incrementally by creation time). create_post now rejects invalid combinations before calling X (only one of poll, media, quote, or DM link; poll duration required with a poll), and get_recent_post_counts drops the search_count_fields input that X rejects. # Xero Source: https://docs.stackone.com/connectors/xero/index How to set up the Xero connector, plus the actions and events that are available.
Xero
v1.3.0
77 actions · 12 events · 1 auth method
Accounting IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Login to your Xero account to connect your data. Optionally, configure receiving Events for Xero into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/xero/index.md for the full list. ## Events See https://docs.stackone.com/connectors/xero/index.md for the full list. # Xero Changelog Source: https://docs.stackone.com/connectors/xero/changelog Release history for the Xero connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Receive Xero webhooks when contacts, invoices, credit notes, prepayments and overpayments are created or updated. `bug-fix` Role and organization lookups now return a not-found error for an unknown id instead of a different record. `xero_unified_get_me`, `xero_unified_get_organization`, `xero_unified_get_role`, `xero_unified_get_user`, `xero_unified_list_organizations`, `xero_unified_list_roles`, `xero_unified_list_users` `data-sync` `bug-fix` Added data sync support to 18 list actions (accounts, contacts, invoices, payments, and more) with incremental sync via If-Modified-Since where supported. Fixed list_quotes returning an XML-shaped response instead of JSON. `xero_list_accounts`, `xero_list_bank_transactions`, `xero_list_branding_themes`, `xero_list_companies`, `xero_list_contacts`, `xero_list_credit_notes`, `xero_list_invoices`, `xero_list_items`, `xero_list_manual_journals`, `xero_list_payments`, `xero_list_purchase_orders`, `xero_list_quotes`, `xero_list_tax_rates`, `xero_list_tracking_categories`, `xero_list_users`, `xero_unified_list_organizations`, `xero_unified_list_roles`, `xero_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `xero_unified_get_me`, `xero_unified_get_organization`, `xero_unified_get_role`, `xero_unified_get_user`, `xero_unified_list_organizations`, `xero_unified_list_roles`, `xero_unified_list_users` `new-actions` Added unified IAM actions for users, roles, organizations, and credentials. # Xyleme Source: https://docs.stackone.com/connectors/xyleme/index How to set up the Xyleme connector, plus the actions that are available.
Xyleme
v1.1.0
79 actions · 1 auth method
LMS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Use your Xyleme account username and password to authenticate. The API will return a context token for subsequent reques... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/xyleme/index.md for the full list. # Xyleme Changelog Source: https://docs.stackone.com/connectors/xyleme/changelog Release history for the Xyleme connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added Data Sync support for users, groups, channels, classifications, custom attributes, documents, and document history collections. # YouTube Source: https://docs.stackone.com/connectors/youtube/index How to set up the YouTube connector, plus the actions and events that are available.
YouTube
v2.1.0
55 actions · 3 events · 1 auth method
Media
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires registering an OAuth app in Google Cloud Console with the YouTube Data API v3 and YouTube Analytics API enabled... Optionally, configure receiving Events for YouTube into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/youtube/index.md for the full list. ## Events See https://docs.stackone.com/connectors/youtube/index.md for the full list. # YouTube Changelog Source: https://docs.stackone.com/connectors/youtube/changelog Release history for the YouTube connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added webhook support for the Feed Changed event, fired when the connected channel uploads a video, edits a video's title or description, or deletes a video. `new-actions` `auth` `guide` `breaking` Added YouTube Analytics actions for channel, video and playlist performance reports and analytics groups. Requires the YouTube Analytics API and yt-analytics.readonly scope; existing accounts must reconnect. # Zelt Source: https://docs.stackone.com/connectors/zelt/index How to set up the Zelt connector, plus the actions that are available.
Zelt
v1.1.0
34 actions · 1 auth method
HRIS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Zelt uses OAuth 2.0 for secure API access through their Developer Hub Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zelt/index.md for the full list. # Zelt Changelog Source: https://docs.stackone.com/connectors/zelt/changelog Release history for the Zelt connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` Added periodic data sync for users, sites, departments, job positions, job levels, permission groups, document types, and absences to keep records continuously up to date. `zelt_list_absences`, `zelt_list_departments`, `zelt_list_document_types_for_company`, `zelt_list_job_levels`, `zelt_list_job_positions`, `zelt_list_permission_group_members`, `zelt_list_sites`, `zelt_list_users` Token refresh now sends the OAuth callback resolved for the connected account instead of a hardcoded URL, so redirect_uri always matches the URI used at authorization. # Zendesk Source: https://docs.stackone.com/connectors/zendesk/index How to set up the Zendesk connector, plus the actions and events that are available.
Zendesk
v2.3.0
72 actions · 109 events · 3 auth methods
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Best for single-account integrations and internal tools. Uses email + API token for basic authentication. Recommended for partners and apps serving multiple Zendesk customers. Single OAuth client works across all accounts. Best for single-account integrations needing OAuth. Provides tighter control over token handling and permissions. Optionally, configure receiving Events for Zendesk into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zendesk/index.md for the full list. ## Events See https://docs.stackone.com/connectors/zendesk/index.md for the full list. # Zendesk Changelog Source: https://docs.stackone.com/connectors/zendesk/changelog Release history for the Zendesk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Zendesk native webhook mapping `guide-changes` Clearer connection guides: the setup steps are now separate from the credentials you enter in StackOne, and the API Token and Scopes fields show example values. `bug-fix` User and trigger sideload inputs now accept a list of values, delete actions return an explicit confirmation instead of an empty body, and trigger condition and group membership descriptions were corrected. The list_ticket_triggers sort_by and sort_order inputs, which never had an effect under the cursor pagination this action uses, were removed in favour of sort, which now also supports descending order. `zendesk_create_trigger`, `zendesk_create_user`, `zendesk_delete_brand`, `zendesk_delete_brand_logo`, `zendesk_delete_group`, `zendesk_delete_group_membership`, `zendesk_delete_organization`, `zendesk_delete_organization_membership`, `zendesk_delete_ticket`, `zendesk_delete_ticket_field`, `zendesk_delete_ticket_form`, `zendesk_delete_ticket_trigger`, `zendesk_list_organization_memberships`, `zendesk_list_ticket_triggers`, `zendesk_list_users`, `zendesk_search_ticket_triggers`, `zendesk_search_users`, `zendesk_show_self`, `zendesk_show_user`, `zendesk_update_ticket_trigger` `new-feature` Enabled Data Sync on 11 list actions covering tickets, users, organizations, groups, group and organization memberships, brands, tags, ticket forms, ticket fields and triggers. Synced collections can be searched and filtered without consuming Zendesk API quota. `zendesk_list_brands`, `zendesk_list_group_memberships`, `zendesk_list_groups`, `zendesk_list_organization_memberships`, `zendesk_list_organizations`, `zendesk_list_tags`, `zendesk_list_ticket_fields`, `zendesk_list_ticket_forms`, `zendesk_list_ticket_triggers`, `zendesk_list_tickets`, `zendesk_list_users` `guide-changes` Added screenshot-backed connection guides for the API Token, OAuth 2.0 (Global), and OAuth 2.0 (Account-level) authentication methods. `new-actions` `bug-fix` Renamed actions to match Zendesk's documented operation names, removed two duplicate actions, and added ticket field, ticket form, membership, count, and user management actions. # Zinc Source: https://docs.stackone.com/connectors/zinc/index How to set up the Zinc connector, plus the actions that are available.
Zinc
v1.1.0
9 actions · 1 auth method
Background Checks
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Bearer token authentication using a Zinc Partner API key. Each key is bound to a single Zinc customer account, so all re... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zinc/index.md for the full list. # Zinc Changelog Source: https://docs.stackone.com/connectors/zinc/changelog Release history for the Zinc connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` `new-feature` Enabled scheduled data sync on the packages list, so a customer's configured background-check packages can be kept in sync and read without calling Zinc on every request. It refreshes in full each run, because the packages endpoint exposes no updated-since filter. Request search is not included, because Zinc's search endpoint requires a candidate email or a request ID and cannot return the full collection. # Zoho Books Source: https://docs.stackone.com/connectors/zohobooks/index How to set up the Zoho Books connector, plus the actions and events that are available.
Zoho Books
v1.4.0
115 actions · 46 events · 1 auth method
Accounting IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Zoho Books account securely using OAuth 2.0. Access tokens expire after 1 hour and refresh automatically. R... Optionally, configure receiving Events for Zoho Books into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zohobooks/index.md for the full list. ## Events See https://docs.stackone.com/connectors/zohobooks/index.md for the full list. # Zoho Books Changelog Source: https://docs.stackone.com/connectors/zohobooks/changelog Release history for the Zoho Books connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Added 45 webhook events for invoices, quotes, sales orders, credit notes, recurring invoices, customer and vendor payments, bills, purchase orders, vendor credits, expenses, customers, vendors, projects and items (created, updated and deleted). StackOne creates the Zoho Books webhooks and workflow rules when an account connects and deletes them on disconnect. `bug-fix` Unified IAM roles now come from Zoho Books' own role list, including custom roles, and each user shows the role they actually hold. Role ids change from names like "admin" to Zoho Books role ids, so update any stored role ids. Looking up an unknown role now returns not found. Connecting with a wrong Organization ID now fails the connection test instead of connecting. `zohobooks_auth_test`, `zohobooks_unified_get_me`, `zohobooks_unified_get_organization`, `zohobooks_unified_get_role`, `zohobooks_unified_get_user`, `zohobooks_unified_list_organizations`, `zohobooks_unified_list_roles`, `zohobooks_unified_list_users` `data-sync` `bug-fix` Added Data Sync support to 25 list actions, with incremental (last modified) syncing on 17 of them. Added a last_modified_time filter to 15 list actions, and page/per_page pagination to taxes, currencies, users, vendor payments, and project tasks. Fixed List Unified Users failing with a 500 whenever results spanned more than one page. `zohobooks_list_bank_accounts`, `zohobooks_list_bank_transactions`, `zohobooks_list_bills`, `zohobooks_list_chart_of_accounts`, `zohobooks_list_contacts`, `zohobooks_list_credit_notes`, `zohobooks_list_currencies`, `zohobooks_list_customer_payments`, `zohobooks_list_debit_notes`, `zohobooks_list_estimates`, `zohobooks_list_expenses`, `zohobooks_list_invoices`, `zohobooks_list_items`, `zohobooks_list_journals`, `zohobooks_list_organizations`, `zohobooks_list_projects`, `zohobooks_list_purchase_orders`, `zohobooks_list_recurring_invoices`, `zohobooks_list_sales_orders`, `zohobooks_list_tasks`, `zohobooks_list_taxes`, `zohobooks_list_users`, `zohobooks_list_vendor_payments`, `zohobooks_unified_list_organizations`, `zohobooks_unified_list_roles`, `zohobooks_unified_list_users` `bug-fix` Standardized action category capitalization for more consistent portal filters. `zohobooks_auth_test`, `zohobooks_unified_get_me`, `zohobooks_unified_get_organization`, `zohobooks_unified_get_role`, `zohobooks_unified_get_user`, `zohobooks_unified_list_organizations`, `zohobooks_unified_list_roles`, `zohobooks_unified_list_users` `new-actions` Added unified IAM actions for managing users, organizations, roles, and credentials. # Zoho BugTracker Source: https://docs.stackone.com/connectors/zohobugtracker/index How to set up the Zoho BugTracker connector, plus the actions and events that are available.
Zoho BugTracker
v1.2.0
51 actions · 23 events · 1 auth method
Project Management
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Zoho BugTracker account securely using OAuth 2.0 authorization. Access tokens expire after 1 hour and refre... Optionally, configure receiving Events for Zoho BugTracker into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zohobugtracker/index.md for the full list. ## Events See https://docs.stackone.com/connectors/zohobugtracker/index.md for the full list. # Zoho BugTracker Changelog Source: https://docs.stackone.com/connectors/zohobugtracker/changelog Release history for the Zoho BugTracker connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added 22 webhook events for issues, projects, phases and users, with a setup guide for configuring Zoho BugTracker webhooks and rules. `data-sync` Added Data Sync support to the List Portals action, so portal records can be pulled into StackOne and kept up to date automatically. # Zoho CRM Source: https://docs.stackone.com/connectors/zohocrm/index How to set up the Zoho CRM connector, plus the actions and events that are available.
Zoho CRM
Previewv1.3.0
136 actions · 52 events · 1 auth method
CRM IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Zoho CRM account securely using OAuth 2.0 authorization. Access tokens expire after 1 hour and refresh auto... Optionally, configure receiving Events for Zoho CRM into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zohocrm/index.md for the full list. ## Events See https://docs.stackone.com/connectors/zohocrm/index.md for the full list. # Zoho CRM Changelog Source: https://docs.stackone.com/connectors/zohocrm/changelog Release history for the Zoho CRM connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `webhook` `new-actions` Added webhook support for 51 record events (created, updated, and deleted) across 17 CRM modules, with the Zoho notification channel created and removed automatically. `data-sync` `auth` `bug-fix` Enabled Data Sync for currencies, roles, profiles, territories, users, and the unified IAM users, groups, roles, and organizations. Corrected the OAuth scopes for List Currencies and List Territories and fixed List Territories pagination. `zohocrm_add_tags_to_record`, `zohocrm_add_tags_to_records_bulk`, `zohocrm_convert_lead`, `zohocrm_create_account`, `zohocrm_create_call`, `zohocrm_create_campaign`, `zohocrm_create_case`, `zohocrm_create_contact`, `zohocrm_create_deal`, `zohocrm_create_event`, `zohocrm_create_invoice`, `zohocrm_create_lead`, `zohocrm_create_note`, `zohocrm_create_price_book`, `zohocrm_create_product`, `zohocrm_create_purchase_order`, `zohocrm_create_quote`, `zohocrm_create_sales_order`, `zohocrm_create_solution`, `zohocrm_create_task`, `zohocrm_create_vendor`, `zohocrm_delete_account`, `zohocrm_delete_attachment`, `zohocrm_delete_call`, `zohocrm_delete_campaign`, `zohocrm_delete_case`, `zohocrm_delete_contact`, `zohocrm_delete_deal`, `zohocrm_delete_event`, `zohocrm_delete_invoice`, `zohocrm_delete_lead`, `zohocrm_delete_note`, `zohocrm_delete_price_book`, `zohocrm_delete_product`, `zohocrm_delete_purchase_order`, `zohocrm_delete_quote`, `zohocrm_delete_records_bulk`, `zohocrm_delete_sales_order`, `zohocrm_delete_solution`, `zohocrm_delete_tag`, `zohocrm_delete_task`, `zohocrm_delete_vendor`, `zohocrm_download_attachment`, `zohocrm_get_account`, `zohocrm_get_blueprint`, `zohocrm_get_call`, `zohocrm_get_campaign`, `zohocrm_get_case`, `zohocrm_get_contact`, `zohocrm_get_custom_view`, `zohocrm_get_deal`, `zohocrm_get_deleted_records`, `zohocrm_get_event`, `zohocrm_get_fields`, `zohocrm_get_invoice`, `zohocrm_get_lead`, `zohocrm_get_module`, `zohocrm_get_modules`, `zohocrm_get_organization_info`, `zohocrm_get_price_book`, `zohocrm_get_product`, `zohocrm_get_profile`, `zohocrm_get_purchase_order`, `zohocrm_get_quote`, `zohocrm_get_record_count`, `zohocrm_get_record_tags`, `zohocrm_get_role`, `zohocrm_get_sales_order`, `zohocrm_get_solution`, `zohocrm_get_task`, `zohocrm_get_user`, `zohocrm_get_users`, `zohocrm_get_vendor`, `zohocrm_list_accounts`, `zohocrm_list_attachments`, `zohocrm_list_calls`, `zohocrm_list_campaigns`, `zohocrm_list_cases`, `zohocrm_list_contacts`, `zohocrm_list_currencies`, `zohocrm_list_custom_views`, `zohocrm_list_deals`, `zohocrm_list_events`, `zohocrm_list_invoices`, `zohocrm_list_layouts`, `zohocrm_list_leads`, `zohocrm_list_notes`, `zohocrm_list_notes_by_ids`, `zohocrm_list_notifications`, `zohocrm_list_pricebooks`, `zohocrm_list_products`, `zohocrm_list_profiles`, `zohocrm_list_purchaseorders`, `zohocrm_list_quotes`, `zohocrm_list_roles`, `zohocrm_list_salesorders`, `zohocrm_list_solutions`, `zohocrm_list_tags`, `zohocrm_list_tasks`, `zohocrm_list_territories`, `zohocrm_list_vendors`, `zohocrm_mass_delete_records`, `zohocrm_mass_update_records`, `zohocrm_remove_tags_from_record`, `zohocrm_search_contacts`, `zohocrm_search_leads`, `zohocrm_unified_get_group`, `zohocrm_unified_get_me`, `zohocrm_unified_get_organization`, `zohocrm_unified_get_role`, `zohocrm_unified_get_user`, `zohocrm_unified_list_groups`, `zohocrm_unified_list_organizations`, `zohocrm_unified_list_roles`, `zohocrm_unified_list_users`, `zohocrm_update_account`, `zohocrm_update_call`, `zohocrm_update_campaign`, `zohocrm_update_case`, `zohocrm_update_contact`, `zohocrm_update_currency_exchange_rate`, `zohocrm_update_deal`, `zohocrm_update_event`, `zohocrm_update_invoice`, `zohocrm_update_lead`, `zohocrm_update_note`, `zohocrm_update_price_book`, `zohocrm_update_product`, `zohocrm_update_purchase_order`, `zohocrm_update_quote`, `zohocrm_update_sales_order`, `zohocrm_update_solution`, `zohocrm_update_task`, `zohocrm_update_vendor`, `zohocrm_upload_attachment`, `zohocrm_upsert_records` `new-actions` Added unified IAM actions for Zoho CRM organization users, hierarchical roles, user groups, the connected organization, and connection credentials. # Zoho Desk Source: https://docs.stackone.com/connectors/zoho-desk/index How to set up the Zoho Desk connector, plus the actions that are available.
Zoho Desk
v3.1.0
45 actions · 1 auth method
Customer Support Ticketing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). OAuth 2.0 authentication using Client ID and Client Secret from your Zoho API Console application. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zoho-desk/index.md for the full list. # Zoho Desk Changelog Source: https://docs.stackone.com/connectors/zoho-desk/changelog Release history for the Zoho Desk connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-actions` `data-sync` Added DataSync capability to 8 list actions for periodic data synchronisation. Added webhook CRUD actions. `zoho-desk_create_webhook`, `zoho-desk_delete_webhook`, `zoho-desk_get_webhook`, `zoho-desk_list_webhooks`, `zoho-desk_update_webhook` `zoho-desk_add_agent`, `zoho-desk_add_department`, `zoho-desk_create_account`, `zoho-desk_create_contact`, `zoho-desk_create_skill`, `zoho-desk_create_skill_type`, `zoho-desk_create_ticket`, `zoho-desk_delete_accounts`, `zoho-desk_delete_contacts`, `zoho-desk_delete_skill`, `zoho-desk_delete_skill_type`, `zoho-desk_disable_department`, `zoho-desk_enable_department`, `zoho-desk_get_account`, `zoho-desk_get_agent`, `zoho-desk_get_contact`, `zoho-desk_get_department`, `zoho-desk_get_organization`, `zoho-desk_get_skill`, `zoho-desk_get_skill_type`, `zoho-desk_get_ticket`, `zoho-desk_list_accounts`, `zoho-desk_list_agents`, `zoho-desk_list_all_associated_tickets`, `zoho-desk_list_contacts`, `zoho-desk_list_departments`, `zoho-desk_list_organizations`, `zoho-desk_list_skill_types`, `zoho-desk_list_skills`, `zoho-desk_list_tickets`, `zoho-desk_list_tickets_by_contact`, `zoho-desk_move_ticket`, `zoho-desk_move_tickets_to_trash`, `zoho-desk_update_account`, `zoho-desk_update_agent`, `zoho-desk_update_contact`, `zoho-desk_update_department`, `zoho-desk_update_skill`, `zoho-desk_update_skill_type`, `zoho-desk_update_ticket` `bug-fix` Fixed list_tickets viewId parameter type from string to number to prevent 422 errors when non-numeric values were passed. `zoho-desk_list_tickets` `bug-fix` Removed unsupported dueDate and closedTime query filters from list_tickets that caused 502 errors or were silently ignored by Zoho. `zoho-desk_list_tickets` `bug-fix` Fixed update actions returning empty responses. Removed unsupported fields causing errors on create ticket and list tickets. `zoho-desk_create_skill`, `zoho-desk_create_ticket`, `zoho-desk_list_tickets`, `zoho-desk_update_account`, `zoho-desk_update_agent`, `zoho-desk_update_contact`, `zoho-desk_update_department`, `zoho-desk_update_skill`, `zoho-desk_update_skill_type`, `zoho-desk_update_ticket` `breaking-change` `improved` `actions-updated` `bug-fix` Migrated requiredScopes to authRequirements. Added due date support to update_ticket. Added overdue filter to list_tickets. Improved action descriptions. `zoho-desk_add_agent`, `zoho-desk_add_department`, `zoho-desk_create_account`, `zoho-desk_create_contact`, `zoho-desk_create_skill`, `zoho-desk_create_skill_type`, `zoho-desk_create_ticket`, `zoho-desk_delete_accounts`, `zoho-desk_delete_contacts`, `zoho-desk_delete_skill`, `zoho-desk_delete_skill_type`, `zoho-desk_disable_department`, `zoho-desk_enable_department`, `zoho-desk_get_account`, `zoho-desk_get_agent`, `zoho-desk_get_contact`, `zoho-desk_get_department`, `zoho-desk_get_organization`, `zoho-desk_get_skill`, `zoho-desk_get_skill_type`, `zoho-desk_get_ticket`, `zoho-desk_list_accounts`, `zoho-desk_list_agents`, `zoho-desk_list_all_associated_tickets`, `zoho-desk_list_contacts`, `zoho-desk_list_departments`, `zoho-desk_list_organizations`, `zoho-desk_list_skill_types`, `zoho-desk_list_skills`, `zoho-desk_list_tickets`, `zoho-desk_list_tickets_by_contact`, `zoho-desk_move_ticket`, `zoho-desk_move_tickets_to_trash`, `zoho-desk_update_account`, `zoho-desk_update_agent`, `zoho-desk_update_contact`, `zoho-desk_update_department`, `zoho-desk_update_skill`, `zoho-desk_update_skill_type`, `zoho-desk_update_ticket` `improved` `actions-updated` Fixed response envelope for single-resource GET (get_*) and CREATE actions. Removed non-writable fields from update_agent, update_ticket, create_ticket, and add_agent. Improved field descriptions across all resources. # Zoho People Source: https://docs.stackone.com/connectors/zohopeople/index How to set up the Zoho People connector, plus the actions that are available.
Zoho People
v1.1.0
73 actions · 1 auth method
HRIS
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Zoho People account securely using OAuth 2.0 authorization. Access tokens expire after 1 hour and refresh a... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zohopeople/index.md for the full list. # Zoho People Changelog Source: https://docs.stackone.com/connectors/zohopeople/changelog Release history for the Zoho People connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `data-sync` Enabled data sync for clients, projects, forms, holidays, and case categories. List Timesheet Projects now returns every project in the organization by default instead of only the connected user's. `zohopeople_fetch_forms`, `zohopeople_get_all_holidays_v2`, `zohopeople_get_clients`, `zohopeople_get_projects`, `zohopeople_list_case_categories` `bug-fix` Clarified descriptions across attendance, forms, job schedules, and leave actions to disambiguate similar actions flagged in behavioural testing. # Zoho Recruit Source: https://docs.stackone.com/connectors/zohorecruit/index How to set up the Zoho Recruit connector, plus the actions that are available.
Zoho Recruit
v1.1.0
63 actions · 1 auth method
ATS IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Zoho Recruit account securely using OAuth 2.0 authorization. Access tokens expire after 1 hour and refresh... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zohorecruit/index.md for the full list. # Zoho Recruit Changelog Source: https://docs.stackone.com/connectors/zohorecruit/changelog Release history for the Zoho Recruit connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Enabled Data Sync for candidates, job openings, interviews, contacts, clients, departments, tasks, events, notes, users, modules, roles, and profiles, with incremental syncing on the record modules via the If-Modified-Since header. # Zoho Show Source: https://docs.stackone.com/connectors/zohoshow/index How to set up the Zoho Show connector, plus the actions that are available.
Zoho Show
v1.0.0
9 actions · 1 auth method
Documents Internal
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Zoho Office Integrator authenticates every Show API request with a single application-level API key ("apikey"). The key... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zohoshow/index.md for the full list. # Zoho Show Changelog Source: https://docs.stackone.com/connectors/zohoshow/changelog Release history for the Zoho Show connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `release` Promoted to GA. Version normalized to 1.0.0 in line with the GA versioning policy (GA connectors are versioned 1.0.0 or higher); no functional changes in this version. `bug-fix` Standardized action category capitalization for more consistent portal filters. `zohoshow_co_edit_presentation`, `zohoshow_convert_presentation`, `zohoshow_create_presentation`, `zohoshow_delete_presentation`, `zohoshow_delete_session`, `zohoshow_edit_presentation`, `zohoshow_get_session`, `zohoshow_preview_presentation` `bug-fix` `guide` Fixed presentation conversion to return the exact file as base64 (no corruption), made create_presentation callback settings optional, corrected the accepted save and convert formats, and updated the connection guide. `zohoshow_co_edit_presentation`, `zohoshow_convert_presentation`, `zohoshow_create_presentation`, `zohoshow_edit_presentation` `new-connector` Initial release of the Zoho Show connector — 8 actions across presentations and editor sessions, plus an internal connection-test action, built on the Zoho Office Integrator Show API. Application-level API key auth with multi-datacenter base URL and a connection guide. # Zoho Sprints Source: https://docs.stackone.com/connectors/zohosprints/index How to set up the Zoho Sprints connector, plus the actions and events that are available.
Zoho Sprints
v1.3.0
87 actions · 44 events · 1 auth method
Project Management IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Connect your Zoho Sprints account securely using OAuth 2.0. Access tokens expire after 1 hour and refresh automatically. Optionally, configure receiving Events for Zoho Sprints into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zohosprints/index.md for the full list. ## Events See https://docs.stackone.com/connectors/zohosprints/index.md for the full list. # Zoho Sprints Changelog Source: https://docs.stackone.com/connectors/zohosprints/changelog Release history for the Zoho Sprints connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `new-feature` `webhook` Added 43 webhook events for projects, sprints, sprint comments, work items, item comments, log hours, epics, releases, meetings, meeting comments, workspace and project users, commits and pull requests. StackOne creates one Zoho Sprints webhook per selected event when an account connects and deletes it on disconnect. The default scopes now include ZohoSprints.automation.READ. `zohosprints_add_custom_tag`, `zohosprints_add_item_comment`, `zohosprints_add_items_to_epic`, `zohosprints_add_items_to_release`, `zohosprints_add_log_hours`, `zohosprints_add_project_users`, `zohosprints_add_workspace_users`, `zohosprints_associate_item_tags`, `zohosprints_complete_sprint`, `zohosprints_create_backlog_item`, `zohosprints_create_epic`, `zohosprints_create_item`, `zohosprints_create_project`, `zohosprints_create_project_status`, `zohosprints_create_release`, `zohosprints_create_sprint`, `zohosprints_create_subitem`, `zohosprints_delete_backlog_item`, `zohosprints_delete_custom_tag`, `zohosprints_delete_epic`, `zohosprints_delete_item`, `zohosprints_delete_item_attachment`, `zohosprints_delete_item_comment`, `zohosprints_delete_log_hours`, `zohosprints_delete_project`, `zohosprints_delete_project_status`, `zohosprints_delete_project_user`, `zohosprints_delete_release`, `zohosprints_delete_sprint`, `zohosprints_delete_subitem`, `zohosprints_delete_workspace_user`, `zohosprints_get_active_sprint`, `zohosprints_get_all_projects`, `zohosprints_get_all_sprints`, `zohosprints_get_all_workspaces`, `zohosprints_get_backlog_item_details`, `zohosprints_get_epic_details`, `zohosprints_get_epic_items`, `zohosprints_get_epics`, `zohosprints_get_item_activity`, `zohosprints_get_item_attachments`, `zohosprints_get_item_comments`, `zohosprints_get_item_details`, `zohosprints_get_item_tags`, `zohosprints_get_item_types`, `zohosprints_get_items`, `zohosprints_get_log_hours`, `zohosprints_get_project_backlog`, `zohosprints_get_project_backlog_id`, `zohosprints_get_project_details`, `zohosprints_get_project_groups`, `zohosprints_get_project_priorities`, `zohosprints_get_project_status`, `zohosprints_get_project_users`, `zohosprints_get_release_details`, `zohosprints_get_release_stages`, `zohosprints_get_releases`, `zohosprints_get_sprint_details`, `zohosprints_get_subitems`, `zohosprints_get_tags`, `zohosprints_get_workspace_settings`, `zohosprints_get_workspace_users`, `zohosprints_move_backlog_items_to_sprint`, `zohosprints_move_items`, `zohosprints_move_items_to_backlog`, `zohosprints_start_sprint`, `zohosprints_unified_get_me`, `zohosprints_unified_get_organization`, `zohosprints_unified_get_role`, `zohosprints_unified_get_user`, `zohosprints_unified_list_organizations`, `zohosprints_unified_list_resource_types`, `zohosprints_unified_list_resource_users`, `zohosprints_unified_list_roles`, `zohosprints_unified_list_users`, `zohosprints_update_backlog_item`, `zohosprints_update_custom_tag`, `zohosprints_update_epic`, `zohosprints_update_item`, `zohosprints_update_item_comment`, `zohosprints_update_log_hours`, `zohosprints_update_project`, `zohosprints_update_project_status`, `zohosprints_update_release`, `zohosprints_update_sprint`, `zohosprints_update_subitem`, `zohosprints_update_user_role` `data-sync` Added DataSync support for workspaces, unified organizations, unified roles, and unified users. `zohosprints_get_all_workspaces`, `zohosprints_unified_list_organizations`, `zohosprints_unified_list_roles`, `zohosprints_unified_list_users` `new-actions` Added unified IAM support for users, roles, organizations, credentials, and resource users. `zohosprints_unified_get_me`, `zohosprints_unified_get_organization`, `zohosprints_unified_get_role`, `zohosprints_unified_get_user`, `zohosprints_unified_list_organizations`, `zohosprints_unified_list_resource_types`, `zohosprints_unified_list_resource_users`, `zohosprints_unified_list_roles`, `zohosprints_unified_list_users` `zohosprints_add_custom_tag`, `zohosprints_add_item_comment`, `zohosprints_add_items_to_epic`, `zohosprints_add_items_to_release`, `zohosprints_add_log_hours`, `zohosprints_add_project_users`, `zohosprints_add_workspace_users`, `zohosprints_associate_item_tags`, `zohosprints_complete_sprint`, `zohosprints_create_backlog_item`, `zohosprints_create_epic`, `zohosprints_create_item`, `zohosprints_create_project`, `zohosprints_create_project_status`, `zohosprints_create_release`, `zohosprints_create_sprint`, `zohosprints_create_subitem`, `zohosprints_delete_backlog_item`, `zohosprints_delete_custom_tag`, `zohosprints_delete_epic`, `zohosprints_delete_item`, `zohosprints_delete_item_attachment`, `zohosprints_delete_item_comment`, `zohosprints_delete_log_hours`, `zohosprints_delete_project`, `zohosprints_delete_project_status`, `zohosprints_delete_project_user`, `zohosprints_delete_release`, `zohosprints_delete_sprint`, `zohosprints_delete_subitem`, `zohosprints_delete_workspace_user`, `zohosprints_get_active_sprint`, `zohosprints_get_all_projects`, `zohosprints_get_all_sprints`, `zohosprints_get_all_workspaces`, `zohosprints_get_backlog_item_details`, `zohosprints_get_epic_details`, `zohosprints_get_epic_items`, `zohosprints_get_epics`, `zohosprints_get_item_activity`, `zohosprints_get_item_attachments`, `zohosprints_get_item_comments`, `zohosprints_get_item_details`, `zohosprints_get_item_tags`, `zohosprints_get_item_types`, `zohosprints_get_items`, `zohosprints_get_log_hours`, `zohosprints_get_project_backlog`, `zohosprints_get_project_backlog_id`, `zohosprints_get_project_details`, `zohosprints_get_project_groups`, `zohosprints_get_project_priorities`, `zohosprints_get_project_status`, `zohosprints_get_project_users`, `zohosprints_get_release_details`, `zohosprints_get_release_stages`, `zohosprints_get_releases`, `zohosprints_get_sprint_details`, `zohosprints_get_subitems`, `zohosprints_get_tags`, `zohosprints_get_workspace_settings`, `zohosprints_get_workspace_users`, `zohosprints_move_backlog_items_to_sprint`, `zohosprints_move_items`, `zohosprints_move_items_to_backlog`, `zohosprints_start_sprint`, `zohosprints_update_backlog_item`, `zohosprints_update_custom_tag`, `zohosprints_update_epic`, `zohosprints_update_item`, `zohosprints_update_item_comment`, `zohosprints_update_log_hours`, `zohosprints_update_project`, `zohosprints_update_project_status`, `zohosprints_update_release`, `zohosprints_update_sprint`, `zohosprints_update_subitem`, `zohosprints_update_user_role` `bug-fixes` Fixed delete_item_attachment failing with Zoho error 7500 by sending docResourceId as a query parameter, which the provider API requires despite its documentation showing a request body. # Zoom Source: https://docs.stackone.com/connectors/zoom/index How to set up the Zoom connector, plus the actions and events that are available.
Zoom
v1.4.1
66 actions · 39 events · 2 auth methods
Messaging IAM Meetings
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Login to your Zoom account to connect your data. Admin privileges may be required for certain scopes. Use Server-to-Server OAuth for machine-to-machine authentication without user interaction. Requires a Server-to-Server O... Optionally, configure receiving Events for Zoom into StackOne. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zoom/index.md for the full list. ## Events See https://docs.stackone.com/connectors/zoom/index.md for the full list. # Zoom Changelog Source: https://docs.stackone.com/connectors/zoom/changelog Release history for the Zoom connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `bug-fix` User lists now return pending invitees after active users, reading up to 2000 pending users (400 above that), and get user resolves their invitation ids. `zoom_unified_get_user`, `zoom_unified_list_users` `data-sync` Added scheduled data sync to the users, groups, roles, and organizations list actions (native and unified IAM) so these collections can be kept in sync and read back without calling Zoom on every request. Each refreshes in full on every run, since Zoom exposes no updated-since filter for these endpoints. `zoom_list_groups`, `zoom_list_users`, `zoom_unified_list_groups`, `zoom_unified_list_organizations`, `zoom_unified_list_roles`, `zoom_unified_list_users` `improvement` `bug-fix` Fixed the webhook setup handshake failing, corrected a misleading description on the user list action, and documented the payload each of the 39 webhook events delivers. `zoom_unified_get_group`, `zoom_unified_get_me`, `zoom_unified_get_user`, `zoom_unified_list_groups`, `zoom_unified_list_organizations`, `zoom_unified_list_resource_users`, `zoom_unified_list_roles`, `zoom_unified_list_users` `bug-fix` Fixed IAM unified actions — collapsed a duplicate field-mapping source on unified_get_me, removed composite-id encoding from the raw auth_test debug action, corrected resource_id composite-decode documentation, moved organization-lookup fetches off the auth-probe path, and cleaned up enum expressions and stale citations. `zoom_auth_test`, `zoom_unified_get_group`, `zoom_unified_get_me`, `zoom_unified_get_role`, `zoom_unified_get_user`, `zoom_unified_list_groups`, `zoom_unified_list_resource_users`, `zoom_unified_list_roles` `new-actions` `webhooks` Added native webhook events support — 38 event handlers across meetings, webinars, cloud recordings, and users, with endpoint URL validation and a webhook setup guide. `new-actions` Added unified IAM actions for users, groups, organizations, roles, resource users, and credentials. # ZoomInfo Source: https://docs.stackone.com/connectors/zoominfo/index How to set up the ZoomInfo connector, plus the actions that are available.
ZoomInfo
Betav1.2.0
76 actions · 2 auth methods
CRM Marketing IAM
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). ZoomInfo OAuth 2.0 with PKCE for user-context apps. Tokens are rotated on each refresh; access tokens expire in approxim... ZoomInfo OAuth 2.0 Client Credentials for server-to-server integrations. No user redirect — the app authenticates with i... Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zoominfo/index.md for the full list. # ZoomInfo Changelog Source: https://docs.stackone.com/connectors/zoominfo/changelog Release history for the ZoomInfo connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support to the Studio audiences, folders, agent teams, products, buyer personas, competitors, ideal customer profile and user list actions, so their records can be periodically pulled into StackOne and kept up to date, with paging handled automatically and incremental updates on folders. `zoominfo_list_agent_teams`, `zoominfo_list_audiences`, `zoominfo_list_customer_buyer_personas`, `zoominfo_list_customer_competitors`, `zoominfo_list_folders`, `zoominfo_list_ideal_customer_profiles`, `zoominfo_list_products_or_services`, `zoominfo_unified_list_users` `new-actions` Added identity and access actions for listing ZoomInfo users, with an optional SCIM API token and base URL. # Zuora Source: https://docs.stackone.com/connectors/zuora/index How to set up the Zuora connector, plus the actions and events that are available.
Zuora
Betav1.1.0
56 actions · 9 events · 1 auth method
Billing
## Getting Started Set up a new project or select an existing one. See [Organizations & Projects](/gateway/concepts/organizations-and-projects). Enable the connector and set up a Connector Profile in your project. See [Setup Connector Profile](/gateway/quickstart#setup-connector-profile). Requires an OAuth 2.0 client created in Zuora UI. Uses client credentials grant to obtain a bearer token. Link an account [from the dashboard](/connect/managing-connectors/linking-accounts#link-from-the-dashboard) (or via [StackOne Hub](/embed/account-linking/overview)). See the guide for the authentication type chosen in the Connector Profile: Connect an AI platform to the linked account's actions. See [AI Platforms](/connect/ai-platforms/overview). Other ways to call actions are listed in [Protocols & SDKs](/connect/protocols-and-sdks). ## Actions See https://docs.stackone.com/connectors/zuora/index.md for the full list. ## Events See https://docs.stackone.com/connectors/zuora/index.md for the full list. # Zuora Changelog Source: https://docs.stackone.com/connectors/zuora/changelog Release history for the Zuora connector. Each version lists what changed and which actions were affected. Back to the connector overview, authentication methods, and actions. `data-sync` Added data sync support for 10 list actions (credit memos, debit memos, invoices, invoice items, orders, payment methods, payments, products, refunds, subscriptions). # Connector Building Source: https://docs.stackone.com/connector-building/overview Build, customize, test, and publish your own connectors. Custom connector building is only available on certain plans. Each custom connector takes up one of your plan's slots. See [plans and pricing](https://www.stackone.com/pricing/). Need a connector that isn't in the catalog yet? Request it from StackOne, or build it yourself. ## When to build a custom connector Connect proprietary APIs or custom-built tools Add actions not covered by standard connectors Support vertical-specific SaaS not in our catalog Transform data to match your requirements ## How it works A connector is a YAML definition of how to interact with a provider's API. Once published, StackOne exposes it through every protocol automatically: REST endpoints at `api.stackone.com` for backend integrations Model Context Protocol for agents like Claude Code and Cursor TypeScript and Python SDKs built for LLM tool calling Write the connector once and it works across all of them, whether your users are building traditional apps, agents, or both. ## Two ways to add a connector ### StackOne Request StackOne connector build process: you request a connector, StackOne builds it through automated QA, AI optimization, and manual QA, then delivers it for you to use or fork StackOne builds and maintains the connector for you. Delivery defined for plans with SLAs. - **Fast turnaround:** typically days, not weeks (when API access is provided). - **Full support:** StackOne handles API mapping and authentication. - **QA pipeline:** AI-driven optimization and manual verification. - **Fork & customize:** optionally fork and edit actions after delivery. **[Request it from StackOne](https://www.stackone.com/demo)** ### Build it yourself AI-assisted connector development workflow: your prompt goes to your coding assistant, which uses StackOne's MCP and skills to research, build, and test a connector.yaml that you deploy through your own CI/CD Connectors are defined as code, so you build and publish them on your own schedule. - **AI-assisted:** use StackOne's MCP and skills to turn provider docs into YAML. - **Test locally:** run actions against a sandbox account. - **Full control:** version, test, and publish when you choose. - **Your environments:** publish through your existing CI/CD. **[Build it yourself](/connector-building/first-connector)** # First Connector Source: https://docs.stackone.com/connector-building/first-connector Build, test, and deploy your first StackOne connector. Custom connector building is only available on certain plans. Each custom connector takes up one of your plan's slots. See [plans and pricing](https://www.stackone.com/pricing/). A connector turns a third-party API into agent-ready actions, defined as YAML. This guide builds one from scratch with the [StackOne CLI](/connector-building/stackone-cli) and its agent, then pushes it to your project. To adapt a connector that already exists instead, see [Customizing Connectors](/connector-building/customizing-connectors). ## Before you start The CLI needs **Node.js 22.22 or later**. Nothing else is required. - Open **Terminal** (press `Cmd + Space`, type Terminal, press Enter). - Check what you have: `node --version`. - No Node.js 22.22+? Install it from [nodejs.org](https://nodejs.org/). - Open **Command Prompt** or **PowerShell** from the Start menu. - Check what you have: `node --version`. - No Node.js 22.22+? Install it from [nodejs.org](https://nodejs.org/). - Open your terminal application. - Check what you have: `node --version`. - Install Node.js 22.22+ from [nodejs.org](https://nodejs.org/) or [NodeSource](https://github.com/nodesource/distributions), since distribution packages are often older. Create an [API key](/embed/api-keys) with the `connectors:read`, `connectors:write`, and `credentials:read` scopes. Install the StackOne CLI globally via npm: ```bash npm install -g @stackone/cli ``` The `-g` flag installs the CLI globally so the `stackone` command is available in any directory. Verify the install. It prints the installed version: ```bash stackone --version ``` Make a directory to hold your connectors and move into it: ```bash mkdir custom-connectors && cd custom-connectors ``` From inside your working directory, set up the agent: ```bash stackone agent setup --local ``` This authenticates you, writes an `.mcp.json` so your AI assistant gets StackOne's tools, and installs the connector-building skills, slash commands, and subagents into `.claude/` along with a guide block in `CLAUDE.md`. The CLI owns everything under `.claude/`, so re-run `stackone agent sync` after each CLI update to pick up new skills and commands. Create a named profile so deployment commands like `stackone push` can authenticate without you pasting your API key each time: ```bash stackone init ``` You'll be prompted for a profile label and an API key. Paste the key you generated above. Profiles point at production unless you pass `--env staging`, so create one of each if you deploy to both, then reference them with `--profile [profile-label]`. Open [Claude Code](https://claude.com/claude-code) in your working directory: ```bash claude ``` It picks up the `.mcp.json` and the skills that `agent setup --local` just installed. Approve the StackOne MCP server when prompted, so the agent can reach StackOne's tools. Then run the onboarding command that `agent setup --local` installed, which walks you through the build rather than leaving you to describe it: ```text /connector-onboarding ``` It asks which provider you're connecting to and what kind of connector you want, then works through authentication, the endpoints worth exposing, and the actions themselves, confirming each part with you before moving on. This command needs CLI 1.47.0 or later. Earlier versions install the other connector skills but skip this one, so if it isn't listed, update the CLI and re-run `stackone agent sync`. Have the provider's API documentation to hand, along with the authentication type you plan to use. You can also skip it and describe what you want in plain language, letting the agent work out the endpoints, pagination, and field mappings from the provider's documentation: ```text I want to connect to Acme HR, our HR system. Their API docs are at https://developer.acme.com/reference and we authenticate with an API key. I want to be able to look up who works at the company, along with their job title and manager. ``` The agent reports the directory it wrote the connector to. Substitute that path for `[connector-dir]` below. `validate` checks the YAML against the connector schema and reports what's malformed or missing. `--watch` keeps it running so it rechecks every time you save: ```bash stackone validate [connector-dir] --watch ``` `run` executes a single action for real against the provider, so you see what it returns rather than what the YAML claims. Before you push, point it at local account and credential files: ```bash echo '{"environment": "production", "provider": "[provider]"}' > account.json echo '{"apiKey": "your_sandbox_api_key"}' > credentials.json ``` Add `credentials.json` to `.gitignore` so credentials never reach version control. `--debug` adds the raw request and response and each step's inputs and outputs: ```bash stackone run --connector [connector-dir]/[provider].connector.s1.yaml \ --account account.json --credentials credentials.json \ --action-id [action-id] --debug ``` Once the connector is pushed and an account is linked, swap both files for `--account-id [account-id] --profile [profile-label]`. That path needs a profile, because the CLI fetches the stored credentials from the API. Expect to go back and forth between building and testing. Tell the agent what you saw and rerun the action until it returns what you want. What `--debug` surfaces, and the common symptoms with their causes. `push` uploads the connector to your project's registry, which is what makes it available to link accounts against. `--profile` is the name you set with `stackone init`: ```bash stackone push [connector-dir] --profile [profile-label] ``` Connectors are code, so keeping them in version control gives you history and review as they change. It's also what publishing through [GitHub CI/CD](/connector-building/github-ci-cd) builds on. Covers authentication patterns, testing against an account, and the iterate loop. Every field, step function, and expression the schema supports. Pull an existing connector, change it, and push it back. Release new versions without breaking existing linked accounts. # Customizing Connectors Source: https://docs.stackone.com/connector-building/customizing-connectors Use the StackOne CLI to pull, edit, test, and push changes to an existing connector. Custom connector building is only available on certain plans. Each custom connector takes up one of your plan's slots. See [plans and pricing](https://www.stackone.com/pricing/). Adapt an existing connector — its actions, fields, and data mappings — by pulling it down with the [StackOne CLI](/connector-building/stackone-cli), editing the YAML, and pushing your changes back. ```bash npm install -g @stackone/cli ``` Set up a profile with your API key. Customizing needs an [API key](/embed/api-keys#scopes) with the `connectors:read` and `connectors:write` scopes. ```bash stackone init ``` Download the connector's files to your machine. ```bash stackone pull --connector [provider] --profile [profile-label] ``` Files save to `./connectors/[provider]/` by default. Append a version to pull a specific one, such as `--connector [provider]@1.0.0`, or pass `--output-path` to save elsewhere. Edit `[provider].connector.s1.yaml` to adjust authentication, add or change actions, and map provider fields to your own schema. Every field, step function, and expression the schema supports. Check syntax and structure. `--watch` re-runs on every save. ```bash stackone validate ./connectors/[provider]/ --watch ``` Run an action against a linked account to confirm your changes behave as expected. ```bash stackone run \ --connector [provider].connector.s1.yaml \ --account-id [account-id] \ --action-id [action-id] ``` Upload the updated connector back to StackOne. ```bash stackone push ./connectors/[provider]/ --profile [profile] ``` All commands, flags, and test-file formats. # Build Workflow Source: https://docs.stackone.com/connector-building/build-workflow Pull first, get authentication working, then build actions and iterate. Building a connector is a loop, and the order matters: every action you write depends on authentication already working. Validate each stage before moving to the next. ```mermaid flowchart LR A[Pull existing or create] --> B[Build authentication] B --> C[Connect an account] C --> D[Build actions] D --> E[Test and debug] E --> D E --> F[Publish] style A fill:#ecfdf5,stroke:#10b981,color:#065f46 style B fill:#ecfdf5,stroke:#10b981,color:#065f46 style C fill:#ecfdf5,stroke:#10b981,color:#065f46 style D fill:#dbeafe,stroke:#3b82f6,color:#1e40af style E fill:#dbeafe,stroke:#3b82f6,color:#1e40af style F fill:#fef9c3,stroke:#eab308,color:#854d0e ``` This assumes you've already got the [CLI installed and authenticated](/connector-building/first-connector). ## Pull existing or create Always check whether a connector already exists before writing one, since starting from the registry gives you a working foundation. Files save to `./connectors/[provider]/` by default: ```bash stackone pull --connector [provider] --profile [profile-label] ls connectors/[provider]/ ``` If nothing exists to pull, the agent writes the files for you, laid out as described in [File Structure](/connector-yaml-reference/file-structure). ## Build authentication Don't move on until authentication works. Everything else depends on it. Configure authentication in the main connector file. The common patterns: ```yaml authentication: - custom: type: custom label: API Key authorization: type: bearer token: $.credentials.apiKey configFields: - key: apiKey label: API Key type: password required: true secret: true testActionsIds: - list_users # simple action to test authentication ``` ```yaml authentication: - custom: type: custom label: API Key authorization: type: none customHeaders: X-API-Key: $.credentials.apiKey configFields: - key: apiKey label: API Key type: password required: true secret: true ``` ```yaml authentication: - custom: type: custom label: Basic Auth authorization: type: basic username: $.credentials.username password: $.credentials.password configFields: - key: username label: Username type: text required: true - key: password label: Password type: password required: true secret: true ``` Add one simple action — a `list_users` or equivalent — and use it to prove authentication works before building anything else. ## Connect an account Most providers offer sandbox or developer accounts. Check the provider's developer portal to sign up and generate credentials, and note any rate limits or restrictions that apply to sandbox access. For local development, keep the account config and credentials in separate files: ```bash echo '{"environment": "production", "provider": "[provider]"}' > account.json echo '{"apiKey": "your_sandbox_api_key"}' > credentials.json ``` Add `credentials.json` to `.gitignore`. Keep sandbox credentials separate from production ones. Then run your test action against those files: ```bash stackone run \ --connector connectors/[provider]/[provider].connector.s1.yaml \ --account account.json \ --credentials credentials.json \ --action-id list_users \ --debug ``` Rather than local credential files, you can push the connector and link an account in the dashboard, then run against that account by ID: ```bash stackone push connectors/[provider]/ --profile [profile] # link the account in the dashboard, then: stackone run \ --connector connectors/[provider]/[provider].connector.s1.yaml \ --account-id [account-id] \ --action-id list_users ``` `[profile]` is the name you set with `stackone init`. A pushed connector appears in the dashboard alongside the StackOne ones, so linking an account against it is the same flow as any other connector: [create a connector profile](/gateway/quickstart#setup-connector-profile), then [link an account](/gateway/quickstart#link-account). Other linking methods are covered in [Linking Accounts](/connect/managing-connectors/linking-accounts). ## Build actions and iterate With authentication proven, add your remaining actions to the resource partials. Each action is built from [step functions](/connector-yaml-reference/step-functions/overview). Then cycle: validate the syntax, run the action with `--debug`, fix, repeat. If the actions should return a normalized shape rather than the provider's own, see [Defined Output Schemas](/connector-building/defined-output-schemas). ```bash stackone validate connectors/[provider]/ --watch ``` Running `validate` with `--watch` keeps checking as you edit, so you catch schema mistakes without rerunning by hand. The [Playground](/embed/call-actions/troubleshooting/playground) also runs your connector's actions in natural language, which is handy for a quick check without the CLI. ## Debugging Add `--debug` to any `stackone run` to surface: - The raw HTTP request sent to the provider: URL, method, headers, body - The full response body, before any mapping is applied - The inputs and outputs of each step - The resolved values of any JSONPath or JEXL expressions When mapping produces something unexpected, work backwards from the raw response: Temporarily return the unmapped data so you can see what the provider actually sent: ```yaml result: data: $.steps.get_employees.output.data # raw, before map_fields ``` Run with `--debug` and inspect the real paths: ```bash stackone run --debug ... | jq '.steps.get_employees.output' ``` Start with a single field in `map_fields`, confirm it resolves, then add the rest. Inline fields in `map_fields` reference the field directly (`$.email`), not via the step (`$.get_employees.email`). | Symptom | Likely cause | Fix | |---------|--------------|-----| | 401 Unauthorized | Invalid credentials | Check the API key, regenerate if needed | | Empty data array | Wrong `dataKey` path | Use `--debug` to verify the actual response structure | | Null field values | Incorrect expression path | Check the nested paths match the real response | | Pagination returns the same data | Wrong `iterator.key` | Check the provider's docs for the expected cursor parameter name | | Enum not translated | `matchExpression` case mismatch | The provider might return `"ACTIVE"` rather than `"Active"` | ## Publish When the connector behaves, push it to your project's registry so linked accounts can use it: ```bash stackone push connectors/[provider]/ --profile [profile] ``` For team workflows, connectors are usually published through a Git pipeline rather than a direct push. See [GitHub CI/CD](/connector-building/github-ci-cd). Release new versions without breaking existing linked accounts. ### Other ways to test Once it's published, `stackone run` is no longer the only way in. Each of these exercises the deployed version against a linked account's real credentials, so they need a [connector profile](/gateway/quickstart#setup-connector-profile) and a [linked account](/gateway/quickstart#link-account) first: | Surface | Use it to | |---|---| | [Request Tester](/embed/call-actions/troubleshooting/request-tester) | Pick an action in the dashboard, fill in parameters, and inspect the response | | [`POST /actions/rpc`](/embed/call-actions/rpc-http) | Call the action the way your own backend will | | [Playground](/embed/call-actions/troubleshooting/playground) | Check an agent picks the right action from your descriptions | An action only shows up on these surfaces once it's enabled on the [connector profile](/secure/scoping-connectors). ## Next steps Map provider responses onto a schema of your own. The building blocks each action is made of. Full command reference for pull, validate, run, and push. Define the events your connector emits. # Defined Output Schemas Source: https://docs.stackone.com/connector-building/defined-output-schemas Map provider responses onto an output schema you define, so every provider in a category returns the same shape. A connector can pass the provider's response through as-is, or map it onto an output schema you define so every provider in a category returns the same shape. That mapping is where most of the work goes, and where most of the mistakes are. ## Mapping to your schema Two step functions do the work, both documented in full on [Step Functions](/connector-yaml-reference/step-functions/overview): | Step function | Role | |---|---| | [`map_fields`](/connector-yaml-reference/step-functions/map-fields) | Maps provider fields onto your `targetFieldKey` names, including enum translation via `enumMapper` | | [`typecast`](/connector-yaml-reference/step-functions/typecast) | Runs after `map_fields` to coerce the mapped values to their declared types | Use `version: "2"` for both `map_fields` and `typecast`. ## Give the agent your target schema Your target schema is the thing you'd otherwise restate for every provider you map, so write it down where the agent can read it: ````markdown --- name: Employee Sync Schema description: Target schema for employee data synchronization --- # Employee Sync Schema ## Target schema | Field | Type | Required | Notes | |-------|------|----------|-------| | id | string | yes | Unique identifier | | email | string | yes | Primary email | | first_name | string | yes | | | last_name | string | yes | | | status | enum | yes | Values: active, inactive, terminated | | department | string | no | | | hire_date | datetime_string | no | ISO 8601 format | ## Enum mappings ### status | Provider value | Schema value | |----------------|--------------| | Active, active, ACTIVE | active | | Inactive, inactive, INACTIVE | inactive | | Terminated, terminated, TERMINATED | terminated | | * (default) | unknown | ```` With that in place, the agent maps a new provider's employee response to your schema without being asked, including the enum normalization that is easy to get subtly wrong by hand. ## Checklist Before publishing a connector with a defined output schema, verify: - [ ] Target schema documented before building - [ ] All required fields identified - [ ] Field types specified (string, number, enum, datetime_string) - [ ] Enum values defined with mappings - [ ] `fieldConfigs` map all schema fields - [ ] `targetFieldKey` uses your schema names, not the provider's - [ ] Nested paths verified against the actual response - [ ] Enum mappings handle every provider value plus a default case - [ ] `cursor.enabled: true` for list actions - [ ] `dataKey` path verified with `--debug` - [ ] `nextKey` path verified with `--debug` - [ ] `result.next` returns the cursor for the next page - [ ] Tested against the first page, next page, last page, and empty results - [ ] `map_fields` step with `version: "2"` - [ ] `typecast` step with `version: "2"` - [ ] Correct `dataSource` references between steps ## Related The build and debug loop this fits into. Full reference for `map_fields`, `typecast`, and the rest. JSONPath and JEXL for the expressions in your mappings. # GraphQL Actions Source: https://docs.stackone.com/connector-building/graphql-actions Call a provider's GraphQL API from a connector using the request step function. For GraphQL APIs, use the `request` step function with `method: post` and the query in the body. Pass the query and its variables as separate `body` args. ```yaml steps: - stepId: graphql_query stepFunction: functionName: request parameters: url: /graphql method: post args: - name: query value: | query ListUsers($first: Int, $after: String) { users(first: $first, after: $after) { nodes { id name email } pageInfo { hasNextPage endCursor } } } in: body - name: variables value: first: '{{$.inputs.page_size ?? 50}}' after: '{{$.inputs.cursor ?? null}}' in: body ``` ## Error handling GraphQL returns `200` even for errors, so check the response's `errors` field rather than the status code: ```yaml - stepId: check_errors condition: '{{present(steps.graphql_query.output.data.errors)}}' stepFunction: # Handle the error case. ``` ## Best practices - Define variables for every dynamic value, and pass them in a separate `variables` object rather than inlining them in the query string. - Request only the fields you need, and use fragments for reusable field selections. - For pagination, use the provider's cursor fields, such as `pageInfo.hasNextPage` and `pageInfo.endCursor`. Keep the query static and supply values through `variables`: ```yaml args: - name: query value: 'query GetUser($id: ID!) { user(id: $id) { name } }' in: body - name: variables value: id: $.inputs.user_id in: body ``` ## Related The request step used to issue the GraphQL POST. JEXL defaults and conditions used in the query variables and error check. # Implementing Events Source: https://docs.stackone.com/connector-building/implementing-events Define the events your connector emits in its YAML, so StackOne can normalize and deliver them. Events let your connector turn a provider's webhooks into normalized StackOne events. As a connector author, you declare the events in the connector YAML; StackOne handles subscription, signature verification, and delivery to a [webhook](/connect/webhooks). This is the **producing** side. For how a consumer subscribes and receives events, see [Webhook Events](/connect/webhooks); for the concept, see [Events](/gateway/concepts/events). ## Where events live Event handlers go in a `{provider}.events.s1.partial.yaml` partial, referenced from the connector's `events` block rather than the top-level `actions`. See [File structure](/connector-yaml-reference/file-structure) for the layout. ## The events block The `events` block has four parts, from provisioning a receiver to handling a delivery: 1. `setup` runs the webhook receiver lifecycle with the provider (create, activate, and delete the receiver). 2. `externalAccountIdExtractor` resolves which linked account an incoming event belongs to. 3. `router` maps each incoming payload to an event action. 4. `actions[]` hold the `actionType: event` handlers that process the matched event. ## Anatomy of an event Each event is an action with `actionType: event`. It names the provider's native events, maps the incoming webhook payload to its `inputs`, and emits a normalized event with the `emit_event` step function: ```yaml # {provider}.events.s1.partial.yaml - actionId: webhook_employee_created categories: - hris actionType: event label: Employee Created description: Processes employee.created events fired when a new employee is added. providerEvents: - employee.created # the provider's native event name(s) inputs: # shape of the incoming webhook payload - name: type type: string in: body - name: triggeredAt type: string in: body - name: data type: object in: body properties: - name: employeeId type: string steps: - stepId: emit description: Emit the normalized event to the StackOne dispatcher. stepFunction: functionName: emit_event parameters: event: eventId: $.inputs.data.employeeId eventType: $.inputs.type eventDate: $.inputs.triggeredAt data: $.inputs.data result: statusCode: 200 # acknowledge receipt to the provider body: status: OK ``` | Field | Purpose | |-------|---------| | `actionType: event` | Marks the action as an inbound event handler, not an API call. | | `providerEvents` | The provider's native event names this handler accepts. | | `inputs` | The fields of the incoming webhook payload. | | `emit_event` step | Maps the payload to a normalized event (`eventId`, `eventType`, `eventDate`, `data`). | | `result` | The `200` acknowledgement returned to the provider. | ## Registering the receiver When the provider has a webhook API, provision the receiver programmatically in the `events.setup` block. StackOne runs its phases against the provider: `creation` (required) when events are enabled on a Connector Profile, `deletion` (required) when they are removed, and an optional `activation` step in between. Each phase is a list of ordinary `request` steps. StackOne threads two values through these steps: - `${inputs.callbackUrl}` — the StackOne receiver URL the provider should post events to. Map it into the create request. - `${inputs.remoteId}` — the id of the webhook the provider created, read from `creation.result`. `activation` and `deletion` reference it to target that webhook. ```yaml # {provider}.connector.s1.yaml events: setup: creation: steps: - stepId: create_webhook stepFunction: functionName: request parameters: url: /webhooks method: post args: - { name: url, value: '${inputs.callbackUrl}', in: body } result: $.steps.create_webhook.output.data.id # StackOne stores this as ${inputs.remoteId} deletion: steps: - stepId: delete_webhook stepFunction: functionName: request parameters: url: '/webhooks/${inputs.remoteId}' method: delete ``` If the provider has no webhook API, leave `setup` out and register manually with a [Native Webhook URL](#native-webhook-url). ## Native Webhook URL When a provider is configured manually, expose a Native Webhook URL on the connector profile by adding a field to your authentication config: ```yaml - key: nativeWebhookUrl label: Native Webhook URL value: "{{webhookEventsUrl(webhooks_url, orgId, projectSecureId, connectorProfileId, external_trigger_token)}}" description: Paste this into the provider's webhook settings. ``` The user copies this URL into the provider's own webhook configuration, guided by the steps you define in `events.guides.setup`. ## Related Every field of the events block, with examples. # Rendering Guides Source: https://docs.stackone.com/connector-building/rendering-guides Fetch a connector's guides from the API and render them in your own product. Guides live in the connector YAML under `support.guides`, so they ship and version with the connector instead of going stale in a separate docs site while the connector changes. Fetch them from the API to render in your own product. The schema: sections, steps, warnings, images, and scope filtering. ## Fetch the guides Guides come back from `GET /actions` when you ask for them: ```bash curl -X GET "https://api.stackone.com/actions?include=authentication_guides&filter[connectors]=[provider]" \ -H "Authorization: Basic $(echo -n 'YOUR_API_KEY:' | base64)" ``` | Parameter | Description | |-----------|-------------| | `include=authentication_guides` | Returns `support.guides` for each authentication method | | `include=event_guides` | Returns the event guides from `events.guides` | | `include=action_details` | Returns extended action metadata | | `filter[connectors]` | Restrict to one connector key, such as `filter[connectors]=bamboohr` | | `page_size` | Results per page | | `next` | Pagination cursor from the previous response | Full parameter and response reference. ## Response shape Guides are nested per authentication method, since each method needs different instructions: ```json { "data": [ { "key": "your_provider", "name": "Your Provider", "authentication": [ { "type": "custom", "label": "API Key", "key": "api_key", "configFields": [ { "key": "apiKey", "label": "API Key", "type": "password", "required": true } ], "support": { "guides": { "config": { "warning": "Admin access required to generate an API key.", "sections": [ { "title": "Generating an API Key", "content": "Generate an API key from your admin dashboard.", "steps": [ { "title": "Sign in and open API settings", "content": "Sign in to your Provider account.", "list": [ "Click **Settings** in the top navigation", "Select **API** from the sidebar", "Click **Create API Key**" ] } ] } ] } } } } ], "actions": [ { "id": "your_provider_list_employees", "label": "List Employees", "required_scopes": ["employees:read"] } ] } ], "next": null } ``` ## Render in your own UI The shape is small enough to type by hand. `title` and `content` are always present; everything else is optional: ```typescript interface GuideImage { src: string; alt: string; } interface GuideStep { title: string; content: string; list?: string[]; image?: GuideImage; /** Space-separated scope names, not an array */ applicableScopes?: string; /** Render badges for the actions these scopes unlock */ displayScopes?: boolean; } interface GuideSection { title: string; content: string; list?: string[]; image?: GuideImage; steps?: GuideStep[]; applicableScopes?: string; } interface AuthGuides { config?: { warning?: string; sections: GuideSection[] }; setup?: { warning?: string; sections: GuideSection[] }; } async function fetchConnectorGuides( connectorKey: string, apiKey: string, authMethodKey?: string, ): Promise { const authHeader = Buffer.from(`${apiKey}:`).toString("base64"); const response = await fetch( `https://api.stackone.com/actions?include=authentication_guides&filter[connectors]=${connectorKey}`, { headers: { Authorization: `Basic ${authHeader}` } }, ); const { data } = await response.json(); const connector = data?.find((c: any) => c.key === connectorKey); if (!connector) { throw new Error(`Connector "${connectorKey}" not found`); } const auth = authMethodKey ? connector.authentication?.find((a: any) => a.key === authMethodKey) : connector.authentication?.[0]; return auth?.support?.guides ?? {}; } ``` In the browser, swap `Buffer.from(...)` for `btoa(`${apiKey}:`)`. `content` and `list` items contain markdown: links, bold for UI labels, backticks for URLs and values. Render them through a markdown component such as `react-markdown` and sanitize the output. Building HTML strings by hand and injecting them with `dangerouslySetInnerHTML` puts provider-authored text straight into your DOM. ```tsx import ReactMarkdown from "react-markdown"; function Section({ section }: { section: GuideSection }) { return (

{section.title}

{section.content} {section.list && (
    {section.list.map((item) => (
  • {item}
  • ))}
)} {section.image && {section.image.alt}} {section.steps?.map((step) => (

{step.title}

{step.content}
))}
); } ```
`applicableScopes` marks a section or step as relevant only to certain scopes, so a read-only integration isn't told to grant write access. It's a **space-separated string**, so split it before comparing: ```typescript function appliesTo(scopes: string | undefined, selected: string[]): boolean { if (!scopes) { return true; } return scopes.split(/\s+/).some((scope) => selected.includes(scope)); } const visible = sections.filter((section) => appliesTo(section.applicableScopes, selected)); ``` A section with no `applicableScopes` always shows. Steps carry the same field, so filter them the same way.
## Related The guide, section, and step fields in full. # Connector Versioning Source: https://docs.stackone.com/connector-building/connector-versioning Connector versioning ensures your linked accounts aren't affected by breaking changes until you're ready to adopt them. Pin each connector profile to a version and upgrade on your own schedule. Connectors are versioned with semver (`major.minor.patch`). Each connector profile resolves to a specific connector version when linked accounts make requests. Because each connector profile pins independently, you can test a new version against a staging profile before rolling it out to production, and migrate different customer groups to a new connector version at their own pace. ## Version selection By default, a connector profile resolves to: 1. The latest **custom** version of the connector, if one exists in your project. 2. Otherwise, the latest **StackOne** version. Custom connectors are connectors you [build and publish yourself](/connector-building/overview). If you only use StackOne's built-in connectors then point 1 does not apply. Custom connectors always take precedence over StackOne connectors with the same key, including when version numbers match. Publishing a new StackOne version does not override a custom connector with the same key. ### Pinning a version When creating or editing a connector profile, you can override the default and pin the version to: - **Latest StackOne** - always resolves to the latest published StackOne version, ignoring custom versions. Use this when you rely on StackOne's managed updates. - **Latest custom** - always resolves to the latest published custom version. Use this when you maintain your own connector and want deploys to roll out automatically. - **A specific version** - pin to an exact version number (StackOne or custom). Use this in production when you need full control over when updates apply. When pinned to a "latest" option, existing linked accounts automatically pick up new versions as they are published. When pinned to a specific version, linked accounts stay on that version until the pin is changed. The accepted pin formats are: | Pin | Resolves to | Auto-updates | |-----|-------------|--------------| | `latest` | Newest version (custom if exists, else StackOne) | Yes | | `1.x.x` | Latest minor + patch within major version 1 | Yes, within major 1 | | `1.2.x` | Latest patch within 1.2.* | Yes, patch only | | `1.2.0` | Exactly 1.2.0, never changes | No | | *(no pin)* | Custom latest if exists, else StackOne latest | Yes | Note: npm-style caret (`^1.2.0`) and tilde (`~1.2`) are not accepted. In the dashboard, the pin is the profile's **Update strategy**: always use the latest, or pin to a major, minor, or exact version. Set it in the **Create Profile** panel, or later from **Edit profile** in the menu on the profile's card. Or set it via the API: ```bash curl -X PUT https://api.stackone.com/connector_profiles/{connector_profile_id}/pinned_version \ -H "Authorization: Basic " \ -H "Content-Type: application/json" \ -d '{"pinned_version": "1.x.x"}' ``` To revert to the default resolution (custom latest, then StackOne latest): ```bash curl -X DELETE https://api.stackone.com/connector_profiles/{connector_profile_id}/pinned_version \ -H "Authorization: Basic " ``` Pin production connector profiles to a major version wildcard, for example `1.x.x` rather than `latest`. A new major version can include authentication or scope changes that break existing linked accounts if they upgrade without warning. With `1.x.x`, you pick up bug fixes and new optional fields automatically while keeping control over breaking upgrades. ## Breaking changes and version updates This is how StackOne classifies changes when versioning its built-in connectors. Understanding these categories helps you interpret what a version bump means and whether it requires action on your end. Publishing a new connector version does not invalidate existing linked accounts. Accounts continue to work and automatically pick up the new version on the next request, provided the connector profile is on an auto-updating pin (`latest`, `1.x.x`, or `1.2.x`). Accounts pinned to a specific version remain on that version until the pin is manually updated. Any change that is not backwards compatible is released as a new **major** version. This includes, but is not limited to: - **Authentication changes** - switching authentication type, adding required scopes, or changing required credential fields. These require linked accounts to re-authenticate. - **Response shape changes** - renaming or removing fields, changing field types, or restructuring nested objects in an action's response. - **Request shape changes** - renaming or removing parameters, making optional parameters required, or changing accepted value types. - **Removed or renamed actions** - any action that callers may currently reference. - **Behavioral changes** - changes to pagination, filtering, error semantics, or default values that consumers may have relied on. | Version bump | Example change | Breaking for consumers | |--------------|----------------|------------------------| | Patch (`1.2.3 → 1.2.4`) | Bug fix, description update, internal refactor | No | | Minor (`1.2.3 → 1.3.0`) | New action, new optional parameter, new optional response field | No | | Major (`1.2.3 → 2.0.0`) | New authentication type or required scope, removed/renamed field, changed response shape, removed action | Yes | ## Versioning strategy When building custom connectors, you set your own versioning convention. The version number communicates what kind of migration work a change requires for anyone pinned to it. Auth-breaking changes — new OAuth flow, required scopes, or changed credential fields — require end users to reauthenticate. These almost always warrant a major version bump. The migration involves creating a new connector profile and prompting users through a new connect flow. A common approach: | Level | Use for | Who needs to act | |-------|---------|-----------------| | **Major** | Auth flow or scope changes | Your end users: they reauthenticate through the new flow | | **Minor** | New actions, new optional fields or parameters | Nobody: existing code keeps working | | **Patch** | Bug fixes, internal refactors | Nobody: existing code keeps working | The version level is your contract with yourself. Pick the convention that makes your migration work predictable. ## Checking available versions To see every published version for a connector profile and which one is currently active: ```bash curl https://api.stackone.com/connector_profiles/{connector_profile_id}/versions \ -H "Authorization: Basic " ``` ```json [ { "version": "1.0.0", "pinned": false, "builtin": true, "owner": "stackone" }, { "version": "1.2.0", "pinned": true, "builtin": true, "owner": "stackone" } ] ``` The `pinned: true` entry is the version currently serving requests for this connector profile. Note that the response shows the resolved exact version (`1.2.0`), not the pin format (`1.2.x`). The pin itself is set on the connector profile, not returned here. ## Migrating to a new version ### Non-breaking releases For releases your team has classified as non-breaking (patch fixes, new optional fields, additive changes), connector profiles pinned to `latest`, a major wildcard (`1.x.x`), or a minor wildcard (`1.2.x`) will pick up the new version automatically on the next request. No action required. If your connector profile is pinned to an exact version (e.g. `1.2.0`), it won't move until you update the pin manually: ```bash curl -X PUT https://api.stackone.com/connector_profiles/{connector_profile_id}/pinned_version \ -H "Authorization: Basic " \ -H "Content-Type: application/json" \ -d '{"pinned_version": "1.2.1"}' ``` ### Auth/permissions breaking changes When a connector introduces a new OAuth flow or required scope, existing accounts stay on their current connector profile until you explicitly migrate them. This is a coordinated rollout rather than a silent upgrade. The existing connector profile and all accounts on it are untouched. This new profile handles the updated authentication flow. Call [`GET /v2/connector_profiles`](/platform/api-reference/v2/connector-profiles/list-connector-profiles) and read the `id` of the profile you created. Pass that value as `connector_profile_id` when creating connect sessions. (`integration_id` is a deprecated alias for the same field in some payloads.) Pass `connector_profile_id` explicitly when creating connect sessions. This routes the session to the new profile. Alternatively, make the new connector profile the project default and omit `connector_profile_id`. See [Target a specific connector profile](/embed/connect-session#target-a-specific-connector-profile) for the request format. Send an email, in-app notification, or modal prompting users to reconnect through the Integration Hub. The connect flow uses the new session token, which routes to the new connector profile. You can identify which accounts still need migration by checking which remain associated with the old connector profile. When a user completes the new authentication flow, their linked account moves to the new connector profile. Subsequent requests resolve against the new major version. The recommended migration pattern is a staging connector profile pinned to the new version. Test your integration against it before updating the production profile. Each connector profile pins independently, so there's no coupling between environments. ## Immutable versioning Immutable versioning controls whether published versions can be overwritten. It is **enabled by default**. The setting can be found in **Project Settings → General → Danger Zone**. Immutable Versioning toggle enabled in the Danger Zone tab of Project Settings - **Enabled** (default) - Each version number is locked once published. Subsequent publishes must use a new version number. Use this to guarantee that linked accounts on a pinned version see exactly the connector that was originally published. - **Disabled** - Republishing the same version number is allowed when pushing with the [CLI's](/connector-building/stackone-cli) `--force` flag (`stackone push --force`). Without `--force`, the CLI still rejects overwrites. Linked accounts resolving to an overwritten version will pick up the new content on the next request. When immutable versioning is enabled, the `--force` flag has no effect - overwrites are rejected regardless. Enable immutable versioning in production projects to prevent accidental overwrites of a version that linked accounts depend on. Disable it in development projects where iterating on a version without bumping the number is convenient. # GitHub CI/CD Source: https://docs.stackone.com/connector-building/github-ci-cd Validate and publish connectors automatically with GitHub Actions. Publishing from a Git pipeline instead of your own machine means every change is validated on the pull request, and merging is what pushes the connector to a project. It also gives you one API key per environment rather than one on each developer's laptop. CI/CD workflow: Edit YAML → Validate → Push → GitHub Actions → StackOne Projects (dev/staging/prod) The pipeline is yours to shape: - **Single project**: push to one project from any branch - **Multi-environment**: route branches to separate projects, such as develop to dev and main to production - **Custom**: your own branch strategy and approval gates ## Repository structure Organize the repository however suits your team. What matters is that the connector directories keep the layout described in [File Structure](/connector-yaml-reference/file-structure), so `validate` and `push` can be pointed at a single parent directory: ``` custom-connectors/ ├── .github/ │ └── workflows/ │ └── deploy.yml # CI/CD pipeline ├── connectors/ │ └── {provider}/ │ ├── {provider}.connector.s1.yaml │ └── {provider}.{resource}.s1.partial.yaml └── README.md ``` ## Add your API key as a secret In the repository, go to **Settings → Secrets and variables → Actions** and add the API key for the project you're publishing to: | Secret | Description | |--------|-------------| | `STACKONE_API_KEY` | API key for your StackOne project | The key needs the `connectors:write` scope to push. See [API Keys](/embed/api-keys) for generating one. ## Create the workflow file Create `.github/workflows/deploy.yml`. Both examples validate on pull requests and publish only on a push to a release branch: ```yaml name: Validate and Deploy Connectors on: push: branches: [main] paths: - 'connectors/**' pull_request: branches: [main] paths: - 'connectors/**' jobs: validate-and-deploy: name: Validate and Deploy runs-on: ubuntu-latest steps: - uses: actions/checkout@v4 - name: Setup Node.js uses: actions/setup-node@v4 with: node-version: '20' - name: Install StackOne CLI run: npm install -g @stackone/cli - name: Validate connectors run: stackone validate connectors/ - name: Check agent skills are in sync run: stackone agent sync --check - name: Deploy if: github.event_name == 'push' env: STACKONE_API_KEY: ${{ secrets.STACKONE_API_KEY }} run: stackone push connectors/ --api-key $STACKONE_API_KEY ``` For separate dev, staging, and production projects, add one secret per project: | Secret | Description | |--------|-------------| | `STACKONE_API_KEY_DEV` | Development project | | `STACKONE_API_KEY_STAGING` | Staging project | | `STACKONE_API_KEY_PROD` | Production project | ```yaml name: Validate and Deploy Connectors on: push: branches: [develop, staging, main] paths: - 'connectors/**' pull_request: branches: [develop, staging, main] paths: - 'connectors/**' jobs: validate: name: Validate Connectors runs-on: ubuntu-latest steps: - uses: actions/checkout@v4 - uses: actions/setup-node@v4 with: node-version: '20' - run: npm install -g @stackone/cli - run: stackone validate connectors/ - run: stackone agent sync --check deploy-dev: needs: validate if: github.ref == 'refs/heads/develop' && github.event_name == 'push' runs-on: ubuntu-latest steps: - uses: actions/checkout@v4 - uses: actions/setup-node@v4 with: node-version: '20' - run: npm install -g @stackone/cli - run: stackone push connectors/ --api-key ${{ secrets.STACKONE_API_KEY_DEV }} deploy-staging: needs: validate if: github.ref == 'refs/heads/staging' && github.event_name == 'push' runs-on: ubuntu-latest steps: - uses: actions/checkout@v4 - uses: actions/setup-node@v4 with: node-version: '20' - run: npm install -g @stackone/cli - run: stackone push connectors/ --api-key ${{ secrets.STACKONE_API_KEY_STAGING }} deploy-prod: needs: validate if: github.ref == 'refs/heads/main' && github.event_name == 'push' runs-on: ubuntu-latest environment: production # Optional: require manual approval steps: - uses: actions/checkout@v4 - uses: actions/setup-node@v4 with: node-version: '20' - run: npm install -g @stackone/cli - run: stackone push connectors/ --api-key ${{ secrets.STACKONE_API_KEY_PROD }} ``` `stackone agent sync --check` compares the `.claude/skills/` and `CLAUDE.md` guide committed in the repository against the ones bundled with the installed CLI, and exits non-zero if they differ. It needs no credentials. Because the workflow installs the latest CLI, a new CLI release that ships updated skills will fail this step until someone runs `stackone agent sync` and commits the result. Pin the CLI version in the workflow if you'd rather choose when that happens. ## Test after deploying A published connector needs a linked account before you can call anything against it: Open your custom connector in the project's [Connectors](https://app.stackone.com/connectors) page and click **Add Profile**. Select the actions you want exposed, click **Continue**, fill in authentication, and click **Create Profile**. Connector profiles, authentication, and scoping. Create a linked account through the [Hub](/embed/account-linking/overview) or the API. Select the account in the [Playground](/embed/call-actions/troubleshooting/playground) and try the actions in natural language, or run one directly: ```bash stackone run \ --connector connectors/[provider]/[provider].connector.s1.yaml \ --account-id [account-id] \ --profile [profile-label] \ --action-id [action-id] ``` The profile's API key needs the `credentials:read` scope to use a linked account's stored credentials. Push updates as you refine the connector. Existing linked accounts are unaffected until you move them, which is covered in [Connector Versioning](/connector-building/connector-versioning). ## Common errors - Check YAML indentation, which must be 2 spaces rather than tabs - Partial files start with `-`, not `actions:` - Every `$ref` matches an actual file name, which matters on case-sensitive CI runners even when it works on macOS - Run `stackone validate connectors/` locally against the same parent directory the workflow uses - The secret name in the workflow matches the one in repository settings - The API key carries the `connectors:write` scope - The key belongs to the project you intended to publish to, not another environment - The file sits in `.github/workflows/` - Branch names in `on.push.branches` match your actual branches - The `paths` filter covers the files you changed. Editing only a workflow or README will not match `connectors/**` ## Next steps The build and debug loop that comes before publishing. Release new versions without breaking existing linked accounts. Full reference for validate, run, and push. # StackOne CLI Source: https://docs.stackone.com/connector-building/stackone-cli StackOne CLI commands for building, validating, testing, and deploying connectors The StackOne CLI (`@stackone/cli`) provides commands for building, validating, testing, and deploying custom connectors. Complete CLI documentation on npm ## Installation ```bash npm install -g @stackone/cli ``` --- ## Command Reference ### Agent Commands Set up the agent, and the MCP server that gives an AI coding assistant StackOne's tools. | Command | Description | |---------|-------------| | `stackone agent setup --local` | Authenticate, write `.mcp.json`, and install the connector-building skills into `.claude/` plus a guide block in `CLAUDE.md` | | `stackone agent setup --global` | Authenticate and register the MCP server in `~/.claude.json`. No skills or guide | | `stackone agent skills` | List the bundled skills | | `stackone agent sync` | Refresh this project's skills and guide | | `stackone agent cleanup` | Remove stored credentials and configuration | ```bash # In a connector repo: auth + MCP server + skills + CLAUDE.md guide stackone agent setup --local # Install into a directory other than the current one stackone agent setup --local --path ~/code/custom-connectors # Auth + MCP server only, for projects that aren't connector repos stackone agent setup --global # Remove all API keys and credentials stackone agent cleanup ``` The API key is stored in `~/.stackone/agent-config.json` either way. The MCP server entry goes to `~/.claude.json` for `--global`, or the project's `.mcp.json` for `--local`. Use `--local` in the repo where you build connectors, since it's the only mode that installs the skills and the guide. It authenticates you at the same time, so `--global` is not a prerequisite. Passing neither flag prompts for the mode. #### Skills `agent setup --local` installs a set of connector-building skills into `.claude/skills/`. List what you have, and the subset recommended for a mode: ```bash stackone agent skills stackone agent skills --mode build ``` After upgrading the CLI, refresh the copies in your project: ```bash stackone agent sync # Report drift and exit non-zero instead of writing, for CI stackone agent sync --check ``` --- ### Connector Development | Command | Description | |---------|-------------| | `stackone validate ` | Validate connector YAML syntax and structure | | `stackone run` | Execute a connector action locally for testing | ```bash # Validate with watch mode stackone validate ./my-connector/ --watch # Run an action with local credentials stackone run \ --connector my-connector.connector.s1.yaml \ --account account.json \ --credentials credentials.json \ --action-id list_employees \ --debug # Run with parameters stackone run \ --connector my-connector.connector.s1.yaml \ --account account.json \ --credentials credentials.json \ --action-id get_employee \ --params params.json # Run custom action code (for testing action definitions) stackone run \ --connector my-connector.connector.s1.yaml \ --account-id acme-corp-provider \ --action ./custom-action.yaml # Save output to file stackone run \ --connector my-connector.connector.s1.yaml \ --account-id acme-corp-provider \ --action-id list_employees \ --output-file results.json ``` **Test file formats:** ```json account.json { "environment": "production", "provider": "provider" } ``` ```json credentials.json (API Key) { "apiKey": "your_api_key" } ``` ```json credentials.json (OAuth2) { "accessToken": "token", "refreshToken": "refresh_token", "clientId": "client_id", "clientSecret": "client_secret" } ``` ```json params.json { "path": { "id": "emp_123" }, "queryParams": { "include": "manager" } } ``` **Params structure:** each top-level key corresponds to an input's `in:` location in the action's YAML. Put every value under the key that matches where the input is sent. | Key | Inputs it carries | |-----|-------------------| | `path` | `in: path`: URL path parameters | | `queryParams` | `in: query` | | `header` | `in: headers` (singular `header`) | | `body` | `in: body` | You can pass the same object inline instead of a file: ```bash stackone run \ --connector connectors/[provider]/[provider].connector.s1.yaml \ --account-id [account-id] \ --action-id get_employee \ --params '{"path": {"id": "emp_123"}, "queryParams": {"include": "manager"}}' ``` **Faster iteration:** Once your connector is pushed or an account is already linked, skip the credentials file and use `--account-id` instead: ```bash stackone run \ --connector my-connector.connector.s1.yaml \ --account-id acme-corp-provider \ --action-id list_employees ``` This uses stored credentials from the linked account, making it easier to iterate on action logic without managing local credential files. **Note:** Using `--account-id` requires an API key with `connectors:read` scope. ### Deployment Deployment commands require an API key with **Connectors** scopes. See [API Keys](/embed/api-keys) to generate one. | Command | Description | Required Scope | |---------|-------------|----------------| | `stackone push ` | Upload connector to StackOne registry | `connectors:write` | | `stackone pull` | Download connector files to local filesystem | `connectors:read` | | `stackone drop ` | Delete a connector version from registry | `connectors:write` | | `stackone get` | Retrieve connector configuration (YAML or JSON output) | `connectors:read` | ```bash # Push using saved profile stackone push ./my-connector/ --profile prod # Push with API key directly stackone push ./my-connector/ --api-key v1.eu1.xxxxx # Pull connector files (saves to ./connectors/my_provider/ by default) stackone pull --connector my_provider --profile prod # Pull a specific version to a different directory stackone pull --connector my_provider@1.0.0 --profile prod --output-path ./custom-connectors # Get connector config as YAML (default) stackone get --connector my_provider # Get connector config from a linked account stackone get --account-id acme-corp-provider --format json --output-file config.json ``` --- ### Configuration | Command | Description | |---------|-------------| | `stackone init` | Configure authentication profiles interactively | | `stackone version` | Show version with update check | | `stackone update` | Update CLI to latest version | ```bash # Interactive setup (prompts for profile name and API key) stackone init # Setup for different environments stackone init --env staging stackone init --env production # Check version and available updates stackone version # Update to latest version stackone update ``` --- ## Environment Variables | Variable | Description | |----------|-------------| | `STACKONE_AGENT_MCP_TOKEN` | MCP server access token (set by `agent setup`) | API keys are passed via `--api-key` flag or stored in your profile configuration, not as environment variables. --- ## Next Steps Build a connector from scratch with these commands Automated validation and publishing with GitHub Actions # Connector YAML Reference Source: https://docs.stackone.com/connector-yaml-reference/overview YAML Schema reference for connector configurations Custom connector building is only available on certain plans. Each custom connector takes up one of your plan's slots. See [plans and pricing](https://www.stackone.com/pricing/). StackOne connectors are defined in YAML. The same schema powers every pre-built connector, and you can use it to build your own. If you're new to connectors, start with [Build your first connector](/guides/connector-engine/building-first-connector) and [Connector structure](/connector-yaml-reference/file-structure). How a connector's files are organized, from the main file to resource partials. Every top-level connector property: info, baseUrl, authentication, actions, events, and more. The step functions you compose inside action and event setup steps. JSONPath, JEXL, and string interpolation used throughout the schema. # File Structure Source: https://docs.stackone.com/connector-yaml-reference/file-structure How to organize connector files using partial files and suggested naming conventions. Connectors are organized into a **main connector file** and, optionally, **partial files**. Partial files can be used to split large connectors up into more manageable chunks for maintenance and are consumed in the StackOne platform as if it were a single configuration file. ## Best practices For maintaining connectors for development, use the directory structure below: ``` connectors/{provider}/ ├── {provider}.connector.s1.yaml # Main connector file (authentication, metadata) ├── {provider}.{resourceA}.s1.partial.yaml # Partial file (actions grouped by resourceA) ├── {provider}.{resourceB}.s1.partial.yaml # Partial file (actions grouped by resourceB) └── {provider}.events.s1.partial.yaml # Partial file (event handlers - if available) ``` ### Main connector file The main connector file defines the top-level properties (see [YAML Schema](/connector-yaml-reference/yaml-schema/overview)): connector metadata, authentication, and an `actions` block (plus an `events` block for webhooks) that reference the partial files. Partial files are referenced in the main file by the filename without the `.s1.partial.yaml` extension. Parital files must be within the same folder as the main connector file. ```yaml # acme.connector.s1.yaml StackOne: 1.0.0 ... actions: - $ref: acme.employees # references acme.employees.s1.partial.yaml - $ref: acme.departments # references acme.departments.s1.partial.yaml events: setup: {...} router: {...} externalAccountIdExtractor: {...} actions: - $ref: acme.events # references acme.events.s1.partial.yaml ``` Add references in alphabetical order for readability. ### Partial files Each partial file is a group of actions, e.g. grouped per resource. ```yaml # acme.employees.s1.partial.yaml - actionId: list_employees ... - actionId: get_employee ... ``` ```yaml # acme.departments.s1.partial.yaml - actionId: list_departments ... - actionId: get_department ... ``` Event handlers are grouped the same way: ```yaml # acme.events.s1.partial.yaml - actionId: employee_created actionType: event ... - actionId: employee_updated actionType: event ... ``` ## Related Full YAML schema for building connectors with field tables and examples. # YAML Schema Source: https://docs.stackone.com/connector-yaml-reference/yaml-schema/overview Complete reference for all connector YAML properties with examples and impact analysis. ## Top-level structure ```yaml StackOne: 1.0.0 actions: [ ... ] authentication: [ ... ] baseUrl: 'https://api.provider.com' concurrency: { ... } documentation: { ... } events: { ... } forkedFrom: acme_hris info: { ... } mcp: { ... } rateLimit: { ... } releaseStage: ga resources: 'https://api.provider.com/docs' scopeDefinitions: { ... } ```
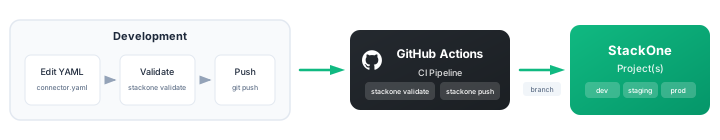
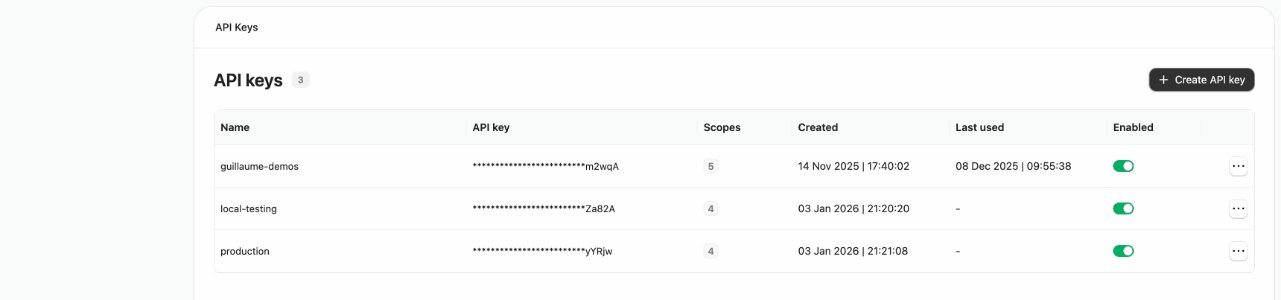
Field Description Type Required
`StackOne` Connector schema version, set to `1.0.0`. string Yes
[`actions`](#actions) Actions the connector exposes. object[] No
[`authentication`](#authentication) Authentication methods the connector supports. object[] No
[`baseUrl`](#baseurl) Root URL for all API requests. Supports expressions. string Yes
[`concurrency`](#concurrency) Request concurrency configuration for the connector. object No
[`documentation`](#documentation) External documentation links for the connector. object No
[`events`](#events) Event and webhook configuration for the connector. object No
`forkedFrom` Key of the connector this one was forked from. Not currently in use. string No
[`info`](#info) Connector metadata. object Yes
[`mcp`](#mcp) MCP-specific configuration for the connector. object No
[`rateLimit`](#ratelimit) Request rate-limit configuration for the connector. object No
`releaseStage` Default maturity level inherited by actions, events and authentication methods that do not declare their own. The stage of the connector itself is computed from theirs, never authored here.
Allowed: `preview`, `beta`, `ga`, `deprecated`, `internal`
enum No
`resources` Source of information for the connector, usually a URL to the provider's documentation. string No
[`scopeDefinitions`](#scopedefinitions) Requirements actions can depend on, keyed by name, such as OAuth scopes, pricing tiers, or feature flags. object No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaOverview path="/" */} ## actions The operations the connector exposes, each with inputs, steps, and a result. See [actions](/connector-yaml-reference/yaml-schema/actions). ## authentication An array of authentication methods (OAuth 2.0, custom/API key, and others). See [authentication](/connector-yaml-reference/yaml-schema/authentication). ## baseUrl **Examples** ```yaml # Static URL baseUrl: 'https://api.bamboohr.com/api/gateway.php' # Dynamic URL with credentials: baseUrl: 'https://api.bamboohr.com/api/gateway.php/${credentials.subdomain}/v1' ``` Individual actions can override baseUrl in their step parameters. ## concurrency Request concurrency configuration for the connector.
Field Description Type Required
`mainMaxConcurrency` Maximum number of concurrent in-flight requests per linked account. number Yes
[`subPools`](#concurrency-subpools) Per-URL-pattern concurrency overrides. object[] No
Per-URL-pattern concurrency overrides.
Field Description Type Required
`maxConcurrency` Maximum concurrent requests for the matched URLs. number Yes
`subPoolKey` Identifier for this concurrency sub-pool. string Yes
`urlPattern` URL pattern the sub-pool's limit applies to. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/concurrency" */} **Examples** ```yaml concurrency: mainMaxConcurrency: 5 subPools: - subPoolKey: reports urlPattern: '/reports' maxConcurrency: 1 ``` ## documentation External documentation links for the connector.
Field Description Type Required
[`references`](#documentation-references) External documentation links. object[] Yes
External documentation links.
Field Description Type Required
`description` Explains what the reference covers. string No
`title` Link text for the reference. string Yes
`url` URL of the referenced document. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/documentation" */} **Examples** ```yaml documentation: references: - title: API reference url: https://api.acme.com/docs description: Full REST API documentation. ``` ## events Webhook and event configuration for the connector. See [events](/connector-yaml-reference/yaml-schema/events). ## info Connector metadata.
Field Description Type Required
[`assets`](#info-assets) Visual assets for the connector. object Yes
[`changelog`](#info-changelog) Description of what changed in this version. object No
`description` Brief one-line summary of the connector. string Yes
`details` Extended description of capabilities and limitations. string No
`key` Unique lowercase identifier for the connector. string Yes
`title` Human-readable provider name shown in Hub and Dashboard. string Yes
`version` Connector version following semantic versioning. string Yes
Visual assets for the connector.
Field Description Type Required
`icon` URL to the provider logo. string Yes
Description of what changed in this version.
Field Description Type Required
`labels` Tags categorizing the changelog entry for filtering. string[] No
`summary` Human-readable summary of the changes in this version. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/info" */} ### info.assets.icon Requirements: - 24x24 pixels minimum - SVG or PNG format - Transparent background preferred - Hosted on HTTPS ### info.description Best practices: - Keep under 200 characters - Mention key capabilities - Include category context (HRIS, CRM, etc.) ### info.version See [Connector Versioning](/connector-building/connector-versioning) **Examples** ```yaml info: title: Acme HRIS key: acme_hris version: 1.0.0 description: HRIS connector for Acme covering employees, departments, and time-off. assets: icon: https://stackone-logos.com/api/acme/filled/png ``` ## mcp MCP-specific configuration for the connector.
Field Description Type Required
`instructions` Guidance text surfaced to MCP clients (max 2000 characters). string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/mcp" */} ## rateLimit The runtime tracks requests per linked account and throttles when limits are reached. Requests exceeding the limit are queued and retried with exponential backoff. Request rate-limit configuration for the connector.
Field Description Type Required
`mainRatelimit` Maximum requests per second for each linked account, across all of the connector's endpoints. number Yes
[`mappedRateLimitErrors`](#ratelimit-mappedratelimiterrors) Provider responses that should be treated as rate-limit signals. object[] No
[`subPools`](#ratelimit-subpools) Per-URL-pattern rate limit overrides. object[] No
Provider responses that should be treated as rate-limit signals.
Field Description Type Required
`errorMessage` Provider error message identifying a rate-limit error. string Yes
`errorMessagePath` Path to the error message in the response body. string No
`errorStatus` HTTP status code indicating a rate-limit error. number Yes
`retryAfterPath` Path to the retry-after value within the response headers, not the body. string No
`retryAfterUnit` Unit the retry-after value is expressed in.
Allowed: `seconds`, `milliseconds`, `date`
enum No
`retryAfterValue` Fixed delay to wait before retrying. number No
Per-URL-pattern rate limit overrides.
Field Description Type Required
`rateLimit` Maximum requests per second for the matched URLs. number Yes
`subPoolKey` Identifier for this rate-limit sub-pool. string Yes
`urlPattern` URL pattern the sub-pool's limit applies to. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/rateLimit" */} **Best practices** - Set slightly below provider’s documented limit - Check provider API docs for per-endpoint limits - Some providers have different limits for different endpoints **Examples** ```yaml rateLimit: mainRatelimit: 10 subPools: - subPoolKey: search urlPattern: '/search' rateLimit: 2 mappedRateLimitErrors: - errorStatus: 429 errorMessage: Too Many Requests retryAfterPath: "$['retry-after']" retryAfterUnit: seconds ``` ## scopeDefinitions Requirements actions can depend on, keyed by name, such as OAuth scopes, pricing tiers, or feature flags.
Field Description Type Required
`description` Explains what this scope grants. string Yes
`includes` Another scope this scope implies. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/scopeDefinitions" */} **Examples** ```yaml scopeDefinitions: employees:read: description: Read employee data employees:write: description: Create and update employee records includes: employees:read ``` ## Related How connector files and partials are organized. The step functions actions are built from. # Authentication Source: https://docs.stackone.com/connector-yaml-reference/yaml-schema/authentication Field reference for a connector's authentication types. # Structure Multiple authentication methods per connector are allowed. ```yaml authentication: # Authentication using OAuth - oauth2: type: oauth2 label: OAuth 2.0 # ...remaining oauth2 fields # Authentication using API key - api_key: type: custom label: API Key # ...remaining custom fields ``` # Properties Authentication methods the connector supports.
Field Description Type Required
[`authorization`](#authorization) Runtime authorization strategy applied to outgoing requests. union Yes
[`certificates`](#certificates) Mutual-TLS certificates and keys for this method. object No
[`configFields`](#configfields) Credentials the end-user enters when linking an account. array No
[`configNotices`](#confignotices) Callouts shown while entering config fields. object[] No
[`environments`](#environments) Deployment targets selectable for this method. object[] Yes
`grantType` OAuth grant flow used to obtain tokens.
Allowed: `authorization_code`, `client_credentials`
Default: `authorization_code`
enum No
`label` Display name for this authentication method. string Yes
[`refreshAuthentication`](#refreshauthentication) Configuration for refreshing expired credentials. object No
`releaseStage` Maturity level of this authentication method. Defaults to the highest stage among the actions and events it can run.
Allowed: `preview`, `beta`, `ga`, `deprecated`, `internal`
enum No
`requiredScopes` Scope names required by this authentication method. Space-separated, with any name that contains spaces wrapped in double quotes. string No
[`setupFields`](#setupfields) Credentials entered when creating a Connector Profile. array No
[`setupNotices`](#setupnotices) Callouts shown while entering setup fields. object[] No
[`support`](#support) Help resources shown while connecting with this method. object No
[`testActions`](#testactions) Actions run to validate a connection after authentication. object[] No
`type` Selects the OAuth 2.0 authentication method. string Yes
[`authorizationFlow`](#authorizationflow) MCP OAuth authorization flow; static credentials are used when omitted. object No
`serverUrl` MCP server URL this authentication method connects to. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaOverview path="/properties/authentication" */} The variants share a common set of fields and are told apart by `type`. The `grantType` field selects the OAuth grant flow, either `authorization_code` (default) or `client_credentials`. ```yaml authentication: - oauth2: type: oauth2 label: OAuth 2.0 grantType: authorization_code authorization: { ... } environments: [ ... ] # ...remaining fields ``` The general-purpose method, for providers whose authentication doesn't fit `oauth2`, `oidc`, or `mcp`. ```yaml authentication: - api_key: type: custom label: API Key authorization: { ... } environments: [ ... ] # ...remaining fields ``` Runs the authorization-code flow using standard OpenID Connect discovery. ```yaml authentication: - oidc: type: oidc label: OpenID Connect authorization: { ... } environments: [ ... ] # ...remaining fields ``` Authenticates against a remote MCP server. The optional `authorizationFlow` field runs the MCP OAuth sequence when present, and falls back to static credentials like `custom` when omitted. ```yaml authentication: - mcp: type: mcp label: MCP Server authorizationFlow: clientRegistration: dcr scopes: [read, write] authorization: { ... } environments: [ ... ] # ...remaining fields ``` ## authorization Runtime authorization strategy applied to outgoing requests.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/authorization" */} When the `authorization` type is `oauth2`, the runtime runs the authorization-code flow: 1. The end-user clicks Connect in the StackOne Hub. 2. The runtime builds the authorization URL from `authorizationUrl` and `authorizationParams`. 3. The end-user signs in at the provider and grants access. 4. The provider redirects back to the callback URL with an authorization code. 5. The runtime exchanges that code for tokens at `tokenUrl`. 6. The tokens are stored as the Linked Account's credentials. **Examples** ```yaml authorization: type: none ``` ```yaml authorization: type: basic username: $.credentials.username password: $.credentials.password ``` ```yaml authorization: type: bearer token: $.credentials.accessToken ``` ```yaml authorization: type: oauth2 authorizationUrl: https://auth.provider.com/oauth2/authorize authorizationParams: response_type: code client_id: $.credentials.clientId redirect_uri: ${apiHostUri}/connect/oauth2/{provider}/callback scope: $.credentials.scopes tokenUrl: https://auth.provider.com/oauth2/token token: $.credentials.accessToken includeBearer: true ``` ## authorizationFlow MCP OAuth authorization flow; static credentials are used when omitted.
Field Description Type Required
`clientRegistration` Client registration mechanism used with the MCP server.
Allowed: `cimd`, `dcr`
Default: `cimd`
enum Yes
`discovery` Whether OAuth authorization-server metadata is discovered automatically.
Default: `true`
boolean Yes
`scopes` OAuth scopes requested during the MCP authorization flow. string[] No
`serverUrl` MCP server URL the connect flow authorizes against. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/3/properties/authorizationFlow" */} **Examples** ```yaml authorizationFlow: clientRegistration: dcr scopes: [read, write] ``` ## certificates Mutual-TLS certificates and keys for this method.
Field Description Type Required
`certs` Client certificates used for mutual-TLS. string[] No
`keys` Private keys used for mutual-TLS. string[] No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/certificates" */} **Examples** ```yaml configFields: - key: client_cert label: Client certificate (PEM) type: password required: true secret: true - key: client_key label: Client private key (PEM) type: password required: true secret: true certificates: certs: [client_cert] keys: [client_key] ``` ## configFields Credentials the end-user enters when linking an account.
Field Description Type Required
`computed` Field value is a JEXL expression in `value`, evaluated at runtime rather than entered by the user. boolean No
`description` Helper text explaining what the user should enter. string No
`externalSystemAccountIdentifier` Value identifies the account in the external system, used to match incoming webhook events to a linked account. boolean No
`key` Identifier the credential value is stored and referenced under. string Yes
`label` Human-readable name shown for this field. string Yes
`placeholder` Example value shown in the empty input to hint the expected format. string No
`readOnly` Whether the field is displayed but cannot be edited by the user.
Default: `false`
boolean Yes
`required` Whether the field must have a value.
Default: `false`
boolean Yes
`secret` Encrypt the value at rest and mask it in the UI.
Default: `false`
boolean Yes
`tooltip` Additional guidance shown on hover for this field. string No
`type` Input control rendered for this credential field.
Allowed: `text`, `password`, `text_area`
enum Yes
[`validation`](#configfields-text-password-text-area-validation) Client-side validation constraint applied to the entered value. object No
`value` Preset or computed value for the field, such as a fixed default or a JEXL expression. string No
Client-side validation constraint applied to the entered value.
Field Description Type Required
`errorMessage` Message shown when the value fails the pattern or format check. string No
`format` Named format the entered value must match, standing in for a common regular expression. Provide this or `pattern`, not both.
Allowed: `email`, `url`, `uri`, `uuid`, `date`, `datetime`
enum No
`pattern` Regular expression the entered value must match. Provide this or `format`, not both. string No
Field Description Type Required
`computed` Field value is a JEXL expression in `value`, evaluated at runtime rather than entered by the user. boolean No
`description` Helper text explaining what the user should enter. string No
`externalSystemAccountIdentifier` Value identifies the account in the external system, used to match incoming webhook events to a linked account. boolean No
`key` Identifier the credential value is stored and referenced under. string Yes
`label` Human-readable name shown for this field. string Yes
[`options`](#configfields-select-options) Selectable choices offered for this field. object[] Yes
`placeholder` Example value shown in the empty input to hint the expected format. string No
`readOnly` Whether the field is displayed but cannot be edited by the user.
Default: `false`
boolean Yes
`required` Whether the field must have a value.
Default: `false`
boolean Yes
`secret` Encrypt the value at rest and mask it in the UI.
Default: `false`
boolean Yes
`tooltip` Additional guidance shown on hover for this field. string No
`type` Input control rendered for this credential field. string Yes
`value` Preset or computed value for the field, such as a fixed default or a JEXL expression. string No
Selectable choices offered for this field.
Field Description Type Required
`label` Human-readable text shown for this option. string Yes
`value` Value stored when this option is selected. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/configFields/items" */} **Examples** ```yaml configFields: - key: subdomain label: Subdomain type: text required: true placeholder: acme-corp - key: client_id label: Client ID type: text required: true - key: client_secret label: Client Secret type: password required: true secret: true - key: region label: Region type: select required: true options: - { value: us, label: United States } - { value: eu, label: European Union } ``` ## configNotices Callouts shown while entering config fields.
Field Description Type Required
`anchor` Field key the notice is shown above. Only valid when position is top. string No
`description` Text shown in the notice. string Yes
`key` Identifier for the notice. string Yes
`position` Whether the notice appears above or below the fields.
Allowed: `top`, `bottom`
Default: `top`
enum Yes
`type` Visual style of the notice.
Allowed: `warning`, `info`
Default: `info`
enum Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/configNotices/items" */} **Examples** ```yaml configNotices: - key: sandbox_warning type: warning description: Use your sandbox credentials while testing. position: top anchor: client_id ``` ## environments Deployment targets selectable for this method.
Field Description Type Required
`key` Identifier stored for the selected environment. string Yes
`name` Human-readable environment name. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/environments/items" */} **Examples** ```yaml environments: - key: production name: Production - key: sandbox name: Sandbox ``` ## refreshAuthentication Configuration for refreshing expired credentials.
Field Description Type Required
[`action`](#refreshauthentication-action) Action executed to refresh the credentials. object Yes
`schedule` Cron expression for proactively refreshing credentials. string No
Action executed to refresh the credentials. Same fields as [actions](/connector-yaml-reference/yaml-schema/actions). {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/refreshAuthentication" */} The initial OAuth exchange stores the provider's refresh token in the Linked Account's credentials. `refreshAuthentication` then keeps the access token current: 1. On the `schedule` cron, the runtime runs the `refresh_token` action. 2. The action sends the stored refresh token to the provider's token endpoint. 3. The provider returns a new access token, and sometimes a new refresh token. 4. The returned tokens replace the Linked Account's credentials. Set `schedule` to fire before the access token expires, so requests never use a stale token. **Examples** ```yaml refreshAuthentication: schedule: '*/50 * * * *' # every 50 minutes (10 min before 60 min token expiry) action: actionId: refresh_oauth_token actionType: refresh_token label: Refresh OAuth token description: Exchange refresh_token for a new access_token. steps: - stepId: refresh description: POST to the token endpoint. stepFunction: functionName: request version: v1 parameters: url: https://auth.provider.com/oauth/token method: post args: - { name: grant_type, value: refresh_token, in: body } - { name: refresh_token, value: '${credentials.refresh_token}', in: body } - { name: client_id, value: '${credentials.client_id}', in: body } - { name: client_secret, value: '${credentials.client_secret}', in: body } ``` ## setupFields Credentials entered when creating a Connector Profile.
Field Description Type Required
`computed` Field value is a JEXL expression in `value`, evaluated at runtime rather than entered by the user. boolean No
`description` Helper text explaining what the user should enter. string No
`externalSystemAccountIdentifier` Value identifies the account in the external system, used to match incoming webhook events to a linked account. boolean No
`key` Identifier the credential value is stored and referenced under. string Yes
`label` Human-readable name shown for this field. string Yes
`placeholder` Example value shown in the empty input to hint the expected format. string No
`readOnly` Whether the field is displayed but cannot be edited by the user.
Default: `false`
boolean Yes
`required` Whether the field must have a value.
Default: `false`
boolean Yes
`secret` Encrypt the value at rest and mask it in the UI.
Default: `false`
boolean Yes
`tooltip` Additional guidance shown on hover for this field. string No
`type` Input control rendered for this credential field.
Allowed: `text`, `password`, `text_area`
enum Yes
[`validation`](#setupfields-text-password-text-area-validation) Client-side validation constraint applied to the entered value. object No
`value` Preset or computed value for the field, such as a fixed default or a JEXL expression. string No
Client-side validation constraint applied to the entered value.
Field Description Type Required
`errorMessage` Message shown when the value fails the pattern or format check. string No
`format` Named format the entered value must match, standing in for a common regular expression. Provide this or `pattern`, not both.
Allowed: `email`, `url`, `uri`, `uuid`, `date`, `datetime`
enum No
`pattern` Regular expression the entered value must match. Provide this or `format`, not both. string No
Field Description Type Required
`computed` Field value is a JEXL expression in `value`, evaluated at runtime rather than entered by the user. boolean No
`description` Helper text explaining what the user should enter. string No
`externalSystemAccountIdentifier` Value identifies the account in the external system, used to match incoming webhook events to a linked account. boolean No
`key` Identifier the credential value is stored and referenced under. string Yes
`label` Human-readable name shown for this field. string Yes
[`options`](#setupfields-select-options) Selectable choices offered for this field. object[] Yes
`placeholder` Example value shown in the empty input to hint the expected format. string No
`readOnly` Whether the field is displayed but cannot be edited by the user.
Default: `false`
boolean Yes
`required` Whether the field must have a value.
Default: `false`
boolean Yes
`secret` Encrypt the value at rest and mask it in the UI.
Default: `false`
boolean Yes
`tooltip` Additional guidance shown on hover for this field. string No
`type` Input control rendered for this credential field. string Yes
`value` Preset or computed value for the field, such as a fixed default or a JEXL expression. string No
Selectable choices offered for this field.
Field Description Type Required
`label` Human-readable text shown for this option. string Yes
`value` Value stored when this option is selected. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/setupFields/items" */} **Examples** ```yaml setupFields: - key: oauth_client_id label: OAuth Client ID type: text required: true - key: oauth_client_secret label: OAuth Client Secret type: password required: true secret: true ``` ## setupNotices Callouts shown while entering setup fields.
Field Description Type Required
`anchor` Field key the notice is shown above. Only valid when position is top. string No
`description` Text shown in the notice. string Yes
`key` Identifier for the notice. string Yes
`position` Whether the notice appears above or below the fields.
Allowed: `top`, `bottom`
Default: `top`
enum Yes
`type` Visual style of the notice.
Allowed: `warning`, `info`
Default: `info`
enum Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/setupNotices/items" */} **Examples** ```yaml setupNotices: - key: rotation_reminder type: info description: Rotate the client secret every 90 days. position: bottom ``` ## support Help resources shown while connecting with this method.
Field Description Type Required
`description` Help text guiding the user through connecting. string No
[`guides`](#support-guides) Step-by-step connection guides. object No
`link` URL to external setup documentation. Defaults to the generated connector guide on docs.stackone.com when omitted. string No
Step-by-step connection guides.
Field Description Type Required
[`config`](#support-guides-config) Guide for the credentials end-users enter per connection. object No
[`setup`](#support-guides-setup) Guide for the credentials your team registers once. object No
Guide for the credentials end-users enter per connection.
Field Description Type Required
[`sections`](#support-guides-config-sections) Ordered sections making up the guide. object[] Yes
`warning` Cautionary note shown at the top of the guide. string No
Ordered sections making up the guide.
Field Description Type Required
`applicableScopes` Scope names for which this section is shown. Space-separated, with any name that contains spaces wrapped in double quotes. string No
`content` Introductory text for the section. string Yes
[`image`](#support-guides-config-sections-image) Illustrative image for the section. object No
`list` Ordered items elaborating the section. string[] No
[`steps`](#support-guides-config-sections-steps) Ordered steps making up the section. object[] No
`title` Heading for this guide section. string Yes
Illustrative image for the section.
Field Description Type Required
`alt` Alternative text describing the image. string Yes
`src` Image URL or a path relative to the connector. string Yes
Ordered steps making up the section.
Field Description Type Required
`applicableScopes` Scope names for which this step is shown. Space-separated, with any name that contains spaces wrapped in double quotes. string No
`content` Body text describing what the user should do. string Yes
`displayScopes` Whether the step shows badges for the actions its scopes unlock. boolean No
[`image`](#support-guides-config-sections-steps-image) Illustrative image for the step. object No
`list` Ordered items elaborating the step. string[] No
`title` Heading for this guide step. string Yes
Illustrative image for the step.
Field Description Type Required
`alt` Alternative text describing the image. string Yes
`src` Image URL or a path relative to the connector. string Yes
Guide for the credentials your team registers once.
Field Description Type Required
[`sections`](#support-guides-setup-sections) Ordered sections making up the guide. object[] Yes
`warning` Cautionary note shown at the top of the guide. string No
Ordered sections making up the guide.
Field Description Type Required
`applicableScopes` Scope names for which this section is shown. Space-separated, with any name that contains spaces wrapped in double quotes. string No
`content` Introductory text for the section. string Yes
[`image`](#support-guides-setup-sections-image) Illustrative image for the section. object No
`list` Ordered items elaborating the section. string[] No
[`steps`](#support-guides-setup-sections-steps) Ordered steps making up the section. object[] No
`title` Heading for this guide section. string Yes
Illustrative image for the section.
Field Description Type Required
`alt` Alternative text describing the image. string Yes
`src` Image URL or a path relative to the connector. string Yes
Ordered steps making up the section.
Field Description Type Required
`applicableScopes` Scope names for which this step is shown. Space-separated, with any name that contains spaces wrapped in double quotes. string No
`content` Body text describing what the user should do. string Yes
`displayScopes` Whether the step shows badges for the actions its scopes unlock. boolean No
[`image`](#support-guides-setup-sections-steps-image) Illustrative image for the step. object No
`list` Ordered items elaborating the step. string[] No
`title` Heading for this guide step. string Yes
Illustrative image for the step.
Field Description Type Required
`alt` Alternative text describing the image. string Yes
`src` Image URL or a path relative to the connector. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/support" */} **Examples** ```yaml support: link: https://docs.provider.com/oauth-setup description: How to register an OAuth app in the provider dashboard. guides: setup: sections: - title: Register an OAuth app content: Sign in to the provider dashboard and create an app. steps: - title: Open the Developer settings content: Click your avatar, then Developer settings. image: { src: /images/connectors/provider/dev-settings.png, alt: Developer settings menu } - title: Create a new OAuth app content: Set the redirect URL to the value shown in the Hub. ``` ## testActions Actions run to validate a connection after authentication.
Field Description Type Required
[`action`](#testactions-action) Action id or definition executed to test the connection. union Yes
`condition` JEXL expression gating whether the test action runs. string No
`required` Currently not in use.
Default: `true`
boolean Yes
Action id or definition executed to test the connection. A `string` value. Same fields as [actions](/connector-yaml-reference/yaml-schema/actions). {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/authentication/items/additionalProperties/anyOf/0/properties/testActions/items" */} **Examples** ```yaml testActions: - action: get_current_user required: true - action: list_admin_settings condition: '${credentials.scope.contains("admin")}' required: false ``` ## Related Declare available scopes; profiles can pin requiredScopes. Typically interpolates a ${credentials.subdomain} here. Connector-level external doc links, separate from per-auth guides. Actions referenced by testActions and refresh_token must exist in actions[]. # Actions Source: https://docs.stackone.com/connector-yaml-reference/yaml-schema/actions Field reference for the operations a connector exposes: inputs, steps, fieldConfigs, result, responses, cursor, dataSync, executionMode, compositeIdentifiers, validationRules, and examples. ## overview
Field Description Type Required
`actionId` Identifier for the action, prefixed with the connector key to form its MCP tool name. string Yes
`actionType` Operation kind the engine treats this action as.
Allowed: `list`, `get`, `create`, `update`, `delete`, `custom`, `refresh_token`, `event`, `unknown`
enum Yes
[`annotations`](#annotations) Explicit MCP tool-annotation overrides. Any field set here wins over the hint derived from `effects`. object No
[`authRequirements`](#authrequirements) Per-authentication-method scopes required to run the action. Supersedes the deprecated `requiredScopes`. object No
`categories` Business-domain classifications used for filtering the action. string[] Yes
[`compositeIdentifiers`](#compositeidentifiers) Configuration for building a record id from multiple provider fields. object No
[`cursor`](#cursor) Engine-managed cursor pagination configuration. object No
[`dataSync`](#datasync) Data Sync configuration for bulk syncing this action's records. object No
`description` Short description shown in the UI and MCP tool declarations. string Yes
`details` Extended context about the action for agents and developers. Used as the MCP tool description in place of `description` when set. string No
[`effects`](#effects) Semantic effects the action performs, used for MCP annotations and dashboard filtering. string[] No
`entrypointHttpMethod` HTTP method of the primary request. string No
`entrypointUrl` URL path of the action's primary request. Paired with `entrypointHttpMethod` to form the action key such as `GET /employees`, and used as the request log URL. string No
[`examples`](#examples) Example input values for the action, each optionally labeled with `exampleDescription`. object[] No
`executionMode` Whether the action runs synchronously or is dispatched to an async workflow. An action with a `browser_use` step must be `async`.
Allowed: `sync`, `async`
enum No
[`fieldConfigs`](#fieldconfigs) Field-level mapping and typing configuration for the result. array No
[`inputs`](#inputs) Parameters the action accepts, forming its tool input schema. object[] No
`label` Human-readable display name for the action. string Yes
`prerequisiteActions` Action ids this action declares as dependencies. string[] No
`providerEvents` Provider event names this action handles. string[] No
`releaseStage` Maturity level of the action.
Allowed: `preview`, `beta`, `ga`, `deprecated`, `internal`
enum No
`requiredScopes` Permission scopes required to run the action. Deprecated; use `authRequirements`. string No
`resources` URL to provider documentation for this action. string No
[`responses`](#responses) Documented HTTP responses the action can return. object[] No
[`result`](#result) Data returned to the caller, given as an expression or a map of output keys to expressions. union No
`schema` Name of the output schema the action conforms to. string No
`schemaType` Whether the output follows the native provider shape or the unified StackOne schema.
Allowed: `native`, `unified`
Default: `native`
enum Yes
[`steps`](#steps) Ordered steps executed to carry out the action. A single step runs one step function, and an iterator step runs step functions over each item of an array. array Yes
`tags` Free-form tags for grouping and filtering the action. string[] No
`userScoped` The action answers for the acting user, filtering the provider by `$.user`. The engine refuses the call when there is no acting user email. The object form also checks each returned record against the caller. union No
[`validationRules`](#validationrules) Cross-field validation rules applied to the action inputs. array No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaOverview path="/properties/actions/items" */} `actionType` tells the engine how to treat the operation. **Unified types (`list`, `get`, `create`, `update`, `delete`)** return normalized data: - Consistent response schemas across providers. - Cross-provider compatibility. - Automatic pagination handling. - Normalized error responses. A `list` action always returns `{ data: [...], next: }`. **Custom** (`custom`) returns the raw provider response, with no schema normalization. Use it for provider-specific endpoints that need full flexibility. **Special-purpose types** are used in other blocks, not `actions[]`: - `event` — an event handler under [`events.actions`](/connector-yaml-reference/yaml-schema/events#actions) that runs when a matching provider event arrives (matched via `providerEvents`). Same shape as a regular action. - `refresh_token` — the credential-refresh action under [`refreshAuthentication`](/connector-yaml-reference/yaml-schema/authentication#refreshauthentication). **Examples** ```yaml actions: - actionId: list_tickets actionType: custom effects: [read] label: List tickets description: List tickets from the provider. inputs: - name: limit description: Maximum number of results to return. type: number in: query required: false - name: offset description: Number of results to skip. type: number in: query required: false steps: - stepId: list_tickets_request description: Fetch tickets from the provider. stepFunction: functionName: request parameters: url: /tickets method: get args: - name: limit value: $.inputs.limit in: query condition: '{{present(inputs.limit)}}' - name: offset value: $.inputs.offset in: query condition: '{{present(inputs.offset)}}' result: data: $.steps.list_tickets_request.output.data ``` ## annotations Explicit MCP tool-annotation overrides. Any field set here wins over the hint derived from `effects`.
Field Description Type Required
`destructiveHint` Whether the action may delete or overwrite data. boolean No
`idempotentHint` Whether repeating the action has no additional effect. boolean No
`openWorldHint` Whether the action interacts with an open, external world. boolean No
`readOnlyHint` Whether the action only reads data. boolean No
`title` Human-readable title exposed to MCP clients. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/annotations" */} **Examples** ```yaml annotations: title: List employees readOnlyHint: true destructiveHint: false idempotentHint: true openWorldHint: false ``` ## authRequirements Per-authentication-method scopes required to run the action. Supersedes the deprecated `requiredScopes`. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/authRequirements" */} **Examples** ```yaml authRequirements: oauth2: - employees:read api_key: - employees:read ``` ## compositeIdentifiers Configuration for building a record id from multiple provider fields.
Field Description Type Required
`enabled` Whether composite identifiers are built for records. boolean Yes
[`fields`](#compositeidentifiers-fields) Field mappings that make up each composite identifier. object[] No
`version` Version of the composite identifier encoding. number No
Field mappings that make up each composite identifier.
Field Description Type Required
`components` Ordered output field keys whose values combine into the identifier. string[] Yes
`remote` Provider field the identifier component is read from. string No
`targetFieldKey` Key the composite identifier is written to. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/compositeIdentifiers" */} **Examples** ```yaml compositeIdentifiers: enabled: true version: 1 fields: - targetFieldKey: id remote: '$.record.identifier' components: [tenant_id, employee_id] ``` ## cursor Engine-managed cursor pagination configuration.
Field Description Type Required
`enabled` Whether cursor pagination is enabled. Only applies to list actions and has no effect on others. boolean Yes
`pageSize` Number of records requested per page. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/cursor" */} **Examples** ```yaml cursor: enabled: true pageSize: 100 ``` ## dataSync Synced records are stored for reading with [Deep Query](/optimize/deep-query). See [Data Sync](/optimize/data-sync/overview). Data Sync configuration for bulk syncing this action's records.
Field Description Type Required
`allowed` Whether Data Sync is enabled for this action. boolean Yes
`dataKey` Path within the step output to the records array, used when the action returns them in a single call rather than paginating. string No
[`incremental`](#datasync-incremental) Change-tracking configuration for incremental syncs. union No
`indexField` Field or fields forming each record's primary key during sync. Must uniquely identify each record; a value shared across records collapses them and a record missing it is dropped. union Yes
`maxDurationMinutes` Maximum time a single sync run may take. integer No
`maxPages` Maximum number of pages fetched in a single sync run. integer No
[`pagination`](#datasync-pagination) Pagination strategy used while syncing. union No
Change-tracking configuration for incremental syncs.
Field Description Type Required
`format` Encoding of the timestamp value: `iso8601`, `unix_seconds`, or `unix_millis`.
Allowed: `iso8601`, `unix_seconds`, `unix_millis`
enum Yes
[`iterator`](#datasync-incremental-time-filter-iterator) Names the request parameter carrying the last-sync timestamp and where on the request to place it. object Yes
[`response`](#datasync-incremental-time-filter-response) Configures reading the newest record timestamp from each page to advance the watermark. object No
`safetyBufferSeconds` Seconds subtracted from the run start time when falling back to the local clock so records near the boundary are not skipped.
Default: `60`
integer Yes
`type` Selects the updated-since strategy where each sync requests only records changed after the last watermark. string Yes
Names the request parameter carrying the last-sync timestamp and where on the request to place it.
Field Description Type Required
`in` Where to add the timestamp parameter: `query`, `body`, or `headers`.
Allowed: `query`, `body`, `headers`
enum Yes
`key` Request parameter name the last-sync timestamp is sent under. string Yes
Configures reading the newest record timestamp from each page to advance the watermark.
Field Description Type Required
`updatedAtPath` Path within each returned record to its last-updated timestamp, read to advance the watermark. string Yes
Field Description Type Required
[`iterator`](#datasync-incremental-delta-token-iterator) Names the request parameter carrying the previous delta token and where on the request to place it. object Yes
[`response`](#datasync-incremental-delta-token-response) Configures reading the next delta token from the response. object Yes
`type` Selects the delta-token strategy where each sync sends the token returned by the previous sync. string Yes
Names the request parameter carrying the previous delta token and where on the request to place it.
Field Description Type Required
`in` Where to add the delta token: `query`, `body`, or `headers`.
Allowed: `query`, `body`, `headers`
enum Yes
`key` Request parameter name the delta token is sent under. string Yes
Configures reading the next delta token from the response.
Field Description Type Required
`onlyOnFinalPage` When `true`, read the delta token only from the final page of results. boolean No
`path` Response key for the delta token used on the next sync: a dot-path into the action result, or a `{{ }}` expression evaluated against the result with response headers at `$.headers` (lowercased). string Yes
Pagination strategy used while syncing.
Field Description Type Required
[`iterator`](#datasync-pagination-cursor-iterator) Request parameter that carries the next-page cursor. object Yes
[`response`](#datasync-pagination-cursor-response) How records and the next-page cursor are located in the response. object Yes
`stopCondition` JEXL expression evaluated against each response to stop paging, with response headers at `$.headers` (lowercased). Defaults to stopping when the resolved next-page cursor is `null`. string No
`type` Selects the cursor-based pagination strategy. string Yes
Request parameter that carries the next-page cursor.
Field Description Type Required
`in` Where to add the pagination parameters: `query`, `body`, or `headers`.
Allowed: `query`, `body`, `headers`
enum Yes
`key` Request parameter the next-page cursor is sent in. string Yes
How records and the next-page cursor are located in the response.
Field Description Type Required
`dataKey` Response key holding the array of records for each page. string Yes
`nextKey` Response key for the next-page cursor: a dot-path into the action result, or a `{{ }}` expression evaluated against the result with response headers at `$.headers` (lowercased). string Yes
Field Description Type Required
[`iterator`](#datasync-pagination-offset-iterator) Request parameters that page through results by offset and limit. object Yes
[`response`](#datasync-pagination-offset-response) How each page of records is located in the response. object Yes
`stopCondition` JEXL expression evaluated against each response to stop paging, with response headers at `$.headers` (lowercased). Defaults to stopping when the data key returns no records. string No
`type` Selects the offset-based pagination strategy. string Yes
Request parameters that page through results by offset and limit.
Field Description Type Required
`defaultLimit` Number of records requested per page. Defaults to `100` when omitted. number No
`in` Where to add the pagination parameters: `query`, `body`, or `headers`.
Allowed: `query`, `body`, `headers`
enum Yes
`limitKey` Request parameter set to the number of records requested per page. string Yes
`offsetKey` Request parameter set to the offset of the first record on each page. string Yes
`startOffset` Offset sent on the first page. Defaults to `0`. Set to `1` for APIs that count records from 1 rather than 0, such as SCIM's `startIndex`. integer No
How each page of records is located in the response.
Field Description Type Required
`dataKey` Response key holding the array of records for each page. string Yes
Field Description Type Required
[`iterator`](#datasync-pagination-page-iterator) Request parameters that page through results by page number. object Yes
[`response`](#datasync-pagination-page-response) How each page of records is located in the response. object Yes
`stopCondition` JEXL expression evaluated against each response to stop paging, with response headers at `$.headers` (lowercased). Defaults to stopping when the data key returns no records. string No
`type` Selects the page-number pagination strategy. string Yes
Request parameters that page through results by page number.
Field Description Type Required
`defaultPageSize` Number of records requested per page. Defaults to `100` when omitted. number No
`in` Where to add the pagination parameters: `query`, `body`, or `headers`.
Allowed: `query`, `body`, `headers`
enum Yes
`pageKey` Request parameter set to the page number for each request. string Yes
`pageSizeKey` Request parameter set to the number of records requested per page. Omit when the endpoint takes no page-size parameter. string No
`startPage` Page number requested for the first page. Defaults to `1` when omitted. number No
How each page of records is located in the response.
Field Description Type Required
`dataKey` Response key holding the array of records for each page. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/dataSync" */} **Examples** ```yaml dataSync: allowed: true indexField: id pagination: type: cursor response: dataKey: data nextKey: next iterator: key: next in: query incremental: { ... } ``` ```yaml dataSync: allowed: true indexField: id pagination: type: offset response: dataKey: data.data iterator: offsetKey: offset limitKey: limit in: query incremental: { ... } ``` ```yaml dataSync: allowed: true indexField: id pagination: type: page response: dataKey: data.records iterator: pageKey: page pageSizeKey: per_page startPage: 1 in: query incremental: { ... } ``` ```yaml dataSync: allowed: true indexField: id pagination: { ... } incremental: type: time_filter iterator: key: updated_since in: query format: iso8601 ``` ```yaml dataSync: allowed: true indexField: id pagination: { ... } incremental: type: delta_token iterator: key: after in: query response: path: data.cursor ``` ## effects Semantic effects the action performs, used for MCP annotations and dashboard filtering. Optional, but worth setting on every action so an MCP client can auto-approve reads and prompt before writes. | Effect | Use for | |--------|---------| | `read` | Fetching a record or a list. Changes nothing. | | `search` | Querying with filters. Changes nothing. | | `write` | Creating or updating records. | | `delete` | Removing records. | | `execute` | Operations that aren't CRUD: send, sync, deploy, approve, merge. | An action can carry more than one effect. A find-or-create gets `[read, write]`. | Annotation | Derived from | |------------|--------------| | `readOnlyHint` | `true` when every effect is `read` or `search`. | | `destructiveHint` | `true` when effects include `delete`. | | `openWorldHint` | Always `true`, since actions call external provider APIs. | | `title` | The action's `label`. | | `idempotentHint` | Never derived. Set it with `annotations`. | With no `effects` and no `annotations` override, no hints are emitted, so a read looks no safer than a delete. Annotations are hints, not enforcement. Clients use them for grouping and approval defaults, not as a security boundary. To actually restrict what a linked account can call, disable the actions on its Connector Profile. See [Scoping connectors](/secure/scoping-connectors). **Examples** ```yaml effects: - read ``` ## examples Example input values for the action, each optionally labeled with `exampleDescription`.
Field Description Type Required
`exampleDescription` Explains what this usage example demonstrates. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/examples/items" */} **Examples** ```yaml examples: - exampleDescription: Fetch a single active employee. input: employee_id: emp_123 output: id: emp_123 name: Ada Lovelace status: active - exampleDescription: Employee not found. input: employee_id: emp_does_not_exist output: error: not_found statusCode: 404 ``` ## fieldConfigs Field-level mapping and typing configuration for the result. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/fieldConfigs/items" */} **Examples** ```yaml fieldConfigs: - targetFieldKey: id alias: employee_id type: string - targetFieldKey: name expression: '${item.first_name} ${item.last_name}' type: string - targetFieldKey: country alias: country_code type: string enumMapper: matcher: country_alpha2code_by_country_name - targetFieldKey: address type: object properties: - { targetFieldKey: street, alias: street_address, type: string } - { targetFieldKey: city, alias: city, type: string } - targetFieldKey: salary type: number requiredScopes: read:compensation # hidden if scope not granted ``` ## inputs Parameters the action accepts, forming its tool input schema.
Field Description Type Required
`array` Whether the input accepts a list of values.
Default: `false`
boolean Yes
`arrayFormat` How a list input's values are formatted in the request, such as repeated, comma-separated, or bracketed. Currently not in use.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`description` Explains the input for callers and generated tool schemas. string Yes
`in` Part of the HTTP request this input is placed in.
Allowed: `body`, `query`, `path`, `headers`
enum Yes
`name` Parameter name exposed to callers and mapped into the request. string Yes
[`oneOf`](#inputs-oneof) Allowed values when the input is an enum. union No
`properties` Nested inputs when the input is an object. Each has the same shape as a top-level input, minus `in`. object[] No
`required` Whether the caller must supply this input. boolean Yes
[`rules`](#inputs-rules) Validation rules applied to the input value. object No
`type` Data type of the input value.
Allowed: `string`, `number`, `boolean`, `datetime_string`, `object`, `enum`
enum No
`variants` An input that accepts more than one type. Provide at least two variants, each defining one of those types the way an input does. The input itself sets no top-level `type`, `array`, `properties`, `oneOf`, or `rules`. object[] No
Allowed values when the input is an enum.
Field Description Type Required
`values` Explicit list of allowed enum values. string[] Yes
Field Description Type Required
`ref` Name of a shared enum definition supplying the allowed values. One of: `employment_status`, `employment_type`, `gender`, `marital_status`. string Yes
Validation rules applied to the input value.
Field Description Type Required
`errorMessage` Message shown when the value violates a rule. string No
`format` Named format the value must conform to.
Allowed: `email`, `url`, `uri`, `uuid`, `date`, `datetime`
enum No
`max` Maximum numeric value allowed. number No
`maxLength` Maximum number of characters the value may have. number No
`min` Minimum numeric value allowed. number No
`minLength` Minimum number of characters the value must have. number No
`pattern` Regular expression the value must match. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/inputs/items" */} **Examples** ```yaml inputs: - name: employee_id type: string required: true in: path description: Provider's employee identifier. - name: status type: enum required: false in: query description: Filter by employment status. oneOf: values: [active, inactive, terminated] - name: hire_date type: datetime_string required: false in: body description: ISO 8601 hire date. rules: format: date - name: skills type: string array: true arrayFormat: comma in: query description: Comma-separated skill filter. - name: destination in: body required: true description: Where to send the payload. The type field selects the variant. variants: - type: object description: Post to a webhook URL. properties: - name: type type: enum required: true oneOf: values: [webhook] - name: url type: string required: true - type: object description: Send to an email address. properties: - name: type type: enum required: true oneOf: values: [email] - name: address type: string required: true ``` ## responses Documented HTTP responses the action can return.
Field Description Type Required
`description` What this response status means. string Yes
`statusCode` HTTP status code being documented. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/responses/items" */} **Examples** ```yaml responses: - statusCode: 200 description: Employee record returned. - statusCode: 404 description: No employee found with the provided ID. - statusCode: 409 description: Conflicts with an existing record; check inputs. ``` ## result Data returned to the caller, given as an expression or a map of output keys to expressions. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/result" */} **Examples** ```yaml result: '${steps.cast.output.data}' ``` ```yaml result: user: '${steps.fetch_user.output.data}' team: '${steps.fetch_team.output.data}' last_synced_at: '{{now()}}' ``` ## steps See [Step Functions](/connector-yaml-reference/step-functions/overview) for the full catalog and their parameters. Ordered steps executed to carry out the action. A single step runs one step function, and an iterator step runs step functions over each item of an array.
Field Description Type Required
`condition` JEXL expression gating whether this step runs. string No
`description` Explains what this step does. string Yes
`ignoreError` Whether a failure in this step is ignored so execution continues. boolean No
`onConditionError` How to behave when the condition expression errors: `false` (default) skips the step, `true` runs it anyway, and `break` halts the action.
Allowed: `true`, `false`, `break`
enum No
[`stepFunction`](#steps-single-step-stepfunction) Step function executed by this step. object Yes
`stepId` Identifier for this step, used to reference its output. string Yes
Step function executed by this step.
Field Description Type Required
`functionName` Name of the step function to execute. string Yes
`parameters` Arguments passed to the step function. object Yes
`version` Version of the step function to use. string No
Field Description Type Required
`condition` JEXL expression gating whether this step runs. string No
`description` Explains what this step does. string Yes
`ignoreError` Whether a failure in this step is ignored so execution continues. boolean No
`iterator` Expression that produces the array this step loops over. The step function(s) run once per item until the array is exhausted, halting early if an item fails and `ignoreError` is not set. string Yes
`onConditionError` How to behave when the condition expression errors: `false` (default) skips the step, `true` runs it anyway, and `break` halts the action.
Allowed: `true`, `false`, `break`
enum No
[`stepFunction`](#steps-iterator-step-stepfunction) Step function run for each iterated item. Provide this or `stepFunctions`, not both. object No
[`stepFunctions`](#steps-iterator-step-stepfunctions) Step functions run in sequence for each iterated item. Provide this or `stepFunction`, not both. object[] No
`stepId` Identifier for this step, used to reference its output. string Yes
Step function run for each iterated item. Provide this or `stepFunctions`, not both.
Field Description Type Required
`functionName` Name of the step function to execute. string Yes
`parameters` Arguments passed to the step function. object Yes
`version` Version of the step function to use. string No
Step functions run in sequence for each iterated item. Provide this or `stepFunction`, not both.
Field Description Type Required
`functionName` Name of the step function to execute. string Yes
`parameters` Arguments passed to the step function. object Yes
`version` Version of the step function to use. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/steps/items" */} ## validationRules Cross-field validation rules applied to the action inputs.
Field Description Type Required
`errorMessage` Message shown when the rule is violated. string No
`fields` Input names of which at least one must be provided. string[] Yes
`rule` Requires at least one of the listed inputs to be provided. string Yes
Field Description Type Required
[`condition`](#validationrules-requiredif-condition) Condition under which the field is required. object Yes
`errorMessage` Message shown when the rule is violated. string No
`field` Input that becomes required when the condition holds. string Yes
`rule` Requires an input when another field satisfies a condition. string Yes
Condition under which the field is required.
Field Description Type Required
`equals` Condition holds when the referenced field equals this value. string No
`field` Name of the other input this condition inspects. string Yes
`notEquals` Condition holds when the referenced field does not equal this value. string No
`present` When true, the condition holds if the referenced field is present. When false, it holds if the field is absent. boolean No
Field Description Type Required
`errorMessage` Message shown when the rule is violated. string No
`fields` Input names of which at most one may be provided. string[] Yes
`rule` Allows at most one of the listed inputs to be provided. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/validationRules/items" */} **Examples** ```yaml validationRules: - rule: atLeastOneOf fields: [email, employee_id] errorMessage: Provide either email or employee_id. ``` ```yaml validationRules: - rule: requiredIf field: termination_date condition: { field: status, equals: terminated } errorMessage: termination_date is required when status is "terminated". ``` ```yaml validationRules: - rule: mutuallyExclusive fields: [start_date, anchor_date] errorMessage: Use one of start_date or anchor_date, not both. ``` ## Related Full catalog of stepFunction implementations. JEXL syntax for condition, iterator, result, and step inputs. # Events Source: https://docs.stackone.com/connector-yaml-reference/yaml-schema/events Field reference for a connector's events block: event actions, router, setup lifecycle, and the external account id extractor. Configures a connector's inbound webhooks. For how event handling works end to end, see [Implementing events](/connector-building/implementing-events). ## overview Event and webhook configuration for the connector.
Field Description Type Required
[`actions`](#actions) Event actions that process incoming provider events. object[] No
[`externalAccountIdExtractor`](#externalaccountidextractor) Action that reads the provider's external account identifier from an incoming payload so the event can be matched to a linked account. It is a `custom` action with a required `result`. object No
[`guides`](#guides) Manual webhook setup guides. object No
[`router`](#router) Rules mapping incoming payloads to event actions. object No
[`setup`](#setup) Programmatic webhook lifecycle configuration. object No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaOverview path="/properties/events" */} **Examples** ```yaml events: setup: creation: steps: - stepId: create_webhook description: Register a webhook receiver. stepFunction: functionName: request version: v1 parameters: url: /webhooks method: post args: - name: url value: '${inputs.callbackUrl}' in: body result: '$.id' deletion: steps: - stepId: delete_webhook description: Remove the webhook receiver. stepFunction: functionName: request version: v1 parameters: url: '/webhooks/${inputs.remoteId}' method: delete router: rules: - when: '${event.type == "user.created"}' then: { action: user_created_event } ``` ## actions Event actions that process incoming provider events. Same fields as [actions](/connector-yaml-reference/yaml-schema/actions), plus:
Field Description Type Required
`requiresManualSetup` Whether the webhook must be configured manually in the provider UI. Pair with `guides.setup` to document that setup. boolean No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/events/properties/actions/items" */} **Examples** ```yaml events: actions: - actionId: handle_ticket_created actionType: event label: Ticket created webhook description: Processes ticket.created events from the provider. providerEvents: [ticket.created] inputs: - name: event description: The provider event object from the delivery. type: object in: body required: false steps: - stepId: emit description: Emit the ticket.created event to StackOne's dispatcher. stepFunction: functionName: emit_event parameters: event: eventType: ticket.created eventId: $.inputs.event.id data: $.inputs.event result: statusCode: 200 body: status: OK ``` ## externalAccountIdExtractor Action that reads the provider's external account identifier from an incoming payload so the event can be matched to a linked account. It is a `custom` action with a required `result`. Same fields as [actions](/connector-yaml-reference/yaml-schema/actions). {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/events/properties/externalAccountIdExtractor" */} **Examples** ```yaml events: externalAccountIdExtractor: actionId: extract_account_id actionType: custom label: Extract account ID from event description: Map provider tenant ID to StackOne linked account. steps: - stepId: lookup stepFunction: functionName: request version: v1 parameters: url: 'https://internal/accounts/by-tenant/${inputs.tenant_id}' method: get result: '${steps.lookup.output.data.linked_account_id}' ``` ## guides Manual webhook setup guides.
Field Description Type Required
[`setup`](#guides-setup) Guide for configuring webhooks in the provider UI. object No
Guide for configuring webhooks in the provider UI.
Field Description Type Required
[`sections`](#guides-setup-sections) Ordered sections making up the guide. object[] Yes
`warning` Cautionary note shown at the top of the guide. string No
Ordered sections making up the guide.
Field Description Type Required
`applicableScopes` Scope names for which this section is shown. Space-separated, with any name that contains spaces wrapped in double quotes. string No
`content` Introductory text for the section. string Yes
[`image`](#guides-setup-sections-image) Illustrative image for the section. object No
`list` Ordered items elaborating the section. string[] No
[`steps`](#guides-setup-sections-steps) Ordered steps making up the section. object[] No
`title` Heading for this guide section. string Yes
Illustrative image for the section.
Field Description Type Required
`alt` Alternative text describing the image. string Yes
`src` Image URL or a path relative to the connector. string Yes
Ordered steps making up the section.
Field Description Type Required
`applicableScopes` Scope names for which this step is shown. Space-separated, with any name that contains spaces wrapped in double quotes. string No
`content` Body text describing what the user should do. string Yes
`displayScopes` Whether the step shows badges for the actions its scopes unlock. boolean No
[`image`](#guides-setup-sections-steps-image) Illustrative image for the step. object No
`list` Ordered items elaborating the step. string[] No
`title` Heading for this guide step. string Yes
Illustrative image for the step.
Field Description Type Required
`alt` Alternative text describing the image. string Yes
`src` Image URL or a path relative to the connector. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/events/properties/guides" */} **Examples** ```yaml guides: setup: sections: - title: Enable webhooks content: Turn on event delivery in the provider dashboard. steps: - title: Open webhook settings content: Go to Settings, then Webhooks. ``` ## router Rules mapping incoming payloads to event actions.
Field Description Type Required
[`delivery`](#router-delivery) Rules matched against the whole delivery payload, rather than the individual events `itemsPath` splits it into. The first match short-circuits, so the per-event `rules` are skipped. object[] No
`itemsPath` JEXL expression that splits a batched delivery payload into individual events, so each is routed on its own through `rules`. When omitted, the whole payload is treated as a single event. string No
[`rules`](#router-rules) Rules matched in order against each individual event, where the first match maps it to an event action. Skipped when a `delivery` rule matches. object[] Yes
Rules matched against the whole delivery payload, rather than the individual events `itemsPath` splits it into. The first match short-circuits, so the per-event `rules` are skipped.
Field Description Type Required
[`then`](#router-delivery-then) Action to invoke when the rule matches. object Yes
`when` JEXL expression evaluated against the incoming request. This rule is selected when the expression returns anything other than null, false, or undefined. string Yes
Action to invoke when the rule matches.
Field Description Type Required
`action` Event action id invoked when the rule matches. string Yes
`input` JEXL expressions evaluated against the incoming request whose results become the invoked action's input. object No
Rules matched in order against each individual event, where the first match maps it to an event action. Skipped when a `delivery` rule matches.
Field Description Type Required
[`then`](#router-rules-then) Action to invoke when the rule matches. object Yes
`when` JEXL expression evaluated against the incoming request. This rule is selected when the expression returns anything other than null, false, or undefined. string Yes
Action to invoke when the rule matches.
Field Description Type Required
`action` Event action id invoked when the rule matches. string Yes
`input` JEXL expressions evaluated against the incoming request whose results become the invoked action's input. object No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/events/properties/router" */} **Examples** ```yaml events: router: rules: - when: '${event.type == "user.created"}' then: { action: handle_user_created } - when: '${event.type == "user.updated" && event.changes.contains("email")}' then: action: handle_email_change input: user_id: '${event.data.id}' new_email: '${event.data.email}' ``` ## setup Programmatic webhook lifecycle configuration.
Field Description Type Required
[`activation`](#setup-activation) Optional phase that activates the receiver after creation. Must reference `${inputs.remoteId}` in at least one step parameter. object No
[`creation`](#setup-creation) Phase that registers the webhook receiver. object Yes
[`deletion`](#setup-deletion) Phase that removes the webhook receiver. Must reference `${inputs.remoteId}` in at least one step parameter. object Yes
`isConsolidated` Whether one receiver handles all events rather than one per event.
Default: `false`
boolean Yes
Optional phase that activates the receiver after creation. Must reference `${inputs.remoteId}` in at least one step parameter.
Field Description Type Required
`result` Value produced by the phase, such as the created webhook id. string No
`steps` Ordered steps performed in this webhook phase. array Yes
Phase that registers the webhook receiver.
Field Description Type Required
`result` Expression selecting the value this phase produces, such as the created receiver's remote id (e.g. `$.steps.create.output.data.id`), which later phases reference as `${inputs.remoteId}`. string Yes
`steps` Ordered steps performed in this webhook phase. array Yes
Phase that removes the webhook receiver. Must reference `${inputs.remoteId}` in at least one step parameter.
Field Description Type Required
`result` Value produced by the phase, such as the created webhook id. string No
`steps` Ordered steps performed in this webhook phase. array Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/events/properties/setup" */} **Examples** ```yaml events: setup: creation: steps: - stepId: create_webhook description: Register a webhook receiver. stepFunction: functionName: request version: v1 parameters: url: /webhooks method: post args: - { name: url, value: '${inputs.callbackUrl}', in: body } - { name: events, value: '${inputs.eventTypes}', in: body } result: '$.id' activation: steps: - stepId: activate description: Mark webhook active. stepFunction: functionName: request version: v1 parameters: url: '/webhooks/${inputs.remoteId}/activate' method: post deletion: steps: - stepId: delete_webhook description: Remove the receiver. stepFunction: functionName: request version: v1 parameters: url: '/webhooks/${inputs.remoteId}' method: delete isConsolidated: false ``` ## Related The full action shape event actions and the extractor are built from. Fan out events to downstream subscribers. JEXL syntax for the router's when rules. The step shape each setup phase reuses. # Step Functions Source: https://docs.stackone.com/connector-yaml-reference/step-functions/overview The operations you chain together as steps to build a connector's actions and event setup. **Step functions** are the operations a connector runs, one step at a time, to carry out an [action](/connector-yaml-reference/yaml-schema/actions) or set up [events](/connector-yaml-reference/yaml-schema/events). Each step takes parameters and returns output that later steps and the result of the action or event setup can use. See [Expression Language](/connector-yaml-reference/expression-language) for how to reference a step's output. ## Step shape Steps take one of two shapes: Runs one step function once.
Field Description Type Required
`condition` JEXL expression gating whether this step runs. string No
`description` Explains what this step does. string Yes
`ignoreError` Whether a failure in this step is ignored so execution continues. boolean No
`onConditionError` How to behave when the condition expression errors: `false` (default) skips the step, `true` runs it anyway, and `break` halts the action.
Allowed: `true`, `false`, `break`
enum No
[`stepFunction`](#steps-stepfunction) Step function executed by this step. object Yes
`stepId` Identifier for this step, used to reference its output. string Yes
Step function executed by this step.
Field Description Type Required
`functionName` Name of the step function to execute. string Yes
`parameters` Arguments passed to the step function. object Yes
`version` Version of the step function to use. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/steps/items/anyOf/0" */}
Runs one or more step functions once for each item in the array its `iterator` resolves to.
Field Description Type Required
`condition` JEXL expression gating whether this step runs. string No
`description` Explains what this step does. string Yes
`ignoreError` Whether a failure in this step is ignored so execution continues. boolean No
`iterator` Expression that produces the array this step loops over. The step function(s) run once per item until the array is exhausted, halting early if an item fails and `ignoreError` is not set. string Yes
`onConditionError` How to behave when the condition expression errors: `false` (default) skips the step, `true` runs it anyway, and `break` halts the action.
Allowed: `true`, `false`, `break`
enum No
[`stepFunction`](#steps-stepfunction) Step function run for each iterated item. Provide this or `stepFunctions`, not both. object No
[`stepFunctions`](#steps-stepfunctions) Step functions run in sequence for each iterated item. Provide this or `stepFunction`, not both. object[] No
`stepId` Identifier for this step, used to reference its output. string Yes
Step function run for each iterated item. Provide this or `stepFunctions`, not both.
Field Description Type Required
`functionName` Name of the step function to execute. string Yes
`parameters` Arguments passed to the step function. object Yes
`version` Version of the step function to use. string No
Step functions run in sequence for each iterated item. Provide this or `stepFunction`, not both.
Field Description Type Required
`functionName` Name of the step function to execute. string Yes
`parameters` Arguments passed to the step function. object Yes
`version` Version of the step function to use. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: SchemaFields path="/properties/actions/items/properties/steps/items/anyOf/1" */}
## Step functions ### Requests Calls that send a request and return a response for later steps to use. Sends an HTTP request to the provider's API and returns the response. Sends HTTP requests to a paginated endpoint until it has one page of results, then returns a cursor for the next page. Sends a SOAP request to the provider and returns the parsed response. Sends SOAP requests to a paginated endpoint until it has one page of results, then returns a cursor for the next page. Calls a tool on the provider's MCP server, or lists the tools it offers. Invokes an AWS Lambda function, returning its response when invoked synchronously. Runs another action and returns its result. ### Authentication Prepare credentials that later requests use for authorization. Signs a JWT with a private key, for later requests to use as a credential. ### Transform Data Work on manipulating data already available in the action from the current context and previous steps. Maps fields from source data onto the shape the action returns. Converts fields in source data to their declared types. Combines the output of several earlier steps into one record or list. Returns fixed values, or the result of an expression. ### Files Upload files to a provider or download them from one. Uploads a file to the provider as a multipart form. Uploads raw binary content to the provider. Downloads a file from the provider, as a buffer or a stream. ### Events & Automation Start work outside the action's request and response flow. Emits an event with a type, date and payload. Runs a task in a browser session, starting at a given URL. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionCards */} # browser_use Source: https://docs.stackone.com/connector-yaml-reference/step-functions/browser-use Step function: browser_use Browser use is only available on certain plans. Each run also consumes credits from your allowance. See [plans and pricing](https://www.stackone.com/pricing/). Runs a task in a browser session, starting at a given URL. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="browser_use" */} Any action whose `steps[]` includes `browser_use` **must** declare `executionMode: async` on the action. The runtime enforces this — a sync action containing `browser_use` fails schema validation at build time. ## Input
Field Description Type Required
[`auth`](#auth) Credential handling for the browser task. object No
[`budgets`](#budgets) Execution limits the task must run within. object Yes
`locale` Locale the browser session runs in. string No
`startUrl` URL where the browser session begins.
Format: `uri`
string Yes
`systemPrompt` Author-defined preamble, persona, and guardrails applied to every invocation. string No
[`viewport`](#viewport) Browser viewport dimensions. object No
Credential handling for the browser task.
Field Description Type Required
`allowedDomains` Overrides the default allowed-domains policy, for auth flows that cross a domain boundary. string[] No
`requiresSession` Reserved for tasks that need a pre-authenticated browser session rather than form substitution. Not yet in use. boolean No
`sensitiveKeys` Credential keys masked from the LLM and substituted only at the typing layer. string[] No
Execution limits the task must run within.
Field Description Type Required
`maxDurationMs` Maximum task duration in milliseconds. integer Yes
`maxSteps` Maximum number of steps the agent may take. integer Yes
Browser viewport dimensions.
Field Description Type Required
`height` Viewport height in pixels. integer Yes
`width` Viewport width in pixels. integer Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="browser_use" version="v1" kind="input" */}
## Output {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="browser_use" version="v1" kind="output" */} # call_action Source: https://docs.stackone.com/connector-yaml-reference/step-functions/call-action Step function: call_action Runs another action and returns its result. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="call_action" */} ## Input
Field Description Type Required
`actionId` Id of the action to run, with or without the connector key prefix. Must be a literal: expressions are rejected so that cycles can be caught at validation time.
Pattern: `^[A-Za-z0-9_-]+$`
string Yes
[`inputs`](#inputs) Inputs for the callee, grouped by the location each one is declared `in:`. A value written under the wrong location is dropped rather than reported, and a callee that declares no inputs ignores all of them. object No
Inputs for the callee, grouped by the location each one is declared `in:`. A value written under the wrong location is dropped rather than reported, and a callee that declares no inputs ignores all of them.
Field Description Type Required
`body` Values for the callee's inputs declared `in: body`. any No
`headers` Values for the callee's inputs declared `in: header`. object No
`path` Values for the callee's inputs declared `in: path`. object No
`query` Values for the callee's inputs declared `in: query`. object No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="call_action" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The callee's `data`, when its result declares one. A result that is not an object is placed here whole, and a failed call puts the provider's parsed error body here. any No
`message` Error message, present only when the call failed. string No
`raw` The callee's raw provider response, present only when the call failed. any No
`statusCode` Status code of the callee's response. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="call_action" version="v1" kind="output" */}
# code_execution_lambda Source: https://docs.stackone.com/connector-yaml-reference/step-functions/code-execution-lambda Step function: code_execution_lambda Invokes an AWS Lambda function, returning its response when invoked synchronously. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="code_execution_lambda" */} ## Input
Field Description Type Required
[`args`](#args) Key/value pairs combined into the JSON payload sent to the Lambda function object[] No
`dataKey` Path to the field in the Lambda response to extract as data. string No
`endpoint` Custom Lambda service endpoint URL to call instead of the default. string No
`invocationType` How the Lambda is invoked. `RequestResponse` waits synchronously for the Lambda response, `Event` fires asynchronously and returns no response body, and `DryRun` validates parameters and permissions without invoking the function.
Allowed: `RequestResponse`, `Event`, `DryRun`
enum No
`lambdaName` Name or ARN of the Lambda function to invoke. string Yes
`qualifier` Function version or alias to invoke. string No
`region` AWS region the Lambda function runs in. string No
Key/value pairs combined into the JSON payload sent to the Lambda function
Field Description Type Required
`condition` A JEXL expression that includes the field only when it evaluates true. string No
`name` Payload field name. string Yes
`value` Payload field value. Supports expressions. any Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="code_execution_lambda" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The parsed Lambda response payload, or the value at `dataKey` when `dataKey` is set. any No
`executedVersion` Version of the Lambda function that was invoked. string No
`message` Status or error message from the response. string No
`raw` The full Lambda invocation result, including the parsed `payload`, `statusCode`, and `executedVersion`. any No
`statusCode` HTTP status code of the Lambda invocation. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="code_execution_lambda" version="v1" kind="output" */}
# download_file Source: https://docs.stackone.com/connector-yaml-reference/step-functions/download-file Step function: download_file Downloads a file from the provider. Set `responseMode: stream` for any file an action returns: REST pipes the bytes to the caller, and an MCP tool call returns a single-use download link with the file's name, type and size. A streaming step must be the last step of its action. The default, `buffer`, returns the content in `data`, which only suits content a later step in the same action needs to read. Use `fileName` when the provider's response carries no file name. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="download_file" */} ## Input
Field Description Type Required
[`args`](#args) Additional request parameters sent as query params, headers, or the request body, per each entry's `in`. object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Overrides the connector's base URL for the download. string No
[`customErrors`](#customerrors) Remaps matching provider error responses to different statuses or messages. object[] No
`encoding` Encoding applied to `data` when `responseMode` is `buffer`. Ignored when streaming. Use `none` to return a raw Buffer.
Allowed: `base64`, `utf8`, `binary`, `raw`, `none`
Default: `base64`
enum Yes
`fileName` Name to give the downloaded file, overriding any name from the provider's Content-Disposition header or `response.fileNameKey`. Supports expressions, so it can come from an earlier step such as a metadata lookup. Falls back to the provider's name when it resolves to nothing. A name with no extension gets one from the download's content type, so an exported document named `Q3 plan` saves as `Q3 plan.pdf`. string No
`followRedirects` Whether to follow HTTP redirects.
Default: `true`
boolean Yes
`maxRedirects` Maximum number of redirects to follow.
Default: `5`
number Yes
`method` HTTP method to use for the download.
Allowed: `get`, `post`, `put`, `delete`, `patch`
Default: `get`
enum Yes
[`response`](#response) Options for extracting file content from a JSON-wrapped response. object No
`responseMode` How the file is returned. `buffer` (the default) holds the whole file in memory and returns it in `data`, encoded per `encoding`, so an MCP tool call carries the entire file inline. `stream` returns a readable stream instead: REST pipes the bytes to the caller and an MCP tool call returns a single-use download link. Use `stream` for files. A streaming step must be the last step of its action.
Allowed: `buffer`, `stream`
Default: `buffer`
enum Yes
`responseType` Underlying HTTP response type requested. Used only when responseMode is buffer.
Allowed: `arraybuffer`, `blob`, `text`, `json`
Default: `arraybuffer`
enum Yes
`url` Download endpoint path appended to the base URL. string Yes
Additional request parameters sent as query params, headers, or the request body, per each entry's `in`.
Field Description Type Required
`arrayFormat` How array values are serialized in the query string: repeat, brackets, comma, or stringify.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`condition` A JEXL expression that includes the parameter only when it evaluates true. string No
`in` Where to send the parameter: query, body, or headers.
Allowed: `query`, `body`, `headers`
enum Yes
`name` Name of the request parameter. string Yes
`spread` Merges the value's object entries into the target location instead of setting a single named field. boolean No
`value` Value of the parameter. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
Remaps provider error responses to different statuses or messages. Useful for GraphQL APIs that return errors with a 200 status, normalizing provider-specific error formats, and giving AI agents clearer error messages.
Field Description Type Required
`condition` A JEXL expression that applies the remap only when it evaluates true. string No
`message` Error message to return in place of the provider's. string No
`receivedStatus` Provider HTTP status code to match. number Yes
`targetStatus` HTTP status code to return in place of the matched one. number Yes
Options for extracting file content from a JSON-wrapped response.
Field Description Type Required
`contentIsBase64` Whether the content in the JSON response is already base64 encoded.
Default: `false`
boolean Yes
`contentType` Fallback content type used when the JSON response exposes none to extract. `contentTypeKey` wins if it resolves. string No
`contentTypeKey` JSONPath to the content type within a JSON-wrapped response. string No
`dataKey` JSONPath to the file content within a JSON-wrapped response. string No
`fileNameKey` JSONPath to the filename within a JSON-wrapped response. string No
`forwardAuth` Whether to forward authentication headers to the secondary download request when following urlKey.
Default: `false`
boolean Yes
`urlKey` JSONPath to a download URL in the response to follow for the file. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="download_file" version="v1" kind="input" */}
## Output
Field Description Type Required
`contentDisposition` Content-Disposition header value for the client to use. string No
`data` Downloaded file content. A string in the format set by the `encoding` input (base64 by default), or a raw binary Buffer when `encoding: "none"`. Absent when `responseMode: "stream"` (content is piped via the stream output instead). union No
[`fileMetadata`](#filemetadata) File metadata extracted from response headers or a JSON-wrapped response. object No
`finalUrl` Final URL the file was downloaded from after redirects or a followed link. string No
`headers` All response headers returned with the download. object No
`message` Status or error message from the response. string No
`raw` The raw provider response before parsing. any No
`statusCode` HTTP status code of the provider response. number Yes
File metadata extracted from response headers or a JSON-wrapped response.
Field Description Type Required
`contentLength` Size of the file in bytes. number No
`contentType` MIME type of the downloaded file. string No
`etag` Entity tag identifying the file version. string No
`fileName` Name of the downloaded file. string No
`lastModified` Last-modified timestamp reported for the file. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="download_file" version="v1" kind="output" */}
# emit_event Source: https://docs.stackone.com/connector-yaml-reference/step-functions/emit-event Step function: emit_event Emits an event with a type, date and payload. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="emit_event" */} ## Input
Field Description Type Required
[`event`](#event) The event to emit. object No
The event to emit.
Field Description Type Required
`data` Normalized payload carried by the event. any No
`eventDate` Timestamp for when the event occurred. string No
`eventId` Unique identifier for this event. string No
`eventType` Name of the event type being emitted. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="emit_event" version="v1" kind="input" */}
## Output {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="emit_event" version="v1" kind="output" */} # group_data Source: https://docs.stackone.com/connector-yaml-reference/step-functions/group-data Step function: group_data Combines the output of several earlier steps into one record or list. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="group_data" */} ## Input
Field Description Type Required
`isSingleRecord` When true, returns a single record keyed by step ID, otherwise an array merged per key across steps. boolean No
`stepsDataToGroup` IDs of the steps whose output data should be grouped together. string[] Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="group_data" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The combined output data grouped from the referenced steps. any Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="group_data" version="v1" kind="output" */}
# map_fields Source: https://docs.stackone.com/connector-yaml-reference/step-functions/map-fields Step function: map_fields Maps fields from source data onto the shape the action returns. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="map_fields" */} ## Input
Field Description Type Required
`dataSource` Reference to the source data to transform. string Yes
`externalSources` Additional named data sources referenced by mapping expressions. object No
`fields` Field mapping definitions applied to the source data. array Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="map_fields" version="v2" kind="input" */}
## Output
Field Description Type Required
`data` The mapped fields produced from the source data. any Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="map_fields" version="v2" kind="output" */}
# mcp_request Source: https://docs.stackone.com/connector-yaml-reference/step-functions/mcp-request Step function: mcp_request Calls a tool on the provider's MCP server, or lists the tools it offers. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="mcp_request" */} ## Input
Field Description Type Required
[`args`](#args) Arguments passed to the MCP tool call. object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Overrides the connector's base URL for the MCP server. string No
`method` The MCP method to call. Either `tools/call` or `tools/list`.
Allowed: `tools/call`, `tools/list`
Default: `tools/call`
enum Yes
`timeout` Request timeout in milliseconds. integer No
`toolName` Name of the tool to call. Required when method is tools/call. string No
`url` MCP server endpoint path. string No
Arguments passed to the MCP tool call.
Field Description Type Required
`condition` A JEXL expression that includes the argument only when it evaluates true. string No
`name` Name of the argument. string Yes
`value` Value of the argument. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="mcp_request" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The parsed MCP response. For `tools/call` it holds the tool result, for `tools/list` it holds the list of tools. any No
`message` Status or error message from the response. string No
`raw` The raw MCP response before parsing. any No
`statusCode` Returns 200 for success, or 502 when the tool returns an error. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="mcp_request" version="v1" kind="output" */}
# paginated_request Source: https://docs.stackone.com/connector-yaml-reference/step-functions/paginated-request Step function: paginated_request Sends HTTP requests to a paginated endpoint until it has one page of results, then returns a cursor for the next page. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="paginated_request" */} ## Input
Field Description Type Required
[`args`](#args) Request parameters to send as query, body, or header values. object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Base URL the paginated requests are made against. string Yes
`cacheTTL` Minutes to serve each page from the shared per-account response cache. 0 or omitted disables caching. integer No
[`cursor`](#cursor) Pagination position carried over from the previous page request. object No
[`customErrors`](#customerrors) Remaps matching provider error responses to different statuses or messages. object[] No
`encodeQueryParams` Whether to URL-encode query parameter values before sending. boolean No
[`iterator`](#iterator) Controls how subsequent pages are requested. object Yes
`method` HTTP method to use: get, post, put, patch, or delete.
Allowed: `get`, `post`, `put`, `delete`, `patch`
enum Yes
[`response`](#response) Controls how each page response is parsed and paginated. object No
[`saml`](#saml) Generates a signed SAML assertion and merges it into the request body for token exchange. object No
`url` Endpoint path appended to the base URL. string Yes
Request parameters to send as query, body, or header values.
Field Description Type Required
`arrayFormat` How array values are serialized in the query string: repeat, brackets, comma, or stringify.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`condition` A JEXL expression that includes the parameter only when it evaluates true. string No
`in` Where to send the parameter: query, body, or headers.
Allowed: `query`, `body`, `headers`
enum Yes
`name` Name of the request parameter. string Yes
`spread` Merges the value's object entries into the target location instead of setting a single named field. boolean No
`value` Value of the parameter. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
Pagination position carried over from the previous page request.
Field Description Type Required
`position` Numeric offset or page position carried over from the previous page. union No
`token` Cursor token from the previous page used to fetch the next one. union No
Remaps provider error responses to different statuses or messages. Useful for GraphQL APIs that return errors with a 200 status, normalizing provider-specific error formats, and giving AI agents clearer error messages.
Field Description Type Required
`condition` A JEXL expression that applies the remap only when it evaluates true. string No
`message` Error message to return in place of the provider's. string No
`receivedStatus` Provider HTTP status code to match. number Yes
`targetStatus` HTTP status code to return in place of the matched one. number Yes
Controls how subsequent pages are requested.
Field Description Type Required
`condition` A JEXL expression that continues pagination only while it evaluates true. string No
`in` Where the pagination field is sent: query or body.
Allowed: `query`, `body`
enum Yes
`key` Request field name that carries the page token, offset, or number. string Yes
`maxPage` Highest page number allowed in `page` mode. Requesting a higher page fails the step with an error. integer No
`mode` Pagination strategy. `cursor` sends the returned next token back as the key and stops when none returns. `offset` advances the key by the number of records consumed. `page` increments the page number and stops on an empty or repeated page. Every mode also stops once `page_size` records are gathered or `iterator.condition` is false.
Allowed: `cursor`, `offset`, `page`
enum No
`startOffset` First record offset to request. Valid only in offset mode. Defaults to `0`; set to `1` for APIs that count records from 1, such as SCIM's `startIndex`. integer No
`startPage` First page number to request. Valid only in page mode. integer No
Controls how each page response is parsed and paginated.
Field Description Type Required
`dataKey` Path to the records array in the response. A path that resolves to a non-array or resolves to nothing is treated as an empty page, so the step succeeds with the records collected so far and logs a warning. string No
`indexField` Field used to key results when returning an indexed map. string No
`nextKey` Path to the next-page token or cursor in the response. string No
`nextKeyIn` Where the next-page token is read from: the response data or headers.
Allowed: `data`, `headers`
enum No
Generates a signed SAML assertion and merges it into the request body for token exchange.
Field Description Type Required
`audience` Intended audience for the assertion. string No
`cert` Signing certificate for the SAML assertion. any No
`clientId` Client identifier included as the api_key attribute in the assertion. string Yes
`issuer` Issuer identifier declared in the assertion. string No
`key` Base64-encoded private key used to sign the SAML assertion. string Yes
`lifetime` Assertion validity window in seconds. number No
`nameId` Subject NameID identifying the authenticating principal. string No
`nameIdentifierFormat` Format URI for the subject NameID. string No
`objectKey` Request body key under which the generated base64 SAML assertion is placed. string Yes
`tokenEndpoint` Recipient token endpoint the assertion is addressed to. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="paginated_request" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` Records accumulated across the fetched pages. any No
`message` Status or error message from the response. string No
`next` Pagination cursor for the next page, or null when no further pages remain. union No
`position` Numeric offset or page position reached, for offset and page pagination modes. number No
`raw` The raw provider response before parsing. any No
`statusCode` HTTP status code of the provider response. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="paginated_request" version="v1" kind="output" */}
# request Source: https://docs.stackone.com/connector-yaml-reference/step-functions/request Step function: request Sends an HTTP request to the provider's API and returns the response. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="request" */} ## Input
Field Description Type Required
[`args`](#args) Request parameters to send as query, body, or header values. object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Overrides the connector's base URL for this request. string No
`cacheTTL` Minutes to serve this request from the shared per-account response cache. 0 or omitted disables caching. integer No
[`certificates`](#certificates) Client TLS certificates and keys for mutual TLS connections. object No
[`customErrors`](#customerrors) Remaps matching provider error responses to different statuses or messages. object[] No
`encodeQueryParams` Whether to URL-encode query parameter values before sending. boolean No
`method` HTTP method to use: get, post, put, patch, or delete.
Allowed: `get`, `post`, `put`, `delete`, `patch`
enum Yes
[`response`](#response) Controls how the raw response is parsed into step output data. object No
[`saml`](#saml) Generates a signed SAML assertion and merges it into the request body for token exchange. object No
`url` Endpoint path appended to the base URL. string Yes
Request parameters to send as query, body, or header values.
Field Description Type Required
`arrayFormat` How array values are serialized in the query string: repeat, brackets, comma, or stringify.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`condition` A JEXL expression that includes the parameter only when it evaluates true. string No
`in` Where to send the parameter: query, body, or headers.
Allowed: `query`, `body`, `headers`
enum Yes
`inline` Sends the string value as the raw request body. Valid only as the sole in: body argument. boolean No
`name` Name of the request parameter. string Yes
`spread` Merges the value's object entries into the target location instead of setting a single named field. boolean No
`value` Value of the parameter. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
Client TLS certificates and keys for mutual TLS connections.
Field Description Type Required
`certs` PEM-encoded client certificates for mutual TLS. Each entry is a raw or base64-encoded PEM certificate. string[] No
`keys` PEM-encoded client private keys for mutual TLS. Each entry is a raw or base64-encoded PEM private key. string[] No
Remaps provider error responses to different statuses or messages. Useful for GraphQL APIs that return errors with a 200 status, normalizing provider-specific error formats, and giving AI agents clearer error messages.
Field Description Type Required
`condition` A JEXL expression that applies the remap only when it evaluates true. string No
`message` Error message to return in place of the provider's. string No
`receivedStatus` Provider HTTP status code to match. number Yes
`targetStatus` HTTP status code to return in place of the matched one. number Yes
Controls how the raw response is parsed into step output data.
Field Description Type Required
`collection` Whether to treat the response payload as a collection of records to index. boolean No
`dataKey` Path to the field in the response holding the records to extract. string No
`indexField` Field used to key results when returning an indexed map. string No
Generates a signed SAML assertion and merges it into the request body for token exchange.
Field Description Type Required
`audience` Intended audience for the assertion. string No
`cert` Signing certificate for the SAML assertion. any No
`clientId` Client identifier included as the api_key attribute in the assertion. string Yes
`issuer` Issuer identifier declared in the assertion. string No
`key` Base64-encoded private key used to sign the SAML assertion. string Yes
`lifetime` Assertion validity window in seconds. number No
`nameId` Subject NameID identifying the authenticating principal. string No
`nameIdentifierFormat` Format URI for the subject NameID. string No
`objectKey` Request body key under which the generated base64 SAML assertion is placed. string Yes
`tokenEndpoint` Recipient token endpoint the assertion is addressed to. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="request" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The parsed response payload extracted from the provider response. any No
`message` Status or error message from the response. string No
`raw` The raw provider response before parsing. any No
`statusCode` HTTP status code of the provider response. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="request" version="v1" kind="output" */}
# sign_jwt Source: https://docs.stackone.com/connector-yaml-reference/step-functions/sign-jwt Step function: sign_jwt Signs a JWT with a private key, for later requests to use as a credential. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="sign_jwt" */} ## Input
Field Description Type Required
`algorithm` Signing algorithm. Only RS256 is supported. string Yes
`claims` Claims to include in the JWT payload, such as `iss`, `scope`, and `aud`. `iat` and `exp` are required numbers with `exp` after `iat`, and accept `now` or `now+<N>s|m|h` tokens. object Yes
`privateKey` PEM-encoded private key used to sign the token. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="sign_jwt" version="v1" kind="input" */}
## Output
Field Description Type Required
`expiresIn` Token lifetime in seconds. number Yes
`publicKeyFingerprint` Fingerprint of the public key matching the signing key. string Yes
`token` The signed JWT. string Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="sign_jwt" version="v1" kind="output" */}
# soap_paginated_request Source: https://docs.stackone.com/connector-yaml-reference/step-functions/soap-paginated-request Step function: soap_paginated_request Sends SOAP requests to a paginated endpoint until it has one page of results, then returns a cursor for the next page. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="soap_paginated_request" */} ## Input
Field Description Type Required
[`args`](#args) Request parameters to send as query, body, or header values. object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Overrides the connector's base URL for the SOAP service. string No
[`cursor`](#cursor) Pagination position carried over from the previous page request. object No
[`customErrors`](#customerrors) Remaps matching provider error responses to different statuses or messages. object[] No
`encodeQueryParams` Whether to URL-encode query parameter values before sending. boolean No
`envelope` SOAP envelope template, as a string or object, used to build the request body. union No
[`iterator`](#iterator) Controls how subsequent pages are requested. object Yes
`method` HTTP method to use for the SOAP call, typically post.
Allowed: `get`, `post`, `put`, `delete`, `patch`
enum Yes
[`namespaces`](#namespaces) XML namespace declarations added to the SOAP envelope. object[] No
[`response`](#response) Controls how each page response is parsed and paginated. object No
`soapAction` Value sent in the SOAPAction HTTP header. string No
`soapOperation` Name of the SOAP operation to invoke. string No
`url` SOAP endpoint path appended to the base URL. string Yes
`useSoapContext` Whether to wrap the request using the SOAP context.
Default: `true`
boolean Yes
Request parameters to send as query, body, or header values.
Field Description Type Required
`arrayFormat` How array values are serialized in the query string: repeat, brackets, comma, or stringify.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`condition` A JEXL expression that includes the parameter only when it evaluates true. string No
`in` Where to send the parameter: query, body, or headers.
Allowed: `query`, `body`, `headers`
enum Yes
`name` Name of the request parameter. string Yes
`value` Value of the parameter. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`type` Selects no authentication. string Yes
Field Description Type Required
`encoding` Encoding applied to the username and password, such as base64. string No
`password` Password for basic authentication. string No
`type` Selects HTTP basic authentication. string Yes
`username` Username for basic authentication. string No
Field Description Type Required
`includeBearer` Whether to prefix the token with `Bearer ` in the header. Defaults to true.
Default: `true`
boolean Yes
`token` Bearer token sent with the request. string Yes
`type` Selects bearer token authentication. string Yes
Field Description Type Required
`includeBearer` Whether to prefix the token with `Bearer ` in the header. Defaults to true.
Default: `true`
boolean Yes
`token` OAuth 2.0 access token sent with the request. string Yes
`type` Selects OAuth 2.0 authentication. string Yes
Pagination position carried over from the previous page request.
Field Description Type Required
`position` How far into the previous page was read, so this request resumes from there. union No
`token` Cursor token from the previous page used to fetch the next one. union No
Remaps provider error responses to different statuses or messages. Useful for GraphQL APIs that return errors with a 200 status, normalizing provider-specific error formats, and giving AI agents clearer error messages.
Field Description Type Required
`condition` A JEXL expression that applies the remap only when it evaluates true. string No
`message` Error message to return in place of the provider's. string No
`receivedStatus` Provider HTTP status code to match. number Yes
`targetStatus` HTTP status code to return in place of the matched one. number Yes
Controls how subsequent pages are requested.
Field Description Type Required
`in` Where the pagination field is sent: query or body.
Allowed: `query`, `body`
enum Yes
`key` Request field name that carries the page token or number. string Yes
XML namespace declarations added to the SOAP envelope.
Field Description Type Required
`namespace` Namespace URI bound to the prefix. string Yes
`namespaceIdentifier` XML namespace prefix. string Yes
Controls how each page response is parsed and paginated.
Field Description Type Required
`collection` Currently not in use. boolean No
`dataKey` Path to the records array within the response. string No
`indexField` Field used to key results when returning an indexed map. string No
`nextKey` Path to the next-page token or cursor in the response. string No
`nextKeyIn` Where the next-page token is read from: the response data or headers.
Allowed: `data`, `headers`
enum No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="soap_paginated_request" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` Records accumulated across the fetched pages. any No
`message` Status or error message from the response. string No
`next` Cursor token for the next page. Null means the next request continues from `position` in the current page, and it is omitted when no pages remain. union No
`position` How far into the current page has been read, saved in the cursor so the next request resumes from there. number No
`raw` The raw provider response before parsing. any No
`statusCode` HTTP status code of the provider response. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="soap_paginated_request" version="v1" kind="output" */}
# soap_request Source: https://docs.stackone.com/connector-yaml-reference/step-functions/soap-request Step function: soap_request Sends a SOAP request to the provider and returns the parsed response. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="soap_request" */} ## Input
Field Description Type Required
[`args`](#args) Request parameters to send as query, body, or header values. object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Overrides the connector's base URL for the SOAP service. string No
[`customErrors`](#customerrors) Remaps matching provider error responses to different statuses or messages. object[] No
`encodeQueryParams` Whether to URL-encode query parameter values before sending. boolean No
`envelope` SOAP envelope template, as a string or object, used to build the request body. union No
`method` HTTP method to use for the SOAP call, typically post.
Allowed: `get`, `post`, `put`, `delete`, `patch`
enum Yes
[`namespaces`](#namespaces) XML namespace declarations added to the SOAP envelope. object[] No
[`response`](#response) Controls how the raw response is parsed into step output data. object No
`soapAction` Value sent in the SOAPAction HTTP header. string No
`soapOperation` Name of the SOAP operation to invoke. string No
`url` SOAP endpoint path appended to the base URL. string Yes
`useSoapContext` Whether to wrap the request using the SOAP context.
Default: `true`
boolean Yes
Request parameters to send as query, body, or header values.
Field Description Type Required
`arrayFormat` How array values are serialized in the query string: repeat, brackets, comma, or stringify.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`condition` A JEXL expression that includes the parameter only when it evaluates true. string No
`in` Where to send the parameter: query, body, or headers.
Allowed: `query`, `body`, `headers`
enum Yes
`name` Name of the request parameter. string Yes
`value` Value of the parameter. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
Remaps provider error responses to different statuses or messages. Useful for GraphQL APIs that return errors with a 200 status, normalizing provider-specific error formats, and giving AI agents clearer error messages.
Field Description Type Required
`condition` A JEXL expression that applies the remap only when it evaluates true. string No
`message` Error message to return in place of the provider's. string No
`receivedStatus` Provider HTTP status code to match. number Yes
`targetStatus` HTTP status code to return in place of the matched one. number Yes
XML namespace declarations added to the SOAP envelope.
Field Description Type Required
`namespace` Namespace URI bound to the prefix. string Yes
`namespaceIdentifier` XML namespace prefix. string Yes
Controls how the raw response is parsed into step output data.
Field Description Type Required
`collection` Whether to treat the response payload as a collection of records to index. boolean No
`dataKey` Top-level response key holding the records to extract. string No
`indexField` Field used to key results when returning an indexed map. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="soap_request" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The parsed response payload extracted from the SOAP response. any No
`message` Status or error message from the response. string No
`raw` The raw provider response before parsing. any No
`statusCode` HTTP status code of the provider response. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="soap_request" version="v1" kind="output" */}
# static_values Source: https://docs.stackone.com/connector-yaml-reference/step-functions/static-values Step function: static_values Returns fixed values, or the result of an expression. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="static_values" */} ## Input
Field Description Type Required
`values` Static values to return, as an object, an array, or an expression string. union Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="static_values" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The static values returned by the step. any Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="static_values" version="v1" kind="output" */}
# typecast Source: https://docs.stackone.com/connector-yaml-reference/step-functions/typecast Step function: typecast Converts fields in source data to their declared types. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="typecast" */} ## Input
Field Description Type Required
`dataSource` Reference to the source data to cast. string Yes
`fields` Definitions of the fields to cast. array No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="typecast" version="v2" kind="input" */}
## Output
Field Description Type Required
`data` The source data with fields cast to their target types. any Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="typecast" version="v2" kind="output" */}
# upload_binary Source: https://docs.stackone.com/connector-yaml-reference/step-functions/upload-binary Step function: upload_binary Uploads raw binary content to the provider. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="upload_binary" */} ## Input
Field Description Type Required
[`args`](#args) Additional request parameters (query params, headers) object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Overrides the connector's base URL for the upload. string No
[`binaryContent`](#binarycontent) Raw binary content for octet-stream uploads object Yes
[`customErrors`](#customerrors) Remaps matching provider error responses to different statuses or messages. object[] No
`method` HTTP method to use for the upload.
Allowed: `get`, `post`, `put`, `delete`, `patch`
Default: `post`
enum Yes
[`response`](#response) Controls how the raw response is parsed into step output data. object No
`url` Upload endpoint path appended to the base URL. string Yes
Additional request parameters (query params, headers)
Field Description Type Required
`arrayFormat` How array values are serialized in the query string: repeat, brackets, comma, or stringify.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`condition` A JEXL expression that includes the parameter only when it evaluates true. string No
`in` Where to send the parameter: query, body, or headers.
Allowed: `query`, `body`, `headers`
enum Yes
`name` Name of the request parameter. string Yes
`spread` Merges the value's object entries into the target location instead of setting a single named field. boolean No
`value` Value of the parameter. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
Raw binary content for octet-stream uploads
Field Description Type Required
`content` The file content as base64 encoded string string Yes
`contentType` The MIME type for the binary content (defaults to application/octet-stream) string No
Remaps provider error responses to different statuses or messages. Useful for GraphQL APIs that return errors with a 200 status, normalizing provider-specific error formats, and giving AI agents clearer error messages.
Field Description Type Required
`condition` A JEXL expression that applies the remap only when it evaluates true. string No
`message` Error message to return in place of the provider's. string No
`receivedStatus` Provider HTTP status code to match. number Yes
`targetStatus` HTTP status code to return in place of the matched one. number Yes
Controls how the raw response is parsed into step output data.
Field Description Type Required
`collection` Whether to treat the response payload as a collection of records to index. boolean No
`dataKey` Top-level response key holding the records to extract. string No
`indexField` Field used to key results when returning an indexed map. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="upload_binary" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The parsed response payload from the upload. any No
`message` Status or error message from the response. string No
`raw` The raw provider response before parsing. any No
`statusCode` HTTP status code of the provider response. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="upload_binary" version="v1" kind="output" */}
# upload_file Source: https://docs.stackone.com/connector-yaml-reference/step-functions/upload-file Step function: upload_file Uploads a file to the provider as a multipart form. {/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionDescription name="upload_file" */} ## Input
Field Description Type Required
[`additionalFields`](#additionalfields) Additional form fields to include in the multipart request object[] No
[`args`](#args) Additional request parameters (query params, headers) object[] No
[`authorization`](#authorization) Overrides the connector's default authentication for this request. union No
`baseUrl` Overrides the connector's base URL for the upload. string No
[`customErrors`](#customerrors) Remaps matching provider error responses to different statuses or messages. object[] No
[`file`](#file) The file to upload object Yes
`method` HTTP method to use for the upload.
Allowed: `get`, `post`, `put`, `delete`, `patch`
Default: `post`
enum Yes
[`response`](#response) Controls how the raw response is parsed into step output data. object No
`url` Upload endpoint path appended to the base URL. string Yes
Additional form fields to include in the multipart request
Field Description Type Required
`condition` A JEXL expression that includes the field only when it evaluates true. string No
`contentType` The MIME type for this form field (e.g., "application/json") string No
`name` Name of the form field. string Yes
`value` Value of the form field. any Yes
Additional request parameters (query params, headers)
Field Description Type Required
`arrayFormat` How array values are serialized in the query string: repeat, brackets, comma, or stringify.
Allowed: `repeat`, `brackets`, `comma`, `stringify`
enum No
`condition` A JEXL expression that includes the parameter only when it evaluates true. string No
`in` Where to send the parameter: query, body, or headers.
Allowed: `query`, `body`, `headers`
enum Yes
`name` Name of the request parameter. string Yes
`spread` Merges the value's object entries into the target location instead of setting a single named field. boolean No
`value` Value of the parameter. Supports expressions. any Yes
Overrides the connector's default authentication for this request.
Field Description Type Required
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
[`signing`](#authorization-none-signing) Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing. union No
`type` Sends requests without an authorization header. string Yes
Optional request signing applied to outgoing requests. Selects AWS SigV4 or HMAC signing.
Field Description Type Required
`region` AWS region used in the signing credential scope. Falls back to the credential region or `us-east-1` when omitted. string No
`service` AWS service name used in the signing credential scope. For example `s3` or `execute-api`. string Yes
`strategy` Signs requests with AWS Signature Version 4. string Yes
Field Description Type Required
`algorithm` Hash algorithm for the HMAC signature. Defaults to `sha256`.
Allowed: `sha1`, `sha256`, `sha512`
enum No
`dateFormat` Timestamp format used in the signed string. Either `iso8601` (default) or `rfc2822`.
Allowed: `iso8601`, `rfc2822`
enum No
`headerName` Header the signature is written into. Defaults to `X-Signature`. string No
`includeBodyHash` Hash the request body into the signed string, defaulting to `true`. When `false`, form-urlencoded body params are folded into the canonical string instead. boolean No
`includeHost` Include the request hostname in the signed canonical string. Defaults to `false`. boolean No
`outputFormat` Where the signature is emitted. `header` writes a signature header and `basic` writes an HTTP Basic `Authorization` header.
Allowed: `header`, `basic`
enum No
`prefix` Prefix prepended to the signature value in the header. Defaults to `hmac-<algorithm>`. string No
`strategy` Signs requests with an HMAC signature over a canonical request string. string Yes
`username` Username paired with the signature when `outputFormat` is `basic`. string No
Field Description Type Required
`encoding` Encoding applied to the `username:password` pair. Defaults to `base64`. string No
`password` Password for HTTP Basic authentication. string No
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`type` Configures HTTP Basic authentication. string Yes
`username` Username for HTTP Basic authentication. string No
Field Description Type Required
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`redirectUri` OAuth callback URL carried as connect-time metadata. Not used when authorizing requests. string No
`token` Token sent on each request. Supports expressions. string Yes
`type` Configures bearer token authentication. string Yes
Field Description Type Required
`additionalTokenFields` Extra credential fields to read from the token endpoint response. Each key is a credential name and each value an expression. object No
`authorizationParams` Extra query parameters appended to the authorization URL. Values support expressions. object No
`authorizationUrl` Provider authorization endpoint where the user grants access. string No
`callbackParams` Maps OAuth callback query parameter names to the credential keys their values are stored under. Cannot target reserved credential keys. object No
`customHeaders` Additional HTTP headers sent with token endpoint requests. object No
`includeBearer` Prefix the token with `Bearer ` in the `Authorization` header. Defaults to `true`.
Default: `true`
boolean Yes
`issuer` OpenID Connect issuer identifier for the provider. string No
`pkce` Enable PKCE for the authorization code flow. boolean No
`redirectUri` Overrides the OAuth callback URL. The computed callback URL can be seen on the connector profile. string No
`scopeDelimiter` Delimiter used to separate scopes when requesting authorization. string No
`scopes` OAuth scopes requested during authorization. string No
`token` Expression that resolves the access token sent on each request. string Yes
`tokenExpiresIn` Access token lifetime in seconds. number No
`tokenParams` Extra parameters sent to the token endpoint. Values support expressions. object No
`tokenRefreshExpiresIn` Refresh token lifetime in seconds. number No
[`tokenResponse`](#authorization-oauth2-tokenresponse) Adjusts how a non-standard token endpoint response is parsed. object No
`tokenUrl` Provider token endpoint used to exchange the authorization code and to refresh tokens. string No
`type` Configures OAuth 2.0 authentication. string Yes
Adjusts how a non-standard token endpoint response is parsed.
Field Description Type Required
`acceptTokenTypes` Allowlist of `token_type` values to accept from the token endpoint beyond `Bearer` and `DPoP`. Matched case-insensitively. string[] No
`accessToken` Expression locating the access token in the token endpoint response. Takes precedence over the standard `access_token` field when it resolves to a non-empty string. string No
`refreshToken` Expression locating the refresh token in the token endpoint response. Takes precedence over the standard `refresh_token` field when it resolves to a non-empty string. string No
Remaps provider error responses to different statuses or messages. Useful for GraphQL APIs that return errors with a 200 status, normalizing provider-specific error formats, and giving AI agents clearer error messages.
Field Description Type Required
`condition` A JEXL expression that applies the remap only when it evaluates true. string No
`message` Error message to return in place of the provider's. string No
`receivedStatus` Provider HTTP status code to match. number Yes
`targetStatus` HTTP status code to return in place of the matched one. number Yes
The file to upload
Field Description Type Required
`content` The file content as base64 encoded string string Yes
`contentType` The MIME type of the file (e.g., "image/png", "application/pdf") string No
`fieldName` The form field name for the file string Yes
`filename` The filename to use in the upload string Yes
Controls how the raw response is parsed into step output data.
Field Description Type Required
`collection` Whether to treat the response payload as a collection of records to index. boolean No
`dataKey` Top-level response key holding the records to extract. string No
`indexField` Field used to key results when returning an indexed map. string No
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="upload_file" version="v1" kind="input" */}
## Output
Field Description Type Required
`data` The parsed response payload from the upload. any No
`message` Status or error message from the response. string No
`raw` The raw provider response before parsing. any No
`statusCode` HTTP status code of the provider response. number Yes
{/* AUTO-GENERATED by docs/scripts/schema-reference/expand-mdx.ts. Do not edit by hand. */} {/* schema-reference: StepFunctionParams name="upload_file" version="v1" kind="output" */}
# Expression Language Source: https://docs.stackone.com/connector-yaml-reference/expression-language Complete reference for JSONPath, JEXL, and string interpolation expressions in connector YAML StackOne uses the [`@stackone/expressions`](https://www.npmjs.com/package/@stackone/expressions) library to evaluate dynamic values throughout connector YAML files. Three expression formats are available, each suited to different use cases. ## Expression Formats (`$.path`) - Directly accessing values - No transformation needed - Can use value as returned (`${...}`) - Building strings/URLs - Concatenating with static text - Simple variable substitution (`'{{...}}'`) - Setting default values (`??` operator) - Conditional Logic - Complex transformations | Scenario | Format | Example | |----------|--------|---------| | Access a credential value | JSONPath | `$.credentials.apiKey` | | Access an input parameter | JSONPath | `$.inputs.userId` | | Reference step output | JSONPath | `$.steps.fetch.output.data` | | Build a URL with parameters | String Interpolation | `/users/${inputs.id}` | | Dynamic base URL | String Interpolation | `https://${credentials.subdomain}.api.com` | | Provide a default value | JEXL | `'{{inputs.limit ?? 100}}'` | | Conditional argument | JEXL | `'{{present(inputs.filter)}}'` | | Ternary logic | JEXL | `'{{x > 0 ? x : 0}}'` | | String concatenation with logic | JEXL | `'{{inputs.first + " " + inputs.last}}'` | | Enum matching | JEXL | `'{{$.status == "ACTIVE"}}'` | ## JSONPath Expressions When an expression starts with `$`, it is treated as a JSONPath expression. Use this for direct data access without transformation. ### Syntax | Operator | Description | Example | |----------|-------------|---------| | `$` | Root object | `$.user.name` | | `.` | Child operator | `$.user.name` | | `@` | Current object (in filters) | `@.age` | | `*` | Wildcard: all elements/properties | `$.users[*]` | | `..` | Recursive descent | `$..name` | | `[]` | Subscript | `$.users[0]` | | `[,]` | Union | `$.users[0,2]` | | `[start:end:step]` | Array slice | `$.users[0:2]` | | `[?(expression)]` | Filter expression | `$.users[?(@.age > 30)]` | | `()` | Script expression | Custom expressions | ### Available Contexts | Context | Description | Example | |---------|-------------|---------| | `$.credentials` | Authentication credentials | `$.credentials.apiKey` | | `$.inputs` | Action input parameters | `$.inputs.userId` | | `$.context` | Connection context, such as `environment` and `authenticationType` | `$.context.environment` | | `$.steps.{stepId}.output` | Previous step output | `$.steps.fetch_users.output.data` | | `$.iterator` | Current foreach iteration context | `$.iterator.item` | | `$.result` | The action's assembled result | `$.result.id` | **Examples** ```yaml # Simple value access token: $.credentials.apiKey value: $.inputs.employee_id # Step output dataSource: $.steps.fetch_users.output.data # Nested access expression: $.user.address.city # Bracket notation (for keys with special characters) value: $["info/email"] # Array access value: $.steps.get_all_employees.output.data.employees[0].id # Wildcard iterator: $.steps.get_all_employees.output.data.employees[*].id ``` For more details on JSONPath syntax, refer to the [JSONPath specification](https://goessner.net/articles/JsonPath/). ## String Interpolation Use `${...}` syntax to embed values within strings. This is the preferred method for building URLs, composing strings, and simple variable substitution. ### Syntax ``` ${variable.path} ``` The content inside `${...}` supports the same dot-notation paths as JSONPath but without the `$` root prefix. **Examples** ```yaml # URL path parameters url: /users/${inputs.id} url: /users/${inputs.userId}/posts/${inputs.postId} # Dynamic base URLs baseUrl: https://${credentials.subdomain}.api.provider.com baseUrl: https://api.${credentials.region}.provider.com/v2 # OAuth callback URLs redirect_uri: ${apiHostUri}/connect/oauth2/${connector}/callback # Composing strings value: Bearer ${credentials.accessToken} ``` String interpolation only substitutes values. It does not support operators, conditionals, or function calls. Use JEXL expressions for logic. ## JEXL Expressions JEXL (JavaScript Expression Language) expressions are enclosed in double curly brackets `{{expression}}` and support variables, operators, functions, and conditional logic. In YAML, these must be wrapped in single quotes: `'{{...}}'`. ### Operators #### Arithmetic | Operator | Description | Example | Result | |----------|-------------|---------|--------| | `+` | Addition / string concatenation | `{{x + y}}` | `15` | | `-` | Subtraction | `{{x - y}}` | `5` | | `*` | Multiplication | `{{x * 2}}` | `20` | | `/` | Division | `{{x / y}}` | `2` | | `//` | Floor division | `{{7 // 2}}` | `3` | | `%` | Modulus | `{{x % 3}}` | `1` | | `^` | Exponentiation | `{{2 ^ 3}}` | `8` | #### Comparison | Operator | Description | Example | Result | |----------|-------------|---------|--------| | `==` | Equal | `{{x == 10}}` | `true` | | `!=` | Not equal | `{{x != y}}` | `true` | | `>` | Greater than | `{{x > y}}` | `true` | | `>=` | Greater than or equal | `{{x >= 10}}` | `true` | | `<` | Less than | `{{x < 100}}` | `true` | | `<=` | Less than or equal | `{{x <= 10}}` | `true` | | `in` | Element of string or array | `{{x in [1, 2, 3]}}` | `false` | #### Logical | Operator | Description | Example | |----------|-------------|---------| | `!` | Logical NOT | `{{!active}}` | | `&&` | Logical AND | `{{x > 5 && y < 10}}` | | `\|\|` | Logical OR | `{{x < 5 \|\| y > 10}}` | #### Special | Operator | Description | Example | |----------|-------------|---------| | `? :` | Ternary operator | `{{x > 10 ? "big" : "small"}}` | | `??` | Nullish coalescing | `{{x ?? "default"}}` | ### Identifiers and Context Access Access variables from the evaluation context using dot notation: ```yaml # Given context: { name: { first: "John" }, jobs: ["Developer", "Designer"] } '{{name.first}}' # "John" '{{jobs[1]}}' # "Designer" ``` ### Collection Filtering Filter arrays using bracket expressions: ```yaml # Given context: { users: [{ name: "John", age: 30 }, { name: "Jane", age: 25 }] } '{{users[.name == "John"].age}}' # 30 '{{users[.age > 25].name}}' # ["John"] ``` ### Common Patterns in Connector YAML ```yaml # Conditional argument inclusion condition: '{{present(inputs.filter)}}' # Default values value: '{{inputs.limit || 100}}' value: '{{$.inputs.status ?? "active"}}' # Ternary logic value: '{{$.count > 0 ? $.count : 0}}' # String concatenation expression: '{{$.first_name + " " + $.last_name}}' # Null checking with fallback value: '{{present(inputs.cursor) ? inputs.cursor : null}}' # Complex conditionals condition: '{{present(inputs.start_date) && present(inputs.end_date)}}' ``` ### Conditional Arguments Within a step's `args`, attach a `condition` to include an argument only when the condition evaluates to `true`. The most common use of JEXL in connector YAML is omitting optional query parameters, body fields, or headers when the corresponding input is absent. ```yaml args: - name: filter value: '{{inputs.filter}}' in: query condition: '{{present(inputs.filter)}}' - name: updated_since value: $.inputs.updated_after in: query condition: '{{present(inputs.updated_after)}}' - name: include_inactive value: "true" in: query condition: '{{inputs.include_inactive == true}}' ``` --- ## JEXL Functions The expression engine includes a set of built-in functions available in JEXL expressions. ### Presence & Type Checking #### `present(value)` Returns `true` if the value is not null or undefined. This is the most commonly used function in connector YAML for conditional argument inclusion. ```yaml # Include query param only if provided condition: '{{present(inputs.filter)}}' condition: '{{present(inputs.cursor)}}' # Check step output exists condition: '{{present(steps.fetch_data.output.data)}}' ``` | Input | Result | |-------|--------| | `present("hello")` | `true` | | `present(0)` | `true` | | `present([])` | `true` | | `present({})` | `true` | | `present(null)` | `false` | | `present(undefined)` | `false` | #### `missing(value)` Returns `true` if the value is null or undefined. The inverse of `present()`. ```yaml condition: '{{missing(inputs.optional_field)}}' ``` ### String Functions #### `capitalize(value, mode?)` Capitalizes characters in a string. By default capitalizes the first character; use `'each'` mode to capitalize each word. ```yaml value: '{{capitalize(inputs.name)}}' # "john" → "John" value: '{{capitalize(inputs.name, "each")}}' # "john doe" → "John Doe" ``` #### `truncate(value, maxLength, suffix?)` Truncates a string to a maximum length, appending a suffix (default `"..."`). ```yaml value: '{{truncate(inputs.description, 100)}}' # Truncate to 100 chars with "..." value: '{{truncate(inputs.title, 50, "…")}}' # Custom suffix value: '{{truncate(inputs.note, 80, "")}}' # No suffix ``` #### `padStart(value, targetLength, padString?)` Pads the start of a string to reach a target length. Numbers are converted to strings automatically. ```yaml value: '{{padStart(inputs.id, 8, "0")}}' # "42" → "00000042" value: '{{padStart(5, 3, "0")}}' # 5 → "005" ``` #### `encodeBase64(value)` Encodes a string to Base64. ```yaml value: '{{encodeBase64(credentials.apiKey + ":" + credentials.secret)}}' ``` #### `decodeBase64(value)` Decodes a Base64 string. ```yaml value: '{{decodeBase64(inputs.encoded_data)}}' ``` #### `regexMatch(value, pattern, groupIndex?)` Extracts a value from a string using a regular expression. Returns the specified capture group (default: `1`) or `null` if no match. ```yaml # Extract cursor from Link header value: '{{regexMatch(steps.request.output.headers.link, "after=([^&>]+)", 1)}}' # Extract numeric ID value: '{{regexMatch(inputs.reference, "user_id=(\\d+)", 1)}}' # Full match (group 0) value: '{{regexMatch(inputs.text, "World", 0)}}' ``` #### `upper(value)` / `lower(value)` Uppercase or lowercase a string. Returns an empty string for non-string input. ```yaml value: '{{upper(inputs.code)}}' # "abc" → "ABC" value: '{{lower(credentials.subdomain)}}' # "MyOrg" → "myorg" ``` #### `replace(value, search, replacement, replaceAll?)` Replaces occurrences of a substring. By default replaces only the first; pass `true` as the fourth argument to replace all. ```yaml value: '{{replace(inputs.path, " ", "_")}}' # first occurrence value: '{{replace(inputs.path, "-", "_", true)}}' # all occurrences ``` #### `split(value, separator?)` Splits a string into an array (default separator `","`). Returns an empty array for non-string input. ```yaml value: '{{split(inputs.fields)}}' # "a,b,c" → ["a", "b", "c"] value: '{{split(inputs.tags, " ")}}' # "a b c" → ["a", "b", "c"] ``` #### `asString(value)` Converts any value to its string representation (objects/arrays are JSON-stringified). Returns `""` for null/undefined. ```yaml value: '{{asString(inputs.count)}}' # 42 → "42" value: '{{asString(inputs.filter)}}' # { a: 1 } → '{"a":1}' ``` #### `decodeUri(value)` Decodes a URI-encoded string (percent-decoding). Useful for pre-encoded values like pagination cursors that would otherwise be double-encoded. ```yaml value: '{{decodeUri(steps.request.output.data.next_cursor)}}' # "a%3Db" → "a=b" ``` #### `urlParam(url, paramName)` Extracts a query-parameter value from a URL string. Returns `null` if the param is absent or inputs are invalid. ```yaml # Pull the next page number out of a `next` URL value: '{{urlParam(steps.request.output.data.paging.next, "page")}}' ``` | Input | Result | |-------|--------| | `urlParam("https://api.x.com/items?page=2&limit=10", "page")` | `"2"` | | `urlParam("https://api.x.com/items?page=2", "missing")` | `null` | ### Crypto Functions #### `sha256(value, encoding?)` Computes the SHA-256 hash of a string. Useful for request signing and content verification. - `value` (string): The string to hash - `encoding` (string, optional): `'hex'` (default) or `'base64'` - Returns: hash string, or empty string for invalid input ```yaml value: '{{sha256(inputs.body)}}' value: '{{sha256(inputs.body, "base64")}}' ``` | Input | Result | |-------|--------| | `sha256("hello")` | `"2cf24dba5fb0a30e..."` (64-char hex) | | `sha256("hello", "base64")` | `"LPJNul+wow4m6Dsq..."` (base64) | | `sha256(null)` | `""` | #### `hmacSha256(value, key, encoding?)` Computes an HMAC-SHA256 signature using a secret key. Used for webhook signature verification and API request signing. - `value` (string): The string to sign - `key` (string): The secret key - `encoding` (string, optional): `'hex'` (default) or `'base64'` - Returns: HMAC digest, or empty string for invalid input ```yaml value: '{{hmacSha256(inputs.body, credentials.signingSecret)}}' value: '{{hmacSha256(inputs.body, credentials.signingSecret, "base64")}}' ``` | Input | Result | |-------|--------| | `hmacSha256("hello", "secret")` | `"88aab3ede8d3adf9..."` (64-char hex) | | `hmacSha256("hello", "secret", "base64")` | base64-encoded HMAC | | `hmacSha256(null, "secret")` | `""` | | `hmacSha256("hello", null)` | `""` | #### `md5(value, encoding?)` Computes the MD5 hash of a string. - `value` (string): The string to hash - `encoding` (string, optional): `'hex'` (default) or `'base64'` - Returns: hash string, or empty string for invalid input ```yaml value: '{{md5(inputs.body)}}' value: '{{md5(inputs.body, "base64")}}' ``` | Input | Result | |-------|--------| | `md5("hello")` | `"5d41402abc4b2a76b9719d911017c592"` | | `md5("hello", "base64")` | `"XUFAKrxLKna5cZ2REBfFkg=="` | | `md5(null)` | `""` | --- ### Array Functions #### `includes(array, value)` Checks if an array includes a value. If `value` is an array, checks that ALL values are included. ```yaml condition: '{{includes(inputs.roles, "admin")}}' condition: '{{includes(inputs.scopes, ["read", "write"])}}' # All must match ``` #### `includesSome(array, value)` Checks if an array includes AT LEAST ONE of the given values. ```yaml condition: '{{includesSome(inputs.tags, ["urgent", "critical"])}}' ``` #### `dedupe(array)` Removes duplicate entries from an array, preserving order. Works with primitives and objects (compared by content with sorted keys). ```yaml value: '{{dedupe(steps.merge_data.output.data.ids)}}' ``` | Input | Result | |-------|--------| | `dedupe([1, 2, 2, 3, 1])` | `[1, 2, 3]` | | `dedupe(["a", "b", "a"])` | `["a", "b"]` | | `dedupe([{id: 1}, {id: 2}, {id: 1}])` | `[{id: 1}, {id: 2}]` | #### `join(array, separator?)` Joins array elements into a string with a separator (default: `","`). Filters out null/undefined values. ```yaml value: '{{join(inputs.fields, ",")}}' value: '{{join(inputs.tags, " - ")}}' value: '{{join(["first", "last"], " ")}}' ``` | Input | Result | |-------|--------| | `join(["a", "b", "c"])` | `"a,b,c"` | | `join(["a", "b"], " - ")` | `"a - b"` | | `join(["a", null, "b"])` | `"a,b"` | | `join(["a", "b", "c"], "")` | `"abc"` | #### `reduce(array, operation, field?)` Applies an aggregate operation to an array. When `field` is specified, that field is extracted from each object before applying the operation. Supported operations: | Operation | Description | |-----------|-------------| | `"sum"` | Adds all numeric values | | `"avg"` | Averages all numeric values | | `"count"` | Returns the number of items | | `"min"` | Returns the smallest numeric value | | `"max"` | Returns the largest numeric value | | `"concat"` | Extracts an array field from each object (requires `field`) and concatenates the results into a single flat array | | `"flatten"` | Flattens one level of nesting when the array elements are themselves arrays (no `field` needed) | ```yaml # Sum an array of numbers value: '{{reduce([1, 2, 3], "sum")}}' # 6 # Sum a field across objects value: '{{reduce(steps.fetch.output.data.items, "sum", "price")}}' # Average a field across objects value: '{{reduce(steps.fetch.output.data.scores, "avg", "value")}}' # 85 # Count items value: '{{reduce(steps.fetch.output.data.records, "count")}}' # Concatenate nested arrays from a field value: '{{reduce(steps.fetch.output.data.items, "concat", "tags")}}' # ["a", "b", "c"] # Flatten an array of arrays (no field required) value: '{{reduce([[1, 2], [3, 4]], "flatten")}}' # [1, 2, 3, 4] ``` | Input | Result | |-------|--------| | `reduce([1, 2, 3], "sum")` | `6` | | `reduce([{v: 10}, {v: 20}], "sum", "v")` | `30` | | `reduce([{v: 80}, {v: 90}], "avg", "v")` | `85` | | `reduce([1, 2, 3], "count")` | `3` | | `reduce([{v: 1}, {v: 3}], "max", "v")` | `3` | | `reduce([{t: ["a"]}, {t: ["b"]}], "concat", "t")` | `["a", "b"]` | | `reduce([[1, 2], [3, 4]], "flatten")` | `[1, 2, 3, 4]` | | `reduce(null, "sum")` | `null` | #### `min(...values)` Returns the smallest number from the arguments. Accepts either individual values or a single array. Returns `null` when no valid numbers are provided. ```yaml value: '{{min(inputs.page_size, 100)}}' # cap page size at 100 value: '{{min(steps.fetch.output.data.prices)}}' # smallest of an array ``` | Input | Result | |-------|--------| | `min(1, 2, 3)` | `1` | | `min([5, 2, 8])` | `2` | | `min(42)` | `42` | ### Object Functions #### `keys(object)` Returns the keys of an object as an array. Returns empty array for non-objects. ```yaml value: '{{keys(steps.fetch_data.output.data.metadata)}}' ``` #### `values(object)` Returns the values of an object as an array. Returns empty array for non-objects. ```yaml value: '{{values(steps.fetch_data.output.data.attributes)}}' ``` #### `zipObject(keys, values)` Combines two parallel arrays into an object by pairing `keys[i]` with `values[i]`. If the arrays are different lengths, extra elements from the longer array are ignored. Non-string keys are skipped. Returns `{}` if either input is missing or not an array. ```yaml # Build an object from field names and values value: '{{zipObject(steps.fetch.output.data.fields, steps.fetch.output.data.values)}}' # Combine static keys with dynamic values value: '{{zipObject(["name", "email"], [inputs.name, inputs.email])}}' ``` | Input | Result | |-------|--------| | `zipObject(["a", "b"], [1, 2])` | `{a: 1, b: 2}` | | `zipObject(["name", "email"], ["John", "john@example.com"])` | `{name: "John", email: "john@example.com"}` | | `zipObject(["a", "b", "c"], [1, 2])` | `{a: 1, b: 2}` | | `zipObject([], [])` | `{}` | | `zipObject(null, [1, 2])` | `{}` | #### `groupBy(array, key)` Array utility that groups items but returns an object result; it's documented here alongside object helpers for convenience (see the Array Functions section for related utilities). Groups an array of objects by the value of a specified key, producing an object where each unique key value maps to an array of matching items. Items without the key or with a null/undefined value for that key are collected under `"__missing__"`. Returns `{}` if the input is missing, not an array, or the key is not a string. ```yaml # Group employees by department value: '{{groupBy(steps.fetch.output.data.employees, "department")}}' # Group by status value: '{{groupBy(steps.fetch.output.data.records, "status")}}' ``` | Input | Result | |-------|--------| | `groupBy([{dept: "eng", name: "Alice"}, {dept: "hr", name: "Bob"}, {dept: "eng", name: "Carol"}], "dept")` | `{eng: [{...}, {...}], hr: [{...}]}` | | `groupBy([{status: "active"}, {status: "inactive"}, {status: "active"}], "status")` | `{active: [{...}, {...}], inactive: [{...}]}` | | `groupBy([{name: "Alice"}, {status: "active"}], "status")` | `{__missing__: [{name: "Alice"}], active: [{status: "active"}]}` | | `groupBy(null, "key")` | `{}` | #### `parseJson(value)` Parses a JSON string into its decoded value (object, array, or primitive). Returns `null` on missing/non-string/empty/invalid input. Useful when a provider delivers a field as a JSON-encoded string (e.g. inside a form-urlencoded webhook body). ```yaml # Decode a JSON-encoded `payload` form field from a webhook body value: '{{parseJson(inputs.payload)}}' ``` | Input | Result | |-------|--------| | `parseJson('{"id":"abc"}')` | `{ id: "abc" }` | | `parseJson('[1,2,3]')` | `[1, 2, 3]` | | `parseJson("not json")` | `null` | ### Date Functions Date-time values with no UTC offset are resolved in the host timezone. Prefer offset-bearing input (e.g. `...Z` or `+00:00`) when the exact instant matters. #### `now()` Returns the current date/time in ISO 8601 format. ```yaml value: '{{now()}}' # "2025-04-10T12:00:00.000Z" ``` #### `yearsElapsed(startDate, format, endDate?)` Calculates the number of complete years between two dates. If `endDate` is omitted, uses today. ```yaml value: '{{yearsElapsed(inputs.hire_date, "yyyy-MM-dd")}}' value: '{{yearsElapsed("2015-01-01", "yyyy-MM-dd", "2025-01-01")}}' # 10 ``` #### `hasPassed(date, format, yearsToAdd?)` Checks whether a date (optionally with years added) has already passed. ```yaml condition: '{{hasPassed(inputs.expiry_date, "yyyy-MM-dd")}}' condition: '{{hasPassed(inputs.start_date, "yyyy-MM-dd", 5)}}' # Has start + 5 years passed? ``` #### `nextAnniversary(initialDate, format)` Calculates the next anniversary of a date. ```yaml value: '{{nextAnniversary(inputs.hire_date, "dd/MM/yyyy")}}' ``` #### `deltaFromNowMs(dateInput, format?)` Calculates milliseconds between a date and now. Supports ISO strings (default), Unix timestamps (`'timestamp'`), and seconds (`'seconds'`). ```yaml value: '{{deltaFromNowMs(inputs.expires_at)}}' value: '{{deltaFromNowMs(inputs.timestamp, "timestamp")}}' ``` #### `unixToIso(value, unit?)` Converts a Unix epoch timestamp to an ISO-8601 date-time string. Accepts epoch `'seconds'` (default) or `'ms'`, as a number or numeric string. Returns `null` for non-numeric / out-of-range input. Useful when a provider returns epoch timestamps but the defined schema expects a date-time string. ```yaml value: '{{unixToIso(steps.fetch.output.data.created_at)}}' # seconds value: '{{unixToIso(steps.fetch.output.data.created_ms, "ms")}}' # milliseconds ``` | Input | Result | |-------|--------| | `unixToIso(1769518356)` | `"2026-01-27T12:52:36.000Z"` | | `unixToIso(1769518356722, "ms")` | `"2026-01-27T12:52:36.722Z"` | | `unixToIso("not-a-number")` | `null` | #### `isoToUnix(value, unit?)` The inverse of `unixToIso` — converts a date-time string to a Unix epoch timestamp. Returns epoch `'seconds'` (default, floored) or `'ms'`; `null` for unparsable input. ```yaml value: '{{isoToUnix(inputs.updated_at)}}' # → epoch seconds value: '{{isoToUnix(inputs.updated_at, "ms")}}' # → epoch milliseconds ``` #### `formatDate(value, formatString)` Formats a date-time value into a string using a token-based format. Output is rendered in UTC, so numeric offset tokens and instant fields are stable across host timezones. Accepts an ISO 8601 string (with or without offset) or one of these fallback formats: `yyyy-MM-dd`, `yyyy/MM/dd`, `dd/MM/yyyy`, `dd-MM-yyyy`, `yyyy-dd-MM`, `yyyy/dd/MM`, `MM/dd/yyyy`, `MM-dd-yyyy`. For epoch numbers, compose with `unixToIso` first. **Common tokens** | Token | Meaning | Example | |-------|---------|---------| | `yyyy` | 4-digit calendar year | `2026` | | `MM` | 2-digit month (01–12) | `01` | | `MMM` | Abbreviated month name | `Jan` | | `MMMM` | Full month name | `January` | | `dd` | 2-digit day of month | `27` | | `do` | Day of month, ordinal | `27th` | | `EEE` | Abbreviated weekday | `Tue` | | `EEEE` | Full weekday | `Tuesday` | | `HH` | Hour (00–23) | `12` | | `hh` | Hour (01–12) | `12` | | `mm` | Minutes (00–59) | `52` | | `ss` | Seconds (00–59) | `36` | | `SSS` | Milliseconds | `722` | | `a` | AM/PM marker | `PM` | | `xxx` | Numeric offset (`+00:00`) | `+00:00` | | `X` | Short offset (`Z` for UTC) | `Z` | | `'text'` | Literal text (wrap in single quotes) | `at` | ```yaml # Date only value: '{{formatDate(inputs.created_at, "yyyy-MM-dd")}}' # "2026-01-27" # SQL-style datetime value: '{{formatDate(inputs.created_at, "yyyy-MM-dd HH:mm:ss")}}' # "2026-01-27 12:52:36" # HTTP Date header (RFC 1123) value: '{{formatDate(inputs.created_at, "EEE, dd MMM yyyy HH:mm:ss ''GMT''")}}' # Format the current instant value: '{{formatDate(now(), "yyyy-MM-dd")}}' # today, e.g. "2026-01-27" # Compose with unixToIso for epoch input value: '{{formatDate(unixToIso(steps.fetch.output.data.created_at), "yyyy-MM-dd")}}' ``` | Input | Result | |-------|--------| | `formatDate("2026-01-27T12:52:36.722Z", "yyyy-MM-dd")` | `"2026-01-27"` | | `formatDate("2026-01-27T12:52:36.722Z", "HH:mm:ss")` | `"12:52:36"` | | `formatDate("2026-01-27T12:52:36.722Z", "EEE, dd MMM yyyy")` | `"Tue, 27 Jan 2026"` | | `formatDate("not-a-date", "yyyy-MM-dd")` | `null` | **Case matters.** Lowercase `mm` is minutes; uppercase `MM` is month (`yyyy-mm-dd` silently renders `"2026-52-27"`). Uppercase `YYYY`-`MM`-`DD` (the SQL/ISO convention) returns `null`. Use `yyyy-MM-dd` instead. For epoch timestamps, use `isoToUnix(value)` instead of the `t`/`T` tokens. ### Advanced Functions #### `parseJson`, XML & webhook helpers A few functions exist for specialized transport/webhook scenarios: | Function | Purpose | |----------|---------| | `wrapXmlArray(value, wrapperElement?, typeAttribute?)` | Wraps an array so it serializes correctly for XML APIs (used with SOAP/XML request bodies via `fast-xml-parser`). | | `webhookEventsUrl(webhooksUrl, orgId, projectSecureId, connectorProfileId, token?)` | Builds the StackOne events webhook URL (with a base64url-encoded routing context) for provisioning native provider webhooks. Used inside `events.setup` steps. | These appear in generated webhook setup and XML/SOAP connectors. ## Validation and Error Handling ### `isValidExpression(expression)` The expression engine validates syntax before evaluation. Invalid expressions return errors that help identify issues. ### Incremental JSONPath Errors When using the expression engine with `incrementalJsonPath: true`, detailed error messages are provided for JSON Path evaluation failures: ``` Key 'age' not found at '$.user.details'. Available keys: name ``` This is used internally by StackOne Agent for self-repair during connector development. ### Safe Evaluation The `safeEvaluate` function returns `null` instead of throwing errors, which is useful for optional expressions and fallback patterns. # Embed Source: https://docs.stackone.com/embed/overview Bring StackOne into your product or your agent. Embed StackOne in your product: ship integrations and agent actions to your own customers, under your brand. Your customers connect the tools they already use. Your product or agent acts on them. ## What are you building? I'm building an application and my customers need to connect the tools they already use. I'm building an agent and it needs to act on real business systems. ## Want to connect data to your agent? If you just need to connect data sources to your agent, you don't need any of the above. Start here. I want to connect my AI agent to a system I already use and run my first actions. # Getting Started Source: https://docs.stackone.com/embed/getting-started The path to embedding StackOne in your product, from setup to production. Bring StackOne into your own product: connect your users' accounts and call connector actions from your code. Here's the path end to end. Just exploring, or prefer a no-code route? Start with the [Quickstart](/gateway/quickstart) to connect your first connector from the dashboard. Create a project and an API key with the scopes **Actions** and **Platform API**. This **API key** will be used to authenticate all backend and API calls below. A Connector Profile configures a provider's authentication and the actions your users can use. This sets up a [**connector profile**](/gateway/concepts/connector-profiles) for the provider you chose (e.g. `hubspot`) — its authentication and enabled actions — which you target when creating a session. Instantiate a connect session on your backend to open the linking flow for a specific user. Using your **API key** and **provider** from the previous steps, this returns a short-lived **session token** for the frontend. Open the Hub or send an Auth Link so users connect their accounts. React to accounts being linked, updated, or disconnected. The Hub is initiated using the **session token**. Once a user links an account, the Hub returns its **account ID** (or you pick it up from the **account event**) for calling actions. Use the Agent SDK, MCP, A2A, or RPC/HTTP, whichever fits your stack. Every call uses your **API key** and the **account ID** from the previous step, selecting which [linked account](/gateway/concepts/linked-accounts) to act on. ## Before you go to production Your brand on the consent screen and dedicated rate limits. React to account and data changes. Inspect calls, debug failures, and watch rate limits. # API Keys Source: https://docs.stackone.com/embed/api-keys Generate and manage a StackOne API key from the dashboard. An API key authenticates every call your backend makes to StackOne. Keys are scoped to a single [project](/gateway/concepts/organizations-and-projects#projects). A key can only reach the connector profiles and linked accounts in the project it was created in. ## Generate an API key Log in to the [StackOne dashboard](https://app.stackone.com) and go to **Project Settings → API Keys** in the left navigation. API Keys management page Click **Create API key** and enter a name (e.g. `my-agent-key` or `production-hris-sync`). This label can't be changed later. Create API key dialog with scopes New keys come with a default set of scopes. Expand the **Scopes** section to enable or restrict access for your use case. The [scopes reference](#scopes) below lists what each scope allows. After clicking **Generate**, the key is shown **once**. Copy it immediately and store it securely. Store the key in a password manager or secrets vault. Never commit API keys to source control. ## Scopes An API key's scopes control what it can access. Set them when creating the key; new keys start with the defaults below. | Scope | Default | Grants | |-------|---------|--------| | **Platform API** | Read + Write | Account management, [connect sessions](/embed/connect-session), and connector profiles. Required for [Platform API](/platform-api/overview) operations such as StackOne Connect and account management. | | **Actions** | Execute | Interact with actions via RPC and MCP. | | **Connectors** | Read | Custom connector management. **Read** (`connectors:read`) downloads connectors from the registry; **Write** (`connectors:write`) pushes and deletes them. Required for [connector building](/connector-building/overview) operations. | | **Credentials** | Off | Retrieve stored credentials for direct provider access (read-only). Required for the StackOne CLI and running actions outside the platform. | | **Unified API** | Read + Write | All legacy (unified) endpoints (HRIS, ATS, CRM, LMS, etc.) for reading and writing data across connected providers. | For AI agents, you typically need: **Platform API Read** (list connected accounts), **Actions Execute** (RPC and MCP), **Connectors Read** (download connectors), and **Credentials Read** (direct provider access). ## Key management Your key appears in the **API Keys** table, where you can enable, disable, view scopes for, and delete keys at any time. Usage is tracked. The **Last used** column helps you spot stale keys to revoke. Review the list regularly. ## Next steps Use your key to create a session token and open the account-linking flow for a user. Return to the end-to-end embedding journey. # Connect Session Source: https://docs.stackone.com/embed/connect-session Generate connect session tokens from your backend so your end-users can link their accounts through the Hub. A **connect session** is a short-lived token that authorizes one of your end-users to link an account. Your backend creates it with your [API key](/embed/api-keys), so the key is never exposed to the frontend. **Prerequisites:** a StackOne [API key](/embed/api-keys), and a [connector profile](/gateway/quickstart#setup-connector-profile) enabled for the provider you're connecting. ## Create a session Call the [Connect Sessions endpoint](/platform/api-reference/connect-sessions/create-connect-session) from your backend. Two fields are **required**: - **`origin_owner_id`**: your identifier for the customer's organization - **`origin_owner_name`**: a human-readable name for that organization, stored against the account Always set `origin_owner_id` server-side. Never pass it through from a client-side request, or a customer could claim another customer's linked accounts. ```typescript TypeScript SDK import { StackOne } from "@stackone/stackone-client-ts"; const stackOne = new StackOne({ security: { username: process.env.STACKONE_API_KEY, password: "", }, }); app.post('/stackone_connect_sessions', async (req, res) => { const { originUsername, provider } = req.body; try { const result = await stackOne.connectSessions.createConnectSession({ originOwnerId: "customer-123", originOwnerName: "Acme Inc", originUsername: originUsername, provider, }); res.send({ token: result.connectSessionTokenAuthLink?.token }); } catch (e) { res.status(500).send('error when trying to fetch session'); } }); ``` ```python Python (HTTP) from flask import Flask, request, jsonify import requests import base64 app = Flask(__name__) @app.route('/stackone_connect_sessions', methods=['POST']) def stackone_connect_sessions(): STACKONE_API_KEY = 'YOUR_STACKONE_API_KEY' headers = { 'Authorization': 'Basic ' + base64.b64encode(f"{STACKONE_API_KEY}:".encode()).decode(), 'Content-Type': 'application/json', } req_data = request.json payload = { 'origin_owner_id': 'customer-123', 'origin_owner_name': 'Acme Inc', 'origin_username': req_data.get('originUsername'), 'provider': req_data.get('provider'), } try: response = requests.post( 'https://api.stackone.com/connect_sessions', headers=headers, json=payload ) token = response.json().get('token') return jsonify({'token': token}) except Exception as e: return ('error when trying to fetch session', 500) ``` Return the token to your frontend, where the Hub consumes it to start [account linking](/embed/account-linking/overview). ## New or existing account The `origin_owner_id` + `origin_owner_name` + `provider` combination decides whether a new account is created or an existing one is updated: | Combination seen before? | Result | |---|---| | No | New account created | | Yes | Existing account opened in edit mode | | Yes, with `account_id` | That specific account opened in edit mode | | Yes, with `multiple: true` (no `account_id`) | New account created regardless of existing ones | Use `multiple: true` when one customer needs several separate accounts for the same provider. It has no effect when `account_id` is set. To list a customer's linked accounts later, filter `GET /accounts` by `origin_owner_id`. See [Multi-Tenant Accounts](/features/multi-tenant-accounts). ## Target a specific connector profile Passing `provider` alone uses the project's [default connector profile](/connect/managing-connectors/overview) for that provider, which is right for most cases. To route a session to a specific profile (multiple profiles per provider, or migrating users to a new connector version), pass its `connector_profile_id`. Get the ID from [`GET /v2/connector_profiles`](/platform/api-reference/v2/connector-profiles/list-connector-profiles): ```bash curl -X POST https://api.stackone.com/connect_sessions \ -H "Authorization: Basic " \ -H "Content-Type: application/json" \ -d '{ "origin_owner_id": "customer-123", "origin_owner_name": "Acme Inc", "provider": "bamboohr", "connector_profile_id": "01JHMM0V..." }' ``` The resulting account inherits that profile's connector version pin. The most common reason to target a profile this way is moving end users onto a new connector major version that requires them to reauthenticate. See [Migrating to a new version](/connector-building/connector-versioning#migrating-to-a-new-version) for that flow. ## Filtering connectors Control which connectors appear in the Hub by configuring the connect session on your backend. You can specify a `provider` or `categories` property when creating the connect session to control which connectors appear in the Hub: - **`provider`**: Opens the Hub directly at the credential entry screen for a specific connector, bypassing the connector listing - **`categories`**: Filters the Hub to show only connectors from specified categories (e.g., `hris`, `ats`) If neither is specified, the Hub displays all connectors enabled for the project. The connector specified in `provider` must have an enabled [connector profile](/connect/managing-connectors/overview) in the associated project. Retrieve valid `provider` keys from [`GET /v2/connectors`](/platform/api-reference/v2/connectors/list-connectors). Each connector in the response carries a `key`, which is the value to pass here. ```javascript JavaScript // Skip connector list, go directly to BambooHR const result = await stackOne.connectSessions.createConnectSession({ originOwnerId: "customer-123", originOwnerName: "Acme Inc", provider: "bamboohr", // Go directly to this connector }); ``` ```javascript JavaScript (Categories) // Show only HRIS connectors const result = await stackOne.connectSessions.createConnectSession({ originOwnerId: "customer-123", originOwnerName: "Acme Inc", categories: ["hris"], // Filter to HRIS category }); ``` ## Next steps Embed the Hub, or share an Auth Link, to consume the token you just created. React to accounts being linked, updated, or disconnected. Keep each customer's linked accounts separate with `origin_owner_id`. Every request field and response shape. # Account Linking - StackOne Hub Source: https://docs.stackone.com/embed/account-linking/overview Let end-users authenticate and connect their accounts to your system The **StackOne Hub** allows your end-users to authenticate and connect their accounts into your application or agent. The Hub can either be embedded in your code, or for a no-code approach, you can generate a StackOne hosted web link you share with them that has the Hub pre-embedded. ## How it works 1. Your backend creates a [connect session](/embed/connect-session) and returns its **session token** to your frontend. 2. Display the **Hub** (or share an [Auth Link](/embed/account-linking/auth-link)) with that token. The end-user selects a connector and authenticates. 3. On a successful link, the **account ID** is returned via callback, event, or the `account.created` [webhook](/connect/webhooks). 4. Use that account ID to [call actions](/embed/call-actions/overview) on the account from your product.
StackOne Hub - Connector Selection StackOne Hub - Credential Entry
## Embed it or share a link The Hub reaches your end-users two ways. Embed it in your product for a branded in-app flow, or share an [Auth Link](/embed/account-linking/auth-link), a StackOne-hosted page with the Hub already embedded, generated from the dashboard or programmatically. You can also link an account directly from the dashboard, for internal tools or on a customer's behalf. See [Linking Accounts](/connect/managing-connectors/linking-accounts#link-from-the-dashboard). | | Embedded Hub | Auth Link | |---|---|---| | Where it runs | In your app | StackOne-hosted page | | Frontend work | Install and mount the Hub | None: share a URL | | Branding | Themed to match your app | StackOne-hosted | | Knowing it worked | Callbacks or webhooks | Webhooks only | | Best for | Production apps | Email flows, sales-led onboarding, demos | ## Ways to embed The StackOne Hub as a native React component (`@stackone/hub`). The same Hub as a framework-agnostic custom element (``) for non-React apps. A StackOne hosted web page showing the Hub that can be shared directly with end-users. Using the Legacy Hub? `@stackone/react-hub` remains available for existing implementations, but the Hub is required to fully support new features. Its setup and hook API are documented on [npm](https://www.npmjs.com/package/@stackone/react-hub). ## Next steps With the account linked, call its actions from your product over the Agent SDK, MCP, A2A, or RPC/HTTP. Return to the end-to-end embedding journey. # StackOne Hub (React) Source: https://docs.stackone.com/embed/account-linking/stackone-hub Embed the native React `` component to let end-users connect their accounts The **StackOne Hub** (`@stackone/hub`) is a native React `` component that renders directly in your React tree. It offers filtering, search, detailed error messages, and full theming support. It is the **recommended** way to implement the Hub. ## Quick start ```bash npm npm install @stackone/hub ``` ```bash yarn yarn add @stackone/hub ``` ```bash pnpm pnpm add @stackone/hub ``` The Hub needs a [connect session token](/embed/connect-session) to securely communicate with StackOne. This token must be generated server-side to keep your API key secure. ```typescript async function retrieveConnectSessionToken() { const response = await fetch('/api/stackone/connect-session', { method: 'POST', headers: { 'Content-Type': 'application/json' }, body: JSON.stringify({ username: 'jane@example.com' }), }); const { token } = await response.json(); return token; } ``` To route the session through a specific **connector profile** (when a provider has more than one), pass its `connector_profile_id` when creating the session. See [Target a specific connector profile](/embed/connect-session#target-a-specific-connector-profile). ```tsx import { StackOneHub } from "@stackone/hub"; import { useEffect, useState } from "react"; function ConnectorPage() { const [token, setToken] = useState(); useEffect(() => { retrieveConnectSessionToken().then(setToken); }, []); if (!token) return
Loading...
; return ( { console.log('Connected:', account.id, account.provider); }} onCancel={() => console.log('Cancelled')} onClose={() => console.log('Closed')} /> ); } ```
Your end-users now use the Hub to connect their accounts. Each successful link fires `onSuccess` with the linked account id — persist against your user — it's the account ID you'll use with every [action call](/embed/call-actions/overview). You can also capture it server-side from the `account.created` [webhook event](/embed/handle-account-events).
## Properties The `StackOneHub` component accepts these properties: | Property | Type | Default | Description | |------|------|---------|-------------| | `token` | `string` | — | Connect session token from your backend | | `mode` | `'integration-picker'` | `'integration-picker'` | Hub mode | | `accountId` | `string` | — | Pre-select a specific account to edit | | `baseUrl` | `string` | `'https://api.stackone.com'` | StackOne API base URL | | `appUrl` | `string` | `'https://app.stackone.com'` | StackOne App URL | | `height` | `string` | `'500px'` | Component height | | `theme` | `'light' \| 'dark' \| PartialMalachiteTheme` | `'light'` | Theme configuration | | `showFooterLinks` | `boolean` | `true` | Show footer links | | `onSuccess` | `(account: { id: string; provider: string }) => void` | — | Called when account is connected | | `onCancel` | `() => void` | — | Called when user cancels | | `onClose` | `() => void` | — | Called when hub closes | | `onCloseLabel` | `string` | `'Close'` | Custom label for the close button on the success screen | ```tsx import { StackOneHub } from "@stackone/hub"; { console.log(`Connected ${account.provider} with ID ${account.id}`); }} onCancel={() => console.log('User cancelled')} onClose={() => console.log('Hub closed')} onCloseLabel="Done" /> ``` Use `onSuccess` to update your UI or trigger backend syncs. Use `onClose` as a cleanup handler that always runs. ## Theming The Hub supports full theming with the `theme` property: ```tsx ``` For custom theming, pass a `PartialMalachiteTheme` object: ```tsx ``` See the [@stackone/hub repository](https://github.com/StackOneHQ/hub) for full theme options. For non-React stacks, use the [web components](/embed/account-linking/stackone-hub-web-component) build (``). For the older hook API, see [@stackone/react-hub](https://www.npmjs.com/package/@stackone/react-hub) on npm. ## Next steps With the account linked, call its actions from your product over the Agent SDK, MCP, A2A, or RPC/HTTP. Return to the end-to-end embedding journey. # StackOne Hub Web Component Source: https://docs.stackone.com/embed/account-linking/stackone-hub-web-component Embed StackOne Hub in any framework using the framework-agnostic custom element `@stackone/hub` ships a framework-agnostic custom element, ``, that you can drop into any HTML page or framework template. React and ReactDOM are bundled into the web-component build, so consumers don't need React installed. Use the web component for any non-React stack, or when you want a single code path across multiple frameworks. For a native React app, the [StackOne Hub (Native)](/embed/account-linking/stackone-hub) is usually a better fit. It integrates with your React tree and lets you pass callbacks as props. ## Quick start Install the package and register ``. The import is side-effecting. It registers `` on `customElements`. Point a ` ``` If you'd rather install via npm and bundle the script yourself, use the `import '@stackone/hub/webcomponent'` pattern shown in the other tabs. If you're starting fresh in React, the [`` component](/embed/account-linking/stackone-hub) is usually a better fit. It integrates with your React tree and lets you pass callbacks as props. Reach for the web component when you can't add another copy of React to your bundle, or when you want the same code path as your non-React surfaces. Install the package: ```bash npm npm install @stackone/hub ``` ```bash yarn yarn add @stackone/hub ``` ```bash pnpm pnpm add @stackone/hub ``` Register the element at app entry: ```tsx // src/main.tsx import '@stackone/hub/webcomponent'; import { StrictMode } from 'react'; import { createRoot } from 'react-dom/client'; import App from './App'; const root = document.getElementById('root'); if (!root) { throw new Error('#root element not found'); } createRoot(root).render( , ); ``` Tell TypeScript that `` is a valid JSX tag: ```tsx declare global { // biome-ignore lint/style/noNamespace: JSX intrinsic-element augmentation requires namespace syntax. namespace JSX { interface IntrinsicElements { 'stackone-hub': React.DetailedHTMLProps< React.HTMLAttributes & { token?: string; mode?: string; 'base-url'?: string; 'app-url'?: string; 'account-id'?: string; height?: string; theme?: string; 'show-footer-links'?: boolean | string; 'on-close-label'?: string; }, HTMLElement >; } } } ``` Install the package: ```bash npm npm install @stackone/hub ``` ```bash yarn yarn add @stackone/hub ``` ```bash pnpm pnpm add @stackone/hub ``` Vue's template compiler treats unknown tags as Vue components by default. Mark `stackone-hub` as a custom element so it falls through to the DOM: ```ts // vite.config.ts import vue from '@vitejs/plugin-vue'; import { defineConfig } from 'vite'; export default defineConfig({ plugins: [ vue({ template: { compilerOptions: { isCustomElement: (tag) => tag === 'stackone-hub', }, }, }), ], }); ``` Register the element at app entry: ```ts // src/main.ts import '@stackone/hub/webcomponent'; import { createApp } from 'vue'; import App from './App.vue'; createApp(App).mount('#app'); ``` Svelte treats unknown tags as custom elements automatically. No extra config required. Install the package: ```bash npm npm install @stackone/hub ``` ```bash yarn yarn add @stackone/hub ``` ```bash pnpm pnpm add @stackone/hub ``` Register the element at app entry: ```ts // src/main.ts import '@stackone/hub/webcomponent'; import { mount } from 'svelte'; import App from './App.svelte'; const target = document.getElementById('app'); if (!target) { throw new Error('#app element not found'); } mount(App, { target }); ``` Install the package: ```bash npm npm install @stackone/hub ``` ```bash yarn yarn add @stackone/hub ``` ```bash pnpm pnpm add @stackone/hub ``` Add `CUSTOM_ELEMENTS_SCHEMA` to the component (or module) that uses `` so Angular accepts unknown tags as custom elements: ```ts // src/app/app.component.ts import { CUSTOM_ELEMENTS_SCHEMA, Component } from '@angular/core'; @Component({ selector: 'app-root', standalone: true, schemas: [CUSTOM_ELEMENTS_SCHEMA], templateUrl: './app.component.html', }) export class AppComponent {} ``` Register the element at app entry: ```ts // src/main.ts import '@stackone/hub/webcomponent'; import { bootstrapApplication } from '@angular/platform-browser'; import { AppComponent } from './app/app.component'; bootstrapApplication(AppComponent).catch((err) => console.error(err)); ``` The Hub needs a [connect session token](/embed/connect-session) to communicate with StackOne. Generate it server-side to keep your API key off the client. ```typescript async function retrieveConnectSessionToken() { const response = await fetch('/api/stackone/connect-session', { method: 'POST', headers: { 'Content-Type': 'application/json' }, body: JSON.stringify({ username: 'jane@example.com' }), }); const { token } = await response.json(); return token; } ``` To route the session through a specific **connector profile** (when a provider has more than one), pass its `connector_profile_id` when creating the session. See [Target a specific connector profile](/embed/connect-session#target-a-specific-connector-profile). Mount the element, set the token, and listen for events: ```html ``` React 19 passes unknown props through as attributes, but events still need to be wired with `addEventListener` via a `ref`. React's `onSuccess={...}` JSX shorthand does **not** fire on native DOM `CustomEvent`s. ```tsx import { useEffect, useRef, useState } from 'react'; export default function App() { const [token, setToken] = useState(''); const hubRef = useRef(null); useEffect(() => { retrieveConnectSessionToken().then(setToken); }, []); useEffect(() => { const el = hubRef.current; if (!el) return; const onSuccess = (event: Event) => { const detail = (event as CustomEvent).detail; console.log('Connected:', detail.id, detail.provider); }; const onClose = () => console.log('Closed'); el.addEventListener('success', onSuccess); el.addEventListener('close', onClose); return () => { el.removeEventListener('success', onSuccess); el.removeEventListener('close', onClose); }; }, []); return ( ); } ``` Vue passes `:prop="value"` bindings through as HTML attributes when the tag is registered as a custom element. Vue's `@event` shorthand does **not** fire on native DOM `CustomEvent`s. Subscribe with `addEventListener` via a `ref` instead. ```vue ``` Svelte passes attribute bindings through directly. Its `on:event` shorthand **does** fire on native DOM `CustomEvent`s, so `` works. The example below uses `addEventListener` via `bind:this` to keep the typing explicit. ```svelte ``` Bind attributes with `[attr.name]="value"` to keep them as attributes rather than Angular property bindings. Angular's `(event)` template binding **does** fire on native DOM `CustomEvent`s, so `(success)="onSuccess($event)"` works. The example below uses `addEventListener` via `@ViewChild` for explicit teardown in `ngOnDestroy`. ```ts // src/app/app.component.ts import { AfterViewInit, Component, CUSTOM_ELEMENTS_SCHEMA, ElementRef, OnDestroy, ViewChild, } from '@angular/core'; @Component({ selector: 'app-root', standalone: true, schemas: [CUSTOM_ELEMENTS_SCHEMA], template: ` `, }) export class AppComponent implements AfterViewInit, OnDestroy { @ViewChild('hub') hubRef?: ElementRef; token = ''; private onSuccess = (event: Event) => { const detail = (event as CustomEvent).detail; console.log('Connected:', detail.id, detail.provider); }; private onClose = () => console.log('Closed'); async ngAfterViewInit() { this.token = await retrieveConnectSessionToken(); this.hubRef?.nativeElement.addEventListener('success', this.onSuccess); this.hubRef?.nativeElement.addEventListener('close', this.onClose); } ngOnDestroy() { this.hubRef?.nativeElement.removeEventListener('success', this.onSuccess); this.hubRef?.nativeElement.removeEventListener('close', this.onClose); } } ``` Your end-users now use the Hub to connect their accounts. Each successful link fires the `success` event with the linked account id — persist against your user — it's the account ID you'll use with every [action call](/embed/call-actions/overview). You can also capture it server-side from the `account.created` [webhook event](/embed/handle-account-events). ## Attributes The `` element accepts these attributes. All scalar `StackOneHub` properties map to kebab-case HTML attributes: | Attribute | Type | Default | Description | |---|---|---|---| | `token` | string | — | Connect session token from your backend | | `mode` | `integration-picker` | `integration-picker` | Hub mode | | `base-url` | string | `https://api.stackone.com` | StackOne API base URL | | `app-url` | string | `https://app.stackone.com` | StackOne App URL | | `height` | string | `500px` | Component height | | `theme` | `light` \| `dark` \| JSON object | `light` | Theme keyword or a JSON-encoded `PartialMalachiteTheme` | | `account-id` | string | — | Pre-select a specific account to edit | | `on-close-label` | string | `Close` | Custom label for the close button | | `show-footer-links` | boolean attribute | `true` | Toggle footer visibility | ## Style Customization Set the `theme` attribute to `light` or `dark`: ```html ``` For custom theming, pass a `PartialMalachiteTheme`. Because HTML attributes are strings, use `JSON.stringify(...)` to encode the object first. The `theme` attribute receives a JSON-encoded `PartialMalachiteTheme` string, not an object: ```html ``` Bind the `theme` attribute like any other with `[attr.theme]`, using a component property that holds a JSON-encoded `PartialMalachiteTheme`, the string produced by `JSON.stringify(...)`, since attributes are strings, not objects: ```ts @Component({ selector: 'app-root', standalone: true, schemas: [CUSTOM_ELEMENTS_SCHEMA], template: ` `, }) export class AppComponent { themeJson = JSON.stringify({ colors: { primary: { background: '#6366f1', foreground: '#ffffff', }, card: { background: '#fafafa', }, }, }); } ``` For a keyword theme, bind a plain string (`themeJson = 'dark'`) or set the attribute directly (`theme="dark"`). See the [@stackone/hub repository](https://github.com/StackOneHQ/hub) for full theme options. ## Events Callbacks are dispatched as native DOM `CustomEvent`s on the host element with `bubbles: true` and `composed: true`. | Event | `event.detail` | |---|---| | `success` | `{ id: string; provider: string }` | | `close` | `undefined` | Framework-emitted event shorthands behave differently from native DOM `CustomEvent`s. React's `onSuccess={...}` and Vue's `@event` do **not** fire on them. Subscribe with `addEventListener` via a ref. Svelte's `on:event` and Angular's `(event)` **do** fire on them. ## Next steps With the account linked, call its actions from your product over the Agent SDK, MCP, A2A, or RPC/HTTP. Return to the end-to-end embedding journey. # Hub (Auth Link) Source: https://docs.stackone.com/embed/account-linking/auth-link Get end-users to connect their accounts with only a link! Hub **Auth Links** let you deliver a secure URL to your end users for a secure, in-browser connection experience **without** embedding the StackOne Hub in your application. The hosted webpage already includes an implementation of the Hub so there's no front end implementation required from your side. ## Generating a link You can generate an Auth Link from the dashboard or programmatically via the API. An Auth Link can be generated directly from the StackOne dashboard. Here's how: Log in to the StackOne dashboard and select [Accounts](https://app.stackone.com/accounts) from the left menu. A popup will appear asking you to select a method. Choose **Method 1 - Request Authentication**. ![Accounts page with Link Account button](/images/accounts-page-link-account.png) * **Origin owner ID** - This should be the end-user identifier you use in your own system(s) (most likely, a UUID or integer) * **Origin owner name** - This is the end-user name in your own system(s) * **Origin username** (optional) - The end-user's username (eg: an email address) that will connect or be responsible for the connection Then click **Next**. ![Auth Link form](/images/auth-link-form.png) * **Filter the Hub** - Filter the list of connectors displayed to the end-user * **Connector Profile** - Route the session through a specific connector profile * **Link Expiry** - Control how long the link stays valid (default is 30 days) Then click **Generate**. ![Auth Link generated](/images/auth-link-generated.png) The end-user will now be able to connect their accounts using the link. Once the end-user connects, StackOne fires an `account.created` [webhook event](/embed/handle-account-events) containing the account ID. Persist it against your user: it's the account ID you'll use with every [action call](/embed/call-actions/overview). You can also find it through the dashboard on the [Accounts](https://app.stackone.com/accounts) page.
To support a more scalable solution, you can programmatically generate links for end-users. Call the [Create Connect Session](/platform/api-reference/connect-sessions/create-connect-session) endpoint with the end-user's details: * `origin_owner_id` - The end-user identifier in your own system(s), which is how accounts map to your customers in a [multi-tenant setup](/features/multi-tenant-accounts) * `origin_owner_name` - The end-user name in your own system(s) * `origin_username` (optional) - The end-user's username, e.g. an email address * `categories` (optional) - Filter the list of connectors displayed to the end-user * `expires_in` (optional) - How long the link stays valid, in seconds * `connector_profile_id` (optional) - Route the session through a specific [connector profile](/embed/connect-session#target-a-specific-connector-profile) The response contains an `auth_link_url` property. This is the link to send to the end-user. Deliver the `auth_link_url` to your end-user (for example by email). When they open it, they'll see the **StackOne Hub** listing the connectors enabled on your project, where they select and connect their account. ![StackOne Hub Connector Listing](/images/hub-connector-listing.png) Once the end-user connects, StackOne fires an `account.created` [webhook event](/embed/handle-account-events) containing the account ID. Persist it against your user: it's the account ID you'll use with every [action call](/embed/call-actions/overview). You can also find it through the dashboard on the [Accounts](https://app.stackone.com/accounts) page, or via the [List Accounts endpoint](/platform/api-reference/v2/accounts/list-accounts). Set `expires_in` (in seconds) to give end-users enough time to complete the connection. (eg. 5 days is 432000, 7 days is 604800)
## Next steps With the account linked, call its actions from your product over the Agent SDK, MCP, A2A, or RPC/HTTP. Return to the end-to-end embedding journey. # Handle Account Events Source: https://docs.stackone.com/embed/handle-account-events Subscribe to and handle StackOne's account lifecycle webhooks in your backend. Account events let your backend react to account lifecycle — a user connecting or disconnecting — instead of polling. This is the implementation walkthrough; for the event catalog and payload fields, see [Platform Events](/platform-api/platform-events) in the reference. Expose an HTTPS endpoint in your backend that returns `200` quickly. On the [Webhooks](https://app.stackone.com/webhooks) page, click **Add Webhook** and register its URL. From the **Signing secrets** tab, copy the signing secret if you plan to verify signatures (recommended). Account events are subscribed **on the webhook itself**, not on a connector profile (that's for connector events). When you add or edit the webhook on the [Webhooks](https://app.stackone.com/webhooks) page, select the account events you want: `account.created`, `account.updated`, and `account.deleted`. Via the API, set the webhook's `events` array when you create it (`POST /webhooks`) or update it (`PATCH /webhooks/{id}`): ```json { "webhook_url": "https://your-app.com/webhooks/stackone", "label": "account-lifecycle", "events": ["account.created", "account.updated", "account.deleted"] } ``` Each delivery is signed with HMAC-SHA256 over the raw request body, base64url-encoded, in the `x-stackone-signature` header. Verify it against your signing secret before trusting the payload: ```javascript import { createHmac, timingSafeEqual } from 'crypto'; function isSignatureValid(signature, rawBody, signingSecret) { if (!signature) return false; const expected = createHmac('sha256', signingSecret) .update(rawBody) .digest('base64url'); const a = Buffer.from(expected); const b = Buffer.from(signature); return a.length === b.length && timingSafeEqual(a, b); } ``` Hash the **raw request bytes** (not a re-serialized JSON string), and compare in constant time. See [Verifying webhook signatures](/connect/webhooks#verifying-webhook-signatures) for detail and secret rotation. Switch on the `event` field and act on the account. The payload carries `account_id`, `provider`, and the `origin_*` identifiers. See the [payload reference](/platform-api/platform-events#payload). ```javascript import express from 'express'; const app = express(); app.post('/webhooks/stackone', express.raw({ type: 'application/json' }), (req, res) => { const signature = req.headers['x-stackone-signature']; if (!isSignatureValid(signature, req.body, process.env.STACKONE_SIGNING_SECRET)) { return res.status(401).send('invalid signature'); } const { event, account_id, provider } = JSON.parse(req.body); switch (event) { case 'account.created': // kick off an initial sync for the new account break; case 'account.updated': // re-check scopes or resume a paused sync break; case 'account.deleted': // revoke downstream access and clean up the stored account_id break; } res.sendStatus(200); }); ``` [Auth Links](/embed/account-linking/auth-link) have no frontend callback, so `account.created` is how you know an account was linked. # Call Actions Source: https://docs.stackone.com/embed/call-actions/overview Choose how to invoke StackOne actions: direct API, MCP, A2A, or SDKs Once an account is linked, you can call its actions from your product. For the full journey up to that point — API key, connector profile, account linking — see the [Embed overview](/embed/getting-started). **Actions** are the atomic operations in StackOne: `salesforce_list_contacts`, `gmail_send_message`, `google_drive_list_files`, etc. Every protocol is just a different way to invoke the same underlying actions. All protocols route through the **same engine**, so authentication, rate limiting, data transformation, and error recovery are handled for every action. The choice comes down to your use case and how you're building. ## Protocols **Native TypeScript/Python** with framework integrations (LangChain, CrewAI, OpenAI) **Open standard** for AI tools. Works with Claude, Cursor, Vercel AI, n8n Call a pre-built agent per integration, for multi-agent orchestration. Call an action from any backend or script with no agent or framework. ## Which protocol? | | [Agent SDK](/embed/call-actions/agent-sdk) | [MCP](/embed/call-actions/mcp) | [A2A](/embed/call-actions/agent2agent) | [RPC/HTTP](/embed/call-actions/rpc-http) | |---|-----------|-----|-----|----------| | **Use case** | AI agents with frameworks | MCP-compatible clients | Multi-agent systems | Traditional apps, scripts | | **Best for** | Programmatic control: load, filter, and select tools dynamically | Quick setup, IDE agents, switching accounts by header | Agent orchestration, context isolation, long-running async tasks | Full control, non-agentic | | **Skip it when** | You just want tools in an existing MCP client | You need programmatic control or custom error handling | You need synchronous responses in a single agent | You're building an AI agent | | **Requires code** | Yes | No (config only) | Yes | Yes | | **Works with** | Any AI framework (LangChain, CrewAI, Vercel AI SDK, …) | Any MCP client (Claude, Cursor, Windsurf, n8n, …) | Any A2A orchestrator | Any HTTP client | ## Mixing protocols Many production setups combine protocols. They all use the same actions and authentication, so you can mix and match: - **RPC/HTTP for backend jobs** (scheduled syncs, data pipelines) - **Agent SDK for your product** (customer-facing AI features) - **MCP for internal tools** (Cursor, Claude Desktop for your team) - **A2A for complex workflows** (multi-agent orchestration) Exposing hundreds of actions? Use [Tool Discovery](/features/tool-discovery) so the agent searches at runtime instead of overloading its context window. It works through both MCP (`search_execute` mode) and the SDK (tool search). # Agent SDK Source: https://docs.stackone.com/embed/call-actions/agent-sdk Install, fetch, filter, and execute typed StackOne tools in TypeScript and Python agent frameworks. Bring StackOne actions into your code as typed TypeScript and Python tools. Fetch the tools for a [linked account](/gateway/concepts/linked-accounts), filter them to what your agent needs, and hand them to your framework's function-calling loop. The SDK is available in two languages: | | TypeScript | Python | |---|------------|--------| | Package | [`@stackone/ai`](https://www.npmjs.com/package/@stackone/ai) (npm) | [`stackone-ai`](https://pypi.org/project/stackone-ai/) (pip) | | Frameworks | [OpenAI Functions](/embed/call-actions/agent-sdk/openai), [Vercel AI SDK](/embed/call-actions/agent-sdk/vercel-ai-sdk) | [LangChain](/embed/call-actions/agent-sdk/langchain), [CrewAI](/embed/call-actions/agent-sdk/crewai), [OpenAI](/embed/call-actions/agent-sdk/openai), [LangGraph](/embed/call-actions/agent-sdk/langgraph), [Pydantic AI](/embed/call-actions/agent-sdk/pydantic-ai) | **Not sure if the Agent SDK is right for you?** Check out [Call Actions](/embed/call-actions/overview) to understand when to use the Agent SDK vs MCP vs A2A. StackOne Architecture Your agent connects to StackOne, which handles authentication and data normalization for hundreds of [SaaS providers](/connectors/introduction) like Salesforce, Workday, Slack, and more. | Component | Description | |-----------|-------------| | **Your Agent** | Built with LangChain, CrewAI, OpenAI, Vercel AI, or any framework | | **StackOne** | AI Integration Gateway: handles authentication, transforms data, manages connections | | **SaaS Providers** | Salesforce, Workday, Greenhouse, Slack, Gmail, HubSpot, and hundreds more | Key concepts: - **Initialize a ToolSet**: Create a `StackOneToolSet` instance to access tools for providers like Workday, Greenhouse, Slack, and more - **Filter Tools**: Use provider glob patterns like `workday_*` and `slack_*`, or the `fetch_tools()` method for provider/action/account filters - **Execute Tools**: Call provider APIs through StackOne tool interfaces: list employees, send messages, create tickets - **[Tool Discovery](/features/tool-discovery)**: Discover relevant tools at runtime via natural language queries - **Multi-Tenant**: Each tool execution requires an `account_id` to identify which customer's [account](/gateway/concepts/linked-accounts) to access ## Calling actions Before starting you need to have followed the previous setup steps described in the [Getting Started](/embed/getting-started). Then pick your framework. Each guide is a complete agent loop, from install to handing StackOne tools to your model: TypeScript and Python TypeScript Python Python Python Python ## Resources - **[GitHub (TypeScript)](https://github.com/StackOneHQ/stackone-ai-node)** and **[GitHub (Python)](https://github.com/StackOneHQ/stackone-ai-python)**: Complete source code and examples - **[Examples (TypeScript)](https://github.com/StackOneHQ/stackone-ai-node/tree/main/examples)**: OpenAI integration, semantic search, and file uploads - **[Examples (Python)](https://github.com/StackOneHQ/stackone-ai-python/tree/main/examples)**: LangChain, CrewAI, and semantic search examples - **[NPM Package](https://www.npmjs.com/package/@stackone/ai)** and **[PyPI Package](https://pypi.org/project/stackone-ai/)**: Package details and version history # OpenAI Source: https://docs.stackone.com/embed/call-actions/agent-sdk/openai Build AI agents with OpenAI function calling using the StackOne Agent SDK for TypeScript or Python StackOne tools work with OpenAI's function calling to build AI agents that access business data. **Supported languages:** TypeScript and Python. - **Convert tools** to OpenAI function schemas automatically - **Execute functions** with built-in handling - **Build conversational agents** with tool execution - **Multi-step workflows** for complex tasks ## Calling actions ```bash TypeScript # Requires Node.js 16.0 or higher # TypeScript 4.5 or higher (recommended) # Using npm npm install @stackone/ai openai # Using pnpm pnpm add @stackone/ai openai # Using yarn yarn add @stackone/ai openai # Using bun bun add @stackone/ai openai export STACKONE_API_KEY=your_api_key_here ``` ```bash Python # Requires Python 3.10 or higher # Using uv (recommended) uv add 'stackone-ai[mcp]' openai # Using pip pip install 'stackone-ai[mcp]' openai # Optional: install with example dependencies uv add 'stackone-ai[mcp,examples]' pip install 'stackone-ai[mcp,examples]' export STACKONE_API_KEY=your_api_key_here ``` Two approaches to retrieving tools: 1. [Fetch Tools (with filtering)](/features/tool-discovery#tool-filtering): fetch all tools upfront with optional filters applied. 2. [Advanced Tool Search](/features/tool-discovery#advanced-tool-search): hand the model just `tool_search` + `tool_execute` and let the agent discover what it needs at runtime. See [Tool Discovery](/features/tool-discovery) for more details on which may be best in your scenario. By default this fetches every tool enabled for the account. Narrow it by passing `providers` (specific connectors) or `actions`, exact names or glob patterns, following the `provider_operation_entity` tool naming (e.g. `workday_*`, or `*_list_*` for read-only tools). ```typescript TypeScript import OpenAI from 'openai'; import { StackOneToolSet } from '@stackone/ai'; // Get account ID from your app's auth context or StackOne dashboard const accountId = 'your-account-id'; const openai = new OpenAI(); const toolset = new StackOneToolSet(); // Fetch tools dynamically for this account. // Optionally narrow the fetch with filters: // providers: ["hibob", "workday"] — only these connectors // actions: ["*_list_*", "*_get_*"] — glob patterns, e.g. read-only actions const tools = await toolset.fetchTools({ accountIds: [accountId] }); // Convert to OpenAI function format const openAITools = tools.toOpenAI(); ``` ```python Python from openai import OpenAI from stackone_ai import StackOneToolSet # Initialise clients client = OpenAI() toolset = StackOneToolSet() # Fetch StackOne tools. # Optionally narrow the fetch with filters: # providers=["hibob", "workday"] — only these connectors # actions=["*_list_*", "*_get_*"] — glob patterns, e.g. read-only actions tools = toolset.fetch_tools( actions=['workday_get_worker', 'workday_list_workers'], account_ids=['your-account-id'] ) # Convert to OpenAI function format openai_tools = tools.to_openai() ``` The LLM receives only 2 tools and searches the catalog autonomously: ```typescript TypeScript import { StackOneToolSet } from '@stackone/ai'; const toolset = new StackOneToolSet({ search: { method: 'semantic', topK: 3 }, }); // tools contains only tool_search + tool_execute const tools = toolset.getTools({ accountIds: ['your-account-id'] }); // Convert to OpenAI function format — the agent loop also uses // `tools` to execute the calls the model makes const openAITools = tools.toOpenAI(); ``` ```python Python from stackone_ai import StackOneToolSet toolset = StackOneToolSet( search={"method": "semantic", "top_k": 3}, execute={"account_ids": ["your-account-id"]}, ) # LLM receives only 2 tools - it searches and executes autonomously. # .openai() returns OpenAI-format tools directly, so no conversion is needed openai_tools = toolset.openai(mode="search_and_execute") ``` Create the completion with the tools attached, then execute any tool calls the model makes: ```typescript TypeScript // Create completion with function calling const completion = await openai.chat.completions.create({ model: 'gpt-5.4', messages: [ { role: 'system', content: 'You are an HR assistant with access to employee data.' }, { role: 'user', content: 'How many employees do we have?' } ], tools: openAITools, tool_choice: 'auto' }); // Execute any tool calls const message = completion.choices[0].message; if (message.tool_calls) { for (const toolCall of message.tool_calls) { const tool = tools.getTool(toolCall.function.name); if (tool) { const result = await tool.execute( JSON.parse(toolCall.function.arguments) ); console.log('Result:', result.data); } } } ``` ```python Python # Create an AI agent with tool access response = client.chat.completions.create( model="gpt-5.4", messages=[ { "role": "system", "content": "You are an HR assistant with access to employee data." }, { "role": "user", "content": "How many employees are in engineering?" } ], tools=openai_tools, tool_choice="auto" ) # Handle tool calls message = response.choices[0].message if message.tool_calls: for tool_call in message.tool_calls: tool = tools.get_tool(tool_call.function.name) if tool: result = tool.execute(tool_call.function.arguments) print(f"Result: {result}") ``` The model first calls `tool_search`, then `tool_execute`. The same loop as the Fetch tools tab, run until the model stops calling tools: ```typescript TypeScript // Route every tool call through the toolset and feed the result // back until the model stops import OpenAI from 'openai'; const client = new OpenAI(); const messages: OpenAI.ChatCompletionMessageParam[] = [ { role: 'system', content: 'Use tool_search to find relevant tools, then tool_execute to run them. ' + 'Read parameter schemas from tool_search results carefully.', }, { role: 'user', content: 'List my upcoming Calendly events for the next week.' }, ]; for (let step = 0; step < 10; step++) { const response = await client.chat.completions.create({ model: 'gpt-5.4', messages, tools: openAITools, tool_choice: 'auto', }); const choice = response.choices[0]; if (!choice.message.tool_calls?.length) { console.log(choice.message.content); break; } messages.push(choice.message); for (const toolCall of choice.message.tool_calls) { // Look the meta tool up in the collection from the fetch step const tool = tools.getTool(toolCall.function.name); const result = tool ? await tool.execute(toolCall.function.arguments) : { error: `Tool "${toolCall.function.name}" not found` }; messages.push({ role: 'tool', tool_call_id: toolCall.id, content: JSON.stringify(result), }); } } ``` ```python Python # Route every tool call through the toolset and feed the result # back until the model stops import json from openai import OpenAI client = OpenAI() messages = [ { "role": "system", "content": ( "Use tool_search to find relevant tools, then tool_execute to run them. " "Read parameter schemas from tool_search results carefully." ), }, {"role": "user", "content": "List my upcoming Calendly events for the next week."}, ] for _step in range(10): response = client.chat.completions.create( model="gpt-5.4", messages=messages, tools=openai_tools, tool_choice="auto", ) choice = response.choices[0] if not choice.message.tool_calls: print(choice.message.content) break messages.append(choice.message.model_dump(exclude_none=True)) for tool_call in choice.message.tool_calls: result = toolset.execute(tool_call.function.name, tool_call.function.arguments) messages.append({ "role": "tool", "tool_call_id": tool_call.id, "content": json.dumps(result), }) ``` ## Example A full runnable example: